Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

DCRat

13
Global rank
13 infographic chevron month
Month rank
16 infographic chevron week
Week rank

DCrat, also known as Dark Crystal RAT, is a remote access trojan (RAT), which was first introduced in 2018. It is a modular malware that can be customized to perform different tasks. For instance, it can steal passwords, crypto wallet information, hijack Telegram and Steam accounts, and more. Attackers may use a variety of methods to distribute DCrat, but phishing email campaigns are the most common.

RAT
Type
ex-USSR
Origin
1 July, 2018
First seen
8 October, 2026
Last seen
Also known as
Dark Crystal RAT

How to analyze DCRat with ANY.RUN

RAT
Type
ex-USSR
Origin
1 July, 2018
First seen
8 October, 2026
Last seen

IOCs

IP addresses
172.66.2.5
172.211.123.250
150.171.109.99
192.178.183.132
23.3.89.98
150.171.28.11
135.233.95.135
20.165.94.63
150.171.109.100
104.18.22.222
23.59.18.102
20.190.160.67
140.82.121.4
48.209.138.189
185.199.108.133
150.171.27.11
23.216.77.25
204.79.197.203
128.90.105.90
142.251.14.138
Hashes
8232c450f967d7f2f22c54582f0667f4c033ae62e6d450ff8a35c47486249443
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
6c69ce0fe6fab14f1990a320d704fee362c175c00eb6c9224aa6f41108918ca6
5f4229d18e5606330146ee13bdf726e10c1e06cbb15368c47f1ae68abe9ce4ba
ec78ddd4ccf32b5d76ec701a20167c3fbd146d79a505e4fb0421fc1e5cf4aa63
41ce6a7b18364efecced0419b42165d4f86c43643bbe1043014d4142cf86186a
57f81a5fcbd1fefd6ec3cdd525a85b707b4eead532c1b3092daafd88ee9268ec
89082fb05229826bc222f5d22c158235f025f0e6df67ff135a18bd899e13bb8f
e848603b7a73a88e3fe7bffa20e83397f5d1e93e77babb31473cc99e654a27b7
Domains
onepicce.ydns.eu
google.com
th.bing.com
slscr.update.microsoft.com
fe3cr.delivery.mp.microsoft.com
self.events.data.microsoft.com
edge.microsoft.com
ecs.office.com
login.live.com
www.microsoft.com
config.edge.skype.com
oneocsp.microsoft.com
www.bing.com
copilot.microsoft.com
clients2.googleusercontent.com
edge-consumer-static.azureedge.net
ocsp.digicert.com
api.edgeoffer.microsoft.com
update.googleapis.com
release-assets.githubusercontent.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:qtde-hsrliifrcbjetzlhjhtqkc2nwibtobuy31lfcc&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://github.com/c21cuvik-cyber/aviso-oficio-no.-1151-notifica-sentencia-no.-109-de-tutela-radicado-2026-0018500/releases/download/importante/aviso.oficio.no.1151.notifica.sentencia.no.109.de.tutela.radicado.2026-0018500.js
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://release-assets.githubusercontent.com/github-production-release-asset/1409326475/8f626b95-094e-4592-b236-77f0b6f168ae?sp=r&sv=2018-11-09&sr=b&spr=https&se=2026-10-08t01%3a40%3a46z&rscd=attachment%3b+filename%3daviso.oficio.no.1151.notifica.sentencia.no.109.de.tutela.radicado.2026-0018500.js&rsct=application%2foctet-stream&skoid=96c2d410-5711-43a1-aedd-ab1947aa7ab0&sktid=398a6654-997b-47e9-b12b-9515b896b4de&skt=2026-10-08t00%3a40%3a37z&ske=2026-10-08t01%3a40%3a46z&sks=b&skv=2018-11-09&sig=pav6yiu3jvvhw0kwpchjd4kfr%2bniffux5q6gktdqate%3d&jwt=eyj0exaioijkv1qilcjhbgcioijiuzi1nij9.eyjpc3mioijnaxrodwiuy29tiiwiyxvkijoicmvszwfzzs1hc3nldhmuz2l0ahvidxnlcmnvbnrlbnquy29tiiwia2v5ijoia2v5msisimv4cci6mtc5mtqymdc3mswibmjmijoxnzkxndiwndcxlcjwyxroijoicmvszwfzzwfzc2v0chjvzhvjdglvbi5ibg9ilmnvcmuud2luzg93cy5uzxqifq.en3vrbnsnnle1alq0fq0ieo9qq0rmbzga5h9zrmbfta&response-content-disposition=attachment%3b%20filename%3daviso.oficio.no.1151.notifica.sentencia.no.109.de.tutela.radicado.2026-0018500.js&response-content-type=application%2foctet-stream
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d293%2526e%253d1
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://update.googleapis.com/service/update2/json?cup2key=14:bcugcpbv_kokrgsi6bm2miv_qhh40docmzkf0_ipsfc&cup2hreq=c75cf4fb0521723a6ef70ff0a0f0d39097af1faa689691c6b8ae7f91d05a33fe
https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
https://edge.microsoft.com/abusiveadblocking/api/v1/blocklist
https://clients2.googleusercontent.com/crx/blobs/azpvhcqildrgqxyclcenwovmaua7lwu2mln7dephdl7eqkp9gczqmiehkjncu7a_eigr4ip8elijgyg1mgbqewwsojngu_j8zva9cfi_aj--ikwjbypwnpfv9nmzws17bigaxlka5c7tdptpcgaddf44n1nzr3cqv7qk/ghbmnnjooekpmoecnnnilnnbdlolhkhi_1_110_1_0.crx
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791420469&lafgdate=0
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2367
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 3913
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11489
comments 0

What is DCRat malware?

DCRat, also known as Dark Crystal RAT, is a remote access trojan (RAT) that lets threat actors take control over an infected machine and extract users’ data, such as the information copied to the clipboard and personal credentials from apps. The malware is known for its stealthiness and its ability to evade detection by security software. DCrat has been in operation since 2018, yet it regularly undergoes changes aimed at advancing and expanding its capabilities.

The malware consists of several components each responsible for a certain type of malicious activity, including stealing of cryptocurrency and keylogging. On top of that, the authors of DCrat have published a special software called DCRat Studio, which serves as a tool for developing new modules for the malware.

DCrat's popularity can be attributed in part to its low cost. Its one-month license goes for a mere $5, while a lifetime one is available for $40. This is a stark contrast to other malware-as-a-service options. For instance, a lifetime AgentTesla subscription will require forking out $120. According to researchers, such prices are due to the malware being simply a pet project of a single developer, who does not work on it full-time. The developer is likely based in the ex-USSR region.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of the DCRat malicious software

Although back in 2018, the malicious program utilized Java, it switched to C# in 2019. As a result, nowadays, the majority of Dark Crystal RAT’s modules are written in the C# programming language. However, the administrative server for this malware is developed with JPHP, which is an implementation of PHP that relies on the Java Virtual Machine.

Different samples of the malware have been observed to be outfitted with evasion and obfuscation techniques. For instance, in order to create a layer of protection against malware analysts’ attempts to reverse engineer its code, DCrat’s payload can be obfuscated with Enigma Protector.

The standard set of tools available to threat actors using DCrat includes:

  • DCRat can record the victim's keystrokes, which can be used to steal passwords and other sensitive information.
  • The separate CryptoStealer module of the malware allows attackers to get access to users’ crypto wallet information.
  • It can collect information about the system (CPU and GPU stats, etc.)
  • It can take screenshots of the victim's computer, which can be used to monitor their activity.
  • DCRat can exfiltrate information from browsers, such as session cookies, auto-fill credentials, and credit card details.
  • The malware can transmit the contents of the victim's clipboard to its command-and-control server (C&C).
  • It can hijack Telegram, Steam, Discord accounts.
  • DCrat can function as a loader, dropping other types of malware on the infected computer.

Additionally, DCrat can execute a persistence algorithm to retain control over the system. For instance, the malware can copy itself to a random running process and to the root directory (C:). It then can create shortcuts to these copies in the user's Startup folder. It can also add registry values that point to these shortcuts. This allows DCrat to start automatically when the computer boots up.

It is important to note that Dark Crystal RAT is polymorphic, meaning that attackers can use its builder functionality to add changes to the malware’s code to make it difficult to detect using traditional methods, such as file hash.

Execution process of DCRat

Uploading Dark Crystal RAT to the ANY.RUN sandbox lets you quickly see the malicious activities triggered by the malware. Here is a sample of DCrat executed in the interactive sandbox.

DCrat's flexibility makes it challenging to handle, but there are things that can help us pinpoint it. For example, DCrat rarely produces malicious activity in its current process. Like most malware, it prefers to create large process trees and then infiltrate a harmless process at some point to detonate later. By using ANY.RUN, we can easily identify the process targeted by the malware.
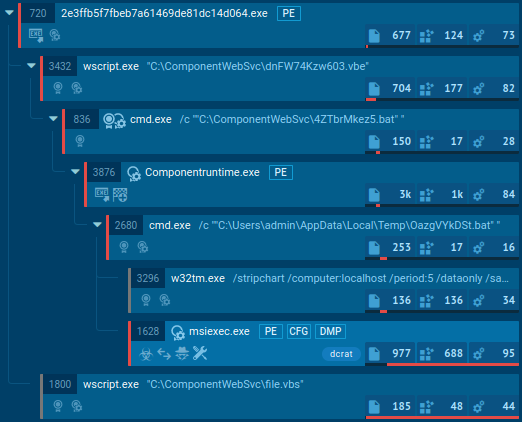
DCRat process tree DCRat's process tree

On top of that, it can delay execution for a period of time after the infection, drop executables, run embedded payloads, and use WMI queries to detect a virtualized environment or or to gain persistence in the system.
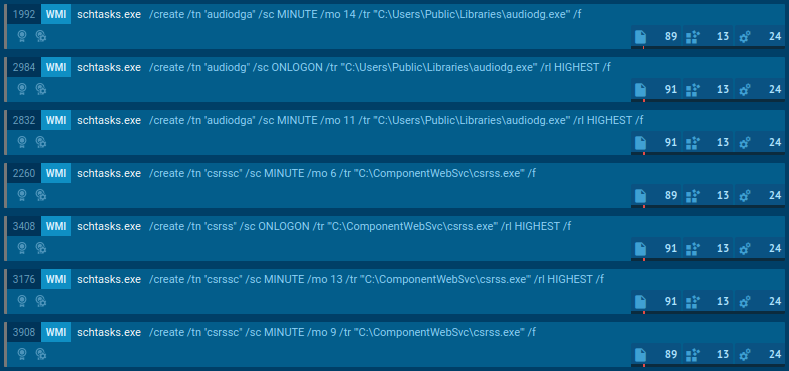
DCRat process tree DCRat's WMI queries

Distribution methods of the DCRat malware

Since Dark Crystal RAT is sold openly on the Internet, cyber criminals of all skill levels have access to it. Subsequently, there are many different methods they implement to drop the payload on victims’ computers. Yet, as is the case with most remote access trojans, including Vidar, njRAT, and QuasarRAT, DCrat’s main way of infecting a system is via phishing emails.

Threat actors devise sophisticated multi-staged attacks intended to manipulate the victim into believing that the fake email is actually legitimate and the attachment file it contains is safe to open. These downloadable files are usually in an office suite format, such as .docx or .xls, and have built-in macros or other mechanisms that can trigger the chain reaction which will result in DCRat being dropped onto the system.

There are also accounts of users unsuspectingly downloading a DCrat executable from websites distributing torrent files. In such cases, the malware can be disguised as a legitimate program. Once executed, the program installs the malicious program and runs it, stealing the user’s data often without them being aware of it.

Conclusion

Dark Crystal RAT is a remote access trojan that constitutes a significant concern for organizations and individuals worldwide. The malware’s low price tag and modular design make it an in-demand tool among cyber criminals. To protect your system from DCrat, you should be very careful about opening links or attachments from unknown senders.

Instead of taking the risk of downloading and opening potentially harmful files or clicking on malicious links, you can first analyze them in a sandbox environment like ANY.RUN. This will allow you to quickly and safely determine whether the file is malicious or not. ANY.RUN will also provide you with a detailed report about the malware, including its indicators of compromise (IOCs) and tactics, techniques, and procedures (TTPs). This information can be used to protect your organization from future attacks.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Phishing kit screenshot
Phishing kit
tycoon evilproxy sneaky2fa
Phishing kits are pre-packaged sets of malicious tools designed to make it easy for cybercriminals to launch phishing attacks. These kits replicate legitimate websites, steal credentials, and often include backend infrastructure for managing stolen data.
Read More
Salty 2FA screenshot
Salty 2FA
salty2fa
Salty 2FA is a sophisticated Phishing-as-a-Service (PhaaS) framework tailored to hijack user sessions, steal credentials, and gain unauthorized access to corporate systems. Delivered primarily via targeted emails, this kit employs multi-stage evasion tactics, making it a stealthy tool for cybercriminals aiming at high-value enterprise accounts.
Read More
Cerber screenshot
Cerber
cerber
Cerber is a Ransomware-as-a-Service (RaaS) that appeared in 2016, spread quickly and has been evolving since. It became well-known for its file encryption, offline capabilities, and sophisticated evasion techniques. It primarily targets enterprises, financial institutions, and government entities, encrypting their data and demanding ransom payments in Bitcoin. It also targets everyday users encrypting personal files (photos, documents) with the risk of their permanent loss.
Read More
SolarisLoader screenshot
SolarisLoader
solaris
SolarisLoader is a malware loader designed to neutralize security infrastructure before deploying high-risk secondary payloads. It utilizes a "Bring Your Own Vulnerable Driver" technique to gain kernel-level access and terminate antivirus processes. To remain undetected, the malware patches internal Windows monitoring interfaces and isolates the machine from security updates. Finally, it establishes a resilient three-layer persistence mechanism involving scheduled tasks, registry backups, and a watchdog component.
Read More
zgRAT screenshot
zgRAT
zgrat
zgRAT is a malware known for its ability to infect systems and exfiltrate sensitive data to command-and-control (C2) servers. It is primarily distributed through loader malware, as well as phishing emails. zgRAT employs various advanced techniques, including process injection and code obfuscation, to evade detection and maintain persistence on infected systems. The malware can also spread via USB drives and uses popular messaging platforms like Telegram and Discord for data exfiltration.
Read More
SalatStealer screenshot
SalatStealer
salatstealer
SalatStealer, also known as WEB_RAT or Salat Stealer, is a Go-based information-stealing malware targeting Windows systems. It operates as a Malware-as-a-Service (MaaS) focusing on harvesting browser credentials, cryptocurrency wallets, and session data from popular applications like Telegram and Steam.
Read More