Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

PrivateLoader

131
Global rank
129 infographic chevron month
Month rank
148 infographic chevron week
Week rank

PrivateLoader is a malware family that is specifically created to infect computer systems and drop additional malicious programs. It operates using a pay-per-install business model, which means that the individuals behind it are paid for each instance of successful deployment of different types of harmful programs, including trojans, stealers, and other ransomware.

Loader
Type
ex-USSR
Origin
1 May, 2021
First seen
29 September, 2026
Last seen

How to analyze PrivateLoader with ANY.RUN

Type
ex-USSR
Origin
1 May, 2021
First seen
29 September, 2026
Last seen

IOCs

IP addresses
57.153.246.3
135.234.160.244
48.192.1.65
94.142.138.131
94.142.138.113
40.126.32.68
208.67.104.60
149.154.158.34
23.59.18.102
2.16.241.9
48.209.6.48
135.234.160.245
40.126.31.2
23.52.181.141
48.209.138.168
74.178.76.128
172.211.123.250
48.209.133.15
23.52.181.212
48.209.138.189
Hashes
3ee5dea5ab6c3e929b4ef3354b8145774289e632038ac790ec0acde475e490b4
e65479d385bc0a9acf84103e7beb385511d0bf6f1ee35c8722640a9d1a6ee0fa
08c9e851321c951410d075af7f8bb2b472485780e5b60e940d01397f9e5c37e8
170737e0f64a43fdd7b49bd9759d67f006d7f769276f9993fa6518b8362b42d9
053cf60422f02eb7f91813de3e07ae427f3ecf6f694931c3c601183428de97fe
b57a88e5b1acf3a784be88b87fa3ee1f0991cb7c1c66da423f3595ffc6e0c5c2
44ee2445a8afa4123bd2edb2bcbe258f8c344f73fda88d03097e22a7928d313d
2f3bf1110899a66d69eed2c93cb7df127d062a1251bf1f8b8589a23f6c12f00b
b2549a6f78c10f7561710d06a9dd3f825f853f0afa20bda1eb37cc7d0b7192a4
f2b942af74f8846ba3b6141c845b368ac8a1eea9cae2226414a735ee920774e4
87a9323ac85ce28867d5d7ce590c8f29b8d1a999961fca71bb33adef48683691
c14d3913451eaaccc04743d2b84c7e1ec8edd9038821dae912e404fcb24aa498
fdff38130fc67a5cbb4c2d00d41f58b727d2eb0bacb8d515ea6d1dd6613e66bc
9eae5300f0e0c167385eb04c9959f4bdc9140f84b33d269f38609af4e684c38a
360cbf56f3d867b67ea52204c90eb73b9df72e345abd5effd34c9fdb409b6dc8
330973e361c9f42a1f4b2917526799398c3feb4fb9c59f66837d7ad4e7532967
5e3bae5378e609ddb26922dcca91f7762a921ab1ed304617347d692a60a4884d
a60a010fefce379cb8f3c20c30fa5f7dd230e6714021b9163ec39dcd2afce11f
293aa5c8425e620f1b7f425ec73d67934e329447f9819475df0ca6129409905a
888397ed65935c39792449357dc8d5c8a4b35ab4e87991816225d74edbc110ce
Domains
crl.microsoft.com
login.live.com
activation-v2.sls.microsoft.com
settings-win.data.microsoft.com
google.com
watson.events.data.microsoft.com
www.microsoft.com
ecs.office.com
slscr.update.microsoft.com
go.microsoft.com
client.wns.windows.com
self.events.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
www.bing.com
api.db-ip.com
c.pki.goog
ocsp.digicert.com
vk.com
www.maxmind.com
db-ip.com
URLs
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://94.142.138.113/api/tracemap.php
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.1.crl
http://23.254.227.214/api/tracemap.php
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is PrivateLoader malware?

PrivateLoader is a loader, which serves to embed other malware families on compromised systems. The creators of this malicious software, who are likely to be from ex-USSR countries, monetize their activity by charging various threat actors for the installation of their particular type of payload. The services are advertised openly on forums and Telegram channels, making them widely accessible.

The earliest instances of the malware’s activity can be traced to the beginning of 2021. However, researchers were able to spot it for the first time only in 2022, when it gained notoriety as the most widely used loader of the year.

A common vector of infection in the case of PrivateLoader has been through websites offering cracked versions of popular software. Once victims downloaded a file from such sites and ran an alleged software executable, they launched a chain reaction, which led to the installation of PrivateLoader and eventually to a trojan, stealer, or another type of malware being deployed on their system.

Some of the known malware families that have been pushed by PrivateLoader include Redline, DCRAT, Raccoon, and Smokeloader.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Technical details of the PrivateLoader malicious software

PrivateLoader is written in C++ and has a control panel, allowing operators to manage its activity, including by adding new payload links and tracking the total number of installations.

PrivateLoader is set up to drop payloads depending on the configuration of each victim’s system. For instance, it can distribute malware based on the geo location. It can also scan the machine to determine if there are any crypto wallets installed and see banking credentials. Yet, in most cases, it does not exfiltrate this information.

PrivateLoader is a modular threat, consisting of three distinct parts, each with its own purpose. It starts with the Loader module, which is intended for downloading the main Core module. The latter then contacts the command-and-control server (C2) and drops the next-stage threat, as well as the Service module that is regularly updated and responsible for keeping the loader on the victim’s system. In certain instances, PrivateLoader can drop several payloads.

The malware also makes use of the Dead Drop Resolver technique, where it utilizes legitimate services, such as Discord, to host malicious payloads.

PrivateLoader employs various techniques to prevent analysis, including encrypting its important strings and obfuscating the C2 communication.

Execution process of PrivateLoader

Let’s see how PrivateLoader operates in detail by uploading its sample to ANY.RUN, an interactive sandbox for malware analysis.

The main PrivateLoader process creates a child process whose executable file is located in the user’s “Pictures” directory. The created child process is added to the startup using Task Scheduler. The executable file of the child process was downloaded from the Internet.

Analyzing the HTTP requests, we can observe connections and data exchanges with the C2 server. The content sent (as well as received) in POST requests consists of BASE64-encoded strings. Moving forward to the indicators, we can see that the malware steals user credentials from browsers.

Read a detailed analysis of PrivateLoader in our blog.
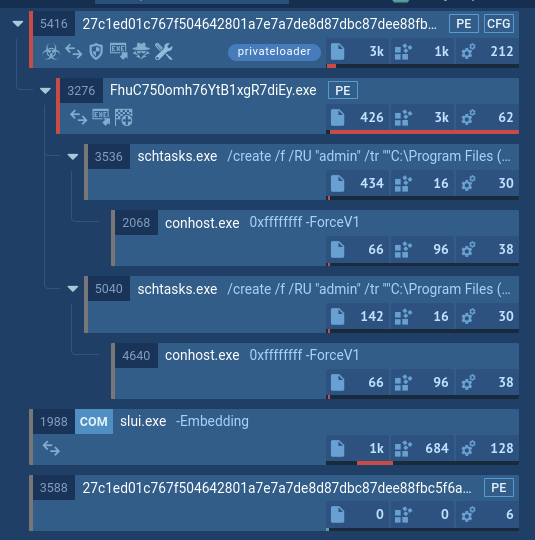
PrivateLoader process tree shown in ANY.RUN PrivateLoader’s process tree demonstrated in ANY.RUN

Distribution methods of the PrivateLoader malware

As mentioned above, the primary way PrivateLoader can infect a computer is via a direct download. Attackers employ SEO poisoning to boost the ranking of their websites. Users visit these links in search of different types of legitimate programs. Yet, after downloading an archive from the website and opening its contents, an infection begins, allowing PrivateLoader to compromise the entire system.

Conclusion

PrivateLoader is a serious threat to organizations and individuals because of the scale of its operation, as it can infect hundreds of thousands of computers in a short period of time. In order to avoid falling victim to this and other malware, it is vital to steer clear of suspicious websites and never download software from unofficial sources.

To determine whether a certain file or link is malicious, use ANY.RUN. It is a malware sandbox that provides users with the ability to interact with the samples at hand in a safe cloud environment. For instance, PrivateLoader usually comes packed into a passworded archive. ANY.RUN lets you easily open it, extract the contents, and run them as if you were using your own computer to expose any harmful behavior and collect IOCs.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

DarkTortilla screenshot
DarkTortilla
darktortilla
DarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.
Read More
Cephalus screenshot
Cephalus
cephalus
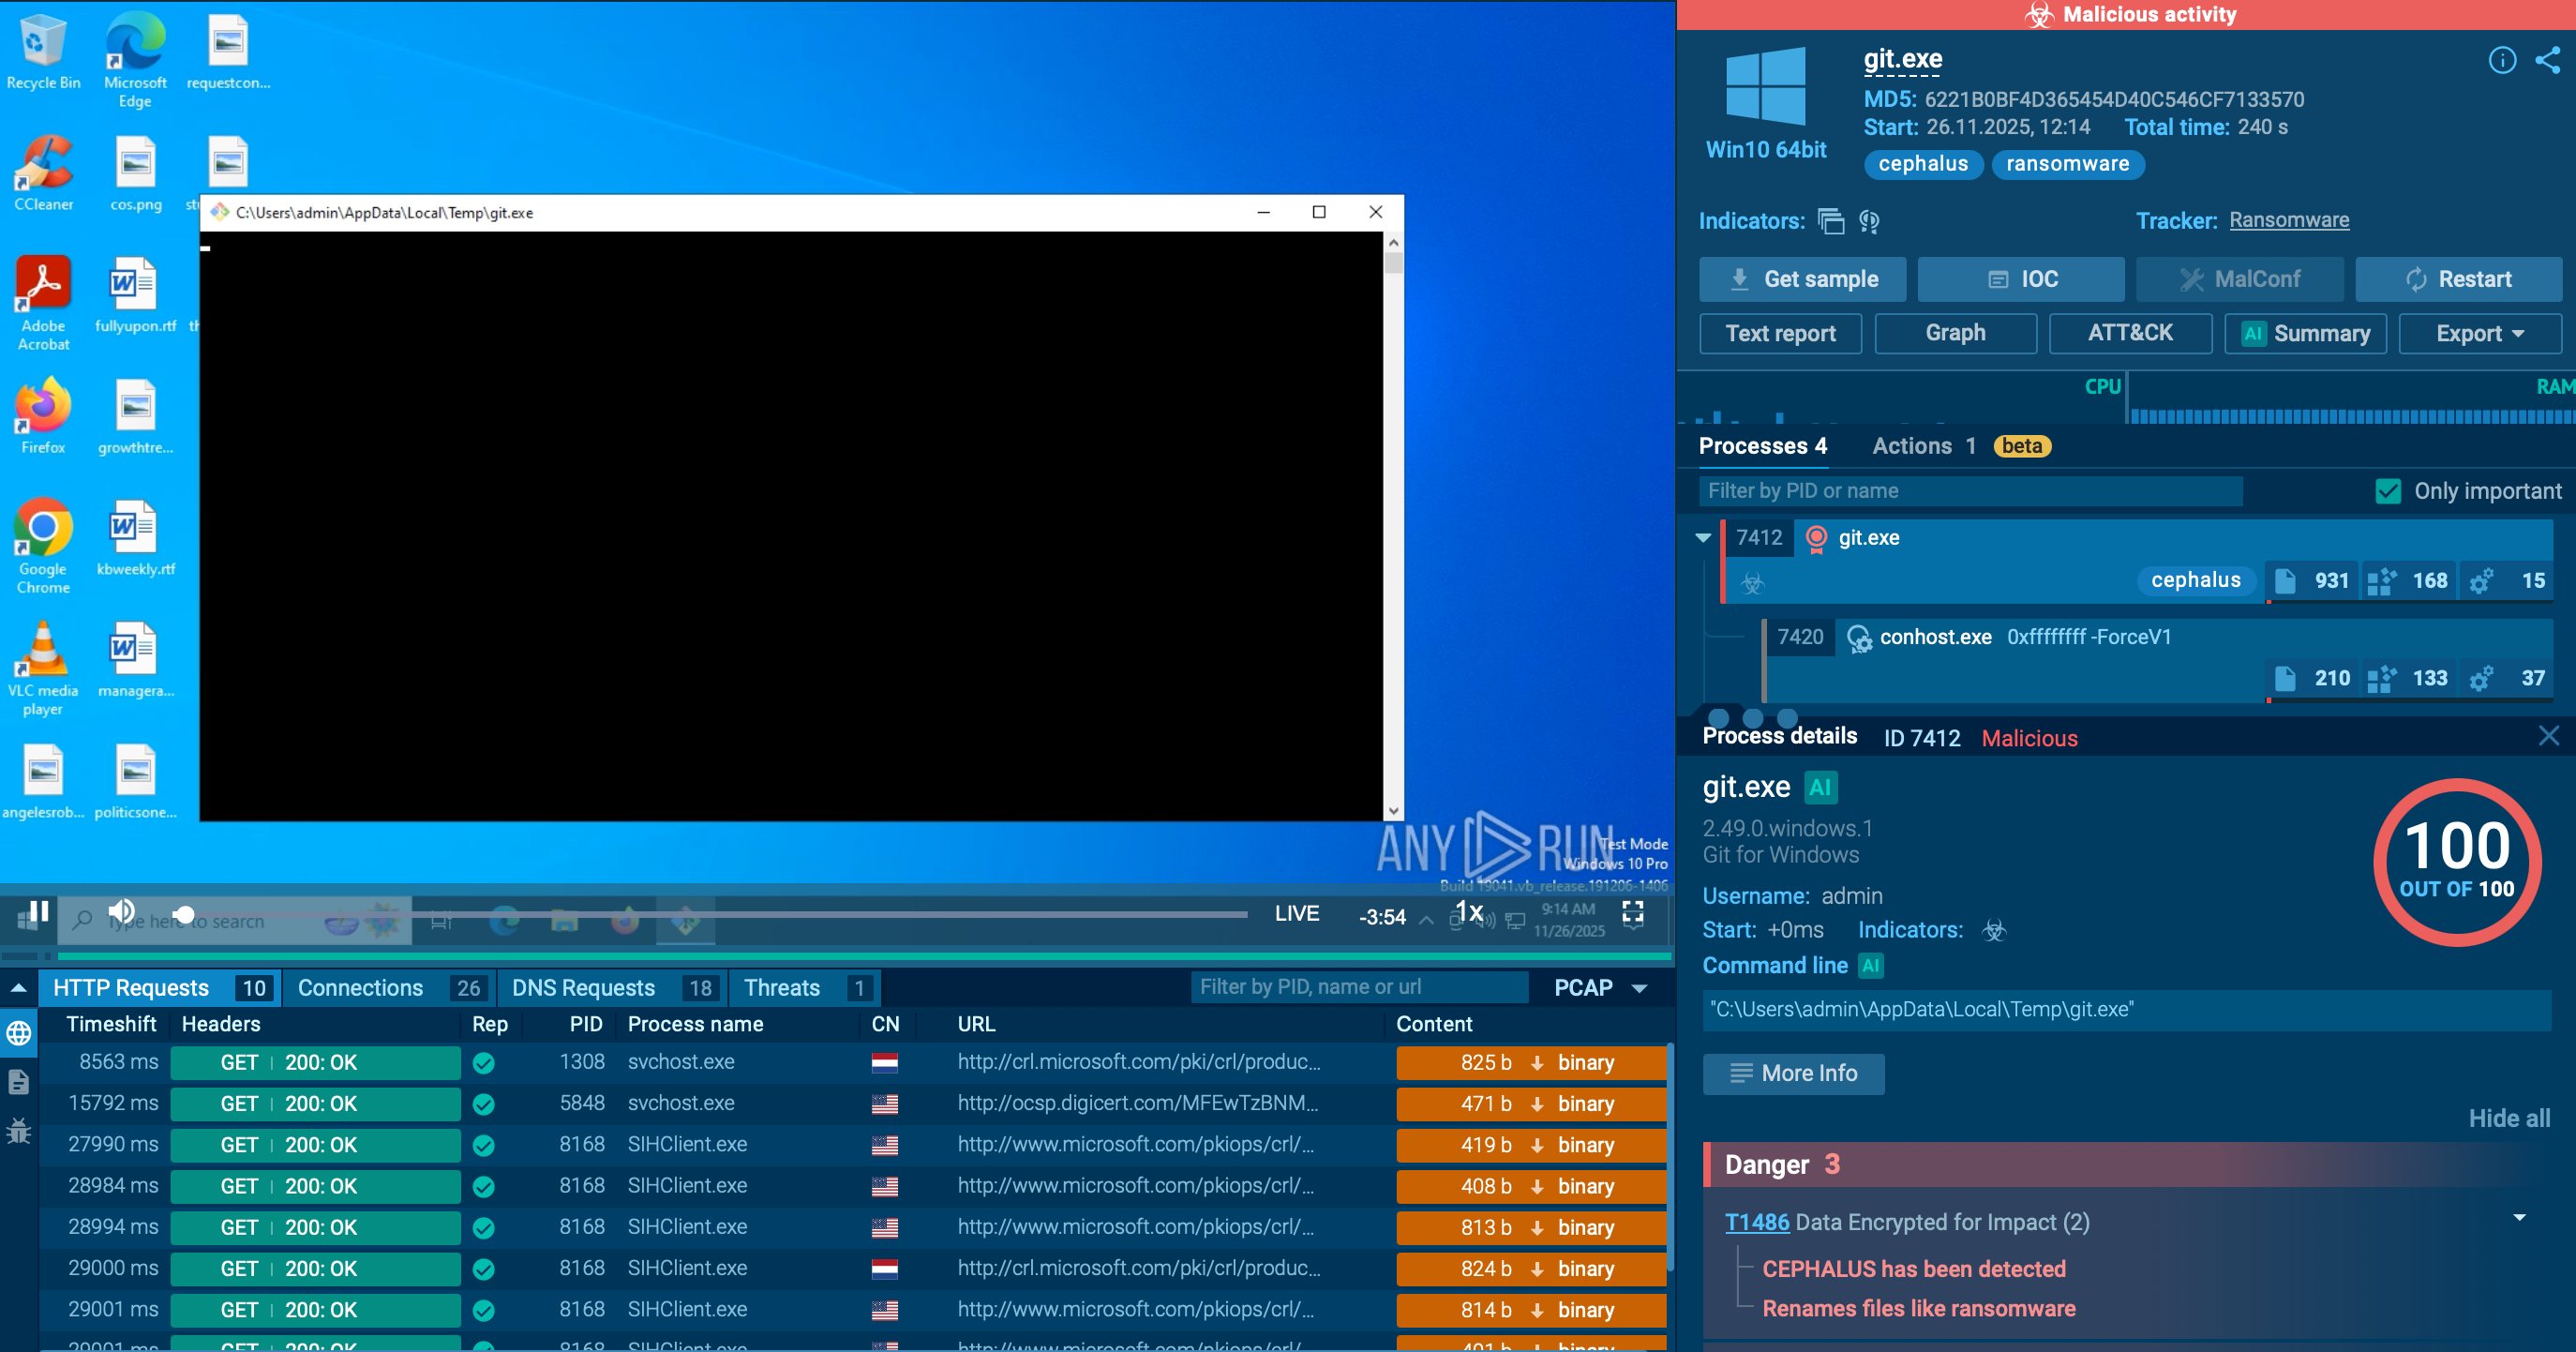
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
Read More
Orcus RAT screenshot
Orcus RAT
orcus rat trojan
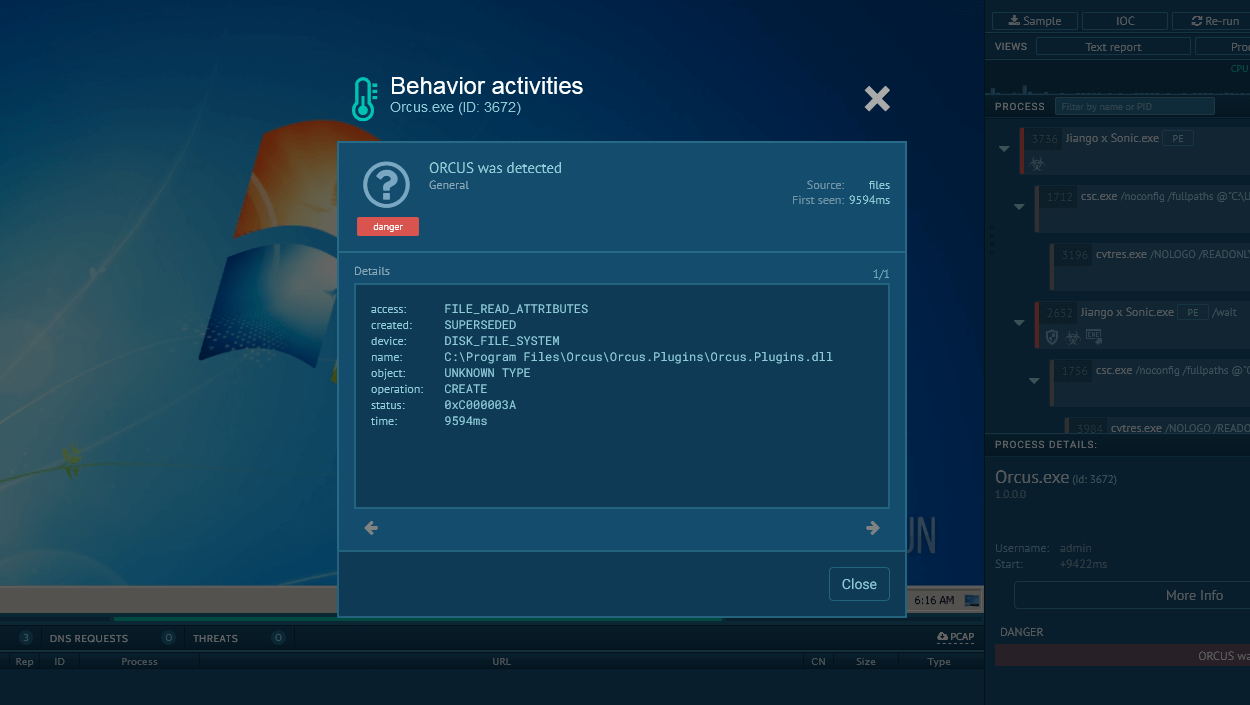
Orcus is a modular Remote Access Trojan with some unusual functions. This RAT enables attackers to create plugins using a custom development library and offers a robust core feature set that makes it one of the most dangerous malicious programs in its class.
Read More
Diamotrix screenshot
Diamotrix
diamotrix
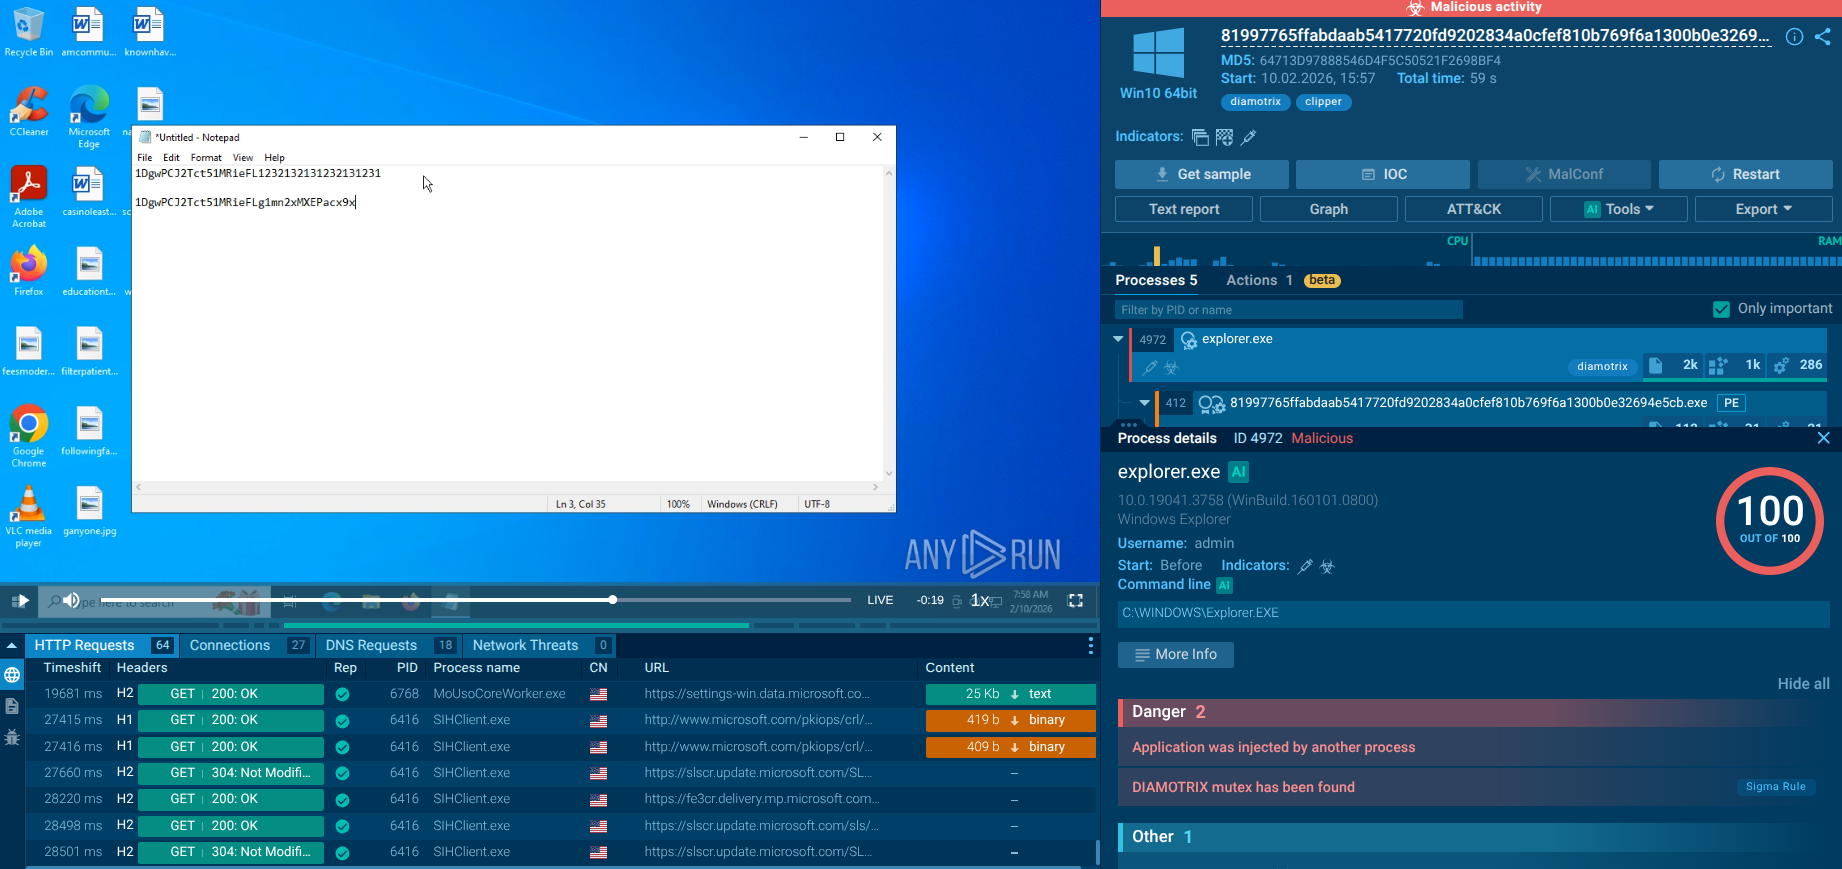
Diamotrix is a stealthy cryptocurrency clipper malware that silently monitors the Windows clipboard, waiting for the moment a user copies a digital wallet address. Diamotrix replaces it with an attacker-controlled wallet, invisibly redirecting any resulting transaction. Because blockchain transfers are irreversible, victims rarely discover the theft until the funds are long gone.
Read More
EvilProxy screenshot
EvilProxy
evilproxy
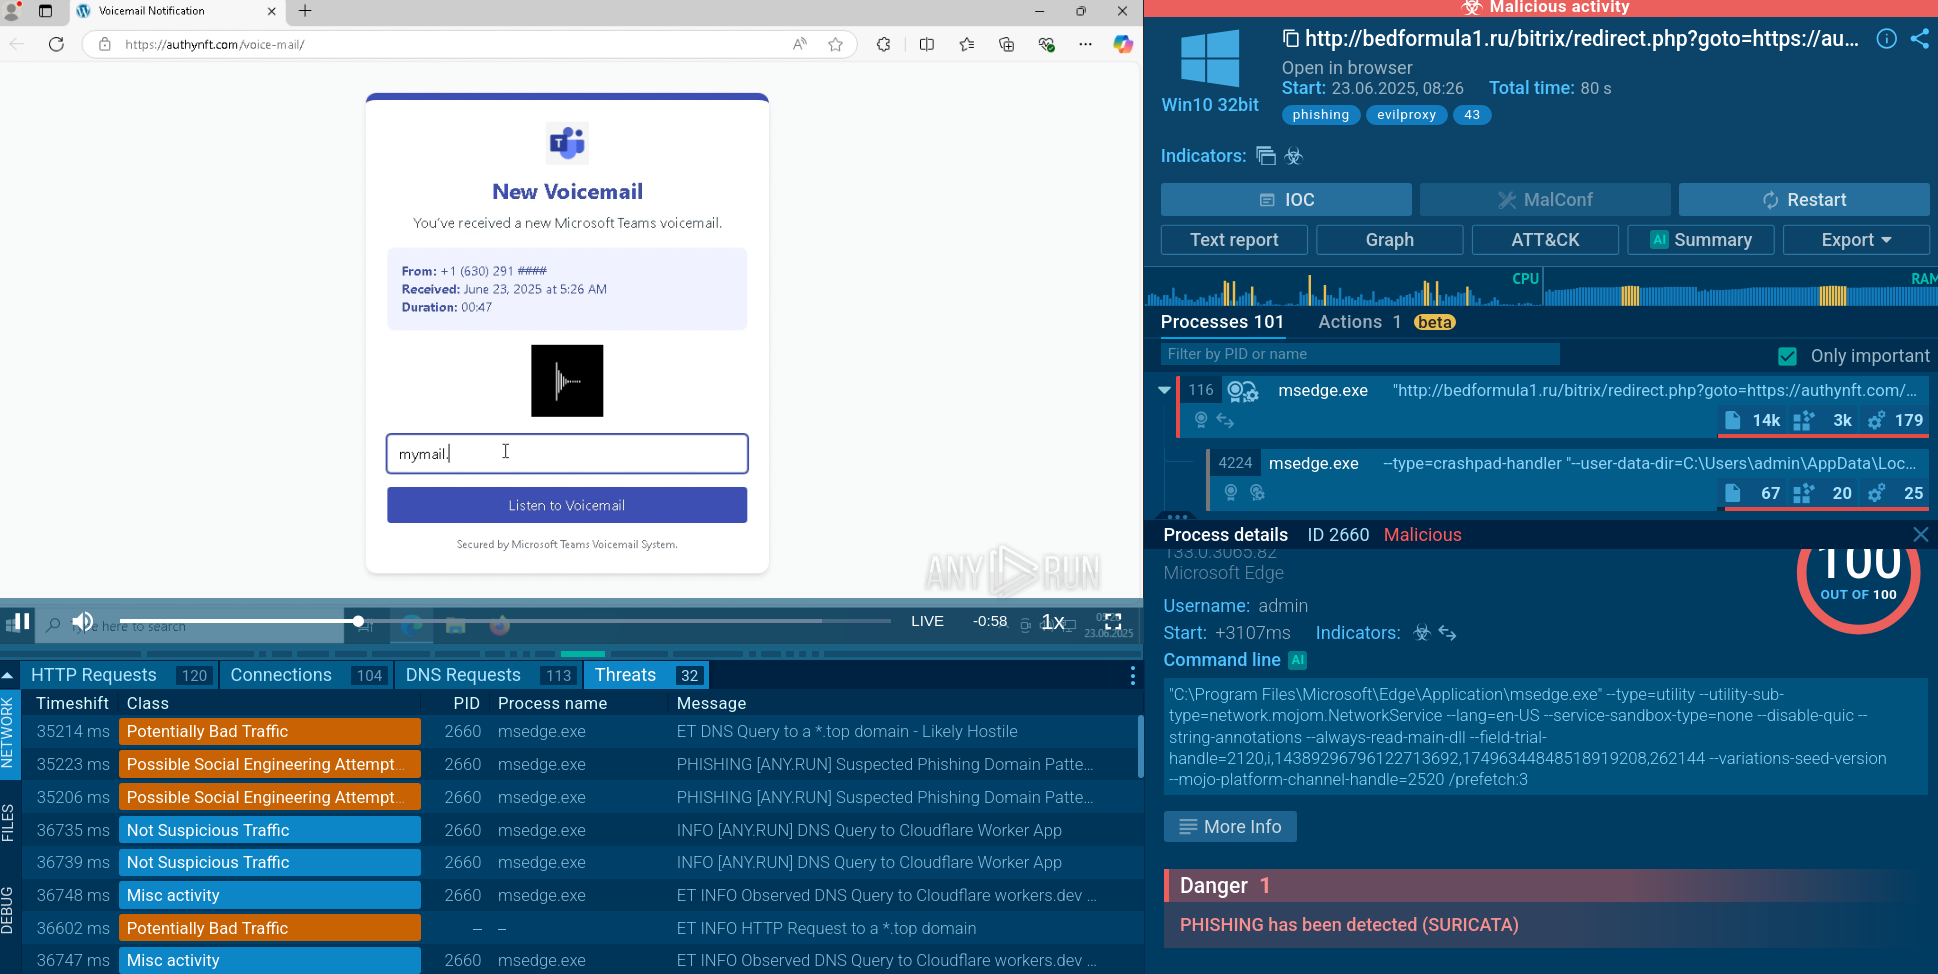
EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.
Read More
Sality screenshot
Sality
sality
Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.
Read More