Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Cerber

117
Global rank
83 infographic chevron month
Month rank
60 infographic chevron week
Week rank

Cerber is a Ransomware-as-a-Service (RaaS) that appeared in 2016, spread quickly and has been evolving since. It became well-known for its file encryption, offline capabilities, and sophisticated evasion techniques. It primarily targets enterprises, financial institutions, and government entities, encrypting their data and demanding ransom payments in Bitcoin. It also targets everyday users encrypting personal files (photos, documents) with the risk of their permanent loss.

Ransomware
Type
Unknown
Origin
1 February, 2016
First seen
2 October, 2026
Last seen

How to analyze Cerber with ANY.RUN

Type
Unknown
Origin
1 February, 2016
First seen
2 October, 2026
Last seen

IOCs

IP addresses
178.33.161.165
178.33.161.209
178.33.162.209
178.33.161.43
178.33.162.128
178.33.160.161
178.33.162.64
178.33.162.175
178.33.160.32
172.66.134.253
178.33.161.92
178.33.161.35
178.33.162.76
178.33.163.190
178.33.162.218
178.33.163.120
178.33.163.254
178.33.161.229
178.33.162.174
178.33.163.17
Hashes
e67834d1e8b38ec5864cfa101b140aeaba8f1900a6e269e6a94c90fcbfe56678
16342a7e5822495863aa38826f3586e595a75bfe4ba155e02819d981ff140118
9022017dfb351e00873ae3ee843e5ff1be5051df466877c56047b1ab19973eb2
e1e0dc4a1f29d962e495184a9256e836eb12fd41ebe539bb4d3a2ccccdec3132
a52cecb7b91c9e75377f9c3ac828985c3e1aa7f933afbe46e78aca5efb1f04fc
c57ee8520ec8b8268f5b05aaaf84f38ee48020e7cf8f2c2f02aaf7658381b3fa
5c8553f709ae168d2e6003524a723e951176d8a52e206846a0cb99d8be9d821d
a15a246c2903de416070c65c18b19150de6841dd98f137694c99b1f3047cadc3
1edfa04ddeefb9959b7511b92fab7dea45034aa18b9588e9d2a4b25b199d06dc
8f3e3a5614911f85a3884d0e89be0bc2756d2c8e53181a44022453d7057569b5
39bbb25595bda62d17c32319ac77f83ceece9509531ff19a4800594d480bbc80
2fb0f0d2c695f5966f3203fd19da82f075f7116e9d9690b23fb89d92c2919c1a
0380e57d016569e2a1e2947db23e08328d637be7c19141f8c3c33a3e782c70de
301d4ed75d9eef10adc038ba16f14435aeb4add28f102f42c85ae63d08a27532
48e261fbc7729725220986f601bd9e8889bdd1f6843f8267a579d5f50842df5d
61ec0d17bf22e5c8a76a1ae76c5dcfac43e2059081a07768c8aefc49097f9738
c00926389111fc86c8ff61d54ff6593ff92bc68d65979407f0d4857736b1cdbe
b5b38ad833a61a545c9fff7154783f37936d9a06d3bb190e101a469550c821ae
a96bd1bef3970701e8fe94be4b3ddb64a24d3690660c4fa8f20be8b4df2fd0d8
4d540754d5aef29795a79a62fae691214f2639b751c78e7b6d9f096a43af0085
Domains
activation-v2.sls.microsoft.com
self.events.data.microsoft.com
crl.microsoft.com
slscr.update.microsoft.com
fe3cr.delivery.mp.microsoft.com
www.microsoft.com
ecs.office.com
settings-win.data.microsoft.com
c.pki.goog
btc.blockr.io
client.wns.windows.com
api.blockcypher.com
ocsp.digicert.com
google.com
bitaps.com
go.microsoft.com
chain.so
login.live.com
nexusrules.officeapps.live.com
xpcx6erilkjced3j.1n5mod.top
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://api.blockcypher.com/v1/btc/main/addrs/17gd1msp5fnmcemf1mittnssys7w7aqyct?_=1790929910649
https://bitaps.com/api/address/transactions/17gd1msp5fnmcemf1mittnssys7w7aqyct/0/sent/all?_=1790929910981
https://chain.so/api/v2/address/btc/17gd1msp5fnmcemf1mittnssys7w7aqyct?_=1790929911181
http://c.pki.goog/we1/bcj6txpewec.crl
http://c.pki.goog/we1/fjedml2peto.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1128
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2922
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10390
comments 0

What is Cerber malware?

Cerber is a Ransomware-as-a-service that does not require an attacker to be a skilled hacker to deploy it. Since its debut in 2016, it has been frequently updated to bypass signature-based detections.

It mostly arrives at the target network via phishing emails with malicious attachments (zipped .DOT files, Windows Script Files [WSF], or self-extracting archives). Some campaigns include password-protected attachments with the password provided in the email to bypass basic email filters.

Once inside a network, Cerber typically waits for an opportune moment (e.g., system reboot or user idle time) to execute, increasing its chances of going unnoticed initially. Then the malware scans local and network drives for specific file types (documents, databases, media). It encrypts the found files using AES-256 and RSA-2048 encryption.
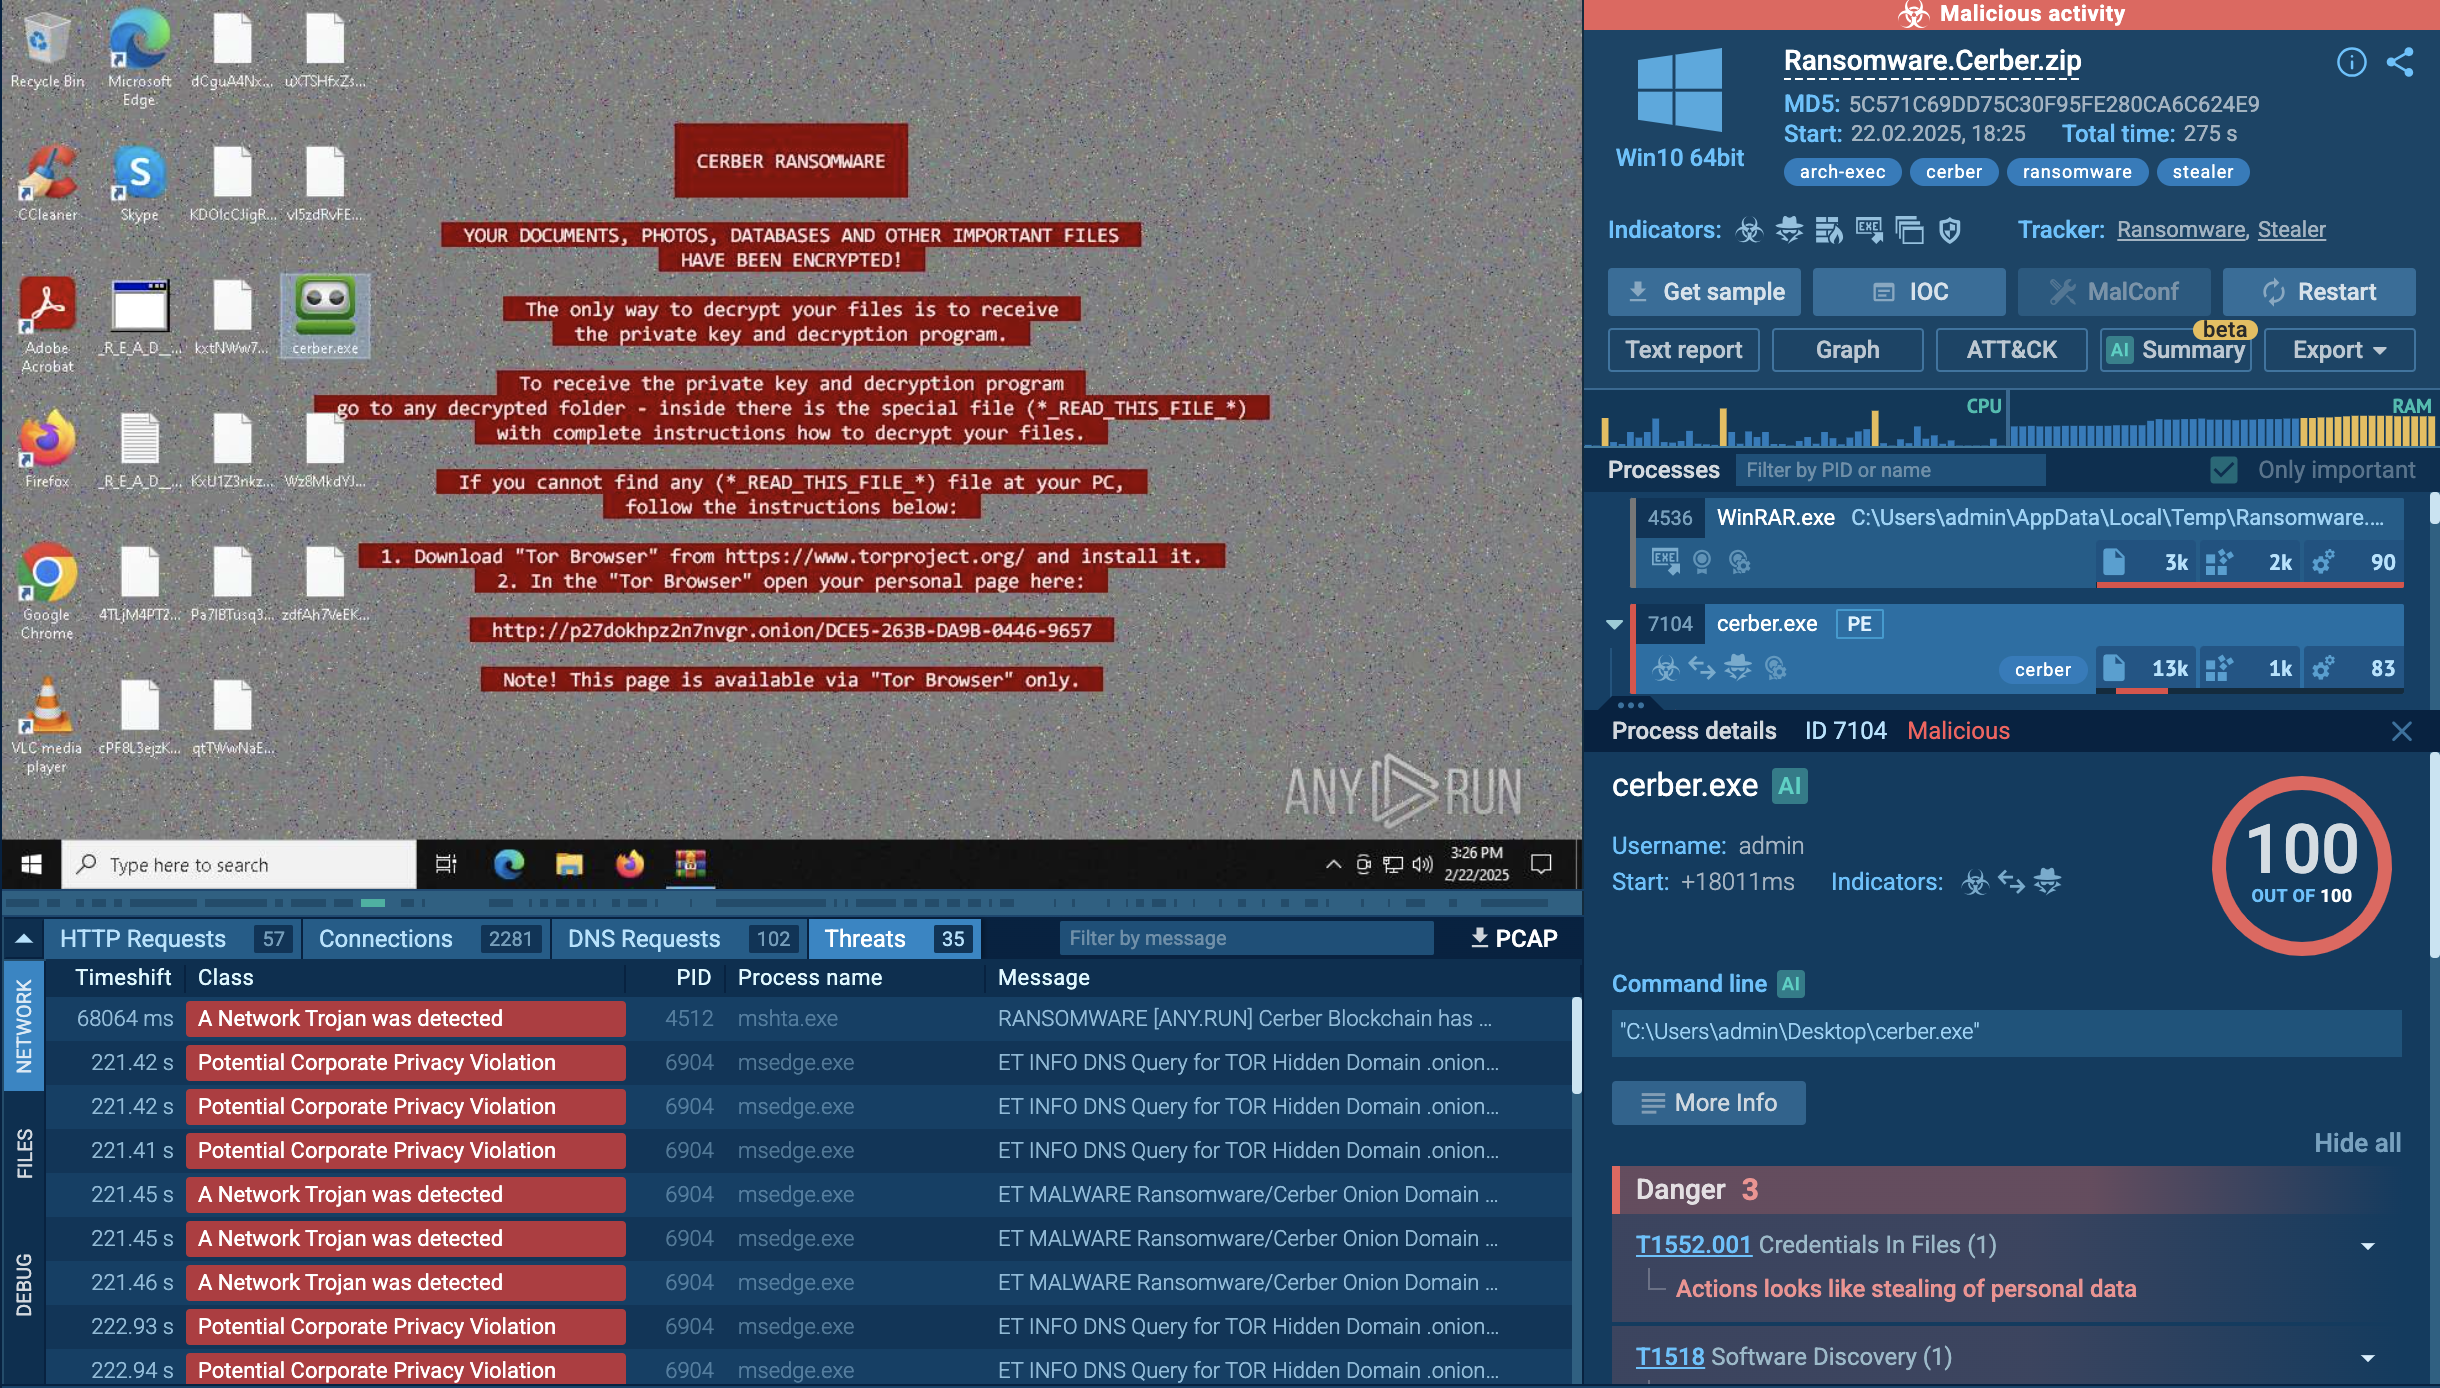
Cerber ransomware analysis in the ANY.RUN Sandbox Analysis of Cerber Ransomware in the ANY.RUN sandbox

It deletes shadow copies of the decrypted files and disables recovery options; after the operations are finished, Cerber generates a ransom note and deletes its executable to minimize forensic evidence.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Cerber’s technical details

Cerber is equipped with advanced capabilities as it:

  • Creates scheduled tasks and registry modifications to ensure persistence.
  • Drops multiple copies of itself in %AppData%, %Temp%, or %LocalAppData%.
  • Scans local and network drives for data files and encrypts them with AES-256 and RSA-2048 algorithms.
  • Drops a ransom note (README.hta) in affected folders with instructions to pay in Bitcoin via a Tor-based payment portal. Some variants use voice-based ransom notes, playing an audio message demanding payment.
  • Uses PowerShell scripts and scheduled tasks to execute itself remotely.
  • Attempts to spread via SMB shares, infecting additional network points.
  • Cerber employs a number of advanced evasion tactics: code obfuscation, sandbox detection, dynamic domain generation, fileless execution (some strains use PowerShell scripts to execute directly in memory). It can encrypt files without an internet connection, preventing detection via network traffic analysis.
  • Cerber’s network traffic and code are encrypted, making it harder to intercept or analyze. Macroses in phishing attachments often include junk code to confuse detection tools.
  • For persistence, Cerber may establish itself in the system registry or running processes to ensure it reactivates after reboots.

Execution process of Cerber Ransomware

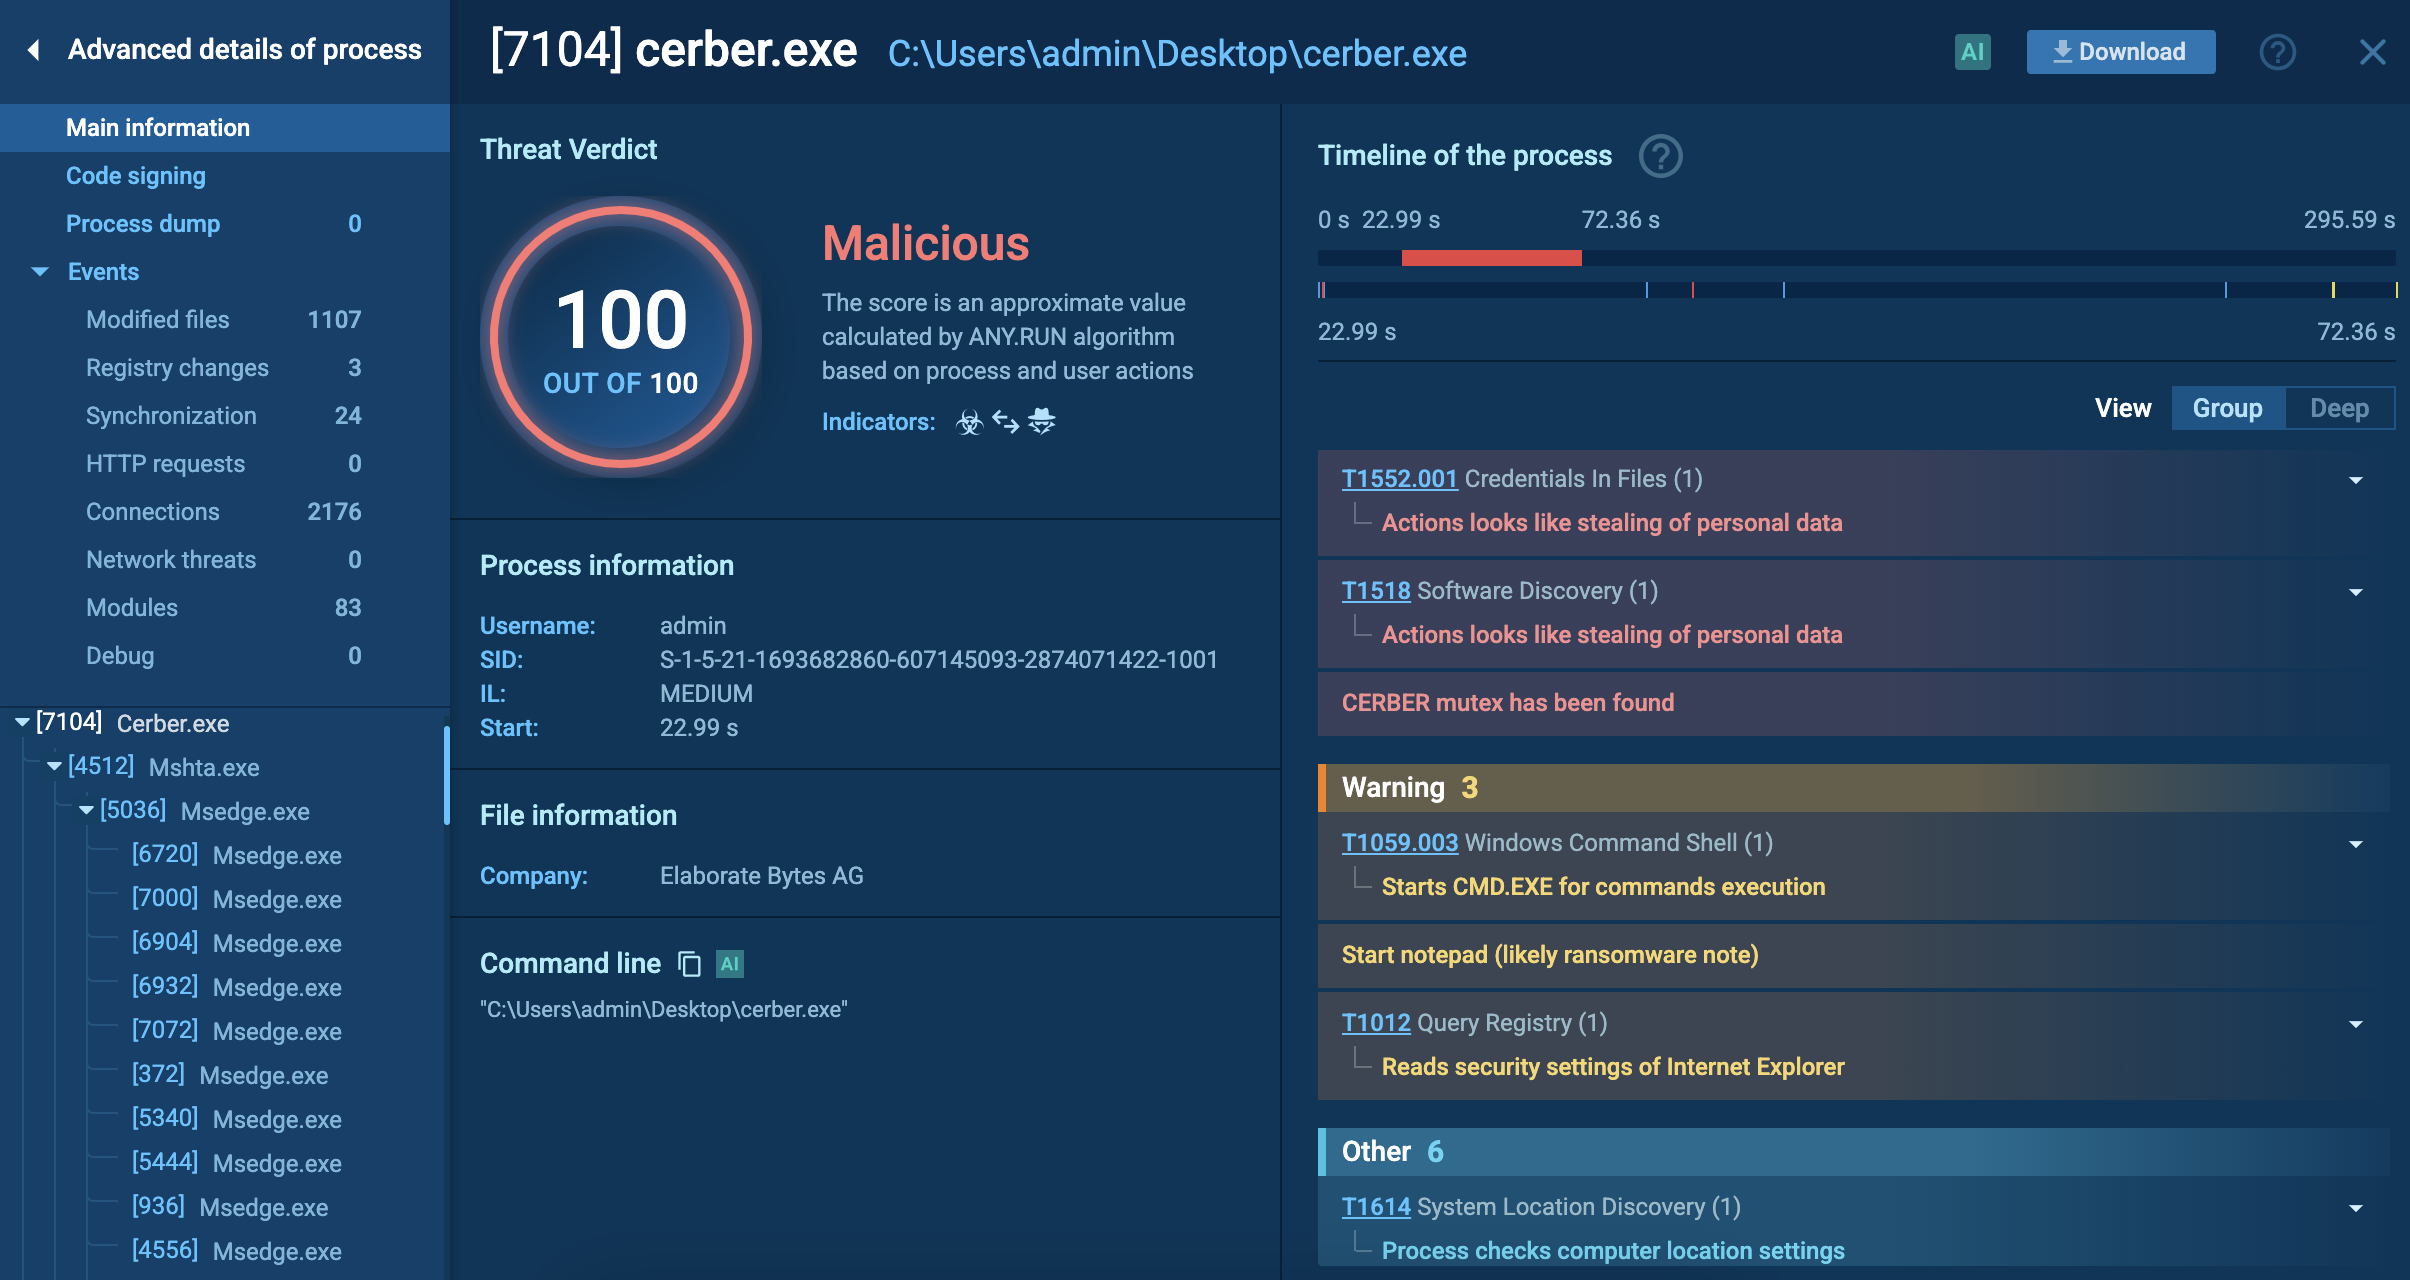
Let's use ANY.RUN's Interactive Sandbox to analyze a sample of the Cerber Ransomware to see how it operates.

Cerber ransomware uses a multi-stage execution chain, often starting with distribution via phishing emails. These emails typically include malicious attachments—either zipped Windows Script Files (WSF) or Microsoft Office files (.DOC or .DOCX). The WSF file directly installs Cerber, while the Office documents prompt users to enable macros, which then download and install the malware. Cerber has also been observed exploiting known vulnerabilities to gain initial access.
View sandbox analysis

Cerber ransomware analysis in ANY.RUN Process analysis of Cerber ransomware in ANY.RUN's Interactive Sandbox

Once executed, Cerber may check for specific mutexes to avoid reinfecting the same machine. In this case, the mutex is SHELL.{9C578142-9AC8-5286-EEAE-C741EB3192B8}, and the ransomware also created several additional mutexes. It checks the system’s country location and terminates if it detects an ex-USSR region. To evade detection, Cerber can configure Windows Firewall rules to block outbound traffic from security tools. Some versions add a time delay to the attack chain to evade sandbox analysis.

Cerber often reboots the system into Safe Mode with Networking, then back to normal mode before initiating the encryption process. It uses AES-256 and RSA to encrypt files, appends a custom extension, and renames files with randomly generated strings. In this analysis, the extension used was “.ae90.” Cerber stores ransom instructions locally, can change the desktop wallpaper, and launches a ransom note in HTA format using mshta.exe. Finally, it deletes its own file from the infected system to conceal its presence.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Gathering threat intelligence on Cerber malware

Countering Cerber demands proactive threat hunting and protective measures. Leverage threat intelligence to track Cerber-related indicators of compromise like C2 domains & IPs, hashes of known Cerber variants, Tor-based payment portals used by attackers (e.g., port 6893 with specific packet structures like Machine GUID hashes).
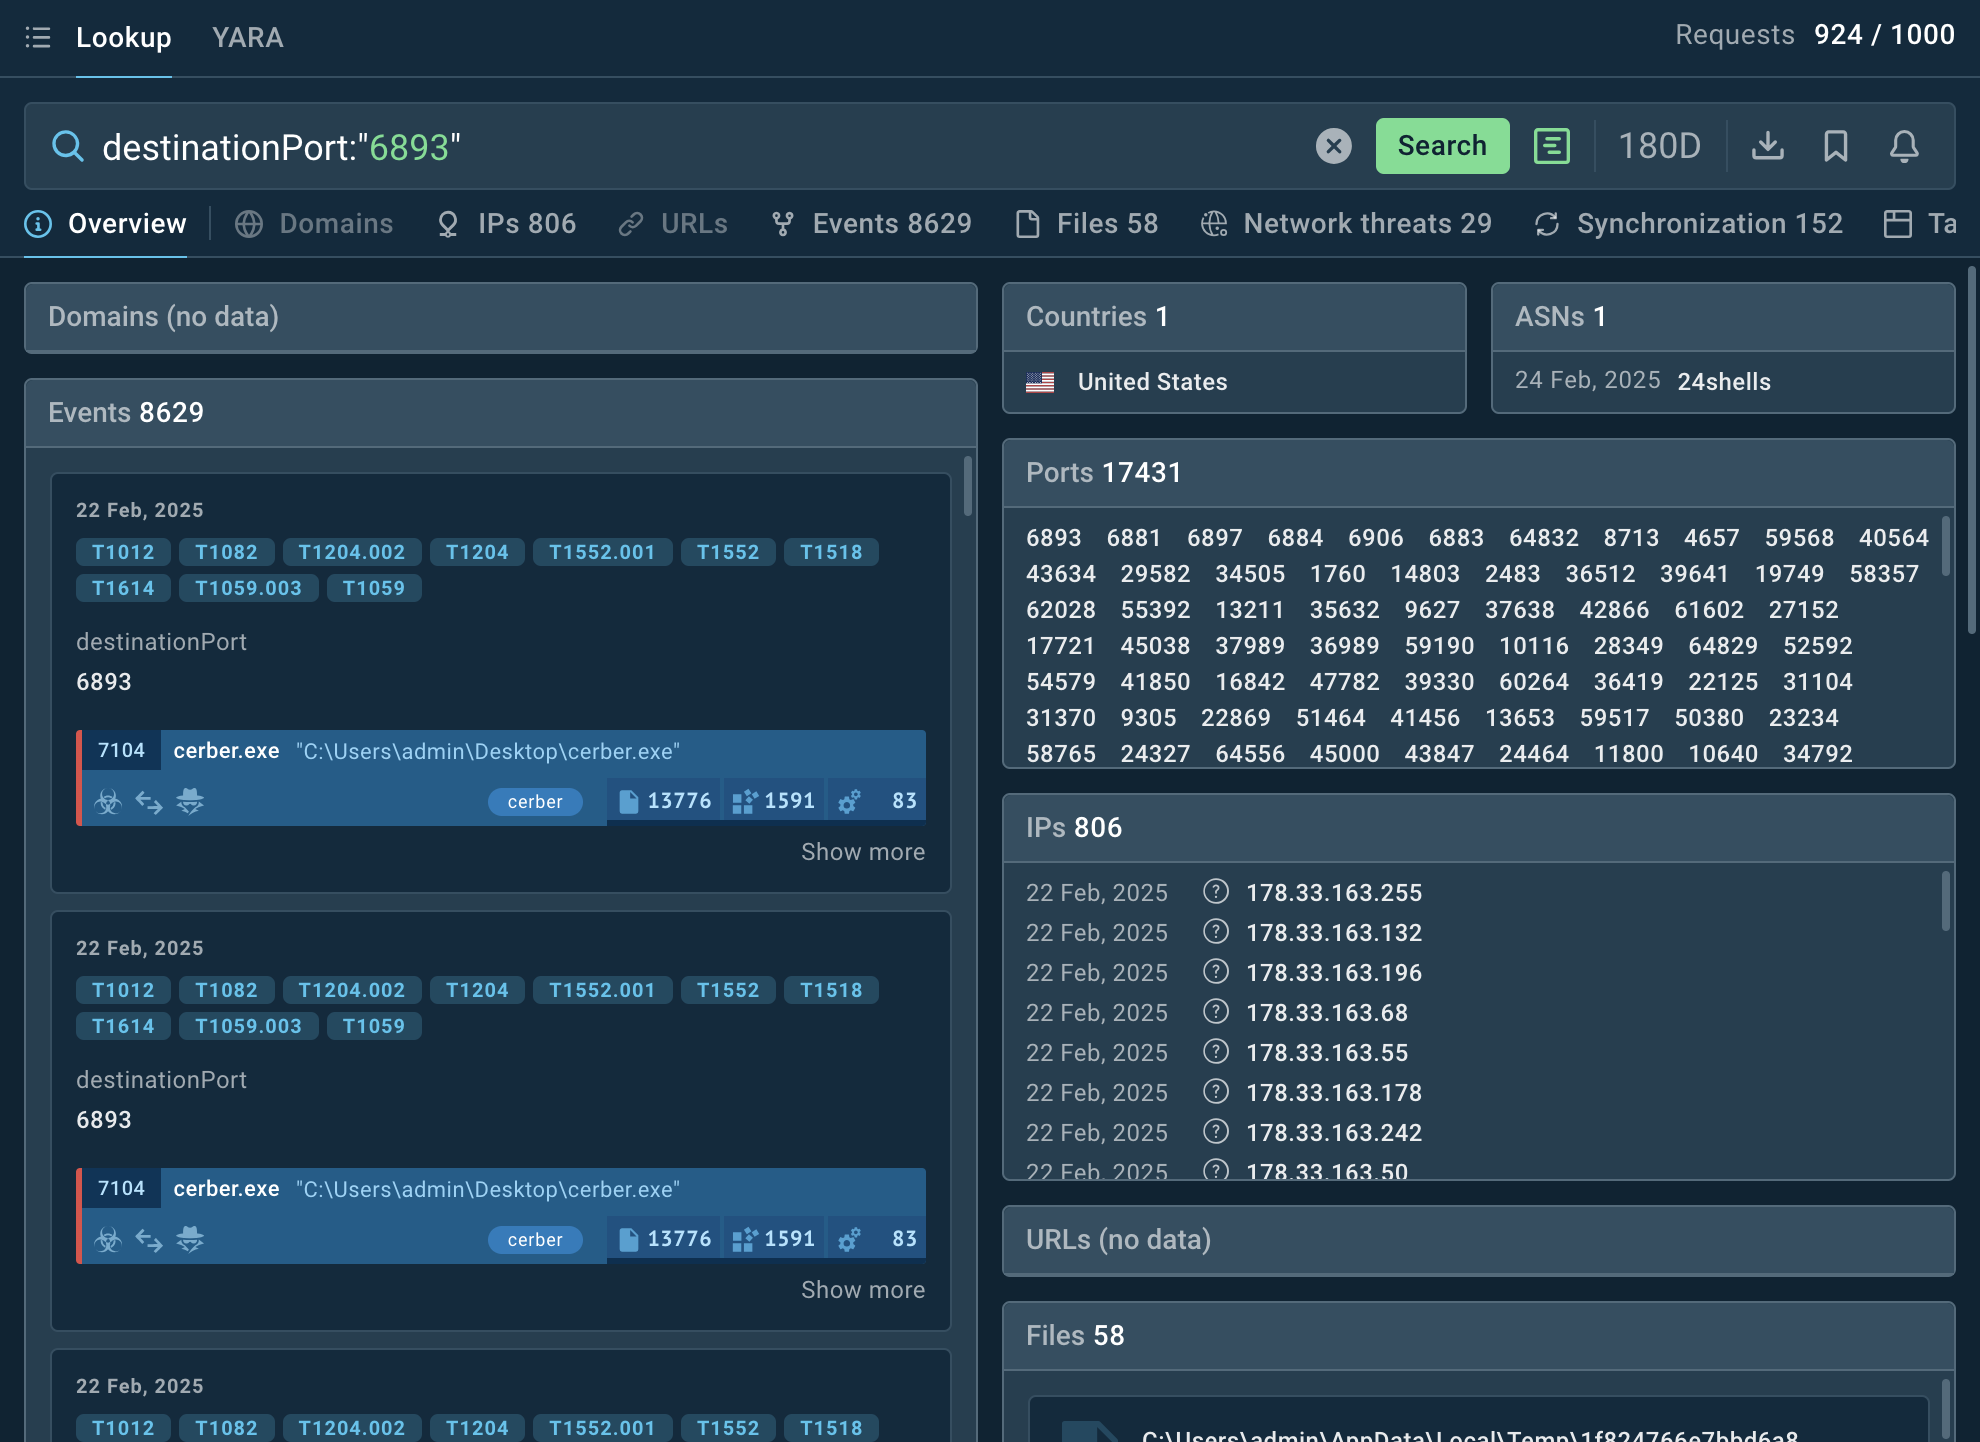
Cerber ransomware results in ANY.RUN TI Lookup TI Lookup helps users collect fresh intel on Cerber Ransomware attacks

Threat Intelligence Lookup by ANY.RUN delivers fresh contextual data on IOCs and provides a selection of the malware’s samples in action detonated in the Interactive Sandbox. Learn more about TI Lookup.

TI Lookup search by a port typically engaged by Cerber gives a number of IOCs for further research: associated URLs, files, mutexes, etc.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Distribution methods of Cerber Ransomware

  • The main method is phishing emails with malicious attachments. Fake invoices, job offers, or security alerts trick victims into downloading malicious Word or Excel files containing macros that drop Cerber.
  • Also used: malvertising and drive-by downloads, compromised websites and exploit kits targeting browser and software vulnerabilities.
  • Cerber is distributed via TrickBot and Dridex—malware families that serve as initial access brokers for ransomware operators.
  • Adversaries can brute-force RDP credentials to gain remote access, disable security tools, and manually deploy Cerber inside corporate networks.
  • Cerber as an RaaS is distributed by various cybercriminals who customize campaigns, making its delivery methods and sender addresses highly variable.
  • Cerber can spread laterally across a network, infecting shared drives and removable media.

Conclusion

Cerber stands out as a highly adaptive ransomware threat, blending traditional infection vectors with cutting-edge evasion techniques. Its danger lies in its ability to target both individuals and organizations, steal data, and disrupt operations while evading detection. By combining robust endpoint security, network monitoring, and real-time threat intelligence, defenders can detect and neutralize Cerber effectively.
Sign up for a free ANY.RUN account to access malware analysis and threat intelligence tools for your company

HAVE A LOOK AT

XRed screenshot
XRed
xred
XRed operates as a stealthy backdoor, enabling cybercriminals to gain unauthorized remote access to infected systems. XRed has gained particular notoriety for its distribution through trojanized legitimate software and hardware drivers, making it exceptionally dangerous due to its ability to masquerade as trusted applications.
Read More
Phorpiex screenshot
Phorpiex
phorpiex
Phorpiex is a malicious software that has been a significant threat in the cybersecurity landscape since 2016. It is a modular malware known for its ability to maintain an extensive botnet. Unlike other botnets, Phorpiex does not concentrate on DDoS attacks. Instead, it has been involved in numerous large-scale spam email campaigns and the distribution of other malicious payloads, such as LockBit.
Read More
Sality screenshot
Sality
sality
Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.
Read More
Stealc screenshot
Stealc
stealc
Stealc is a stealer malware that targets victims’ sensitive data, which it exfiltrates from browsers, messaging apps, and other software. The malware is equipped with advanced features, including fingerprinting, control panel, evasion mechanisms, string obfuscation, etc. Stealc establishes persistence and communicates with its C2 server through HTTP POST requests.
Read More
EvilProxy screenshot
EvilProxy
evilproxy
EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.
Read More
Diamotrix screenshot
Diamotrix
diamotrix
Diamotrix is a stealthy cryptocurrency clipper malware that silently monitors the Windows clipboard, waiting for the moment a user copies a digital wallet address. Diamotrix replaces it with an attacker-controlled wallet, invisibly redirecting any resulting transaction. Because blockchain transfers are irreversible, victims rarely discover the theft until the funds are long gone.
Read More