Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

DarkGate

138
Global rank
137 infographic chevron month
Month rank
153 infographic chevron week
Week rank

DarkGate is a loader, which possesses extensive functionality, ranging from keylogging to crypto mining. Written in Delphi, this malware is known for the use of AutoIT scripts in its infection process. Thanks to this malicious software’s versatile architecture, it is widely used by established threat actors.

Loader
Type
ex-USSR
Origin
15 November, 2018
First seen
29 September, 2026
Last seen
Also known as
Meh

How to analyze DarkGate with ANY.RUN

Type
ex-USSR
Origin
15 November, 2018
First seen
29 September, 2026
Last seen

IOCs

IP addresses
48.209.138.189
80.71.224.146
23.59.18.102
74.178.76.128
172.211.123.248
48.209.133.15
2.16.241.9
48.192.1.64
135.232.92.97
23.216.77.36
2.23.246.9
74.178.76.54
23.11.40.157
23.216.77.21
20.190.160.3
135.232.92.137
48.209.138.168
88.221.169.152
48.211.4.16
135.233.45.223
Hashes
9a1b4e8fb16d69690e52748aac601ace68dc9c1186e2d886fa26220cb8486be1
035db4bb1698e67eed83c217b196e342dc8ab8bb6ace3c2960f413a2bfab3158
8a93eabf56949eb69dc5c81a39645fec215d967d126751a8bb72e2f90a3c41c7
65d01c920b9b12c79cc8cea5f652e17ba7e68c1952058a9b61d388ea29a71a90
23735dd3dc736971f4c90a9a1d105869f7b08c7d4ba625059dc53377601cb296
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
9bc6274de69aff2e702288e329967515e230e455e48701b6b424c13b0f3a8149
744d6de023fd74f0306d846e0845388124857740943f8325397ca4a1cfa06879
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
1eac959455dfebde1694d4ec21649305d42f8ec4b6e039702e126c19b36ad3f5
c292b164b9305469cc48e01b50509abbf5dd5ddb8e3ea4864ab190292667b88b
39c8c95325a5a1cb68805af3f1aa181a6120fe0732276f43dc309bbe8332c0b1
aba462ebeca47251e2b275b79d612061fa0117919a3f0b510acbeb2afd82a33a
7672d33c9dec7ebe6fb8d98048183cafaba69b062e33aa3da0de33d4a8439ec7
3127d190df15063b8e70ece59531292ff654321eb81893901991c9d91965853f
58aba9786c10db64ad5d37df742671d95b758b6928335e1e84dc152a3c9fc5fe
c01f860b36a077977ad7b6c7ebef93e1c9ab8de32a2a7240e9f9352de76cbedc
dd9207fe0a6b1a2c1ea0cd97a98c0981ae145273fd21b7f156361ba080b422c2
e4992e79f8ad70782c9ee478268627b3c917c35582b991d645b1bce826e42d22
Domains
www.microsoft.com
activation-v2.sls.microsoft.com
slscr.update.microsoft.com
crl.microsoft.com
settings-win.data.microsoft.com
sanibroadbandcommunicton.duckdns.org
fe3cr.delivery.mp.microsoft.com
google.com
client.wns.windows.com
nexusrules.officeapps.live.com
ecs.office.com
watson.events.data.microsoft.com
ocsp.digicert.com
self.events.data.microsoft.com
login.live.com
go.microsoft.com
config.edge.skype.com
msedge.b.tlu.dl.delivery.mp.microsoft.com
copilot.microsoft.com
edge.microsoft.com
URLs
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.1.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://watson.events.data.microsoft.com/telemetry.request
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is DarkGate malware?

DarkGate is a loader malware family that was first detected in 2018 and has since been continuously undergoing serious development, significantly expanding its functionality. This malicious software is notable for the use of various evasion techniques, such as process hollowing.

It is distributed based on the malware-as-a-service (MaaS) model by its developer who goes by the name RastaFarEye on popular Darkweb forums. According to the creator of the malware, they have been developing it since 2017.

As of the beginning of 2024, RastaFarEye offers only 30 seats per month to those willing to purchase a subscription, which is priced at $15,000/mo. The malware has been observed to be used by known threat actors in different attacks involving data theft and extortion. Operators get to control the malware via a special panel.

Expose malicious activities and get IOCs with ANY.RUN sandbox

  • Analyze malware in Windows 7, 10, and 11 VMs
  • Interact with files and links, just like on your own computer
  • Work in a private team space with your colleagues
Request 14-day free trial

Technical details of the DarkGate malicious software

DarkGate is a multi-functional malware, meaning that it can be employed for a range of malicious purposes. Here is an overview of its key capabilities:

  • DarkGate can execute malware to memory, making it more difficult to detect and remove.
  • It can remotely control the victim's computer, giving the attacker complete access to the victim's data and system, as well as log its keystrokes and take screenshots.
  • DarkGate can browse and manage files on the victim's computer.
  • It can steal the victim's passwords, credit card numbers, cookies, history, and other sensitive information from their web browsers.
  • The malware can gain administrator privileges on the victim's computer, giving the attacker even more control over the system.
  • DarkGate can steal the victim's Discord login token, which can be used to log in to their account and steal their data.
  • It is also equipped with a cryptominer, allowing operators to mine various cryptocurrencies using the victim's computer's CPU and/or GPU.

The DarkGate virus achieves persistence, making sure it stays on the computer even after a restart, in several ways. For instance, it can create a shortcut in the Startup folder or change a setting in the registry. Additionally, it employs Asynchronous Process Call injection.

In order to evade antivirus software, DarkGate has the functionality to check the presence of a list of popular security products on the system. It also has an anti-sandboxing capability, where it can detect a virtual machine environment and halt or adjust its execution.

All the communication with the command and control (C2) server is performed via HTTP and is obfuscated.

Execution process of DarkGate attacks

Despite having an anti-sandboxing capability, DarkGate can be easily analyzed in ANY.RUN. As a result, we can easily detect the malware and observe its activity by simply uploading its sample to the sandbox.
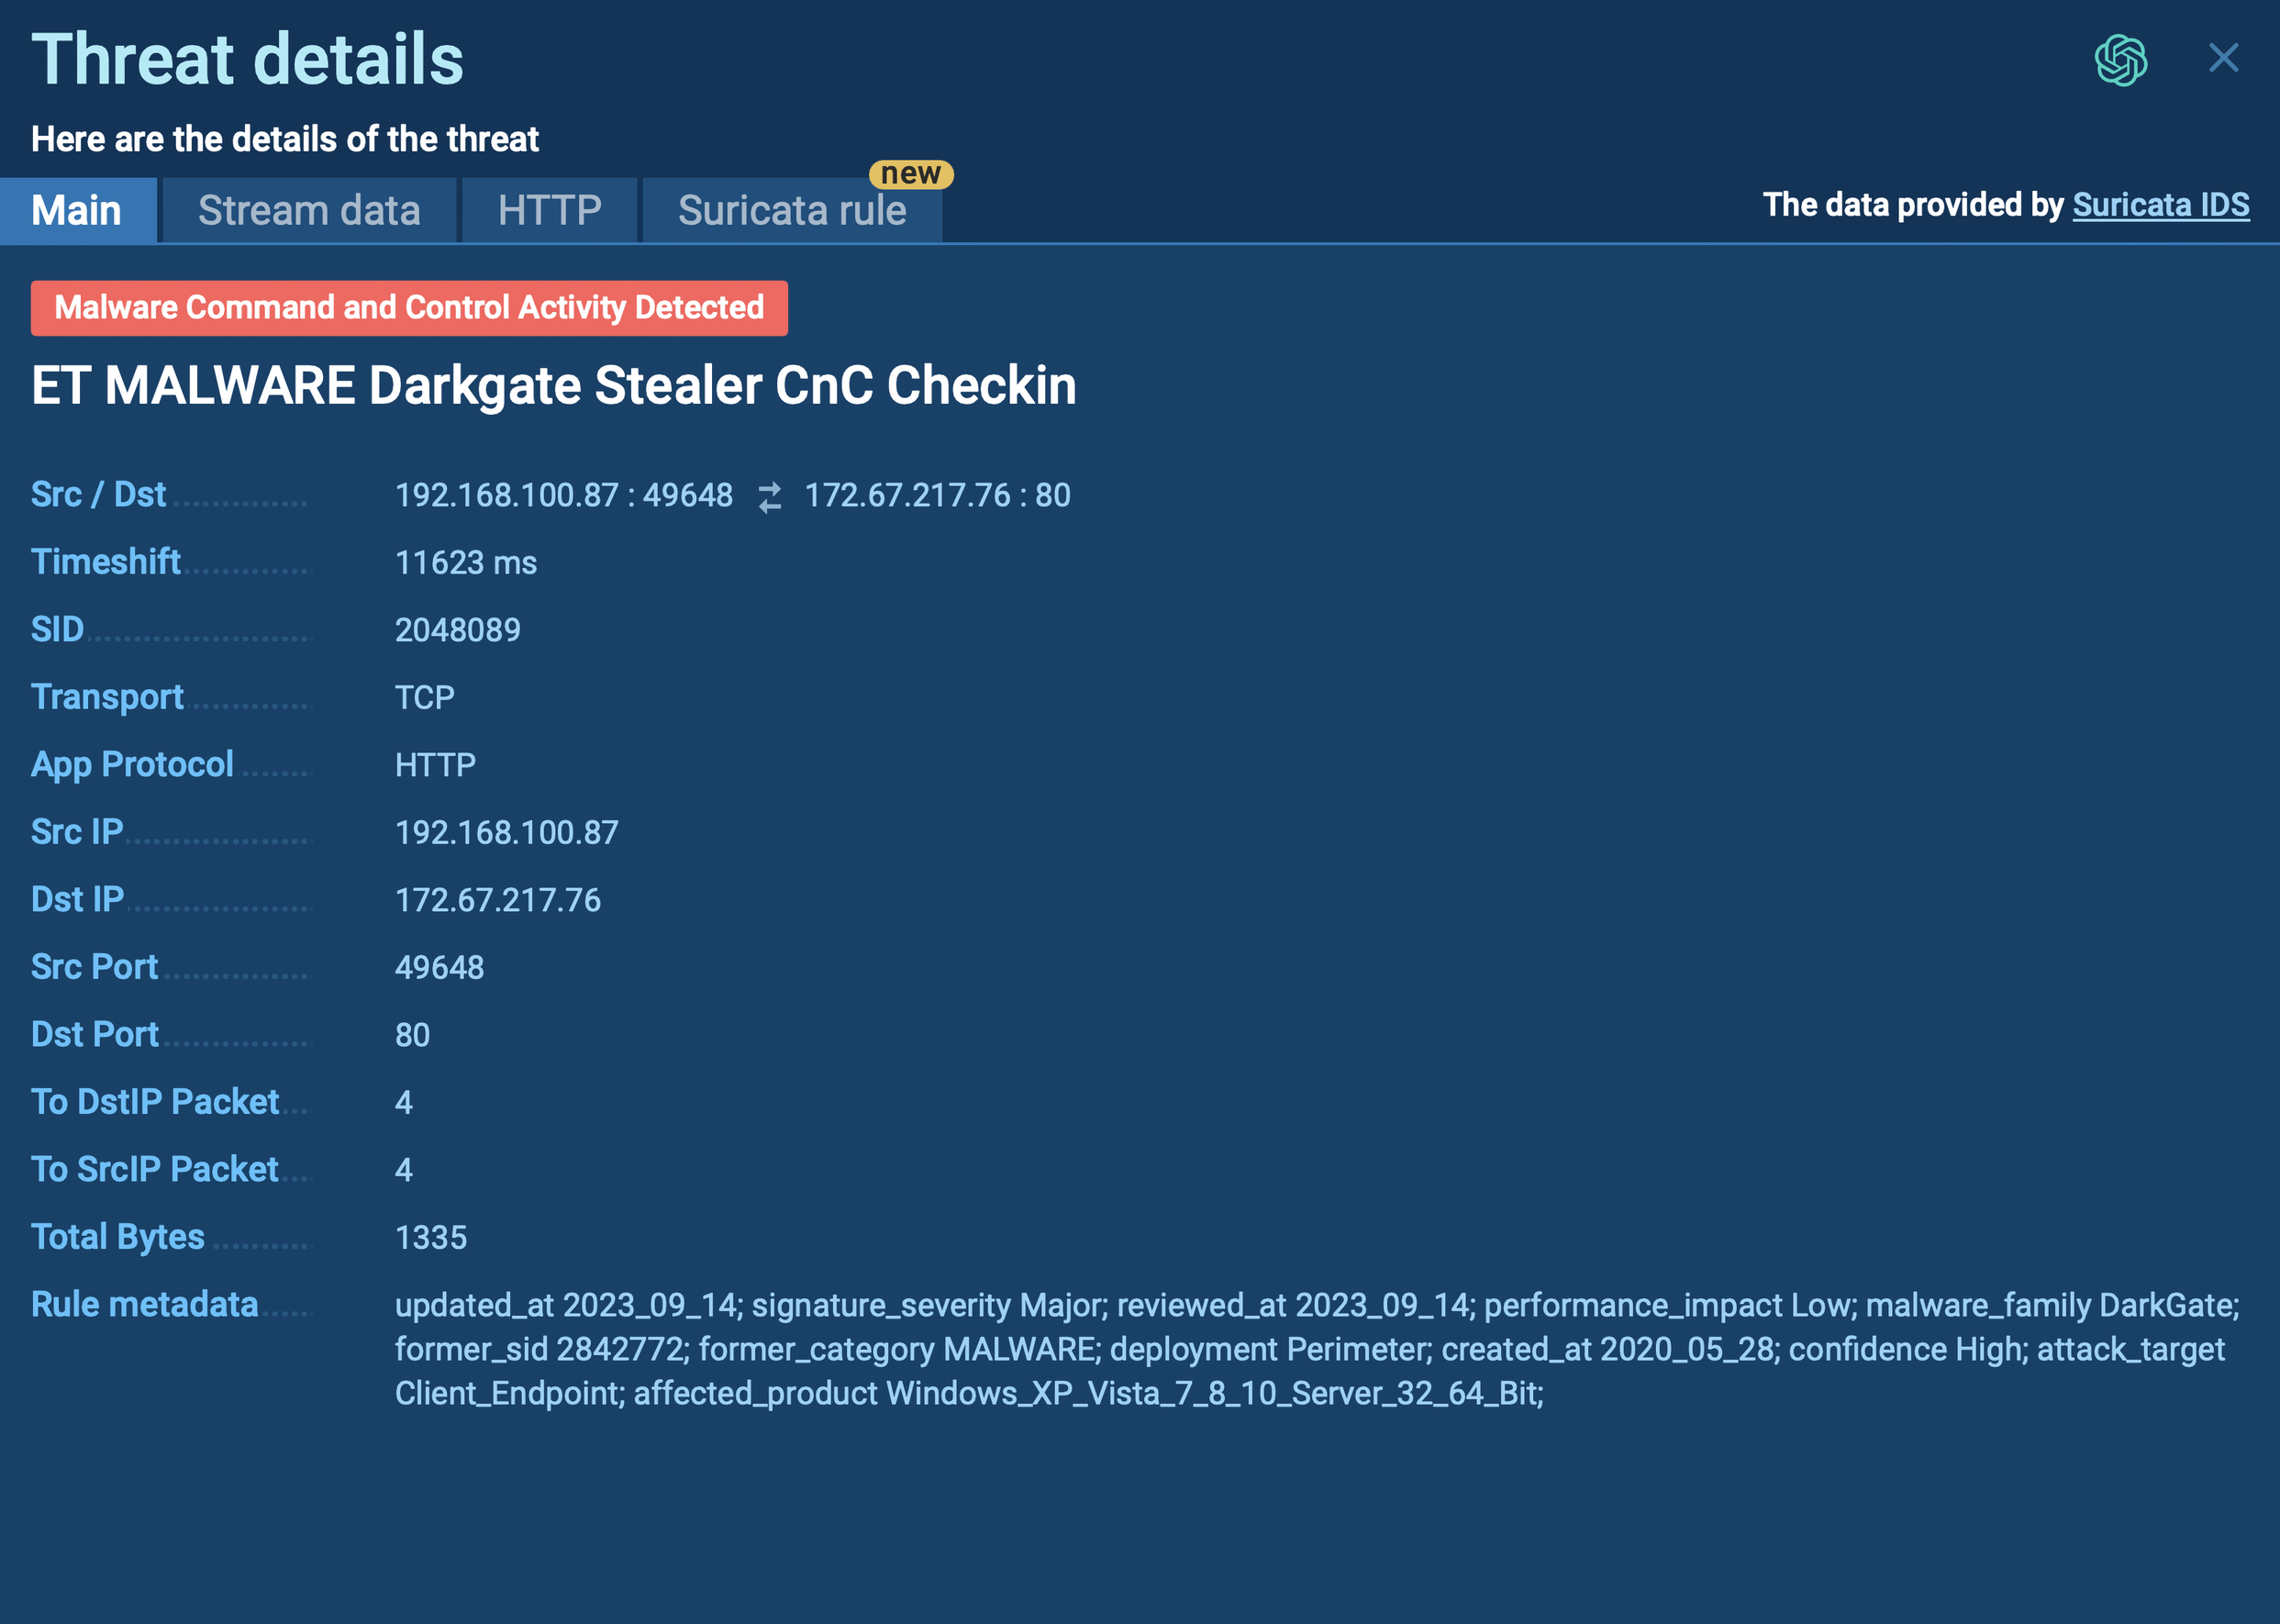
DarkGate threat details shown in ANY.RUN DarkGate`s threat details demonstrated in ANY.RUN

The execution chain of DarkGate may vary depending on the versions and other factors. In some instances, the entire execution chain is contained in a single file that facilitates all activities post-infection. Let's examine our sample.

DarkGate may perform process hollowing into certain processes within the infected operating system. This can include TabTip32, BraveUpdate, MicrosoftEdgeUpdate, ielowutil, or, in our case, GoogleUpdate. This malware often utilizes AutoIT scripts and files for injection and execution of shellcode and other malicious activities. The primary malicious activities are executed through the injected GoogleUpdate process. It adds itself to the startup directory, checks for the presence of antivirus software, connects to the command and control server (C2), downloads payloads, and more.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Gathering threat intelligence on Darkgate malware

To collect up-to-date intelligence on Darkgate, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Darkgate.
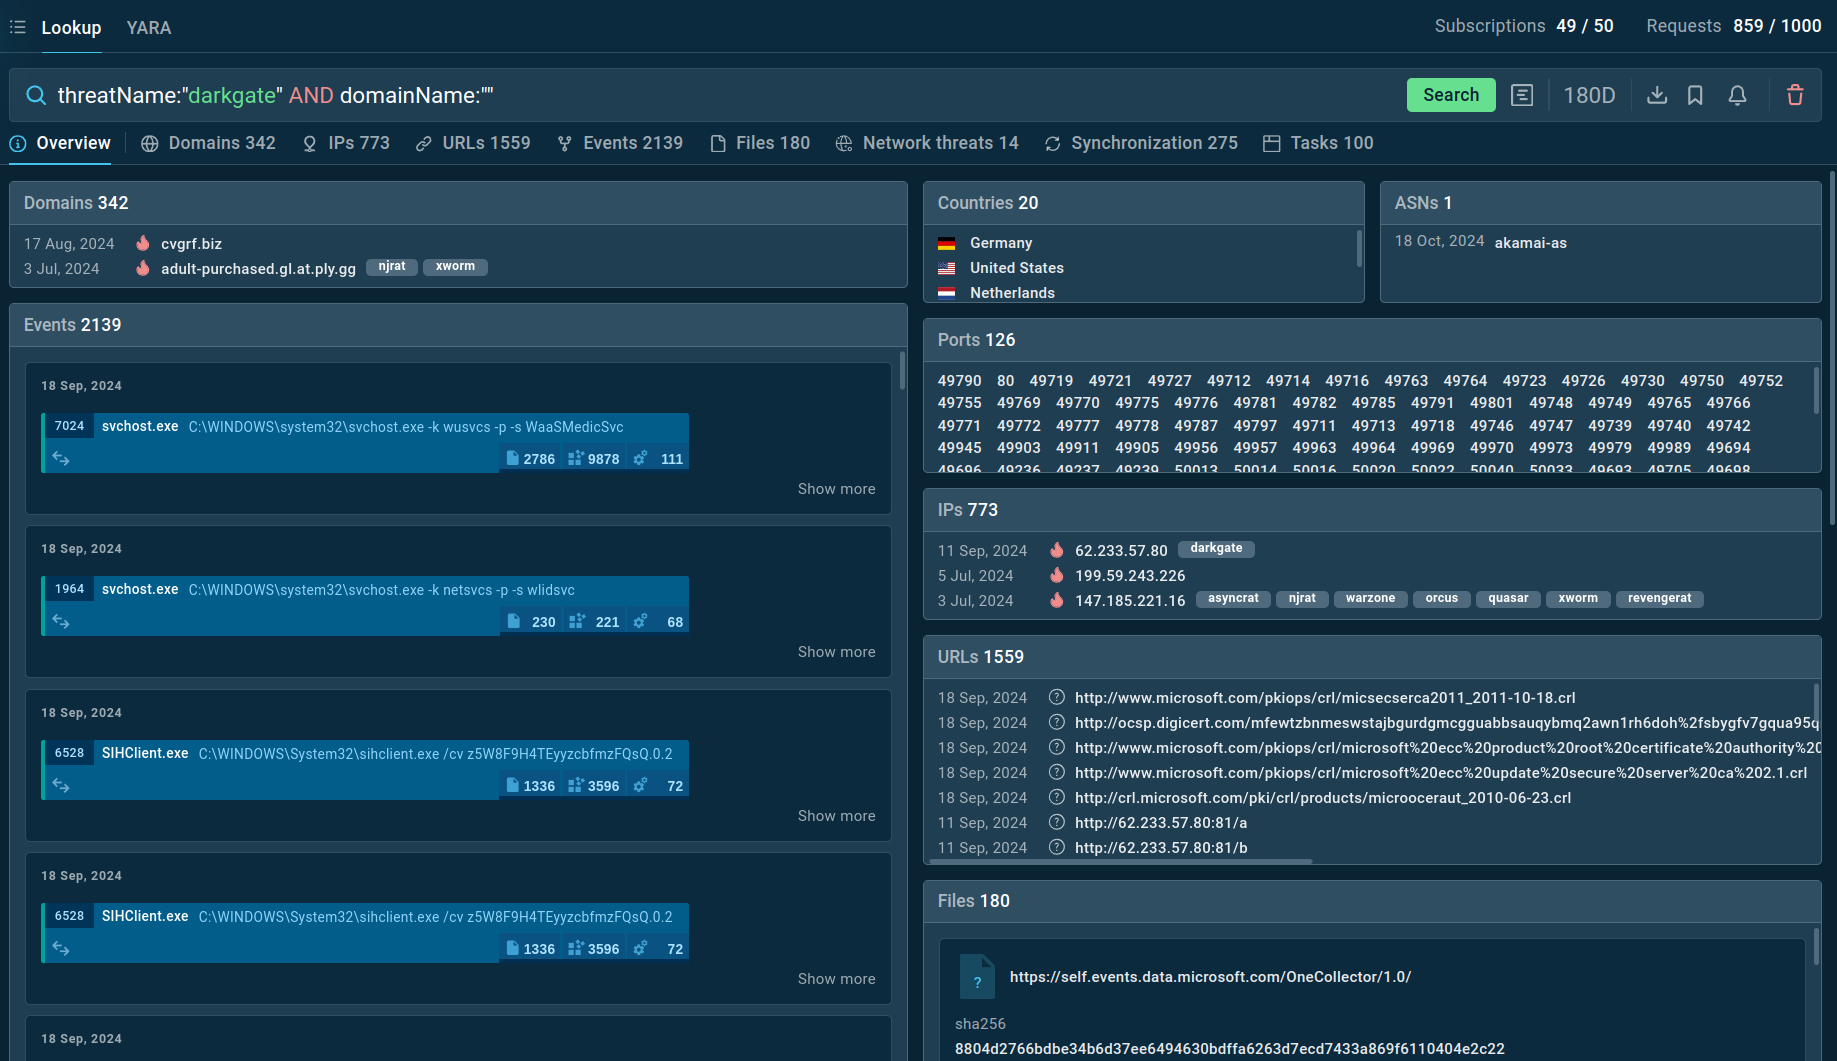
Darkgate ANY.RUN Search results for Darkgate in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"darkgate" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from DarkGate samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Distribution methods of the DarkGate malware

Like other common malware families, including Remcos and njRAT, DarkGate infiltrates systems through deceptive emails.

However, instead of directly embedding malware into an email attachment, DarkGate typically utilizes malicious links that direct users to compromised websites hosting MSI installer files. When unsuspecting users download and execute these infected MSIs, the DarkGate malware silently installs itself on their computers. Once embedded, DarkGate begins to steal sensitive information and perform other similar actions.

Conclusion

DarkGate is an extremely capable malware that is operated by infamous threat groups, which puts it on a list of major cybersecurity concerns. To ensure your organization has the capacity to avoid becoming another victim of the malware, you need to have access to up-to-date information on DarkGate.

Utilize the ANY.RUN sandbox to examine the latest samples of DarkGate and gather up-to-date insights into their behavior patterns. Uncover the TTPs employed by the malware and collect its indicators of compromise. Leverage ANY.RUN's interactive malware analysis approach to safely interact with the malware as if on your own device, extracting even more relevant information.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Mamba 2FA screenshot
Mamba 2FA
mamba
Mamba 2FA is an advanced phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) and target Microsoft 365 accounts. It focuses on intercepting authentication flows in real-time and enables threat actors to hijack user sessions and access sensitive systems even when additional security measures are in place.
Read More
Makop Ransomware screenshot
Makop is a Phobos-derived Ransomware-as-a-Service model that predominantly targets exposed and vulnerable RDP endpoints. Rather than executing as a standalone automated threat, human operators manually navigate the compromised network to escalate privileges, map assets, and disable active defense solutions before deploying the payload.
Read More
Black Basta screenshot
Black Basta
blackbasta
Black Basta is a ransomware-as-a-service operated by Storm-1811. It emerged in 2022 and uses double extortion tactics, encrypting data and stealing it for ransom. The malware often gains access through spear-phishing and uses tools like QakBot and Cobalt Strike. It's known for exploiting system vulnerabilities and using advanced obfuscation techniques.
Read More
Jigsaw screenshot
Jigsaw
jigsaw
The Jigsaw ransomware, initially detected in 2016, encrypts files on compromised systems and requires a ransom payment in Bitcoin. If the ransom is not paid, the malware starts deleting files, increasing the pressure on victims to comply. Its source code is publicly accessible, allowing various threat actors to customize and repurpose the malware for different objectives.
Read More
Lynx screenshot
Lynx
lynx
Lynx is a double extortion ransomware: attackers encrypt important and sensitive data and demand a ransom for decryption simultaneously threatening to publish or sell the data. Active since mid-2024. Among techniques are terminating processes and services, privilege escalation, deleting shadow copies. Distribution by phishing, malvertising, exploiting vulnerabilities.
Read More
BQTLock screenshot
BQTLock
bqtlock baqiyatlock
BQTLock is a ransomware-as-a-service (RaaS) malware family that emerged in 2025 and quickly gained attention due to its combination of file encryption, credential theft, and data exfiltration. BQTLock encrypts files using a hybrid AES-256 and RSA-4096 encryption scheme, demands payment in Monero cryptocurrency, and performs data theft and system reconnaissance.
Read More