Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Gafgyt

109
Global rank
79 infographic chevron month
Month rank
47 infographic chevron week
Week rank

Gafgyt, also known as BASHLITE, is a botnet affecting Internet of Things (IoT) devices and Linux-based systems. The malware aims to compromise and gain control of these devices, often by exploiting weak or default passwords, as well as known vulnerabilities. Gafgyt has been around since 2014 and has evolved into multiple variants, each with its own set of features and capabilities, including the ability to launch distributed denial of service (DDoS) attacks.

Botnet
Type
Unknown
Origin
1 September, 2014
First seen
5 October, 2026
Last seen
Also known as
BASHLITE
LizardStresser
Torlus

How to analyze Gafgyt with ANY.RUN

Type
Unknown
Origin
1 September, 2014
First seen
5 October, 2026
Last seen

IOCs

IP addresses
151.101.1.91
185.252.140.125
129.70.132.33
176.65.139.139
151.101.65.91
151.101.129.91
151.101.193.91
83.168.69.95
162.55.190.98
178.215.228.24
172.104.134.72
193.138.81.81
91.189.91.61
91.189.91.157
185.125.190.56
185.125.190.57
91.189.91.62
91.189.91.98
91.189.91.97
91.189.91.57
Hashes
803cff17b00020a2e4206e84ab2ca22eb06ab61351d97336d960ca90e4d31cea
5c15f8bfcc4d913e925f7504233f29b682820fcec3a3cdfc8225d19944ff4bf5
0313cef6ee5ccac16714f02e3ff9dfd5181c55419f96a6443d9812f0d37a8eaa
296734369e659cfd8682b01ab33e309099359873059fab72189f7ce93a2f9044
00499f1a9eee6704252b483a4172495396bec2c56cc78787da99a38dd2548e9a
547338c703a86c3eaaaaa83f40eb9e131ca7bce36f96e7415a5f3eb87b1f10a4
dba328d783d4c69df88a82e8b851172a697cbcc3fbd392447ea9dee9a188d98c
5279f80f139fcf962ac44abc4b79b67d14807c8f5a6d9ec8e9e3f7023532961d
f7a523cb4af925d39f70483e15164983dab3b51cbcadc7ba4dbc8590c3a171e5
4377e894b3e7956b74d467118164b7023e9b0f0f4c151e464d00991e30f924ac
f9120c06aad5aa4add1b646456199fd34b4fa72c6eb8ba4d37d85a59d7cac478
5d5e1b2d662740e455a5f45c6cd97dba06f6314b6ecb6f24cece7106c07a3f6d
4c15b7f94734569b348c760c1214a2f6dce3d9ae4c0b8ac23b0b8b1d31e63785
8f18903464b4b125d8281cb0ed9c9785155e704c178215ec8e423dd891199fbc
96bed7f389070781fe420b0367f75f4702a27e8d0b2d705c554c71c85874ccf6
2364f5ebe71bd534cdceaea8886bacc10288badd29ca283ef75f42311bfb42c4
6810ff810bf888ebb99ccf93e3a692a85d4762784487bc195ceb204187531575
228da7fadd8f85b13062addcb4aeb8ef960926346deb6c46898e9cf27034cf33
84b352b314d71d6887ef94b8094bbb4c6cbcb409e52ee748dca7583b8f75002a
a0e7e5b25346340da9e58ac4fe8691409f8dbc99d1e2aa3f496c3f9b10016d8c
Domains
2.debian.pool.ntp.org
google.com
9.100.168.192.in-addr.arpa
10.100.168.192.in-addr.arpa
8.100.168.192.in-addr.arpa
connectivity-check.ubuntu.com
3.100.168.192.in-addr.arpa
5.100.168.192.in-addr.arpa
6.100.168.192.in-addr.arpa
7.100.168.192.in-addr.arpa
cdn.fwupd.org
4.100.168.192.in-addr.arpa
www.bing.com
settings-win.data.microsoft.com
crl.microsoft.com
slscr.update.microsoft.com
edge.microsoft.com
ecs.office.com
update.googleapis.com
api.edgeoffer.microsoft.com
URLs
http://connectivity-check.ubuntu.com/
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:uvssy7vkclsznfpgrham5lsrni0e8kkyaazebj-gw1m&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
http://176.65.139.140/bins/i686
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d279%2526e%253d1
https://update.googleapis.com/service/update2/json?cup2key=14:hcs21xg-jkf887cnxifi02uo6pcdbreeviaoszhudmo&cup2hreq=008f724adbdc3c5f7a2c4fc5c1707739791edd4562f7b2c932b1f19b6c3a3151
https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://edge.microsoft.com/abusiveadblocking/api/v1/blocklist
https://clients2.googleusercontent.com/crx/blobs/abe5cl52ck7wwbndbvvaem8oys3yhboz1h4zjji-spceoodztoqtbav4glxcdddxfkjcfz5qxdftce2lflmfl4fmgxvilhkmrudcuedenzrbmgjjiqxwnwfy8qwxmtkglheaxlka5bx6yvrdaanj1smxvmii4akl_ln2/ghbmnnjooekpmoecnnnilnnbdlolhkhi_1_110_1_0.crx
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1790239346&lafgdate=0
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
Last Seen at

Recent blog posts

post image
Threat Coverage Digest: New Malware Reports a...
watchers 7089
comments 0
post image
Phishing Response Protocol: 3 Essential SOC S...
watchers 9185
comments 0
post image
Major Cyber Attacks in September 2026: US and...
watchers 13311
comments 0

What is Gafgyt malware?

Gafgyt, also known as BASHLITE, LizardStresser, and Torlus, is a malware family that targets Linux-based IoT devices such as routers and IP cameras. It is known for its botnet capabilities, which allow it to conduct DDoS attacks and perform other malicious activities.

Gafgyt has been active since at least 2014, when it was initially named Bashdoor. Over the years, it has been responsible for multiple high-profile DDoS attacks. For instance, in 2019, the botnet was used to disrupt the operations of Valve Source Engine and games like Fortnine by targeting their servers.

The prevalence of this malware can be attributed to the fact that its original code was exposed to the public in 2015. Since then, different threat actors have used it to build their own strains of the malware and employed them in numerous attacks.

Gafgyt execution process

We can study the behavior of Gafgyt on an infected system by analyzing its sample in ANY.RUN’s cloud malware sandbox.

We are going to use an .elf file sample, which is an executable format on Linux systems commonly used by attackers to distribute Gafgyt. View the analysis session by following this link.
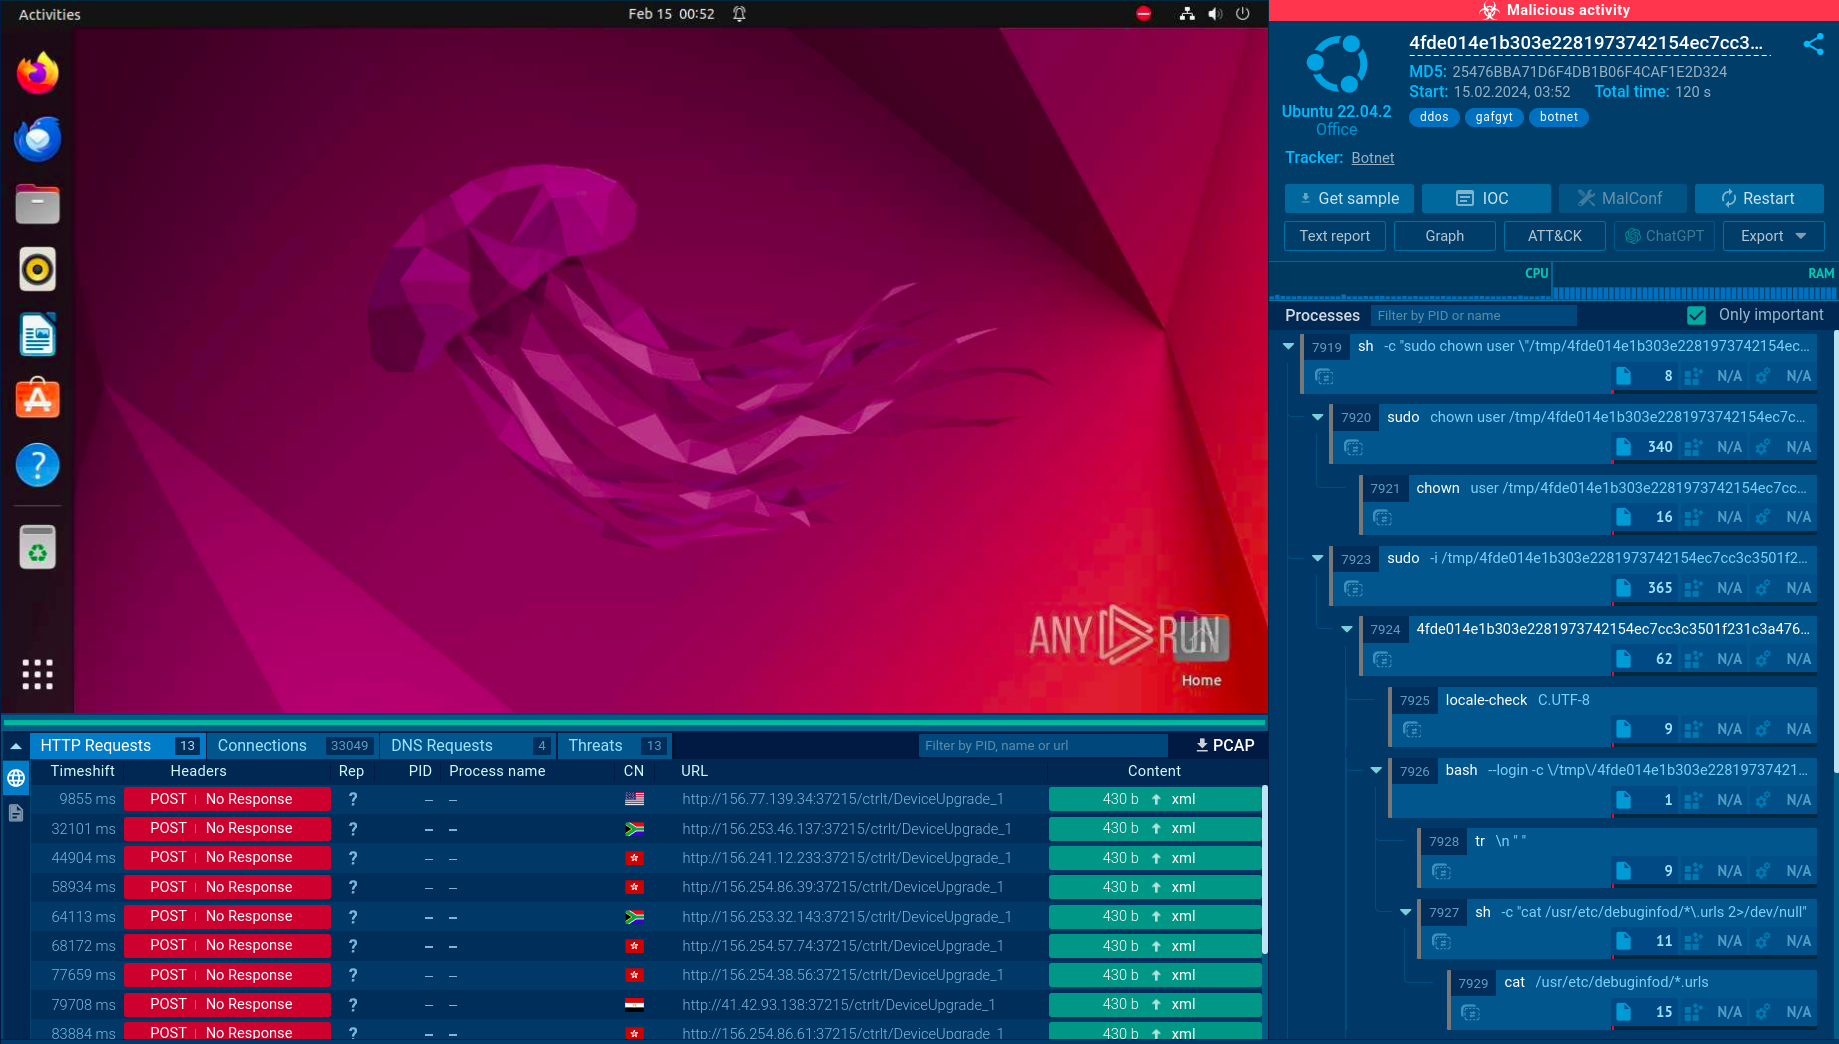
Gafgyt analysis in ANY.RUN Gafgyt analysis in ANY.RUN

After launching the analysis, the service instantly detects Gafgyt and starts to record all of its malicious activities.

When looking at the Connections tab, we can see how the infected machine joins a botnet and participates in a DDoS attack. Specifically, the sandbox shows how the machine begins making thousands of connections.
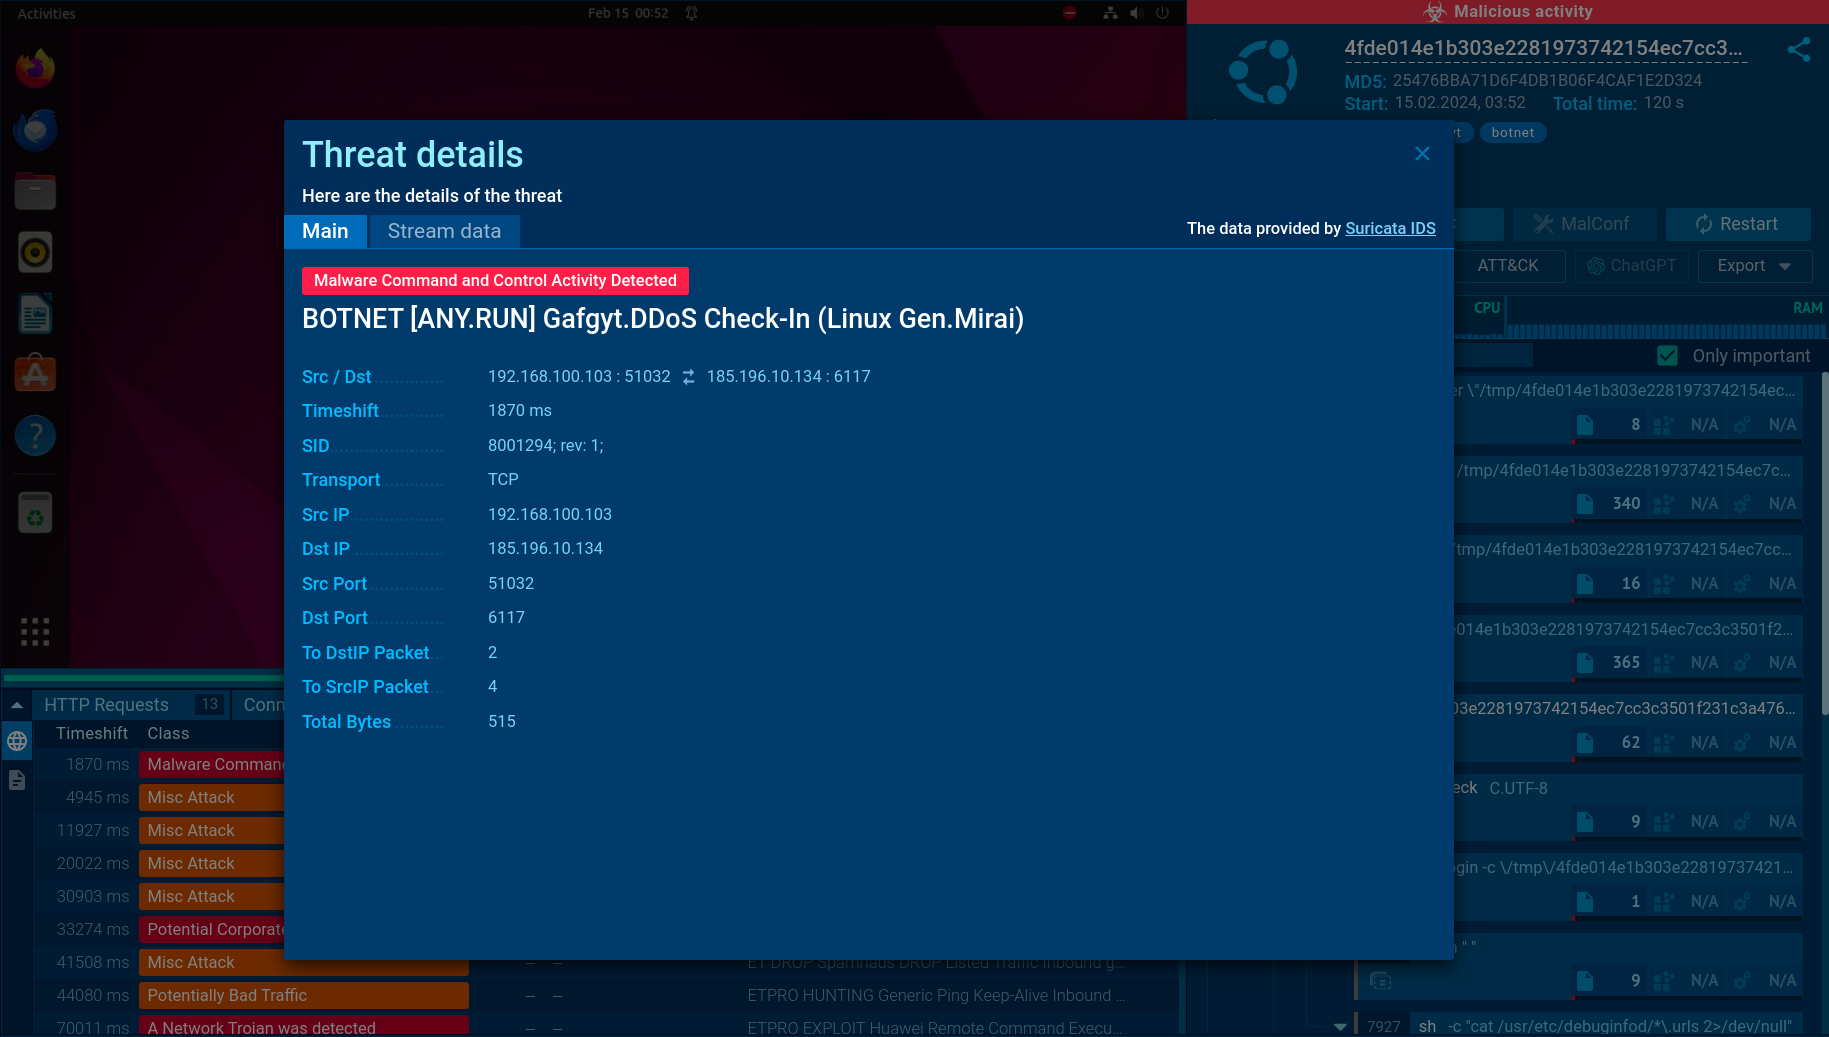
Gafgyt analysis in ANY.RUN ANY.RUN also provides the Suricata rule which was used to detect Gafgyt

When exploring the Threats tab, we can observe the Suirata rules which were triggered during the analysis process. We can click on each one to access more details.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Gafgyt malware technical details

Gafgyt is written in C programming language. It uses a modular structure, which allows it to dynamically load and execute plugins. Interestingly, some of the versions of Gafgyt utilize code originally found in the Mirai malware, including TCP and HTTP flooding modules.

The primary way used by Gafgyt to hijack IoT devices is through brute forcing. The malware has a hard-coded list of default Telnet and SSH credentials which it employs in its attempts to penetrate devices.

Another method of infecting devices utilized by Gafgyt is through vulnerabilities. For instance, CVE-2017-18368 is one of the flaws exploited by the malware to target Zyxel routers. It is possible because of a lack of proper input validation in the Remote System Log forwarding function.

CVE-2023-1389 is another vulnerability abused by the most recent variants of Gafgyt. It is present on TP-Link Archer devices and once again involves the execution of an unauthorized malicious command that can be added to the country form in the web management interface.

After infecting the device, Gafgyt usually downloads a script from a pre-configured address and launches it. After collecting the device’s IP address and system information, it connects to its command-and-control server (C2).

Next, the C2 may send instructions to the malware which usually include engaging in different types of flooding attacks on specified targets.

The malware uses a combination of symmetric and asymmetric encryption for its communication.The malware's C2 servers are typically hosted on compromised devices.

Some versions of Gafgyt also have a persistence mechanism that allows it to survive device reboots.

Gafgyt malware distribution methods

Unlike botnet malware such as Socks5Systemz that spreads via loaders, Gafgyt is usually distributed through exploitation of security flaws in IoT devices. This can include devices with open Telnet or SSH ports, devices with default or weak credentials, and devices that have not been patched for known vulnerabilities.

It also has a self-propagation mechanism, which allows it to spread to other devices without any user interaction. This is typically done by scanning the internet for devices with open ports and attempting to gain access using default credentials.

The malware can also be distributed through malicious downloads. This can occur when a user downloads and executes a file from an untrusted source, such as a malicious website or email attachment.

How to analyze BASHLITE malware

Despite being decade-old, Gafgyt continues to be a considerable threat. It is particularly serious for organizations with Linux-based infrastructure. Protecting against a Gafgyt infection requires a combination of security measures, including strong unique passwords and timely patching.

To understand how Gafgyt and other malware operate, as well as to collect indicators of compromise, use ANY.RUN’s interactive sandbox.

The service is invaluable for malware analysts and SOC professionals, as it:

  • Detects threats in files and links in under 40 seconds.
  • Lets you interact with the samples and the system just like with a standard computer.
  • Offers customizable Windows and Linux virtual machines.
  • Generates comprehensive threat reports.
  • Exposes all malicious network, registry, & files activity and processes.

With ANY.RUN, you can strengthen your security posture.

Create your ANY.RUN account – it’s free!
HAVE A LOOK AT

DragonForce screenshot
DragonForce
dragonforce
DragonForce is a ransomware strain operating under the Ransomware-as-a-Service (RaaS) model. First reported in December 2023, it encrypts files with ChaCha8, renames them with random strings, and appends “.dragonforce_encrypted.” By disabling backups, wiping recovery, and spreading across SMB shares, DragonForce maximizes damage and pressures victims into multimillion-dollar ransom negotiations. It has targeted manufacturing, construction, IT, healthcare, and retail sectors worldwide, making it a severe threat to modern enterprises.
Read More
Cactus Ransomware screenshot
Cactus ransomware-as-a-service (RaaS) was first caught in March 2023 targeting corporate networks. It became known for its self-encrypting payload and double extortion tactics. Cactus primarily targets large enterprises across industries in finance, manufacturing, IT, and healthcare. It is known for using custom encryption techniques, remote access tools, and penetration testing frameworks to maximize damage.
Read More
Moonrise screenshot
Moonrise
moonrise
Moonrise RAT is a newly discovered Go-based remote access trojan with zero detections at launch, featuring credential theft, keylogging, webcam access, clipboard hijacking, and UAC bypass.
Read More
MassLogger screenshot
MassLogger
masslogger
MassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems. It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
Read More
NetSupport RAT screenshot
NetSupport RAT
netsupport
NetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
Read More
ClickFix screenshot
ClickFix is a sophisticated social engineering technique that tricks users into manually executing malicious commands on their devices. It masquerades as a "quick fix" for fake technical issues, CAPTCHA verifications, or error messages, often hijacking the clipboard to paste harmful PowerShell or terminal commands. This user-assisted approach helps it bypass traditional security controls, leading to infostealers like Lumma Stealer, RATs, and other malware.
Read More