Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

DBatLoader

77
Global rank
66 infographic chevron month
Month rank
100 infographic chevron week
Week rank

DBatLoader is a loader malware used for distributing payloads of different types, including WarzoneRAT and Formbook. It is employed in multi-stage attacks that usually start with a phishing email carrying a malicious attachment.

Loader
Type
Unknown
Origin
1 June, 2020
First seen
16 October, 2026
Last seen

How to analyze DBatLoader with ANY.RUN

Type
Unknown
Origin
1 June, 2020
First seen
16 October, 2026
Last seen

IOCs

IP addresses
107.174.192.179
48.209.138.189
82.29.67.160
142.251.20.132
104.26.9.202
2.23.246.9
142.251.13.154
142.251.110.102
172.211.123.250
23.59.18.102
142.251.154.119
20.166.131.27
2.16.204.135
142.251.20.155
188.114.97.3
23.59.17.18
150.171.27.11
104.26.13.64
192.178.183.139
185.111.111.157
Hashes
74441313bb1fb62500484443c4937e90d4e335351a4fcd12a9ac48448500e33e
2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
4094d158e3b0581ba433a46d0dce62f99d8c0fd1b50bb4d0517ddc0a4a1fde24
99653a38c445ae1d4c373ee672339fd47fd098e0d0ada5f0be70e3b2bf711d38
c158322bd963d2a68ffc878d72213a7394d8c16de72279771ffc924365eec0df
59345c006cd9bde5ef532aae1f119758d45030993181c272bb0dd6fc0c5d01e5
2ae1142b08d296c25000e451237ea919f981da28f6a723d39540f43f18bac762
5639c845d56dedecd2cfdb082b734593b5d618a87f1bd8ec612a8b3f4245566a
32ae9531405ef3c59448fe6dbd3be435e726eb17f3ca0d16530a4c6317dea286
7c68f28c6995f47dd77596bab28c6b4388ff93840c3becfd37733ddb640cd0cd
40cf1af5650b699a947899d2b43a00dcb64cdeaf080651c82a7930910c1c03f4
ec249b0dab6fda20cc24f0f25a504c55a05b23fb6cbb4938aa7a41df0c8744b6
0162159b64eb092f94964faf937f263fb9947b25d40e0d82bd3224d136a140de
77eed9211cd8464482f0da3fac4c0f003c2b8a6d76f15445927e66400f102d60
6558013f984e594bb57534910ce0b17bfa15da3cc9bb4b6e0b5c6e4ddf9eb14e
a7109b8374dffa7a0cd69558990f7e96fea9ef61736d89043dad5a6694cdfa4a
758a0b404b3daadbd0d4e88a0bedf5c21d5507392f7b54d4906ffea49d58ab32
558bbe6193a202dcb00cc441421f5d838764e495b8e4d2e10877db7f661b8cd5
db3ac1fd3d65df45d805adb8dfe0c5209db07ef93406db17dfb783dd8048720a
19acfa0adce363a9c9a3be73f5ec0fac0dcf3c630ce18125fd265040ad6ffb6c
Domains
fundingchoicesmessages.google.com
pagead2.googlesyndication.com
copilot.microsoft.com
t.me
ip-api.com
jackthyfuc.run
laminaflbx.shop
identitytoolkit.googleapis.com
fonts.googleapis.com
plausible.io
edge.microsoft.com
tracenep-eu.admaster.cc
ep1.adtrafficquality.google
update.googleapis.com
www.bing.com
must-directed.gl.at.ply.gg
uploadnow.io
oneocsp.microsoft.com
www.googletagmanager.com
edge-consumer-static.azureedge.net
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:qyiwdga5l7ws_4bzfjxxyioxf9ookxt0g7n-czu98sk&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://copilot.microsoft.com/c/api/user/eligibility
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://uploadnow.io/en/share?utm_source=0bcds7g
https://cdn.uploadnow.io/_next/static/css/5117ad1bbac15a06.css
https://cdn.uploadnow.io/_next/static/css/bdb3e22b41fb00da.css
https://cdn.uploadnow.io/_next/static/css/5ded0d5ca9ecc5c1.css
https://cdn.uploadnow.io/_next/static/css/56b52b0051b23322.css
https://cdn.uploadnow.io/_next/static/chunks/framework-76034876ab87df27.js
https://cdn.uploadnow.io/_next/static/chunks/webpack-601ccb16b36d1888.js
https://cdn.uploadnow.io/_next/static/chunks/main-8d1cee1b5c7f376f.js
https://cdn.uploadnow.io/_next/static/chunks/pages/_app-090ad369d35c5500.js
https://cdn.uploadnow.io/_next/static/chunks/62867-3e700a701aca7086.js
https://cdn.uploadnow.io/_next/static/chunks/38993-242fdc22cc1c9823.js
Last Seen at
Last Seen at

Recent blog posts

post image
DORA TLPT Requirements Explained: Where Threa...
watchers 5109
comments 0
post image
Your MSSP Added 10 New Clients. What Breaks F...
watchers 6354
comments 0
post image
Fake AI Tools Put US Companies at Risk: Insid...
watchers 14067
comments 0

What is DBatLoader malware?

DBatLoader is a loader written in Delphi that has been in extensive use among attackers since 2020. One of the key features of the malware is its reliance on legitimate cloud-based platforms such as Discord for hosting its payloads. DBatLoader has been involved in numerous campaigns and leveraged to deploy stealers, trojans, and other threats.

In most cases, DBatLoader manages to infect machines via multi-stage attacks. For instance, victims may receive an email attachment in the form of a PDF file. Upon opening the attachment, users may be prompted to click on a seemingly genuine button embedded with a malicious link. Clicking this link will initiate the download of a Windows Cabinet file, which, in turn, will trigger the installation of DBatLoader on the unsuspecting user's computer.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of the DBatLoader malicious software

DBatLoader’s sole purpose is to distribute other malware on the devices it manages to infect. To do this, the developers behind DBatLoader have equipped their malicious software with several advanced capabilities.

For example, DBatLoader can avoid User Account Control (UAC) to gain elevated privileges. It does this by exploiting the mock folder vulnerability. In Windows, executables launched from certain system directories can auto-elevate. DBatLoader exploits this by creating a mock folder with the same name as a trusted location, such as "C:\Windows\System32 ".

On top of that, DBatLoader copies a legitimate process to this fake folder and then injects it with its malicious DLL that allows the payload downloaded by DBatLoader to execute freely without any security notifications, achieving sustained persistence.

Another common vulnerability abused by DBatLoader in previous attacks was CVE-2018-0798, an exploit targeting Equation Editor in Microsoft Office. The malware has also been observed to utilize steganography.

As mentioned, DBatLoader is usually configured to pull malicious payloads from servers of popular cloud storage services, including Microsoft OneDrive and Google Drive. Some of the notable examples of malware dropped by DBatLoader are Formbook, Warzone, and Remcos.

Execution process of DBatLoader

In order to detect DBatLoader, it is vital to analyze the latest samples of this malware and collect up-to-date information on it. To this end, we can use ANY.RUN, a malware analysis sandbox that lets us quickly analyze any suspicious file or link to spot threats.

Let’s upload a sample of DBatLoader to ANY.RUN and study its behavior.

In this task, DBatLoader was distributed as an executable file with a name mimicking the title of a document, attempting to trick users into opening the file and executing the malicious code. Upon execution, DBatLoader downloads and injects the Formbook malware into the Control and Explorer system processes, enabling its malicious activity.

Analyze malware for free in a fully interactive cloud sandbox – sign up now!
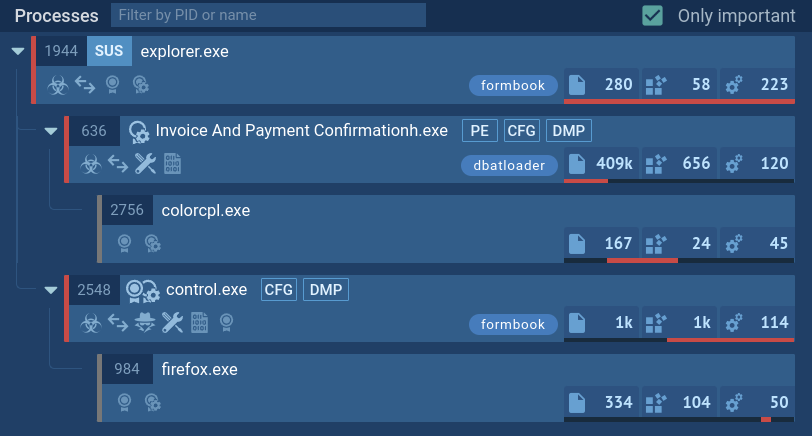
DBatLoader process tree shown in ANY.RUN DBatLoader's process tree demonstrated in ANY.RUN

In addition, this loader can be used in more sophisticated attacks, such as exploiting vulnerabilities to penetrate the system. These can be familiar vulnerabilities like CVE-2017-11882, as well as lesser known ones. On top of that, DBatLoader can also make use of system utilities in its attacks. In this task, a whole arsenal of system utilities is actively used, such as cmd, ping, and xcopy, including for the purpose of lateral movement. Eventually, DBatLoader drops Remcos that instantly begins its operation.

Distribution methods of the DBatLoader malware

Phishing campaigns constitute the most common vector of attack involving DBatLoader. Emails sent by the operators of the malware target different organizations and are masqueraded as genuine messages. In many cases, criminals even use legitimate email addresses they manage to hijack or gain access to.

The subject of such emails concerns different business-related matters, such as payments and other arrangements. For example, attackers may send fake invoices as Microsoft Office or PDF files. These files usually contain a link that, once clicked, can trigger the infection leading to DBatLoader being dropped on the computer and the eventual deployment of the final payload.

Conclusion

DBatLoader remains an active threat commonly used by criminals in their attacks on various types of organizations. To keep your infrastructure safe, it is essential that you have strong security measures in place, especially when it comes to software for detecting and inspecting threats.

Use the ANY.RUN sandbox as a reliable tool for analyzing emails you receive to safely determine if they pose any danger. ANY.RUN’s interactive cloud environment makes it easy to investigate the most advanced phishing campaigns and uncover multi-stage attacks in minutes. The service provides you with convenient text reports containing all the relevant information on the files and links you submit, including fresh IOCs.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

ACR Stealer screenshot
ACR Stealer is a modern information-stealing malware designed to harvest sensitive data from infected devices. Like other infostealers, it targets credentials, financial details, browser data, and files, enabling cybercriminals to monetize stolen information through direct fraud or underground market sales.
Read More
Quasar RAT screenshot
Quasar RAT
quasar trojan rat
Quasar is a very popular RAT in the world thanks to its code being available in open-source. This malware can be used to control the victim’s computer remotely.
Read More
LockBit screenshot
LockBit
lockbit
LockBit, a ransomware variant, encrypts data on infected machines, demanding a ransom payment for decryption. Used in targeted attacks, It's a significant risk to organizations.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More