Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
97
Global rank
94 infographic chevron month
Month rank
74 infographic chevron week
Week rank

AZORult can steal banking information, including passwords and credit card details, as well as cryptocurrency. This constantly updated information stealer malware should not be taken lightly, as it continues to be an active threat.

Stealer
Type
ex-USSR
Origin
1 January, 2016
First seen
3 October, 2026
Last seen
Also known as
PuffStealer
Rultazo

How to analyze Azorult with ANY.RUN

Type
ex-USSR
Origin
1 January, 2016
First seen
3 October, 2026
Last seen

IOCs

IP addresses
150.136.141.142
103.226.124.232
140.82.121.3
188.164.198.15
140.82.121.4
222.141.57.105
185.199.109.133
172.67.141.143
43.228.157.73
69.62.76.225
111.118.212.120
2.23.246.9
61.249.139.64
101.47.31.11
91.204.209.49
184.24.77.136
52.248.41.253
57.129.130.178
185.199.111.133
193.148.57.28
Hashes
efbdbbcd0d954f8fdc53467de5d89ad525e4e4a9cfff8a15d07c6fdb350c407f
6823b98c3e922490a2f97f54862d32193900077e49f0360522b19e06e6da24b4
d3acd72f585872f36d7329faf6146dc2d71c3cbcbd58d94e36da285738adaa68
6b6dd8b11f84fb78e3e8cfaa7c5fca569d79402b9fc5861b00960b25607c911e
e728f79439e07df1afbcf03e8788fa0b8b08cf459db31fc8568bc511bf799537
7f0121322785c107bfdfe343e49f06c604c719baff849d07b6e099675d173961
44fb04b5c72b584b6283a99b34789690c627b5083c5df6e8b5b7ab2c68903c06
aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
13b5cb481e0216a8fc28bfa9d0f6b060cdf5c457b3e12435ca826eb2ef52b068
bc4cbe4c99fd65abea45fbdaf28cc1d5c42119280125fbbd5c2c11892ae460b2
91088bbbf58a704185dec13dbd421296bbd271a1aebbcb3ef85a99cecd848ff8
ba557a3c656275a0c870fb8466f2237850f5a7cf2d001919896725bb3d3eaa4b
0e0732480338a229cc3ad4cdde09021a0a81902dc6edfb5f12203e2aff44668f
12ad1546eb391989105d80b41a87686d3b30626d0c42a73705f33b2d711950cc
2981965bd23a93a09eb5b4a334acb15d00645d645c596a5ecadb88bfa0b6a908
cead5eb2b0b44ef4003fbcb2e49ca0503992ba1d6540d11acbbb84fdbbd6e79a
a7966b95dbe643291fb68e228b60e2dc780f8155e064d96b670c8290f104e4ab
42ef317ea851a781b041dc1951ea5a3ea1e924149c4b868ecd75f24672b28fa8
c7b0377f30e42048492e4710fe5a0a54fa9865395b8a6748f7dac53b901284f9
e809f227e92542c6fb4bac82e6079661eef7700964079aa4d7e289b5b400ec49
Domains
www.google.com
landonirwin.com
vn789win.top
www.microsoft.com
clientservices.googleapis.com
release-assets.githubusercontent.com
ipv6check-http.steamserver.net
sutterpoint.com
optimizationguide-pa.googleapis.com
mogimall.com
vuelaviajero.com
roaming.svc.cloud.microsoft
freegeoip.app
best10cdn.blob.core.windows.net
safeifm.com
go.microsoft.com
infoc0.duba.net
pub-ec081eb0fab74385a17d8d77afeeda3b.r2.dev
the.earth.li
2cfc0222.salamanderprocessing.pages.dev
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
https://www.bing.com/dsb/scenario?name=trendingsearchwithcache&cc=us&setlang=en-us
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f3%2f2026%2c%202%3a01%3a48%20pm
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.46b91287-d025-4e0b-8069-bfd221edc035&pid=dsb
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=c&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=1&cvid=c792658b1d3f4f1798c6c097dd3c1beb&ig=b43082979f7e47efa52486c348fe42df
https://www.bing.com/th?id=osk.7k665ykc-ykkrcjii-v3boij3avk2quatdjap8opw7g&w=80&h=80&qlt=90&c=6&rs=1&cdv=1&pid=rs
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=cm&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=2&cvid=c792658b1d3f4f1798c6c097dd3c1beb&ig=295341b2c0ef4a7598f3420a5af1f5fc
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=cmd&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=3&cvid=c792658b1d3f4f1798c6c097dd3c1beb&ig=d999e0c410974d94b7899aa5b690d700
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://www.bing.com/web/xlsc.aspx?t=5&dl=1&f=9&wsbc=1
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://login.live.com/ppsecure/deviceaddcredential.srf
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1648
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 3378
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10879
comments 0

What is AZORult malware?

AZORult is an information stealer malware that is targeted at stealing credentials and accounts. Updated multiple times over the years, AZORult continues to be an active concern for the users, stealing information such as banking passwords, credit card details, browser histories, and even cryptocurrency.

AZORult stealer was discovered, analyzed, and documented for the first time on July 26, 2016, by Proofpoint researchers. At the time, the virus was distributed together with another trojan called Chthonic. However, subsequent spam email campaigns started distributing AZORult as the main payload while Hermes and Aurora ransomware were added as additional payloads. A new strain of the stealer Trojan was documented In July 2018. The analysis revealed that it brought several upgrades to the functions of both the stealer and the loader of the virus, additionally allowing to distribute AZORult with the RIG exploit kit. The latest recorded version of the malware is v3.3. This strain was first documented in October 2018. Most notably, this strain updated a way of encrypting the C&C domain string and improved crypto-stealing function.

General description of AZORult malware

A trojan type malware originated in one of the ex-USSR countries. AZORult spyware searches for useful information on the affected computer and sends it to the C2 server to potentially steal the victim’s bank account data. AZORult can steal cookies, browser autofill information, desktop files, chat history, and more.

Interestingly, to get into a machine, the virus, in some cases, requires secondary malware like HawkEye or Seamless. Notably, after every bit of useful data is obtained in campaigns with Hermes and Aurora, user files are encrypted, and a ransom is requested to restore the lost data.

One of the interesting features of AZORult is that after execution, the malware is removed from the system due to the lack of a persistence mechanism.

Malware analysis of AZORult

ANY.RUN displays the execution process of AZORult in an interactive virtual environment. As shown by the sandbox simulation, the virus launches the following process during its execution:

  • Firstly, a Microsoft Office file opened, and WINWORD.EXE with enable macros is executed;
  • The malware runs EQNEDT32.EXE and downloads a malicious executable through the exploitation of the CVE-2017-11882 Microsoft Office Equation Editor vulnerability;
  • A kendriknk8523.exe file is then launched, which after a sleep create child process with same name;
  • A child process then proceeds to steal the personal data and connect to the CnC server.

The execution process of AZORult can be viewed in more detail in the video provided by ANY.RUN sandbox.
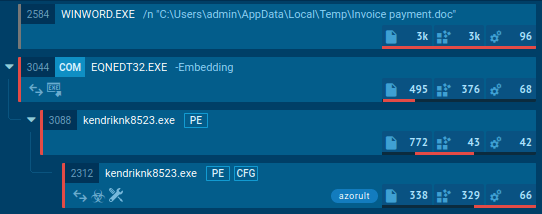
azorult execution process tree

Figure 1: Illustrates the life cycle of malware. Process tree generated by ANY.RUN

How to avoid infection by AZORult?

AZORult is distributed mainly using spam email campaigns or via the RIG exploit kit. Notably, a major AZORult distribution campaign was observed on July 18, 2018, targeting North America.

Spam emails that the attackers sent carried largely employment-related subjects and included an infected and password-protected resume file that triggered the download of the virus.
AZORult malware execution process

text report of the azorult malware analysis

Figure 2: A text report generated by ANY.RUN

AZORult stealer uses a clever technique to trick various antivirus engines. Particularly, the version of the stealer Trojan distributed in the July 2018 spam campaign was activated after unlocking a password-protected document. Since a password protected the document that was attached to the email, antiviruses had not been able to scan it and determine whether it was malicious or not. For the virus to become active, the victim had to unlock and enable macros for the document. In this particular campaign, the malware was distributed with two payloads embedded in the main binary. Both payloads were dropped to the disk and executed, with the first executable payload being the information gatherer – AZORult itself and then the secondary ransomware.

It should be noted that in aforecited ANY.RUN simulation AZORult uses an exploit when a Microsoft Office file is opened, allowing to embed several malicious OLE objects into a document and executes arbitrary code on a machine, and even download any file from a remote server and execute it.

How to share your AZORult malware analysis with others?

If you want to share your virus analysis with others, you can create a text report and send it to anyone you want. Just click the "Text report" button. You can save it by using a printer icon in the upper-right corner of the report, or using your browser function by clicking the "Save page as..." or "Print..." buttons. You can also download or share other malware investigations, for example Adwind or Remcos. Note that you can choose that information section in your report you want to print or save into a file using the "Print..." button by clicking in the checkbox "Add for printing" on the right side of the sections. On the illustration below, the second section won't be included in the report.
text report for azorult Figure 3: Text report

Conclusion

AZORult remains to be a hazardous trojan. The stealer Trojan has been upgraded throughout its lifespan and currently poses even more dangers than during the first days of its lifespan. Particularly, most recent versions of AZORult are distributed in bundles with ransomware and can steal cryptocurrency from the victims.

AZORult's distribution in clever email campaigns makes becoming a victim of the stealer Trojan by accident relatively easy. The interactive sandbox analysis provided by services like ANY.RUN is a great way to learn more about the threat and greatly increase cybersecurity.
HAVE A LOOK AT

DeerStealer screenshot
DeerStealer
deerstealer
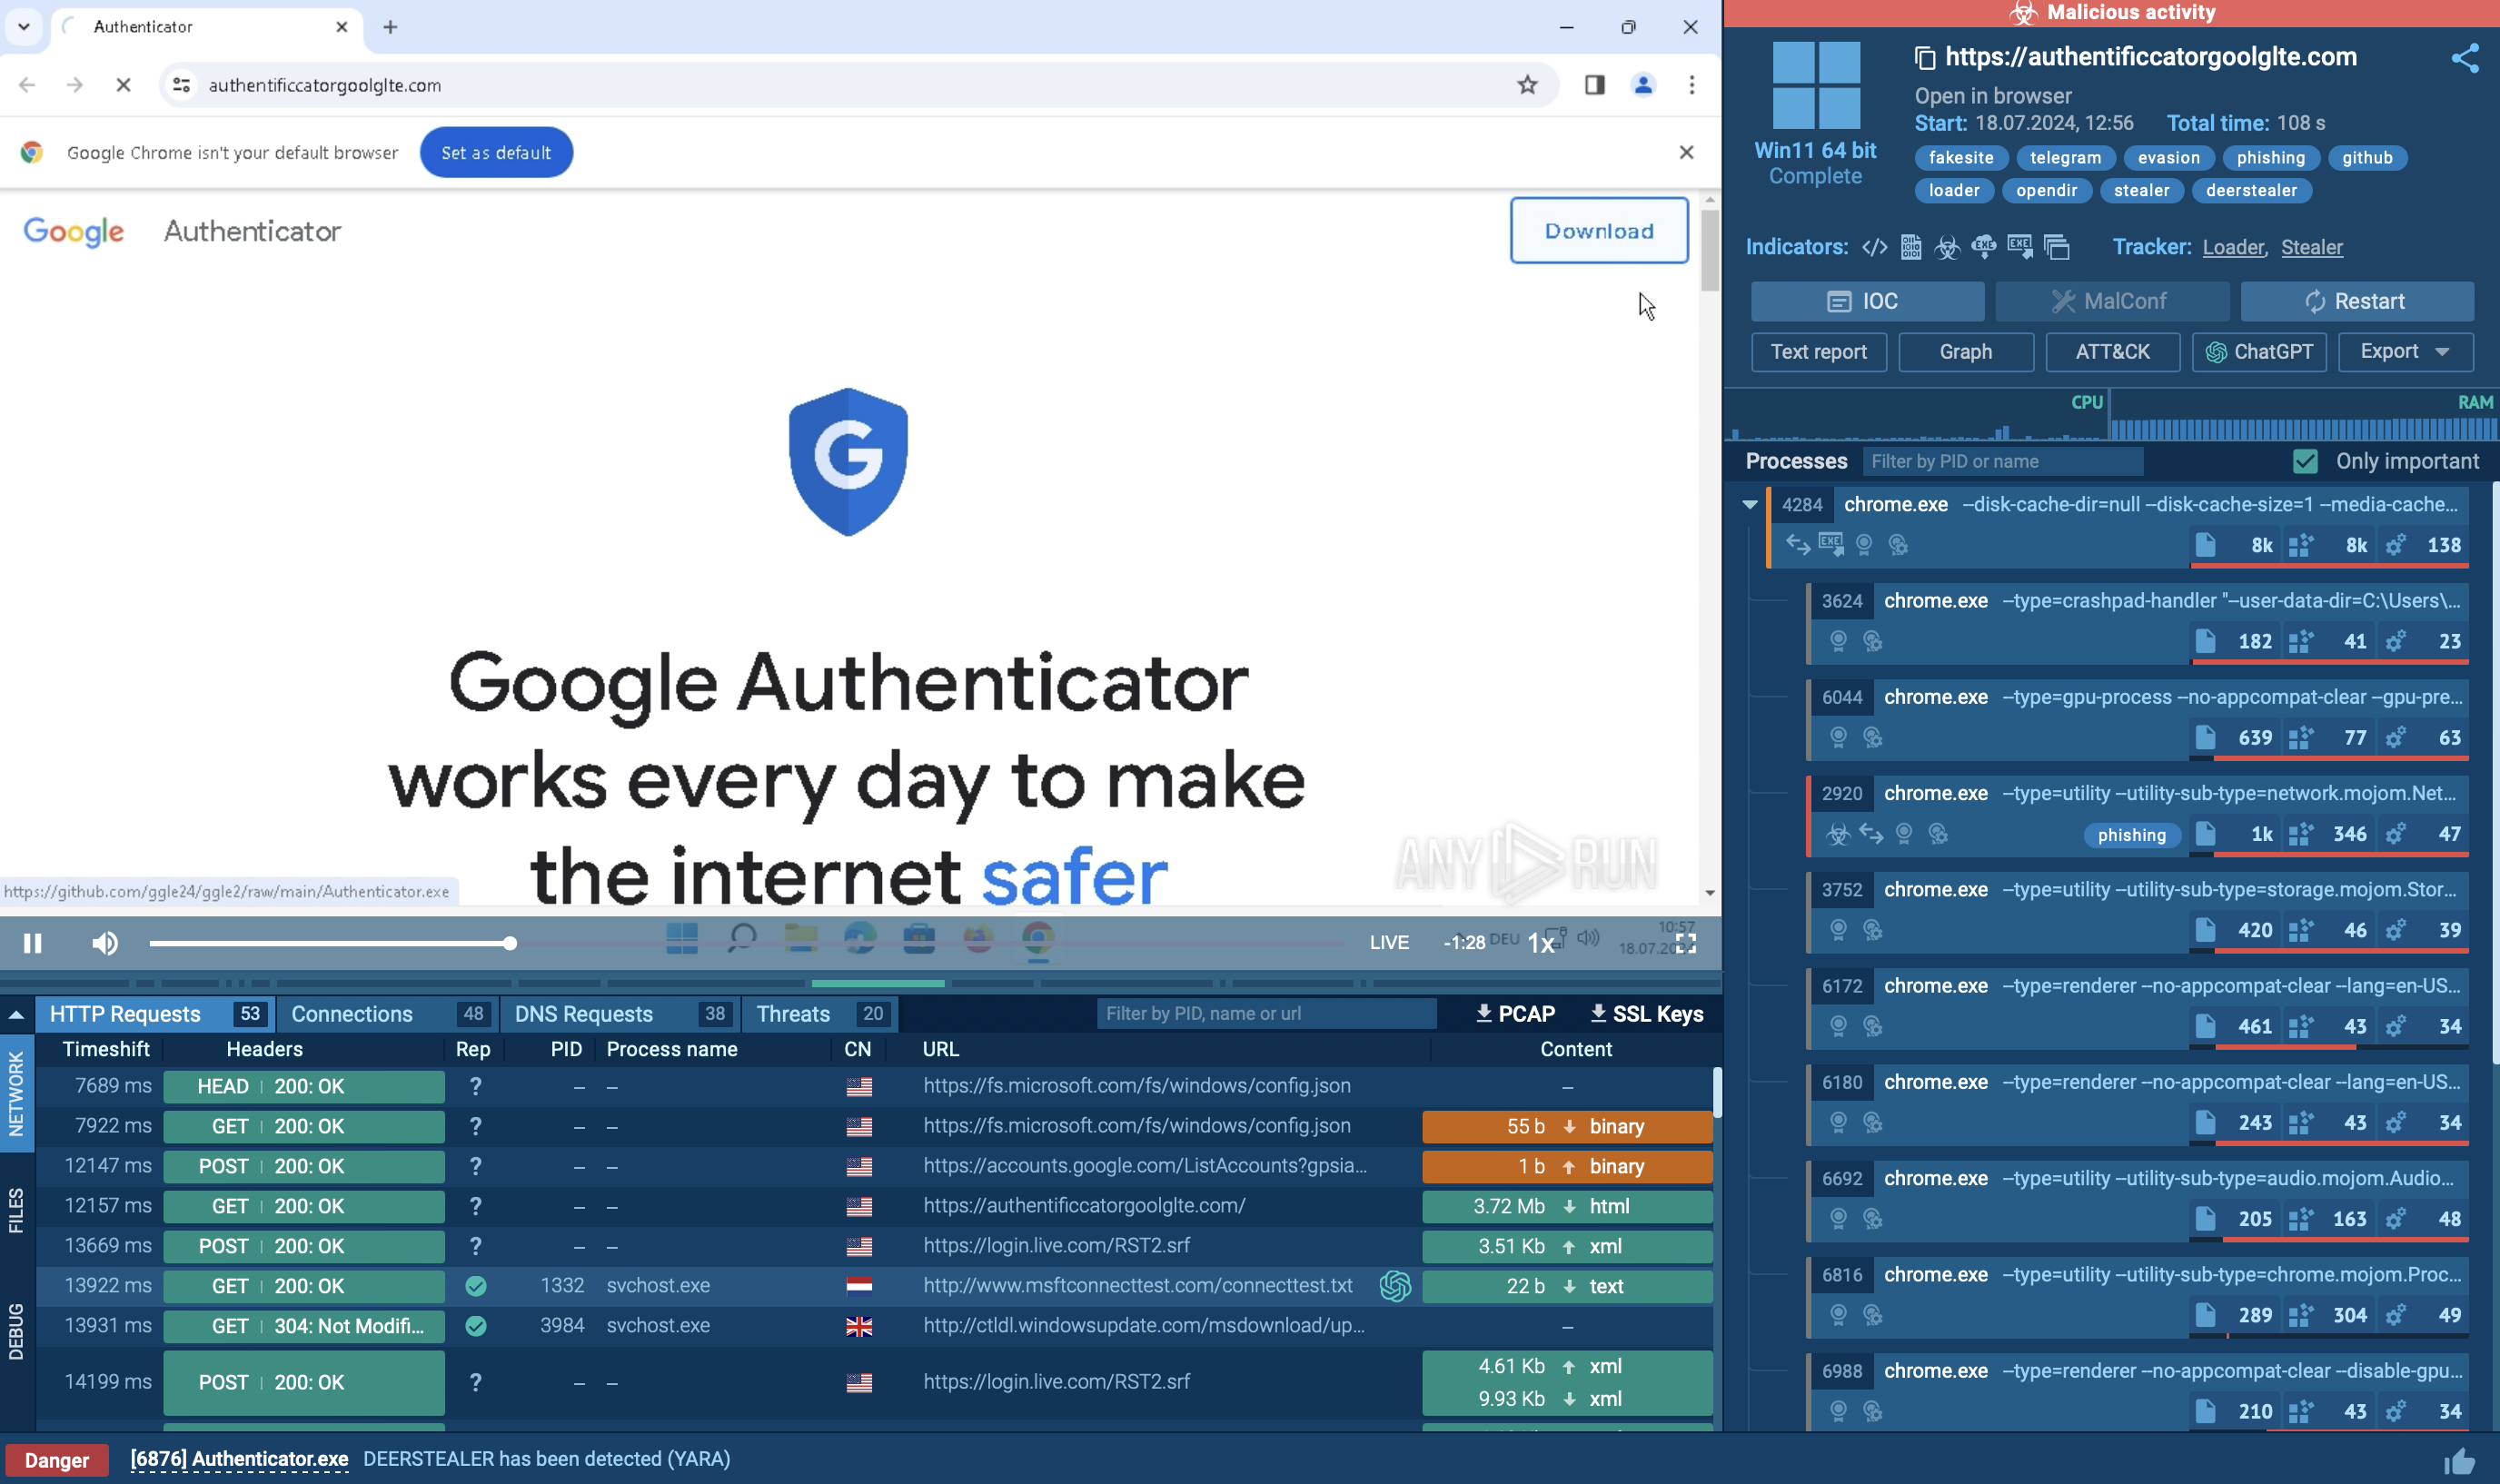
DeerStealer is an information-stealing malware discovered in 2024 by ANY.RUN, primarily targeting sensitive data such as login credentials, browser history, and cryptocurrency wallet details. It is often distributed through phishing campaigns and fake Google ads that mimic legitimate platforms like Google Authenticator. Once installed, it exfiltrates the stolen data to a remote command and control (C2) server. DeerStealer’s ability to disguise itself as legitimate downloads makes it particularly dangerous for unsuspecting users.
Read More
Kratos screenshot
Kratos
kratos
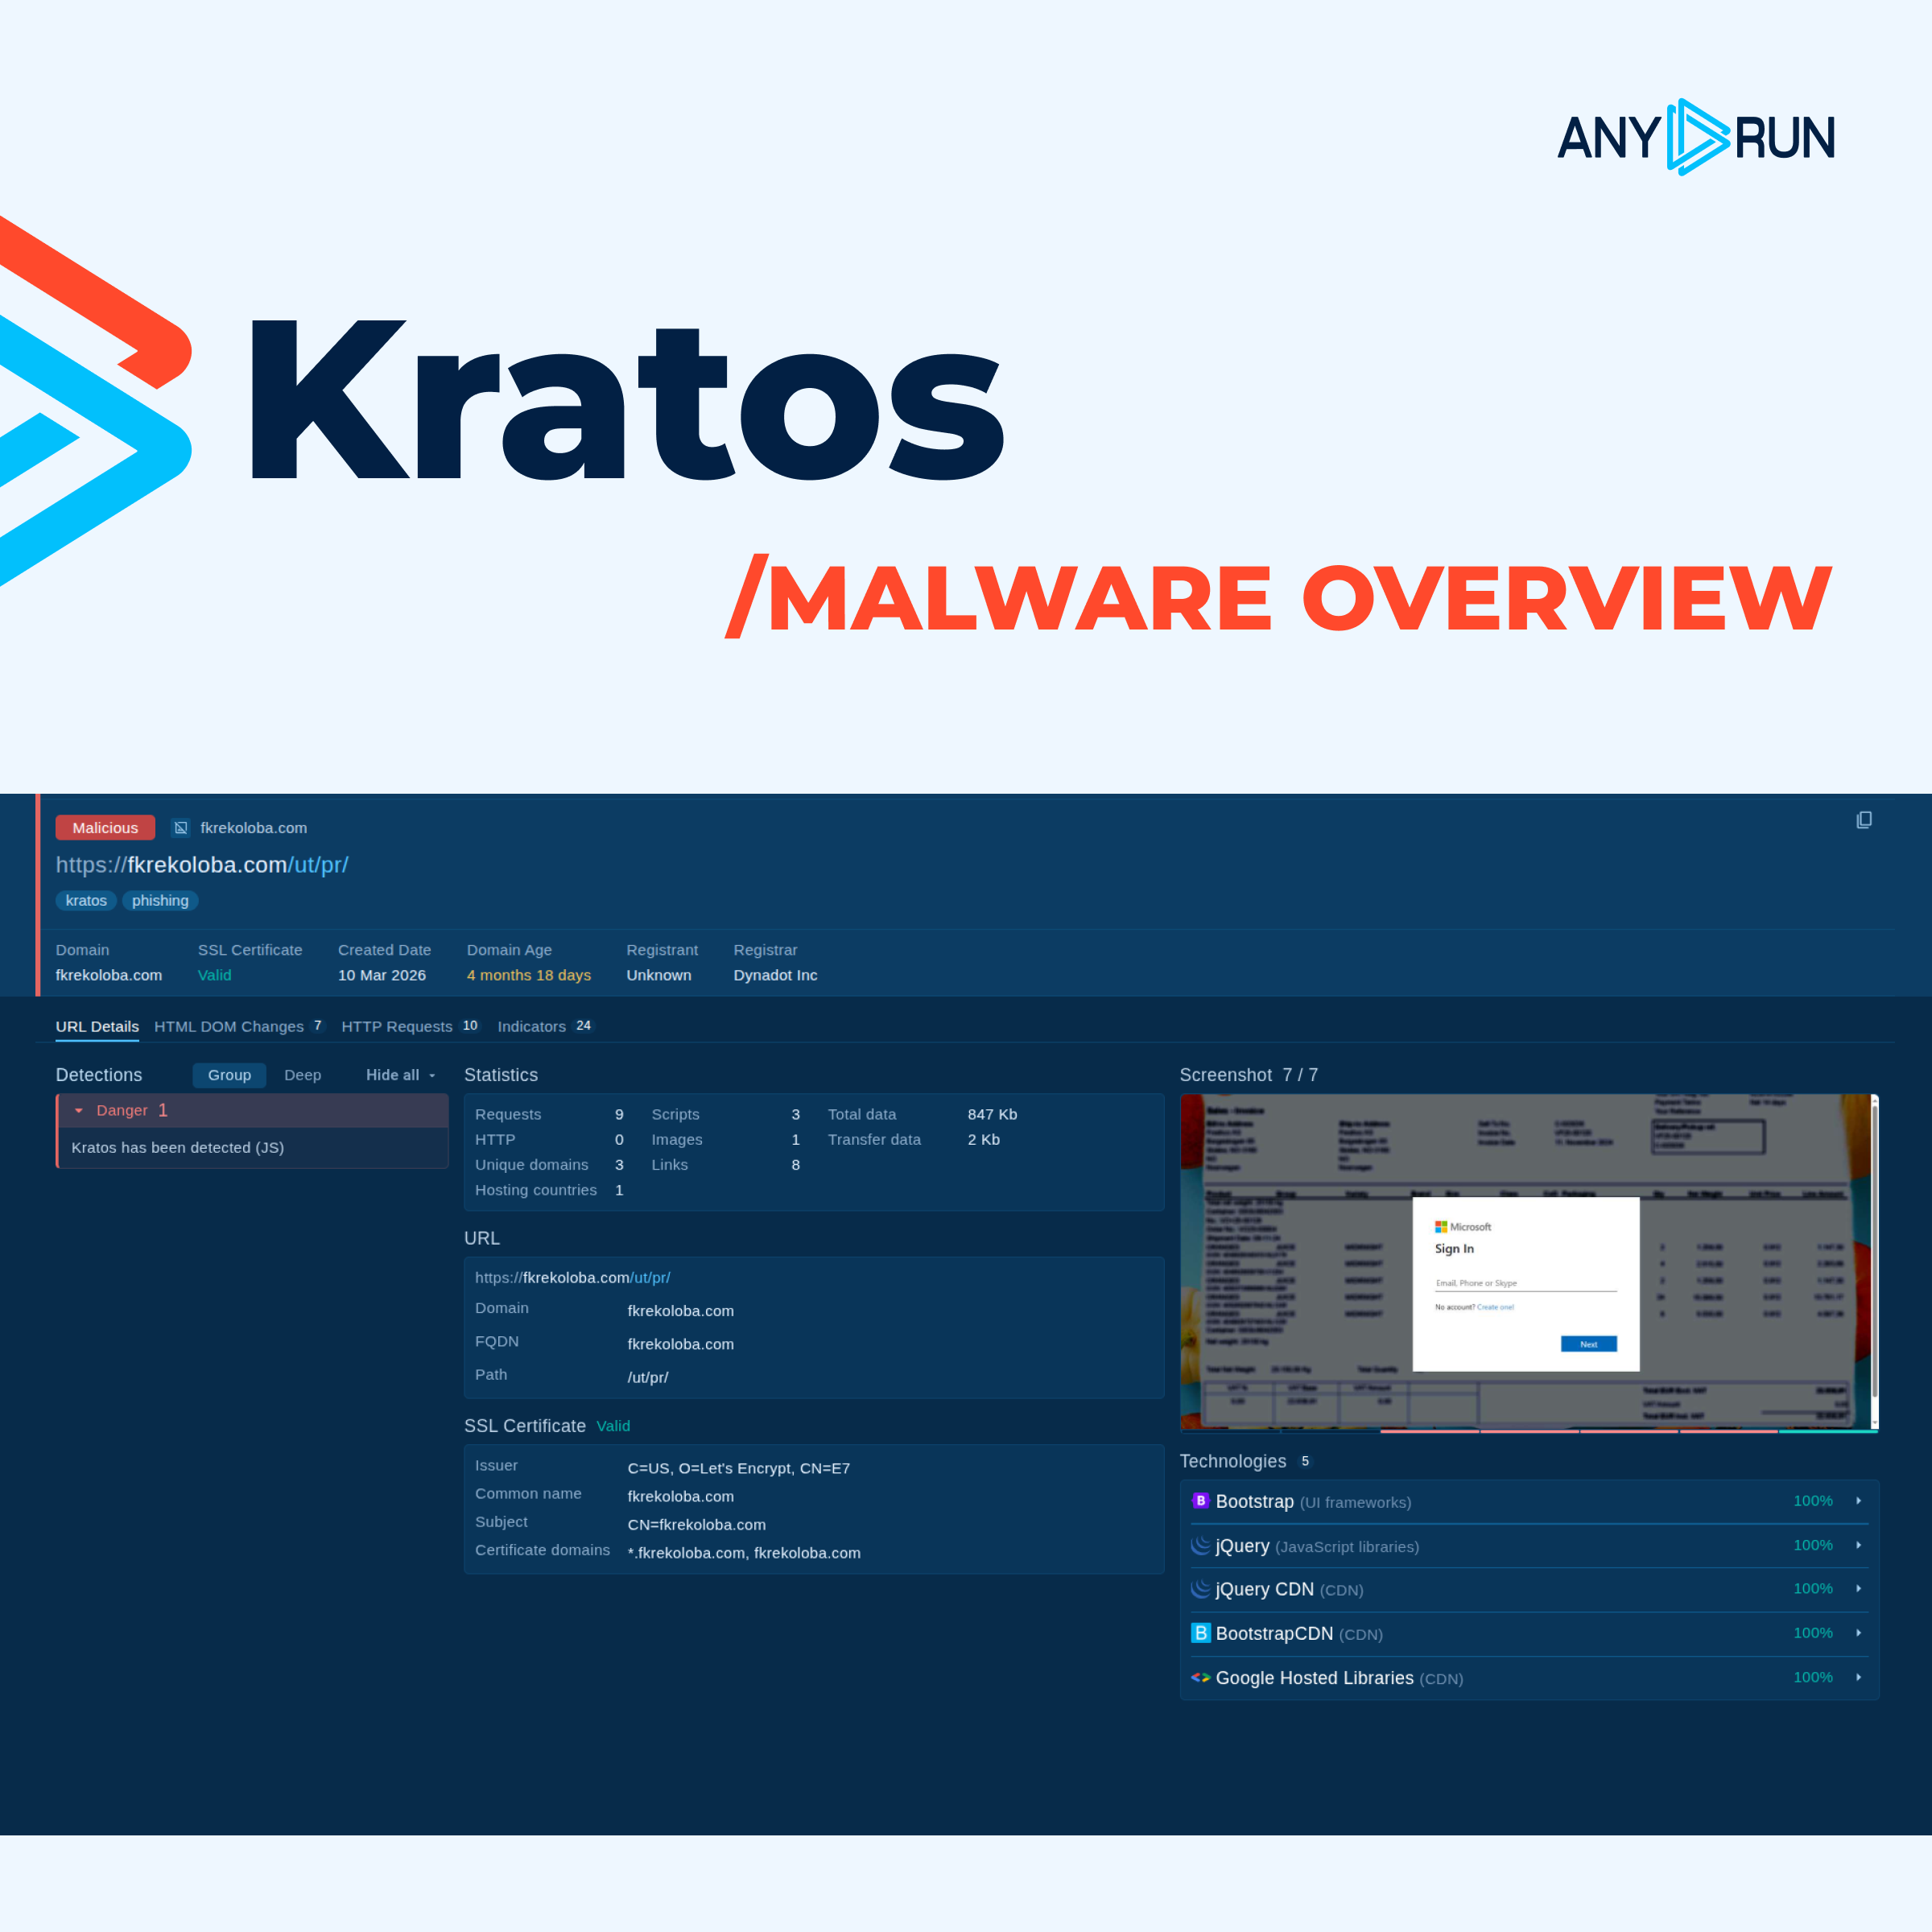
Kratos is a mature Phishing-as-a-Service (PhaaS) platform that evolved from the Sneaky2FA kit to specialize in stealing Microsoft 365 credentials through sophisticated Adversary-in-the-Middle (AiTM) techniques. The service provides low-skilled affiliates with a turnkey solution featuring an advanced administrative dashboard, integrated anti-bot defenses, and real-time data exfiltration via the Telegram Bot API. Although an international law enforcement action known as Operation Olympus Blade disrupted its central infrastructure in July 2026, the kit remains a primary example of the industrialization of modern cybercrime.
Read More
Caminho Loader screenshot
Caminho Loader
caminho caminholoader
Caminho Loader is a Brazilian-origin Loader-as-a-Service operation that uses steganography to conceal .NET payloads within image files hosted on legitimate platforms. Active since March 2025, it has delivered a variety of malware and infostealers to victims within multiple industries across South America, Africa, and Eastern Europe.
Read More
Roning Loader screenshot
Roning Loader
roning
RoningLoader is a multi-stage Windows loader designed to operate quietly while preparing systems for deeper compromise. It abuses trusted system tools and interferes with security controls to reduce the chances of early detection. Instead of acting as a final payload, it creates conditions for follow-on malware to execute more effectively. Its use of staged execution and code injection allows attackers to blend into legitimate activity and escalate impact. This makes early behavioral detection critical before the attack chain progresses further.
Read More
Greatness screenshot
Greatness is a Phishing-as-a-Service (PhaaS) platform that enables cybercriminals, even those with limited technical skills, to launch sophisticated phishing attacks primarily targeting Microsoft 365 (M365) credentials. It acts as a man-in-the-middle (MitM) proxy, facilitating credential theft and MFA bypass while providing affiliates with easy-to-use tools like attachment builders and Telegram notifications.
Read More
DarkGate screenshot
DarkGate
darkgate
DarkGate is a loader, which possesses extensive functionality, ranging from keylogging to crypto mining. Written in Delphi, this malware is known for the use of AutoIT scripts in its infection process. Thanks to this malicious software’s versatile architecture, it is widely used by established threat actors.
Read More