Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

AsyncRAT

3
Global rank
6 infographic chevron month
Month rank
8 infographic chevron week
Week rank

AsyncRAT is a RAT that can monitor and remotely control infected systems. This malware was introduced on Github as a legitimate open-source remote administration software, but hackers use it for its many powerful malicious functions.

RAT
Type
Likely Kuwait
Origin
8 January, 2019
First seen
7 October, 2026
Last seen

How to analyze AsyncRAT with ANY.RUN

RAT
Type
Likely Kuwait
Origin
8 January, 2019
First seen
7 October, 2026
Last seen

IOCs

IP addresses
48.192.1.65
150.171.27.11
3.173.161.14
104.18.23.222
150.171.22.17
142.251.110.100
150.171.109.107
131.253.33.203
40.126.31.128
172.215.188.225
150.171.109.100
23.3.89.98
104.126.36.59
150.171.109.101
150.171.28.11
20.165.94.63
172.211.123.249
2.16.10.153
23.11.41.157
52.218.185.64
Hashes
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
474d668707f1cb929fef1e3798b71b632e50675bd1a9dceaab90c9587f72f680
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
6028bd681dbf11a0a58dde8a0cd884115c04caa59d080ba51bde1b086ce0079d
9c70f766d3b84fc2bb298efa37cc9191f28bec336329cc11468cfadbc3b137f4
eacd09517ce90d34ba562171d15ac40d302f0e691b439f91be1b6406e25f5913
3dbd2c90050b652d63656481c3e5871c52261575292db77d4ea63419f187a55b
b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
a41670d52423ba69c7a65e7e153e7b9994e8dd0370c584bda0714bd61c49c578
54241ebe651a8344235cc47afd274c080abaebc8c3a25afb95d8373b6a5670a2
bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
de6d7b7c2427ec4e738407d7834b71941f69166b030355e00f325ff1391df5a1
Domains
www.bing.com
ocsp.digicert.com
oneocsp.microsoft.com
config.edge.skype.com
msedge.b.tlu.dl.delivery.mp.microsoft.com
copilot.microsoft.com
s3.us-west-2.amazonaws.com
go.microsoft.com
google.com
edge-mobile-static.azureedge.net
settings-win.data.microsoft.com
slscr.update.microsoft.com
edge.microsoft.com
edge-cloud-resource-static.azureedge.net
clients2.googleusercontent.com
login.live.com
fe3cr.delivery.mp.microsoft.com
activation-v2.sls.microsoft.com
update.googleapis.com
nexusrules.officeapps.live.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:7sg8_fjugxkpml8ywrbm53tc02jdgjtwtpb6qfs0ea0&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://docspace-43lqak.onlyoffice.com/s/rvx4sskfph72ygy
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://docspace-43lqak.onlyoffice.com/filehandler.ashx?action=download&fileid=4989351&share=nhjxbm9tbkvldvrctemvugtorklcbnvqt0v1ekhyq2tpneztdlvaae9ubz0_ijhkmdczntgzlwe4mzatngq3nc04nti3ltniy2i1nmuzogy0nsi
https://docspace-43lqak.onlyoffice.com/storage/files/root/folder_4990000/file_4989351/v1/content.js?expire=60&auth=529097307202.euqynf7mrgsu3zdv1bay76zmegrgckeomorejixrqtq&headers=content-disposition%253aattachment%253b%2bfilename*%253dutf-8%2527%2527documento%252520judicial%252520%252520actuaci%2525c3%2525b3n%252520procesal%252520%2525e2%252580%252593%252520radicado%252520no.%2525200049595844334.js%26secure-key%253a639269981072021322-529097307202.bjdfk7i9jlxmkynpxhb1l3oijt4ih0gr7ie7ngzzi&share=nhjxbm9tbkvldvrctemvugtorklcbnvqt0v1ekhyq2tpneztdlvaae9ubz0_ijhkmdczntgzlwe4mzatngq3nc04nti3ltniy2i1nmuzogy0nsi
https://login.live.com/ppsecure/deviceaddcredential.srf
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791401304&lafgdate=0
https://s3.us-west-2.amazonaws.com/docspace.data.onlyoffice.com/61/69/64/files/folder_4990000/file_4989351/v1/content.js?x-amz-expires=15&response-content-disposition=attachment%3b%20filename%2a%3dutf-8%27%27documento%2520judicial%2520%2520actuaci%25c3%25b3n%2520procesal%2520%25e2%2580%2593%2520radicado%2520no.%25200049595844334.js&x-amz-algorithm=aws4-hmac-sha256&x-amz-credential=akia6quhbsfse5o5ydu6%2f20261007%2fus-west-2%2fs3%2faws4_request&x-amz-date=20261007t192827z&x-amz-signedheaders=host&x-amz-signature=460f610d4c8343a3de308ffb02b30afb5887c56ce042b0fd2de104dde7428325
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d292%2526e%253d1
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://update.googleapis.com/service/update2/json?cup2key=14:yl0mslico5aucy3cdjjqc2ttcaq5wzn39_7rf2wl37q&cup2hreq=209cfae9f51baae658ab674706f12ede11c89f2fe197afbe638da705fce9c0db
https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1648
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 3378
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10879
comments 0

What is AsyncRAT malware

In 2019 and 2020, researchers observed the first campaigns distributing AsyncRAT. A modified version of the malware was arriving in spam email campaigns with mentions of the Covid-19 pandemic. In another tactic, attackers impersonated local banks and law enforcement institutions. The malware was gaining popularity and, in late 2020, surfaced in numerous threads in Chinese underground forums.

In 2021, AsyncRAT was spotted in a phishing campaign called Operation Spalax. In an unrelated incident, it was dropped by an HCrypt loader. Soon after, researchers saw the first strain of AsyncRAT loading using VBScripts. And in 2022, a heavily modified version of the malware appeared, which was spread in a spear phishing campaign using an attachment that downloaded ISO files. This strain could bypass most security measures.

Because of the open-sourced nature of this malware, attackers have developed numerous alterations of AsyncRAT throughout its lifetime. In 2022, researchers found a new variant that can be distributed in fileless form. It is thought to spread through email using compressed file attachments.

AsyncRAT mainly infects victims in the IT, hospitality, and transportation industries across North, South, and Central America, though its distribution is not limited to these regions. RAT users aim to steal personal credentials or banking details and use them as leverage to demand ransom.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

How to analyze AsyncRAT malware

Researchers can analyze AsyncRAT sample, track the whole execution process, and collect IOCs in real-time using ANY.RUN sandbox.
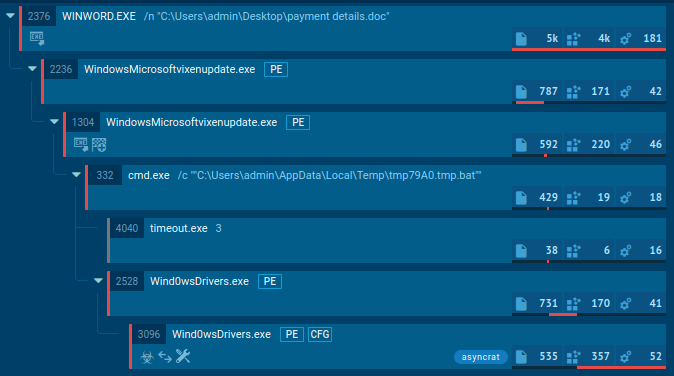
AsyncRAT process tree

Figure 1: AsyncRAT process tree in ANY.RUN

AsyncRAT execution process

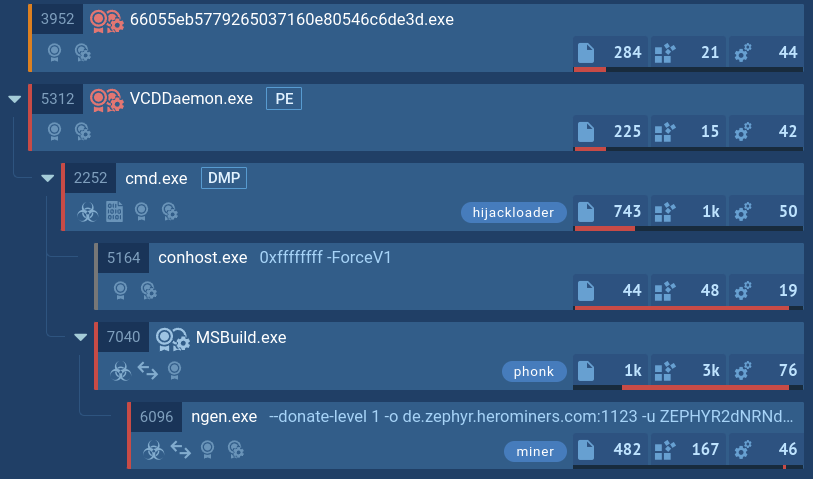
Just like any other malware, the execution process of AsyncRAT may vary and change over time and versions. As mentioned before, its open-source origin made it easy to change its functionality. The execution process is plain and straightforward, just like a lot of other malware. This RAT may make just a single process on the infected system or infects system processes.
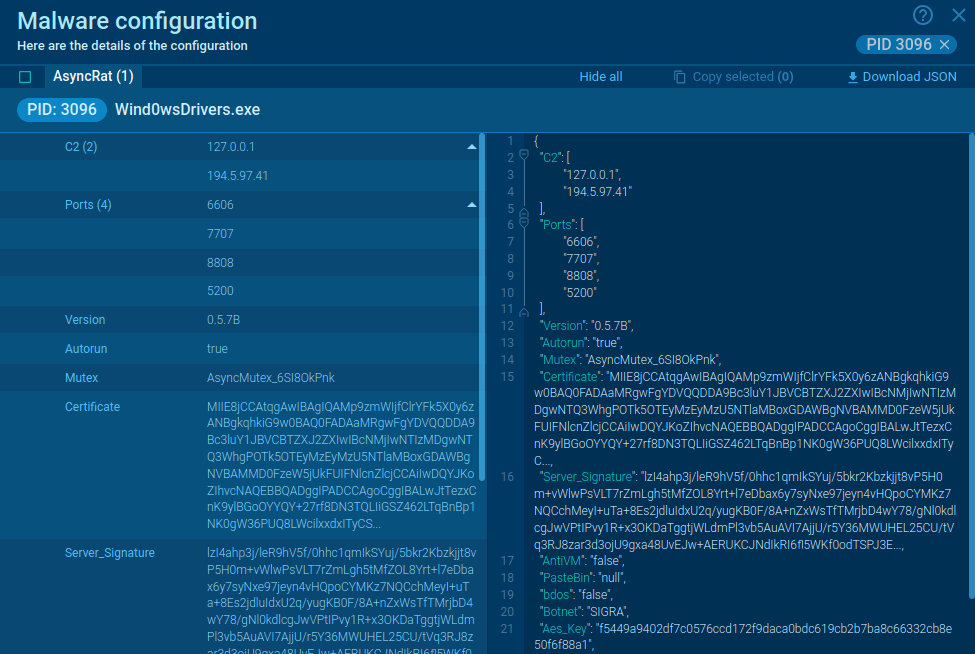
AsyncRAT malware configuration

Figure 2: AsyncRAT malware configuration extracted by ANY.RUN

In our example, the AsyncRAT execution chain started from a malicious document that dropped a payload. After that, malware added itself to autorun and made a little sleep through timeout. In the end, AsyncRAT ran itself as a child process and tried to connect to C2. Malware configuration was successfully extracted from the sample, so analysts can save a lot of time on manual steps.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

How to detect AsyncRAT using ANY.RUN?

The oldest versions of AsyncRAT were identified by writing the key and name D04F4D4D0DF87BA77AAE in the registry. The newest version of the malicious program sends the stolen info to its panel just right after the start of the execution. The detection will happen after less than a minute. Apart from that, AsyncRAT is caught by YARA rules.

Gathering threat intelligence on AsyncRAT malware

To collect up-to-date intelligence on AsyncRAT, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like AsyncRAT.
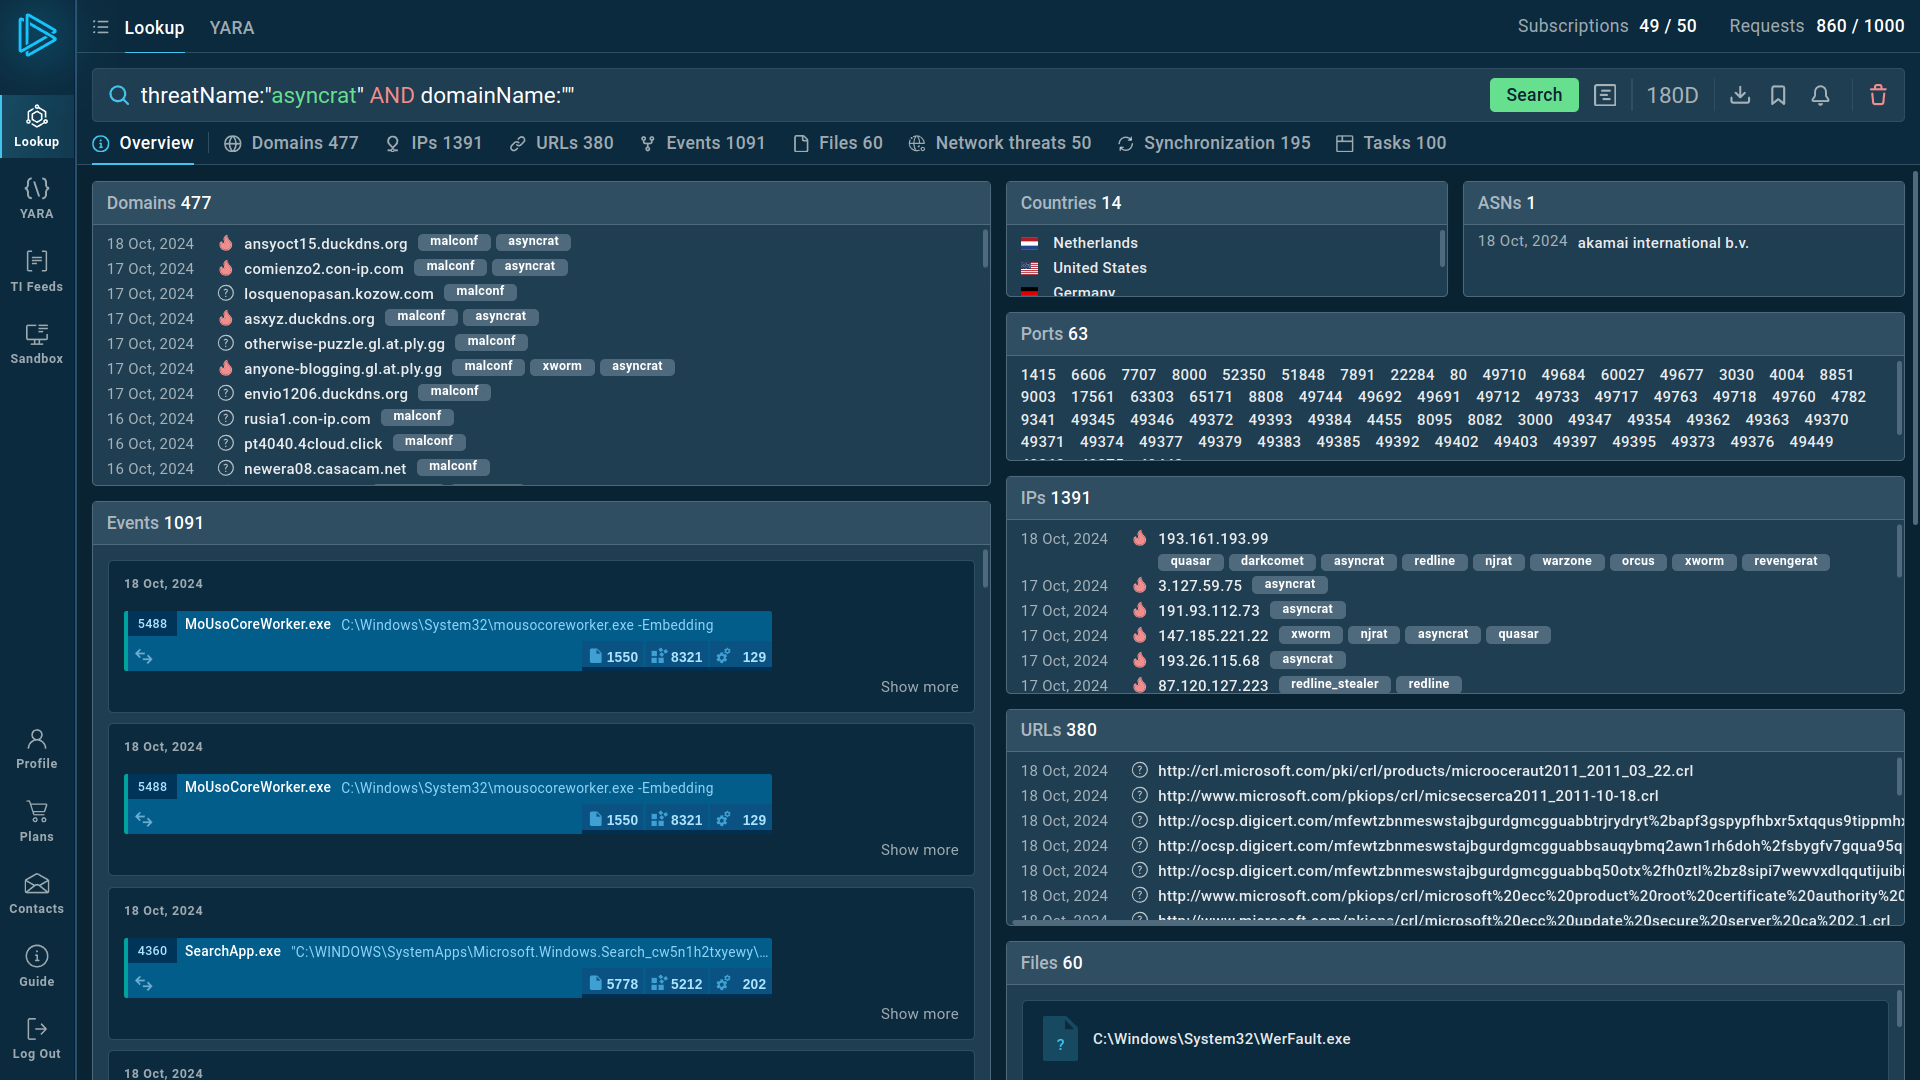
AsyncRAT ANY.RUN Search results for AsyncRAT in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"asyncrat" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from AsyncRAT samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Distribution of AsyncRAT

AsyncRAT uses a couple of distribution methods. It is usually spread with spam email campaigns as malicious attachments or via infected ads on compromised websites. Sometimes the RAT is dropped by other malware, which first infects the system through a VBS script. The Threat Analysis Unit also warned that it can arrive via exploit kits.

Conclusion

It’s difficult to say whether the original release of AsyncRAT was meant to be a harmless remote administration tool. The notes claimed that it was designed for educational purposes. But it could be that the creator simply found a clever way to market malware on a legitimate site.

Regardless of the intent, the code uploaded to GitHub already had enough malicious capabilities to cause monetary losses to organizations. Since then, it has been heavily modified to support countless distribution methods, including fileless delivery, making this RAT highly dangerous.

But researchers can easily identify any of its strains by running an analysis in ANY.RUN sandbox. It takes only 2 minutes on average to launch an emulation, diagnose AsyncRAT and collect indicators of compromise.

Create your free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

EvilTokens screenshot
EvilTokens
eviltokens
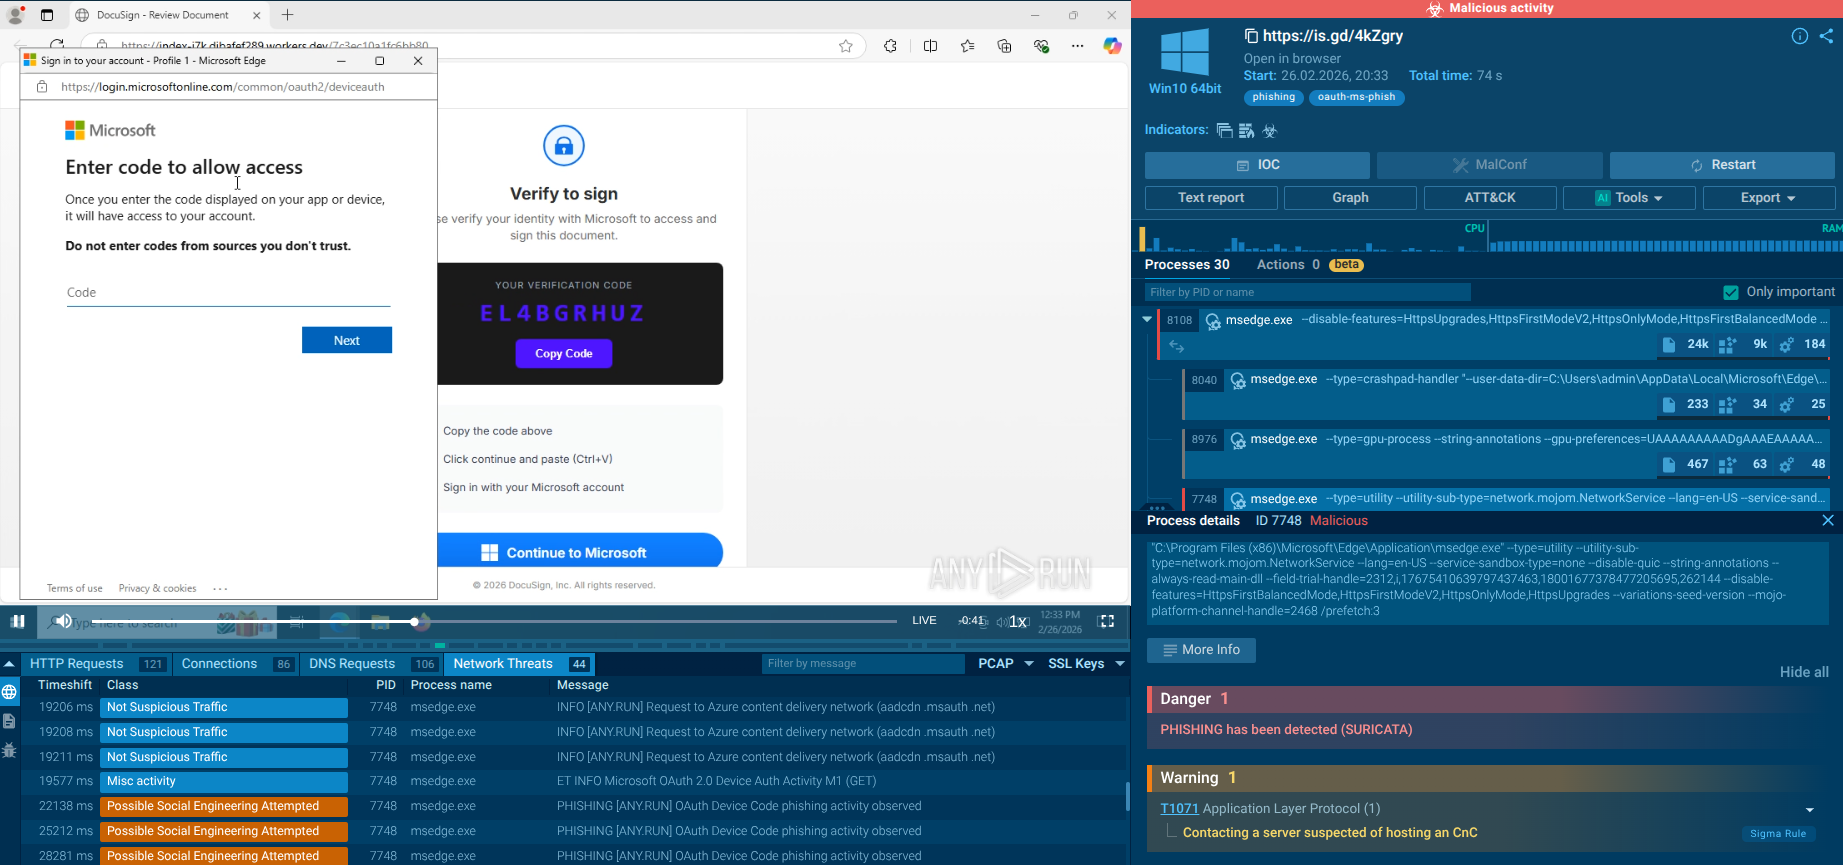
EvilTokens is a phishing-as-a-service (PhaaS) toolkit that emerged in mid-February 2026. It automates device code phishing attacks against Microsoft 365 and Entra ID environments. Unlike traditional credential-harvesting phishing, EvilTokens tricks users into completing legitimate authentication on Microsoft's own login pages, resulting in the issuance of valid OAuth access and refresh tokens directly to the attacker, effectively bypassing MFA without stealing passwords.
Read More
DonutLoader screenshot
DonutLoader
donutloader donut
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
Ramnit screenshot
Ramnit
ramnit
Ramnit is a highly modular banking trojan and worm that evolved from a file-infecting virus into a powerful cybercrime tool. It specializes in financial fraud, credential theft, remote access, and malware delivery, being a serious threat to businesses and individuals. First spotted in 2010, Ramnit became popular after the 2014 takedown of the GameOver Zeus botnet, as cybercriminals sought alternatives for banking fraud.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More