Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
98
Global rank
124 infographic chevron month
Month rank
109 infographic chevron week
Week rank

Arkei is a stealer type malware capable of collecting passwords, autosaved forms, cryptocurrency wallet credentials, and files.

Stealer
Type
ex-USSR
Origin
21 May, 2018
First seen
9 October, 2026
Last seen
Also known as
ArkeiStealer

How to analyze Arkei with ANY.RUN

Type
ex-USSR
Origin
21 May, 2018
First seen
9 October, 2026
Last seen

IOCs

IP addresses
20.190.160.64
74.178.76.128
48.209.138.168
23.52.181.212
172.211.123.249
74.178.76.54
95.100.158.114
48.192.1.64
150.171.109.106
23.209.214.100
48.192.1.65
2.16.241.227
48.209.138.189
95.100.102.101
23.48.23.146
172.211.123.248
57.153.246.3
48.209.133.15
128.24.231.65
23.219.160.19
Hashes
d5cf930756370de6c8bc9e98003056761655b80e4ad0337602ad0d33740a6d8f
772c8625cde6caf1573e9e61f43a9cdcda1e9d957c67f190a9685ddc036df1f7
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
c001b2c8b46b34e555f329a8885b3e0014b6dfeb686ba8445177764487792d72
9bc533130a44071a690cc5b8e18db9157fb40c7d9b82fb6bae2ee00b3218fd6f
08bf3d453bda53f92992c6ca94098e158f805db3f68ec921d5e24cd90380d452
c08f2ebdc5adecfb67ffd9de298a8e7cf40851be01bde6f914d383c807100be2
9012e5f8c8b9986e8d9968f62da444464cc7db57811ff48b21c5f5f2cb516622
5c42497a3b2529d5d469a02bf5e32dac5696cbe2d443a1c75b5fc59f3502b370
d4a3cd4cedbc1987396dfcf571fb5c2a7184546824503d0c44a382bf56e0fcde
8f976956cac14dd16a76f89d51febd5606a0748cafb06f0587218451b571a86c
6b892e17d86f74e9131cb4b796ed8162ce63242c475beb88cae8eec59c77fa8d
a4b4d8e028939cb7848f2b0a0a434520f18d6ec1e72bed4d8c764be2f91e6b54
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
e908466af6563b62d8f8c4bc870beb33b8fdb8682bf7c775a40ea1c6a8f49bf5
0e24672ae24a06f2c30bfeaa1c72bdd0916285097115fb105ef00b7c926375a7
54a5ec6205c8e24ca57013f57ffc10f374ddfc91b2187eff643be92f5e7fd602
6f20d866841c4514782a46142df22b70b8da9783c513e3d41d8f3313483fe38d
a3acc39d4b61f9cc1056c19176d1559f0dacbb0587a700afdbe4d881040ccd52
Domains
google.com
crl.microsoft.com
login.live.com
www.microsoft.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
slscr.update.microsoft.com
www.bing.com
activation-v2.sls.microsoft.com
client.wns.windows.com
ecs.office.com
self.events.data.microsoft.com
nexusrules.officeapps.live.com
watson.events.data.microsoft.com
go.microsoft.com
ocsp.digicert.com
oneocsp.microsoft.com
pagefinder52.uz
validation-v2.sls.microsoft.com
startolete-vn.ug
URLs
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.1.crl
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
Last Seen at

Recent blog posts

post image
Fake AI Tools Put US Companies at Risk: Insid...
watchers 688
comments 0
post image
What's Really Attacking Your Industry? Insigh...
watchers 2281
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 10095
comments 0

What is Arkei malware

Arkei is a stealer designed to exfiltrate information from infected systems. Typical for this malware type, it is distributed using Malware-as-a-Service (MaaL) model, which means that anyone can use the malware with minimal technical knowledge — all you need is to purchase access to a control pane from a website that sells the service.

This malware — which is written in C++ — targets Windows systems and is considered a medium impact and medium risk threat.

Having been around since 2018, Arkei has become popular among adversaries: not only is it widely used, but it has spawned several forks including Mars, Oski, and Vidar stealer, which we have covered before in the ANY.RUN trends trackers.

Arkei is capable of retrieving a variety of information from infected machines, including:

  • Form autosaves stored in the browser
  • Login and passwords
  • Files
  • Cryptocurrency wallets

Cryptocurrency owners are at the highest risk and are the main targets of Arkei. It can extract data from around 40 crypto wallet extensions, including MetaMask that accounts for over 80% of web3 wallet usage.

The stealer also targets more than 30 web browsers, including Chrome, Firefox, Microsoft Edge, Opera, Brave, and TOR.

Arkei can also target 2FA extensions, a capability it has had roughly since the beginning of 2022. It's unclear how attackers are planning to use this data, but it's certain that this development could pose new risks for both corporate and private users.

The specific data types that the malware targets depend on its configuration file — a ​​Base64-encoded file with the .PHP extensions — and will vary from campaign to campaign. The attacker can use it to set Arkei's behavior with custom rules, and target specific information.

It is important to note that Arkei terminates execution on machines from the ex-USSR regions.

The stealer identifies the region by accessing the language identifier of the Region Format setting. This behavior is typical for malware originating from the ex-USSR territories, which gives an insight into Arkei’s origin.

Arkei is equipped with multiple evasion techniques that help it avoid detection. For example, it checks that the computer name is not set to ​ “”HAL9TH”” and the username to “”JohnDoe” — these are the default settings of the Windows Defender emulator. It also checks if several DLLs are loaded in a process against a list of antivirus and emulation software.

Once it's time to gather the data, Arkei compiles its findings into a .zip archive, gives it a random 12-character name, and sends it to its control server. In addition to the information specified by the config file, it captures a system screenshot and extracts system information.

How to get more information from Arkei malware

You can obtain Arkei’s malware configurations in the ANY.RUN's sample.
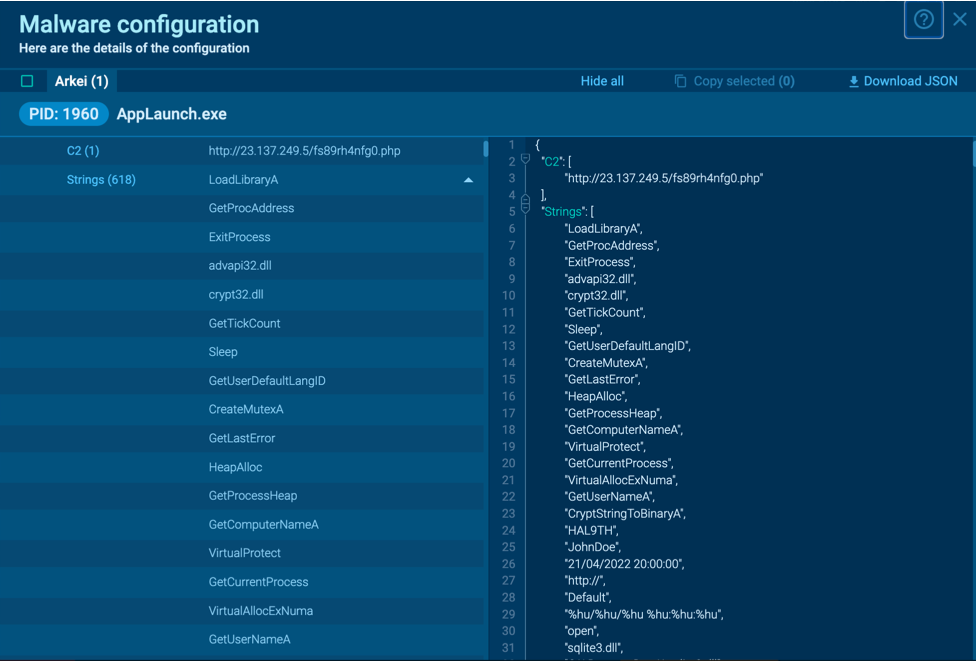
Malware configuration of Arkei stealer Figure 1: Arkei configuration automatically extracted by ANY.RUN

Users can access comprehensive malware configuration data on ANY.RUN interactive online sandbox in as little as 10 seconds after starting the sandbox. There's no need to wait for the emulation to finish running.

Arkei execution process

After a system is infected, a TCP connection is established with the hacker's remote server. The server sends encoded Base64 parameters to the malware, including search path templates and file search masks. Using these parameters, the malware determines which information it needs to steal from the victim's computer.

The malware then requests the libraries necessary for its operation from the remote server. These libraries are sent as ZIP archives.

Subsequent communication with the server involves sending stolen files to the C2 server. Some threat actors use packing techniques on Arkei samples (T1027.002) to avoid detection by signatures. An example of this behavior can be seen in this task we recorded in ANY.RUN.

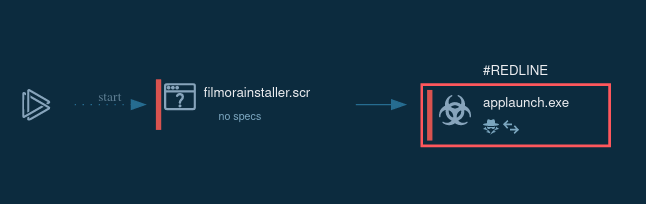
After launching the packed sample, the AppLaunch.exe process is created in the system, which is part of the .NET Framework. The malicious code is then injected into this process.

Distribution of Arkei

Arkei finds its victims in a number of ways. It’s delivered with malicious email campaigns in infected attachments, distributed through malicious ads, and is sometimes found in cracked software.

Adversaries use trojan horse tactics to entice potential victims into installing Arkei to their systems: social engineering techniques can be utilized, such as offering a free version of a premium software.

Arkei has also been tied to campaigns utilizing SmokeLoader — an advanced modular malware used to gain an initial foothold in the system and drop other executables. Although Smoke Loader, as you probably have guessed from its name, is primarily used as a loader, it can be armed with information stealing functionality itself — double the threat, when used together with Arkei.

Conclusion

Arkei is a that poses a significant risk to users' sensitive data, particularly crypto wallets.

But users can keep their login and password information, files, and 2FA data secure by following these best practices:

  • Avoiding clicking on suspicious links
  • Being vigilant with emails from unknown senders
  • Staying clear from lurid ads
  • Being mindful where they download software from

You can identify and analyze threats like Arkei — and more — in a matter of minutes using ANY.RUN’s interactive sandbox. Sign up for a demo!
HAVE A LOOK AT

Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
Bluesky Ransomware screenshot
BlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
Read More
Stealer screenshot
Stealer
stealer
Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns.
Read More