Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Grandoreiro

58
Global rank
24 infographic chevron month
Month rank
15 infographic chevron week
Week rank

Grandoreiro is a Latin American banking trojan first observed in 2016. It targets mostly Spanish-speaking countries, such as Brazil, Spain, Mexico and Peru. This malware is operated as a Malware-as-a-Service (MaaS), which makes it easily accessible for cybercriminals. Besides, it uses advanced techniques to evade detection.

Trojan
Type
Unknown
Origin
1 August, 2017
First seen
9 October, 2026
Last seen

How to analyze Grandoreiro with ANY.RUN

Type
Unknown
Origin
1 August, 2017
First seen
9 October, 2026
Last seen

IOCs

IP addresses
150.171.27.11
23.52.180.165
52.123.129.14
172.211.123.249
52.110.17.48
169.58.45.190
169.58.43.82
18.211.136.6
52.90.61.121
150.171.109.106
52.110.17.61
2.23.244.205
48.192.1.65
52.111.236.4
172.211.123.248
150.171.22.17
48.209.138.168
204.79.197.203
142.251.156.119
150.171.28.11
Hashes
bbe0867984fd439067703f307018f96ea37fda8f8b79fc12843d6068e77dcc32
6f4ece9eef5c4e518ad56a6f82d14e95f93e4e5d07b1cb8d22de8666d7ac3d7f
4256488766553496d02c7dc5868938e34f24028f9841a5021560781e6f5b8d6e
298999caaa697082b5fd80903b1966482f211c921ab1ff74bb239c0db3337022
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
0d5464c80566b2945c7a04afcf792fa8f760279f8bf0d52e3dbd96f642c9821e
49ac386ee6d11314016f0990b0b9e95f8616dfa889f6cf131ba805132f16fc89
3a5078b626e41d20117d260d8b825b039884cfe062c6d462432216d9b07d82b5
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
3ad368c74c9bb5da4d4750866f16d361b0675a6b6dc4e06e2edd72488663450e
6034f27b0823b2a6a76fe296e851939fd05324d0af9d55f249c79af118b0eb31
eacd09517ce90d34ba562171d15ac40d302f0e691b439f91be1b6406e25f5913
3dbd2c90050b652d63656481c3e5871c52261575292db77d4ea63419f187a55b
b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
Domains
ocsp.digicert.com
www.bing.com
xpaywalletcdn.azureedge.net
acroipm2.adobe.com
roaming.svc.cloud.microsoft
edge-cloud-resource-static.azureedge.net
client.wns.windows.com
www.mediafire.com
login.live.com
kygbuz.com
ecs.office.com
oneocsp.microsoft.com
slscr.update.microsoft.com
messaging.engagement.office.com
self.events.data.microsoft.com
dns.google
config.edge.skype.com
clients2.googleusercontent.com
123pdfonline.com
edge.microsoft.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:rbworwphclmpeu17afd_ly3u27zgwy70fl9p9v8sfcq&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
http://share.google/opvrd8y8jb2gvuk3c
http://kygbuz.com/
http://kygbuz.com/gojobttyp05q.php?tipo=inv&yj9=%2f&1d=1791581013&s1=7485a21337c4072122e0af8d5108ac7305aad4272183cbbe0847943700092bb8
http://kygbuz.com/lyojtdysnp07b.css
http://kygbuz.com/favicon.ico
http://kygbuz.com/gojobttyp05q.php?tipo=vis&yj9=%2f&1d=1791581015&s1=4931cd738d7b83e2f3ca5cb1755788abbadf2856c8aeef3de9e563d660a2e071
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://copilot.microsoft.com/c/api/user/eligibility
https://www.google.com/share.google?q=opvrd8y8jb2gvuk3c
https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
https://xpaywalletcdn.azureedge.net/mswallet/expresscheckout/v1/getglobalconfig?edgechannel=stable&edgeversion=133.0.3065.92&configversion=0
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791581011&lafgdate=0
https://edge.microsoft.com/autofillservice/core/page/3780139929063086240/1549548158549168445?cidalgoversion=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 4661
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 6629
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 9796
comments 0

What is Grandoreiro malware?

Grandoreiro is a sophisticated banking trojan first observed in 2016, primarily targeting users in Latin America, including countries like Brazil, Mexico, and Argentina.

Grandoreiro is known for its advanced evasion techniques, including various string encryption methods, and the use of a domain generation algorithm (DGA) that enables it to communicate with multiple command-and-control (C2) servers.

In March 2024, the Grandoreiro banking trojan launched a massive attack targeting over 1,500 banks' applications worldwide, expanding beyond its usual Latin American focus to regions in Central and South America, Europe, Africa, and the Indo-Pacific.

Attacks usually begin with phishing campaigns impersonating government entities, tricking recipients into downloading the malware. Once deployed, Grandoreiro targets specific banking applications, allowing attackers to steal credentials and execute fraudulent transactions.

Key technical features of Grandoreiro include its ability to evade detection, verify victims to avoid sandbox environments, and more. The malware’s sophisticated structure and its ability to adapt to different regions and targets make it a significant threat in financial cybercrime.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Grandoreiro malware technical details

The main functionality of Grandoreiro malware is to steal sensitive financial information of users by targeting banking applications.

Some of the key capabilities of the Grandoreiro malware include:

  • Initiating attacks through sophisticated phishing campaigns impersonating government and financial institutions.
  • Utilizing a loader that verifies targets, collects data, and downloads the main banking trojan payload.
  • Employing techniques such as file bloating, CAPTCHA pop-ups, and environmental checks to avoid detection by security tools.
  • Targeting banking applications to steal credentials and perform fraudulent transactions.
  • Using a reworked Domain Generation Algorithm (DGA) to connect with multiple command-and-control servers, enabling efficient management of large-scale attacks.
  • Harvesting email addresses from infected hosts and uses Microsoft Outlook to send additional phishing emails, spreading the malware further.
  • Establishing persistence through registry modifications and the creation of configuration files on the victim's machine.

Grandoreiro is a complex malware with over 10,000 strings, which would be easily detectable if left unencrypted. To avoid detection, it uses a sophisticated multi-step decryption process. This involves custom encoding and decryption using the same key as the loader, followed by AES decryption, and then further decoding to finally reveal the plaintext strings, making the malware harder to detect and analyze.

Grandoreiro execution process

To see how Grandoreiro operates, let’s upload its sample to the ANY.RUN sandbox for analysis.

Grandoreiro is typically delivered through phishing emails containing malicious links or attachments. These emails often impersonate legitimate organizations, such as government agencies, to deceive victims. Clicking on the link or opening the attachment downloads a malicious ZIP file containing the Grandoreiro loader, disguised as a PDF or another benign file.
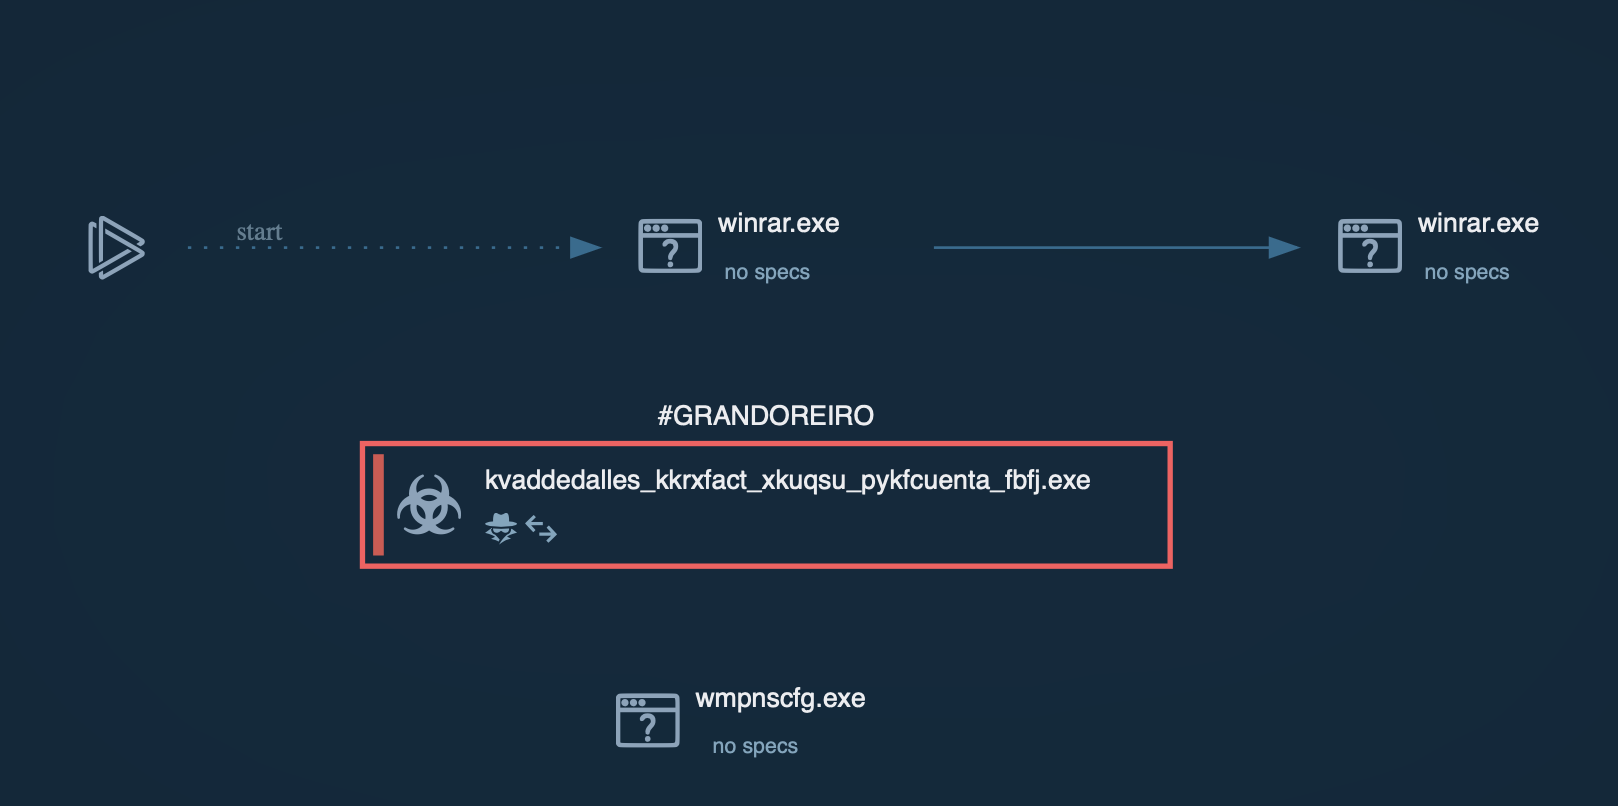
Grandoreiro report in ANY.RUN Grandoreiro process graph displayed in ANY.RUN sandbox

Once executed, the loader performs anti-analysis checks to detect sandboxes and virtual environments. It collects victim information, including IP address, operating system details, installed software, and more. The loader then decrypts a URL using XOR-based decryption and sends a GET request to retrieve the final payload download URL.

The loader downloads the final Grandoreiro payload from the retrieved URL as a large ZIP file. This ZIP file contains a massive executable disguised as an image or PDF file. Then, the loader extracts and renames the executable to a random name with an .exe extension. This renamed executable is the full Grandoreiro banking trojan payload, often signed with a legitimate digital certificate to appear trustworthy and evade detection.
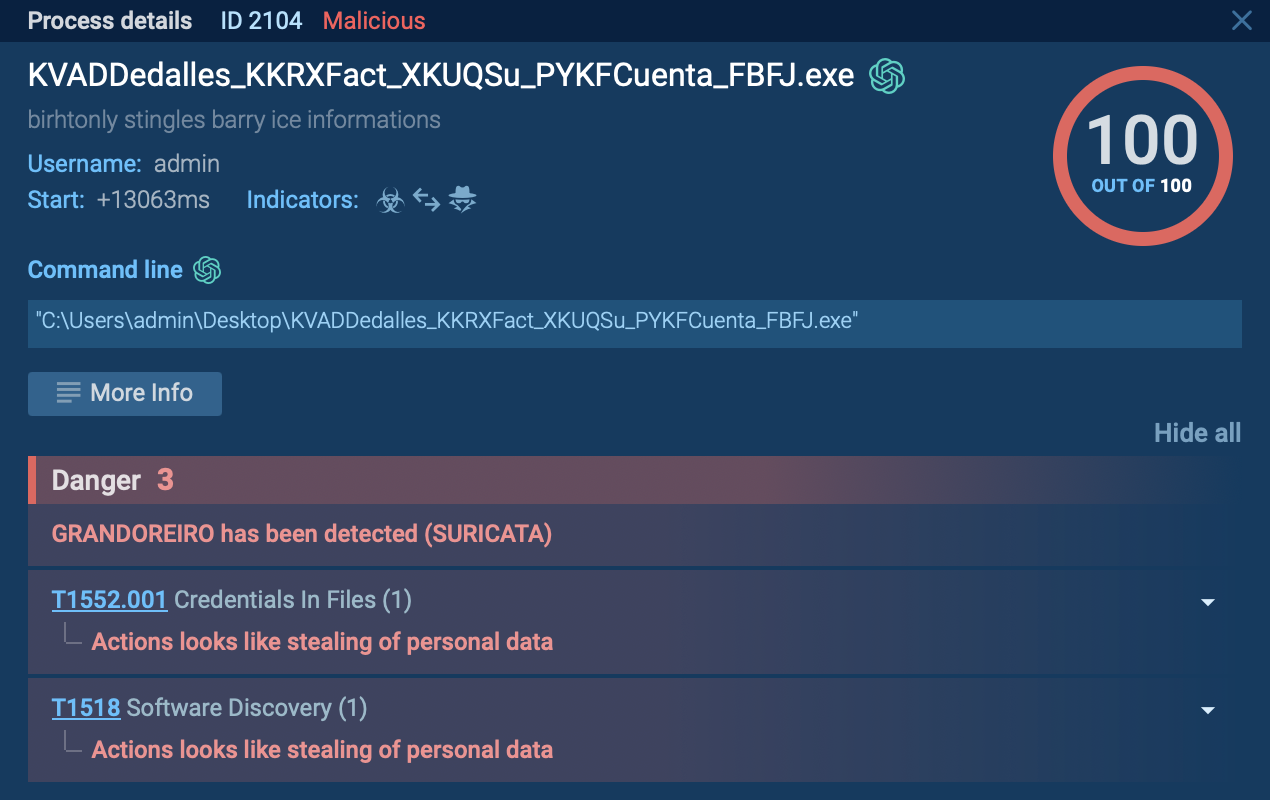
Grandoreiro process in ANY.RUN Malicious process related to Grandoreiro analyzed in ANY.RUN sandbox

Grandoreiro establishes persistence via the Windows registry, ensuring it launches upon user login. It collects more detailed information and sends a POST "check-in" request to the command and control (C2) server with the gathered data. The trojan then proceeds to carry out a range of malicious activities, including browser session hijacking, credential theft, and banking fraud.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Grandoreiro malware distribution methods

Grandoreiro malware is primarily distributed through phishing campaigns.

Attackers often send emails that impersonate legitimate government entities or financial institutions, tricking recipients into clicking on malicious links or downloading infected attachments. These emails may claim to contain important documents, such as tax notices or account statements, which, when opened, initiate the download of the malware.

In addition to phishing emails, Grandoreiro may also be spread through malicious websites that prompt users to download fake software updates or security tools, which actually install the malware.

Conclusion

The impact of the Grandoreiro campaign has been devastating, leading to widespread financial fraud and significant monetary losses. This malware has infiltrated multiple sectors, including banking, finance, manufacturing, public administration, telecommunications, and energy. Its ability to steal sensitive financial information and perform fraudulent transactions has caused severe disruption and harm to countless organizations and individuals, making it one of the most dangerous banking trojans in recent years.

ANY.RUN is a cloud-based service that allows anyone to safely analyze suspicious files and URLs. It enables you to observe malware behavior and collect indicators of compromise in a secure environment. By using ANY.RUN, you can gain valuable insights into Grandoreiro's tactics and improve your defenses against it.
Create your ANY.RUN account – it’s free!

HAVE A LOOK AT

Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More
Sliver screenshot
Sliver
sliver
Sliver is an open-source command-and-control (C2) framework that has been increasingly adopted by threat actors as an alternative to tools like Cobalt Strike. Developed by security firm Bishop Fox, Sliver was initially intended for legitimate security testing and red teaming exercises. However, its robust features and open-source nature have made it attractive to malicious actors seeking to control compromised systems.
Read More
SnappyClient screenshot
SnappyClient is a sophisticated C++-based command-and-control (C2) implant first identified in December 2025. Delivered primarily via the modular HijackLoader, it functions as a versatile remote access tool with strong information-stealing capabilities, particularly focused on cryptocurrency wallets, browser data, and system control. It employs advanced evasion techniques, encrypted communications, and modular configurations to maintain persistence and evade detection.
Read More
Virlock screenshot
Virlock
virlock
Virlock is a unique ransomware strain that combines encryption capabilities with file infection techniques. First observed in 2014, it stands out due to its polymorphic nature and ability to embed its code into compromised files, ensuring continued propagation. Once it infects a system, it encrypts files and locks the screen, demanding a ransom for file recovery and system access.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More