Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
18
Global rank
139 infographic chevron month
Month rank
136 infographic chevron week
Week rank
0
IOCs

Netwire is an advanced RAT — it is a malware that takes control of infected PCs and allows its operators to perform various actions. Unlike many RATs, this one can target every major operating system, including Windows, Linux, and MacOS.

Trojan
Type
ex-USSR territory
Origin
1 January, 2012
First seen
2 September, 2026
Last seen
Also known as
Recam

How to analyze Netwire with ANY.RUN

Type
ex-USSR territory
Origin
1 January, 2012
First seen
2 September, 2026
Last seen

IOCs

IP addresses
48.209.133.15
74.178.76.128
128.24.231.65
40.126.32.134
2.23.246.9
48.209.138.168
172.211.123.249
162.159.36.2
74.178.240.51
184.86.251.25
103.53.199.247
48.209.6.48
88.221.169.205
48.209.138.189
2.16.241.218
74.178.240.61
20.190.160.128
23.11.41.157
172.211.123.248
2.16.241.9
Hashes
03385d9bbefa32f7cdb8d95ba645e52b24261957be87e9d676ef1a7698042929
1dc75220bb88f51c4b5360302d9a27e2c2b4371fd9bf7a4ea22fb473b7c2dc6c
47d9ca64d909654ea8d9cdbf84904c6e109abd5161f9d79bcb029deb337e783b
e84502550a89ff9ad1dd5587000e9e5ff2e3ee0b8563e4c054c4b5e37e5e9d18
98617be63240765a49a2f4b0d677c02e77cb91850008a7a77265b977f172918e
12f0eed74bedd614dafa175f7bd5b66ca6f3cf504ebfe4daa19283ea9b8f13ac
63b49fe447e171f5b4d0e456d4374ddb7658089abbbdfde9dabd6311d4fb8838
af7e05d7b623daab69b92125e2ceba70210a538fca6a8d69d728bb8064869a9e
1967da158234d42db7bddffea780b95eacb916af2731194a2369650ac66ae7ba
e96b397b499d9eaa3f52eaf496ca8941e80c0ad1544879ccadf02bf2c6a1ecfc
eabb8ddf53271041e413cd14bc57acee8687a54ddc89c8896905e0caebc3422b
e2e4d97c20d4478e8e947480c8f6c71a2c795776d405366be70db82e4ea4ba77
4f1bad1a6b9e00473d885bf4e7f3d9d0ec3d91cbdce05b46f6c6cb2d1fca8c2b
dac5a4213654cae1aa622877e7e156c0efd77c0601440df7ce9995e280df8694
5d84ec3f8dee7438b0049d5dc201a68a99f3e471a4c9acac48dd7f67f89fd178
148b8755d228f174f4dbd0b8454e3825f34e6d6e055341d4c3981c2bb7664c07
ef463b4c9e431d3760dd9c203e630fb410f07bdf626ba4739fda8a8f0233ad76
ec94ffbda11b4f750ea732a9986b6dd60d4c87978f810f27336abf4ee178bc03
58c92ae2de19a77bea6f8a934fc317310e33030c93a01205bb375cbae3e5706d
71e16a8c9540cbeb6afc80045a21f7c5954f9e54b5ec731c93afca6d67a61646
Domains
fe3cr.delivery.mp.microsoft.com
go.microsoft.com
www.bing.com
google.com
client.wns.windows.com
settings-win.data.microsoft.com
login.live.com
activation-v2.sls.microsoft.com
slscr.update.microsoft.com
ytferkuygefkuygfe.duckdns.org
www.microsoft.com
crl.microsoft.com
ocsp.digicert.com
oneocsp.microsoft.com
nexusrules.officeapps.live.com
self.events.data.microsoft.com
th.bing.com
edge.microsoft.com
ep1.adtrafficquality.google
region1.google-analytics.com
URLs
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://settings-win.data.microsoft.com/settings/v3.0/waas/featuremanagement?isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&currentbranch=vb_release&accountfirstchar=&activationchannel=retail&oemmodel=dell&flightring=retail&attrdataver=186&installlanguage=en-us&osuilocale=en-us&webexperience=1&flightingbranchname=&chassistypeid=1&osskuid=48&app=cdm&installdate=1661339444&appver=&osarchitecture=amd64&defaultuserregion=244&telemetrylevel=1&osversion=10.0.19045.4046&devicefamily=windows.desktop
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/ping
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaagb6jmmcovb6saaaaaaay%3d
Last Seen at

Recent blog posts

post image
ANY.RUN Secures Leader Status in G2’s Malware...
watchers 4744
comments 0
post image
15 Minutes Saved Per Alert: How a Lean German...
watchers 9543
comments 0
post image
HVNC Backdoor Targets LATAM Organizations wit...
watchers 11471
comments 0

What is Netwire RAT?

Netwire is a remote access trojan-type malware. A RAT is malware used to control an infected machine remotely. This particular RAT can perform over 100 malicious actions on infected machines and can attack multiple systems, including Windows, Apple’s MacOS, and Linux.

Netwire malware is available for purchase on the darknet in the underground hacking communities, where attackers can buy this RAT for the price of 40 to 140 USD. In addition, Netwire can be purchased on the surface internet for a price of 180 USD. Notably, in 2016 Netwire received an update that added the functionality to steal data from devices connected to the infected machine, such as USB credit card readers, allowing Netwire to perform POS attacks.

General description of Netwire RAT

Netwire Trojan core functionality allows this malware to take remote control of infected PCs, record keyboard strokes and mouse behavior, take screenshots, check system information, and create fake HTTP proxies.

The keylogger functionally allows Netwire to record various personal data imputed on a computer connected to the internet or a corporate network. Combined with the ability to steal credit card information and operate undetected for extended periods of time, Netwire RAT is truly capable of inflicting serious dangers to organizations.

In some malicious campaigns, the Netwire trojan was used to target healthcare and banking businesses. The malware was also documented as being used by a group of scammers from Africa who utilized Netwire to take remote control of infected machines.

Netwire RAT creators have put in a lot of work to ensure that researchers have a hard time analyzing this malware, as many precautions are taken to complicate the research process, including techniques like multiple data encryption layers and string obfuscation. In addition, the malware uses a custom C2 binary protocol that is also encrypted, and so is the relevant data before transmission.

During one campaign, researchers have observed Netwire being distributed as “TeamViewer 10” – named so in an effort to trick victims into thinking that they have downloaded the legitimate remote assistance software. Once the execution process began, this version would drop an .EXE file and start establishing persistence right away. The malware created a Windows shortcut in the Startup menu to ensure that the Netwire trojan would always run when the user logged into the system. Interestingly, another trick designed to keep the malware hidden actually gave it away during this particular campaign. The malware would inject its code into the Notepad.exe, unveiling its presence since it’s not normal for the notepad to have an always active network connection. Only after decoding the data prepared for transmission to the C2, the sensitive nature of the stolen information was discovered. Unfortunately, researches did not reveal what the organization was targeted in this particular attack.

Netwire RAT malware analysis

A video simulation recorded on ANY.RUN enables researchers to study the lifecycle of the Netwire in a lot of detail and works like a tutorial.
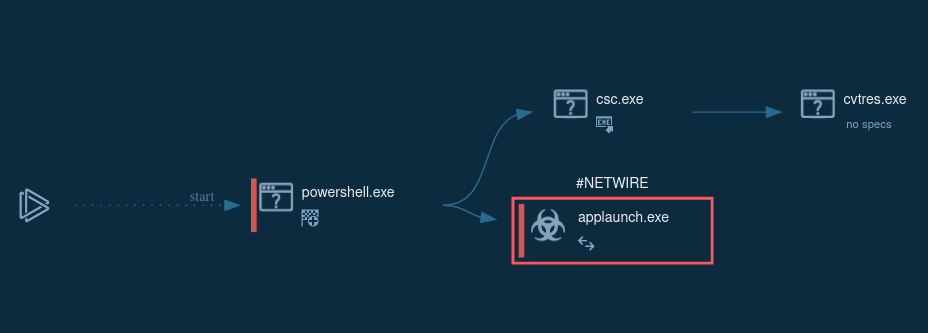
process graph of the Netwire execution Figure 1: Process graph generated by ANY.RUN allows visualizing the life cycle of Netwire
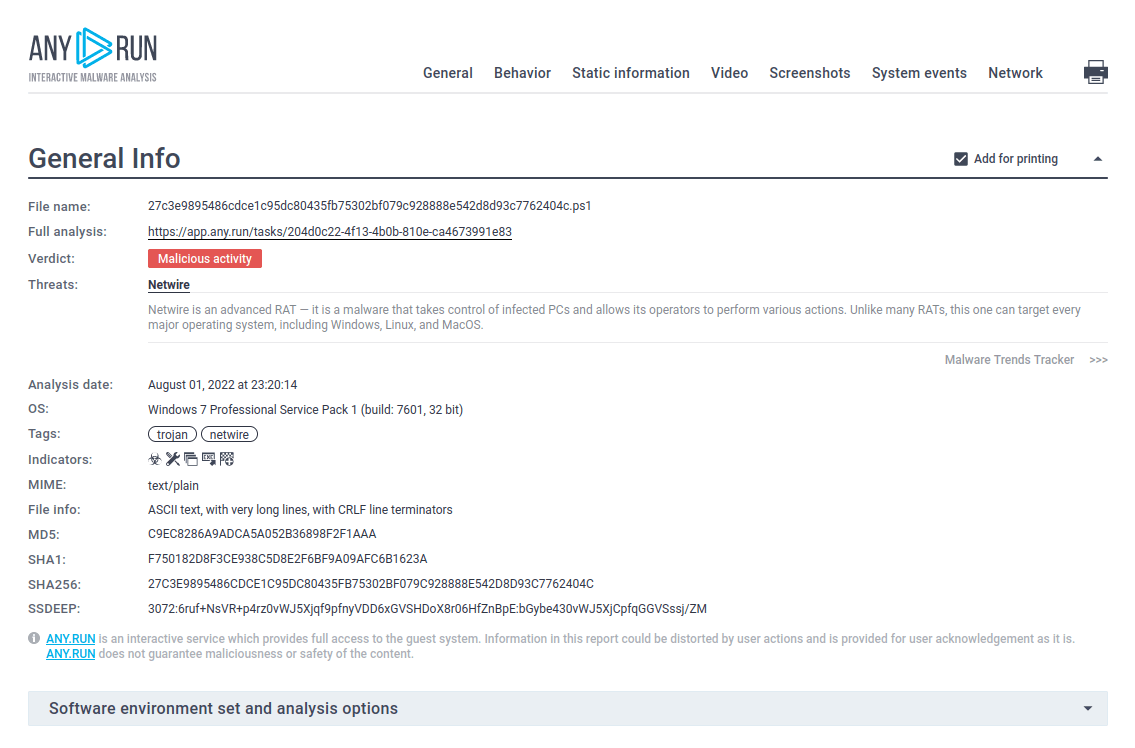
a text report of a netwire analysis Figure 2: A text report generated by ANY.RUN is a great tool to share the research results

Netwire RAT execution process

Netwire isn't as exciting as some other malicious programs can be as far as malware execution goes. It makes its way into the device, mostly in the form of a payload.

The user receives a spam email with an attached Microsoft Word file. After the user downloads and opens this file, the executable is dropped or downloaded onto the machine. After that, the executable starts performing the main malicious activity such as writing itself in autorun, connecting to C2 servers, and stealing information from an infected device. Netwire also has the ability to inject into unsuspicious processes from which it can perform malicious activities.

Distribution of Netwire RAT

Netwire RAT is usually being distributed in email phishing campaigns in the form of a malicious Microsoft Office document. The victim must enable macros for the RAT to enter an active state. The macros then proceed to download Netwire, allowing the malware to start the execution process.

How to export Netwire data using ANY.RUN?

If analysts want to do additional work with events from tasks or share them with colleagues for tutorials, they can export to different formats. Just click on the "Export" button and choose the most suitable format in the drop-down menu. Export of any kind of malware research is available including Predator the Thief or Qbot.
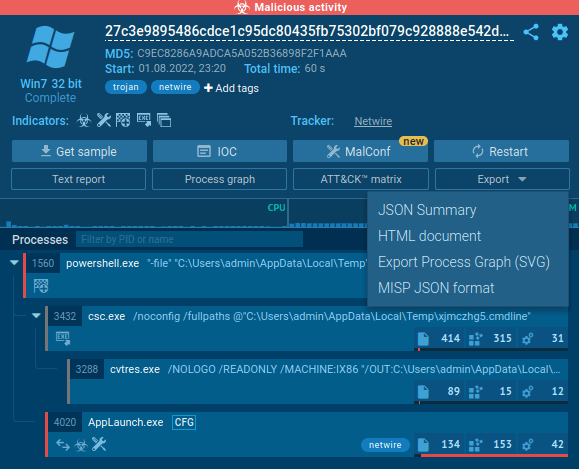
Export options for netwire malware Figure 3: Export options for netwire malware

Conclusion

Diverse information stealing feature sets combined with the ability to target multiple operating systems and steal data from credit cards used in an infected system make Netwire Trojan a highly dangerous remote access trojan.

Despite its impressive functionality, the malware is fairly accessible, “retailing” on underground forums for as little as 40 dollars in some select cases. The situation is further worsened by the fact that creators of Netwire RAT have implemented several features designed to complicate the analysis as much as possible.

However, researchers can take advantage of interactive malware hunting services, such as ANY.RUN, which allows to influence the simulation at any point and get much purer research results.
HAVE A LOOK AT

Razr screenshot
Razr
razr
Razr is a destructive ransomware that infiltrates systems to encrypt files, rendering them inaccessible to users. It appends the ".razr" extension to the encrypted files and drops a ransom note, typically named "README.txt," instructing victims on how to pay the ransom to obtain the decryption key. The malware often spreads through phishing emails with malicious attachments or by exploiting vulnerabilities in software and operating systems. Razr employs strong encryption algorithms, making it challenging to decrypt files without the attackers' key.
Read More
RondoDox screenshot
RondoDox
rondodox
RondoDox is an emerging Linux-based botnet malware that exploits dozens of known vulnerabilities in internet-facing devices like routers, DVRs, and web servers to build massive networks for DDoS attacks, cryptomining, and data exfiltration. First spotted in mid-2025, its "exploit shotgun" tactic (firing multiple payloads at once) has made it a rapid escalator in the IoT threat landscape, compromising unpatched edge devices worldwide.
Read More
WannaCry screenshot
WannaCry
wannacry ransomware
WannaCry is a famous Ransomware that utilizes the EternalBlue exploit. This malware is known for infecting at least 200,000 computers worldwide and it continues to be an active and dangerous threat.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More