Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

DarkCloud

58
Global rank
83 infographic chevron month
Month rank
96 infographic chevron week
Week rank

DarkCloud is an infostealer that focuses on collecting and exfiltrating browser data from the infected device. The malware is also capable of keylogging and crypto address swapping. DarkCloud is typically delivered to victims’ computers via phishing emails.

Stealer
Type
Unknown
Origin
1 November, 2022
First seen
2 October, 2026
Last seen

How to analyze DarkCloud with ANY.RUN

Type
Unknown
Origin
1 November, 2022
First seen
2 October, 2026
Last seen

IOCs

IP addresses
23.52.181.141
48.209.138.189
48.209.133.15
48.209.138.168
23.52.181.212
20.190.159.131
74.179.77.204
149.154.166.110
23.11.41.157
172.211.123.248
48.192.1.64
23.48.23.33
23.48.23.31
192.124.249.117
135.233.95.135
23.209.209.135
162.55.60.2
135.232.92.137
188.114.96.3
40.126.32.72
Hashes
5b8cd38cfdf83e8d0a46af7c34ecb2962621aa69f6eb8458e7c86ac7a66a2948
225d669e47eb14d8c969799c92aaef27b66cd984872ea09284e48db46521e651
4412319ef944ebcca9581cbacb1d4e1dc614c348d1dfc5d2faaaad863d300209
4d03b0f545d0b54c1fac00c63d37a4f4df586aee8ae18f9c193d1ef380423608
0ad44166db3cebf7d7e20e6e5cd49037ecef554aed4180ca8d9f946b8c432562
797ed298b3e0c176e52bfb82abed073cdb5043e61a1d88cd0d1769de4f97d6bb
23993fbed835ef85eabf2489095cd378b04109692325bce7cb6f19a3868b96eb
da5c55cc1039a268437e0bdb3180746f8cfcc2ddc7cd2b2dca7dd43a85556c27
c6b4eee51bc1dc576d85bdeba98a8ea05071d47a17e497fc7e6368a53e8ab8bf
9976b3be2bccc1e252ab830916d22d705464c051e0dea8cbf5b7c180507b1007
34aa12ff78aa93e311a82bff0d0eb6014b22ed175f57a1a12c02fd3cfd8c0f8e
32e716a6021dd73b12f516c736662acd1f44fc9641f1680e1c5a42d0aee156ab
a0f5889e12526b47f8d26fdd1ba6c59d6c275ef36230ca4c325208945221d344
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
3dd5ea8a14eb665ba6057d424f94e5e83757ffaab456578dbf038af04053b19e
8c050fa8576e8c412290e8a9b9015fafbd968663893559b736aa77864cc854bb
faa1f06d38f0fcca70e66fd32f9b81e2822f3b6e07861158659bb70e6148bae8
160d0aaf1ab39ce85b0e22b9aee243e0df769c9e3a41f8feca19a8f618bd13c4
da3a2f83dbcdfabef9e97efdc69f8e7a059ff7db26bc1d1109abb459c962282c
d11c7e4570dfc7636ff6ca717ee542fc6dd5adcb74958bf5d303a5faf5f406fc
Domains
settings-win.data.microsoft.com
slscr.update.microsoft.com
crl.microsoft.com
ocsp.godaddy.com
ecs.office.com
api.telegram.org
ocsp.digicert.com
google.com
go.microsoft.com
login.live.com
fe3cr.delivery.mp.microsoft.com
www.microsoft.com
client.wns.windows.com
self.events.data.microsoft.com
activation-v2.sls.microsoft.com
nexusrules.officeapps.live.com
x2.c.lencr.org
ye.c.lencr.org
mail.xga-cn.com
www.bing.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://ocsp.godaddy.com//meowsdbgmeqwqjajbgurdgmcgguabbs2ca1fbgt26xpkokx4zguoujm0tgquqmk9j47mnimwojpx%2b2yz8lqsgm4ccqcvpitnpqki3g%3d%3d
https://api.telegram.org/bot8052153515:aaey1r0sscqyrtfr5mlz5lbcuc9k_rdiiey/senddocument?chat_id=5022382431&caption=dc-creds:::desktop-jglljld\admin\
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 2474
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 4783
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 7302
comments 0

What is DarkCloud malware?

DarkCloud is a stealer malware written in Visual Basic. The core functionality of the malicious software is collecting and exfiltrating sensitive information from infected machines. The type of data stolen by DarkCloud ranges from user credentials to credit card details in browsers.

The malware has been active since the end of 2022 and has been widely used in attacks in 2023. DarkCloud is sold by its creators on DarkNet forums who also provide customization options, including the additional clipper module, allowing the malware to monitor the content saved by victims to the clipboard.

The most common infection chain for DarkCloud is spam emails, targeting a variety of users. The malware is usually distributed in the form of a malicious attachment. Once downloaded and launched by the user, the malware gets installed on the device and begins its malicious activities.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Technical details of the DarkCloud malicious software

DarkCloud can engage in the following operations on the infected system:

  • Steal information: It can pull data from different browsers and FTP clients, as well as the clipboard.
  • Capture screenshots: DarkCloud can take screenshots of the user’s activities.
  • Record keystrokes: The malware has the keylogging capability, letting it keep track of everything typed on the keyboard by the victim.
  • Exfiltrate files: It is capable of grabbing files of different formats, such as .txt, .rtf, and .pdf.
  • Communicate with the C2: DarkCloud supports several communication protocols, including SMTP and via Telegram, used for relaying stolen data to the attacker.

Additionally, similar to LaplasClipper, DarkCloud is equipped with a crypto swapper, enabling it to replace the user’s crypto wallet addresses with those of the attacker.

The malware can create a Task Scheduler entry in order to gain persistence on the system.

Execution process of DarkCloud

In order to examine the entire execution chain of DarkCloud in more detail, we can upload its sample to the ANY.RUN sandbox.

As stealers strive to conceal their activities, the DarkCloud stealer employs a deliberately straightforward execution chain to minimize visibility. Consequently, the infected operating system experiences a limited number of processes, and the malware refrains from utilizing system tools. Once the payload infiltrates the compromised system, it promptly initiates its execution.

The analyzed sample injects the system binary "AppLaunch" and subsequently executes it. After initiating, DarkCloud employs time-based evasion techniques in an attempt to conceal itself from sandboxes. However, it was detected, and the configuration was successfully extracted. It then starts a process executing all malicious activities, encompassing data theft and communication with the Command and Control (C&C) server.
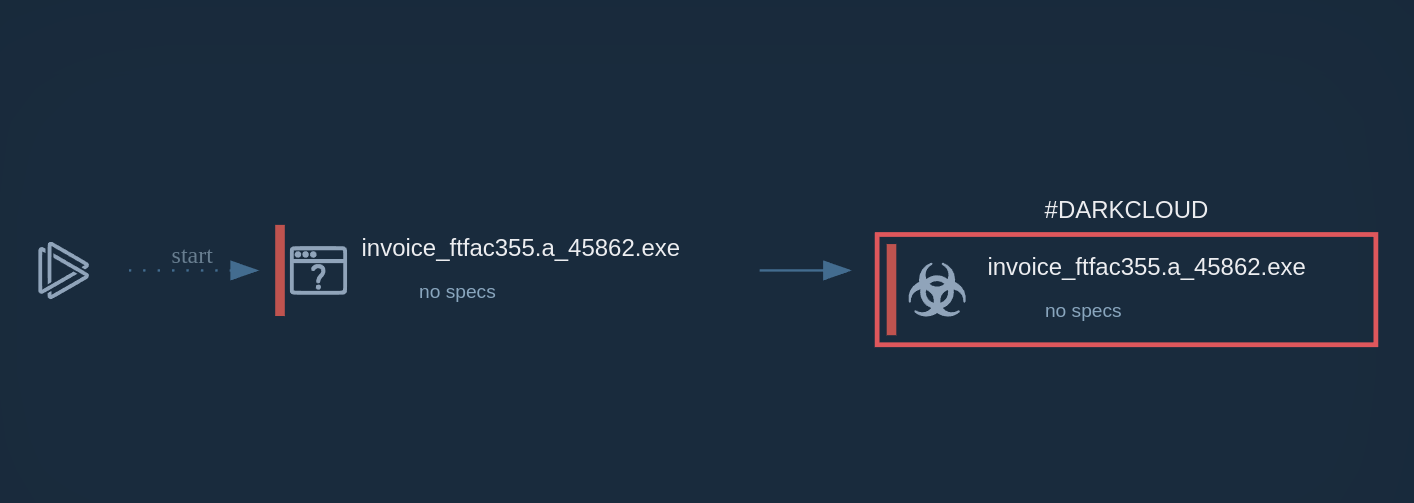
DarkCloud process graph shown in ANY.RUN DarkCloud's process graph demonstrated in ANY.RUN

Distribution methods of the DarkCloud malware

Just like in the case of other stealer malware, such as Formbook and Lokibot, the most common way used by attackers to distribute DarkCloud is via emails. In most cases, criminals employ social engineering and craft their messages to look legitimate. This is why victims often receive fake invoice payment requests and similar emails with files attached to them. Users who fail to recognize a scam end up downloading the malicious attachment and running it on their system, thus triggering the infection process.

Conclusion

In order to avoid falling victim to DarkCloud, it is vital to follow strict security practices. One of them is analyzing suspicious files and links in a malware sandbox. ANY.RUN is a cloud-based service that lets you investigate any email attachment or URL sent to you by an unknown sender and determine whether it poses any risk.

ANY.RUN’s interactive approach to malware analysis enables you to engage with the files and the system just like on your own computer, performing all the necessary actions to execute malicious software fully. The service provides you with comprehensive threat reports that contain details about the attack, indicators of compromise (IOCs), and other relevant information.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More
SnappyClient screenshot
SnappyClient is a sophisticated C++-based command-and-control (C2) implant first identified in December 2025. Delivered primarily via the modular HijackLoader, it functions as a versatile remote access tool with strong information-stealing capabilities, particularly focused on cryptocurrency wallets, browser data, and system control. It employs advanced evasion techniques, encrypted communications, and modular configurations to maintain persistence and evade detection.
Read More
Virlock screenshot
Virlock
virlock
Virlock is a unique ransomware strain that combines encryption capabilities with file infection techniques. First observed in 2014, it stands out due to its polymorphic nature and ability to embed its code into compromised files, ensuring continued propagation. Once it infects a system, it encrypts files and locks the screen, demanding a ransom for file recovery and system access.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More