Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
15
Global rank
13 infographic chevron month
Month rank
13 infographic chevron week
Week rank

Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold.

Trojan
Type
Likely Turkey
Origin
1 January, 2014
First seen
19 September, 2026
Last seen

How to analyze Agent Tesla with ANY.RUN

Type
Likely Turkey
Origin
1 January, 2014
First seen
19 September, 2026
Last seen

IOCs

IP addresses
23.52.181.141
95.100.102.101
48.209.138.168
135.233.95.144
208.95.112.1
2.16.164.72
23.11.41.157
48.192.1.65
20.190.159.75
23.59.18.102
172.211.123.250
74.178.240.51
23.52.181.212
23.216.77.21
184.94.213.209
193.122.6.168
57.153.246.3
2.21.239.135
2.16.204.136
2.23.246.9
Hashes
2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
412bad1c87f5d4e8c3a6955e942628b9615931cc2399c2b316326d15e3a84775
699ec052ecc898bdbdafea0027c4ab44c3d01ae011c17745dd2b7fbddaa077f3
95b90a2f67df2b1412b5a508ff980d3e0e321185ae53c09807bba137af4edef4
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
9734616211f31d7ef17ea26811a1b276276bbbde9abd2148f80cd17ffdd13c5e
19fed10083a7b48930e5a4caab964b445a58ffe14d98b206fa96ccd7d928ae61
e8f64f6f49b8231476e1028b75f2a3e5317ed506db6d1a265dbf3c28eb3e1d1a
708e198608b5b463224c3fb77fcf708b845d0c7b5dbc6e9cab9e185c489be089
687f141ef559268ebcda404ba5dbcfc18c37645e7e9292ff5d17eaa328b5868d
6cf535daeec70899c28c0c6127f210900c2999a97189dedda415987d0f353a72
83e57db5256f6a5f8c533152714f40f14133eafeb8ee9dff2e24221159acb7a9
7d757e510b1f0c4d44fd98cc0121da8ca4f44793f8583debdef300fb1dbd3715
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
3a5078b626e41d20117d260d8b825b039884cfe062c6d462432216d9b07d82b5
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
474d668707f1cb929fef1e3798b71b632e50675bd1a9dceaab90c9587f72f680
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
Domains
ocsp.digicert.com
login.live.com
www.microsoft.com
slscr.update.microsoft.com
activation-v2.sls.microsoft.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
crl.microsoft.com
self.events.data.microsoft.com
ip-api.com
google.com
go.microsoft.com
server356.web-hosting.com
client.wns.windows.com
ecs.office.com
checkip.dyndns.org
officeclient.microsoft.com
www.bing.com
th.bing.com
oneocsp.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://ip-api.com/line/?fields=hosting
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://checkip.dyndns.org/
Last Seen at
Last Seen at

Recent blog posts

post image
How MSSPs Can Prove Their Value When “Nothing...
watchers 2957
comments 0
post image
Enterprise Threat Intelligence Buying Guide:...
watchers 3360
comments 0
post image
ANY.RUN & SentinelOne: One Workspace, Ins...
watchers 4831
comments 0

What is Agent Tesla malware?

Agent Tesla is a password stealer spyware that has been around since 2014. The malware can be used by attackers to spy on victims, allowing them to see everything that has been typed in supported programs and web-browsers.

Being marketed and sold on its own website, which falsely claims that the program is a legitimate keylogger created for personal use, the Agent Tesla virus has become extremely popular in the hacker community. Not lastly due to its ease of use and tech support, available on the “official” website where this malware is being sold by the attackers, as well as on the dedicated Discord server. Despite claiming the legitimacy of the software, support staff gives advice on utilizing the virus illegally. It is thought that Agent Tesla spyware has originated in Turkey.

General description of Agent Tesla

The spyware is created using .Net software framework. It is aimed at stealing personal data and transmitting it back to the C2 server. The malware is able to access information from web browsers, email clients, and FTP servers.

In addition, Agent Tesla malware can capture screenshots and videos. It can also record clipboard information and form values. The virus was being distributed on agenttesla-dot-com where attackers could purchase it for as little as $15. However, depending on the requested options the package price could easily reach roughly $70.

Uniquely, creators of the malware have set up a sort of an ecosystem around the program, providing 24/7 customer support as well as pre-matched purchase plans that include various options tailored for different budgets and goals. The virus is supplied with a dedicated builder that has a simple-to-use control panel. It allows even a non-technically savvy attacker to pack the payload into a malicious document. What’s more, after 2015 the control panel of Agent Tesla has been expanded with extensive automation functionality, allowing the attacker to automatically capture snapshots or remotely activate the webcam on a victim’s PC in set intervals.

Based on the analysis, the malware comes equipped with multiple persistence mechanisms that help it avoid antivirus detection. As such, it can resume operation automatically after a system reboot. It is also able to turn off Windows processes to stay hidden.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Malware analysis of Agent Tesla

The interactivity of ANY.RUN service allows tracking activities in real-time and watching Agent Tesla in action in a controlled, safe environment with full real-time access to the sandbox simulation. A video recorded by the ANY.RUN gives us the ability to take a closer look at the lifecycle of this virus. You can also analyze fresh samples and IOCs in our threat intelligence feed in the public submissions.
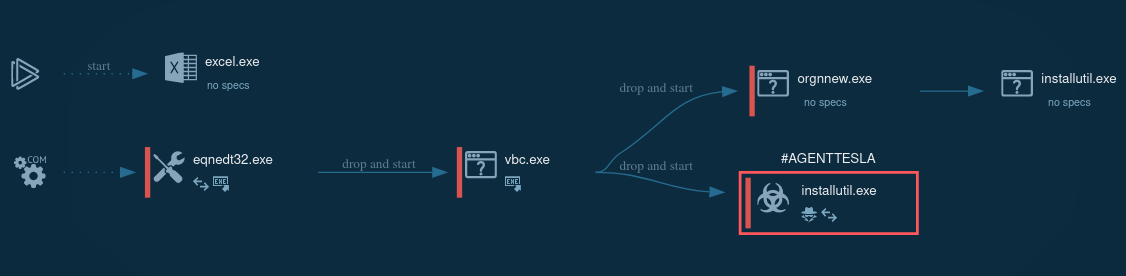
agent tesla execution process graph Figure 1: A lifecycle graph generated by ANY.RUN

How to avoid infection by Agent Tesla?

Agent Tesla malware is not an easy one to identify. The most robust way to stay safe is to exhibit caution when opening suspicious emails or visiting unknown links. Above all, one must be careful to download attachments in emails from unknown senders and try to identify scams.

Distribution of Agent Tesla

The malware is distributed at large via spam email campaigns like Vidar or IcedID. It is usually delivered to victims in malicious documents, or via malicious web links. Upon visiting such a link, a contaminated document will be automatically downloaded to a victim’s PC.

If opened, the document will trigger the download of the actual virus. The spyware saves itself in the “%temp%” folder and then automatically executes. Email campaigns usually target individuals working in different industries. Topics of malicious emails can be extremely diverse.

Agent Tesla execution process

Agent Tesla keylogger is mostly spread via Microsoft Word documents that contain an embedded executed file or exploit. Once clicked, an executable file is downloaded and renamed. The downloaded file runs itself and creates a child process which in turn can create another child process.

The malware is able to use Regsvcs and Regasm to proxy the code execution through a trusted Windows utility. The research and threat intelligence team can pay attention that in the given example RegSvcs.exe process is stealing personal data.
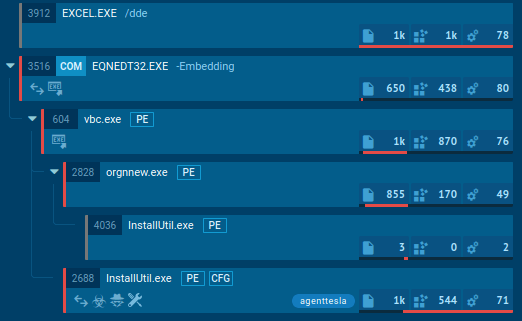
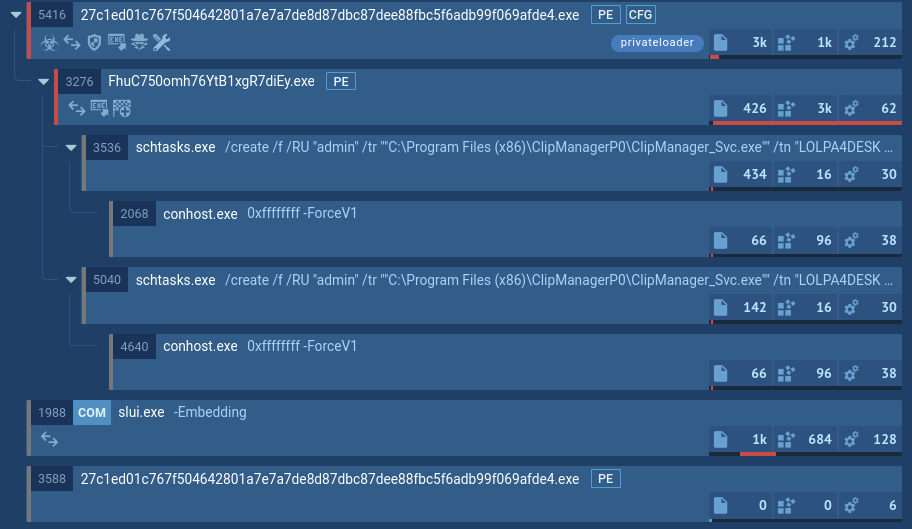
process tree of the agent tesla execution Figure 2: A process tree of the Agent Tesla execution

Since the main purpose of Agent Tesla RAT is stealing personal information you can identify it by behavioral activities. To do so, try the analysis of the indicators of a malicious process (most often it's an injected "RegAsm.exe"). If there is the indicator "Actions looks like stealing of personal data" in the "Process details" section you probably are dealing with the Agent Tesla trojan. Also, you can identify what information the malware has stolen by clicking on the indicator. You can navigate through by clicking right and left arrows in the appeared window.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

How to get more Agent Tesla data using ANY.RUN?

Often Agenttesla packets encryption is unsuccessful and with ANY.RUN service's "Network Stream" analysts can take a look at what data this malware stole. To do it open the "Connections" tab in the lower part of the task's window and simply click on the connection which sent data. Not unusual that you can find inside this information even the attacker’s SMTP credential.
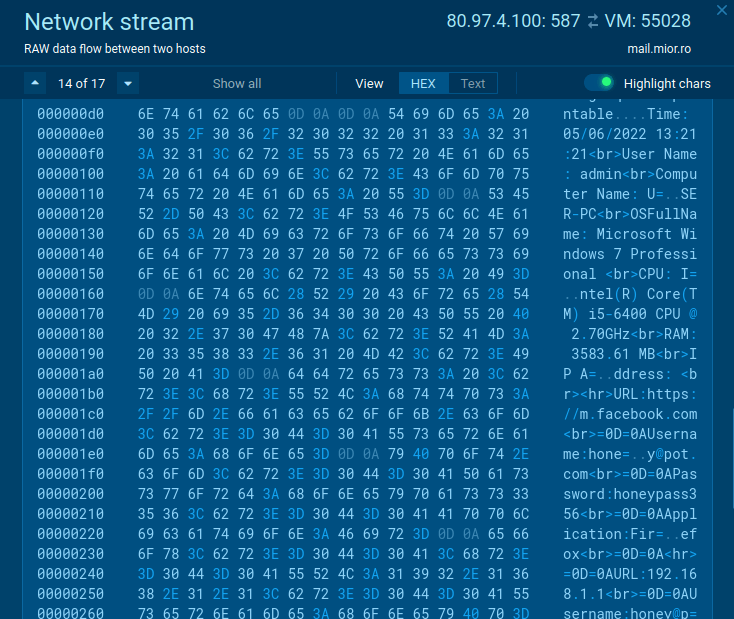
agent tesla's network stream without encryption Figure 2: Agent Tesla’s Network stream without encryption

Gathering threat intelligence on Agent Tesla malware

To collect up-to-date intelligence on Agent Tesla, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Agent Tesla.
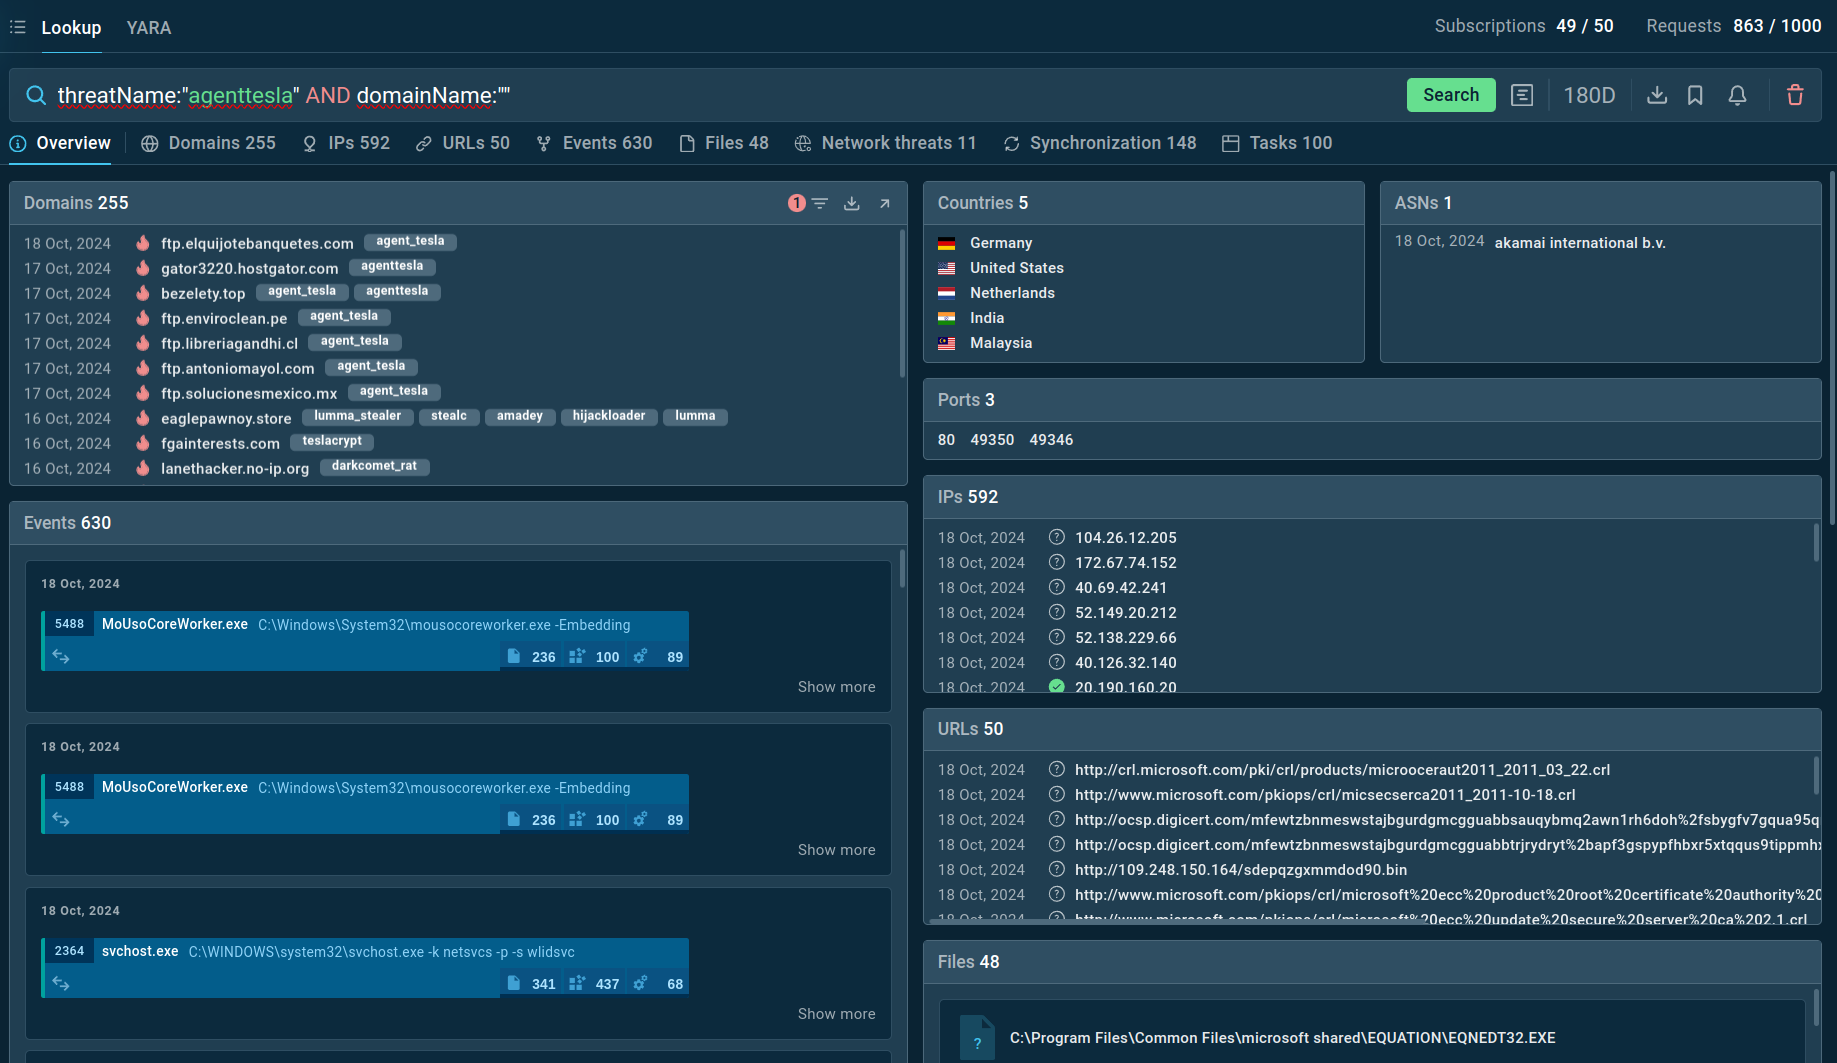
Agent Tesla ANY.RUN Search results for Agent Tesla in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"agenttesla" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from Agent Tesla samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

According to threat intelligence reports, since its creation, Agent Tesla trojan has been used by over 6,300 customers. Unfortunately, the popularity of the virus is only continuing to rise. The upward trend is of, course, supported by the ease of use which allows even novice attackers to set up attacks.

A company-like service provided by the virus creators also plays a significant role. The danger of Agent Tesla for incident response and threat intelligence teams lies not only in the fact that it can be used by almost anybody but also in its ability to open doors to more destructive viruses. Thankfully, interactive analysis services such as ANY.RUN allows professionals to examine the malware behavior in detail and set up appropriate security responses.

Create your free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

Loader screenshot
Loader
loader downloader
A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection.
Read More
WhiteSnake screenshot
WhiteSnake
whitesnake
WhiteSnake is a stealer with advanced remote access capabilities. The attackers using this malicious software can control infected computers and carry out different malicious activities, including stealing sensitive files and data, recording audio, and logging keystrokes. WhiteSnake is sold on underground forums and often spreads through phishing emails.
Read More
LokiBot screenshot
LokiBot
lokibot loader trojan
LokiBot was developed in 2015 to steal information from a variety of applications. Despite the age, this malware is still rather popular among cybercriminals.
Read More
MassLogger screenshot
MassLogger
masslogger
MassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems. It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
Read More
Cactus Ransomware screenshot
Cactus ransomware-as-a-service (RaaS) was first caught in March 2023 targeting corporate networks. It became known for its self-encrypting payload and double extortion tactics. Cactus primarily targets large enterprises across industries in finance, manufacturing, IT, and healthcare. It is known for using custom encryption techniques, remote access tools, and penetration testing frameworks to maximize damage.
Read More
DragonForce screenshot
DragonForce
dragonforce
DragonForce is a ransomware strain operating under the Ransomware-as-a-Service (RaaS) model. First reported in December 2023, it encrypts files with ChaCha8, renames them with random strings, and appends “.dragonforce_encrypted.” By disabling backups, wiping recovery, and spreading across SMB shares, DragonForce maximizes damage and pressures victims into multimillion-dollar ransom negotiations. It has targeted manufacturing, construction, IT, healthcare, and retail sectors worldwide, making it a severe threat to modern enterprises.
Read More