Interactive Sandbox
ANY.RUN Interactive Sandbox for Google SecOps
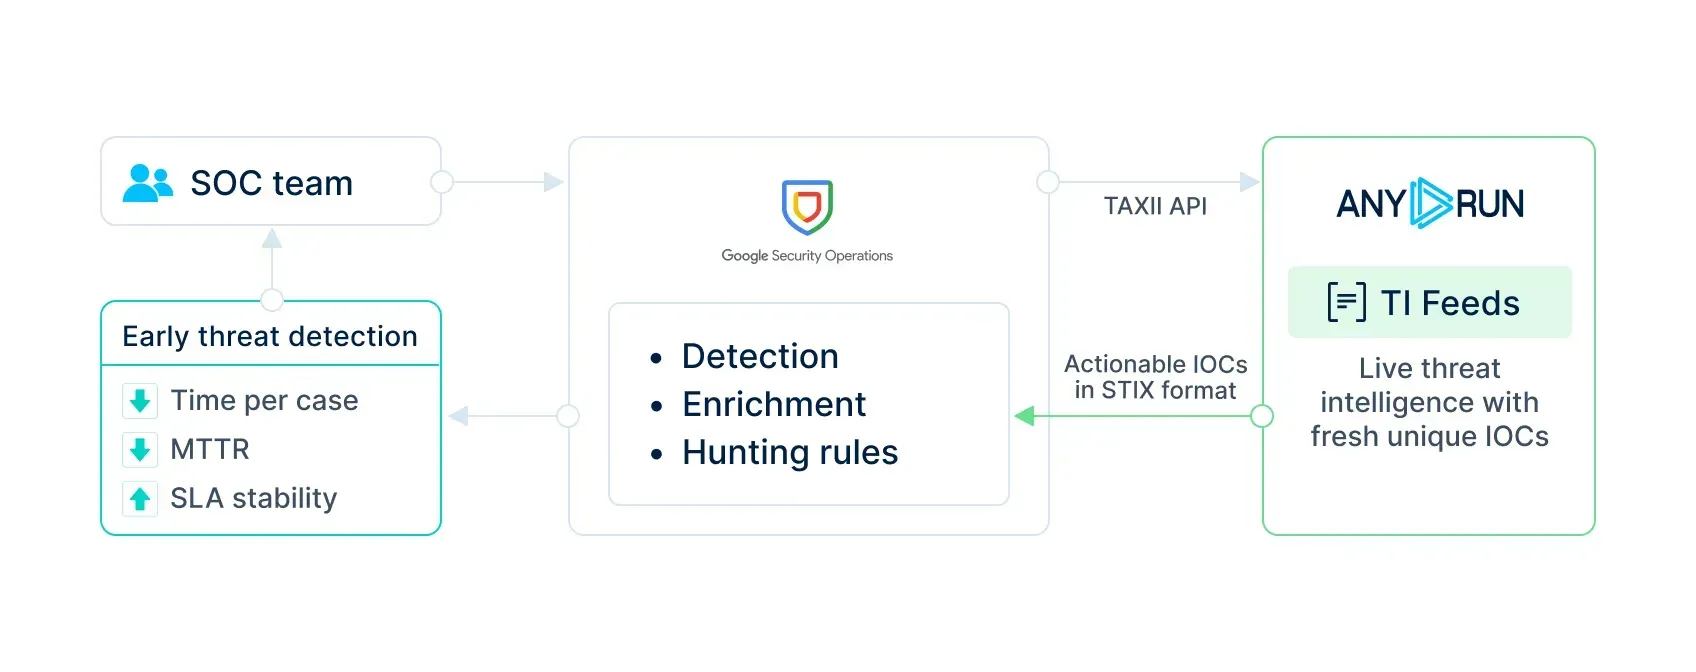
Validate suspicious files and URLs with real behavioral evidence to accelerate alert triage and reduce unnecessary escalations.
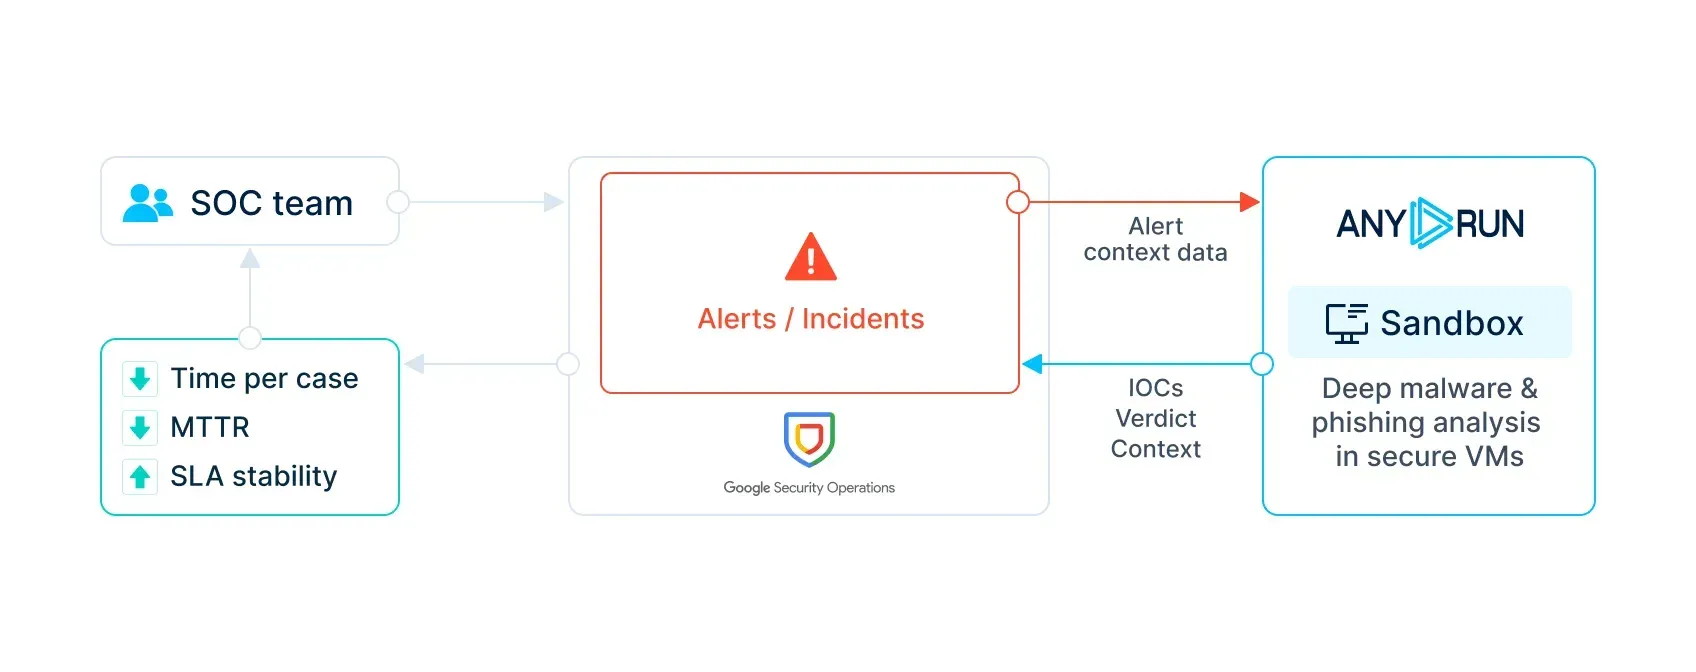
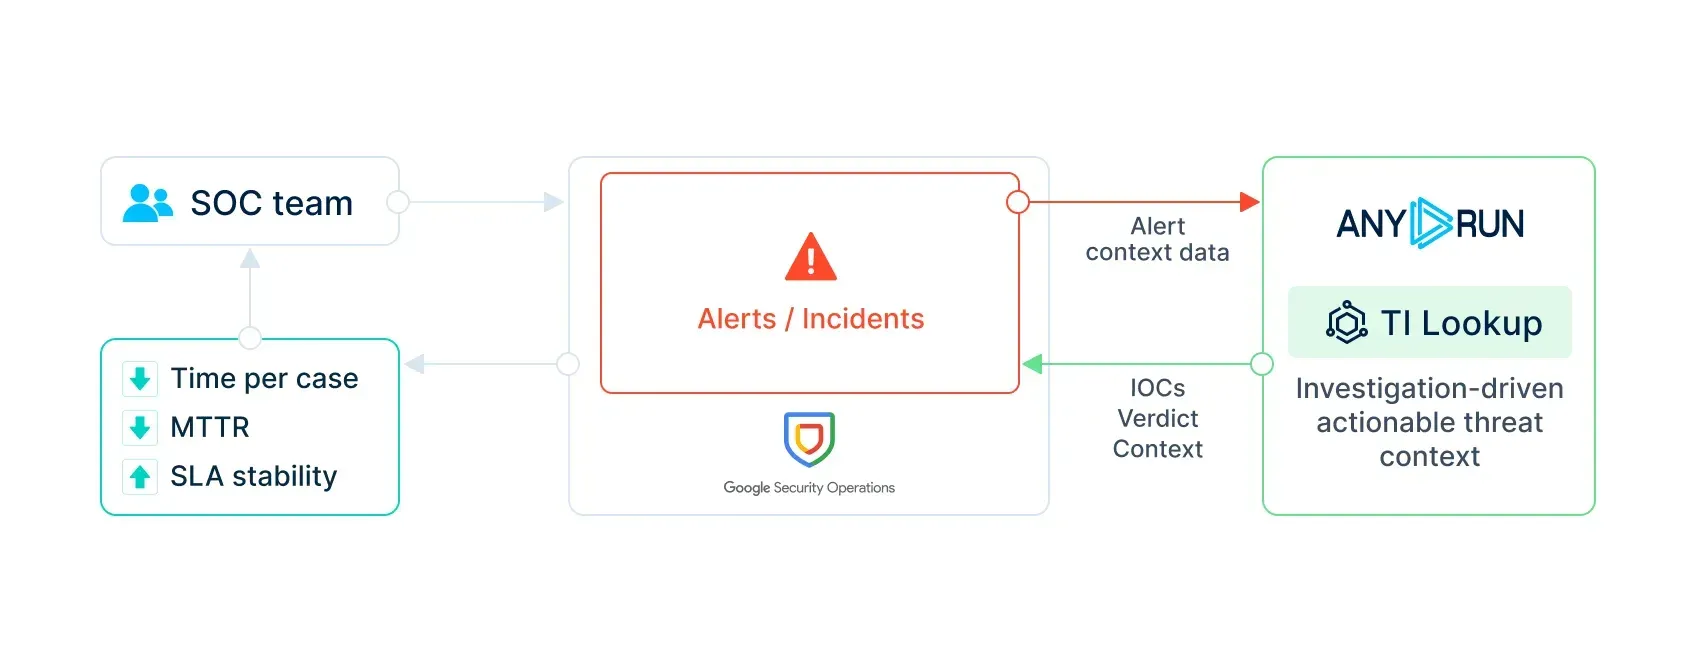
Submit suspicious files and URLs directly from Google SecOps alerts for analysis.
Analyze suspicious activity across Windows, Linux, and Android environments.
Receive verdicts, key analysis artifacts, and detailed reports within Google SecOps alerts.
Configure analysis duration, privacy, and network settings to meet investigation requirements.
Reduce manual investigation steps and help analysts move from threat validation to response faster.
Use cases
Alert validation
Malware analysis
Phishing analysis
Requirements
ANY.RUN Sandbox plan with API access