
Interactive Sandbox
ANY.RUN Interactive Sandbox for MISP
Validate suspicious activity with behavioral evidence and give analysts the context they need to make faster investigation decisions.
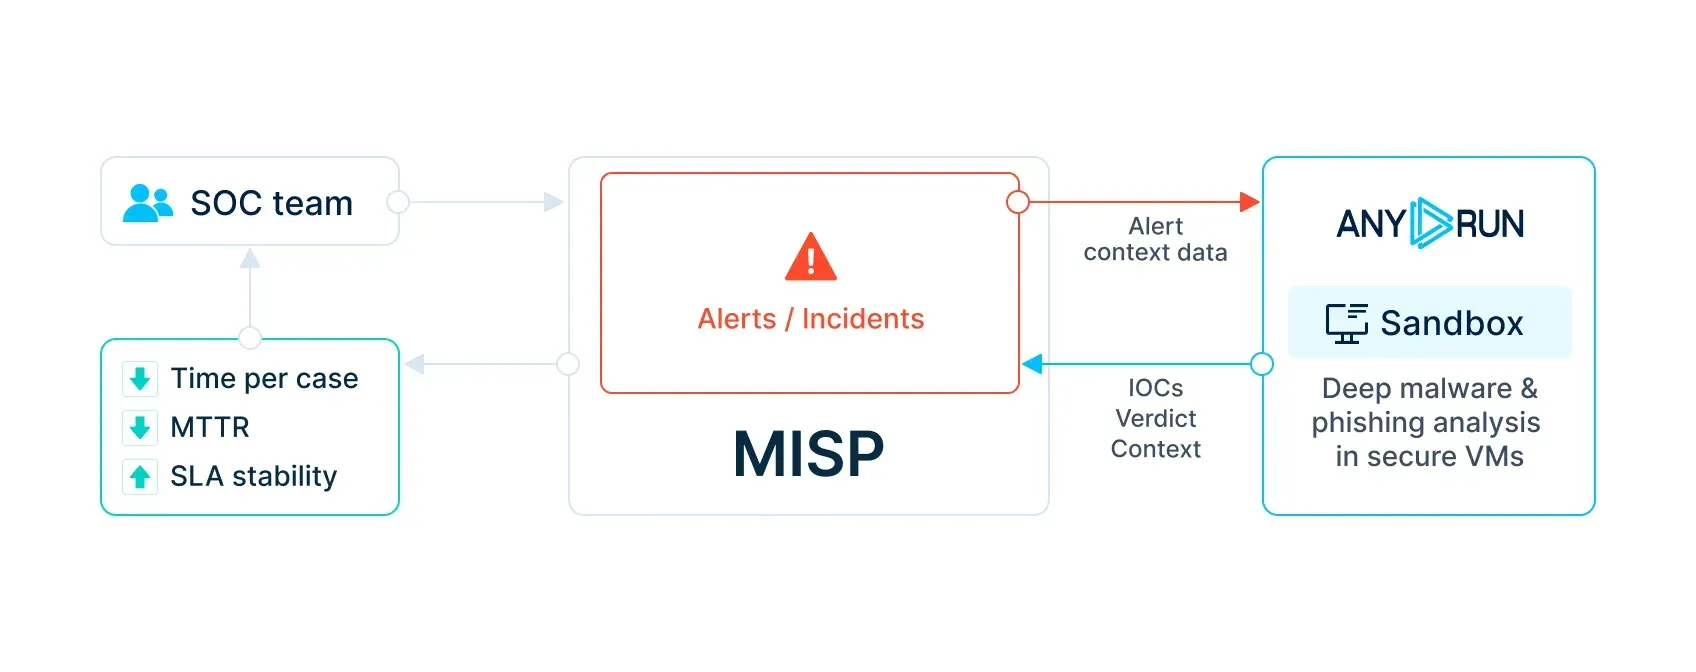
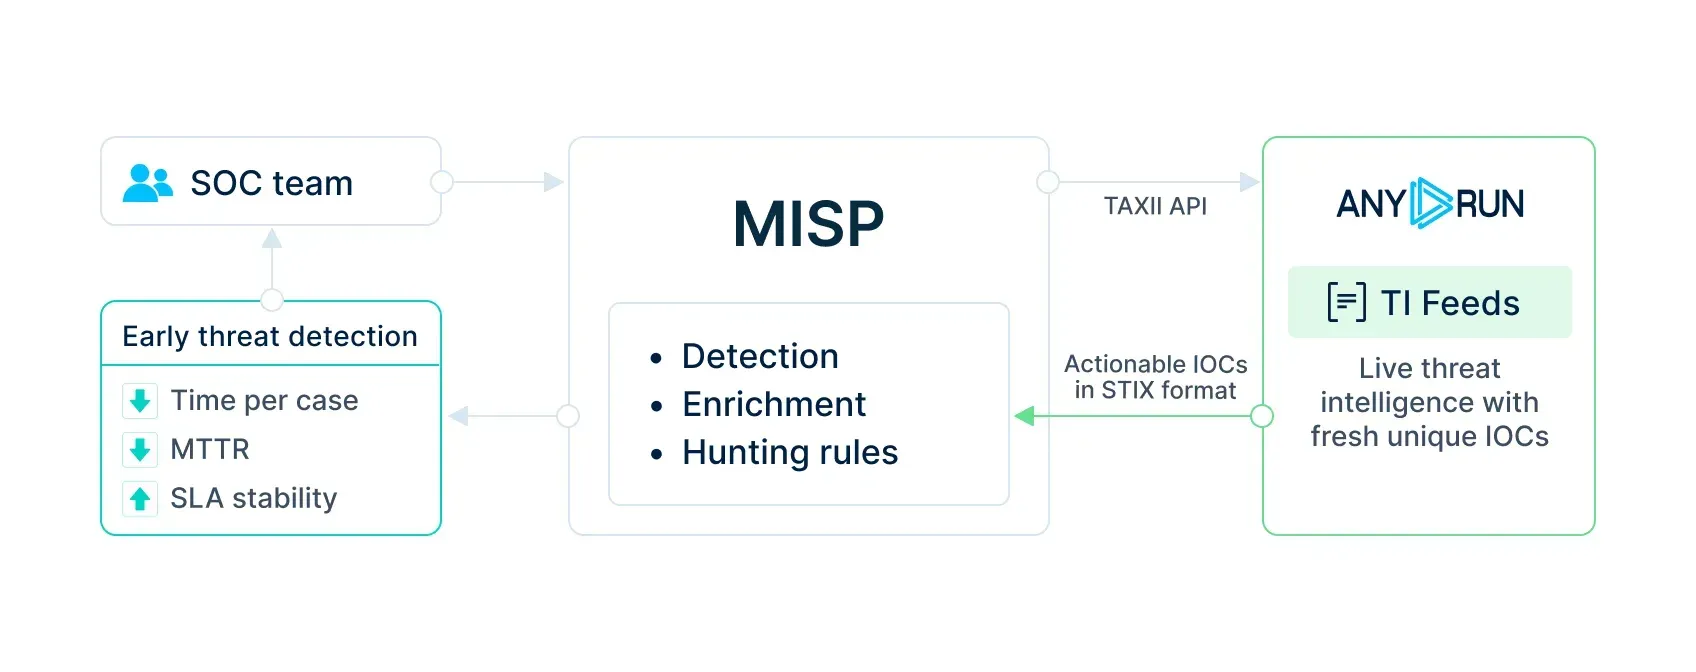
Submit suspicious files and URLs from MISP events for behavioral analysis.
Use Automated Interactivity to expose threats that require user actions to execute.
Bring verdicts, IOCs, MITRE ATT&CK data, and analysis reports back into MISP.
Add behavioral evidence to MISP events to support further investigation and threat correlation.
Reduce MTTR and analyst workload with faster validation and fewer manual investigation steps.
Use cases
Alert validation
Phishing analysis
Malware analysis
Requirements
ANY.RUN Sandbox plan with API access