Threat intelligence Lookup

Deep threat context for faster SOC investigations

Access live data on the latest malware & phishing attacks to power response and threat hunting in your company.

What is Threat Intelligence Lookup?

On-demand context enrichment solution for searching, correlating, and investigating malware and phishing

It gives enterprise SOCs and MSSPs the context to validate cyber threats, prioritize incidents, and make faster response decisions.

  • Available via API

    Integrate threat intelligence into your existing security stack. No infrastructure changes needed.

  • Access online

    Get threat context right after registration with 20 free search requests.

Sourced from the largest malware analysis community

Real-time intelligence from the latest sandbox analyses of malware and phishing attacks across industries.

Unique, fresh context

ANY.RUN continuously enriches its intelligence, helping SOC teams identify emerging threats and respond faster.

700K+ security professionals

Users from 195 countries contribute to our threat intelligence via public analyses or shared anonymized threat data.
Pre-processed data

Interactive Sandbox acts as a threat sensor and validator, capturing and verifying malicious activity while extracting rich contextual data, including events, TTPs, and IOCs.

How to use TI Lookup during investigations

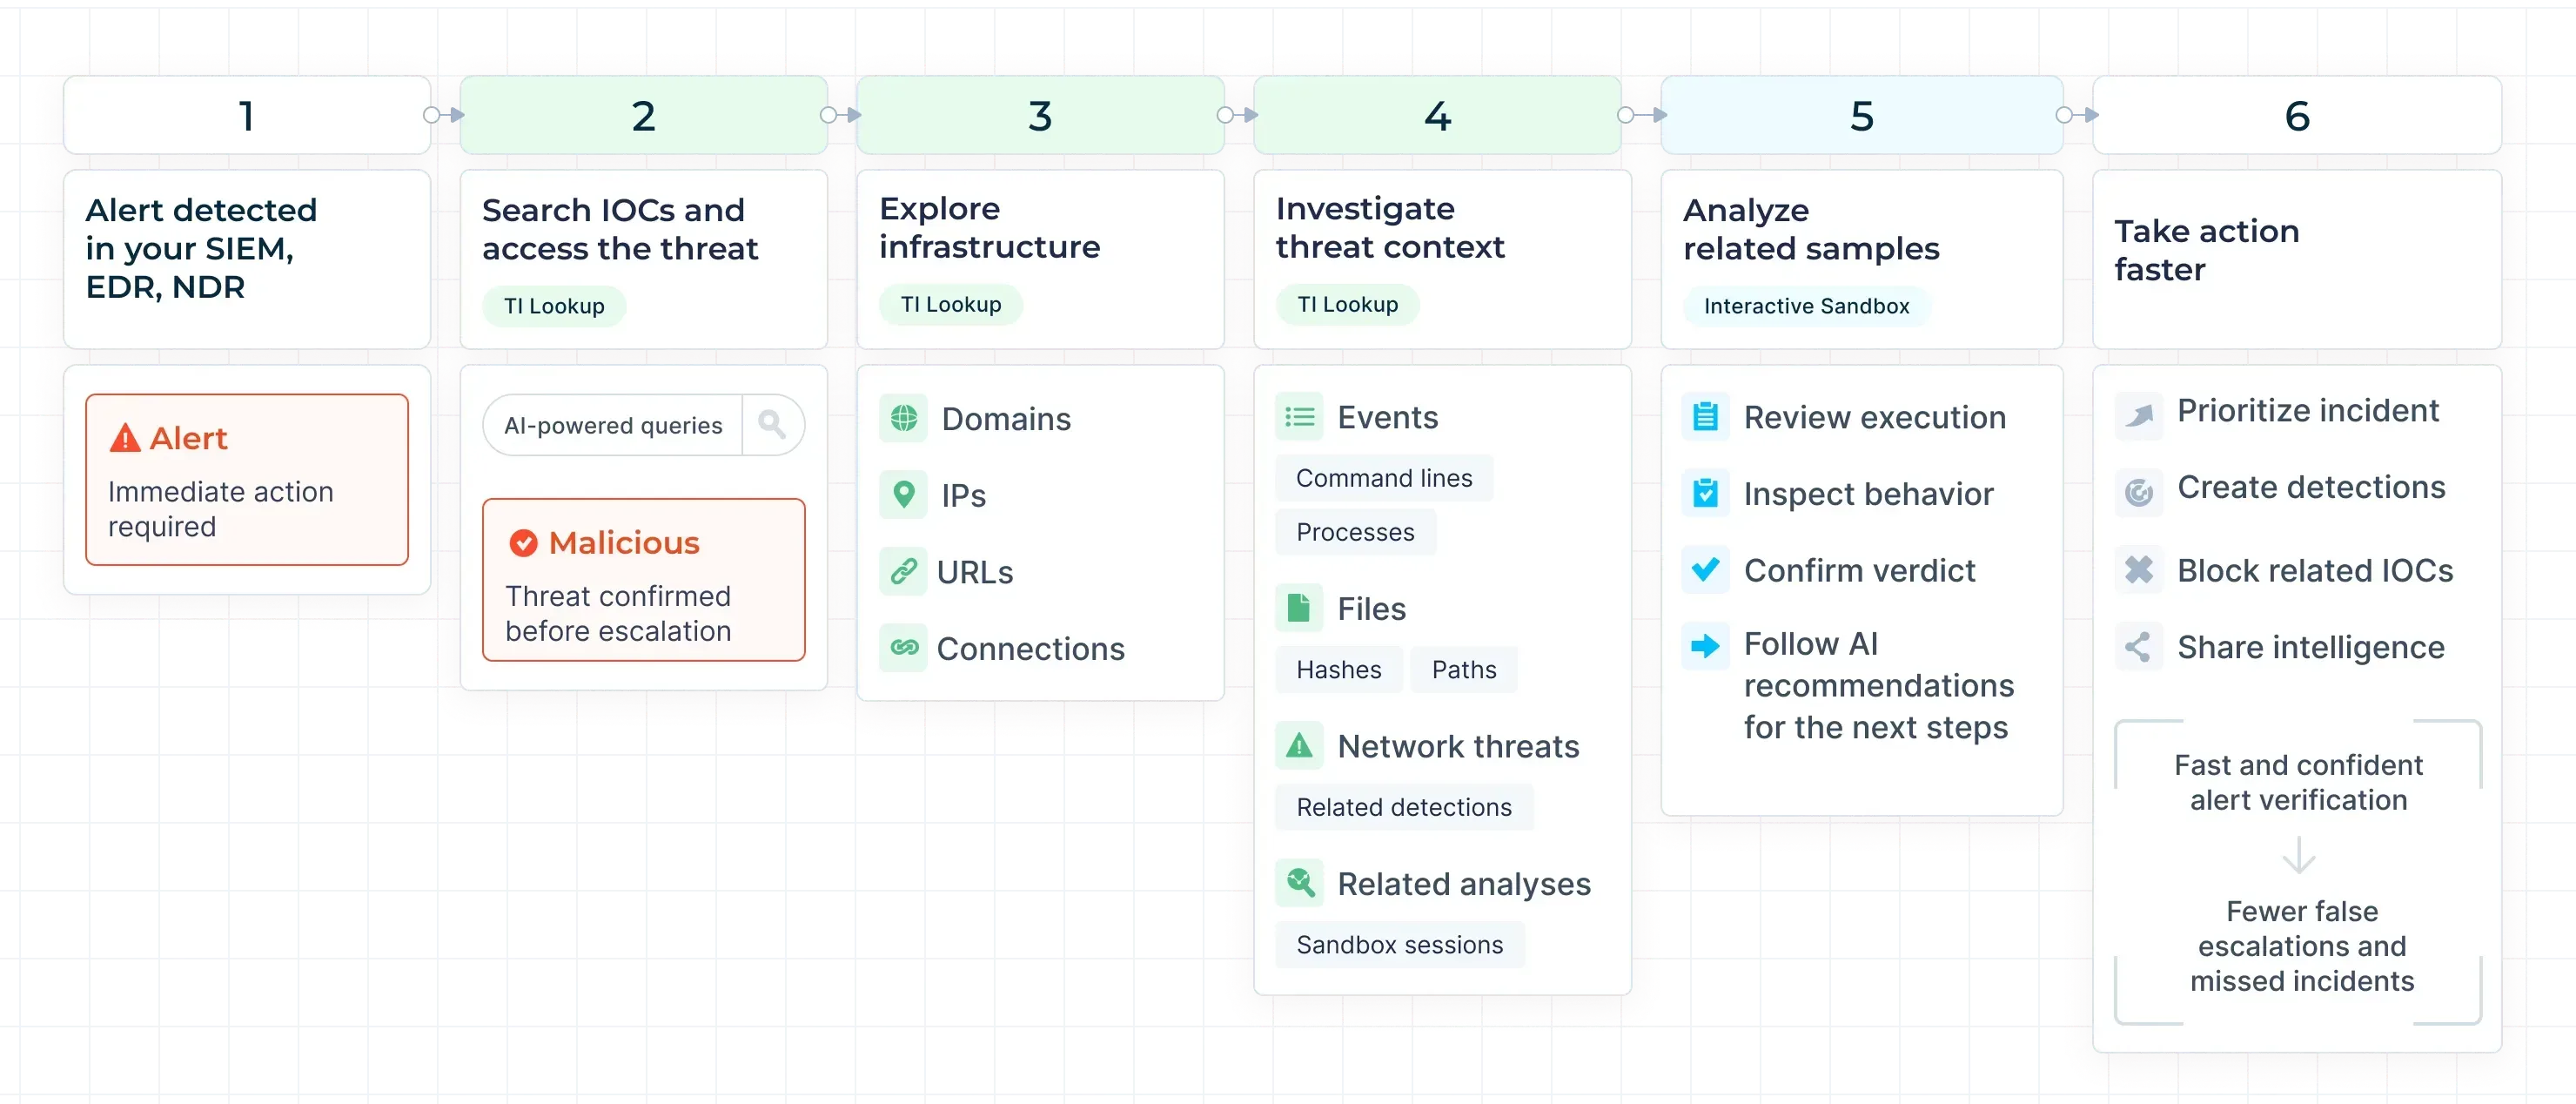
Add contextual intelligence to every investigation. Validate threats faster, uncover related activity, and respond with confidence.
Turn threat context into stronger defense

Threat Intelligence Lookup helps SOC teams optimize workflows, accelerate triage, investigation and response, and improve detection.

  • Identify threats by searching IOCs and system artifacts, including URLs, file hashes, IP addresses, registry keys, and command lines.
  • Enrich detection rules to identify hidden malware.
  • Explore threat landscape by industries and regions to strengthen risk awareness and prioritization
SOC impact

More confident threat validation

  • Quickly gather relevant data to understand the nature of the attack and validate threats in seconds.
  • Use wildcards and search operators in flexible combinations for rich threat context discovery.
  • Get search results in about 2 seconds to reduce time spent on manual investigation.
SOC impact

Faster investigation and response

  • Hunt for threats using IOCs and system artifacts found in your environment, including IPs, hashes, registry keys, processes, and other indicators.
  • Use even the smallest artifacts found in your network to uncover related threats and collect up to 24× more IOCs per case for further investigation and detection.
SOC impact

Deeper threat discovery

  • Free up senior analysts from repetitive enrichment tasks, allowing them to focus on complex investigations and threat response.
  • Help junior analysts make informed decisions with behavioral and infrastructure context.
  • Give analysts richer context for understanding and validating threats.
SOC impact

Fewer unnecessary escalations

  • Identify threats by searching IOCs and system artifacts, including URLs, file hashes, IP addresses, registry keys, and command lines.
  • Enrich detection rules to identify hidden malware.
  • Explore threat landscape by industries and regions to strengthen risk awareness and prioritization
SOC impact

More confident threat validation

TI Lookup core features

Powerful search, advanced capabilities

Turn any suspicious indicator into the context your team needs to investigate threats, uncover connections, and respond faster.
  • Suricata rules
  • Signatures
  • TTPs
  • Hashes
  • Files
  • IPs
  • Process fields
  • URLs
  • Threat names
  • Events
  • Domains
  • Search faster with AI-powered queries

    Query in plain text to skip complex syntax and start analyzing immediately.

  • Catch stealth threats at the core

    Expose malicious behavior from system activity, even as attacker infrastructure shifts.

  • Prioritize threats that matter to you

    Get tailored updates for your industry and region to focus on real risks.

  • Validate hypotheses in a single search

    Combine multiple signals to cut through noise and confirm findings instantly.

ANY.RUN Threat intelligence

Better together. Build a stronger proactive defense

TI Feeds

Receive 99% unique, continuously updated IPs, domains, and URLs from sandbox analyses to enrich detection rules and strengthen automated threat detection.
TI Reports

Get analyst-grade threat intelligence without a dedicated research team. Access curated reports, attack insights, and response guidance.
TI YARA Search

Validate and refine YARA detections against real‑world threat data. Find matching malware at scale and instantly investigate its behavior in related sandbox sessions.
TI Lookup

Get actionable context backed by millions of sandbox investigations to accelerate response. Access reputation, behavior, and relationships from a single search.
Explore TI plans and features

From basic enrichment to full operational intelligence, choose the plan that fits your team's workflows.

Trusted by industry leaders

ANY.RUN Threat Intelligence helps SOC teams reduce risks and strengthen security posture.

  • 1,811finance

    organizations using our services.

  • 16K+

    organizations have integrated ANY.RUN into their security workflows.

  • 74%

    of Fortune 100 companies use ANY.RUN to strengthen their SOC operations.

Customer case

Fewer false escalations and faster triage with TI Lookup

Our analysts spotted a suspicious connection on a client endpoint. TI Lookup immediately showed that it’s tied to a known malicious C2 server.
SOC LeadHealthcare-focused MSSP
  • 34% fewer false escalations thanks to IOC enrichment
  • Isolated indicators linked to live attacks in seconds
  • One IOC leads to the full attack chain and new detection rules
  • Fast adoption. New analysts reach operational readiness in weeks, not months
Read more

Threat intelligence that works with your security stack

Maximize the value of your existing software by integrating ANY.RUN.

Explore integrations

Explore blog posts

  • Related Threat Context: Your New MTTR Shortcut

    Introducing Related Threat Context! You can instantly see whether IOCs have appeared in previous team investigations, industry activity, or ANY.RUN Threat Intelligence.
  • Intelligence-Driven Threat Hunting

    Explore 6 practical use cases: from hypothesis validation to YARA rule development, with real TI Lookup queries you can run right away.
  • How Threat Intelligence Saves Your Money

    See which costly expenses can be minimized or removed completely with timely updates to your detection systems using fresh IOCs.

FAQs about TI Lookup

What is ANY.RUN Threat Intelligence Lookup?
What types of threat data can I access via TI Lookup?
How do you source Threat Intelligence data?
How can TI Lookup provide the threat context needed for NIS2 and DORA risk assessment?
Can TI Lookup improve detection engineering?
Does TI Lookup integrate with existing security tools?
How does TI Lookup support threat hunting?
How is TI Lookup different from a standard IOC lookup?

Integrate TI Lookup in your SOC

Equip your security team with rich context on the latest threats to:

  • Streamline triage & response
  • Gain better incident clarity
  • Boost proactive security
  • Track evolving attacks in real time
+1
I accept ANY.RUN Terms of Use
By submitting the form, I agree to allow ANY.RUN to process my contact information, contact me, and share my details with its partners in accordance with the Privacy Policy.