




ANY.RUN’s malware analysis and threat intelligence products are used by 16K SOCs and 700K analysts. Thanks to flexible API/SDK and ready-made connectors, they seamlessly integrate with security teams’ existing software to expand threat coverage, reduce MTTR, and streamline performance.
For security leaders, integrations help turn existing technology investments into more effective SOC workflows. By bringing malware and phishing analysis, as well as fresh threat intelligence directly into established processes, teams can expand detection coverage, reduce manual work and tool switching, and accelerate response.
Here’s how ANY.RUN’s solutions can transform your security.
Interactive Sandbox: Detect Evasive Phishing & Malware
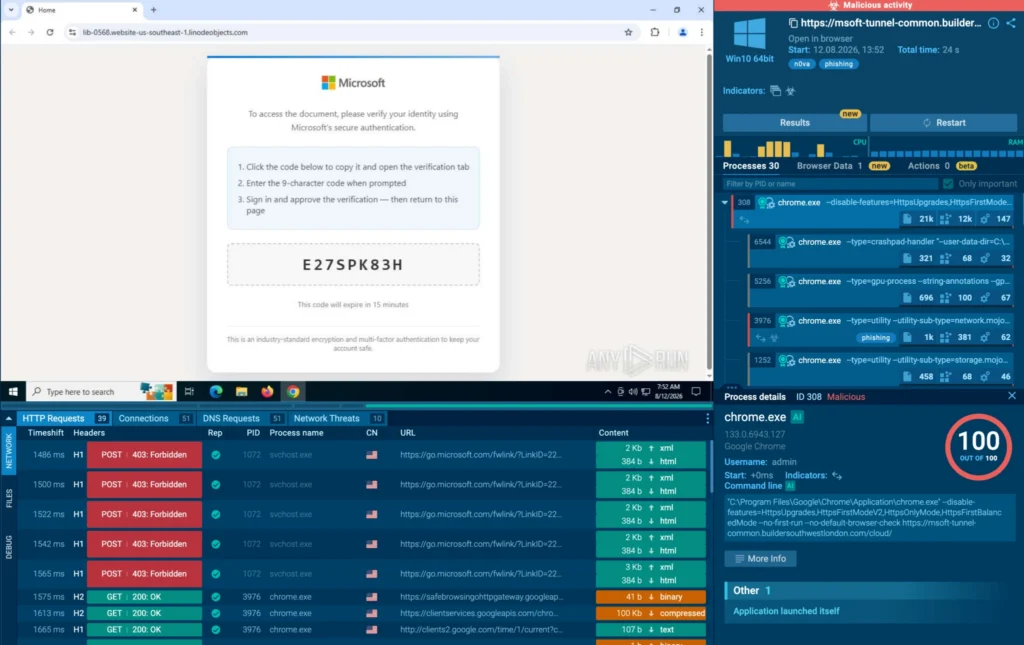
ANY.RUN’s Interactive Sandbox provides a real-time, cloud-based environment for detonating and analyzing suspicious files, URLs, and scripts across Windows, Linux, Android, macOS systems. It lets analysts perform user actions like launching executables or opening links needed to trigger kill chains and force hidden payloads to reveal themselves, enabling faster detection and response.
The sandbox integrates with other solutions like SOAR platforms in an automated mode, which means it can fully detonate complex phishing and malware attacks on its own, including by solving CAPTCHAs and scanning QR codes.
By embedding sandbox analysis into existing workflows, organizations can increase SOC capacity, standardize triage, and get more value from their existing SIEM, SOAR, and EDR investments.
The result is faster, more consistent threat investigation without increasing operational complexity:
- Real-Time Threat Visibility: Observe attack chains as they unfold, with 90% of threats detected within 60 seconds, accelerating mean time to detect (MTTD).
- Higher Detection Rates: Uncover low-detection attacks (e.g., multi-stage malware, CAPTCHA-protected phishing) with up to 58% more threats identified, reducing missed incidents.
- Automated Efficiency: Cut manual analysis time with automated interactivity, reducing Tier 1 workload by 20% and enabling junior analysts to handle complex cases independently.
Connectors and integrations for Interactive Sandbox
Please note: If your solution is not on the list, ANY.RUN’s API or Python-based SDK (see docs on GitHub or PyPi) make it possible to build custom integrations around your existing security architecture.
Threat Intelligence Feeds: Expand Threat Coverage
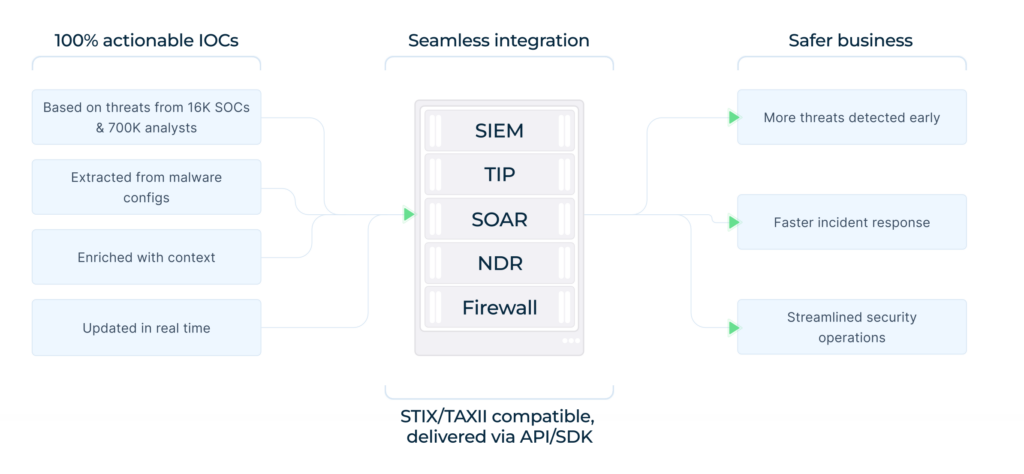
Threat Intelligence Feeds deliver real-time, high-confidence malicious indicators (IPs, domains, URLs) supplied in STIX/TAXII. The indicators are sourced from analyses of the latest malware and phishing attacks performed by 16,000 organizations and 700,000 analysts in ANY.RUN’s Interactive Sandbox.
Thanks to being powered by one of the largest malware analysis communities, these feeds provide 99% unique IOCs, not found in other sources, that are updated in real time.
For security leaders, this means an extended threat coverage without adding another standalone workflow for analysts. As a result, SOCs gain up-to-date visibility into emerging threats while reducing the manual effort required to collect, validate, and operationalize intelligence:
- Strengthen threat coverage: Live intelligence helps teams identify emerging attacks early on.
- Accelerate response: IOCs come with sandbox reports and investigation context for faster decision-making.
- Improve SOC efficiency: Filtering prioritizes high-risk indicators, reducing unnecessary analyst workload.
Connectors and integrations for TI Feeds
| Splunk Enterprise | MISP |
| Microsoft Sentinel | Threat Quotient |
| RapidInsightIDR | Microsoft Defender |
| IBM Security QRadar SIEM | Microsoft Defender |
| Elastic | OpenCTI |
| SentinelONE |
Please note: If your solution is not on the list, you can easily set up a custom integration using ANY.RUN’s API or Python-based SDK (see docs on GitHub or PyPi).
Threat Intelligence Lookup: Contextualize Alerts
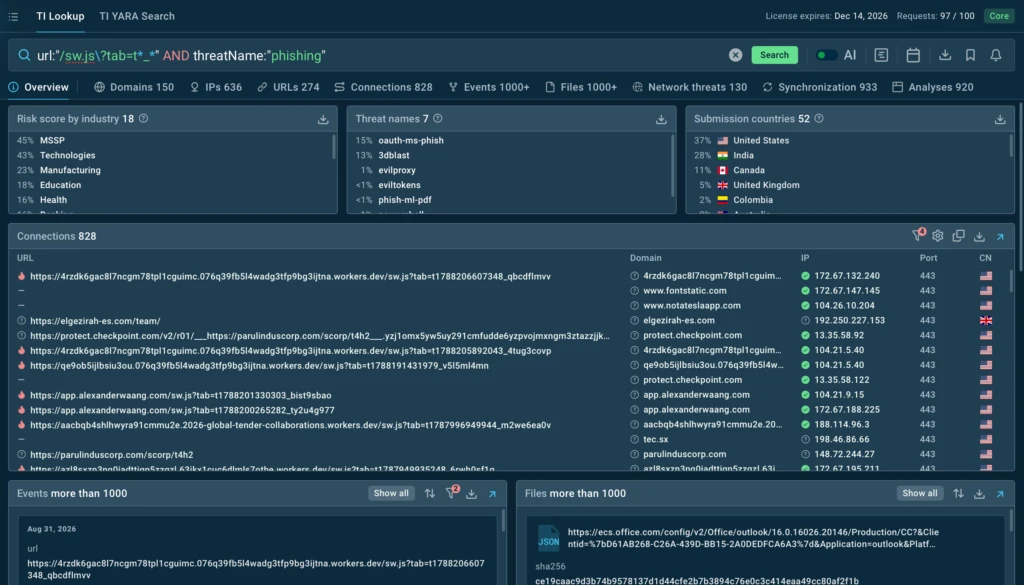
Threat Intelligence Lookup is a powerful solution designed to streamline and accelerate malware investigations, from proactive monitoring to incident response.
SOC teams can use it to quickly get actionable context for over 40 different types of Indicators of Compromise (IOCs), Attack (IOAs), and Behavior (IOBs), from an IP address and a domain to a mutex and a process name.
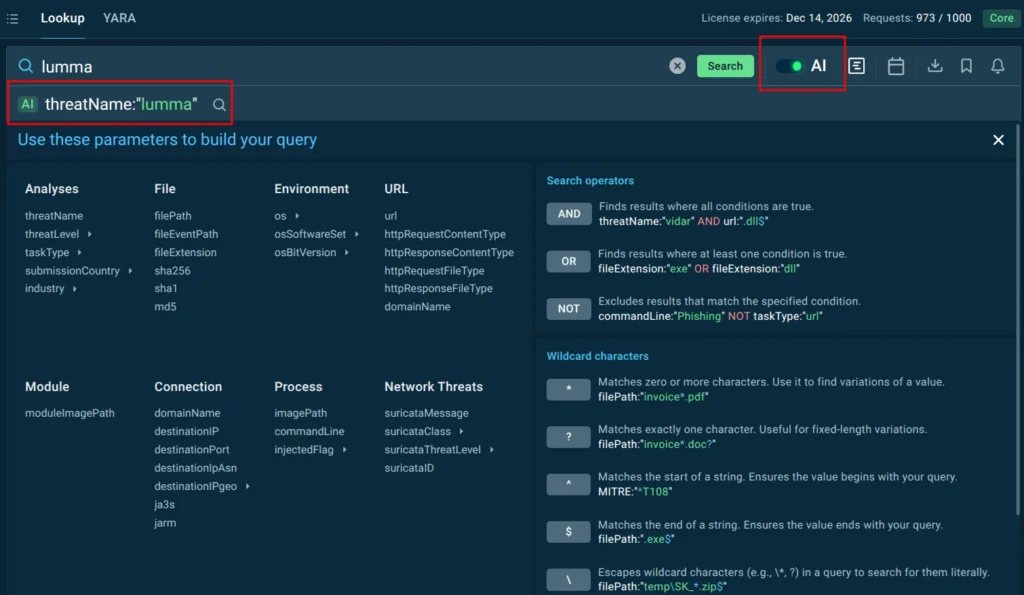
Each indicator in TI Lookup’s database is linked to a sandbox session, where it was observed, providing analysts with a complete view of the attack, including its TTPs.
When integrated into existing SOC workflows, this context becomes available almost instantly, supporting more independent Tier 1 decision-making, and reserving senior analyst capacity for cases that genuinely require escalation.
- Triage alerts faster: Two-second access to millions of past analyses confirms if an IOC belongs to a threat, cutting triage time.
- Shorten response time: Indicator enrichment with behavioral context and TTPs guide precise containment strategies.
- Reduce unnecessary escalations: Provides Tier 1 analysts with the info to make decisions independently, reducing escalations to Tier 2.
Connectors and integrations for TI Lookup
| TheHive | Torq |
| IBM Security QRadar SOAR | Google SecOps SOAR |
| Splunk SOAR | Splunk Enterprise |
| Tines | OpenCTI |
| SentinelONE |
Please note: If your solution is not on the list, you can easily set up a custom integration using ANY.RUN’s API or Python-based SDK (see docs on GitHub or PyPi).
Integrate ANY.RUN’s Solutions in Your SOC
ANY.RUN brings malware analysis and threat intelligence into the SIEM, SOAR, EDR, and other systems already supporting daily security operations, equipping your SOC with the visibility, speed, and efficiency needed to stay ahead.
With ready-made connectors flexible API/SDK, organizations can strengthen existing security investments rather than rebuild their stack: expand threat coverage, reduce repetitive analyst work, accelerate investigations, and scale SOC capacity more efficiently.
About ANY.RUN
Trusted by over 700,000 cybersecurity professionals and 16,000+ organizations in finance, healthcare, manufacturing, and other critical industries, ANY.RUN helps security teams investigate threats faster and with greater accuracy.
Our Interactive Sandbox accelerates incident response by allowing you to analyze suspicious files in real time, watch behavior as it unfolds, and make confident, well-informed decisions.
Our Threat Intelligence Lookup and Threat Intelligence Feeds strengthen detection by providing the context your team needs to anticipate and stop today’s most advanced attacks.
FAQ
ANY.RUN Interactive Sandbox integrates with Splunk SOAR, Microsoft Sentinel, Microsoft Defender, Google Security Operations, ThreatConnect, Tines, Torq, and many more. Custom integrations are also available through the ANY.RUN API and SDK.
ANY.RUN TI Feeds integrate with Elastic Security, Microsoft Sentinel, Microsoft Defender, Splunk, QRadar SIEM, and other security solutions. TI Feeds can also be delivered via STIX/TAXII.
ANY.RUN TI Lookup integrates with Splunk, Torq, Tines, QRadar SOAR, and other security solutions, bringing threat context directly into existing investigation workflows.
Yes. ANY.RUN supports Splunk integrations across its threat intelligence and malware analysis products, including Interactive Sandbox actions and TI Lookup in Splunk SOAR and threat intelligence delivery for Splunk environments.
Yes. ANY.RUN integrates with Microsoft Sentinel, enabling security teams to bring threat intelligence from TI Feeds and malware analysis capabilities from Interactive Sandbox into Microsoft security workflows.
Yes. ANY.RUN supports integrations with Microsoft Defender for threat intelligence and sandbox analysis, helping teams enrich detection and investigation workflows with additional threat context.
Yes. ANY.RUN TI Feeds integrate with Elastic Security to deliver fresh threat indicators directly into existing detection, triage, and investigation workflows.
0 comments