Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Spynote

129
Global rank
141 infographic chevron month
Month rank
129 infographic chevron week
Week rank

SpyNote, also known as SpyMax and CypherRat, is a powerful Android malware family designed primarily for surveillance and data theft, often categorized as a Remote Access Trojan (RAT). Originally emerged in 2016, SpyNote has evolved significantly, with new variants continuing to appear as recently as 2023–2025.

RAT
Type
Unknown
Origin
1 June, 2016
First seen
28 September, 2026
Last seen
Also known as
SpyMax
CypherRat

How to analyze Spynote with ANY.RUN

RAT
Type
Unknown
Origin
1 June, 2016
First seen
28 September, 2026
Last seen

IOCs

IP addresses
94.141.122.123
142.251.127.81
142.251.154.119
142.251.150.119
142.251.157.119
195.189.240.74
142.251.156.119
142.251.20.94
216.239.35.12
142.251.151.119
192.178.183.139
195.189.240.75
142.251.152.119
142.251.13.94
142.251.20.138
142.251.153.119
216.239.35.8
13.226.247.39
142.251.110.101
64.233.166.81
Hashes
1005a525006f148c86efcbfb36c6eac091b311532448010f70f7de9a68007167
fbcfe23a2ecb82b7100c50811691dde0a33aa3da8d176be9882a9db485dc0f2d
0f1bad70c7bd1e0a69562853ec529355462fcd0423263a3d39d6d0d70b780443
58efdfe40baf9802b6e717c2a149afbd698dd64fccdf2ef79f489083ce5f8b65
25dc00877c5ce951cc090d341f880f0ffed0e955896d448e2ca59d7fe83833ee
0fafc8ab15355fca31a19f342222c872786cf55c01dbcce3357f5ca24da11214
e717c7ebd24117cfbdaa053ff5a6bcaa409f380c35881afb1f06711cd7ba47c4
1cef597b50213015133e9815ad1fd494c5042e0b81f270469345915cf3a603b4
bf3d3c5d03eef85ece1e16c4f3e81e6af2f1c36101054abff476c64b5011e96d
93d5b99ce542812a4265dd8ac9cfec74eaf53bff7ee13584e64dfb96eba8a22a
8aa743b1848e5d14a17d72dce5569a6c9187b98c2a028077fea693532b5aabf1
3b9d18d5cc3af6c0cb3e903327ae3da35634c7c3a0b11413b9a3b1c10c640d5e
efc6a645799ce64a05e8b4cf4fd4561847db9b38010107adc68237ddfe802dfd
b09f9f9cac4a20521c8c4025074b5751c9cd7c0d7015d7461876cfb9da5d0488
85f6f38c86005ed98280af1dc0924895dbdc7edf814dc49a8f8fde4e278af81f
bdfab01ba39f908018ae7200689da129070443bf7c0ce0e7027a10f4685b8bed
412a8aa4c566920e3efa4cba25ad6e8618fbd51e8f723a19f2801a7347e6b652
86e0404b20c1fb7e4a8677b9e2dbf02d78f41940dce0685f5fad96c399b573be
1c27419463b0aeb908c9dacb85add26833abfd7254424f2d7d3e70512ba9a686
6682d38d2adca3358f92f9b5f4a8590fa53bfdc9aa7b274ab991db2c4079436a
Domains
connectivitycheck.gstatic.com
update.googleapis.com
www.google.com
time.android.com
clientservices.googleapis.com
diia.gov.ua
google.com
staging-remoteprovisioning.sandbox.googleapis.com
m.stripe.com
d26b395fwzu5fz.cloudfront.net
static-fonts-css.strikinglycdn.com
uploads.strikinglycdn.com
static-assets.strikinglycdn.com
p.typekit.net
static-fonts.strikinglycdn.com
cdnjs.cloudflare.com
m.stripe.network
happypiggy.mystrikingly.com
api.keen.io
edgedl.me.gvt1.com
URLs
http://connectivitycheck.gstatic.com/generate_204
https://www.google.com/generate_204
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:fetcheekchain
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabooc7nzmbilsty9swfkrusfhgy3gl4u_hgre=&request_id=17c35b6a-02e4-48cc-8395-2f0623dd4aa9
https://update.googleapis.com/service/update2/json?cup2key=15:m0jj7zaxnf-b1xajjdud8v5sttgsfejr4cuzwjm0hwa&cup2hreq=de1835f9bd29e5512b1af5eaa26f0b0e67540127aa703a77b79f2816833f79cc
https://clientservices.googleapis.com/chrome-variations/seed?osname=android_webview&milestone=137
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabojtjxkobilsty7njd31ckxmpzdvs9hdf9bi=&request_id=d66a08e0-e878-4a79-9f91-2e77695d1fc7
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaaboivbfd0bilstyxjxdgy9rk0gfwnesq973es=&request_id=551dbbed-6032-4100-ac75-f371d9bfad73
https://update.googleapis.com/service/update2/json?cup2key=15:enjmewrndmexlj0modujbcfij5skqsopzgiyenryy8y&cup2hreq=7db2b167a8dff95e97ea14ef09cdd5c403550a212493ac8eaaeff72f7b234a66
https://update.googleapis.com/service/update2/json
https://edgedl.me.gvt1.com/edgedl/release2/chrome_component/acmmwq7dser4xm5sepzjv74g65vq_2023.7.28.10/cffplpkejcbdpfnfabnjikeicbedmifn_2023.07.28.10_all_acgbwixmcanakp2bkoppyszsbkrq.crx3
https://happypiggy.mystrikingly.com/
https://static-fonts-css.strikinglycdn.com/css?family=playfair+display:400,700,400italic,700italic|playfair+display+sc:regular,italic,700,700italic,900,900italic|montserrat:400,700&subset=latin,latin-ext&display=swap
https://static-assets.strikinglycdn.com/themes/s5-theme/main_v4.53f4fd74d72bc3e5c93f.bundle.css
https://static-assets.strikinglycdn.com/images/fb_images/default.png
https://static-assets.strikinglycdn.com/detectie-c385c24313ef0e9e4e7a1e131bf5e59f0fbd468f9f9ef44fd6739ae84ef0c0a4.js
https://static-assets.strikinglycdn.com/images/ecommerce/ecommerce-footer-logo.png
https://static-assets.strikinglycdn.com/i18n-2ace11ac644d0b40fb8b7cb65e9dd1e553022750e0254118dacbe1fe50735e97.js
https://static-assets.strikinglycdn.com/webpack/lightboostedpage-site-bundle.4ac6ea1bdb388e4a88b9.js
https://custom-images.strikinglycdn.com/res/hrscywv4p/image/upload/c_limit,fl_lossy,h_300,w_300,f_auto,q_100/13403996/512140_449643.png
Last Seen at

Recent blog posts

post image
Threat Coverage Digest: New Malware Reports a...
watchers 6945
comments 0
post image
Phishing Response Protocol: 3 Essential SOC S...
watchers 9046
comments 0
post image
Major Cyber Attacks in September 2026: US and...
watchers 13157
comments 0

What is SpyNote malware?

SpyNote (aka SpyMax and CypherRat) is a Remote Access Trojan (RAT) designed for Android devices. It evades detection while maintaining persistent access and provides attackers with extensive control over infected devices, enabling:

  • Keylogging
  • Screen recording & screenshots
  • Call & SMS interception
  • Microphone & camera activation
  • File theft & remote execution
  • GPS tracking
  • App manipulation (uninstalling security apps).

SpyNote primarily spreads through social engineering tactics, exploiting user trust to install the malware on Android devices. Its infiltration methods include phishing and smishing campaigns when users receive malicious emails and text messages posing as legitimate communications from banks, service providers, or trusted entities, urging users to download fake apps or updates. For example, campaigns have mimicked Italian government alerts or antivirus software. Other examples included SpyNote posing as critical services, such as power or water suppliers, to create urgency and prompt immediate installation.

Targeted attacks, especially against high-value individuals in South Asia, have used WhatsApp to deliver SpyNote payloads disguised as legitimate files. This malware has been hosted on deceptive websites mimicking legitimate platforms, such as Google Play Store pages or antivirus software sites (e.g., fake Avast Mobile Security)

SpyNote has been caught impersonating trusted applications, such as banking apps (e.g., HSBC, Deutsche Bank), system updates, productivity tools, and games. This trojan is frequently distributed through unofficial app stores or sideloaded APKs, bypassing Google Play’s security checks.

Read about Salvador Stealer, another Android threat abusing mobile banking

Once installed, SpyNote requests permissions, particularly Accessibility Services, which it abuses to grant itself additional permissions without user intervention, ensuring deep access to the device.

Besides exfiltrating sensitive data (SMS messages, call logs, contacts, GPS location, files, photos, credentials), SpyNote captures keystrokes and screenshots and activates the microphone and camera to record audio, phone calls, or videos. It allows attackers to initiate transactions and execute arbitrary commands. It can also install additional apps or malware, update itself, or uninstall apps to maintain persistence.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

SpyNote RAT’s Prominent Features

SpyNote is especially notable and dangerous due to its versatility and targeting of sensitive data and sectors:

  • Financial Sector: Targets banking apps (e.g., HSBC, Deutsche Bank, Bank of America) to steal credentials, perform on-device fraud, or bypass 2FA, leading to financial losses. Recent variants focus on cryptocurrency wallets, enabling unauthorized transfers.
  • Critical Infrastructure and Services: Poses as essential service providers (e.g., power, water, or emergency alerts) to exploit user urgency, potentially disrupting trust in legitimate services.
  • High-Value Targets: Used by APT groups to spy on government agencies, NGOs, media organizations, and activists, particularly in South Asia. Campaigns have targeted Indian defense personnel and other high-profile individuals.
  • Widespread Accessibility: Source code leaks (e.g., CypherRat in October 2022) have made SpyNote widely available on darknet forums and Telegram, enabling independent actors and organized groups to deploy custom variants. Variants like SpyNote.A, SpyNote.B, SpyNote.C, SpyMax, Crax RAT, and Eagle Spy continue to evolve with enhanced capabilities.
  • Persistence: Its ability to resist uninstallation and survive reboots makes it a long-term threat, often requiring a factory reset, which results in data loss.

SpyNote’s Execution Process and Technical Details

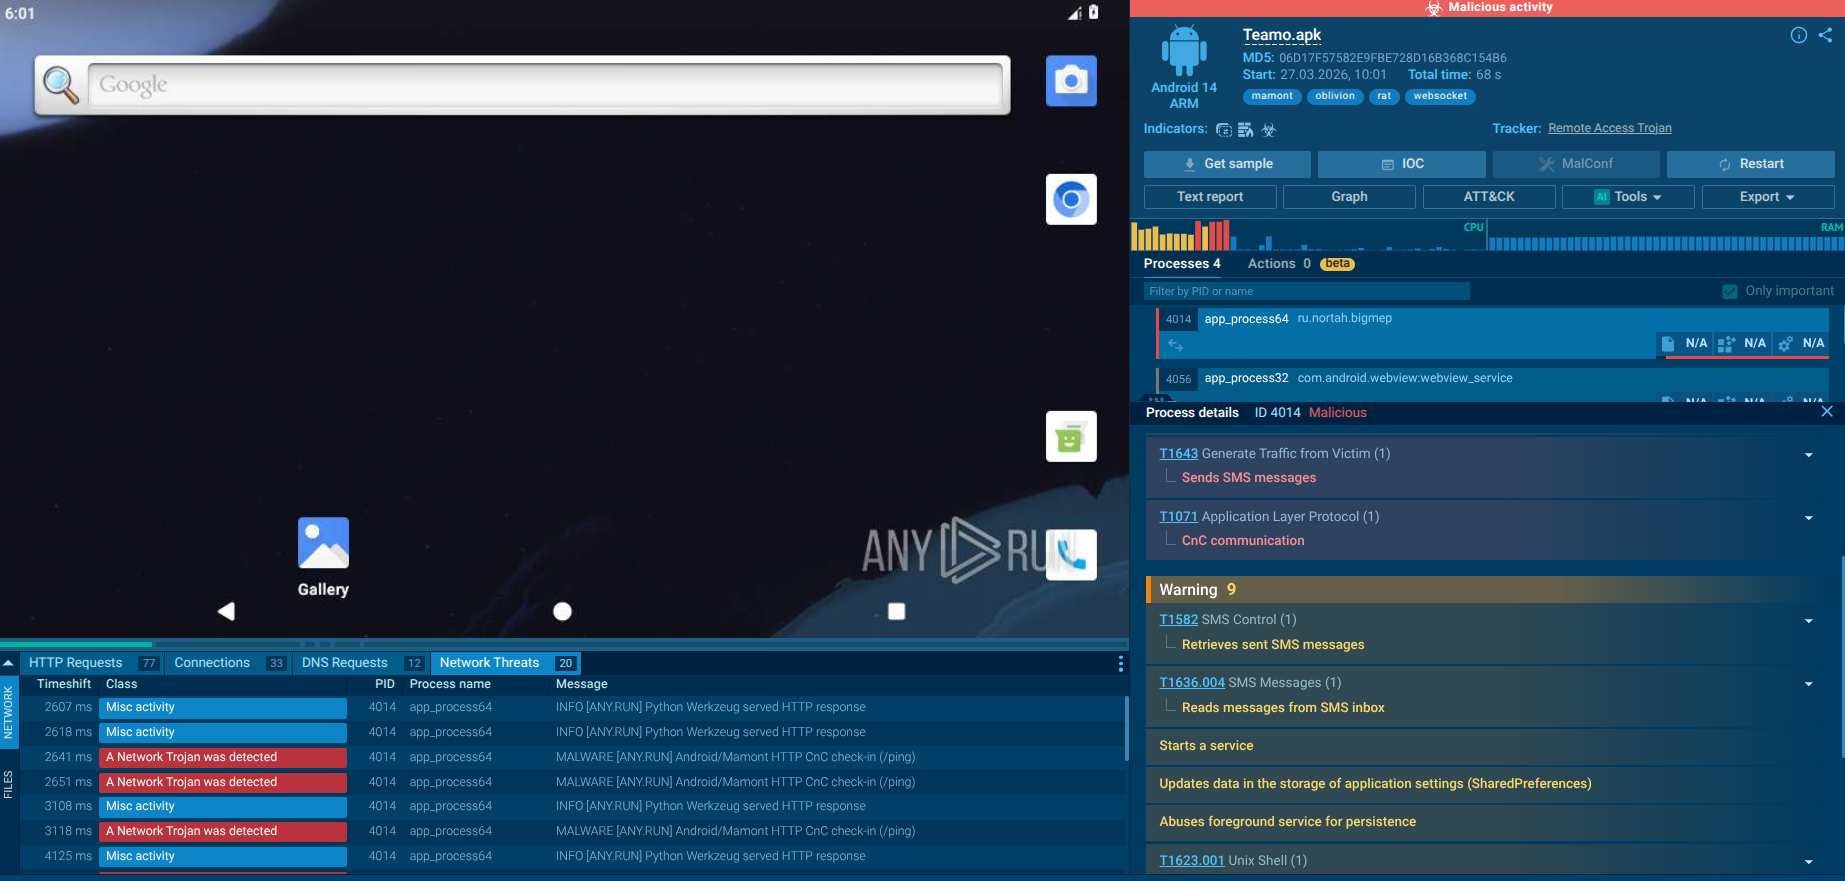
ANY.RUN’s Interactive Sandbox supports the analysis of APK files and enables the research of Android malware, so we can watch SpyNote in action after detonating its APK disguised as an app of the Spanish BBVA Bank in the safe VM environment.

View the analysis session

SpyNote’s execution chain starts with deceptive distribution. Operators clone Google Play pages or send SMS phishing links that claim you need a popular app update or mobile‑banking tool. Tapping the “Install” or “Download” button triggers a short JavaScript snippet that silently drops a tampered APK — often branded with a convincing name and icon like “BBVA Prime” in our case — onto the device.
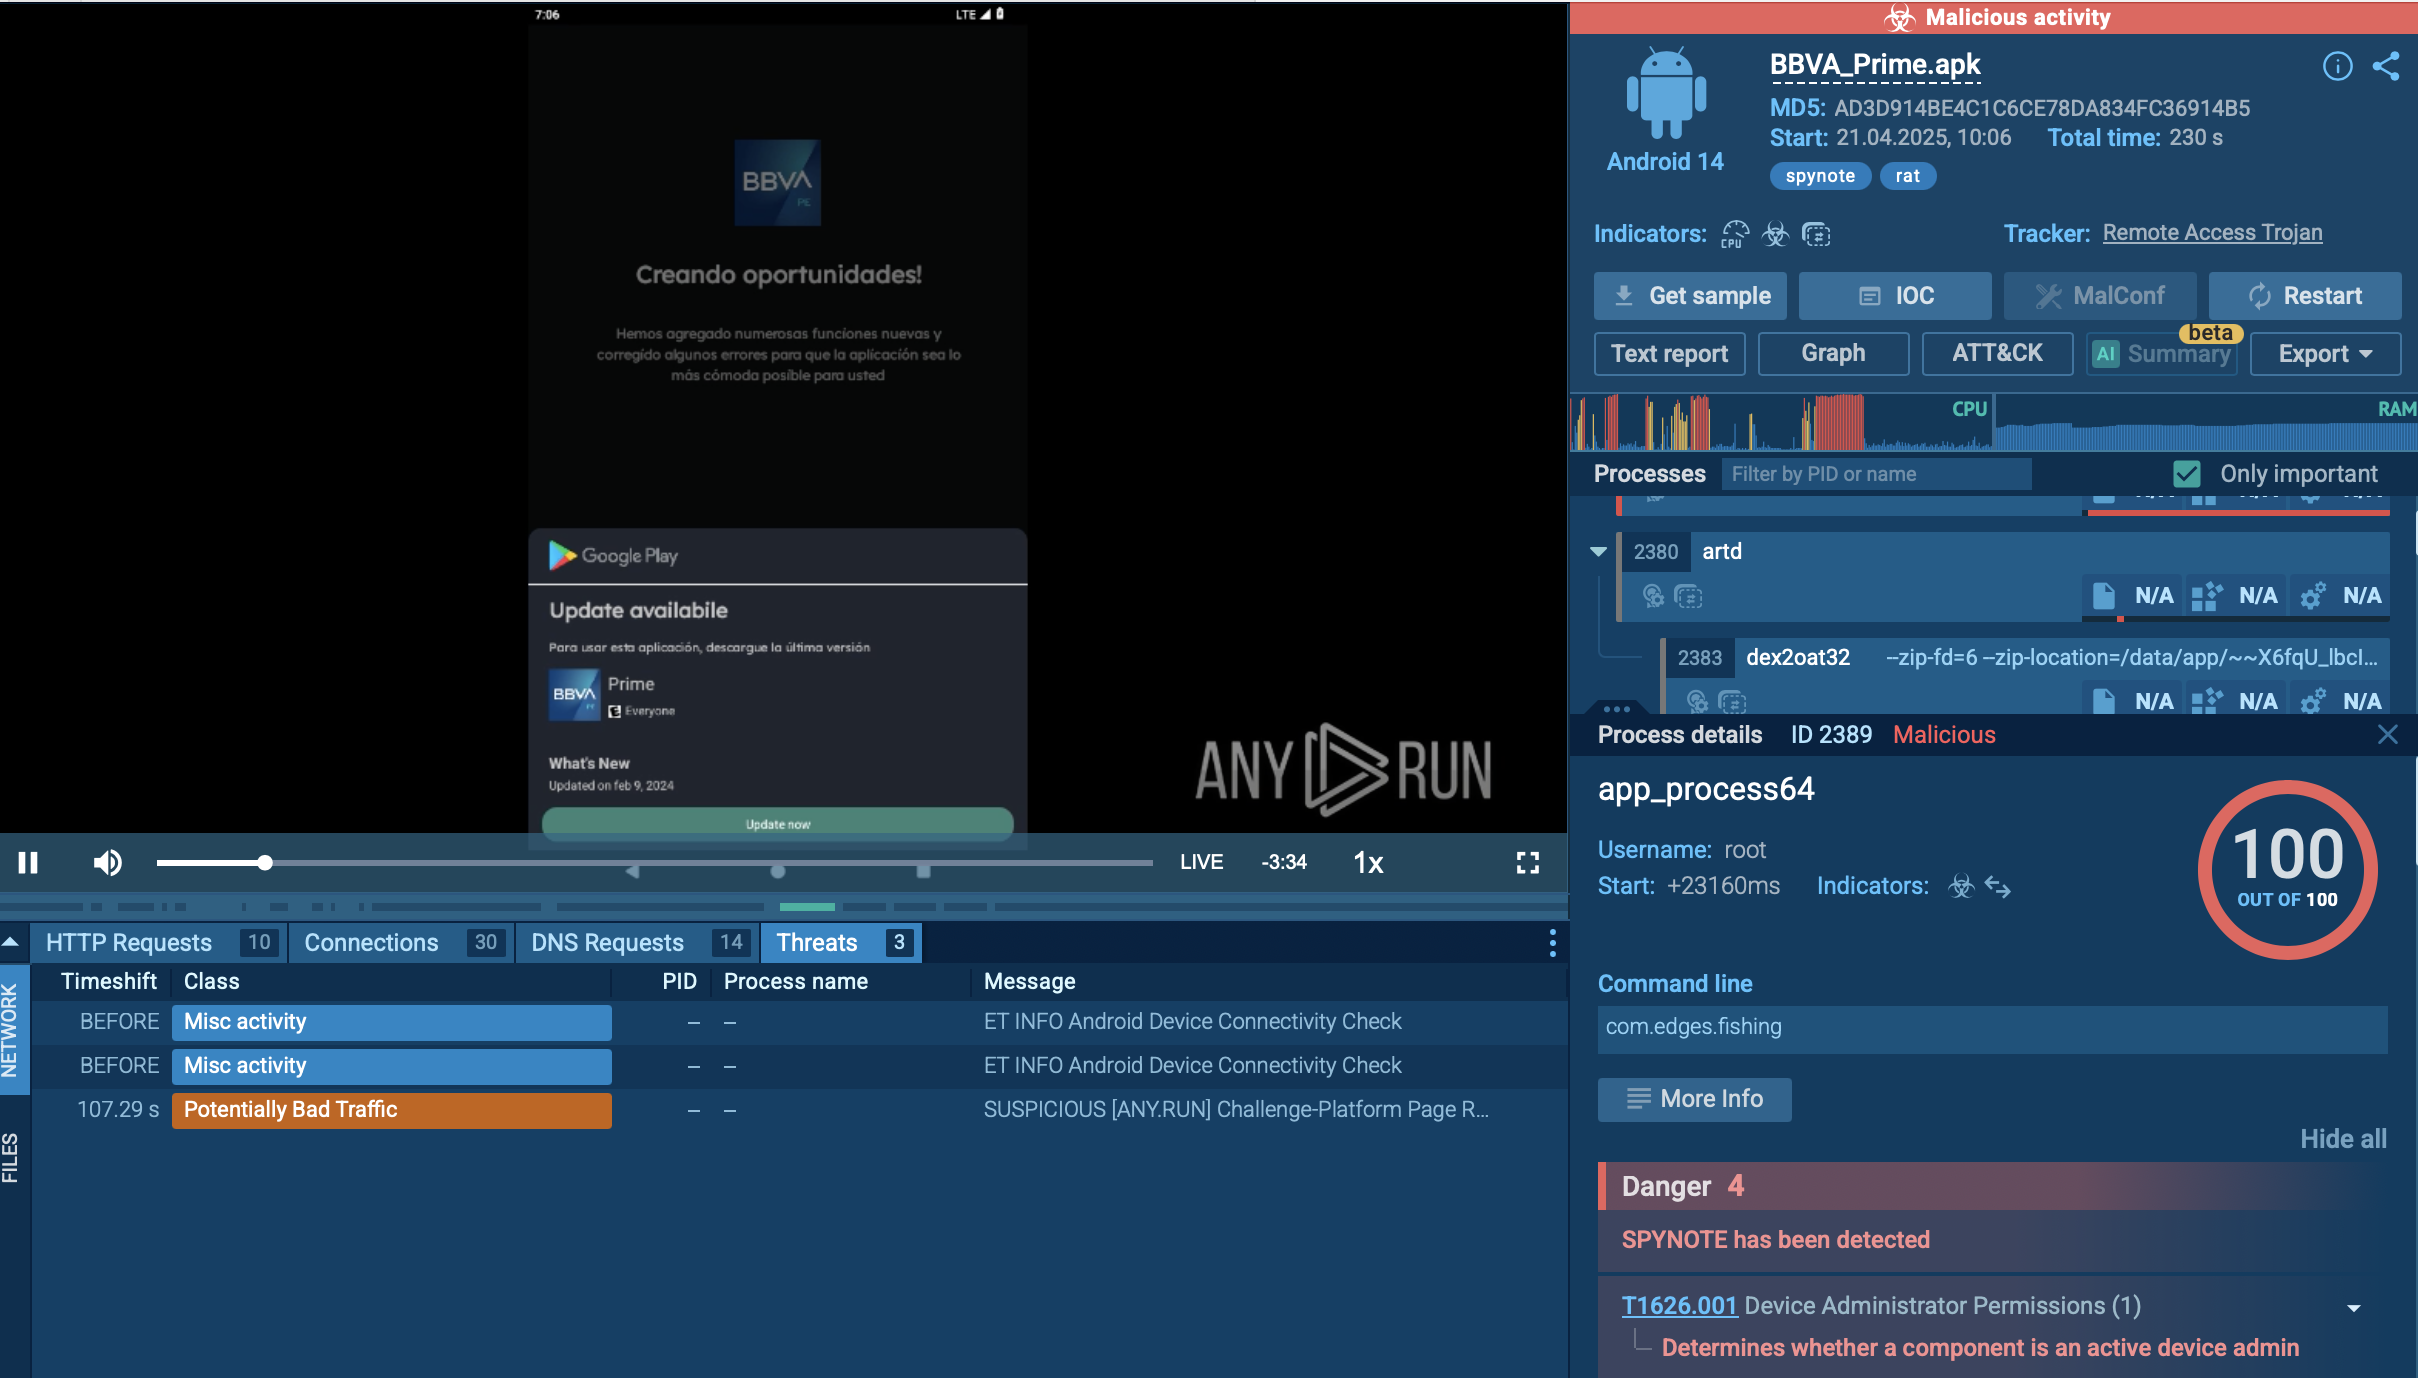
SpyNote malware analysis in ANY.RUN A sample of SpyNote detonated inside ANY.RUN's Interactive Sandbox

When the user opens the app, SpyNote asks for permissions such as Accessibility Service access. Granting that single request is enough: using Accessibility, the malware auto‑clicks its way through every subsequent dialogue to secure dangerous privileges — including reading and sending SMS, recording audio, taking photos, accessing contacts, call logs, and external storage — without showing more pop‑ups.

To avoid discovery, SpyNote immediately hides its icon from the launcher and recent‑apps screen. The implant can then be awakened by several triggers: receipt of certain SMS commands, an outgoing phone call, a visit to a specific URL, or an auxiliary “launcher” dropper that sends an explicit intent. Once active, it establishes an encrypted channel to hard‑coded command‑and‑control servers for tasking and data exfiltration.

Capabilities are extensive: intercepting and forwarding 2FA codes, logging keystrokes, capturing screenshots, recording calls, activating the microphone and both cameras, tracking GPS, and silently downloading further payloads. If the victim opens Settings or long‑presses the app in an attempt to uninstall, SpyNote leverages the same Accessibility control to close those windows or quickly restart its own service, making removal nearly impossible without booting into safe mode or using ADB.

Finally, the authors layer heavy code obfuscation, dynamic string encryption, and anti‑emulator checks to frustrate static scanners and researchers. Dynamic cloud sandboxes like ANY.RUN, however, can still surface its behavior by executing the sample on real Android images, revealing the full attack chain.

What are the best-known SpyNote campaigns?

  • Financial Sector Focus (2022–2023): SpyNote.C began targeting banks like HSBC, Deutsche Bank, and Kotak Bank, combining spyware and banking trojan features.
  • European Surge (June–July 2023): Cleafy reported aggressive campaigns targeting European banks via phishing and smishing.
  • Cryptocurrency Theft (2024): New variants targeted crypto wallets, using Accessibility APIs to steal gestures and initiate transfers.
  • Fake Antivirus Campaigns (2024): SpyNote posed as Avast Mobile Security, using 14 domains to distribute malware.
  • Fake Google Play Pages (2025): Recent campaigns used deceptive websites mimicking Google Play to deliver SpyNote.

Gathering Threat Intelligence on SpyNote malware

ANY.RUN’s Threat Intelligence Lookup aggregates information about Android malware samples analyzed in the Interactive Sandbox. A number of SpyNote-bearing recently encountered APKs are available for investigating and collecting IOCs:
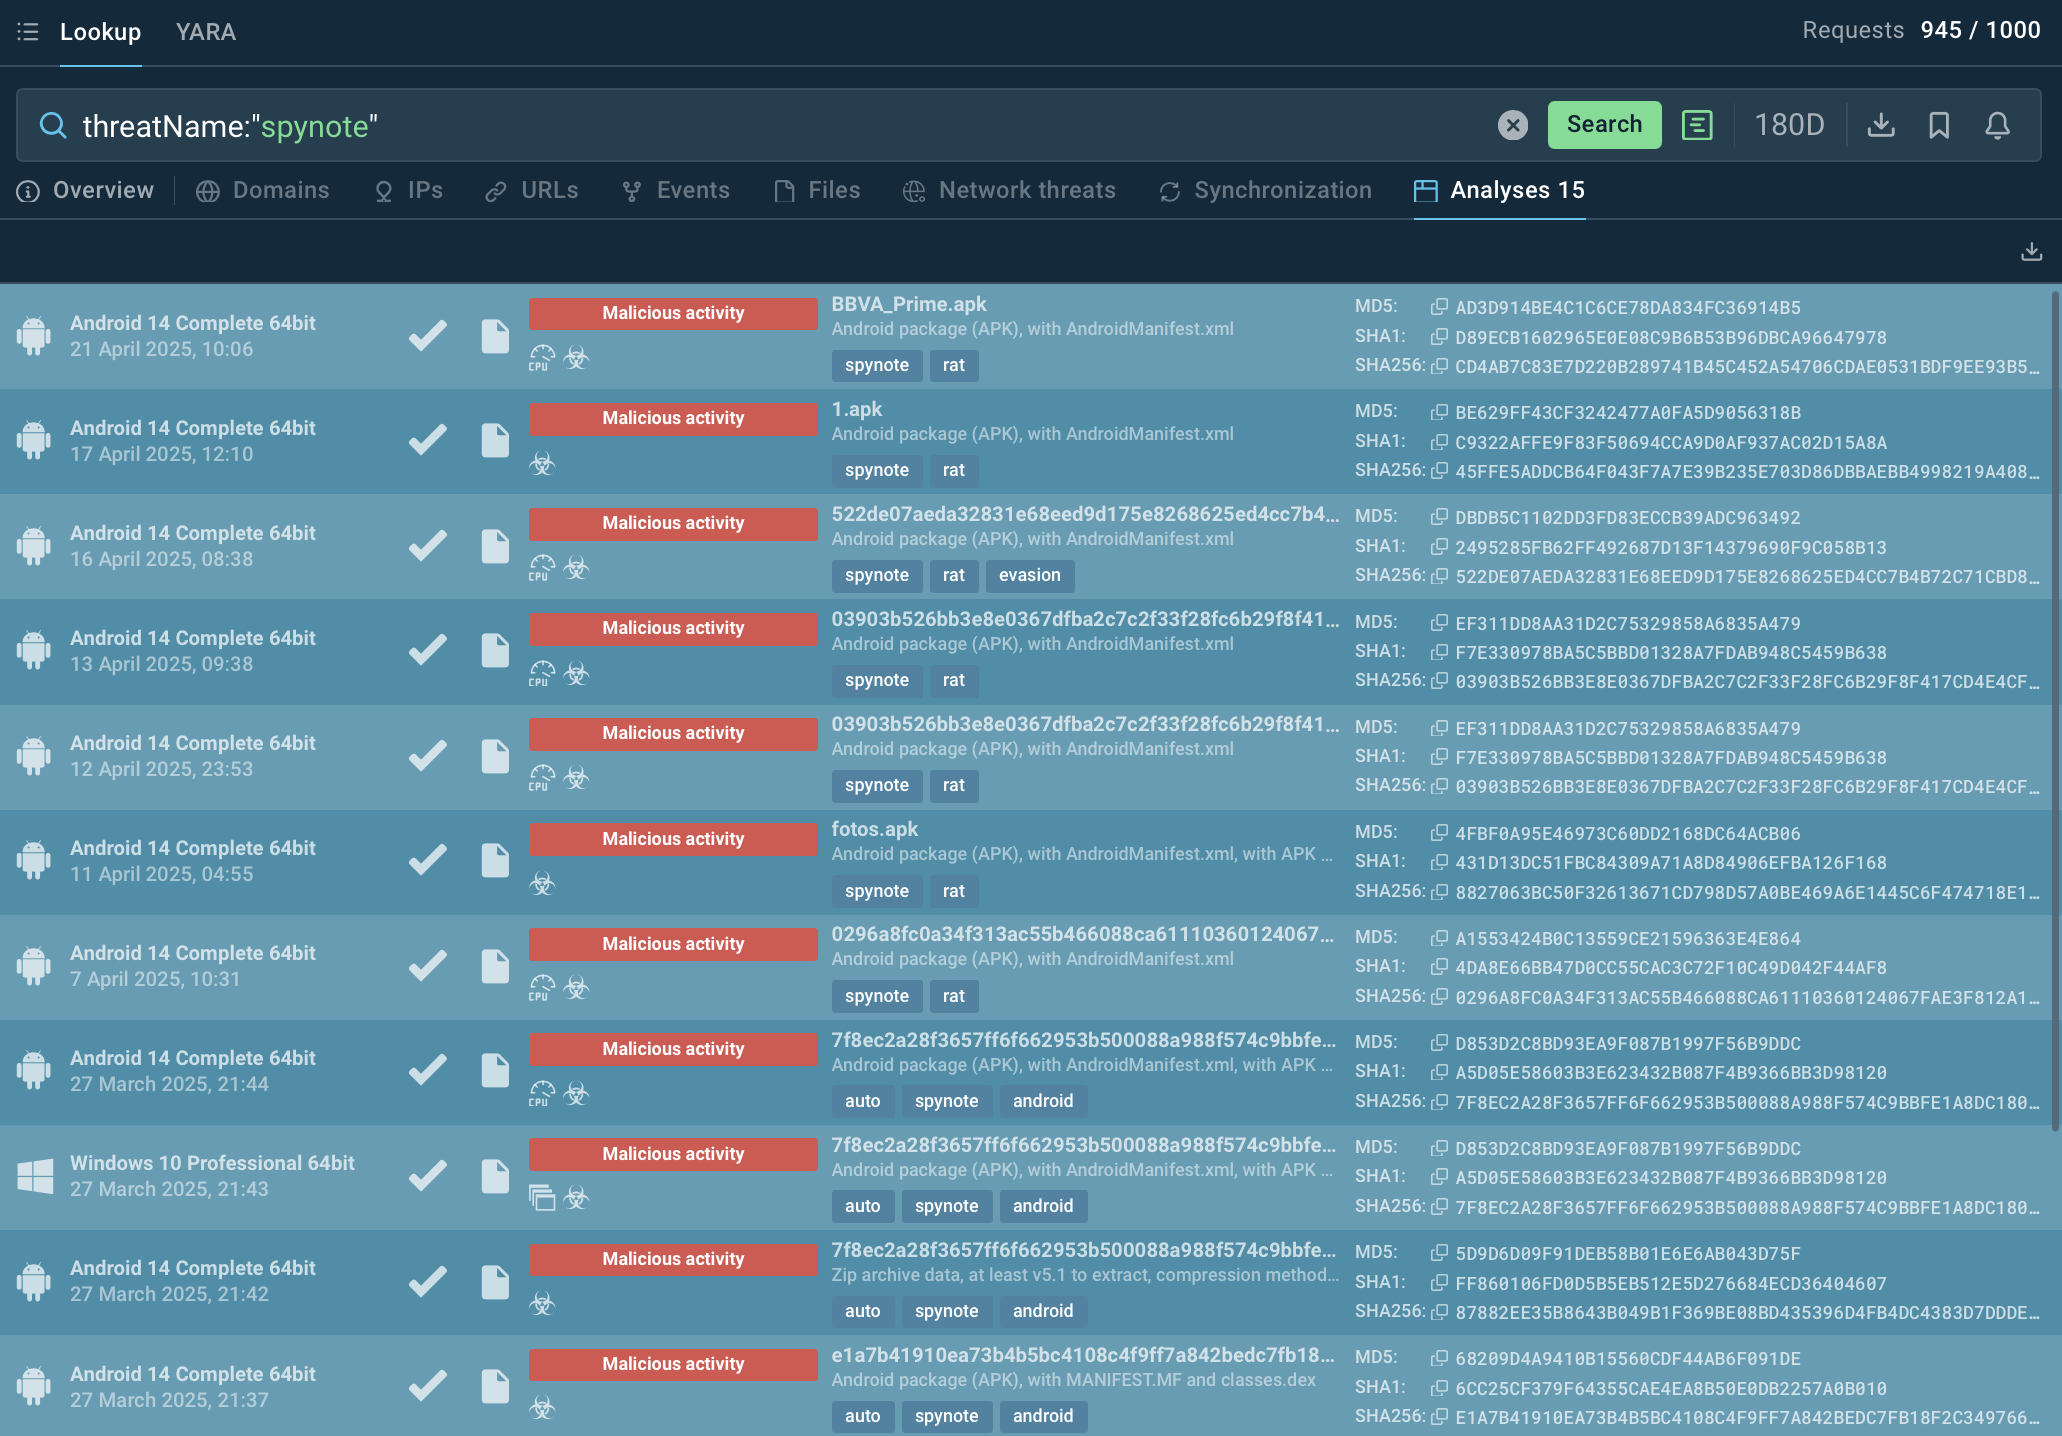
threatName:"SpyNote"

SpyNote malware samples in ANY.RUN Malicious APKs added by the Sandbox users

Each analysis session in the Sandbox contains a number of IOCs. Use them as search requests to TI Lookup for further exploring the threat and gathering data for monitoring and detection.
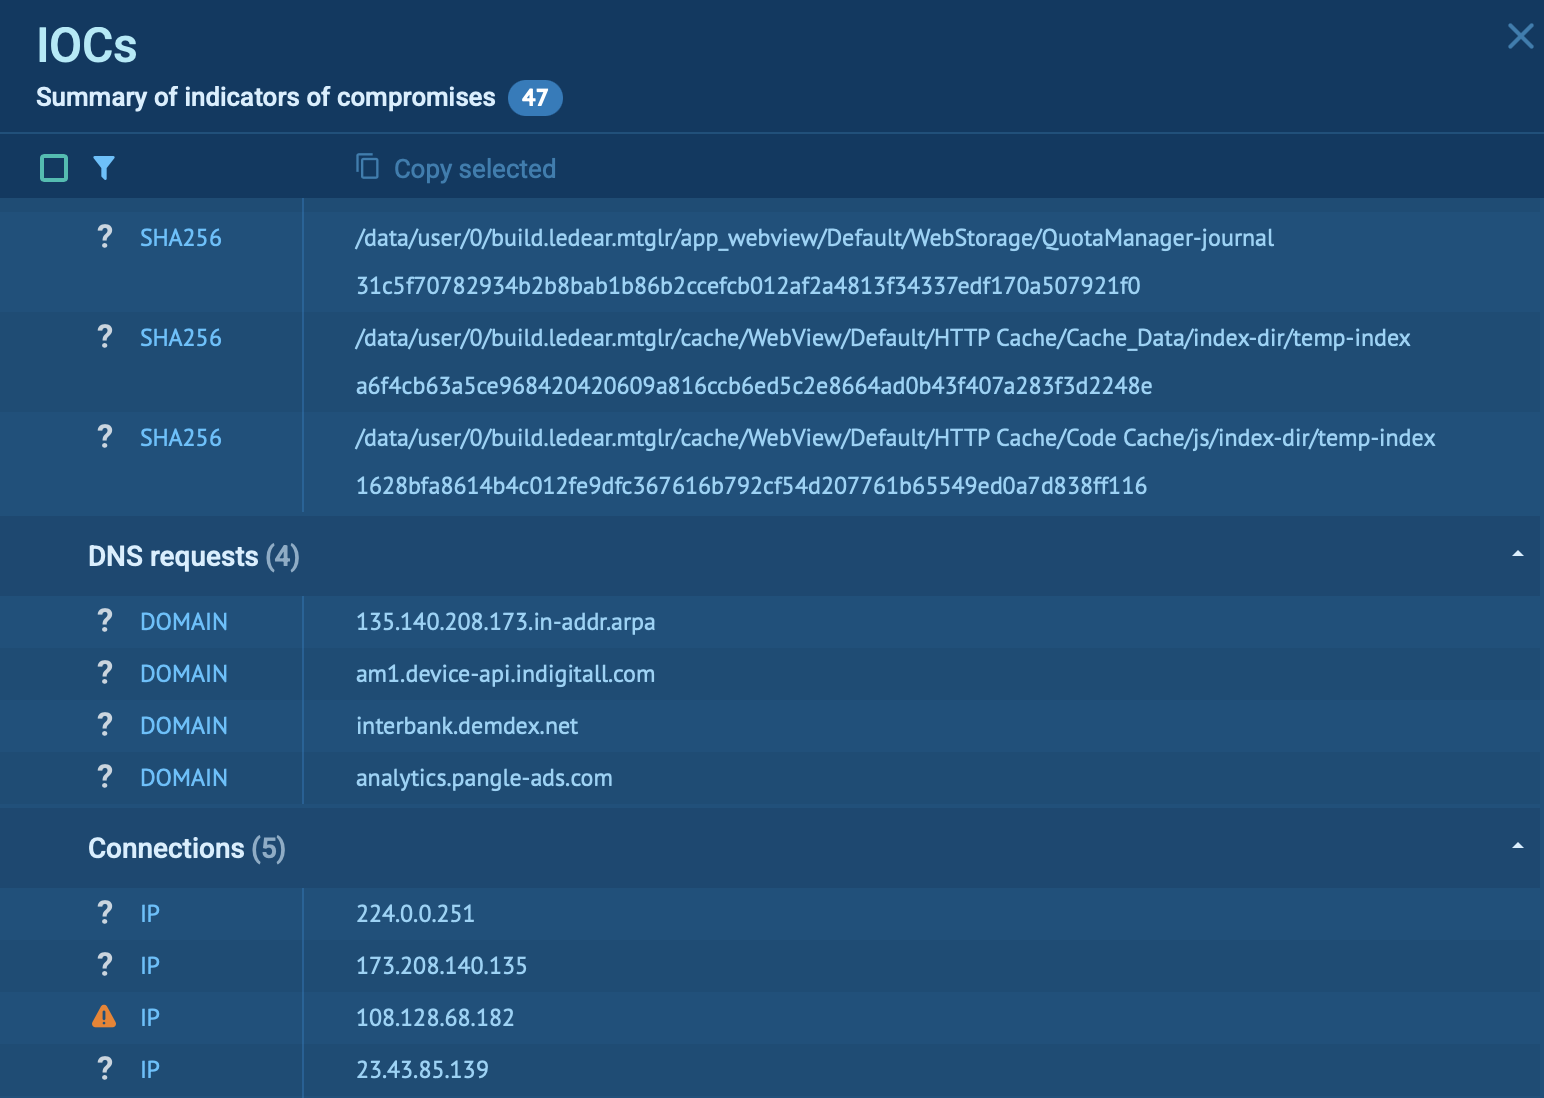
IOCs from SpyNote analysis Indicators of compromise from one of SpyNote samples

You can also view processes initiated by the malware to get the full picture of its operational paradigm and explore its TTPs.
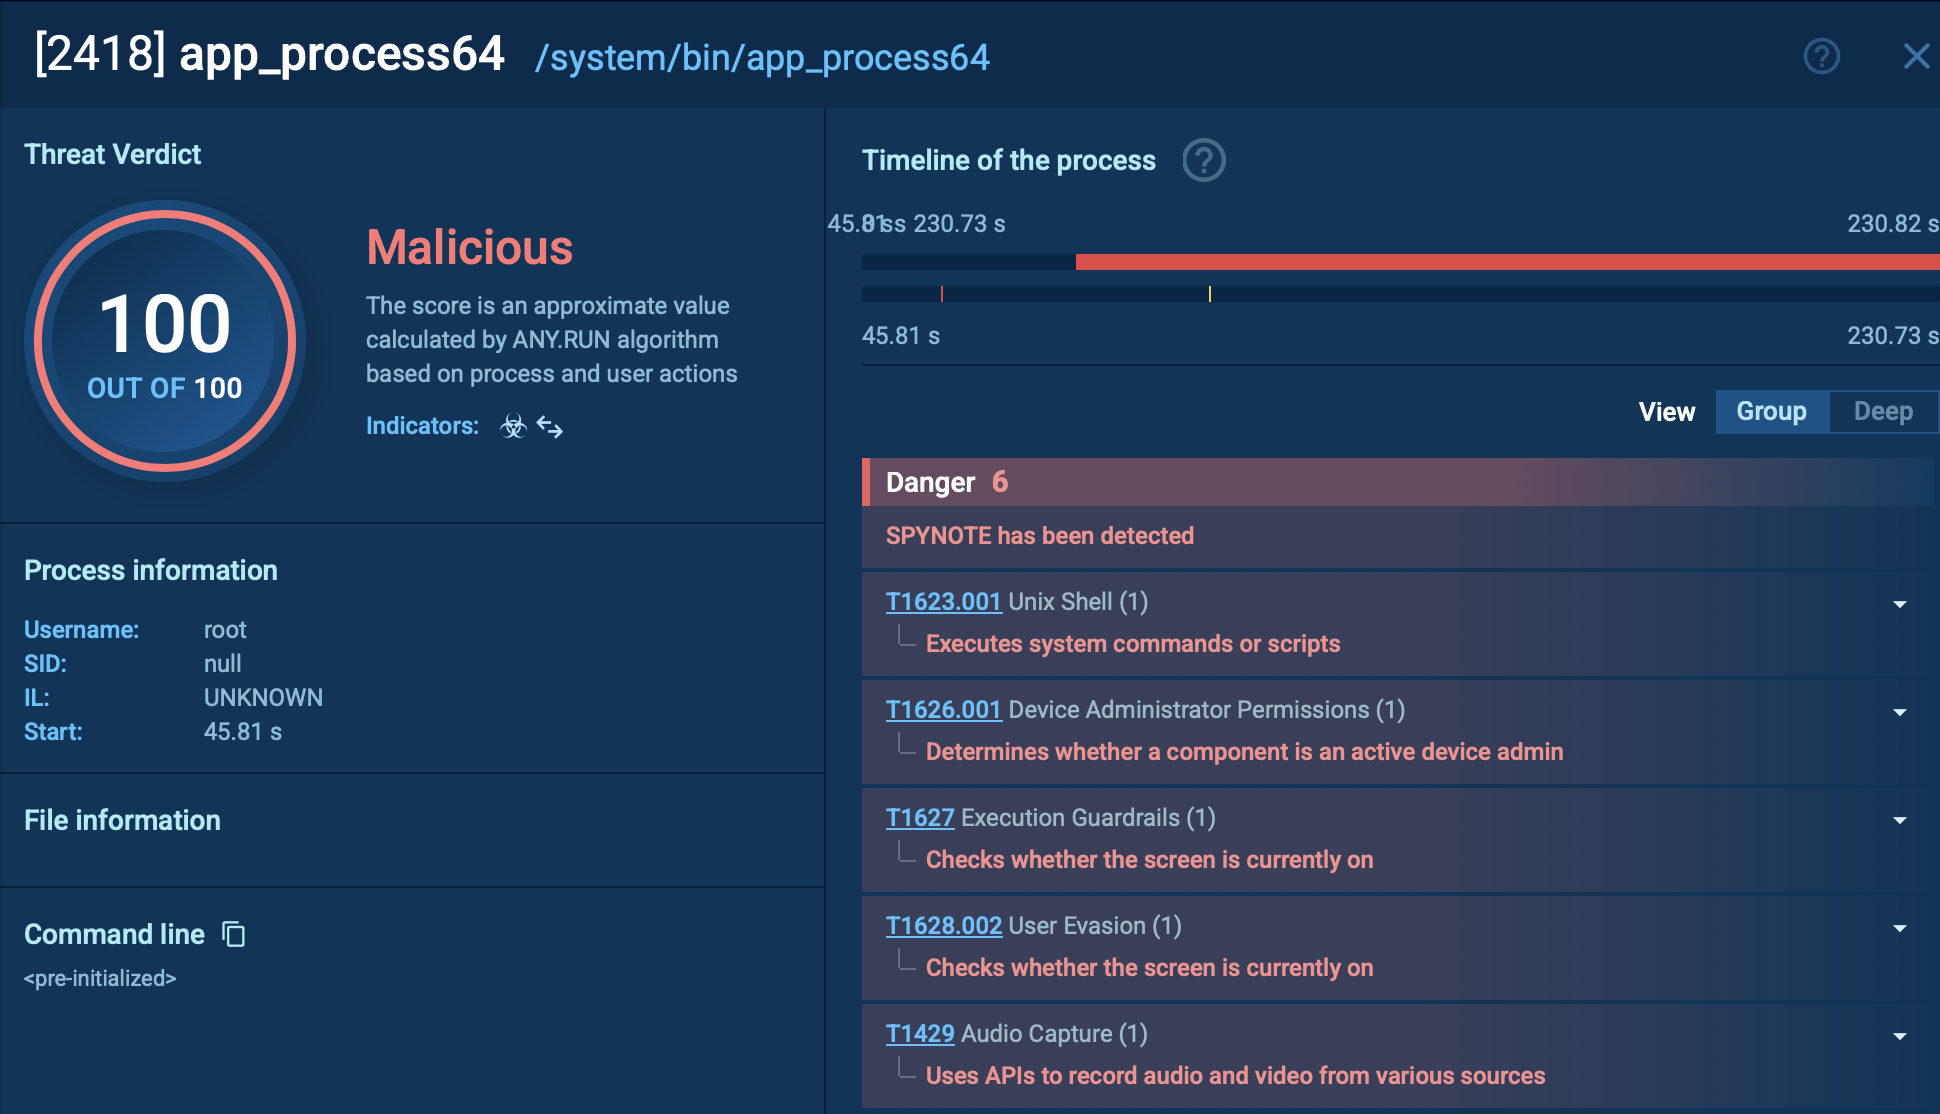
SpyNote malicious processes SpyNotes activities step by step with links to TTPs
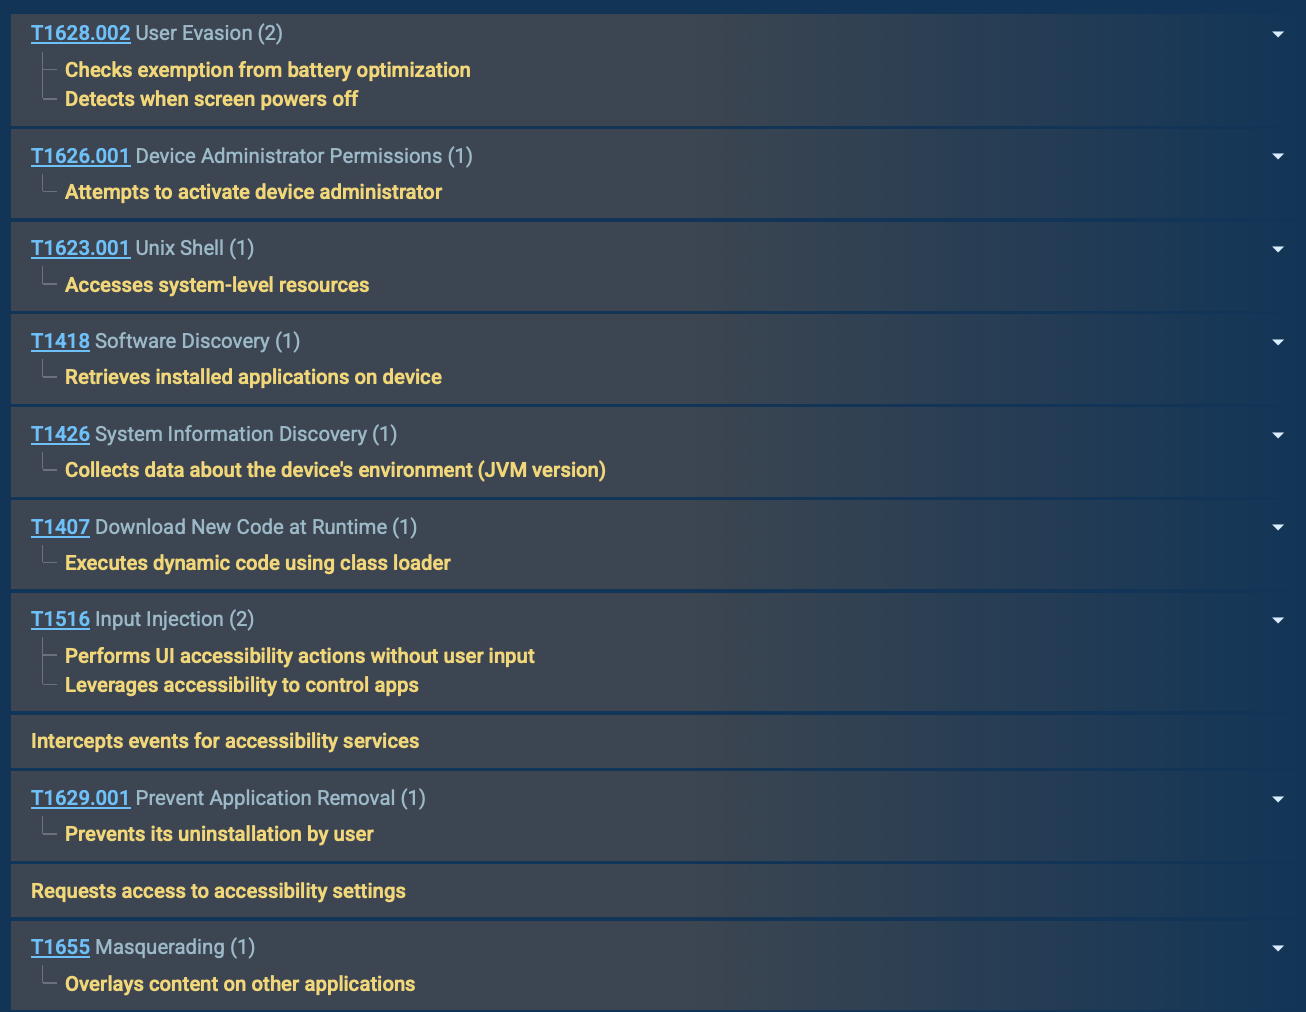
SpyNote malicious processes continued SpyNote malicious processes, continued

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

SpyNote is a sophisticated Android Remote Access Trojan (RAT) that has evolved into a significant threat since its emergence around 2016. It targets Android devices, primarily to steal sensitive data, monitor user activities, and enable remote control by cybercriminals.

It is highly dangerous due to its advanced capabilities, widespread availability, and focus on financial fraud, privacy invasion, and targeted espionage. By leveraging threat intelligence, behavioral and signature-based detection, and proactive countermeasures, users and organizations can mitigate the risks posed by SpyNote.

Engage ANY.RUN’s Threat Intelligence Lookup with 50 trial requests to collect IOCs, enhance your understanding of the malware, and enforce protection.
HAVE A LOOK AT

LockBit screenshot
LockBit
lockbit
LockBit, a ransomware variant, encrypts data on infected machines, demanding a ransom payment for decryption. Used in targeted attacks, It's a significant risk to organizations.
Read More
Quasar RAT screenshot
Quasar RAT
quasar trojan rat
Quasar is a very popular RAT in the world thanks to its code being available in open-source. This malware can be used to control the victim’s computer remotely.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More
Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More