Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

LimeRAT

93
Global rank
98 infographic chevron month
Month rank
103 infographic chevron week
Week rank

LimeRAT is Remote Administration Trojan malware that boasts an array of harmful capabilities. While masquerading as a legitimate tool, it can perform malicious operations like encryption, keylogging, and cryptomining, which makes it appealing to cybercriminals

RAT
Type
Unknown
Origin
1 March, 2019
First seen
9 October, 2026
Last seen

How to analyze LimeRAT with ANY.RUN

RAT
Type
Unknown
Origin
1 March, 2019
First seen
9 October, 2026
Last seen

IOCs

IP addresses
74.178.76.128
92.123.104.26
20.190.159.68
48.192.1.64
48.209.133.15
172.211.123.248
150.171.109.106
174.26.204.152
23.52.181.212
104.20.29.150
74.178.240.51
92.123.104.63
57.153.246.3
92.122.215.99
95.100.102.101
23.194.190.165
48.192.1.65
48.209.138.168
172.211.123.250
2.16.241.9
Hashes
e76749d70a685f5f5456ce90f223404e2b7f143544426f17610a2b020b721886
5f04524c2fe7662661d539f3847e618384aa24809701fc6ef84808e2eb435a75
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
04bc6ef6e5662cc62e738045d36d9fdc5f8c7f582de3b08069444495a265dedc
7af2cedd425df2f75b7c0b6385b97a5a2e836f66ee435bbe52bd6819cd37951f
ad43efbad7622320311fd3f680e3f4281886f3abdaf573fe94bfe315d3044c29
ac3ec20f5e37df3fb4f6b3434815325e3fd8a335276d4ce5c94ecbf4dd2c2e88
19c17d6ad4a98a6d61f448ed366023850c2eadda5a9d597fdf2f94c6bf8464bc
f2c0d90744c5d6862586b03602321270d1baec10009b57af6aba4b71357bec11
24c5d82f79e5a49883feb1752908efccfc93ba03dfa7830f1ee3ce3853f98411
9eadb7215ace208c135ec495c993b582f729bcd380c80d38193a2b6206fa52a7
c929b8afdacf114c7c0fde13b05dce53feecb013c3b5d3a01ac4ef3448b1aa5f
6fcdba6da3c3b1e802b8a05b598316608eccdf7b35c25fb71657e80633079f1b
ccbdc206d2e8eeb8280bd7cf10d545e302c91a22b0885d09154b9ec36c331489
07412da4d5b337d55dda92a10f40b2184e76b57479d7364666529e1da8e11603
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
0e24672ae24a06f2c30bfeaa1c72bdd0916285097115fb105ef00b7c926375a7
10c1bc765592e1e577eb2ed279fc31fc213c5e0a5ce88ce295535d3ffbb6ff43
54a5ec6205c8e24ca57013f57ffc10f374ddfc91b2187eff643be92f5e7fd602
Domains
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
crl.microsoft.com
self.events.data.microsoft.com
google.com
slscr.update.microsoft.com
ecs.office.com
activation-v2.sls.microsoft.com
login.live.com
pastebin.com
www.microsoft.com
settings-win.data.microsoft.com
www.bing.com
go.microsoft.com
vny.st
ocsp.digicert.com
api.msn.com
realpython.com
edge.microsoft.com
img-s-msn-com.akamaized.net
URLs
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.1.crl
https://pastebin.com/raw/zvu0mns4
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://vny.st/raw/n3xem_1d
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 3232
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 5364
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 8137
comments 0

What is LimeRAT malware and cryptocurrency stealer?

Lime Remote Administration Tool (LimeRAT) is a versatile Remote Access Trojan, which also may function as ransomware, cryptominer, cryptocurrency stealer, worm, keylogger, and bot. This versatility is one of the traits that set it apart from other RATs, such as njRAT.

Similarly to Quasar RAT, LimeRAT’s code is written in C#, but is dependent on .NET 4.0, and is a part of an open-source malware library that includes Lime_Miner, Lime_Crypter, and Lime_USB. While it claims to be an educational tool for .NET malware, its robust and well-documented features make it an attractive choice for malicious activities.

Lime RAT uses multiple ports for communication, allowing for redundancy in communication channels. The initial setup only requires port numbers and an AES 128-bit encryption key for secure communication between the client and server. The payloads can be created with a simple interface of checkboxes and text input fields, allowing even inexperienced operators to produce potent, malicious binaries. Customizations include different features and icons, and settings for Command and Control infrastructure and the location for persistent drop files on targeted machines.

Once a payload has been sent to and executed on a target machine, it connects to the control panel, sending details about the system it's on, including OS, CPU, user, and more.

The panel can also automatically assign tasks, such as downloading and executing specific files. The operator can issue commands to the infected machine, initiating various attacks, including encryption for ransomware, mining Monero, enabling Remote Desktop Protocol, or stealing information.

The malware can spread like a worm through USB or pinned task bar applications. Its ransomware feature encrypts the targeted host, changing file extensions to '.Lime'. It also includes a rudimentary keylogging feature, logging only keyboard inputs, not auto-filled or clipboard data.

The screengrab feature within the control panel captures screenshots of the infected machine, while its logging feature records timestamps and IPs of connections and disconnections. Despite being an open-source, well-documented malware, Lime RAT poses a serious threat, capable of stealing a range of valuable information, encrypting data for ransom, and converting the target host into a bot.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

LimeRAT malware technical details

LimeRAT employs advanced obfuscation techniques (MITRE T1027), rendering the classes, methods, and variables in its code into a series of random glyphs. This complex obfuscation aids in evasion of static analysis.

Embedded within LimeRAT's configuration class is a Base64 encoded string. This string isn't just encoded but also encrypted, demonstrating the malware's sophisticated design. Deciphering the string involves a comprehensive understanding of LimeRAT's decryption algorithm.

The decryption mechanism is built upon the RijndaelManaged class — an implementation of the AES encryption algorithm — and the MD5CryptoServiceProvider class. To generate the AES key for decryption, LimeRAT uses the MD5 hash of a particular string from the configuration class. This MD5 hash undergoes a sequence of specific byte manipulations. Post-decryption, the original string is revealed, decoded using the Base64 algorithm, and then decrypted with the AES256-ECB algorithm.

The decrypted string exposes a critical piece of information: a link to a PasteBin note. This link is essentially the C2 address for LimeRAT, serving as a communication channel for the malware to receive commands and exfiltrate data. It's a clear example of the malware's robust concealment tactics, specifically its effective use of encrypted strings to veil C2 communications.
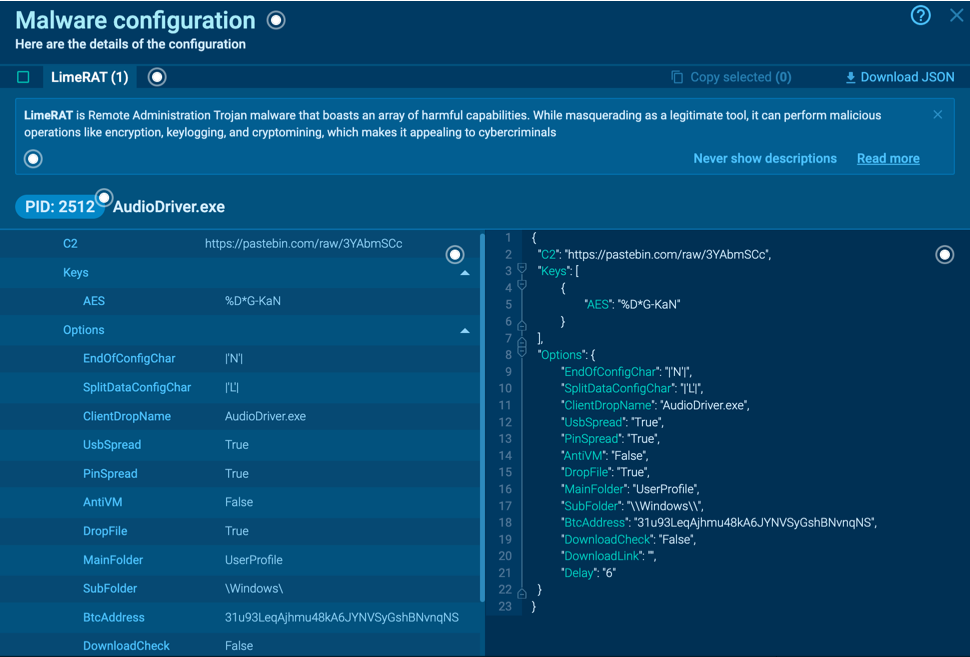
LimeRAT configs LimeRAT’s malware configurations

LimeRAT malware execution process explained

Typical execution flow of the LimeRAT is straight. After the initial access is made, the trojan starts its execution. Firstly, it copies itself into a user directory such as %appdata% or, in our sample, into the directory inside the admin folder. Then it runs with different filenames and starts malicious activity. Further execution flow may vary. In our sample, the C2 server is already dead and doesn't send anything back to malware. When C2 is alive, LimeRAT may download some additional modules based on the commands from C2.

Read a detailed analysis of LimeRAT in our blog.
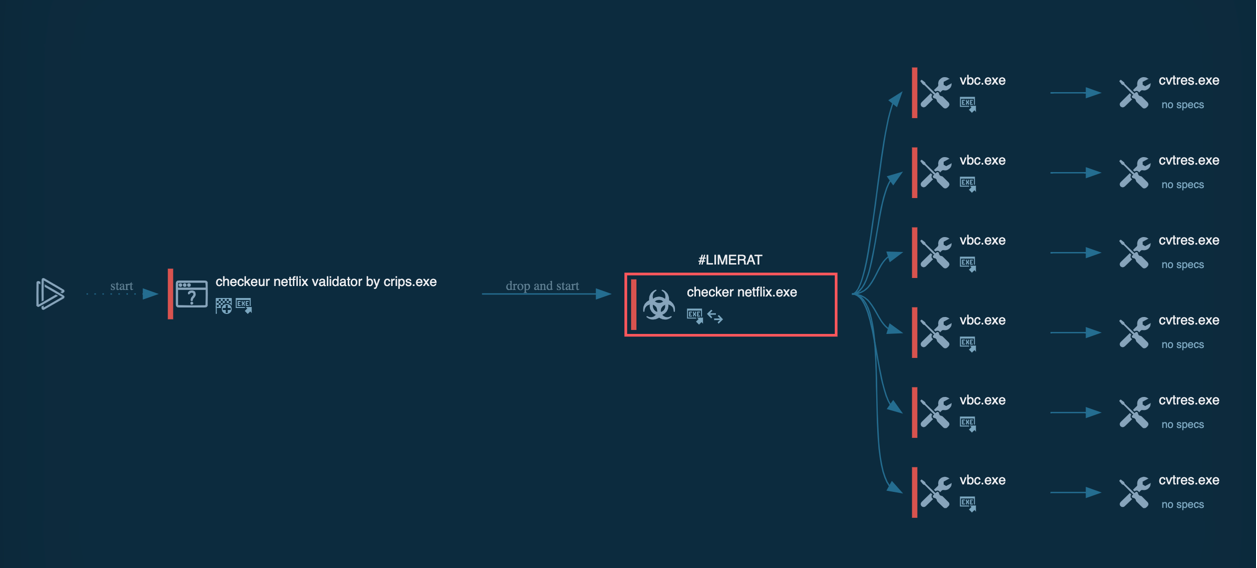
LimeRAT process graph LimeRAT’s process graph

LimeRAT malware distribution methods

LimeRAT primarily propagates through phishing campaigns. It leverages malicious email attachments, often employing embedded macros within Office documents. Upon the execution of these macros, the payload of LimeRAT is released, initiating the infection process. Cracked software, P2P distribution channels and malvertising has also been observed.

Additionally, LimeRAT exploits drive-by downloads. It's designed to take advantage of software vulnerabilities, in both web browsers and installed applications. This can lead to the unintended downloading and installation of LimeRAT merely by visiting a compromised website.

The developers of LimeRAT are persistent in updating its exploits, which maintains its effectiveness against even the latest software patches and updates.

Notably, LimeRAT also employs worm-like behavior for spreading via removable drives. The malware is programmed to replicate itself onto any connected removable drives from an already compromised system. This ability allows LimeRAT to further propagate when these infected drives are connected to other systems.

LimeRAT malware conclusion

LimeRAT's wide range of capabilities, coupled with its lightweight footprint, advanced obfuscation and AES encryption, make it a powerful adversary. While its ability to hide its C2 communication behind encrypted strings shows off the sophisticated tactics adopted by modern malware.

The most effective way to mitigate malware threats like LimeRAT, which are typically spread through phishing, is by educating your team about the potential dangers of malicious emails. For a detailed understanding of how LimeRAT operates, it's recommended to examine its samples using a robust tool like ANY.RUN.

ANY.RUN doesn't just detect and identify this malware family, but it also simplifies the analysis of its execution process. This is particularly useful given that LimeRAT is known for its heavy use of obfuscation, which can make static analysis difficult. With ANY.RUN, the dynamic analysis of this malware becomes a more approachable task.
HAVE A LOOK AT

EvilProxy screenshot
EvilProxy
evilproxy
EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.
Read More
Kali365 screenshot
Kali365 is an emerging Phishing-as-a-Service (PhaaS) platform that targets Microsoft 365 environments by stealing OAuth authentication tokens instead of passwords. First observed in April 2026, the service enables even low-skilled threat actors to bypass multi-factor authentication (MFA), gain persistent access to corporate cloud accounts, and compromise business communications, files, and collaboration platforms. Kali365 represents a shift from traditional credential theft toward session hijacking and token abuse, making it a significant threat to organizations that rely on Microsoft 365.
Read More
Sality screenshot
Sality
sality
Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.
Read More
Stealc screenshot
Stealc
stealc
Stealc is a stealer malware that targets victims’ sensitive data, which it exfiltrates from browsers, messaging apps, and other software. The malware is equipped with advanced features, including fingerprinting, control panel, evasion mechanisms, string obfuscation, etc. Stealc establishes persistence and communicates with its C2 server through HTTP POST requests.
Read More
Phorpiex screenshot
Phorpiex
phorpiex
Phorpiex is a malicious software that has been a significant threat in the cybersecurity landscape since 2016. It is a modular malware known for its ability to maintain an extensive botnet. Unlike other botnets, Phorpiex does not concentrate on DDoS attacks. Instead, it has been involved in numerous large-scale spam email campaigns and the distribution of other malicious payloads, such as LockBit.
Read More
XRed screenshot
XRed
xred
XRed operates as a stealthy backdoor, enabling cybercriminals to gain unauthorized remote access to infected systems. XRed has gained particular notoriety for its distribution through trojanized legitimate software and hardware drivers, making it exceptionally dangerous due to its ability to masquerade as trusted applications.
Read More