Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

GCleaner

70
Global rank
56 infographic chevron month
Month rank
49 infographic chevron week
Week rank

GCleaner is a type of malware loader that has the capability to deliver numerous malicious software programs, which differ based on the location of the targeted victim. This malware is commonly spread through fraudulent websites that advertise free PC optimization tools

Loader
Type
Unknown
Origin
19 September, 2019
First seen
7 October, 2026
Last seen

How to analyze GCleaner with ANY.RUN

Type
Unknown
Origin
19 September, 2019
First seen
7 October, 2026
Last seen

IOCs

IP addresses
20.190.160.128
74.179.77.204
48.209.138.168
74.179.77.164
23.11.41.157
142.251.14.132
142.251.14.94
2.21.239.135
23.59.18.102
23.194.190.165
91.92.242.236
48.192.1.65
204.79.197.203
2.16.204.142
172.211.123.248
109.195.177.157
1.52.220.121
139.175.68.142
64.76.25.127
192.81.131.190
Hashes
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
39c727d70b8bdf5fc324233d0823555eb66ce846119609a22d1cebedbc3cf80c
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
791735e52af30a1c6a750df3837784a34cfe763332e5b45acfd731ddaa159b83
e2c2da27bf6e2c2f8d076b9a95419a249754dc51ce6a4940c80b4af6ec9472e1
cea8d35a92a479c4eb295208aa7326ac0bbffe8b322cb8f566344a3aedb58f8e
f5bd80fbcc4b61b7a0d7dcee014e8e27b3deaae17cd2e1abe7fa1d1e84a71a88
d1111b245f685176180e6f1631e6dc49badf6672368e9ce260c71355165effdf
e6b7e7eda14ccbf350840ea3101d0e2122103ba0897c7f0de5a8ab9347678340
937f694dc3a750c12bbc3951b9fe18f8665be1469178d177d3ede1c95ab8883f
82b558b35028e479c2063a0e3f50478714692f48df9093853bf93aa9b4909471
e801598f5e5c2c96b674d10d03ea6f4a93c6eae29e36a955ad2e3dd25008fe3d
188f9544264ab3cd77641bd2438f70d1e65d3975830208d45a741f7edd2eb355
f1b3e0f2750a9103e46a6a4a34f1cf9d17779725f98042cc2475ec66484801cf
02bdde38e4c6bd795a092d496b8d6060cdbe71e22ef4d7a204e3050c1be44fa9
2026f3c4f830dff6883b88e2647272a52a132f25eb42c0d423e36b3f65a94d08
388a796580234efc95f3b1c70ad4cb44bfddc7ba0f9203bf4902b9929b136f95
d736c413543b6b168dc59769840ae95b5726d428f69a23af1659dea8fb4236c8
31d04c1e4bfdfa34704c142fa98f80c0a3076e4b312d6ada57c4be9d9c7dcf26
e63e7ebe4c2db7e61ffc71af0675e870bcde0a9d8916e5b3be0cb252478030bf
Domains
client.wns.windows.com
nexusrules.officeapps.live.com
www.microsoft.com
google.com
oneocsp.microsoft.com
www.bing.com
slscr.update.microsoft.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
c.pki.goog
th.bing.com
activation-v2.sls.microsoft.com
crl.microsoft.com
login.live.com
ocsp.digicert.com
ecs.office.com
self.events.data.microsoft.com
drive.usercontent.google.com
dns.google
cloudflare-dns.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://c.pki.goog/r/gsr1.crl
https://drive.usercontent.google.com/download?id=1ybvidkzgygnfuu2rbjxxcydrzay5rmdy&export=download&authuser=0&confirm=t
http://c.pki.goog/we2/yk5nphthkqs.crl
http://91.92.242.236/dll
http://91.92.242.236/check
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is the GCleaner loader malware?

The system optimizer market has for a long time been a breeding ground for all kinds of malicious software masking as legitimate to dupe users into downloading and installing it. G-Cleaner, also known as GCleaner, is a notable example of a fake PC optimization program, appearing to be genuine at first glance. In reality, it is a loader designed with one purpose: to get hold of victims’ sensitive data.

GCleaner is a loader, which was first spotted in early 2019. It is capable of a wide variety of malicious activities depending on the payload it is equipped with. Analysts have observed it to drop malware such as AZORult, the Raccoon info stealer, Smoke Loader, RedLine Stealer, and other popular families, depending on the victim’s geographic location.

The GCleaner malware is primarily known as one of the most widespread fake Windows utilities that is intended for targeting both organizations and individuals. It attempts to capitalize on the popularity of system cleaning tools by taking advantage of people’s negligence.

The identity of the individuals responsible for developing the G-Cleaner malware remains a mystery. Nonetheless, experts in the field of cybersecurity suspect that the creation of this malicious software was the work of a highly skilled and organized criminal organization.

Technical details of the GCleaner malicious software

Once G-Cleaner is installed on a computer, it extracts a malicious file in the system's temporary files folder and downloads a payload. For instance, GCleaner often drops AZORult and RedLine, stealers that scan the system for any type of personal information, which from now on becomes known to the attackers, including:

  • Passwords;
  • Credit card details;
  • Crypto addresses.

Although each malware family may exploit different types of vulnerabilities, in most cases, the process involves hijacking the victim’s web browser and then recording their keystrokes.

GCleaner makes use of different persistence mechanisms. For instance, after installation, it creates a number of new processes running in the background. The malware also writes data to a remote process, which is typically a legitimate Windows process. This makes it difficult for antivirus software to detect and remove the malware.

GCleaner attempts to stay hidden by using rootkit capabilities, which allow it to hide its presence from the operating system. As an extra layer of protection, it implements encryption to obfuscate its code, rendering it unreadable and harder for researchers to analyze.

Anti-debugging is also on the menu, which hinders reverse engineering efforts, making it challenging for analysts to debug the code and understand how it works.

Execution process of the GCleaner malware

By utilizing ANY.RUN, we can track the entire execution path of G-Cleaner and retrieve its config automatically. Here is a sample of the malware analyzed in our sandbox.
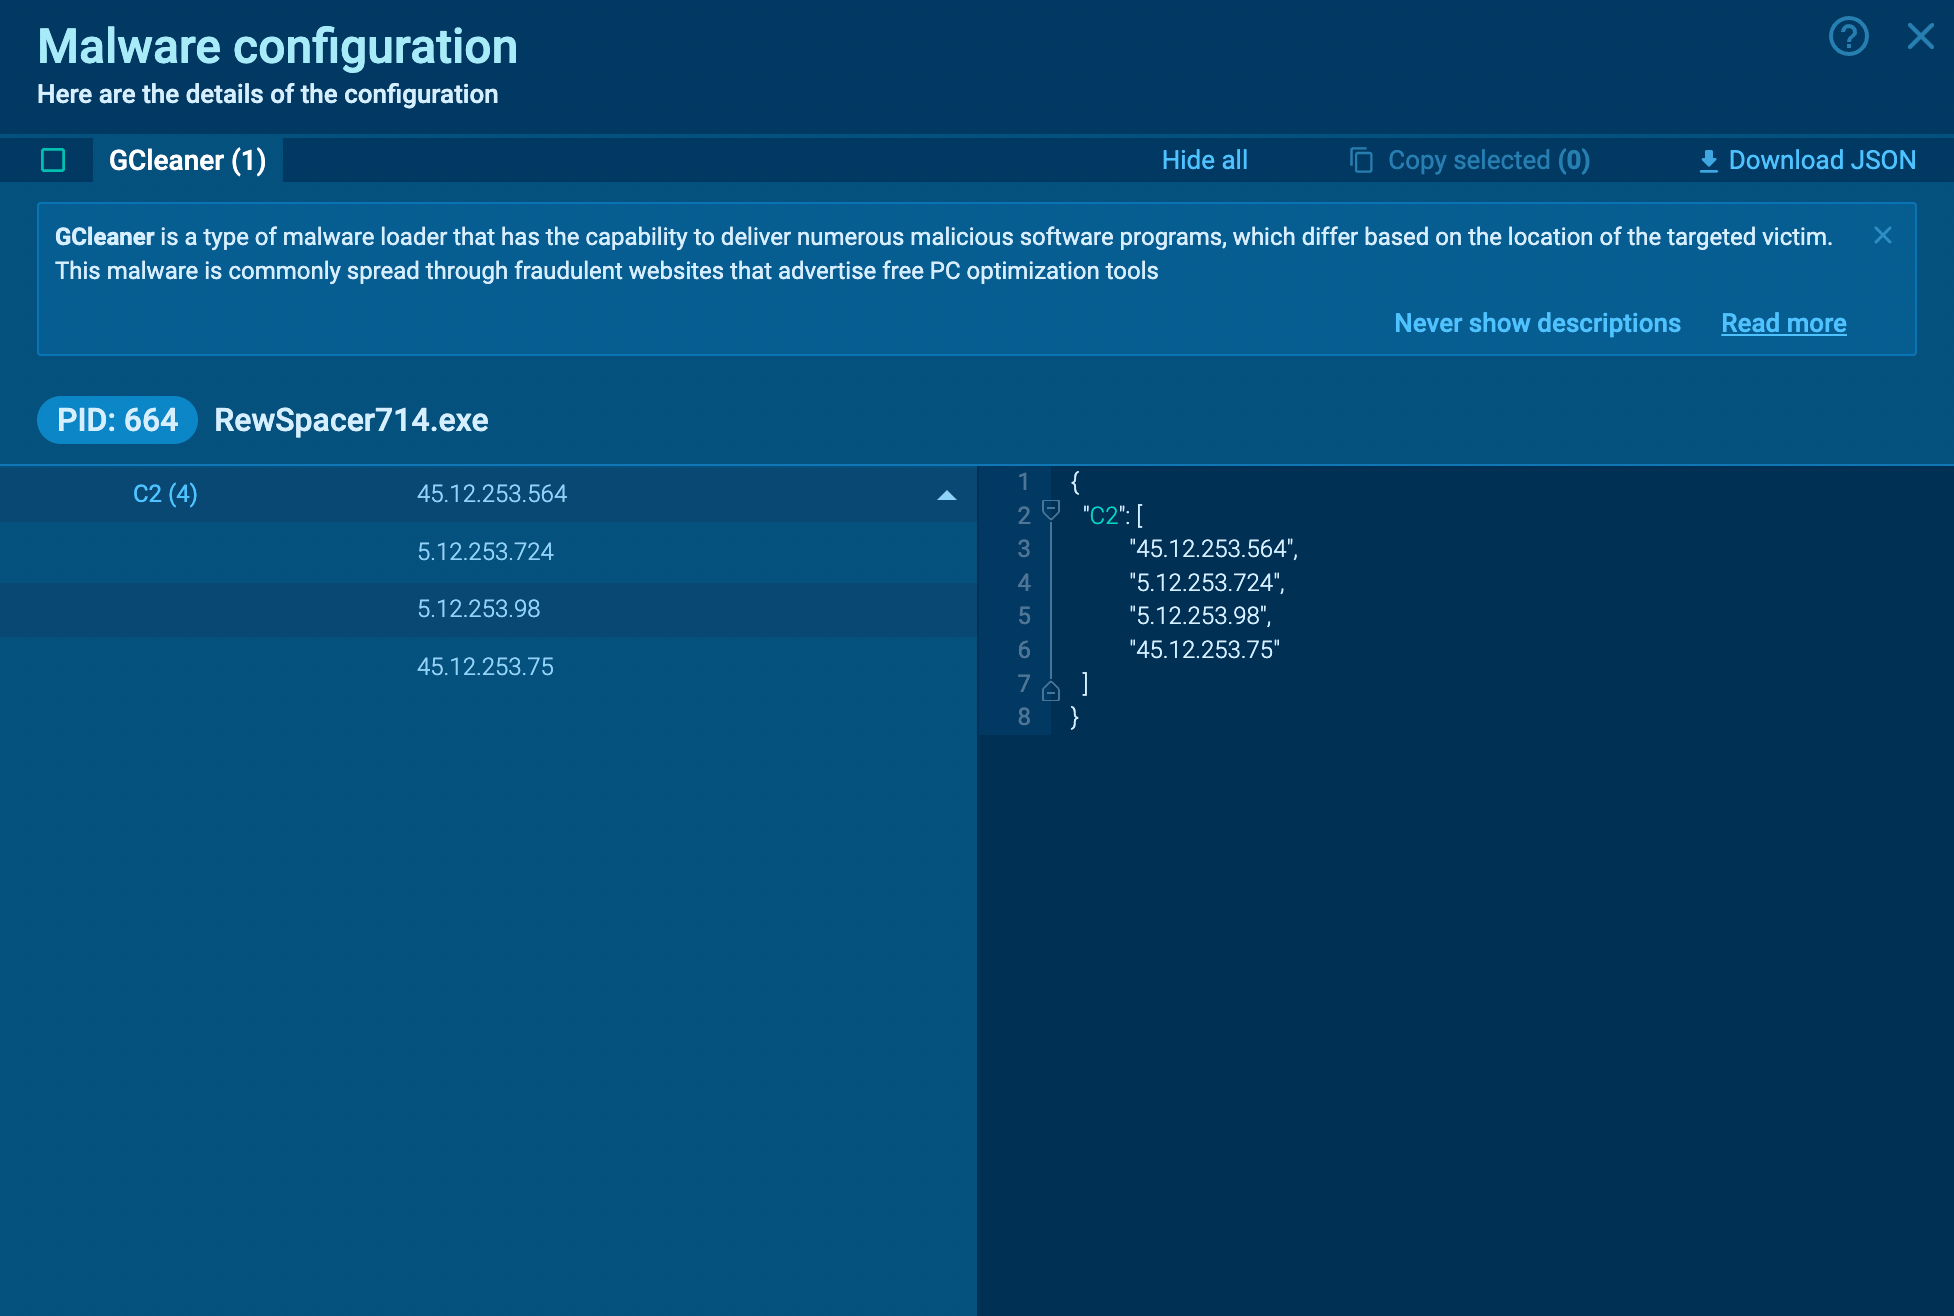
Gcleaner's configuration extracted by ANY.RUN Gcleaner's configuration extracted by ANY.RUN

Since GCleaner is a loader, its main purpose is to download other malware families. As a result, the execution flow varies from one version to another and can include the use of different tools. Overall, after it starts, the loader simply reruns itself under a different name from one of the "Program Files" directories. After that, it mostly attempts to download malware onto the infected system. In our case, GCleaner downloaded Redline.
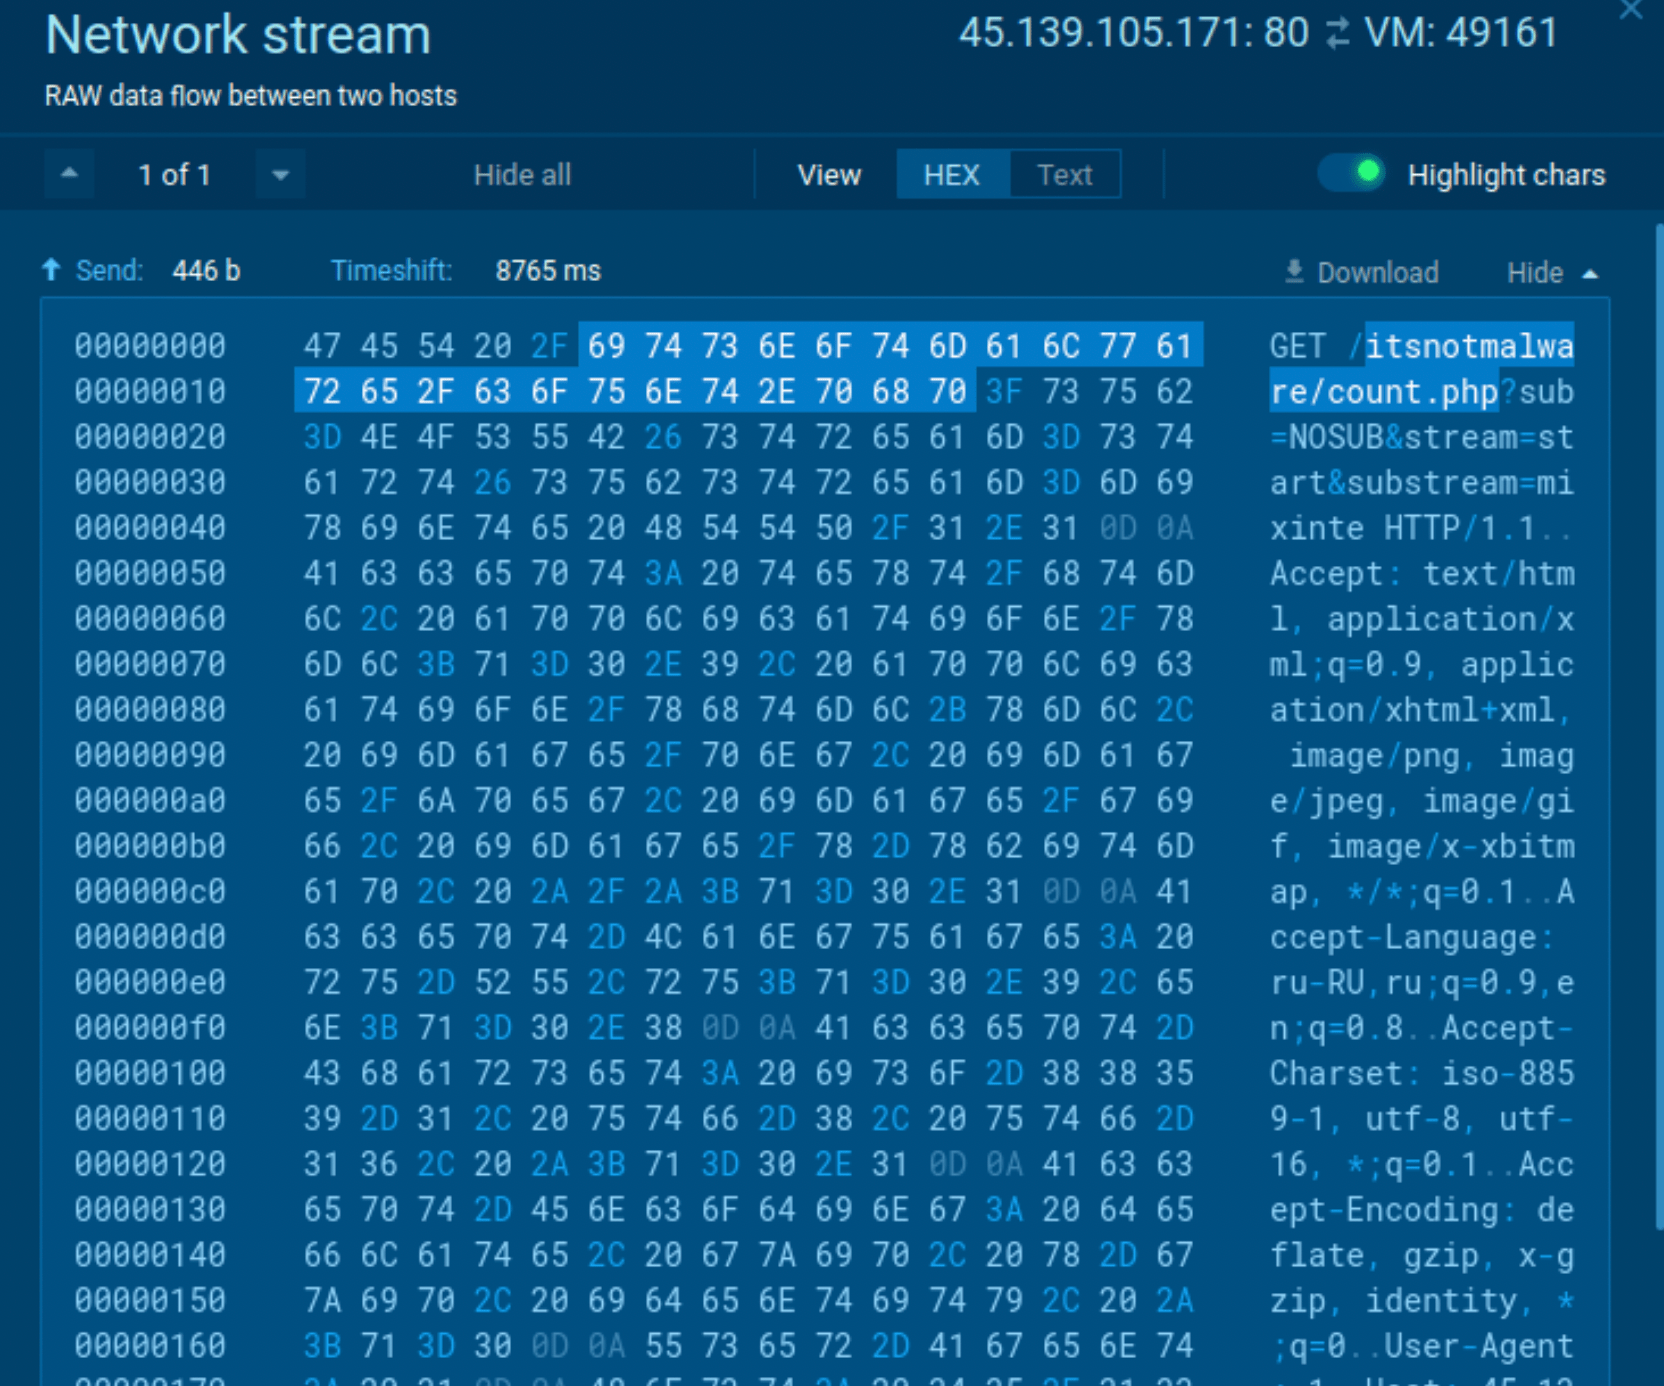
Gcleaner’s network traffic Gcleaner's network traffic

Some samples of GCleaner may be detected by the malware’s network traffic. To do so, just look at the network stream. If you find "itsnotmalware/count.php" there, you can be pretty sure that it is GCleaner.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Distribution methods of the G-Cleaner malware

G-Cleaner has several channels for finding its way to users’ systems:

The most common one is through a website promoting a free optimizer. In fact, such was the first instance of this malware being discovered in 2019. The design of the page is reminiscent of those of CCleaner and other trusted providers, which is how criminals trick users into downloading malware.

Another widespread distribution method for G-Cleaner is through spam emails disguised as legitimate messages from international brands. In such cases, attackers utilize social engineering techniques to get users to install email attachments.

Alternatively, GCleaner can be masked as files not related to PC optimization. These may include game modes, patches, and other types of software.

Conclusion

G-Cleaner is a loader capable of introducing a range of malicious software onto the victim's computer. Generally, it is disseminated through fake websites advertising free PC performance optimization tools or via spam emails.

To prevent GCleaner and other malware from posing a risk to your organization’s infrastructure, you can conveniently scrutinize any questionable files using the ANY.RUN interactive malware analysis sandbox to quickly identify harmful code, study its behavior, and collect IOCs.
HAVE A LOOK AT

DarkGate screenshot
DarkGate
darkgate
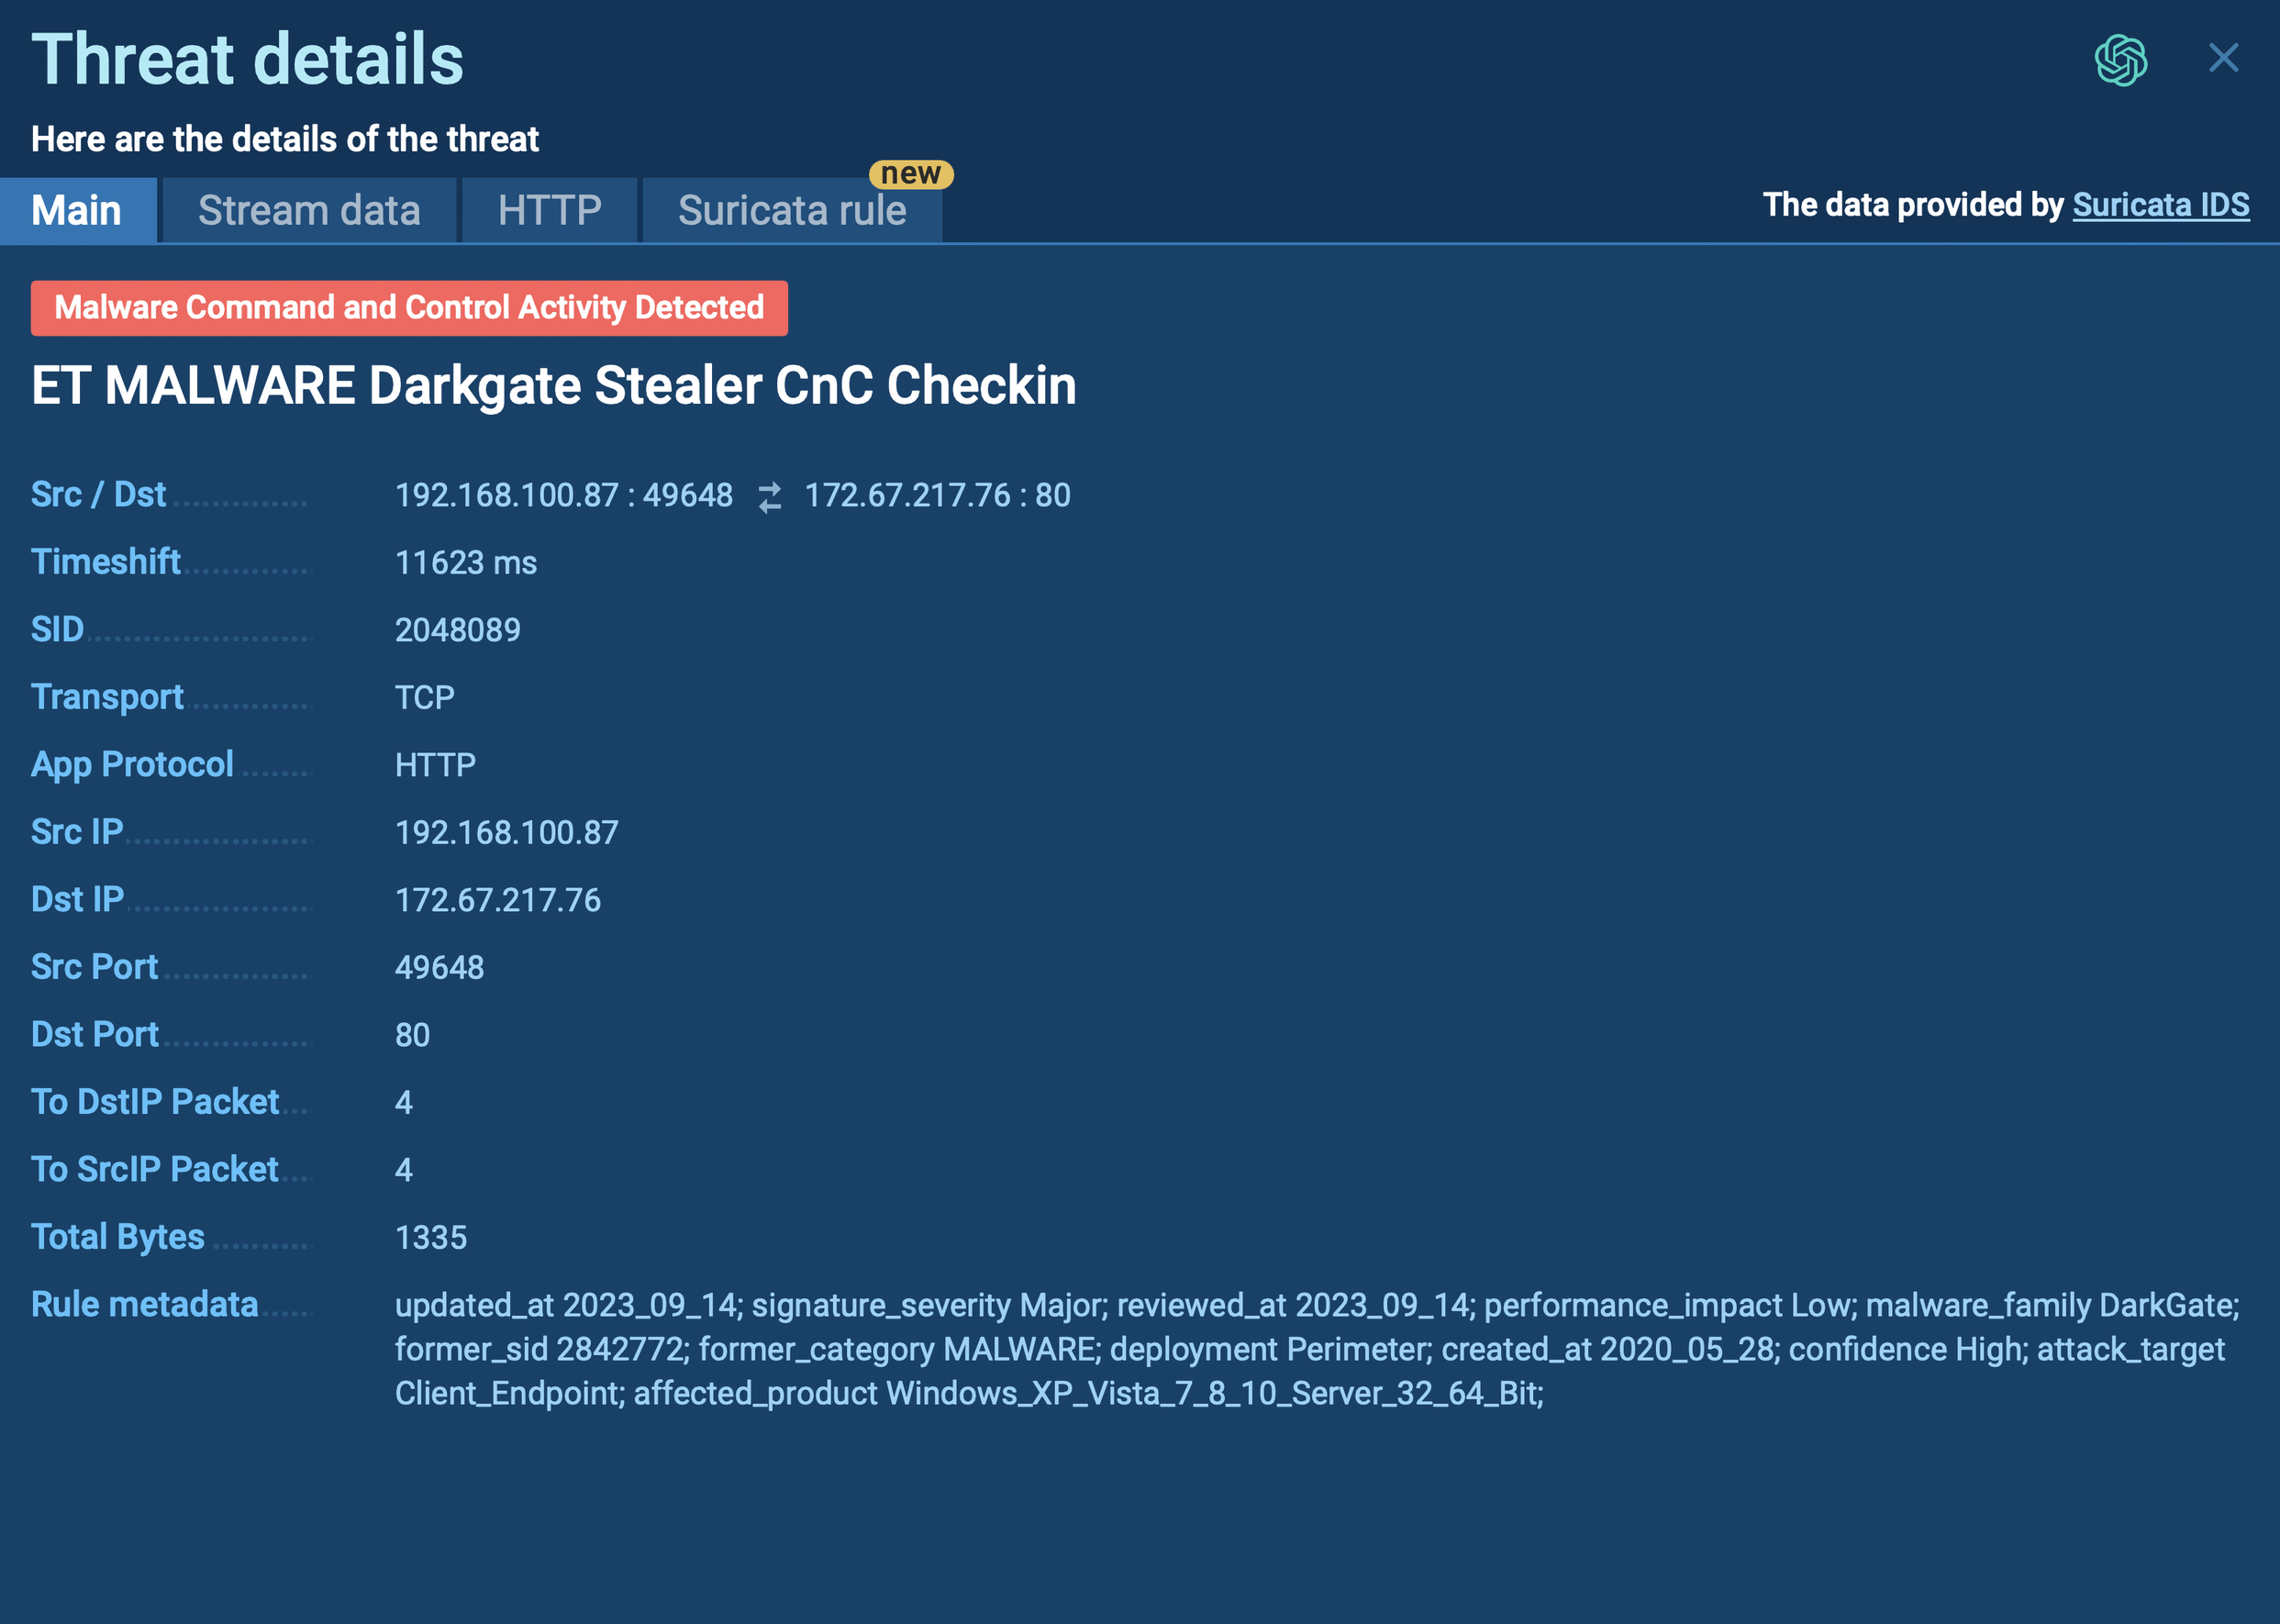
DarkGate is a loader, which possesses extensive functionality, ranging from keylogging to crypto mining. Written in Delphi, this malware is known for the use of AutoIT scripts in its infection process. Thanks to this malicious software’s versatile architecture, it is widely used by established threat actors.
Read More
Gh0st RAT screenshot
Gh0st RAT
gh0st
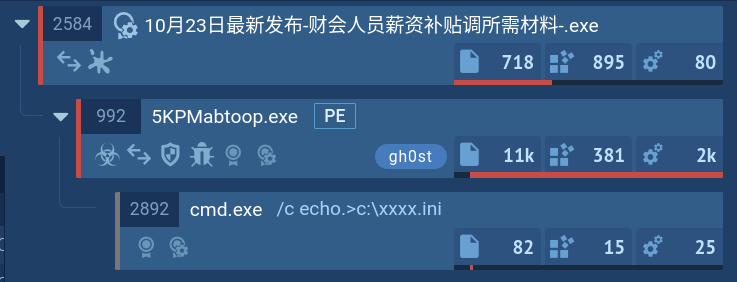
Gh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.
Read More
Netwalker screenshot
Netwalker
netwalker ransomware
Netwalker is ransomware — it belongs to a malware family which encrypts files and demands users to pay a ransom to get their data back. Netwalker utilizes several sophisticated techniques, such as process hollowing and code obfuscation to target corporate victims.
Read More
Greatness screenshot
Greatness is a Phishing-as-a-Service (PhaaS) platform that enables cybercriminals, even those with limited technical skills, to launch sophisticated phishing attacks primarily targeting Microsoft 365 (M365) credentials. It acts as a man-in-the-middle (MitM) proxy, facilitating credential theft and MFA bypass while providing affiliates with easy-to-use tools like attachment builders and Telegram notifications.
Read More
Meduza Stealer screenshot
Meduza Stealer is an information-stealing malware primarily targeting Windows systems, designed to harvest sensitive data such as login credentials, browsing histories, cookies, cryptocurrency wallets, and password manager data. It has advanced anti-detection mechanisms, allowing it to evade many antivirus programs. The malware is distributed through various means, including phishing emails and malicious links. It’s marketed on underground forums and Telegram channels.
Read More
Roning Loader screenshot
Roning Loader
roning
RoningLoader is a multi-stage Windows loader designed to operate quietly while preparing systems for deeper compromise. It abuses trusted system tools and interferes with security controls to reduce the chances of early detection. Instead of acting as a final payload, it creates conditions for follow-on malware to execute more effectively. Its use of staged execution and code injection allows attackers to blend into legitimate activity and escalate impact. This makes early behavioral detection critical before the attack chain progresses further.
Read More