Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
132
Global rank
143 infographic chevron month
Month rank
158 infographic chevron week
Week rank

Exela Stealer is an infostealer malware written in Python. It is capable of collecting a wide range of sensitive information from compromised systems and exfiltrating it to attackers over Discord. It is frequently used to steal browser data, and obtain session files from various applications, including gaming platforms, social media platforms, and messaging apps.

Stealer
Type
Unknown
Origin
1 May, 2023
First seen
30 September, 2026
Last seen

How to analyze Exela Stealer with ANY.RUN

Type
Unknown
Origin
1 May, 2023
First seen
30 September, 2026
Last seen

IOCs

IP addresses
95.100.102.9
155.102.51.36
142.250.154.94
3.36.173.8
205.185.115.131
20.119.144.5
150.171.28.11
142.251.110.157
95.100.102.101
184.24.77.134
142.251.150.119
162.159.135.232
142.251.14.132
188.245.84.166
178.250.1.57
192.178.183.103
144.217.167.73
18.66.102.21
65.8.131.8
147.185.221.29
Hashes
ed01ebfbc9eb5bbea545af4d01bf5f1071661840480439c6e5babe8e080e41aa
2ca2d550e603d74dedda03156023135b38da3630cb014e3d00b1263358c5f00d
146f61db72297c9c0facffd560487f8d6a2846ecec92ecc7db19c8d618dbc3a4
6db650836d64350bbde2ab324407b8e474fc041098c41ecac6fd77d632a36415
b9c5d4339809e0ad9a00d4d3dd26fdf44a32819a54abf846bb9b560d81391c25
97ebce49b14c46bebc9ec2448d00e1e397123b256e2be9eba5140688e7bc0ae6
1f21838b244c80f8bed6f6977aa8a557b419cf22ba35b1fd4bf0f98989c5bdf8
2c95bef914da6c50d7bdedec601e589fbb4fda24c4863a7260f4f72bd025799c
7e491e7b48d6e34f916624c1cda9f024e86fcbec56acda35e27fa99d530d017e
519ad66009a6c127400c6c09e079903223bd82ecc18ad71b8e5cd79f5f9c053e
cb5da96b3dfcf4394713623dbf3831b2a0b8be63987f563e1c32edeb74cb6c3a
5c7f6ad1ec4bc2c8e2c9c126633215daba7de731ac8b12be10ca157417c97f3a
1adfee058b98206cb4fbe1a46d3ed62a11e1dee2c7ff521c1eef7c706e6a700e
e64178e339c8e10eac17a236a67b892d0447eb67b1dcd149763dad6fd9f72729
26fd072fda6e12f8c2d3292086ef0390785efa2c556e2a88bd4673102af703e5
3f33734b2d34cce83936ce99c3494cd845f1d2c02d7f6da31d42dfc1ca15a171
5afa4753afa048c6d6c39327ce674f27f5f6e5d3f2a060b7a8aed61725481150
d5e0e8694ddc0548d8e6b87c83d50f4ab85c1debadb106d6a6a794c3e746f4fa
e48673680746fbe027e8982f62a83c298d6fb46ad9243de8e79b7e5a24dcd4eb
77a250e81fdaf9a075b1244a9434c30bf449012c9b647b265fa81a7b0db2513f
Domains
global.ketchcdn.com
go.microsoft.com
motherboard.vice.com
dpm.demdex.net
avatars.sftcdn.net
edge.microsoft.com
ssp-sync.criteo.com
pixel.rubiconproject.com
sync.1rx.io
crl.microsoft.com
encrypted-tbn2.gstatic.com
kitchen-english.gl.at.ply.gg
www.google.com
softonic.com
cdn-10049480.file.myqcloud.com
gum.criteo.com
dnacdn.net
sdk.privacy-center.org
sb.scorecardresearch.com
static.doubleclick.net
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
http://91.92.242.236/files-129312398/files/file_deaad5d12778941d.exe
https://urlhaus.abuse.ch/downloads/text_online/
http://ip-api.com/line/?fields=countrycode
http://cdn-10049480.file.myqcloud.com/jd/jd145.exe
https://raw.githubusercontent.com/da2dalus/rickware/master/rickroll.exe
https://github.com/keygroup777-ransomware/downloader/raw/refs/heads/main/black.exe
https://github.com/keygroup777-ransomware/downloader1/raw/refs/heads/main/black.exe
http://github.com/keygroup777-ransomware/downloader/raw/refs/heads/main/black.exe
https://raw.githubusercontent.com/keygroup777-ransomware/downloader1/refs/heads/main/black.exe
http://192.162.199.149/uploads/0c83aee7a8ad48ecb075c59c5b4957f3.exe
http://rdm.91yunma.cn/api/upgrade/jd
https://raw.githubusercontent.com/xbest11/ddl1/main/xbest%20v1.exe
https://neihite.cc/gate/handshake
https://api.ipify.org/
http://212.232.22.87/bin/screenconnect.clientsetup.exe
https://raw.githubusercontent.com/loistupidpet/sfdawsdawdaw/main/serials_checker.exe
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 4611
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 6582
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 9728
comments 0

What is malware: Exela Stealer?

Exela Stealer, an open-source Python-based stealer, has been extensively used to target victims’ Discord accounts and browsers to steal sensitive data. This malware was first uploaded to GitHub in May 2023 and has since evolved with additional features.

Despite providing a note about the program being intended for educational purposes, the creators also sell a paid version of the software, which, according to their claims, possesses superior evasion capabilities. This premium version of Exela Stealer is distributed using the common malware-as-a-service (MaaS) model based on a subscription similar to other malware families. Such examples include Formbook and XWorm.

However, according to the message posted on February 10, 2024, in their Telegram channel, the malware’s developer announced that both the free and paid versions would not receive any further updates.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Exela Stealer malicious software technical details

Exela Stealer is a sophisticated tool that can collect a wide range of sensitive information from compromised systems:

  • Discord Injection: Exela Stealer can inject malicious code into the Discord client to obtain tokens, passwords, and email addresses.
  • Browser Data: The stealer can acquire various data from web browsers, cookies, including bookmarks, passwords, browsing history, and downloaded files.
  • Screenshot Capture: The stealer can capture screenshots from all monitors connected to the compromised system. This feature allows the attacker to visually monitor the user's activities.
  • Cryptocurrency and Wallet Information: Exela Stealer can scan the system to obtain cryptocurrency and wallet information stored in web browsers. This can potentially allow the attacker to misappropriate the user's cryptocurrency funds.
  • Autofill Data: The stealer can gain access to autofill data from web browsers. This includes personal information, such as names, addresses, phone numbers, and email addresses.
  • Session Files: Exela Stealer can get hold of session files from various applications, including Telegram, Uplay, Epic Games, Growtopia, Instagram, Twitter, TikTok, Twitch, Spotify, Riot Games, Reddit, Roblox, and Steam. This can provide the attacker with unauthorized access to the user's accounts on these platforms.

It can display fake error messages, as well as detect processes and system settings related to debugging or virtualization. For instance, it can determine the machine’s Universally Unique Identifier (UUID) and then check if it matches any entry on its list of known UUIDs.

Exela Stealer ensures its persistence by enabling automatic execution upon the user’s system login. It can either add an entry to the Windows Registry or create scheduled tasks.

Exela Stealer exfiltrates the data collected from compromised systems via a Discord webhook URL, sending it to the attacker.

Exela Stealer attack execution process

To observe the behavior of Exela Stealer on an actual system, we can upload its sample to the ANY.RUN sandbox for in-depth analysis.

Exela Stealer operates through a sophisticated execution chain involving several stages. Initially, it may be delivered via phishing emails or through compromised websites. Once a user unwittingly downloads and executes the malware, it establishes persistence by modifying system settings or creating new autostart entries in the Windows registry.

Next, Exela Stealer typically employs obfuscation techniques to evade detection by security software, such as encryption or code obfuscation. It then begins its primary function of exfiltrating sensitive information from the infected system, such as login credentials, credit card numbers, or personal documents.

Finally, the stolen data is transmitted to a remote command and control server controlled by the attackers, where it can be used for various malicious purposes, including identity theft or financial fraud. Throughout this execution chain, Exela Stealer aims to operate discreetly to maximize its effectiveness and avoid detection by security measures.
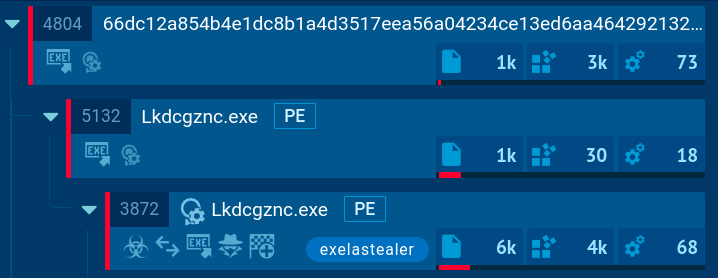
Exela processes shown in ANY.RUN Exela Stealer's processes demonstrated in ANY.RUN

In our example, we can observe that the malware utilizes various system utilities to obtain information about the list of running processes. Additionally, it conducts system language discovery by checking the languages supported by the infected system, modifies file attributes, and gathers various other details about the infected system and its users.

Exela Stealer malware distribution methods

Since the free version of the malware is widely accessible, any ill-intentioned individual can use it to attempt to infect machines of other users. Exela Stealer usually ends up on victims’ computers through phishing emails or messages. Attackers craft these to appear as if they were written by legitimate entities, such as trusted organizations. These messages often contain malicious attachments that, after executing, cause the Exela stealer infection on their machine.

Conclusion

Exela Stealer poses a significant threat to digital security due to its sophisticated tactics for stealing sensitive information. Its ability to leverage legitimate platforms like Discord and its continuous evolution underscore the importance of having proper security tools.

ANY.RUN is a cloud-based sandbox for detecting and analyzing threats, such as Exela Stealer, that offers detailed reports on their technical characteristics. The service lets you examine any suspicious file and check potentially harmful URLs, ensuring informed decision-making and prompt deletion of any malware, as well as proper protection of your infrastructure.
Create your ANY.RUN account – it’s free!

HAVE A LOOK AT

MicroStealer screenshot
MicroStealer
microstealer
MicroStealer is a rapidly emerging infostealer first prominently observed in late 2025. It specializes in stealing browser credentials, active session data, screenshots, cryptocurrency wallets, and system information. It spreads quickly with low detection rates thanks to a sophisticated multi-stage delivery chain and exfiltrates data via Discord webhooks and attacker-controlled servers.
Read More
Black Basta screenshot
Black Basta
blackbasta
Black Basta is a ransomware-as-a-service operated by Storm-1811. It emerged in 2022 and uses double extortion tactics, encrypting data and stealing it for ransom. The malware often gains access through spear-phishing and uses tools like QakBot and Cobalt Strike. It's known for exploiting system vulnerabilities and using advanced obfuscation techniques.
Read More
Jigsaw screenshot
Jigsaw
jigsaw
The Jigsaw ransomware, initially detected in 2016, encrypts files on compromised systems and requires a ransom payment in Bitcoin. If the ransom is not paid, the malware starts deleting files, increasing the pressure on victims to comply. Its source code is publicly accessible, allowing various threat actors to customize and repurpose the malware for different objectives.
Read More
Lynx screenshot
Lynx
lynx
Lynx is a double extortion ransomware: attackers encrypt important and sensitive data and demand a ransom for decryption simultaneously threatening to publish or sell the data. Active since mid-2024. Among techniques are terminating processes and services, privilege escalation, deleting shadow copies. Distribution by phishing, malvertising, exploiting vulnerabilities.
Read More
BQTLock screenshot
BQTLock
bqtlock baqiyatlock
BQTLock is a ransomware-as-a-service (RaaS) malware family that emerged in 2025 and quickly gained attention due to its combination of file encryption, credential theft, and data exfiltration. BQTLock encrypts files using a hybrid AES-256 and RSA-4096 encryption scheme, demands payment in Monero cryptocurrency, and performs data theft and system reconnaissance.
Read More
Interlock screenshot
Interlock
interlock
Interlock is a relatively recent entrant into the ransomware landscape. First identified in 2023, it's a multi-functional malware strain used in ransomware-as-a-service (RaaS) operations.
Read More