

Threat Intelligence
ANY.RUN Threat Intelligence Feeds for IBM QRadar SIEM
Improve threat detection with fresh intelligence from a global community of security professionals, helping your SOC identify malicious activity earlier and respond faster.
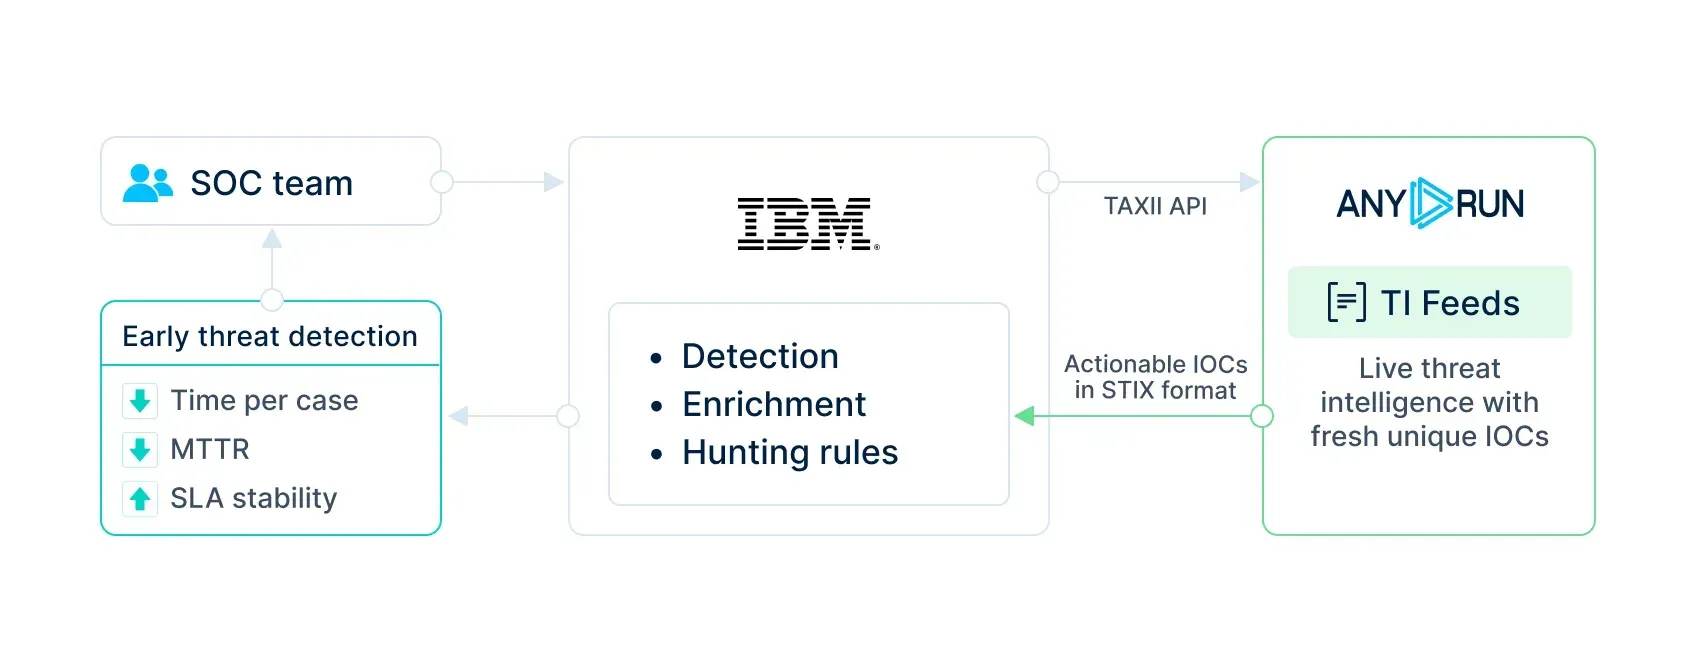
Receive fresh malicious IPs, domains, and URLs from ongoing real-world investigations for timely detection.
Automatically correlate logs and events with the latest IOCs to spot the latest threats and response faster.
Cut alert noise with high-confidence malicious IOCs and reduce unnecessary investigation work.
Expand detection coverage across active malicious infrastructure.
Reduce manual IOC checks and help analysts move from detection to response faster.
Use cases
Threat detection
IOC correlation
Alert triage
Requirements
ANY.RUN Threat Intelligence plan with TI Feeds access


