Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
56
Global rank
82 infographic chevron month
Month rank
73 infographic chevron week
Week rank

Qbot is a banking Trojan — a malware designed to collect banking information from victims. Qbot targets organizations mostly in the US. It is equipped with various sophisticated evasion and info-stealing functions and worm-like functionality, and a strong persistence mechanism.

Botnet
Type
Unknown
Origin
1 January, 2009
First seen
17 September, 2026
Last seen
Also known as
Pinkslipbot
QakBot
Quakbot

How to analyze Qbot with ANY.RUN

Type
Unknown
Origin
1 January, 2009
First seen
17 September, 2026
Last seen

IOCs

IP addresses
2.16.204.158
23.216.77.15
48.192.1.64
23.11.41.157
172.211.123.249
48.209.133.15
23.59.18.102
204.79.197.203
40.126.32.136
57.154.63.210
48.209.6.48
74.179.77.204
95.100.102.101
95.100.102.9
2.21.20.144
48.209.138.168
48.209.138.189
23.209.214.100
74.179.77.164
2.16.241.219
Hashes
b183bd6414c5123465075d76d2413c999d569492fb543acbc29690b4b745bdf2
1521fa3b14eec64c45d1e2fb594975d41fd88ea62a97d341c3733cf0ba3edf2f
7aa65c538c3f7c52aff482b84eb15bd42755b20e94a9cf589e6f2f0f147f55d4
a23ef053cccf6a35fda9adc5f1702ba99a7be695107d3ba5d1ea8c9c258299e4
8eaff2a09a58eeefc698714c0a678d8837d196542a9453baba0555997058281a
c23c9580f06fdc862df3d80fb8dc398b666e01a523f06ffa8935a95dce4ff8f4
d491387b2b5b131d5672849becbf7df87fea9dd1579bcc43e1ae75bcb1b1ecea
76e1f2360ec351b39b63003d1d587c229ff5352d2c74b89ac0840e5a481524c2
78f8a3191bdd5a35bb26d632a6746cde2cfd68b659e373747ee499e36686382b
9edf54bbc75b4448e9191747ee85e76724f8db40cbf3c8948d1e726f13cf65e8
b923ec4a85ef7e039a06436e142d37154c6751fc0b70ac18034342110bf275fc
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
4dbfc417d053ba6867308671f1c61f4dcafc61f058d4044db532da6d3bde3615
e606fbab0395e7c384fcf6eb3e42269ec0a0ac3158c438f9882d7b5a25a3ed02
4290ba7bf03a6d588a220f74cf0ff2107858f7ed20c565e435080c470e25fe4d
b5f23fdea3f4f4c0a84f357a48e100ba020455cd8024d08c916267f4107d1a37
59c1a5562f94ff1c3fb378b1a4e958c7b2c3b950217048989a938af2c06e538a
474d668707f1cb929fef1e3798b71b632e50675bd1a9dceaab90c9587f72f680
6034f27b0823b2a6a76fe296e851939fd05324d0af9d55f249c79af118b0eb31
6028bd681dbf11a0a58dde8a0cd884115c04caa59d080ba51bde1b086ce0079d
Domains
settings-win.data.microsoft.com
oneocsp.microsoft.com
www.microsoft.com
client.wns.windows.com
crl.microsoft.com
activation-v2.sls.microsoft.com
ocsp.digicert.com
google.com
www.bing.com
nexusrules.officeapps.live.com
self.events.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
go.microsoft.com
login.live.com
ecs.office.com
slscr.update.microsoft.com
th.bing.com
edge.microsoft.com
officeclient.microsoft.com
copilot.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
Last Seen at

Recent blog posts

post image
How MSSPs Can Prove Their Value When “Nothing...
watchers 2763
comments 0
post image
Enterprise Threat Intelligence Buying Guide:...
watchers 3146
comments 0
post image
ANY.RUN & SentinelOne: One Workspace, Ins...
watchers 4652
comments 0

What is Qbot?

Qbot, also known as QakBot, Pinkslipbot, and Quakbot, is a banking trojan — malware designed to steal banking credentials, online banking session information, personal details of the victim, or any other banking data.

Although early versions of Qbot were spotted all the way back in 2009, its creators have maintained this trojan. Today, it continues to be active and features worm-like abilities to spread over networks, supports advanced web-injections techniques, and has a persistence mechanism that some researchers believe to be one of the best in its class. Additionally, the trojan has anti-VM, anti-debug and anti-sandbox functionally that makes research and analysis quite difficult.

Furthermore, Qbot is polymorphic, which means that it can change itself even after it is installed on an endpoint. The Trojan constantly modifies files, and the dropper that the newer version of Qbot continuously cycles through command and control servers.

The combination of these functions makes QakBot highly dangerous malware. Qbot has been used in several successful attacks on organizations and governmental structures and has infected tens of thousands of machines.

General description of QakBot malware

Qbot is dispatched in targeted attacks against businesses. With this trojan, the attackers go after bank accounts of organizations or private users who access their personal online banking cabinets from corporate networks by piggybacking into banking sessions of the victim.

The Trojan uses man-in-the-browser functionality to perform web injections, allowing it to alter what the victims see on the banking website when browsing from an infected machine. Interestingly, while most malware samples that use this technique contain the web injection code in their config file, Qbot can fetch the code from a controlled domain as it performs malicious activity.

Another trait that differentiates Qbot from other Trojans is its worm-like functionality. Qbot can copy itself using shared drives and spread over the network, spreading on its own or after receiving a command from the command and control server. Together with a highly developed persistence mechanism that uses registry runkeys and scheduled tasks, these traits make erasing Qbot from the infected network very difficult. The Trojan is designed to sustain itself despite system reboots and automatically launch itself when the system is turned on again.

This infamous persistence functionality has allegedly caused compromise of sensitive information in two government organizations in Massachusetts in 2011, while worm-like behavior helped the Qbot infiltrate thousands of machines and create a botnet with over 1,500 devices resulting from that attack.

Most of the targets that Qbot goes after are US-based organizations. Only about twenty percent of the new attack businesses are located outside of the United States. Although apart from the government offices, most of the attacks have been directed at banking, tech, and healthcare industries, there is no hard evidence to suggest that the attackers are aiming at specific fields. This means that businesses working in any industry can get hit by QakBot.

It is also important to note that an advanced cybergang operates the malware. Qbot attacks have been appearing on the radar of security researchers periodically, with phases of high activity and intervals when attacks would completely stop. This behavior is likely to avoid attracting too much attention from law enforcement and allows attackers to tweak and improve the malware during their time off.

The group behind Qbot is also notoriously known for pushing out new modified malware samples at astonishing rates. They repack and re-scramble the code daily, making malware identification by means of anti-virus software unreliable.

Unfortunately, people's identities behind Qbot are unknown, but it is widely believed that the cyber gang is based somewhere in Eastern Europe.

Qbot malware analysis

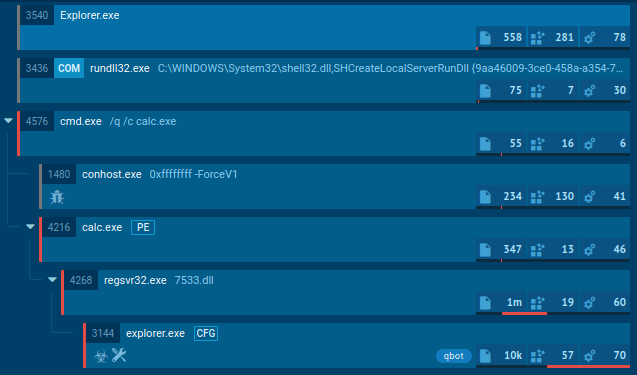
This video recorded in the ANY.RUN interactive malware hunting service shows the execution process of Qbot. You can also research other malware like Netwire and Predator the Thief.
qbot_process_graph

Figure 1: Displays the tree of processes created by the ANY.RUN interactive malware hunting service

QakBot execution process

Since Qbot is mostly targeted at the corporate sector, the main way of its penetration into infected systems is through a malicious document. In our example, maldoc starts several processes, including Powershell through by using a macro. Then, using cmd.exe, this trojan starts a chain of commands and executions, creating folders and temporary files. It utilizes Powershell to download the payload. Notably, the payload's name is as simple as six of the same digits or, less often, letters. Also, the payload often has a .png extension, although it is an executable file.

After that trojan starts its main execution, QakBot tries to evade detection by overwriting itself with the legitimate Windows executable calc.exe using the following commands: cmd.exe /c ping.exe -n 6 127.0.0.1 & type "C:\Windows\System32\calc.exe" > “Path to malware executable.” Qbot also injects explorer.exe and adds itself into autorun for persistence.

Qbot distribution

Qbot uses multiple attack vectors to infect victims. The malware uses email spam and phishing campaigns, as well as vulnerability exploits to infiltrate its targets. One of the more recent versions of the malware was observed being distributed by a dropper.

The dropper that installs Qbot is equipped with a delayed execution function. This means that after the dropper itself is downloaded onto a target machine, it waits around fifteen minutes before dropping the payload, likely in an effort to trick automatic sandboxes and avoid detection.

How to detect Qbot using ANY.RUN?

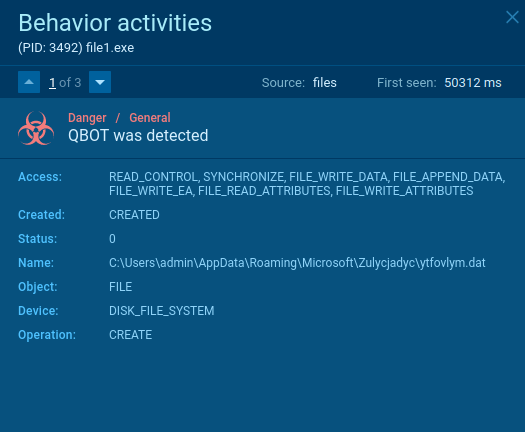
Sometimes Qbot trojan creates files that allow analysts to detect it with a high degree of certainty. To detect Qbot, open the "Files" tab in the lower part of the task's window and take a look at the created folders. If you see folders with names such as "Zulycjadyc" and "imtaykad" within C:\Users\admin\AppData\ Roaming\Microsoft\ directory and .exe or .dat file with a name "ytfovlym," as shown on the figure below, be sure that it is Qbot in front of you.
how_to_detect_qbot

Figure 2: Detecting Qbot by local files

Conclusion

Security researchers successfully reversed a sample of QakBot in a 2020 investigation. Since the researchers managed to pinpoint a command and control server, they could identify the true scale of the attack. What they uncovered was an active Qbot botnet consisting of over 2,000 computers.

If there was any doubt that Qbot is a severe threat, hopefully, this should clear it. Advanced web injections, sophisticated anti-evasion techniques, worm-like functions, and an experienced cyber gang that constantly updates the malware is a dangerous cocktail.

As security researchers, it is essential to analyze malware like Qbot since code obfuscation makes research complicated. Every investigation has the potential to uncover important data that will help businesses avoid attacks or identify and eradicate this Trojan quicker. At the same time, Qbot avoids dynamic analysis with some automatic sandboxes with the delayed execution of its dropper and other tricks, interactive sandboxes like the one presented by the ANY.RUN malware hunting services are not so easily fooled.

ANY.RUN presents a good opportunity to perform dynamic analysis on this malware from a secure online environment and share your findings with fellow researchers in our public malware database.
HAVE A LOOK AT

Phantom Stealer screenshot
Phantom Stealer
phantomstealer
Phantom Stealer is a commercially available Malware-as-a-Service infostealer targeting Windows systems. It harvests browser passwords, session cookies, payment data, cryptocurrency wallets, system information, screenshots, and application data.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More
RondoDox screenshot
RondoDox
rondodox
RondoDox is an emerging Linux-based botnet malware that exploits dozens of known vulnerabilities in internet-facing devices like routers, DVRs, and web servers to build massive networks for DDoS attacks, cryptomining, and data exfiltration. First spotted in mid-2025, its "exploit shotgun" tactic (firing multiple payloads at once) has made it a rapid escalator in the IoT threat landscape, compromising unpatched edge devices worldwide.
Read More
WannaCry screenshot
WannaCry
wannacry ransomware
WannaCry is a famous Ransomware that utilizes the EternalBlue exploit. This malware is known for infecting at least 200,000 computers worldwide and it continues to be an active and dangerous threat.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More