Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
169
Global rank
128 infographic chevron month
Month rank
154 infographic chevron week
Week rank

Laplas Clipper is a crypto-stealing malware that gains unauthorized access to the victim’s clipboard and replaces their crypto addresses to trick them into sending their funds to the attacker’s wallet. This malicious program is offered for sale as a malware-as-a-service (MaaS) and often distributed with the help of loaders, including SmokeLoader.

Stealer
Type
ex-USSR
Origin
1 October, 2022
First seen
17 September, 2026
Last seen

How to analyze Laplas Clipper with ANY.RUN

Type
ex-USSR
Origin
1 October, 2022
First seen
17 September, 2026
Last seen

IOCs

IP addresses
45.159.189.105
2.16.241.221
2.16.241.217
23.207.210.139
57.153.246.3
178.208.87.49
23.52.181.141
2.21.20.144
135.232.92.137
23.52.181.212
204.79.197.203
48.192.1.64
48.209.138.168
92.123.104.34
20.165.94.54
172.211.123.249
95.100.102.101
23.11.41.157
2.21.20.152
40.126.32.136
Hashes
766c1d6bcb81d3e983fb7adbc19c616d7fc01dafb7893738edc242e2adc59c07
34df2d15ee336296547593d47aa1f39f653dcb7b76215dacccd0488e14f579e6
2bd1da2ae0ad87b35400982fadca1bb83efa7b5a91c0057c6ae451e2fd5cca6a
d10544dac98f47873ec5235c504878ce64b8a0f3f5a2416e44ebe03a448ef4b9
3234c70671bb59d9a5682407f89cabdc41c59f1bc82d883b9537544fd6cec19f
81b2bd4ea98c8db66554fbc8d7637a1a69a130f331feb732b75caab4c4868fd5
7bfbc8202b8cdbdcc597a0e789240f0dc0b0e94fa6597e576eaf436bc6223e18
cbc8b288dbd2c72432081cf33cef431572a94c7fb89dbcd59973b99e3871814e
cd0dd26304b88c20801fe80b33c49c009e2e5d4411b5d7f83252e1d90cd461c6
0fabe1548eba982f5518462f66a451b5c5b45220ac6d84bf029121c02aa258a3
792955295ae9c382986222c6731c5870bd0e921e7f7e34cc4615f5cd67f225da
00ad9799527c3fd21f3a85012565eae817490f3e0d417413bf9567bb5909f6a2
81ff65efc4487853bdb4625559e69ab44f19e0f5efbd6d5b2af5e3ab267c8e06
d27d5b27030f4725249377951beb89e84a90a0e8241f0d5fd80ea59c1606e761
7d99fec08182a5b95d18d1569edaa2c60c2aafbd15a56d8882f22f3b395e6460
7ed09f7d2bd632f70077a4ae4f2bd2f3fb654b03cd72652f51678b0c7d027f25
614be0169ec36e67223eb9645a98da66dbfde5dfbb89bb064f428aaeabdd9d97
000e3a78c72a210ca3b5417a3cdd294fbce2a31661601c9d594c75cf2800571c
cbe2dc6abfe25bead60f4dfaf419fc0f441ff8a8dd4a2febf5553be1cbd90c49
7dbbea2dd387eeb85e1f56e02fc9989acde570cd43bfef2c2a827093ba87da6d
Domains
www.microsoft.com
settings-win.data.microsoft.com
client.wns.windows.com
th.bing.com
ocsp.digicert.com
crl.microsoft.com
oneocsp.microsoft.com
fe3cr.delivery.mp.microsoft.com
slscr.update.microsoft.com
login.live.com
ecs.office.com
www.bing.com
go.microsoft.com
google.com
activation-v2.sls.microsoft.com
self.events.data.microsoft.com
www.vodafone.co.uk
watson.events.data.microsoft.com
ads-img.mozilla.org
armmf.adobe.com
URLs
http://45.159.189.105/bot/regex?key=6c78a6e987dfc45100108d0fd40e03bd210668f370b6f27ea666ba07cdab694d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
https://www.bing.com/dsb/scenario?name=trendingsearchwithcache&cc=us&setlang=en-us
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=9%2f16%2f2026%2c%204%3a51%3a36%20am
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaagb6jmmcovb6saaaaaaay%3d
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.28773000-92cc-4cf0-9e91-597f7316a062&pid=dsb
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=n&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=1&cvid=d9292507ab184046bcbb9159d1c499ce&ig=6828bdbdcdaa476db8f77edaf086db79
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=not&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=3&cvid=d9292507ab184046bcbb9159d1c499ce&ig=bb6cd6a6f8cb4fe0b3e36c1d7209a872
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=note&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=4&cvid=d9292507ab184046bcbb9159d1c499ce&ig=27c483f733c545b8825af33e84862cb0
https://www.bing.com/th?id=osk.ac436f082f306a91af11103bd0abbc9d&w=80&h=80&qlt=90&c=6&rs=1&cdv=1&pid=rs
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=no&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=2&cvid=d9292507ab184046bcbb9159d1c499ce&ig=2c3810805ddc44889fe7d15325bb3a6c
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://login.live.com/rst2.srf
Last Seen at

Recent blog posts

post image
Threat Coverage Digest: New Malware Reports a...
watchers 6945
comments 0
post image
Phishing Response Protocol: 3 Essential SOC S...
watchers 9046
comments 0
post image
Major Cyber Attacks in September 2026: US and...
watchers 13157
comments 0

What is Laplas Clipper malware?

Laplas Clipper is a family of malware that possesses stealer capabilities. Specifically, it works by replacing victims’ cryptocurrency addresses with those of the attacker using the clipboard. As a result, users unknowingly end up sending their virtual coins and tokens to the wallet set up by the threat actor. First observed in late 2022, Laplas Clipper remains in operation to this day and gets regular updates.

Laplas is sold openly via Telegram channels and Darknet forums as a Malware-as-a-Service (MaaS). Any user interested in this malicious software can purchase a subscription, starting from one week ($49) and up to one year ($839). As part of the offering, operators receive a web panel that lets them control the entire process of replacing victims’ crypto addresses and get notifications about the malware’s activity.

Phishing campaigns are the most common method employed by threats actors for infecting victims’ computers with Laplas Clipper. Criminals often weaponize .pdf and office-suite format files to conduct multi-stage attacks. In many instances, the malware is being dropped by other malicious software, including SmokeLoader, which penetrates security mechanisms of computers and then downloads Laplas.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Technical details of the Laplas Clipper malicious software

Unlike other stealers, such as FormBook and Arkei, Laplas Clipper has a limited functionality, which focuses exclusively on hijacking victims’ cryptocurrency wallets. The capabilities of the malware include:

  • Generation of crypto addresses: Laplas Clipper can generate Bitcoin addresses for all three types: P2PKH (legacy), P2SH, and SegWit. It can also create addresses for ERC20, BEP20, and other tokens that use the 0x prefix, as well as Tron ones.
  • Choice of prefix or postfix generation: The malware allows users to choose whether to produce addresses with the prefix or postfix. This gives criminals more control over the appearance of illegitimate addresses.
  • Support for over 20 types of wallets: The software can replace addresses in most popular crypto wallets.
  • Web panel: Laplas Clipper can be managed through a web-based interface, letting the operator easily configure and use the clipper.
  • Autobuild functionality: Users of the malware can choose between three versions of the program: C++, Golang, and .NET 4.
  • Automatic balance check: Laplas Clipper can automatically check the balance of victims’ addresses.
  • Support for EXE, DLL extensions: Laplas Clipper can be built for both EXE and DLL extensions.

The malware creates addresses that are almost identical to the original ones. For example, the first three characters after the prefix of the attacker's address will be the same as those of the victim's address. This is often enough for an average user to mistakenly send their cryptocurrency to the wrong address. Apart from generating its own addresses, Laplas Clipper allows operators to use their custom ones.

As for the anti-analysis and anti-detection techniques, some versions of the malware are obfuscated with Babel, a popular obfuscator for .NET, which is capable of renaming symbols and encrypting strings. The malware is also equipped with debugger and virtualization evasion. Read the article “Analyzing a New .NET variant of LaplasClipper: retrieving the config” to learn more about the program’s code and collect its configuration.

Execution process of Laplas Clipper

Let’s load a sample of Laplas Clipper into ANY.RUN, an interactive malware sandbox, to expose its malicious activities and examine its behavior, as well as to gather up-to-date IOCs.
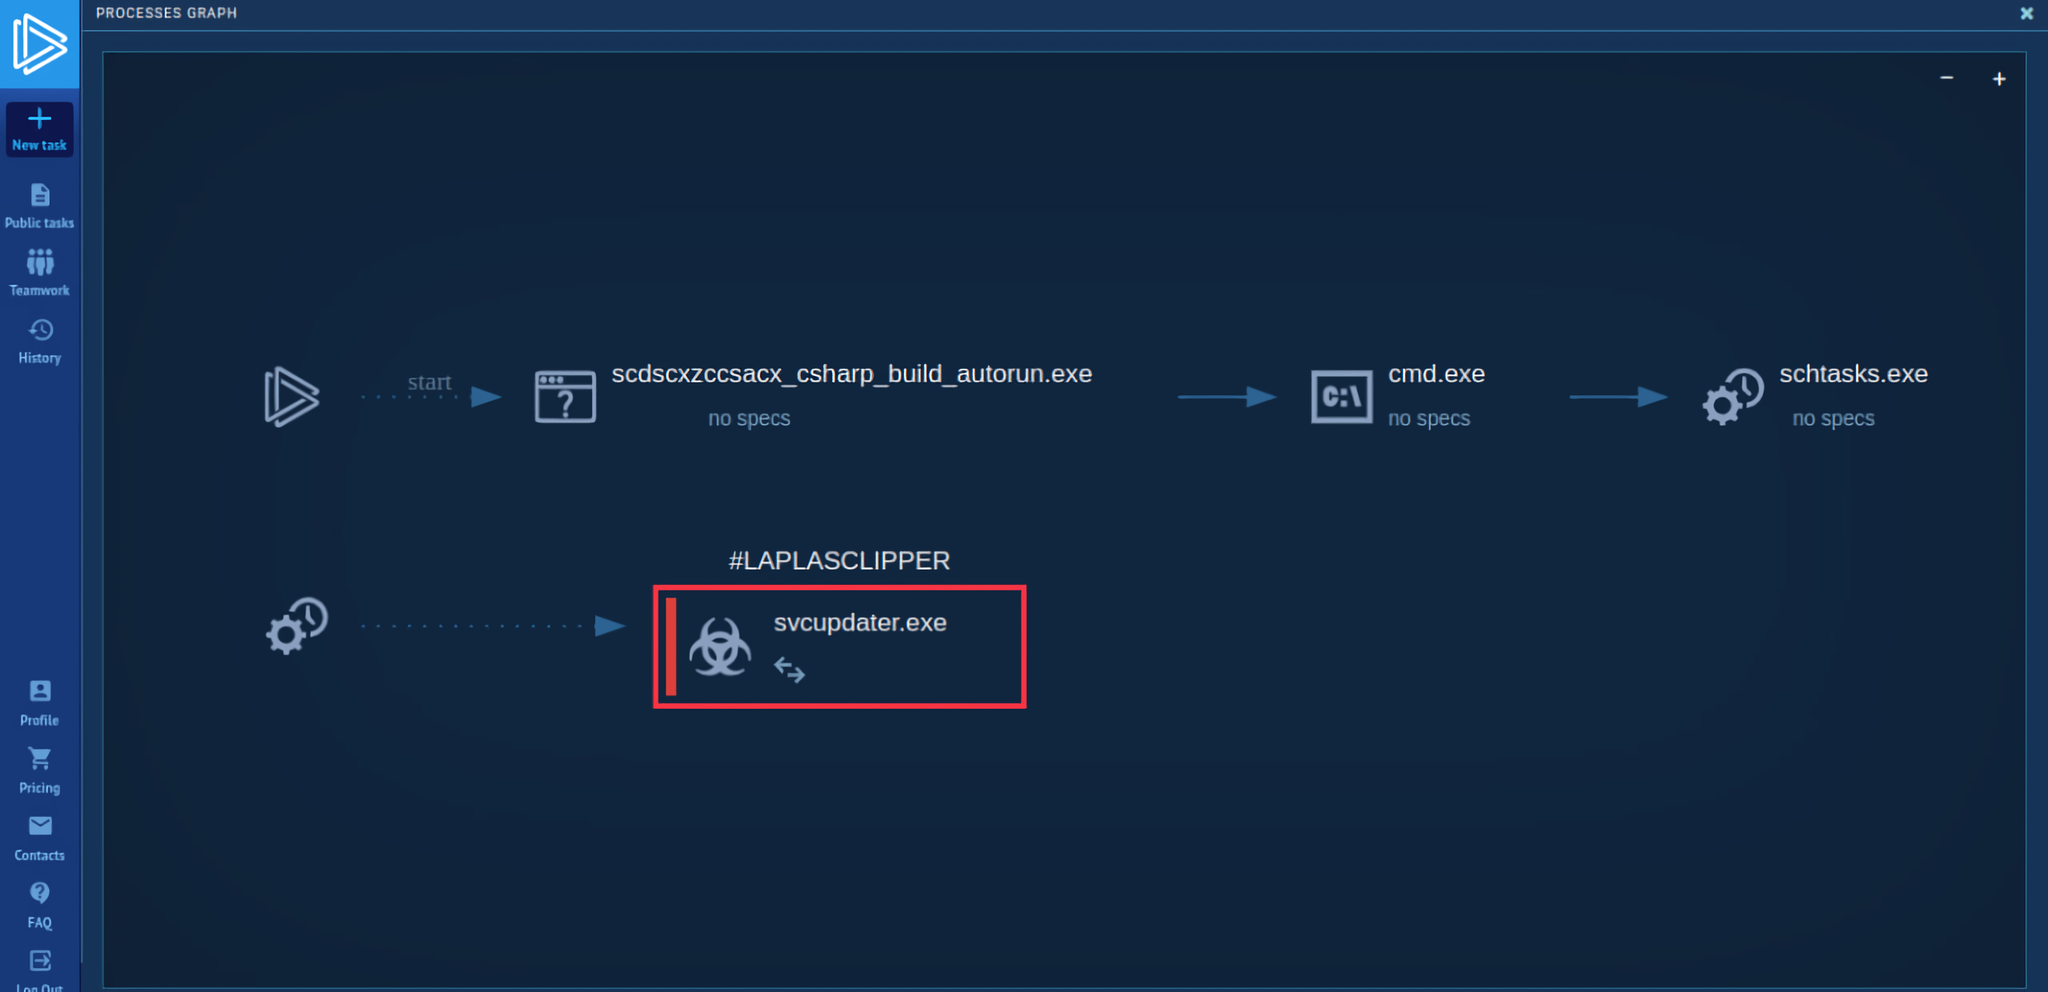
Laplas process tree Laplas Clipper's process tree

The task starts with the execution of a malicious file with the name "scdscxzccsacx_csharp_build_autorun.exe" located in the temporary folder. What's interesting is that this executable creates a scheduled task called "uAGRIUzbtd", which launches another executable named “svcupdater.exe.” This executable is located in the user's roaming folder stored inside the AppData directory (T1053.005). ANY.RUN shows that the "cmd" process was used to execute the "schtasks" process.

After one minute into the VM operation, the scheduled task starts the "svcupdater.exe" file. This indicates that the malware is attempting to establish persistence on the system by scheduling the execution of a file in the user's roaming folder. This behavior is commonly observed in malware that wants to maintain a presence on the system even after a reboot.

After that, the malware performs its main activity and begins to connect to C2 servers and collect information about the system. In this task, we can not only view the malware configuration by clicking the CFG icon next to the process or the MalConf button, but also download a dump of that process by clicking the DMP icon to perform additional analysis if needed.

Read a detailed analysis of Laplas Clipper in our blog.
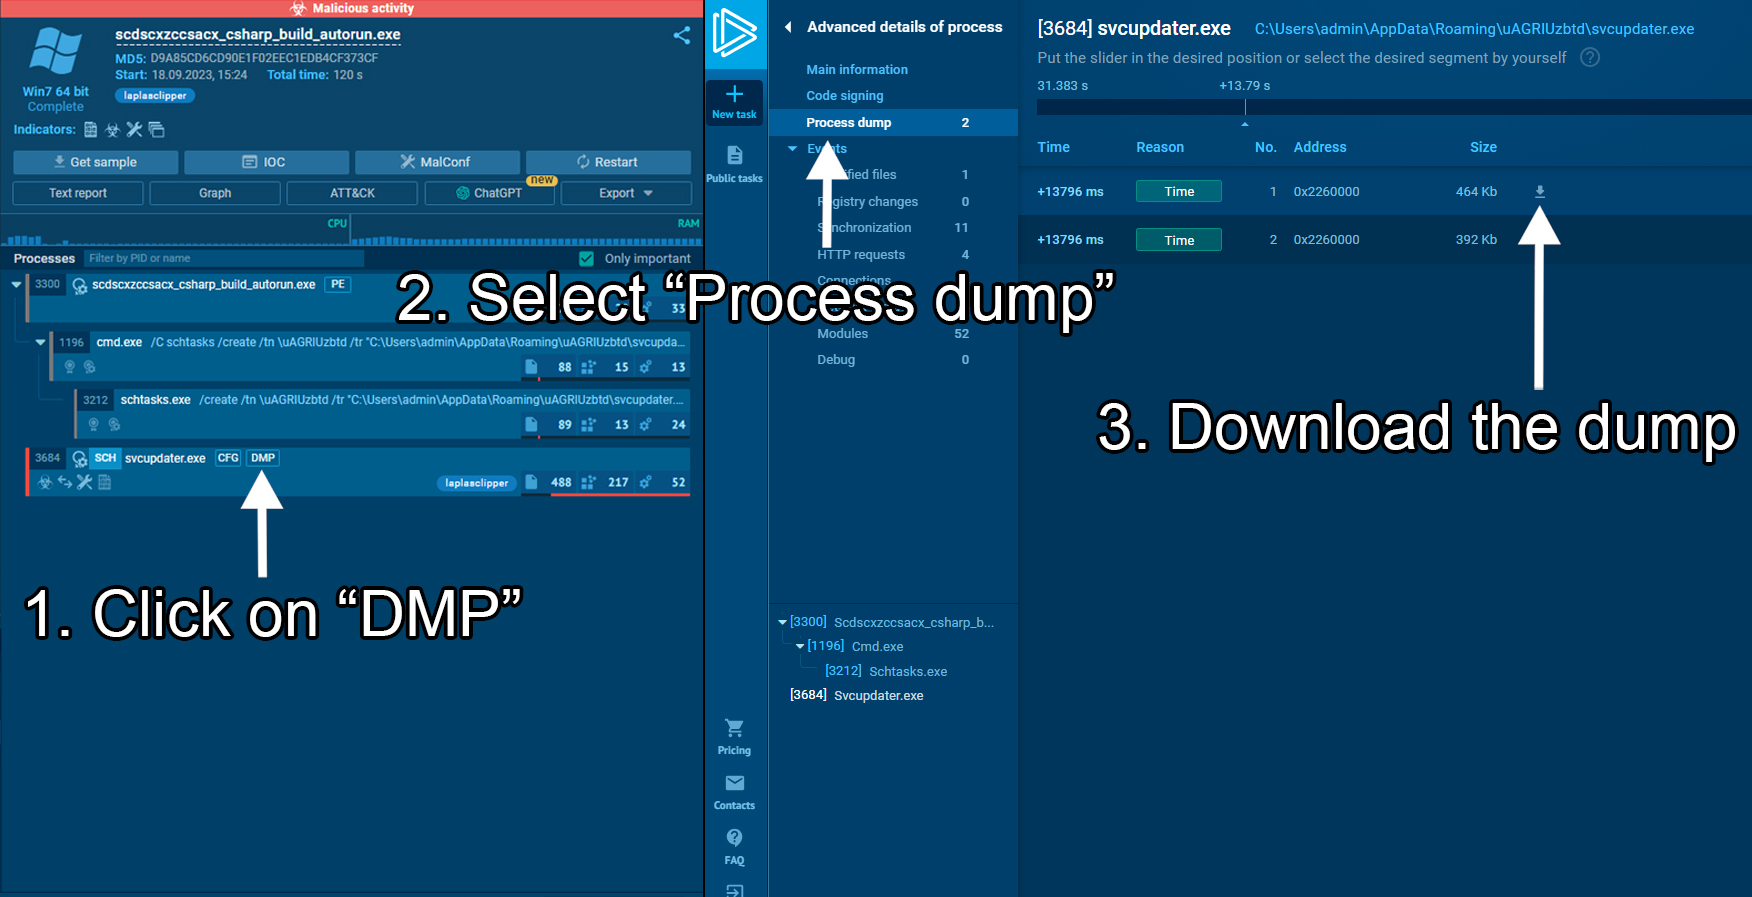
Laplas process dump ANY.RUN lets you download a process dump of the analyzed sample

Distribution methods of the Laplas Clipper malware

Phishing emails are commonly used by criminals as the first step in multi-stage attacks that ultimately lead to LaplasClipper infection. These attackers often create emails that are misleading and deceive individuals into opening attachments that contain harmful files. For instance, attackers have been observed to pose as CoinPayments, a well-known cryptocurrency payment gateway, and request users to download a .zip folder. By executing the files from the archive, users inadvertently install Laplas Clipper on their systems.

Conclusion

Laplas is a newly developed malware that poses a serious threat to crypto holders worldwide. The malicious actors behind Laplas attacks have been successful in stealing substantial amounts of virtual coins. Therefore, individuals and companies that deal with cryptocurrencies must exercise extra caution when opening email attachments from unknown senders and suspicious files from untrusted sources. To ensure the safety of a document or link, it is recommended to use ANY.RUN. This platform provides conclusive verdicts on the malicious behavior of files and URLs and generates detailed reports, containing IOCs and configs for future detection of the threat.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
GREENBLOOD screenshot
GREENBLOOD
greenblood
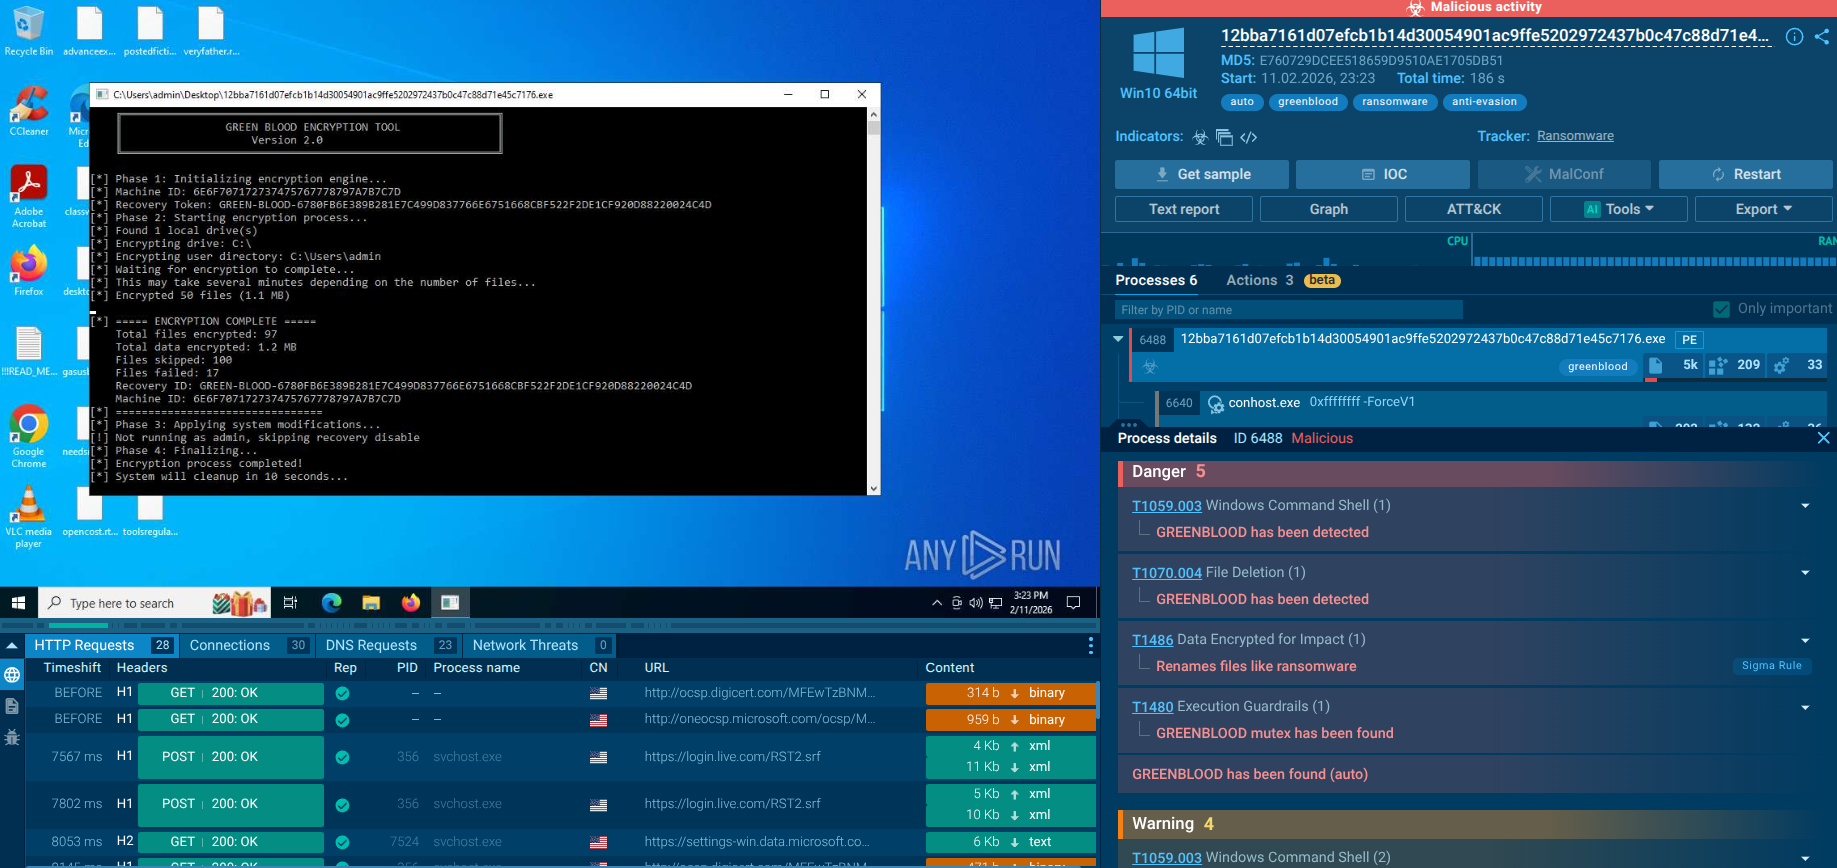
GREENBLOOD is a Go-based ransomware that uses concurrent ChaCha8 encryption to lock entire Windows environments in under a minute while systematically destroying backups, disabling defenses, and threatening double extortion through a Tor-based data leak site.
Read More
Agent Tesla screenshot
Agent Tesla
agenttesla trojan rat stealer
Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold.
Read More
Ransomware screenshot
Ransomware
ransomware
Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying.
Read More
DoubleTrouble screenshot
DoubleTrouble
doubletrouble
DoubleTrouble is a new-generation Android malware designed to quietly infiltrate mobile devices, harvest sensitive data, hijack financial operations, and maintain long-term persistence. Unlike commodity Android trojans, it blends advanced evasion, dual-stage infection, and dynamic payload updates, making it a rising mobile threat for both consumers and organizations.
Read More
Spynote screenshot
Spynote
spynote
SpyNote, also known as SpyMax and CypherRat, is a powerful Android malware family designed primarily for surveillance and data theft, often categorized as a Remote Access Trojan (RAT). Originally emerged in 2016, SpyNote has evolved significantly, with new variants continuing to appear as recently as 2023–2025.
Read More