Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
181
Global rank
134 infographic chevron month
Month rank
89 infographic chevron week
Week rank

Crimson is a Remote Access Trojan — a malware that is used to take remote control of infected systems and steal data. This particular RAT is known to be used by a Pakistani founded cybergang that targets Indian military objects to steal sensitive information.

Trojan
Type
Pakistan
Origin
1 January, 2016
First seen
7 October, 2026
Last seen
Also known as
SEEDOOR
Scarimson

How to analyze Crimson RAT with ANY.RUN

Type
Pakistan
Origin
1 January, 2016
First seen
7 October, 2026
Last seen

IOCs

IP addresses
104.26.3.193
3.121.234.184
108.132.234.191
150.171.27.11
192.178.183.97
142.251.13.157
74.178.76.128
50.31.142.31
35.186.253.211
3.248.136.126
103.67.200.72
20.250.198.32
18.173.205.79
23.52.180.25
3.167.231.118
104.18.7.169
48.209.138.168
129.212.214.111
74.125.250.129
80.77.87.136
Hashes
b848340aef333b6e9a65d2f2ca2f0cde08b7f7fcee661b666c9dae94643168e6
ecc20ed3c5dedbe5bbe73d1e7b14270c65a85f7d0ec4c94c4f0c9f0071e471a2
1e8dcaec98f99c2b1b43ff8b8655680b69bbf150470b20ecbdd1cb45570a0587
d3caf12591d194712facd10bca14f0a924edb59c24447a3fd994a48286db8843
643ac89572093a4c907c1af802b3d354453c64d545dc3f1be1ce689046064511
863b0e04b9e8af02d763cb98563ca8d9f80c6b99a3ec2eb6395db229bc3f8ba9
5dcb549657203cf2939b81f6845e956393179b1e6defc86a091ab2f9dc5096aa
ba3783050d8a2d02e1cdc8463b635dc21ac2a84da9ebd33bf362ed83ee53a2b5
bb9f8df61474d25e71fa00722318cd387396ca1736605e1248821cc0de3d3af8
d2559c5667d71458196c60d7d9614ac0588558e56aa9a58b6e7884a39a599902
01f144d804ea10709de3b63c855e7078d4c7e1f578915761030373b9bb32cf2e
84886342ecdc4b1b095067268cdc5e94241959a551e0fdaa5f2998467f870aa2
8232c450f967d7f2f22c54582f0667f4c033ae62e6d450ff8a35c47486249443
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
f51a7acfffec56d6751561966d947d3fd199b74528c07dabdcf5fcb33d5b2e85
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
7852fce59c67ddf1d6b8b997eaa1adfac004a9f3a91c37295de9223674011fba
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
Domains
googleads4.g.doubleclick.net
zipthelake.com
dpm.demdex.net
ds6.probe.whatismyipaddress.com
stats.prebid.wurflcloud.com
ads.pubmatic.com
data.adsrvr.org
enduser.adsrvr.org
sync.sparteo.com
sync.cootlogix.com
ms-cookie-sync.presage.io
onetag-sys.com
e.clarity.ms
th.bing.com
ep1.adtrafficquality.google
a.nel.cloudflare.com
ssum-sec.casalemedia.com
tag.durationmedia.net
cmp.inmobi.com
match.adsrvr.org
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:oetoboc3cqibavya149bep0q06d3dsoxmnbsbizwo3k&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791345118&lafgdate=0
https://copilot.microsoft.com/c/api/user/eligibility
https://ntp.msn.com/edge/ntp?locale=en-us&title=new%20tab&dsp=1&sp=bing&startpage=1&pc=u531
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://ntp.msn.com/bundles/v1/edgechromium/latest/ssr-extension.c8264382acf37d60.js
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 1389
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 3845
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 5997
comments 0

What is Crimson RAT?

Crimson is a Remote Access Trojan — it is malware that cybercriminals or threat groups can utilize to gather information from infected systems. The malware is also known under the names SEEDOOR and Scarimson. It can be used to spy on victims, capture screenshots, steal credentials, and more.

Crimson is known to be used particularly by an APT (Advanced Persistent Threat), a cyber gang founded by a state. Therefore, the Crimson RAT is targeted at a very specific group of victims, among whom are Indian Government organizations and the military.

General description of Crimson RAT

Crimson RAT is among malware that utilizes information related to the coronavirus to infect the machines of their victims. The strategy of using a natural disaster to exploit the need for information and the stress of potential victims is not new among cybercriminals. In fact, fake information about SARS and other epidemics is still used for phishing by some cyber-attack schemes.

As such, the Crimson malware authors use a fake health advisory email to trick victims into downloading a malicious document.

After the RAT is downloaded and installed it can perform several malicious functions, most of which are targeted at information gathering. The RAT can record and share running processes on an infected machine with the attackers, take screenshots, and steal information from web-browsers. Also, the malware has the capability to download files into infected systems from a control server.

As we mentioned above, the Crimson RAT is operated by an APT. In particular, APT36, which is thought to be sponsored by Pakistani officials to conduct military espionage. Thus, the victims of the RAT are almost exclusively among Indian officials and military personal. It is believed that retrieved sensitive information that the APT collects is used by Pakistan in military efforts against India.

In fact, APT36 is also commonly known under the name Mythic Leopard, has a history of successful attacks on Indian embassies and military infrastructure that resulted in the stealing of tactical and training information. However, other malware samples have been used in previous attacks.

Crimson RAT malware analysis

A video recorded in the ANY.RUN interactive malware analysis service shows the execution process of Crimson RAT.
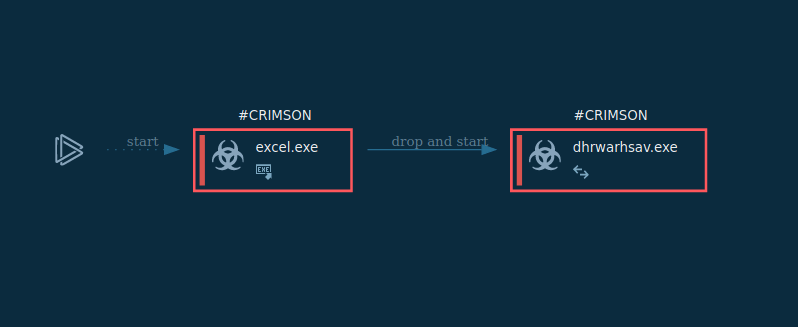
crimson_process_graph

Figure 1: Shows the execution process of the Crimson RAT. This Graph was generated by ANY.RUN.
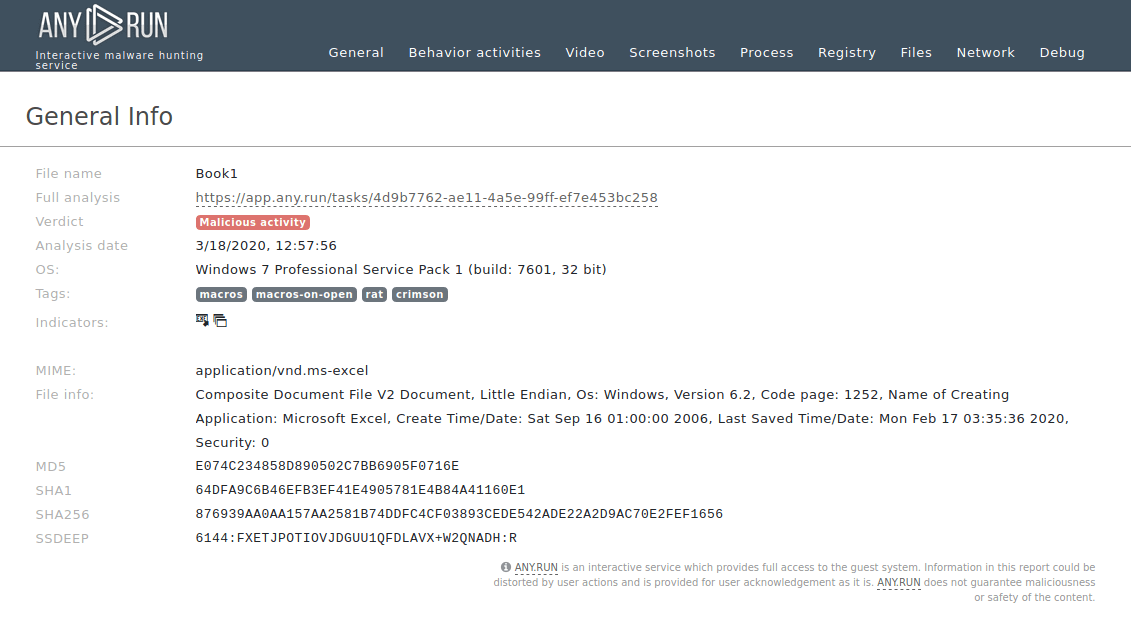
crimson_text_report

Figure 2: Displays a text report that users can create in ANY.RUN. Text reports can be used to demonstrate found information and can be customized to show only necessary data.

Crimson RAT execution process

Crimson RAT execution process is pretty straightforward but it can vary from sample to sample. Often, the malware executable file is located directly inside a malicious document and once the user opens it, the file drops the trojan. In other cases, a maldoc can contain a macro that leverages Powershell to download and start a Crimson executable file. After the trojan starts, it will try to establish a connection with a C2 server and transmit information about the victim's system and the list of running processes on that system.

Crimson RAT malware distribution

Crimson RAT spreads using highly targeted email spam campaigns using the same scenario as Quasar RAT. Spear Phishing techniques that leverage the fear of the Covid-19 pandemic are used to trick victims into downloading a Microsoft Office Excel file, which allegedly contains information related to the outbreak. Once the file is opened, it launches malicious macros or exploits vulnerabilities, such as CVE-2017–0199 for example.

How to detect Crimson RAT

Analysts can detect the Crimson RAT based on file operations. To do so, click on the process in the "Process list" section, and in the appeared "Process details" window click the "More info" button. In the "Event" section switch from "Friendly" to "Raw". After that, enter "Edlacar", "Dhrolas", "Ardscar" or "Dtromera" in the "Filename" field. If operations with a folder with such names are found, be sure — that’s the Crimson RAT in front of you.

Conclusion

Crimson the same as Netwalker is a prime example of a threat actor using a pandemic or other natural disaster to gain leverage over its victims and trick them into installing malware. So far this particular malware has been used almost exclusively in military espionage, but it may very well become more widespread in the future.

Since this is a lesser-known malware, not a lot of samples are available to analyze. Thankfully, ANY.RUN malware hunting service presents an opportunity to study this RAT in an interactive simulation, allowing for quick and simple dynamic analysis in a secure online environment.
HAVE A LOOK AT

DragonForce screenshot
DragonForce
dragonforce
DragonForce is a ransomware strain operating under the Ransomware-as-a-Service (RaaS) model. First reported in December 2023, it encrypts files with ChaCha8, renames them with random strings, and appends “.dragonforce_encrypted.” By disabling backups, wiping recovery, and spreading across SMB shares, DragonForce maximizes damage and pressures victims into multimillion-dollar ransom negotiations. It has targeted manufacturing, construction, IT, healthcare, and retail sectors worldwide, making it a severe threat to modern enterprises.
Read More
Moonrise screenshot
Moonrise
moonrise
Moonrise RAT is a newly discovered Go-based remote access trojan with zero detections at launch, featuring credential theft, keylogging, webcam access, clipboard hijacking, and UAC bypass.
Read More
NetSupport RAT screenshot
NetSupport RAT
netsupport
NetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
Read More
GuLoader screenshot
GuLoader
guloader
GuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
Read More
RatonRAT screenshot
RatonRAT
raton
RatonRAT is a .NET-based Remote Access Trojan targeting Windows systems. It supports credential theft, screen capture, system and hardware discovery, persistence, and C2 communication. Samples use techniques such as Registry Run keys and scheduled tasks for persistence, with some variants employing anti-analysis and evasion techniques.
Read More
StrelaStealer screenshot
StrelaStealer
strela
StrelaStealer is a malware that targets email clients to steal login credentials, sending them back to the attacker’s command-and-control server. Since its emergence in 2022, it has been involved in numerous large-scale email campaigns, primarily affecting organizations in the EU and U.S. The malware’s tactics continue to evolve, with attackers frequently changing attachment file formats and updating the DLL payload to evade detection.
Read More