Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Rhadamanthys

74
Global rank
69 infographic chevron month
Month rank
78 infographic chevron week
Week rank

Rhadamanthys is a C++ information-stealing malware that extracts sensitive data from infiltrated machines. Its layered operational chain and advanced evasion tactics make it a major risk in cybersecurity landscapes.

Stealer
Type
Unknown
Origin
26 September, 2022
First seen
4 October, 2026
Last seen

How to analyze Rhadamanthys with ANY.RUN

Type
Unknown
Origin
26 September, 2022
First seen
4 October, 2026
Last seen

IOCs

IP addresses
23.52.181.141
172.211.123.249
74.178.76.54
20.190.160.14
48.209.6.48
135.232.92.137
188.114.97.3
2.21.20.155
140.82.121.3
23.11.41.157
48.192.1.65
2.23.246.101
185.199.108.133
2.21.20.150
69.222.184.7
73.237.28.132
210.127.88.188
58.222.58.214
174.141.87.185
128.229.248.20
Hashes
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
040f44e6c06d974ad102a864e810b94385deab22b3dca0086ac196c9e8709042
fd4c9fda9cd3f9ae7c962b0ddf37232294d55580e1aa165aa06129b8549389eb
e858f419dcb24be43214fff1097c8acbf37f840e09a6cb0655db7752e019612d
d96856cd944a9f1587907cacef974c0248b7f4210f1689c1e6bcac5fed289368
aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
72f6b34d3c8f424ff0a290a793fcfbf34fd5630a916cd02e0a5dda0144b5957f
5fc25c30aee76477f1c4e922931cc806823df059525583ff5705705d9e913c1c
46079c0a1b660fc187aafd760707f369d0b60d424d878c57685545a3fce95819
2eb96422375f1a7b687115b132a4005d2e7d3d5dc091fb0eb22a6471e712848e
b7ee468f5b6c650dada7db3ad9e115a0e97135b3df095c3220dfd22ba277b607
76d8e4ed946deefeefa0d0012c276f0b61f3d1c84af00533f4931546cbb2f99e
5c9bc70586ad538b0df1fcf5d6f1f3527450ae16935aa34bd7eb494b4f1b2db9
72c639d1afda32a65143bcbe016fe5d8b46d17924f5f5190eb04efe954c1199a
7102f8d9d0f3f689129d7fe071b234077fba4dd3687071d1e2aeaa137b123f86
d6708d1254ed88a948871771d6d1296945e1aa3aeb7e33e16cc378f396c61045
058eb7ce88c22d2ff7d3e61e6593ca4e3d6df449f984bf251d9432665e1517d1
f5183b8d7462c01031992267fe85680ab9c5b279bedc0b25ab219f7c2184766f
ec359f50ca15395f273899c0ff7c0cd87ab5c2e23fdcfc6c72fedc0097161d4b
0b7ed6e2c81e12a0caa32aa89831a68c26b6de783343ca88fbdc3632945cd463
Domains
github.com
ocsp.digicert.com
settings-win.data.microsoft.com
crl.microsoft.com
nexusrules.officeapps.live.com
raw.githubusercontent.com
go.microsoft.com
ecs.office.com
slscr.update.microsoft.com
google.com
self.events.data.microsoft.com
www.microsoft.com
activation-v2.sls.microsoft.com
fe3cr.delivery.mp.microsoft.com
login.live.com
client.wns.windows.com
doxbin.cy
crl3.digicert.com
xvasyijoifann.ru
60aaf9c6.salamanderprocessing.pages.dev
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://github.com/digitalforensiker/myreadme/raw/refs/heads/main/readme.zip
https://raw.githubusercontent.com/digitalforensiker/myreadme/refs/heads/main/readme.zip
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Rhadamanthys Stealer Malware

First observed in late 2022, Rhadamanthys is an advanced info-stealer that targets Windows platforms. It is distributed through the malware-as-a-service (MaaS) model. This, in conjunction with its extremely robust and diverse malicious capabilities contributes to the rising popularity of this malware.

Similar to threats like RedLine or Raccoon, utilizing this new strain, threat actors can extract user passwords and exfiltrate sensitive data from infiltrated systems. The info-stealer also presents a significant threat to various cryptocurrency platforms, where it's employed to seize user credentials and wallets.

Certain indicators suggest that Rhadamanthys stealer has the potential to evolve into a pervasive threat. Notably, the malware's initial launch demonstrated signs of meticulous planning. The individual who first introduced it on an underground forum, operating under the pseudonym "kingcrete2022", began building his account's reputation well in advance of the release announcement. This proactive strategy aimed to establish credibility and set the stage for the malware's introduction.

The tactic proved successful, as the debut post, which promoted Rhadamanthys as a "first-class" stealer, quickly gained momentum and attracted attention in the underground community.

As it stands, Rhadamanthys indiscriminately attacks targets worldwide, even reaching into the territories of the former USSR. The malware has been identified in several malicious spam and Google Ads campaigns, but more on this later in the article.

It should be noted, that Rhadamanthys stealer employs a design philosophy that aims to incorporate an expansive list of features. These features are not strategically targeted but rather prioritize extensive capability. For example, malware is, rather unnecessarily, equipped with capabilities to steal data from web browsers such as KMeleon and Pale Moon, and to steal cryptocurrency from obscure browser extensions like Firefox's Auvitas Wallet.

In terms of system information extraction, Rhadamanthys can capture a wide array of data. This includes:

-Computer name, username, RAM capacity, CPU cores, screen resolution

-Installed software, cookies, browsing history

-Saved credit cards and other sensitive information

Furthermore, Rhadamanthys targets credentials from a vast range of sources: FTP clients like Cyberduck and TotalCommander, mail clients such as Outlook and Thunderbird, and password managers like RoboForm and KeePass. It also has the capacity to extract information from VPN services, note-taking applications, messenger applications, and other services like Steam, TeamViewer, and SecureCRT.

Rhadamanthys shows a particular interest in cryptocurrency. One of its version updates had nearly half of its new features dedicated to exfiltrating and cracking cryptocurrency wallets. The list of targeted wallets is quite extensive and includes Auvitas, BitApp, Crocobit, Exodus, Finnie, ICONex, Metamask, and more.

In addition to the automatic actions, Rhadamanthys also allows for direct intervention by attackers. The malware offers a functionality to push new configurations to the “file grabbing” module, allowing specific files to be exfiltrated. For a more hands-on approach, attackers can execute hand-crafted PowerShell scripts on the victim machine. This added flexibility provides a high degree of control over the infected system.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Rhadamanthys Stealer Technical Details

Written in C++, Rhadamanthys employs a number of sophisticated techniques to ensure its stealth and efficacy. Its operational chain is usually divided into three components:

-the Dropper,

-the Rhadamanthys Loader (second shellcode)

-and the Rhadamanthys Stealer (Nsis module).

In one attack observed the wild, the Dropper initiated the process by executing the shellcode through a callback function. This bypassesed common security measures that track shellcode execution methods like CreateThread or CreateRemoteThread.

Next, the Rhadamanthys Loader, or the second shellcode, comes into play. This shellcode uses several evasion methods. It manipulates exception handling to maintain low visibility, creates a Mutex to simulate legitimate processes, and unhooks API calls to avoid detection. In addition to these, it is responsible for decrypting the malware configuration and managing its network functions.

Lastly, the Rhadamanthys Stealer, or the Nsis module, is activated. Some samples have the ability to manipulate AVAST’s AMSI-related modules to avoid detection. It is this component that ultimately executes the data theft.

Rhadamanthys Stealer Dynamic Analysis

Being a stealer, Rhadamanthys tries to operate as secretively as possible, remaining under the radar and avoiding detection. The malicious activity starts right after infection — Rhadamanthys extracts information from the system and tries to send it to the Command & Control servers.

The execution chain may vary a little — some versions of the Trojan have the ability to inject into system processes, while others simply execute themselves.

It also may delay execution and sleep for some time after infection or use utilities like PowerShell to run commands.
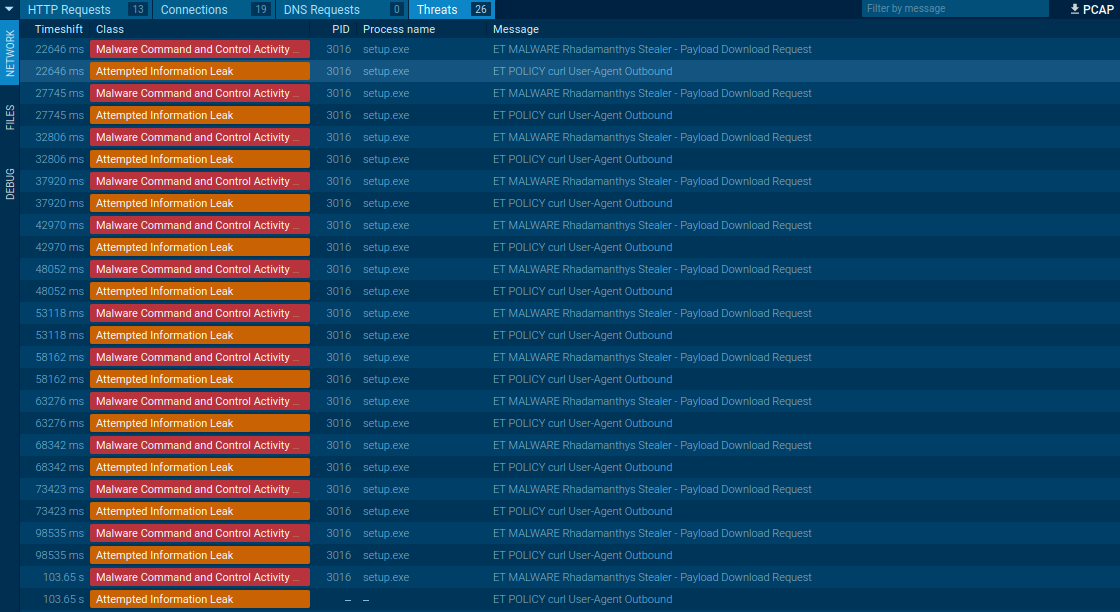
Rhadamanthys’s network traffic Rhadamanthys’s network traffic

Thanks to the network packets structure, Rhadamanthys can be detected by Suricata rules.

Rhadamanthys Stealer Distribution Methods

Rhadamanthys info-stealer employs a couple of key strategies to infiltrate systems. One of its infamous шstribution techniques involves hijacking Google ads, where it covertly replaces the original content with a link to the malware.

It also uses phishing webpages and malicious spam for propagation. In malspam campaigns, a PDF file triggers victims to download the malware. The PDF file was observed presenting a fake Adobe Acrobat DC software update prompt which, when clicked, initiates the execution of the malware.

In phishing-based distribution, the malware creators build fake webpages mimicking legitimate services like Zoom or AnyDesk. Links to these fraudulent sites are then spread via Google ads. These malicious sites facilitate the download of the Rhadamanthys infostealer disguised as a legitimate installer. Consequently, the target unknowingly downloads the malware without noticing the infection.

Conclusion

Boasting an extensive stealing feature set that may well be unmatched among similar types of malware, Rhadamanthys has the potential to emerge as a significant threat in the cybersecurity landscape. We strongly recommend analysts to delve into this threat while it's still relatively new on the scene.

Conveniently, dynamic analysis of Rhadamanthys can be easily carried out on platforms such as ANY.RUN — our cloud interactive sandbox allows for a deeper understanding of its execution process and facilitates the collection of valuable Indicators of Compromise (IOCs).

Investigating the nuances of Rhadamanthys not only aids in its containment but also prepares us for future threats that may adopt a similar design strategy.
HAVE A LOOK AT

Godfather screenshot
Godfather
godfather
The Godfather malware is an Android banking Trojan capable of bypassing MFA that targets mobile banking and cryptocurrency applications. Known for its ability to evade detection and mimic legitimate software, it poses a significant threat to individuals and organizations by stealing sensitive data and enabling financial fraud.
Read More
Roning Loader screenshot
Roning Loader
roning
RoningLoader is a multi-stage Windows loader designed to operate quietly while preparing systems for deeper compromise. It abuses trusted system tools and interferes with security controls to reduce the chances of early detection. Instead of acting as a final payload, it creates conditions for follow-on malware to execute more effectively. Its use of staged execution and code injection allows attackers to blend into legitimate activity and escalate impact. This makes early behavioral detection critical before the attack chain progresses further.
Read More
Netwalker screenshot
Netwalker
netwalker ransomware
Netwalker is ransomware — it belongs to a malware family which encrypts files and demands users to pay a ransom to get their data back. Netwalker utilizes several sophisticated techniques, such as process hollowing and code obfuscation to target corporate victims.
Read More
Gh0st RAT screenshot
Gh0st RAT
gh0st
Gh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.
Read More
Backdoor screenshot
Backdoor
backdoor
A backdoor is a type of cybersecurity threat that allows attackers to secretly compromise a system and conduct malicious activities, such as stealing data and modifying files. Backdoors can be difficult to detect, as they often use legitimate system applications to evade defense mechanisms. Threat actors often utilize special malware, such as PlugX, to establish backdoors on target devices.
Read More
Phobos screenshot
Phobos
phobos ransomware
Phobos is a ransomware that locks or encrypts files to demand a ransom. It uses AES encryption with different extensions, which leaves no chance to recover the infected files.
Read More