Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Cobalt Strike

27
Global rank
35 infographic chevron month
Month rank
36 infographic chevron week
Week rank

Cobalt Strike is a legitimate penetration software toolkit developed by Forta. But its cracked versions are widely adopted by bad actors, who use it as a C2 system of choice for targeted attacks.

Penetration software
Type
Unknown
Origin
20 February, 2012
First seen
22 September, 2026
Last seen

How to analyze Cobalt Strike with ANY.RUN

Penetration software
Type
Unknown
Origin
20 February, 2012
First seen
22 September, 2026
Last seen

IOCs

IP addresses
200.125.60.96
65.109.127.15
206.120.235.210
158.117.155.107
210.245.141.205
187.120.197.126
204.186.227.208
76.156.205.17
108.222.146.109
84.183.170.132
209.135.58.40
21.179.42.221
210.183.0.198
42.198.39.179
181.24.89.243
70.234.134.192
88.116.180.103
48.158.82.100
217.60.195.226
192.209.123.178
Hashes
3e54286e348ebd3d70eaed8174cca500455c3e098cdd1fccb167bc43d93db29d
aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
bad9116386343f4a4c394bdb87146e49f674f687d52bb847bd9e8198fda382cc
40b3d590f95191f3e33e5d00e534fa40f823d9b1bb2a9afe05f139c4e0a3af8d
46079c0a1b660fc187aafd760707f369d0b60d424d878c57685545a3fce95819
2eb96422375f1a7b687115b132a4005d2e7d3d5dc091fb0eb22a6471e712848e
b7ee468f5b6c650dada7db3ad9e115a0e97135b3df095c3220dfd22ba277b607
629e52ba4e2dca91b10ef7729a1722888e01284eed7dda6030d0a1ec46c94086
76d8e4ed946deefeefa0d0012c276f0b61f3d1c84af00533f4931546cbb2f99e
5c9bc70586ad538b0df1fcf5d6f1f3527450ae16935aa34bd7eb494b4f1b2db9
72c639d1afda32a65143bcbe016fe5d8b46d17924f5f5190eb04efe954c1199a
7102f8d9d0f3f689129d7fe071b234077fba4dd3687071d1e2aeaa137b123f86
d6708d1254ed88a948871771d6d1296945e1aa3aeb7e33e16cc378f396c61045
6238cbfe9f57c142b75e153c399c478d492252fda8cb40ee539c2dcb0f2eb232
058eb7ce88c22d2ff7d3e61e6593ca4e3d6df449f984bf251d9432665e1517d1
f5183b8d7462c01031992267fe85680ab9c5b279bedc0b25ab219f7c2184766f
60fe386112ad51f40a1ee9e1b15eca802ced174d7055341c491dee06780b3f92
2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
78bedd9fce877a71a8d8ff9a813662d8248361e46705c4ef7afc61d440ff2eeb
dc58d8ad81cacb0c1ed72e33bff8f23ea40b5252b5bb55d393a0903e6819ae2f
Domains
rcigoqmlncfehy.net
down.54nb.com
client-update.steamstatic.com
check.screenconnect.com
dsrrdiiratdsmo.co.uk
soft.wsyhn.com
cdn-10049480.file.myqcloud.com
safeifm.com
royalindiancurryclub.com
palharesinformatica.com.br
jssetup.com
ad.qqfarmer.com.cn
gro.runtimeforge.cc
login.live.com
projetodegente.com
rdm.91yunma.cn
fileupdates.blob.core.windows.net
x1.c.lencr.org
status.rapidssl.com
bnet.playm8ru.win
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://108.187.43.222/chfs/shared/etup.exe
http://185.99.135.134/bin/screenconnect.clientsetup.msi
http://176.65.148.112/win.exe
http://31.56.209.11/s.bat
http://31.56.209.11/svc.exe
http://193.178.158.107/bin/a595f30d6d74713f_0.exe
http://62.60.226.140/files/logn/rop.exe
http://158.94.210.129/gmt/kkcrypted_stub.ps1
http://176.65.139.220/bot.exe
http://91.92.242.236/files-129312398/files/file_2a246d5665a195b1.exe
http://contididit.conti.pk/contis.exe
Last Seen at
Last Seen at

Recent blog posts

post image
CSuite Targets US and EU Organizations with D...
watchers 2303
comments 0
post image
How MSSPs Can Prove Their Value When “Nothing...
watchers 7199
comments 0
post image
Enterprise Threat Intelligence Buying Guide:...
watchers 7913
comments 0

What is Cobalt Strike malware

Cobalt Strike is a licensed penetration software package developed by Forta (previously Help Systems), that helps red teams simulate an adversary in red-vs-blue games.

While the software itself is completely legal and designed for cybersecurity testing, over the years, many versions of it have been cracked and leaked into the wild. Despite several attempts to stop its abuse — by the developer and the online community — attackers continue to employ it to install multiple payloads after compromising their victims' networks.

Most of these cracked versions were obtained by accessing a trial — which is only given to verified parties, but evidently, hackers found a way to skirt this — and bypass the license check and then trial restrictions. (The trial version of Cobalt Strike has many deliberate giveaways such as the EICAR string embedded in all payloads and a watermark.)

Being a legitimate tool, there is a ton of educational material online, which illustrates what Cobalt Strike can do. Like this official playlist on YouTube. This, of course, lowers the entry threshold and contributes to the popularity of the software among bad actors. One can literally learn how to abuse it directly from its creators.

Cracked Cobalt Strike versions are circulating freely in various underground forums and are sometimes found on clearnet resources, like GitHub. Although most of them are somewhat outdated, they still pose a serious threat — many criminal groups use them to gain initial access and move laterally through victim’s networks.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Cobalt Strike malware analysis review

Cobalt Strike consists of multiple components, which together form a comprehensive hacking suit. The central element of the software is the Team Server component — which acts as both the C2 server and a coordinating program that helps multiple adversaries work together and control hijacked devices. To access it, actors use a Client component which serves as the GUI for the Team Server.

Team Server can generate shellcode implants called Stagers. These fileless implants are available as VBA, Javascript and Powershell macro templates. When an attacker infiltrates and injects one of the Stagers into the victim's network, they can contact the Team Server via HTTP/HTTPS, SMB, or DNS to fetch and install the main payload known as the Beacon.

The Beacon is the core binary which allows the attacker to control infected machines remotely. It supports a wide list of malicious operations, and is designed to be configurable and expandable. This feature is often used to deliver and run custom modules, and makes Cobalt Strike's malicious capabilities virtually limitless. What’s more, there are built-in modules that allow attackers to customize the payload to avoid detection: these include the Artifact Kit, Malleable C2 Profiles, and Resource Kit.

Also, it’s important to note that since Cobalt Strike was originally designed for team exercises, the Team Server and Client modules allow criminal gangs to coordinate hacks with multiple attackers acting simultaneously, potentially targeting multiple weak spots.

The payloads usually delivered by Cobalt Strike range from Ransomware to spyware and even Advanced Persistent Threats.

How to get more information from Cobalt Strike malware

ANY.RUN helps analysts track the execution process of Cobalt Strike in an interactive online sandbox.
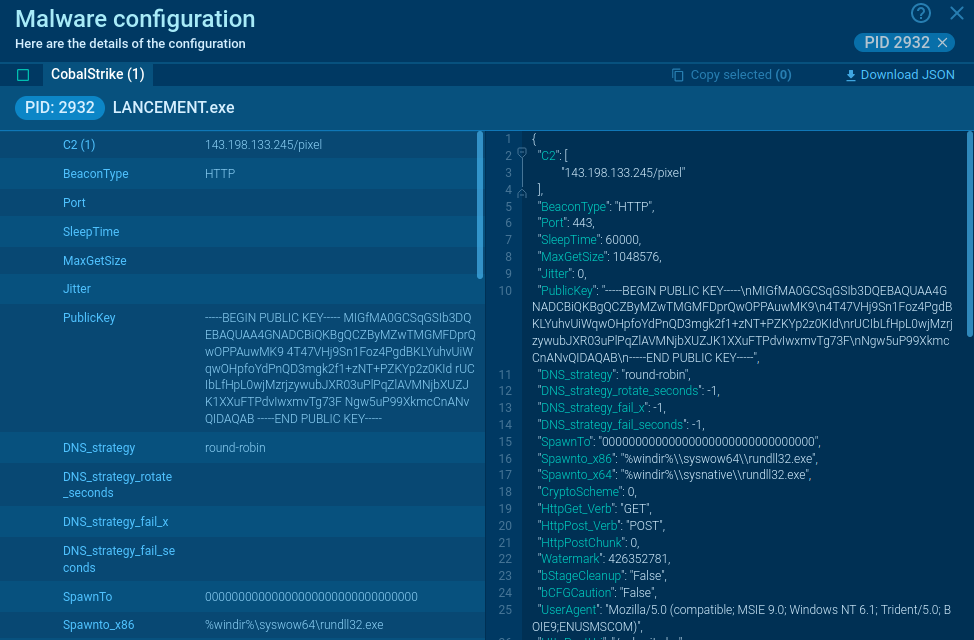
Cobalt Strike malware configuration

Figure 1: Cobalt Strike malware configuration

ANY.RUN users can access the analysis results 10 seconds after launching the sandbox, which saves crucial time, especially during incident response when every second matters.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Cobalt Strike execution process

The execution of CobaltStike varies greatly from sample to sample. Not only are there lots of iterations of the client, but the program itself is frequently updated by the developers. Besides the common type that uses an executable file, there are also versions that use powershell or JS to dominate the infected system.

In ANY.RUN, users can study the config of CobaltStrike’s utility to better understand how it works.

Distribution of Cobalt Strike

Unfortunately, the distribution of Cobalt Strike is poorly documented, but it’s believed to be delivered using macros that come with an infected executable embedded in a phishing email. There are few reports of this particular malware, so the conclusion was drawn based on the little information available, and the fact that it is by far the most common attack vector.

Conclusion

Cobalt Strike has gained an excellent reputation among cybercriminals who continue to use it as their Command and Control system of choice to deliver and execute a wide variety of payloads. This is a perfect example of what a legitimate piece of kit can do in the wrong hands. That said, its abuse is a fairly well-researched topic in the community, and there are guides like this one and this one that can help you defend against attacks using this software.

We hope that as the good research continues, and organizations arm themselves against cracked copies of Cobalt Strike, the abuse of this powerful cybersecurity tool will eventually stop.
HAVE A LOOK AT

EvilProxy screenshot
EvilProxy
evilproxy
EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.
Read More
Kali365 screenshot
Kali365 is an emerging Phishing-as-a-Service (PhaaS) platform that targets Microsoft 365 environments by stealing OAuth authentication tokens instead of passwords. First observed in April 2026, the service enables even low-skilled threat actors to bypass multi-factor authentication (MFA), gain persistent access to corporate cloud accounts, and compromise business communications, files, and collaboration platforms. Kali365 represents a shift from traditional credential theft toward session hijacking and token abuse, making it a significant threat to organizations that rely on Microsoft 365.
Read More
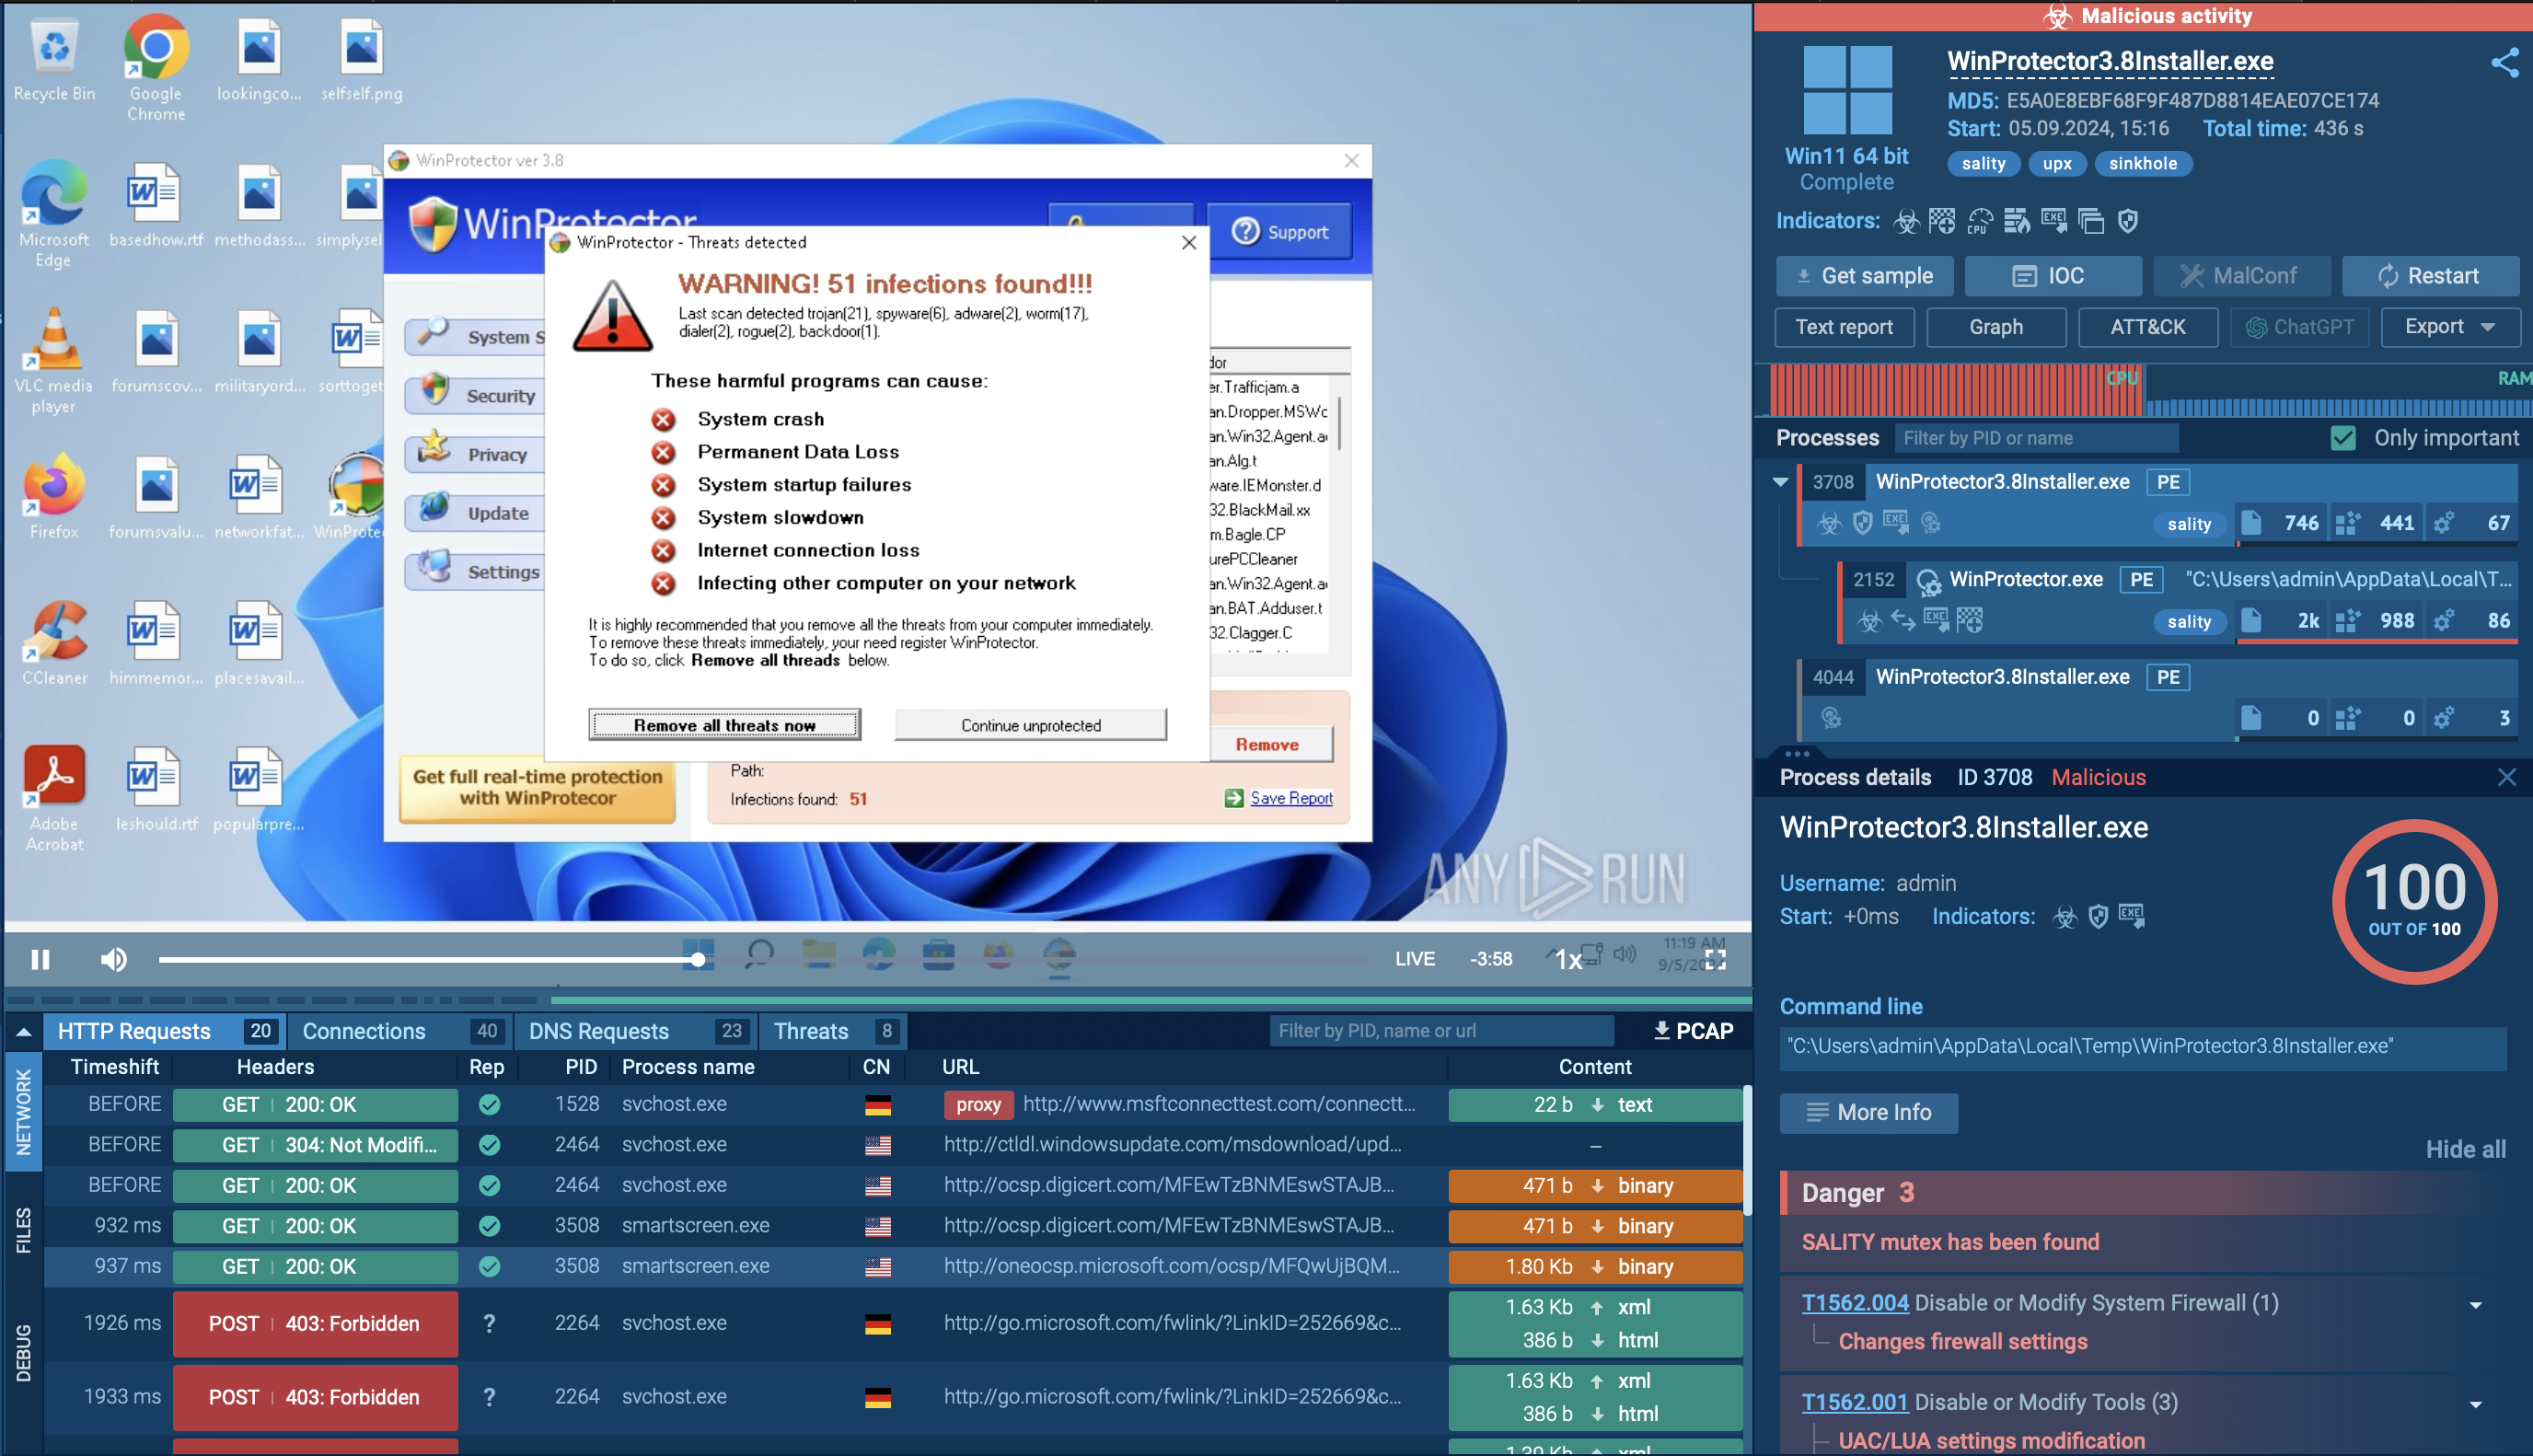
Sality screenshot
Sality
sality
Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.
Read More
Stealc screenshot
Stealc
stealc
Stealc is a stealer malware that targets victims’ sensitive data, which it exfiltrates from browsers, messaging apps, and other software. The malware is equipped with advanced features, including fingerprinting, control panel, evasion mechanisms, string obfuscation, etc. Stealc establishes persistence and communicates with its C2 server through HTTP POST requests.
Read More
Phorpiex screenshot
Phorpiex
phorpiex
Phorpiex is a malicious software that has been a significant threat in the cybersecurity landscape since 2016. It is a modular malware known for its ability to maintain an extensive botnet. Unlike other botnets, Phorpiex does not concentrate on DDoS attacks. Instead, it has been involved in numerous large-scale spam email campaigns and the distribution of other malicious payloads, such as LockBit.
Read More
XRed screenshot
XRed
xred
XRed operates as a stealthy backdoor, enabling cybercriminals to gain unauthorized remote access to infected systems. XRed has gained particular notoriety for its distribution through trojanized legitimate software and hardware drivers, making it exceptionally dangerous due to its ability to masquerade as trusted applications.
Read More