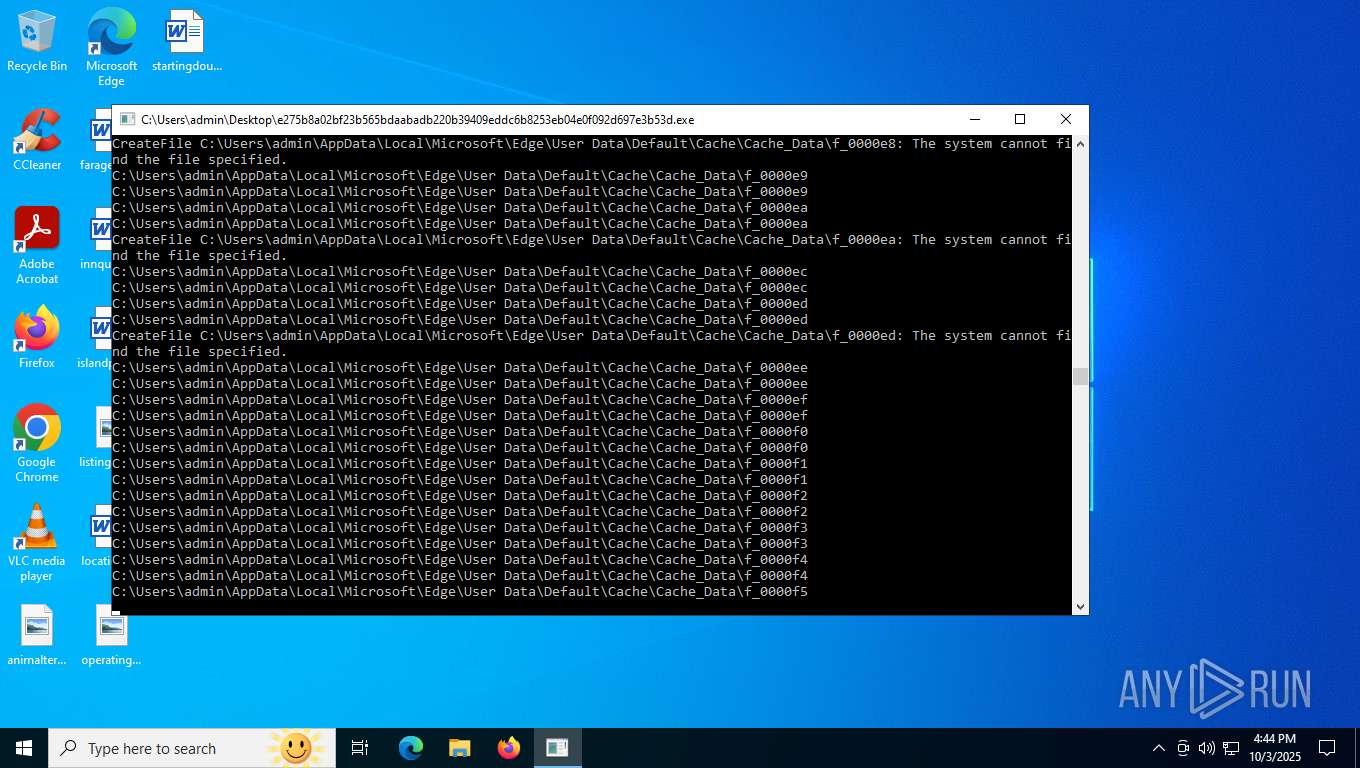
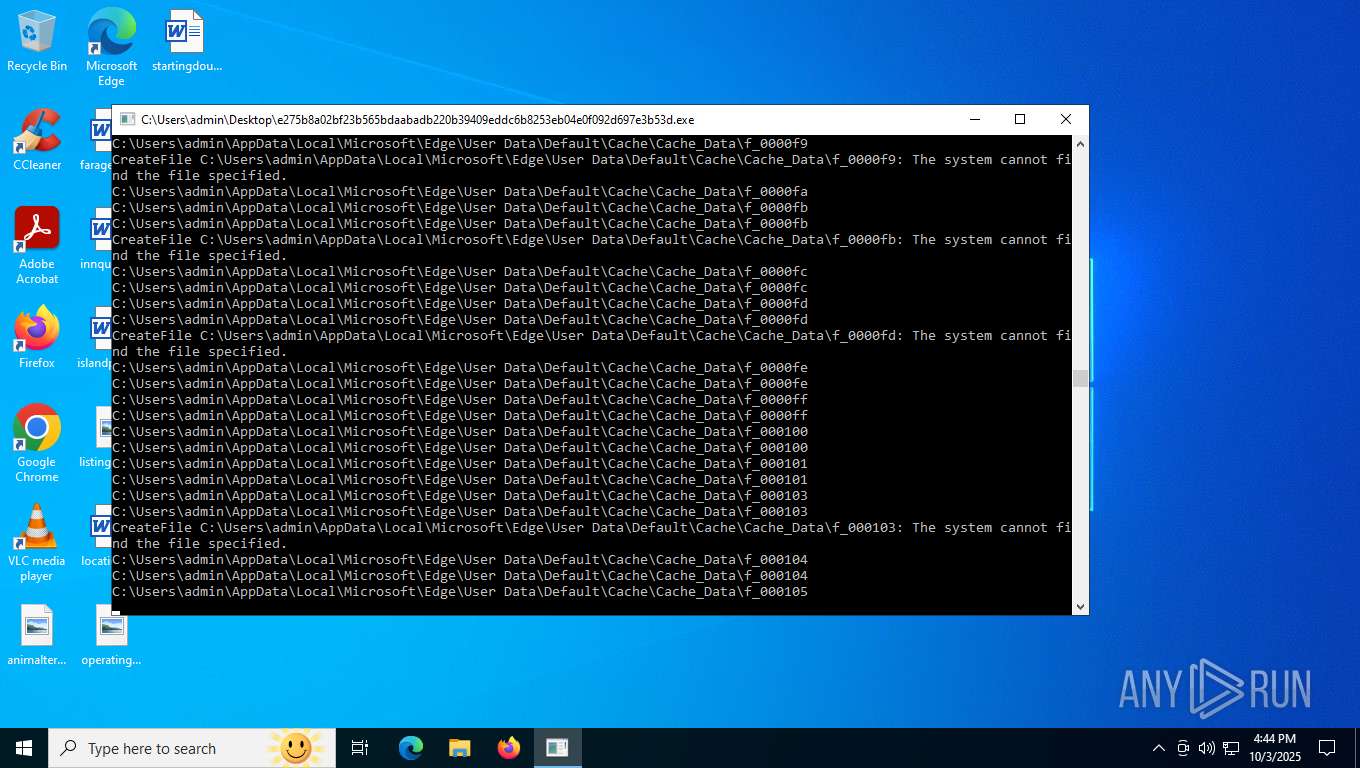
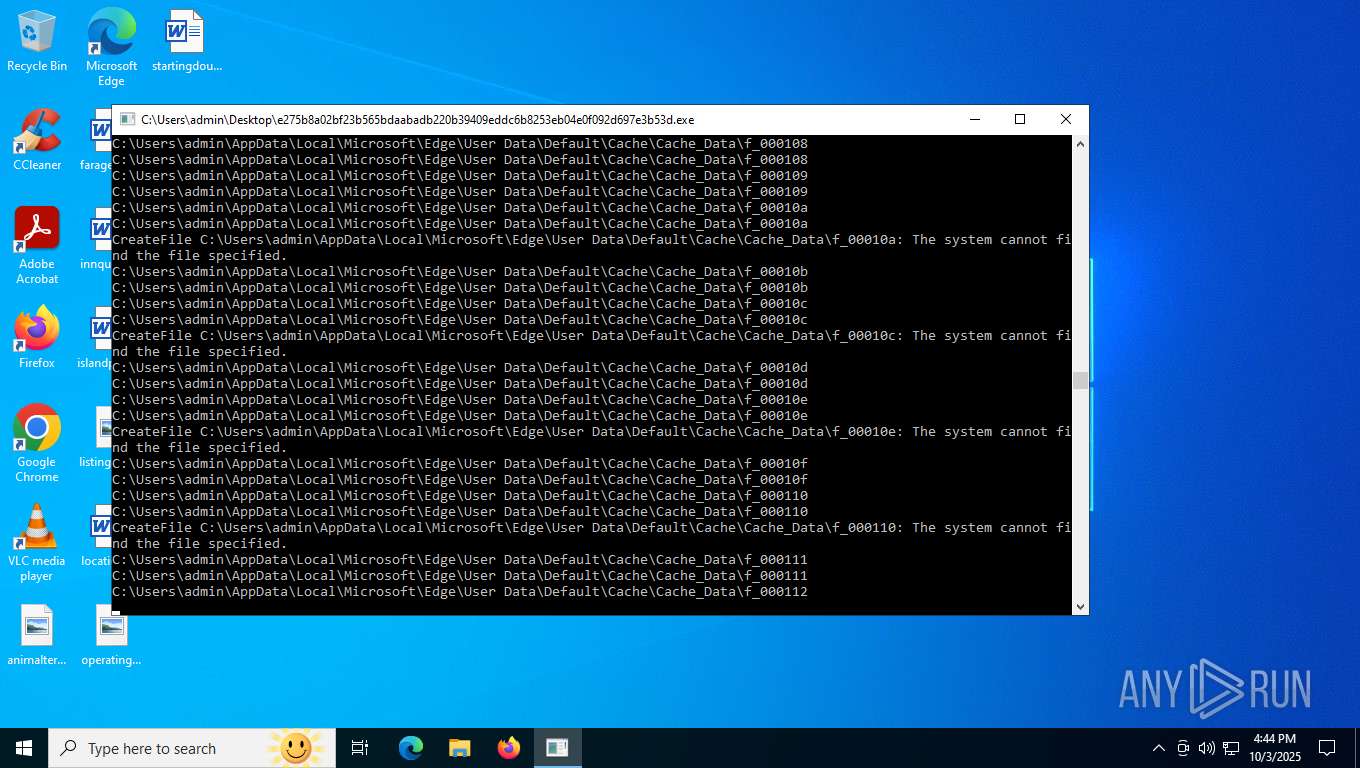
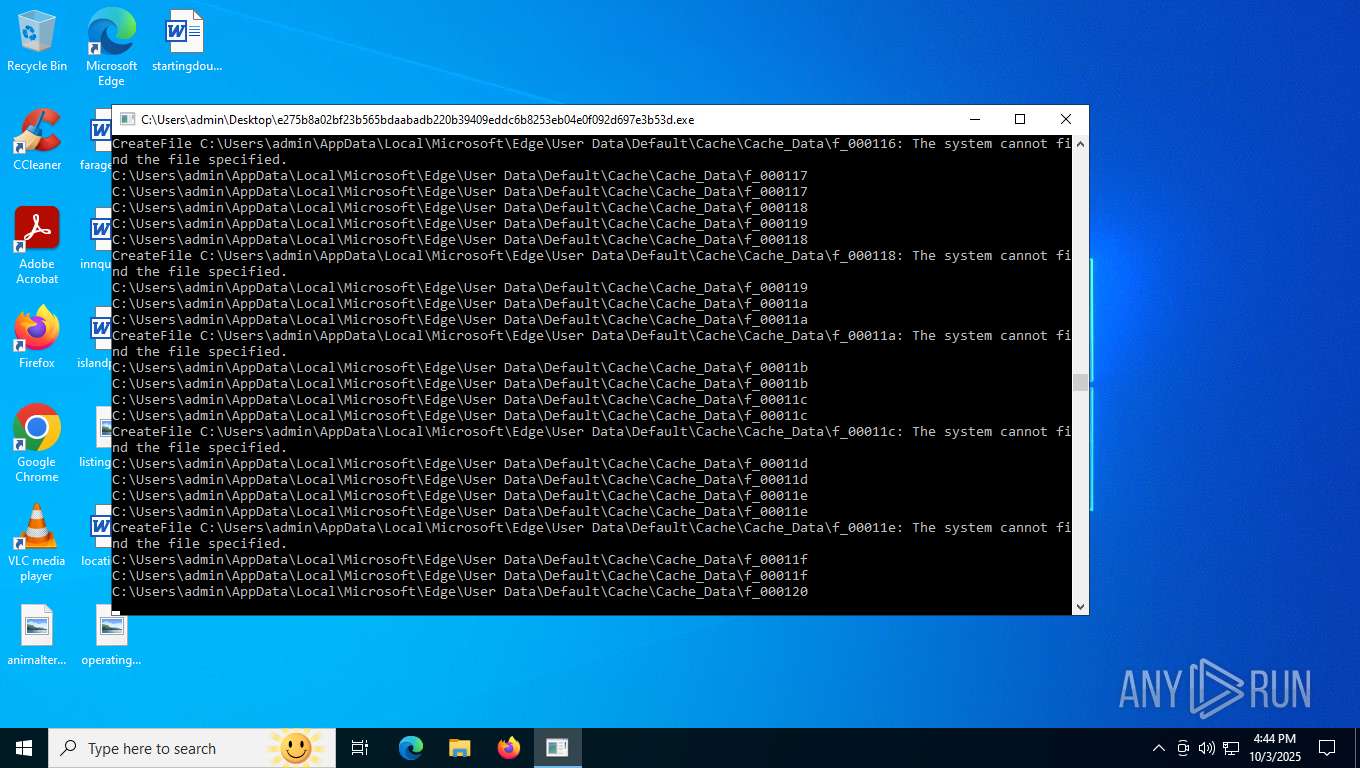
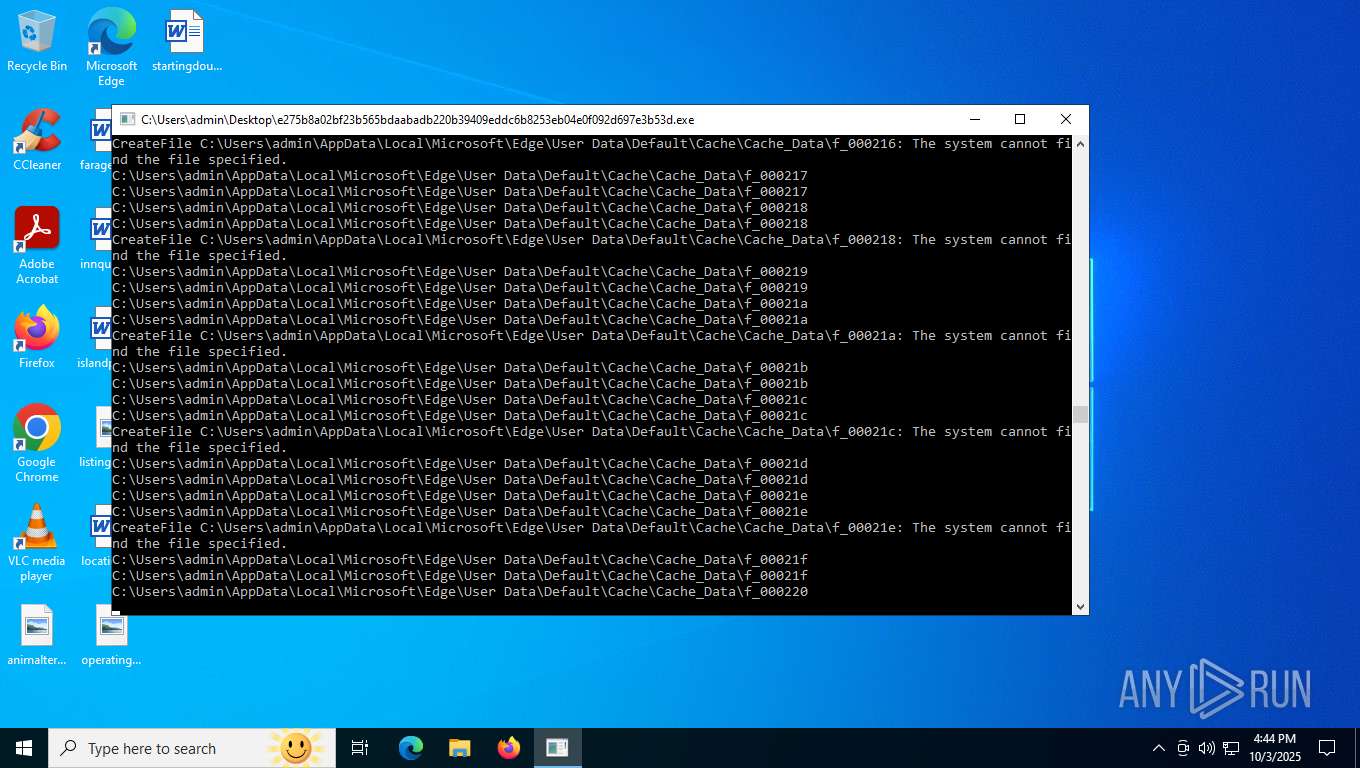
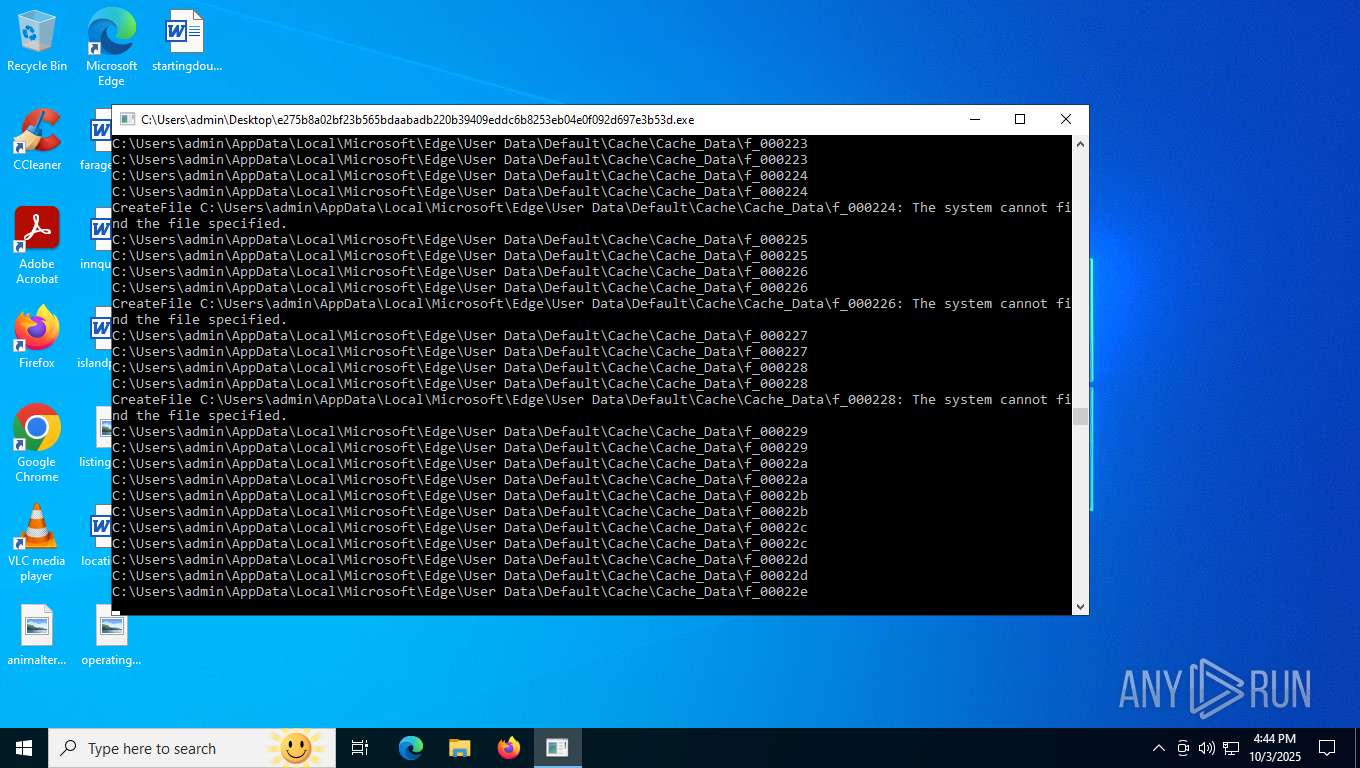
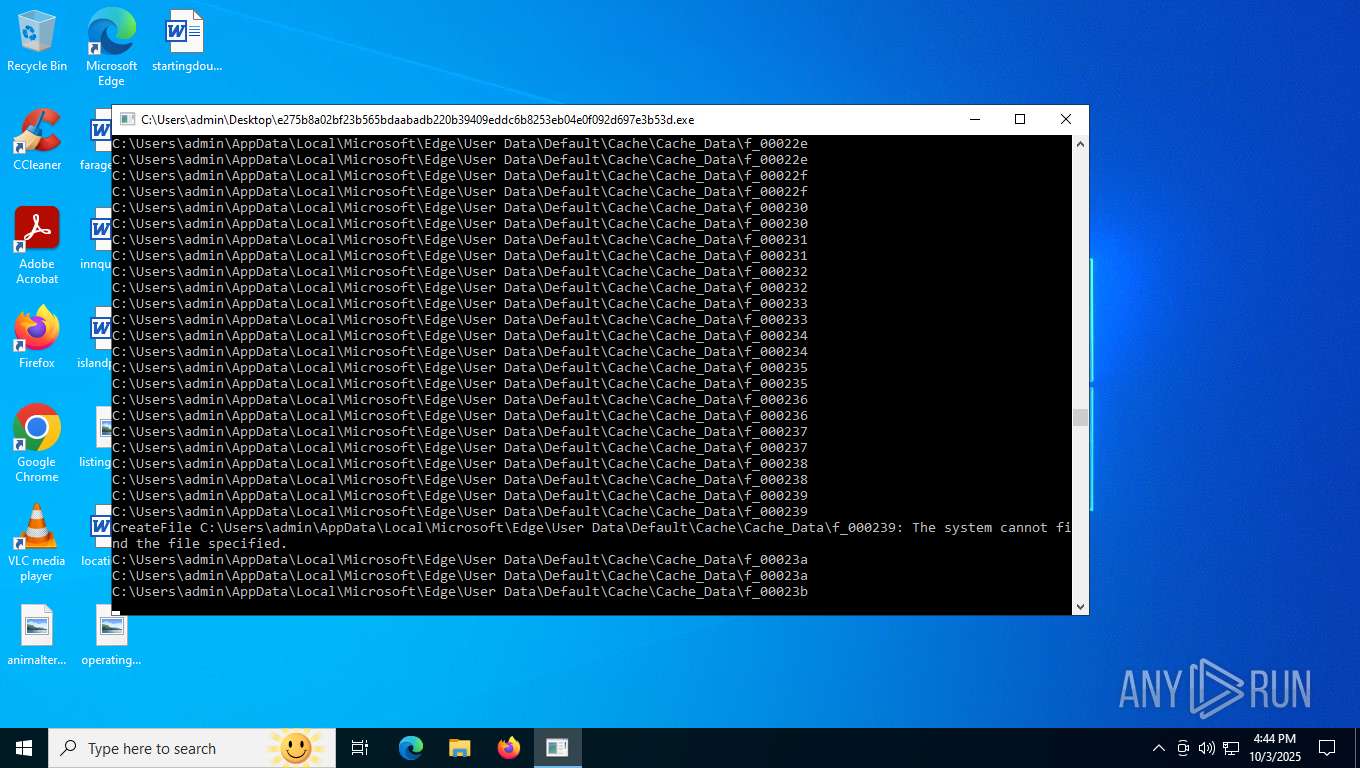
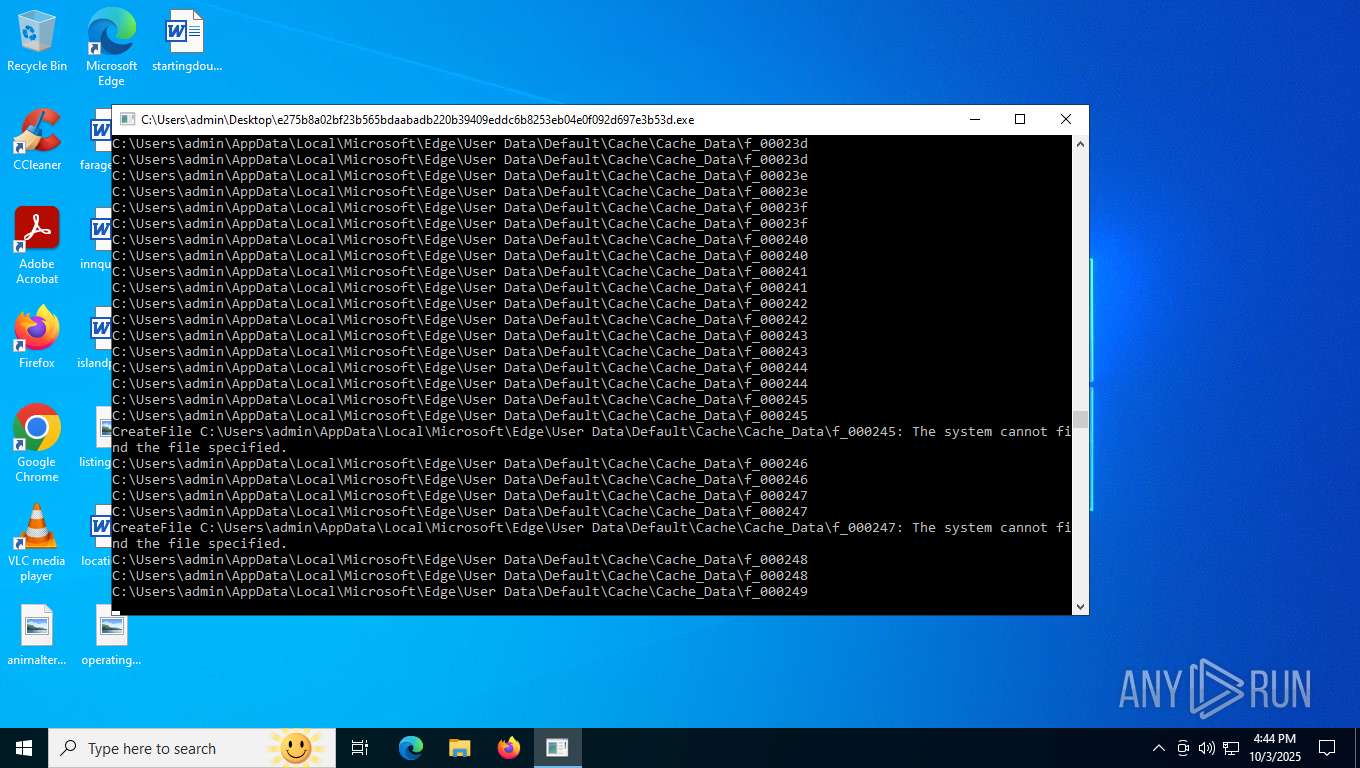
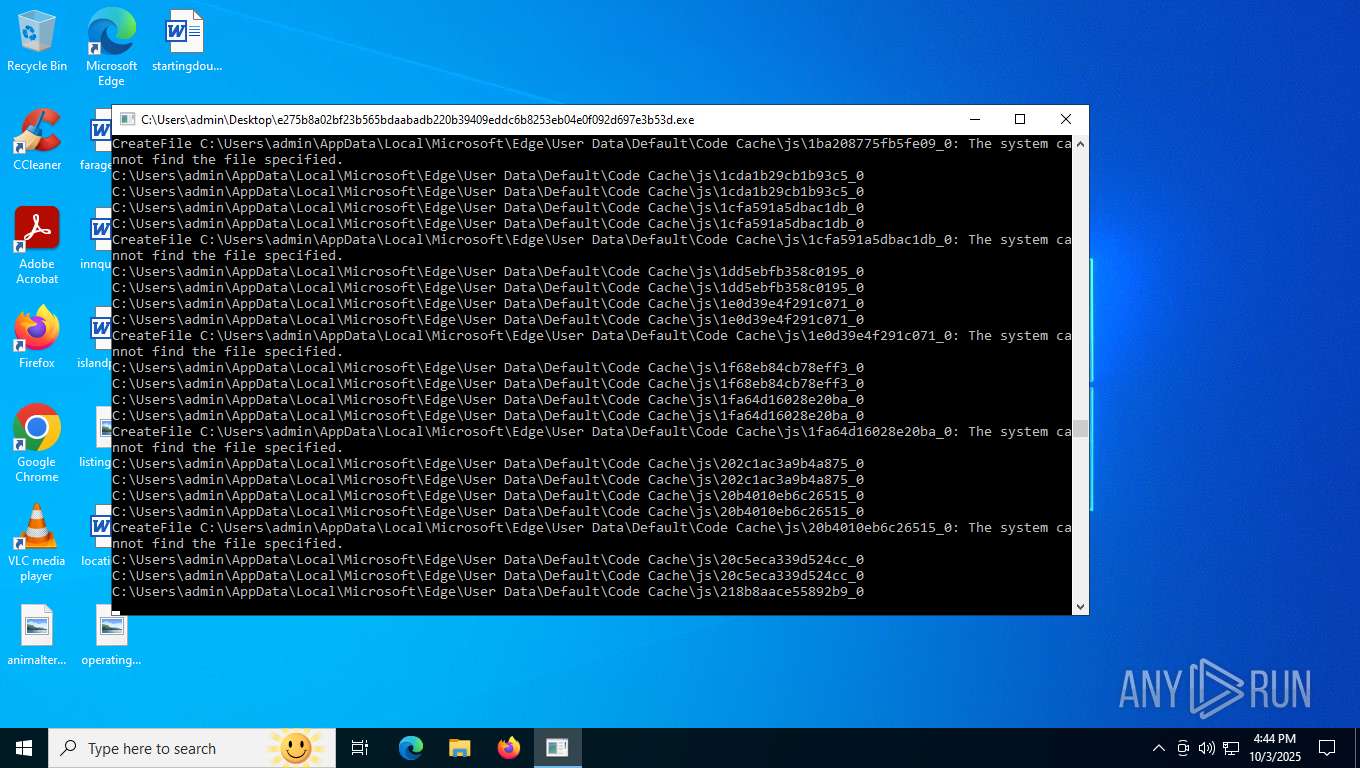
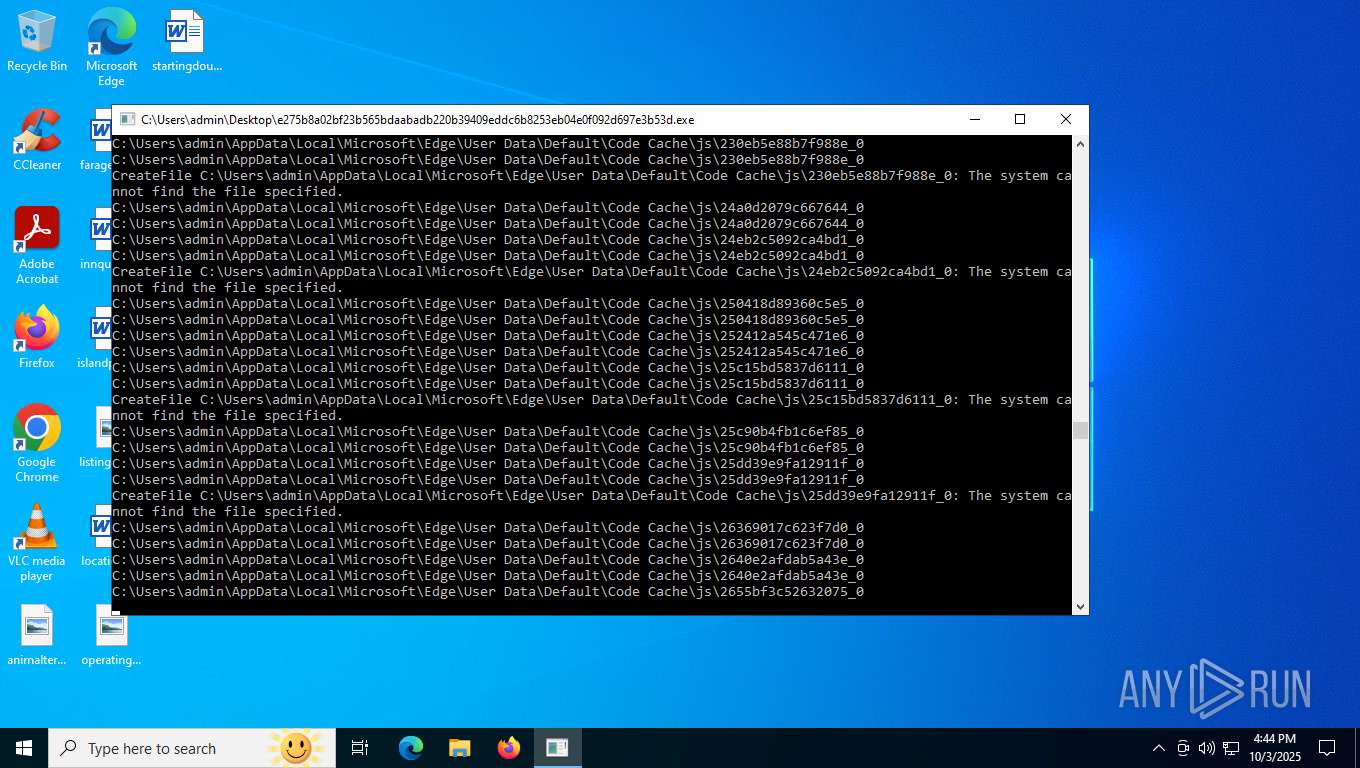
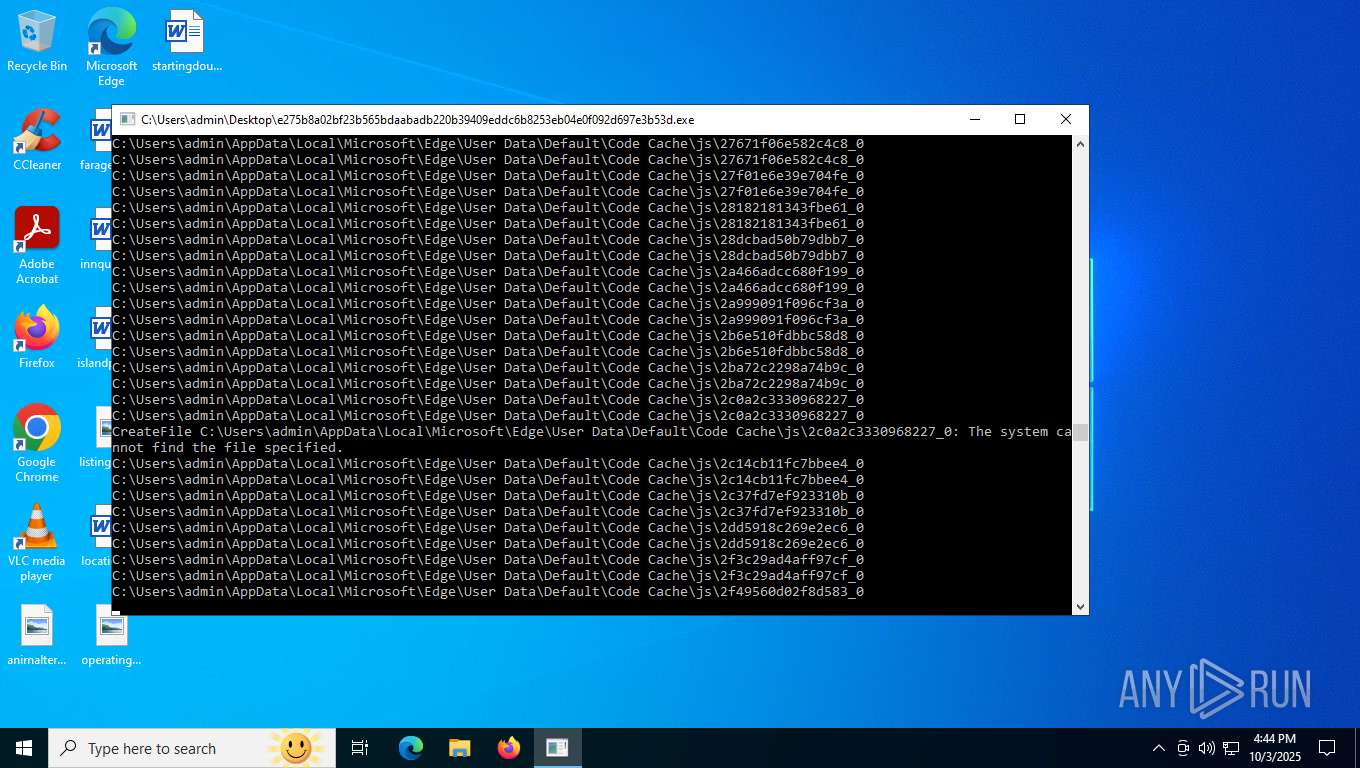
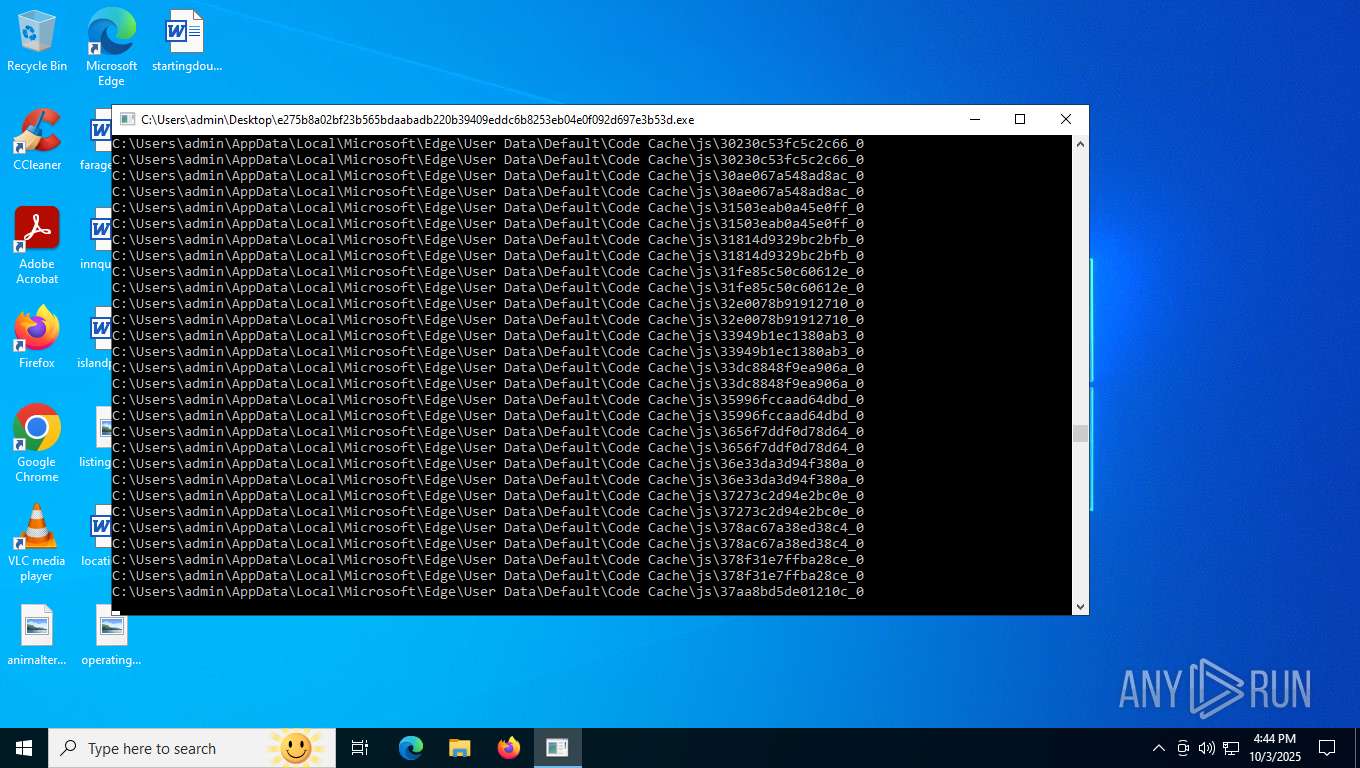
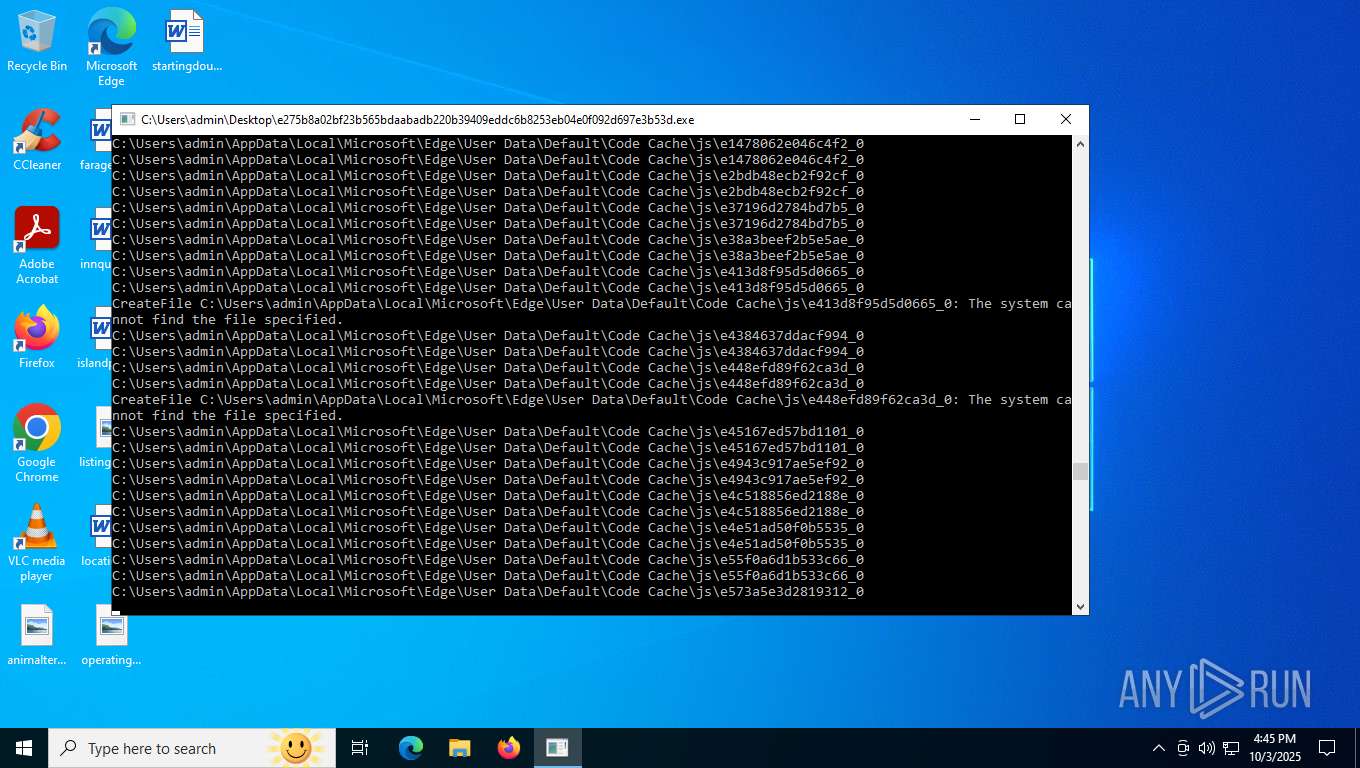
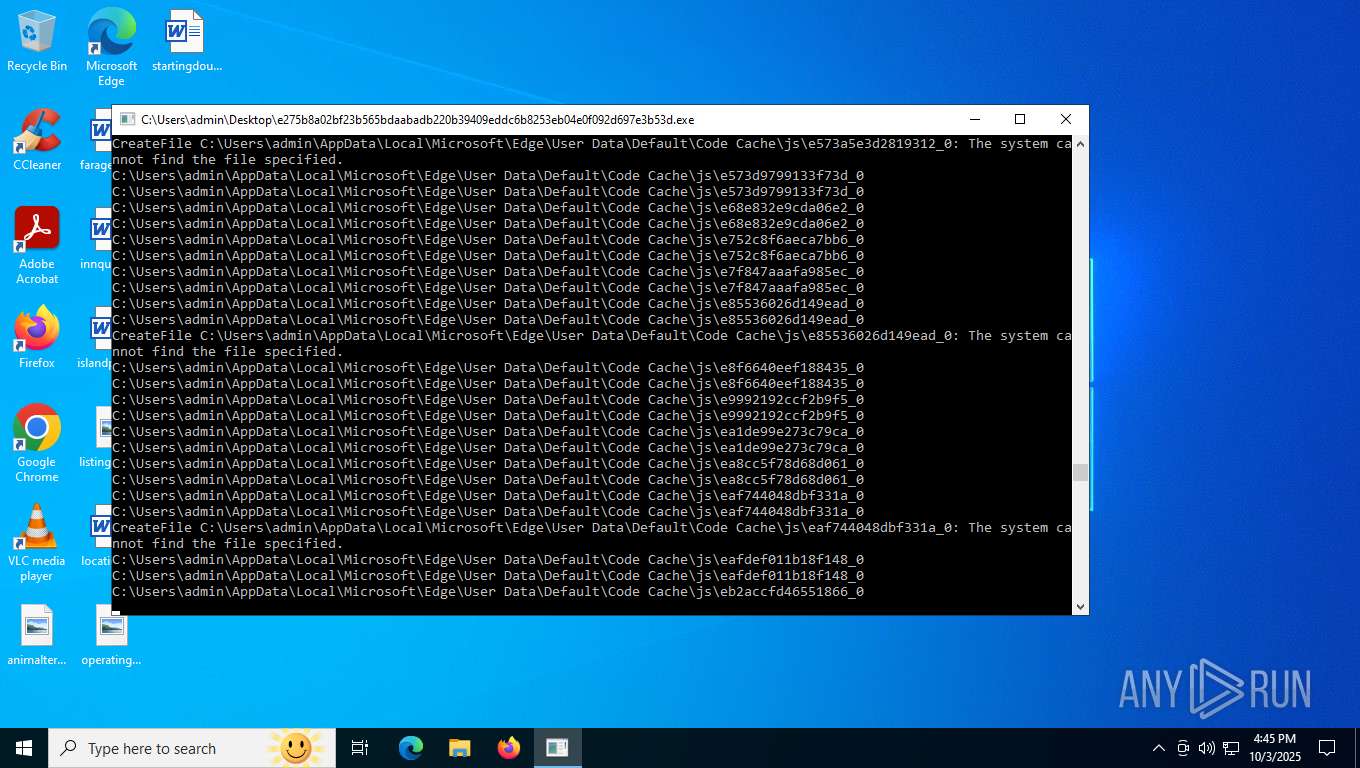
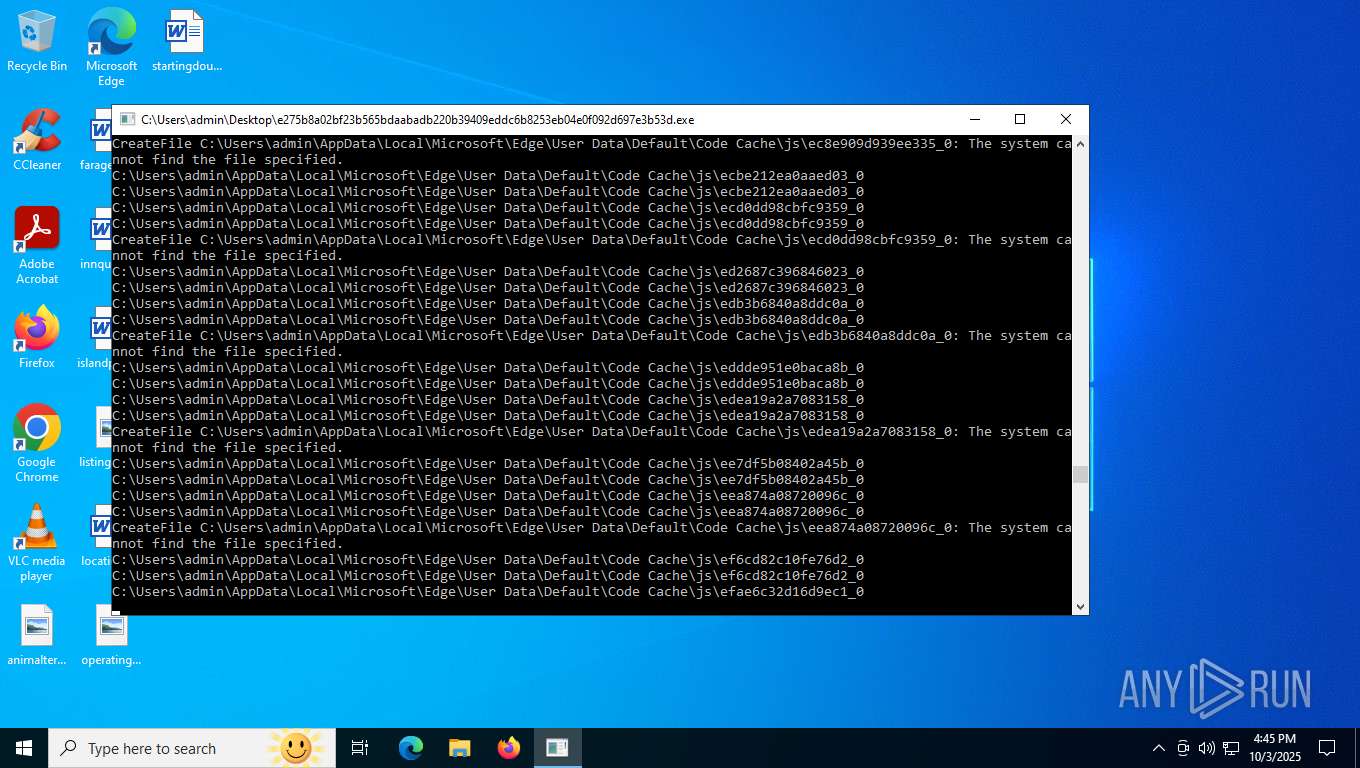
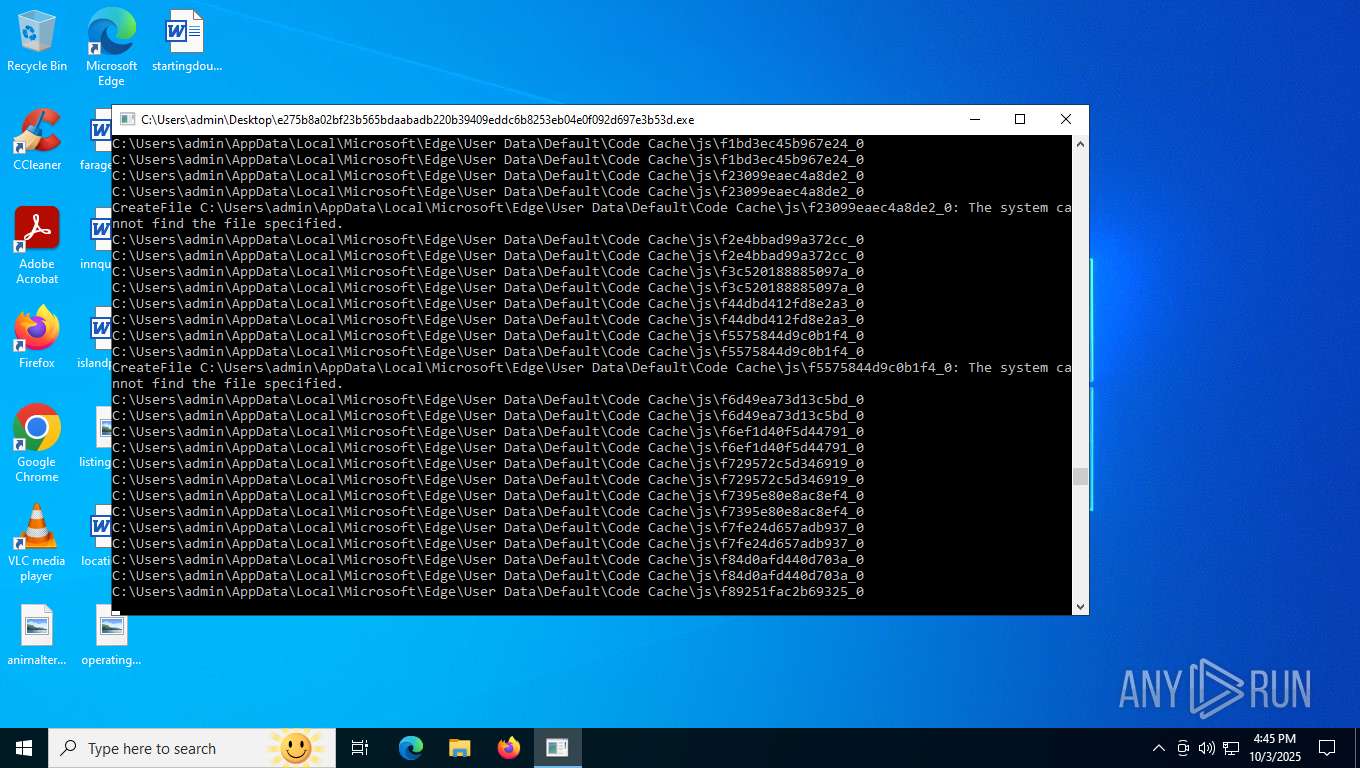
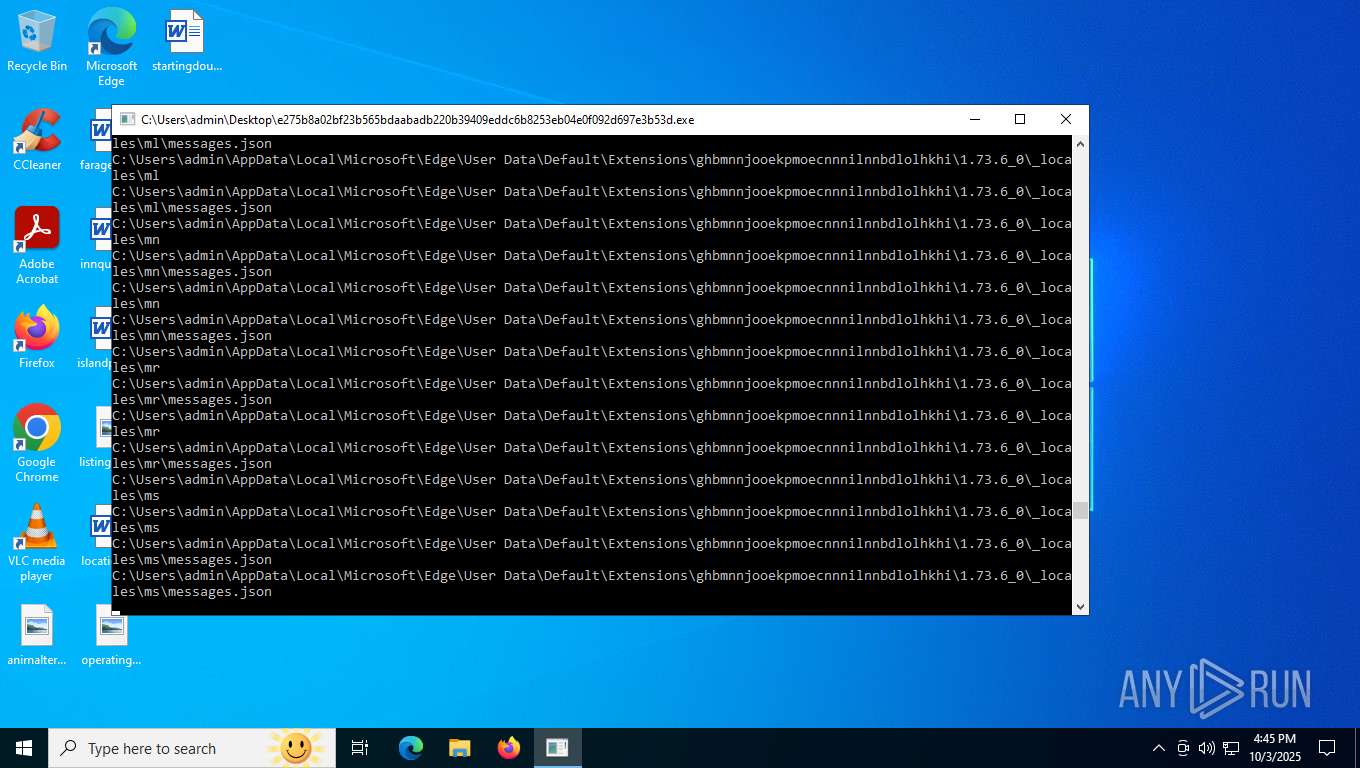
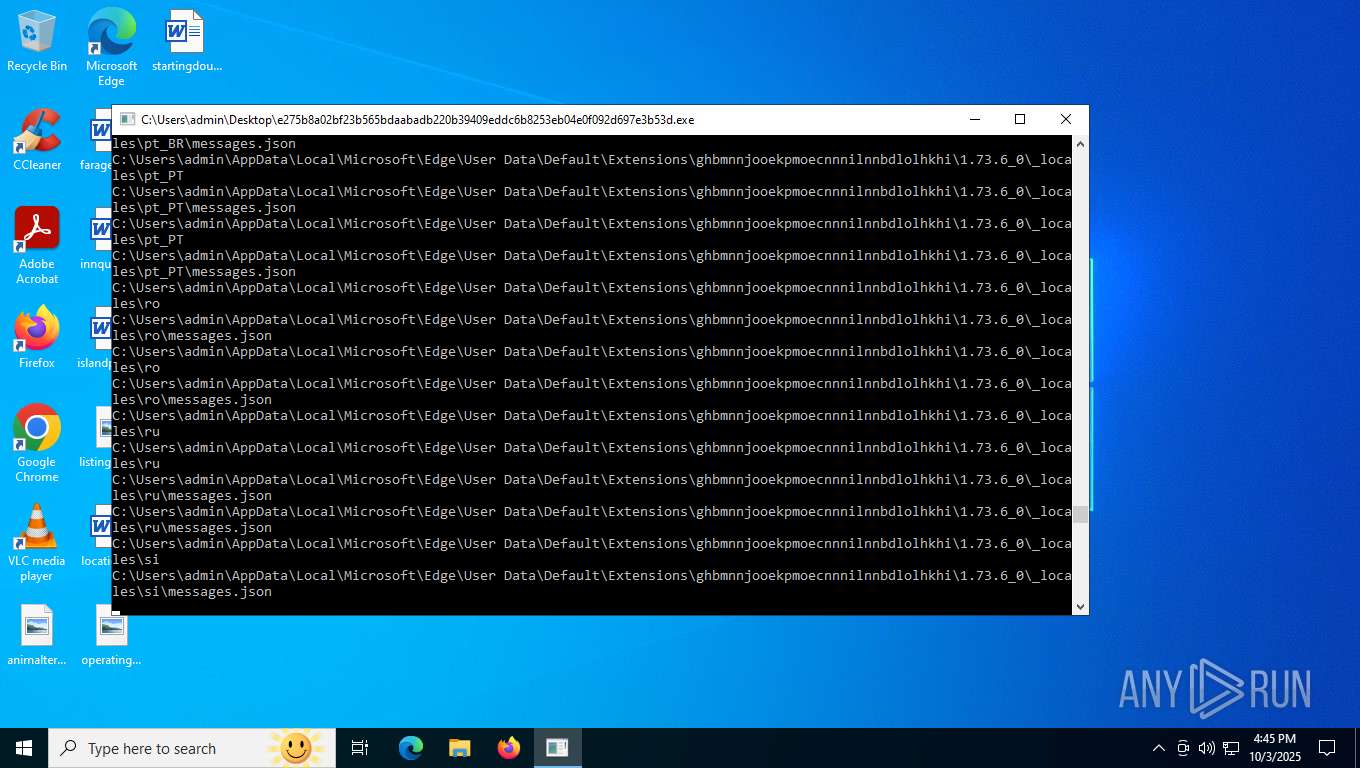
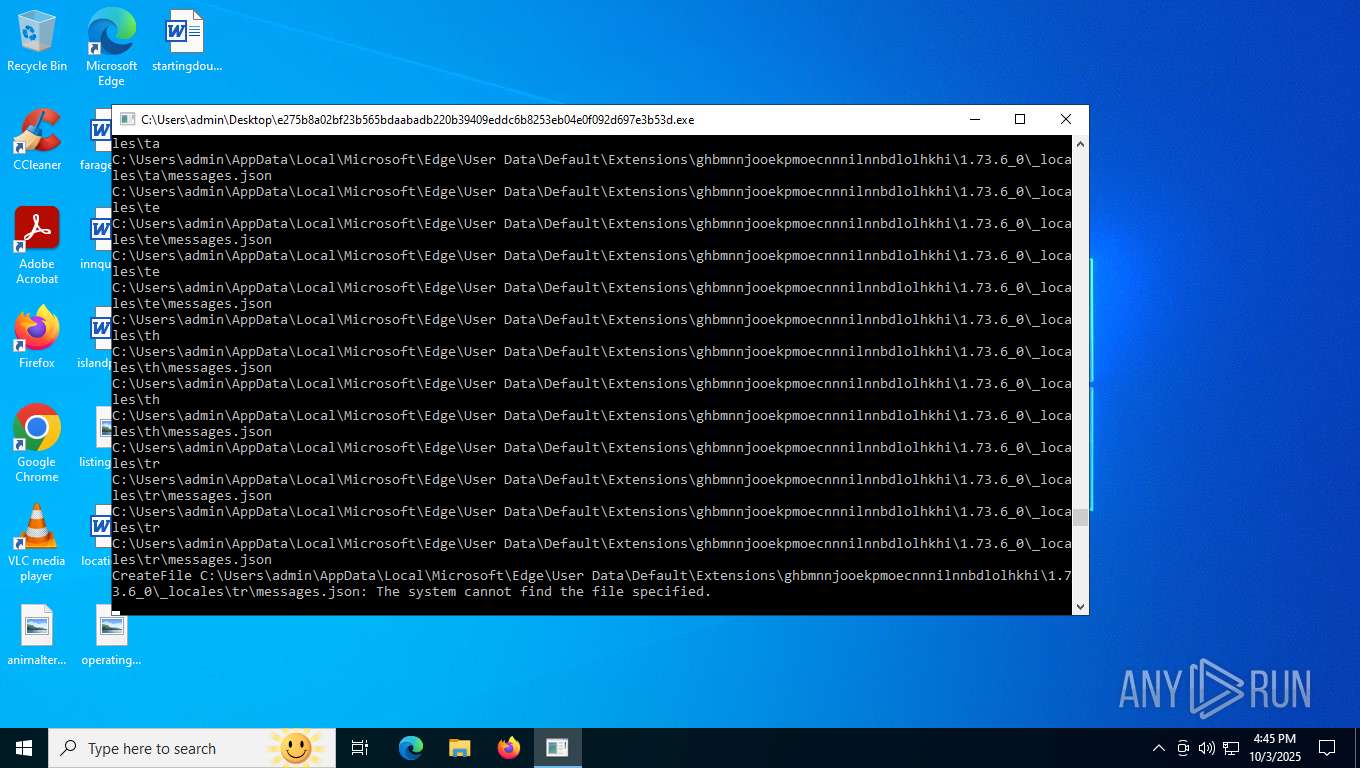
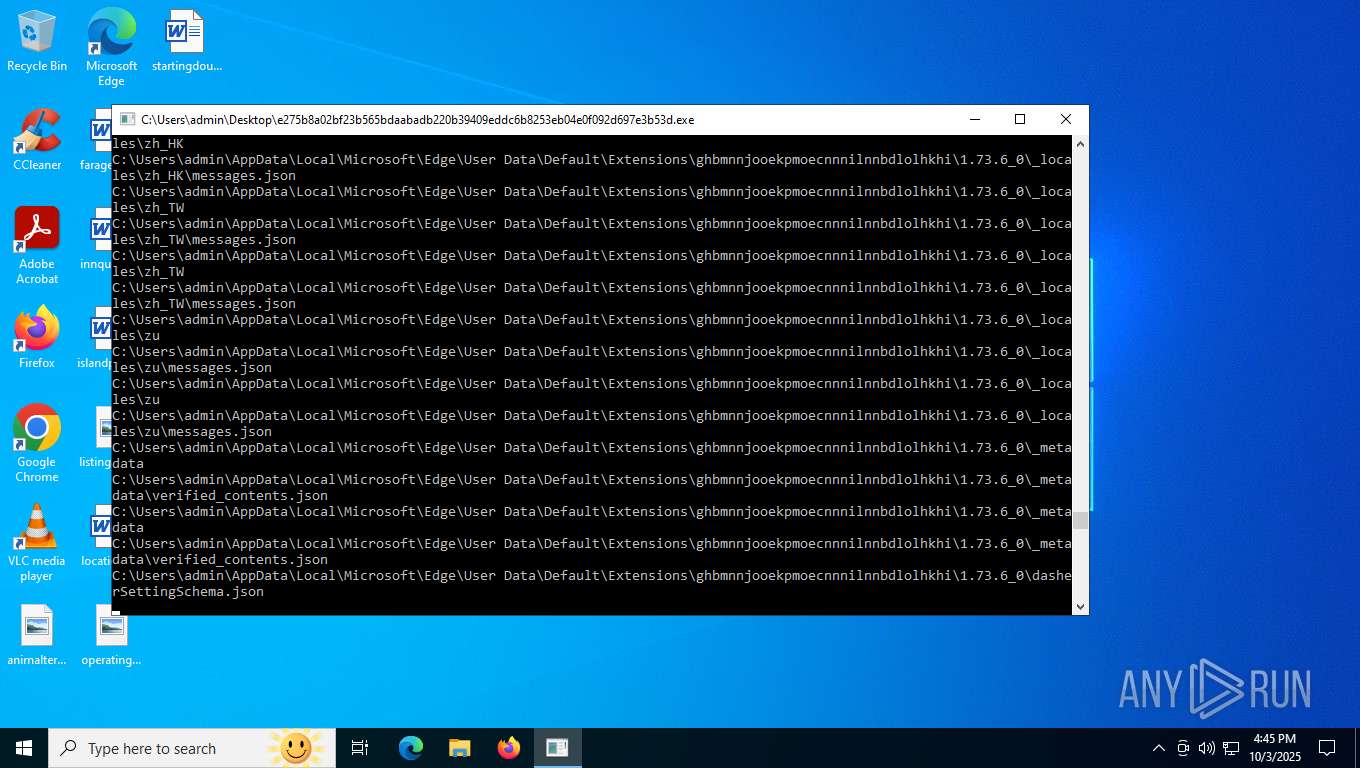
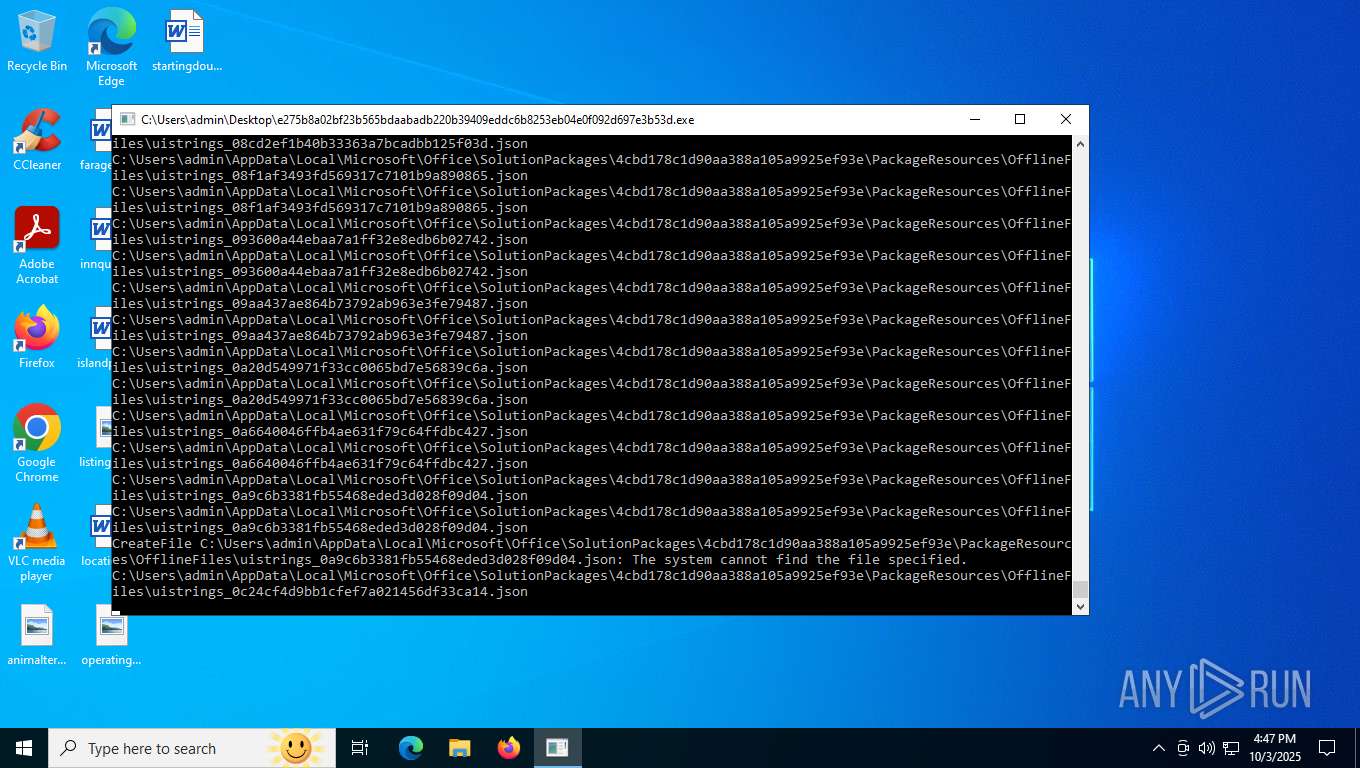
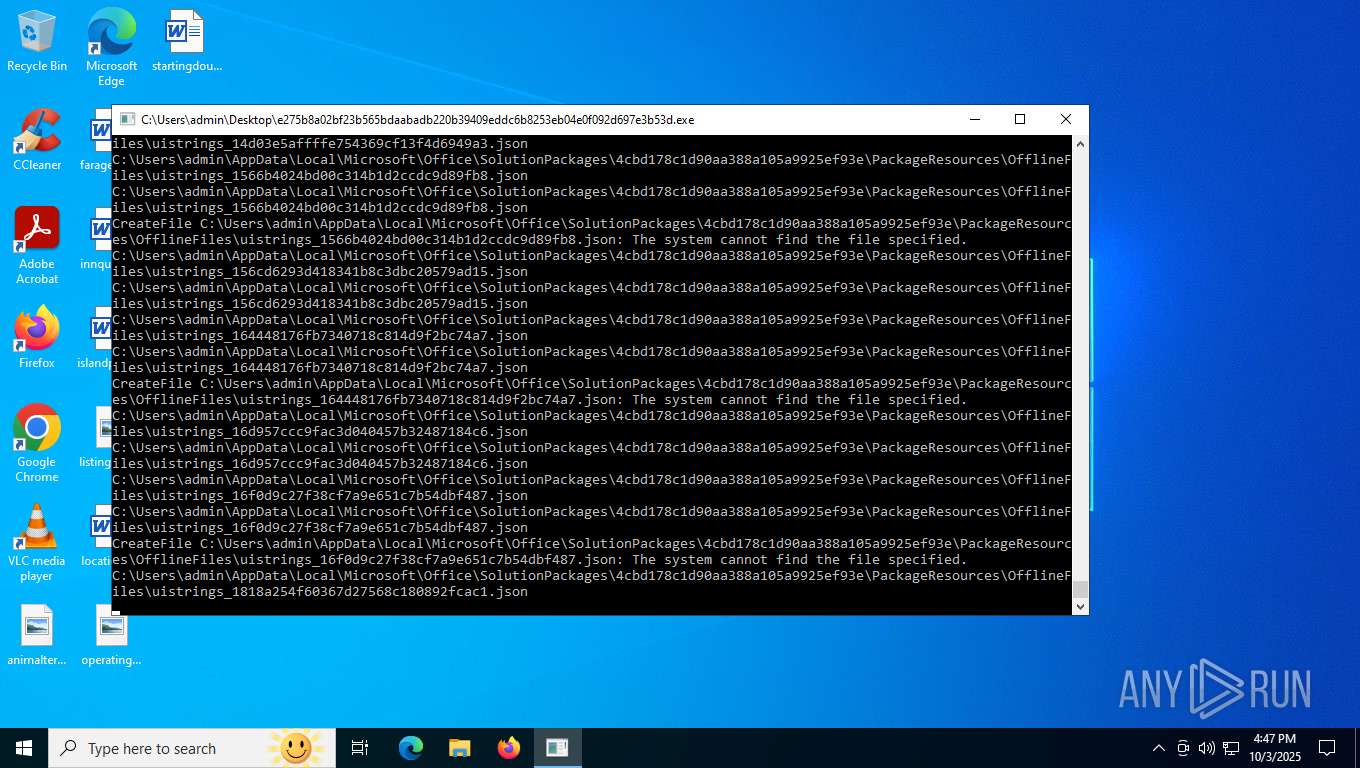
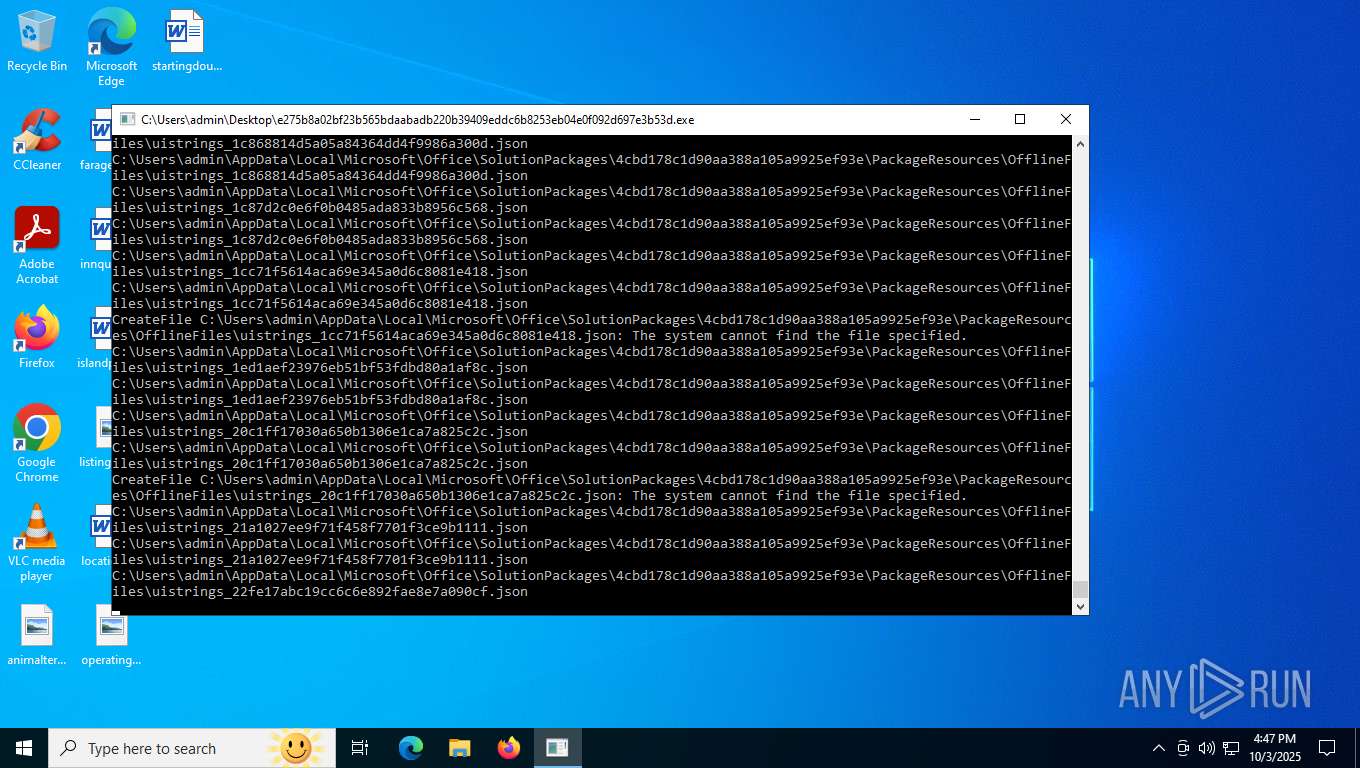
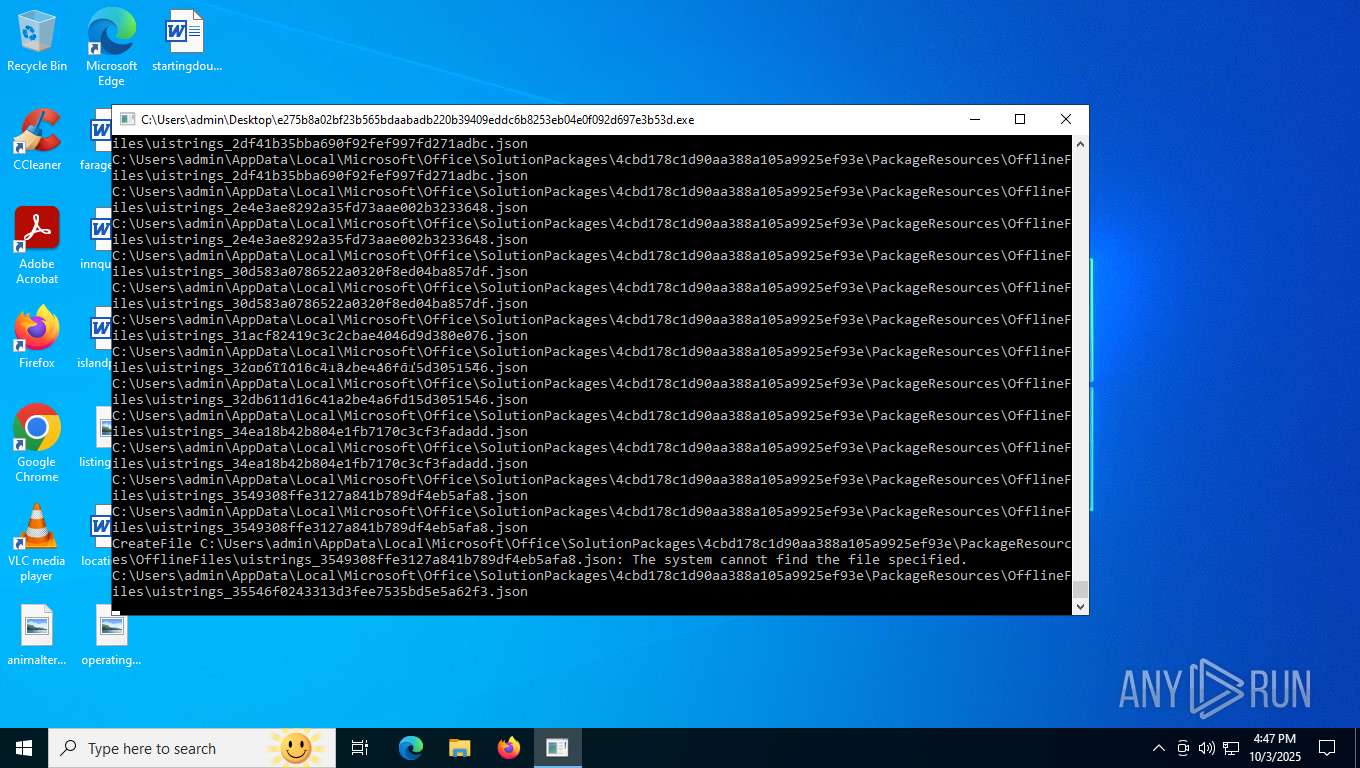
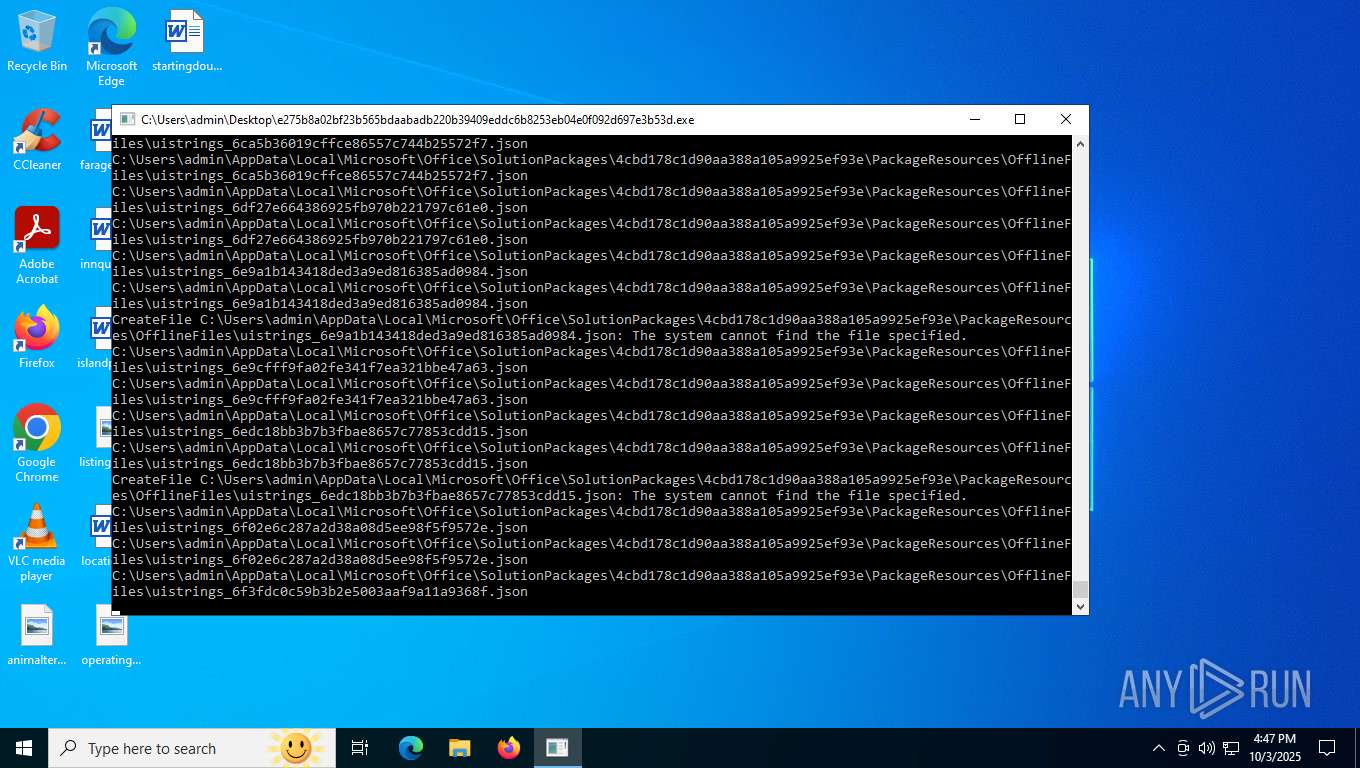
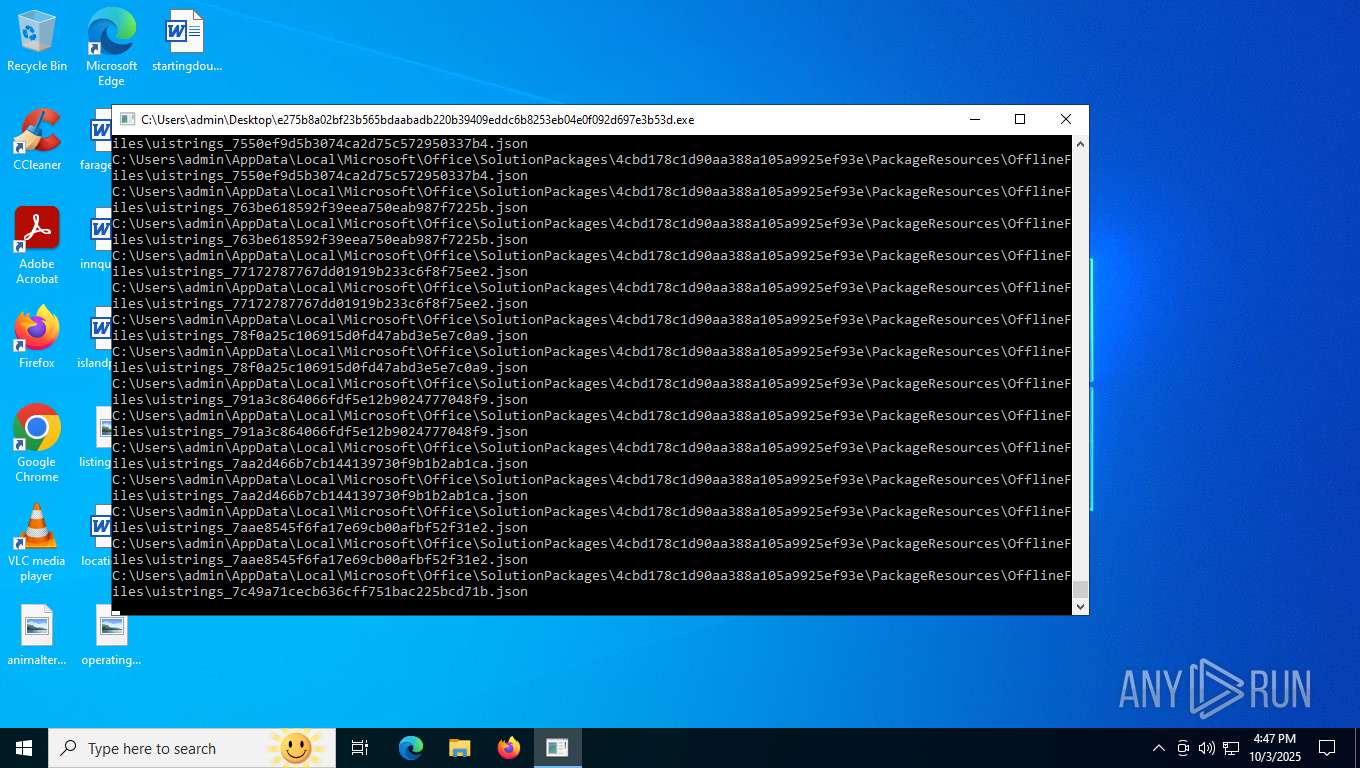
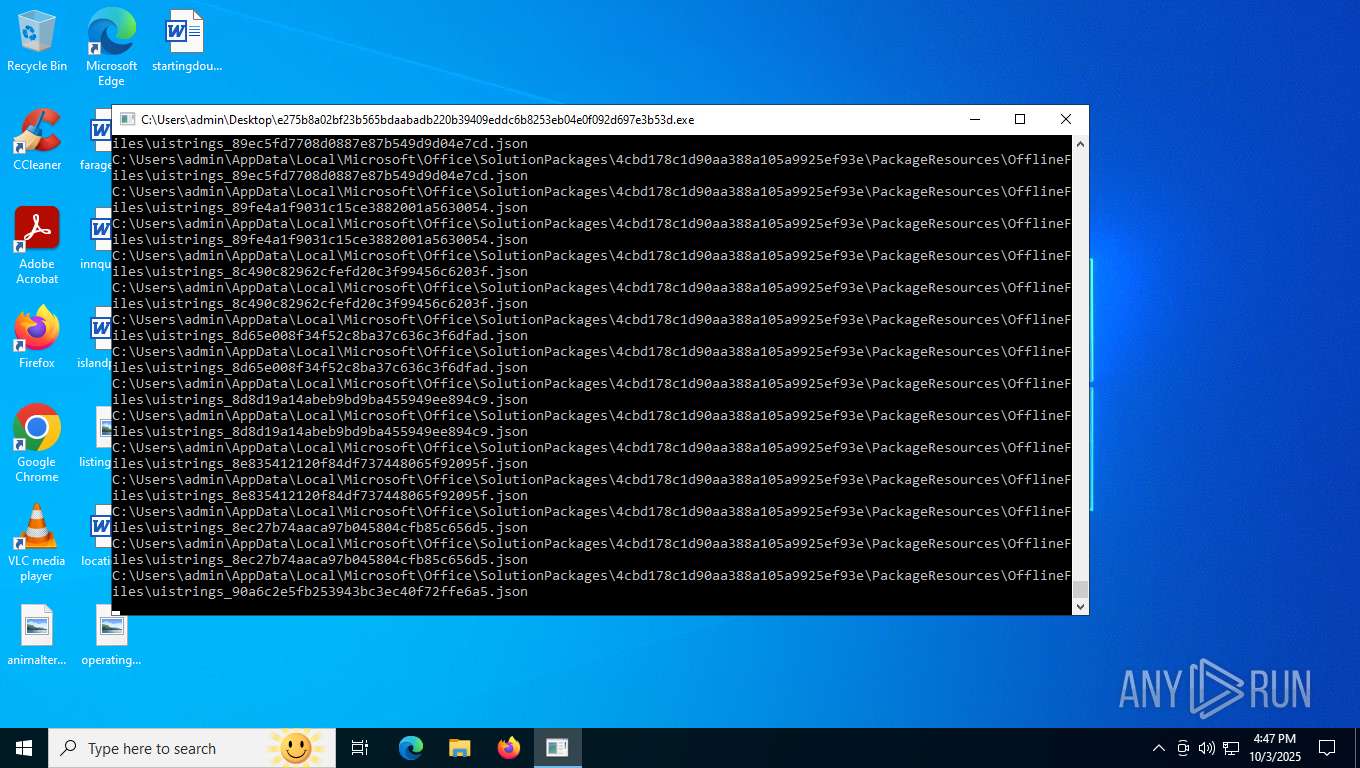
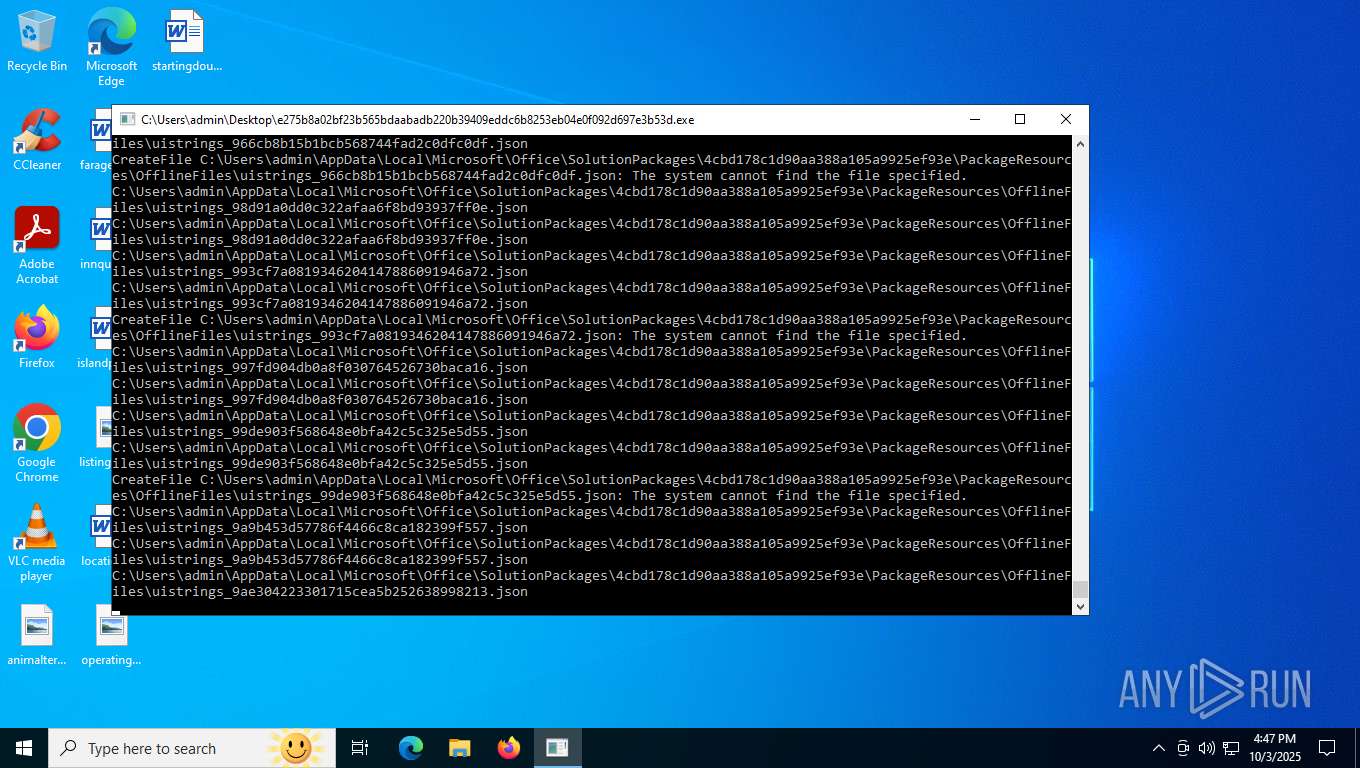
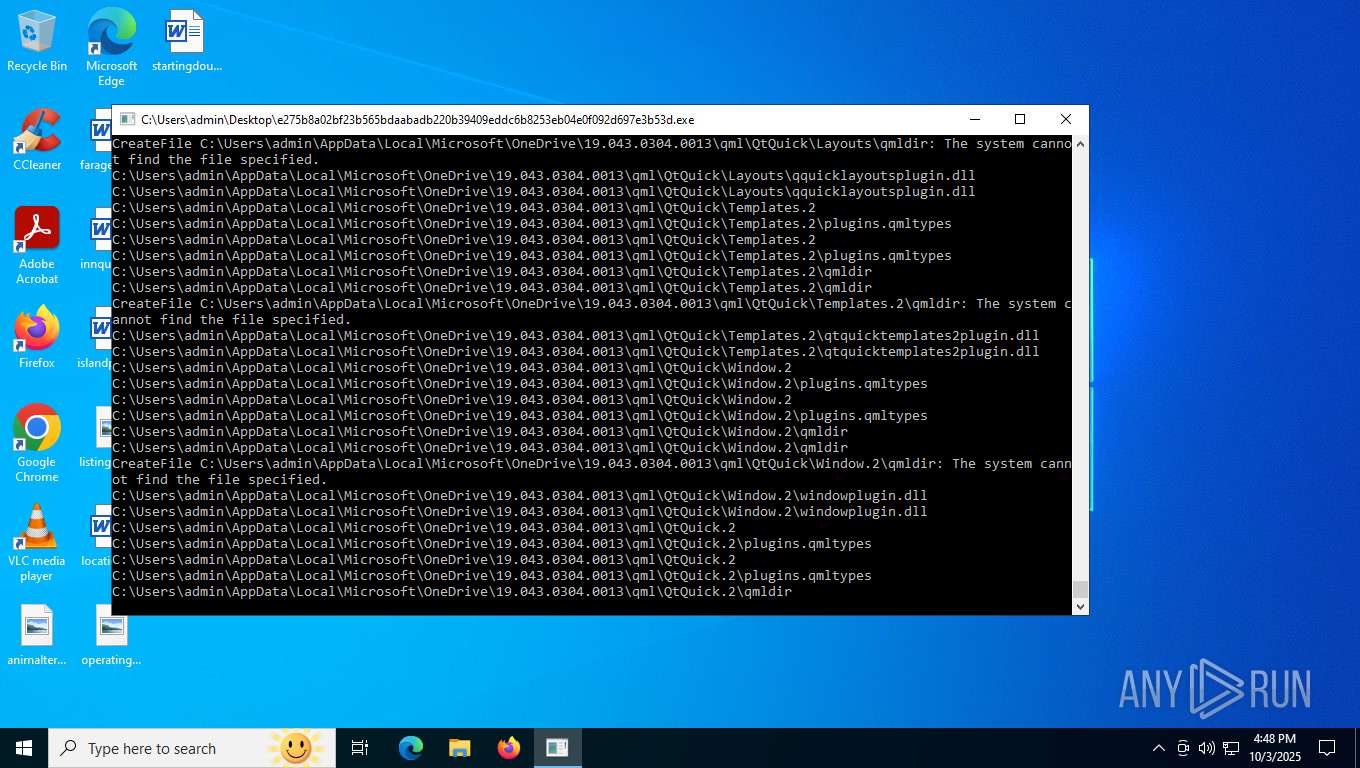
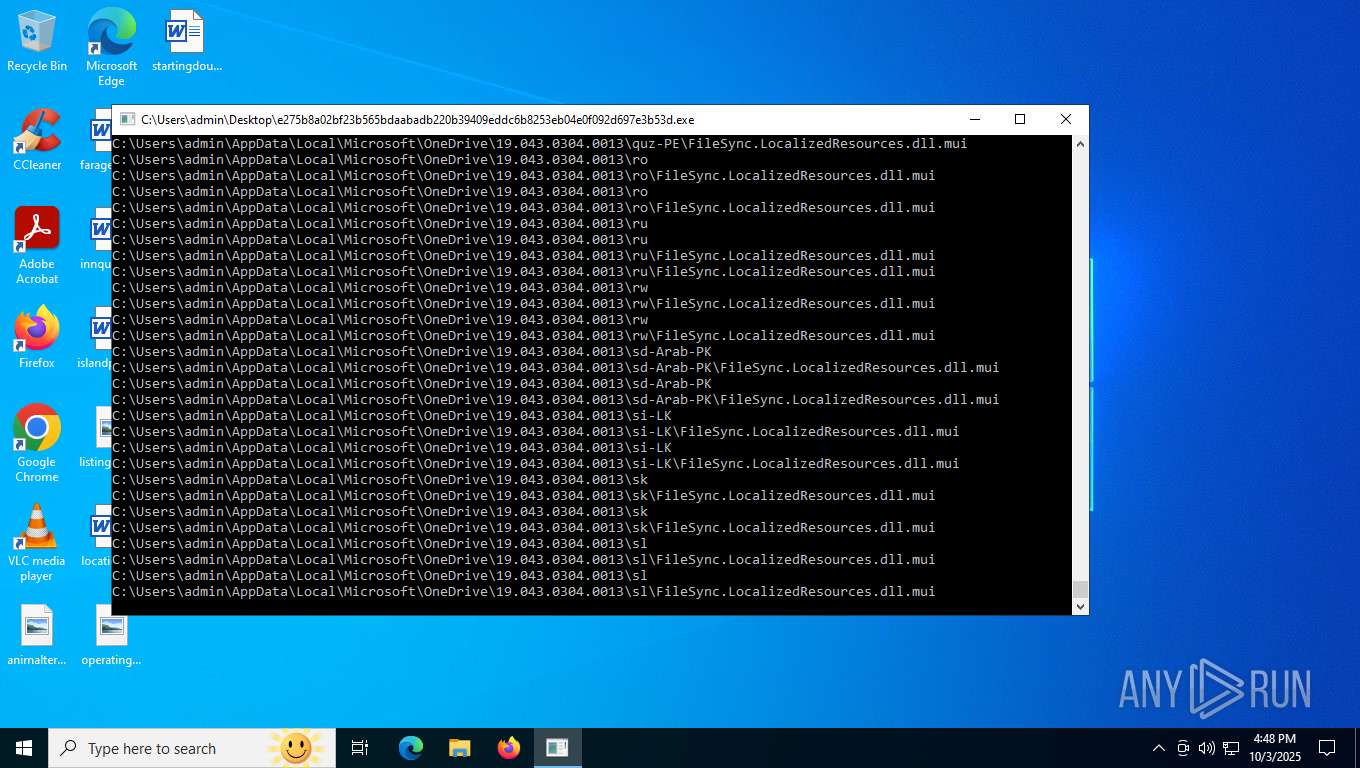
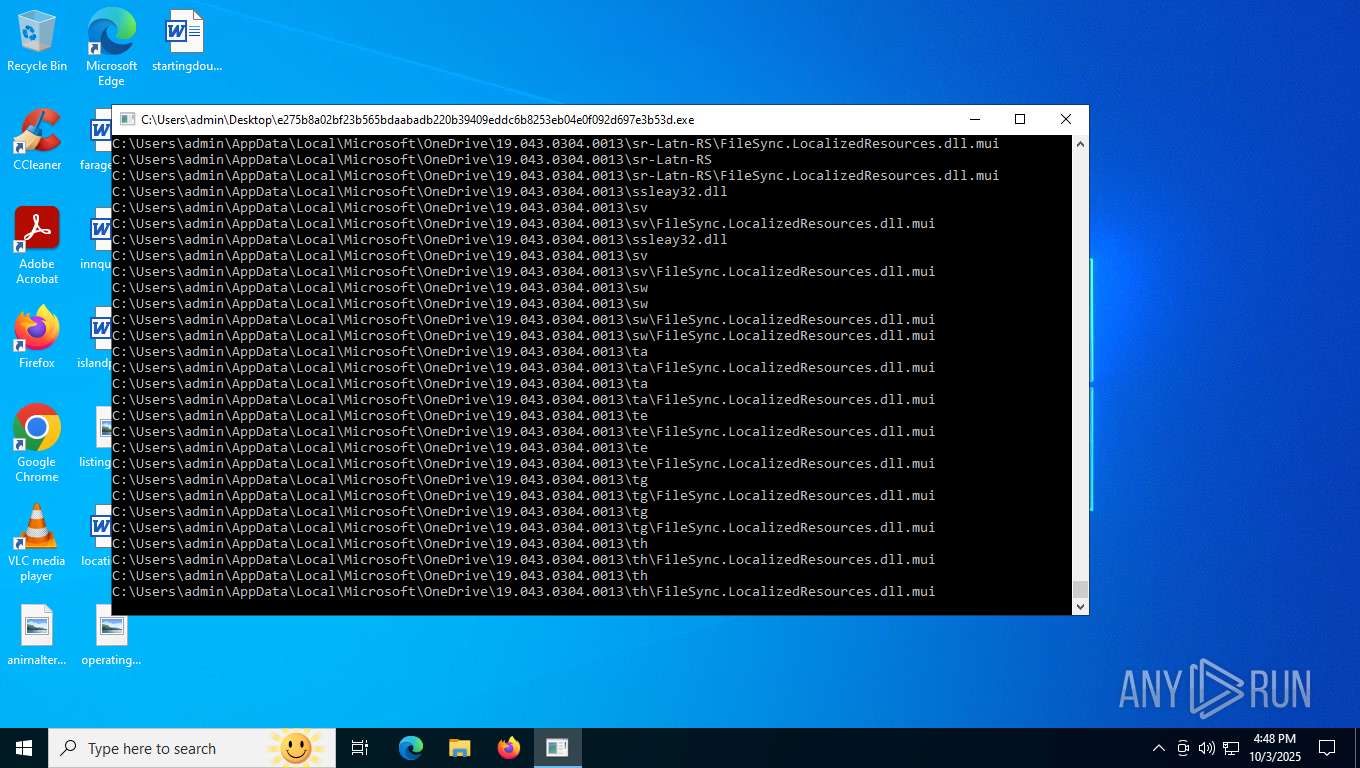
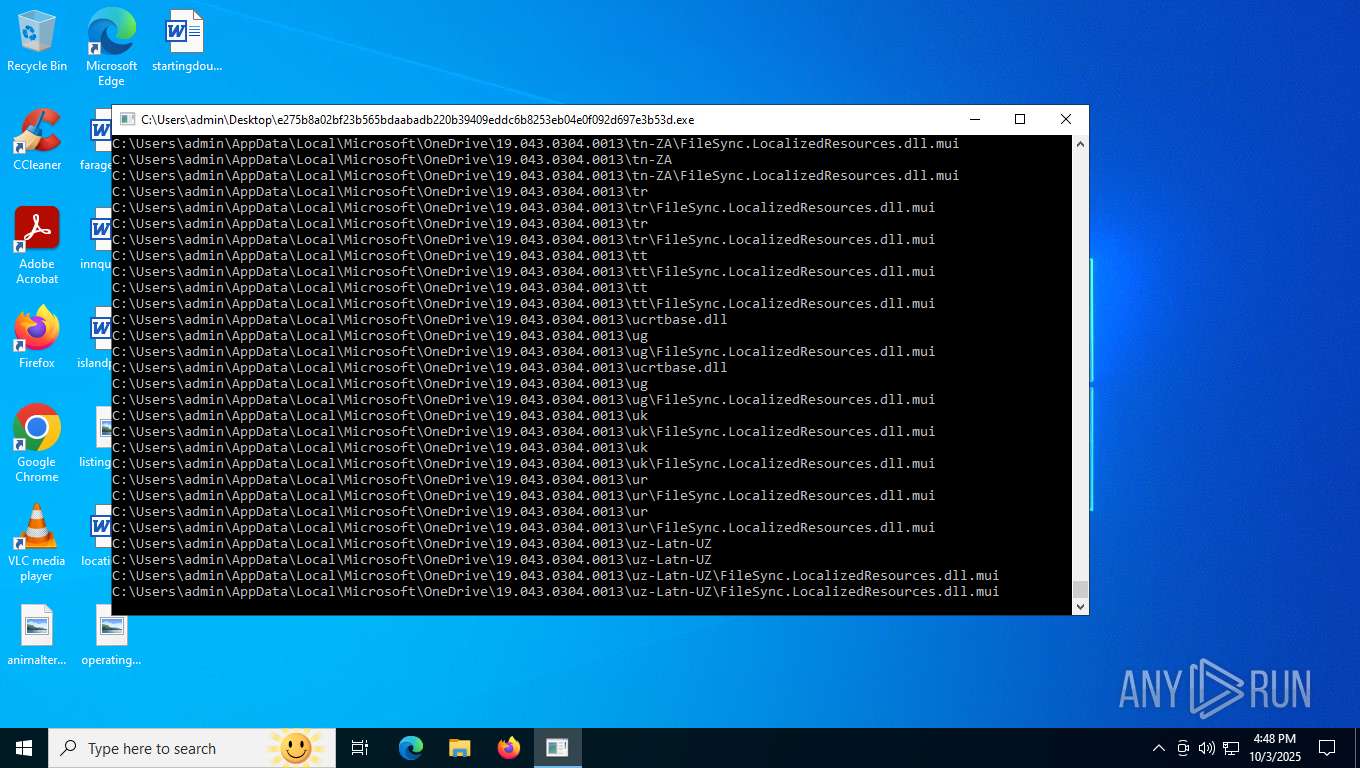
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
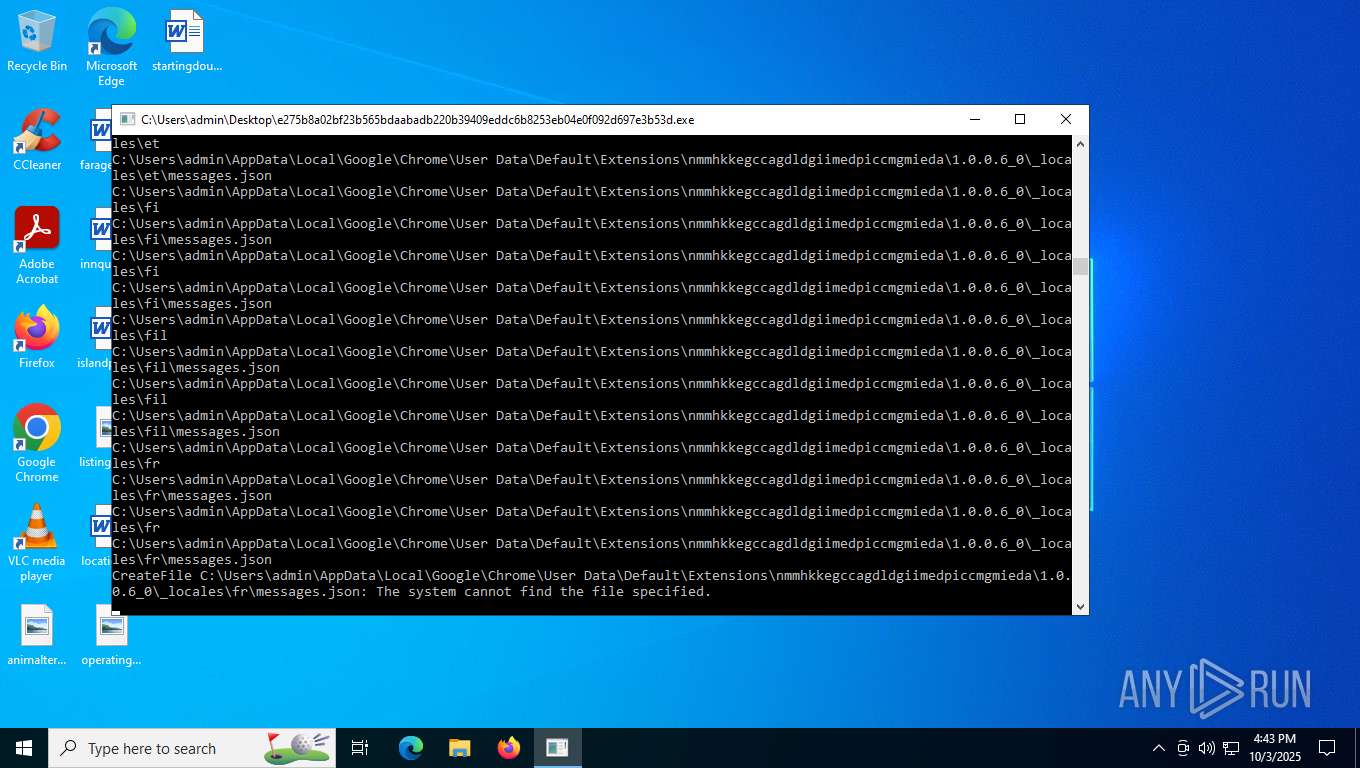
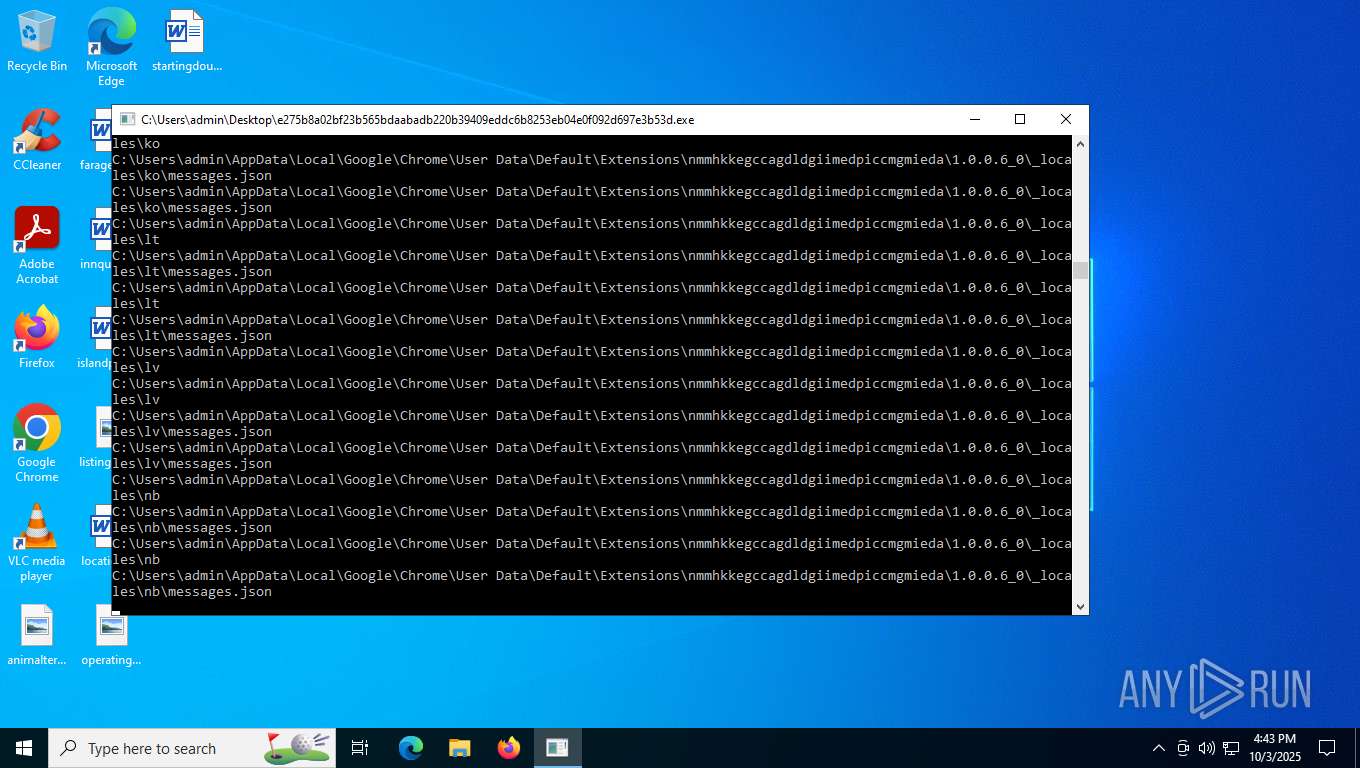
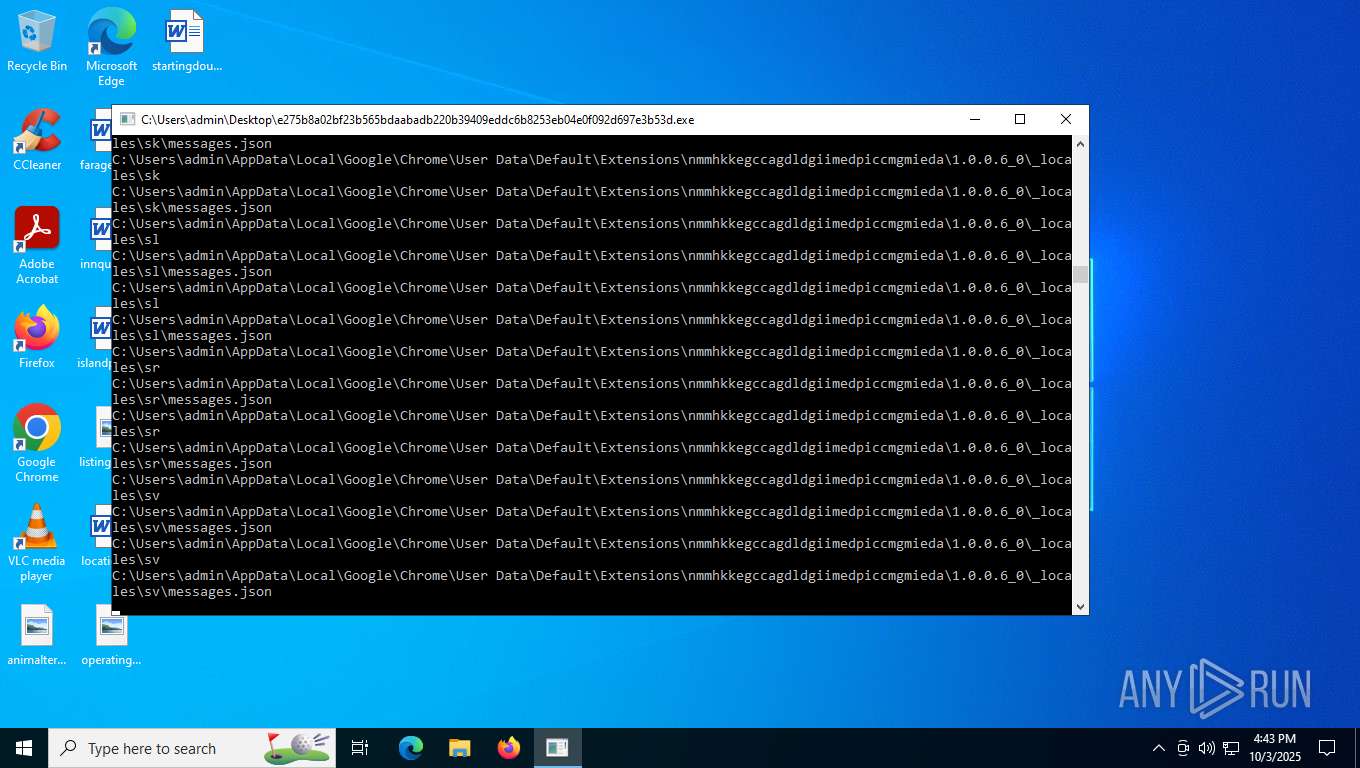
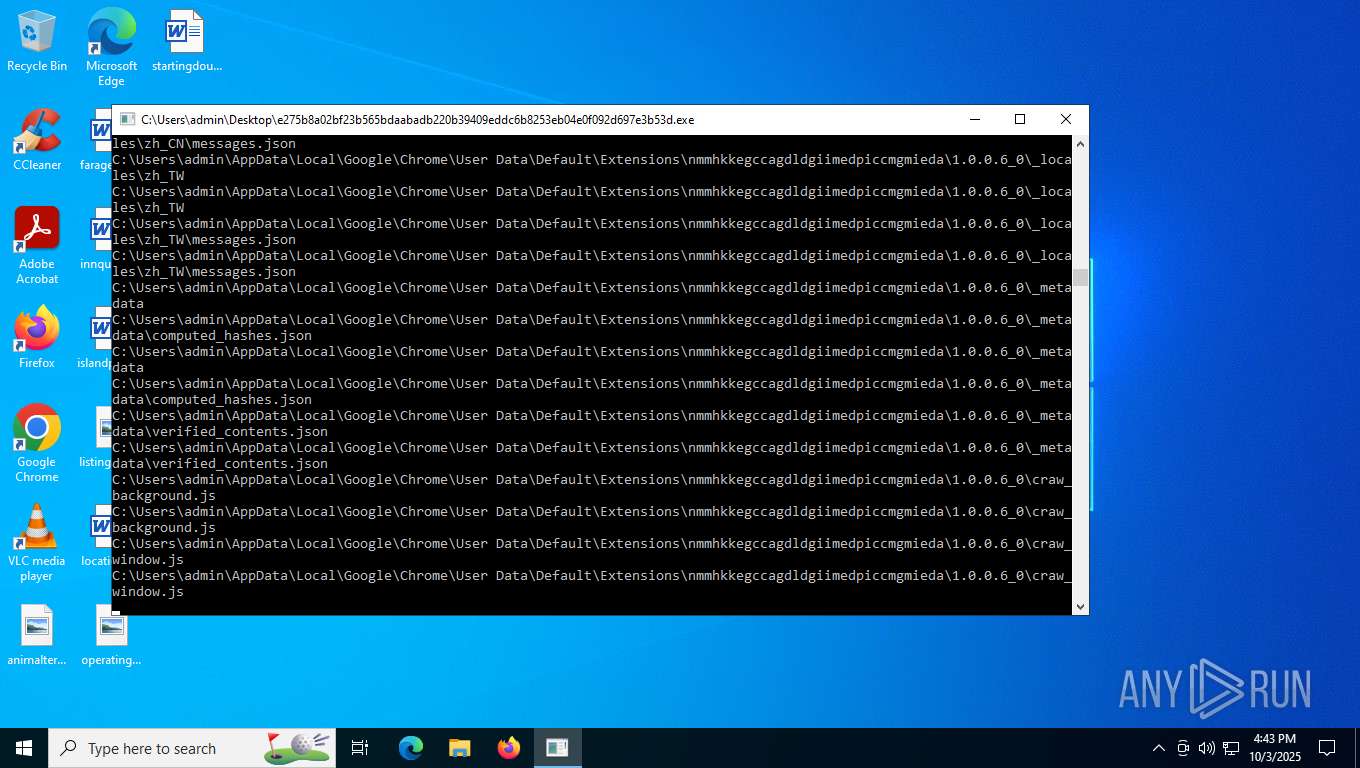
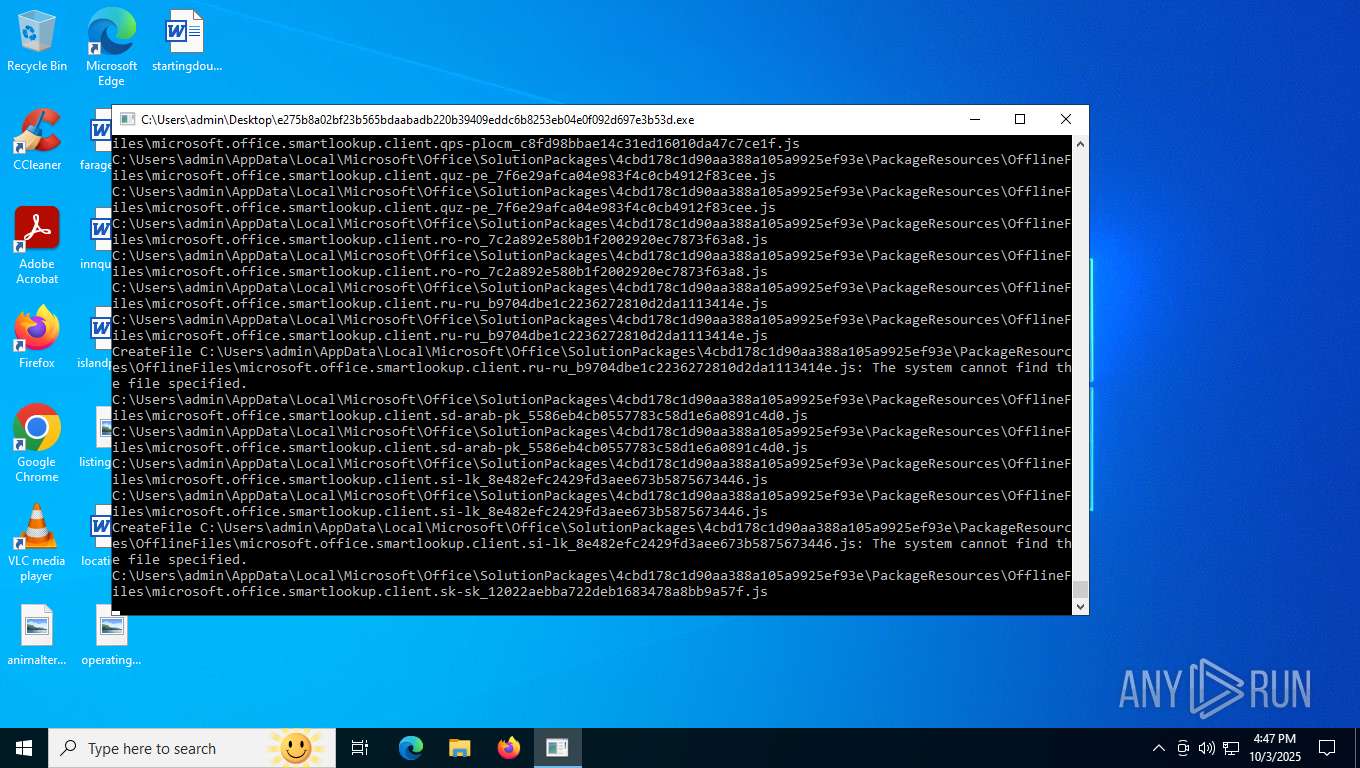
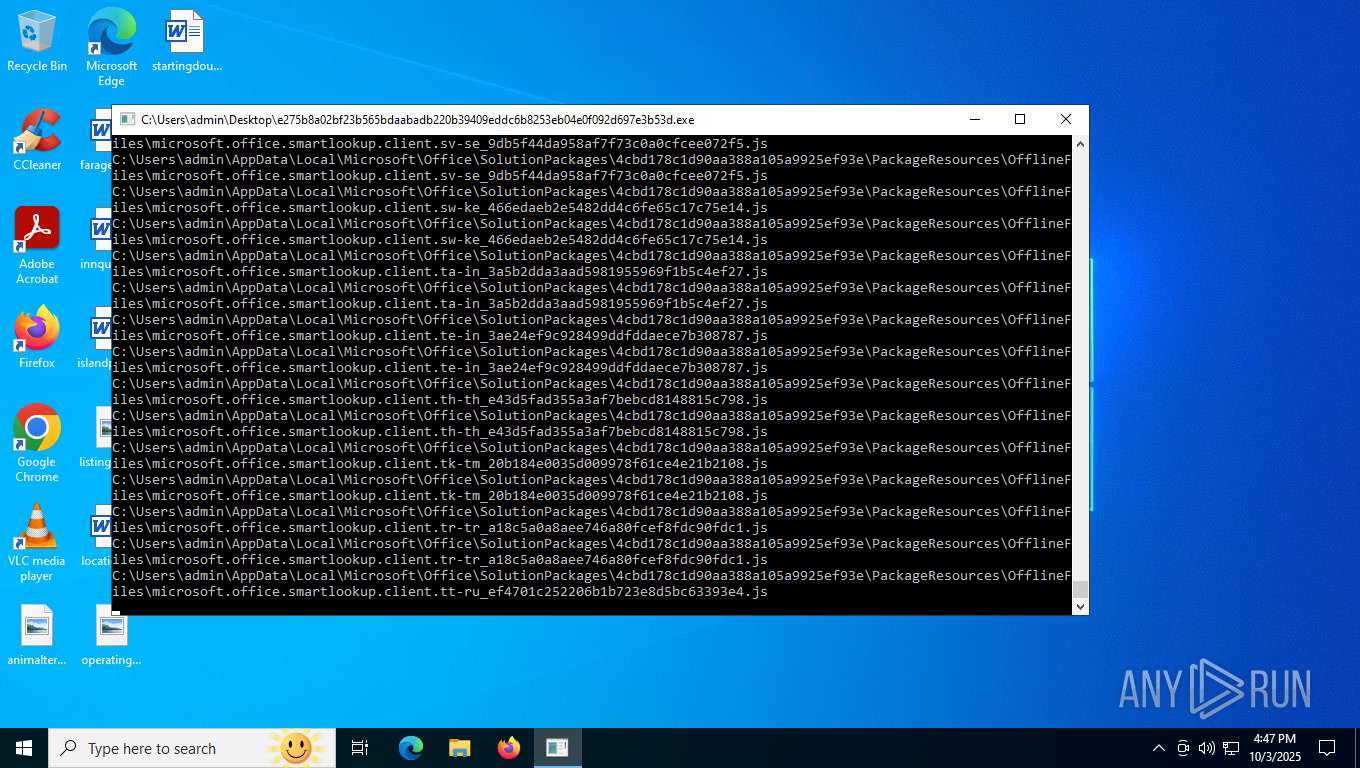
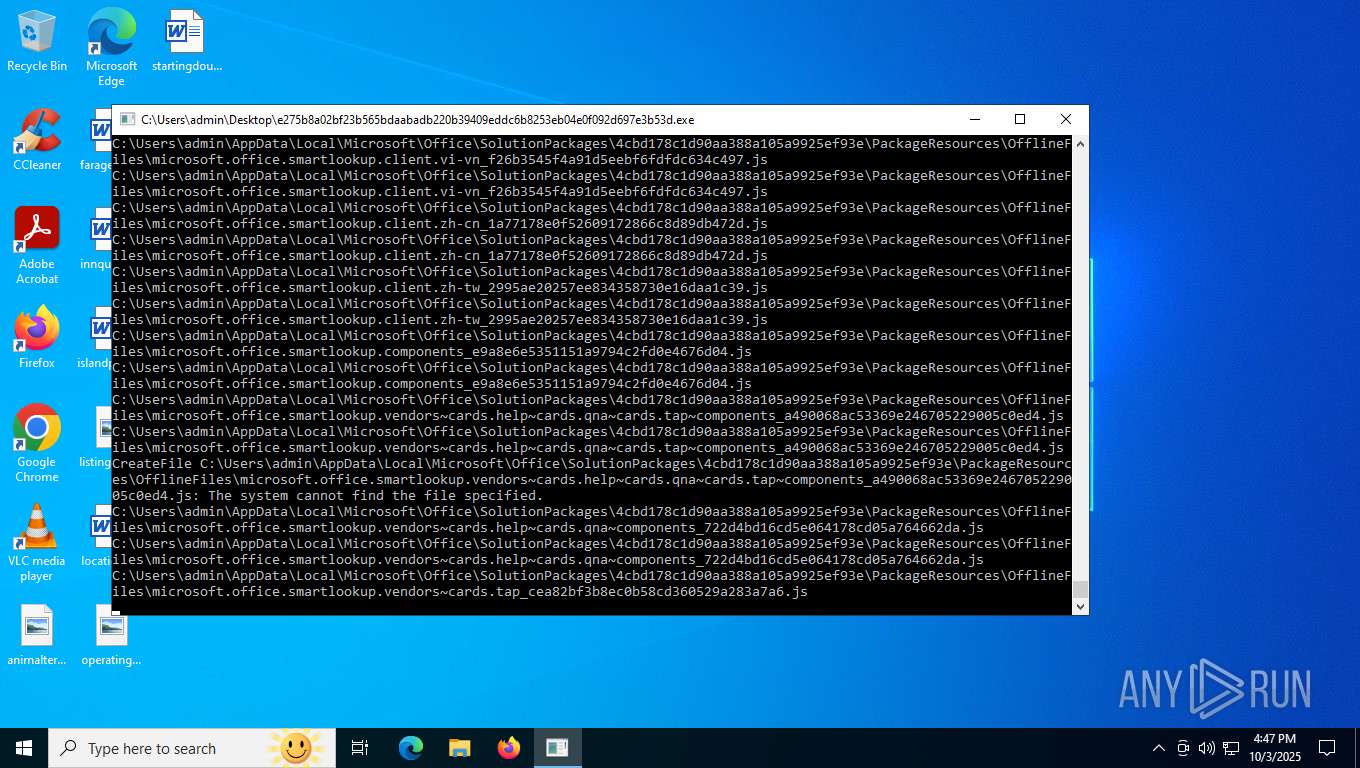
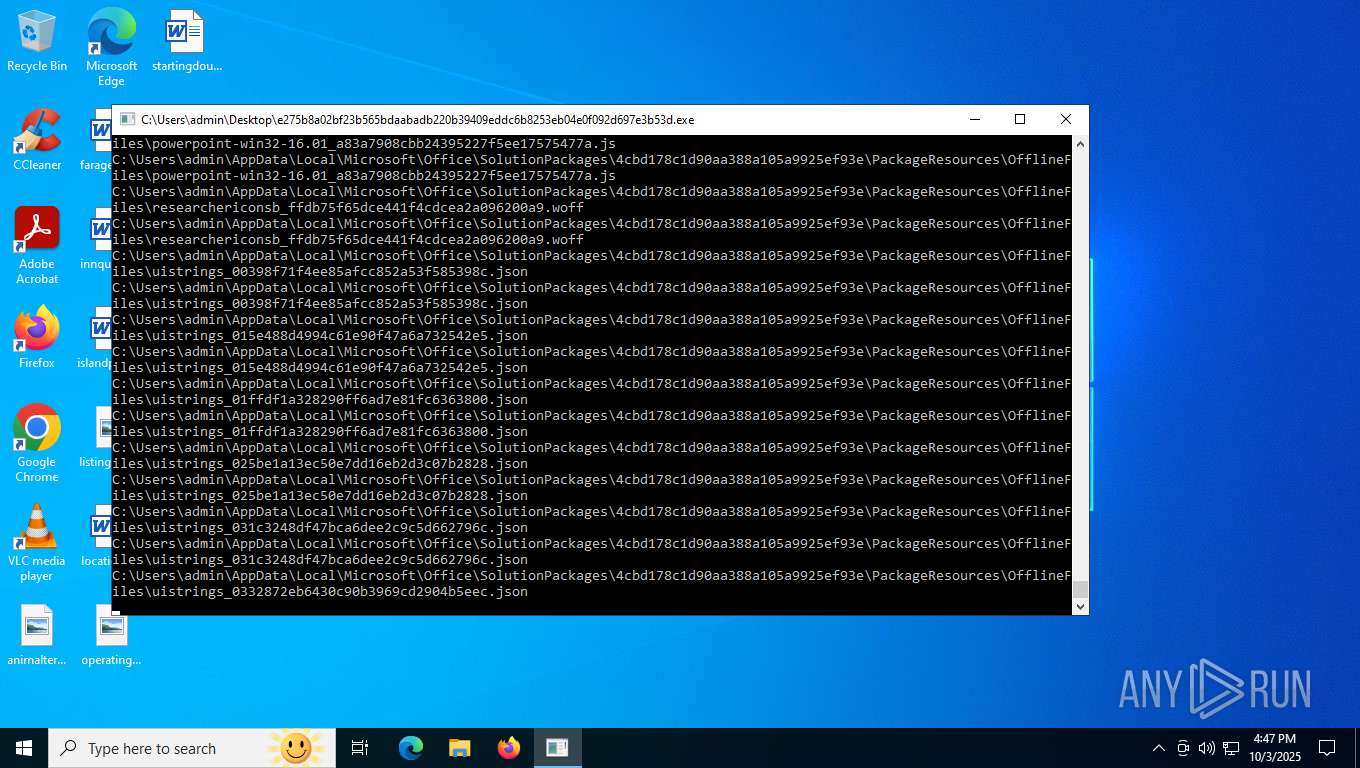
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
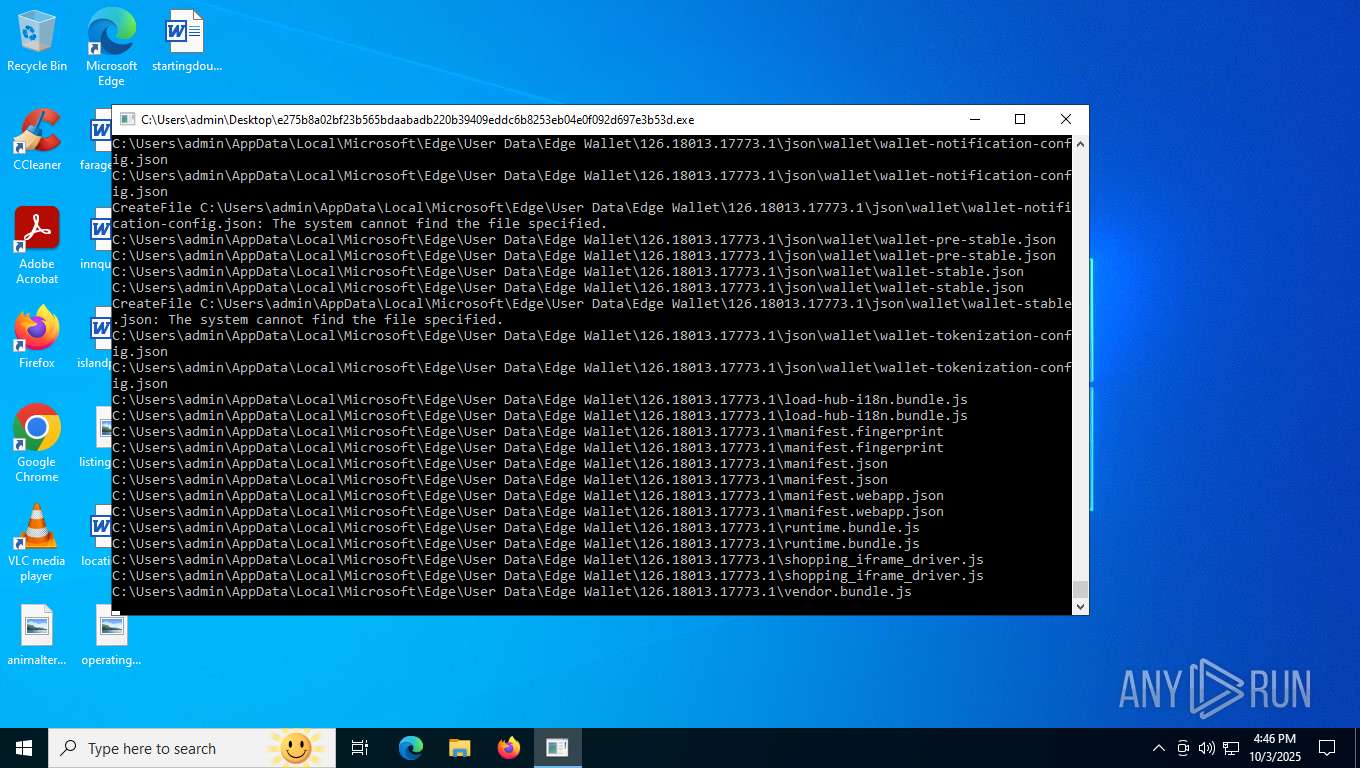
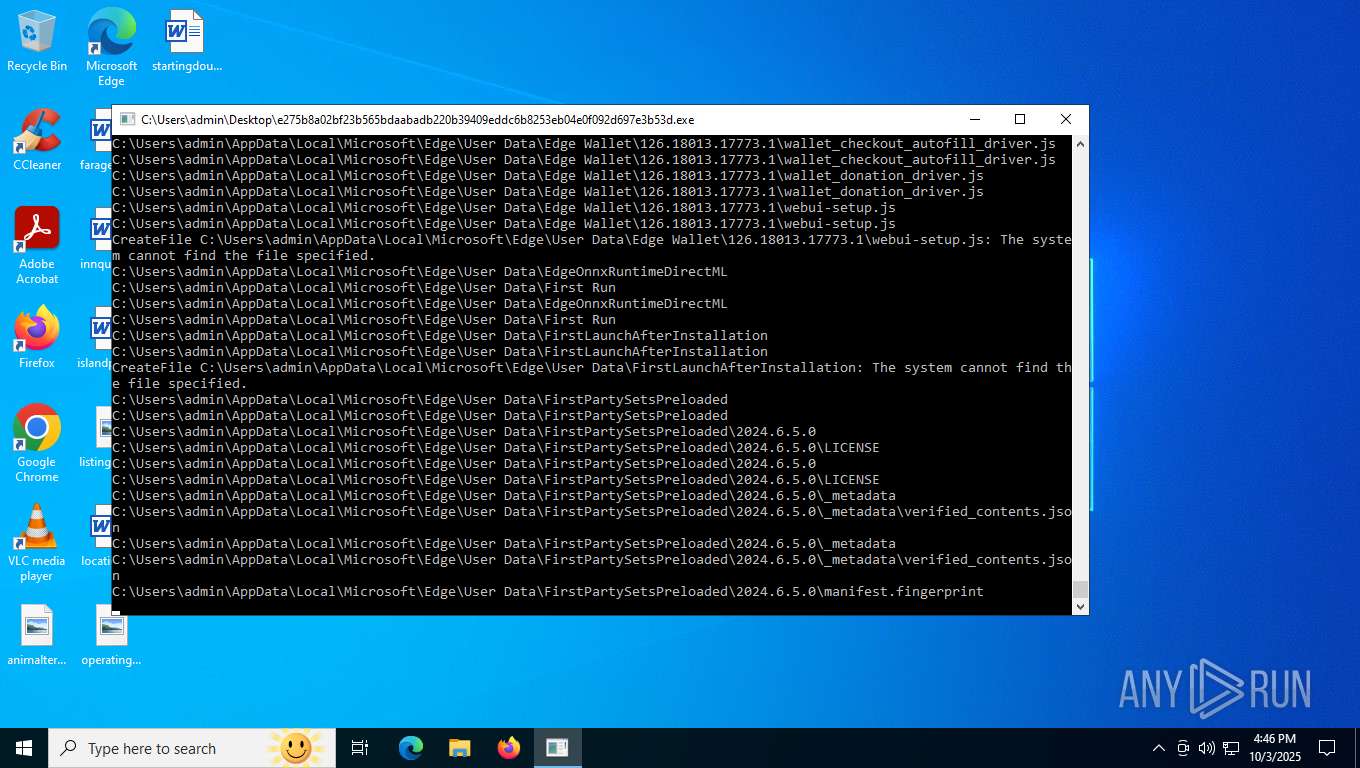
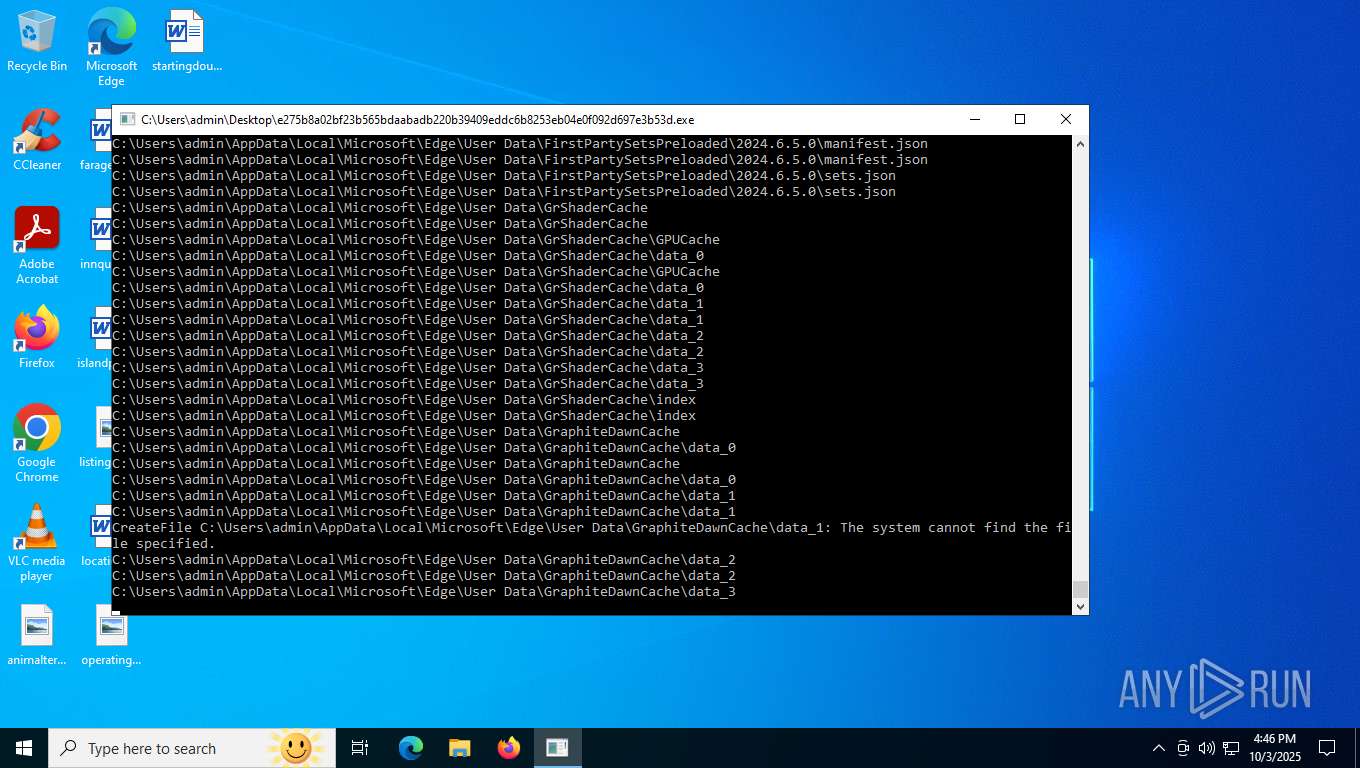
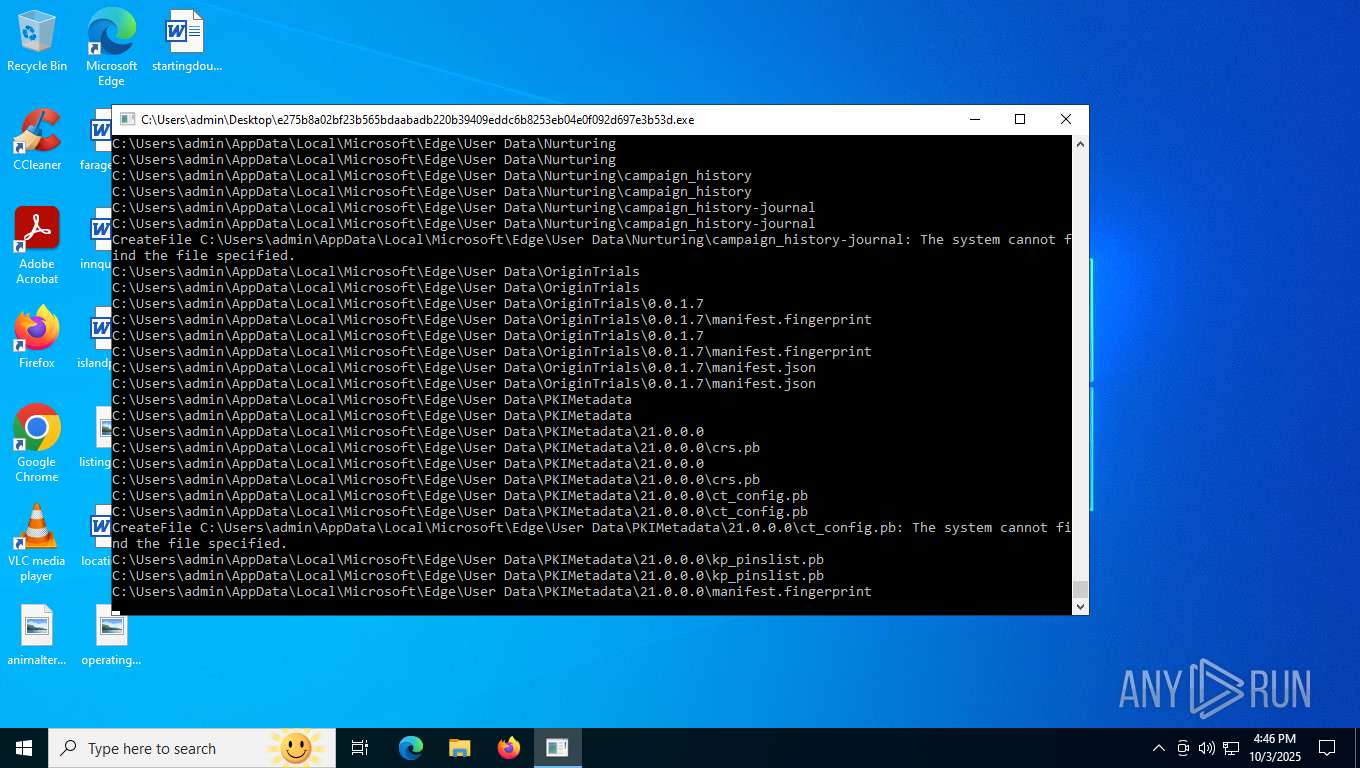
| File name: | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d |
| Full analysis: | https://app.any.run/tasks/70a2b79f-b204-4a7f-9777-2eb43082f89f |
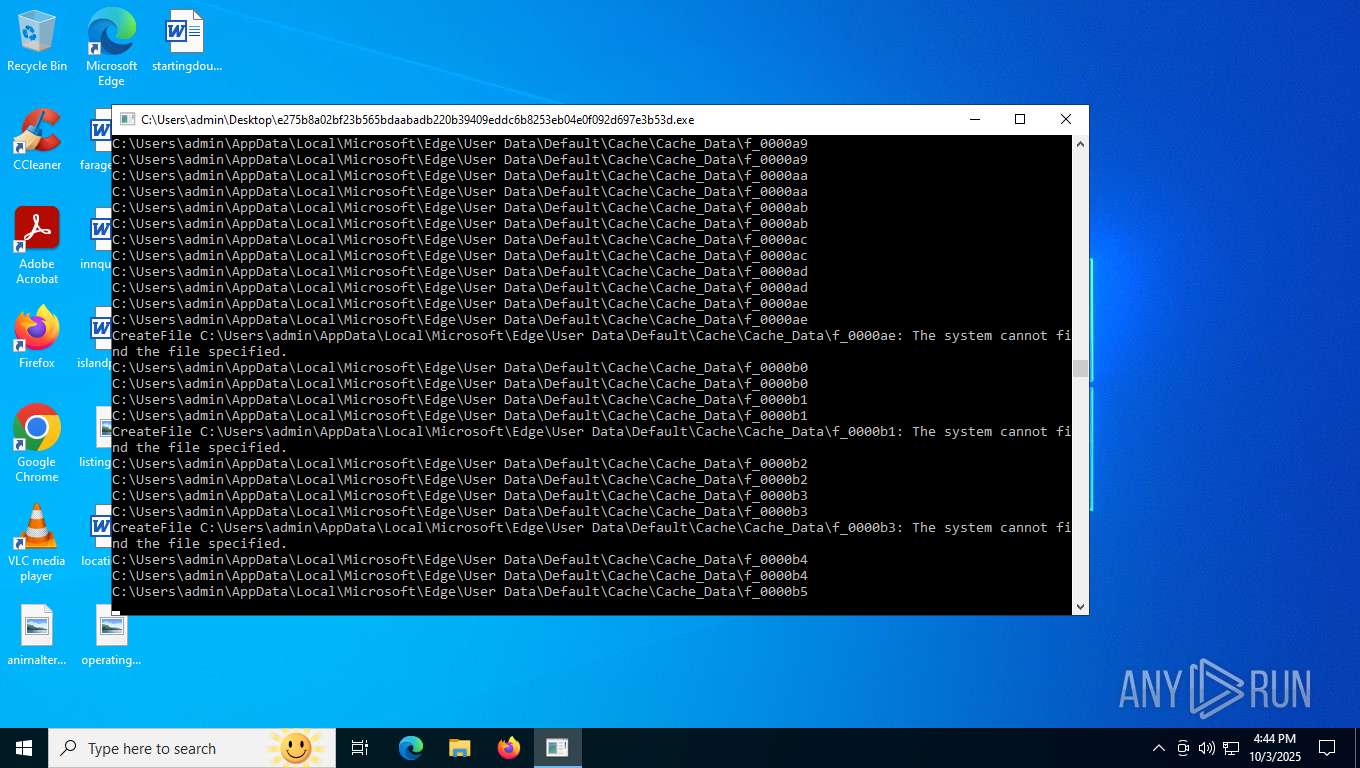
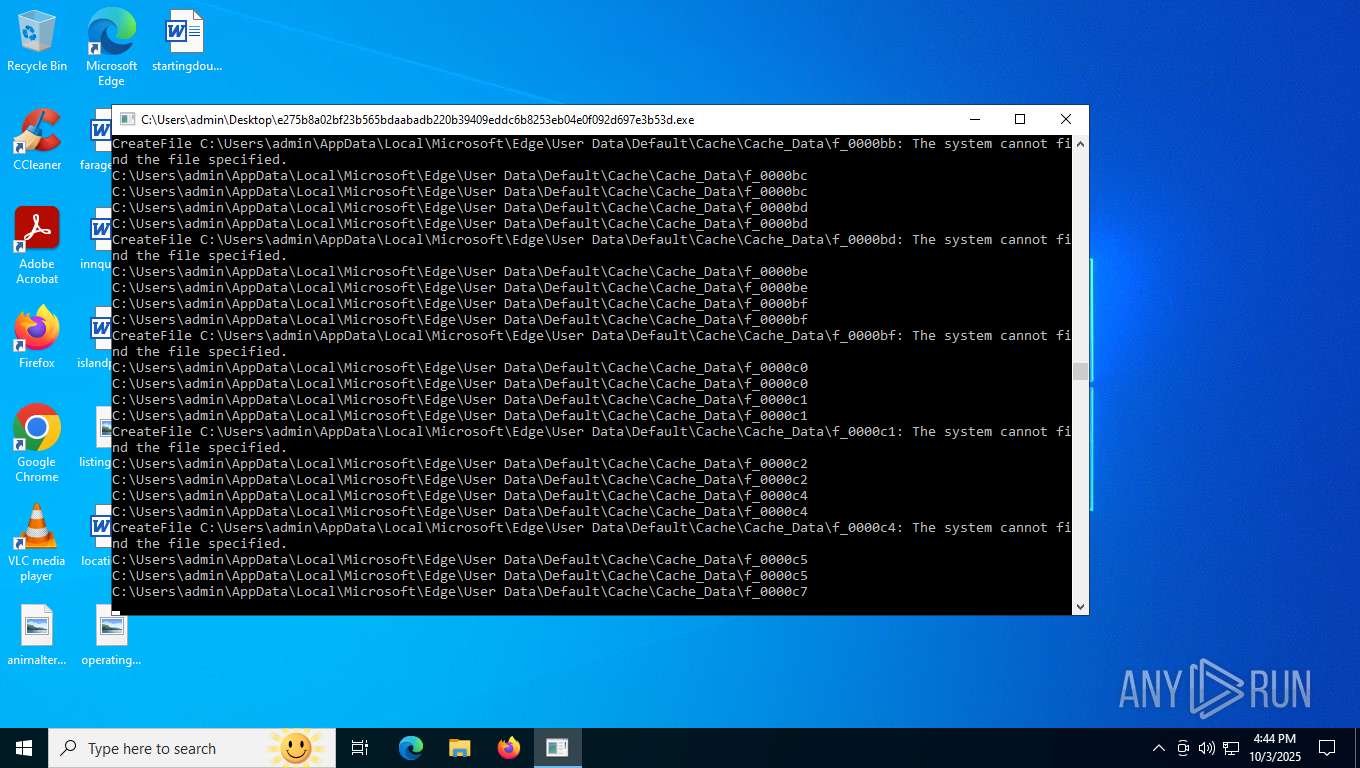
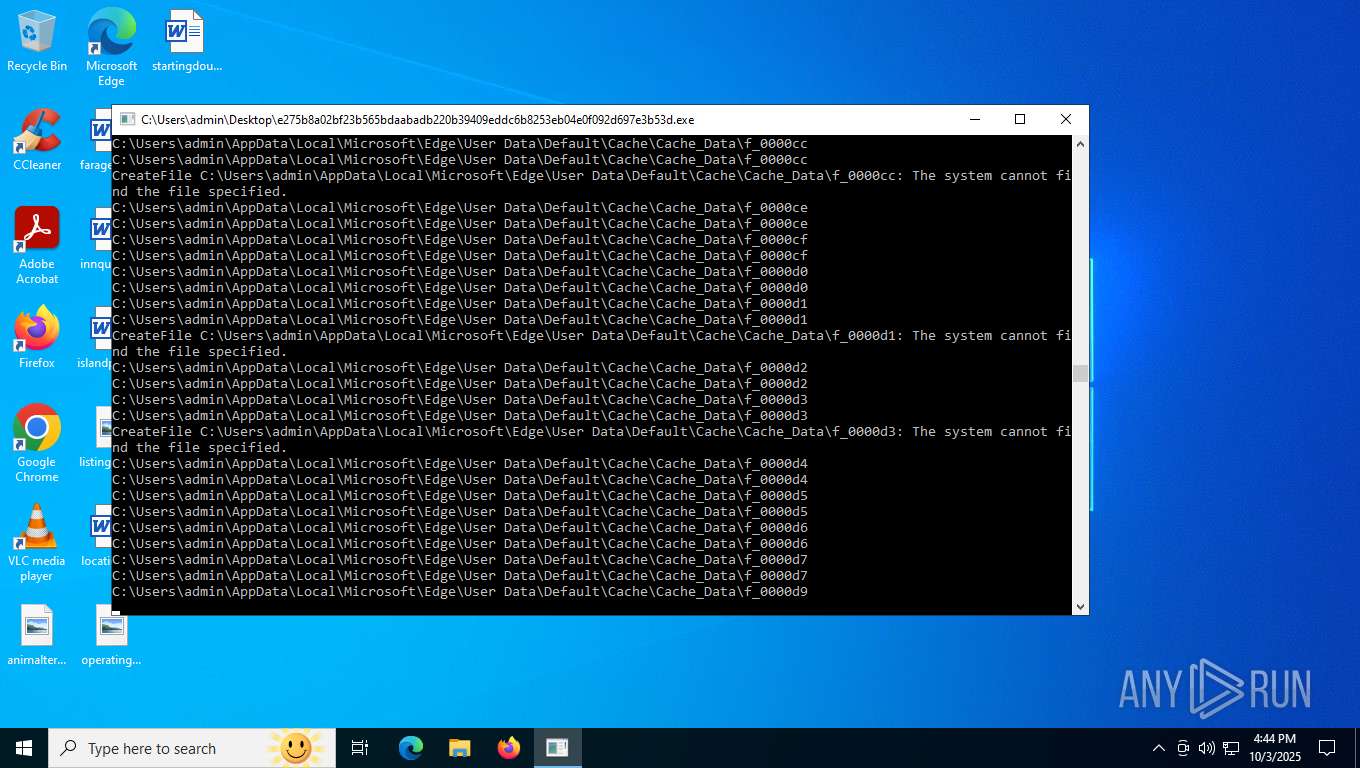
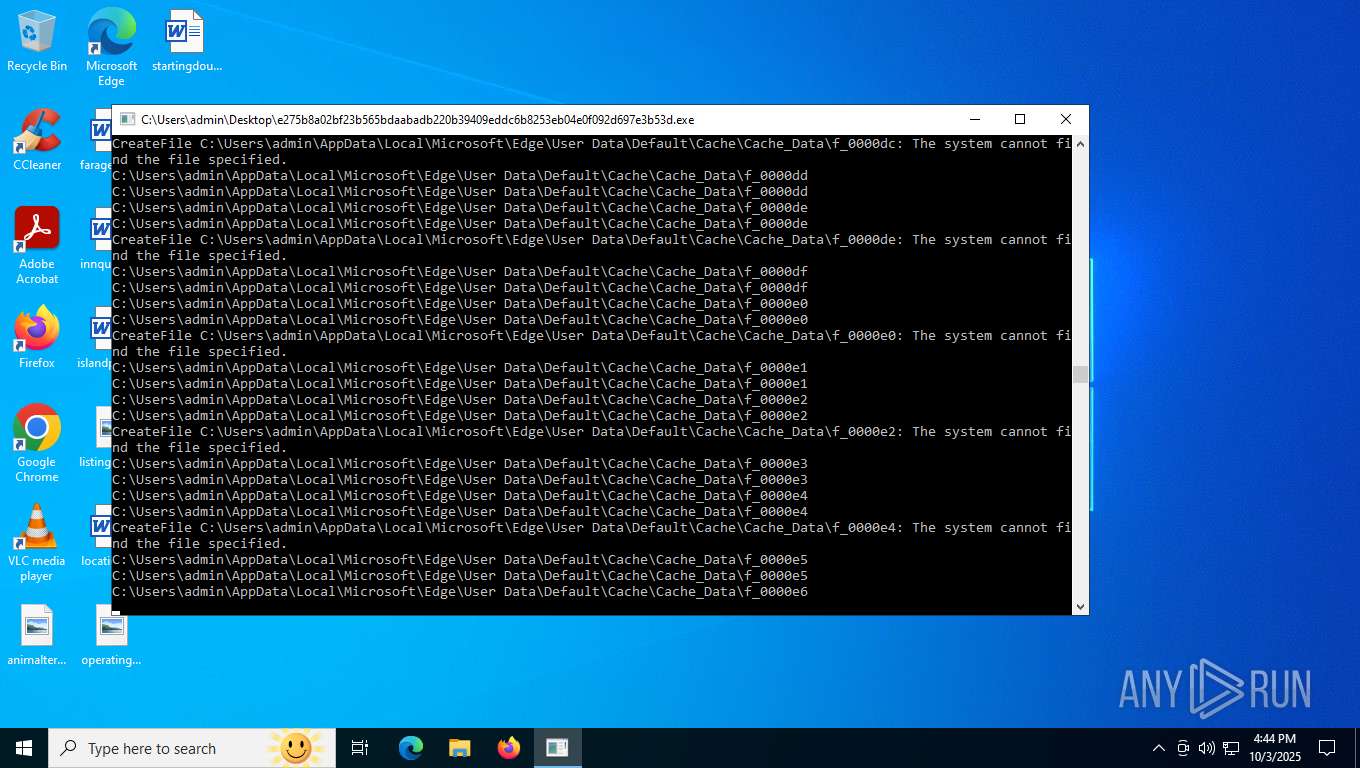
| Verdict: | Malicious activity |
| Threats: | Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying. |
| Analysis date: | October 03, 2025, 16:43:14 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (console) x86-64 (stripped to external PDB), for MS Windows, 13 sections |
| MD5: | 2E07A4DE9E6BA84728FBDF27384EA0B9 |
| SHA1: | 0E31379DCB838B619EC1B44DDA3FC4CC20596764 |
| SHA256: | E275B8A02BF23B565BDAABADB220B39409EDDC6B8253EB04E0F092D697E3B53D |
| SSDEEP: | 98304:29UCaOhX+ZSCU/DttsAXQ+G9BYdmO/olEiLjp2wf+dR6DOYCd5R7K8nL+: |
| .exe | | | Win64 Executable (generic) (87.3) |
|---|---|---|
| .exe | | | Generic Win/DOS Executable (6.3) |
| .exe | | | DOS Executable Generic (6.3) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 0000:00:00 00:00:00 |
| ImageFileCharacteristics: | Executable, Large address aware, No debug |
| PEType: | PE32+ |
| LinkerVersion: | 3 |
| CodeSize: | 1139200 |
| InitializedDataSize: | 128512 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x61b20 |
| OSVersion: | 6.1 |
| ImageVersion: | 1 |
| SubsystemVersion: | 6.1 |
| Subsystem: | Windows command line |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1992 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
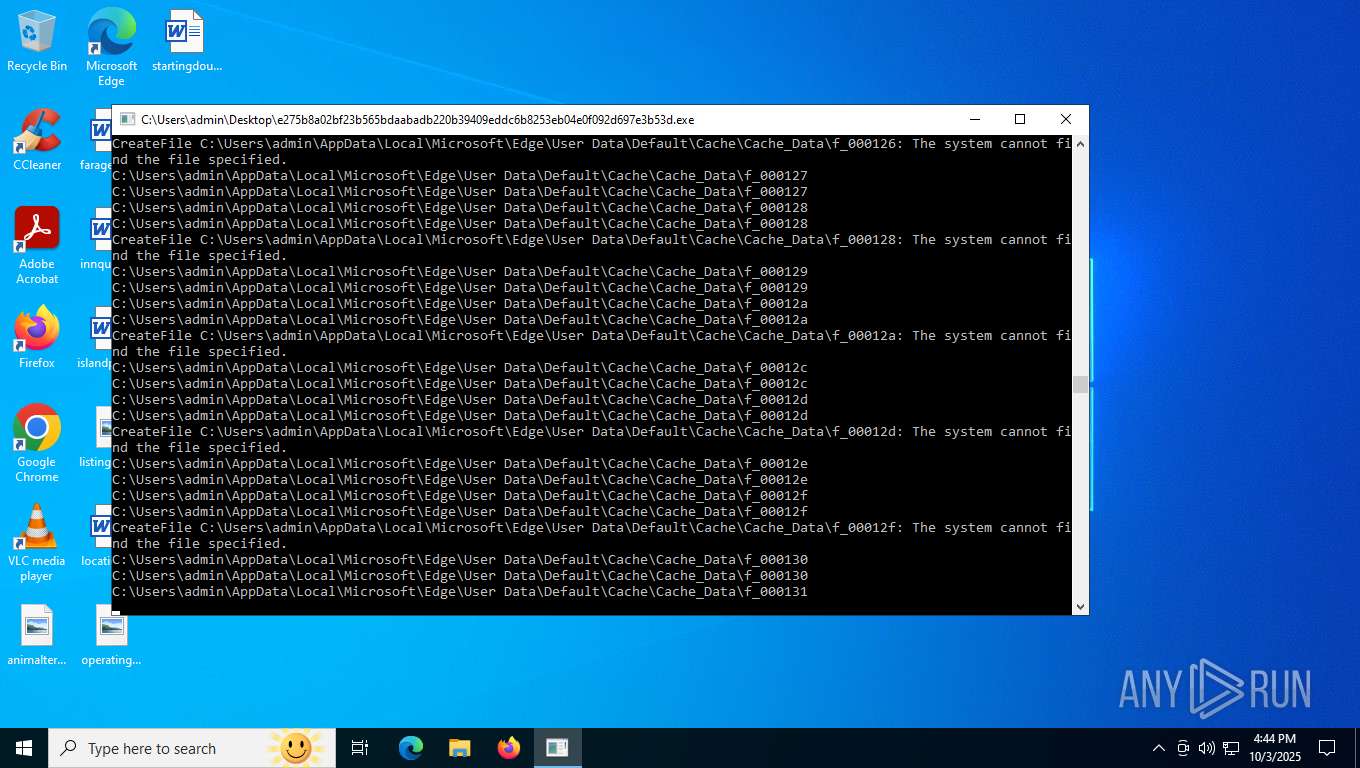
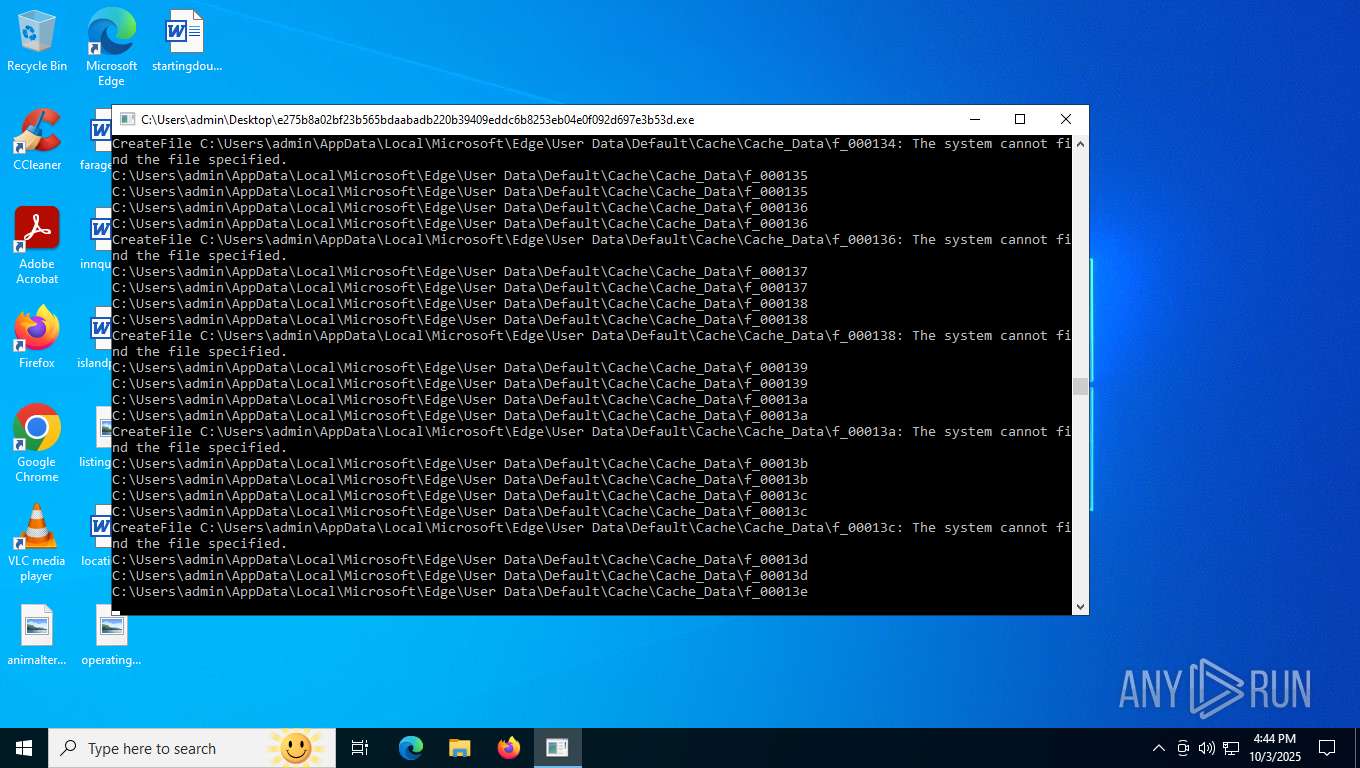
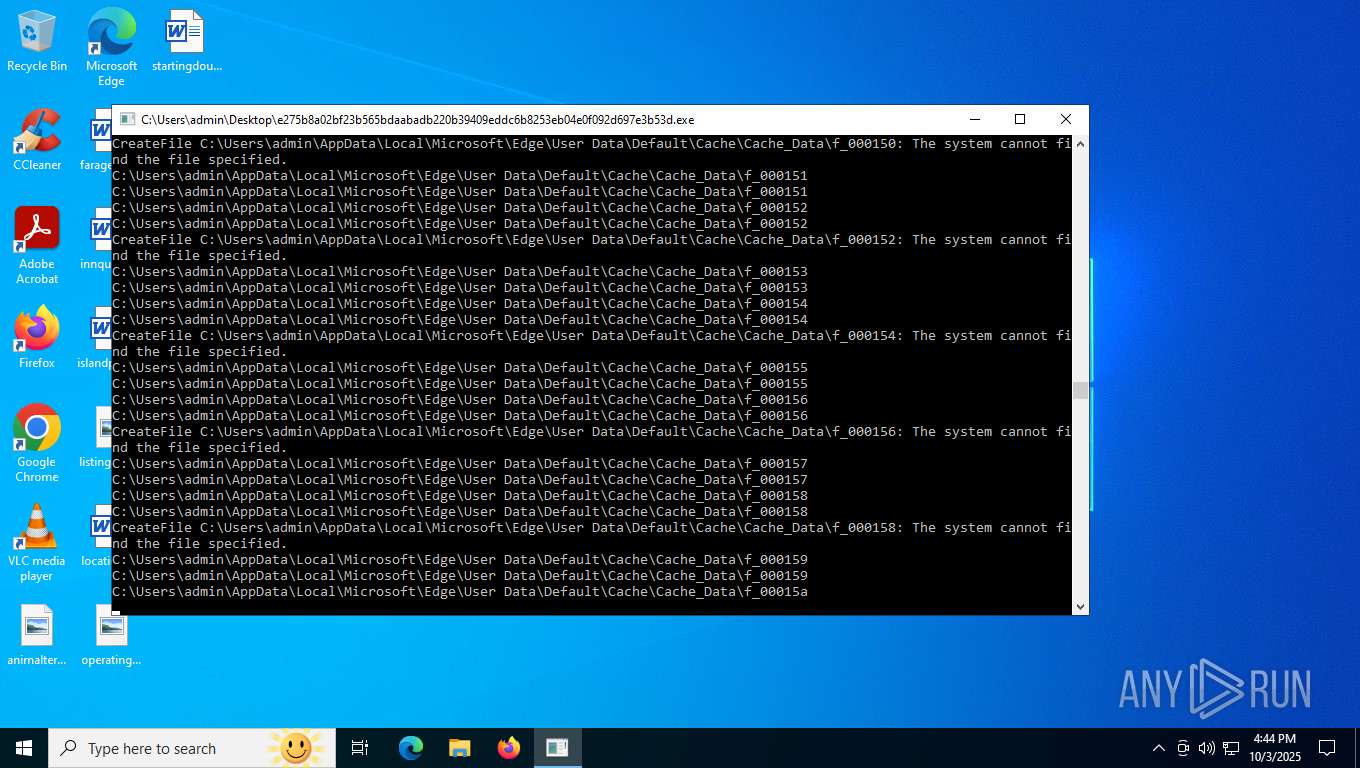
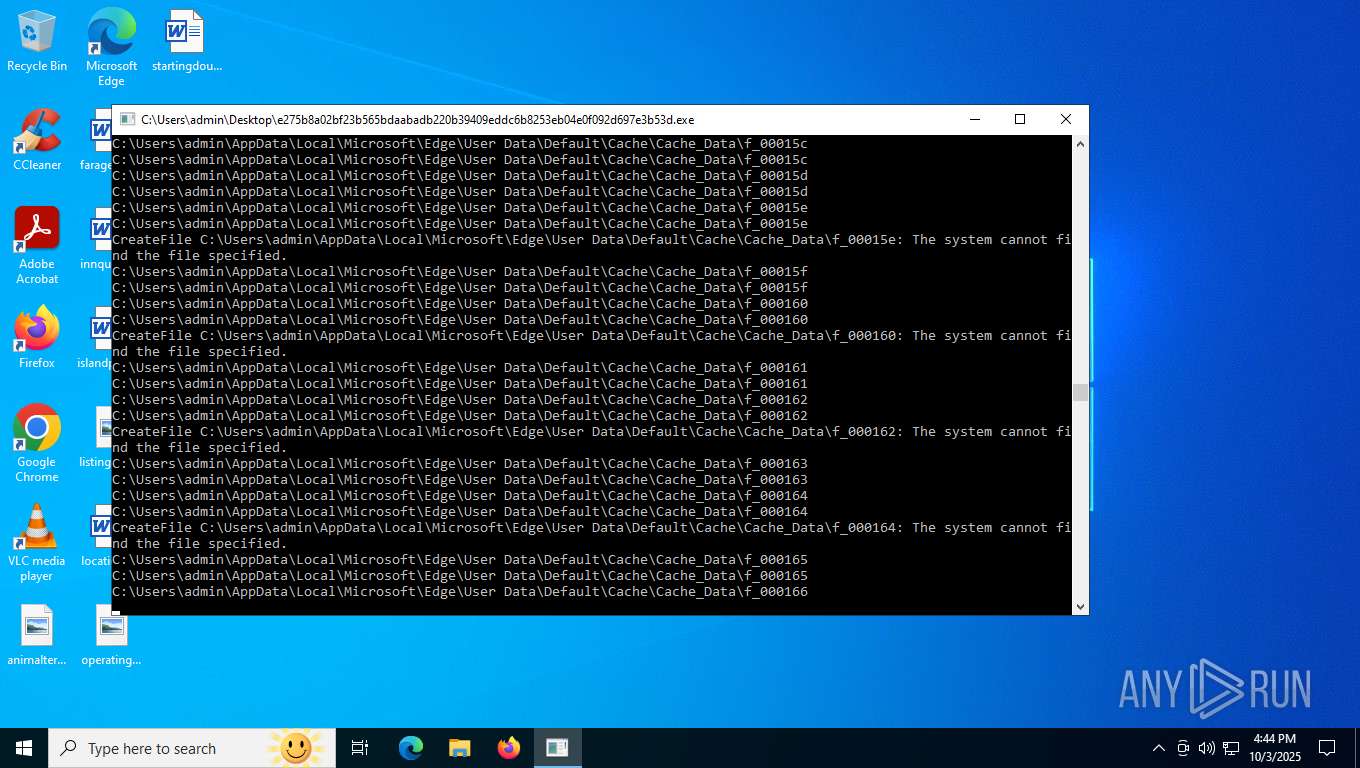
| 2400 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
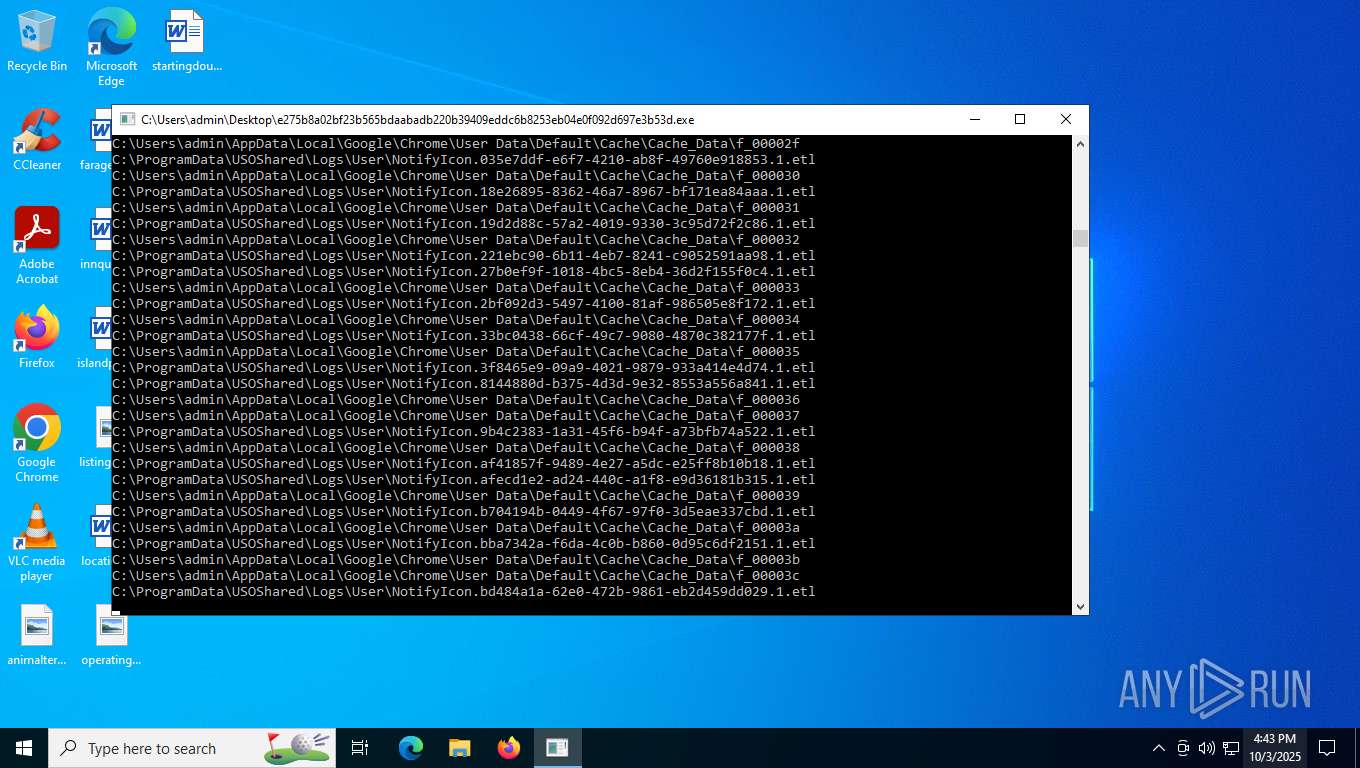
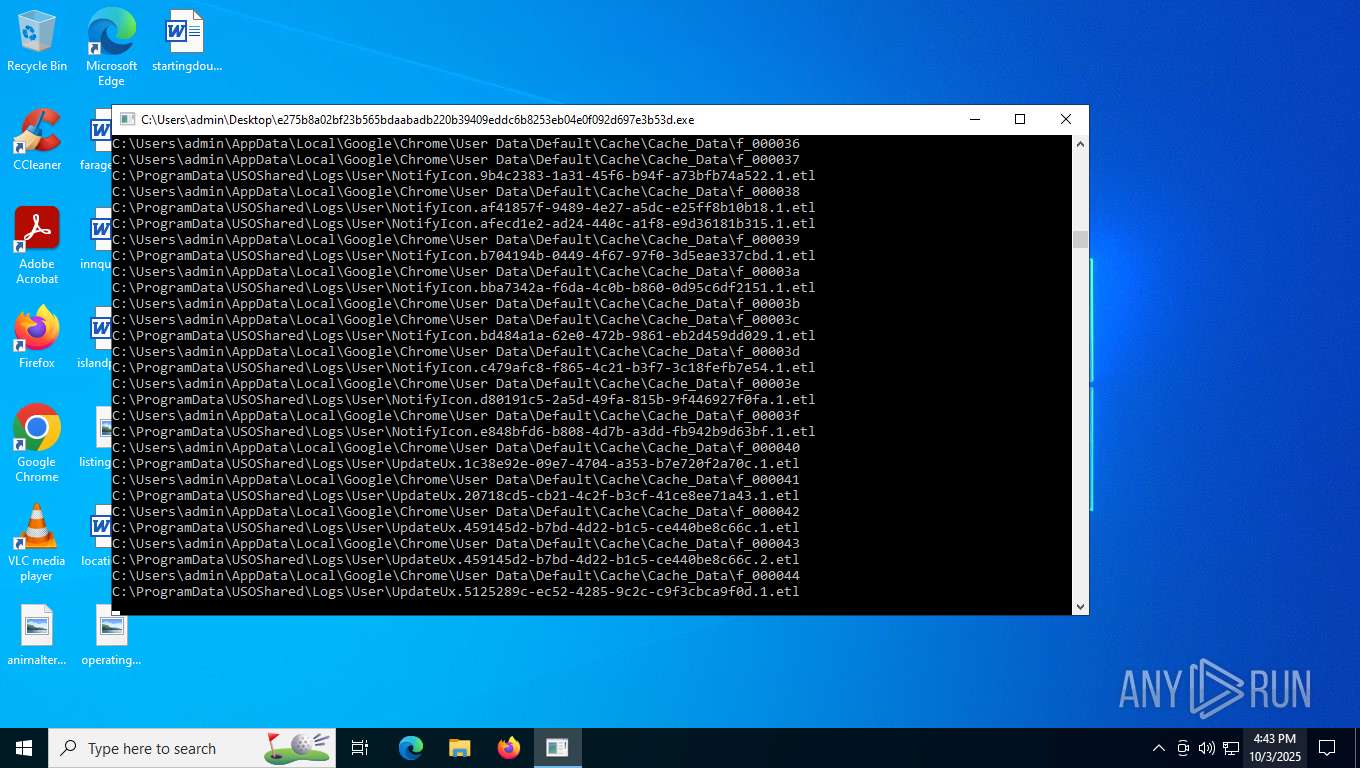
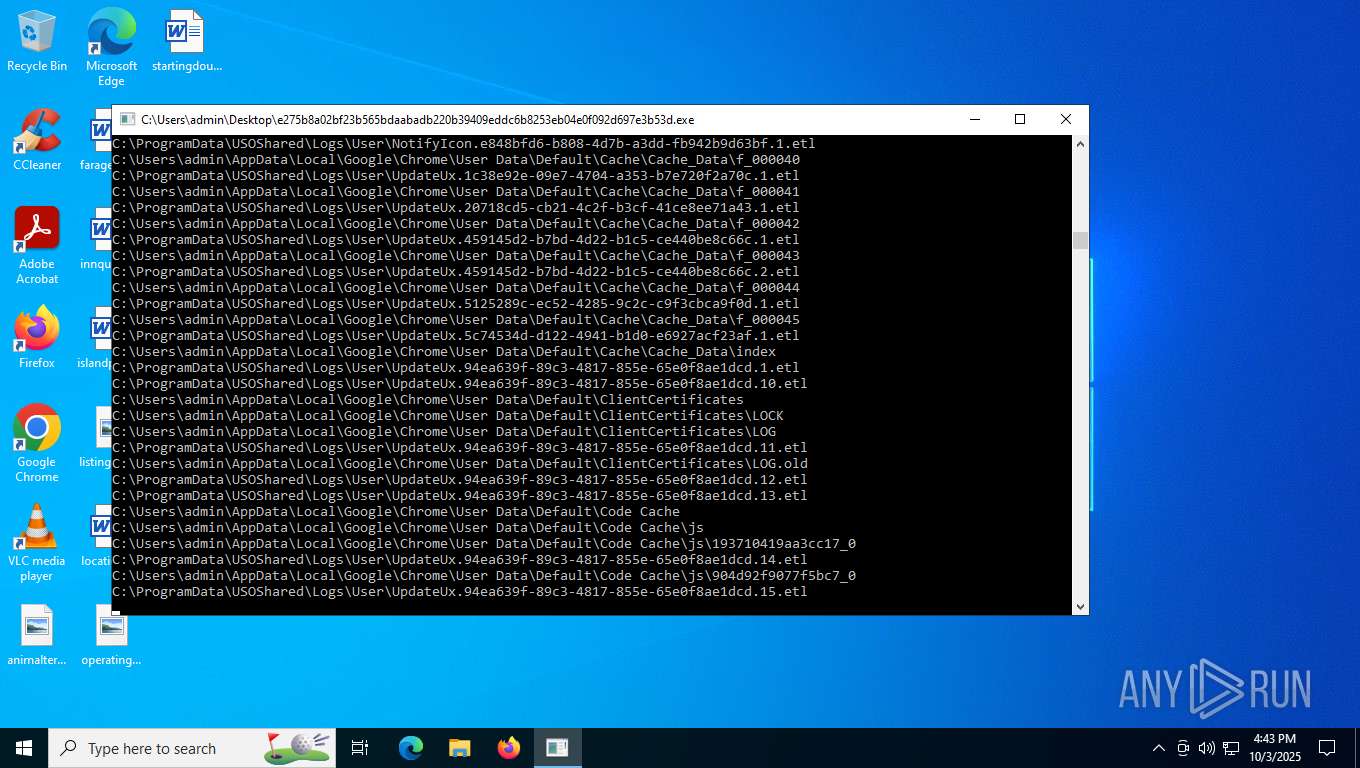
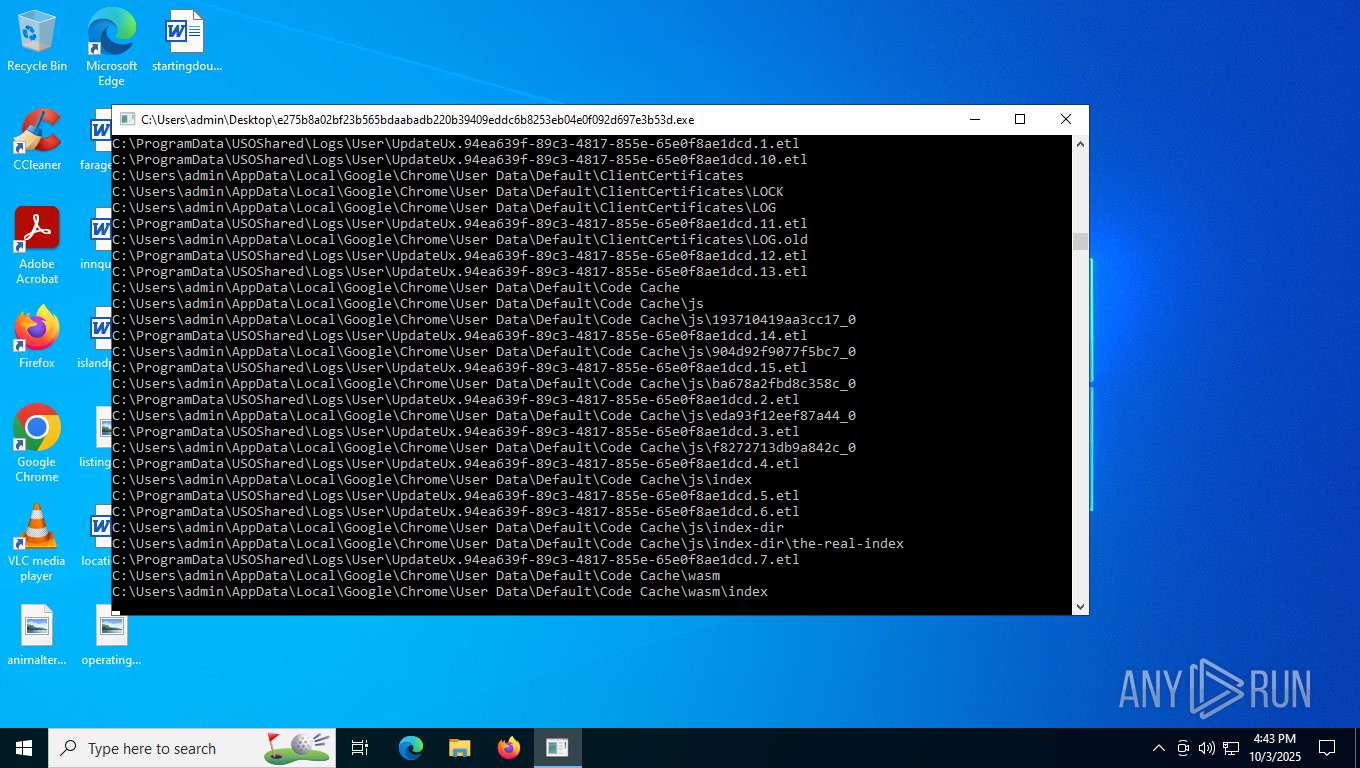
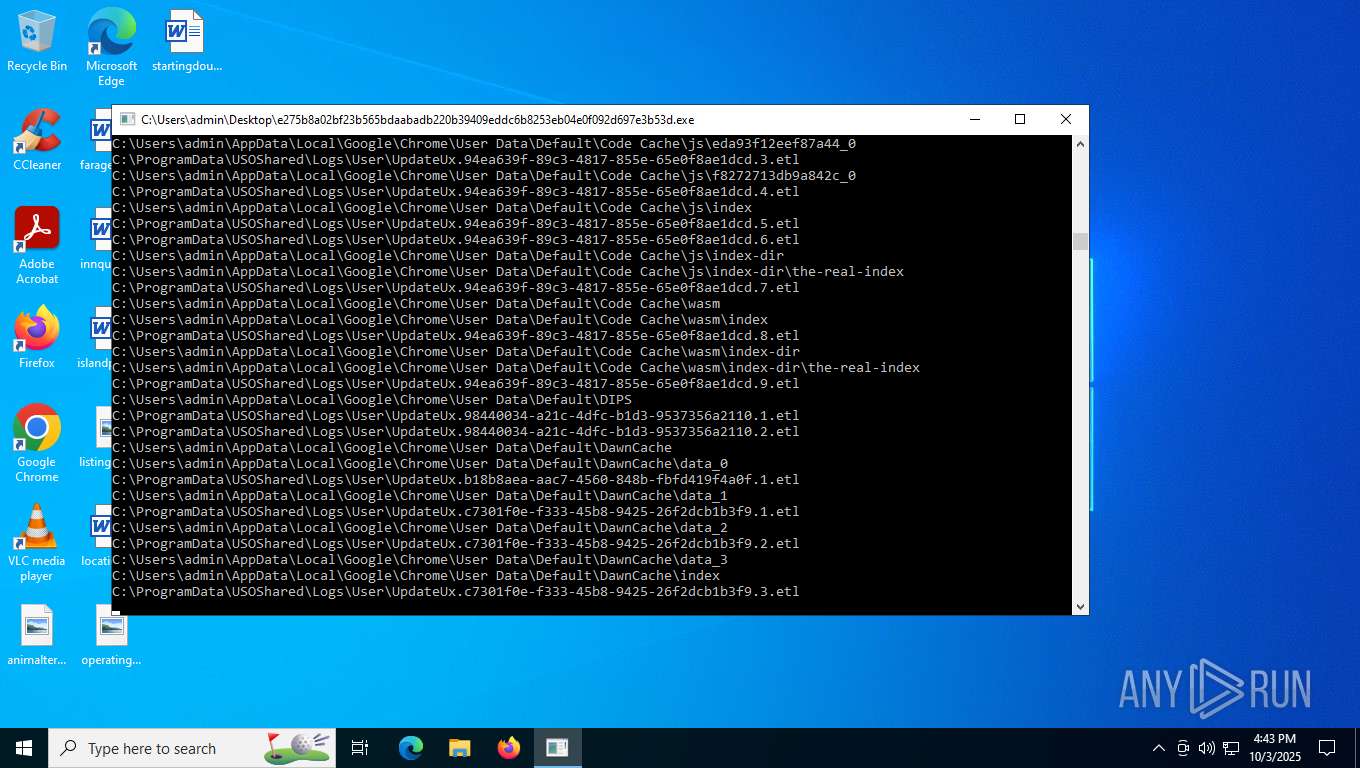
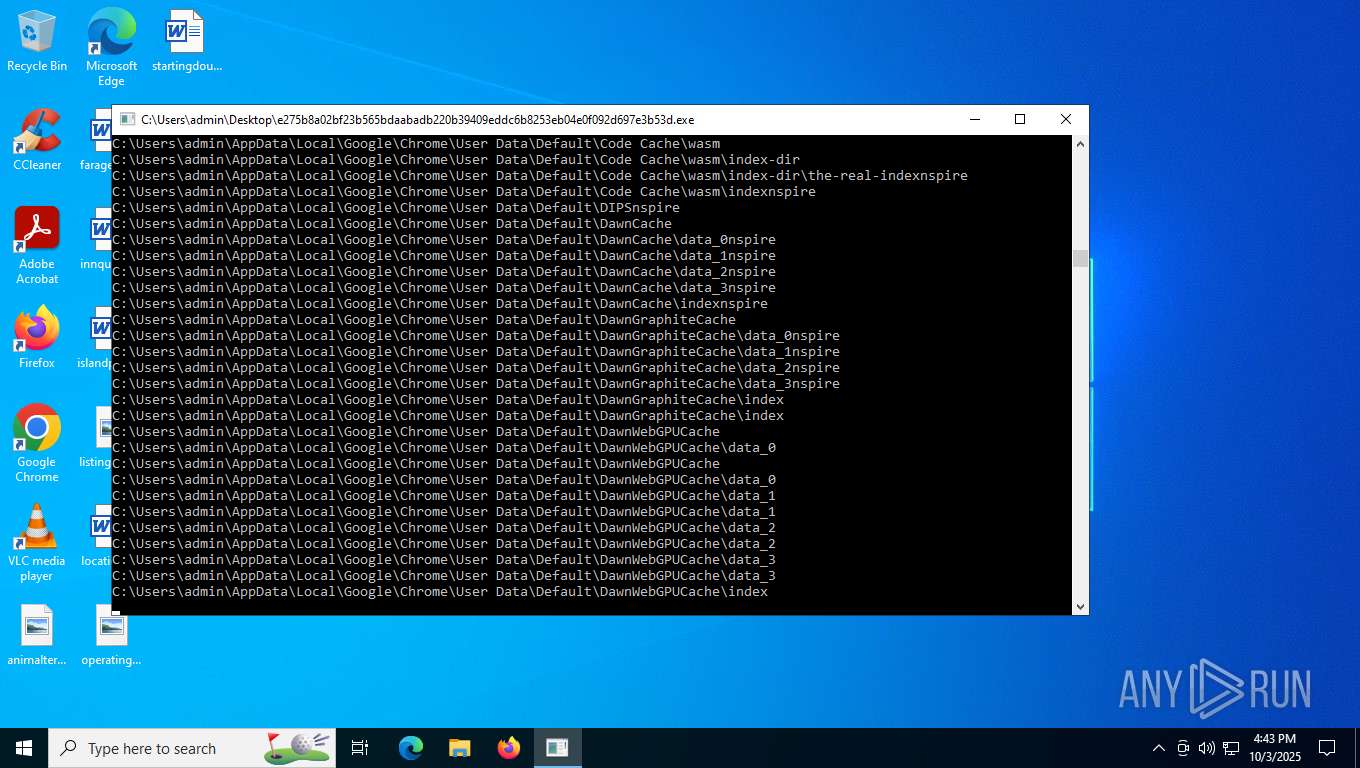
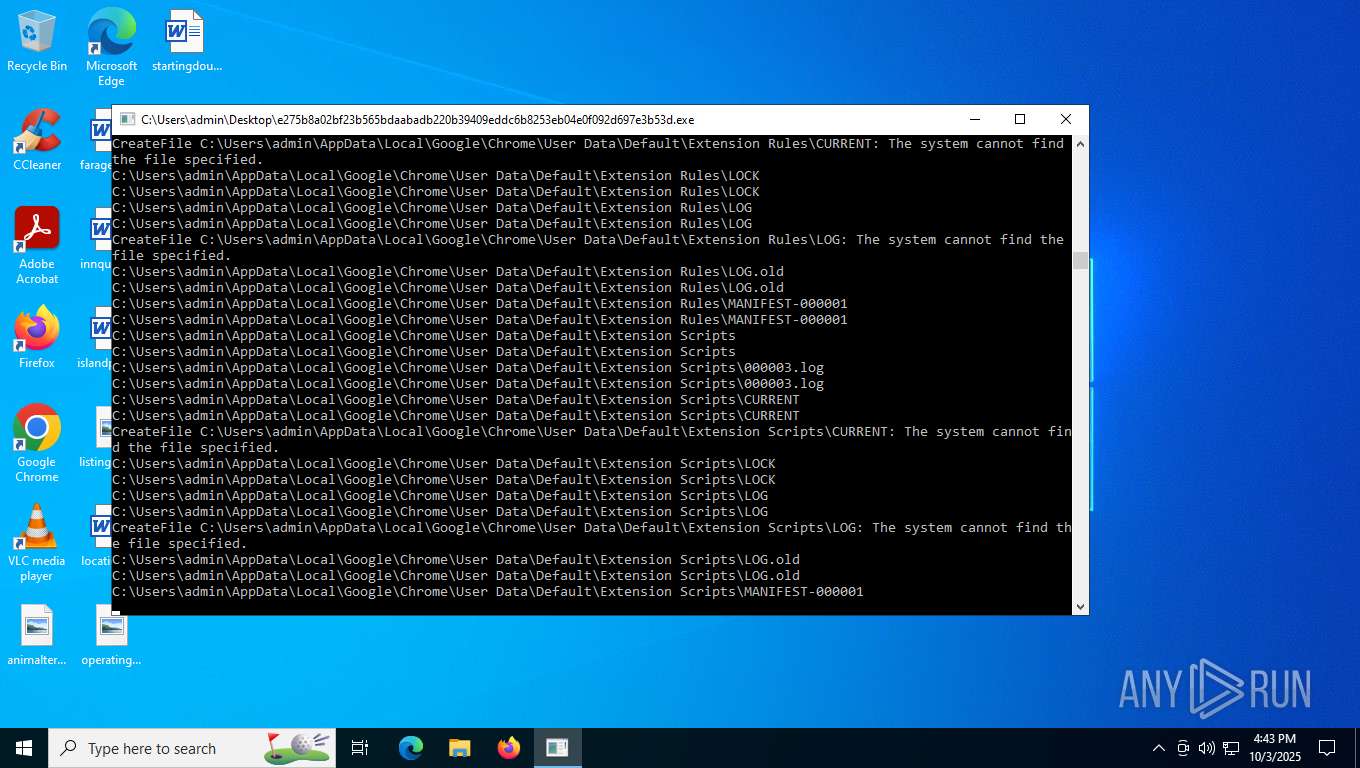
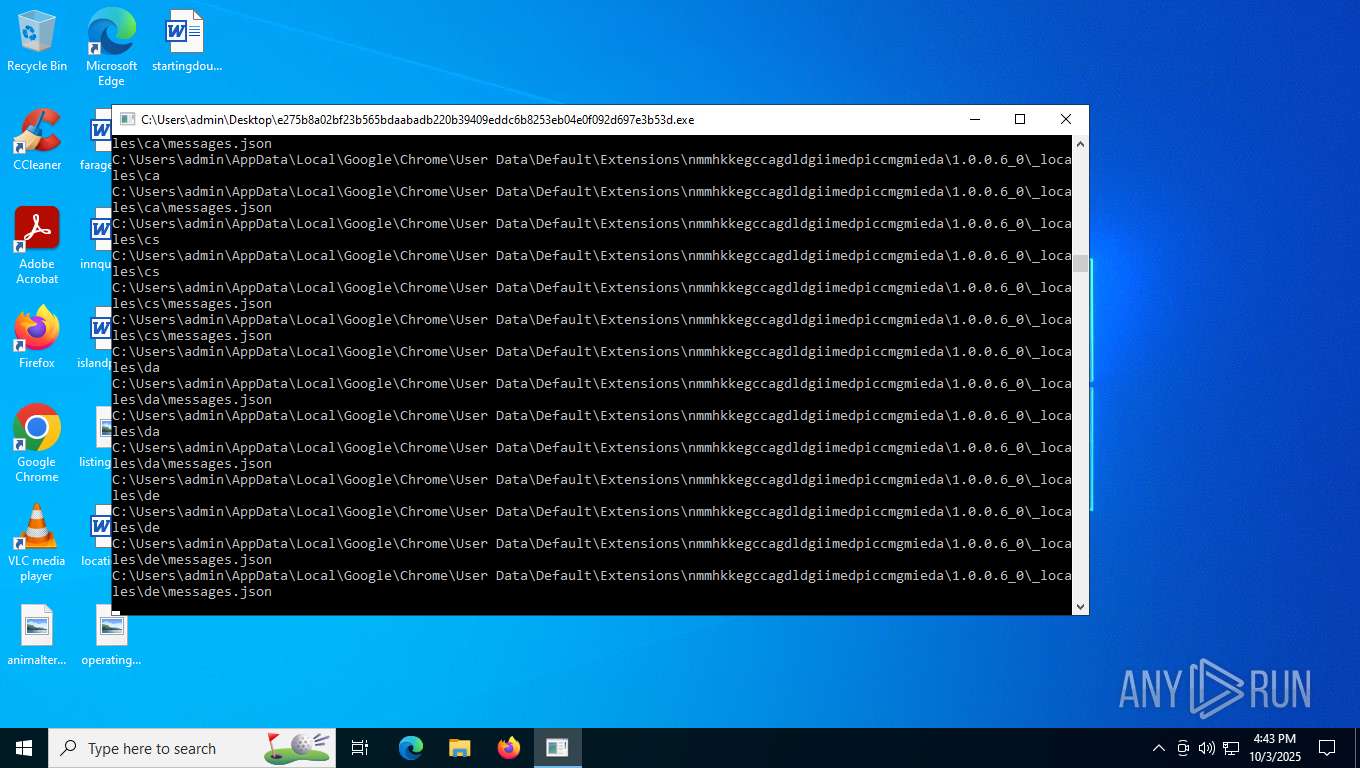
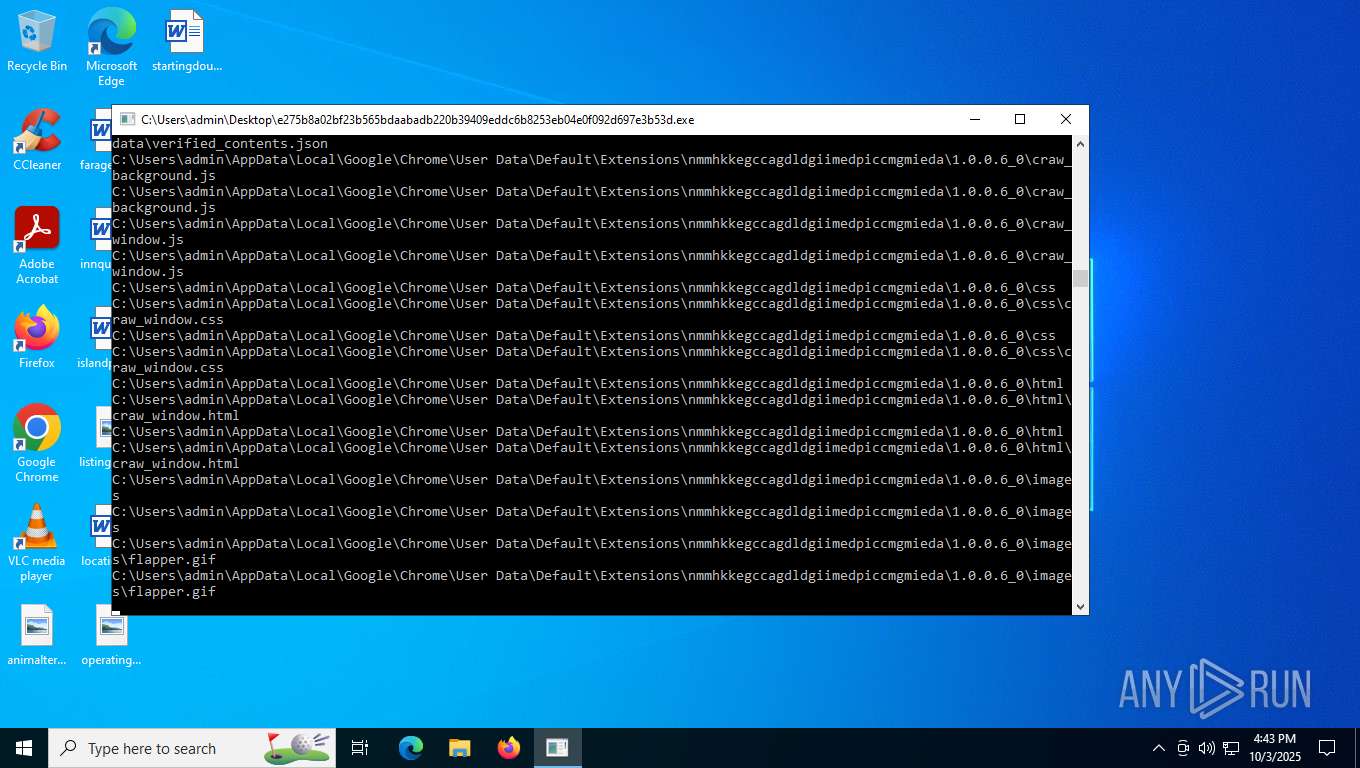
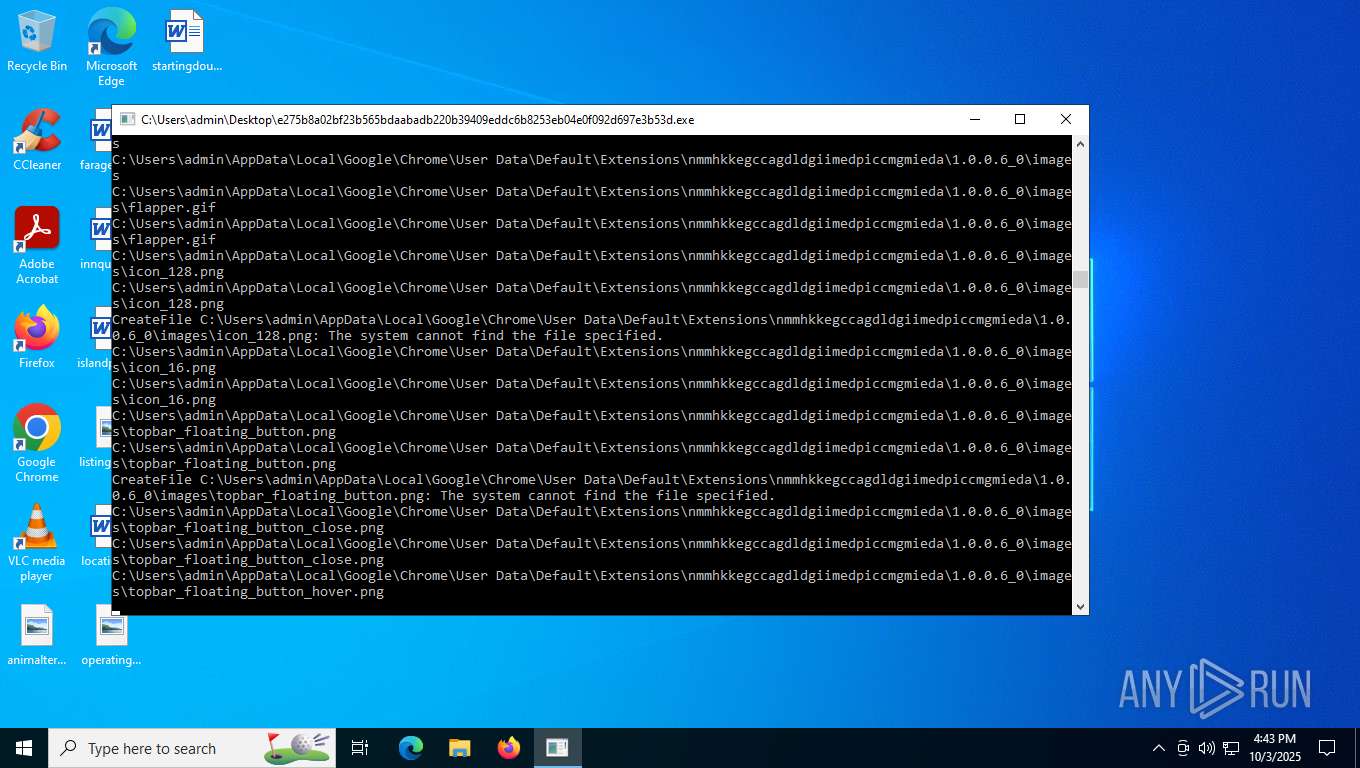
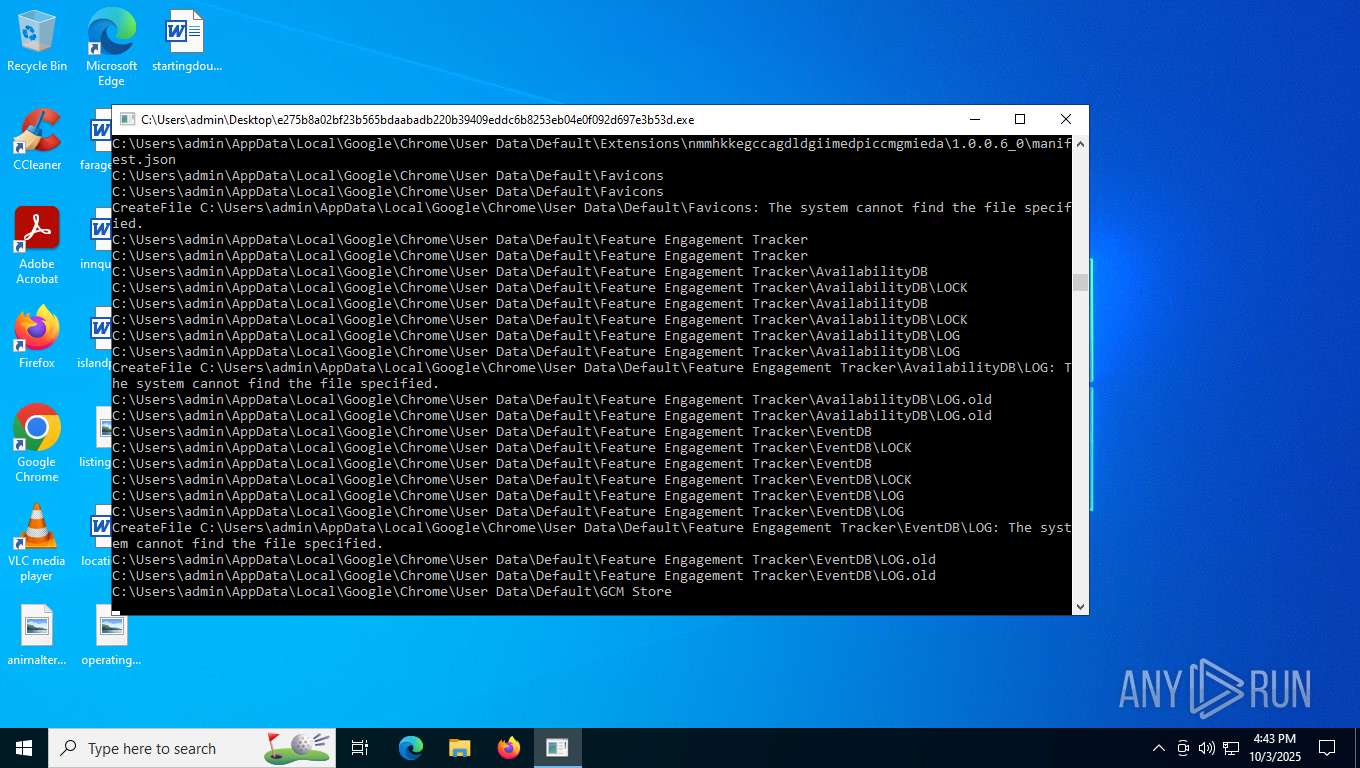
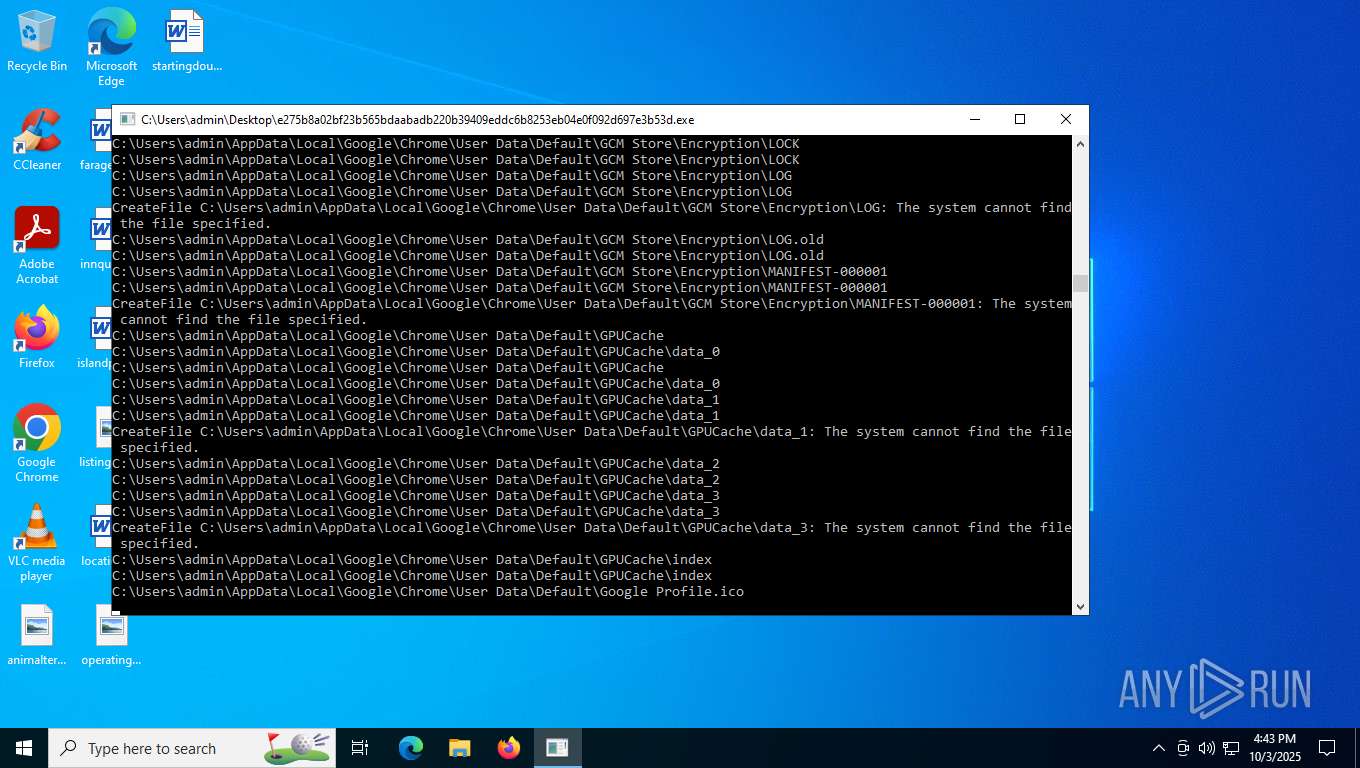
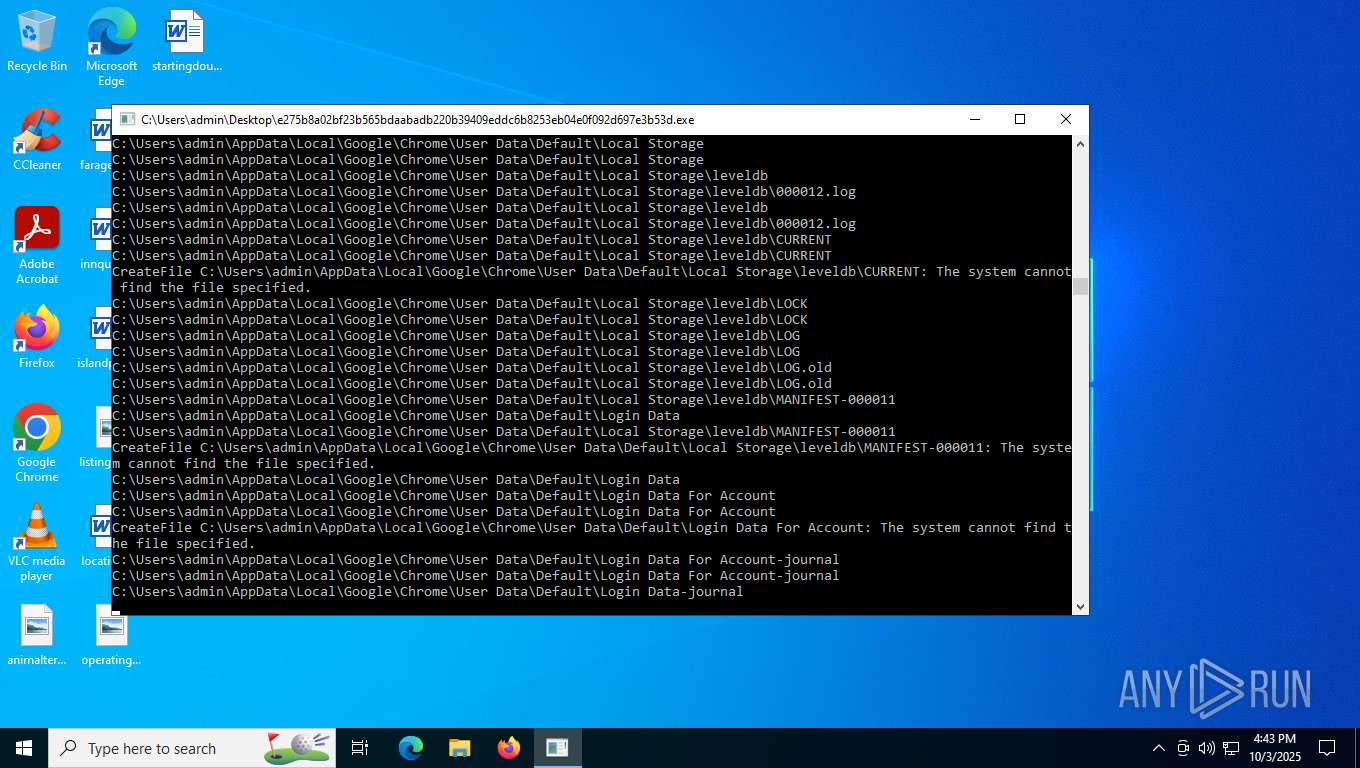
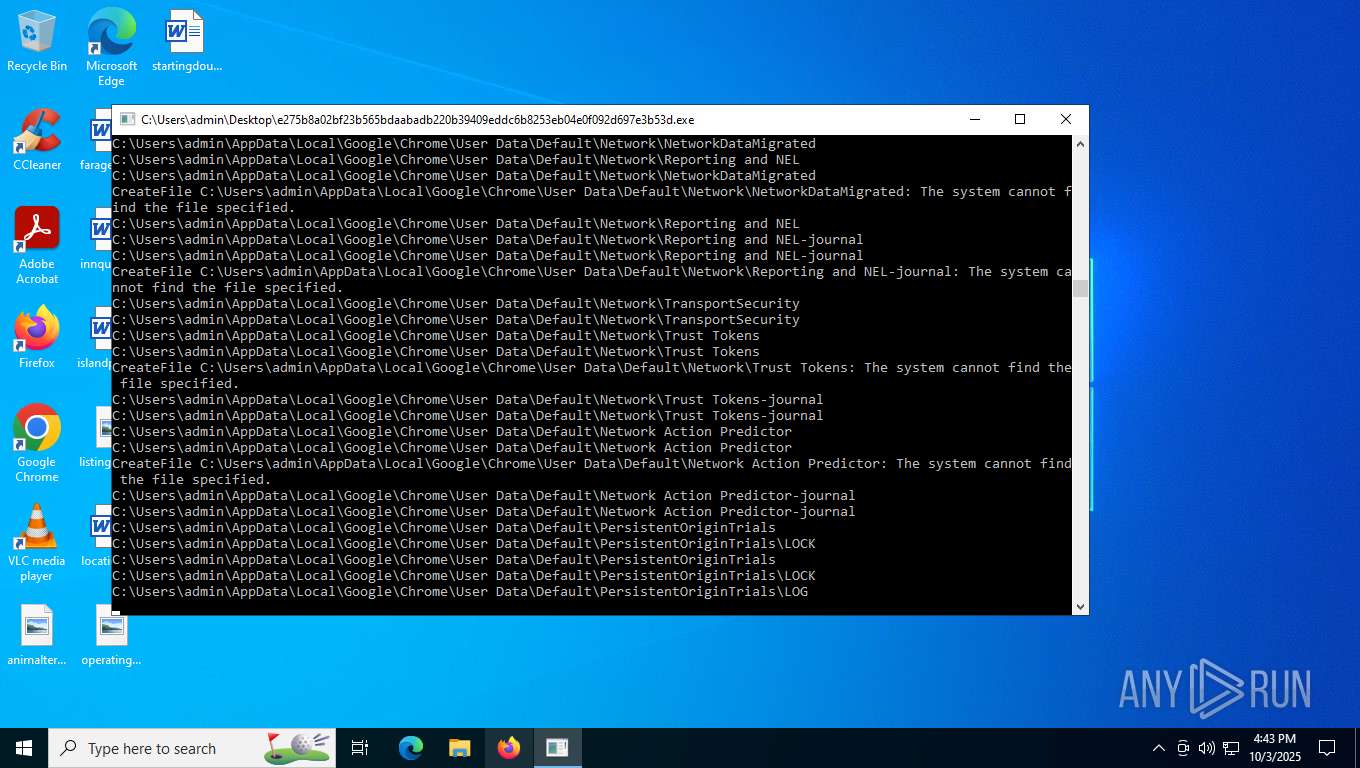
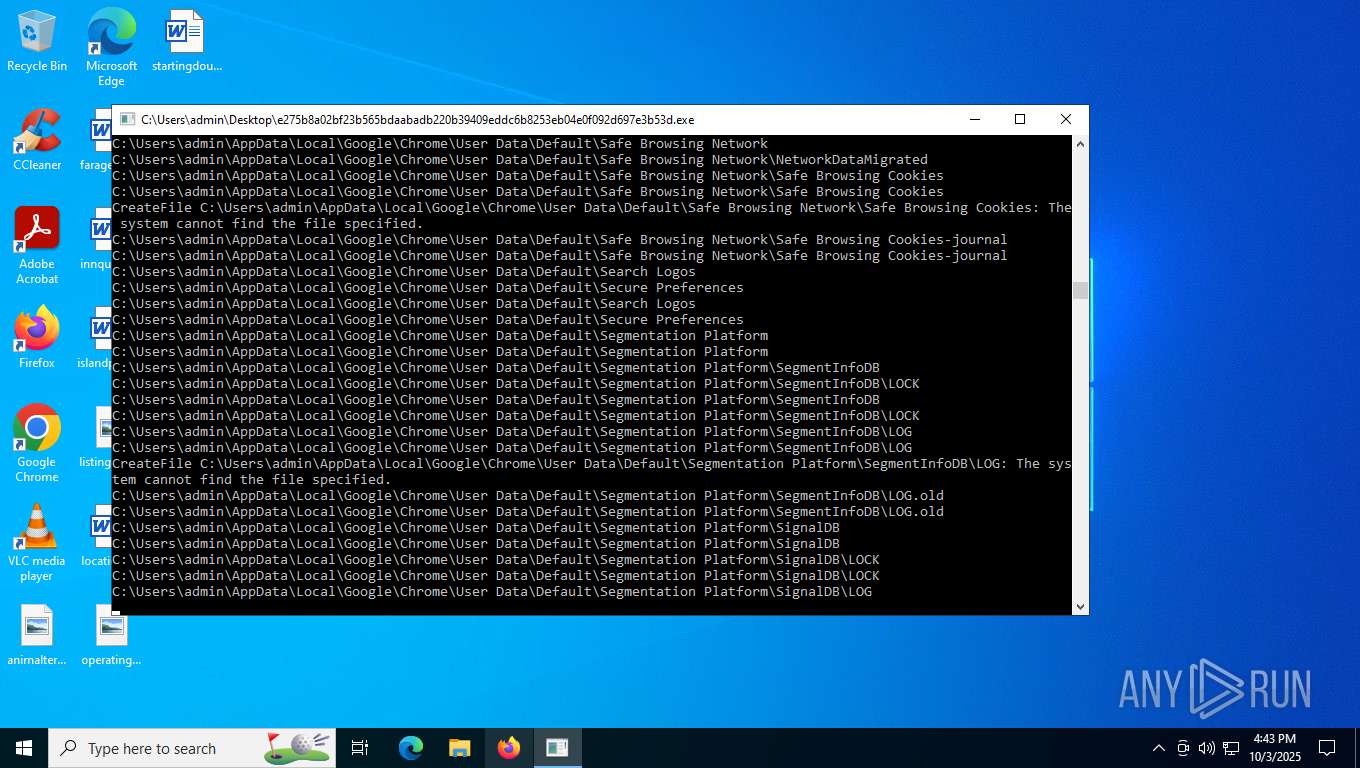
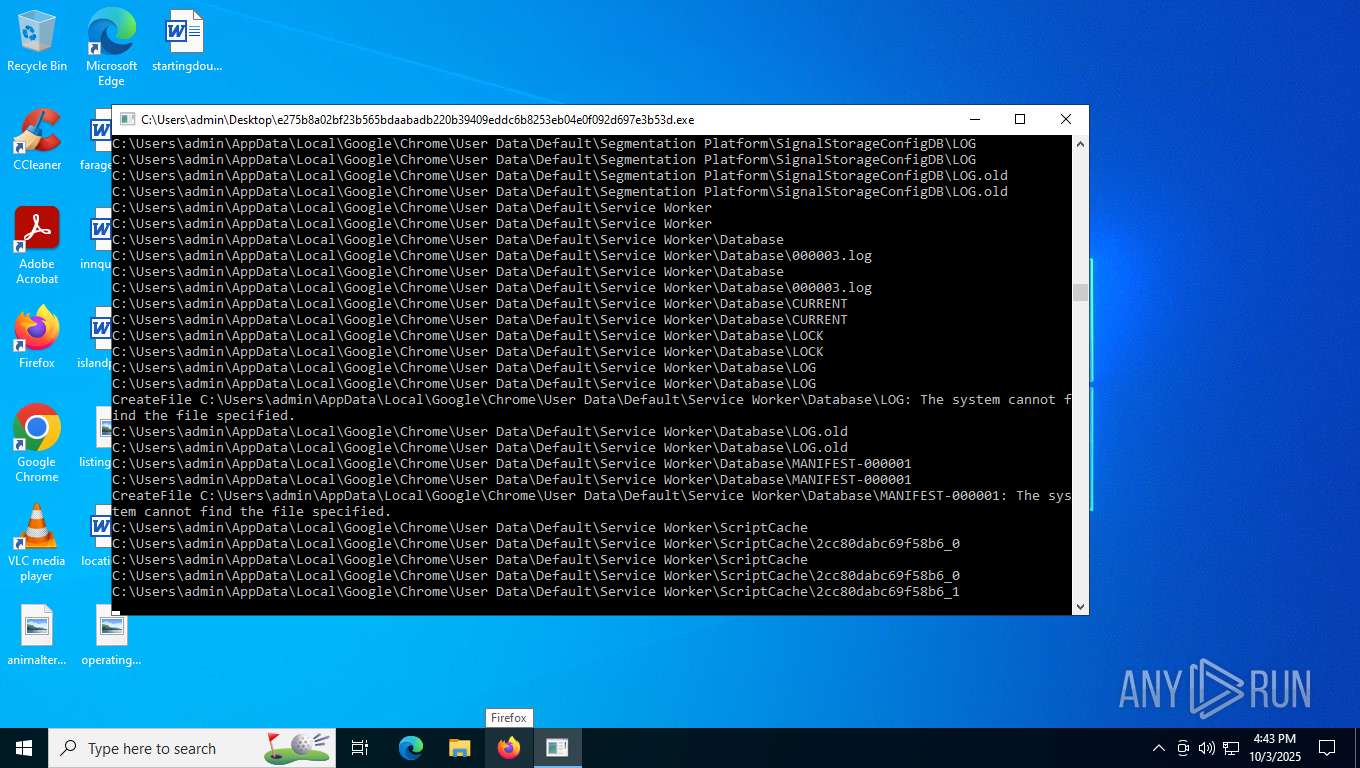
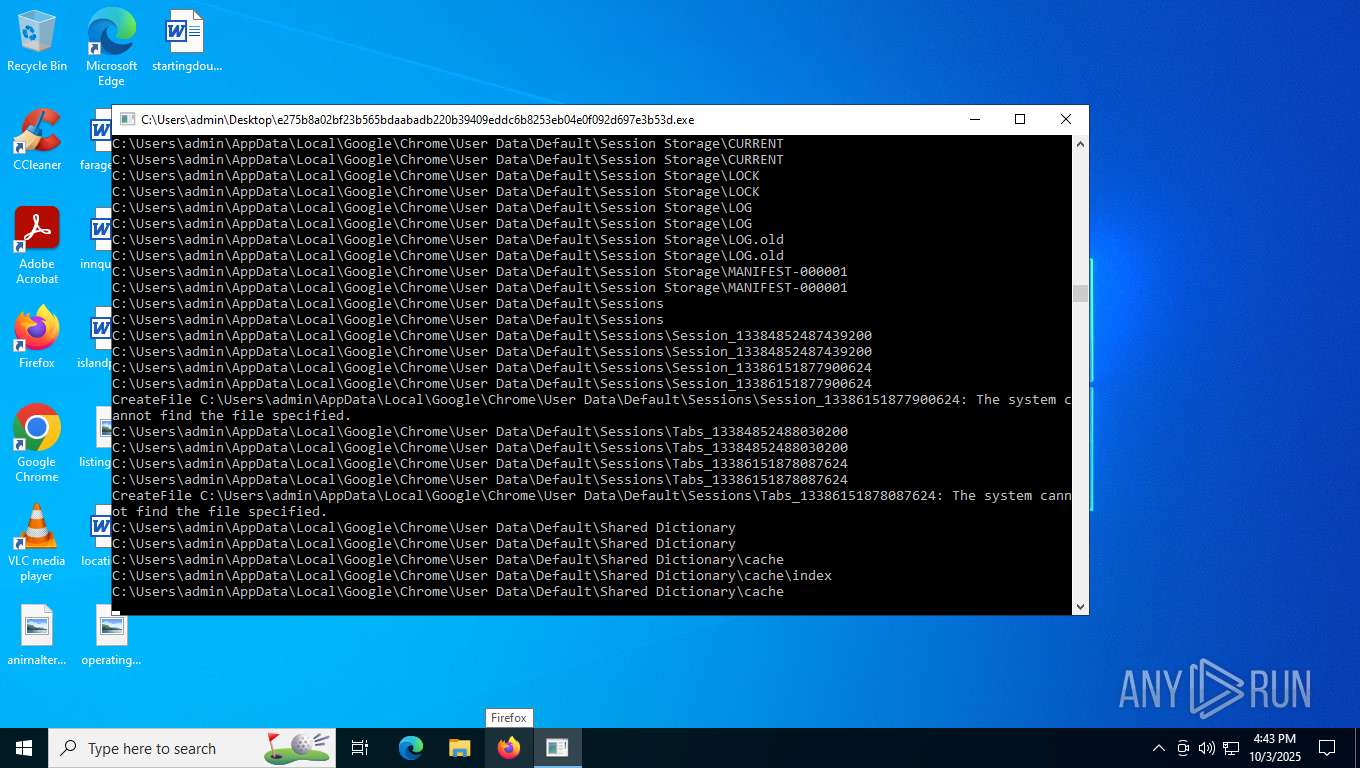
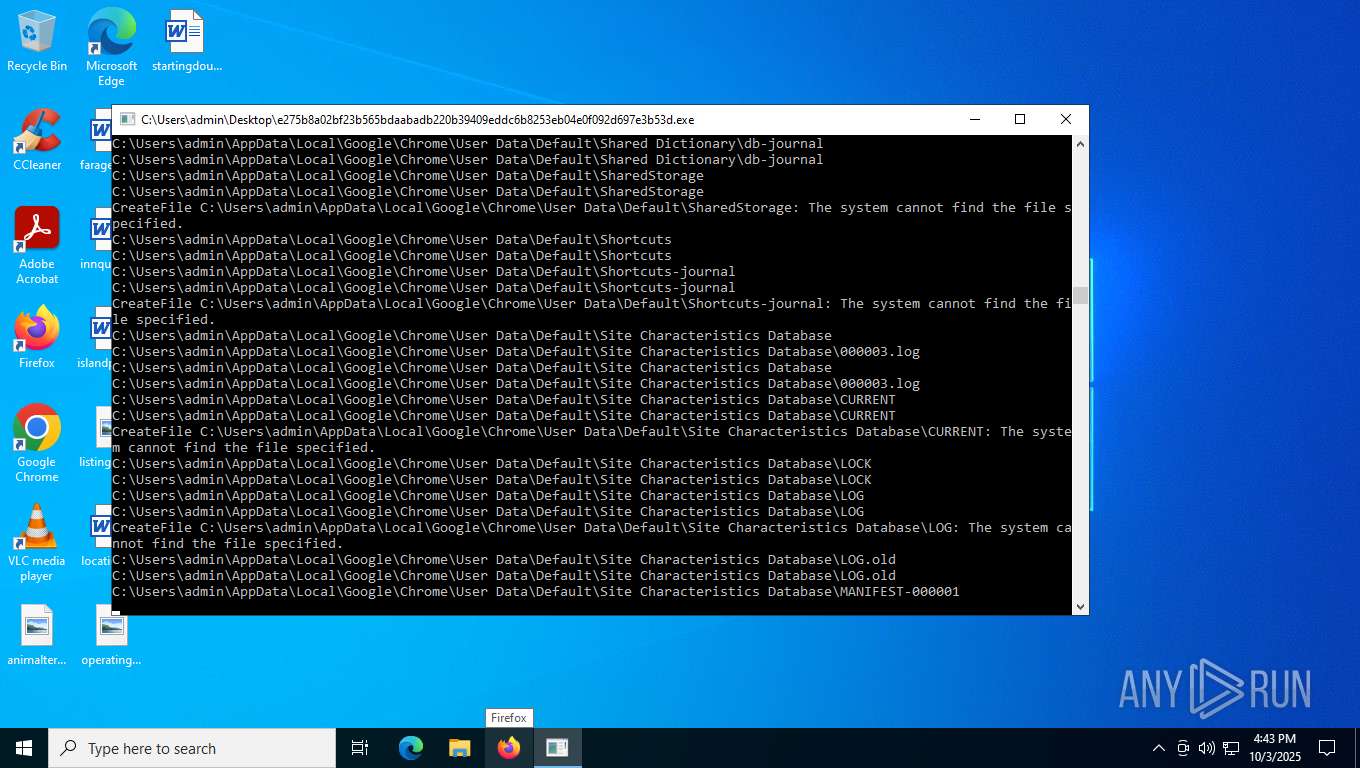
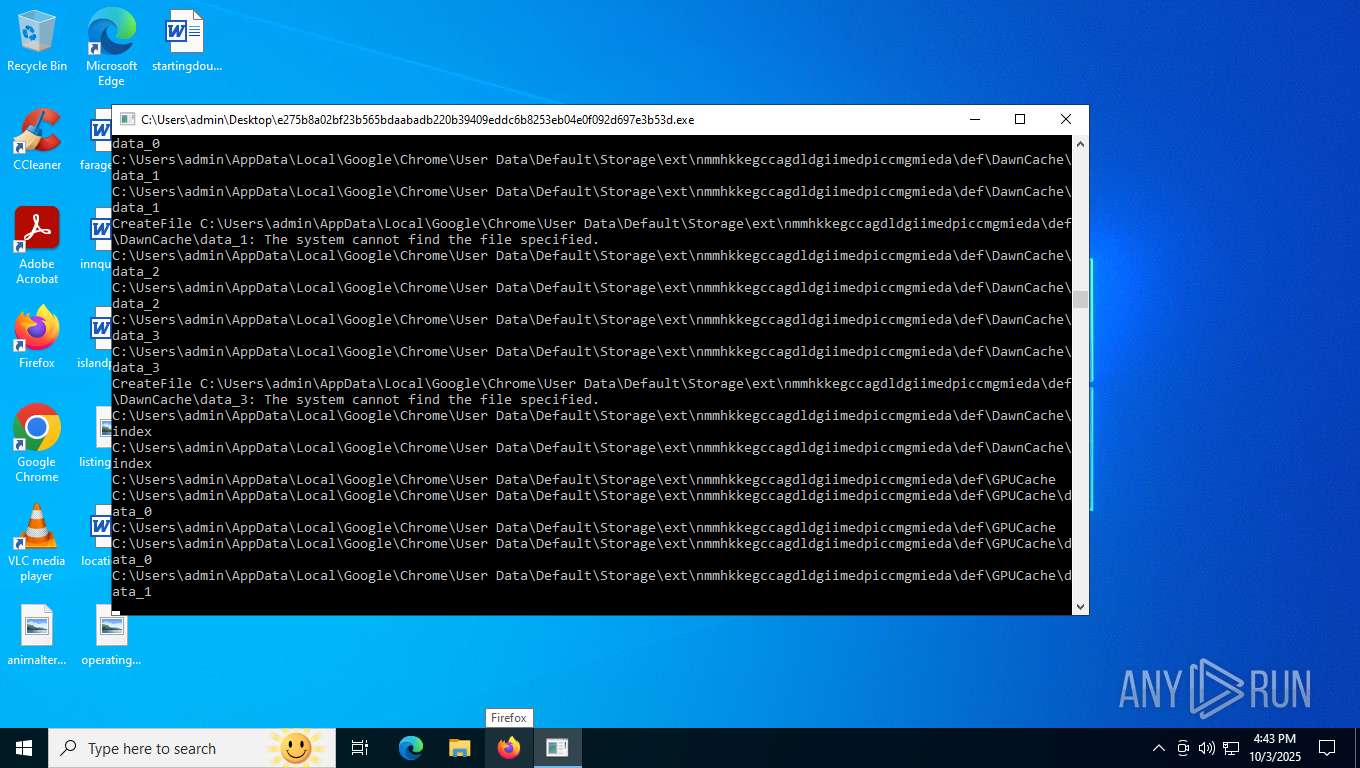
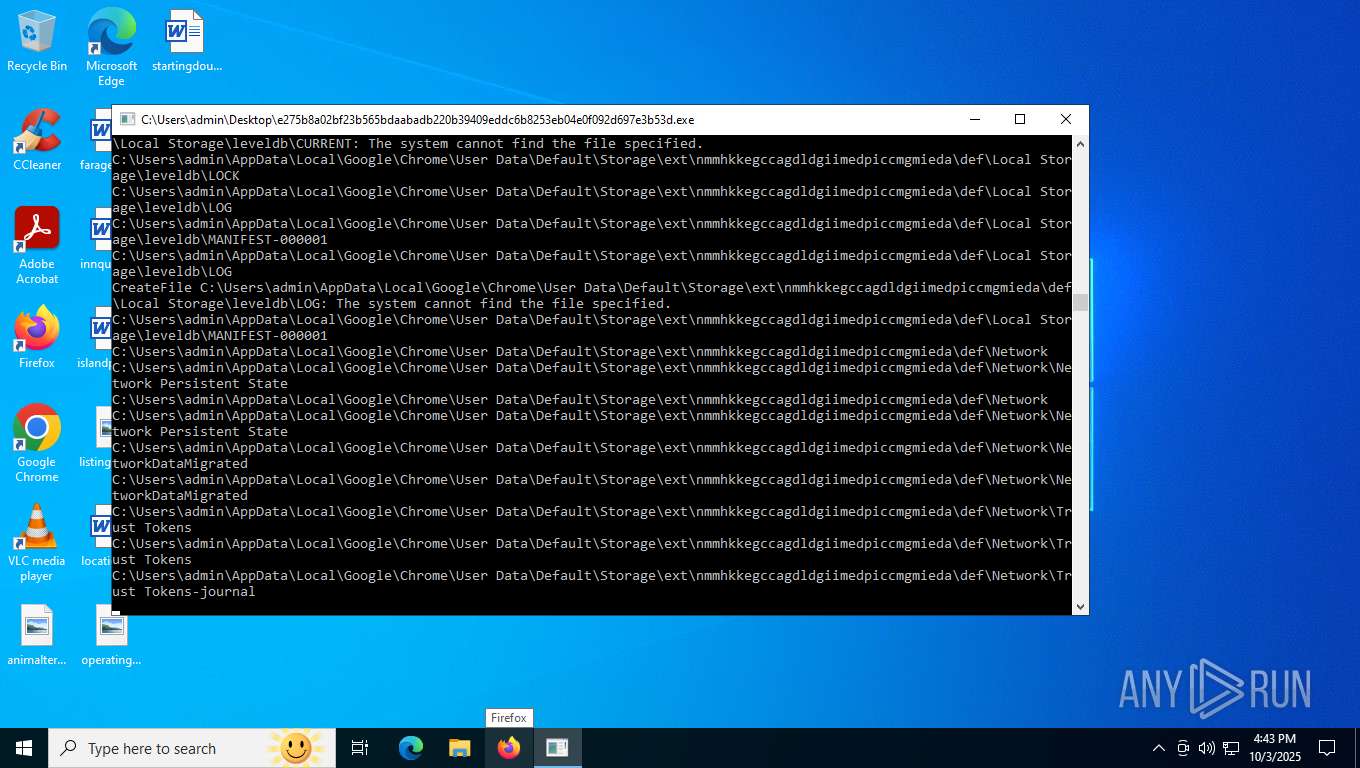
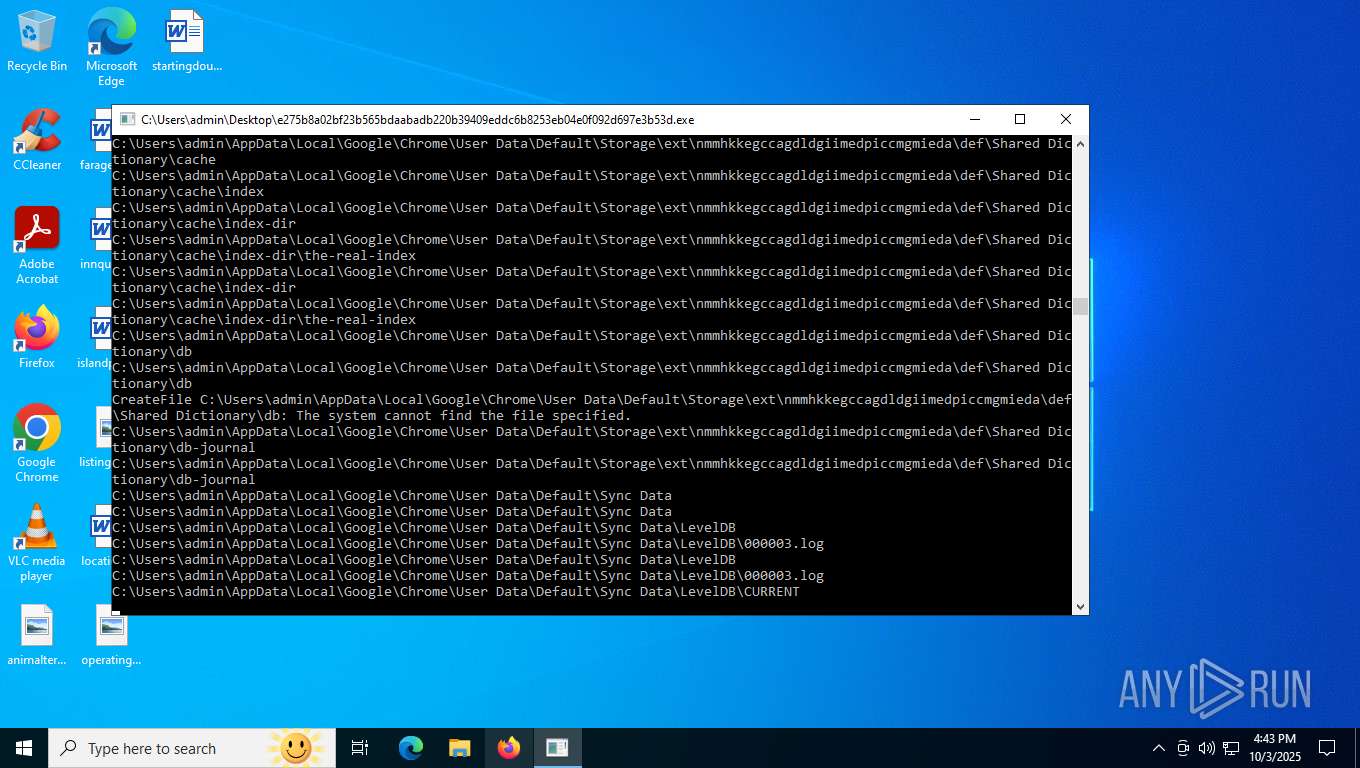
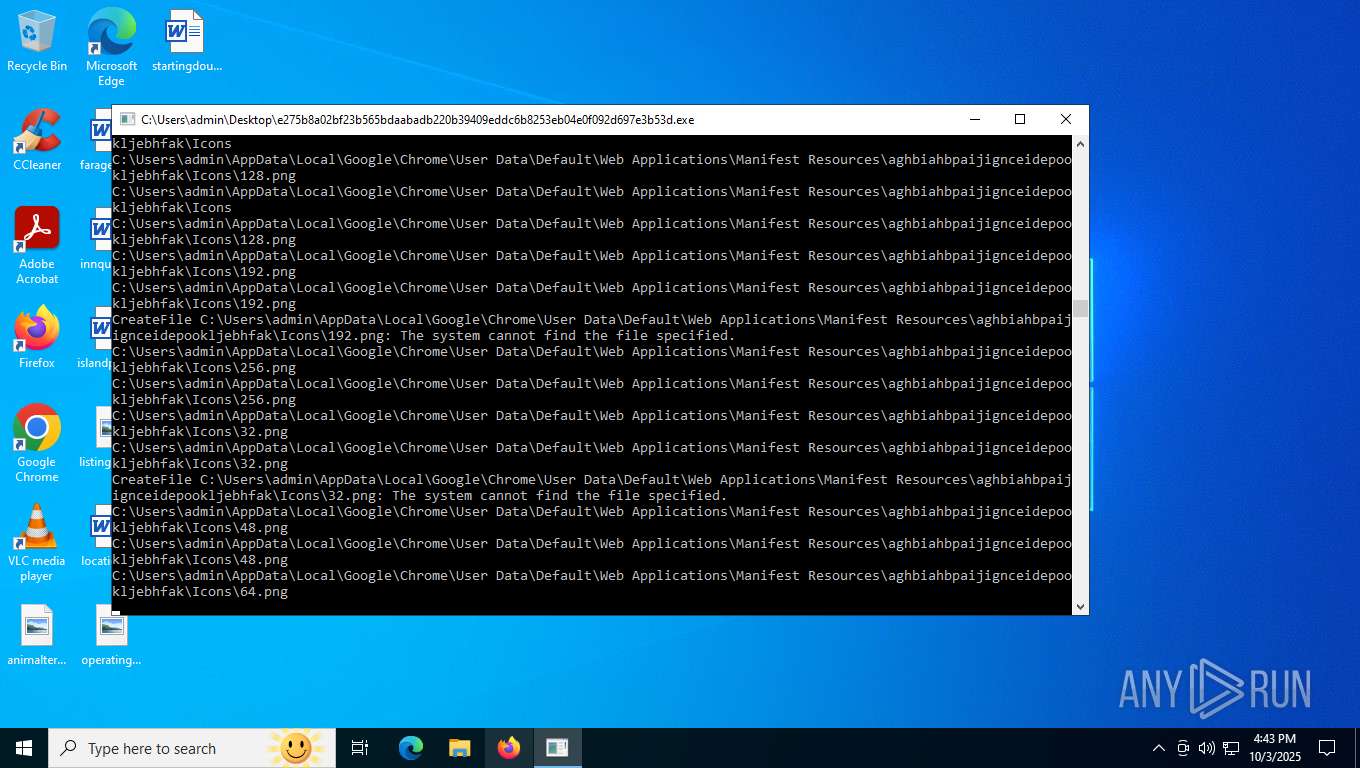
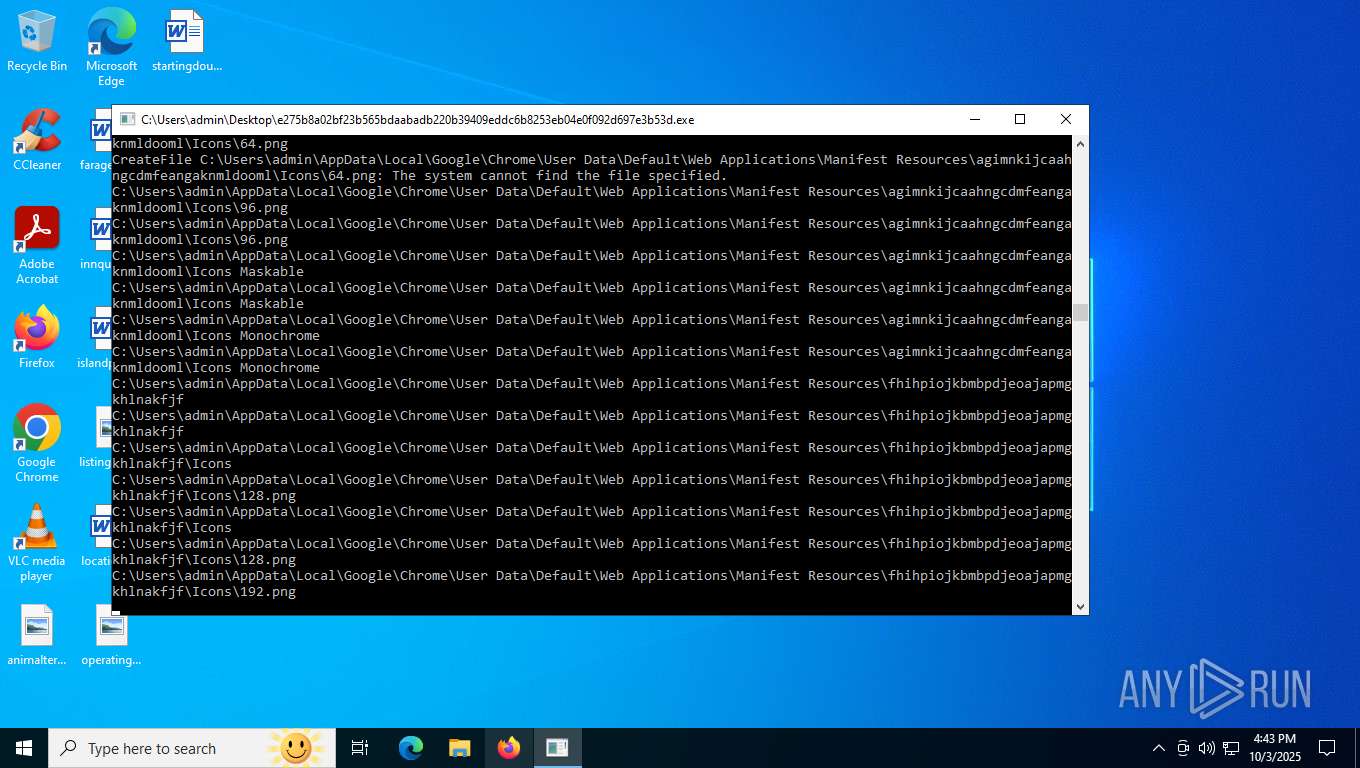
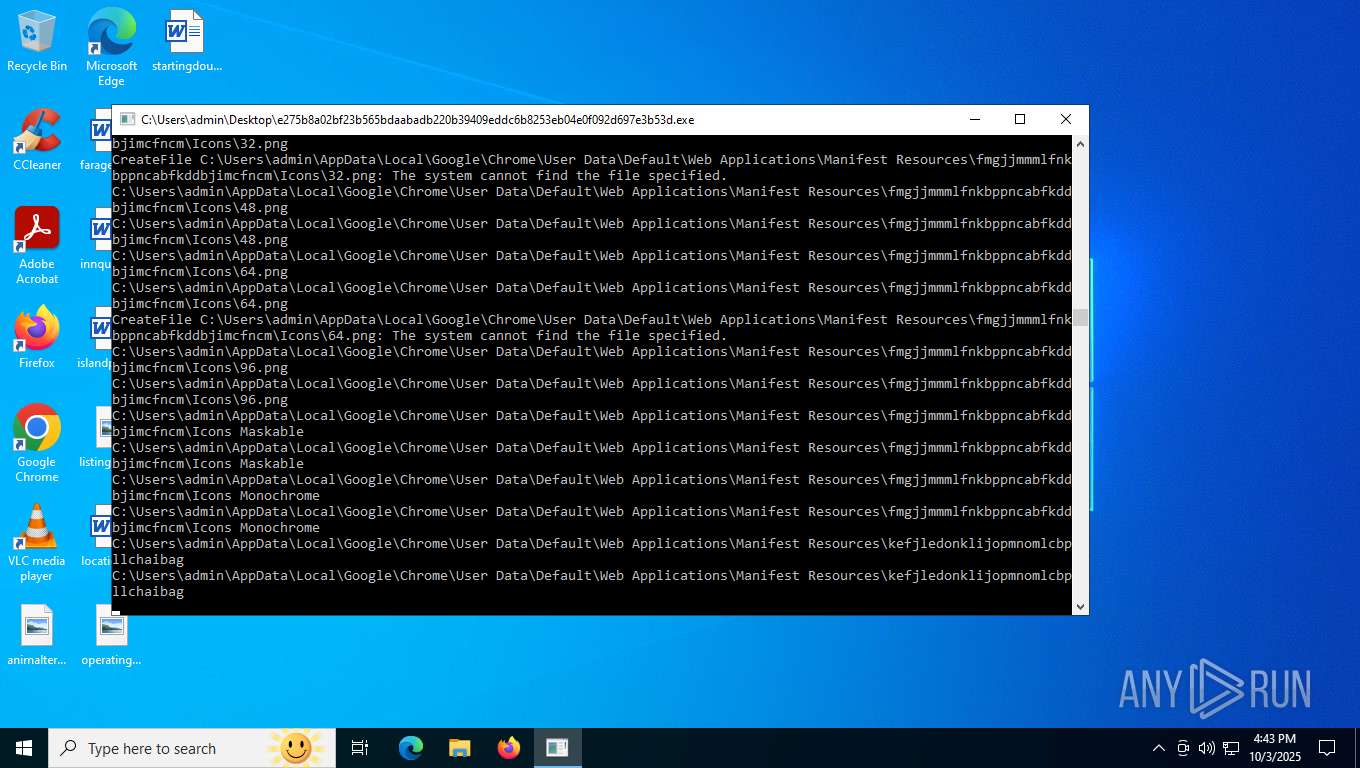
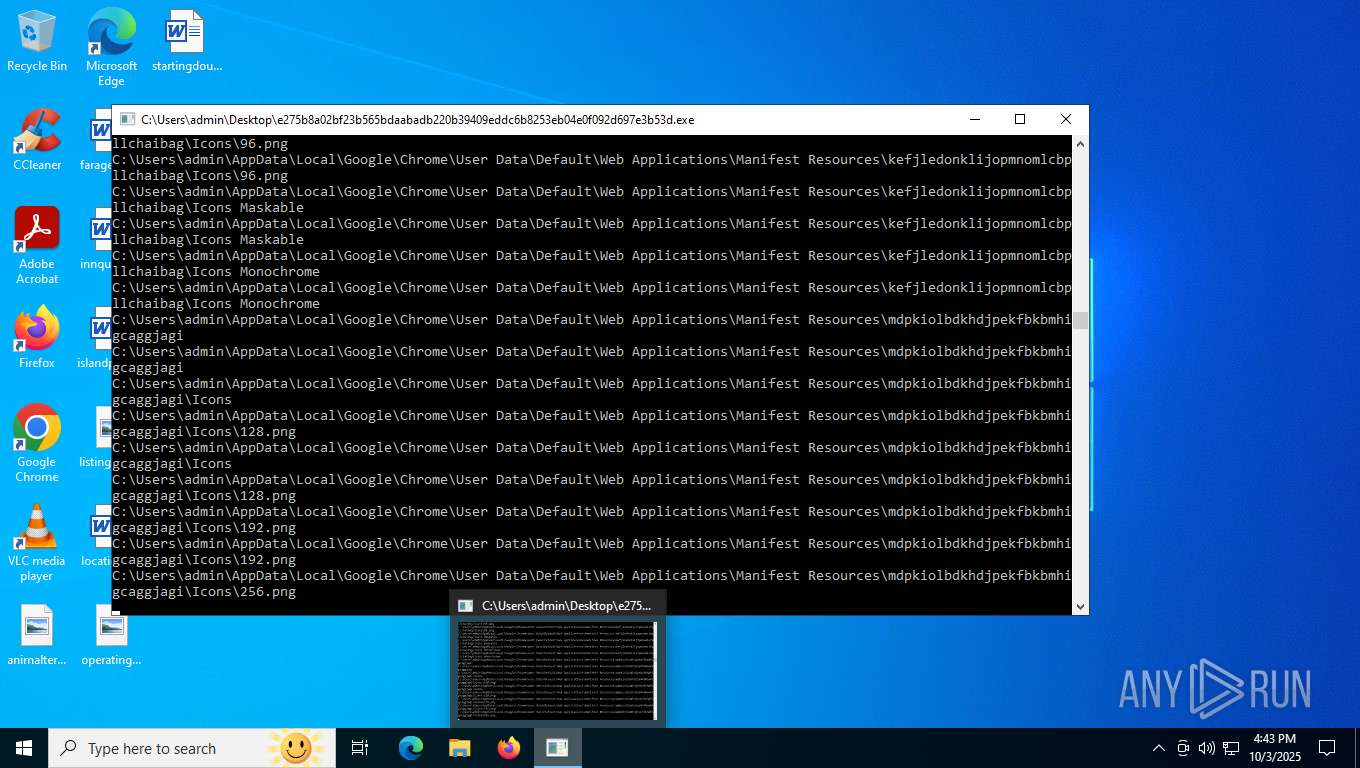
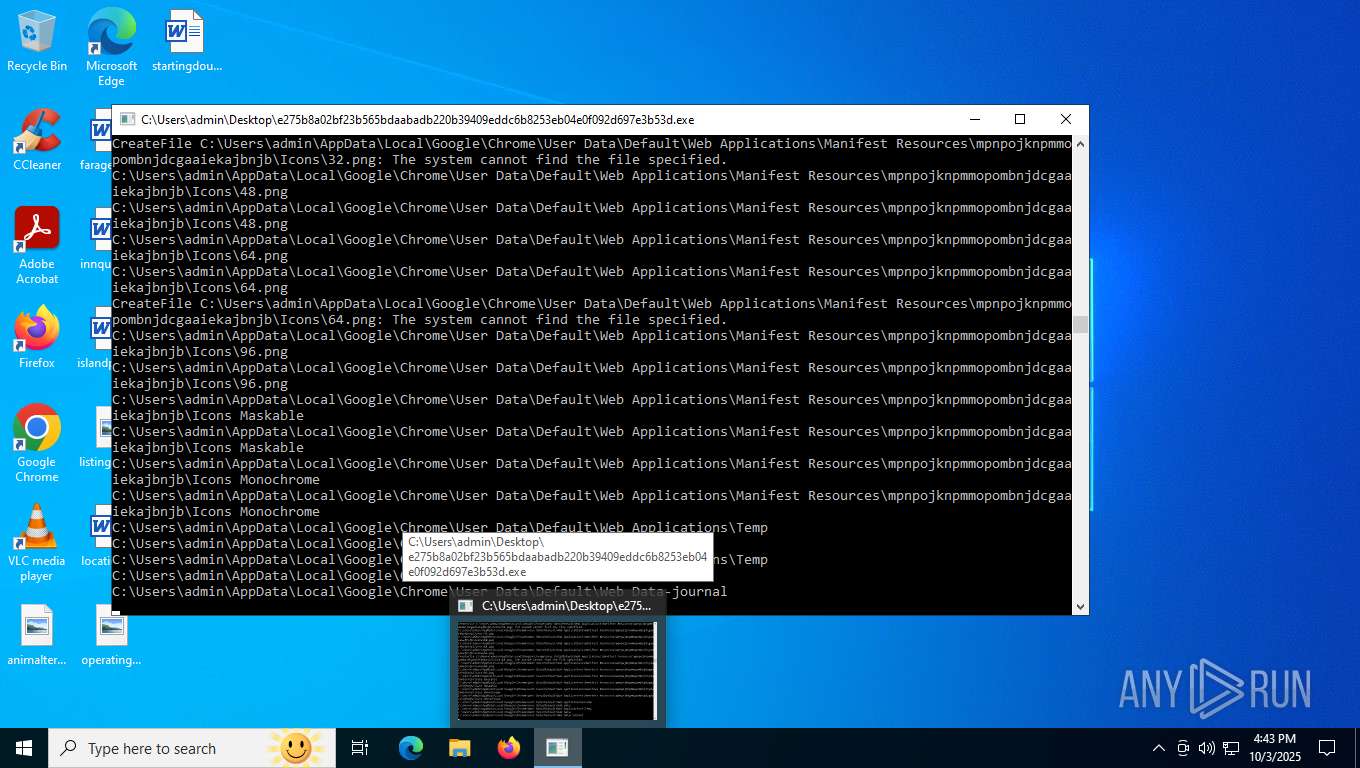
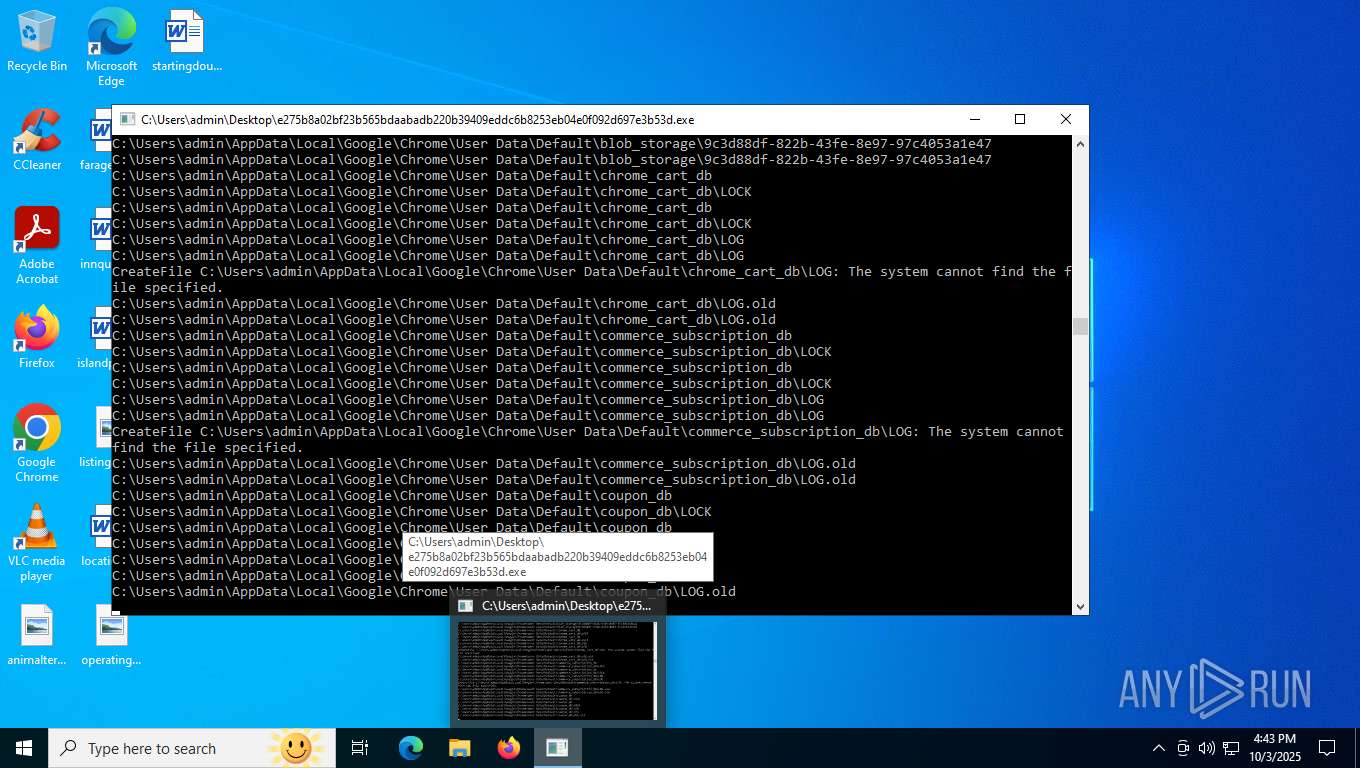
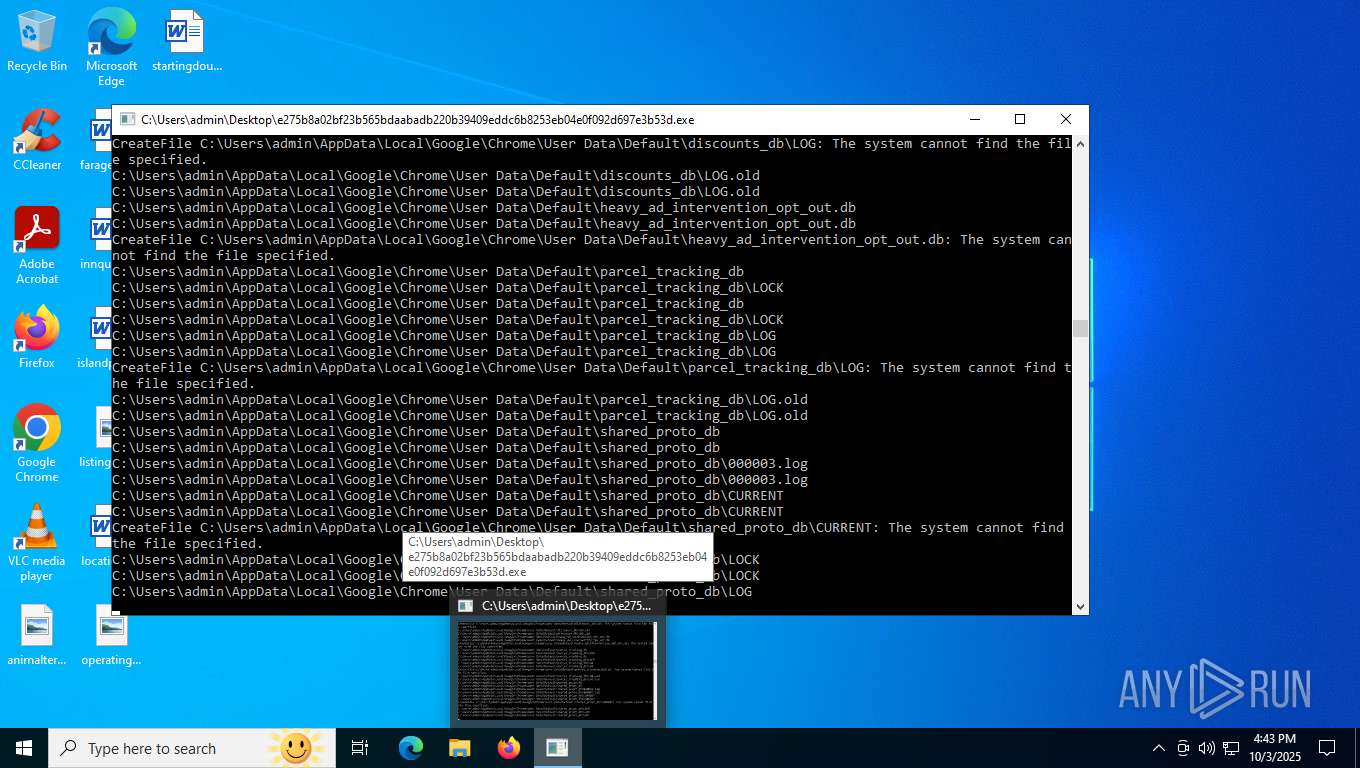
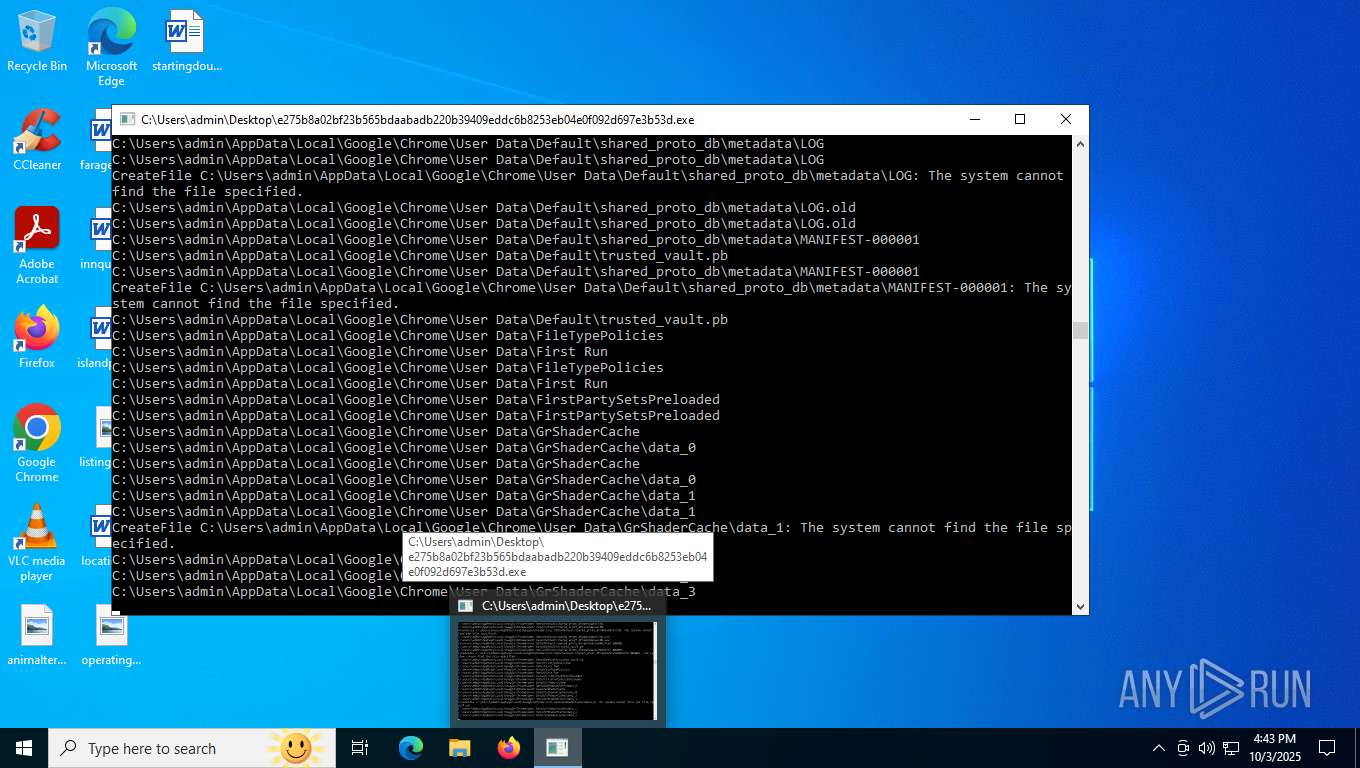
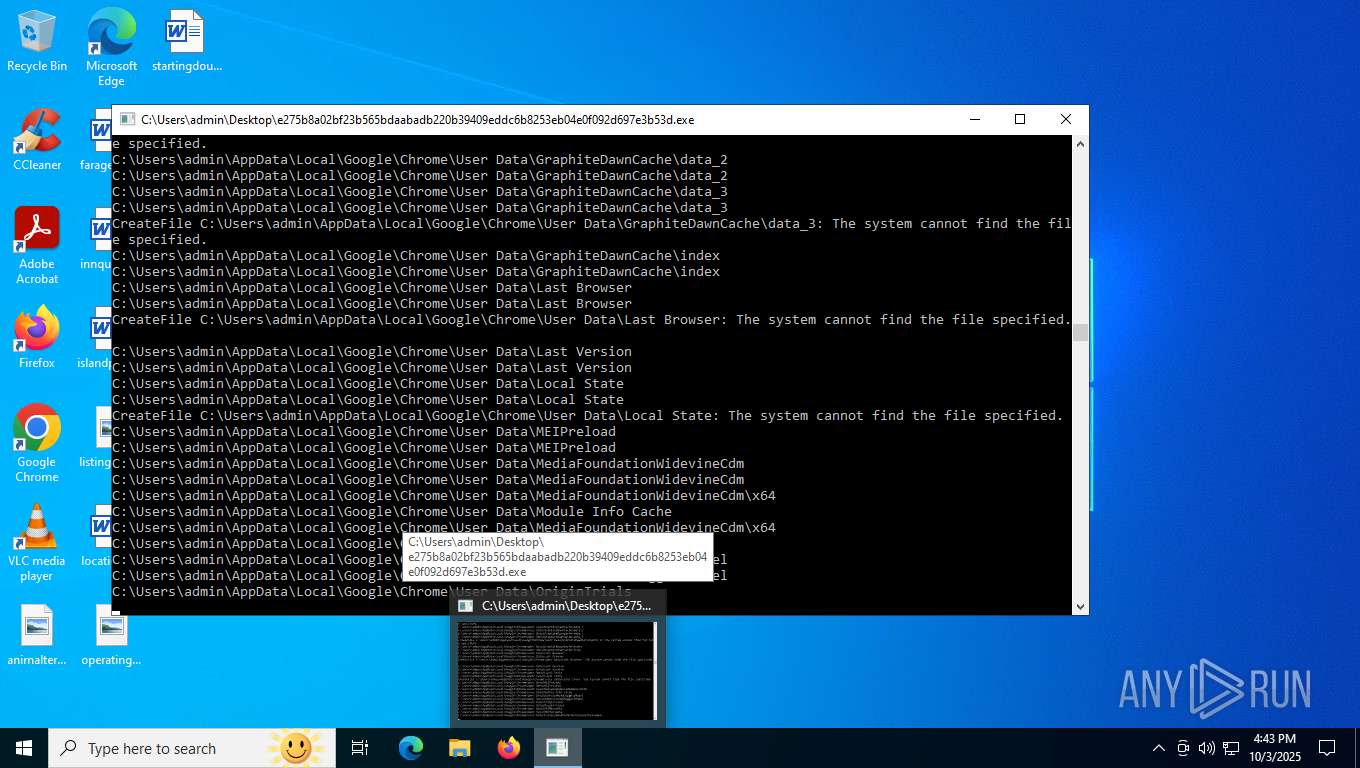
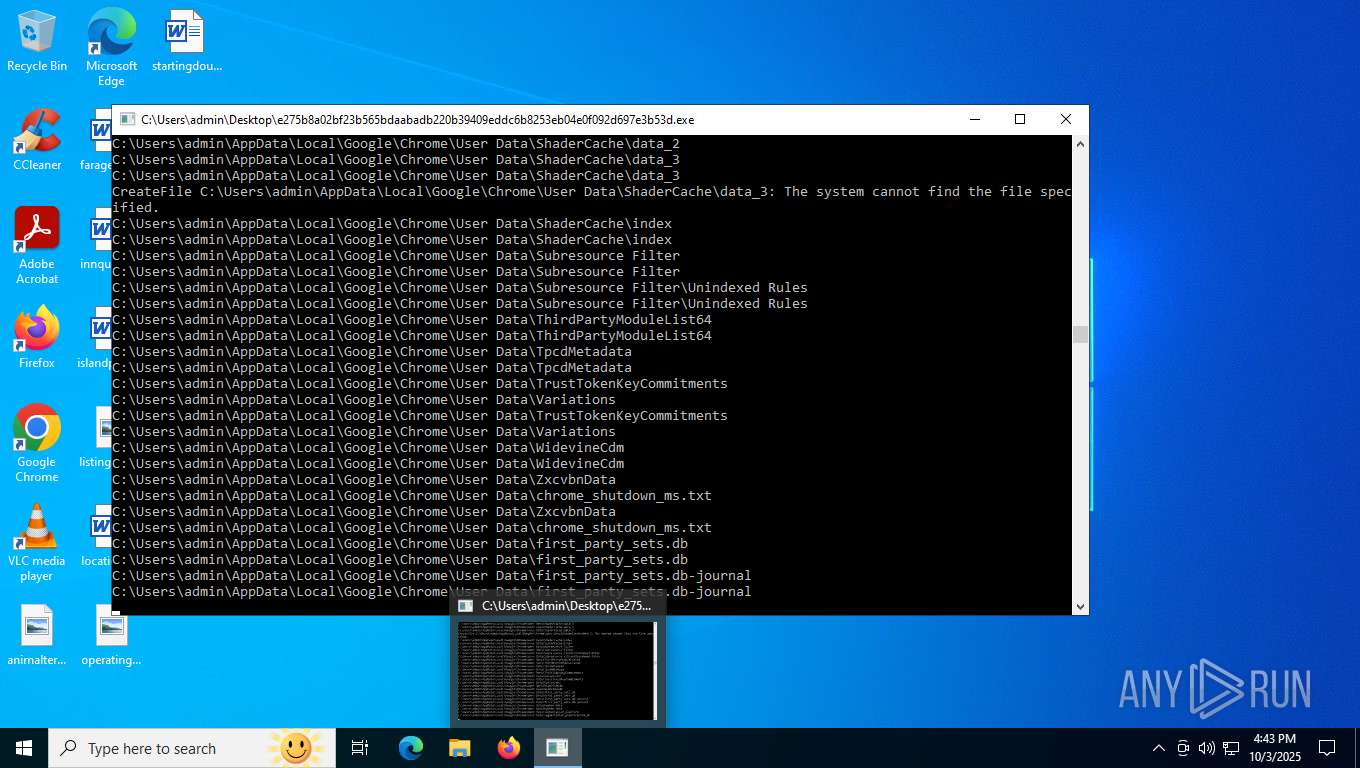
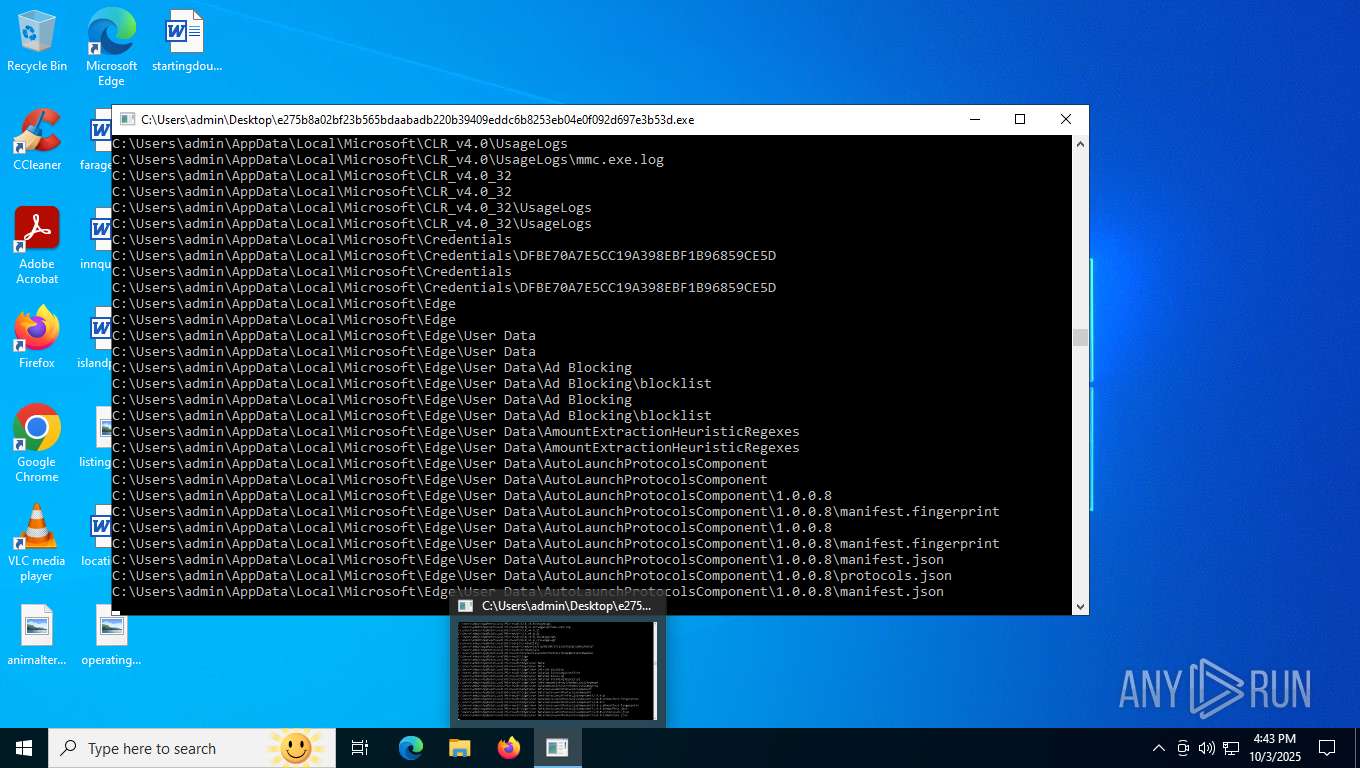
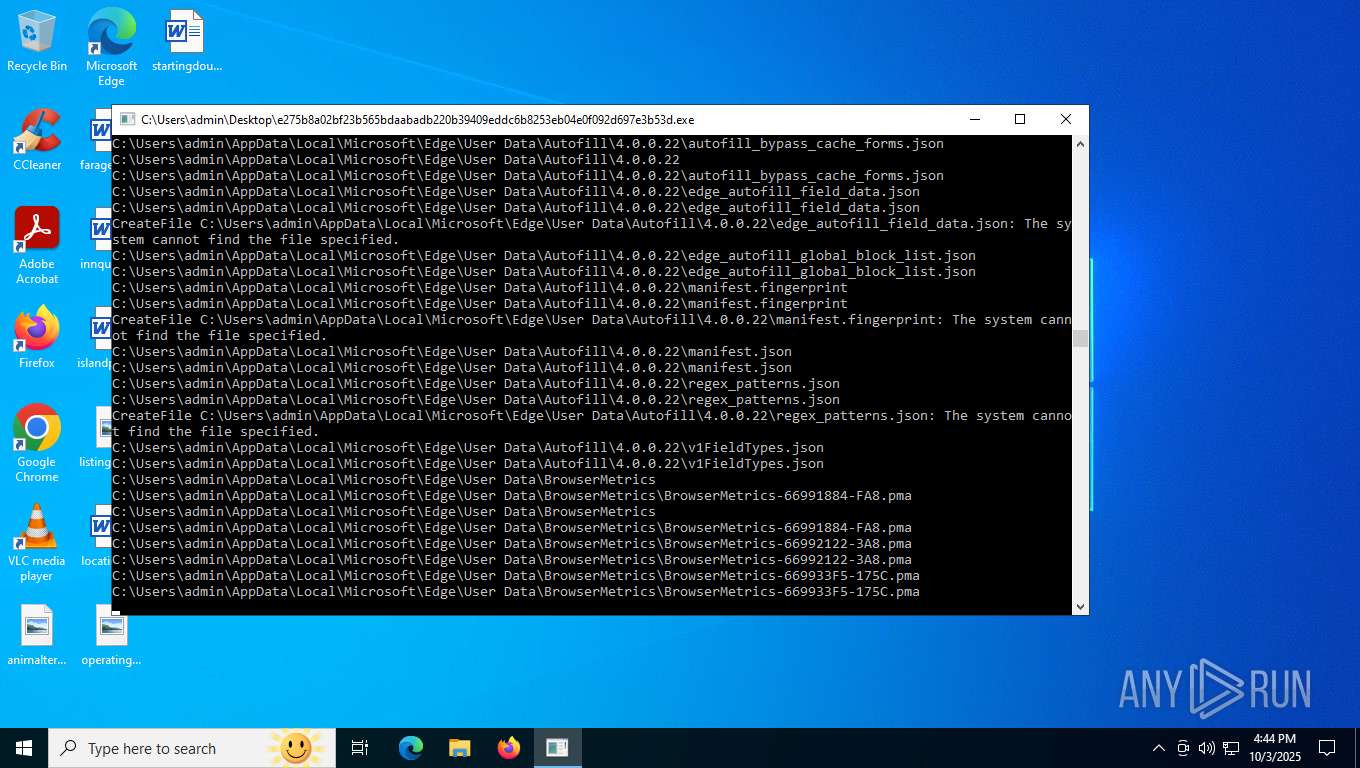
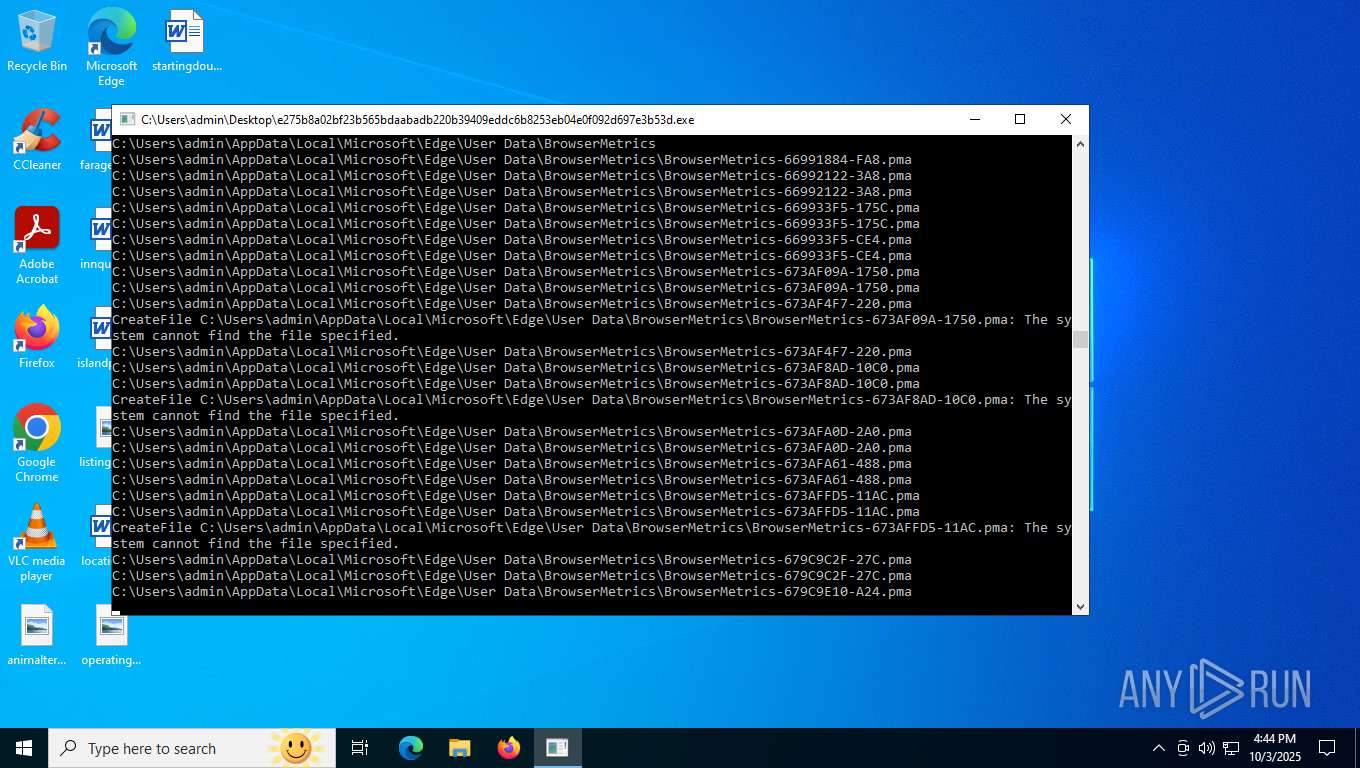
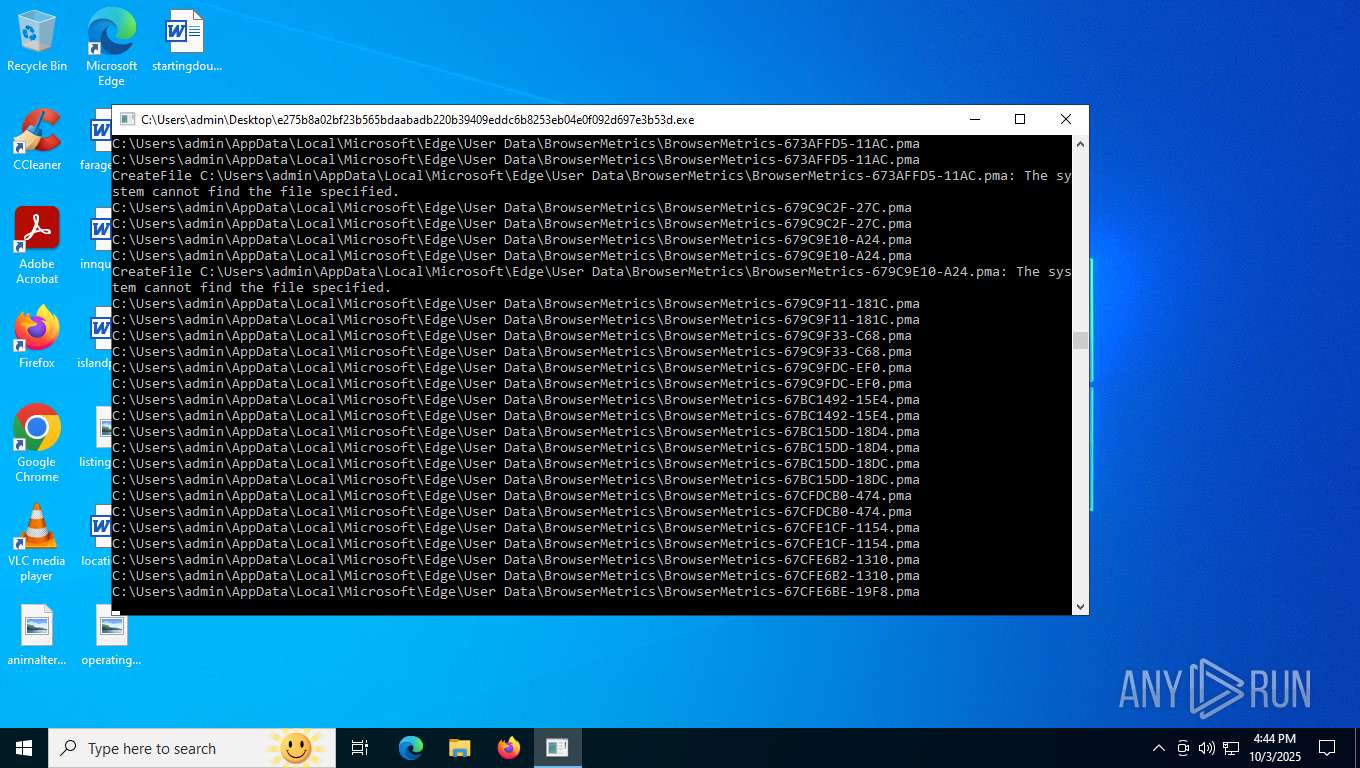
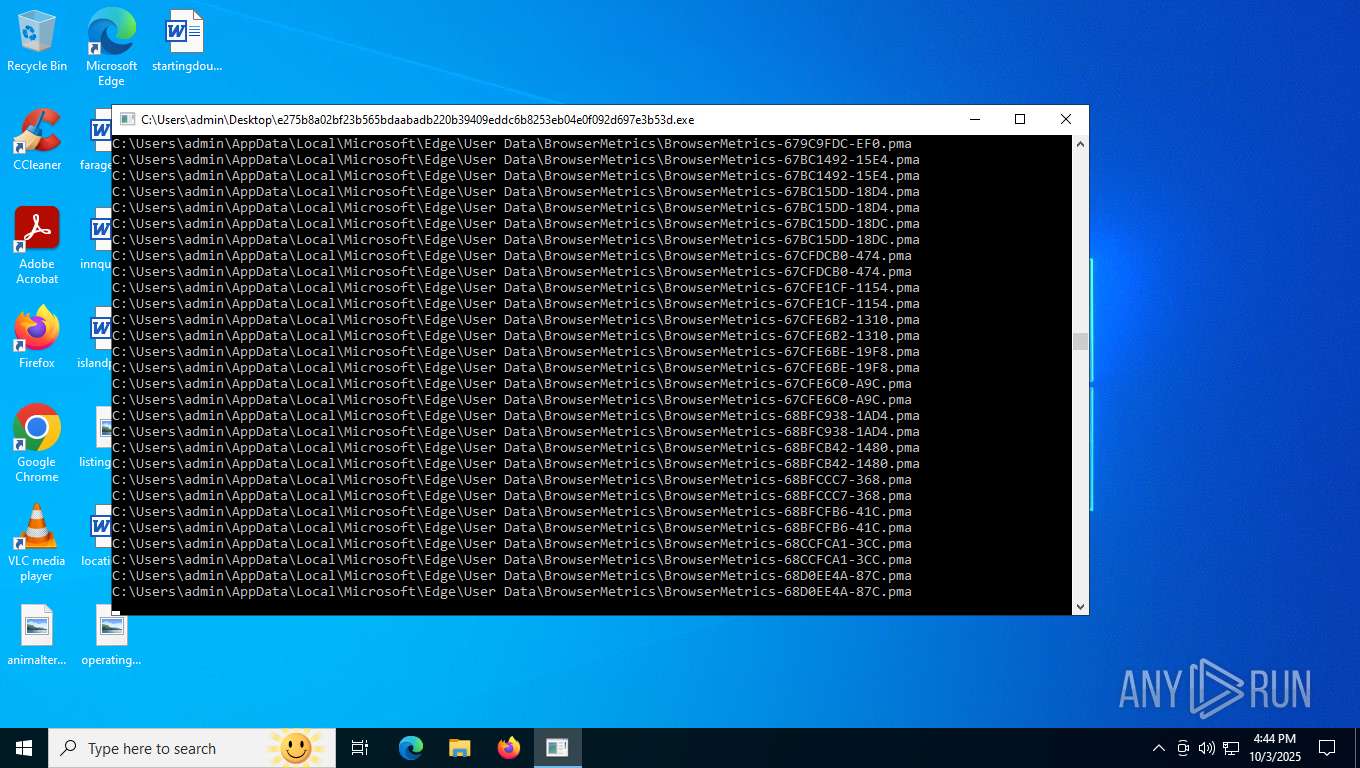
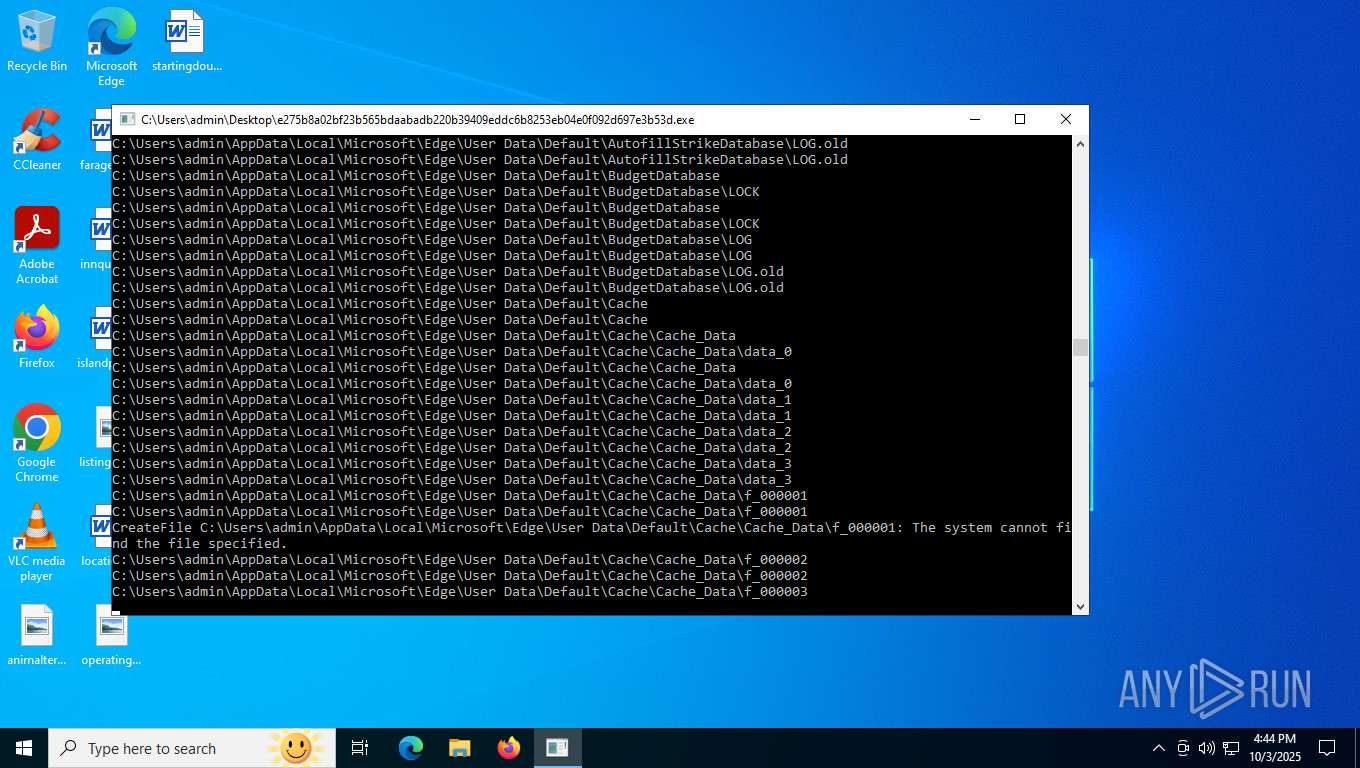
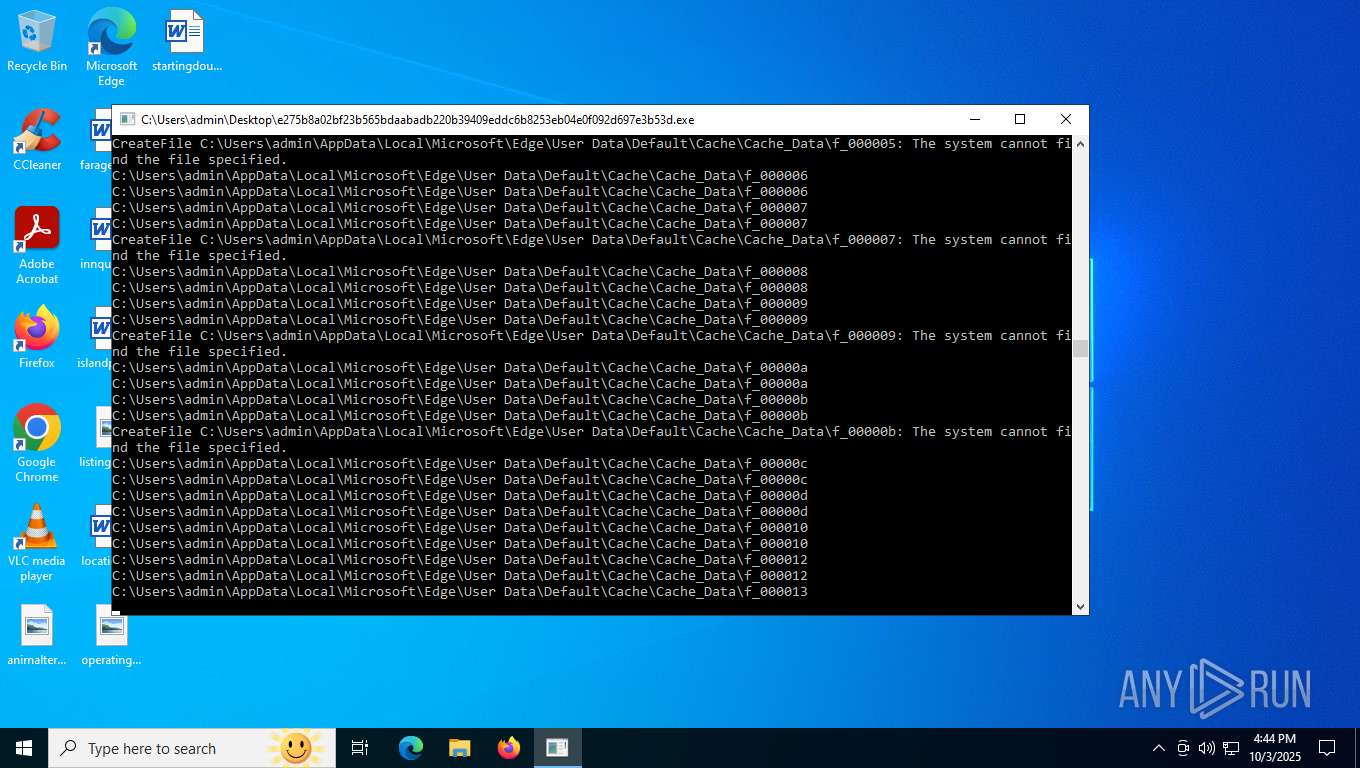
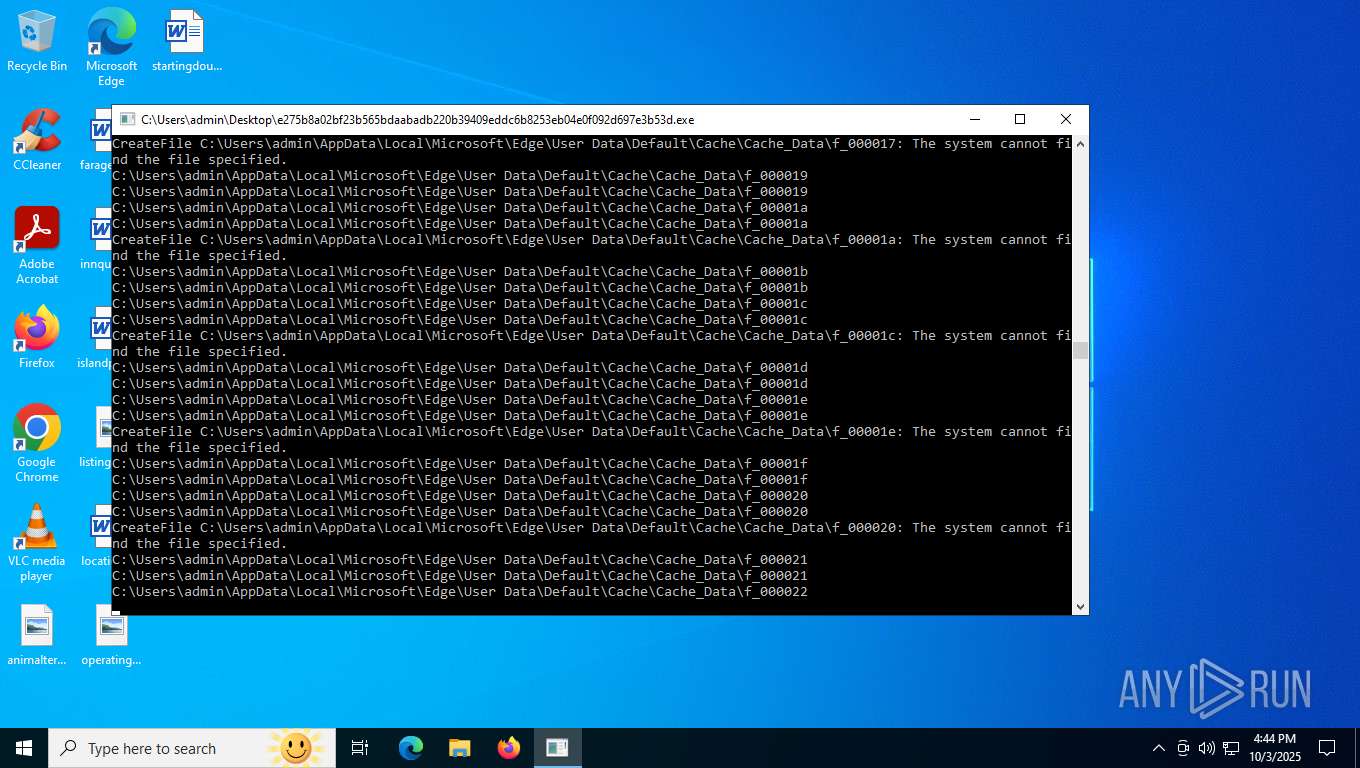
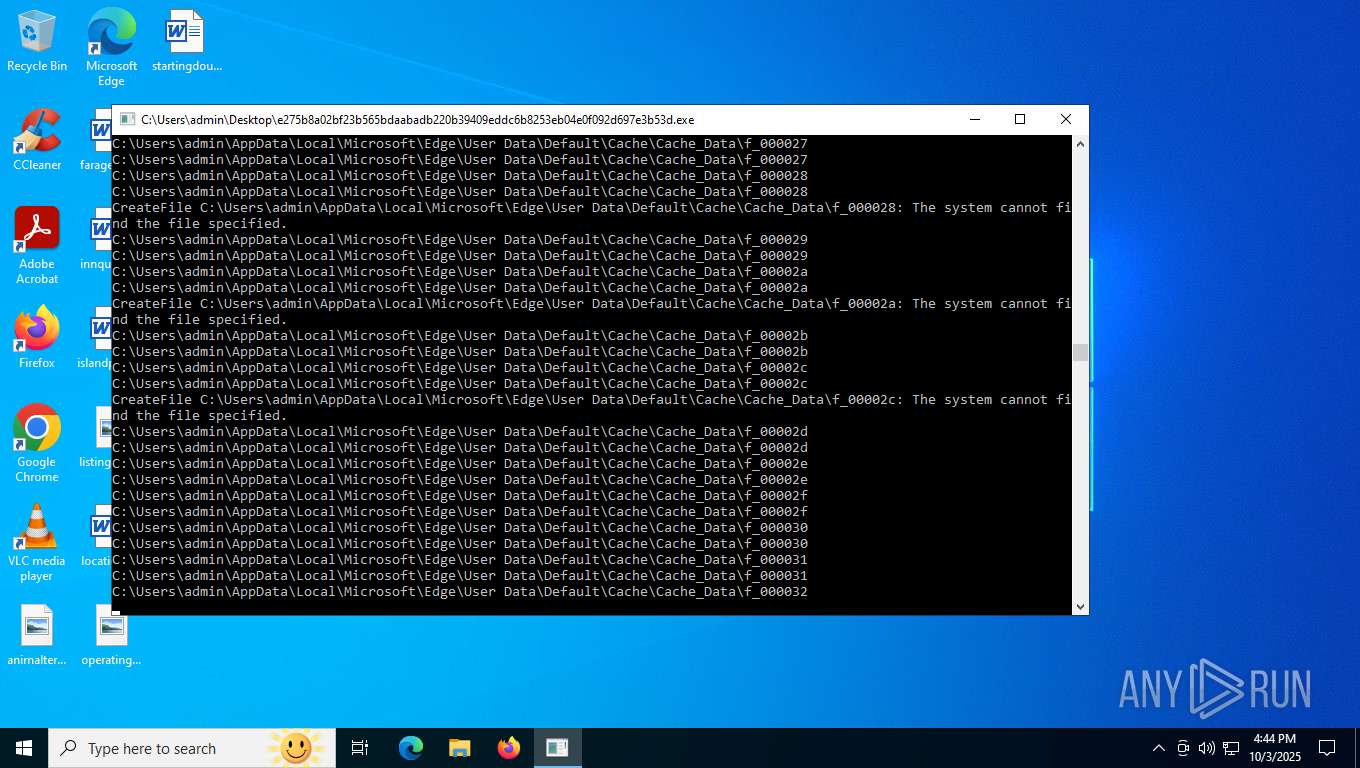
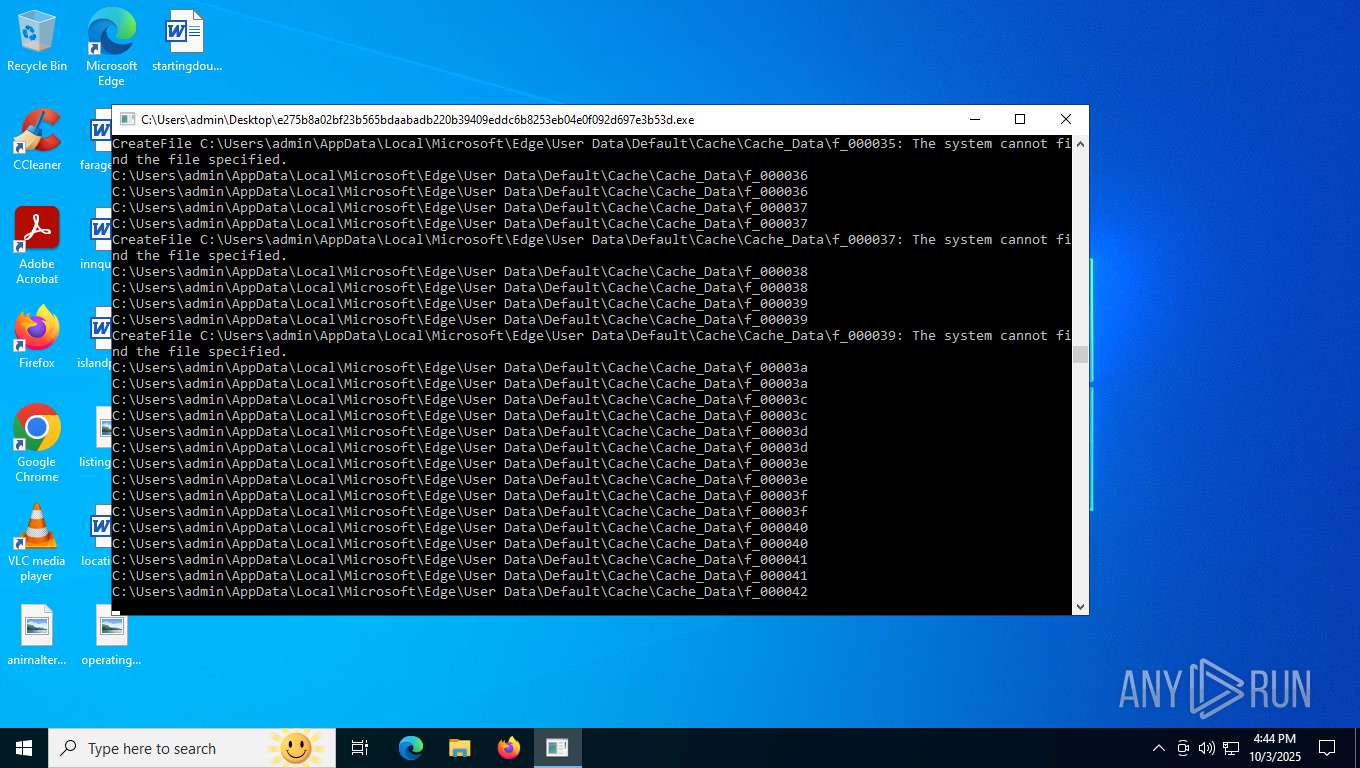
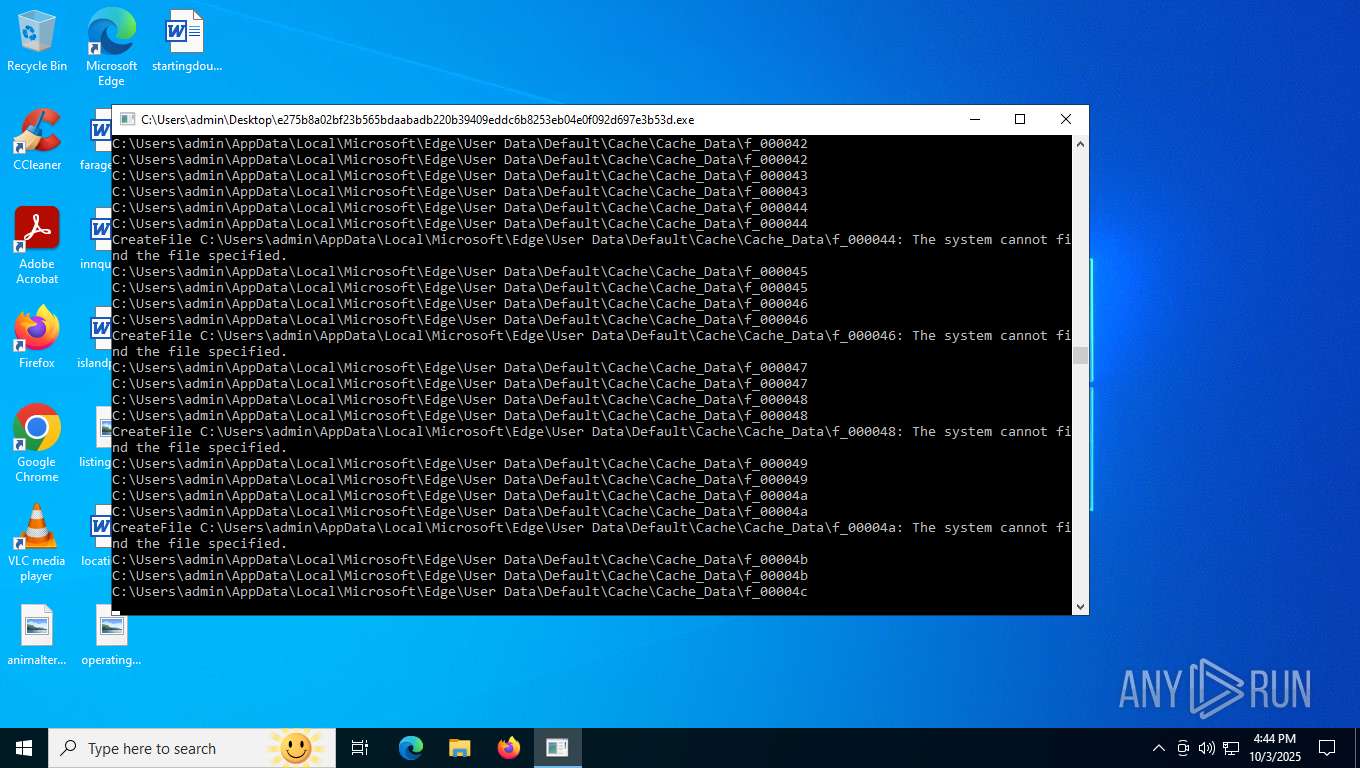
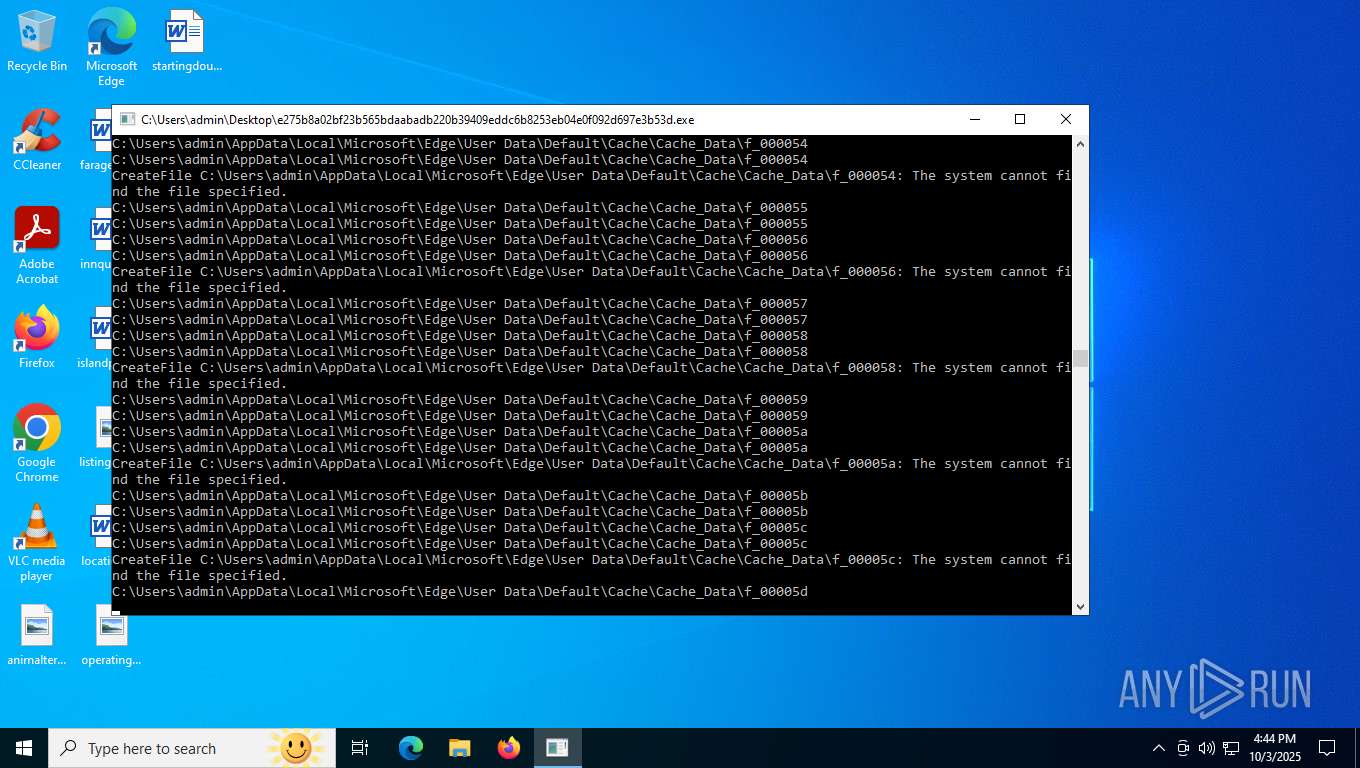
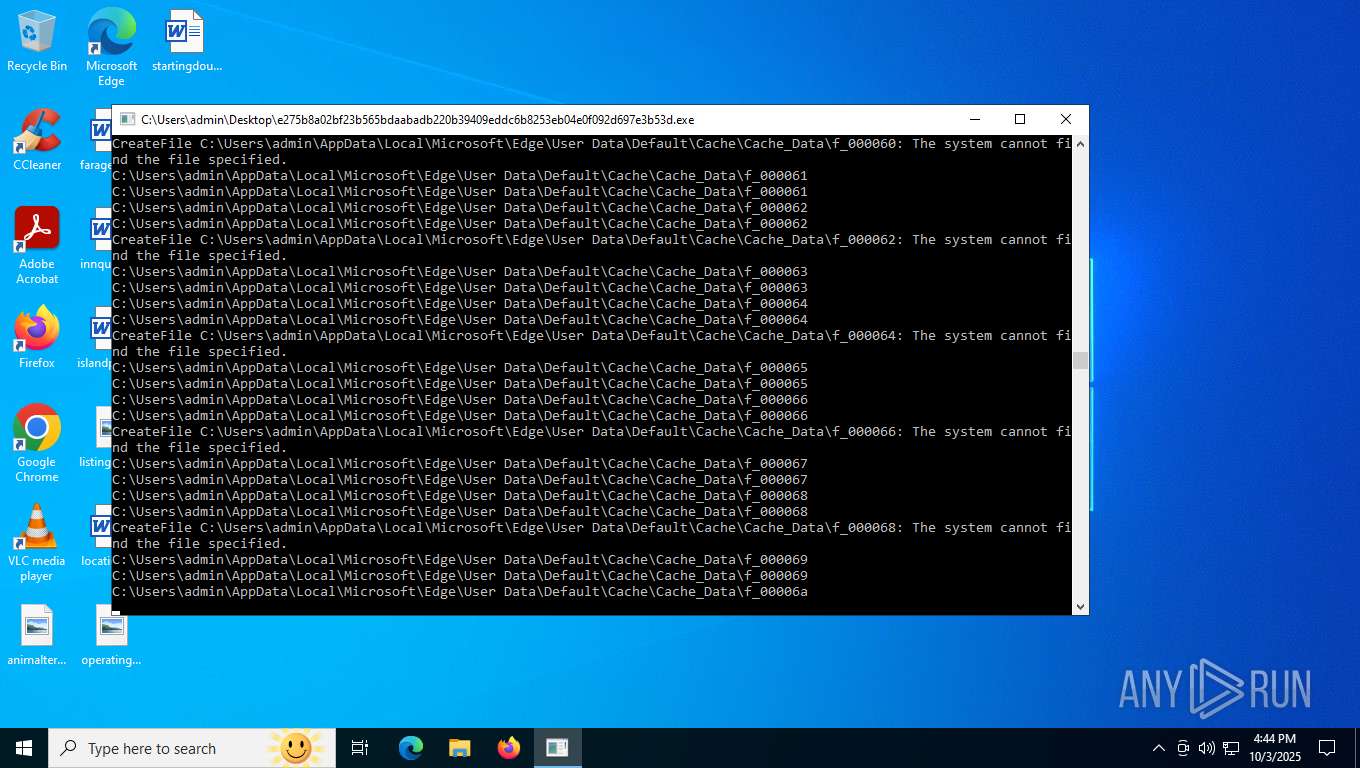
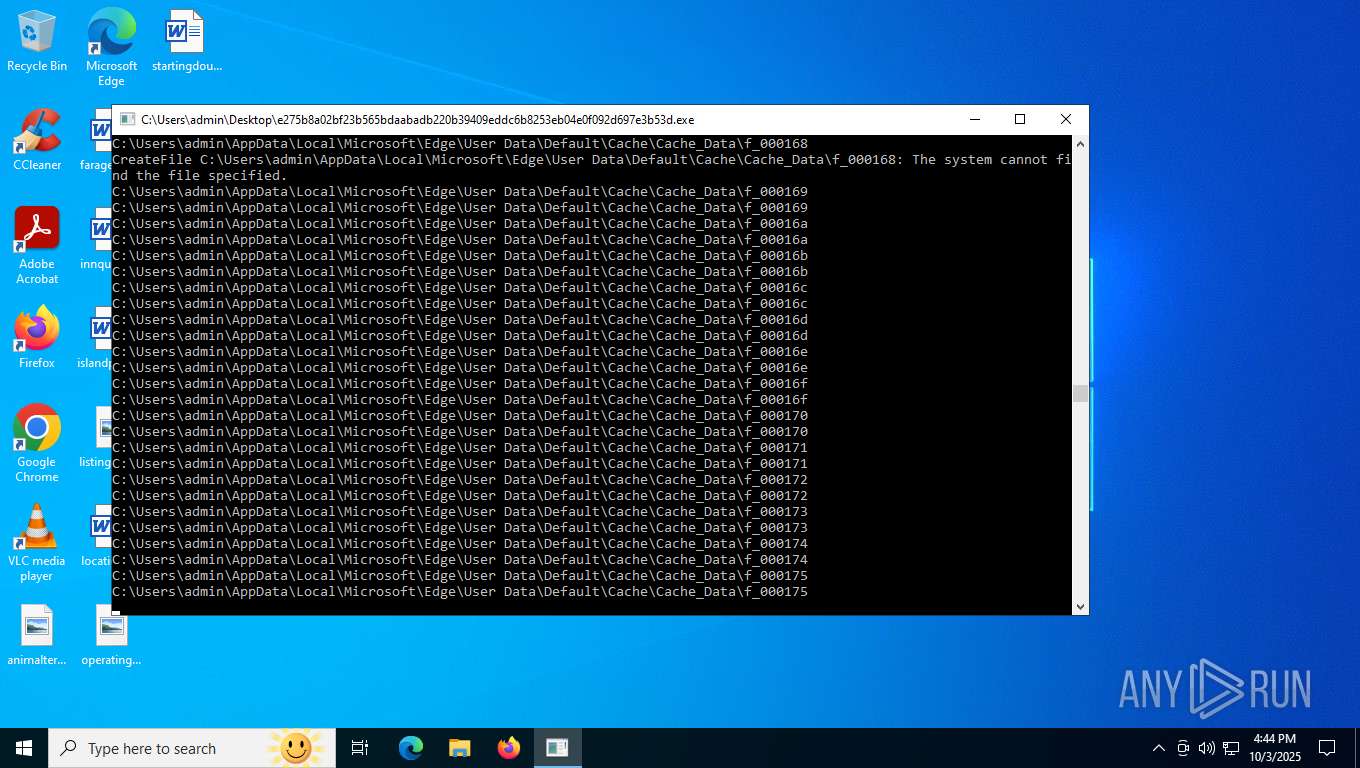
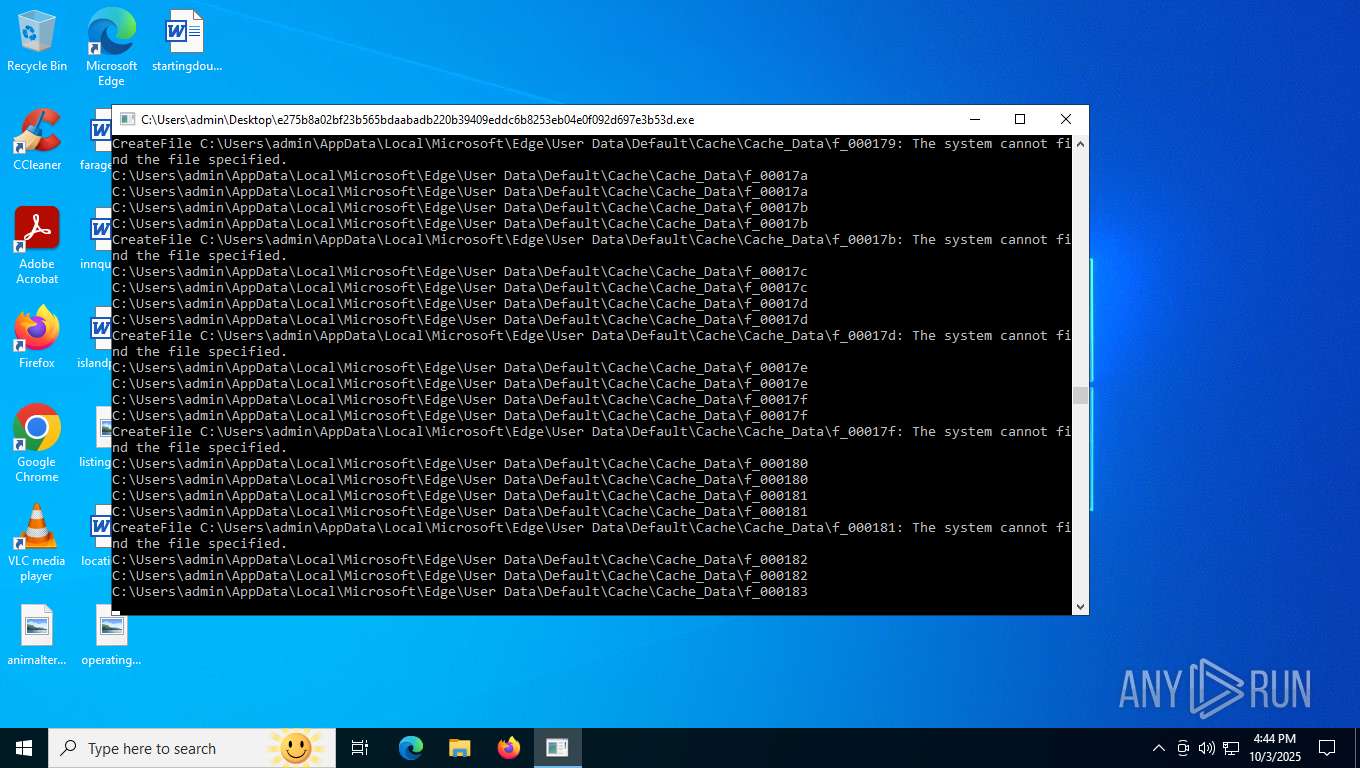
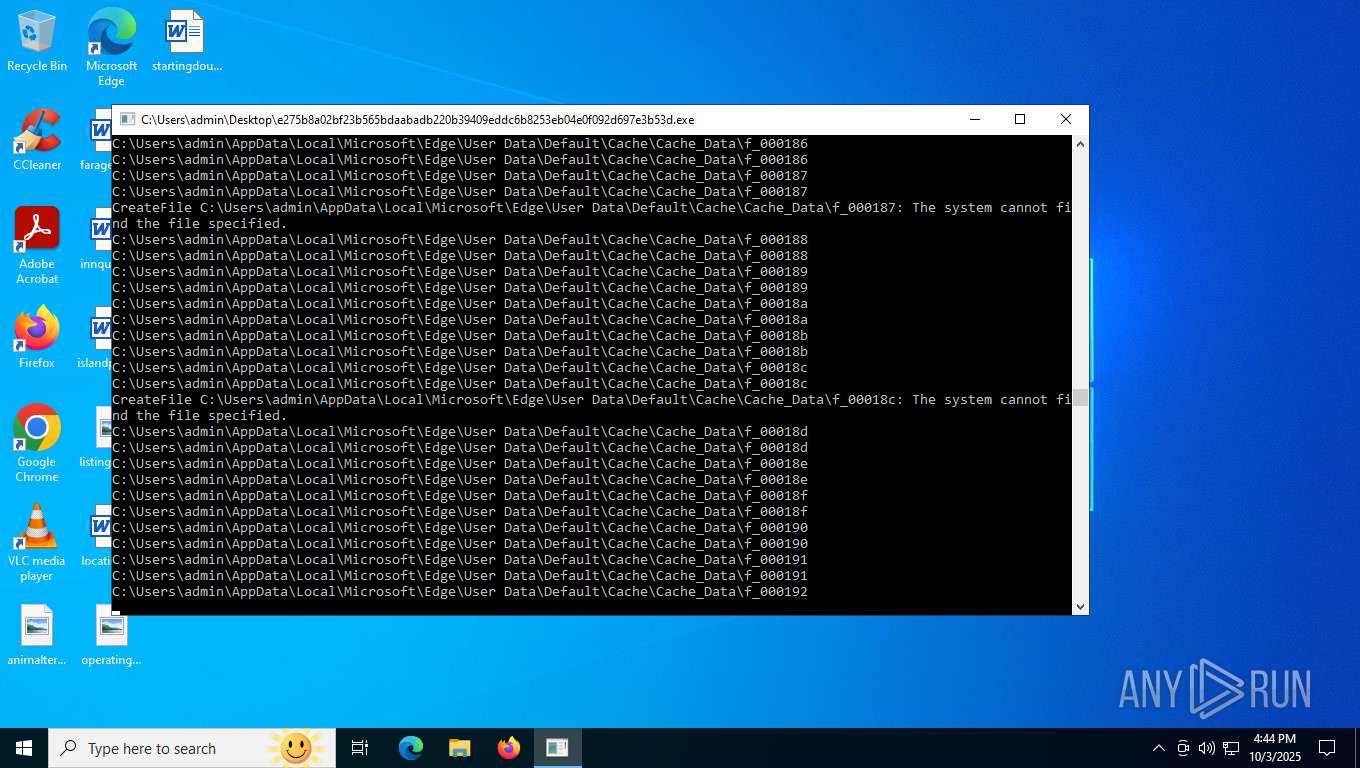
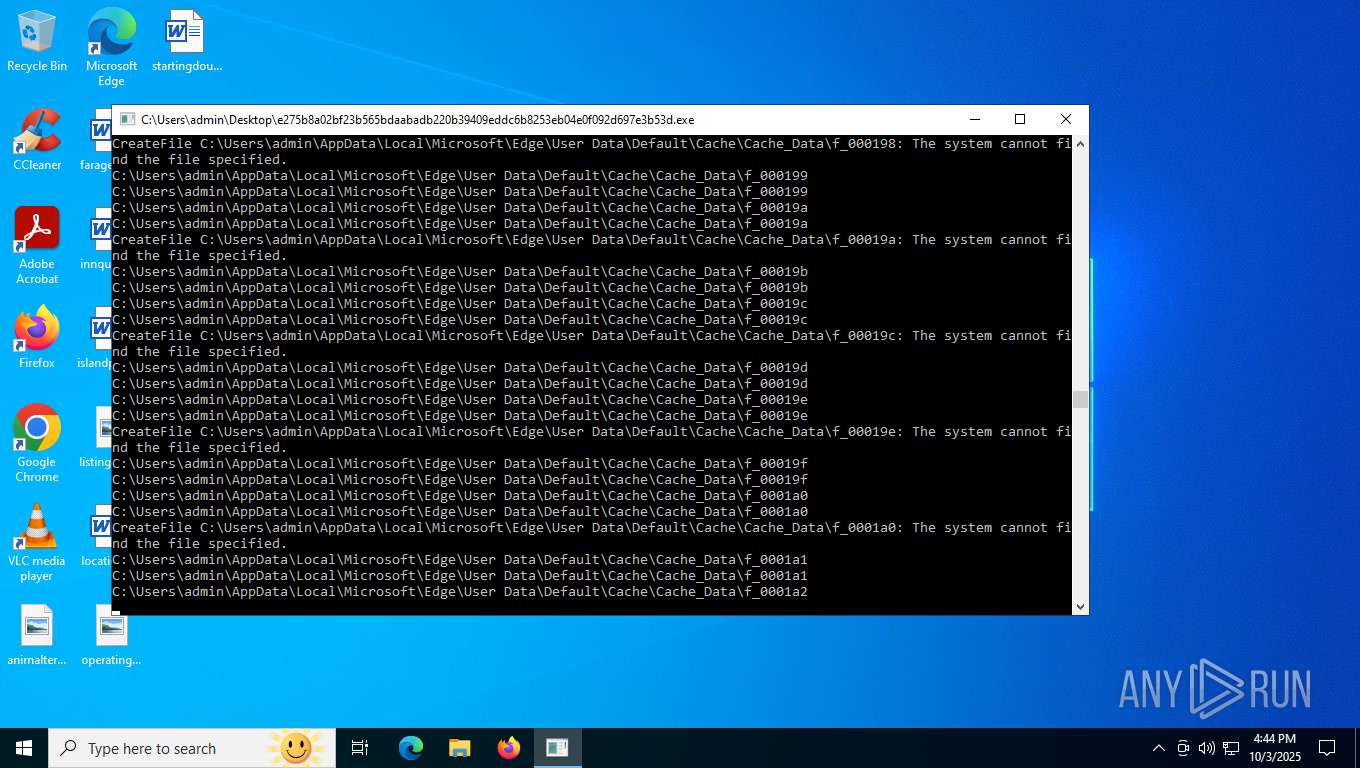
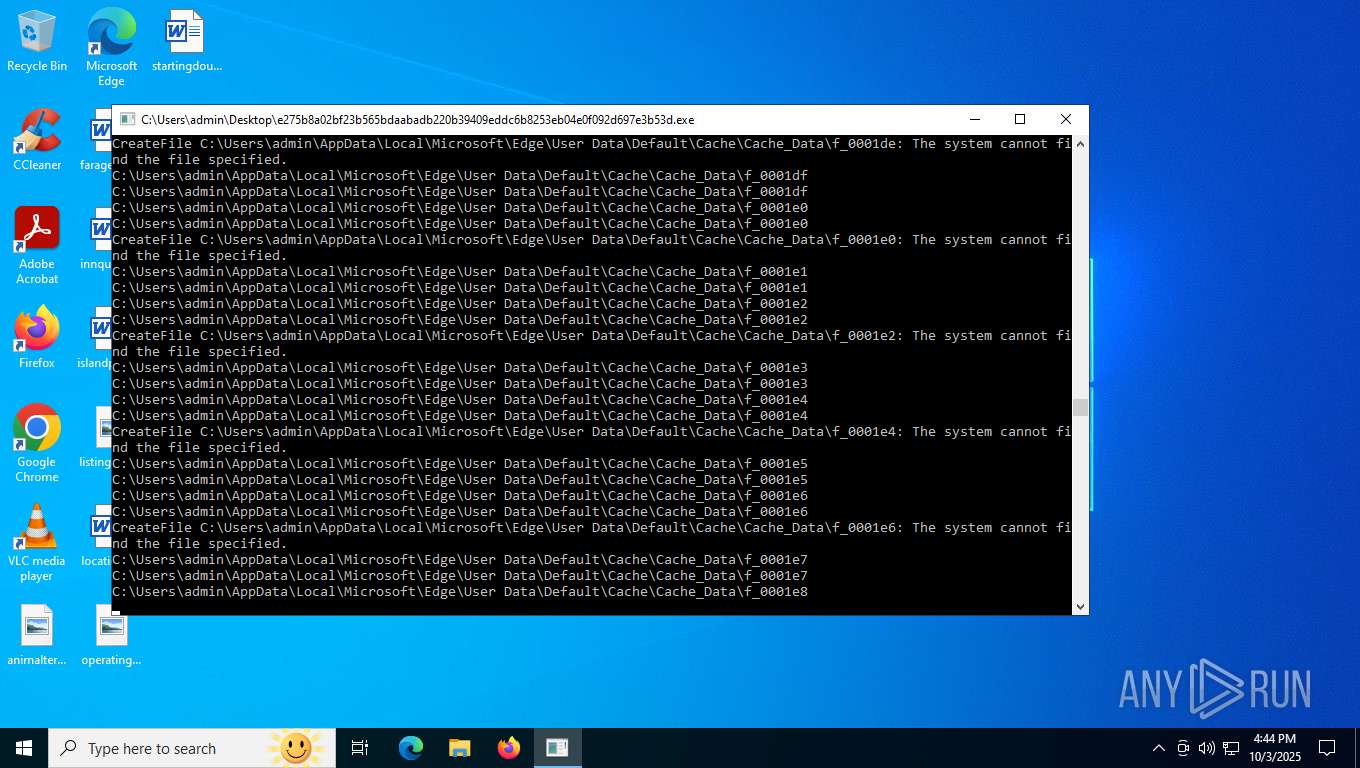
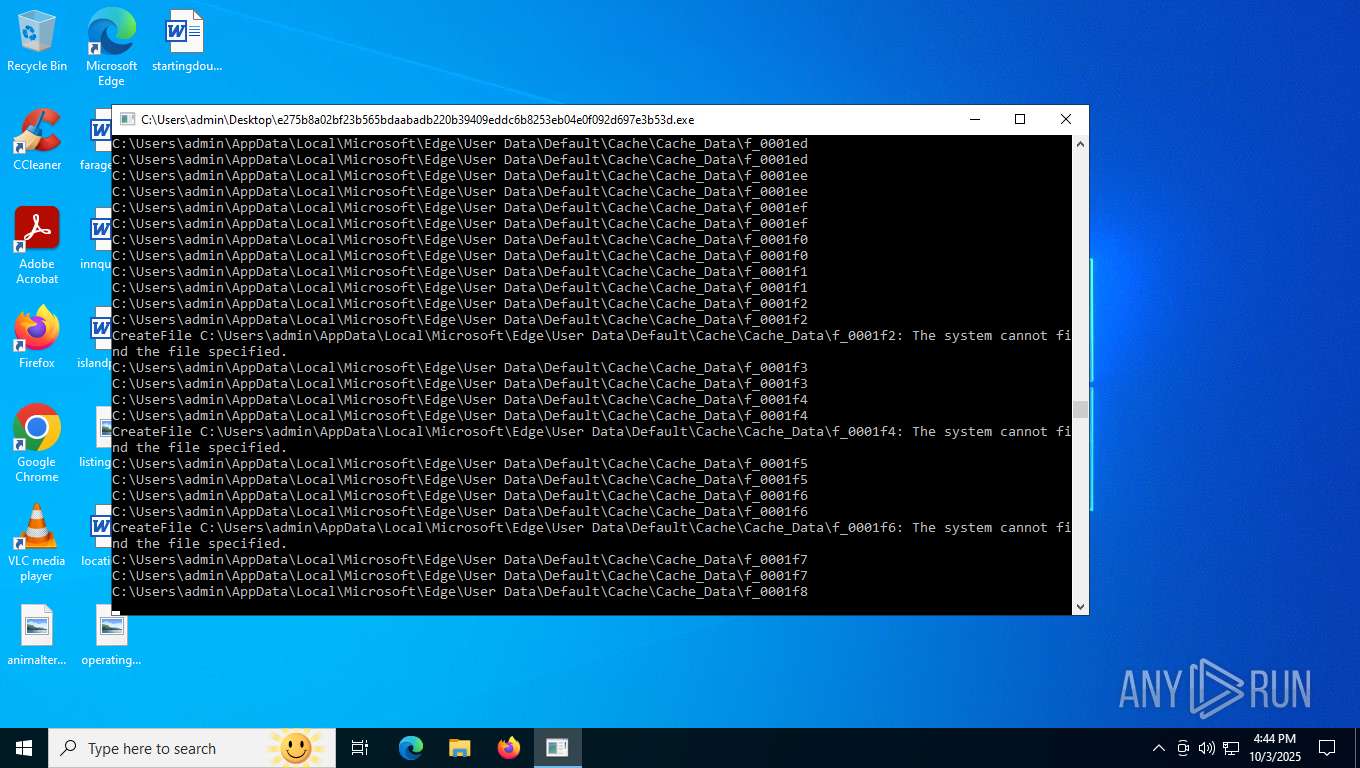
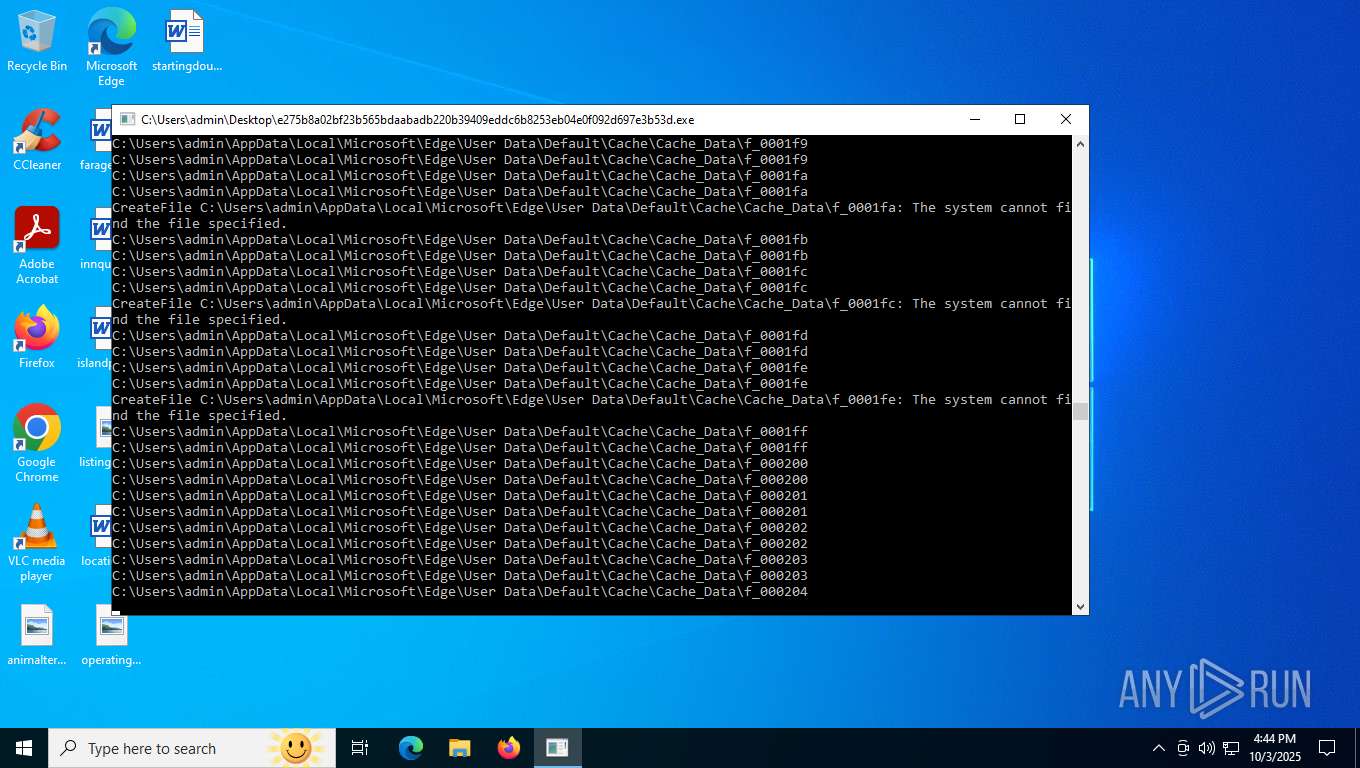
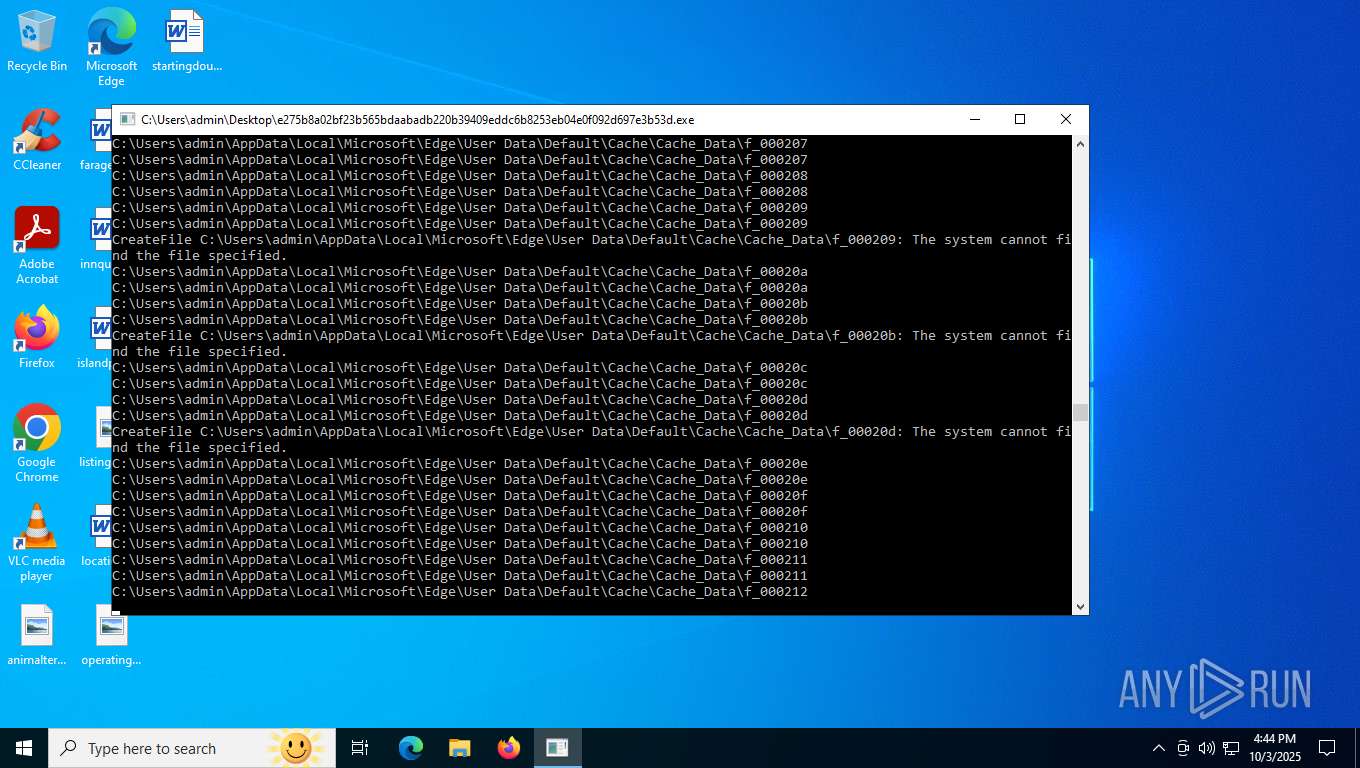
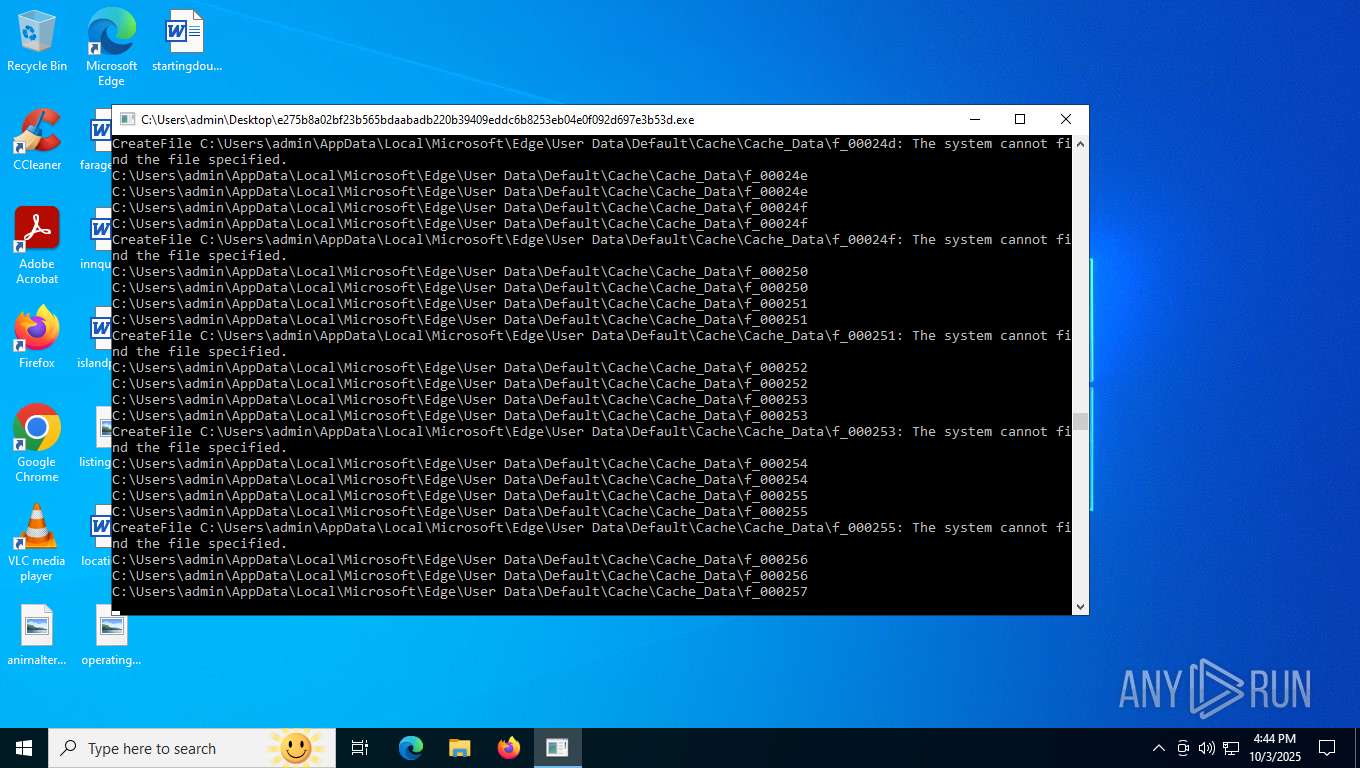
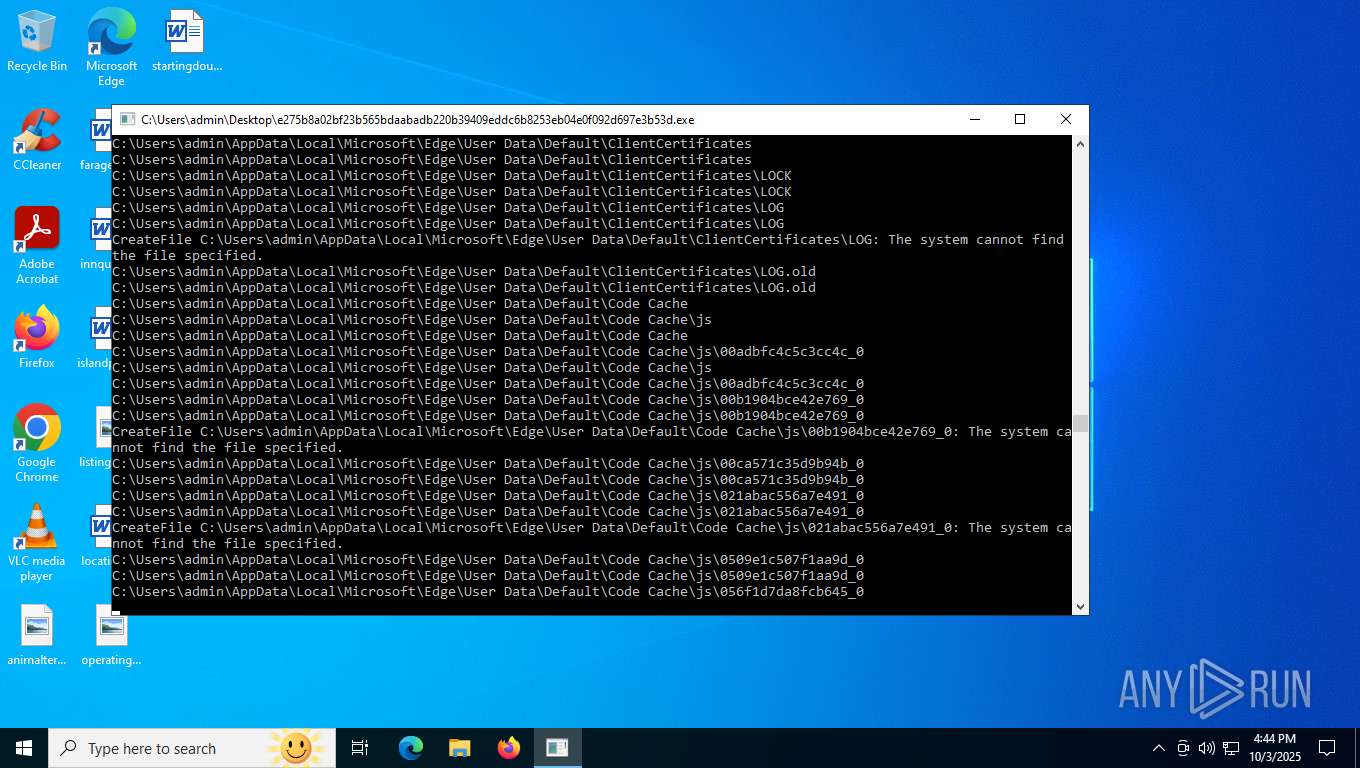
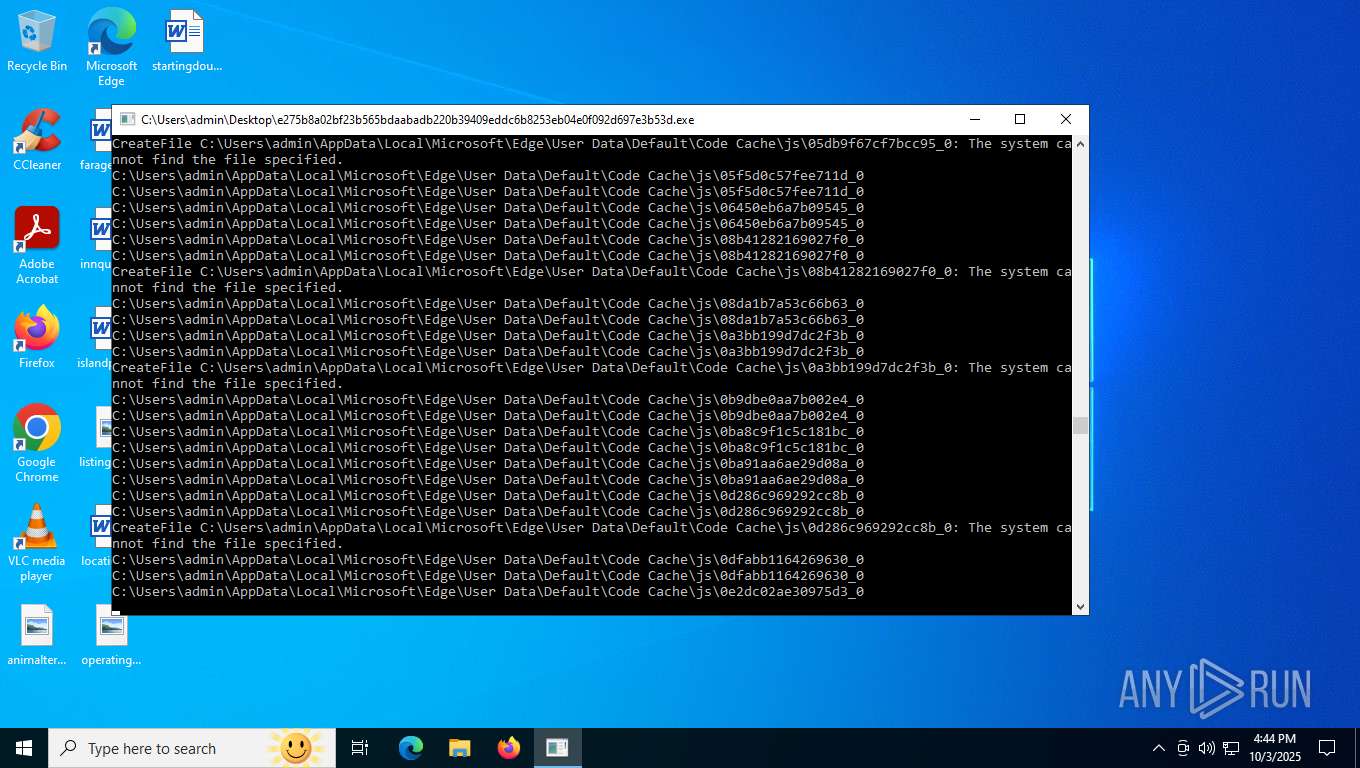
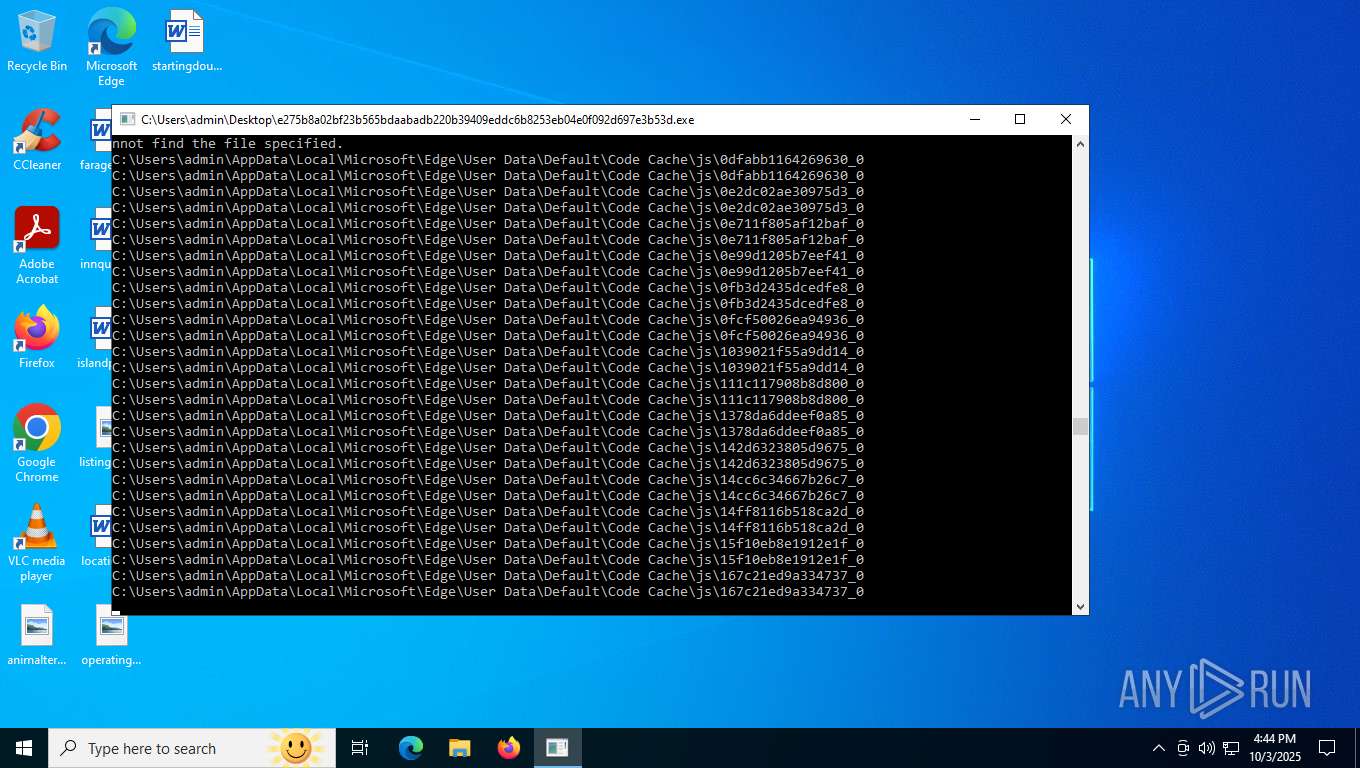
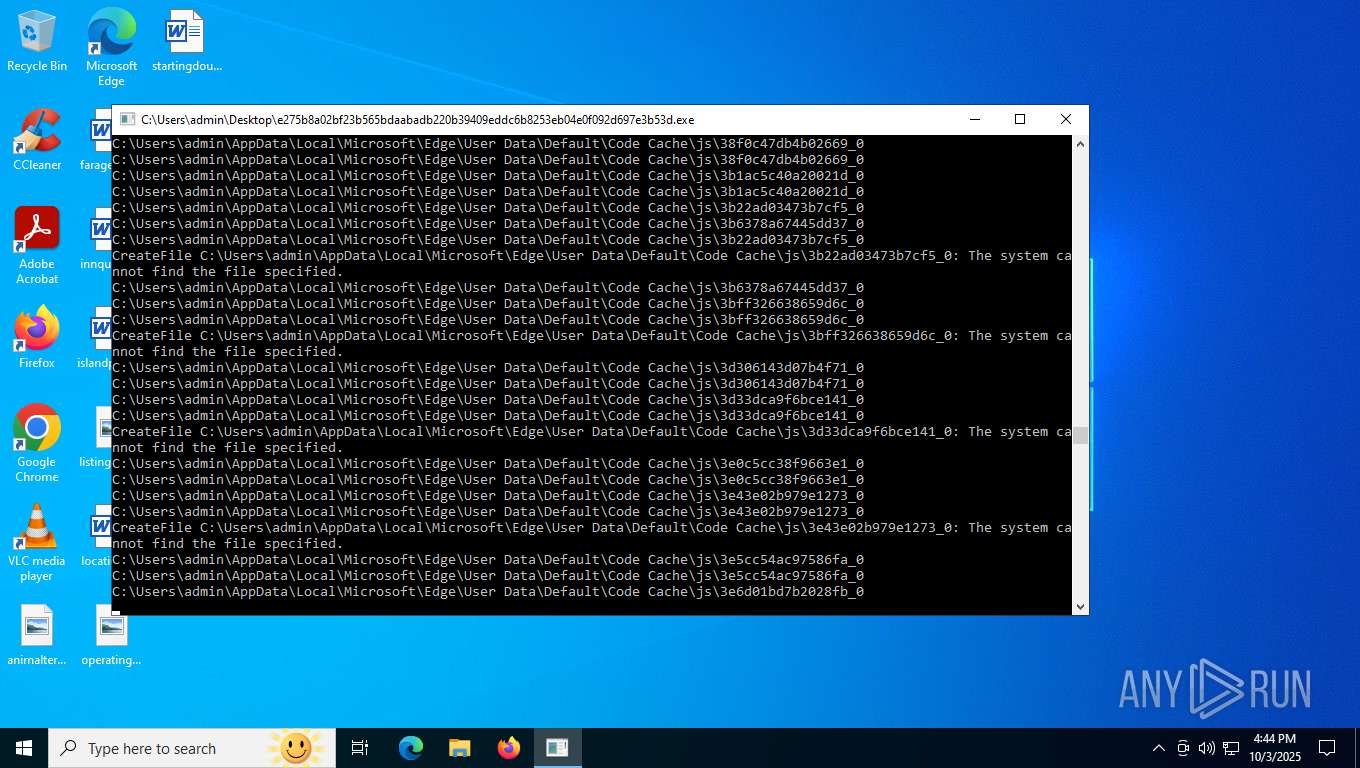
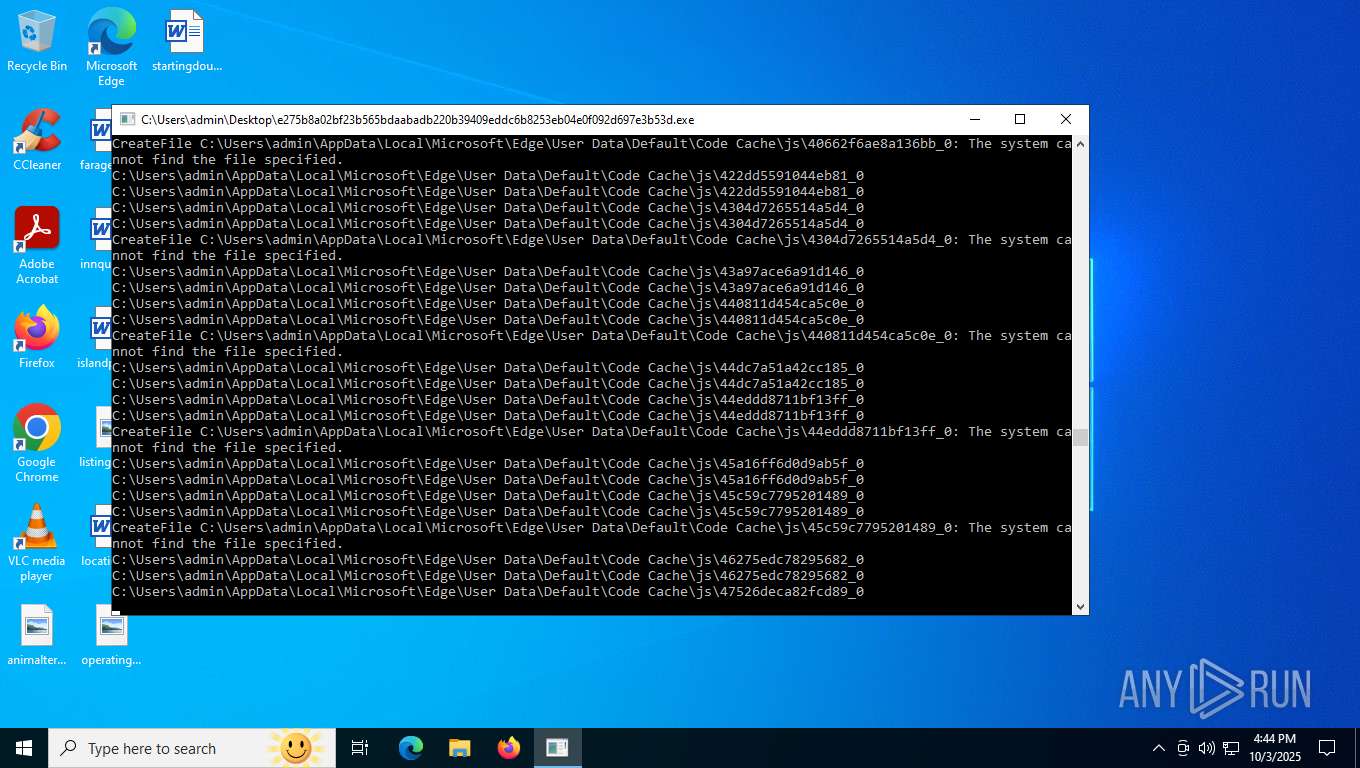
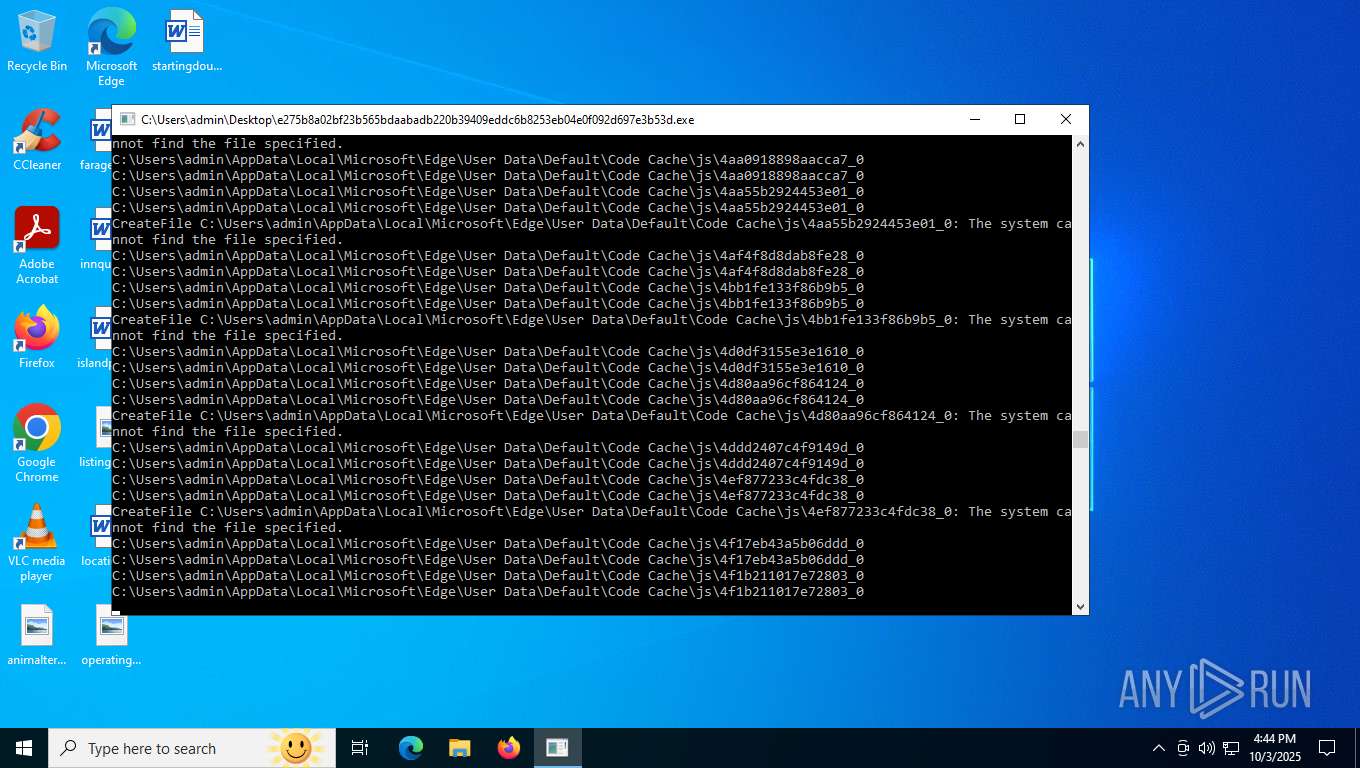
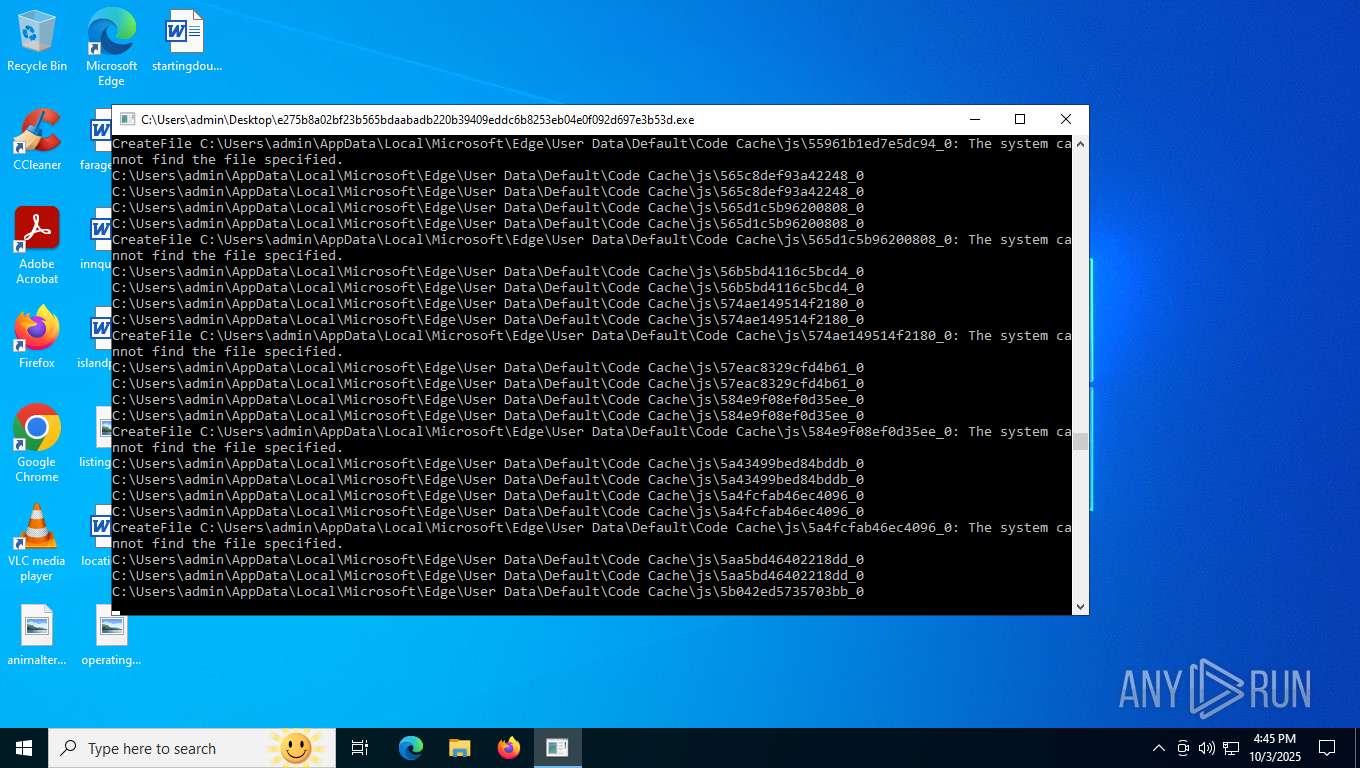
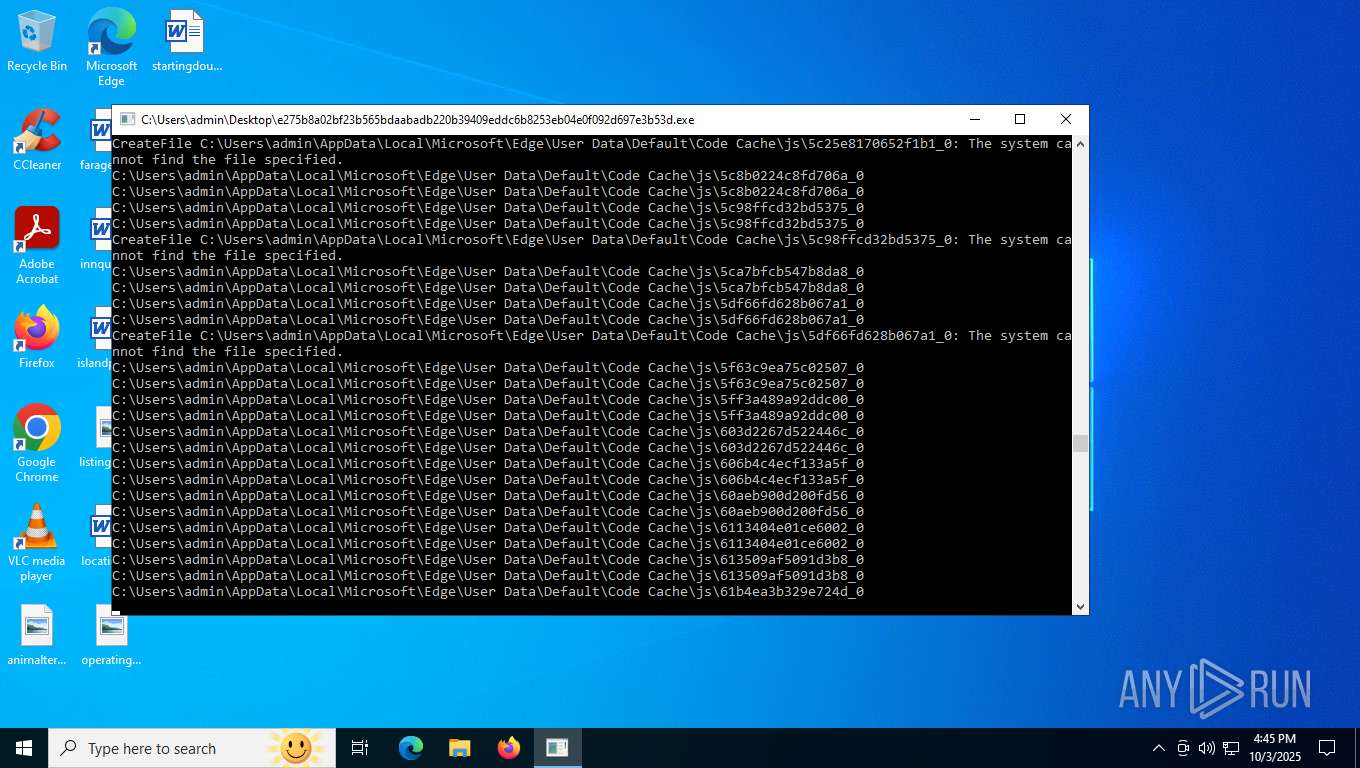
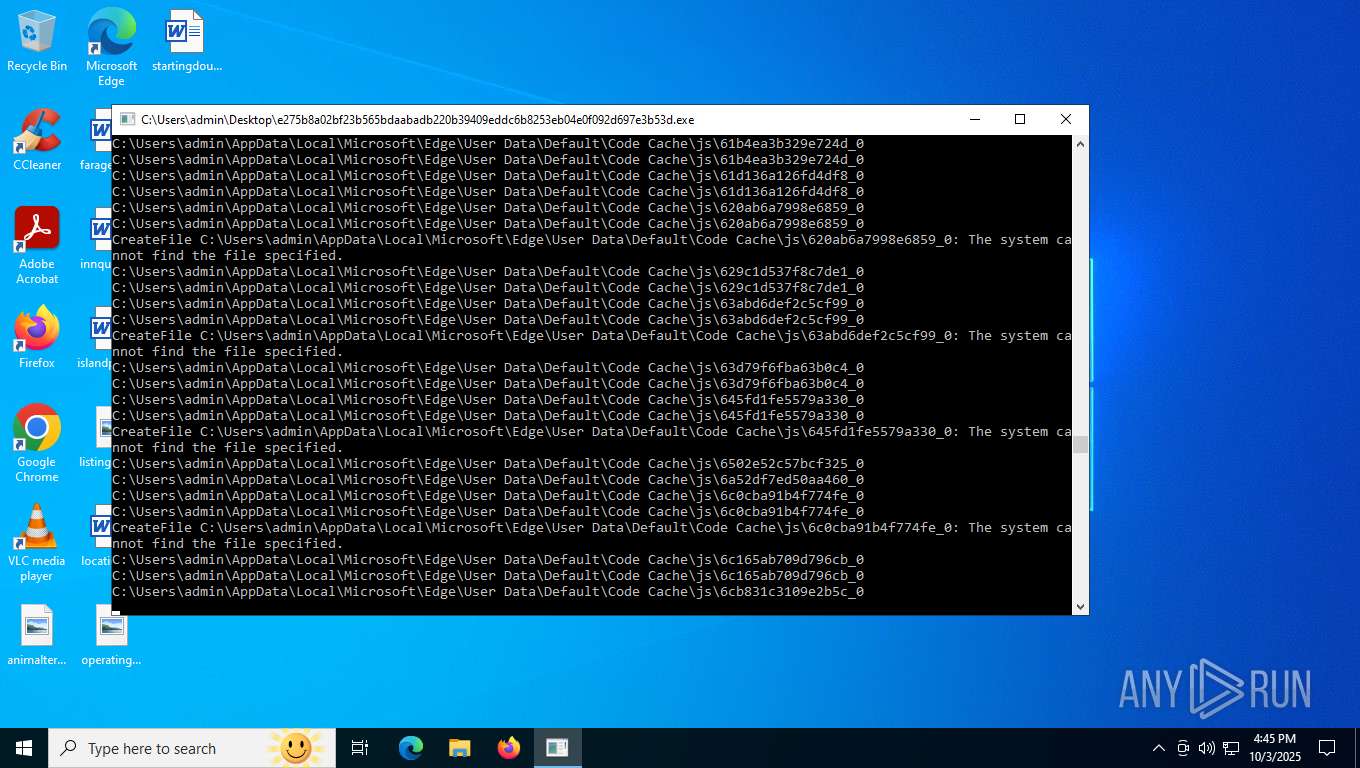
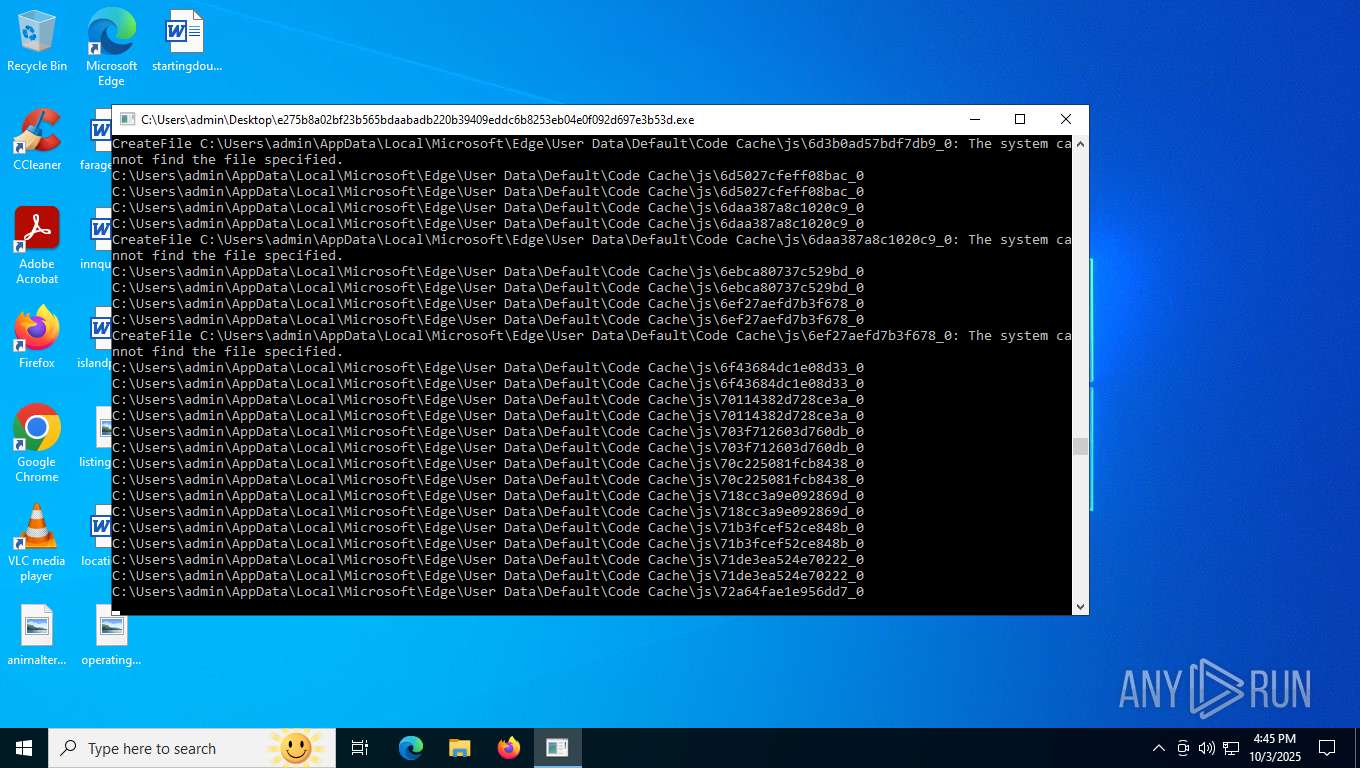
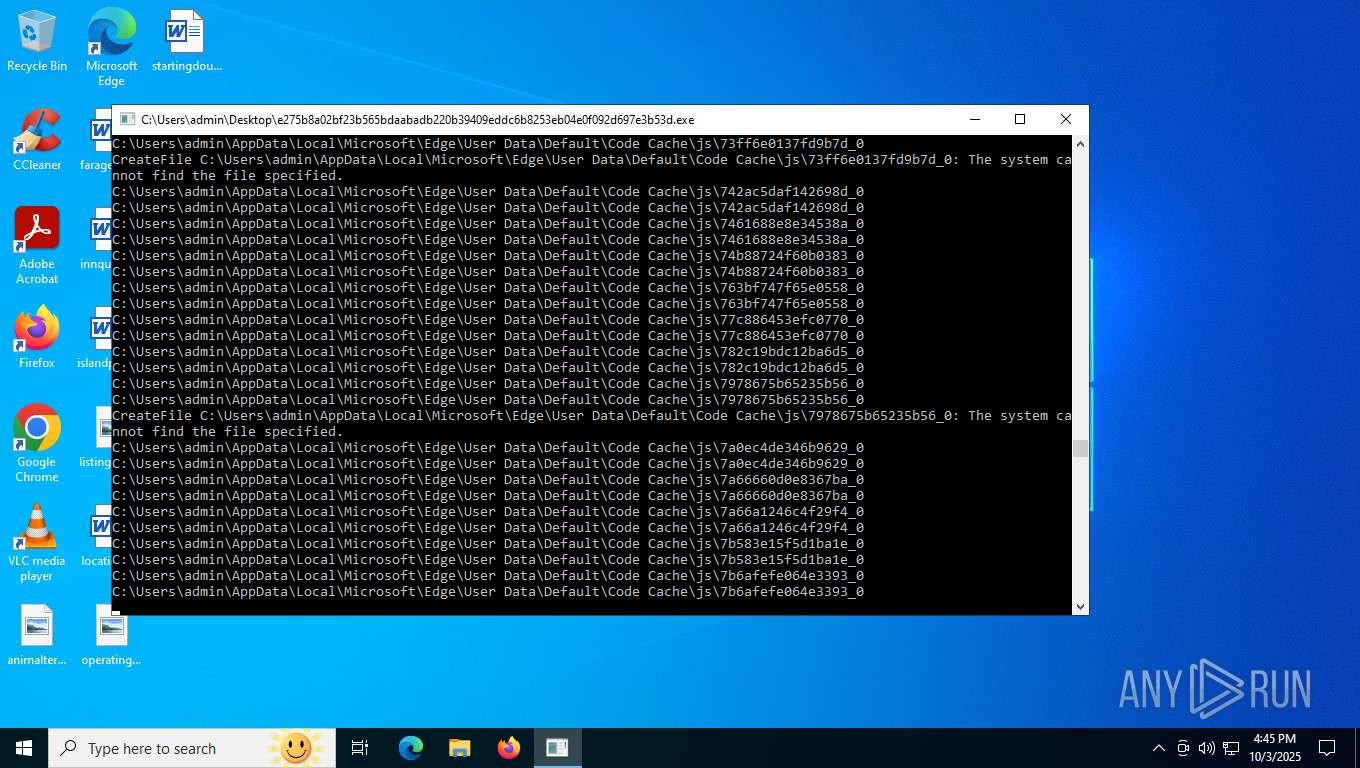
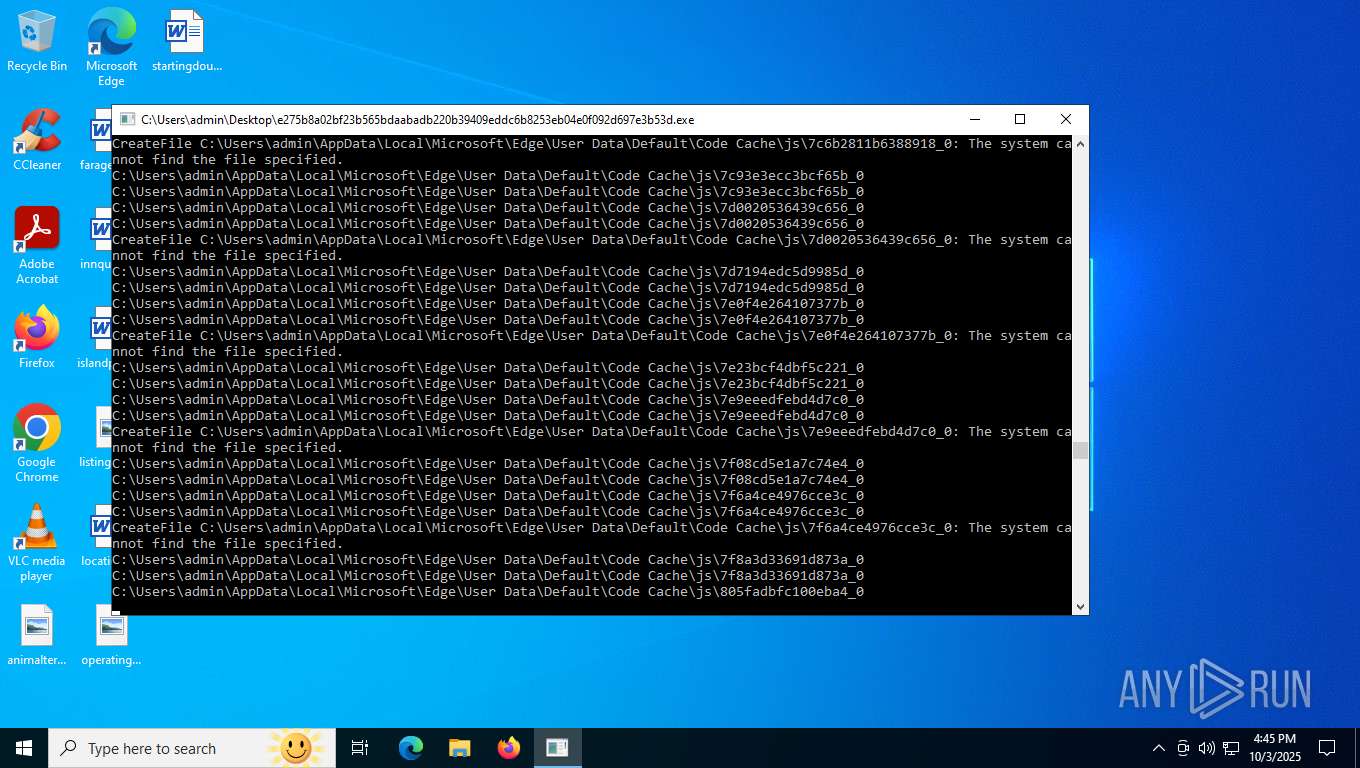
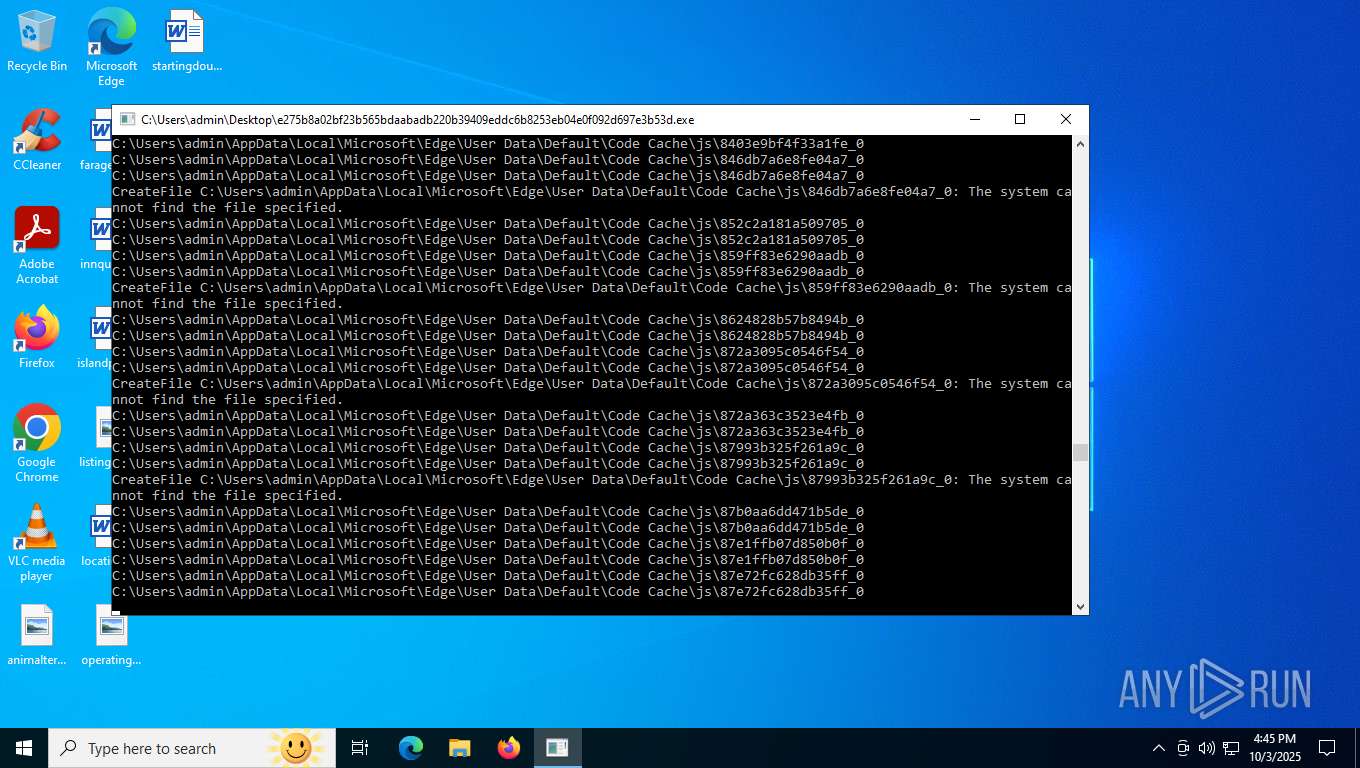
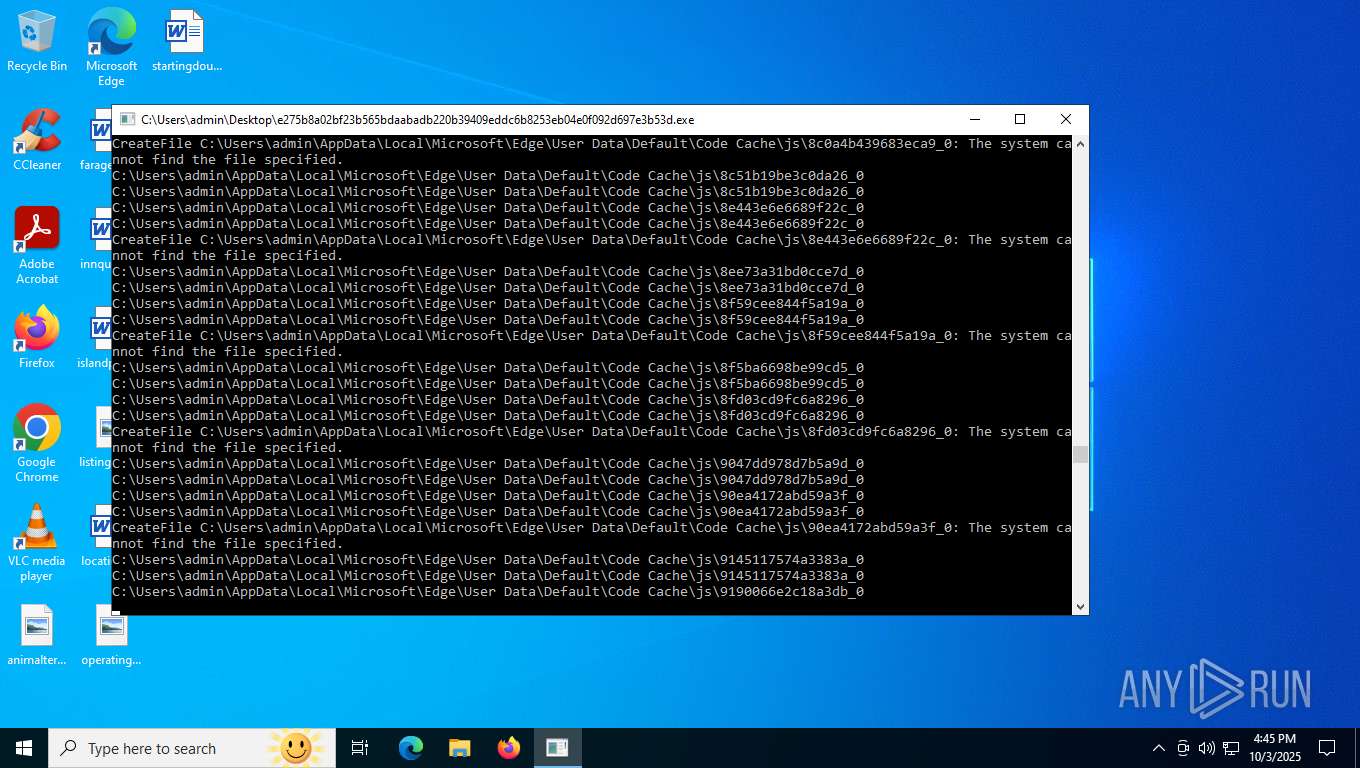
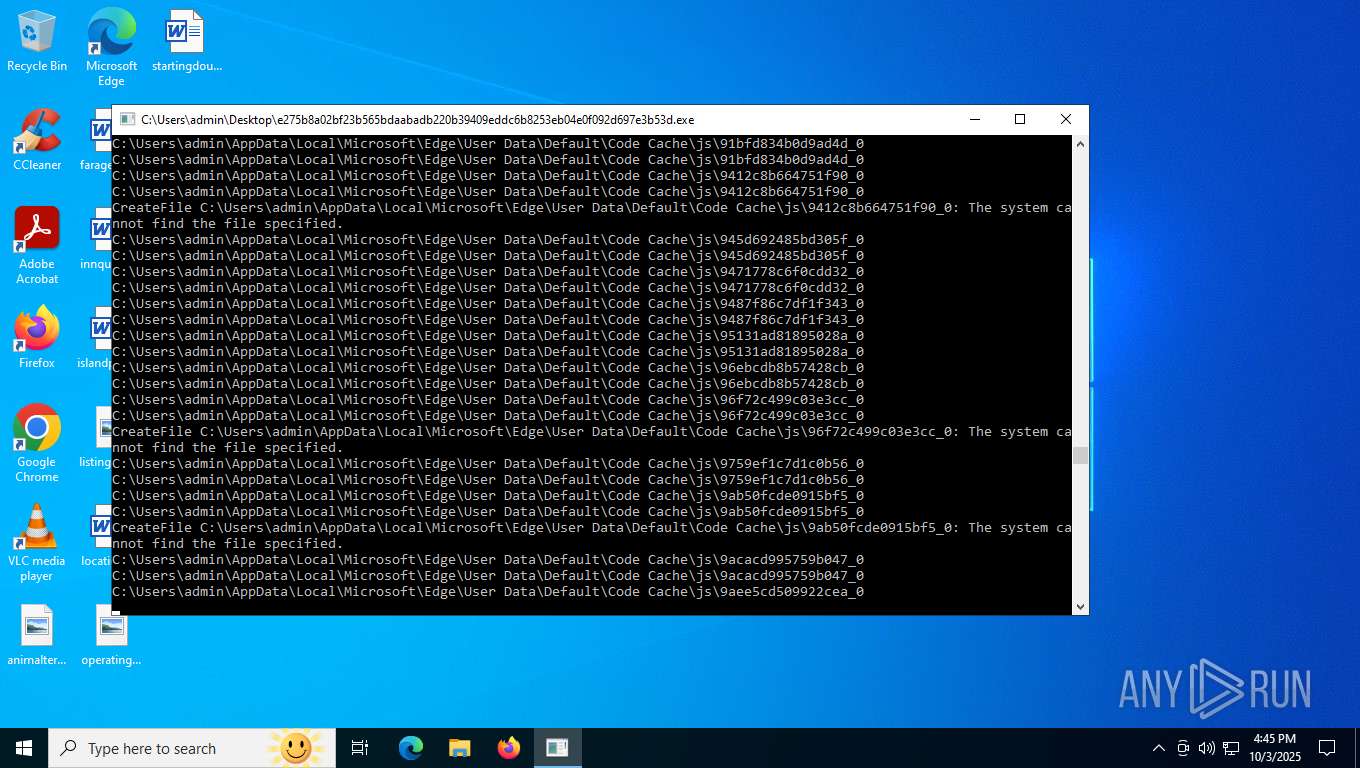
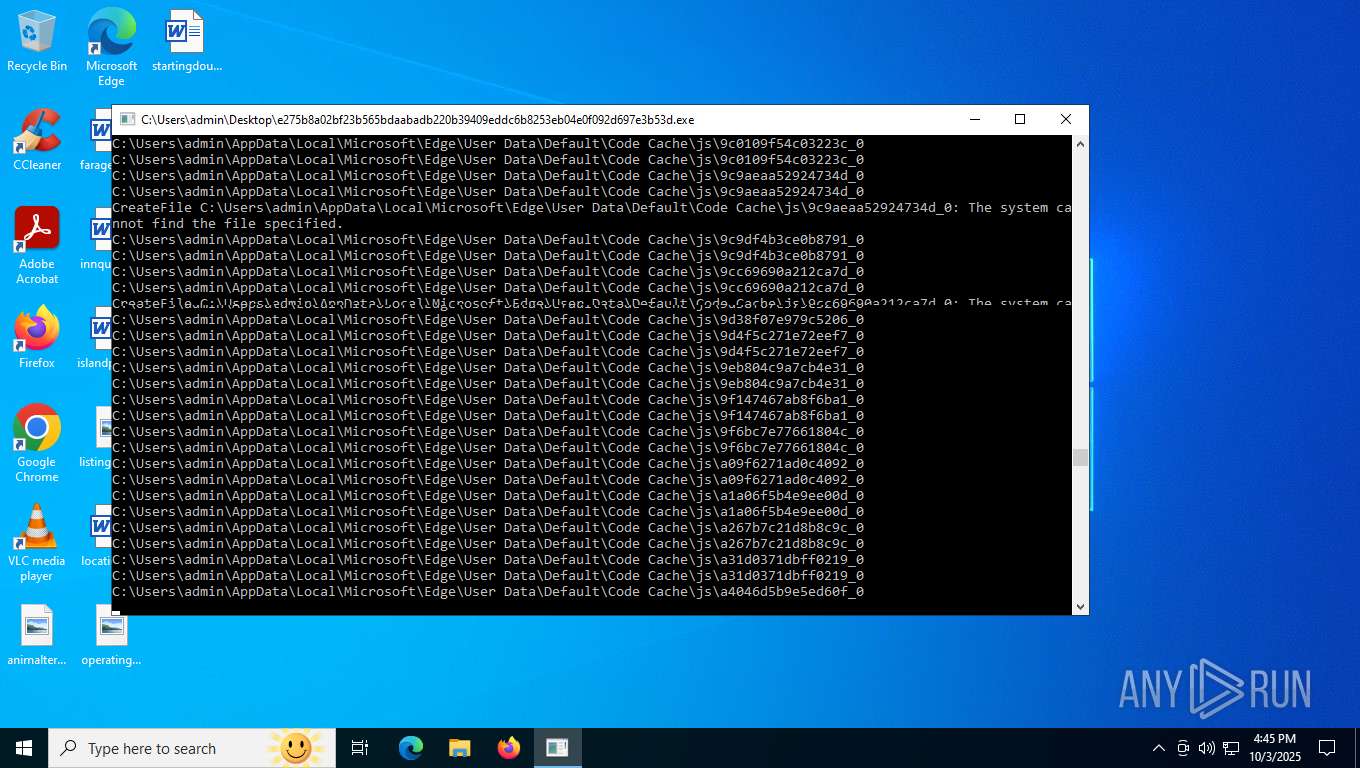
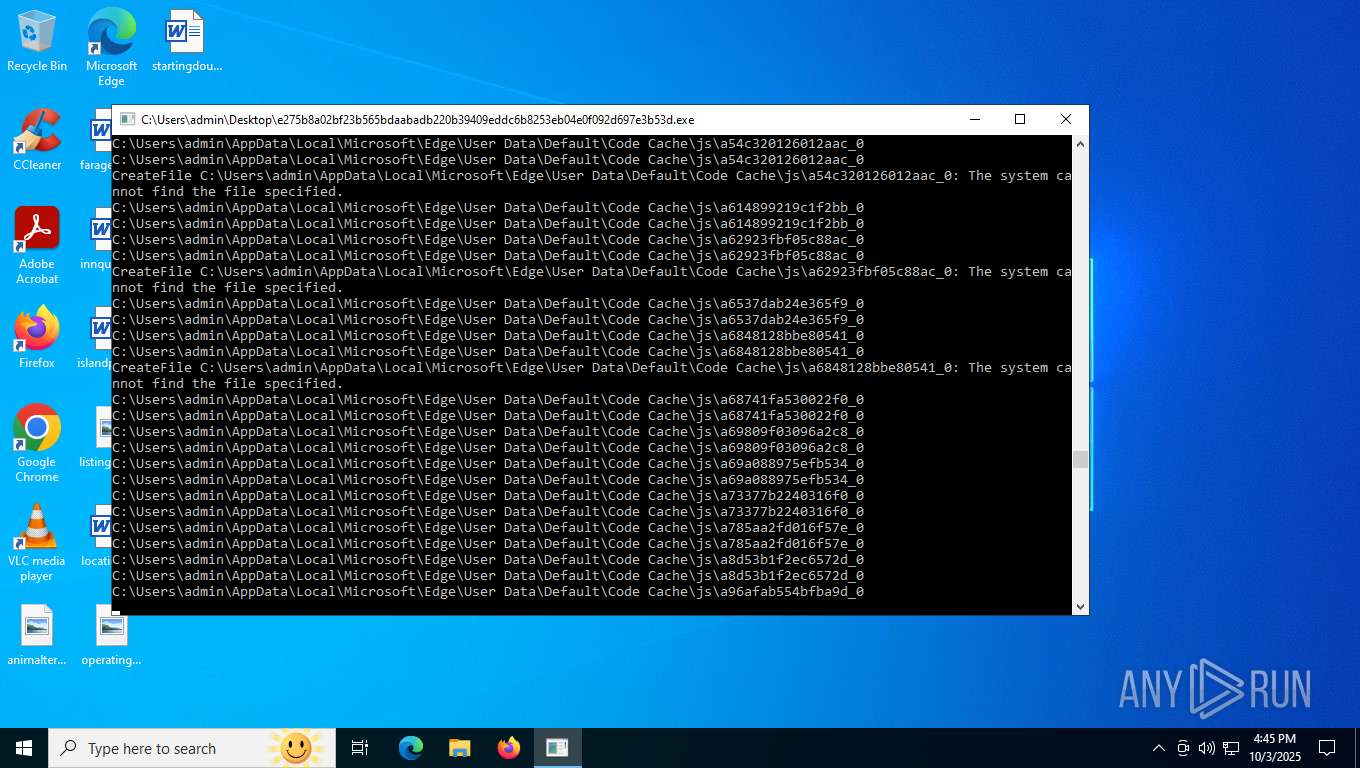
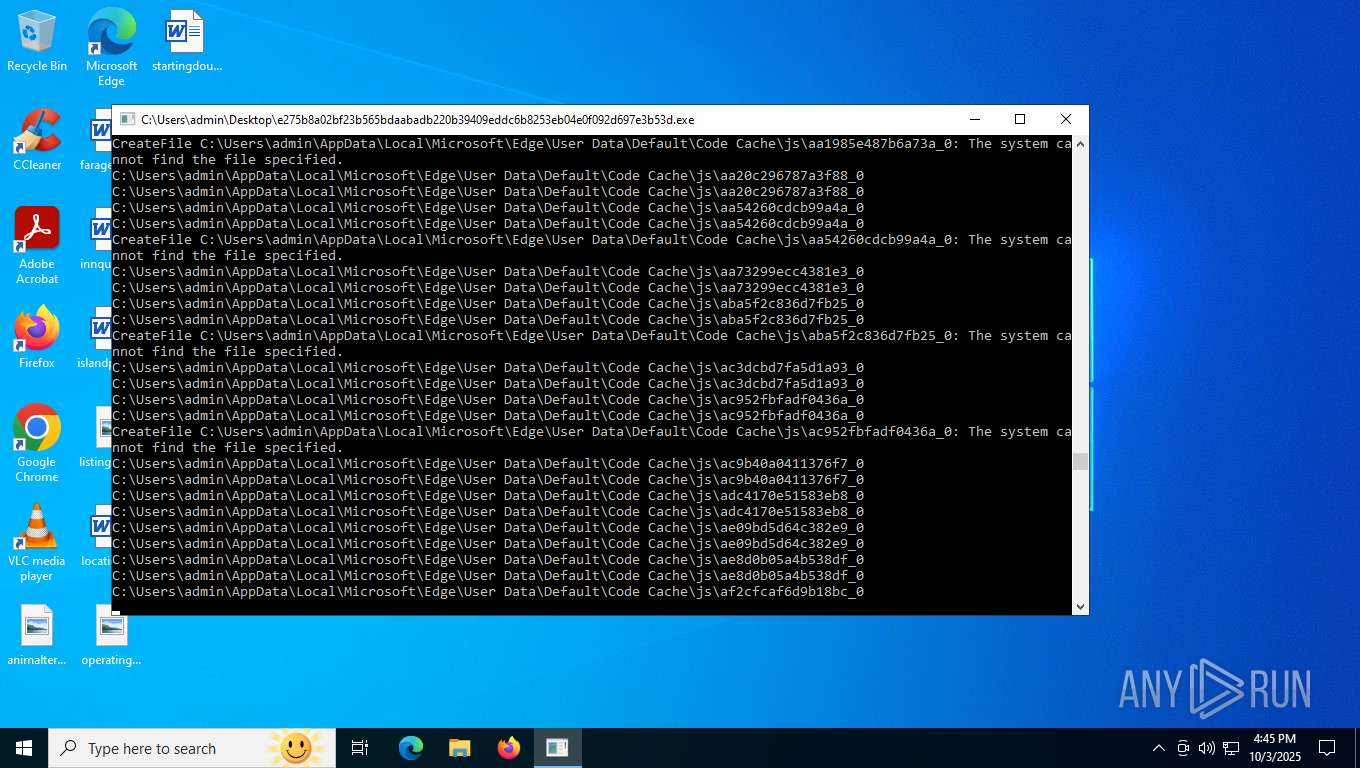
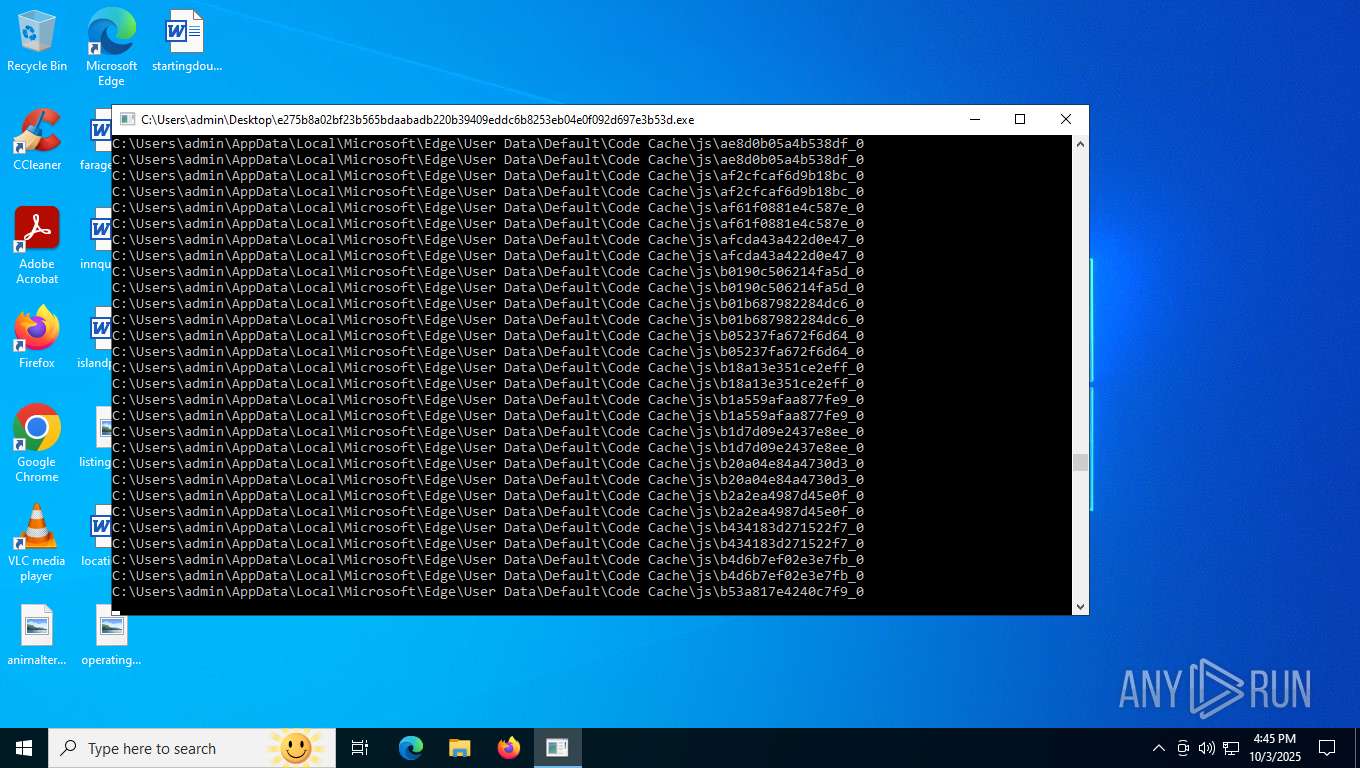
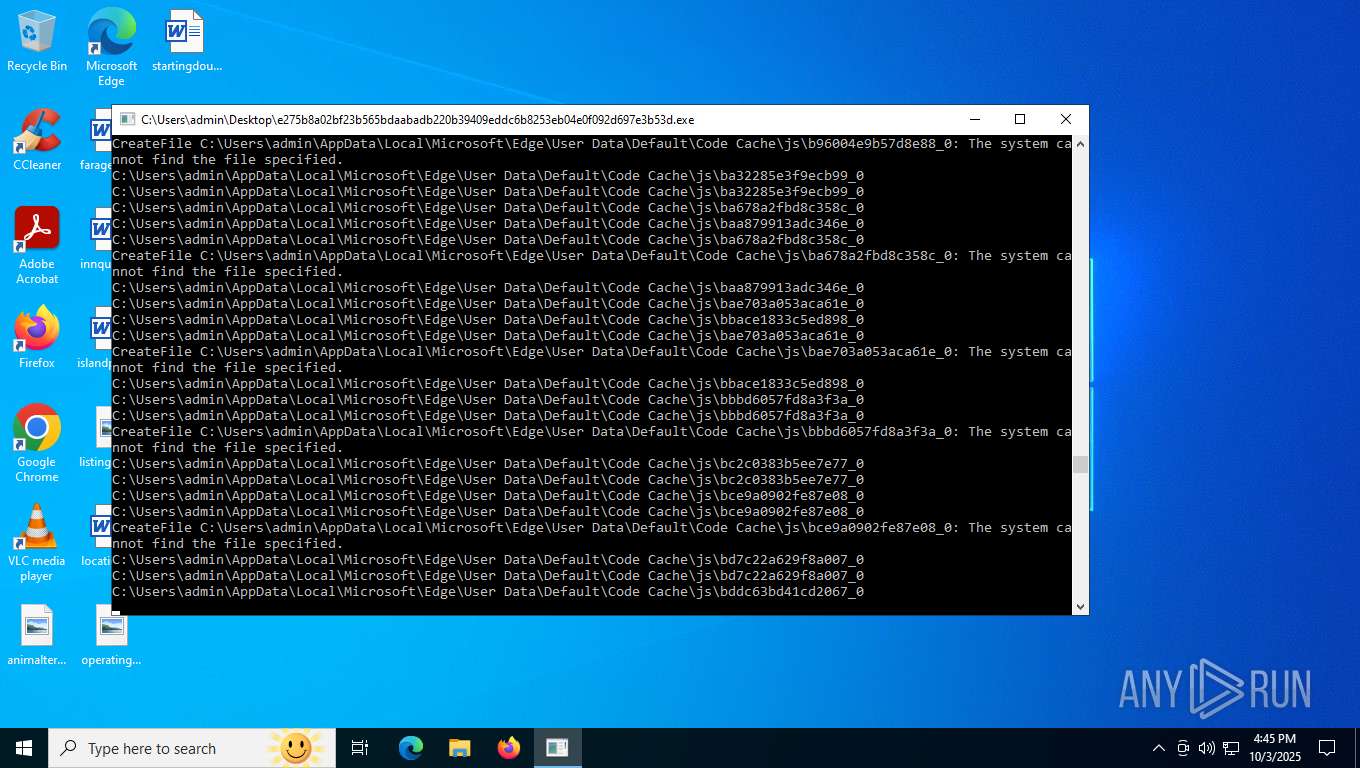
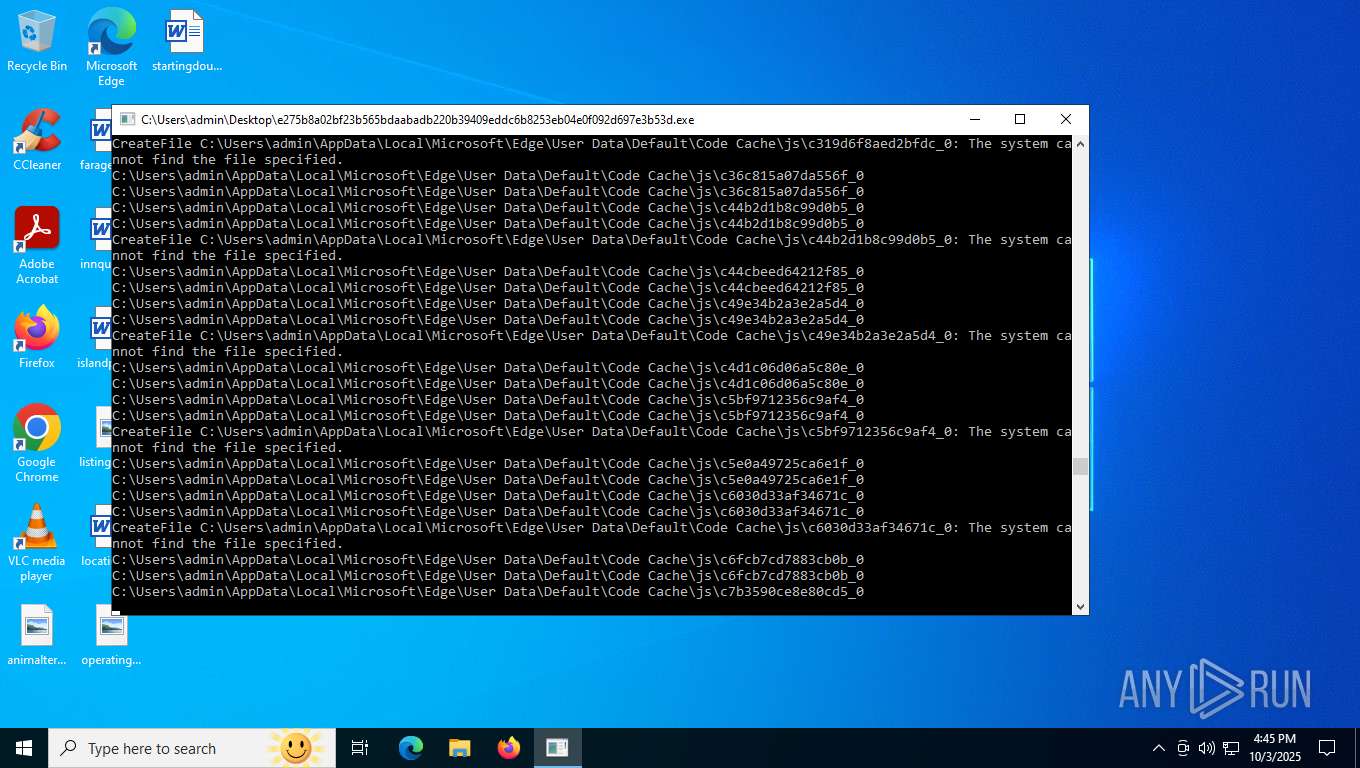
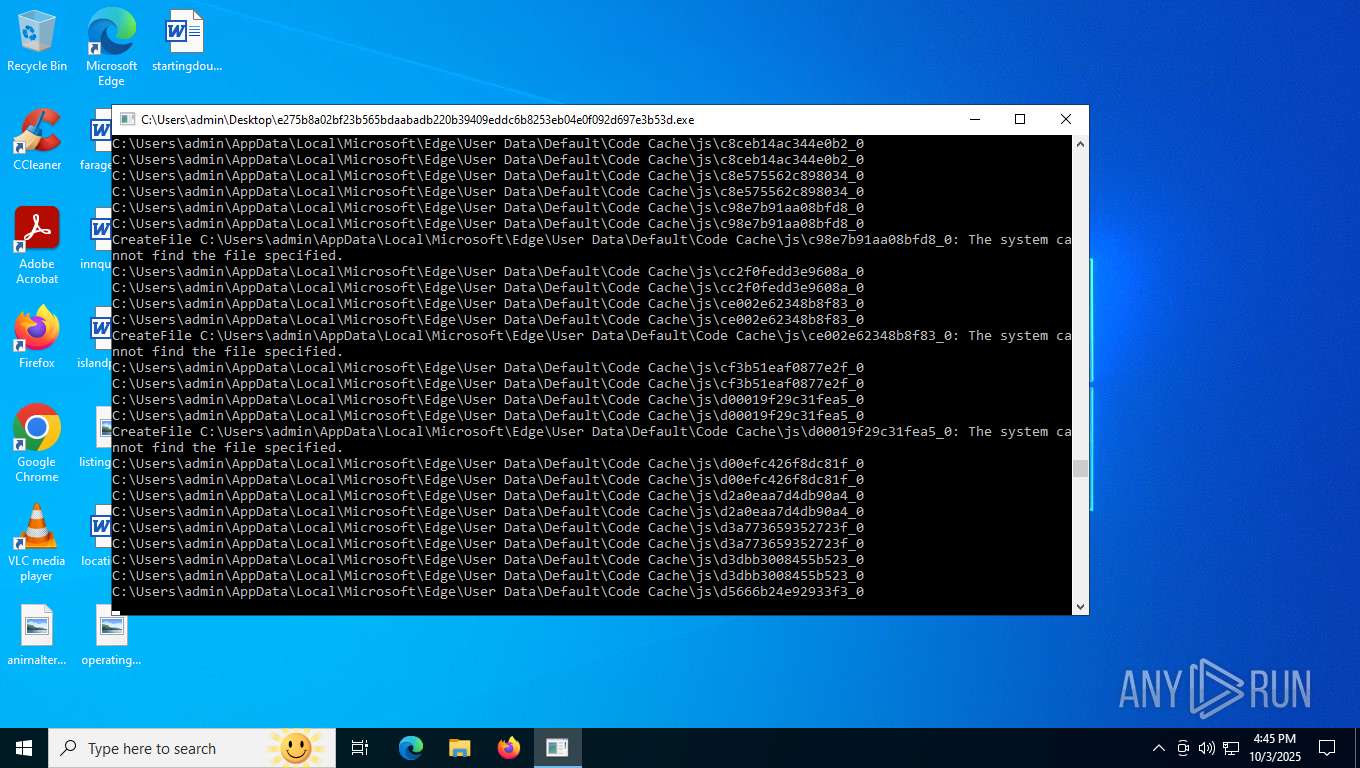
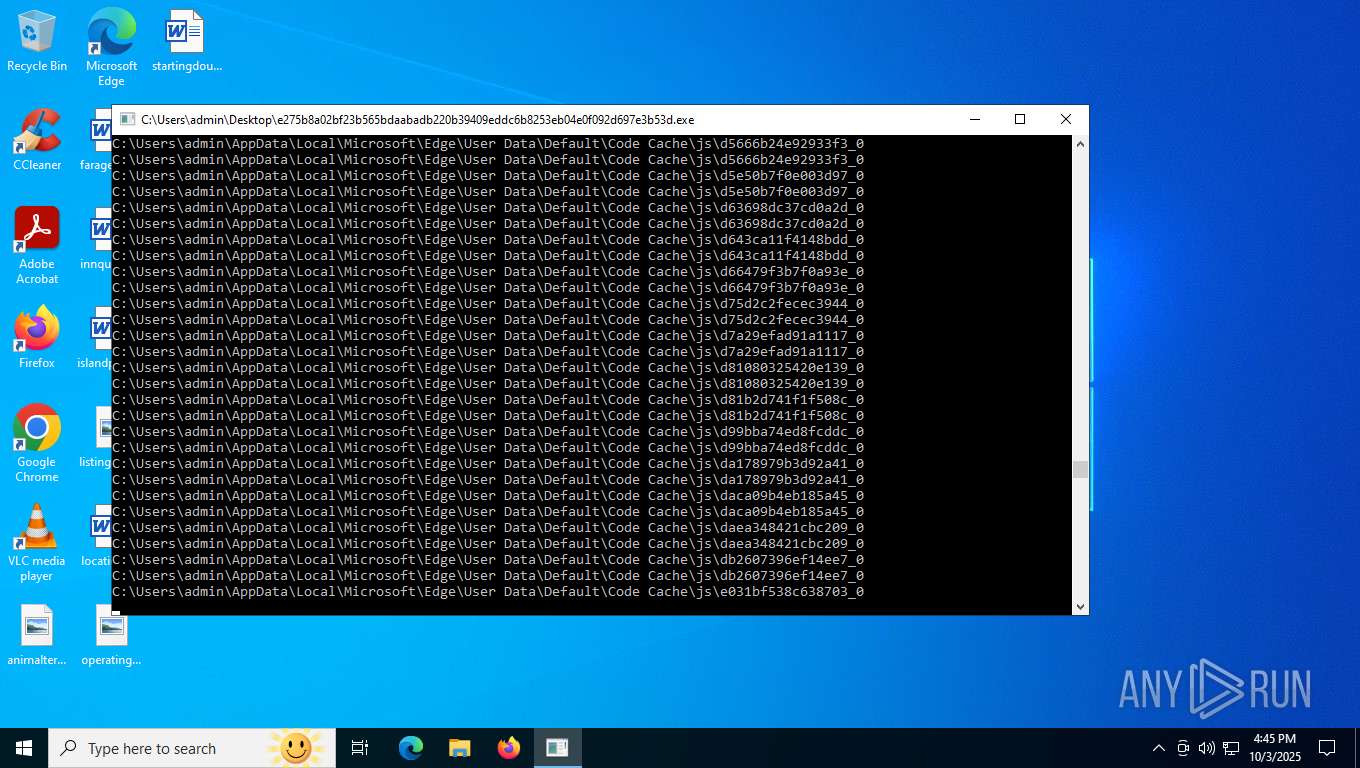
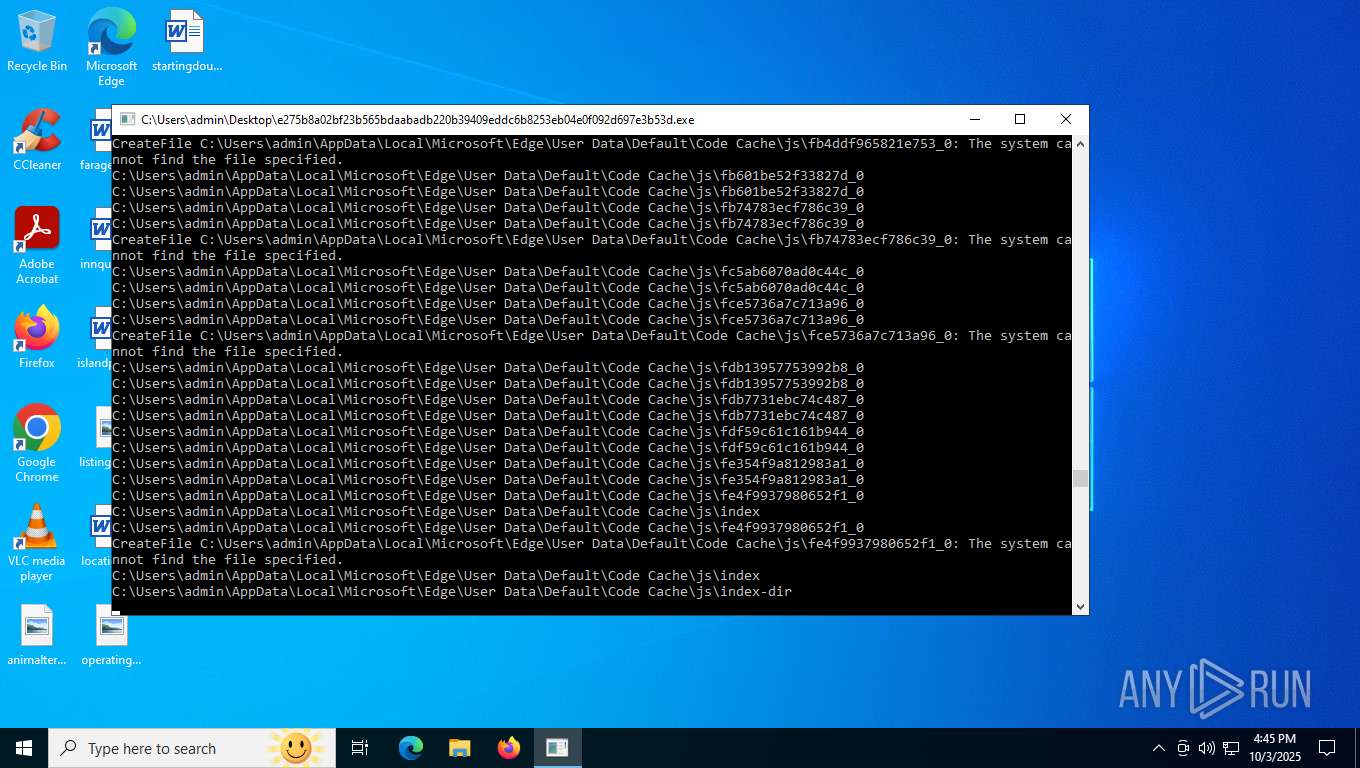
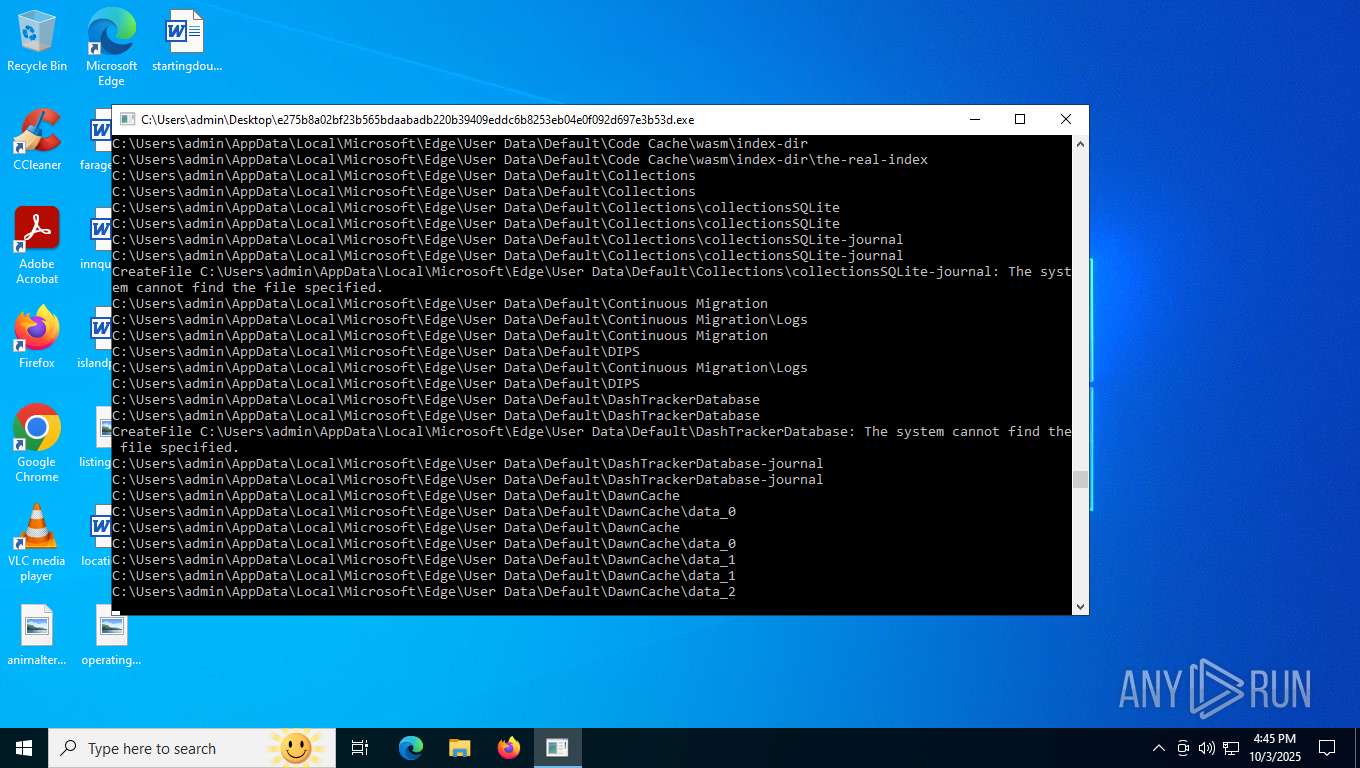
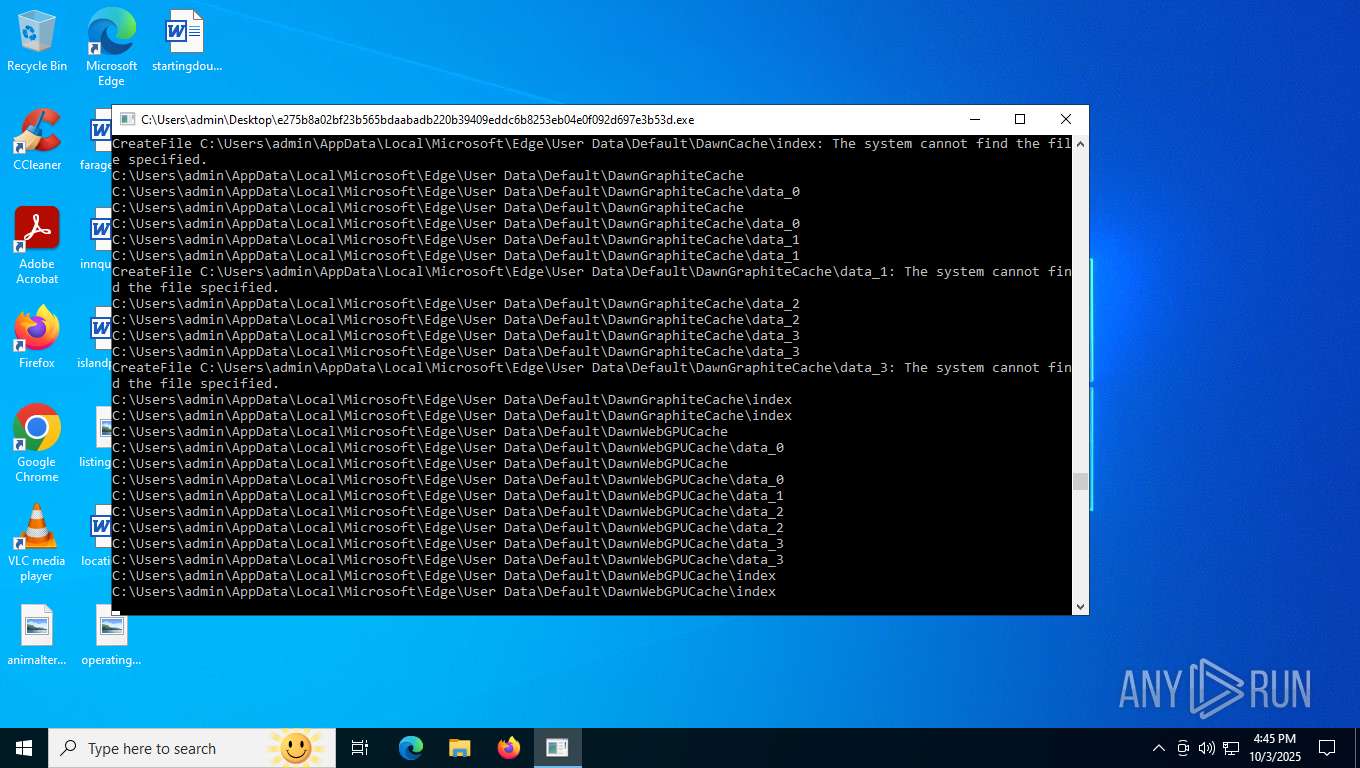
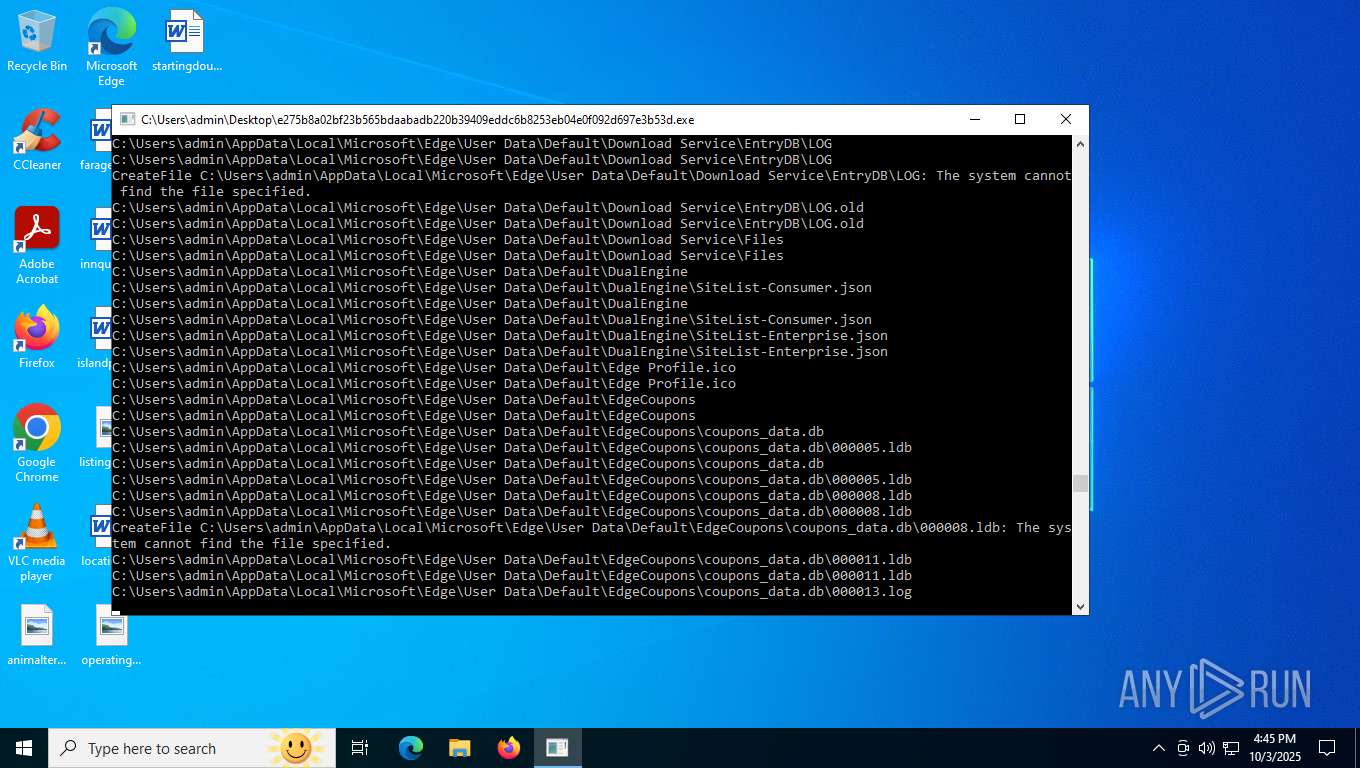
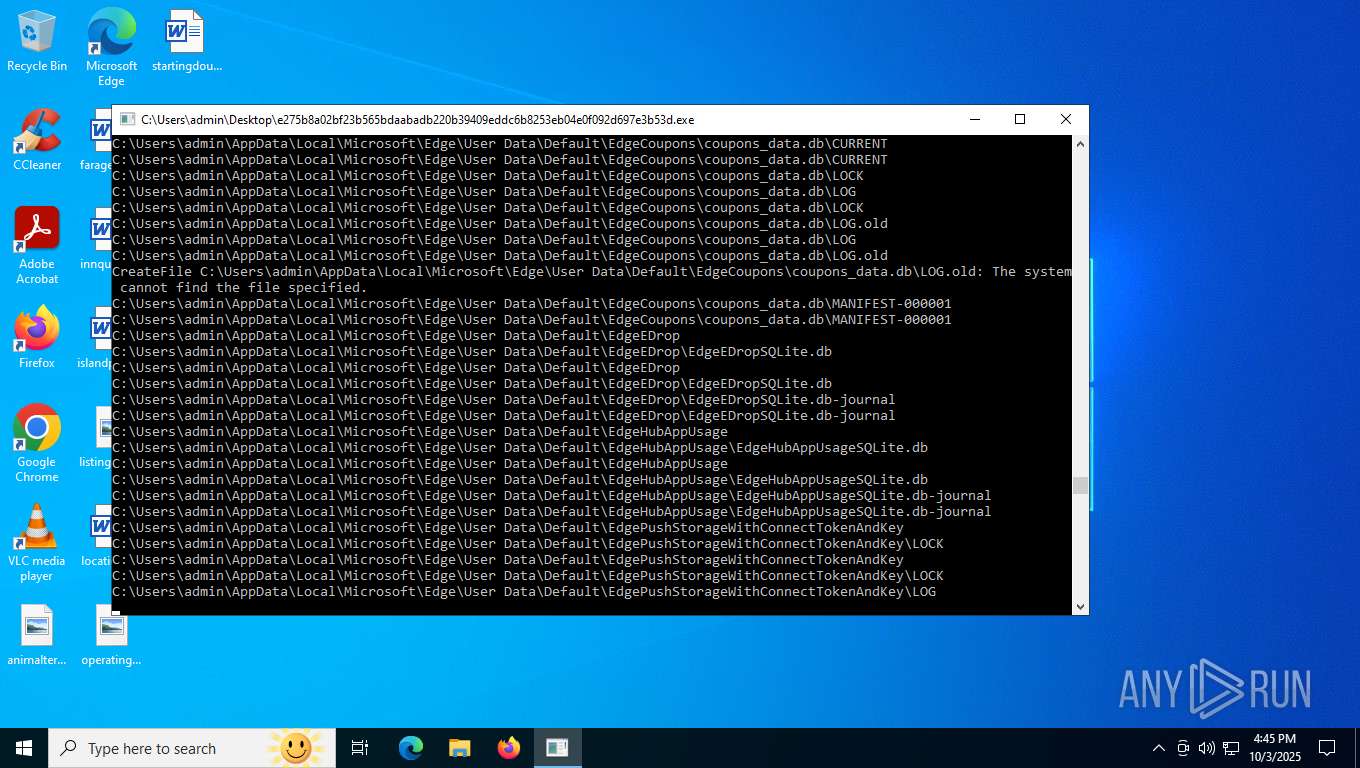
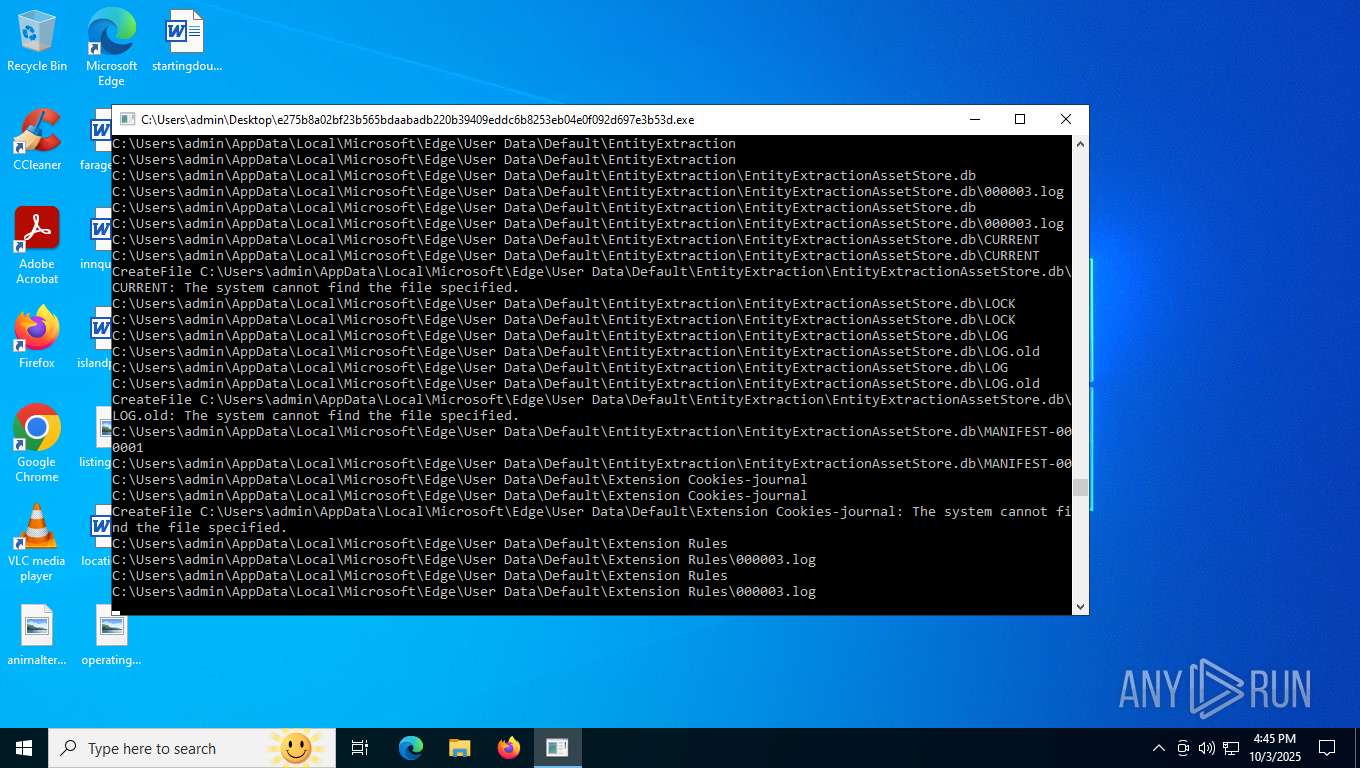
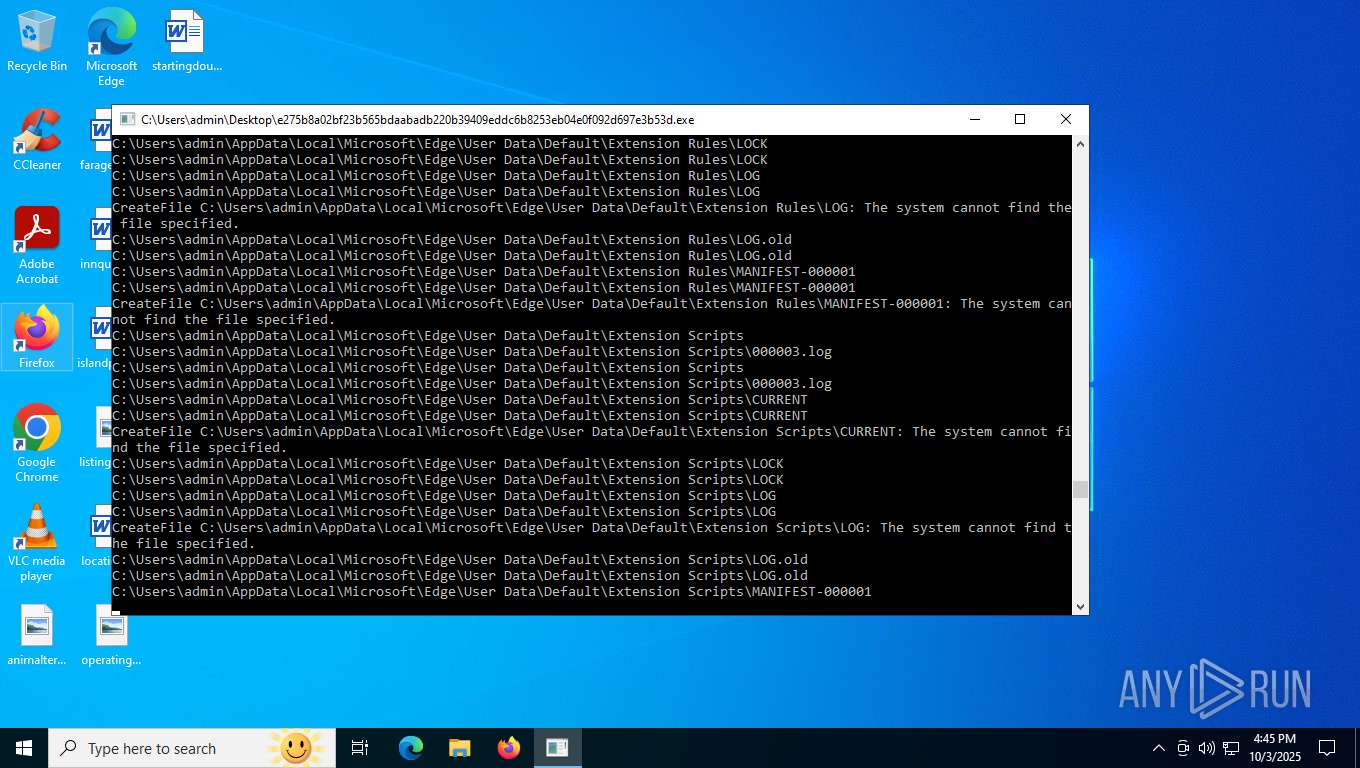
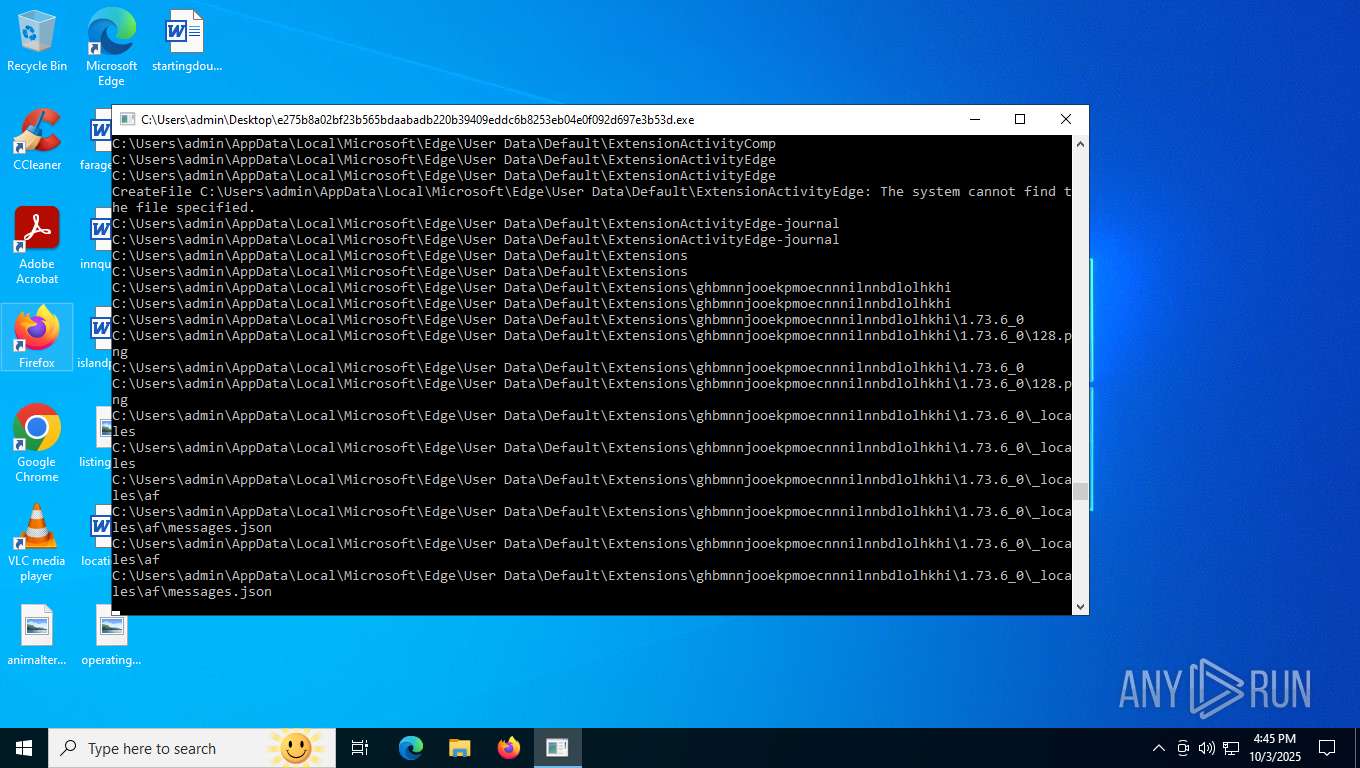
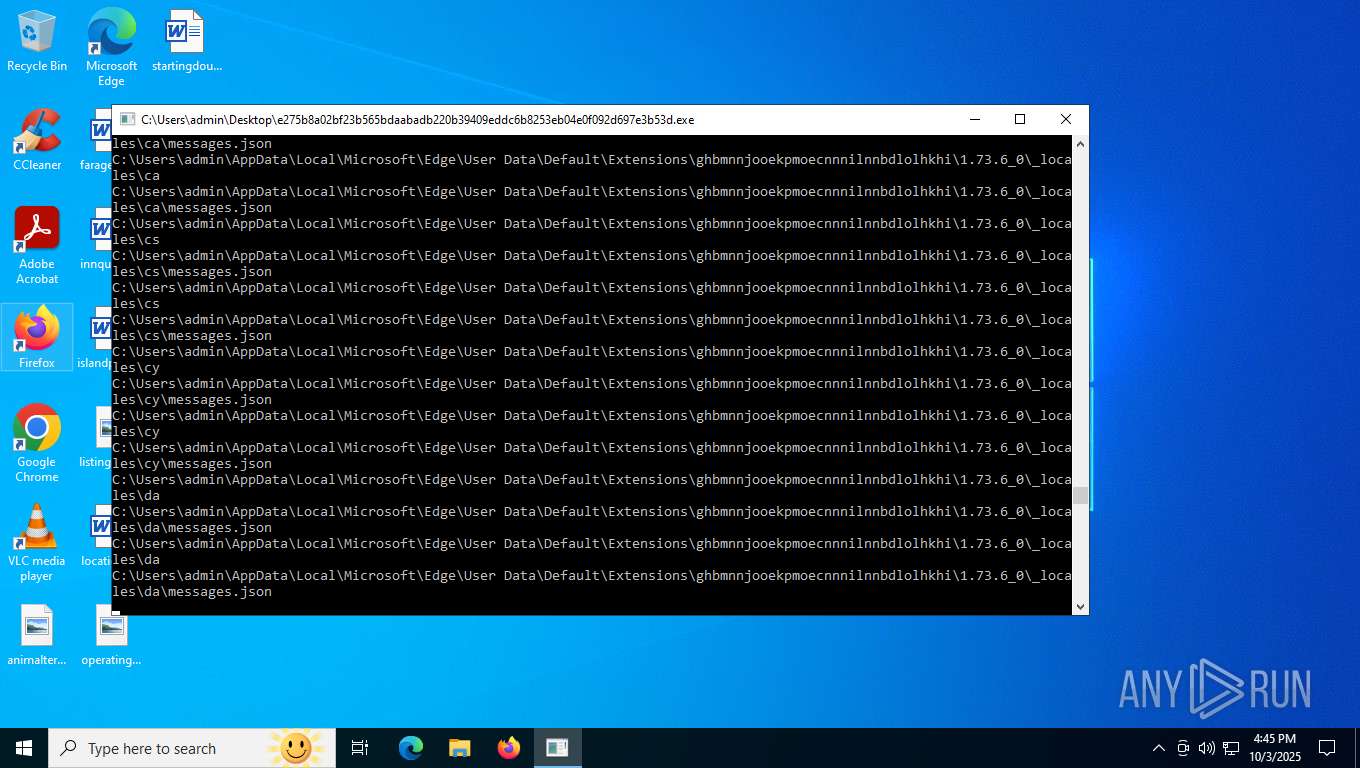
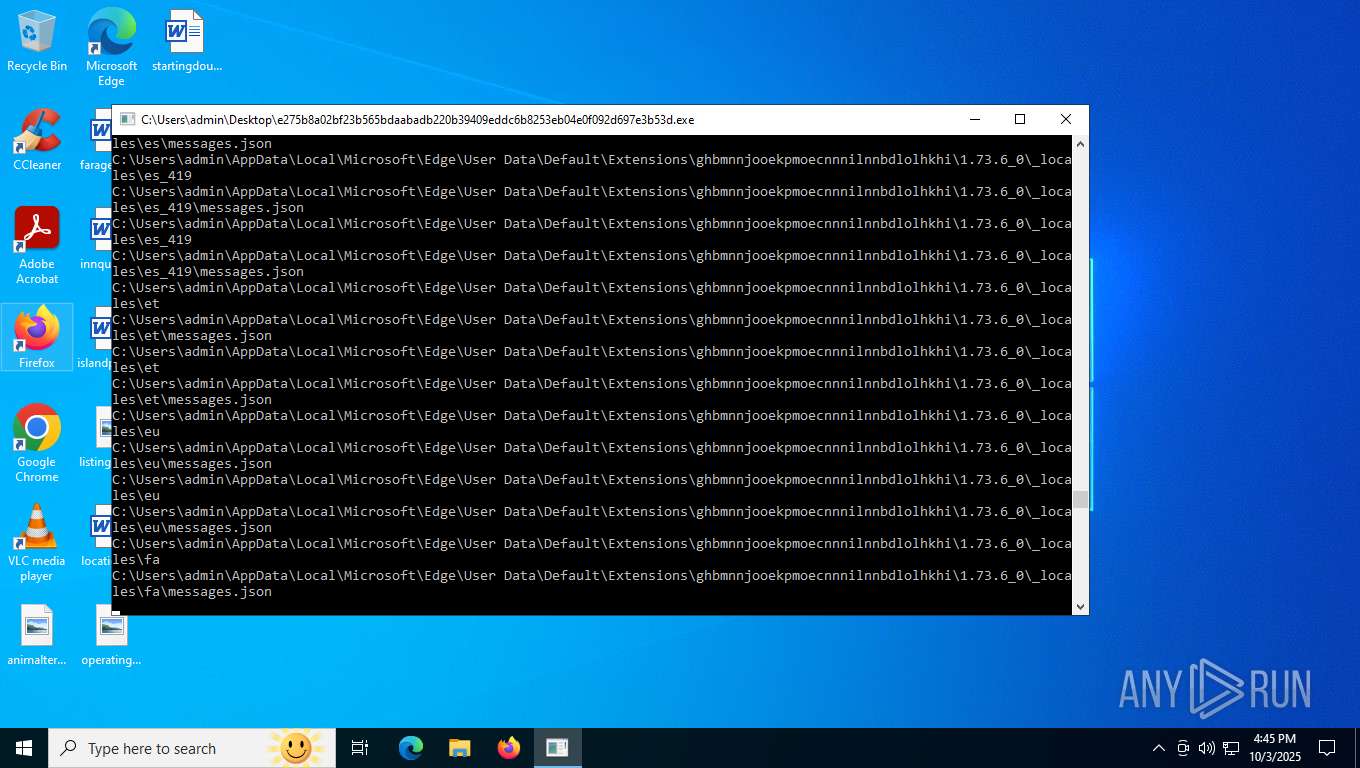
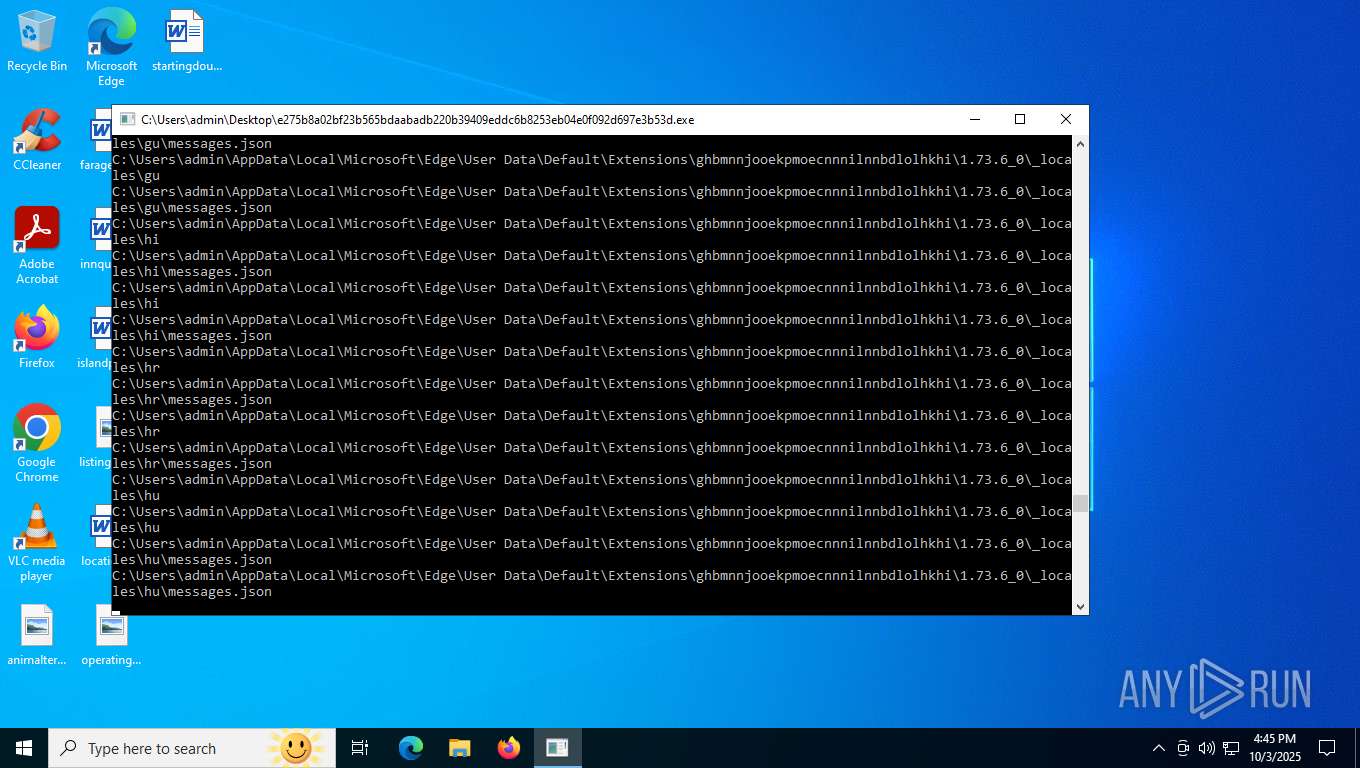
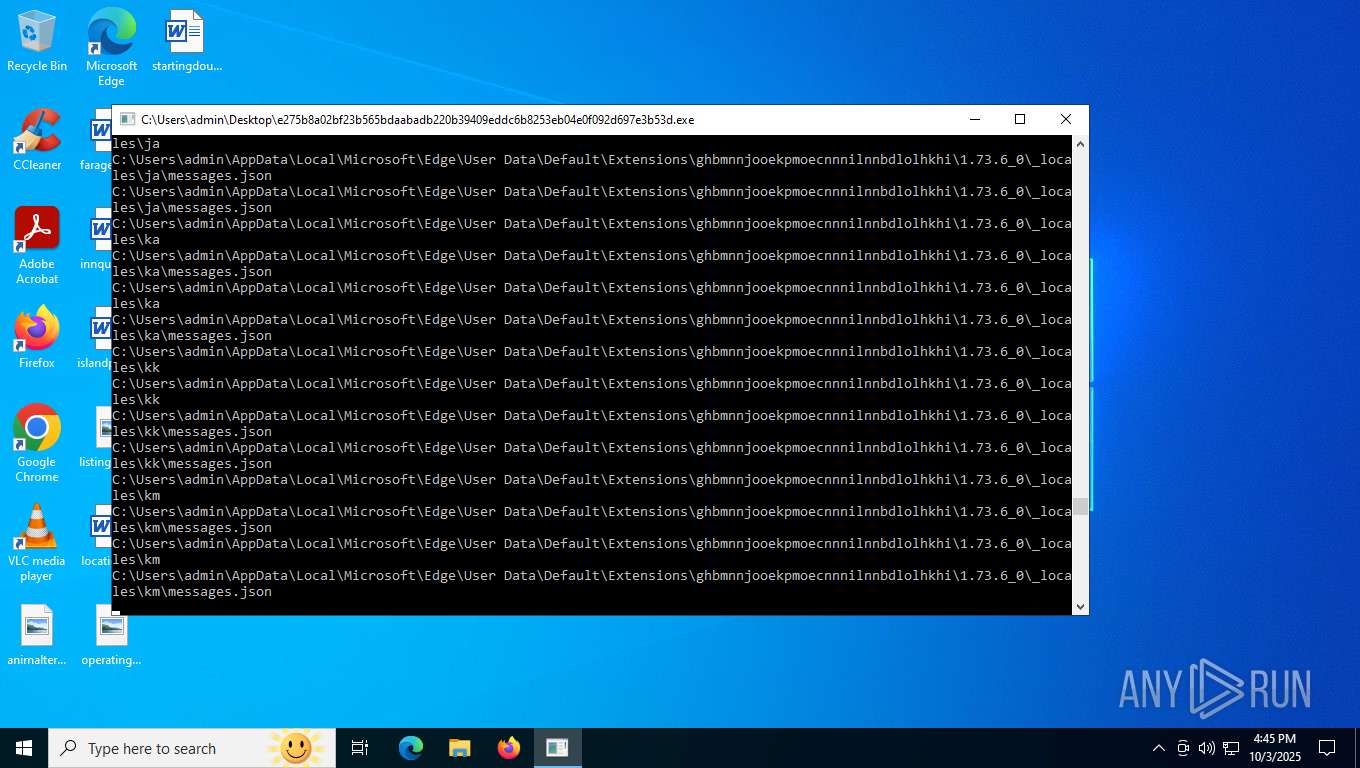
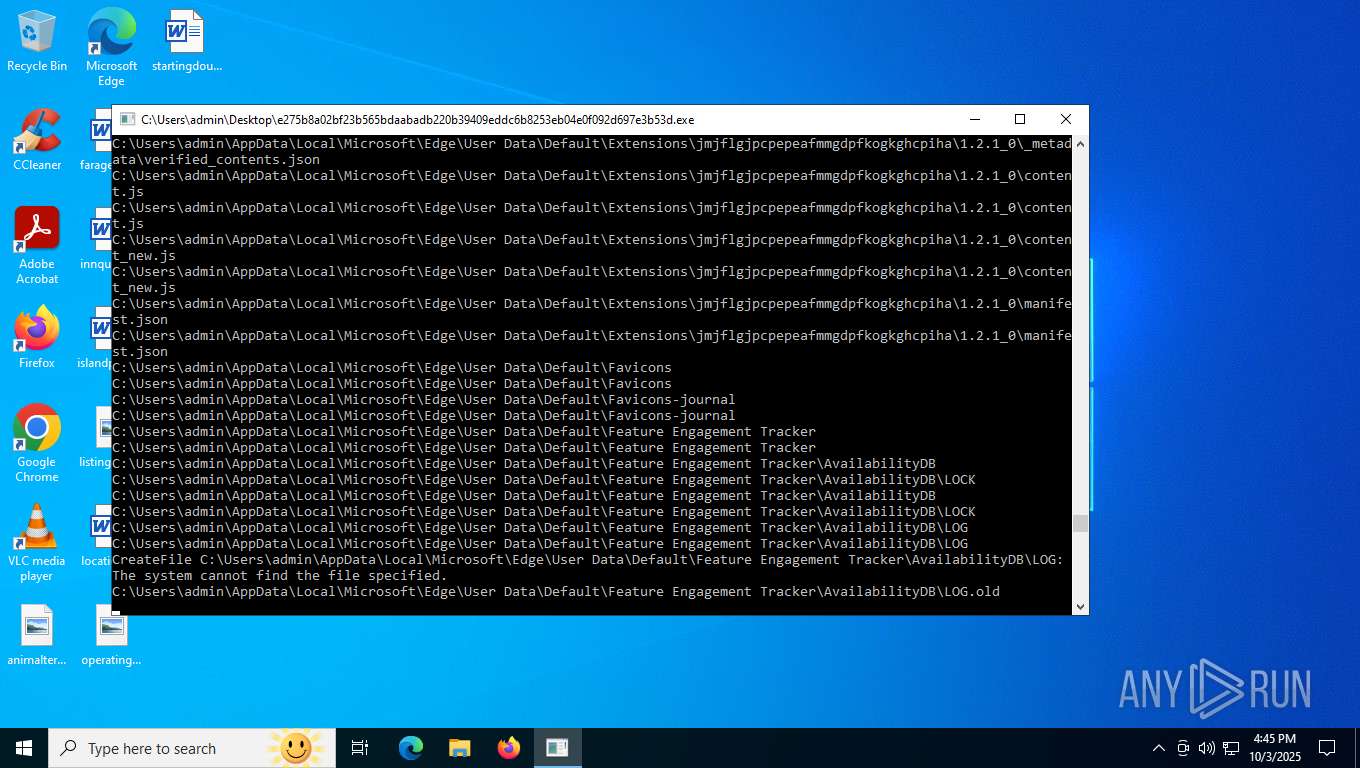
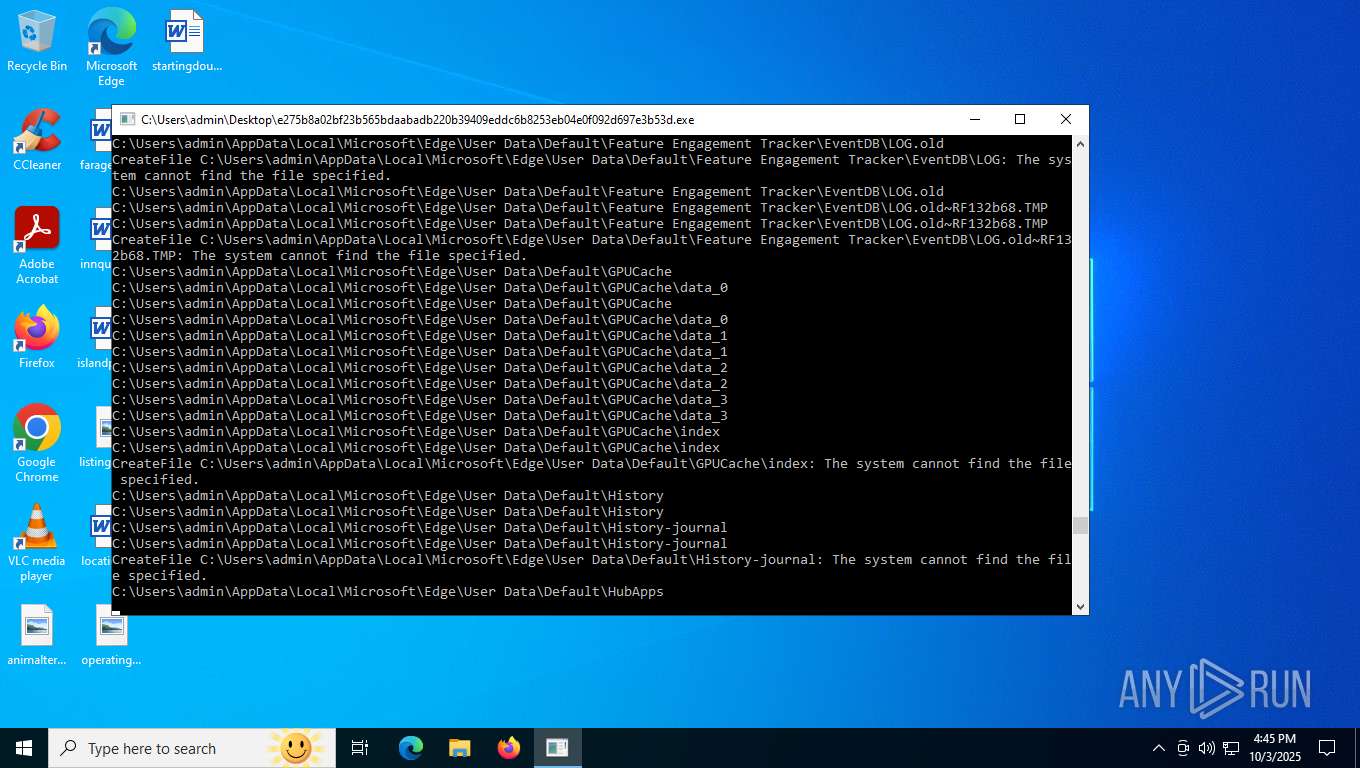
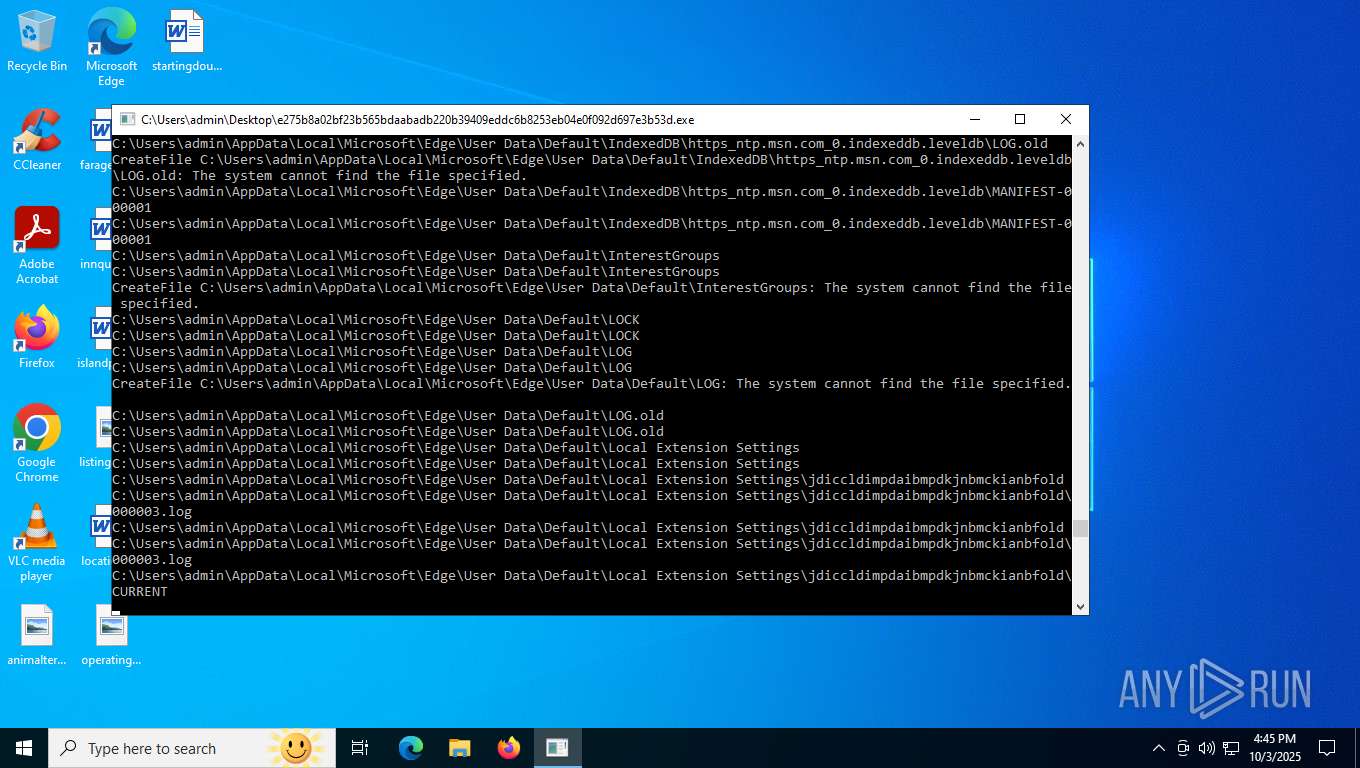
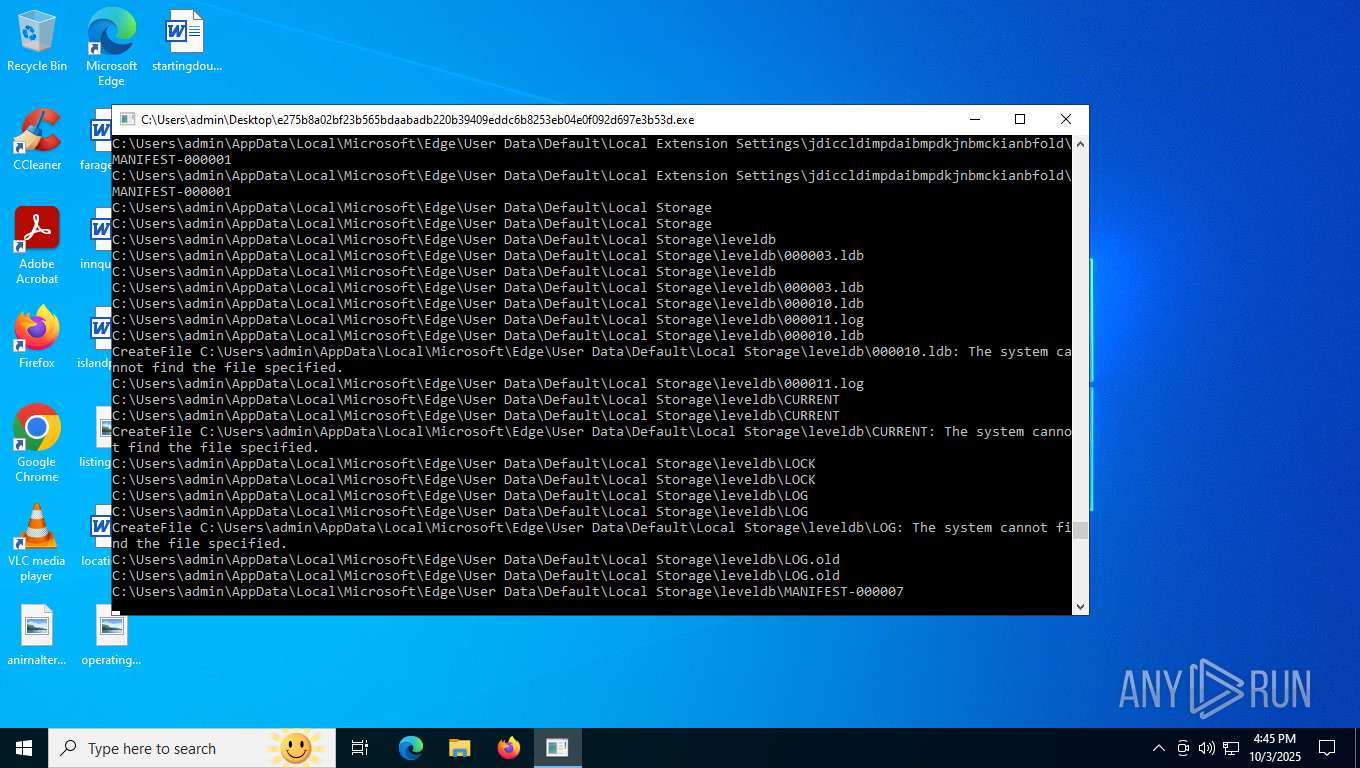
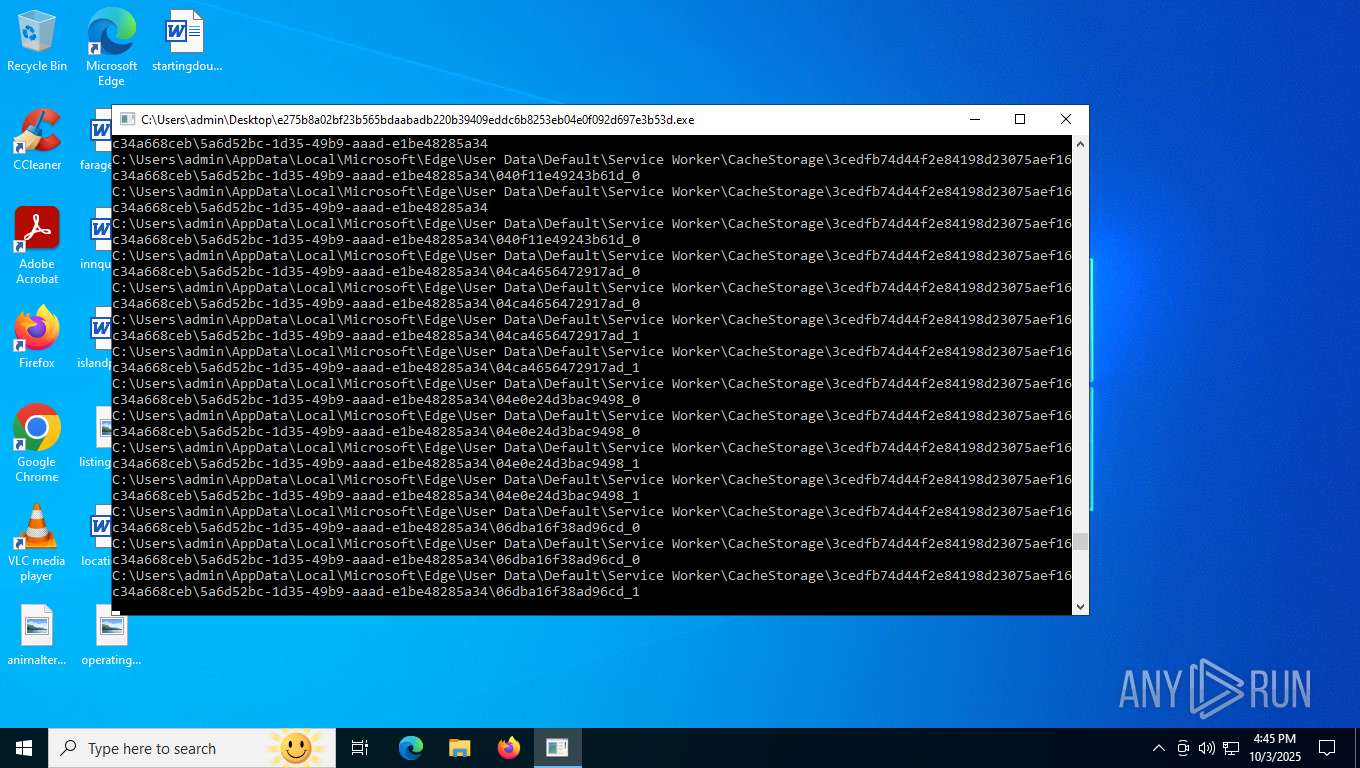
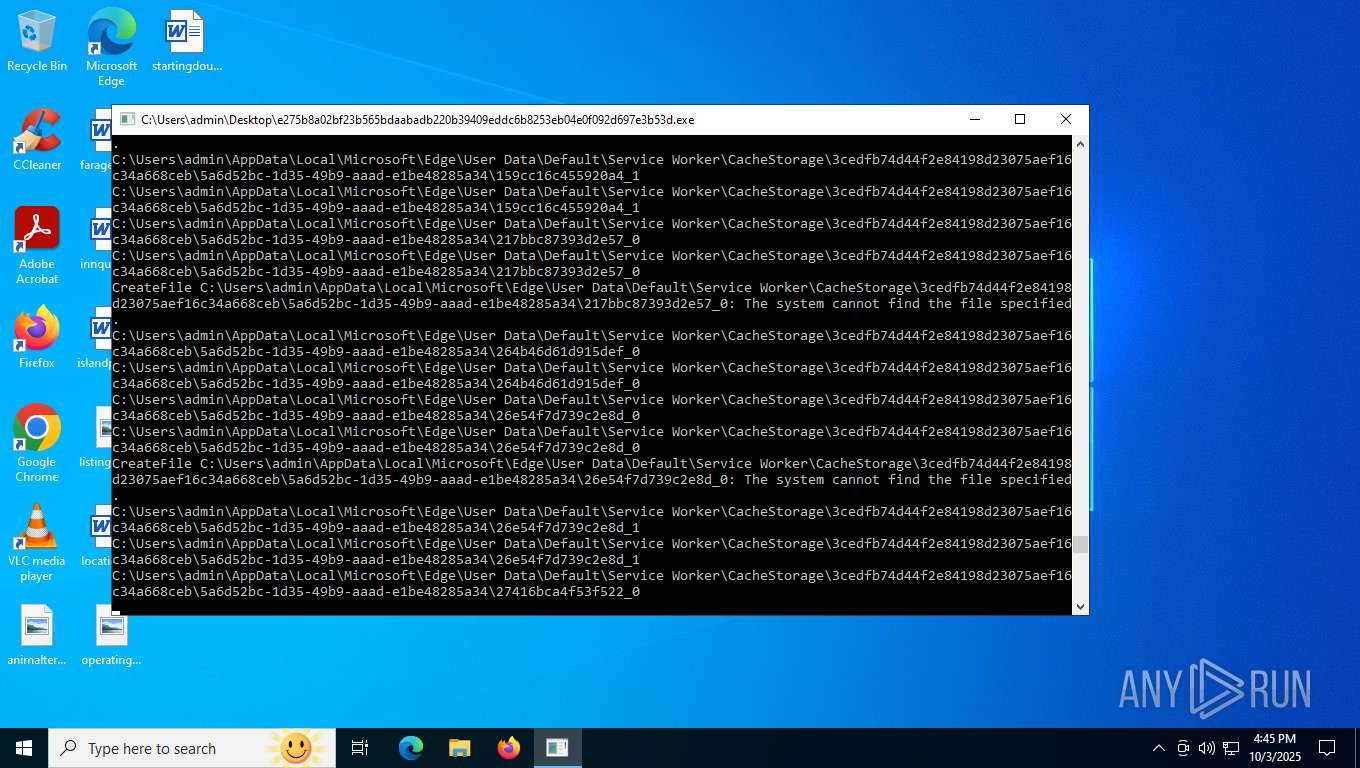
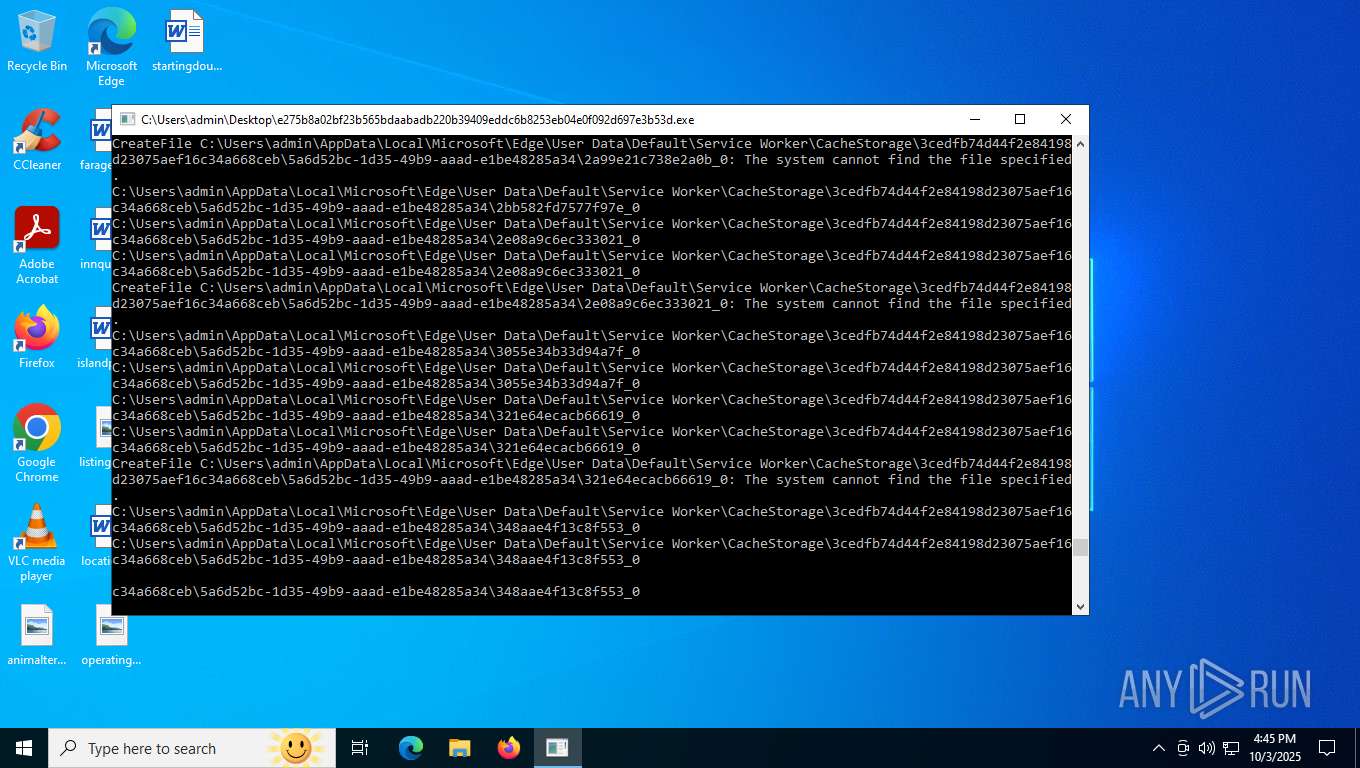
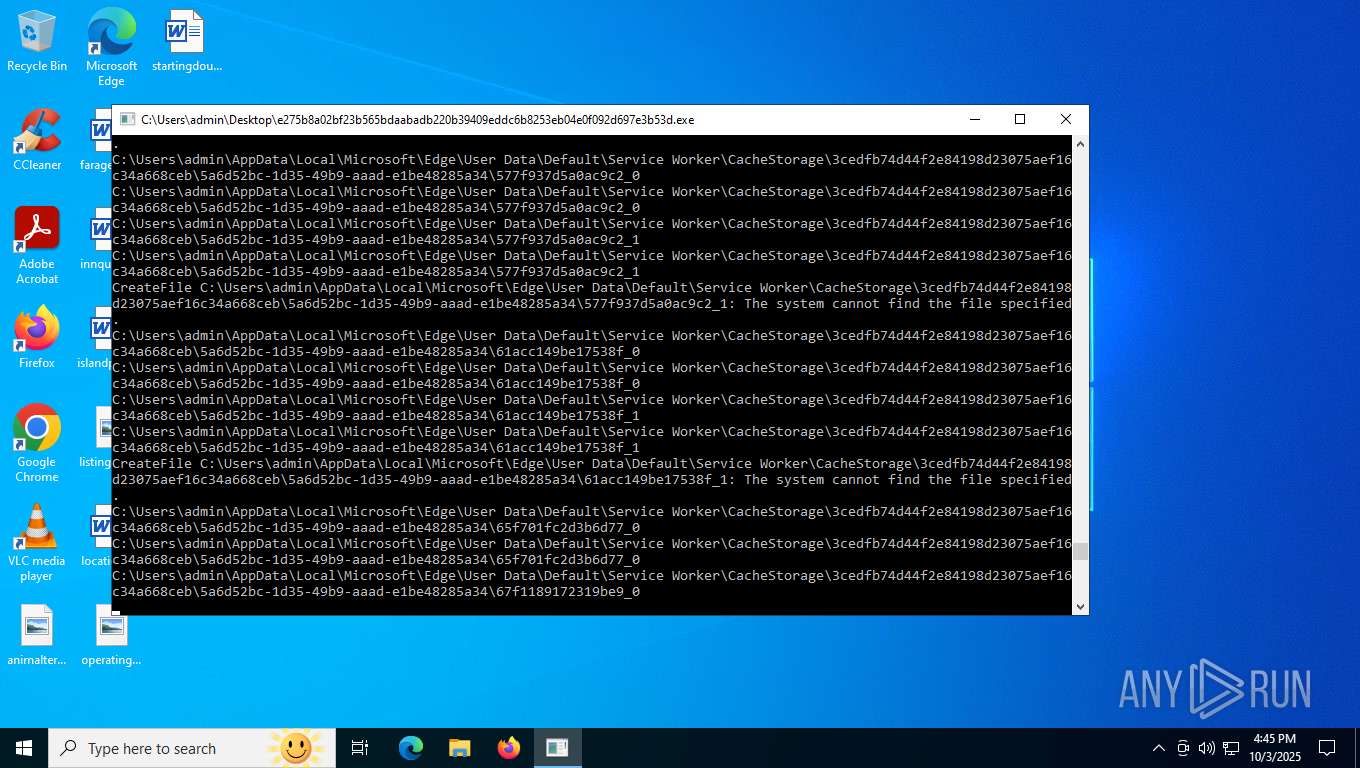
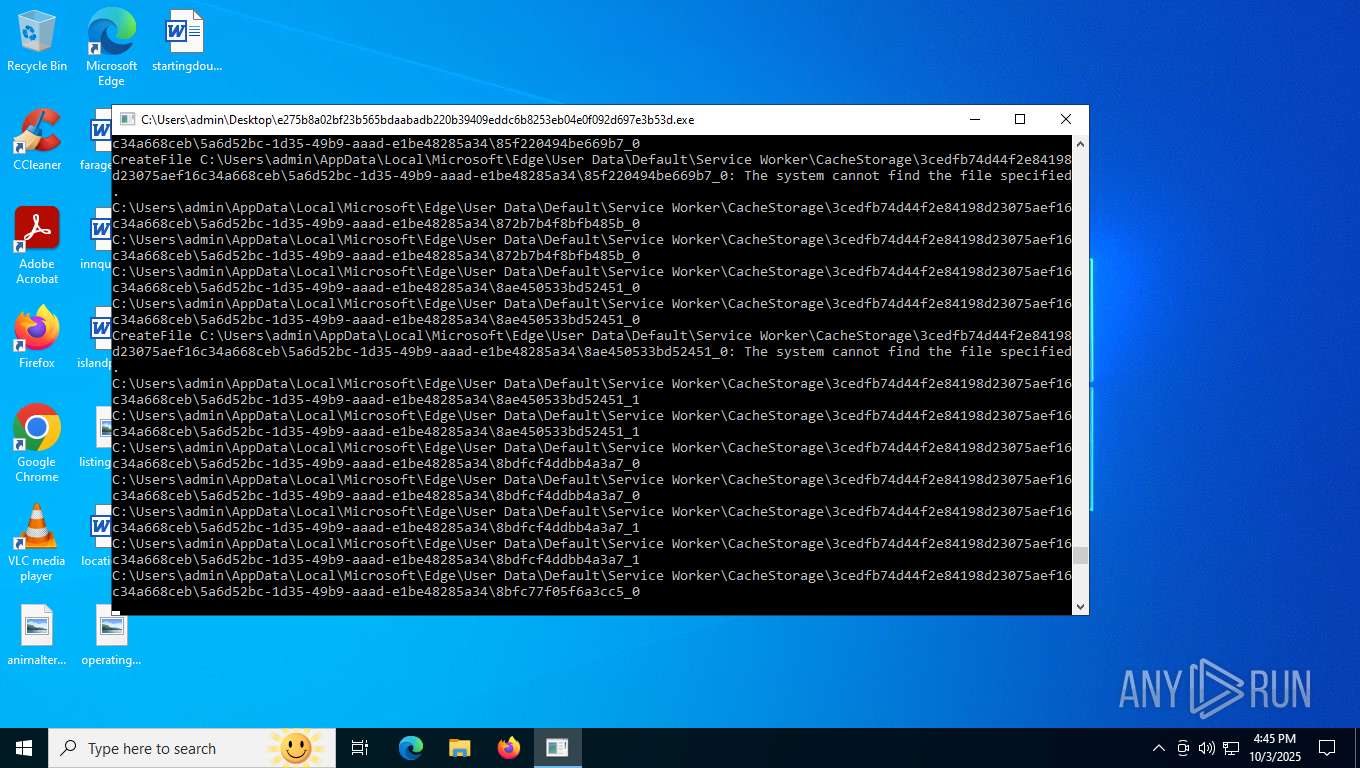
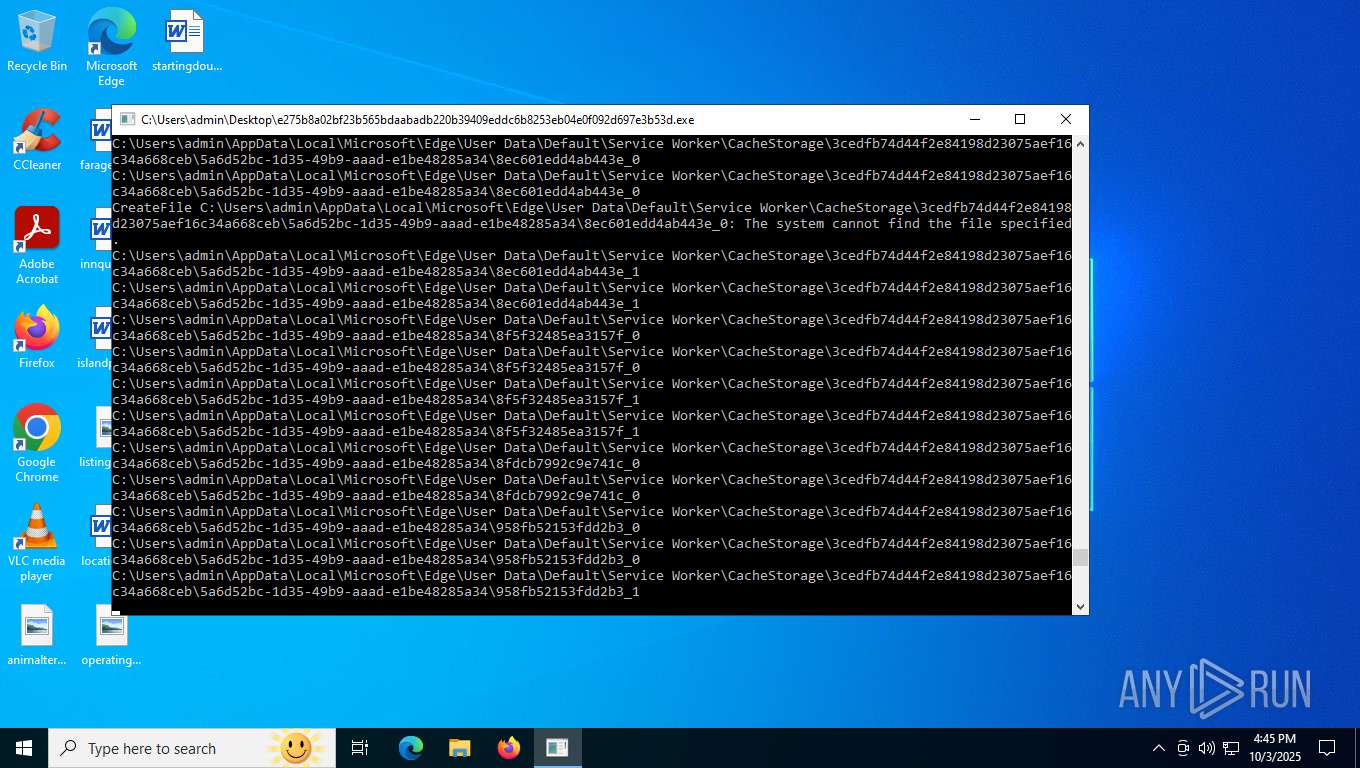
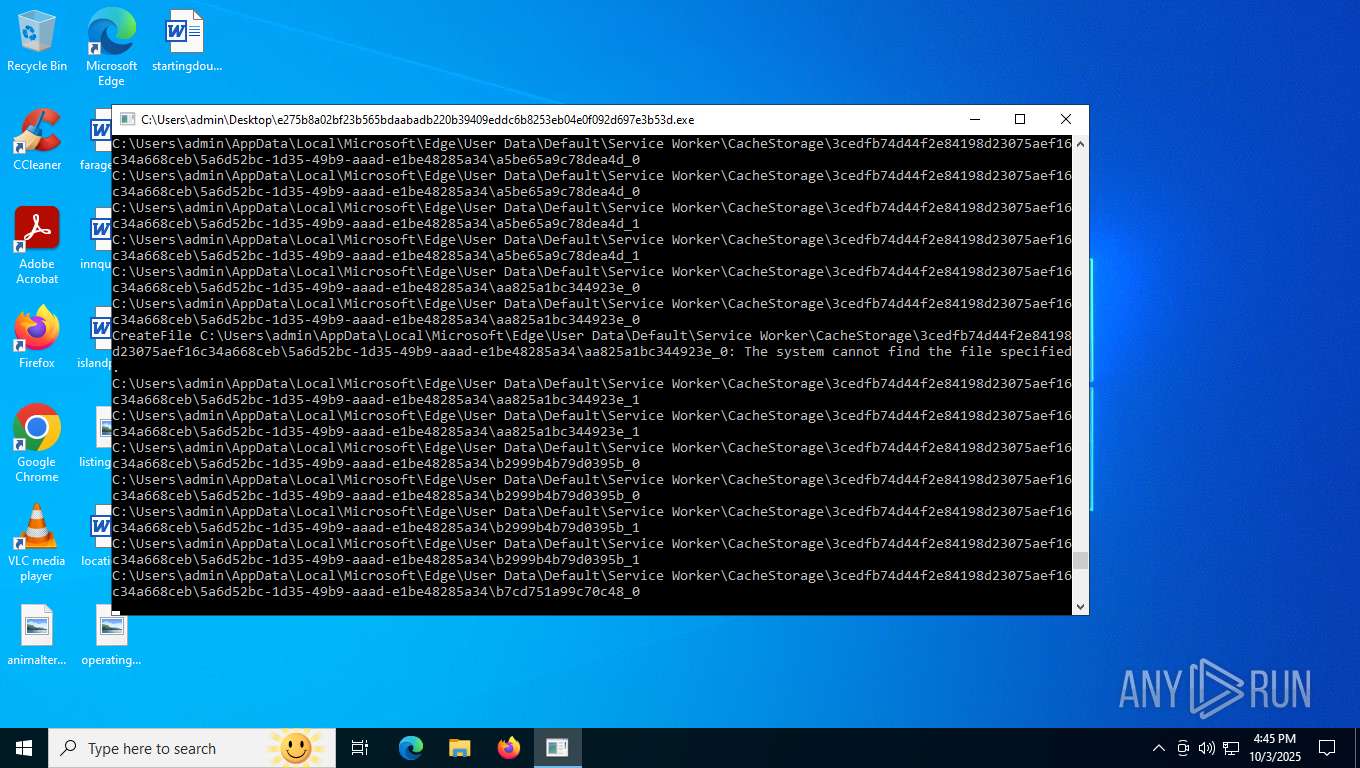
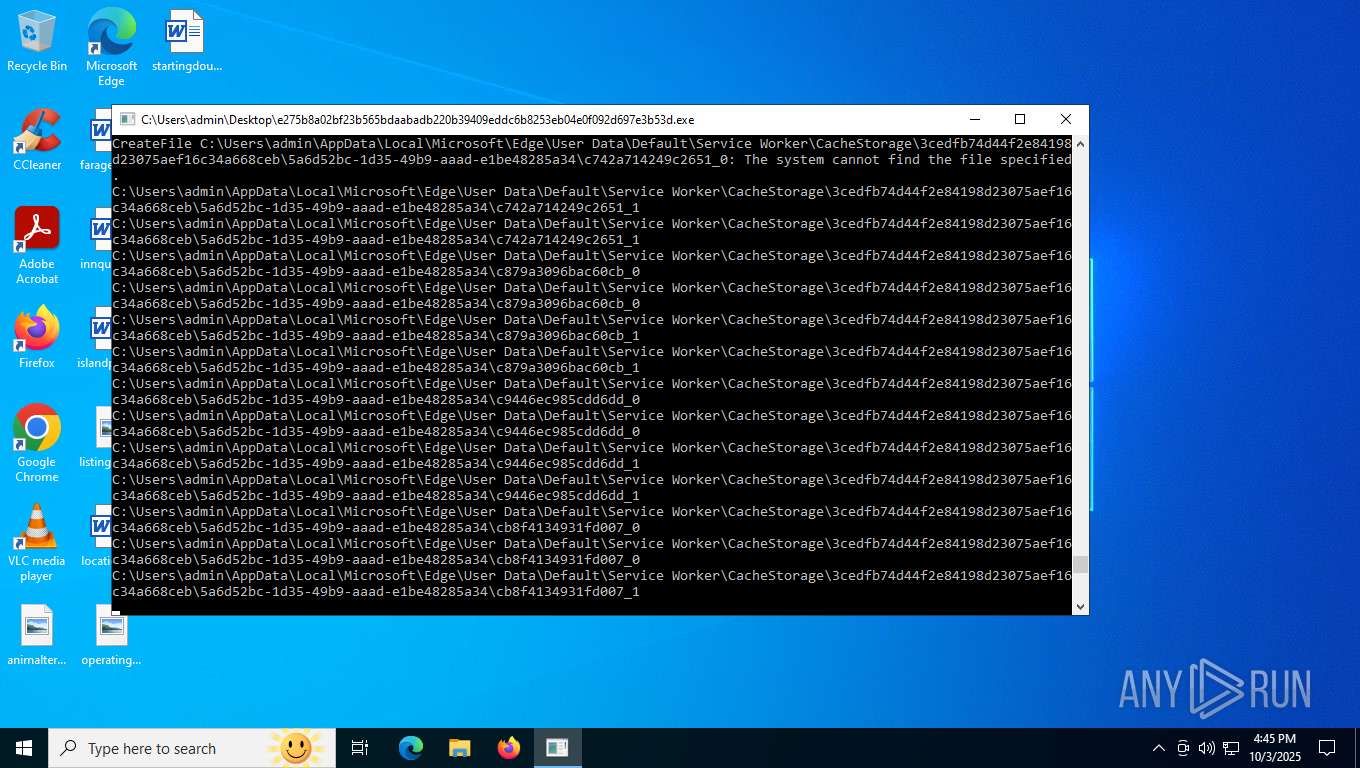
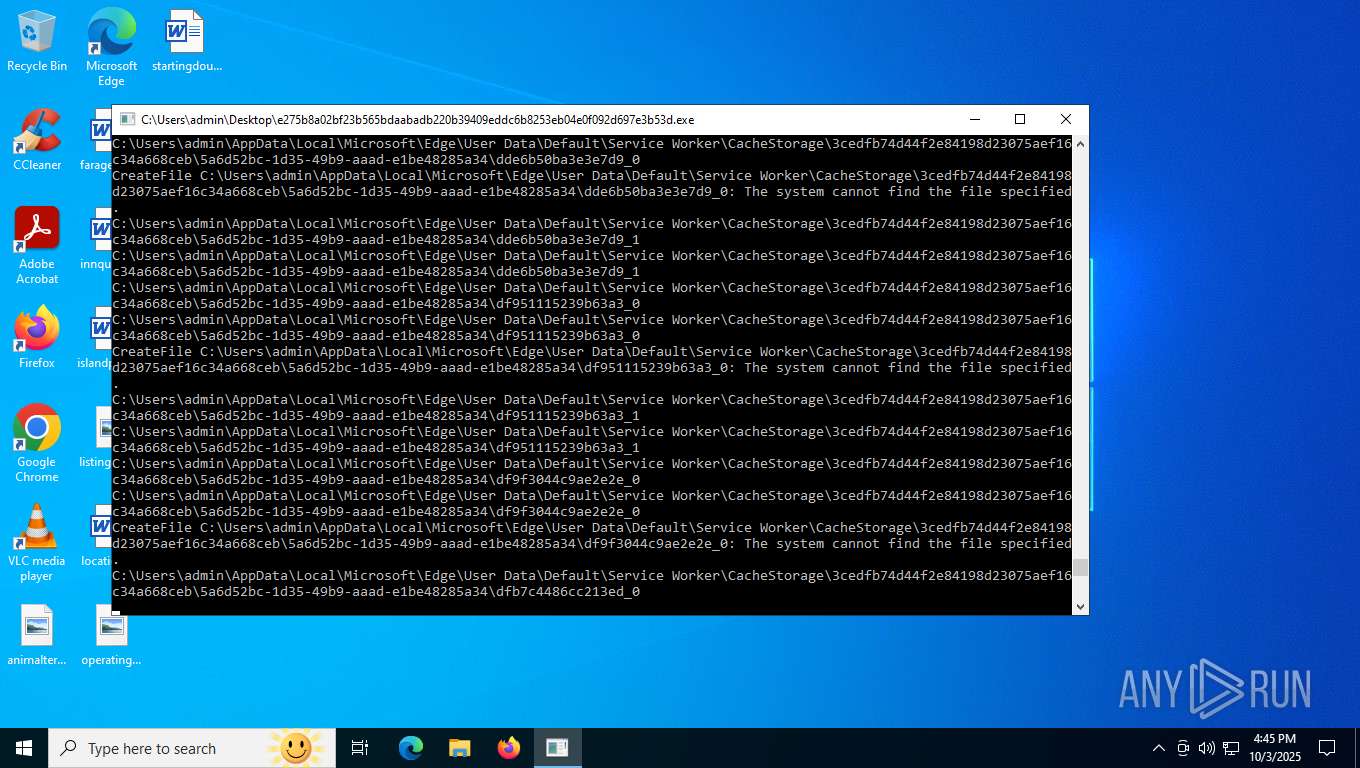
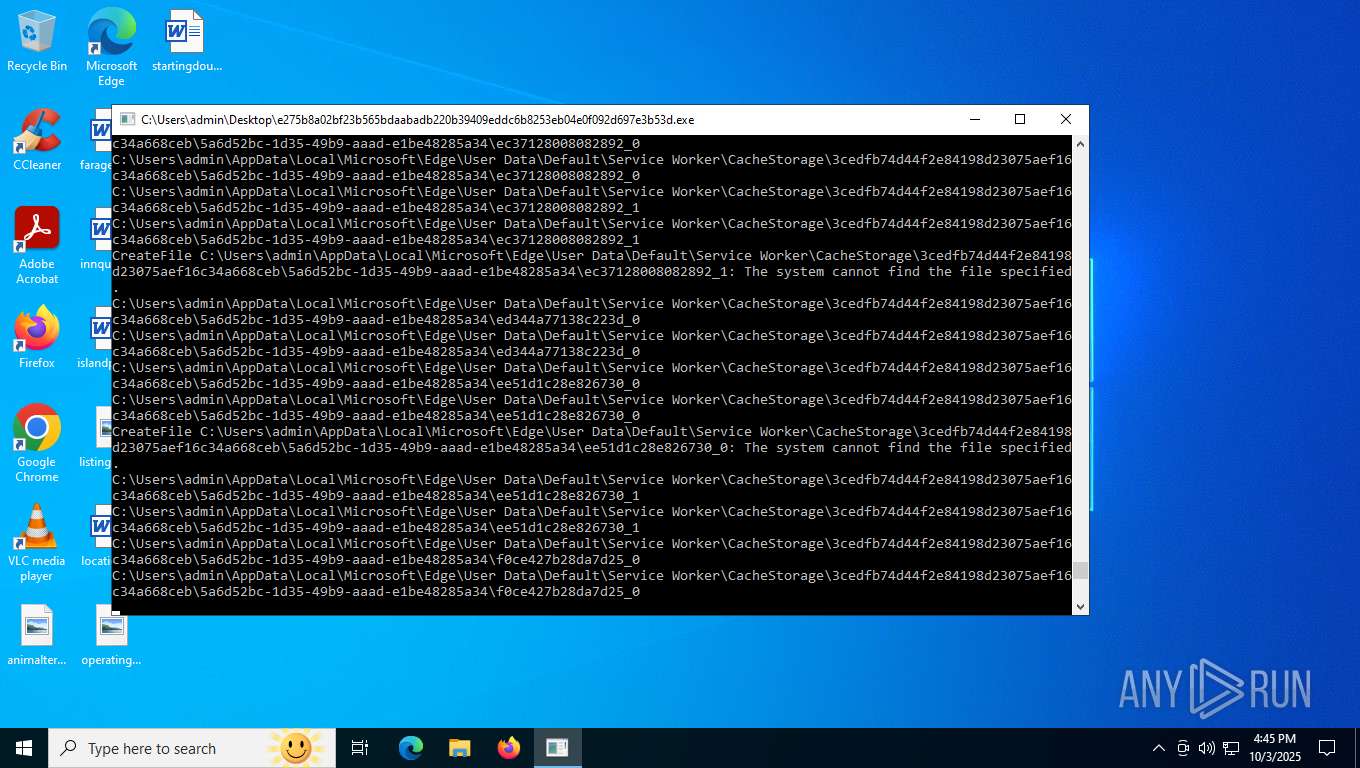
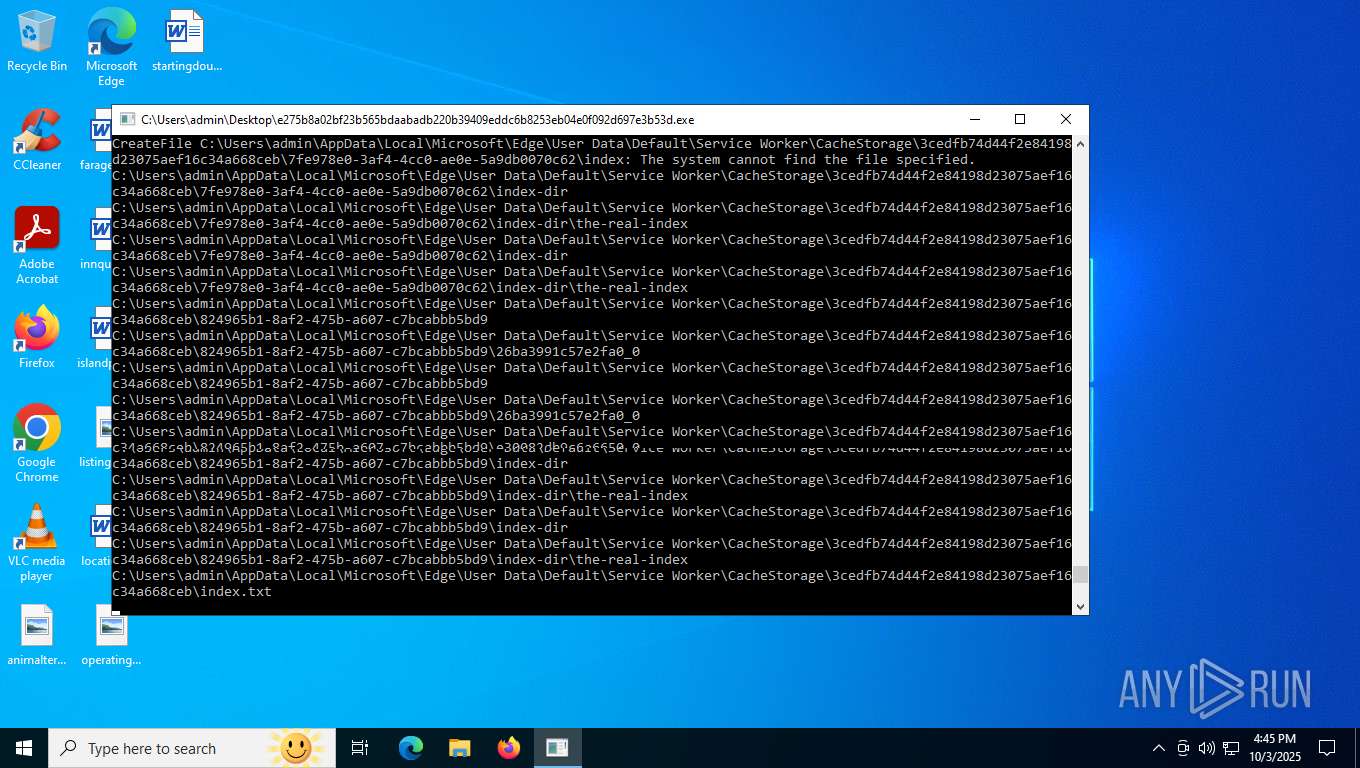
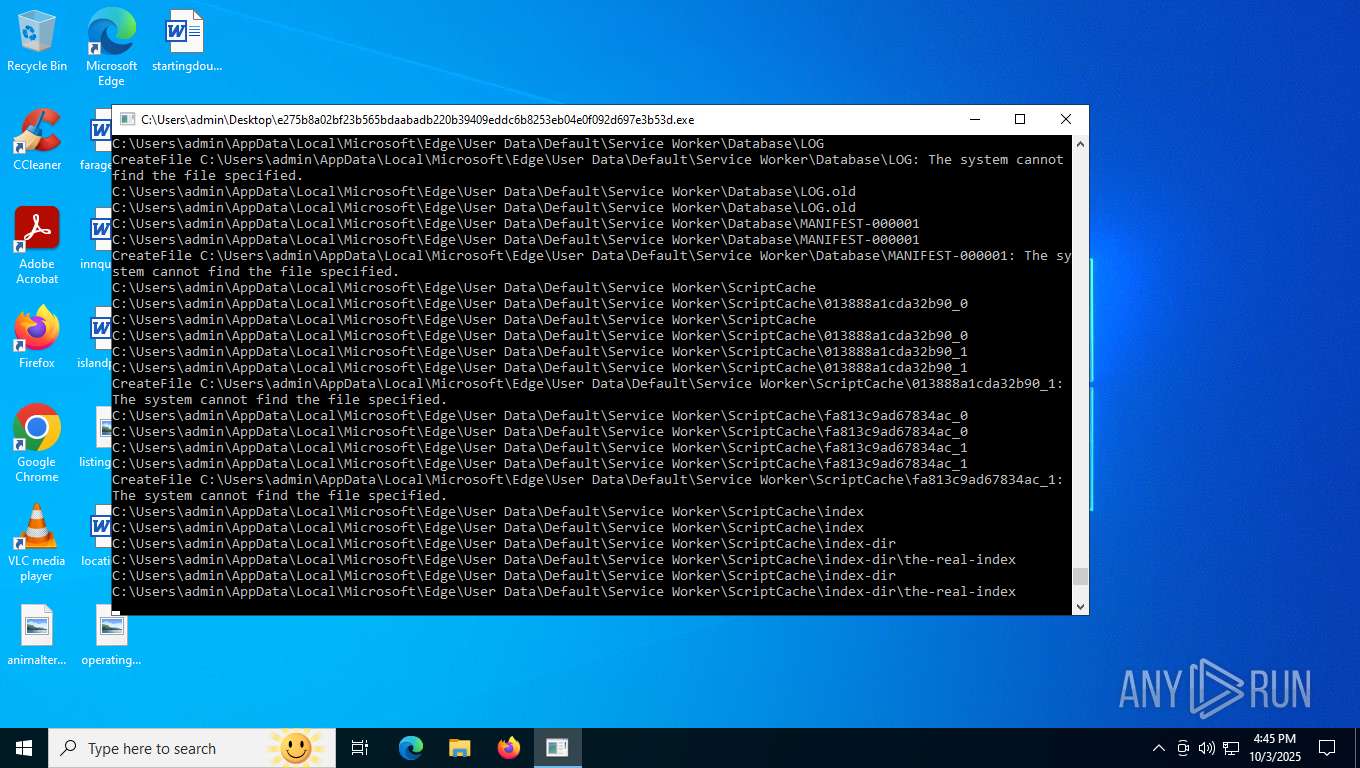
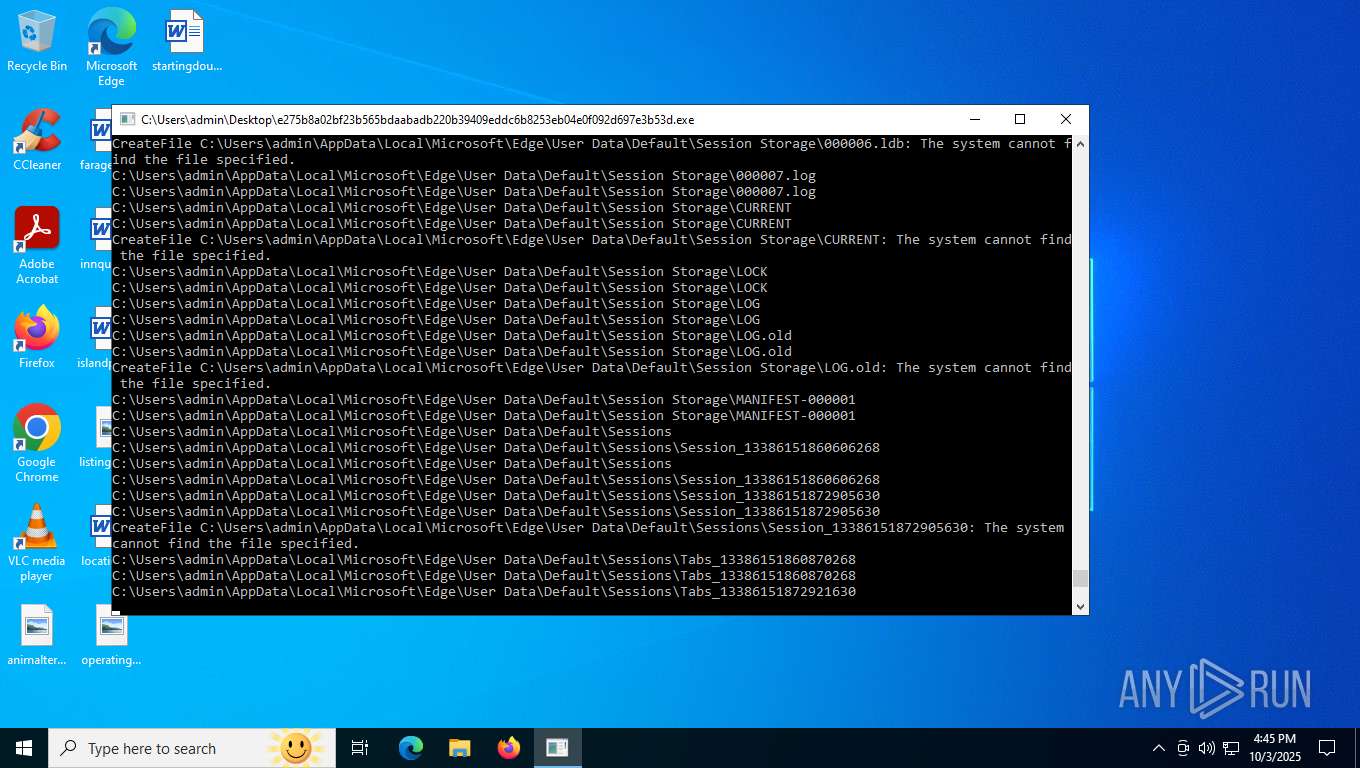
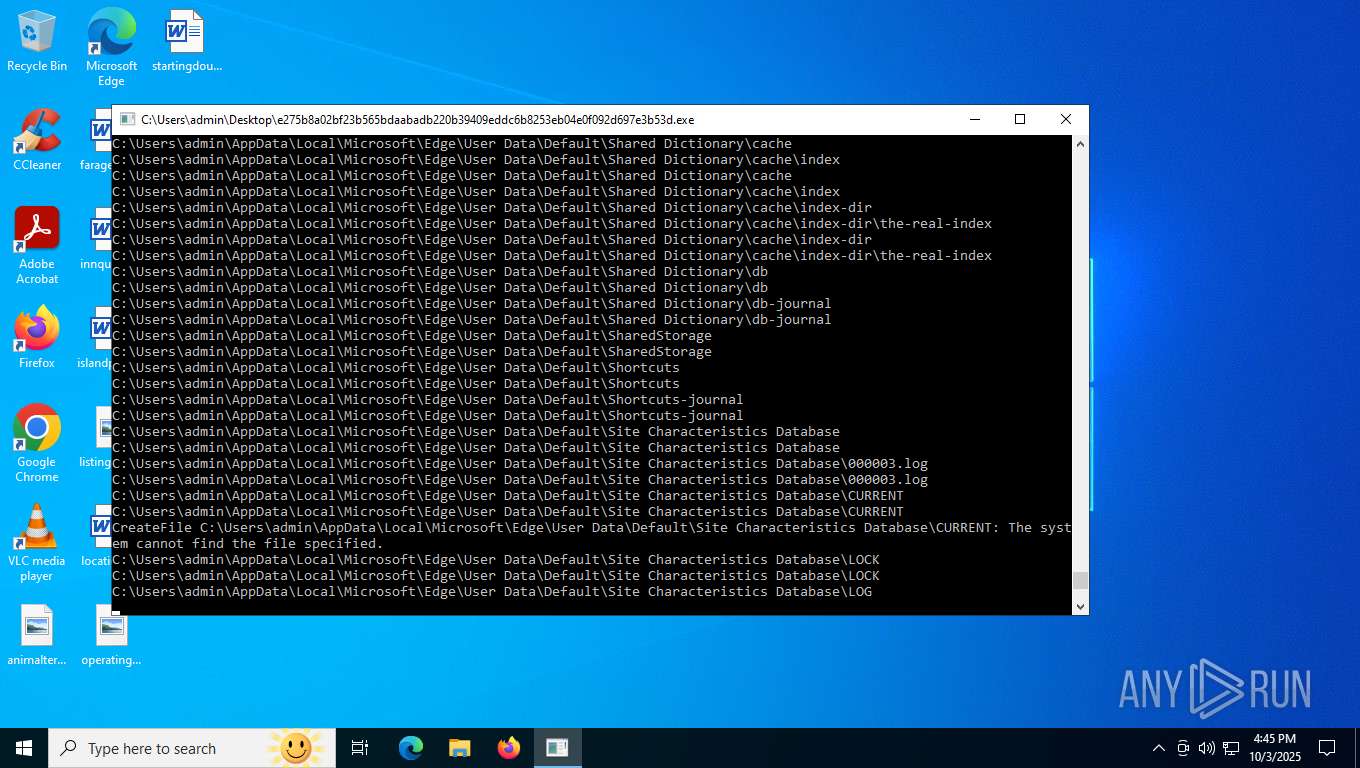
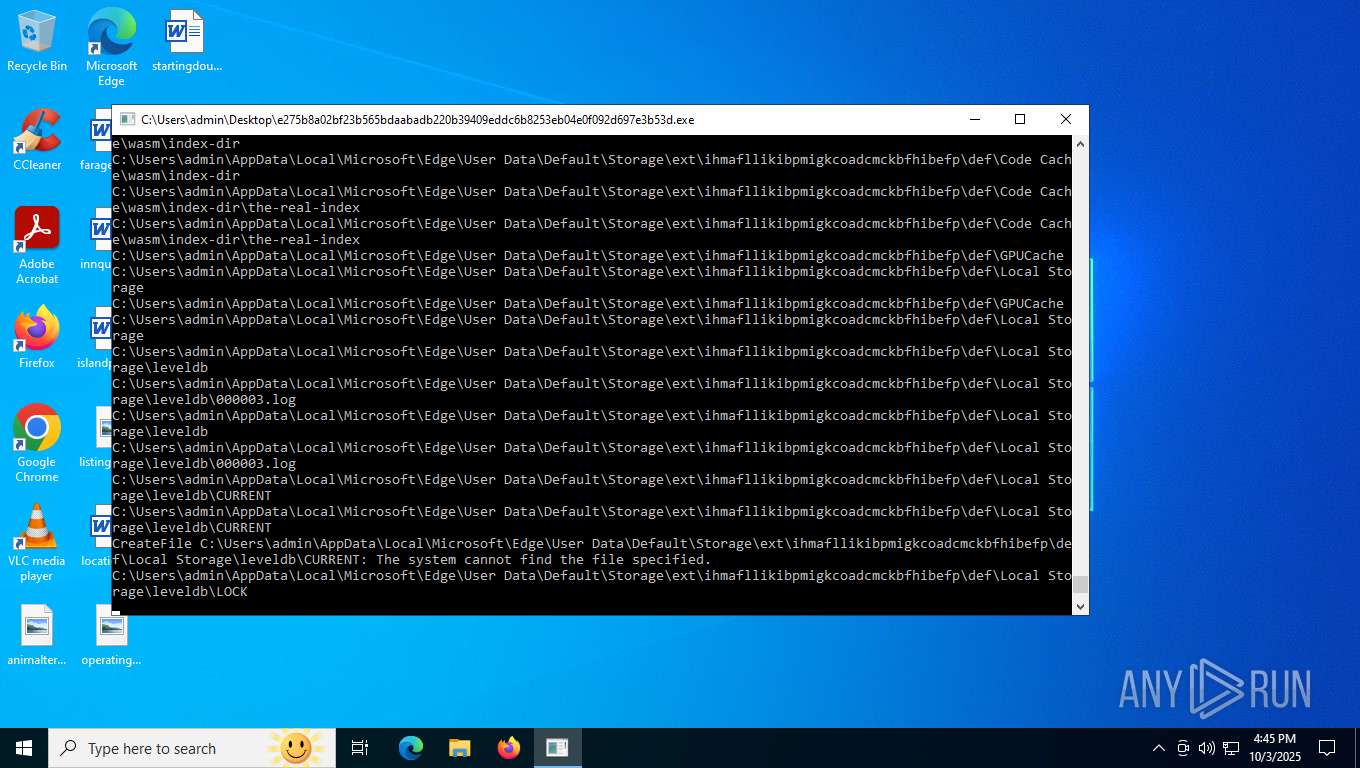
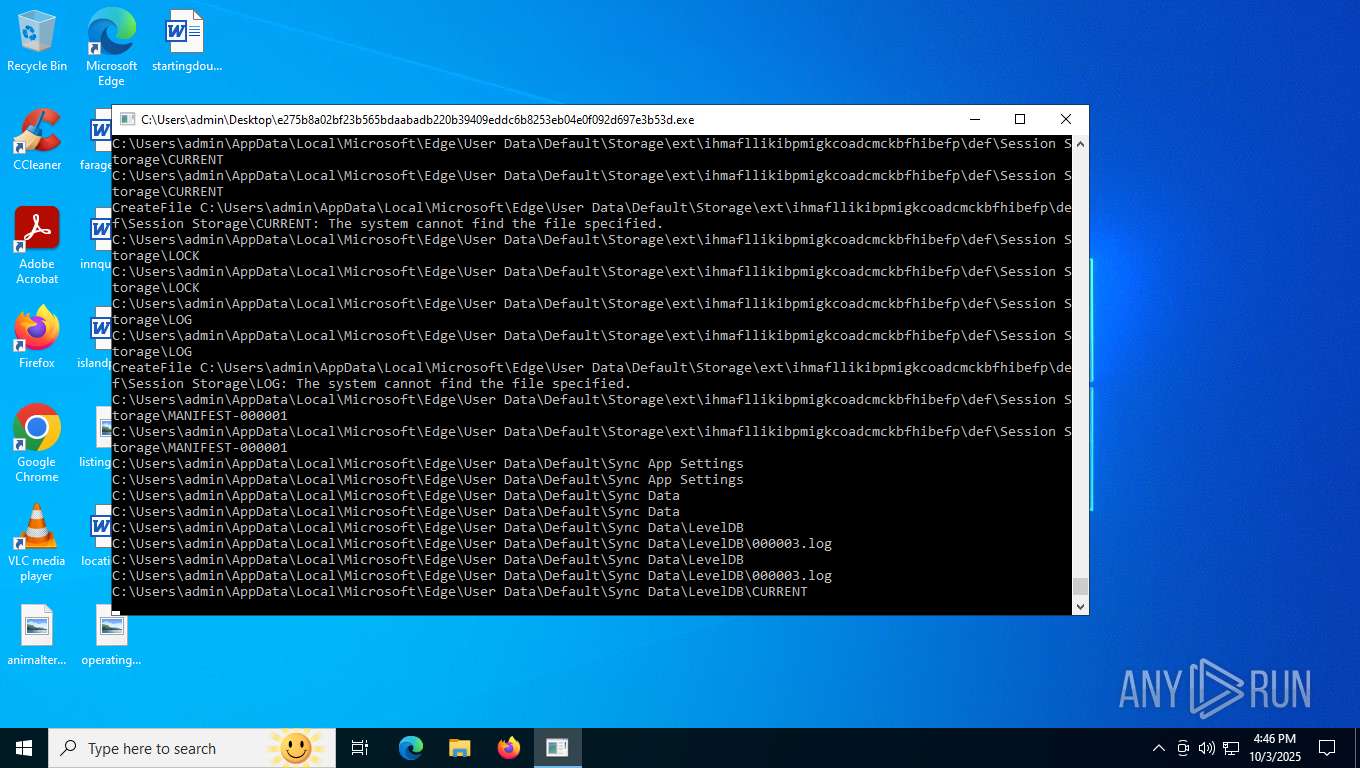
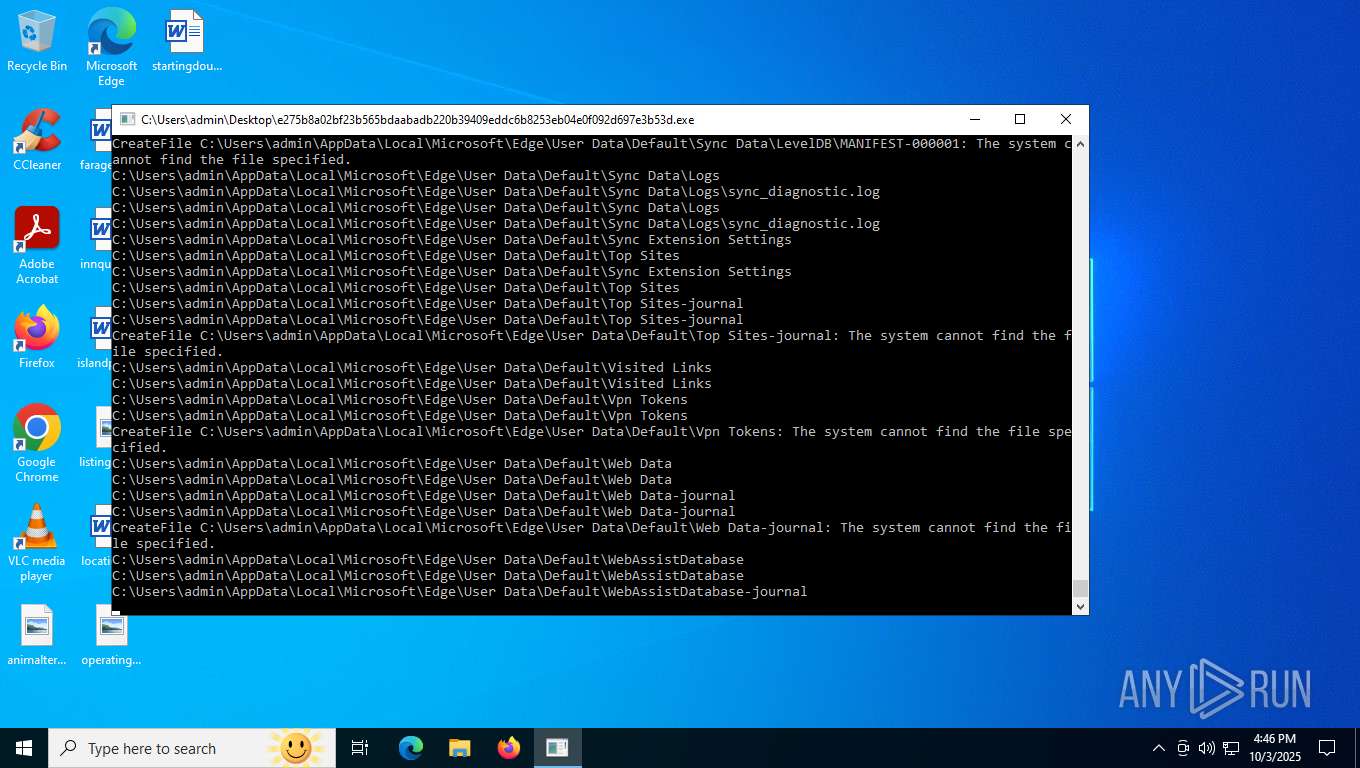
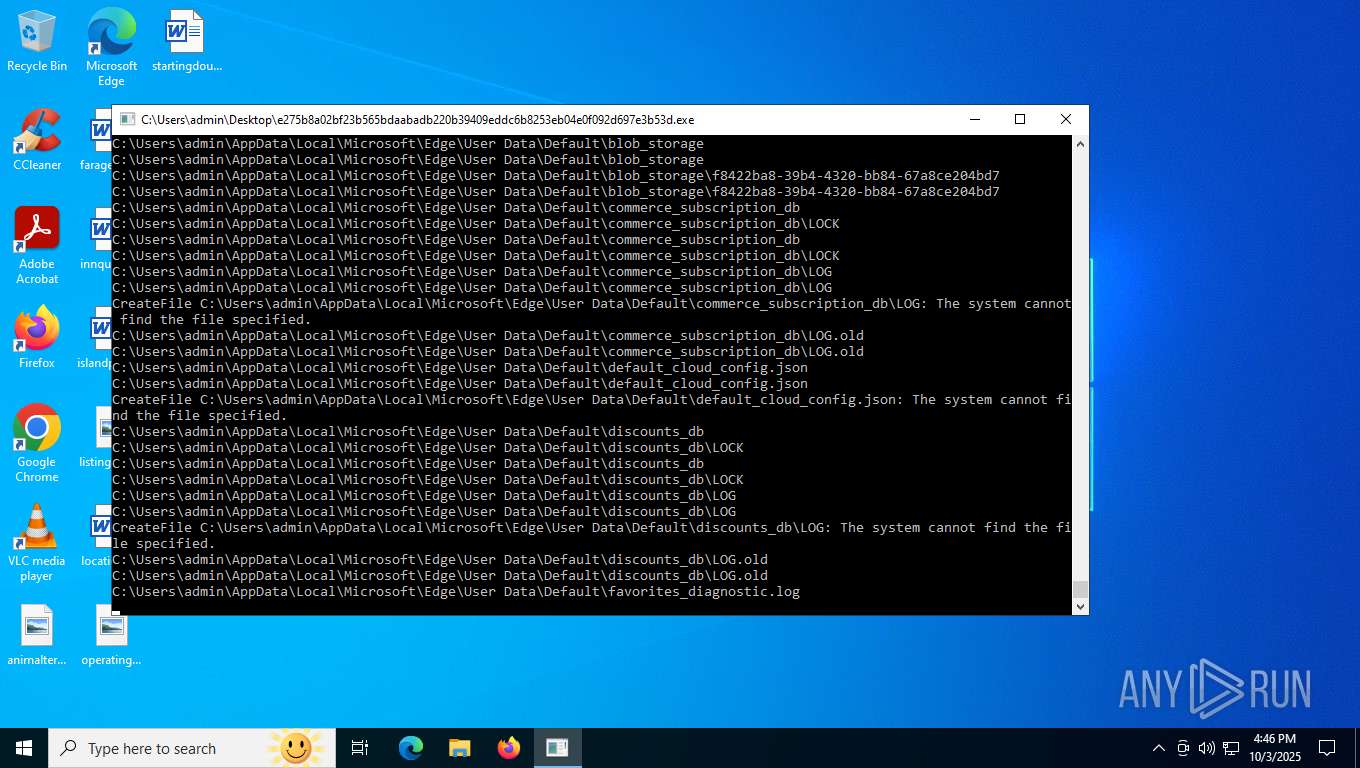
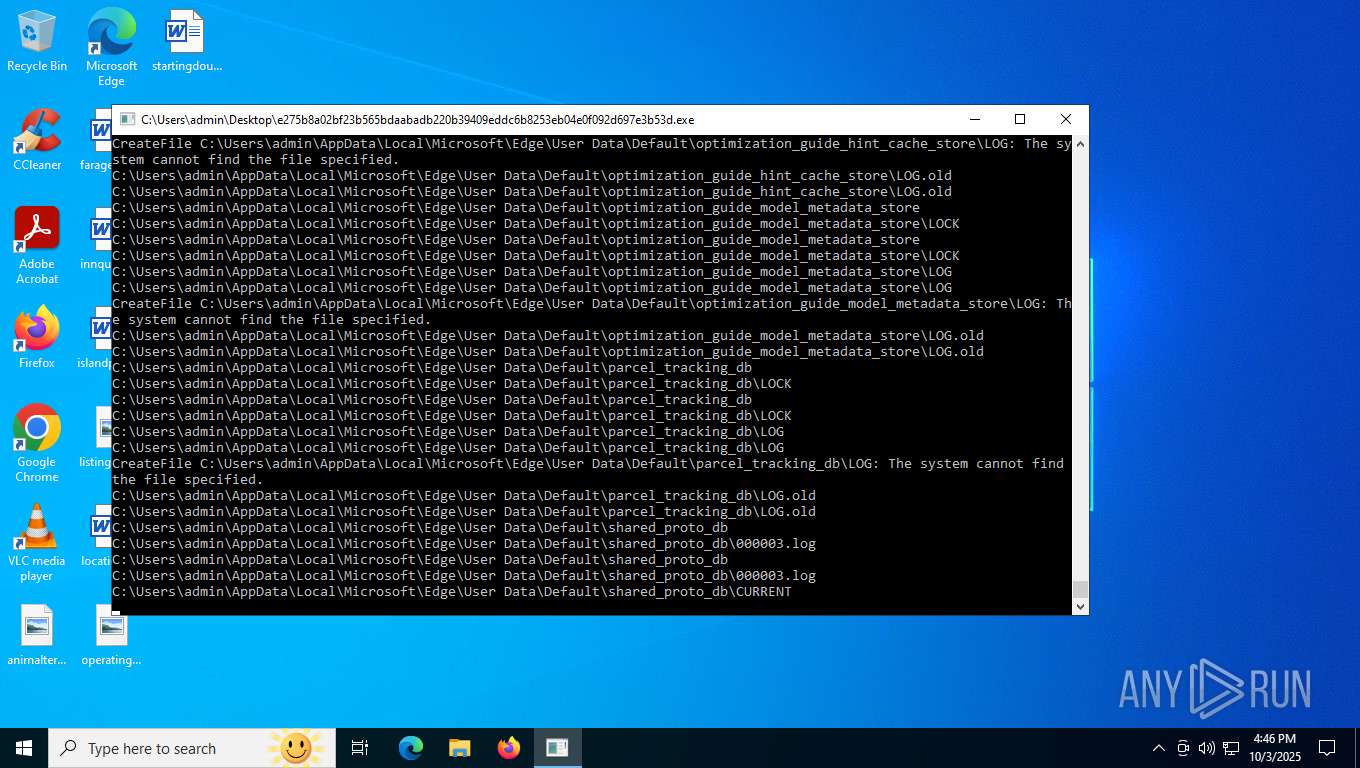
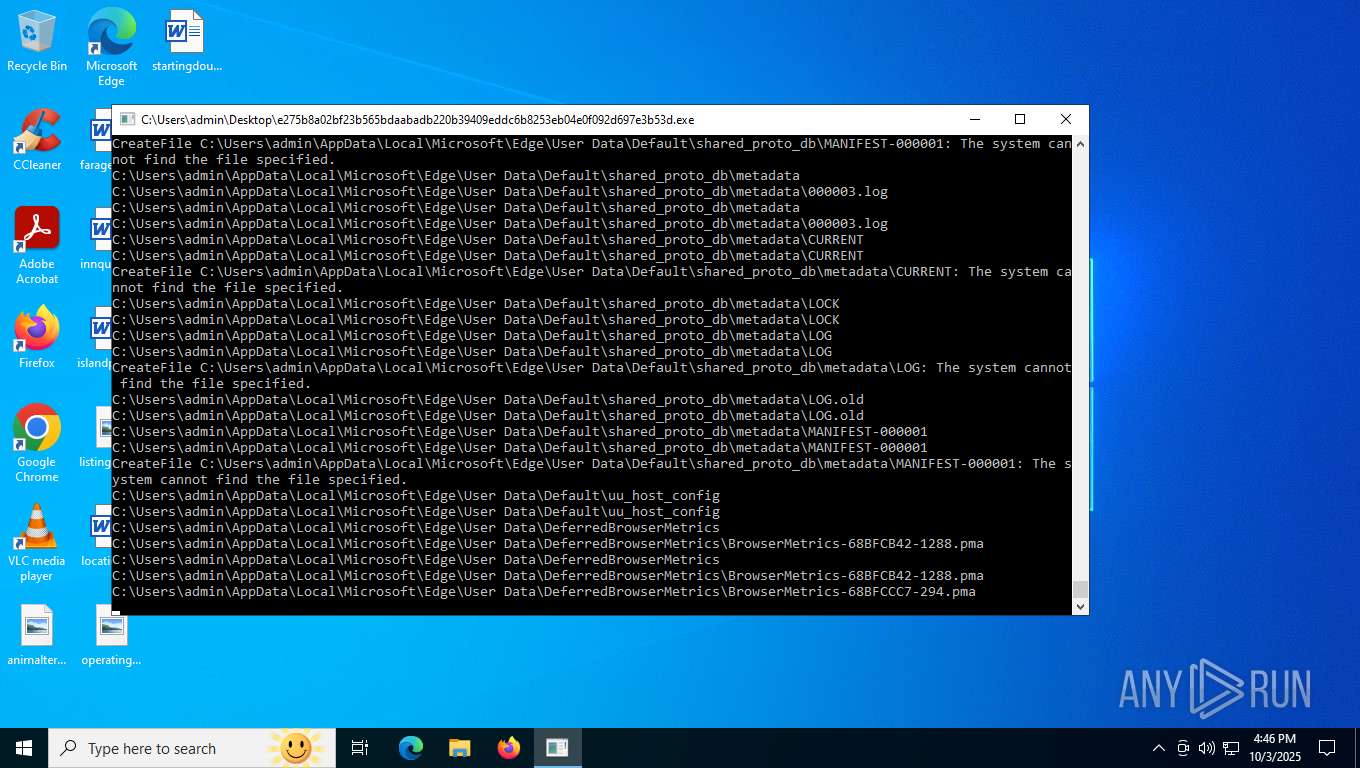
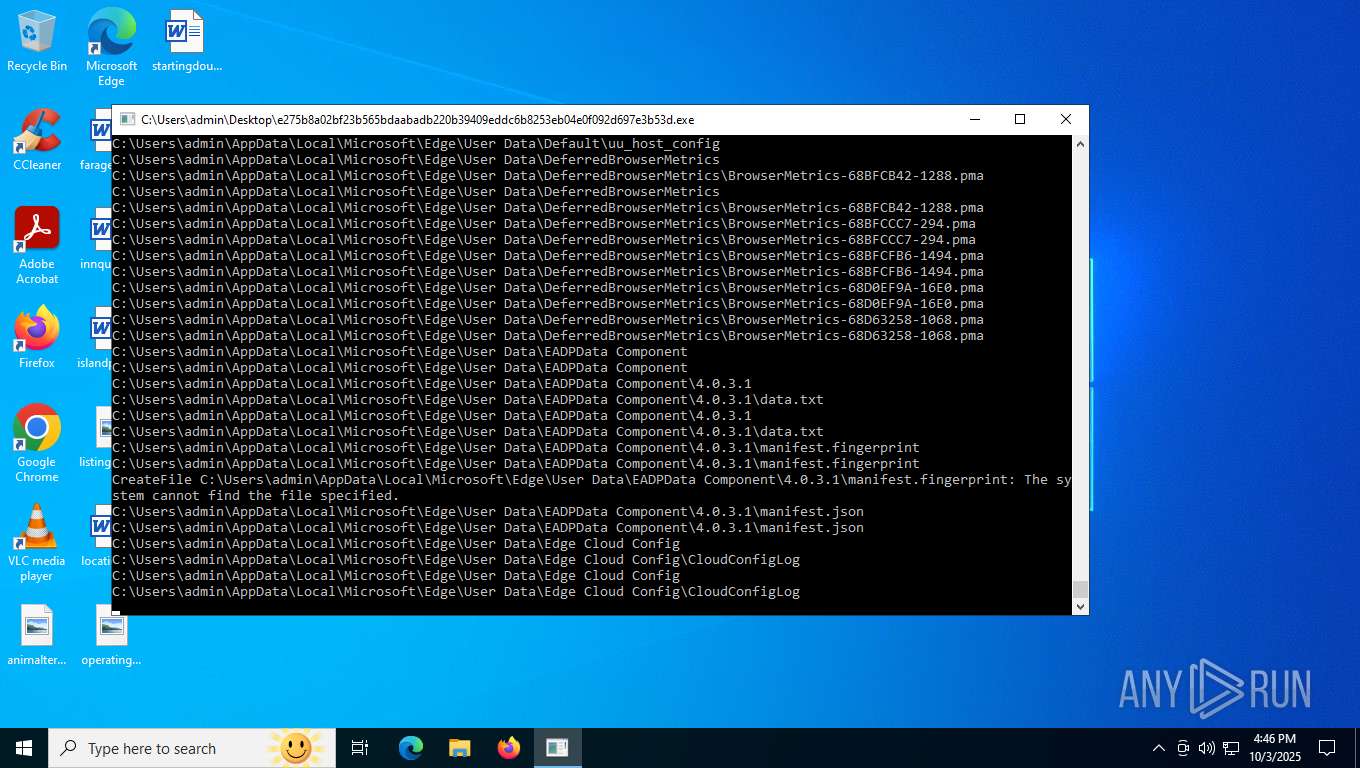
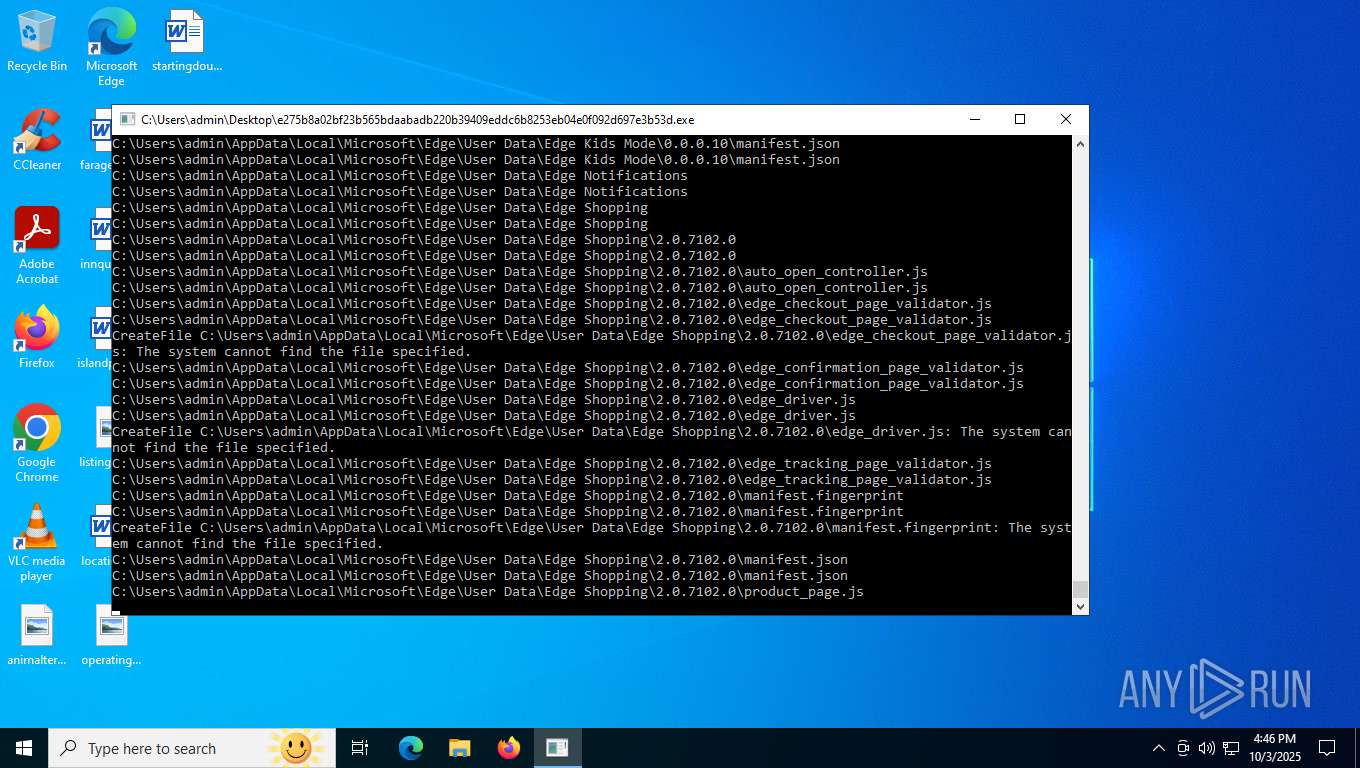
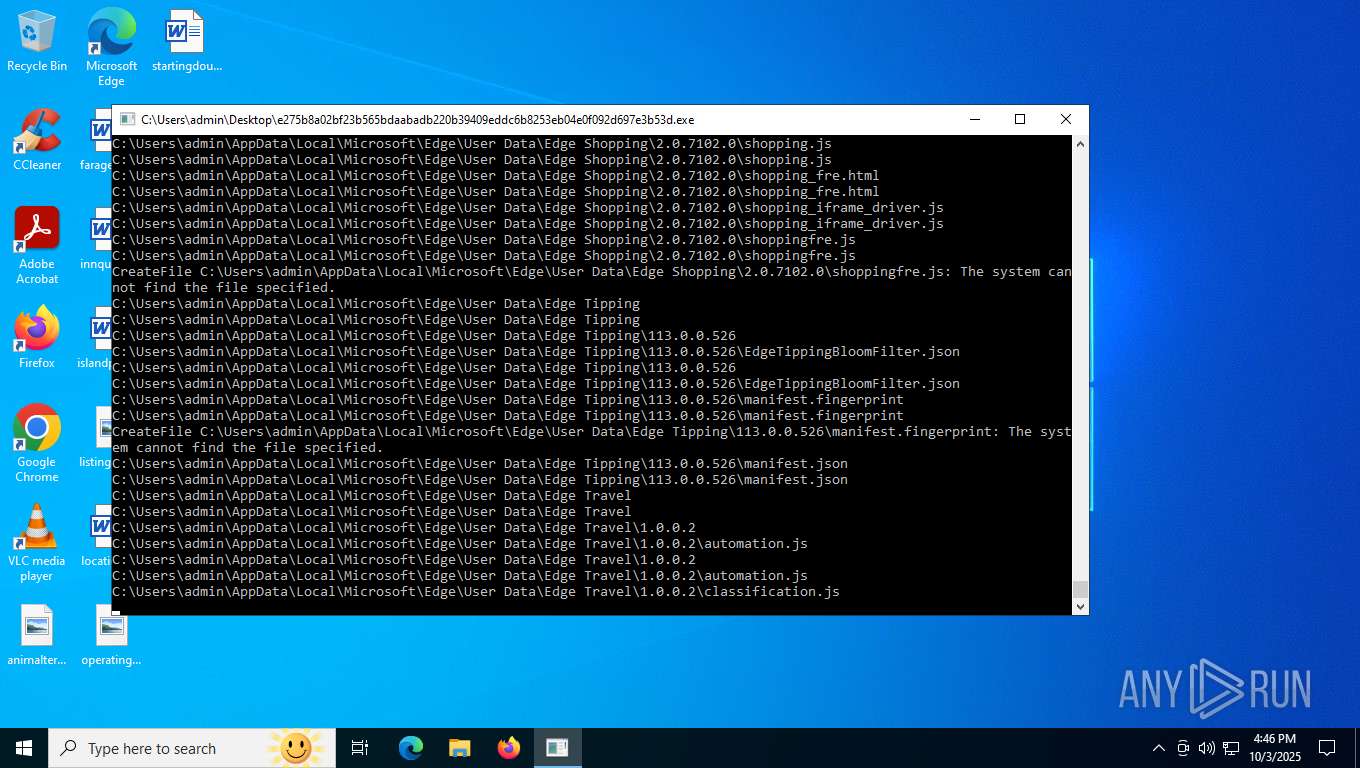
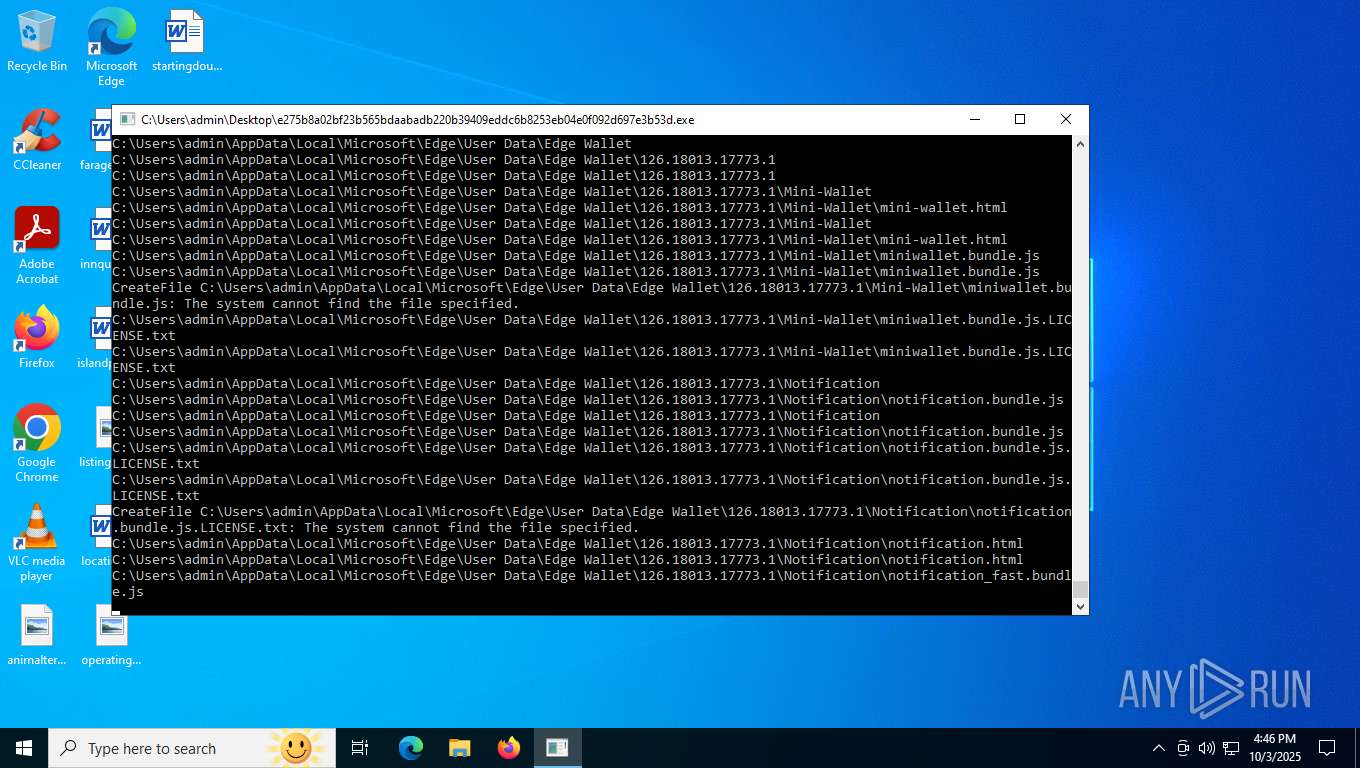
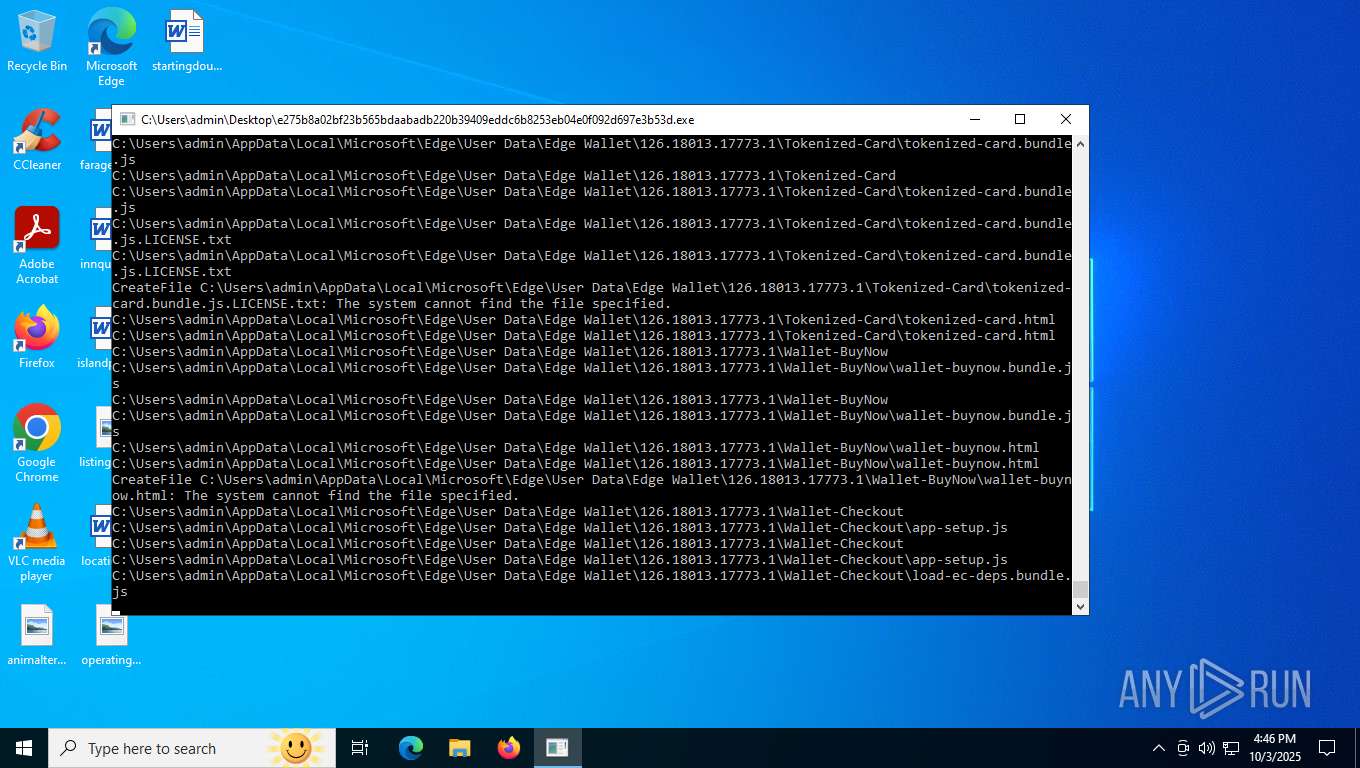
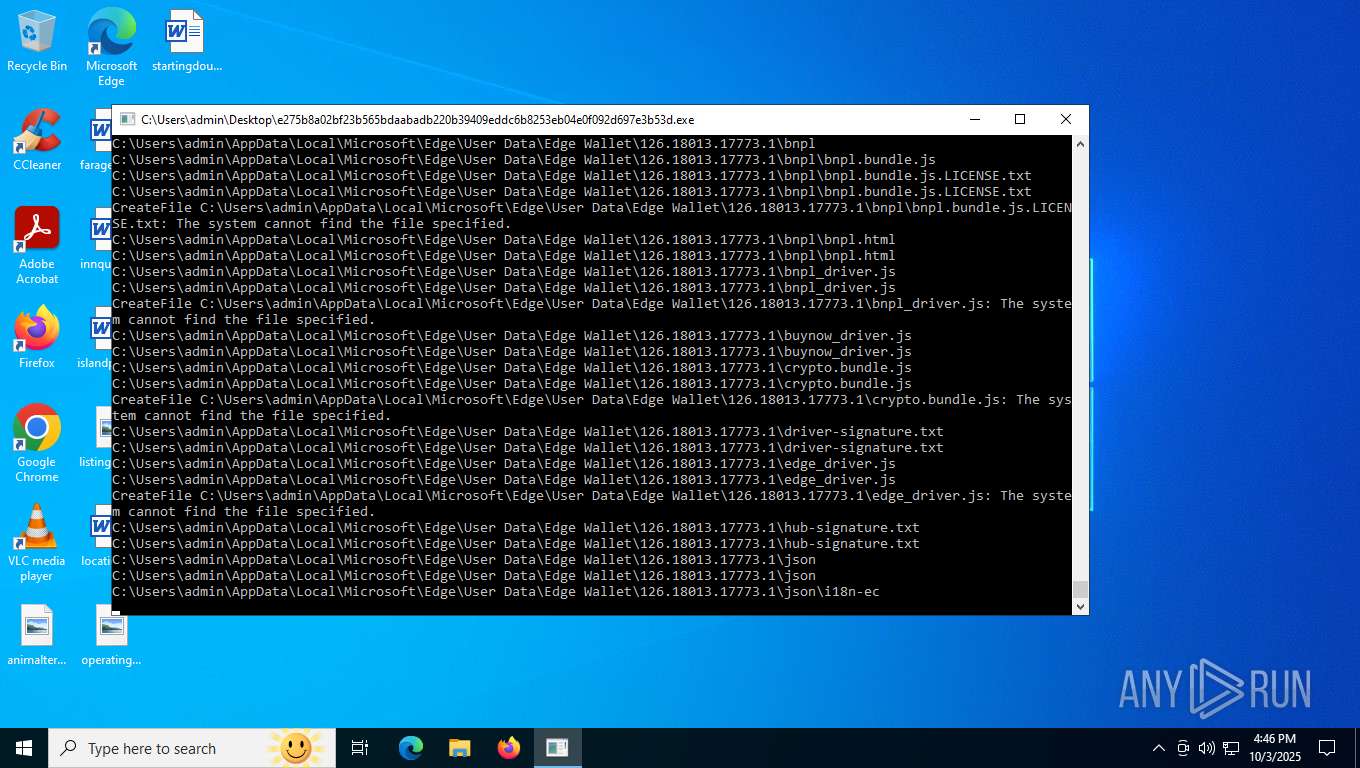
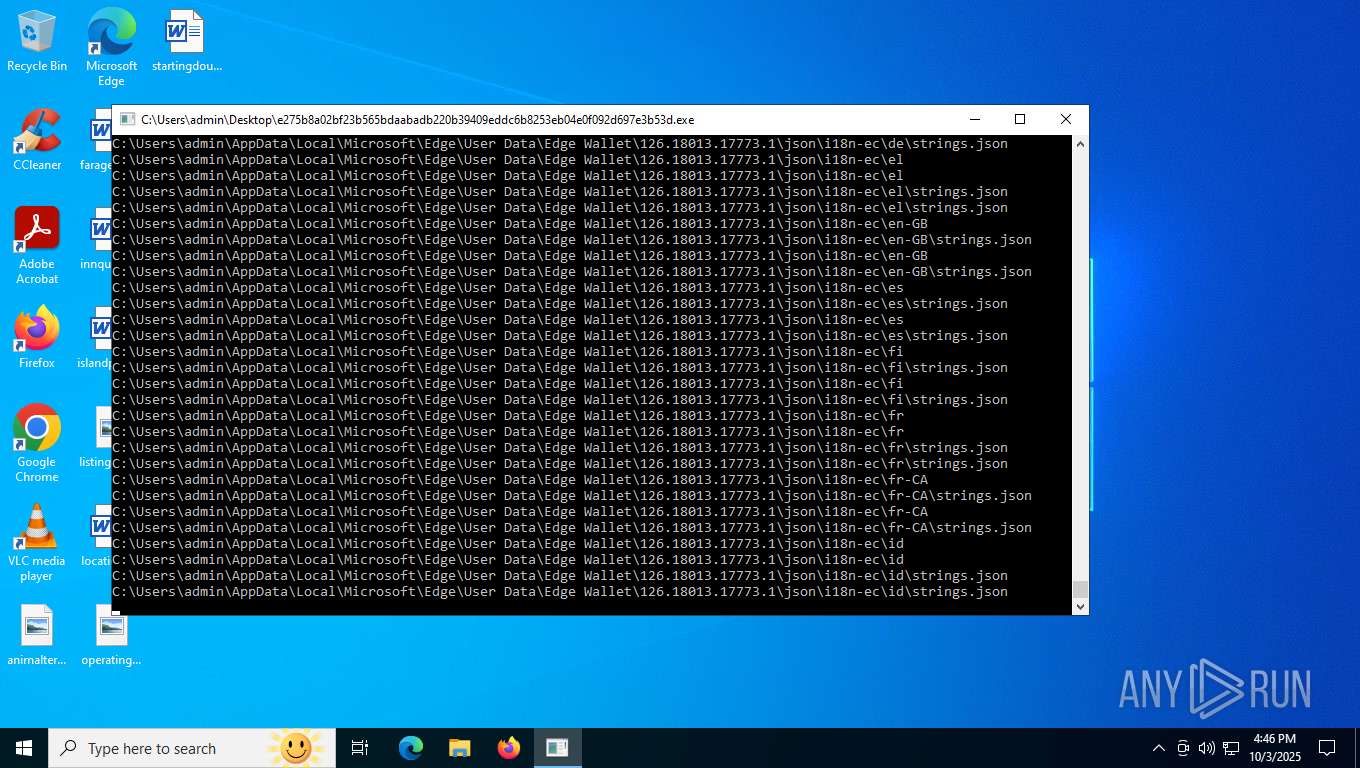
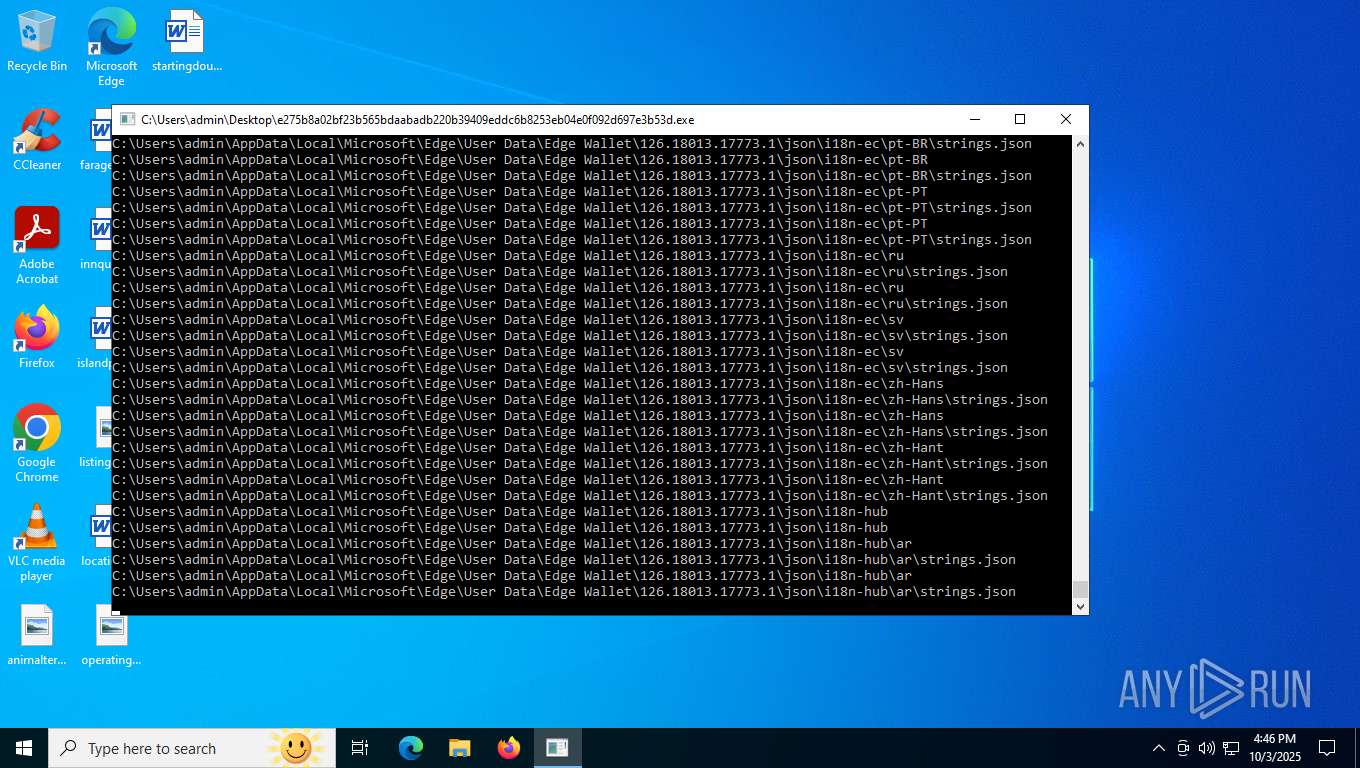
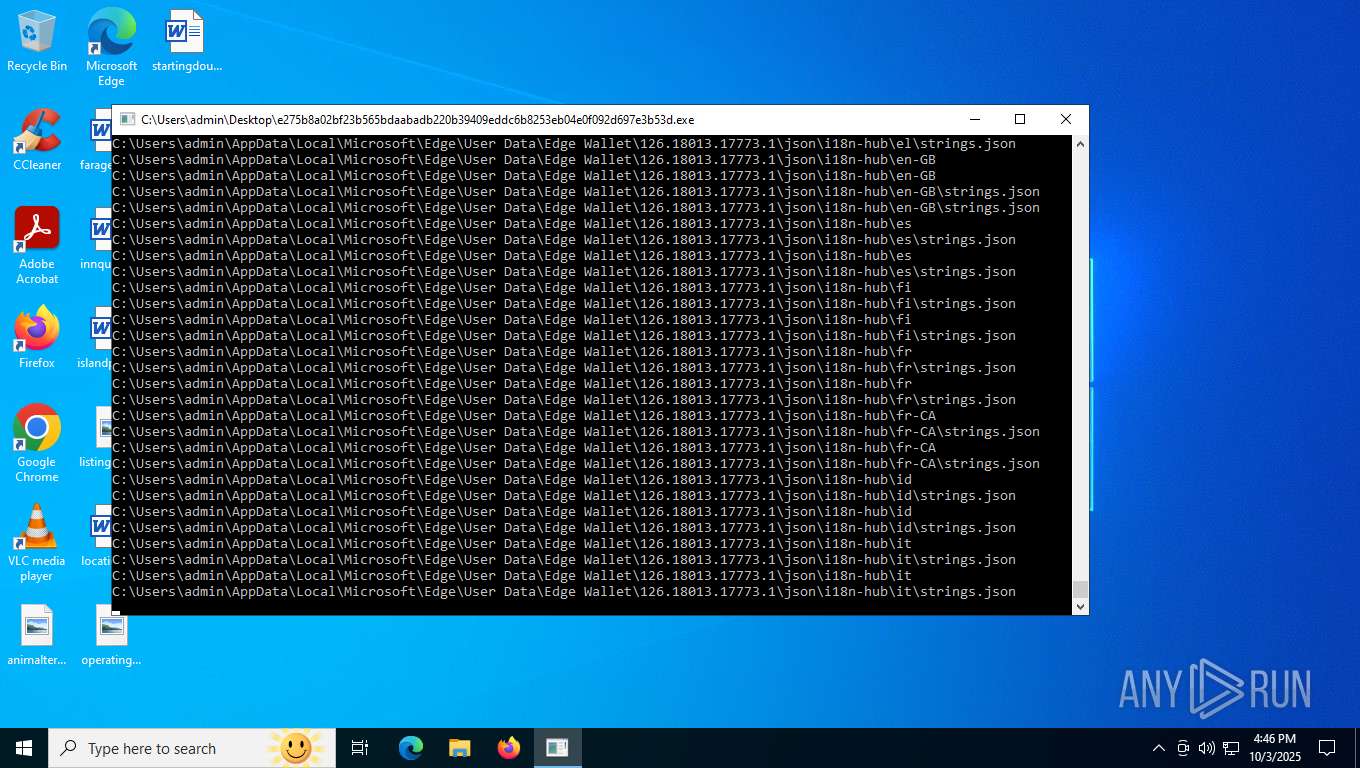
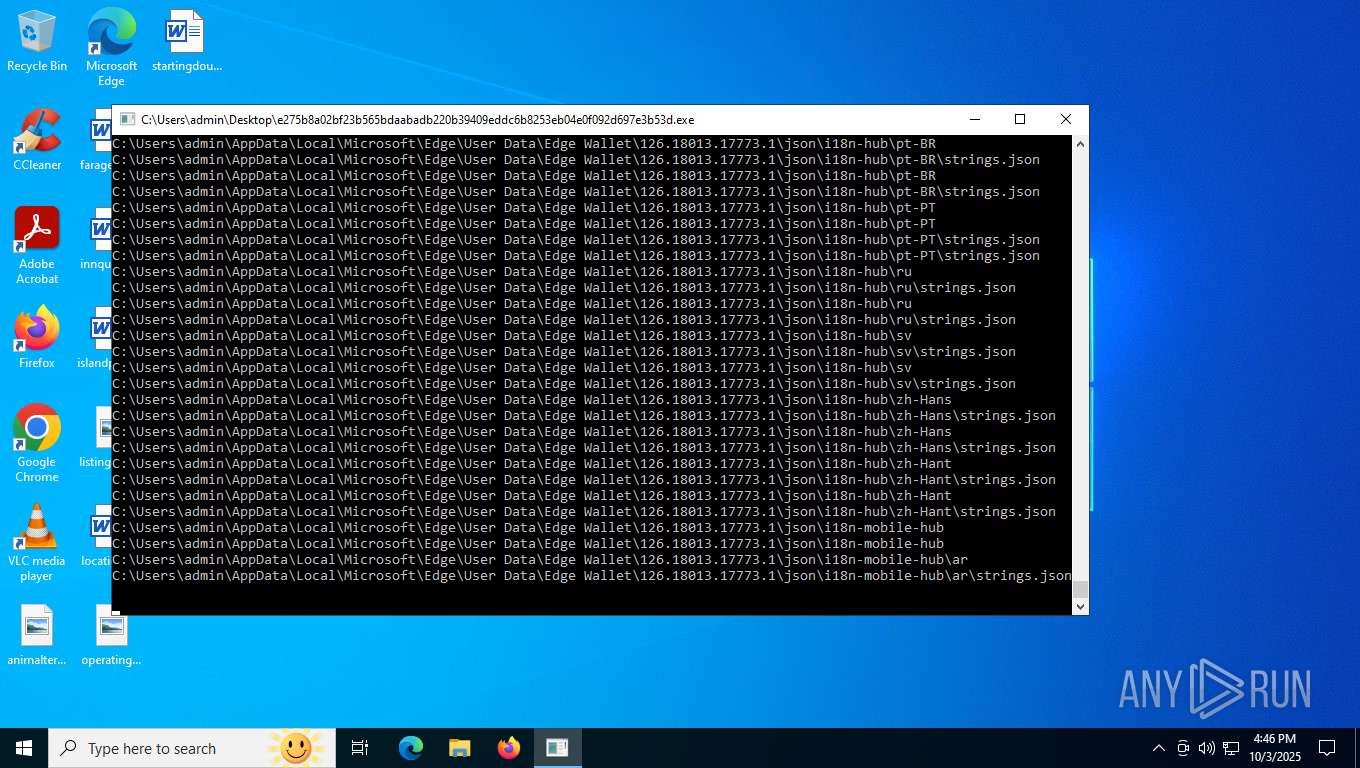
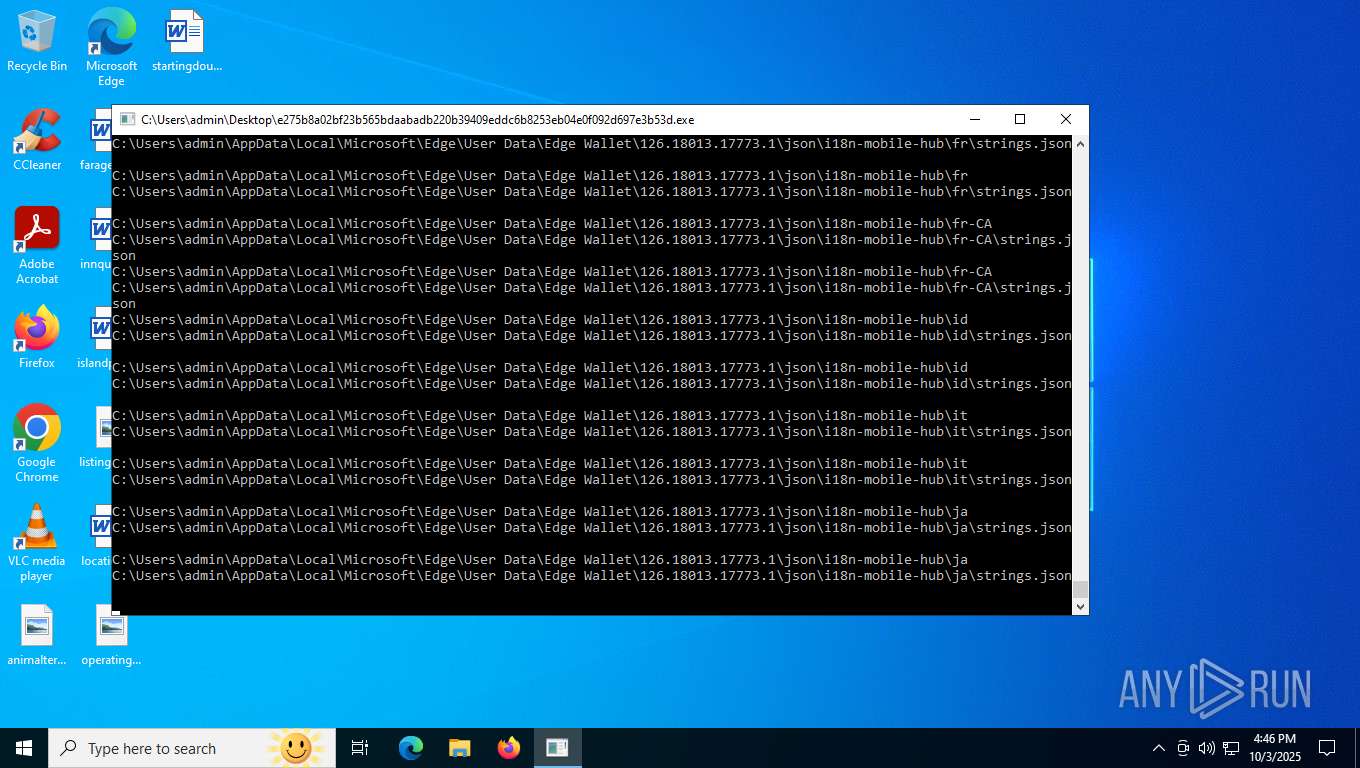
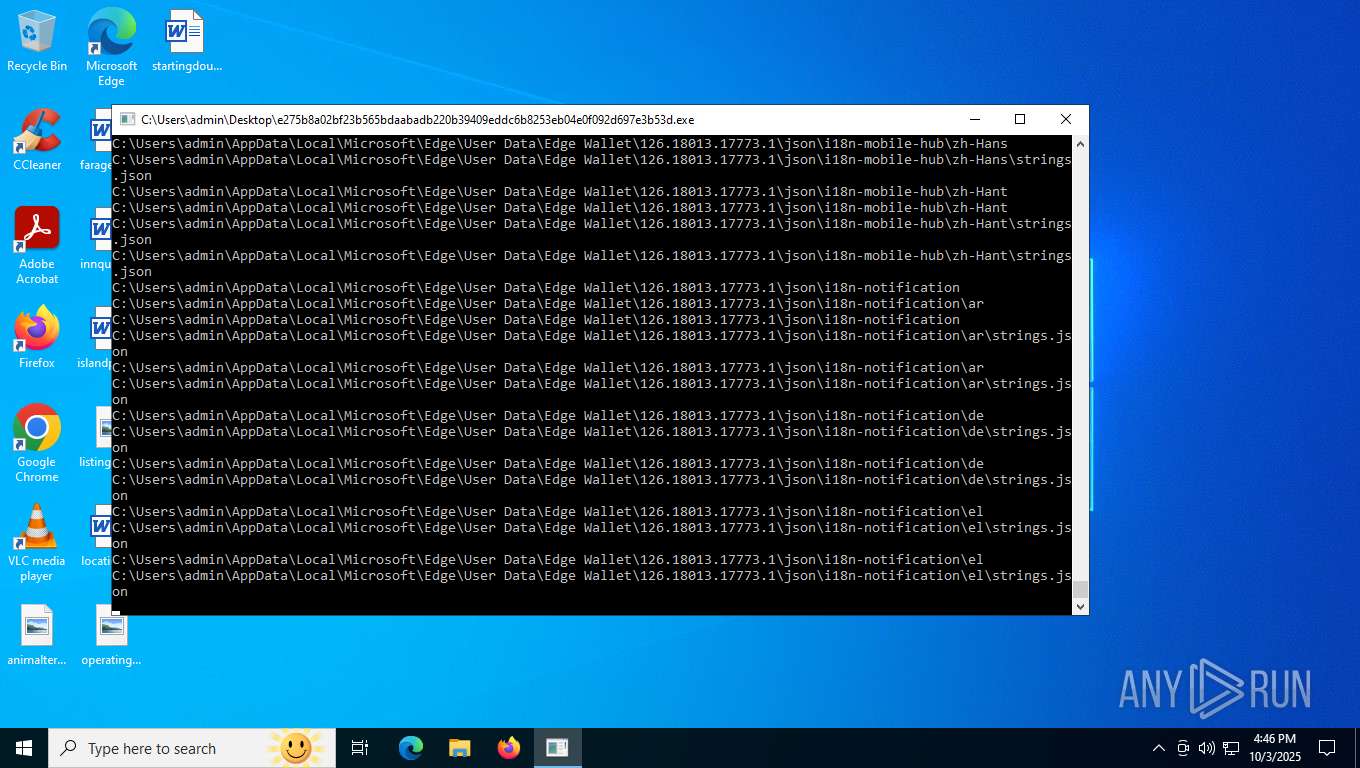
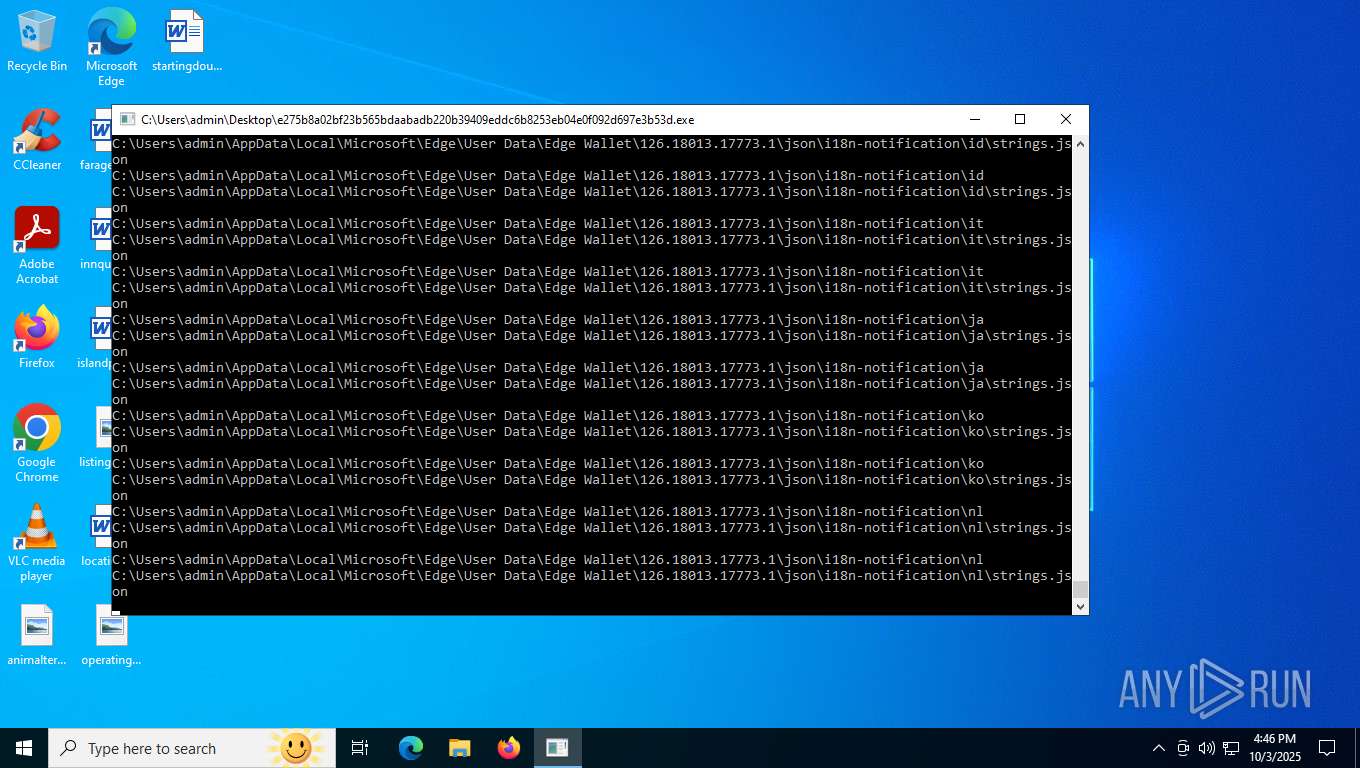
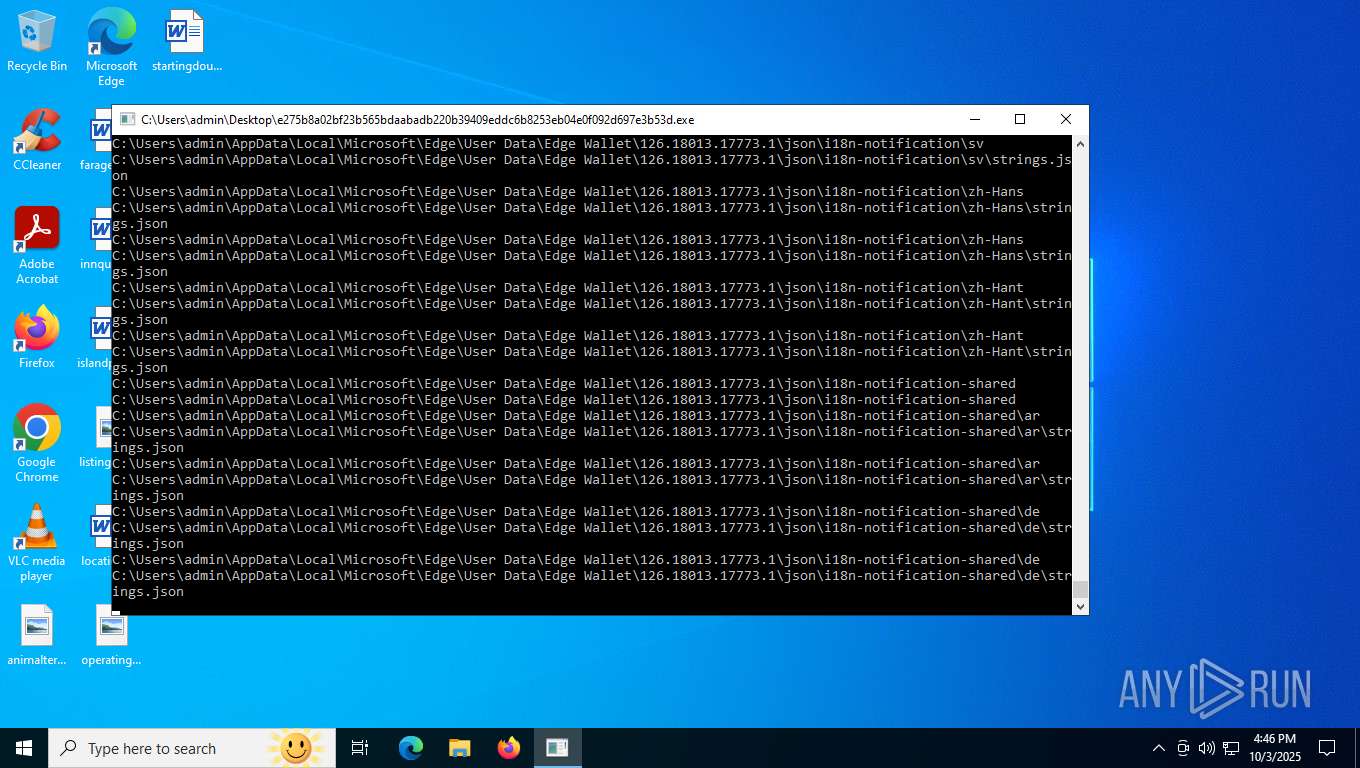
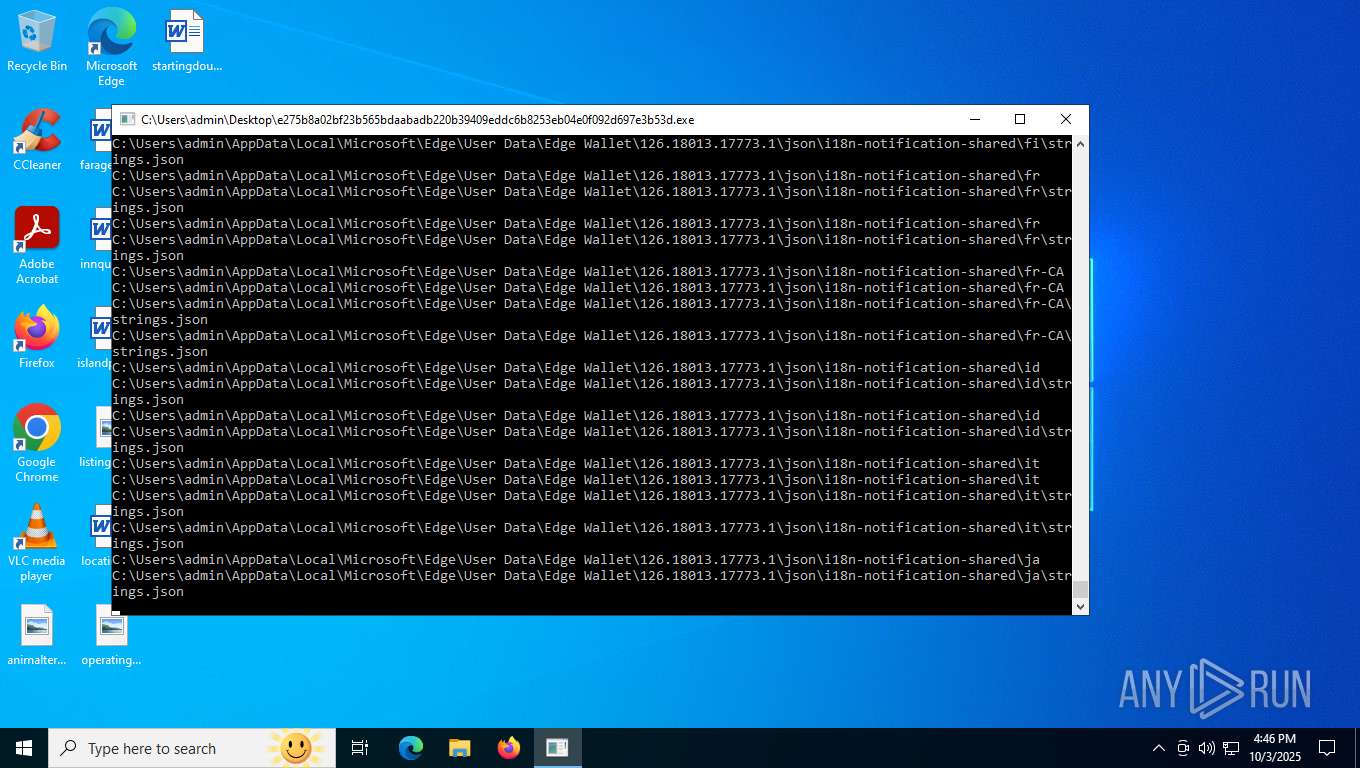
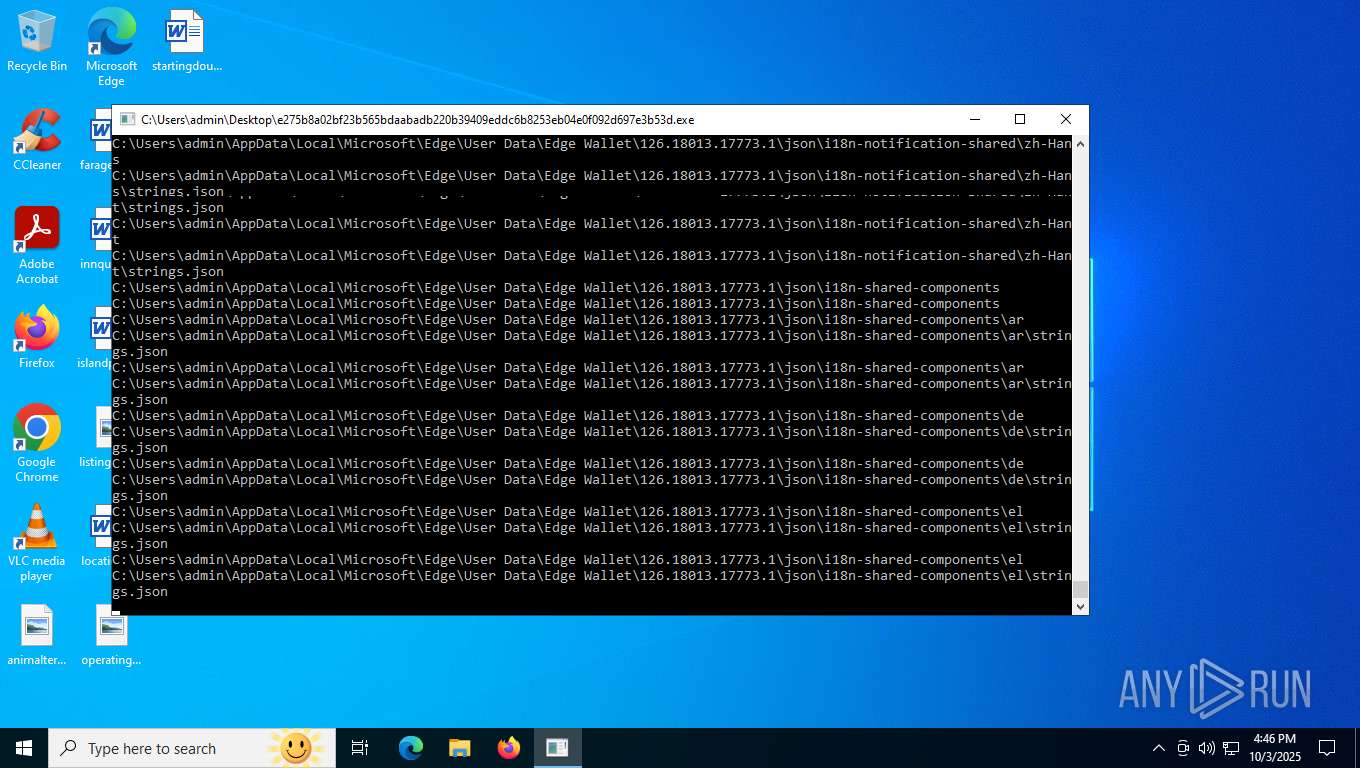
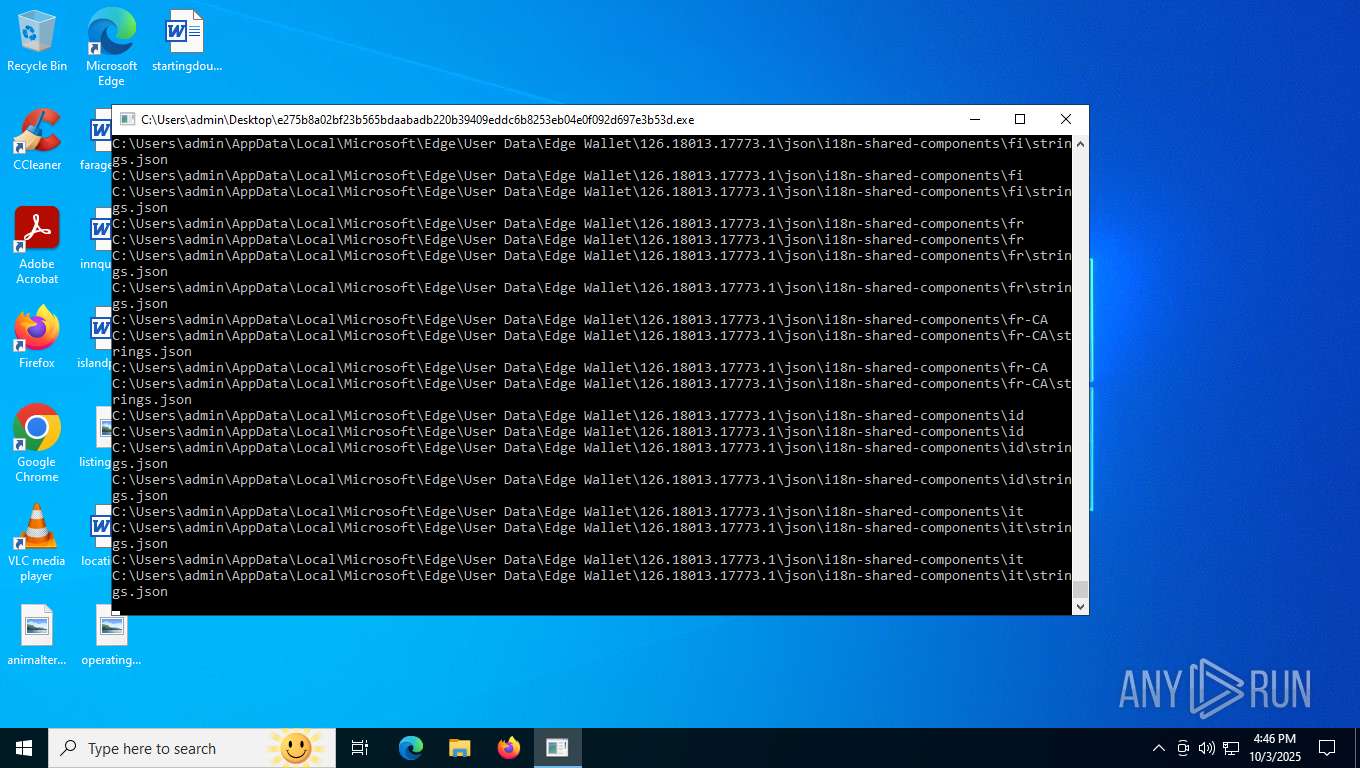
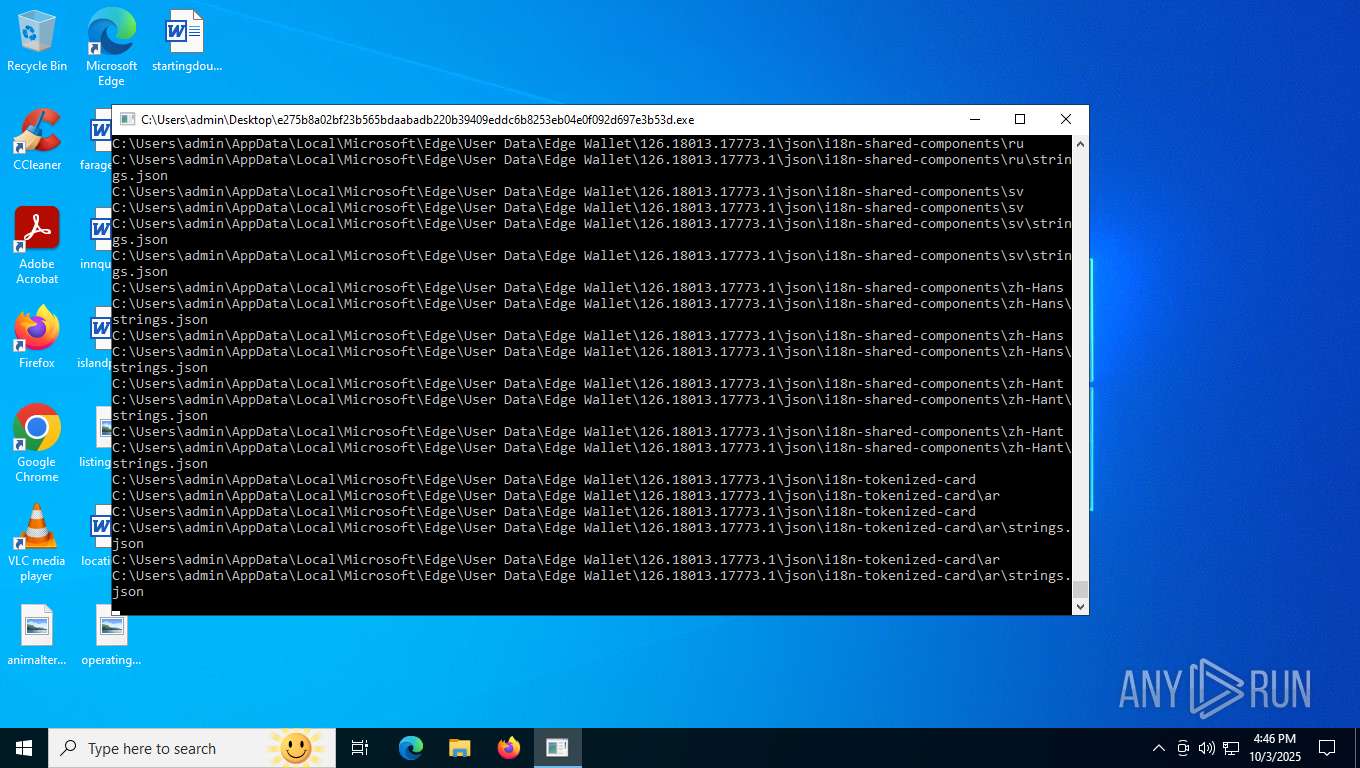
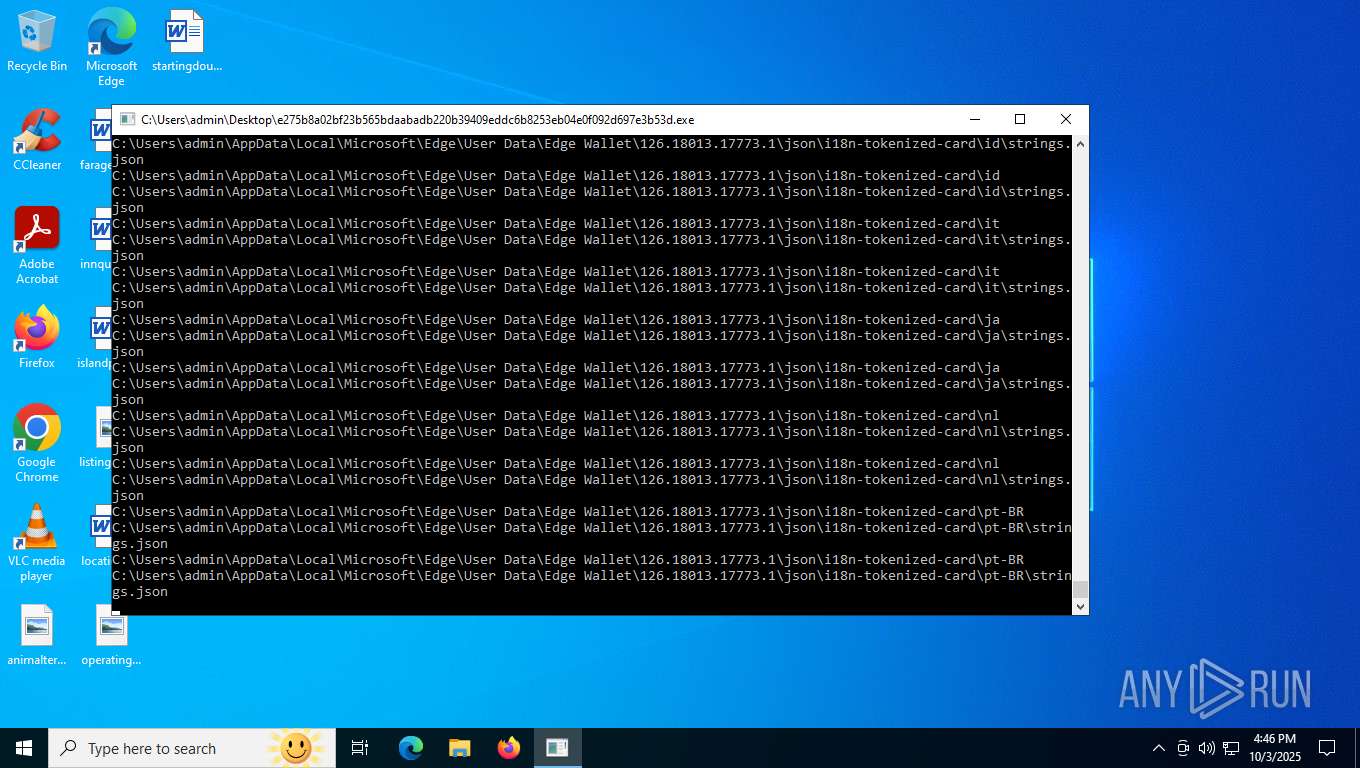
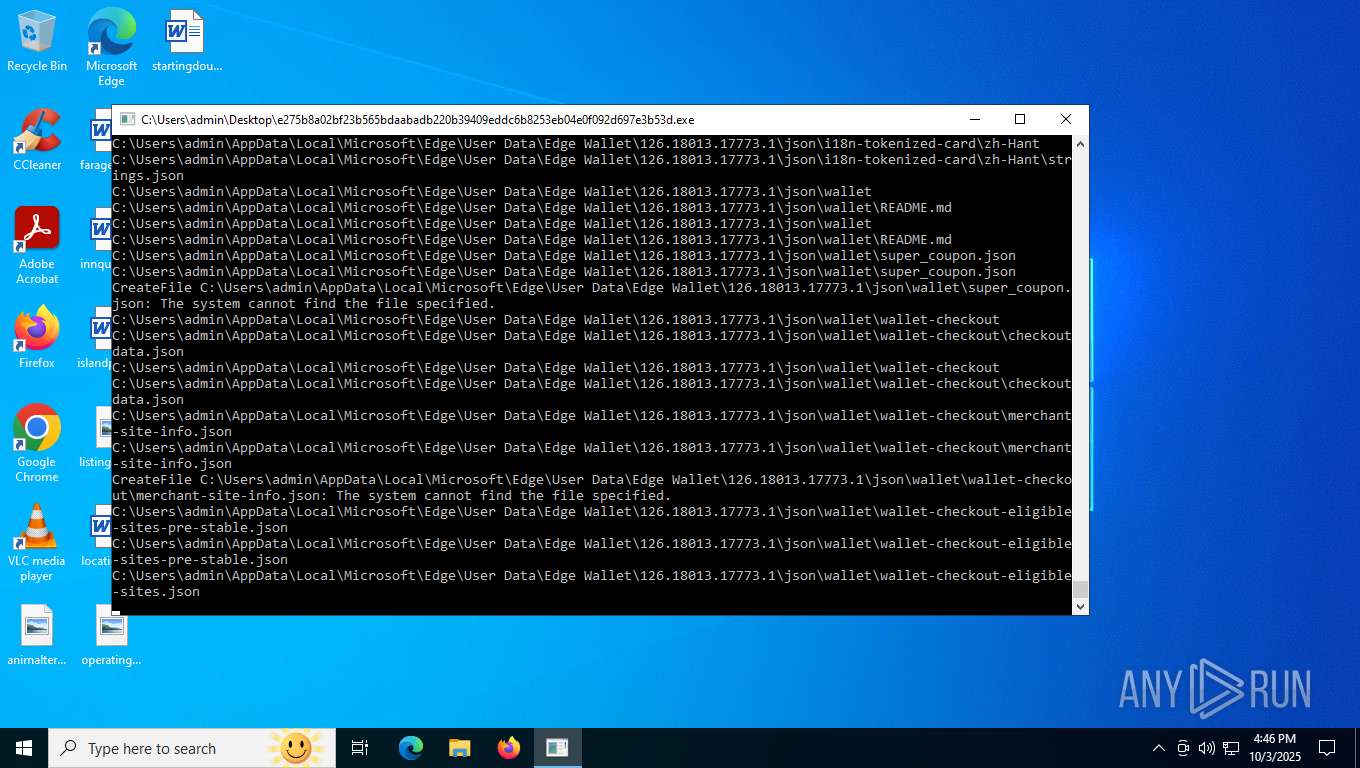
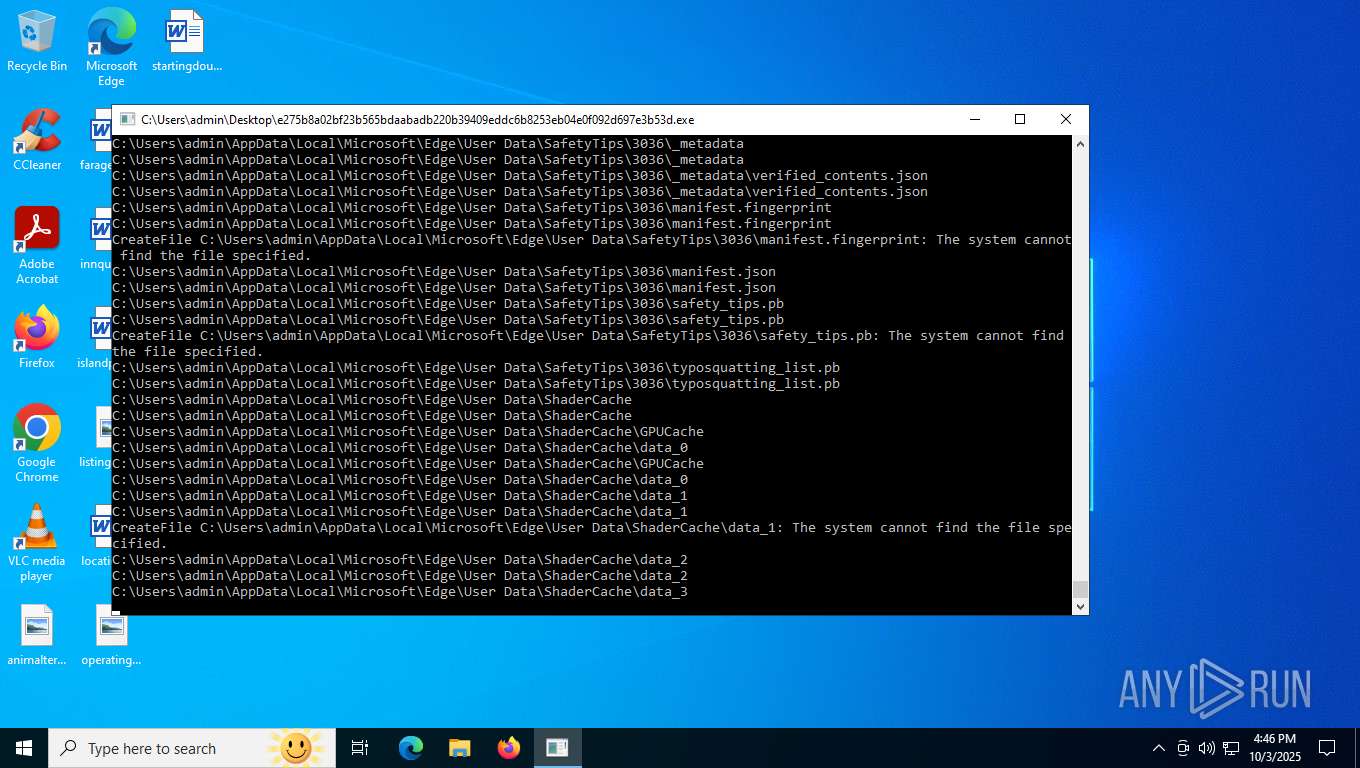
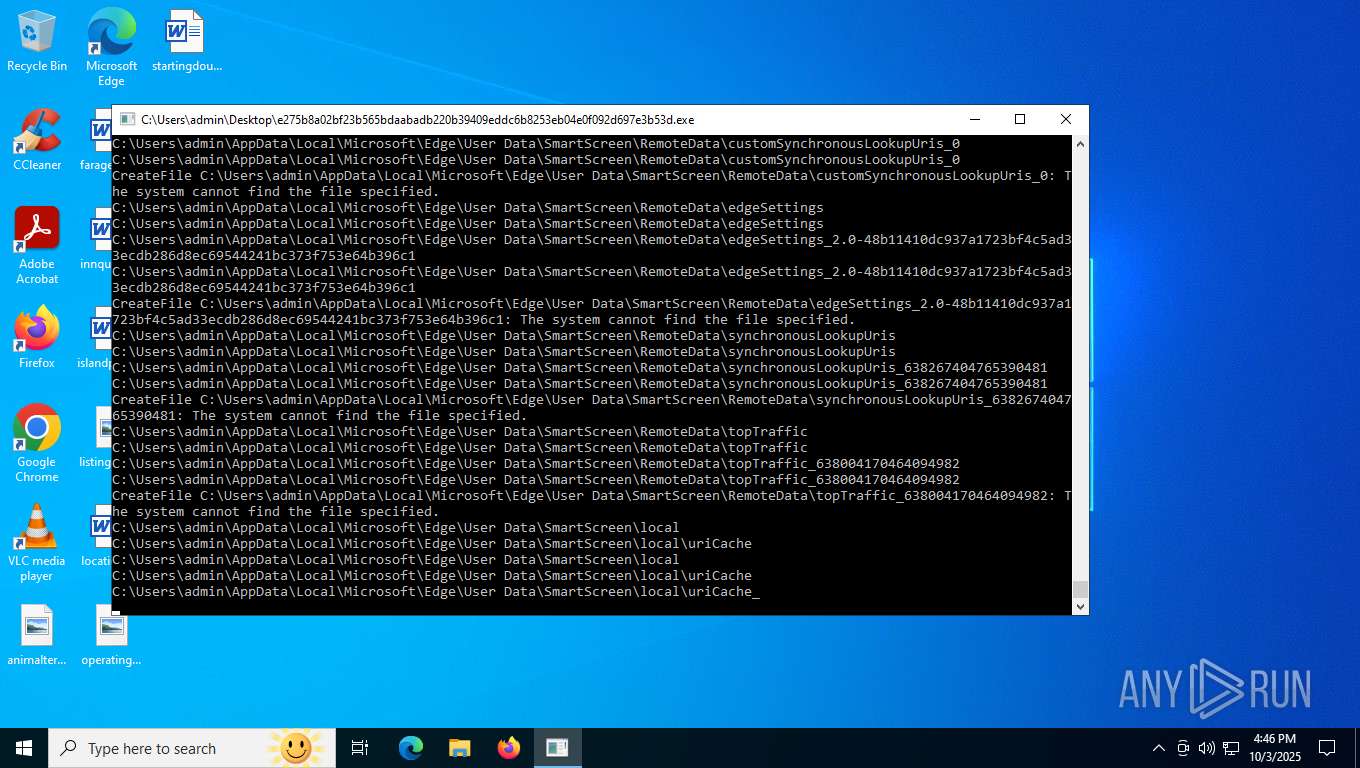
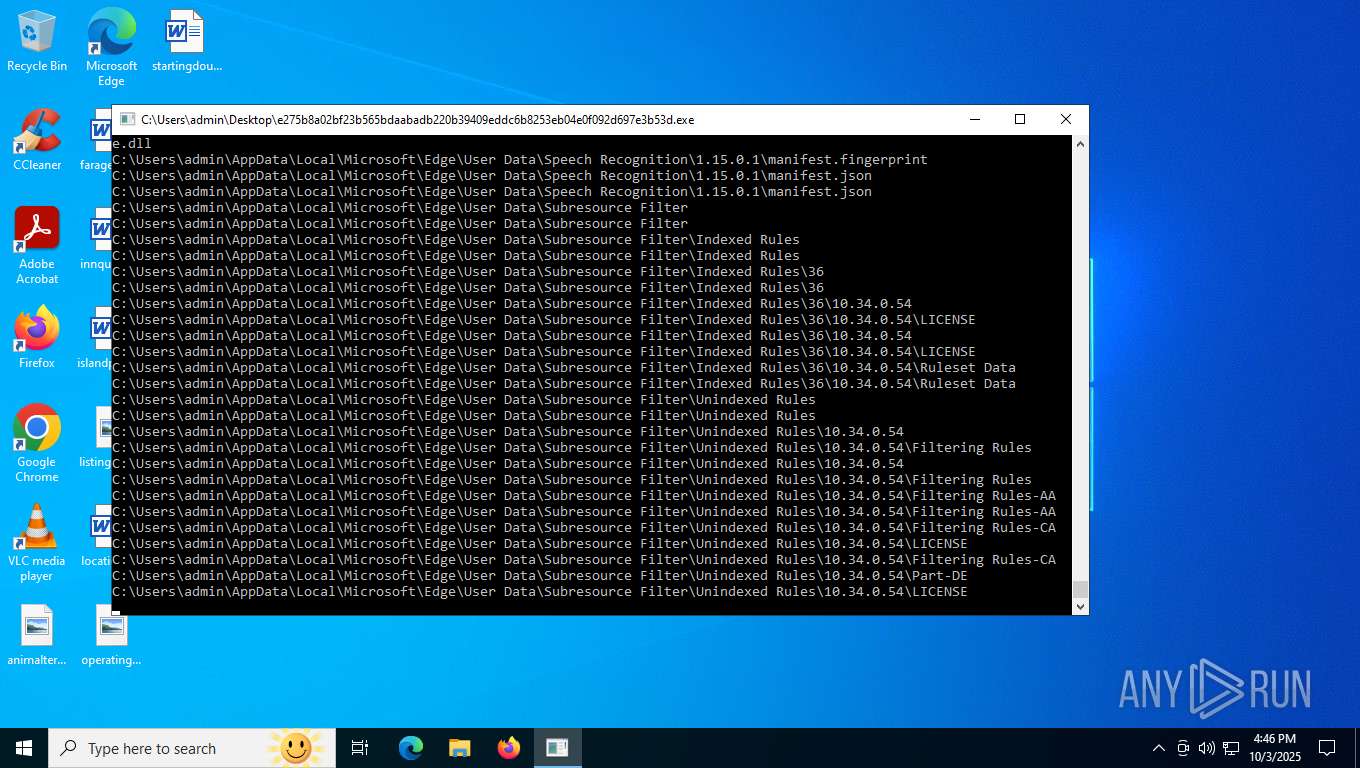
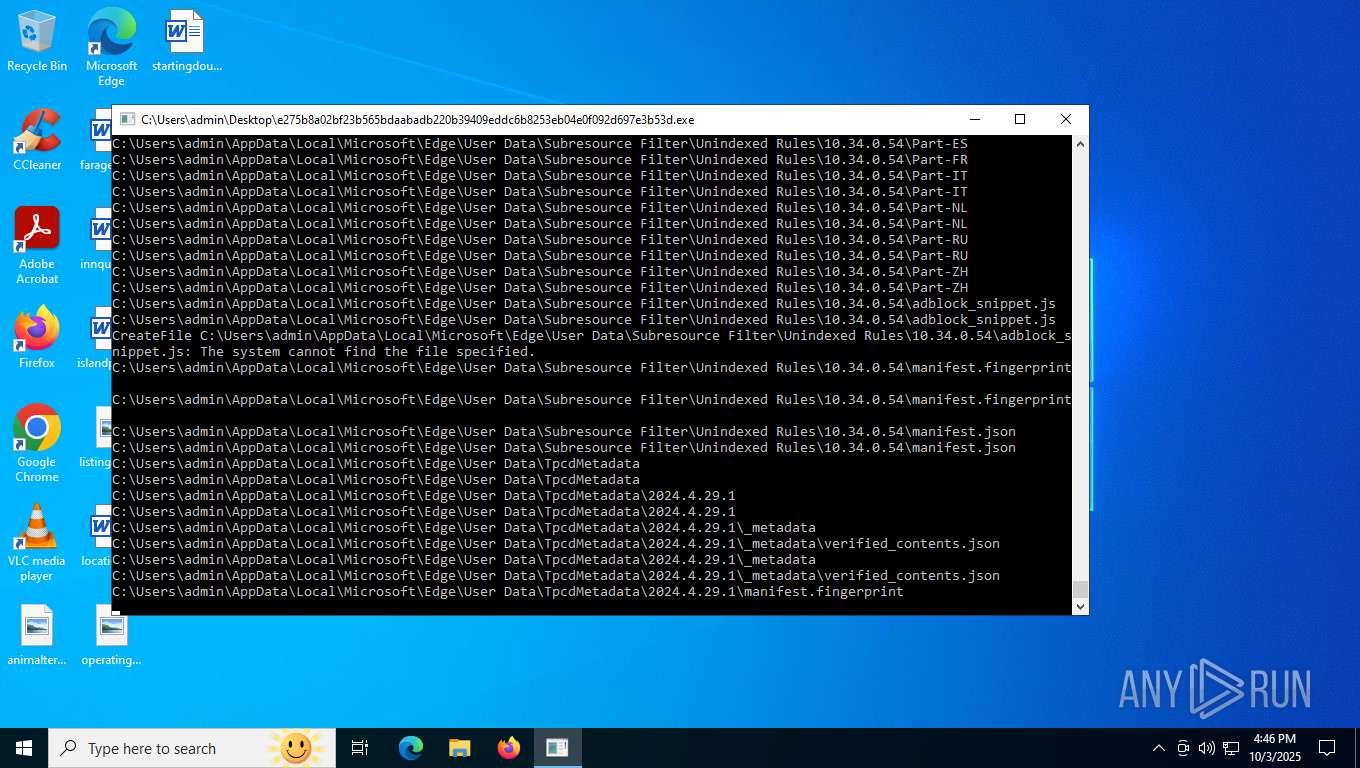
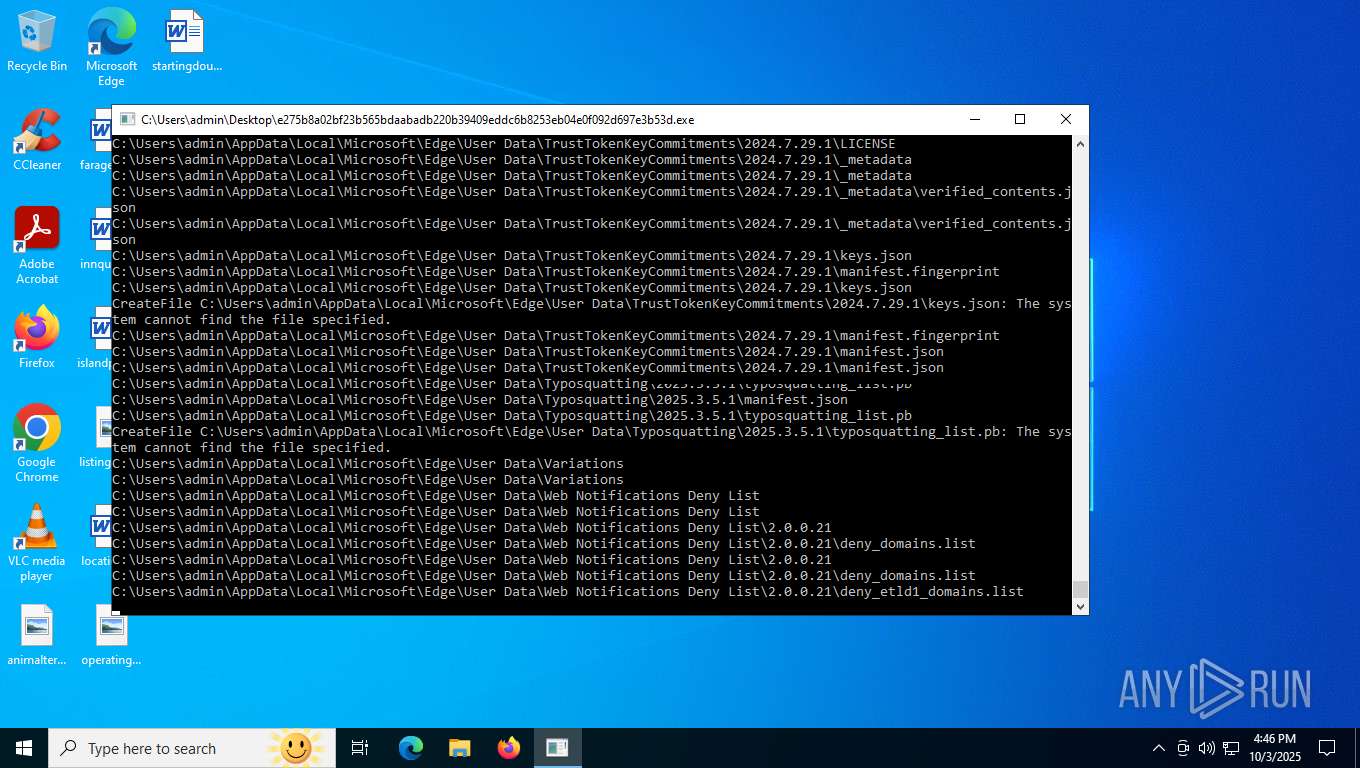
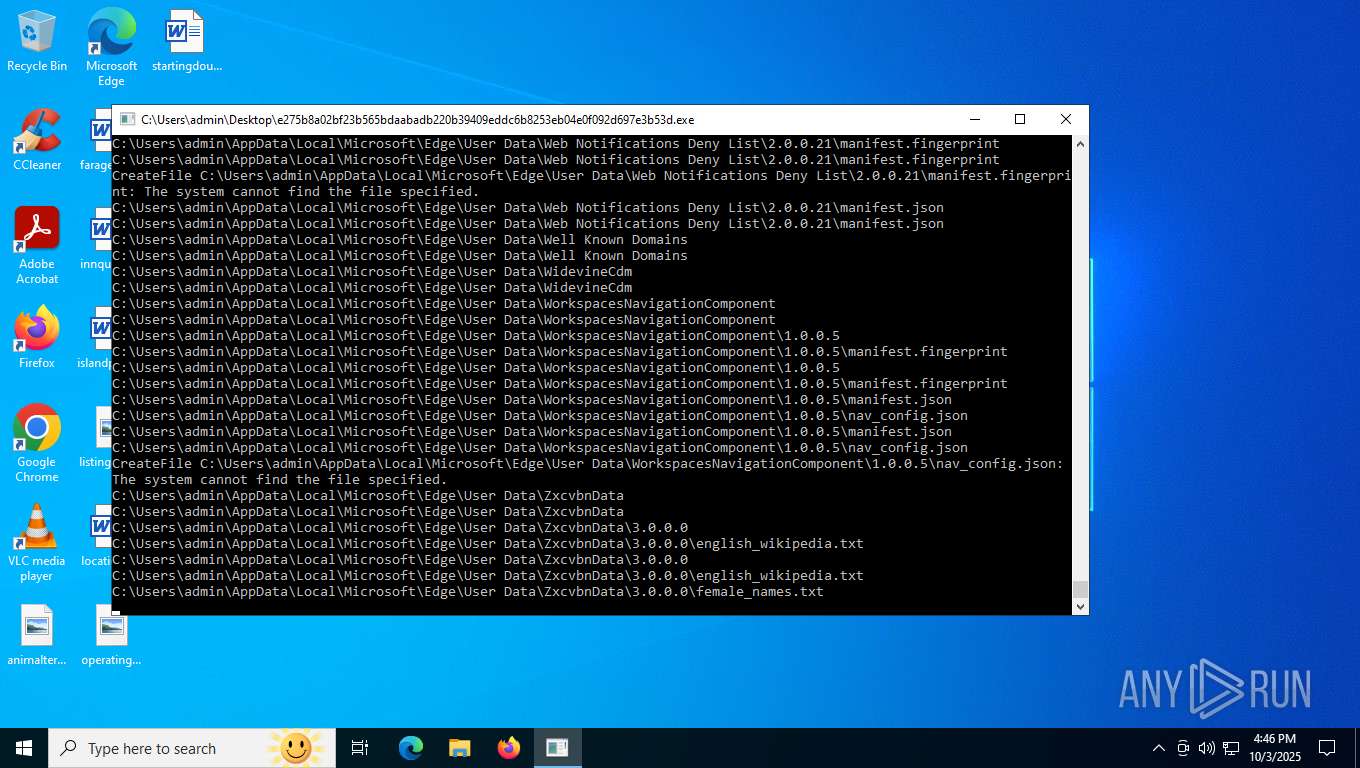
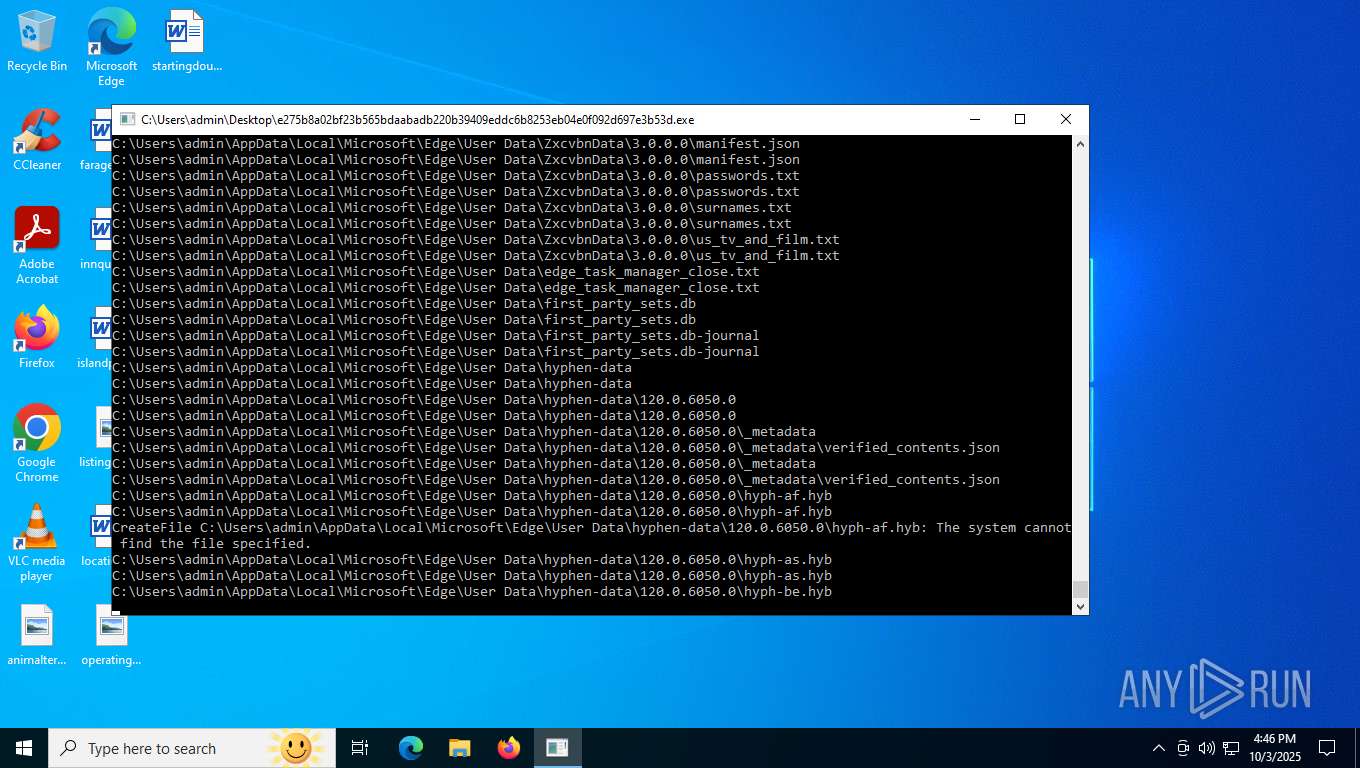
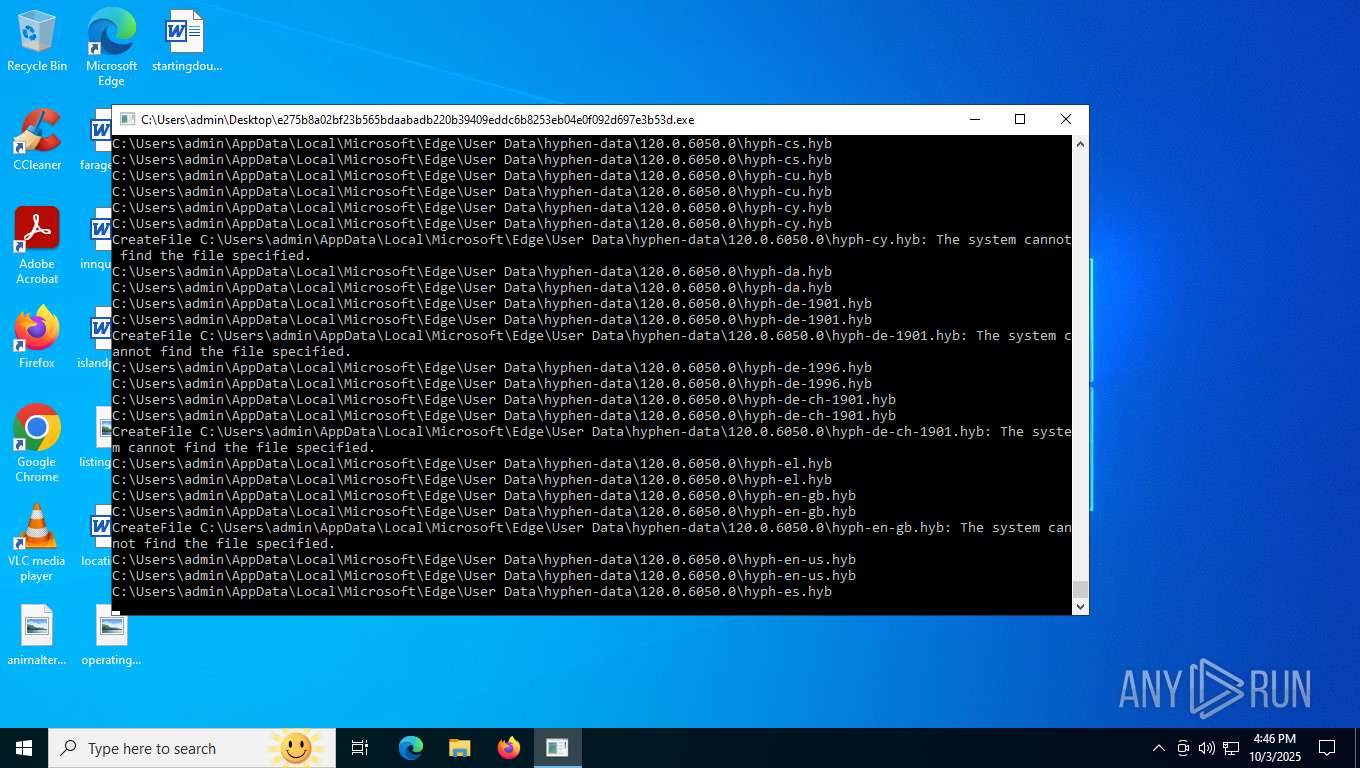
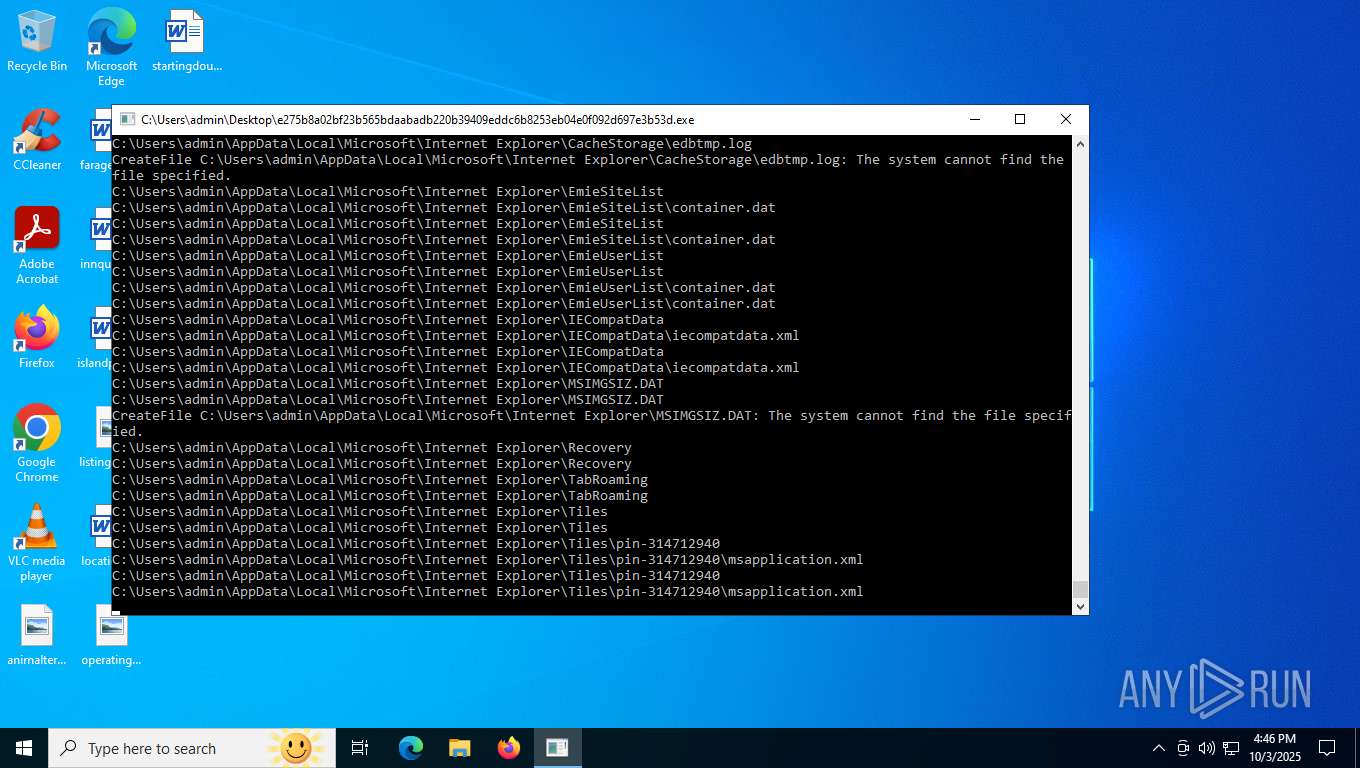
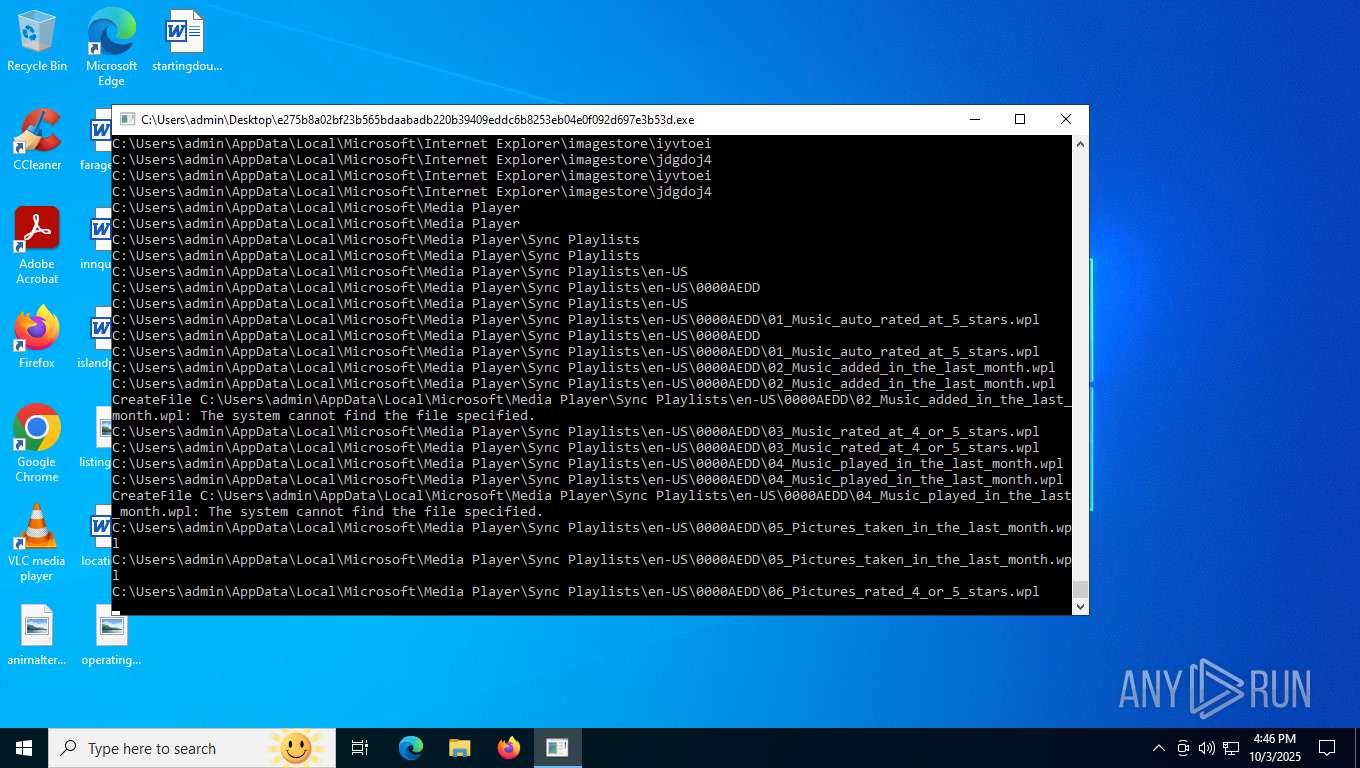
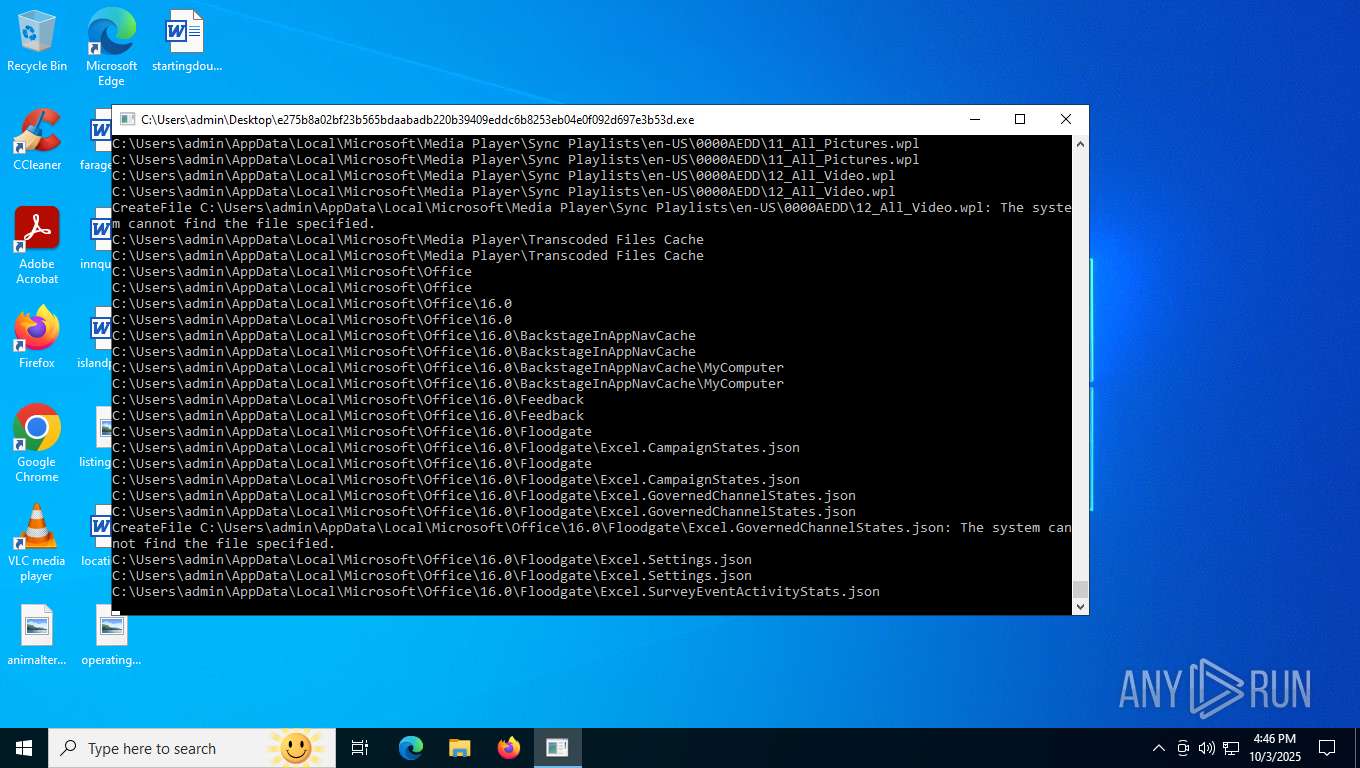
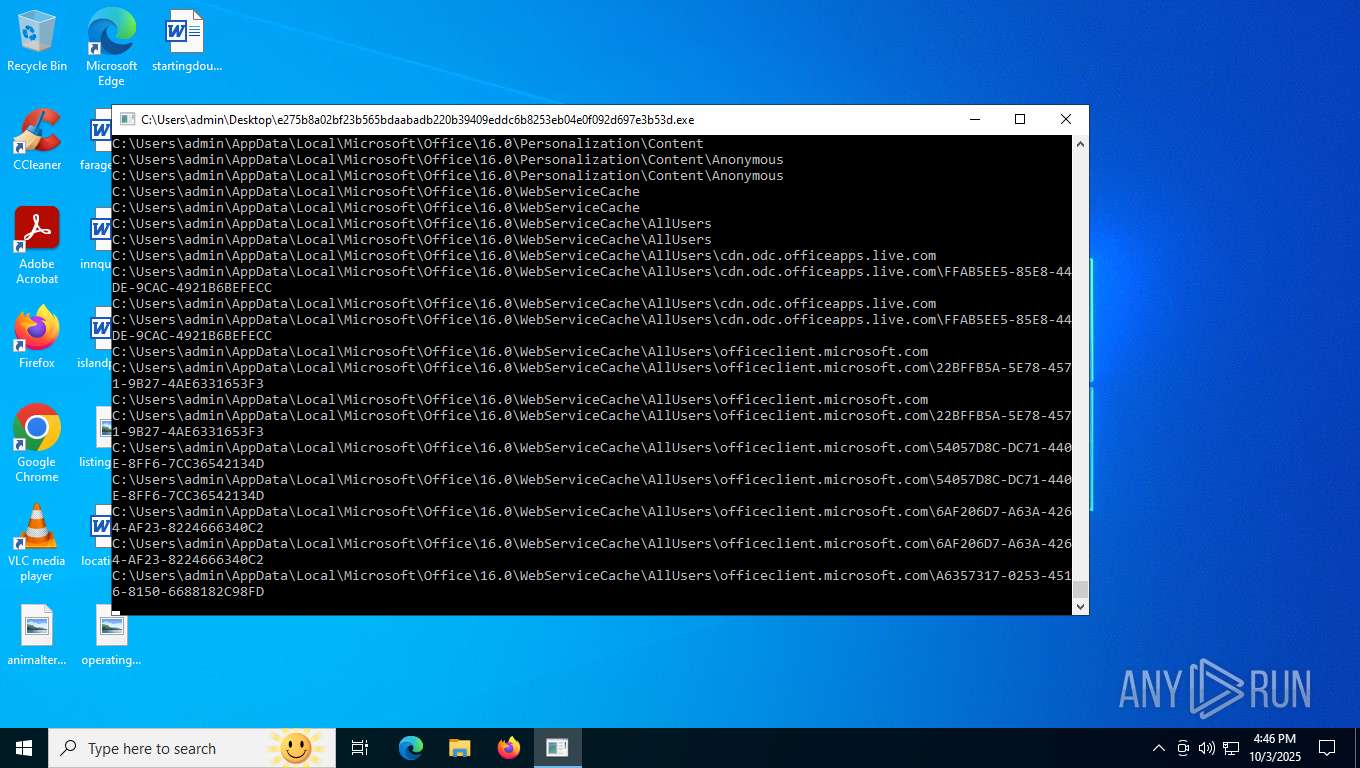
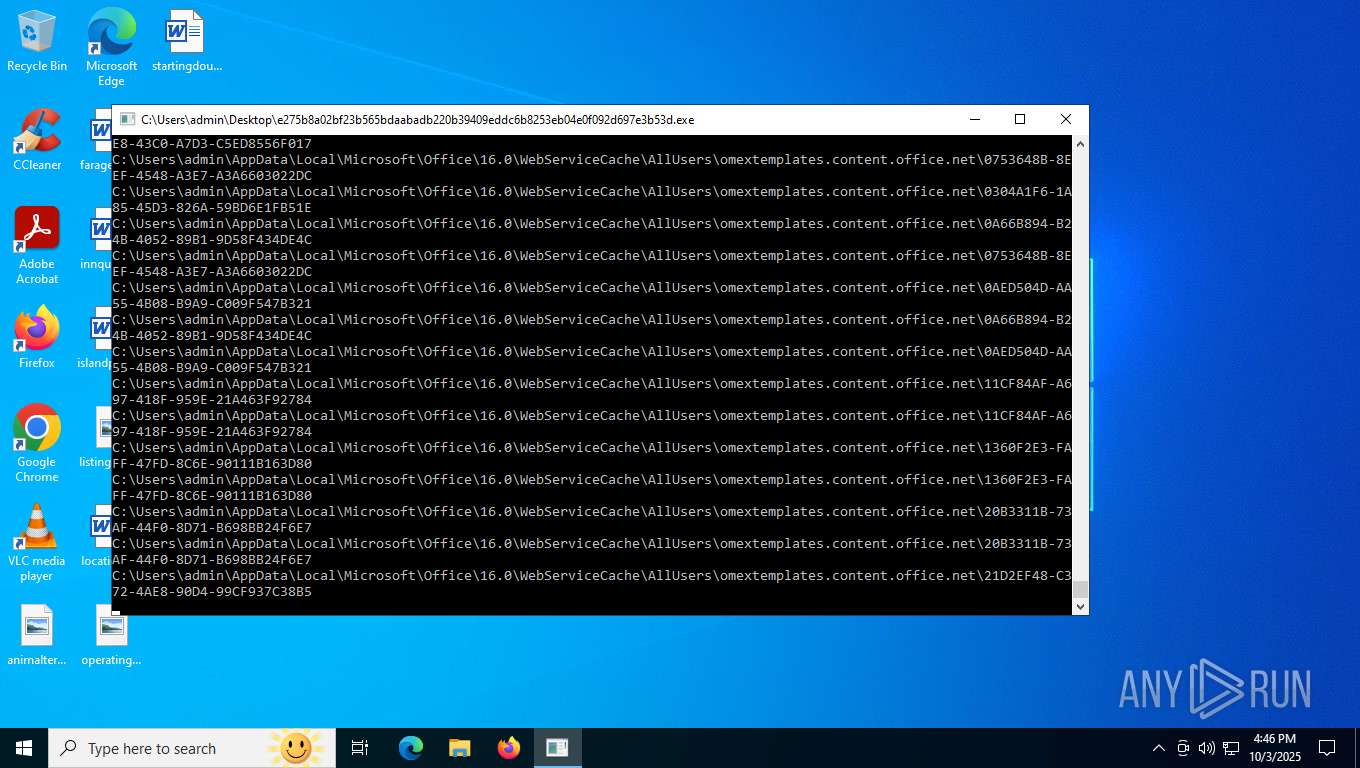
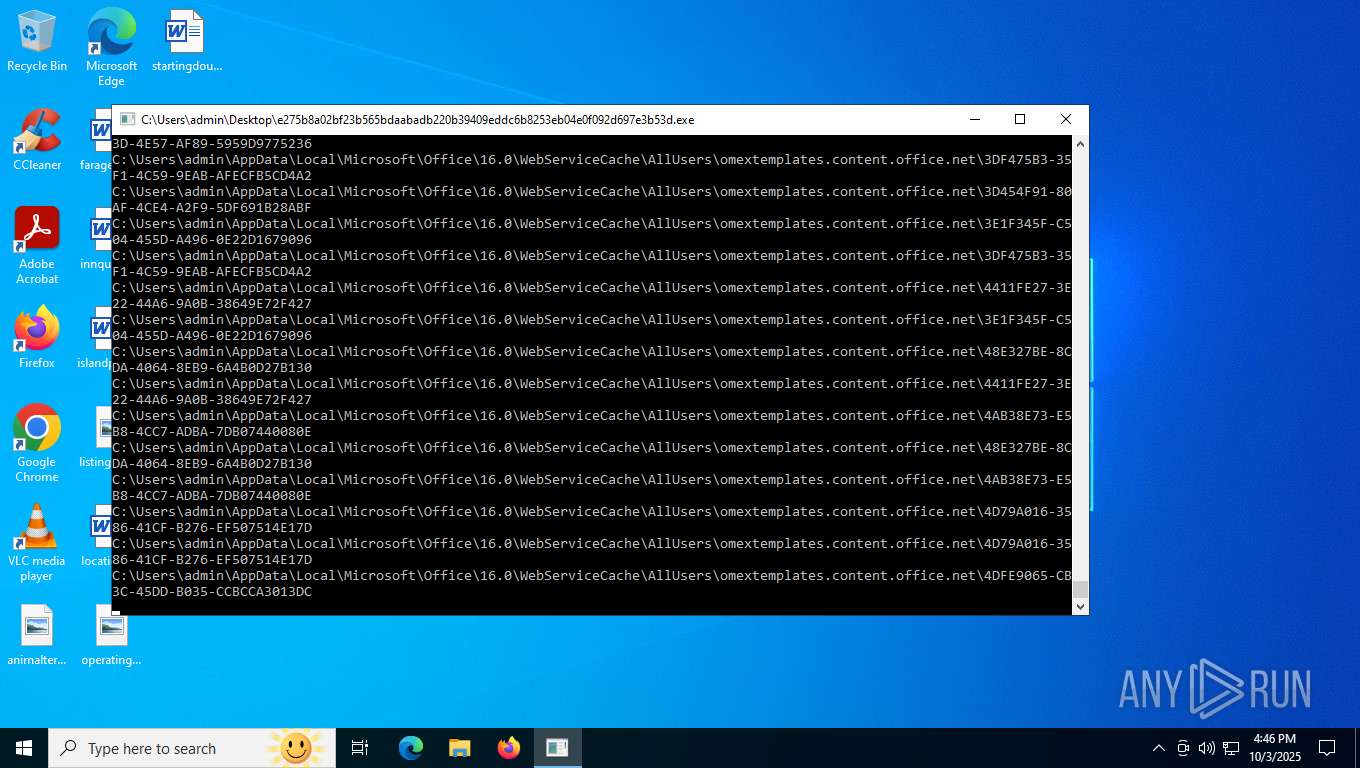
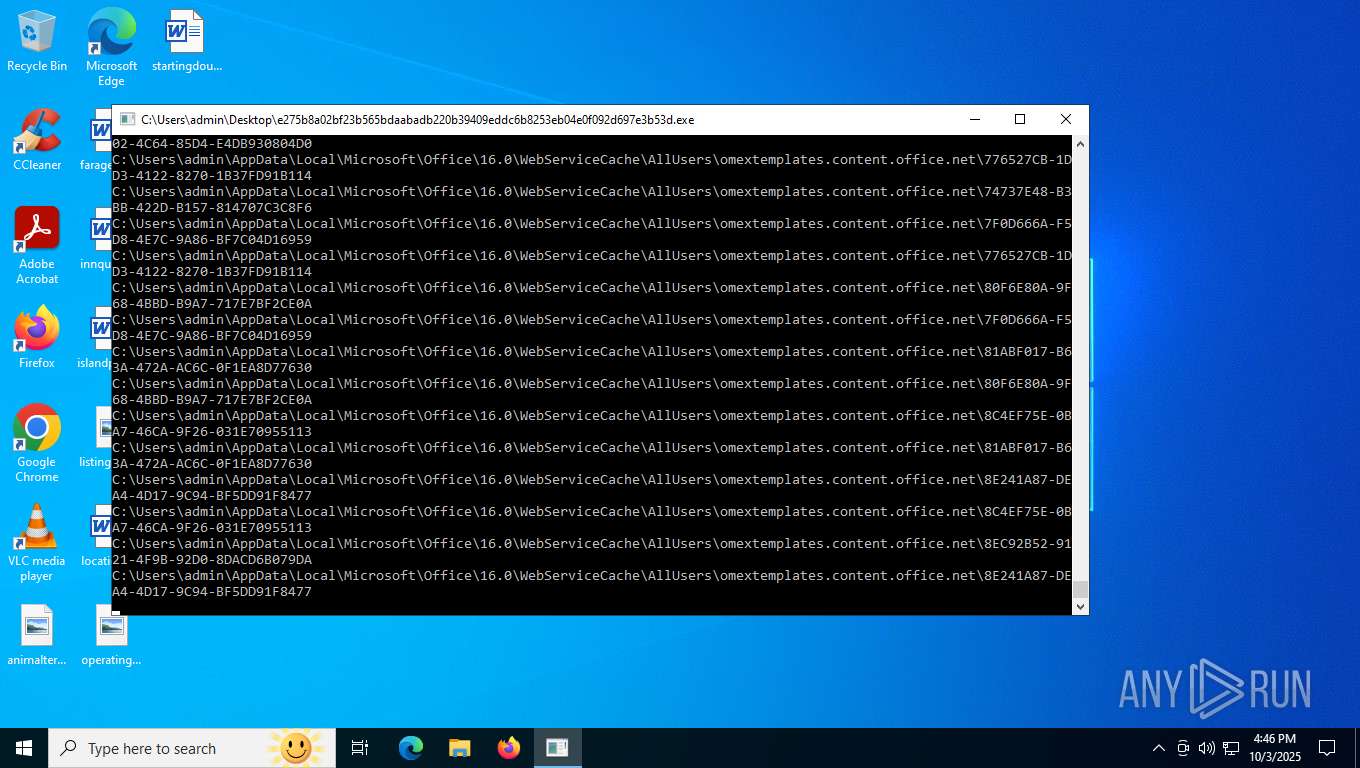
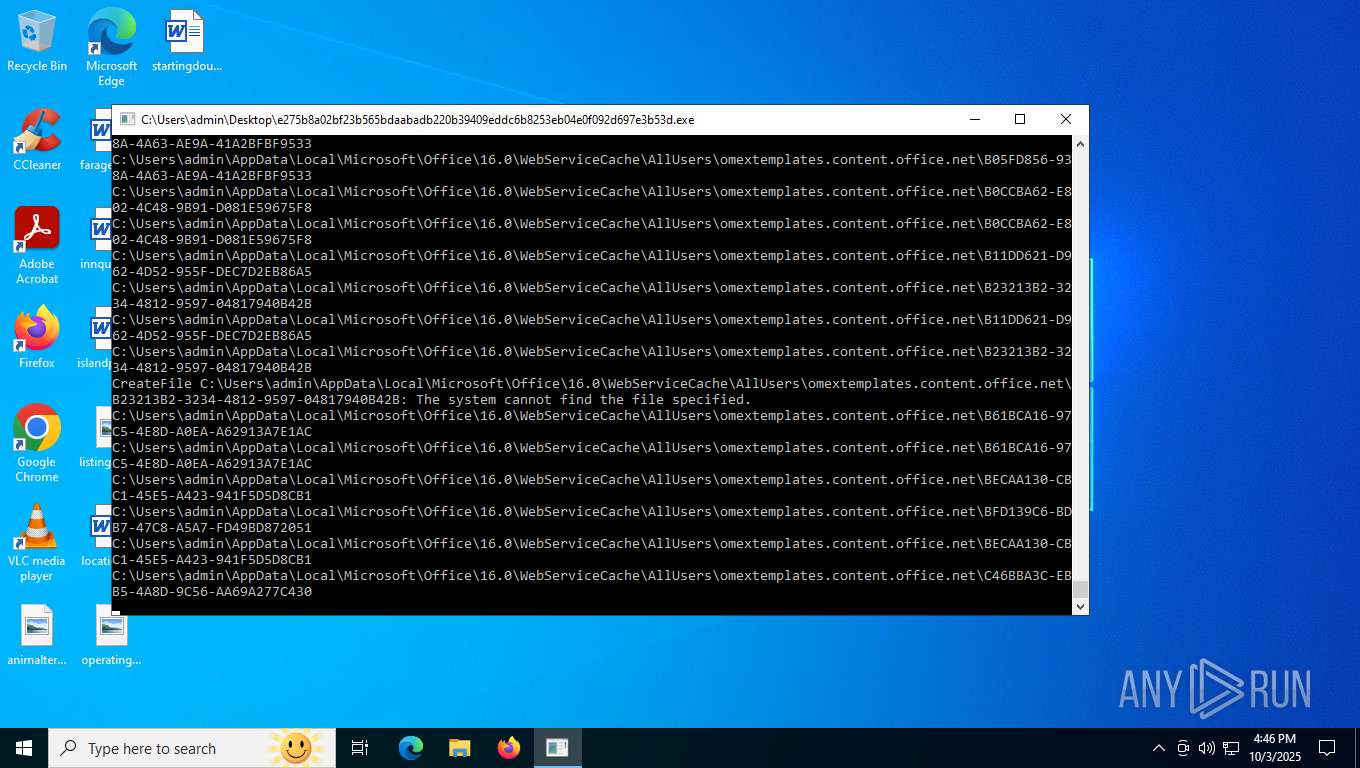
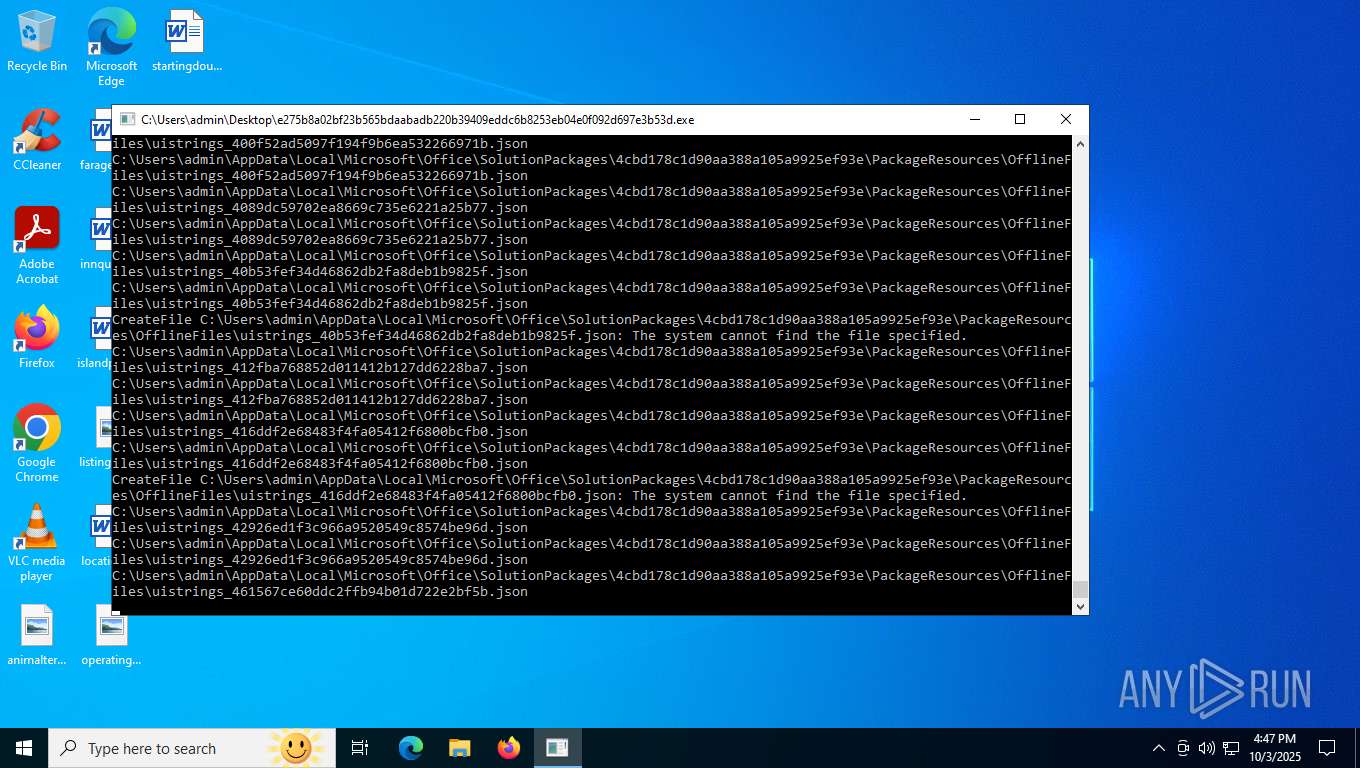
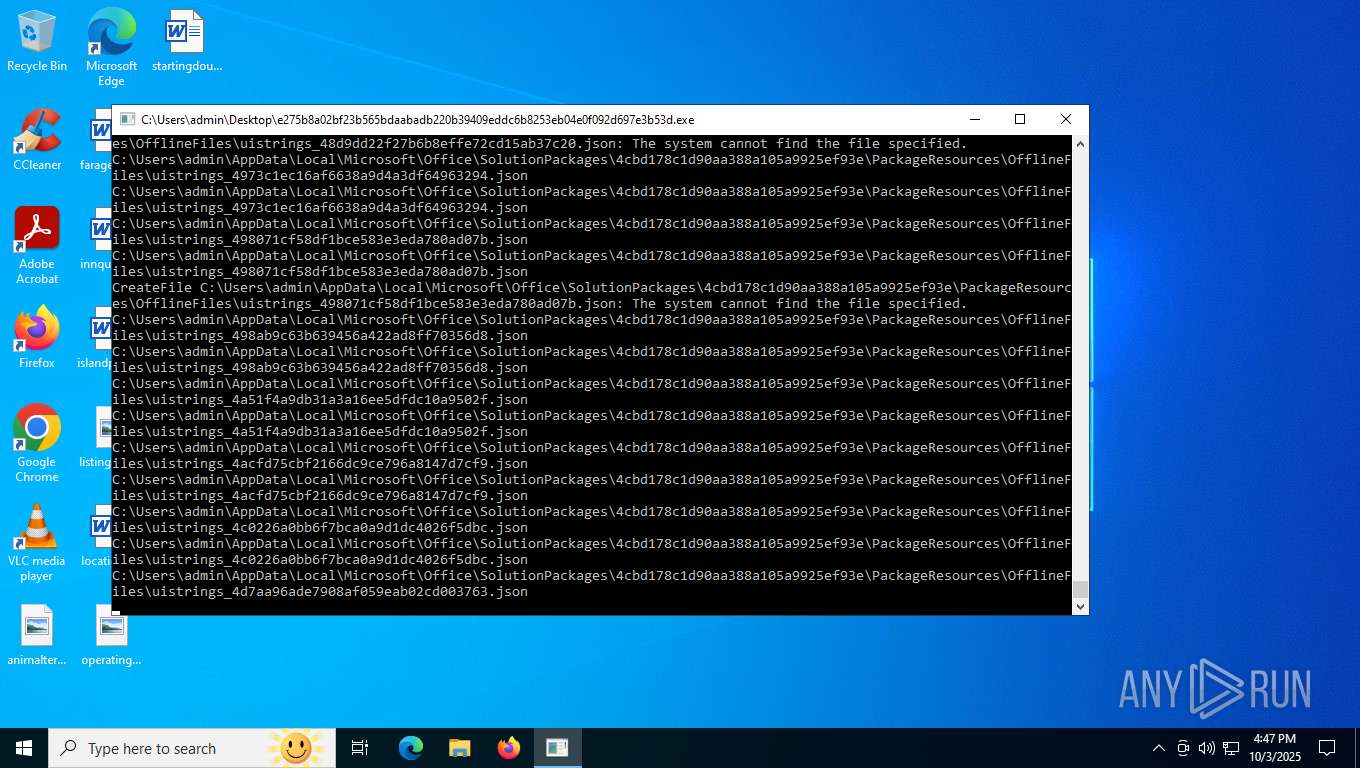
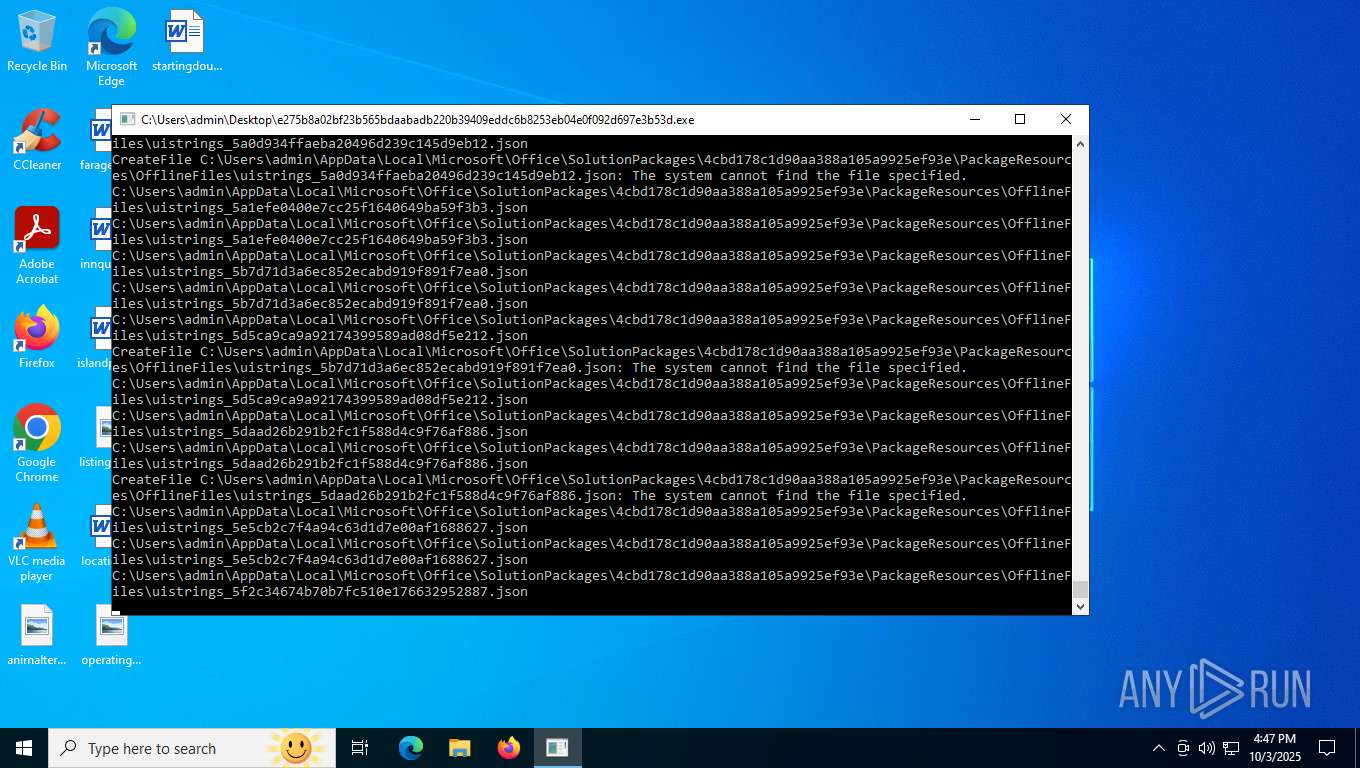
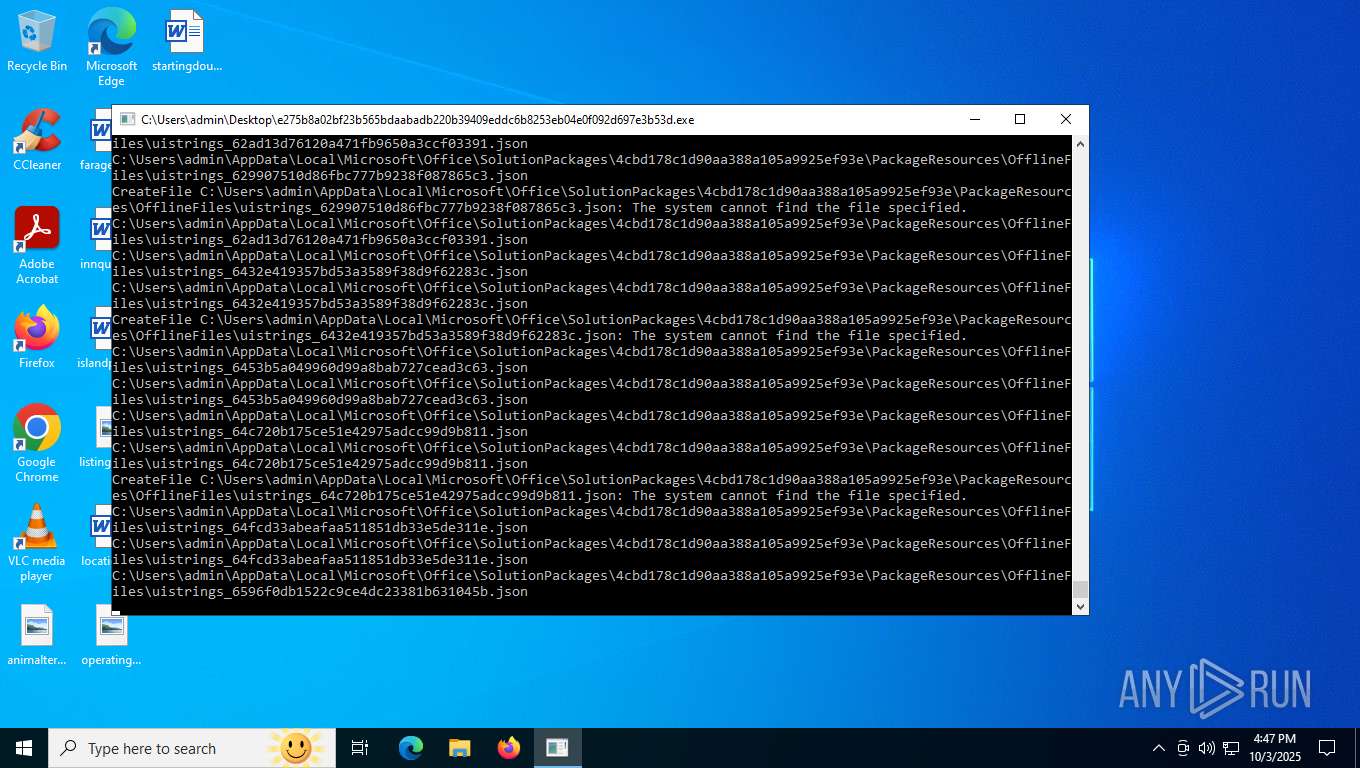
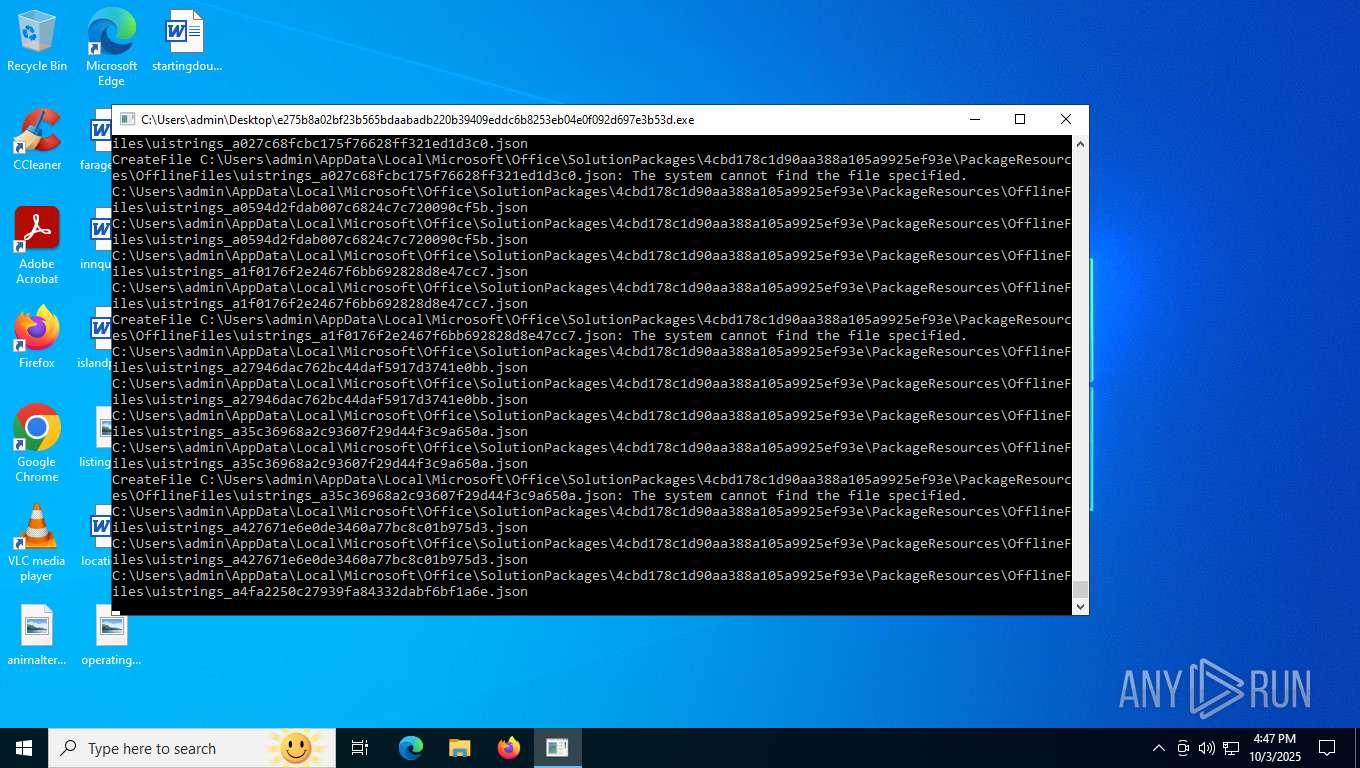
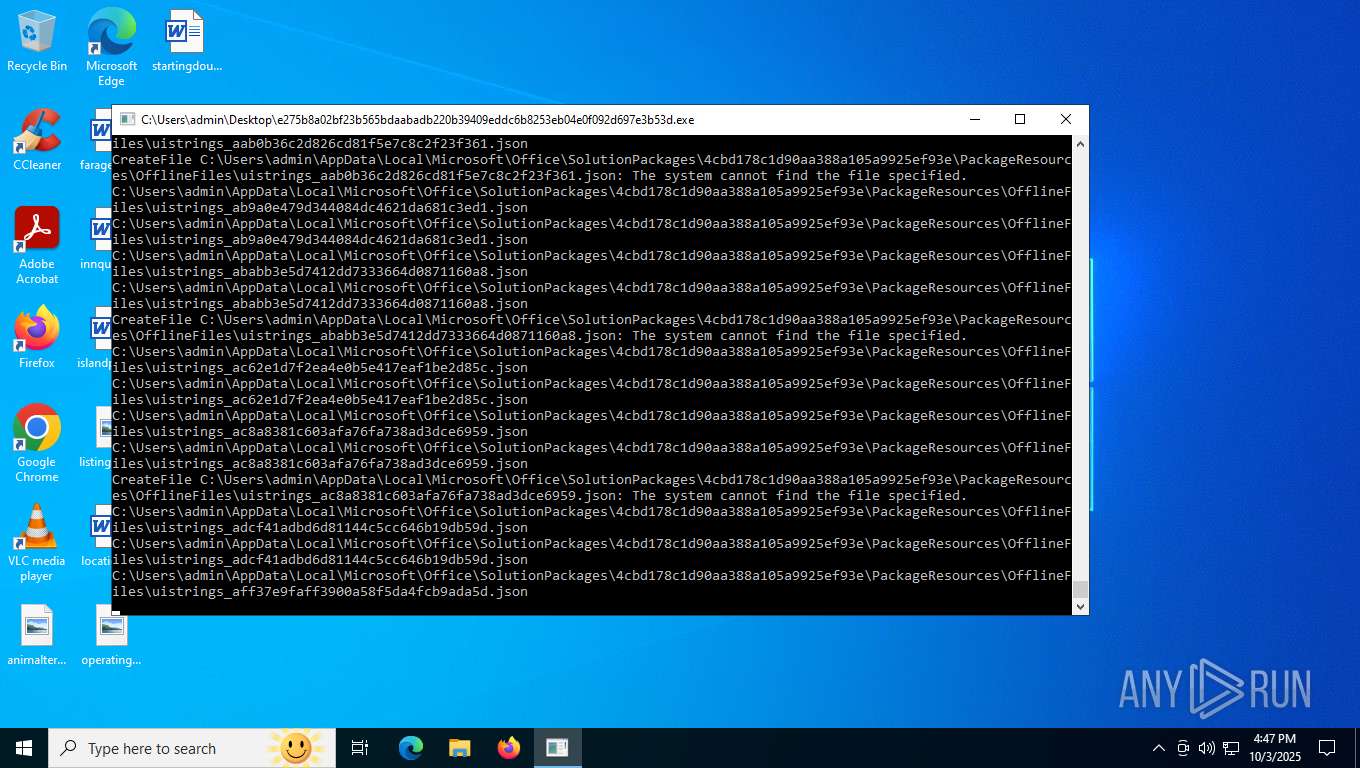
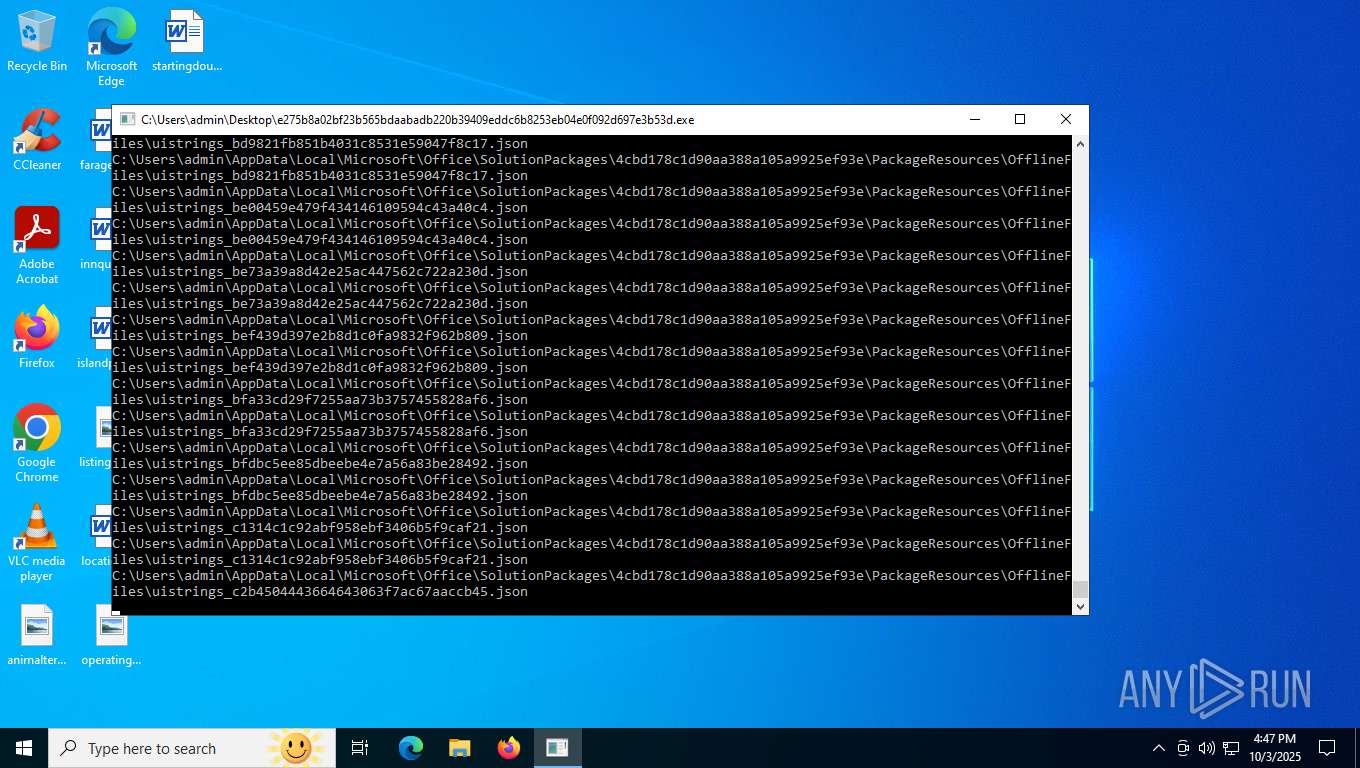
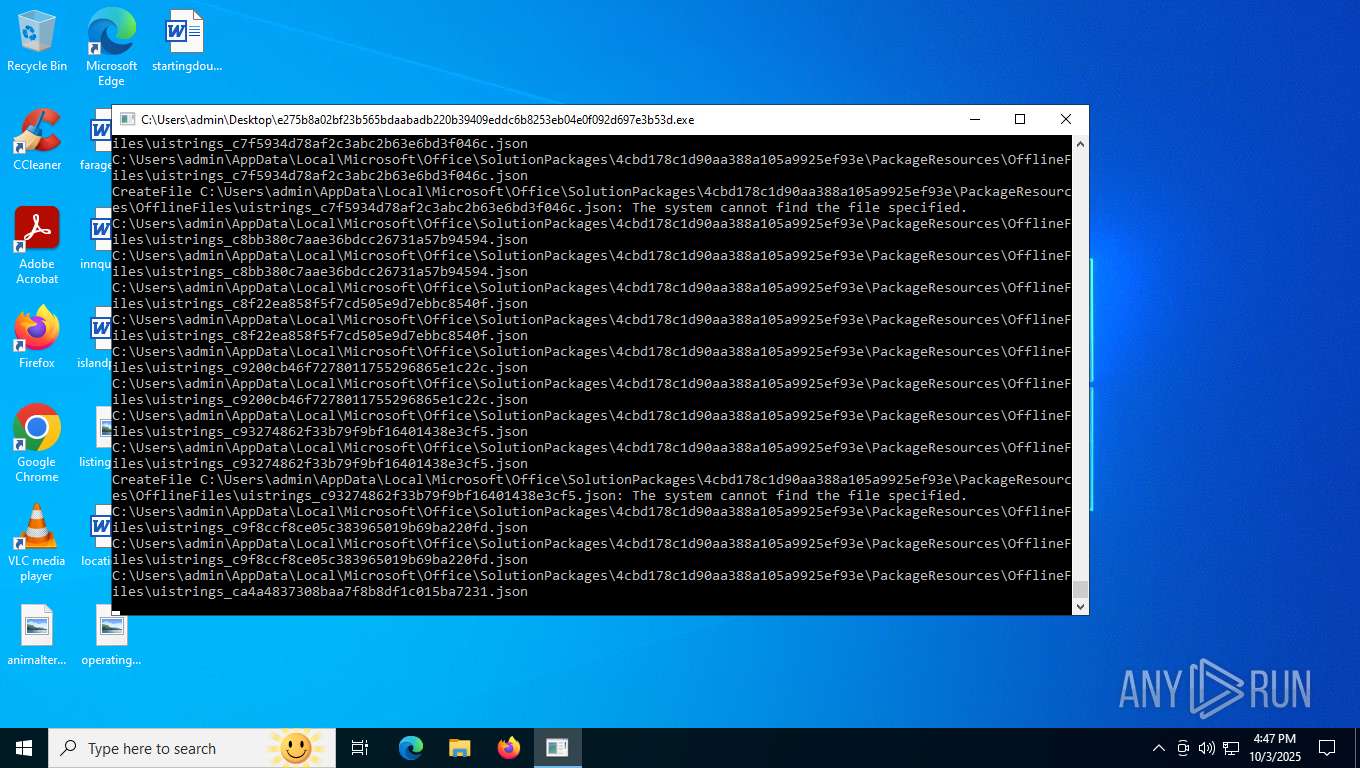
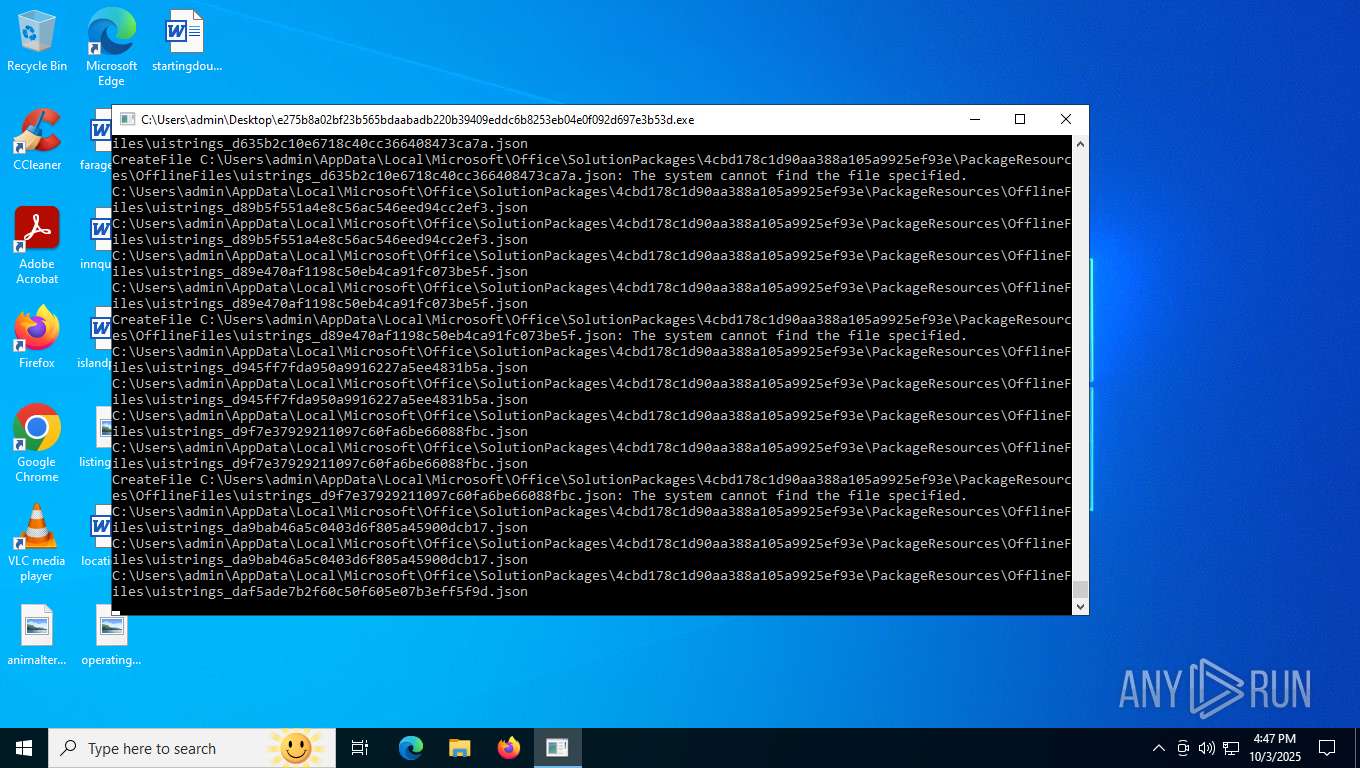
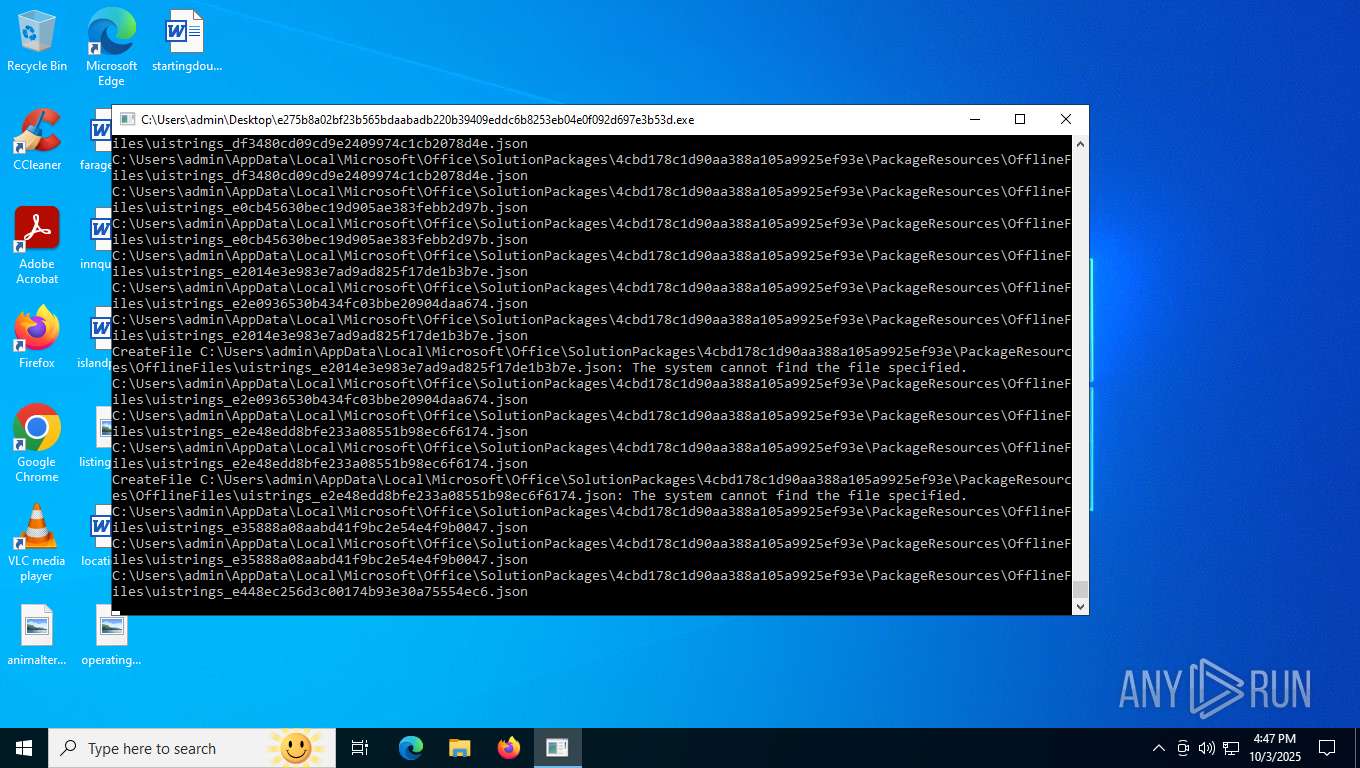
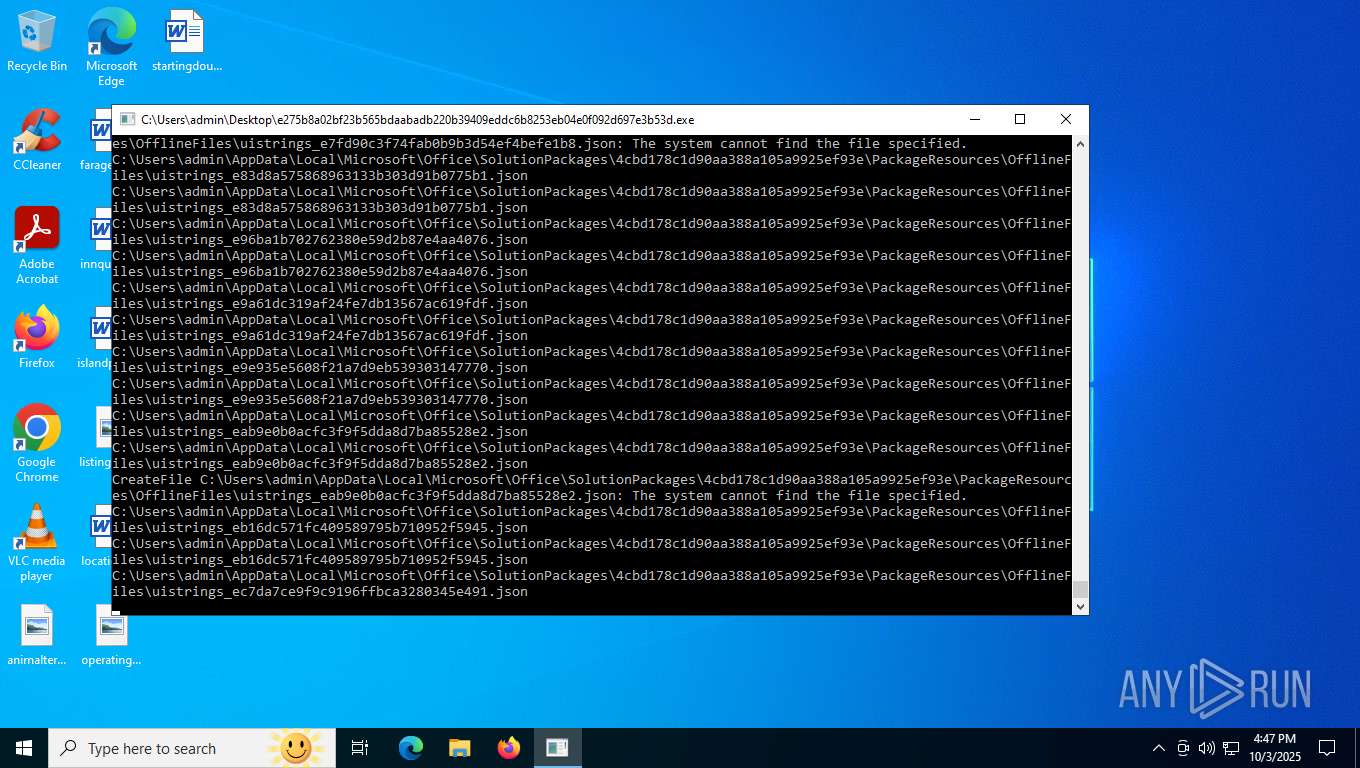
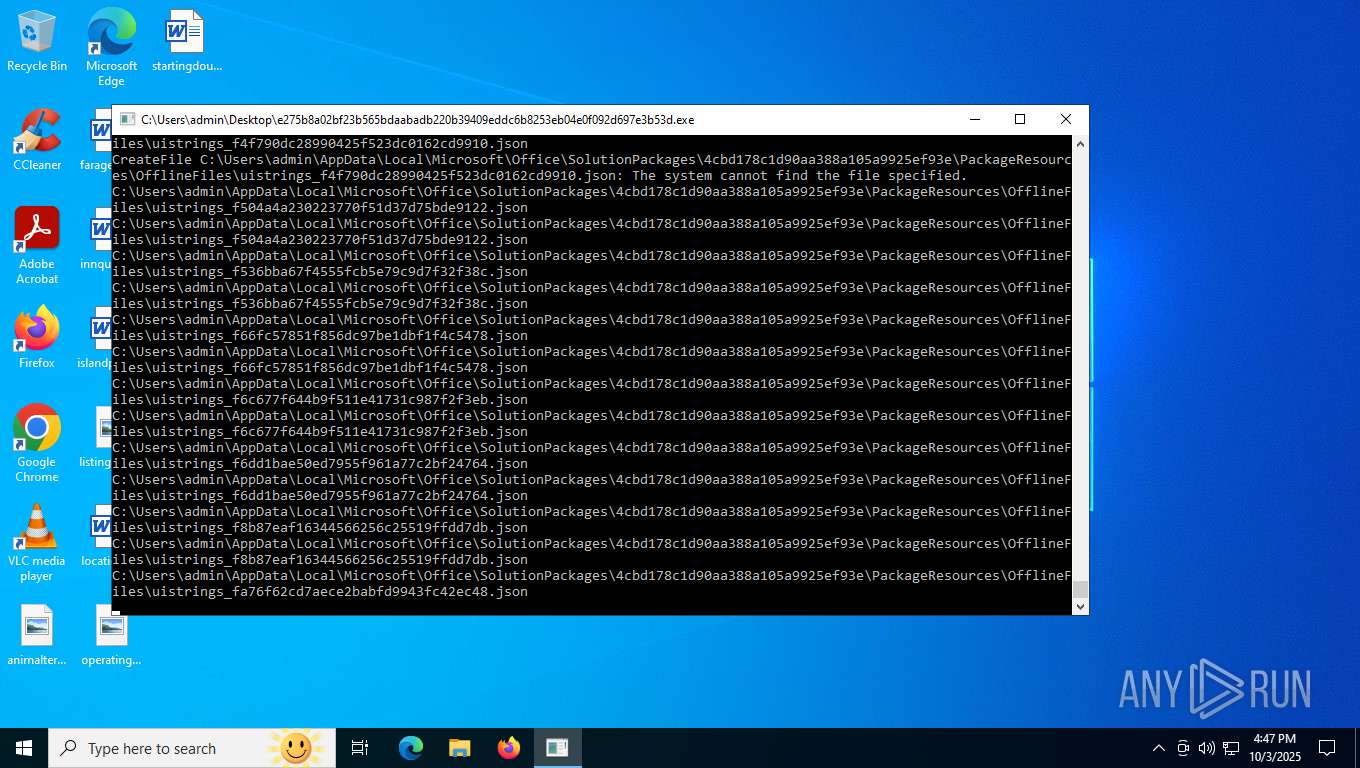
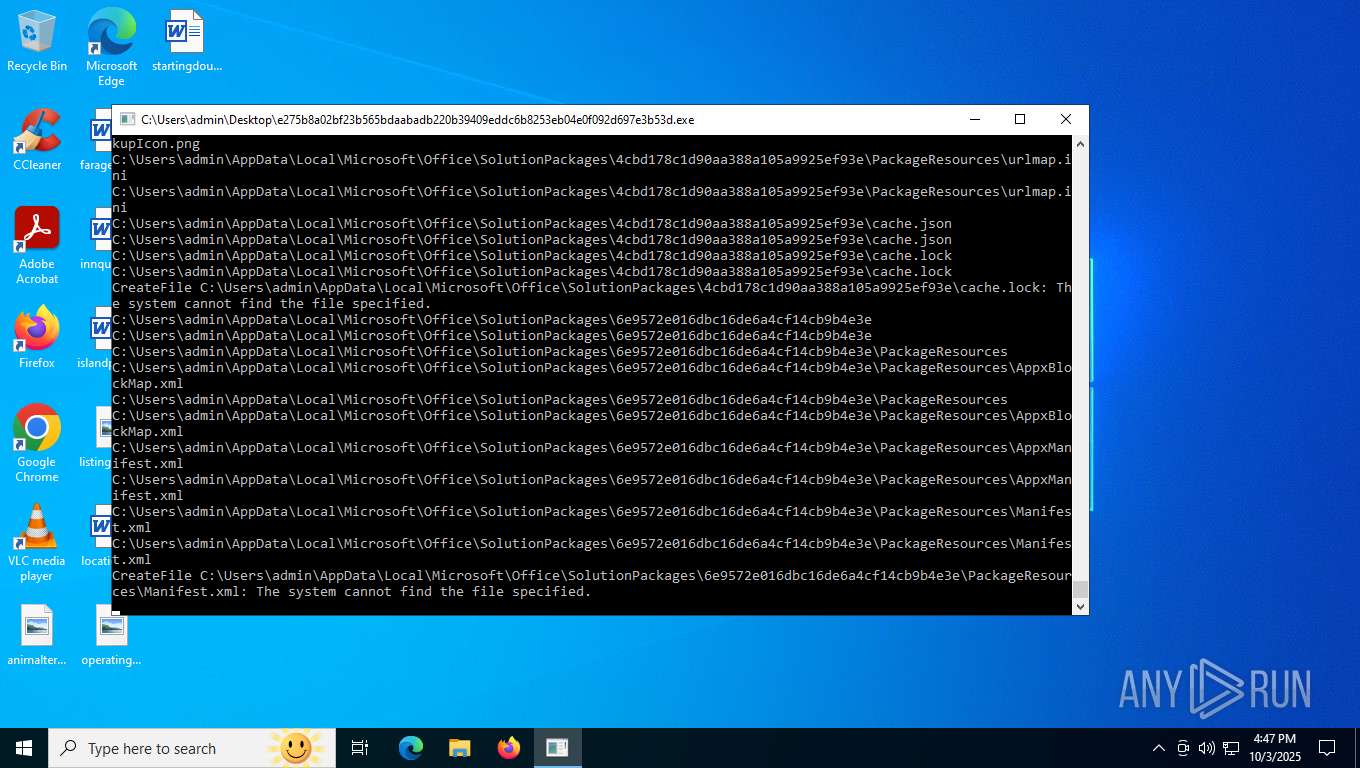
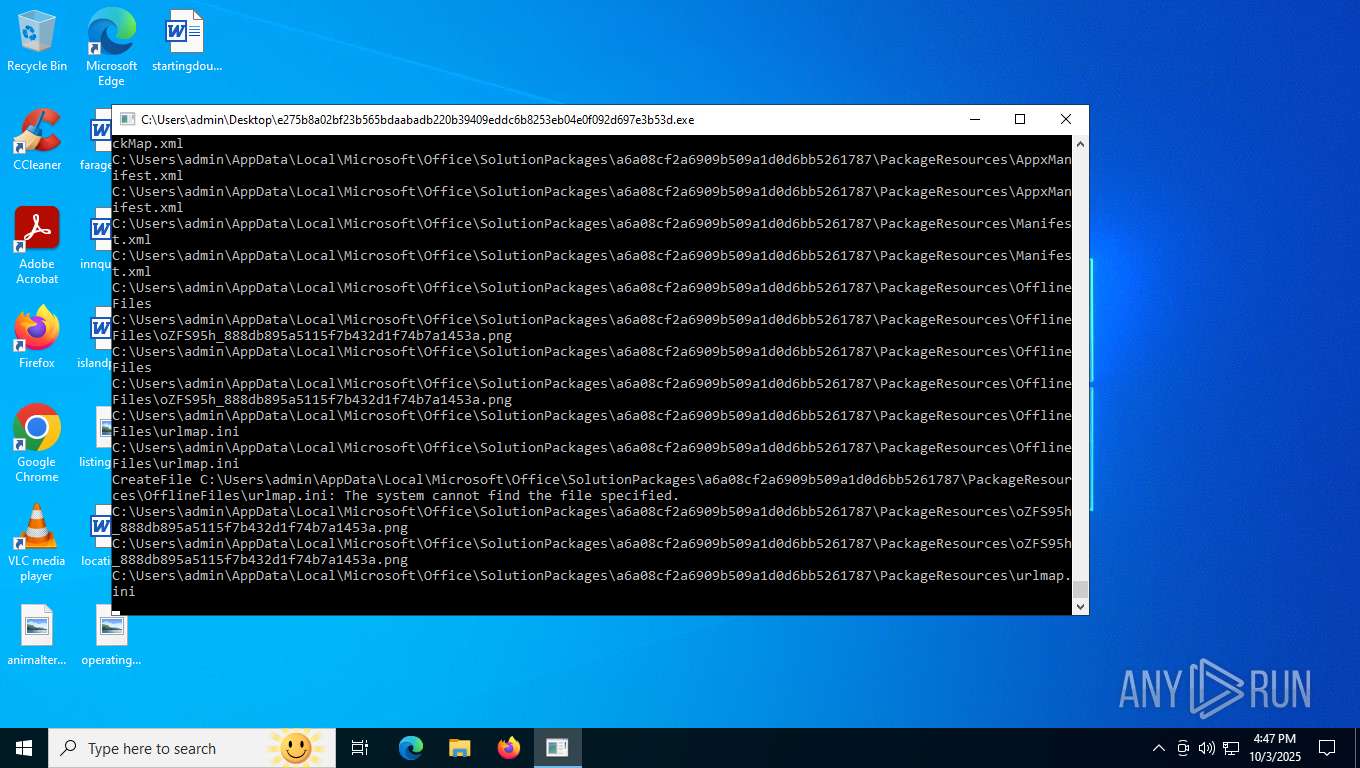
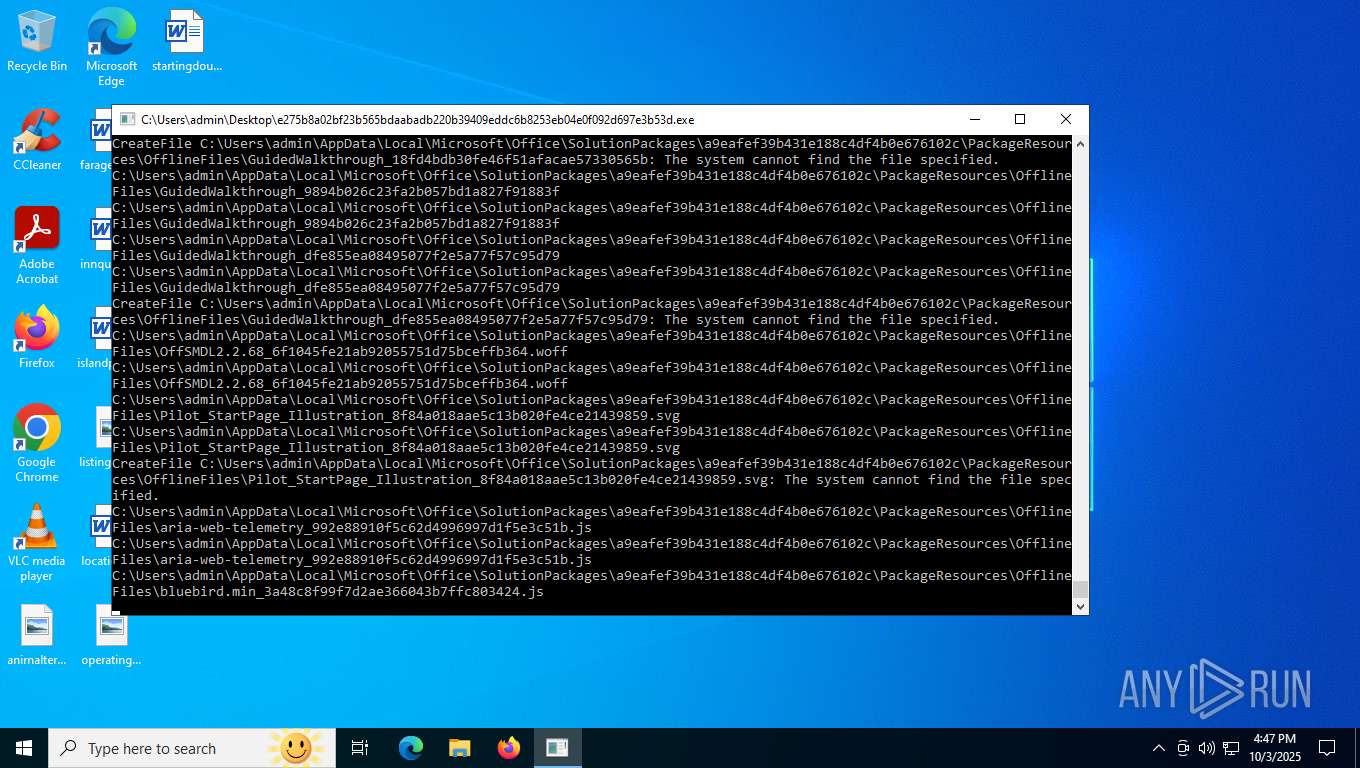
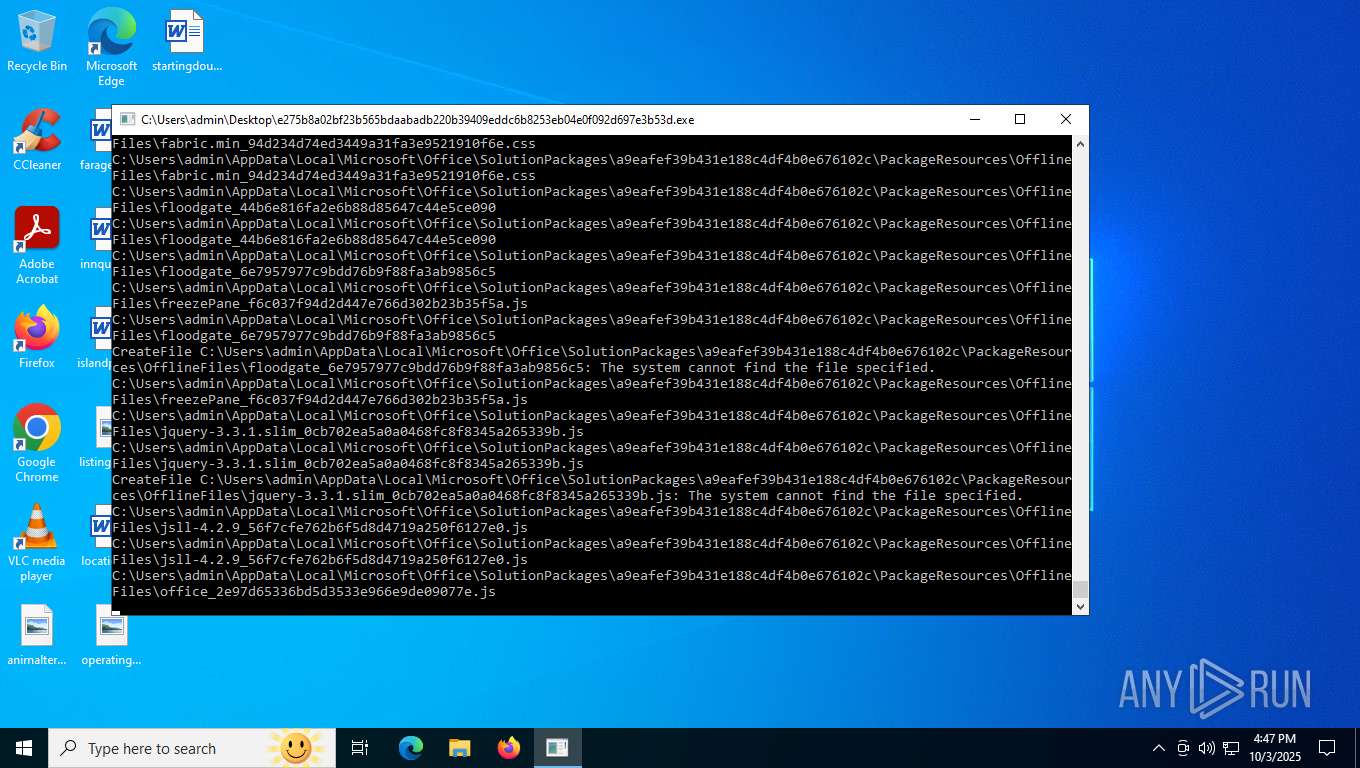
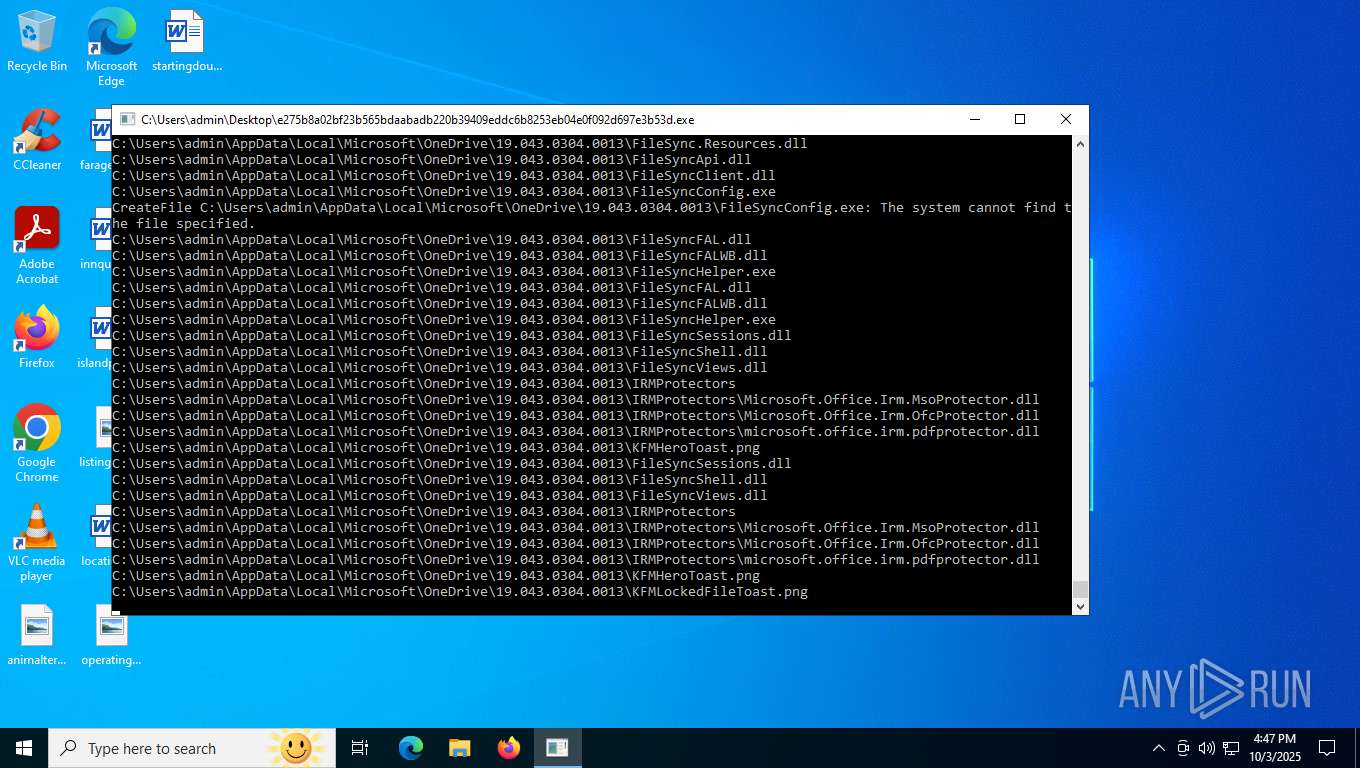
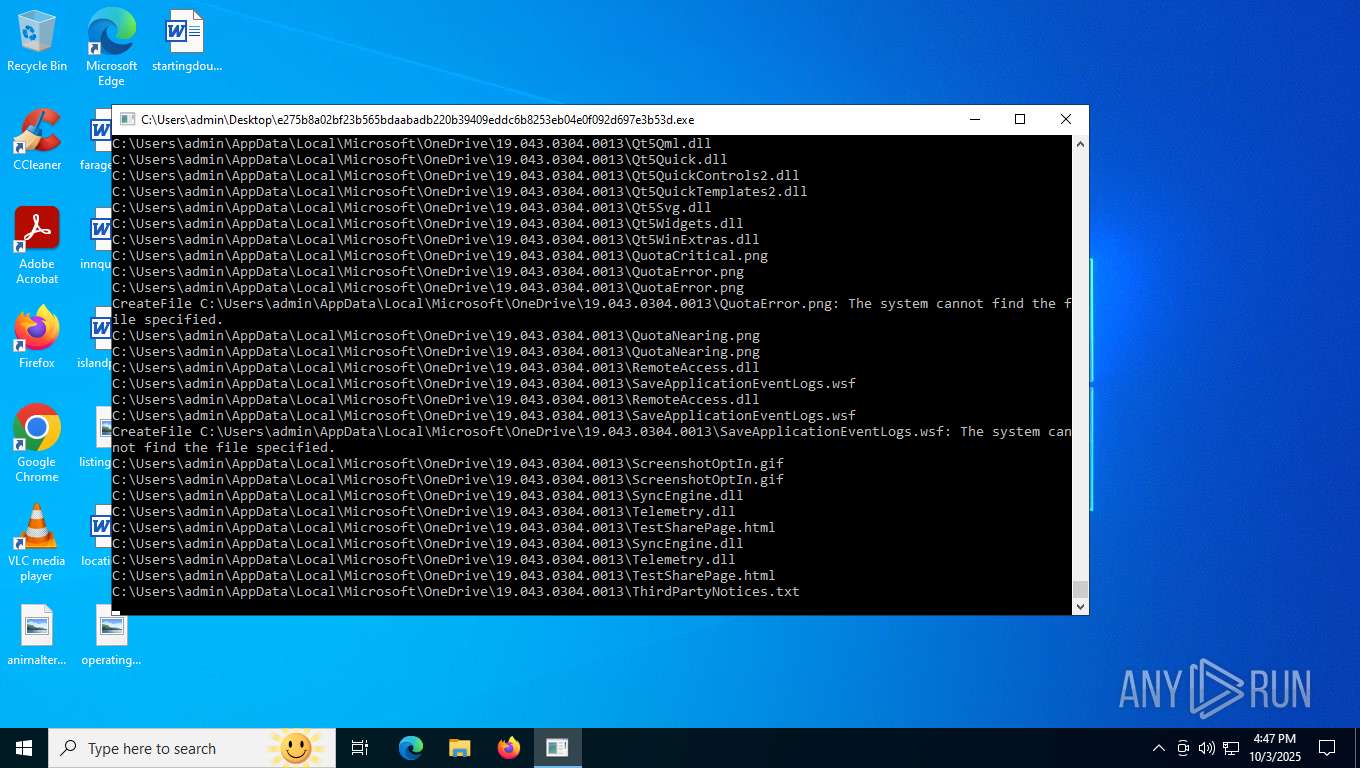
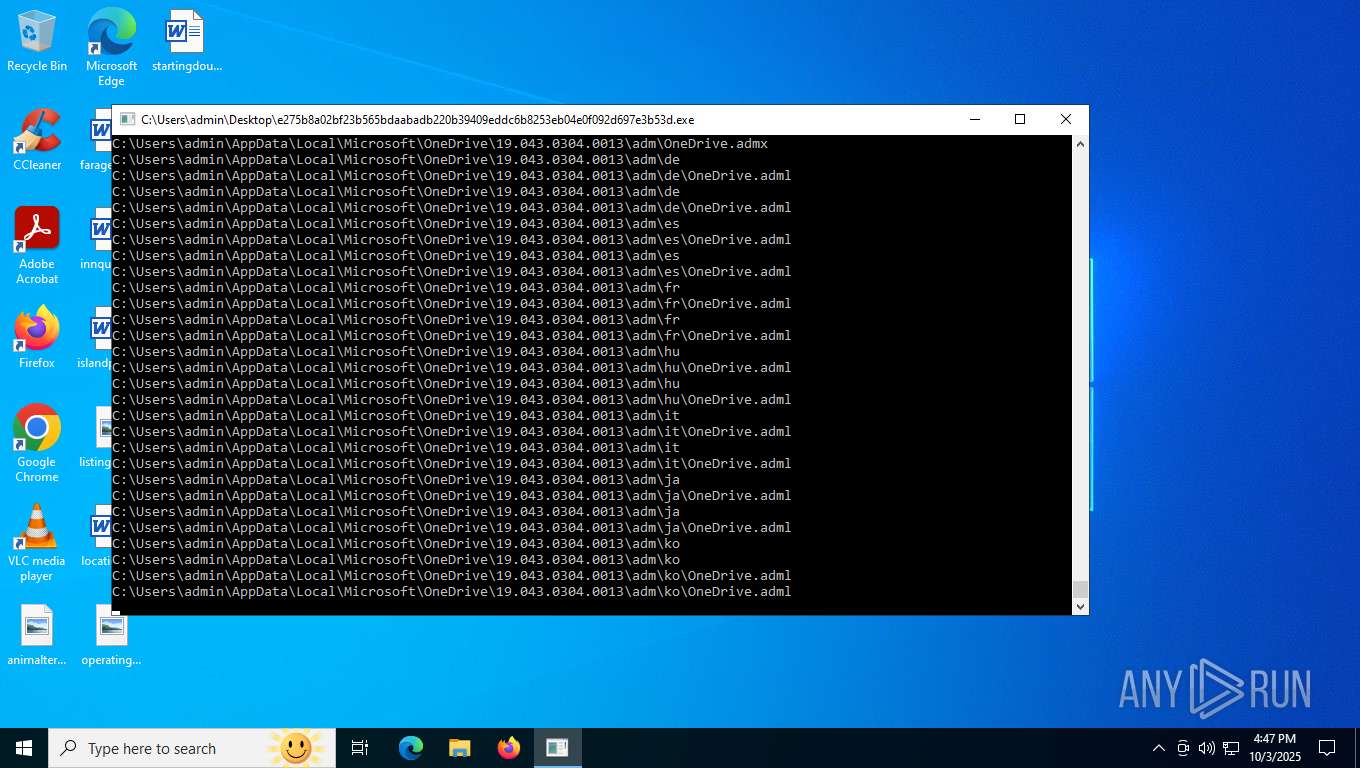
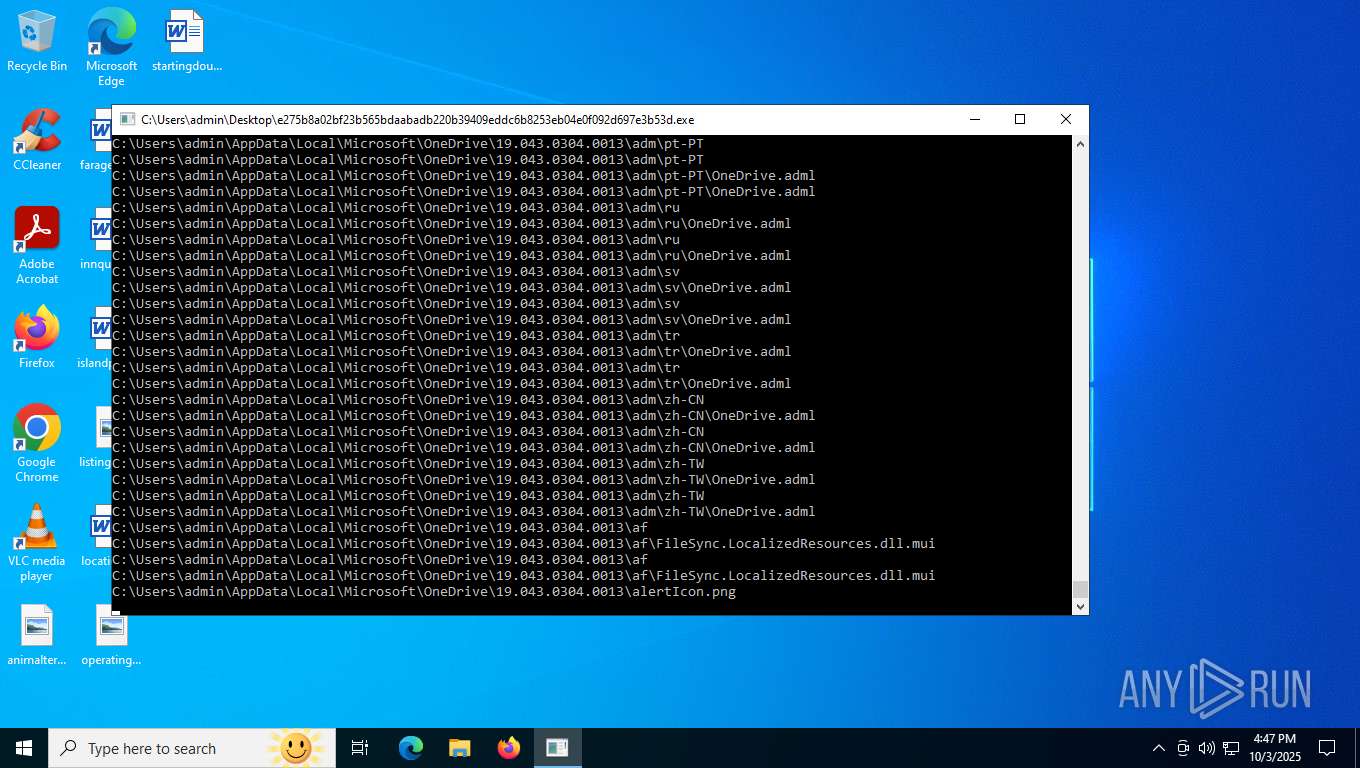
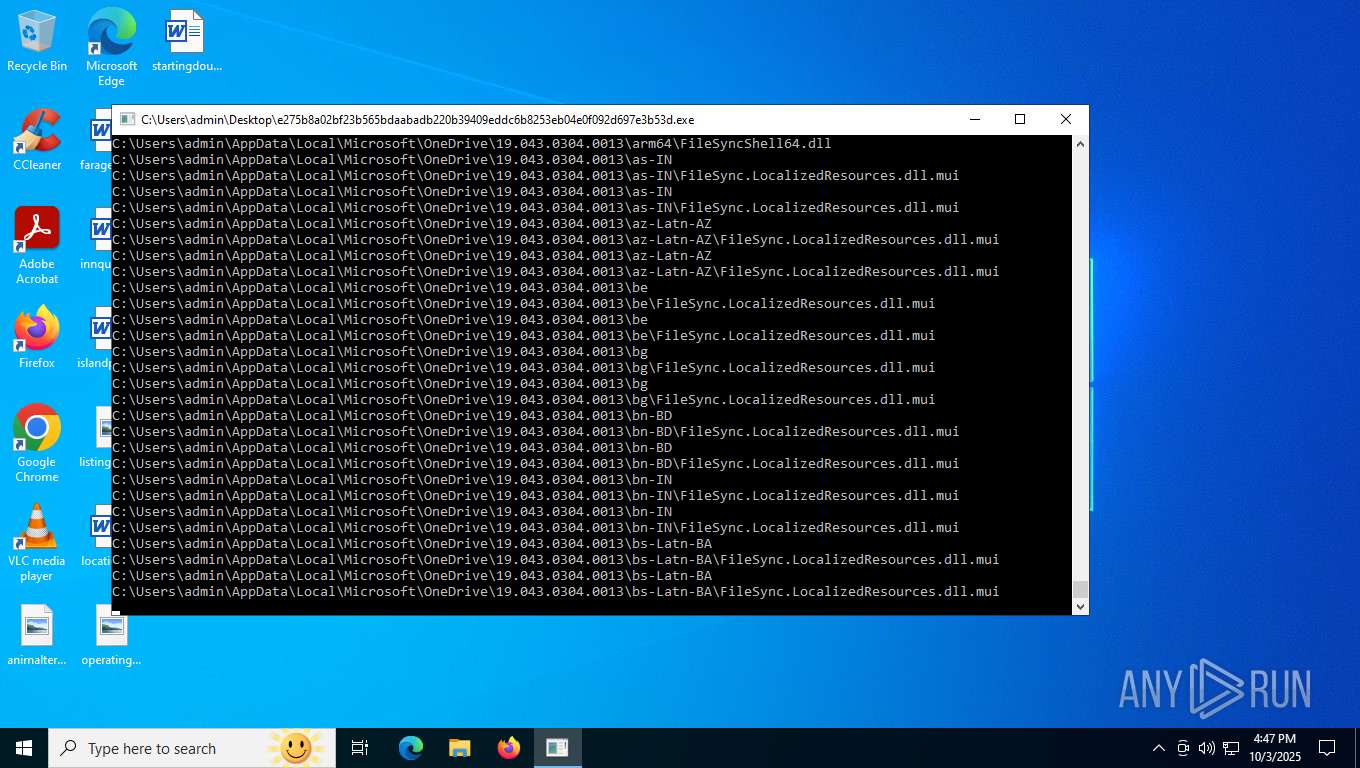
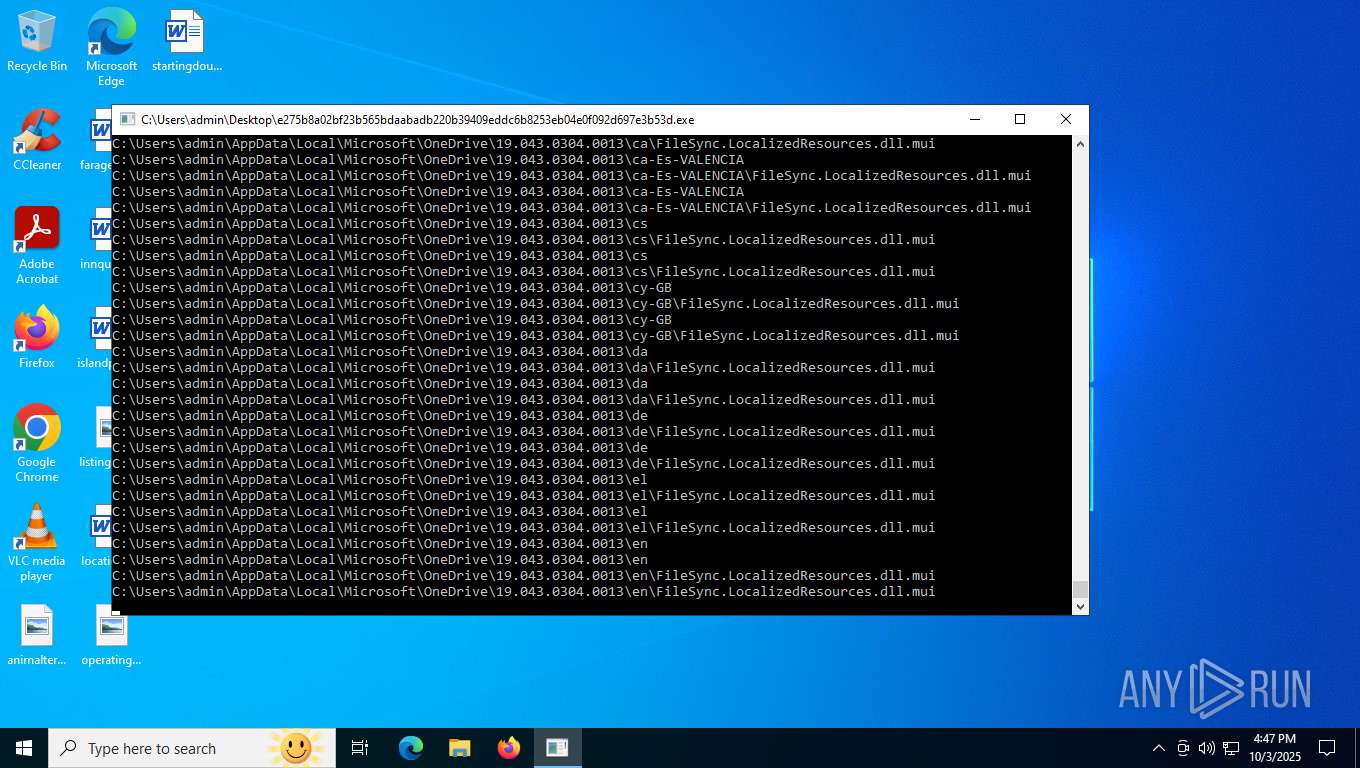
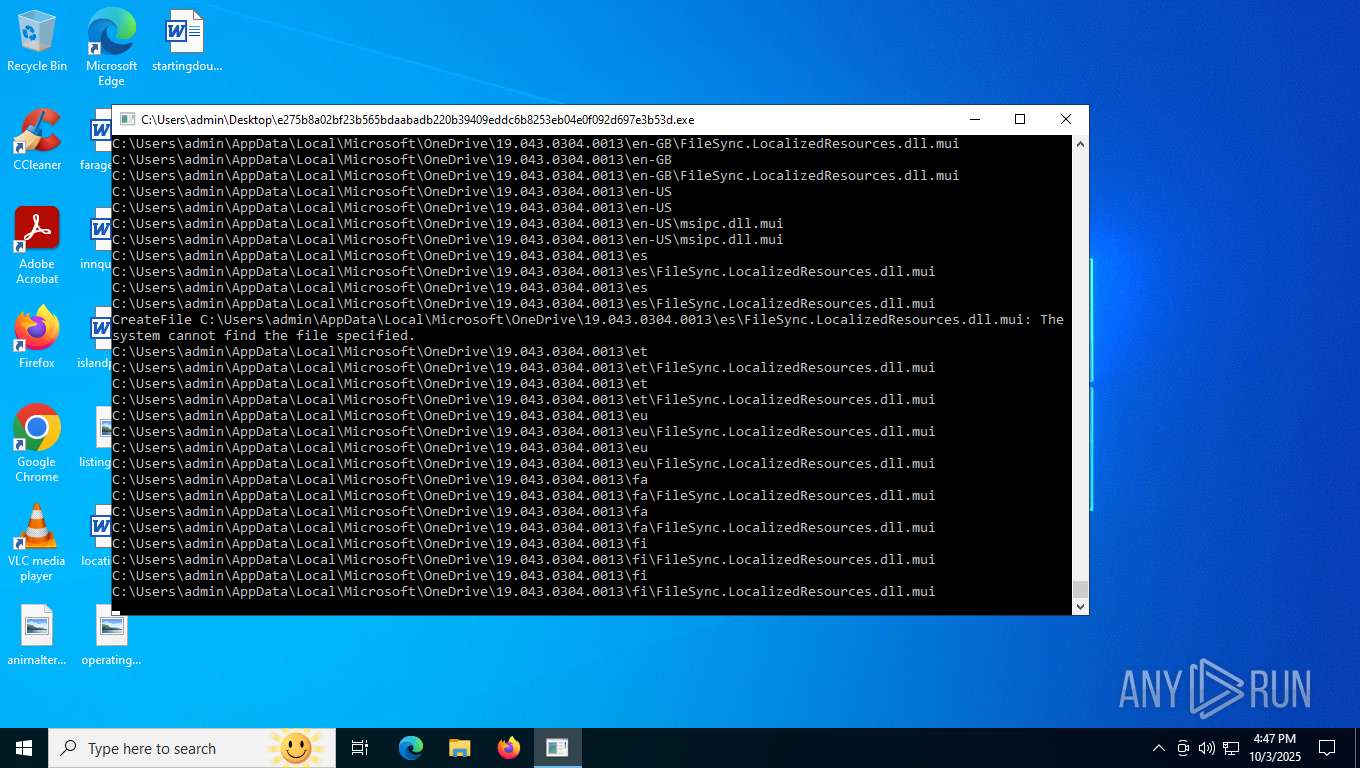
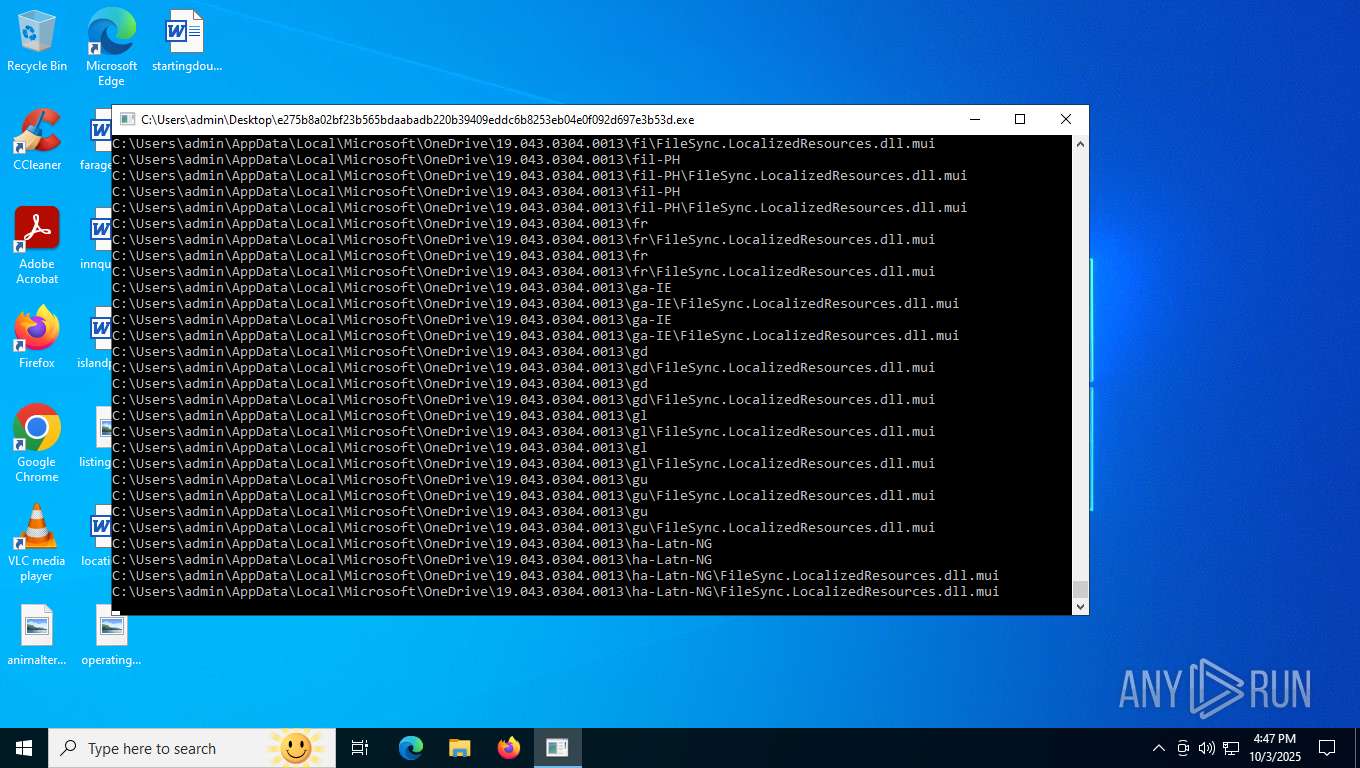
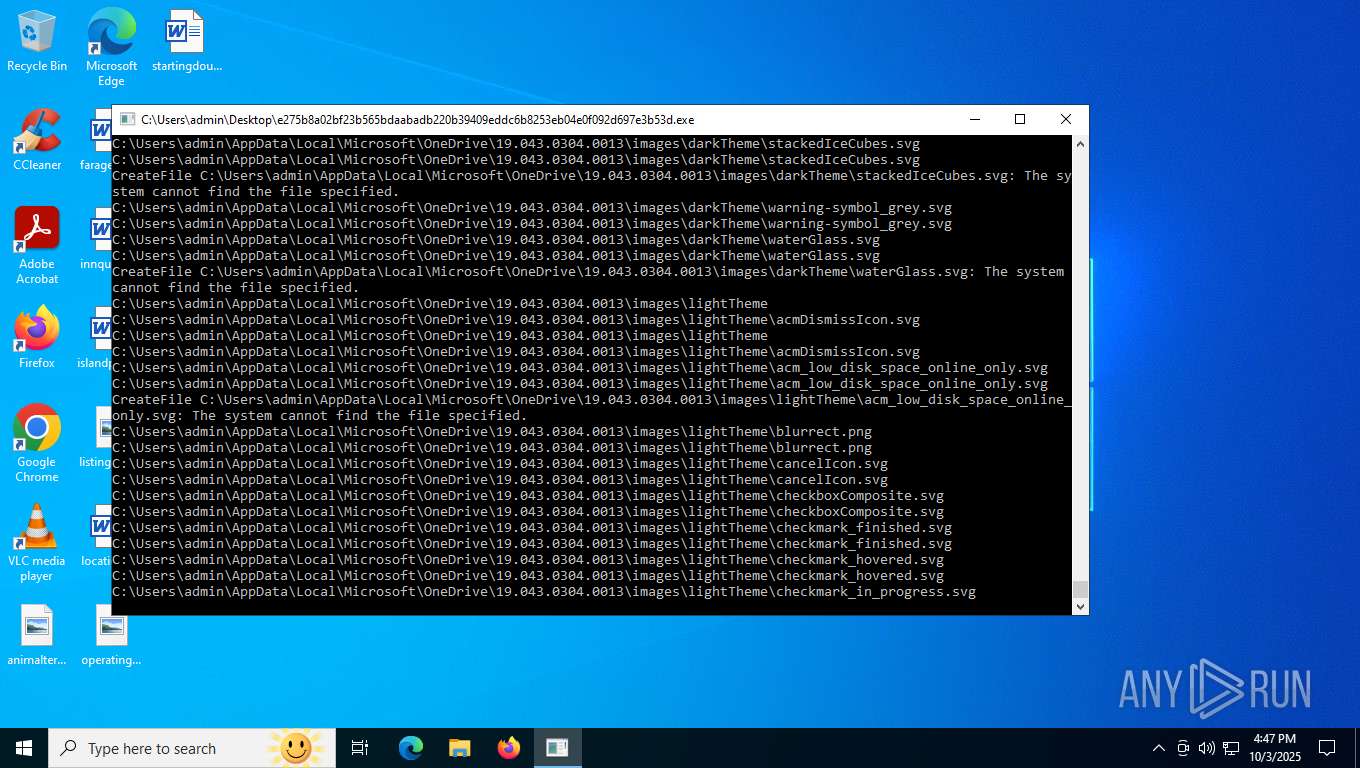
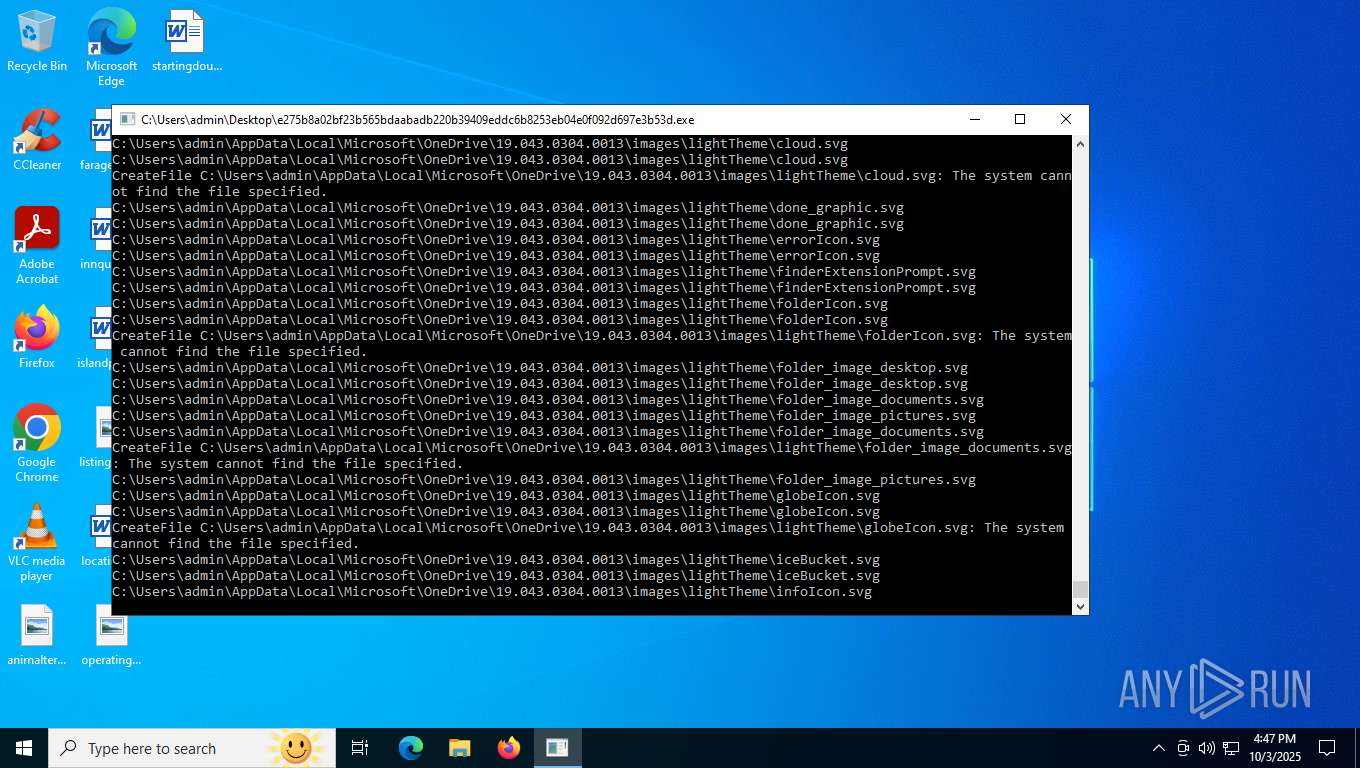
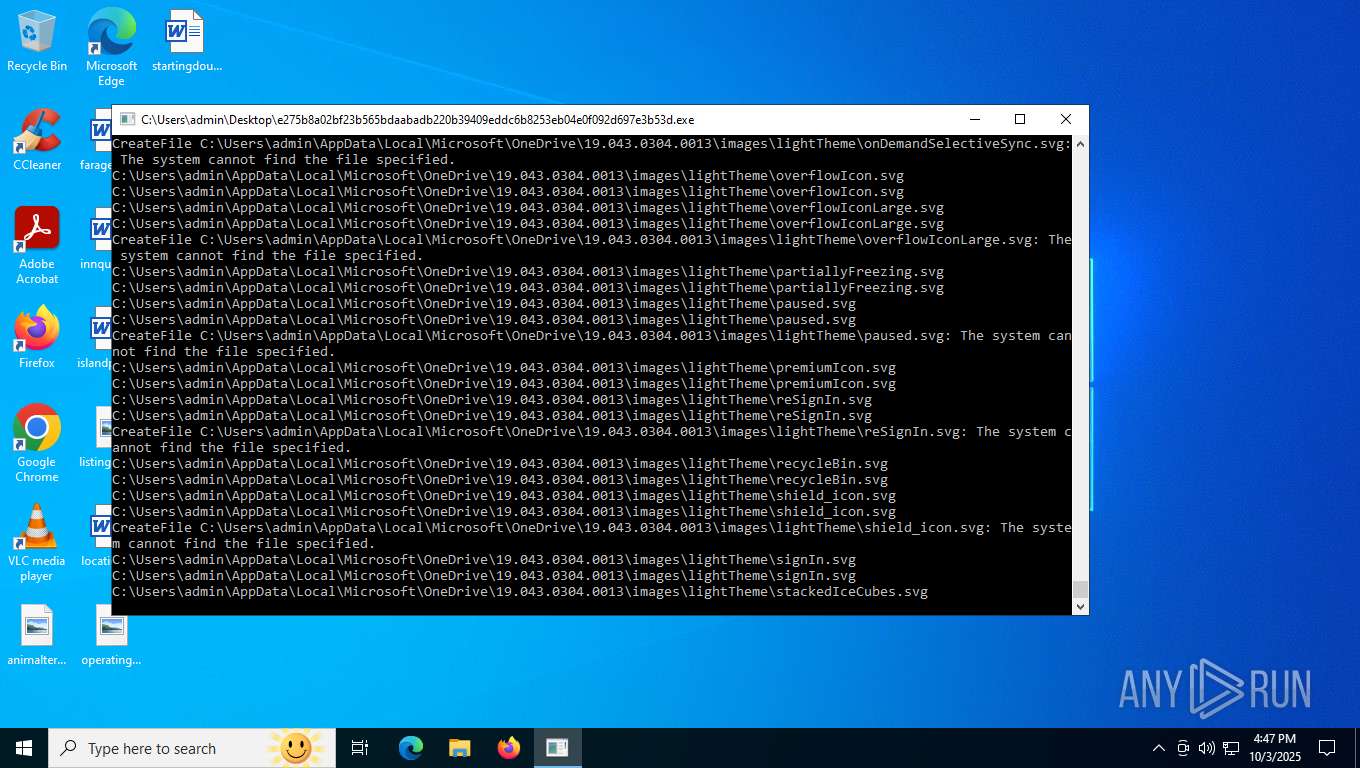
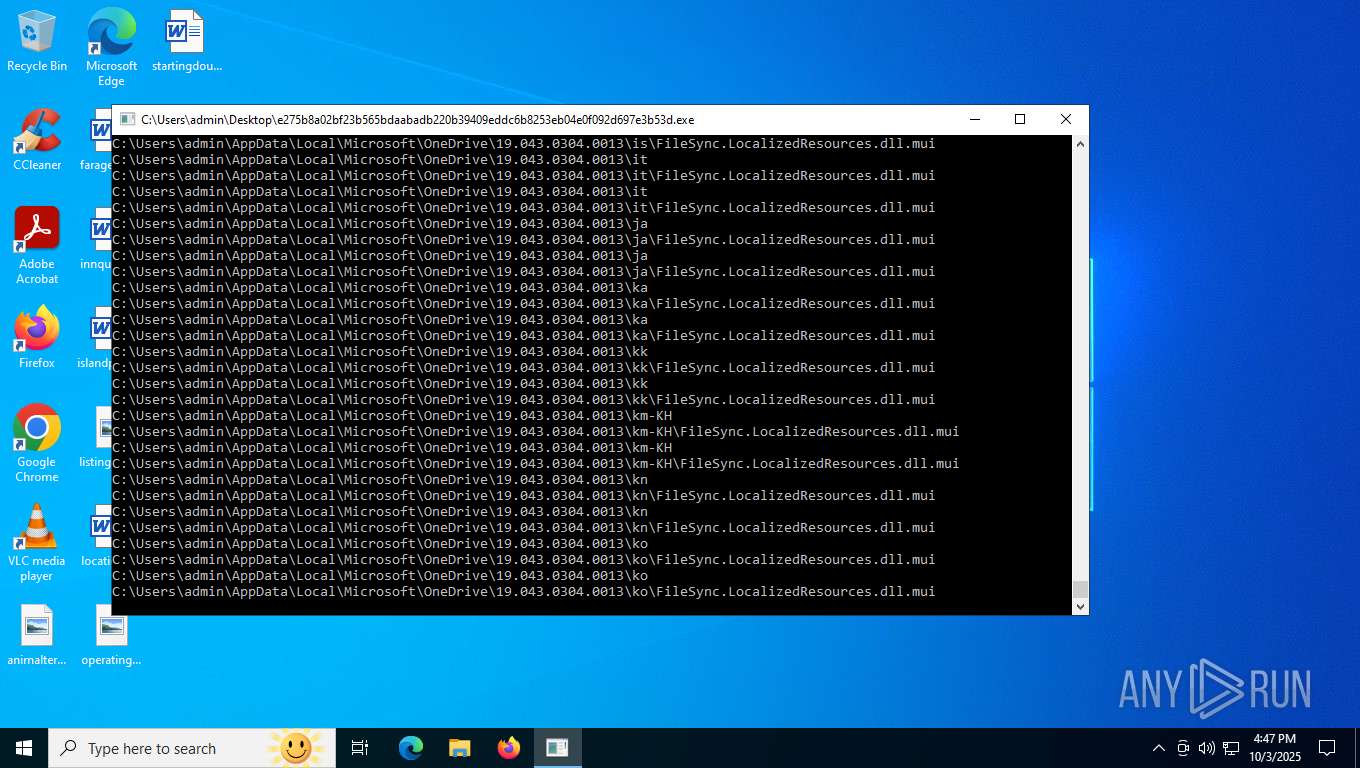
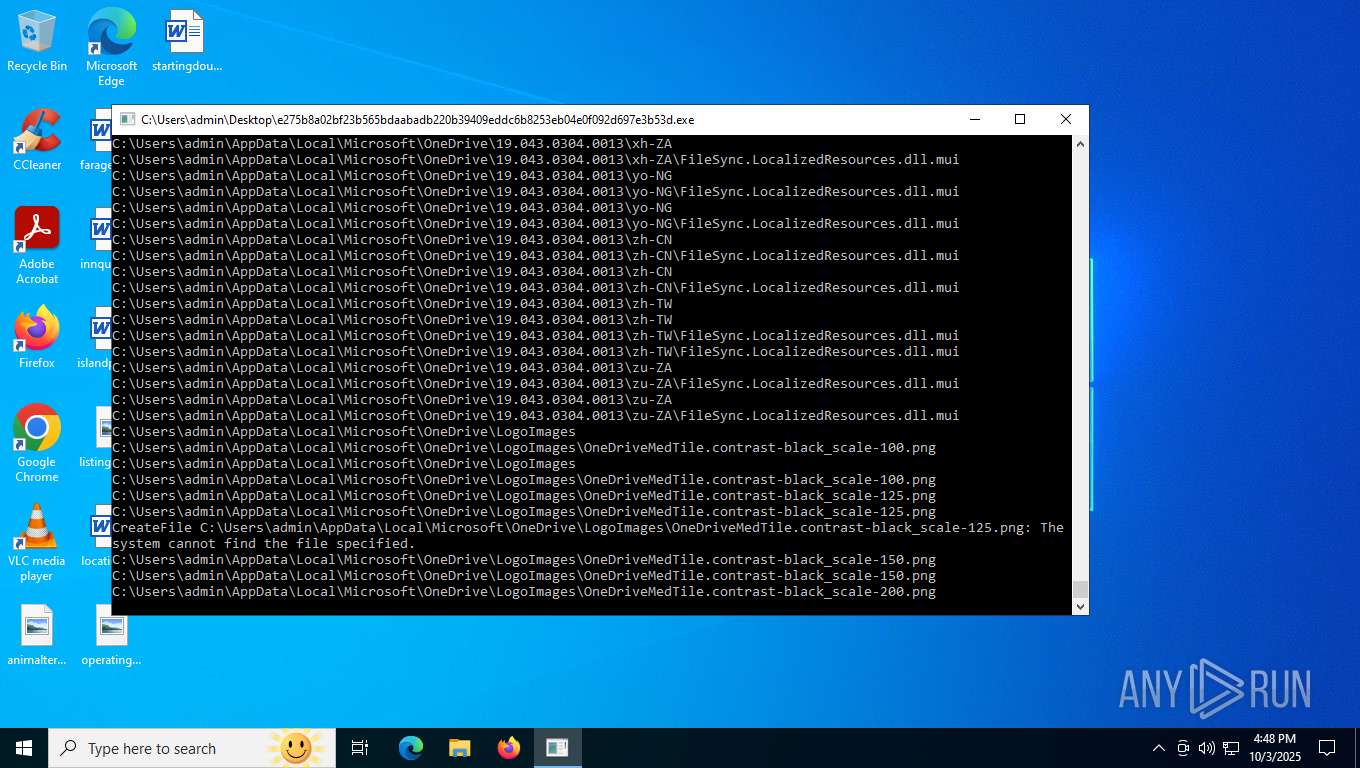
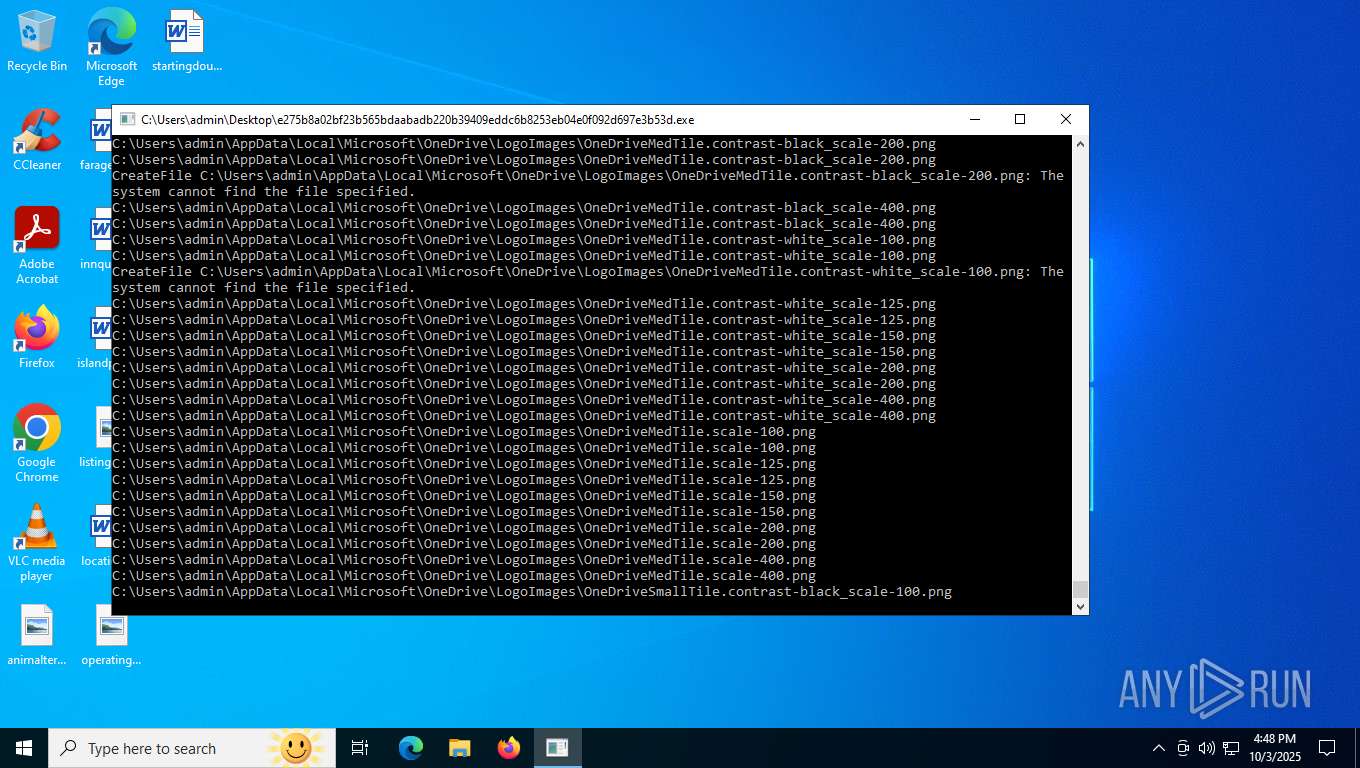
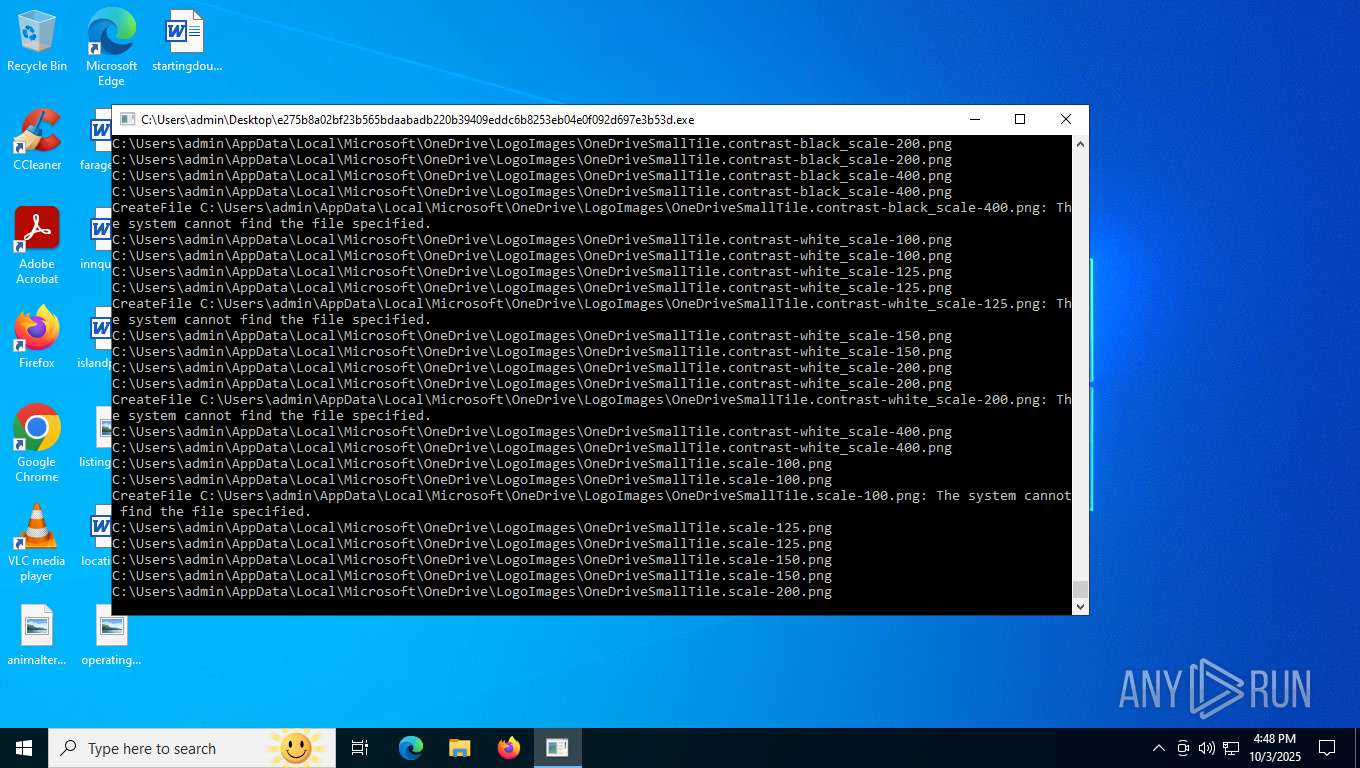
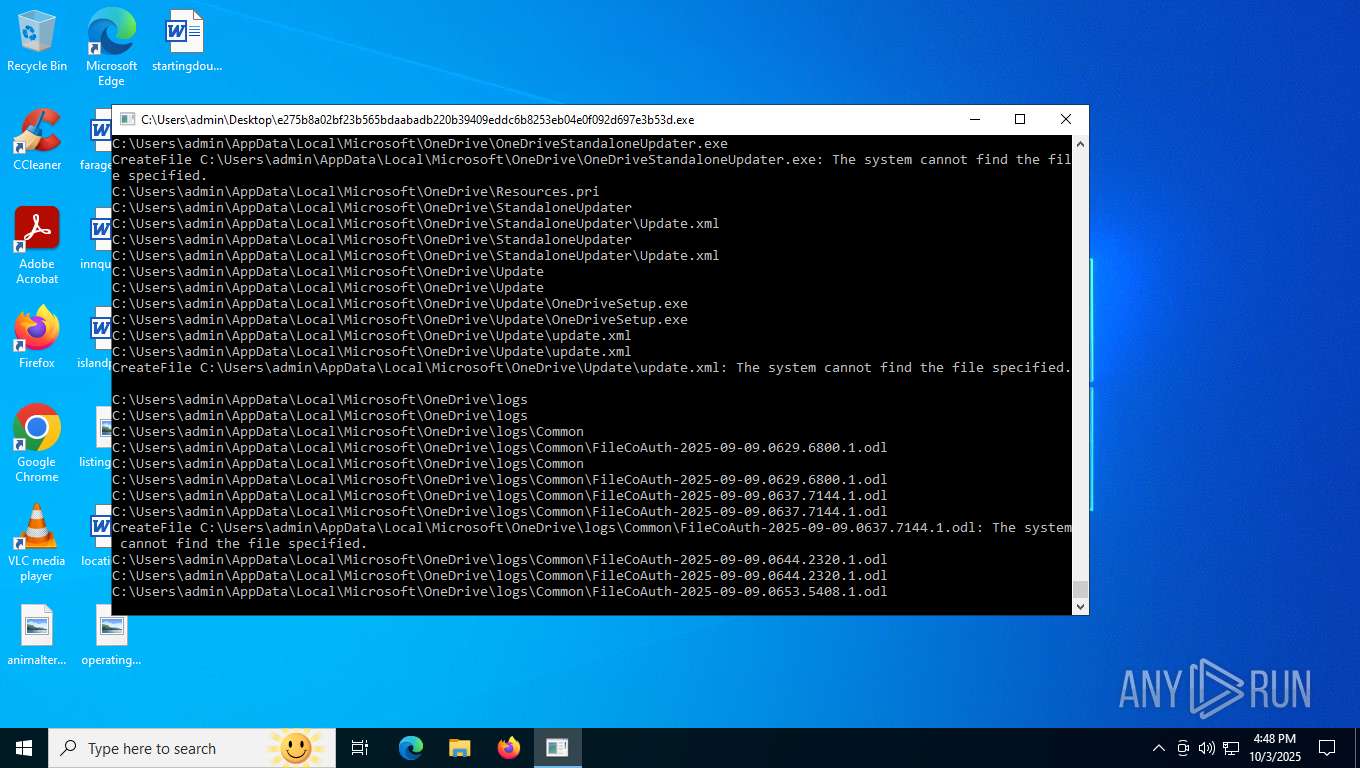
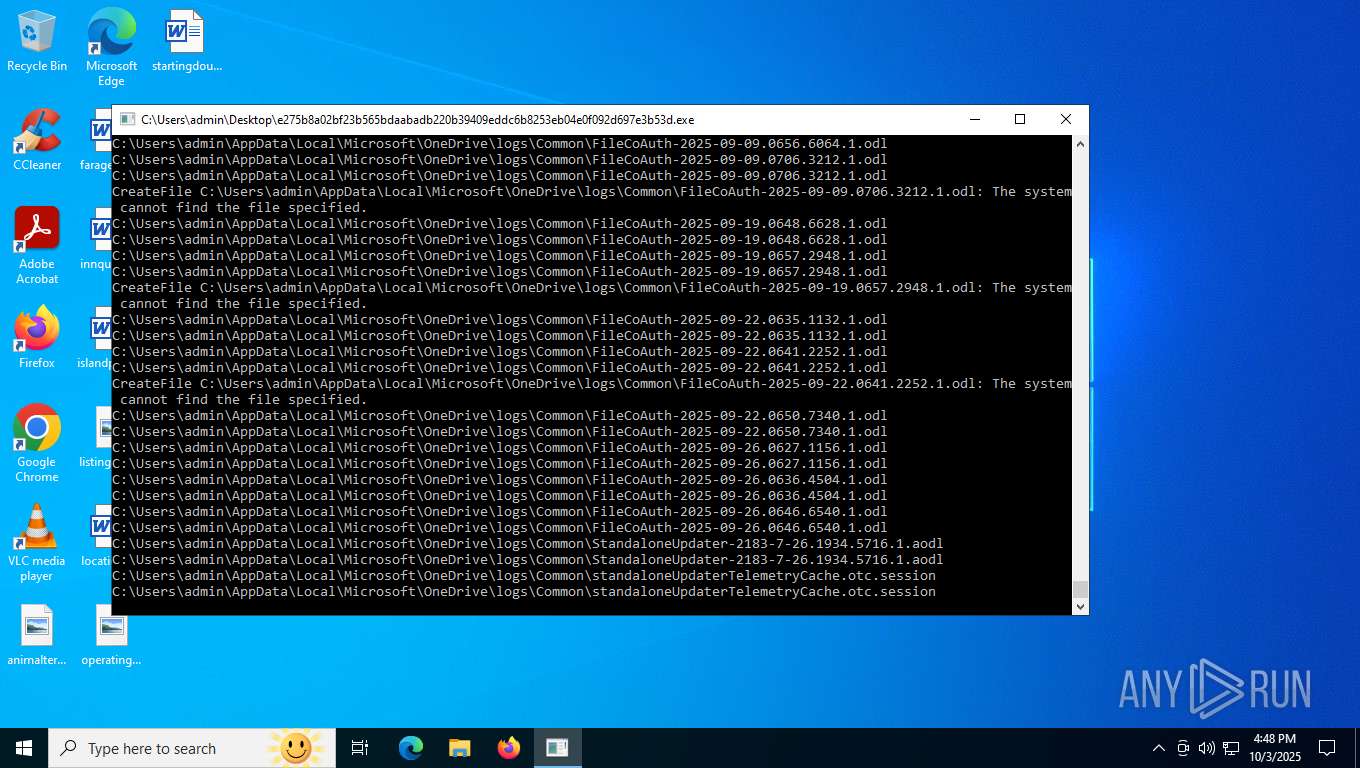
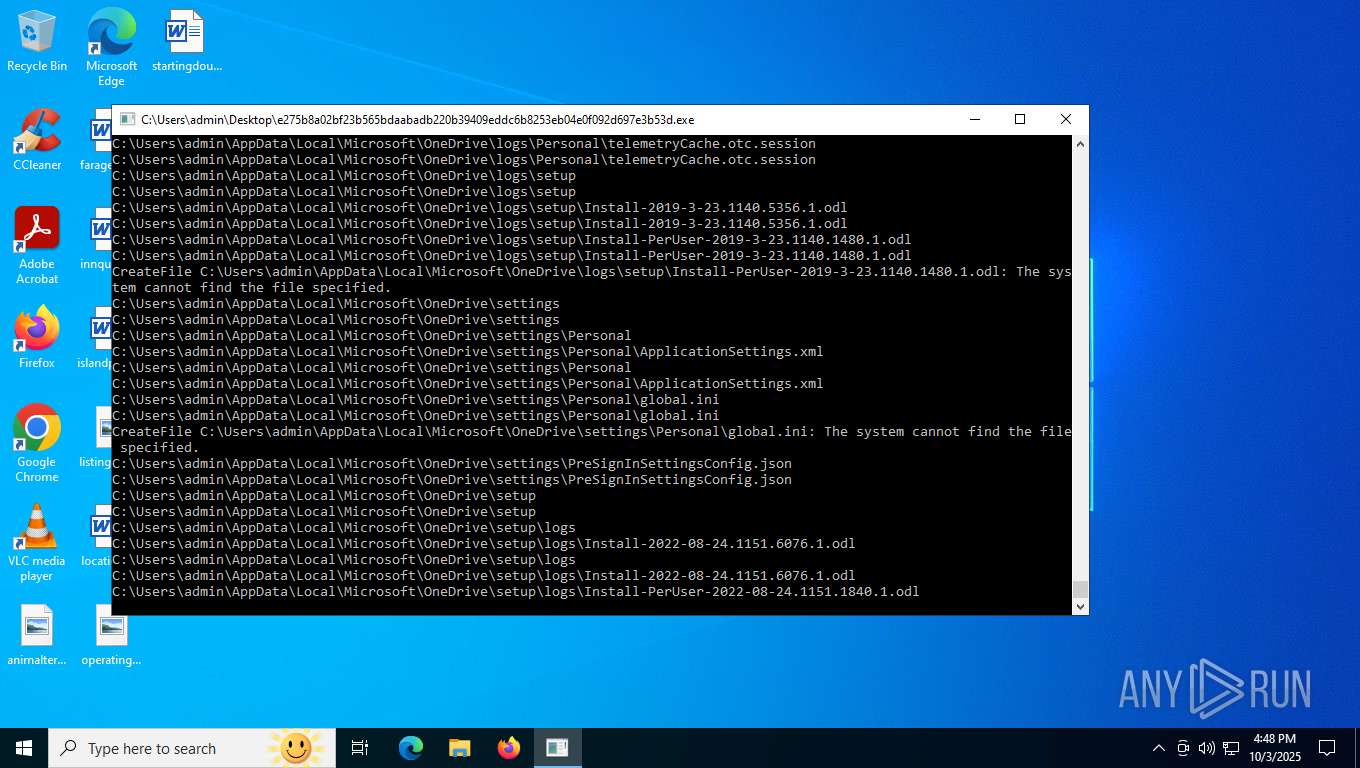
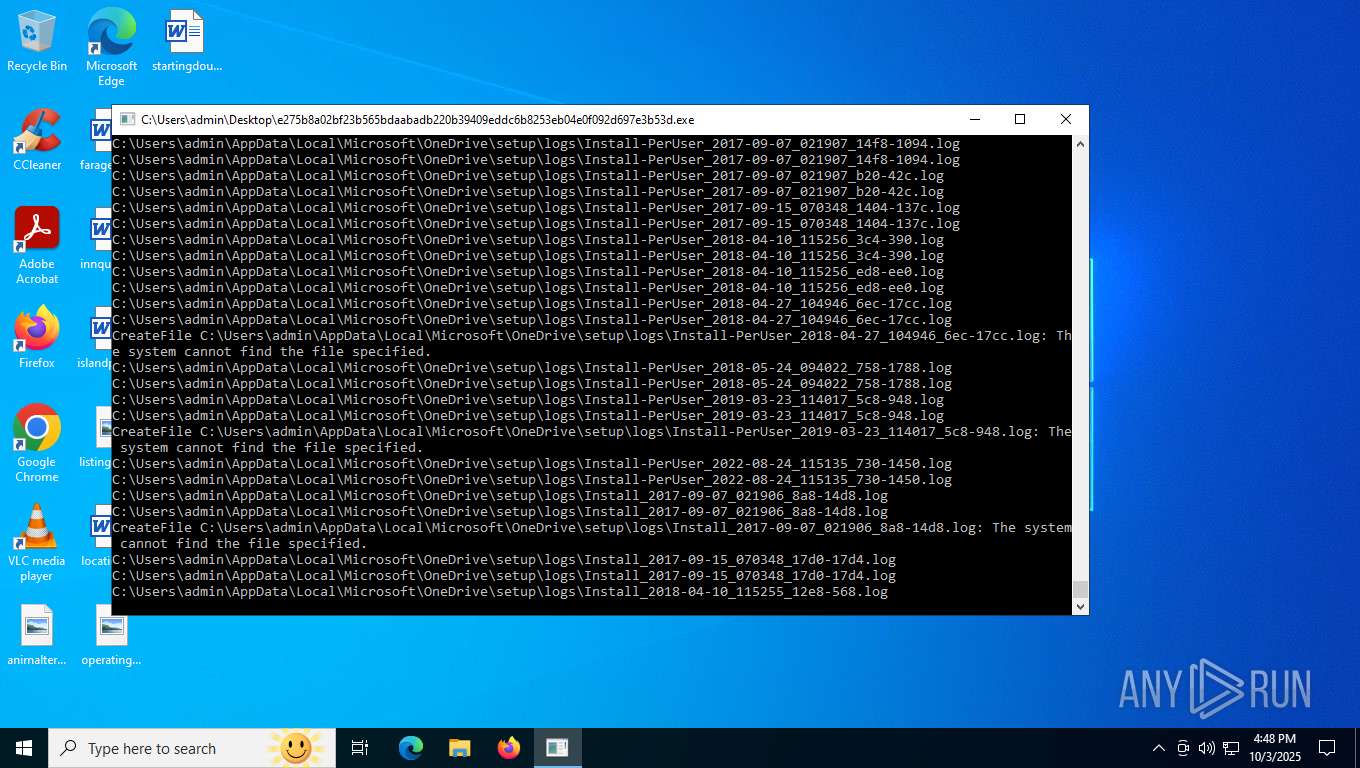
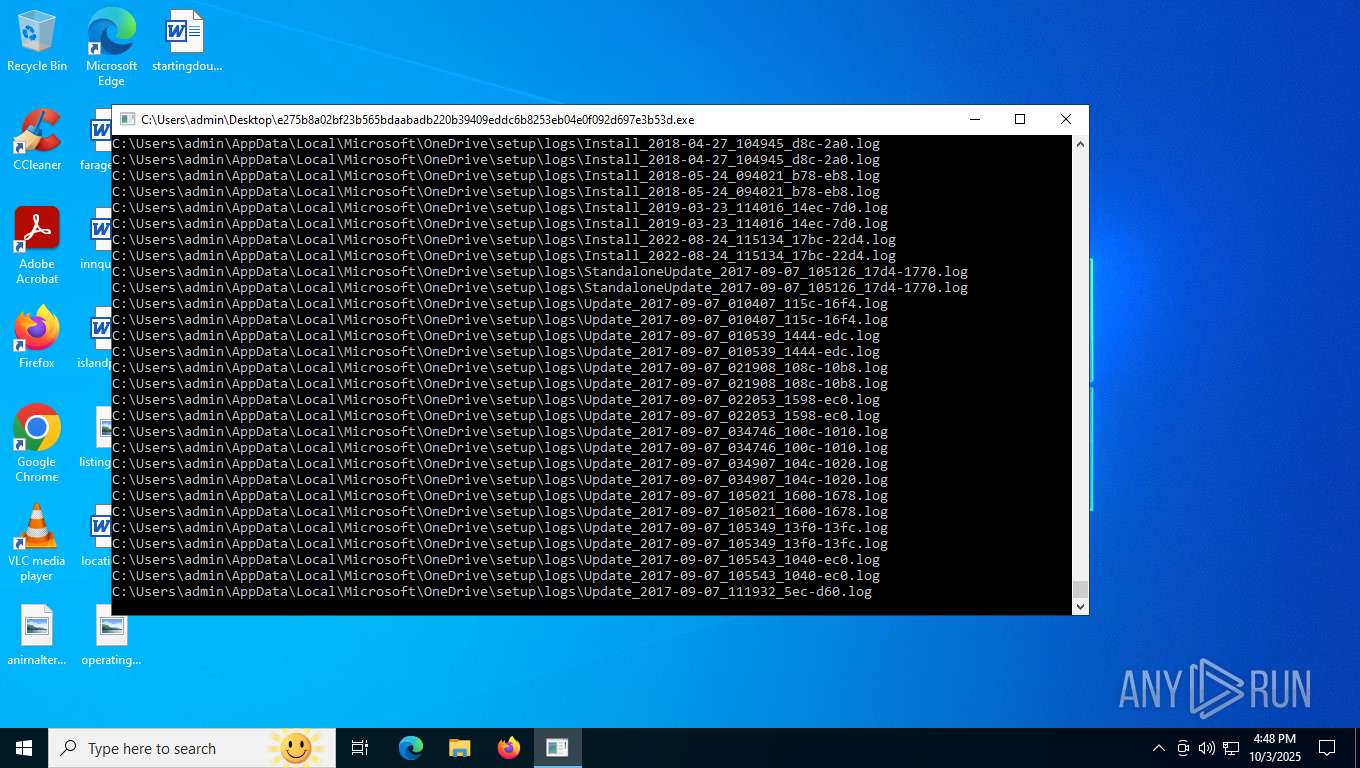
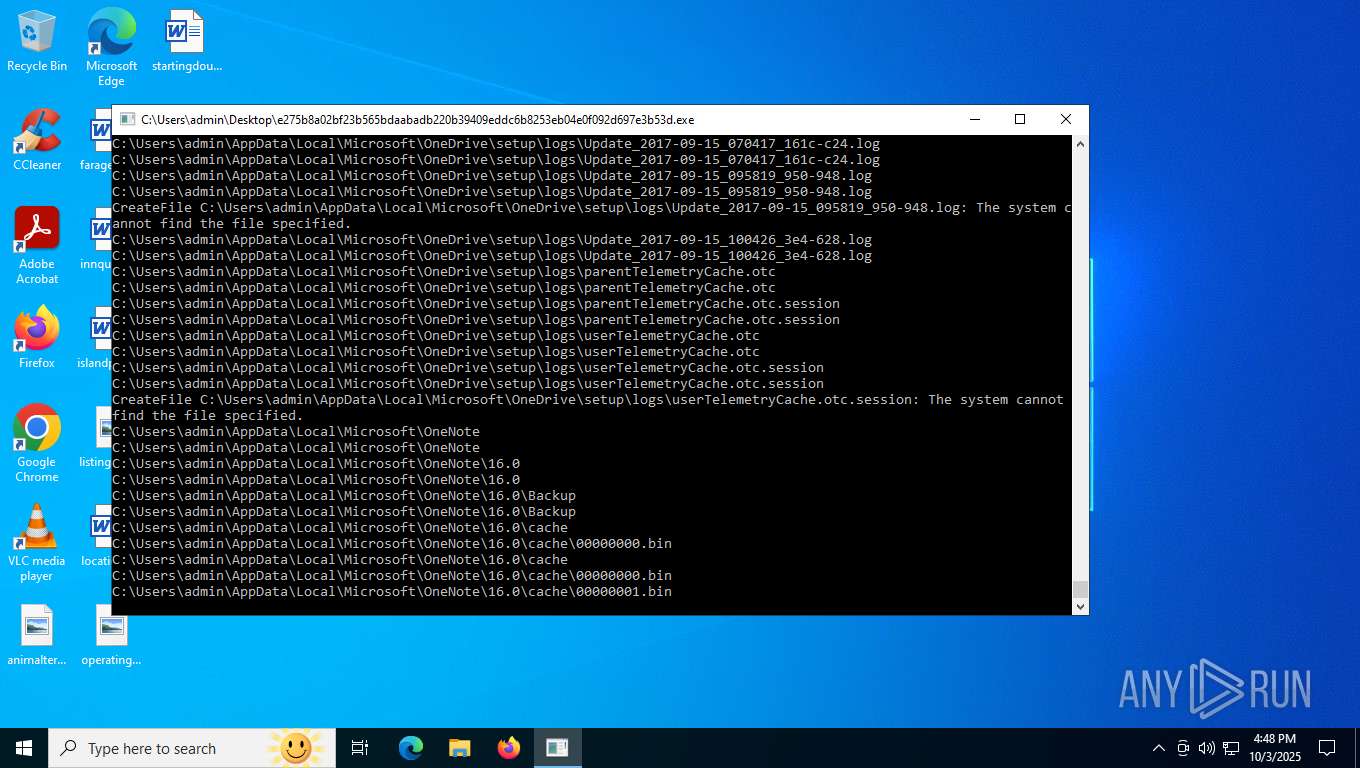
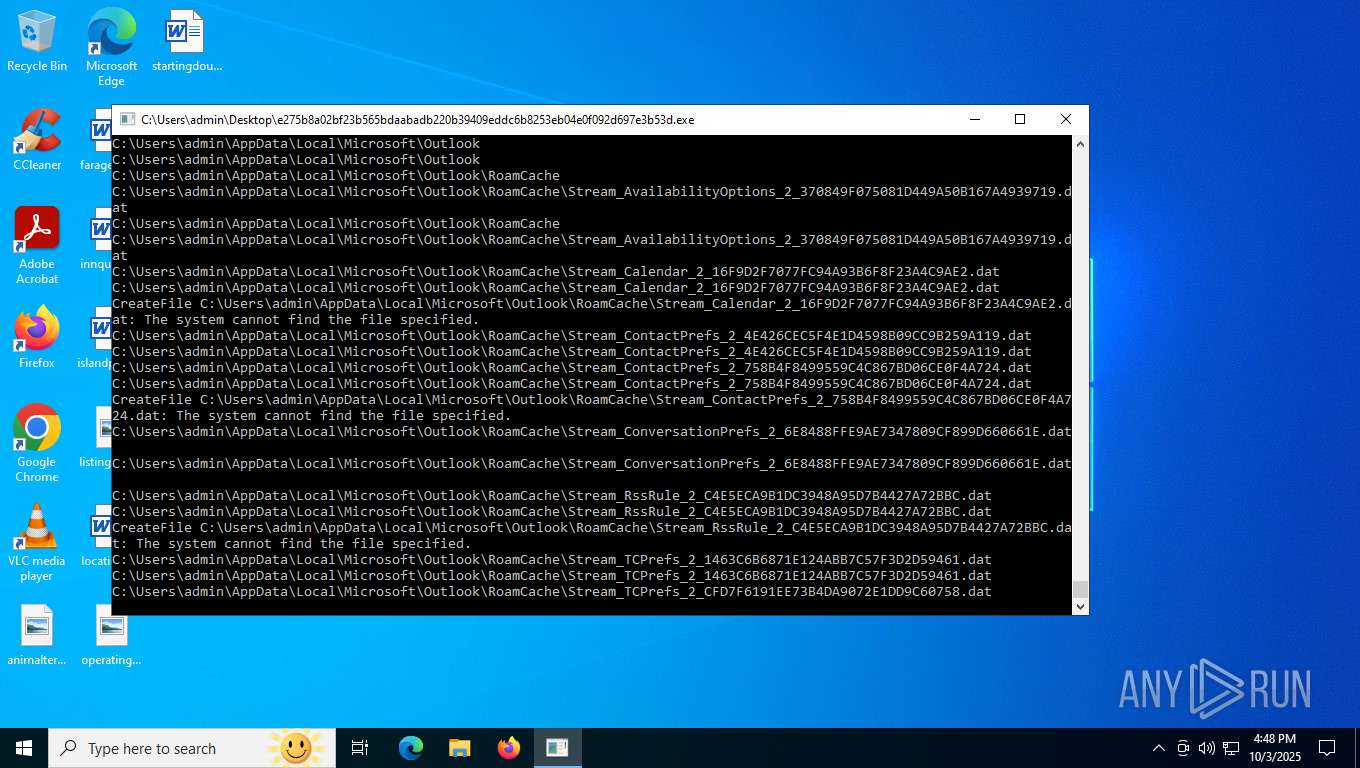
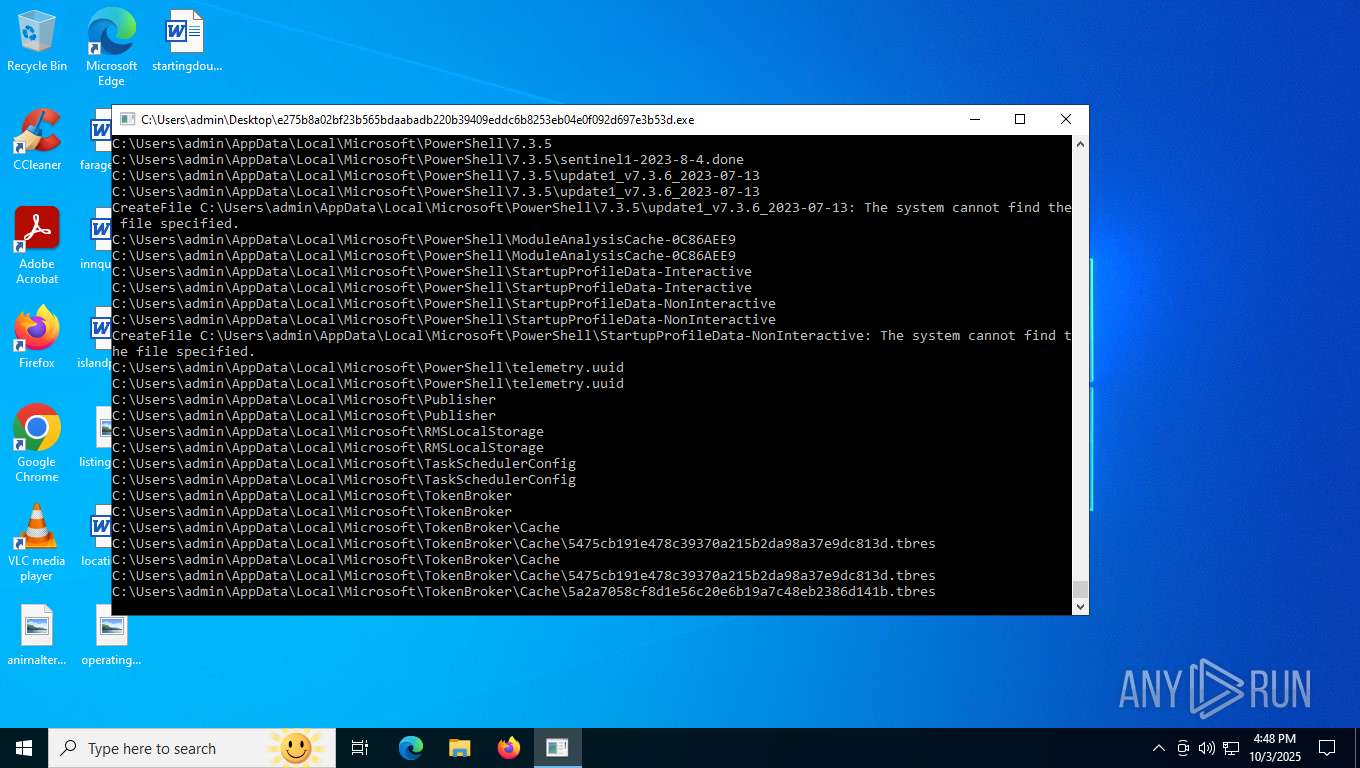
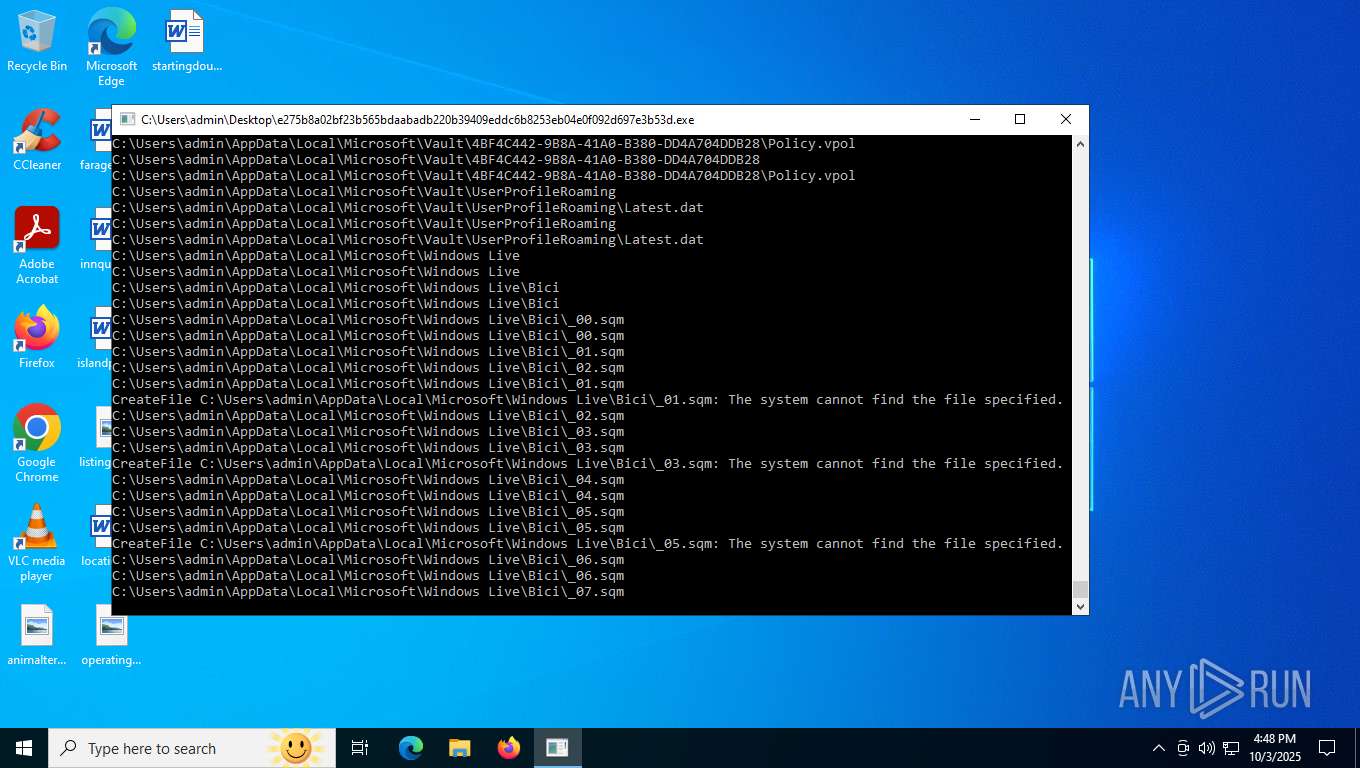
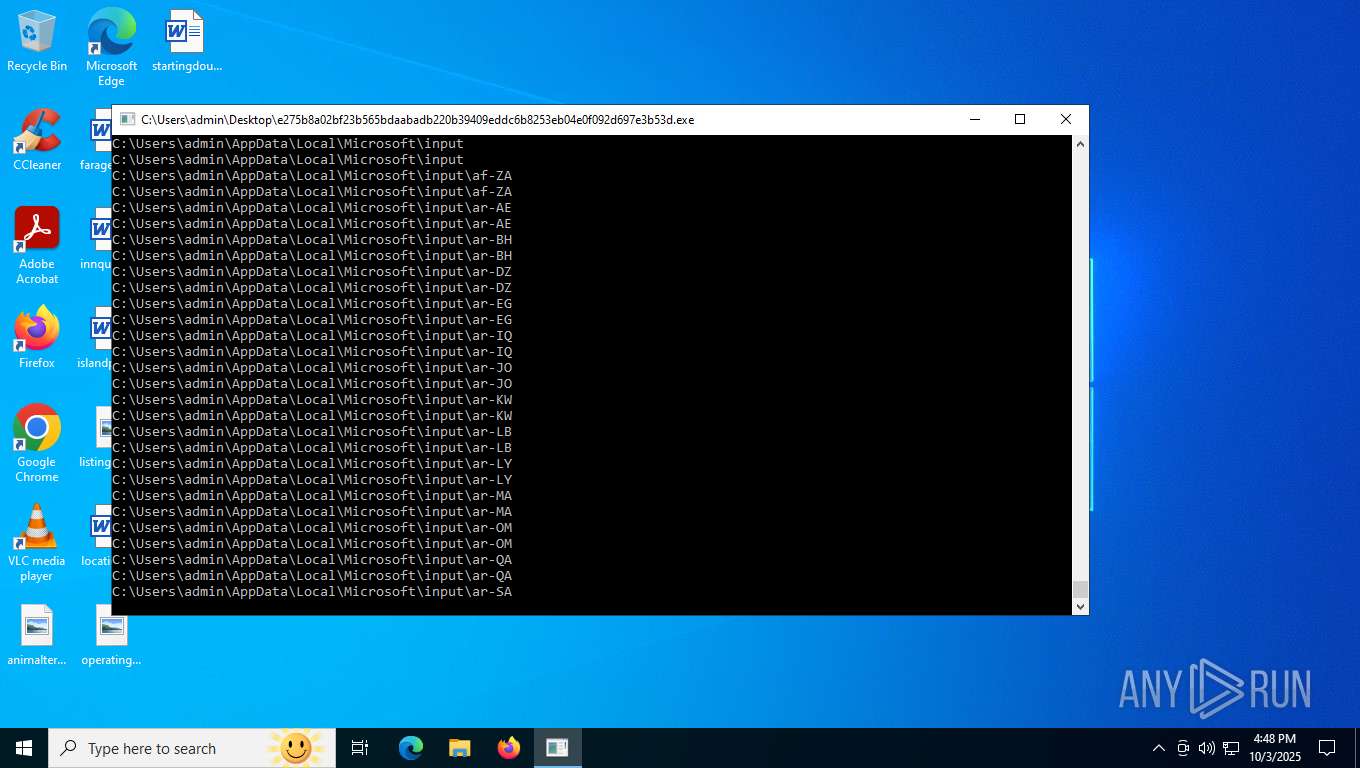
| 3124 | "C:\Users\admin\Desktop\e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe" | C:\Users\admin\Desktop\e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
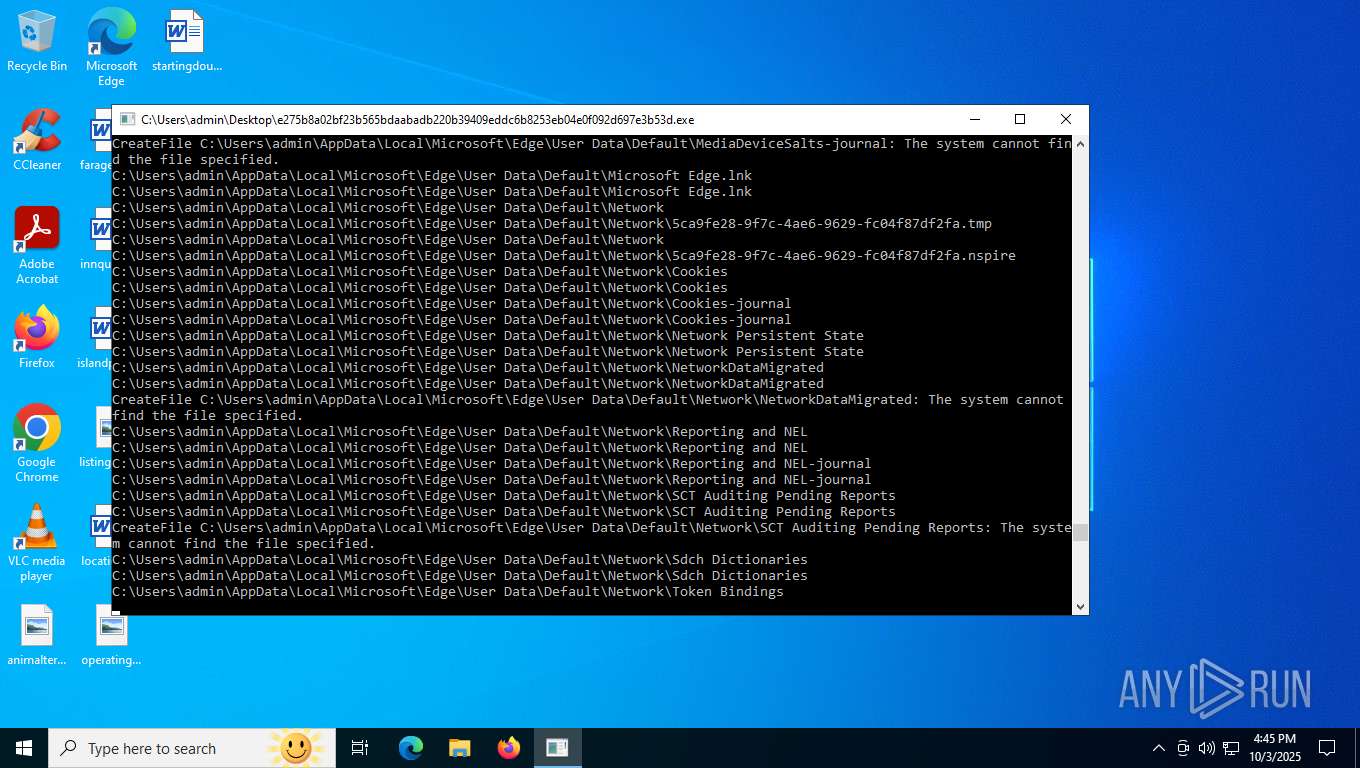
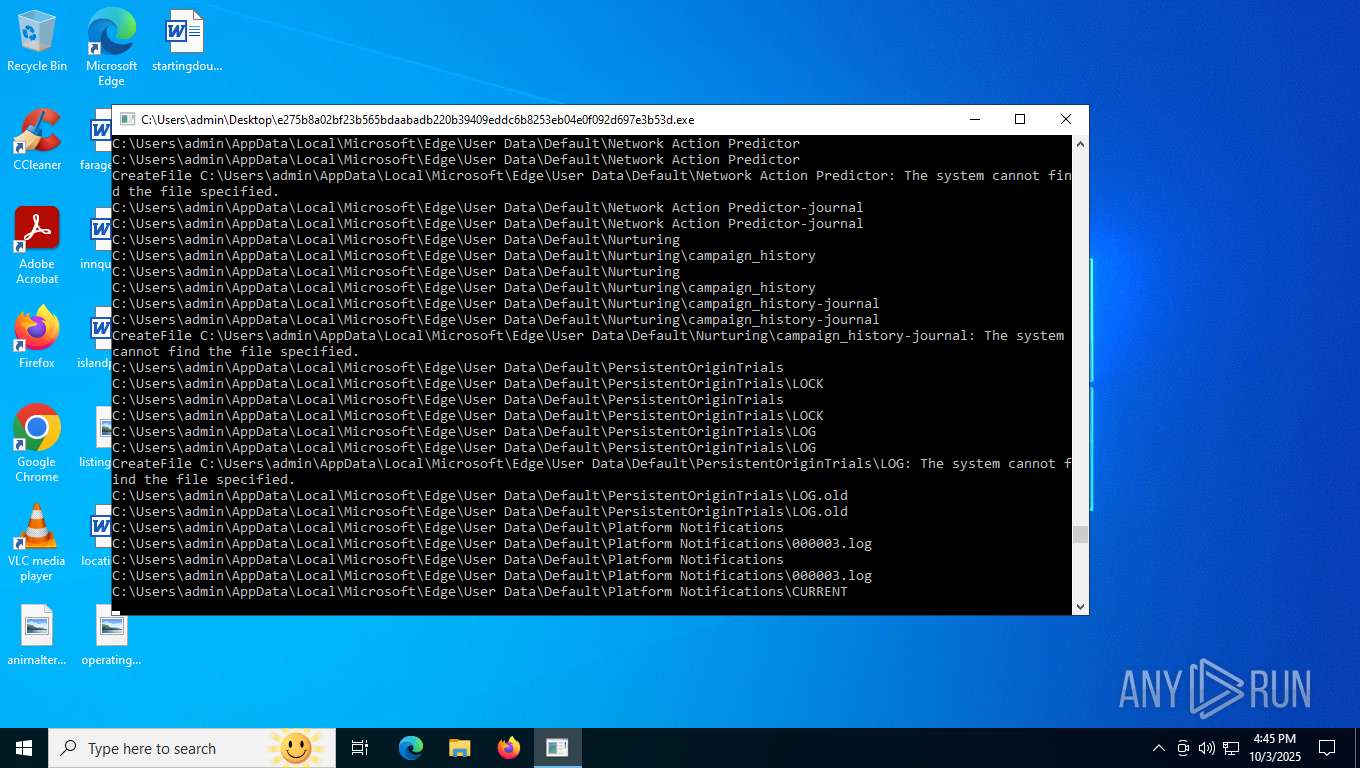
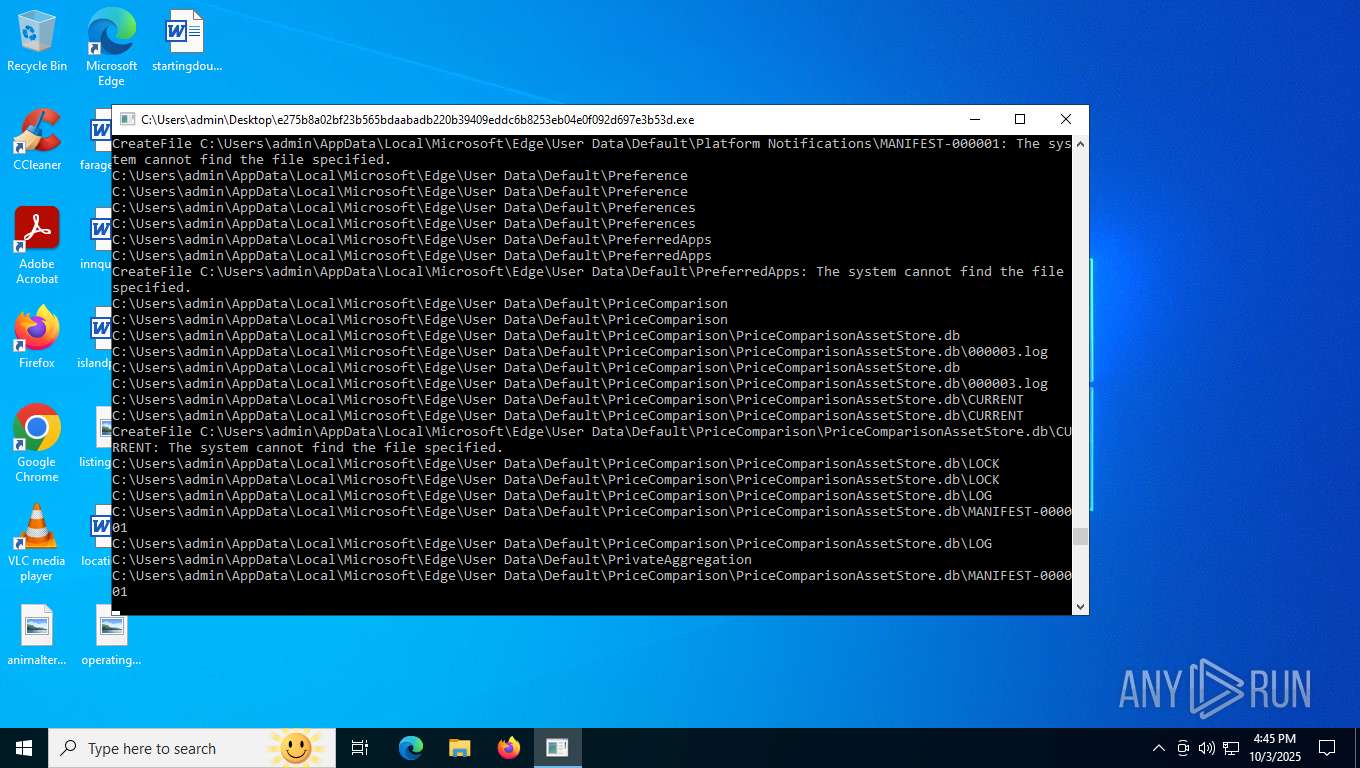
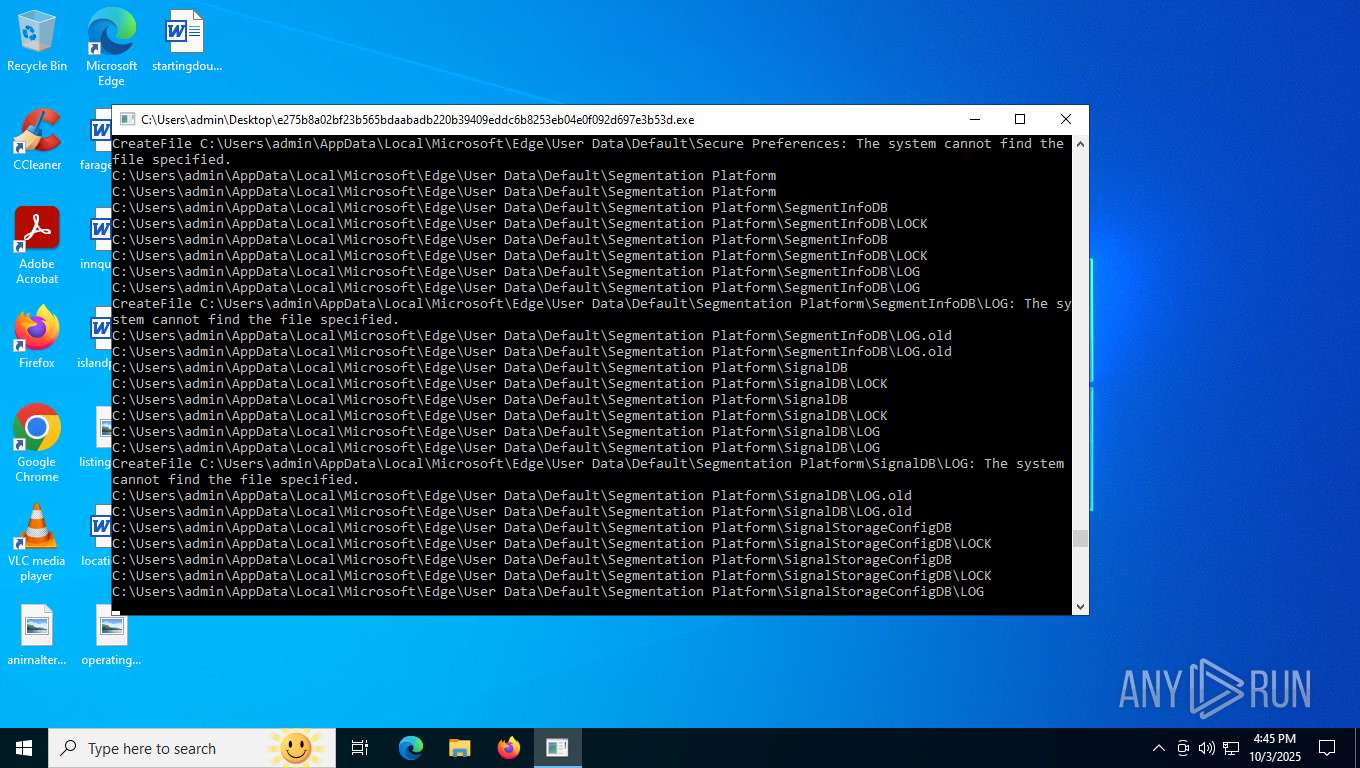
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\Adobe\ARM\Acrobat_23.001.20093\AcroRdrDCx64Upd2300820470_MUI.msp | — | |
MD5:— | SHA256:— | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\Adobe\ARM\Acrobat_23.001.20093\AcroRdrDCx64Upd2300820470_MUI.nspire | — | |
MD5:— | SHA256:— | |||
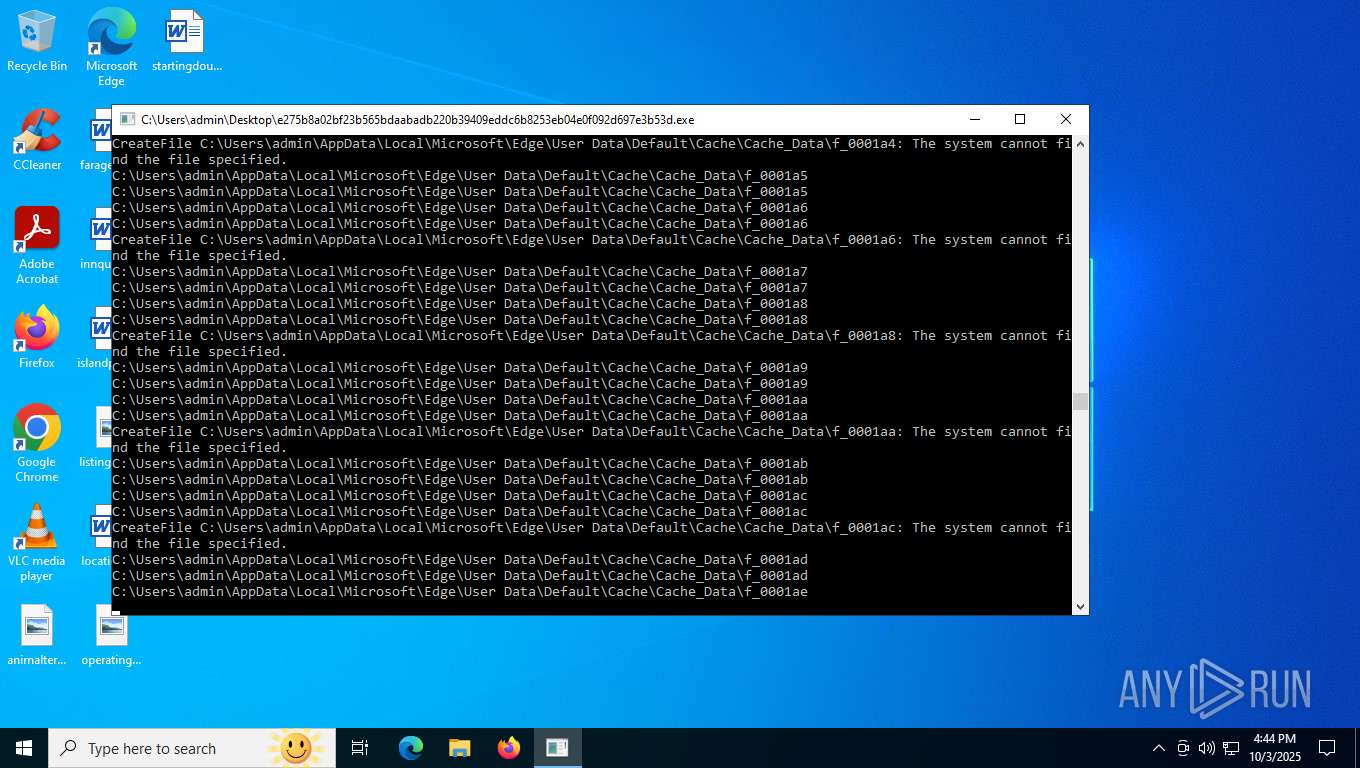
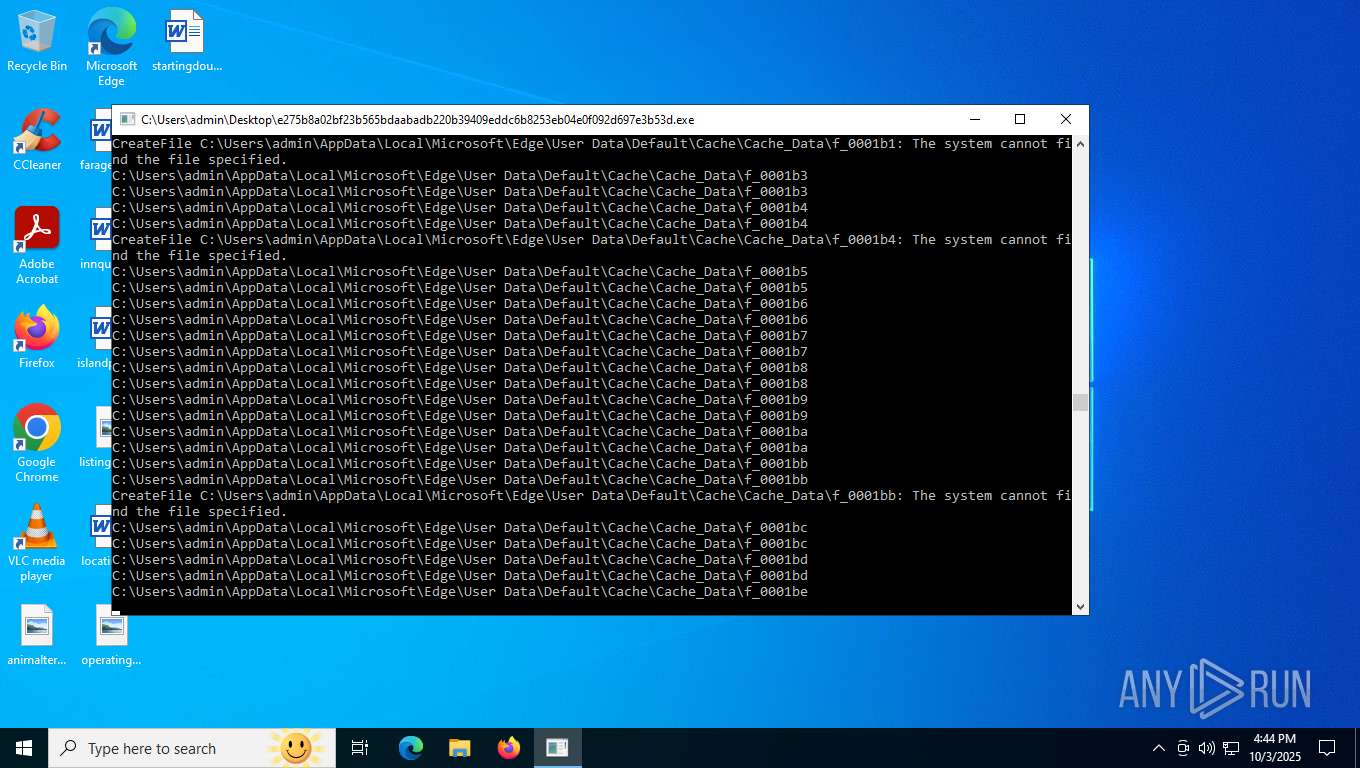
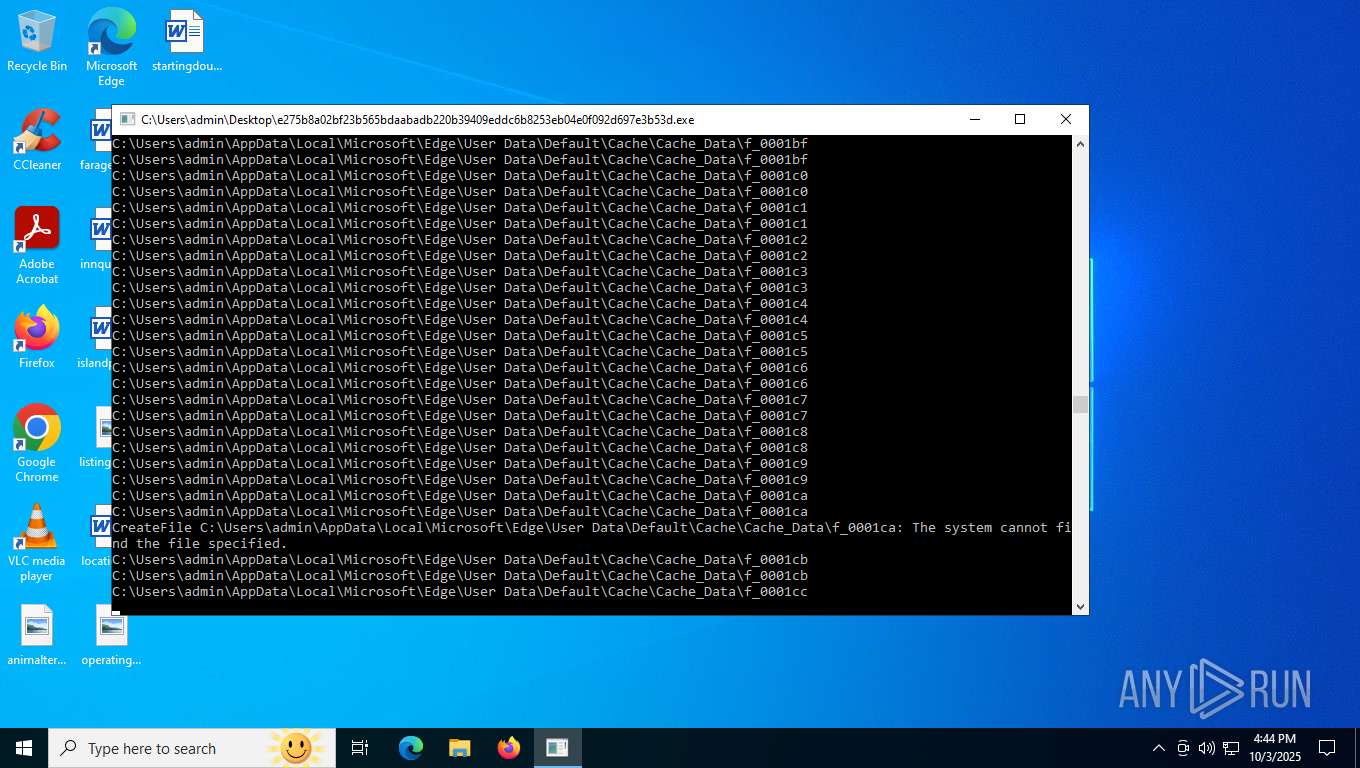
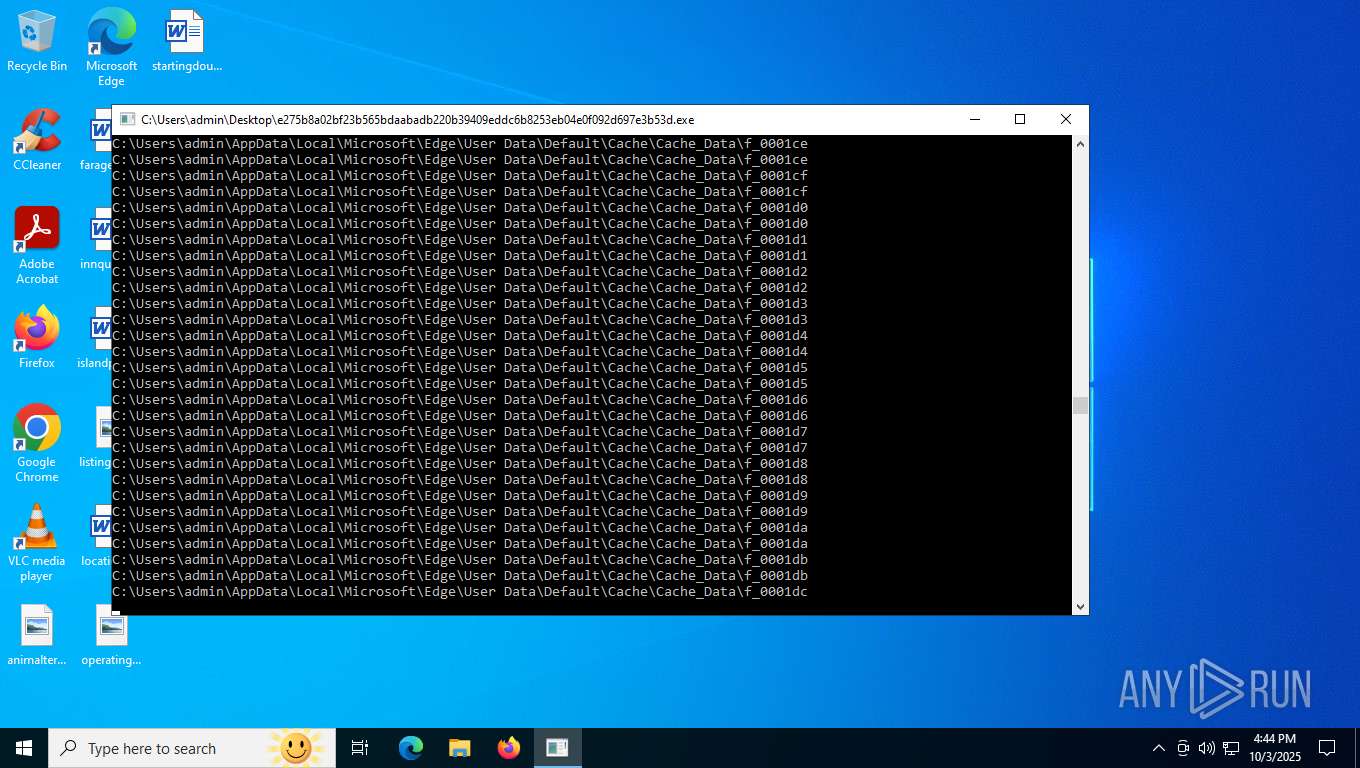
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\Adobe\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\Users\Default\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\Adobe\ARM\Acrobat_23.001.20093\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\Users\Default\AppData\Local\Microsoft\InputPersonalization\TrainedDataStore\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\Users\Default\AppData\Roaming\Microsoft\Internet Explorer\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\ProgramData\Adobe\ARM\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
| 3124 | e275b8a02bf23b565bdaabadb220b39409eddc6b8253eb04e0f092d697e3b53d.exe | C:\Users\Default\Desktop\readme.txt | text | |
MD5:6FEC36FE7E91B6B1989AFA83C1956B11 | SHA256:4D069964C7DF5E4D274D6E9281926A8BAFA28450CE54DFCDA76BDD61A32FF468 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3040 | backgroundTaskHost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
4696 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
6180 | svchost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
6180 | svchost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
7916 | backgroundTaskHost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
6016 | MoUsoCoreWorker.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
7276 | RUXIMICS.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5948 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 92.123.104.33:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
6180 | svchost.exe | 20.190.159.68:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6180 | svchost.exe | 184.30.131.245:80 | ocsp.digicert.com | AKAMAI-AS | US | whitelisted |
3040 | backgroundTaskHost.exe | 92.123.104.33:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
arc.msn.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
fd.api.iris.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |