ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
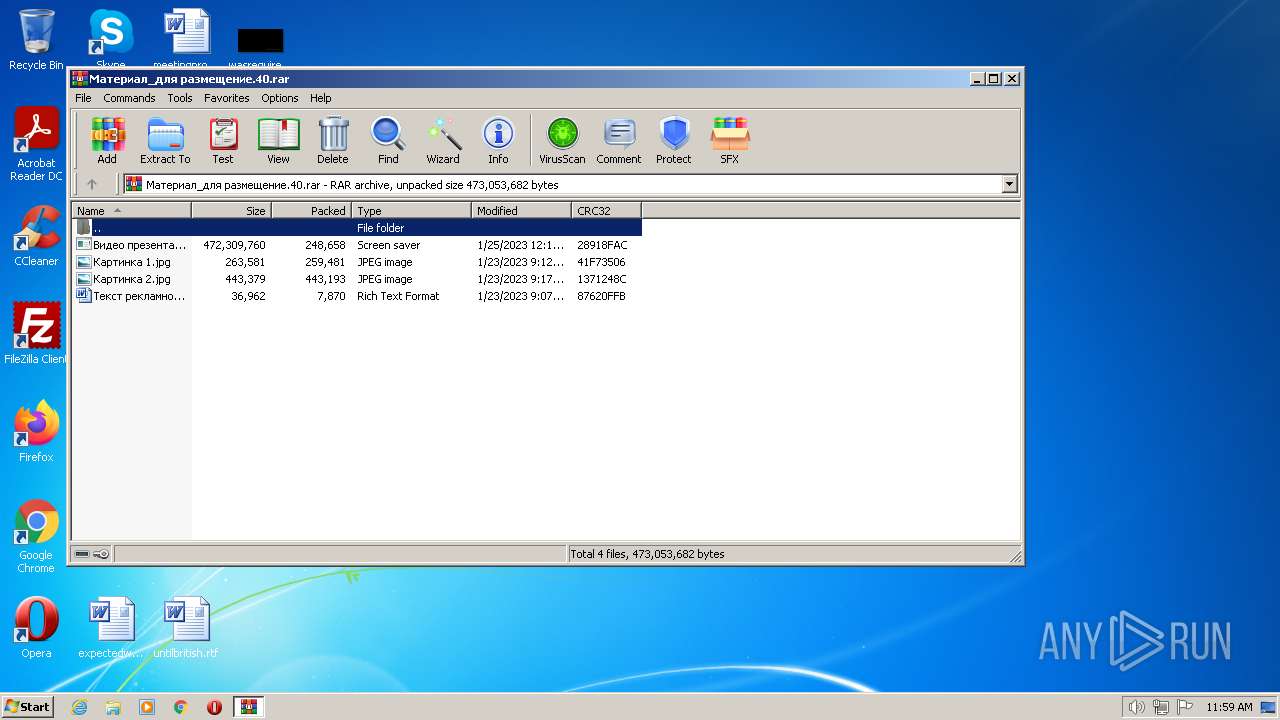
| File name: | Материал_для размещение.40.rar |
| Full analysis: | https://app.any.run/tasks/3053e664-0f70-4236-a937-a4d4d7fac58a |
| Verdict: | Malicious activity |
| Threats: | Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links. |
| Analysis date: | January 26, 2023, 11:59:48 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-rar |
| File info: | RAR archive data, v5 |
| MD5: | 7A47A7F42A3E21C5A1DDA911B2DF0DF5 |
| SHA1: | C11F956D0459E3F27BA14D854482055372C99A1F |
| SHA256: | E1F3C6CD1BD194A15B5441691F7C61B4690B47BB72105AB002CF381C000938DE |
| SSDEEP: | 24576:hZICmP/xhOCumi8otzdF7tToPoqBimBgg2mnz2KmX6:y7iN5Zqrgg1qKmX6 |
| .rar | | | RAR compressed archive (v5.0) (61.5) |
|---|---|---|
| .rar | | | RAR compressed archive (gen) (38.4) |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 2436 | "C:\Program Files\WinRAR\WinRAR.exe" "C:\Users\admin\AppData\Local\Temp\Материал_для размещение.40.rar" | C:\Program Files\WinRAR\WinRAR.exe | — | Explorer.EXE | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.91.0 Modules
| |||||||||||||||
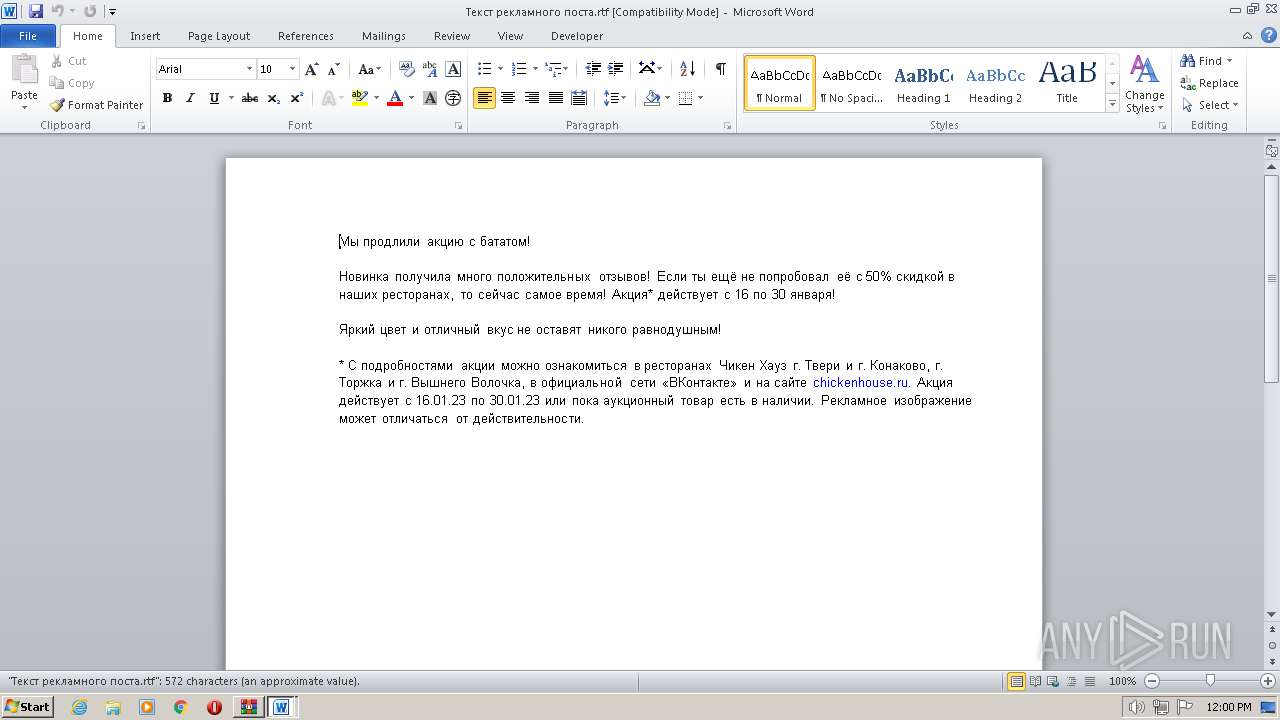
| 3064 | "C:\Program Files\Microsoft Office\Office14\WINWORD.EXE" /n "C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43222\Текст рекламного поста.rtf" | C:\Program Files\Microsoft Office\Office14\WINWORD.EXE | — | WinRAR.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Word Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 3148 | "C:\Program Files\Microsoft Office\Office14\WINWORD.EXE" /n "C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43175\Текст рекламного поста.rtf" | C:\Program Files\Microsoft Office\Office14\WINWORD.EXE | — | WinRAR.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Word Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 3616 | "C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.40830\Видео презентация.40.scr" /S | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.40830\Видео презентация.40.scr | WinRAR.exe | ||||||||||||
User: admin Company: AVG Technologies Integrity Level: MEDIUM Description: AVG Self-Extract Package Exit code: 0 Version: 21.3.3208.0 Modules
RedLine(PID) Process(3616) Видео презентация.40.scr C2 (1)79.137.207.219:12330 Botnet37 Err_msg Auth_valuea7d69e5e9267a898caee9be204b585c5 US (135) Environment System.Text Cryptography Generic FileInfo Linq UNKNOWN cFileStreamredFileStreamit_cFileStreamardFileStreams FileStream \ Host Port : User Pass IList<> GetDirectories Entity12 EnumerateDirectories String.Replace String.Remove net.tcp:// / localhost a7d69e5e9267a898caee9be204b585c5 Authorization ns1 HRsIByQnOWAtCTsePQ1nGC4mAkU5BygZPxMySQ== HhsATw== Sacrist Id3 EnumerateFiles ExpandEnvironmentVariables Id2 Id1 FullName Replace Directory wa l et d a t . *wallet* _ T e gr am ex \TeEnvironmentlegraEnvironmentm DEnvironmentesktoEnvironmentp\tdEnvironmentata \Discord\Local Storage\leveldb *.loSystem.Collections.Genericg System.Collections.Generic 1 String MyG string.Replace %USERPFile.WriteROFILE%\AppFile.WriteData\RoamiFile.Writeng File.Write Handler npvo* %USERPserviceInterface.ExtensionROFILE%\ApserviceInterface.ExtensionpData\LocaserviceInterface.Extensionl serviceInterface.Extension ProldCharotonVoldCharPN oldChar nSystem.CollectionspvoSystem.Collections* System.Collections Microsoft\Windоws - AddRange % ( UNIQUE " FileStream.IO string.Empty uint UnmanagedType hKey pszProperty Encoding bMasterKey {0} | https://api.ip.sb/ip SELSystem.Windows.FormsECT * FRSystem.Windows.FormsOM WinSystem.Windows.Forms32_ProcSystem.Windows.Formsessor System.Windows.Forms roSystem.Linqot\CISystem.LinqMV2 System.Linq SELSystem.LinqECT * FRSystem.LinqOM WinSystem.Linq32_VideoCoSystem.Linqntroller AdapterRAM Name SOFTWARE\WOW6432Node\Clients\StartMenuInternet SOFTWARE\Clients\StartMenuInternet shell\open\command Unknown Version SELESystem.ManagementCT * FRSystem.ManagementOM WiSystem.Managementn32_DisSystem.ManagementkDrivSystem.Managemente System.Management SerialNumber SELSystem.Text.RegularExpressionsECT * FRSystem.Text.RegularExpressionsOM Win32_PSystem.Text.RegularExpressionsrocess WSystem.Text.RegularExpressionshere SessSystem.Text.RegularExpressionsionId=' System.Text.RegularExpressions ' FileSystem SSystem.ELECT * FRSystem.OM WiSystem.n32_ProcSystem.ess WherSystem.e SessiSystem.onId=' System. ExecutablePath [ ] Concat0 MConcatb oConcatr Concat0 Concat SELEMemoryCT * FMemoryROM WiMemoryn32_OperMemoryatingSMemoryystem Memory {0}{1}{2} x32 x64 x86 SOFTWARE\Microsoft\Windows NT\CurrentVersion ProductName CSDVersion Unknown _[ Network\ 80 81 0.0.0.0 | |||||||||||||||
| 3816 | "C:\Windows\Microsoft.NET\Framework\v4.0.30319\vbc.exe" | C:\Windows\Microsoft.NET\Framework\v4.0.30319\vbc.exe | Видео презентация.40.scr | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Visual Basic Command Line Compiler Exit code: 0 Version: 12.0.51209.34209 Modules
| |||||||||||||||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\16D\52C64B7E |
| Operation: | write | Name: | LanguageList |
Value: en-US | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\virtio_ivshmem_master_build.zip | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\Win7-KB3191566-x86.zip | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\Материал_для размещение.40.rar | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (2436) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2436 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.40830\Видео презентация.40.scr | — | |
MD5:— | SHA256:— | |||
| 3148 | WINWORD.EXE | C:\Users\admin\AppData\Local\Temp\CVRC592.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 3064 | WINWORD.EXE | C:\Users\admin\AppData\Local\Temp\CVRC6EA.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 3148 | WINWORD.EXE | C:\Users\admin\AppData\Roaming\Microsoft\Templates\~$Normal.dotm | pgc | |
MD5:1646108EA4DF6F25C328443AB72C513B | SHA256:B6D1B3C1C4D4FAFEF48A35A08D50AB9A7383F7CEF336DEA74640D2C675829365 | |||
| 2436 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43222\Текст рекламного поста.rtf | text | |
MD5:AD32EEF2BAA38862C95D0FCBBE8E2FCB | SHA256:8CDA2A82C3FA51AD3A63F520788E26D26CB796D5F802A9EF5D2665170035744B | |||
| 2436 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43175\Текст рекламного поста.rtf | text | |
MD5:AD32EEF2BAA38862C95D0FCBBE8E2FCB | SHA256:8CDA2A82C3FA51AD3A63F520788E26D26CB796D5F802A9EF5D2665170035744B | |||
| 3148 | WINWORD.EXE | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43222\~$кст рекламного поста.rtf | pgc | |
MD5:0D06288B865AB62FBEF39B5CC7A0B885 | SHA256:10DC71E2CCC4ACB5F7CFDD1075230E8454AA7FC3CBB4D0732F3AEEDD6B913823 | |||
| 3148 | WINWORD.EXE | C:\Users\admin\AppData\Local\Temp\Rar$DIa2436.43175\~$кст рекламного поста.rtf | pgc | |
MD5:3B47C566041DBEA9DED30EACB41CAEA2 | SHA256:69DF5778A7B8EAC87F0DEB221AE2EEFB6206791235457395A5D1A60D8CDC9672 | |||
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
3816 | vbc.exe | 79.137.207.219:12330 | — | — | RU | malicious |