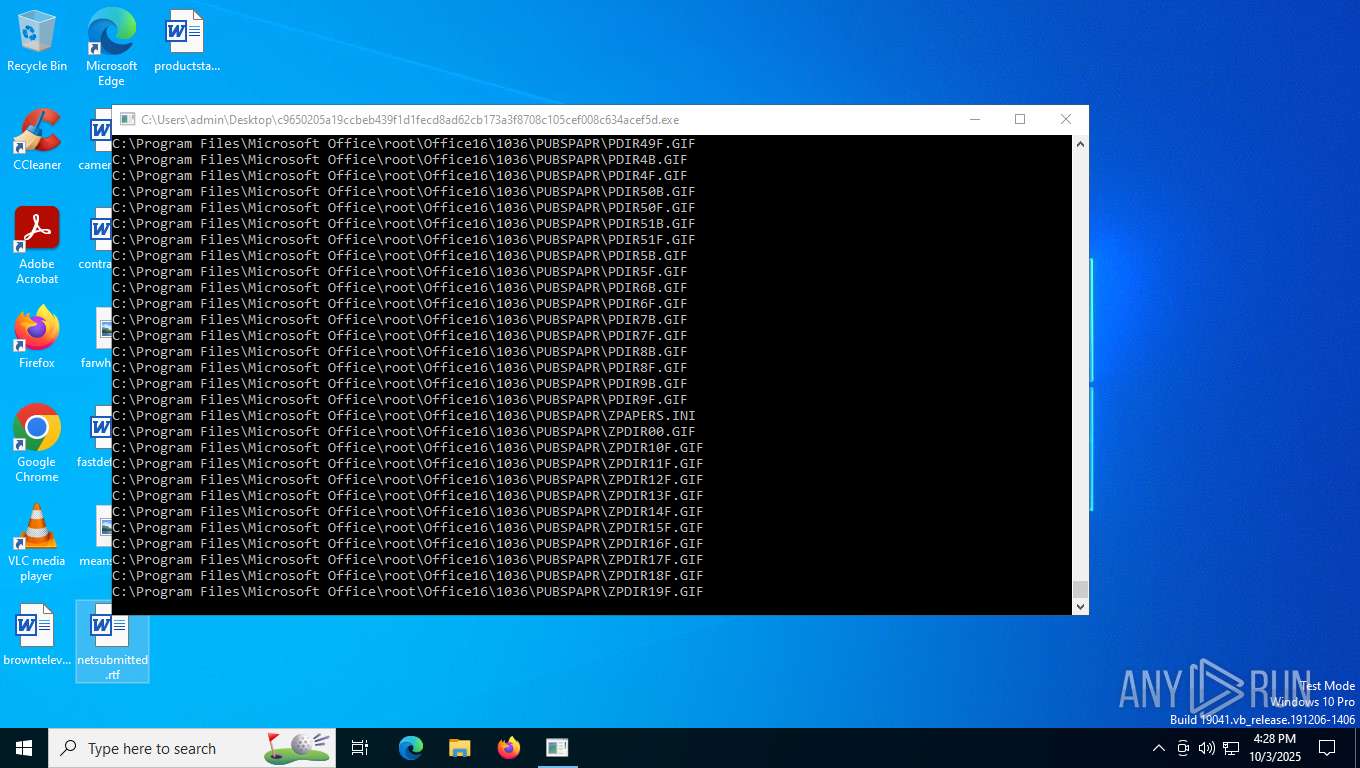
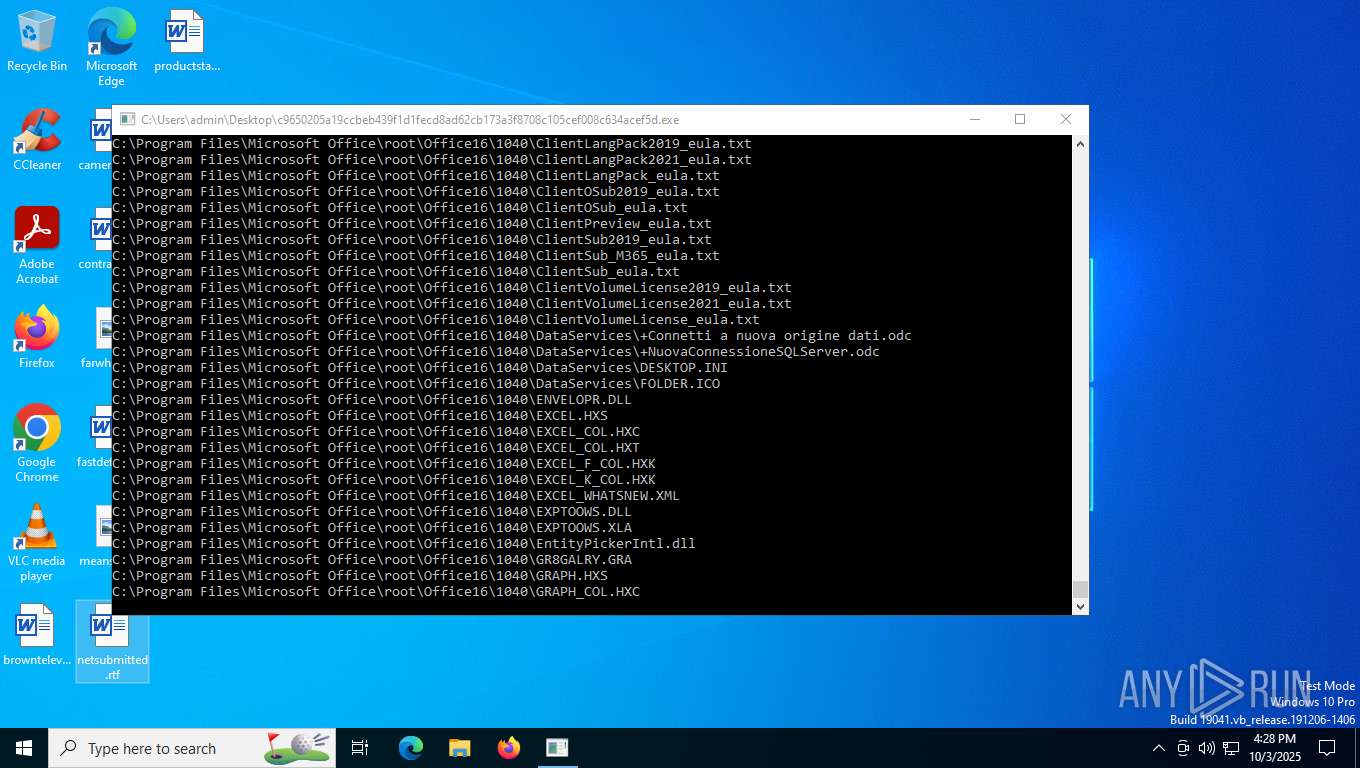
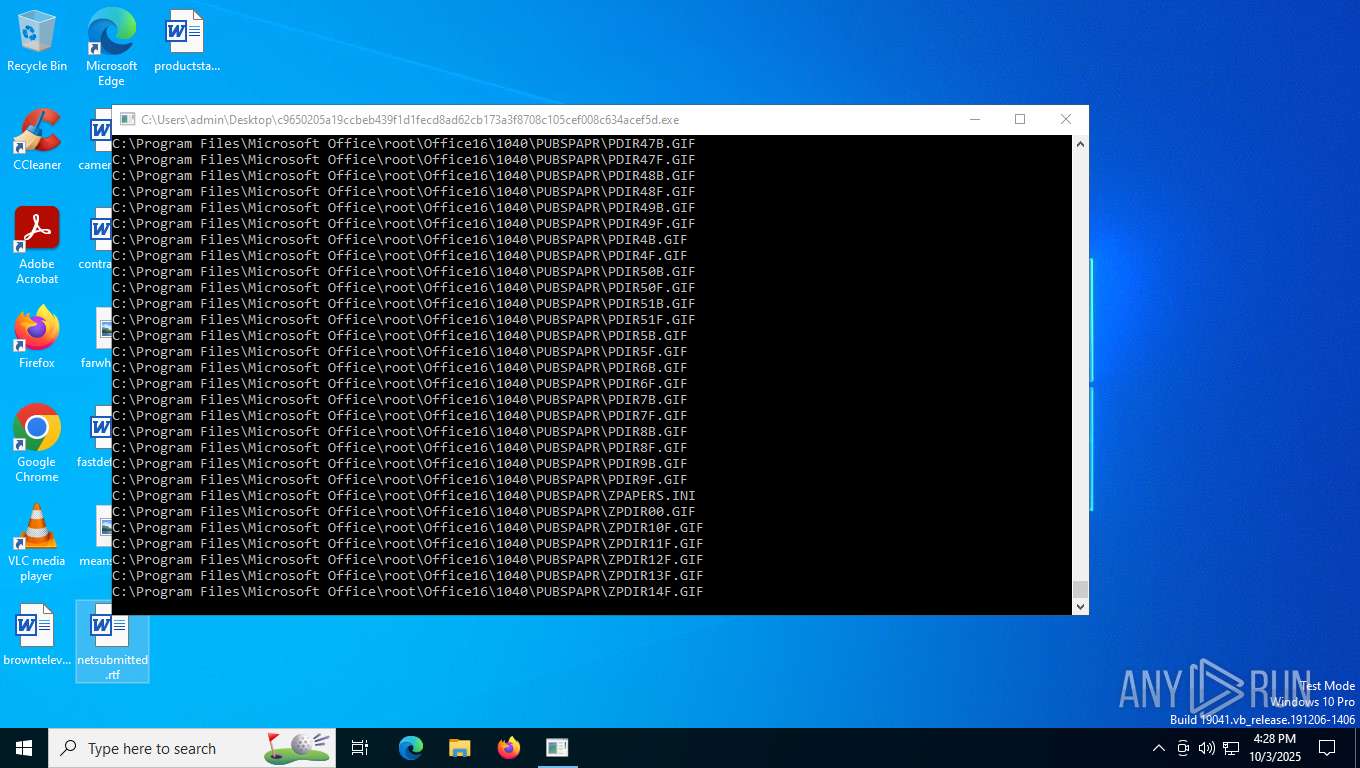
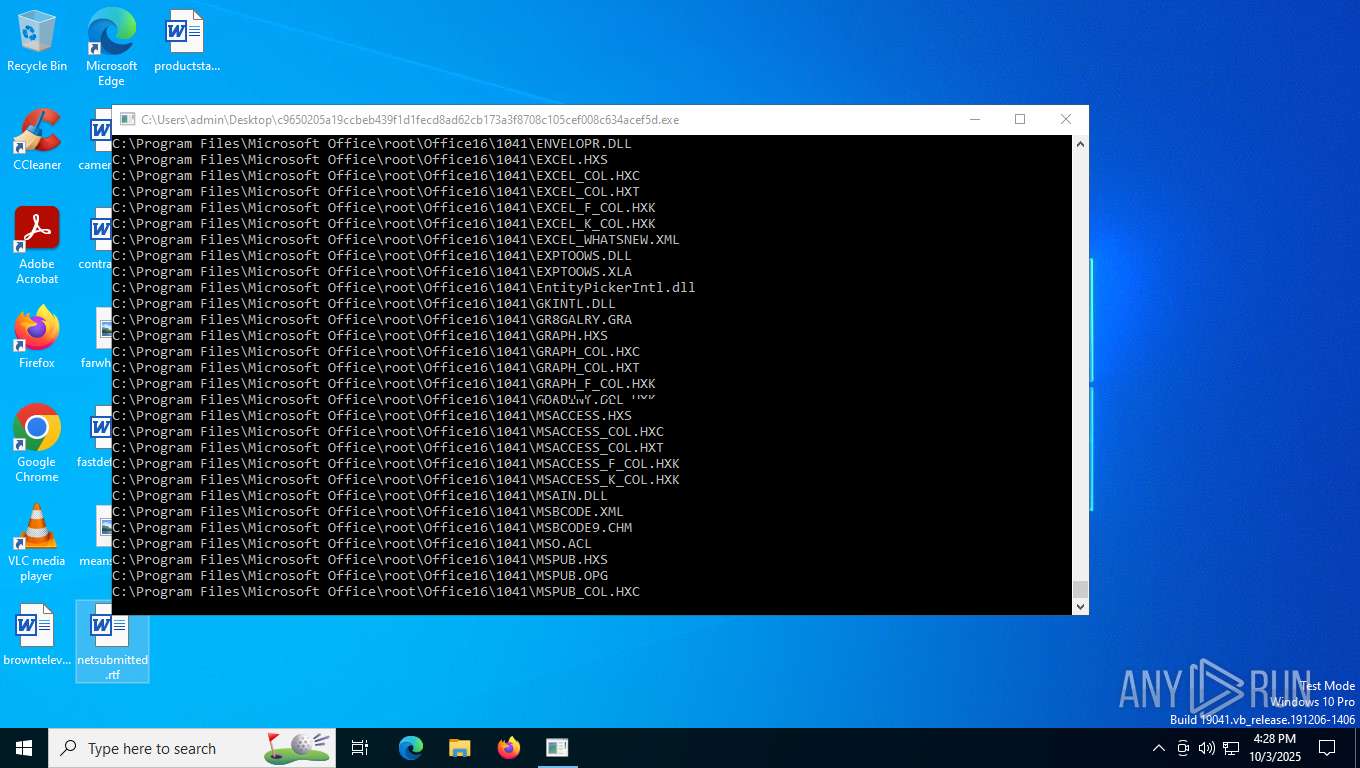
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe |
| Full analysis: | https://app.any.run/tasks/898bdf90-dde7-4c7f-a8de-cab4c10dc26b |
| Verdict: | Malicious activity |
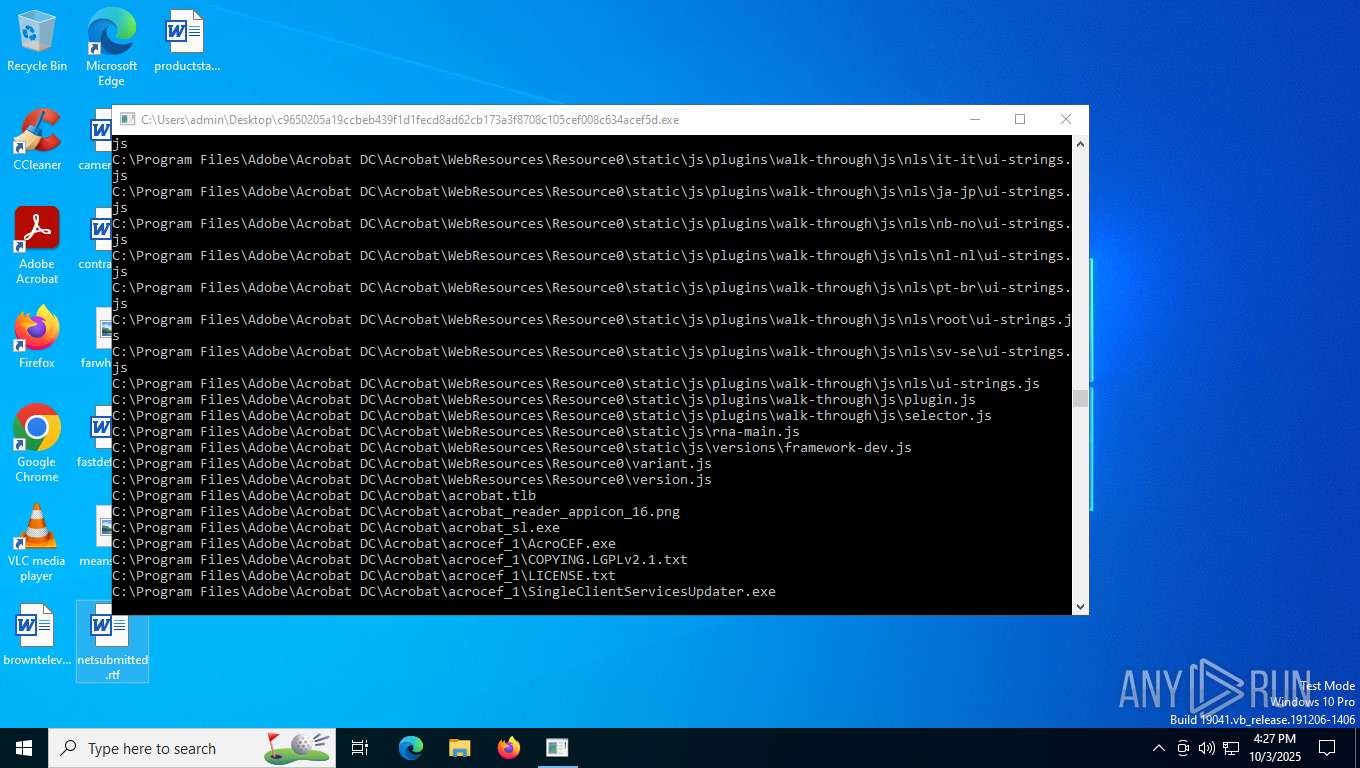
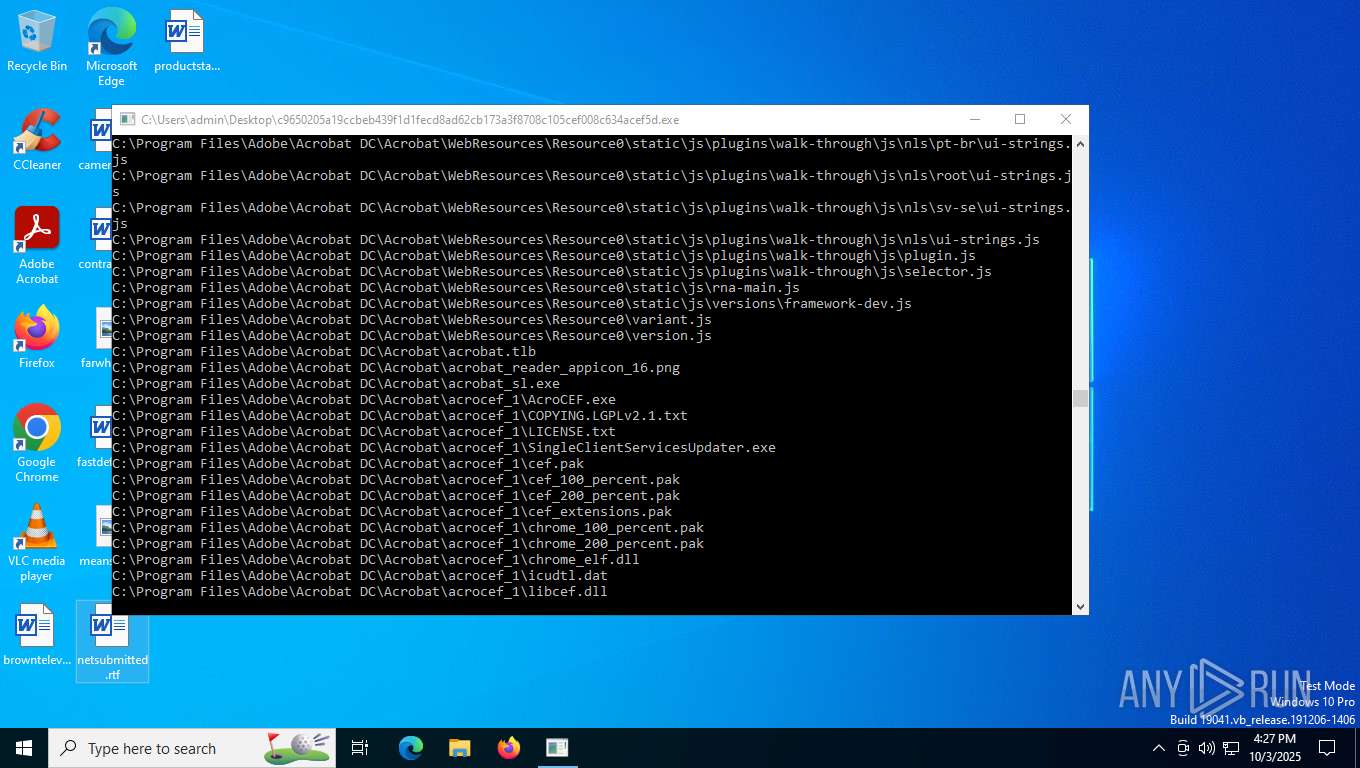
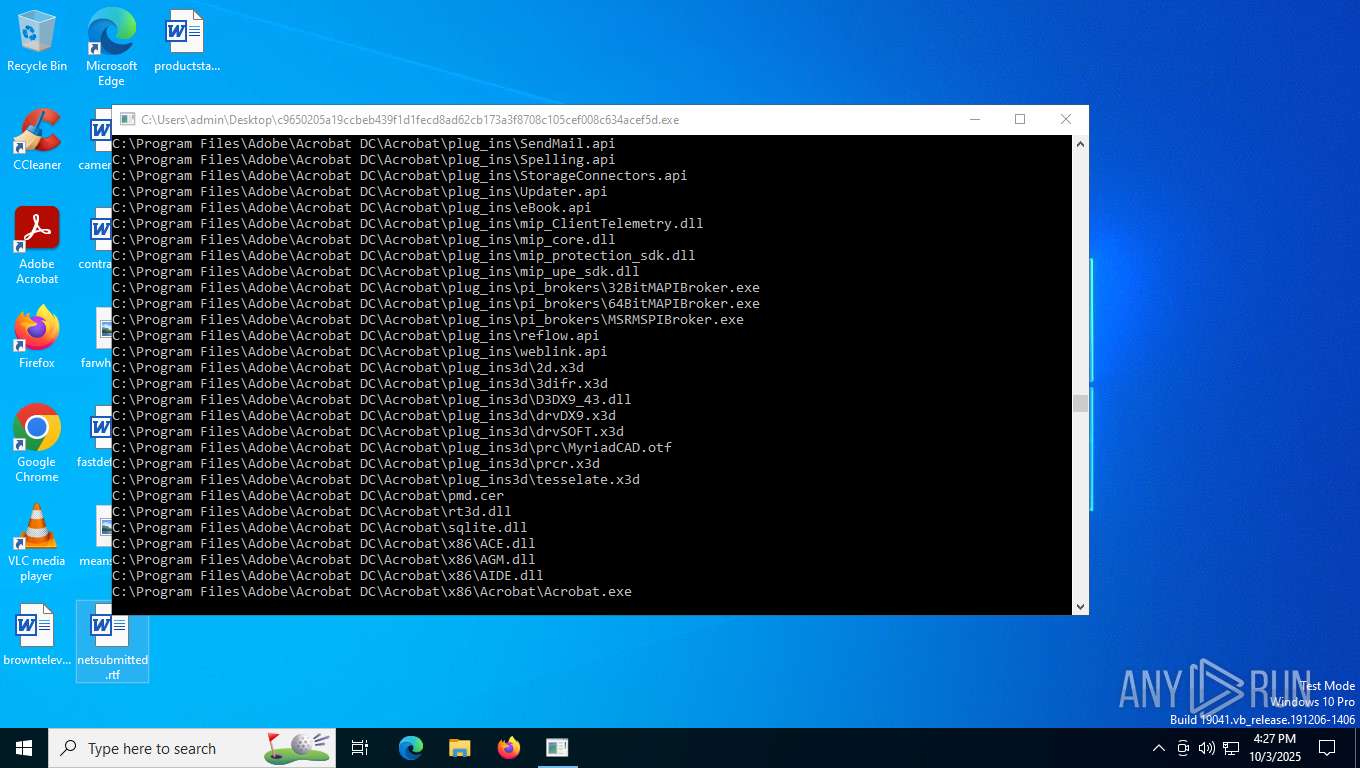
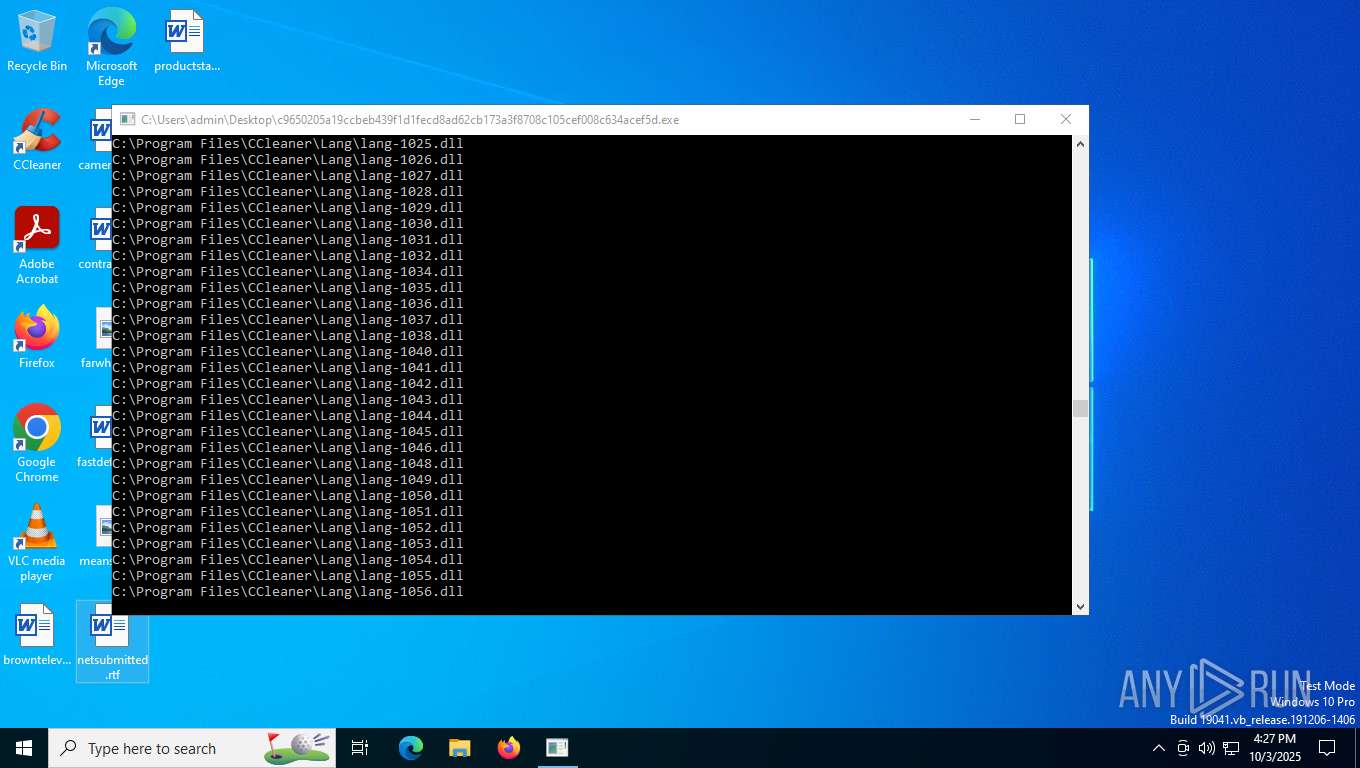
| Threats: | GravityRAT is a sophisticated spyware and remote access trojan that has been actively targeting organizations and government entities since 2016. It uses innovative anti-analysis techniques and made an evolution from a Windows-only threat to a cross-platform espionage tool capable of compromising Windows, Android, and macOS systems. |
| Analysis date: | October 03, 2025, 16:26:21 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (console) x86-64 (stripped to external PDB), for MS Windows, 5 sections |
| MD5: | D61B0C0981D23844D820A440A0FE7501 |
| SHA1: | B1D16B0E9AAC310552B0A69BBCAC04DE4EB02E93 |
| SHA256: | C9650205A19CCBEB439F1D1FECD8AD62CB173A3F8708C105CEF008C634ACEF5D |
| SSDEEP: | 98304:6AbDg6Mruq2aOhsFn9i1VO0B1St3Q9eGx28ivLwP+1GDeGx28ivLwP+1GveGx28d:NP1StZ3nsmoMm7Beqii |
| .exe | | | Win64 Executable (generic) (76.3) |
|---|---|---|
| .exe | | | Win32 Executable (generic) (12.4) |
| .exe | | | Generic Win/DOS Executable (5.5) |
| .exe | | | DOS Executable Generic (5.5) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 0000:00:00 00:00:00 |
| ImageFileCharacteristics: | No relocs, Executable, Large address aware, No debug |
| PEType: | PE32+ |
| LinkerVersion: | 3 |
| CodeSize: | 2279424 |
| InitializedDataSize: | 210432 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x58b20 |
| OSVersion: | 4 |
| ImageVersion: | 1 |
| SubsystemVersion: | 4 |
| Subsystem: | Windows command line |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 560 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
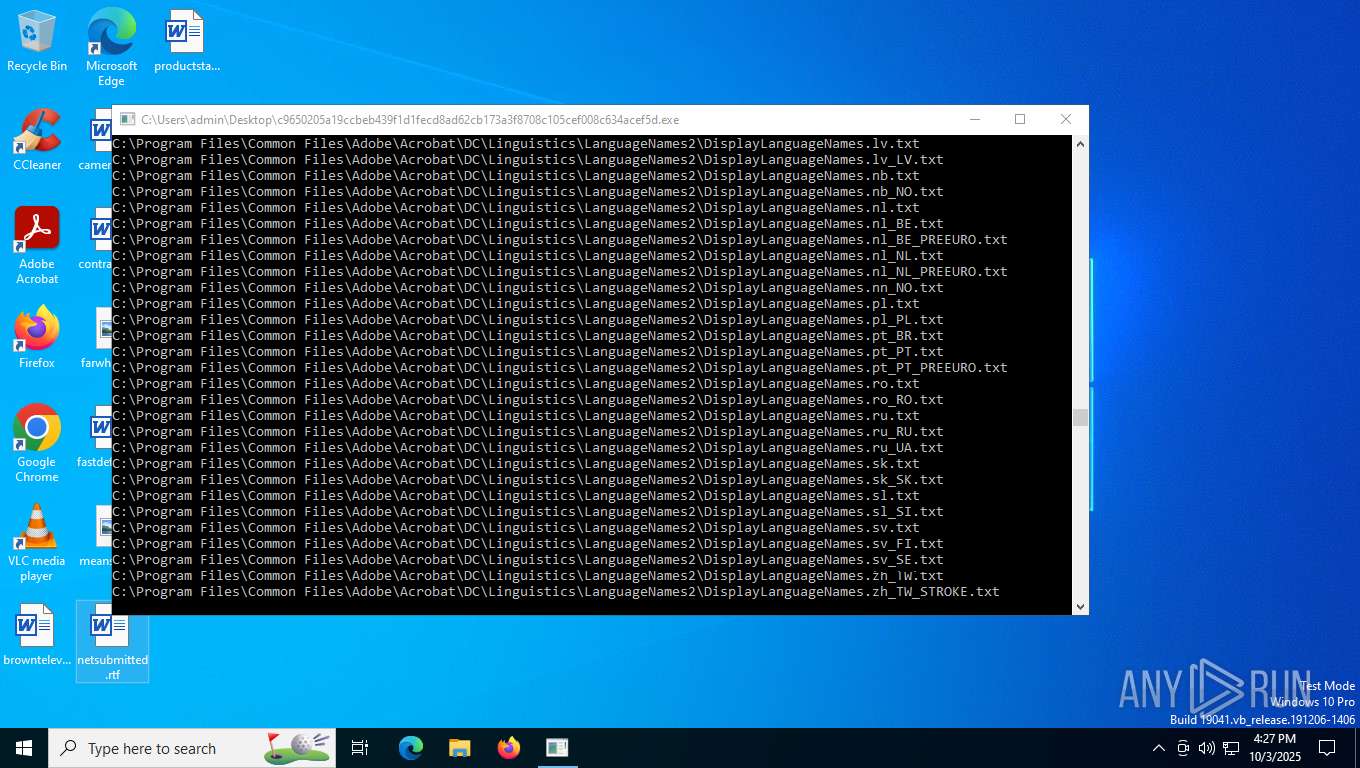
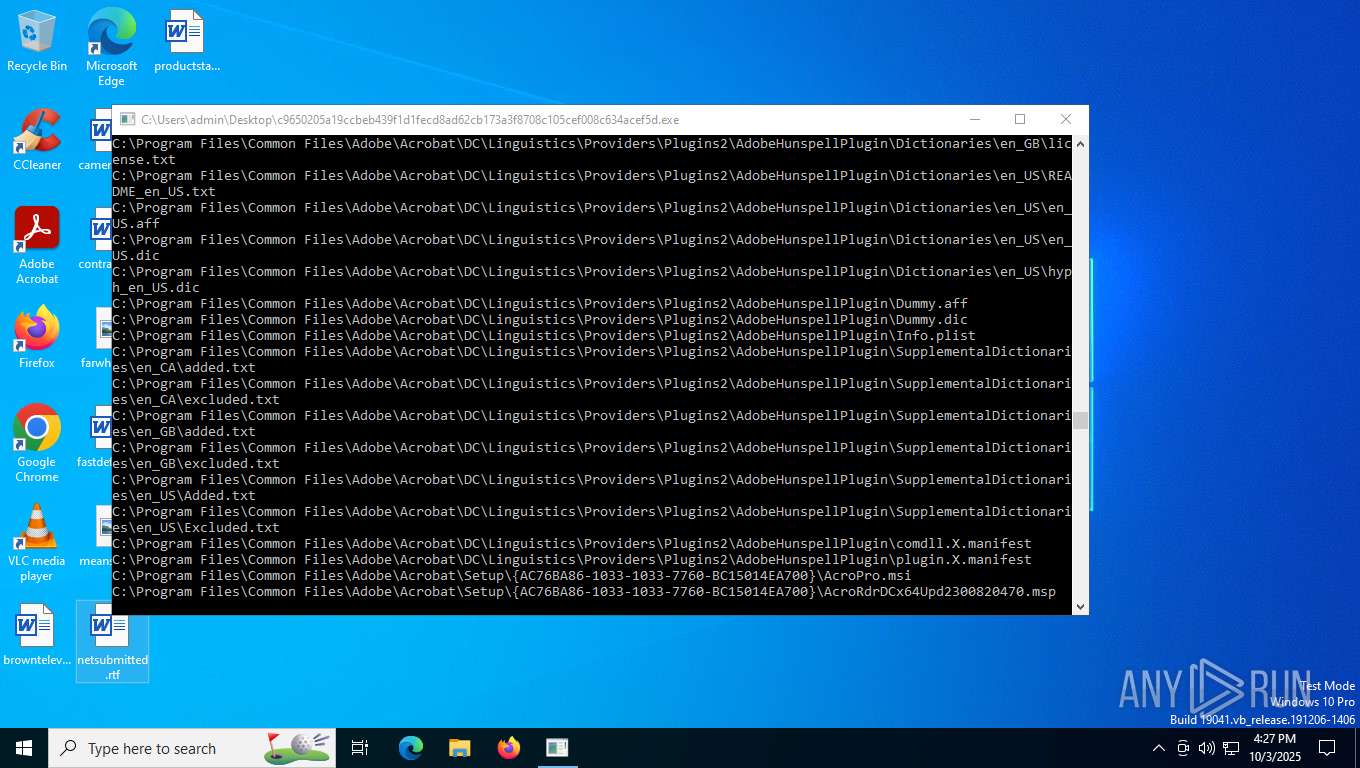
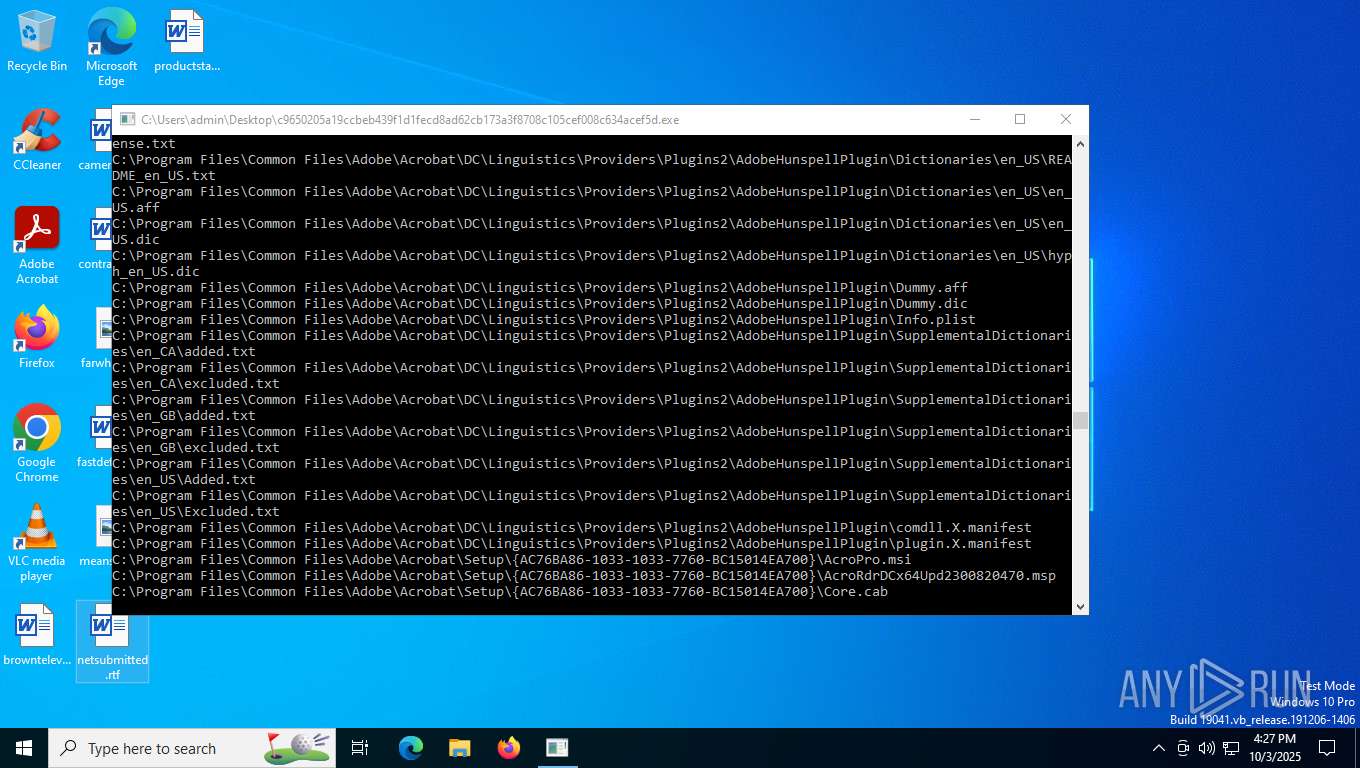
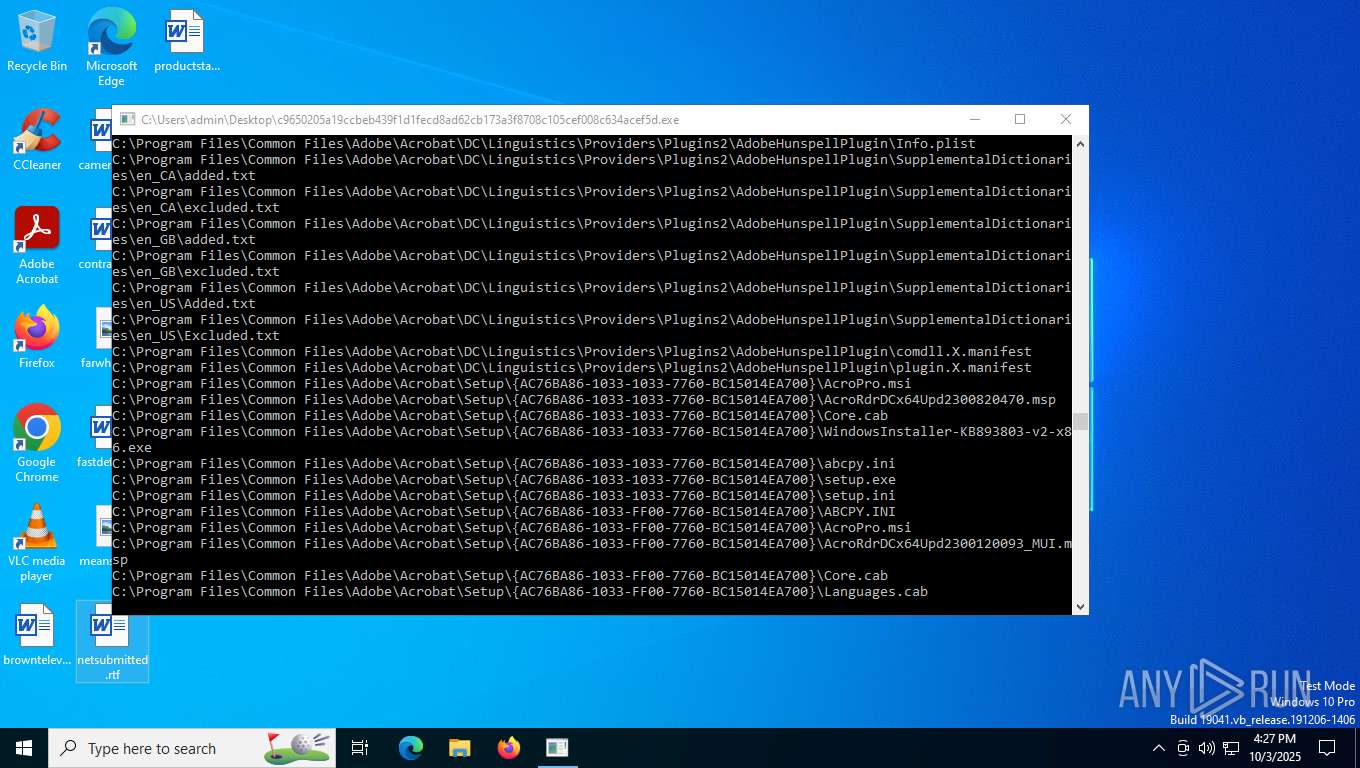
| 756 | "C:\Users\admin\Desktop\c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe" | C:\Users\admin\Desktop\c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 2 Modules
| |||||||||||||||
| 2652 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
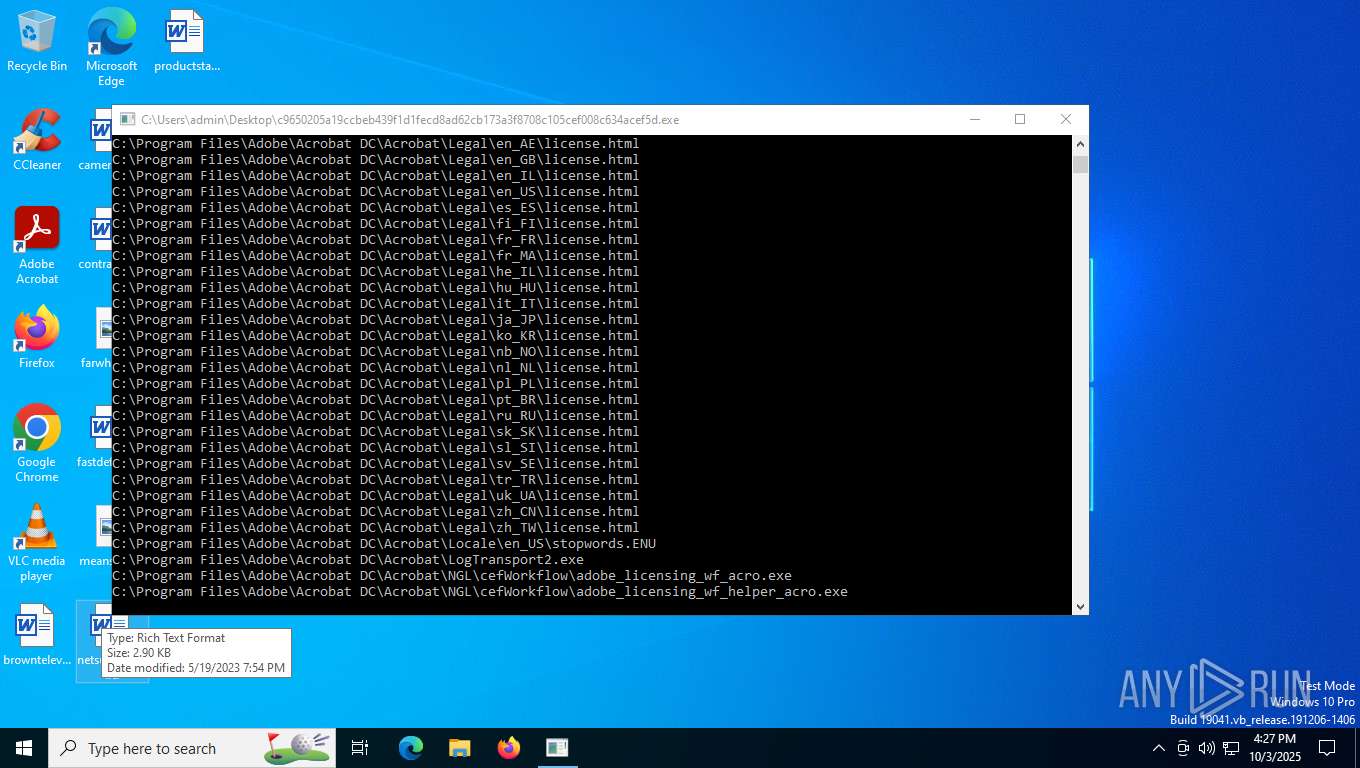
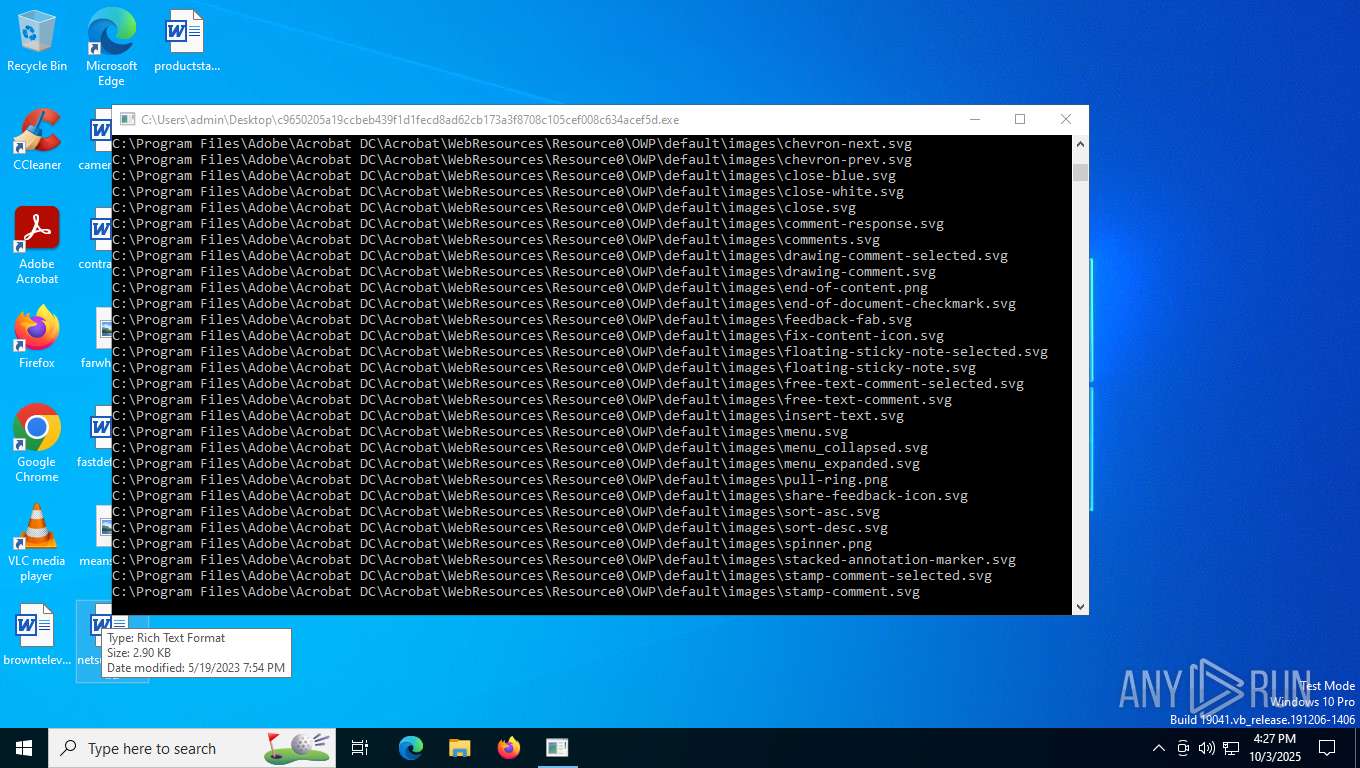
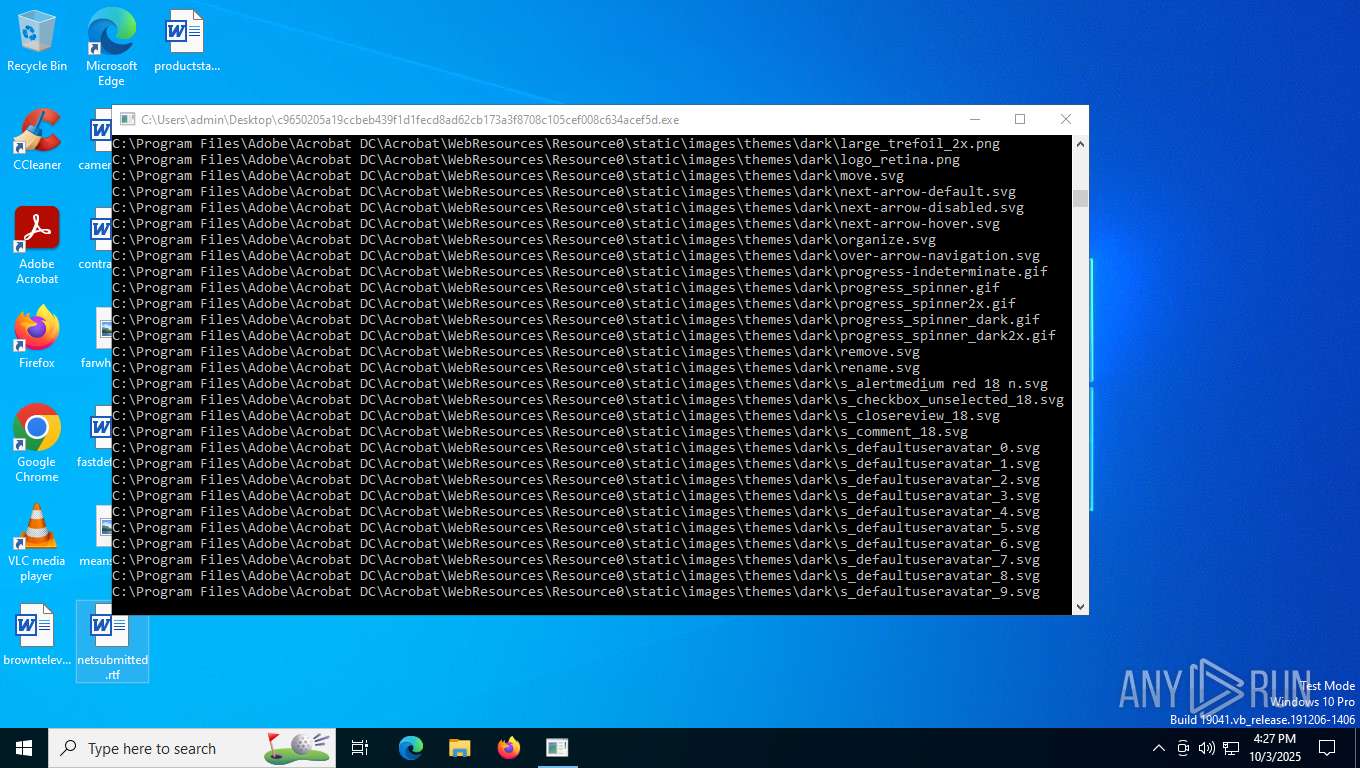
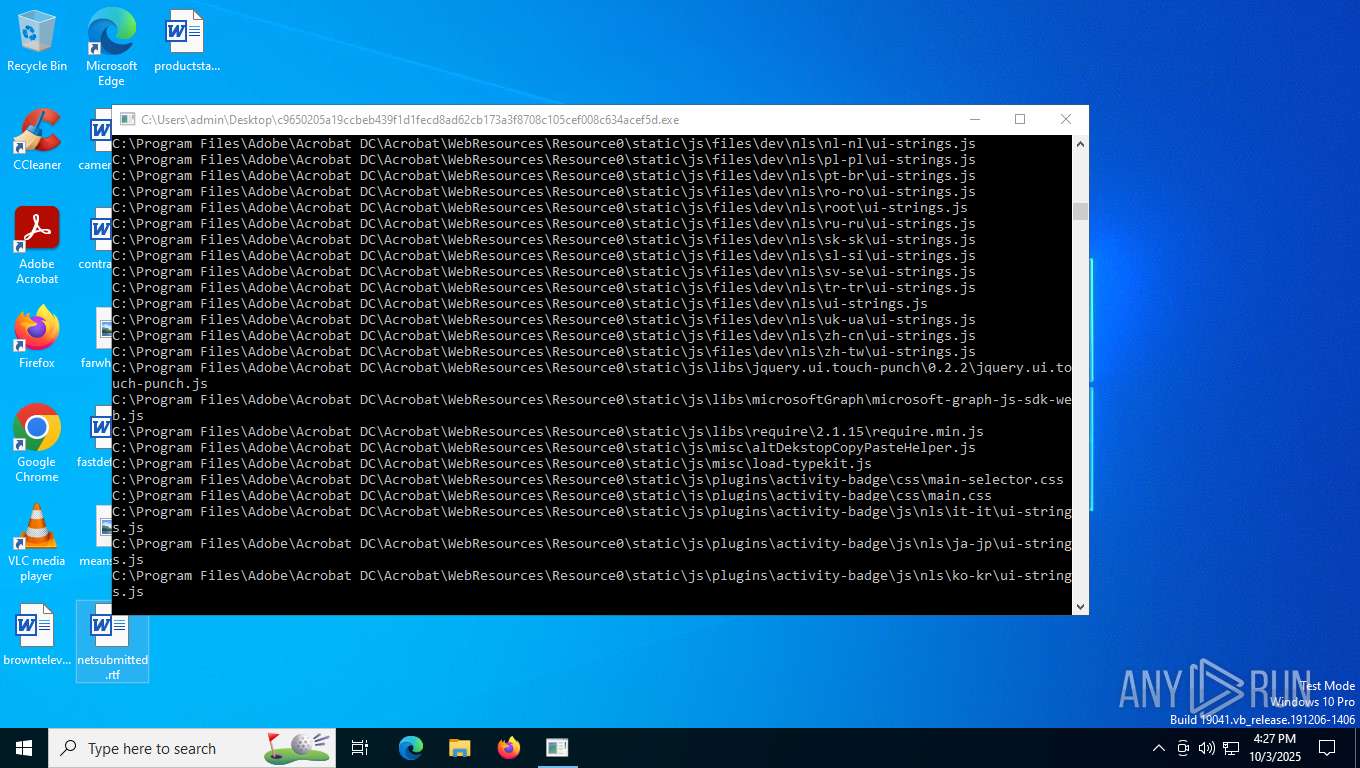
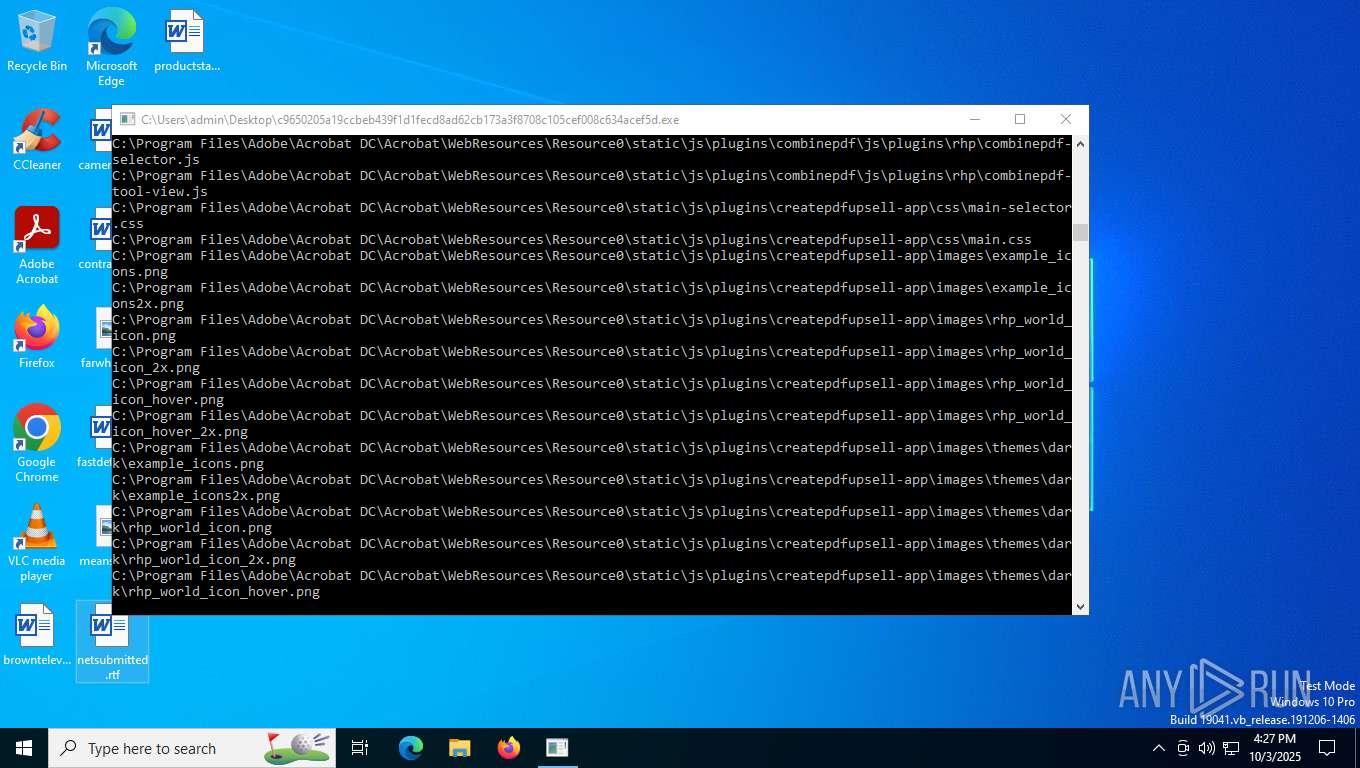
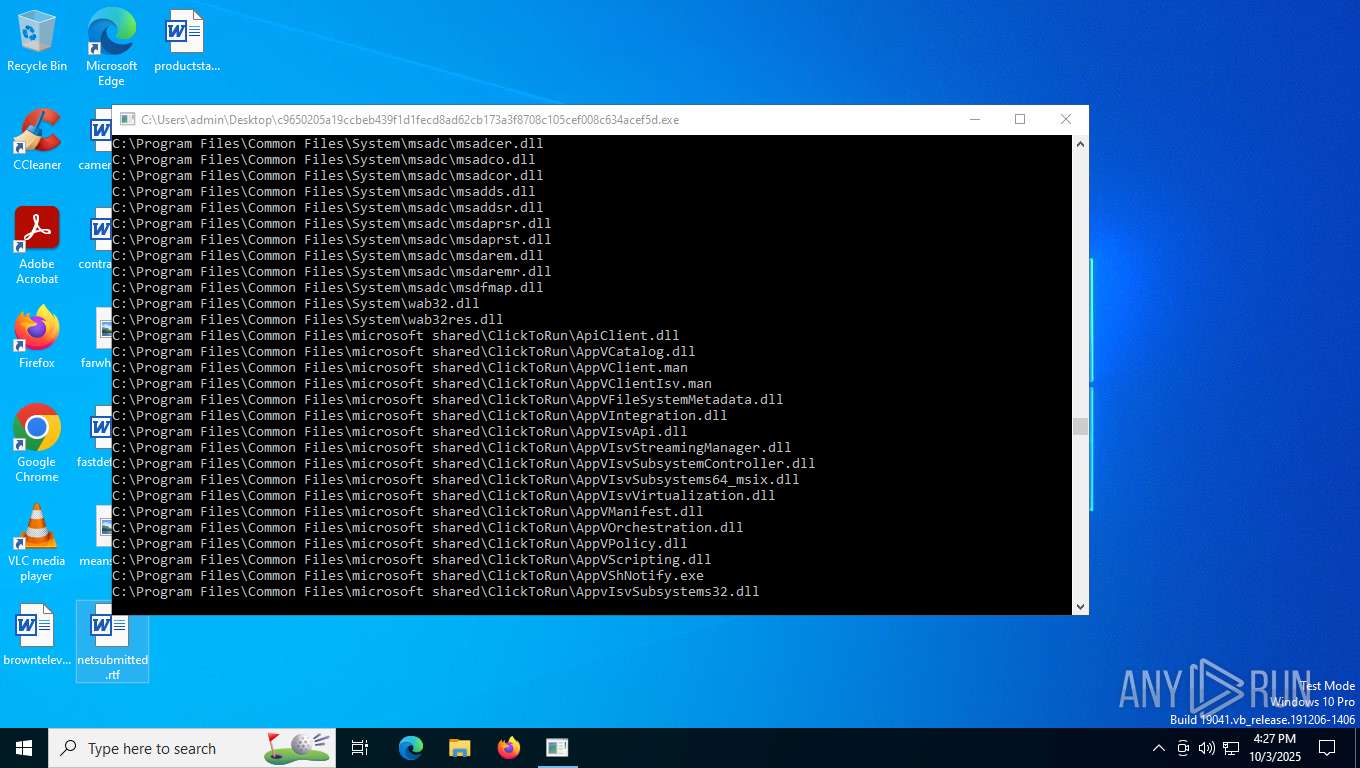
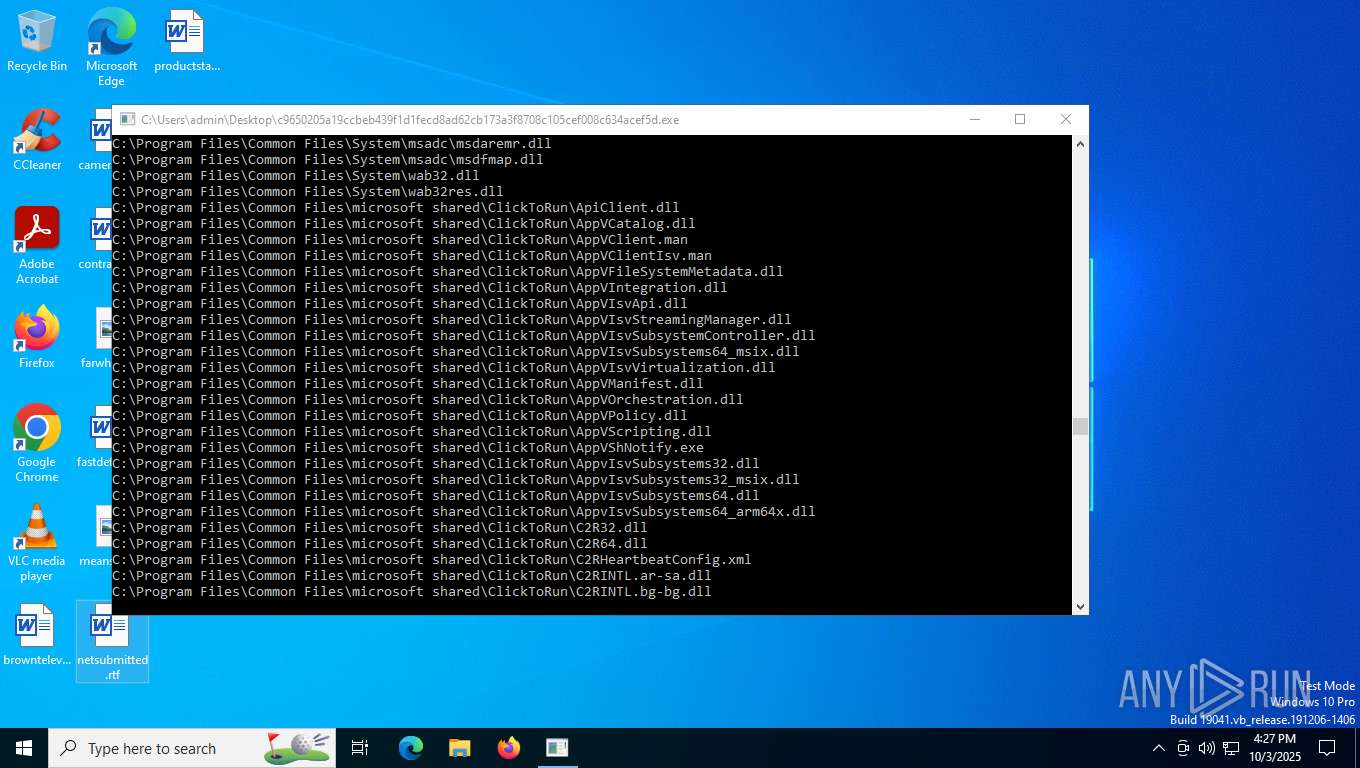
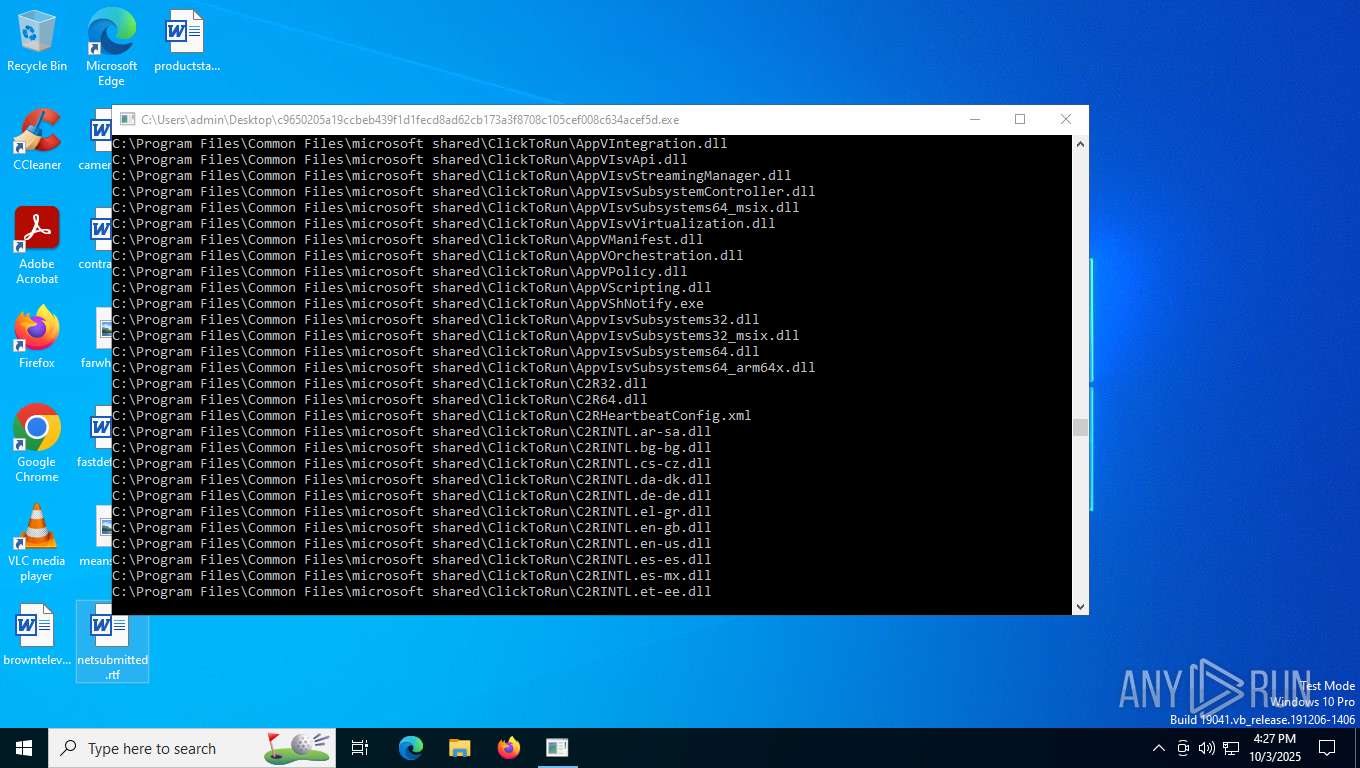
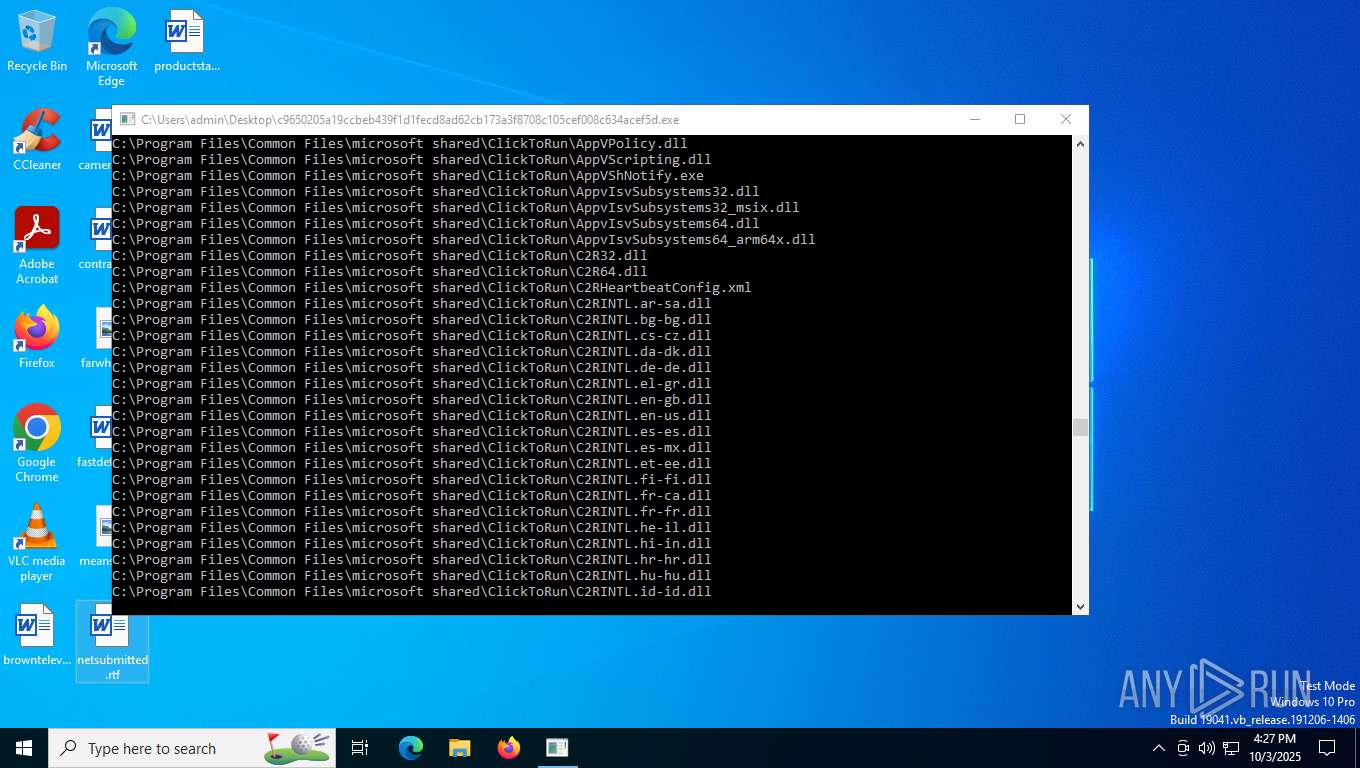
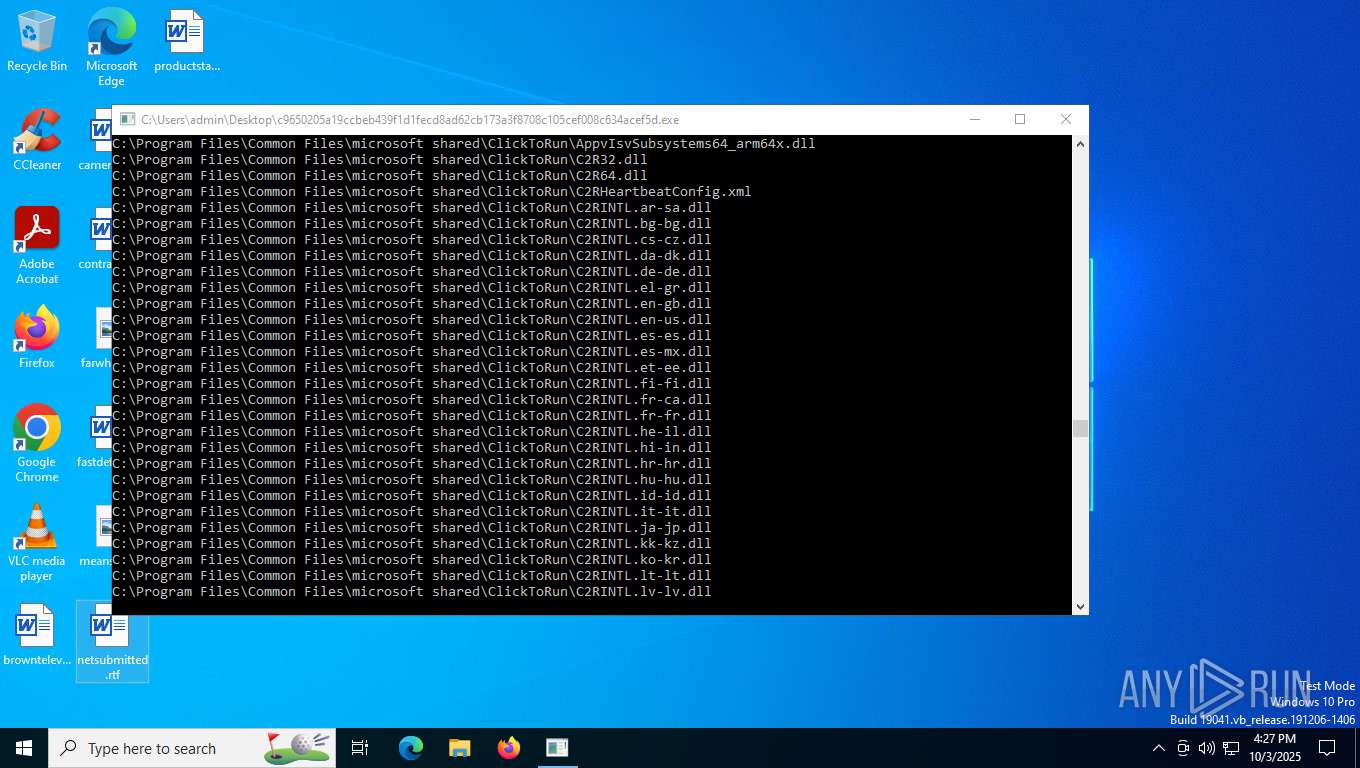
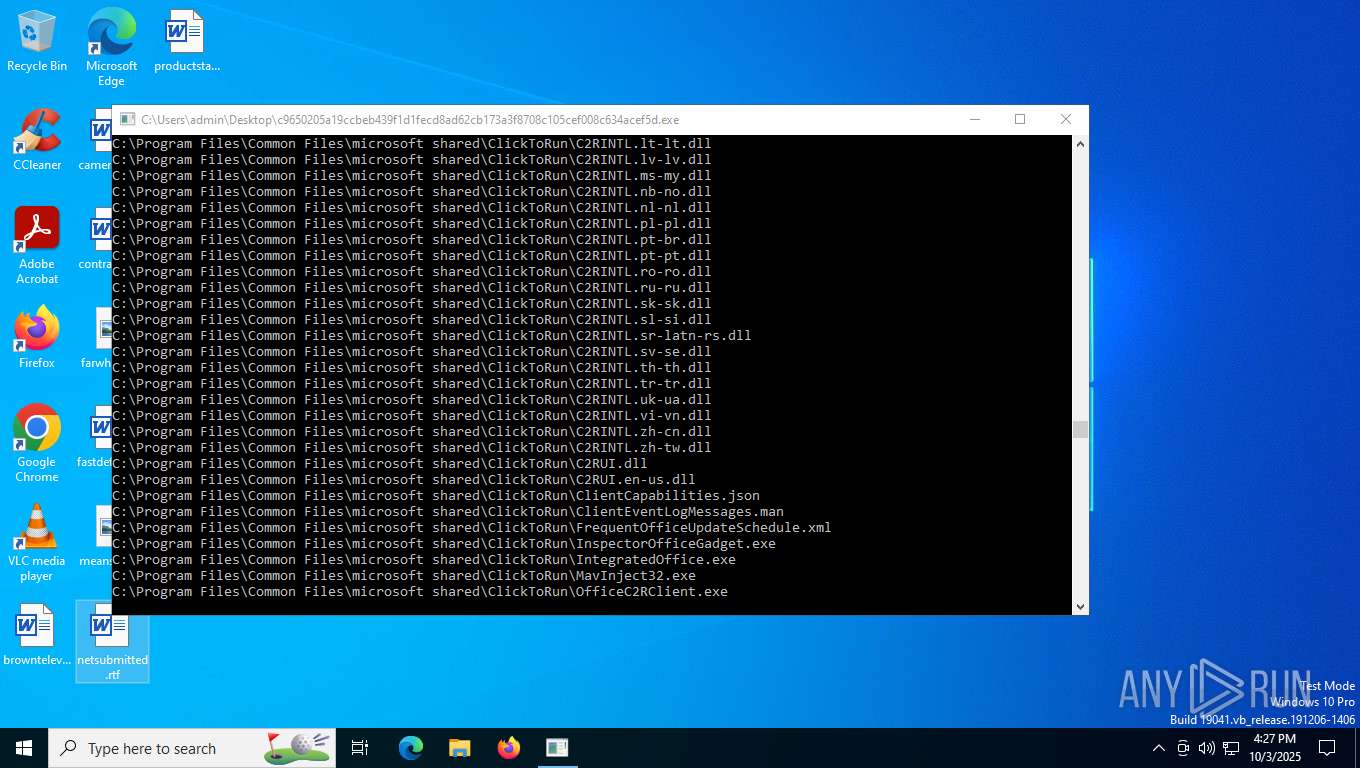
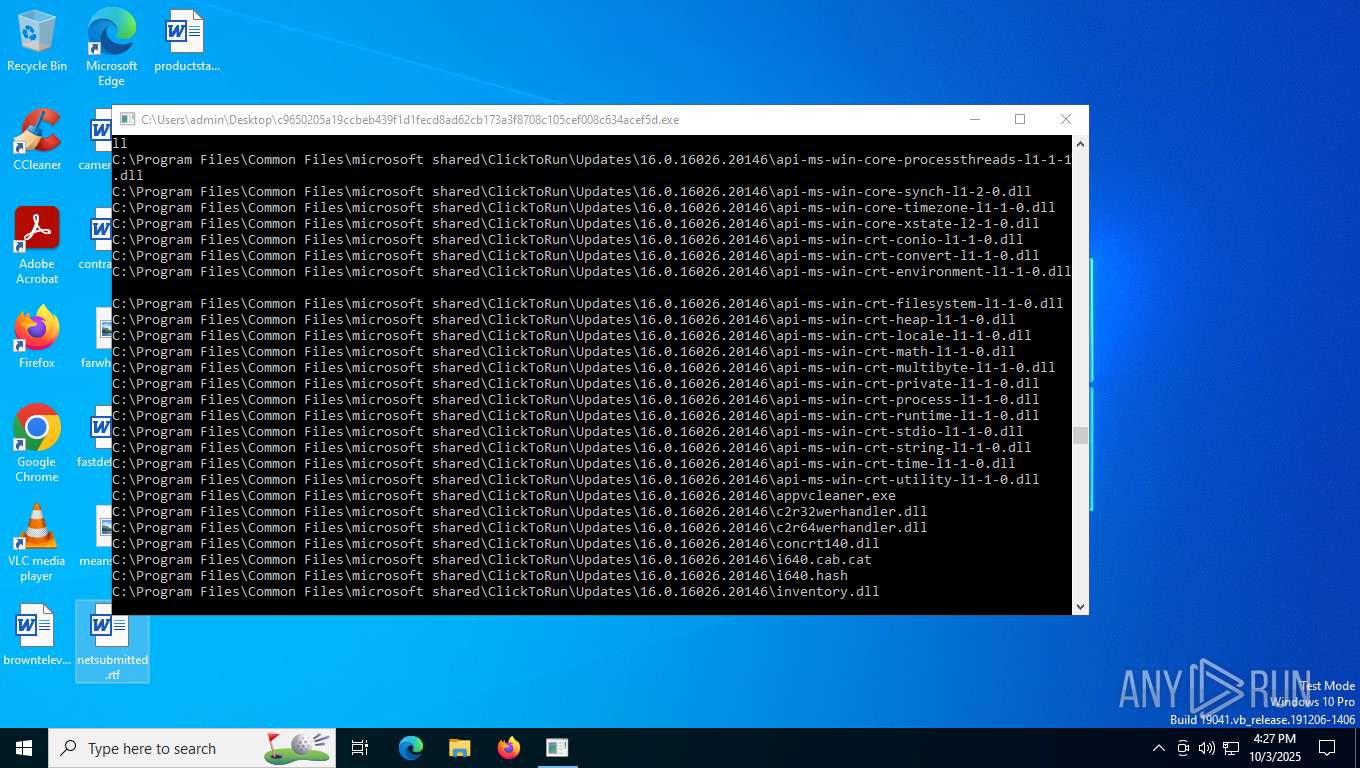
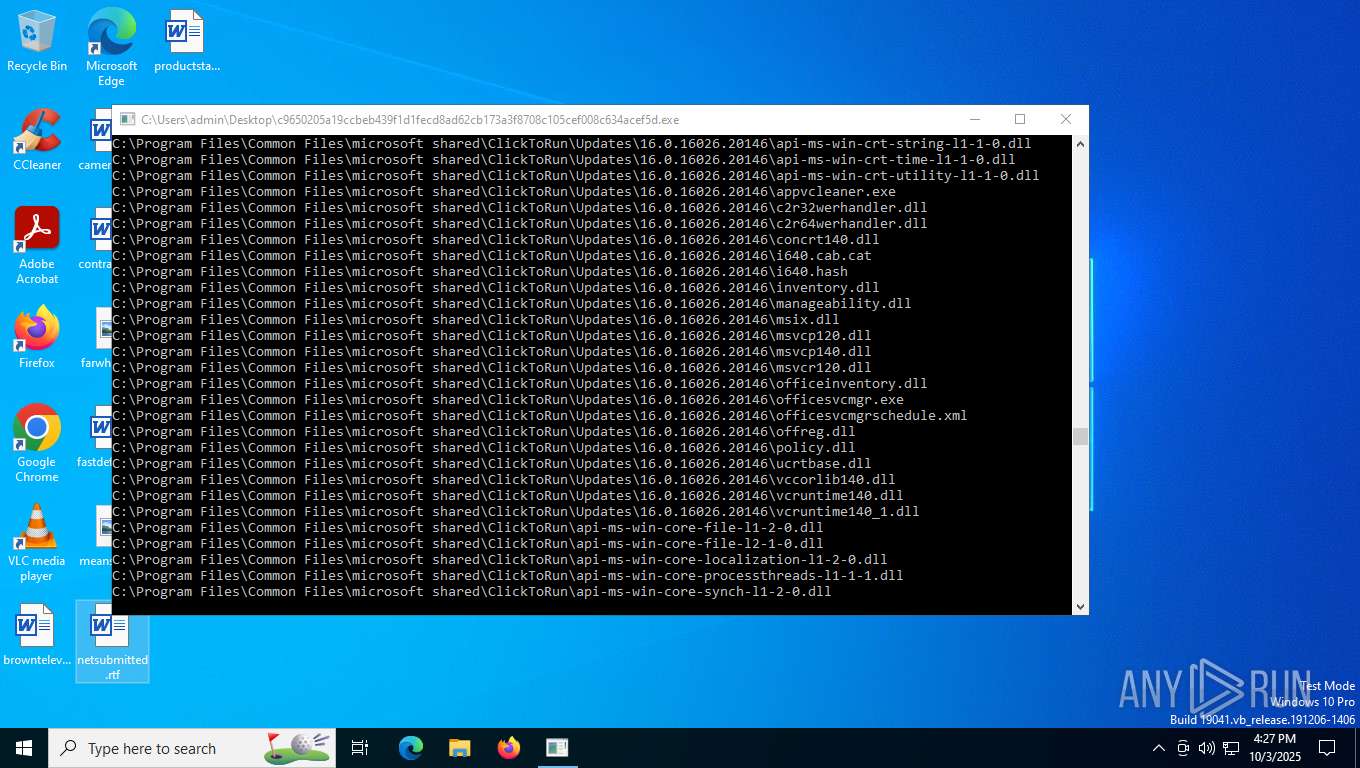
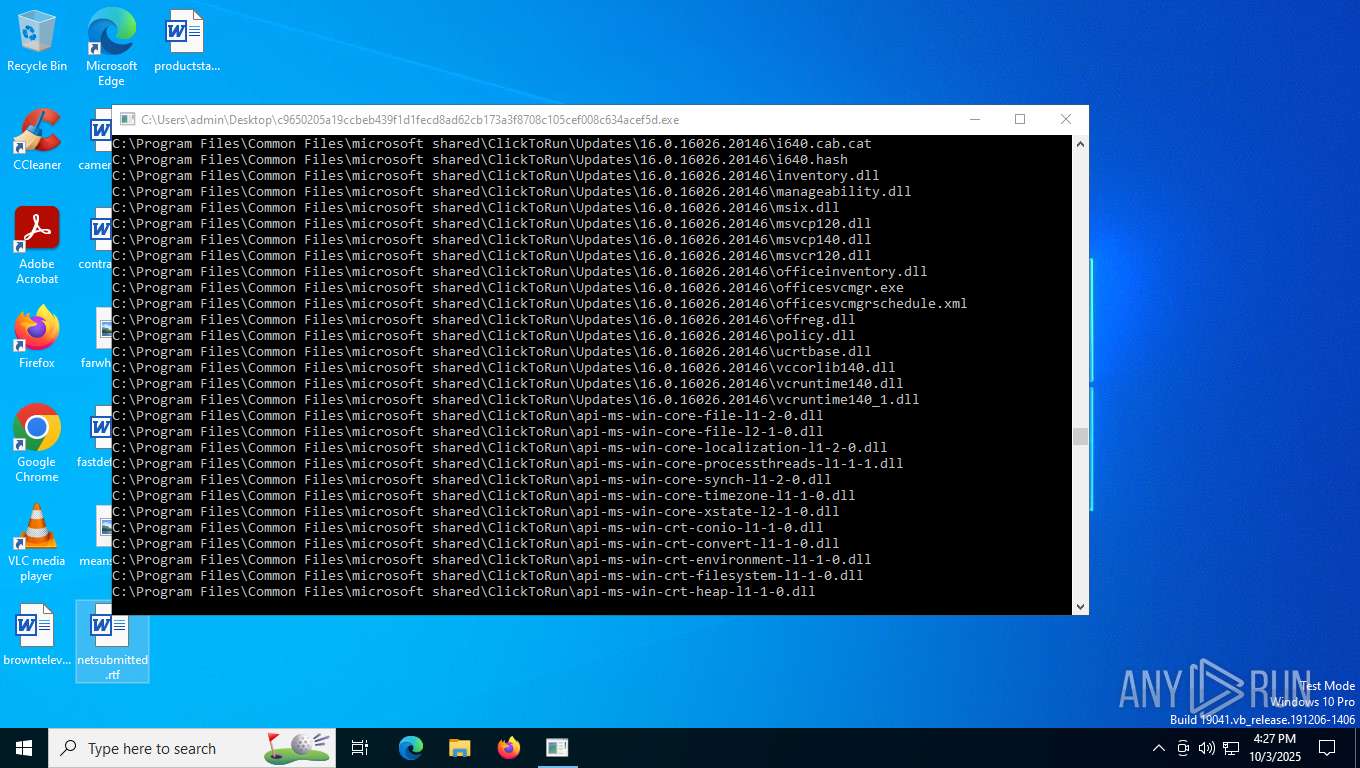
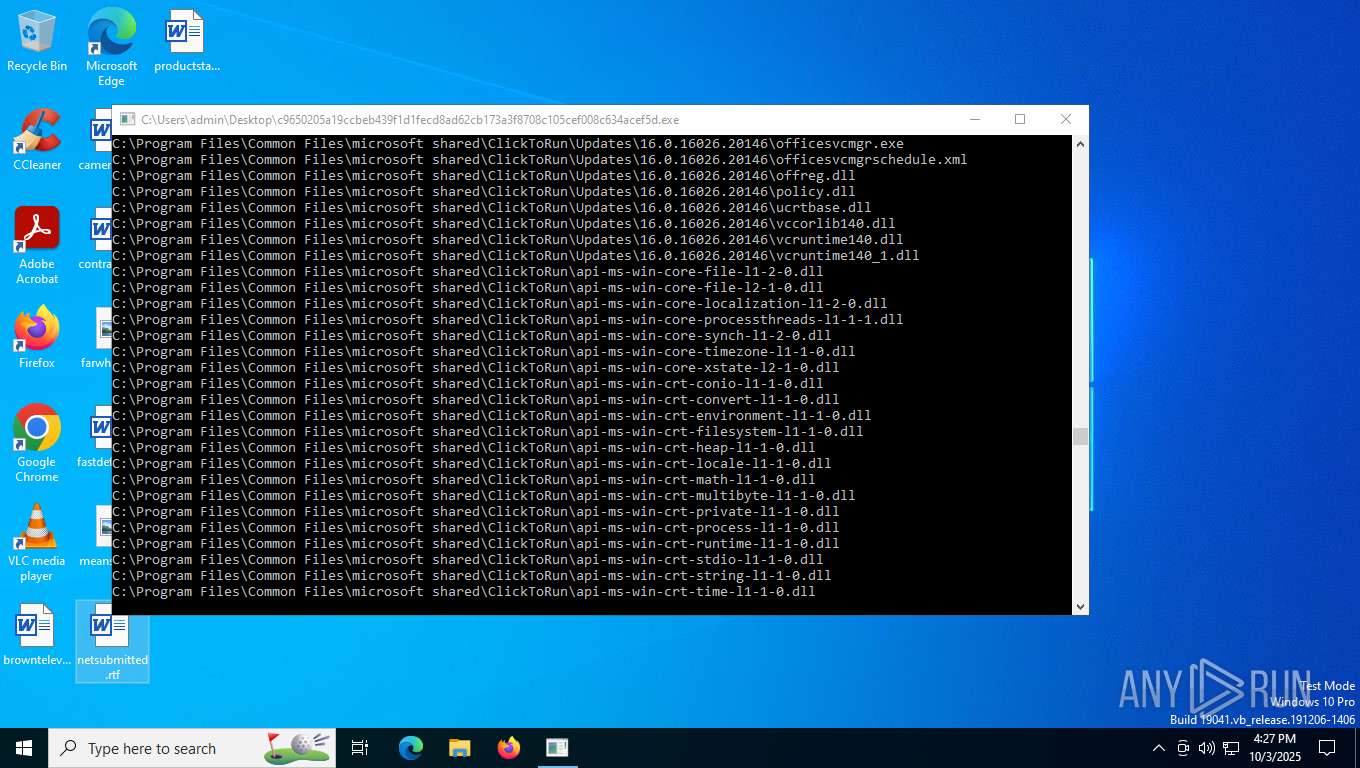
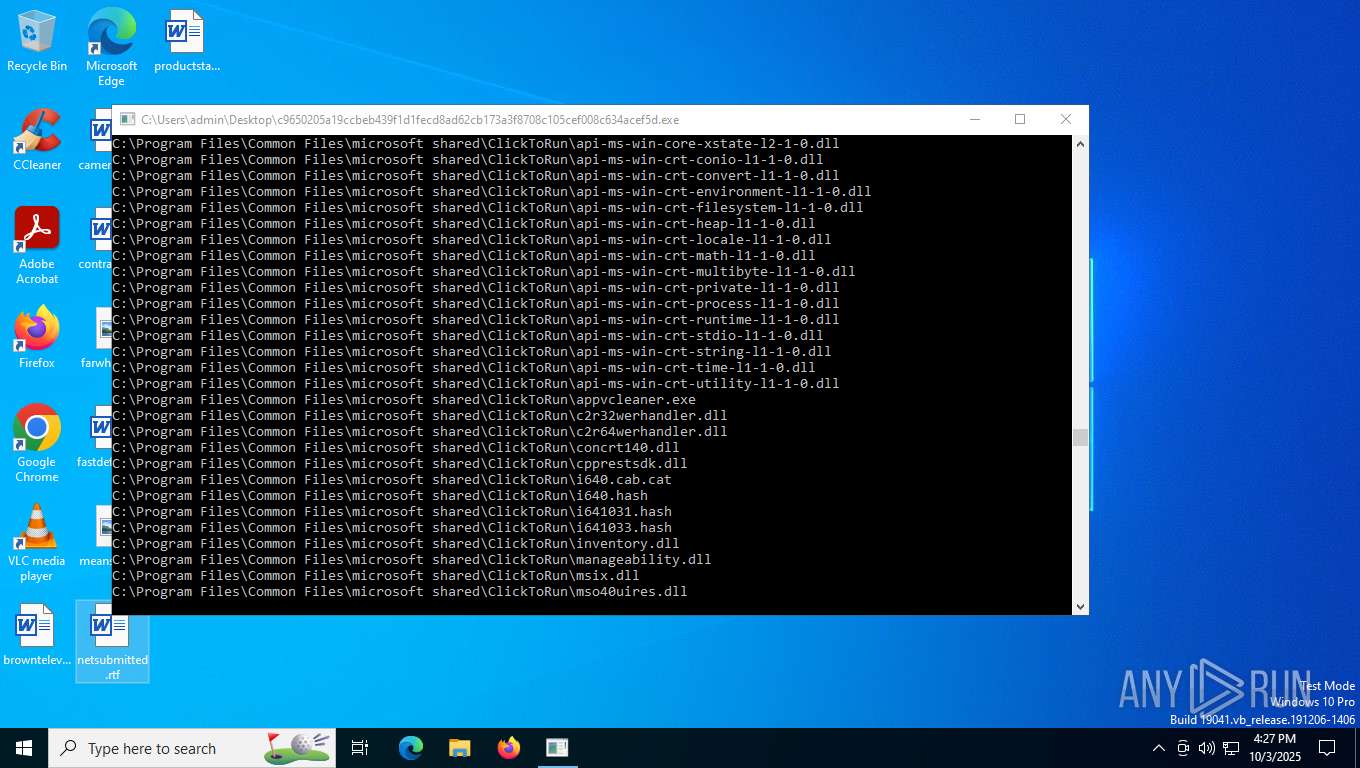
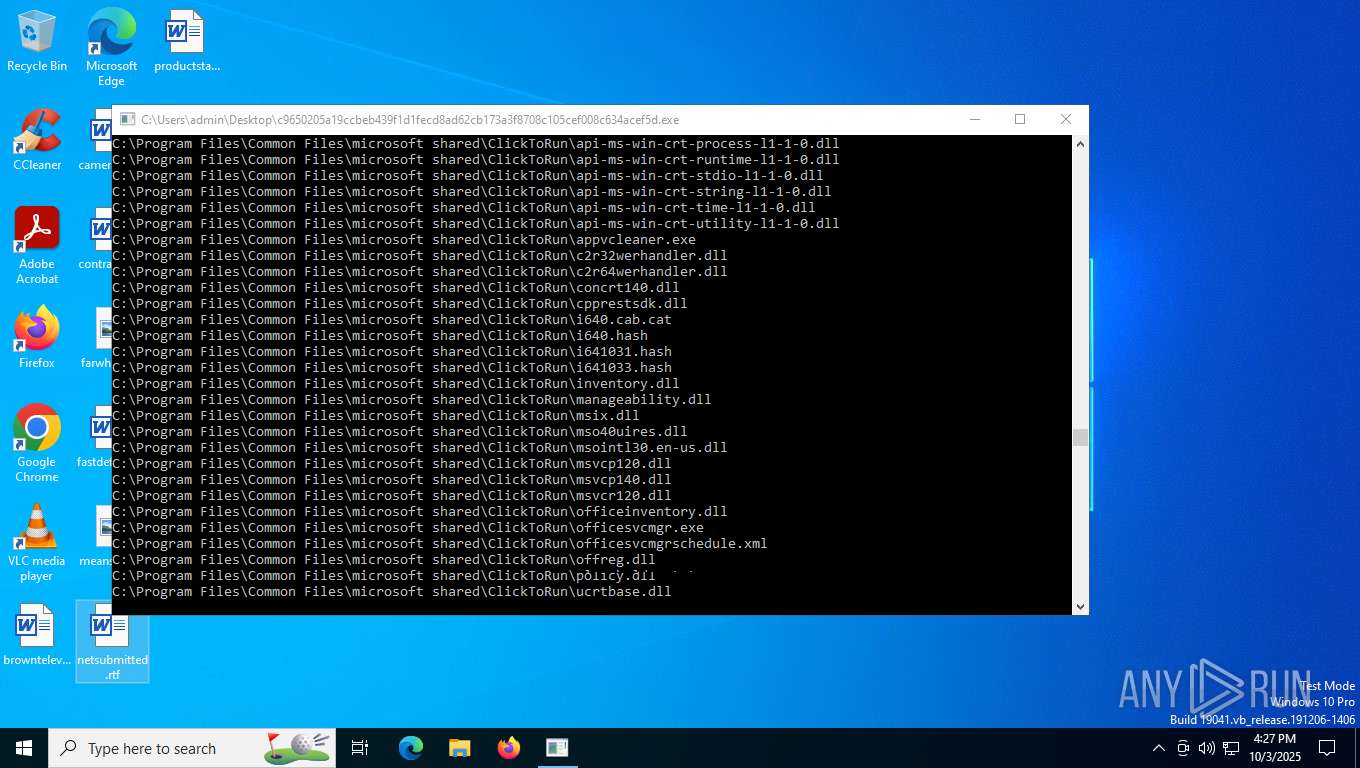
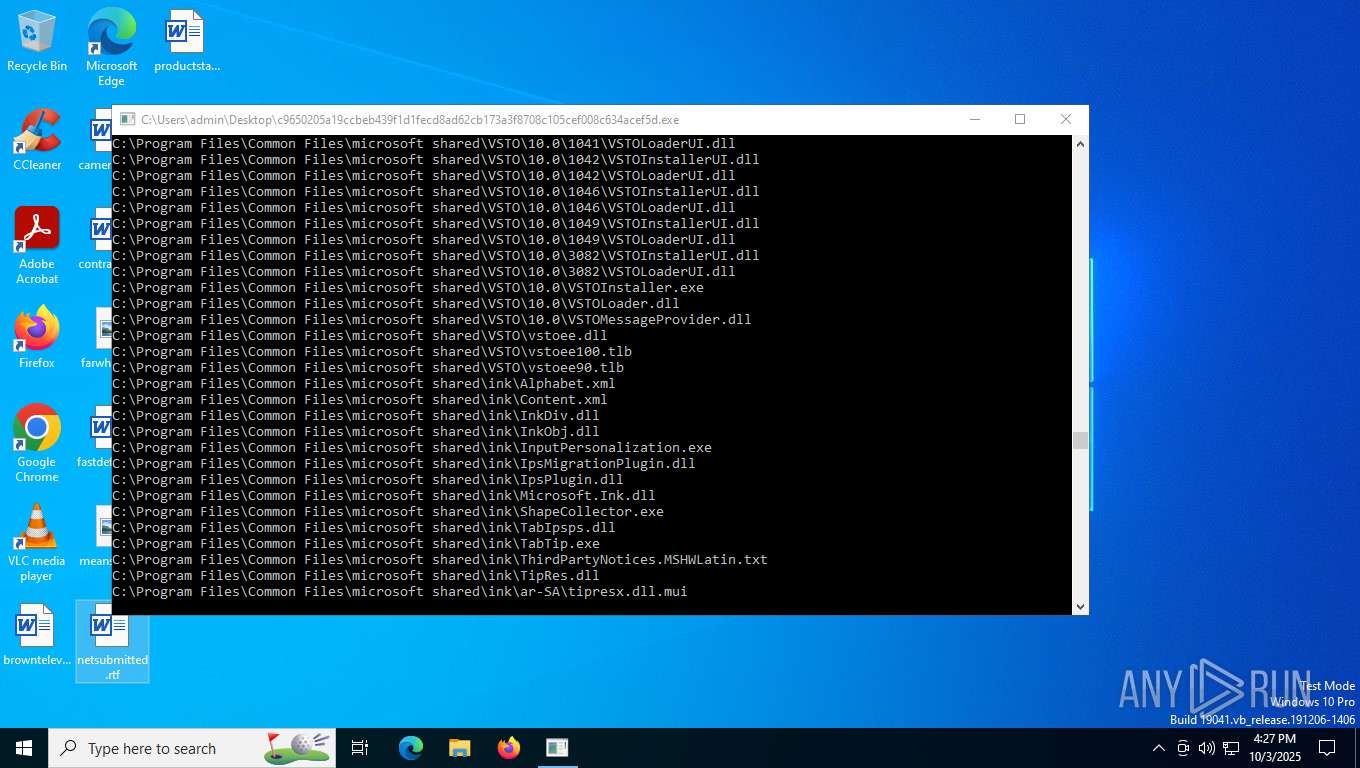
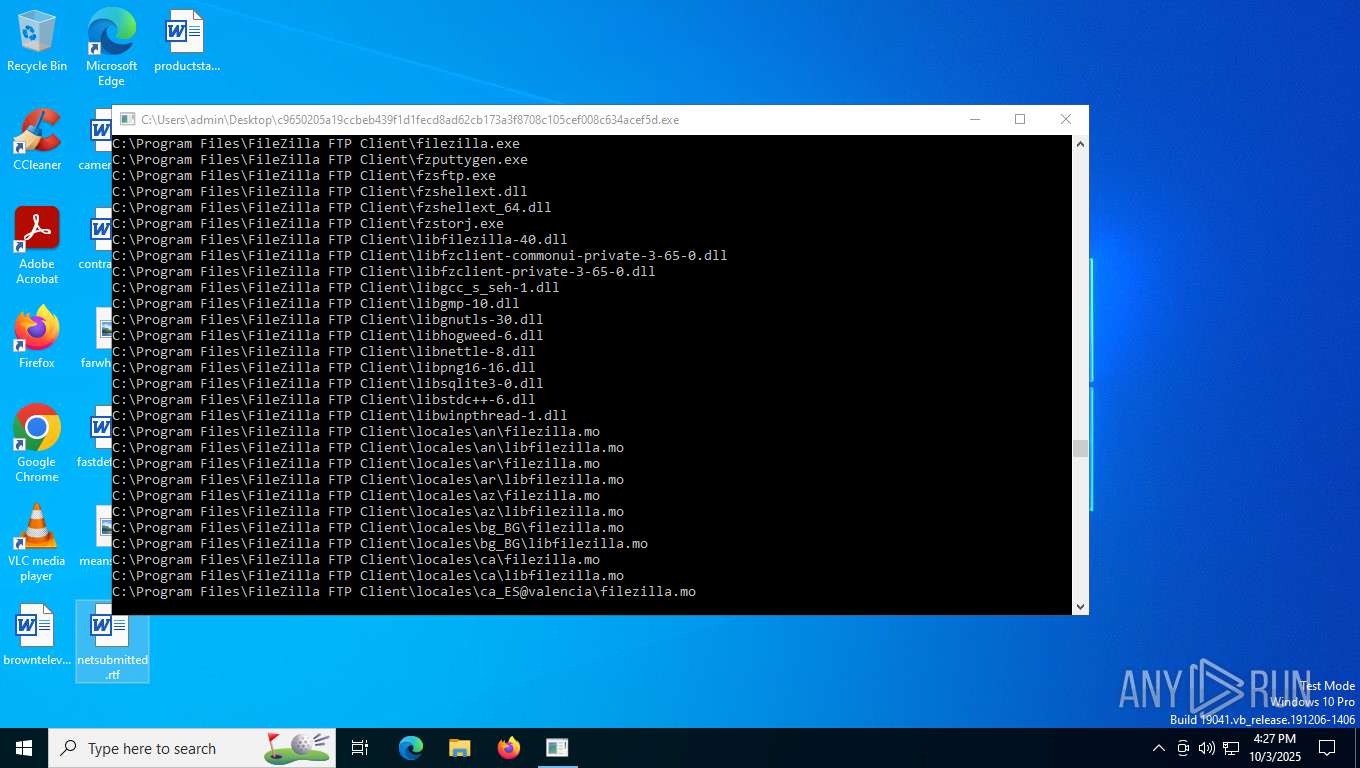
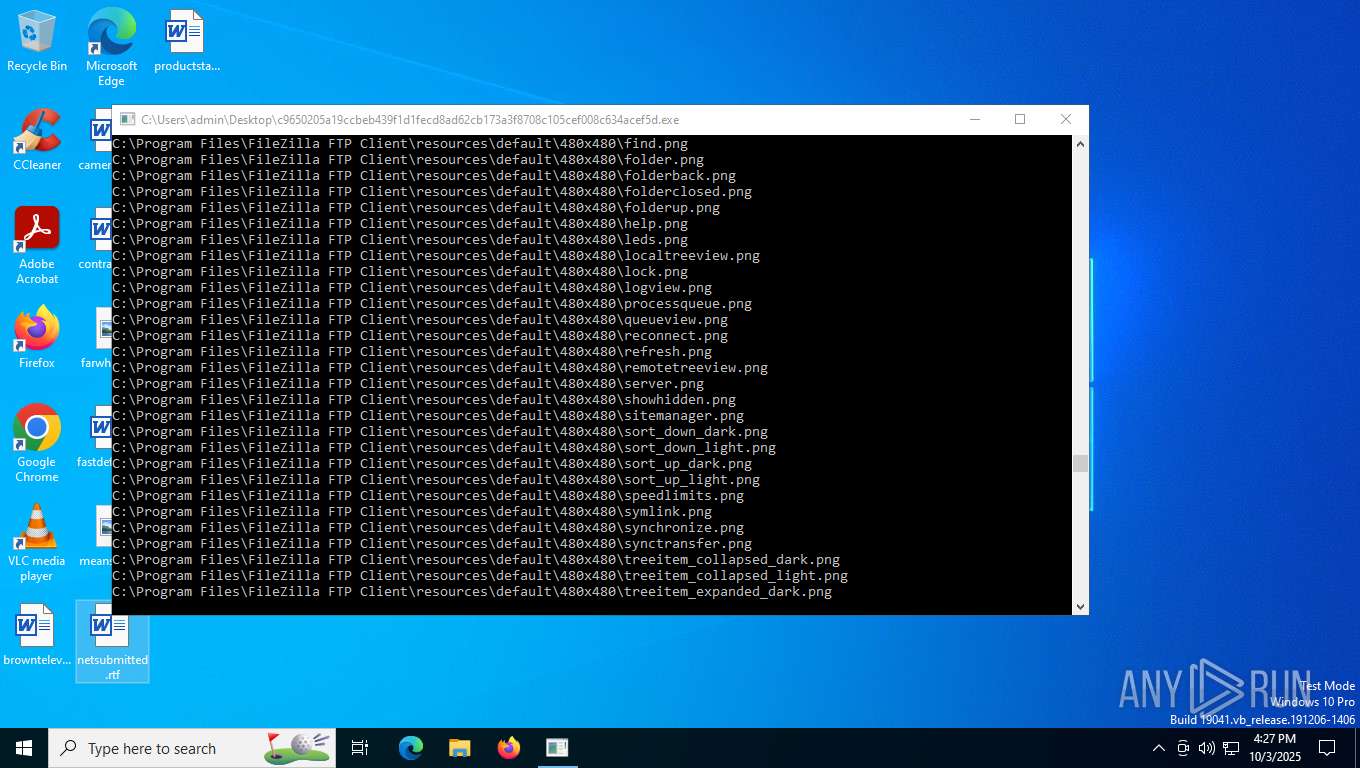
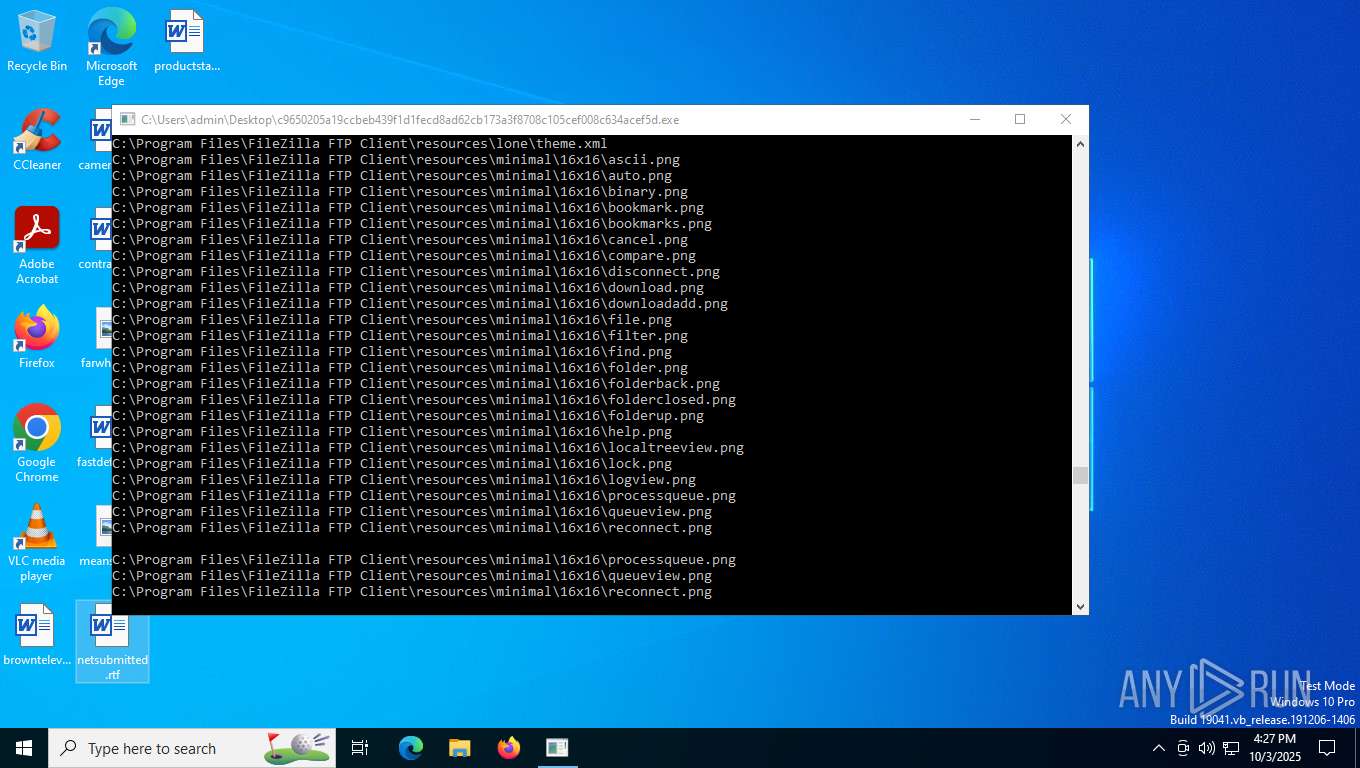
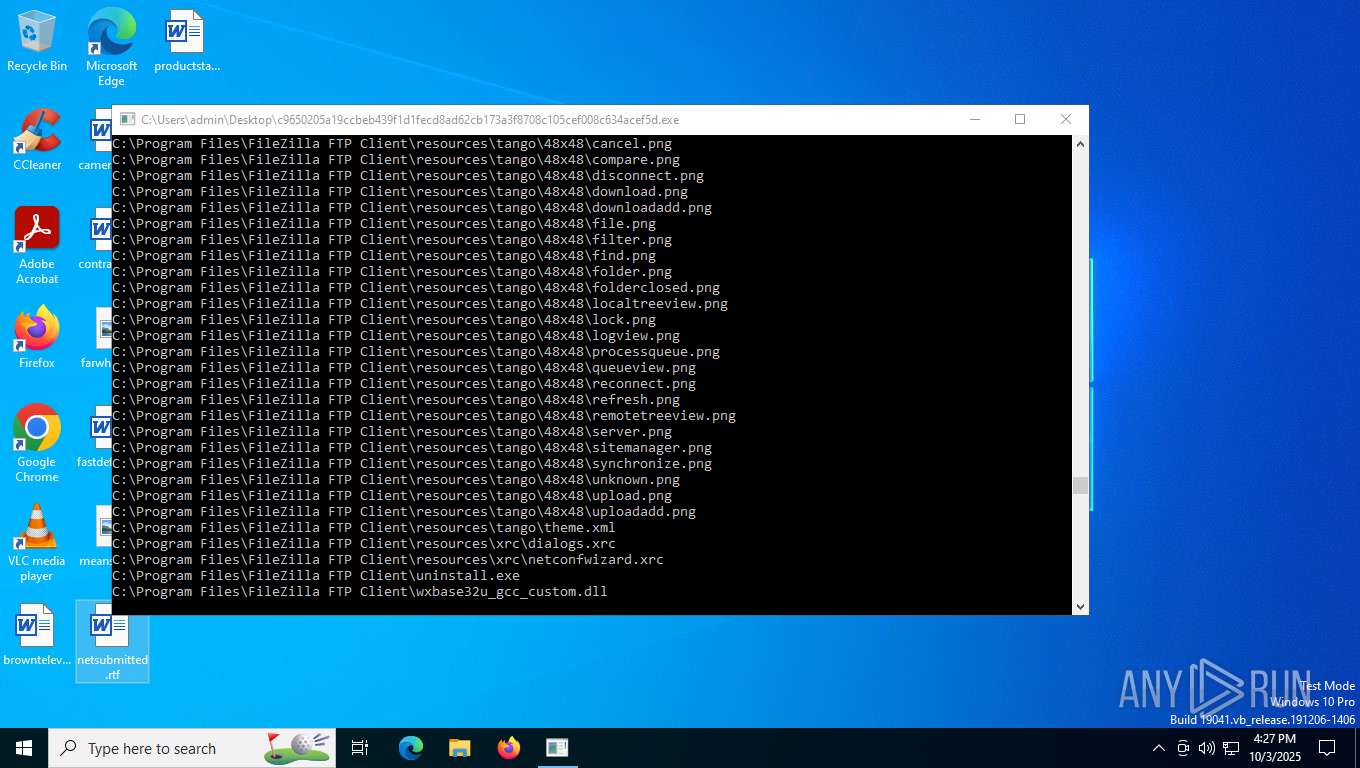
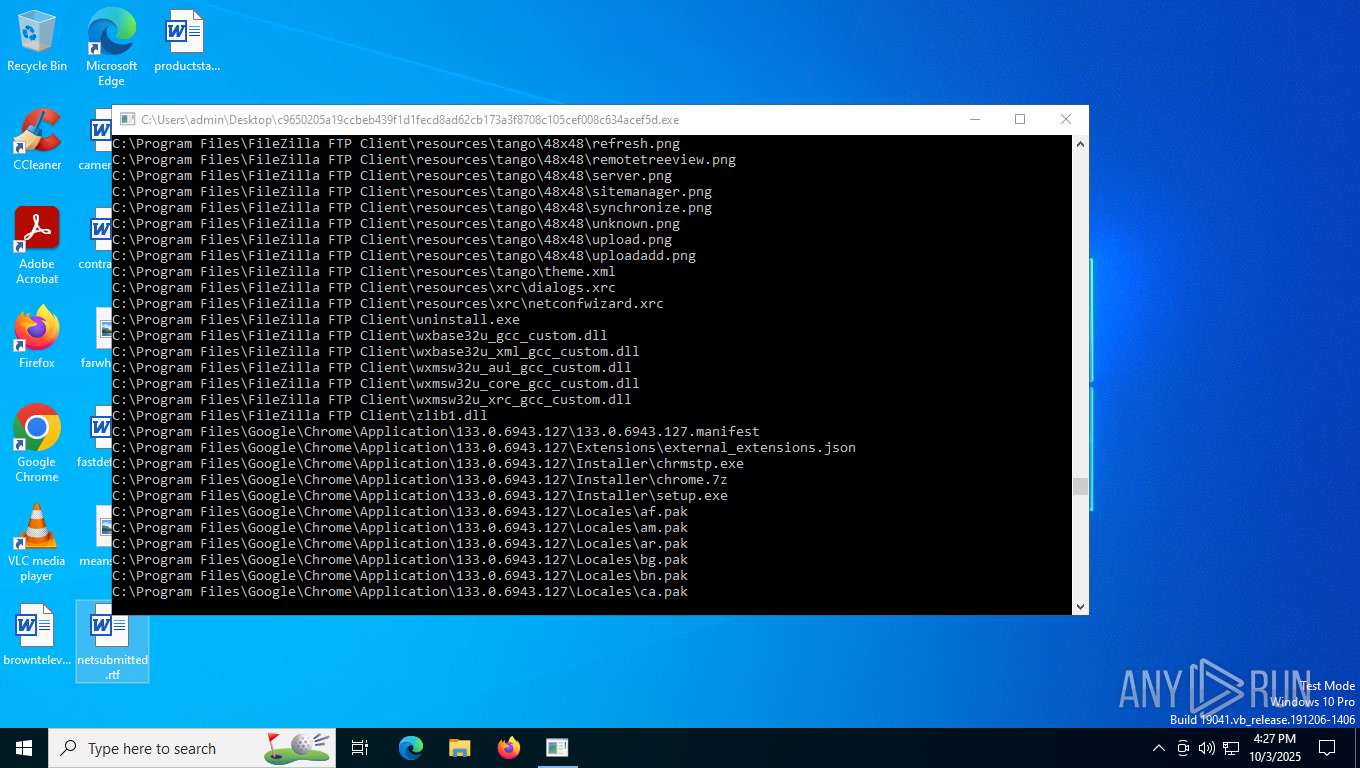
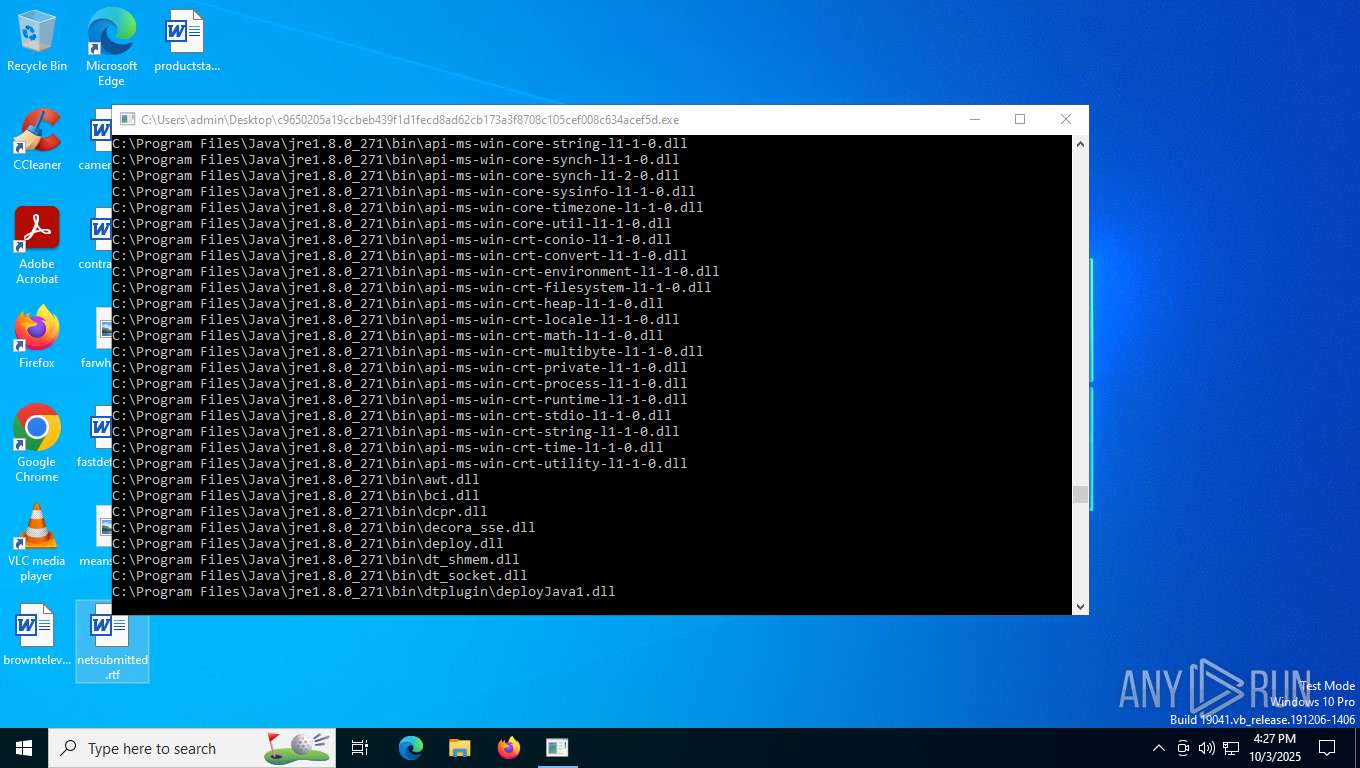
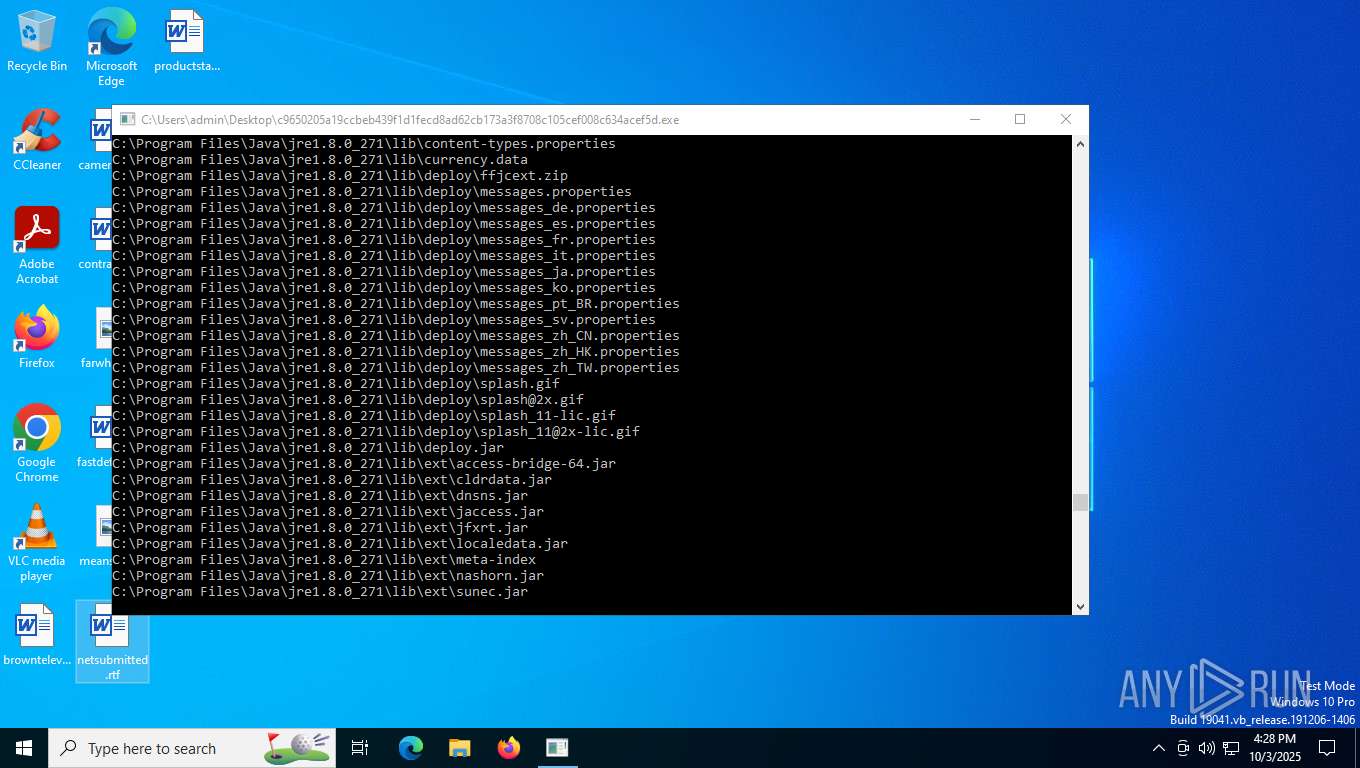
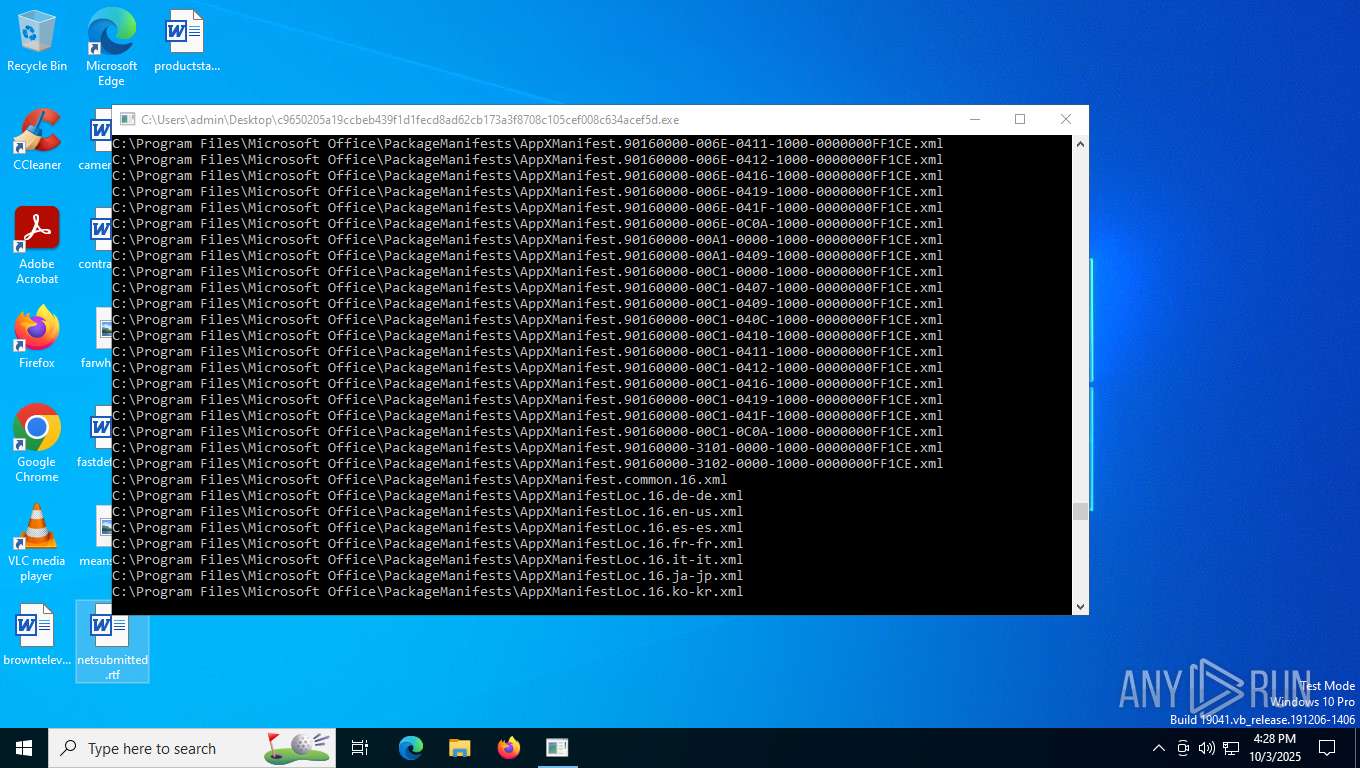
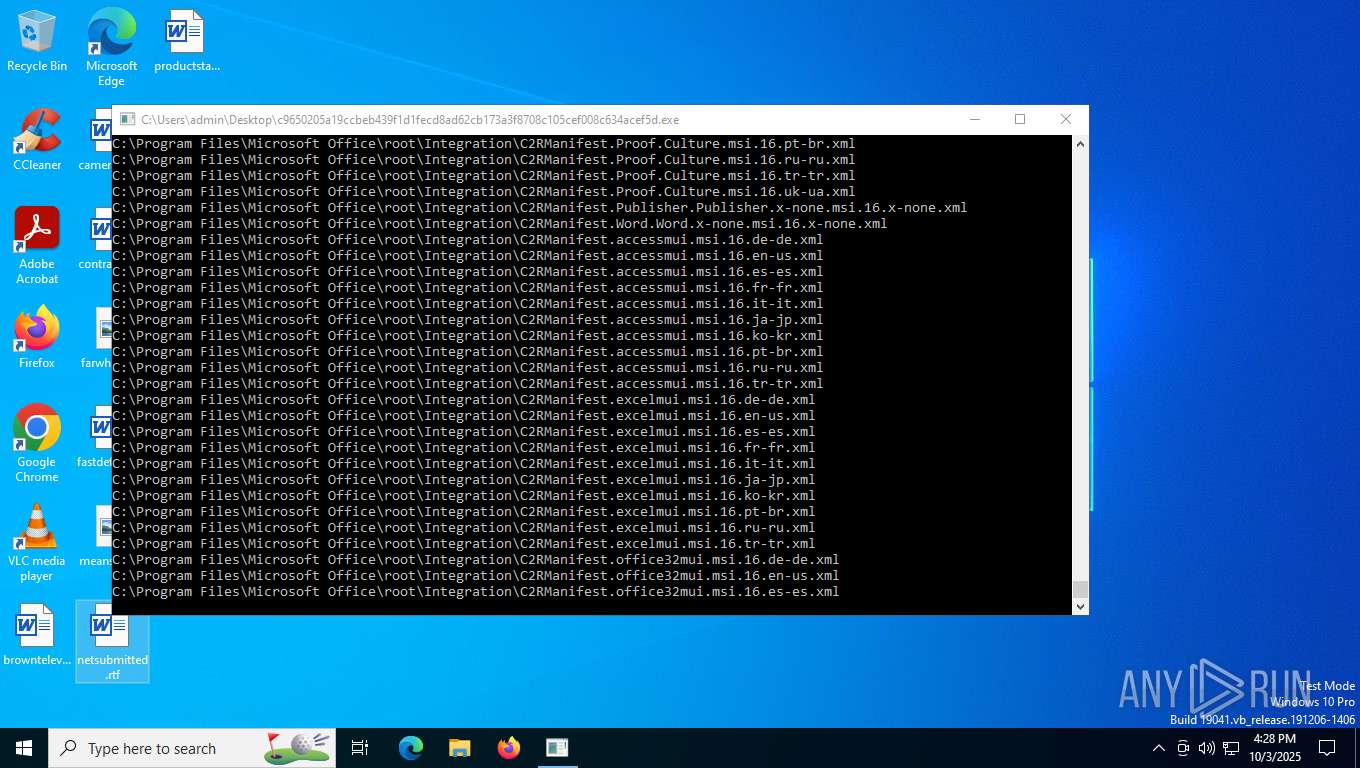
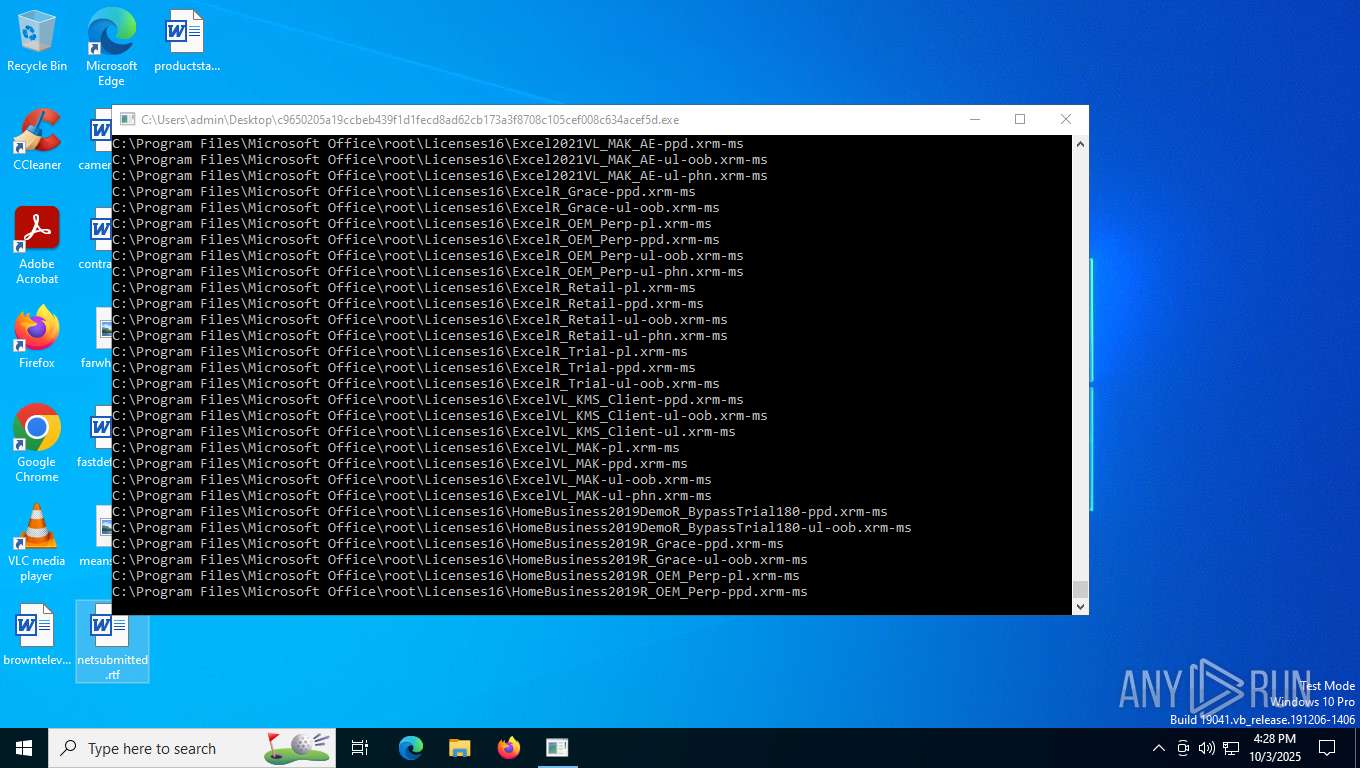
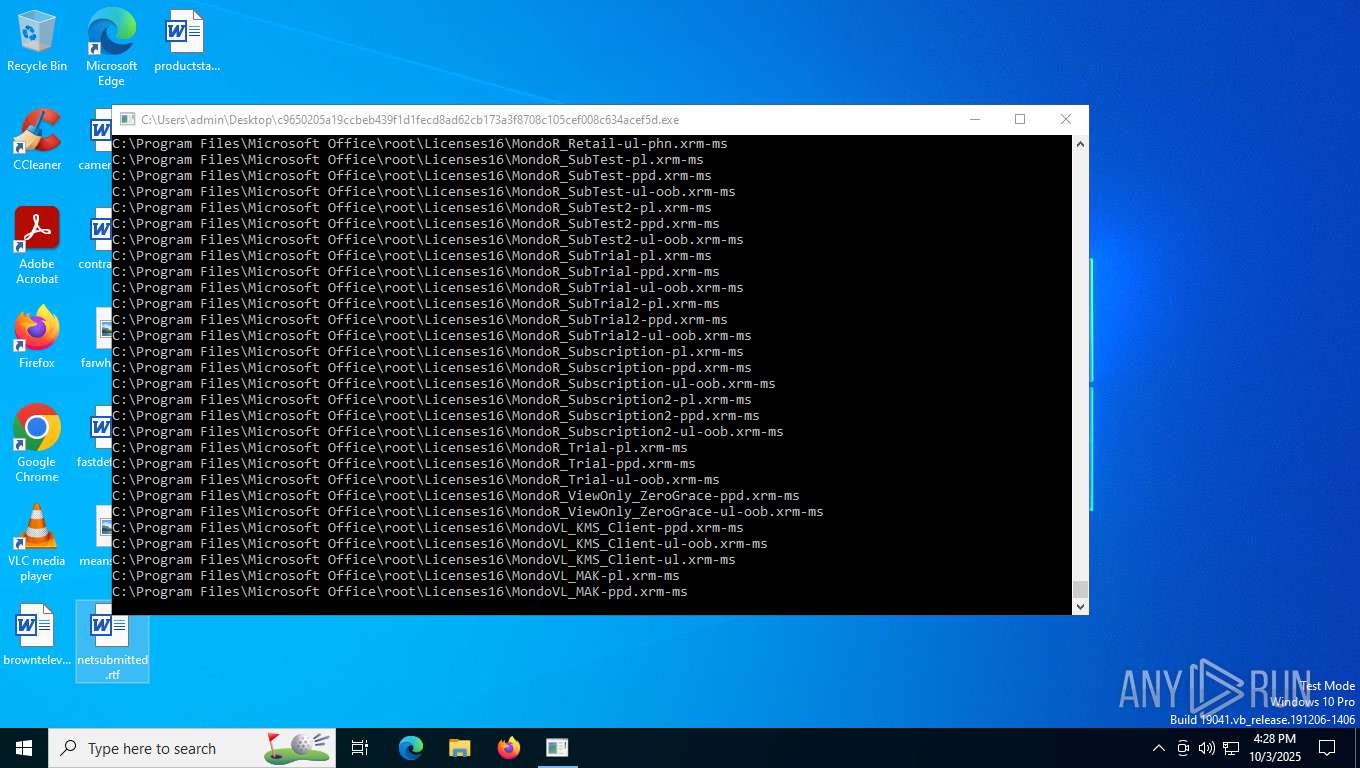
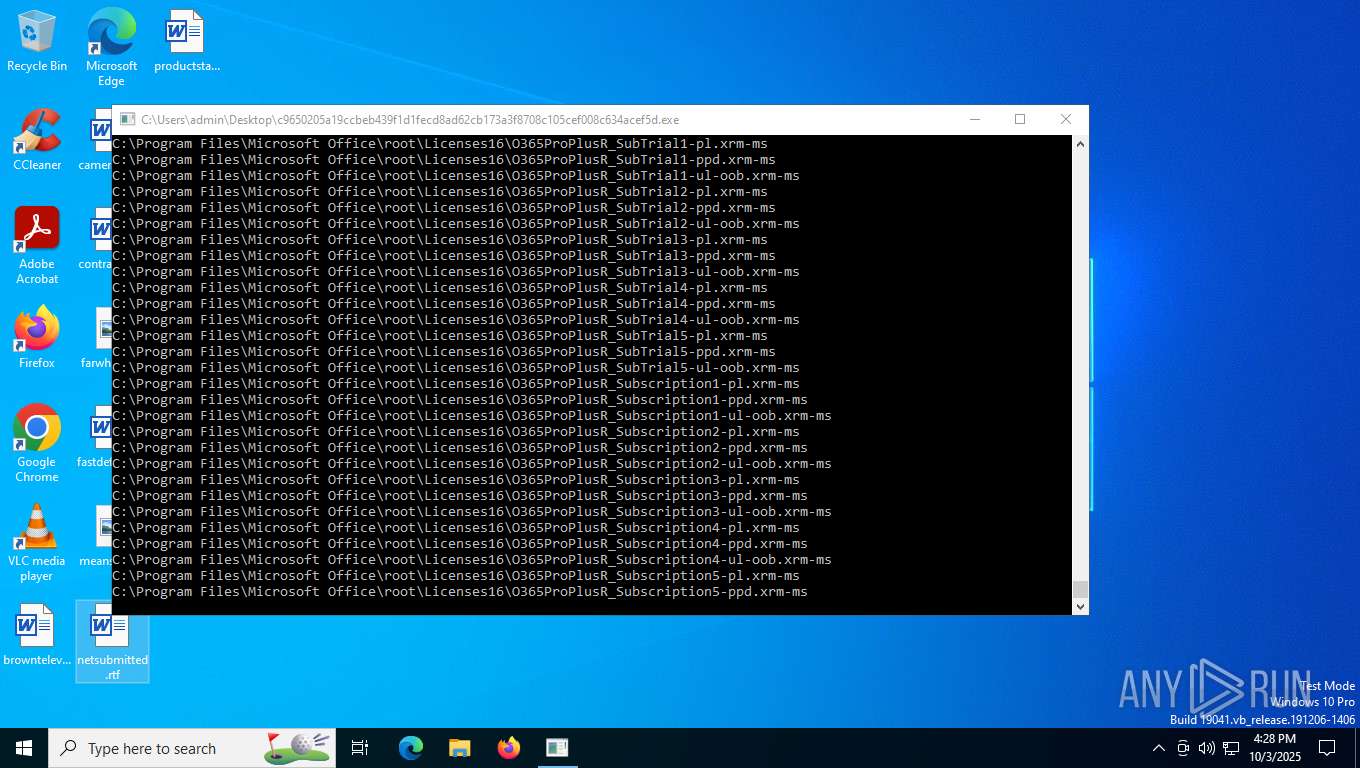
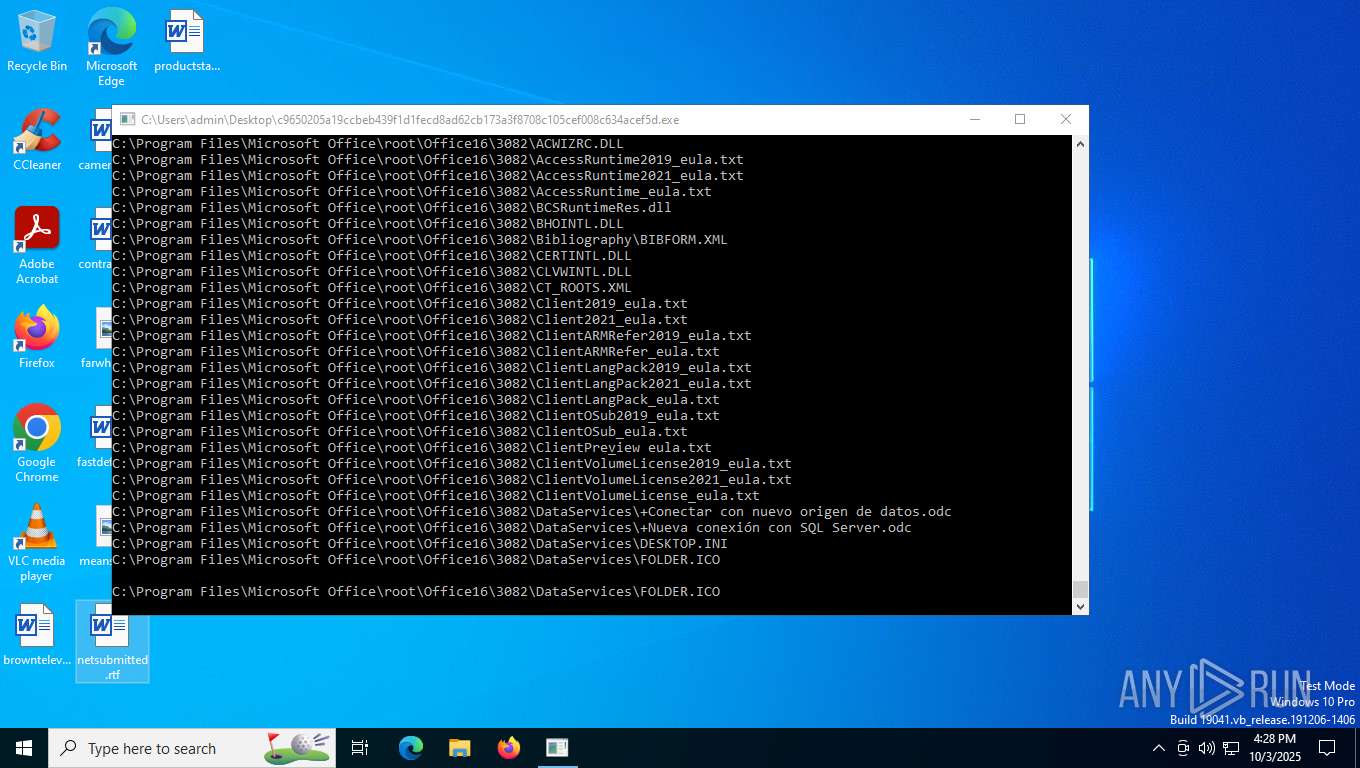
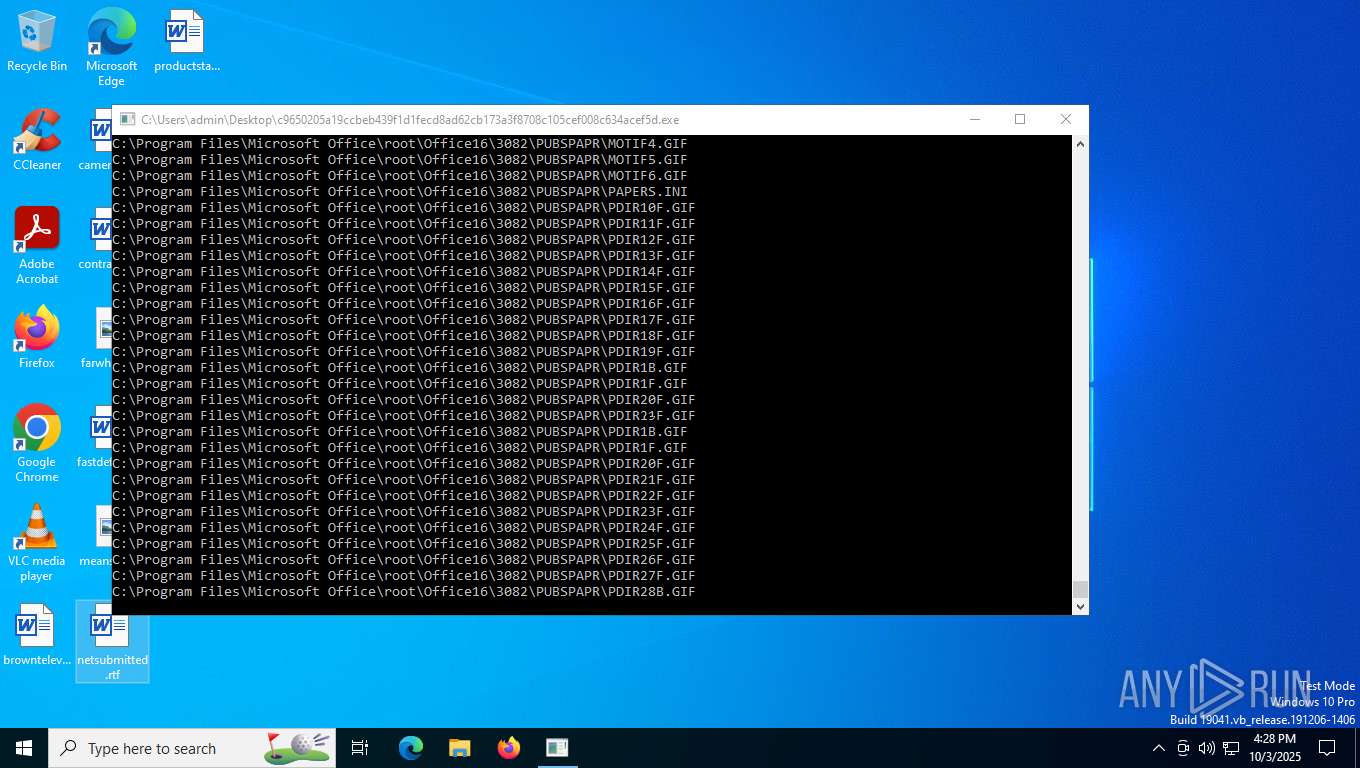
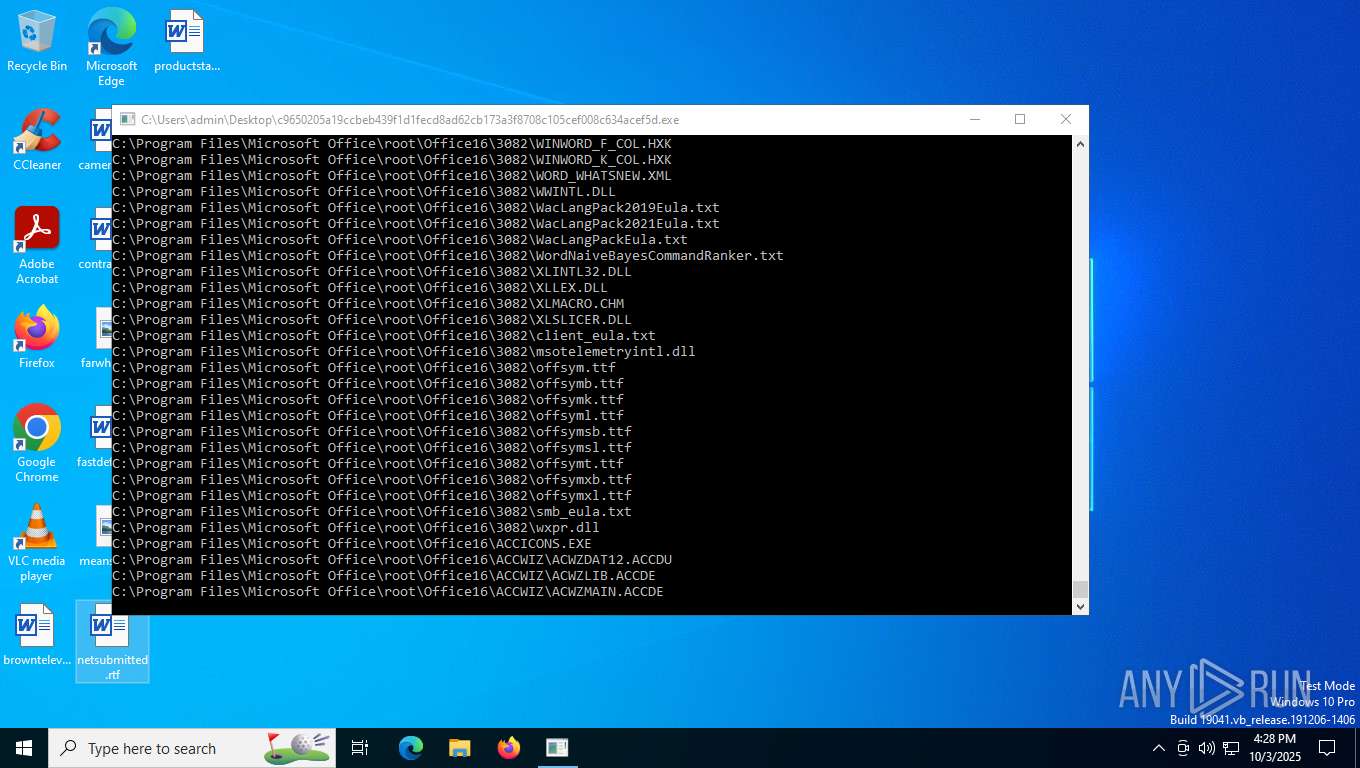
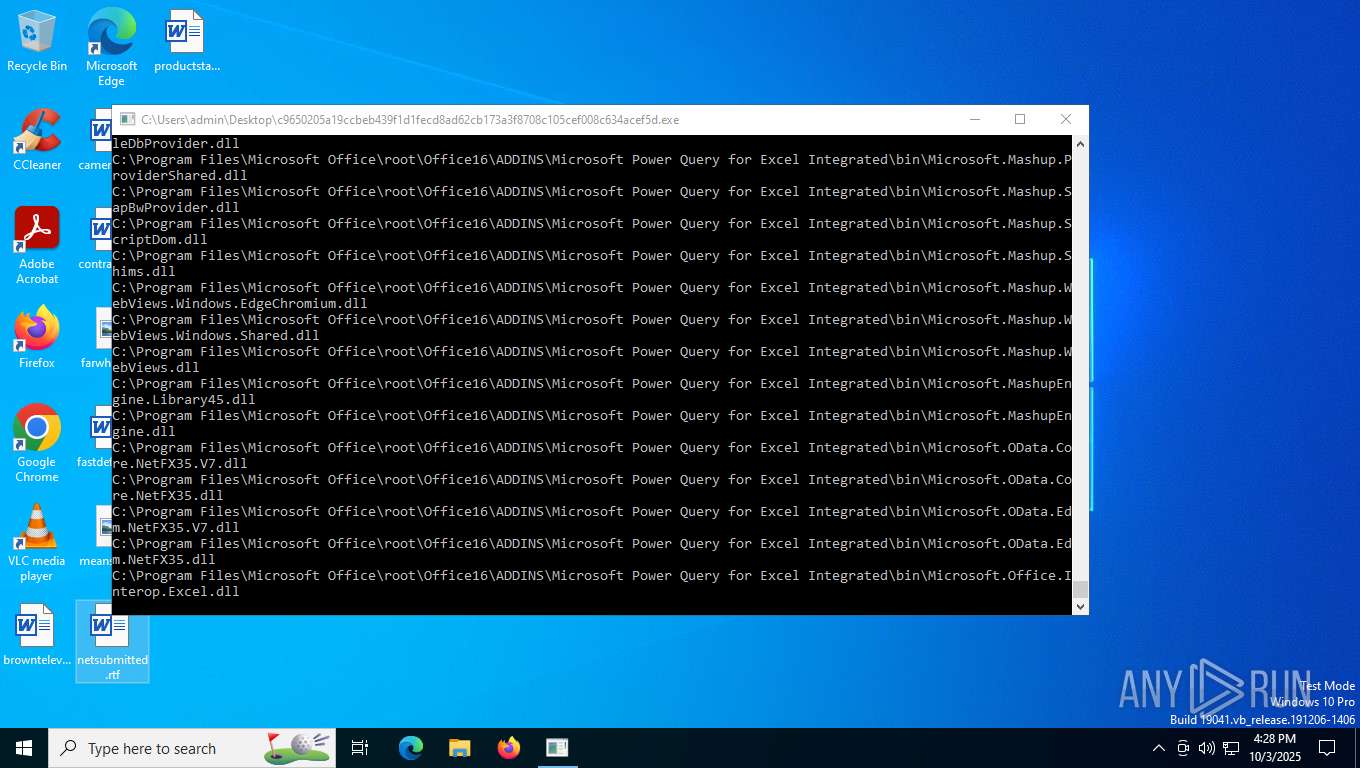
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppvIsvSubsystems64_arm64x.dll | executable | |
MD5:CA4B234DE63DB13F9DDE8B1EB25B175F | SHA256:8507C69781ECA884EF1BC693698D2ED3CDD4BA3E5A79C79C4E60974D6EFBCC91 | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppVIsvSubsystems64_msix.dll | executable | |
MD5:09F5C2B521EBCC7053D3B7F89C29BD49 | SHA256:1DEB5B848860BA2BD232D5CC4294432EA64CD25A9218FC4D1D8C25421982BA7D | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\C2RINTL.ar-sa.dll | executable | |
MD5:559D579A4B6165DF573A31011E74E19D | SHA256:7E8C001091FC75B28059AD25BD833CB9C79CA401EBC47938B83B4043075F0ABB | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppVScripting.dll | executable | |
MD5:DB7382ECFE39AE5853706295B6A4846B | SHA256:276E2CE8527500D511D77D1A2840156B8F139E8A61BDCC3AAAA4C6E8866FED7F | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppVClientIsv.man | executable | |
MD5:53E7DB60DC1856DA42398EE99AFF5E4E | SHA256:F89820927C557BC74632E006A5C481CD0CE14E6182692EB14B73CD7C905712AA | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppVShNotify.exe | executable | |
MD5:B1C19913A2396634BBDDF7AD31A507A8 | SHA256:9FE338AC711E24360201FBBDB2CD1D4DFF6B92AF9C64422BECCF33BEBDF23D80 | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppVClient.man | executable | |
MD5:30AA080983E3C2F97FC6B260464DB635 | SHA256:4732D6DF2C7BEDE6F99B35C0065109921EF7438BCCBF9F5625EFE6D28DCB9A1F | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppvIsvSubsystems32_msix.dll | executable | |
MD5:25D49E63B6EC7BBD638814DA01D7591D | SHA256:61ABA1D4CB2CD9DCCDBACF8FDDA576A44885D0D1A6F2C07699B65F3C9335E06A | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppvIsvSubsystems32.dll | executable | |
MD5:9F862844D38D238026324A3E71A640FC | SHA256:C20A20FB3F628CE79FBB58BDCEBEA8CA81F104D357A7623CB5CAF169DB8F8E6D | |||
| 756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | C:\Program Files\Common Files\microsoft shared\ClickToRun\AppvIsvSubsystems64.dll | executable | |
MD5:F9833C32D5CDEE22C24B1CBFAB576072 | SHA256:52E0584A63CC59F87B8678228B36925B44C54DF2E00971B42A3BF52DEEE54805 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | POST | 500 | 4.154.209.85:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | unknown |
— | — | POST | 500 | 4.154.209.85:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
— | — | 92.123.104.52:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
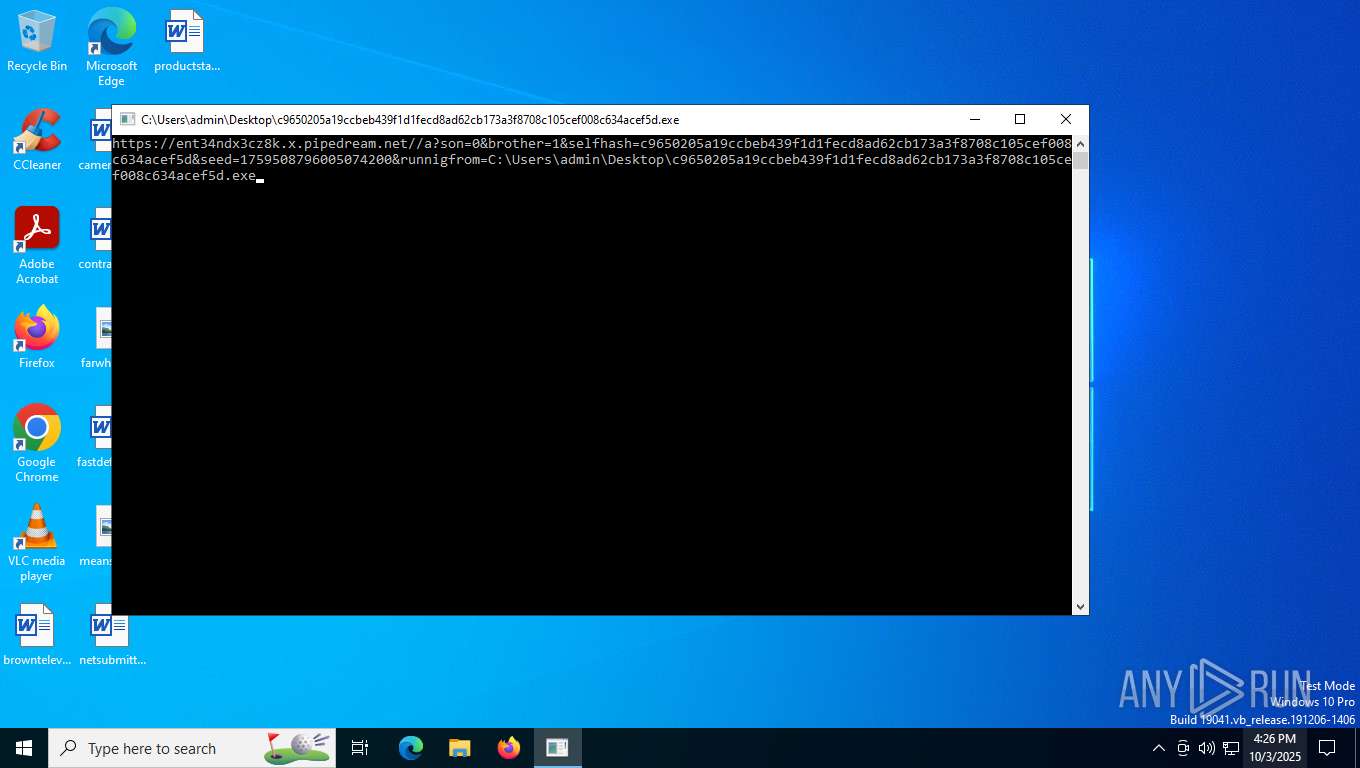
756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | 198.51.100.1:443 | ent34ndx3cz8k.x.pipedream.net | — | — | whitelisted |
3848 | slui.exe | 4.154.185.43:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
2652 | slui.exe | 4.154.185.43:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
ent34ndx3cz8k.x.pipedream.net |
| unknown |
EvlXFW.b17da333ec194ec4b767.d.requestbin.net |
| unknown |
soHFIBPq.b17da333ec194ec4b767.d.requestbin.net |
| unknown |
t.b17da333ec194ec4b767.d.requestbin.net |
| unknown |
stdEvN.b17da333ec194ec4b767.d.requestbin.net |
| unknown |
MTwl.b17da333ec194ec4b767.d.requestbin.net |
| unknown |
activation-v2.sls.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
756 | c9650205a19ccbeb439f1d1fecd8ad62cb173a3f8708c105cef008c634acef5d.exe | Misc activity | ET INFO Webhook/HTTP Request Inspection Service Domain (x .pipedream .net in TLS SNI) |
2428 | svchost.exe | Misc activity | ET INFO DNS Query for Webhook/HTTP Request Inspection Service (x .pipedream .net) |
2428 | svchost.exe | Misc activity | ET INFO DNSBin Demo (requestbin .net) - Data Exfil |