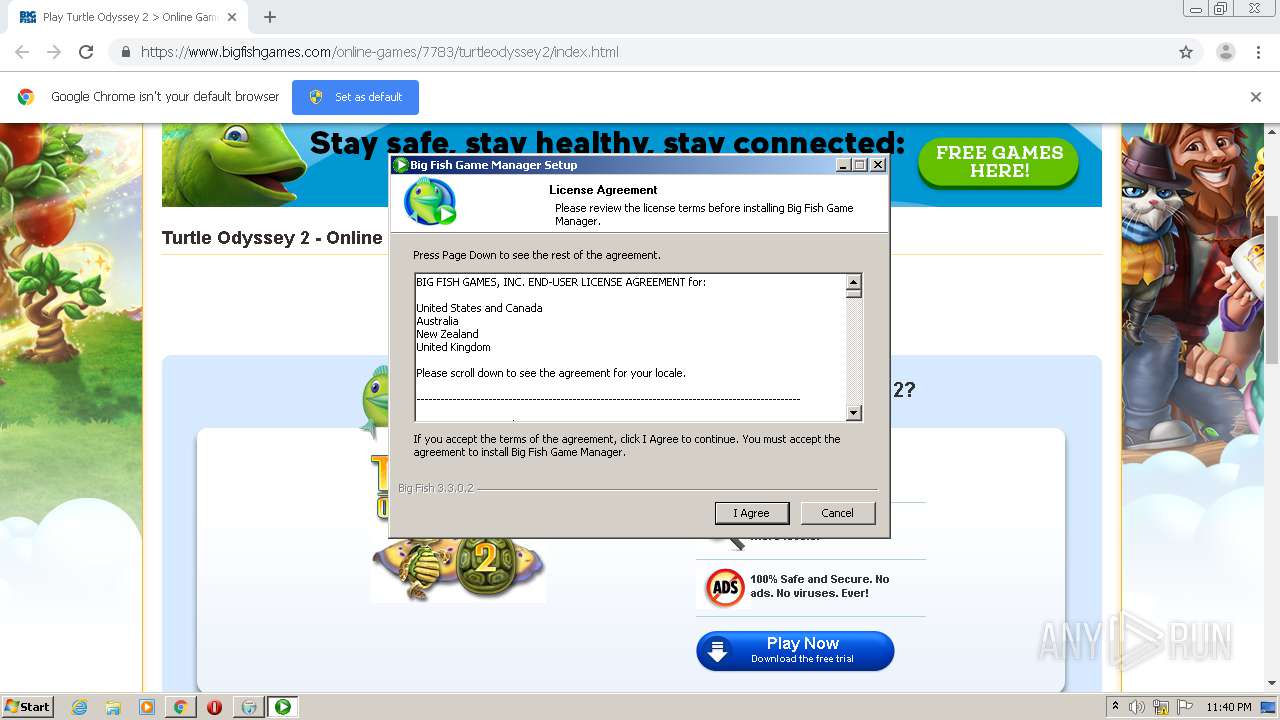
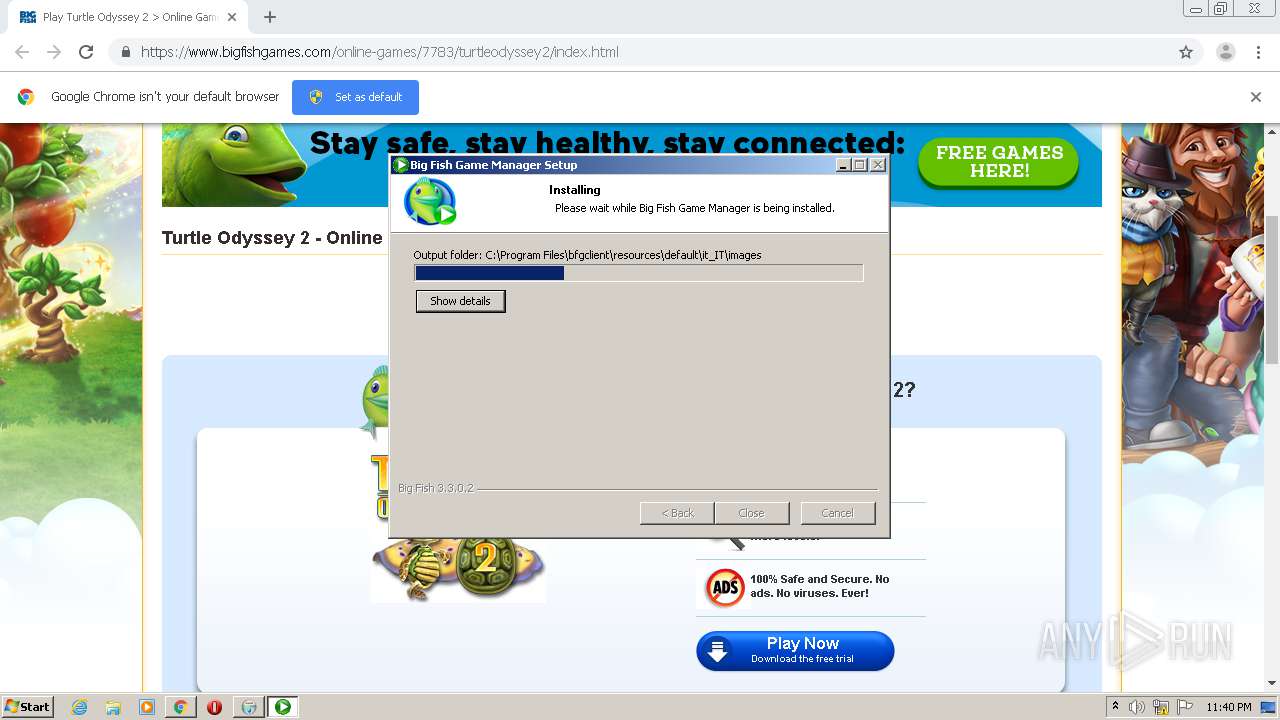
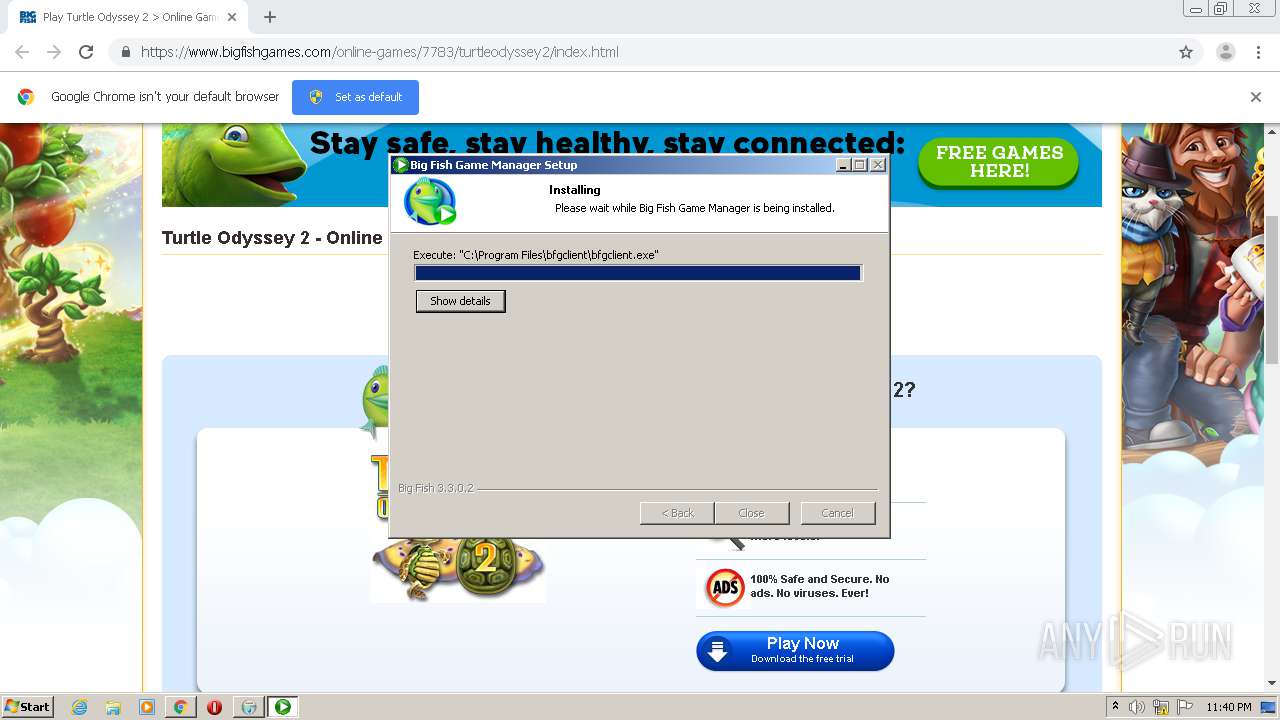
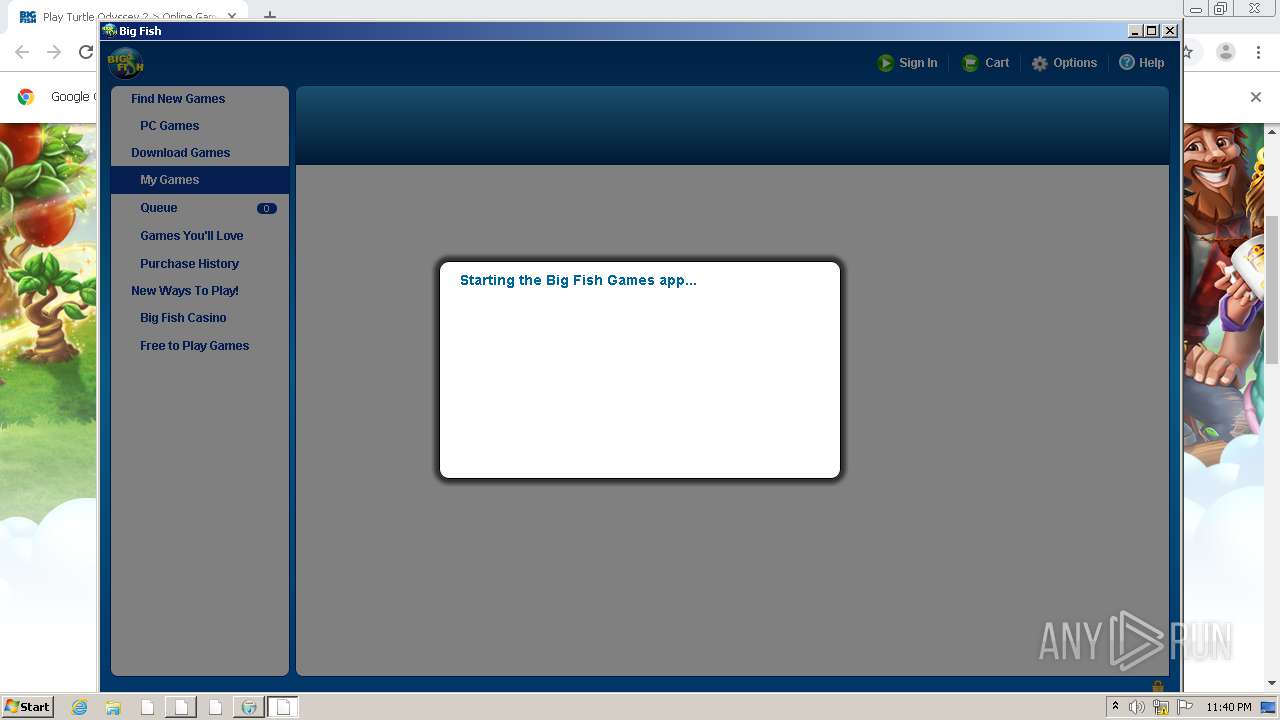
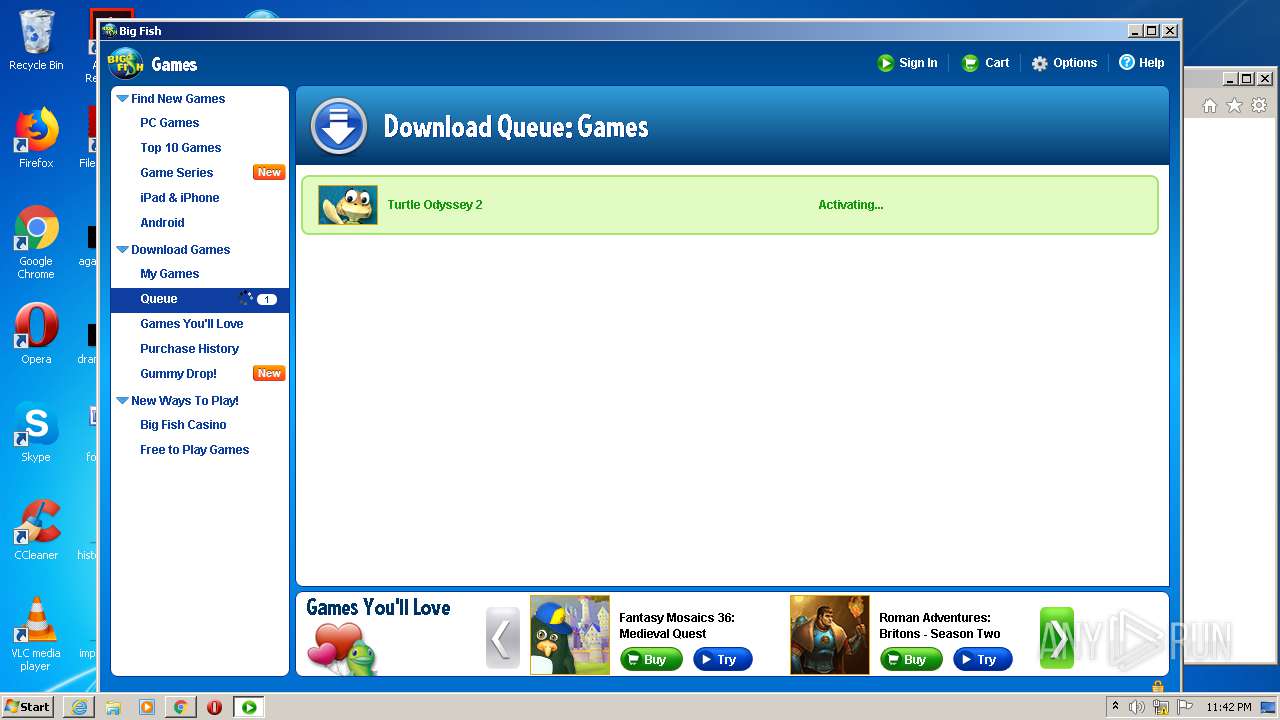
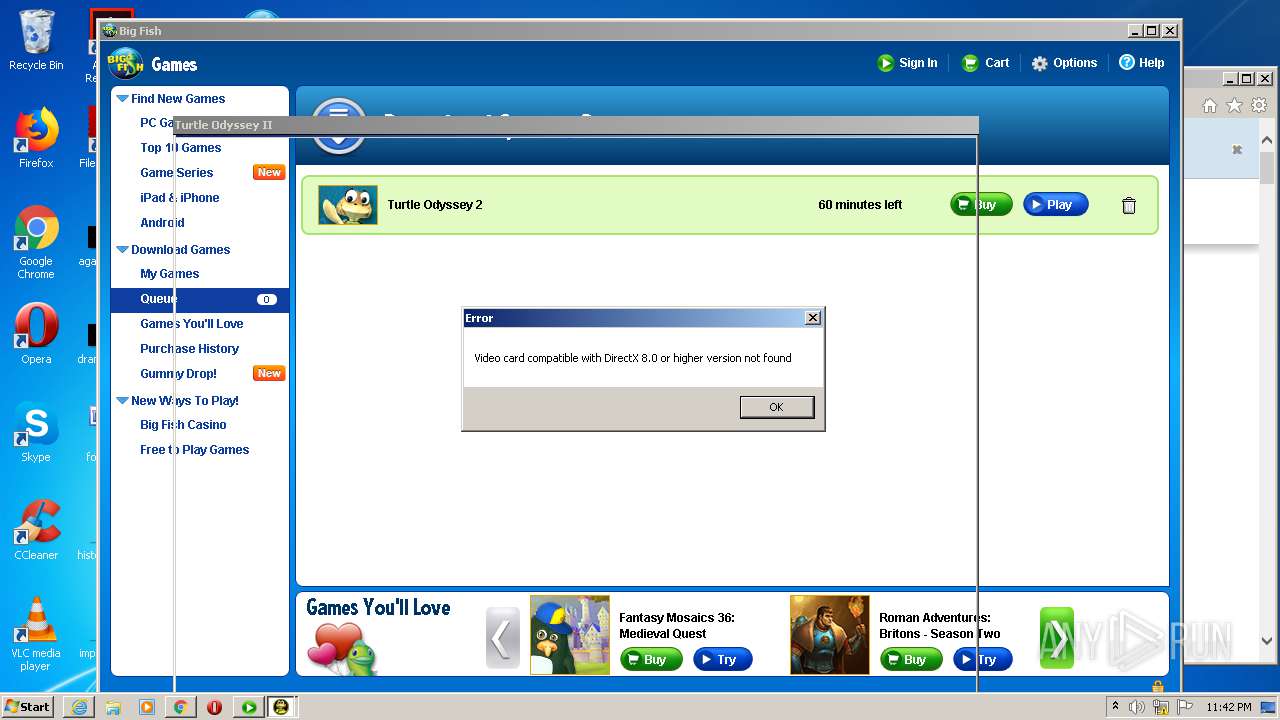
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
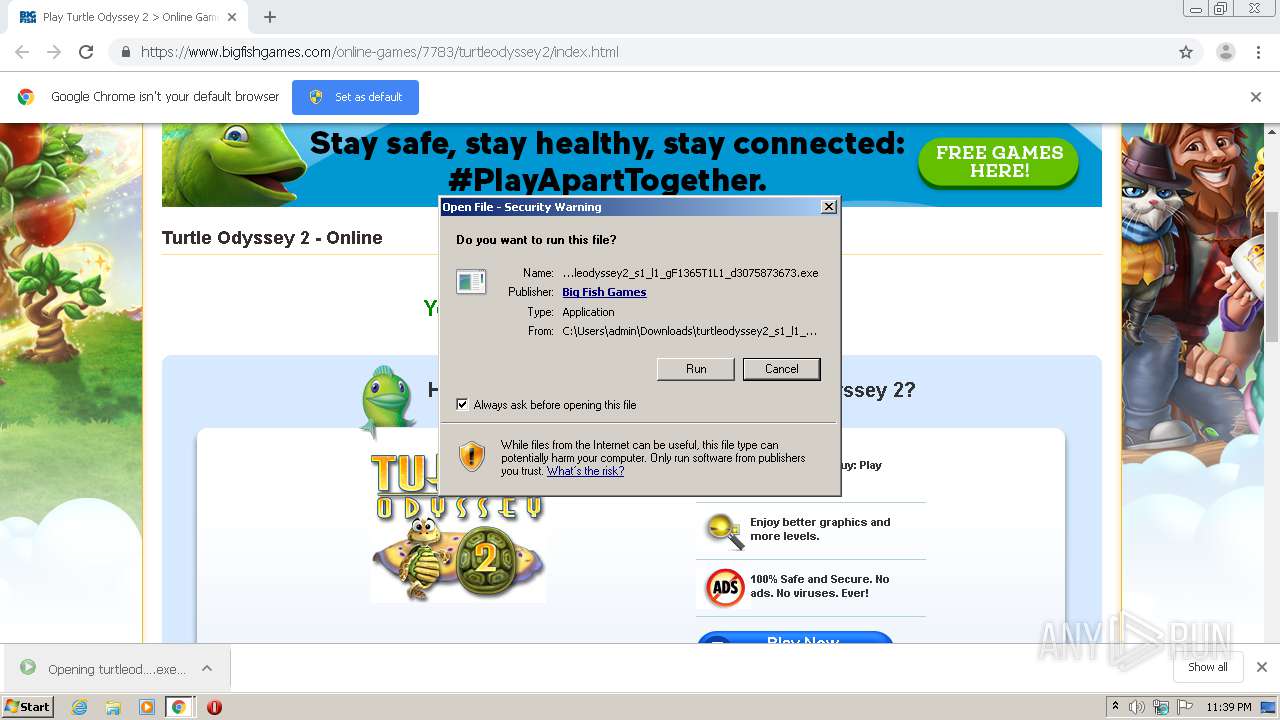
| URL: | https://www.bigfishgames.com/online-games/7783/turtleodyssey2/index.html |
| Full analysis: | https://app.any.run/tasks/80fde6df-74e2-4a93-b725-9e76f0740df4 |
| Verdict: | Malicious activity |
| Threats: | Adware is a form of malware that targets users with unwanted advertisements, often disrupting their browsing experience. It typically infiltrates systems through software bundling, malicious websites, or deceptive downloads. Once installed, it may track user activity, collect sensitive data, and display intrusive ads, including pop-ups or banners. Some advanced adware variants can bypass security measures and establish persistence on devices, making removal challenging. Additionally, adware can create vulnerabilities that other malware can exploit, posing a significant risk to user privacy and system security. |
| Analysis date: | June 09, 2020, 22:38:30 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 650033D671B7292A3B36706D9422B9DE |
| SHA1: | 0DA06638FEAEB53592DACD2E39A11940239281B3 |
| SHA256: | BAA96846F7951992BFC5BD202AB05C209989A0D29AB98337954A0593631911DB |
| SSDEEP: | 3:N8DSLs4NSsL5hAWJZjRCKML65G:2OLs4EsLDTtCKXG |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 276 | "C:\Program Files\bfgclient\bfggameservices.exe" | C:\Program Files\bfgclient\bfggameservices.exe | bfgclient.exe | ||||||||||||
User: admin Integrity Level: HIGH Description: Big Fish Games: Game Services Application Exit code: 0 Version: 3.3.0.2 Modules
| |||||||||||||||
| 572 | "C:\Program Files\bfgclient\bfgclient.exe" -u | C:\Program Files\bfgclient\bfgclient.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Description: Big Fish: Game Manager Application Exit code: 0 Version: 3.3.0.2 Modules
| |||||||||||||||
| 760 | "C:\Program Files\Google\Chrome\Application\chrome.exe" "https://www.bigfishgames.com/online-games/7783/turtleodyssey2/index.html" | C:\Program Files\Google\Chrome\Application\chrome.exe | explorer.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
| 824 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --field-trial-handle=1020,12524004998646490451,14273510568170639986,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=utility --service-request-channel-token=1978108086926911999 --mojo-platform-channel-handle=4604 --ignored=" --type=renderer " /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
| 852 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=crashpad-handler "--user-data-dir=C:\Users\admin\AppData\Local\Google\Chrome\User Data" /prefetch:7 --monitor-self-annotation=ptype=crashpad-handler "--database=C:\Users\admin\AppData\Local\Google\Chrome\User Data\Crashpad" "--metrics-dir=C:\Users\admin\AppData\Local\Google\Chrome\User Data" --url=https://clients2.google.com/cr/report --annotation=channel= --annotation=plat=Win32 --annotation=prod=Chrome --annotation=ver=75.0.3770.100 --initial-client-data=0x7c,0x80,0x84,0x78,0x88,0x6f5ba9d0,0x6f5ba9e0,0x6f5ba9ec | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
| 884 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=gpu-process --field-trial-handle=1020,12524004998646490451,14273510568170639986,131072 --enable-features=PasswordImport --disable-gpu-sandbox --use-gl=disabled --gpu-preferences=KAAAAAAAAADgAAAgAQAAAAAAAAAAAGAAAAAAAAAAAAAIAAAAAAAAACgAAAAEAAAAIAAAAAAAAAAoAAAAAAAAADAAAAAAAAAAOAAAAAAAAAAQAAAAAAAAAAAAAAAFAAAAEAAAAAAAAAAAAAAABgAAABAAAAAAAAAAAQAAAAUAAAAQAAAAAAAAAAEAAAAGAAAA --service-request-channel-token=15938915019532329765 --mojo-platform-channel-handle=4824 /prefetch:2 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
| 916 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --field-trial-handle=1020,12524004998646490451,14273510568170639986,131072 --enable-features=PasswordImport --disable-gpu-compositing --lang=en-US --extension-process --enable-offline-auto-reload --enable-offline-auto-reload-visible-only --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --service-request-channel-token=16573729800734085819 --renderer-client-id=25 --no-v8-untrusted-code-mitigations --mojo-platform-channel-handle=4468 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
| 1168 | "C:\Program Files\Turtle Odyssey 2\Turtle Odyssey 2.exe" | C:\Program Files\Turtle Odyssey 2\Turtle Odyssey 2.exe | — | Turtle Odyssey 2.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 0 Modules
| |||||||||||||||
| 1220 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --field-trial-handle=1020,12524004998646490451,14273510568170639986,131072 --enable-features=PasswordImport --disable-gpu-compositing --lang=en-US --enable-offline-auto-reload --enable-offline-auto-reload-visible-only --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --service-request-channel-token=18069888485076251508 --renderer-client-id=10 --no-v8-untrusted-code-mitigations --mojo-platform-channel-handle=3840 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 75.0.3770.100 Modules
| |||||||||||||||
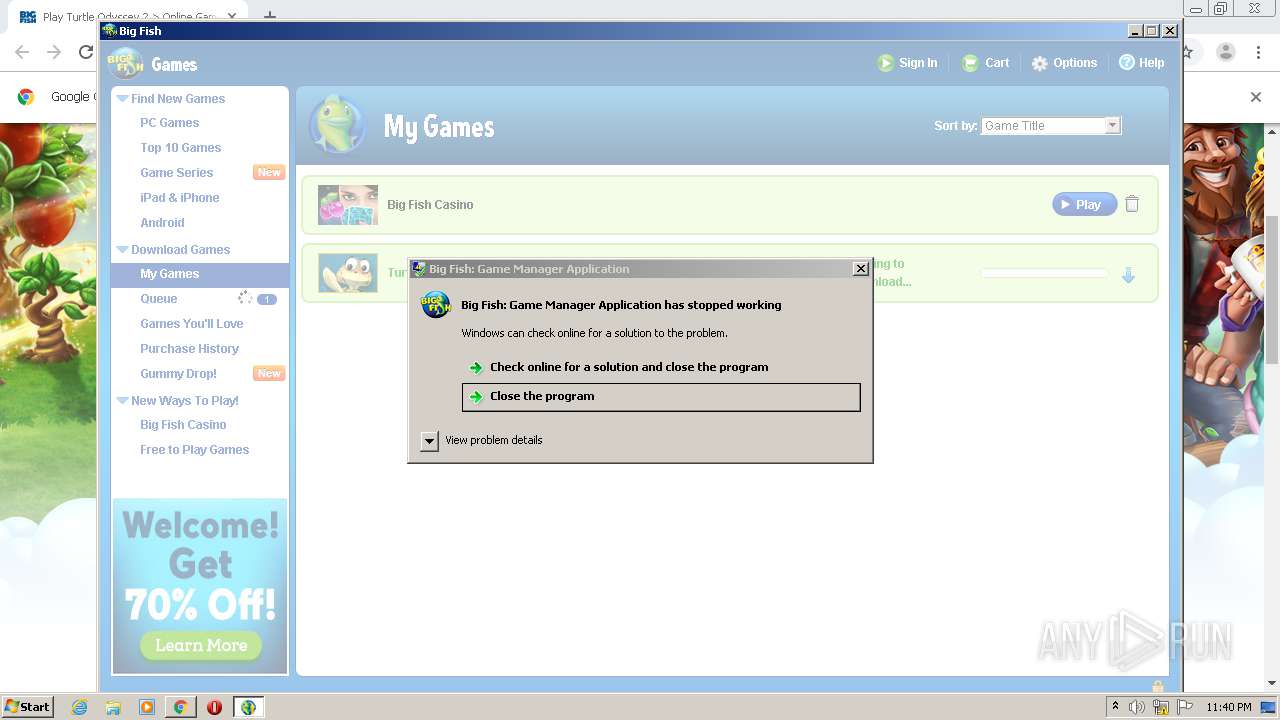
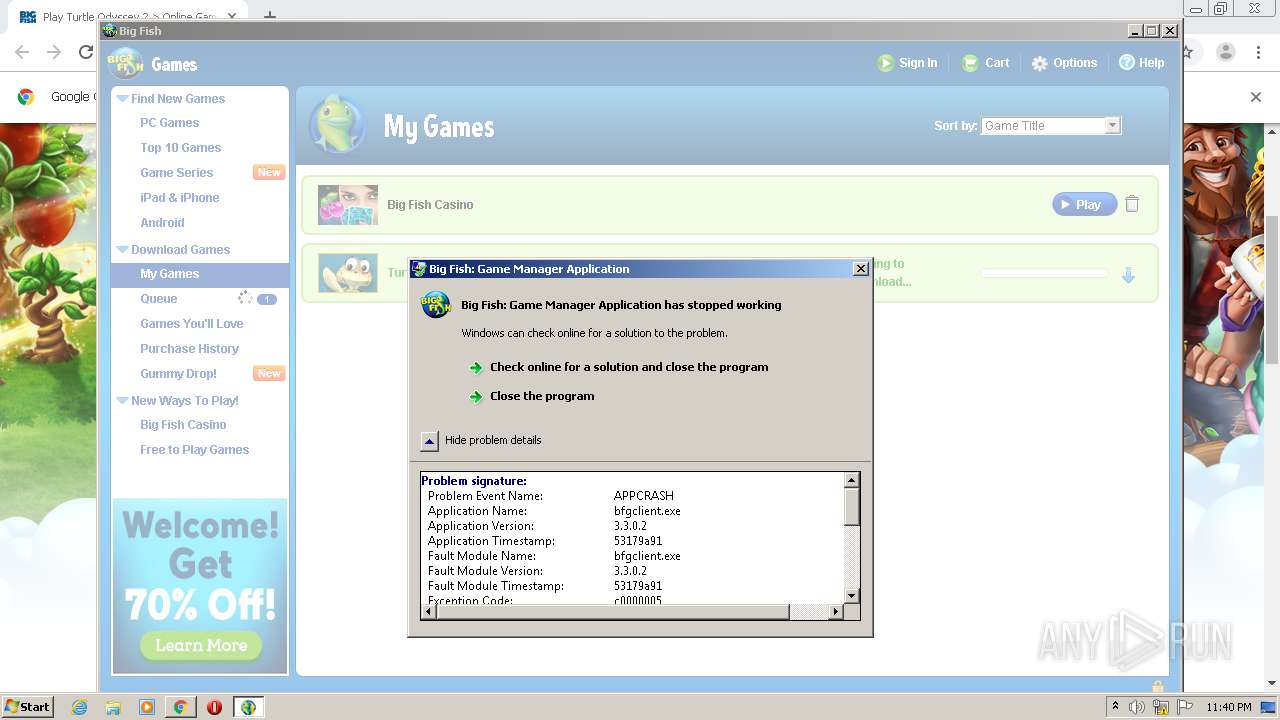
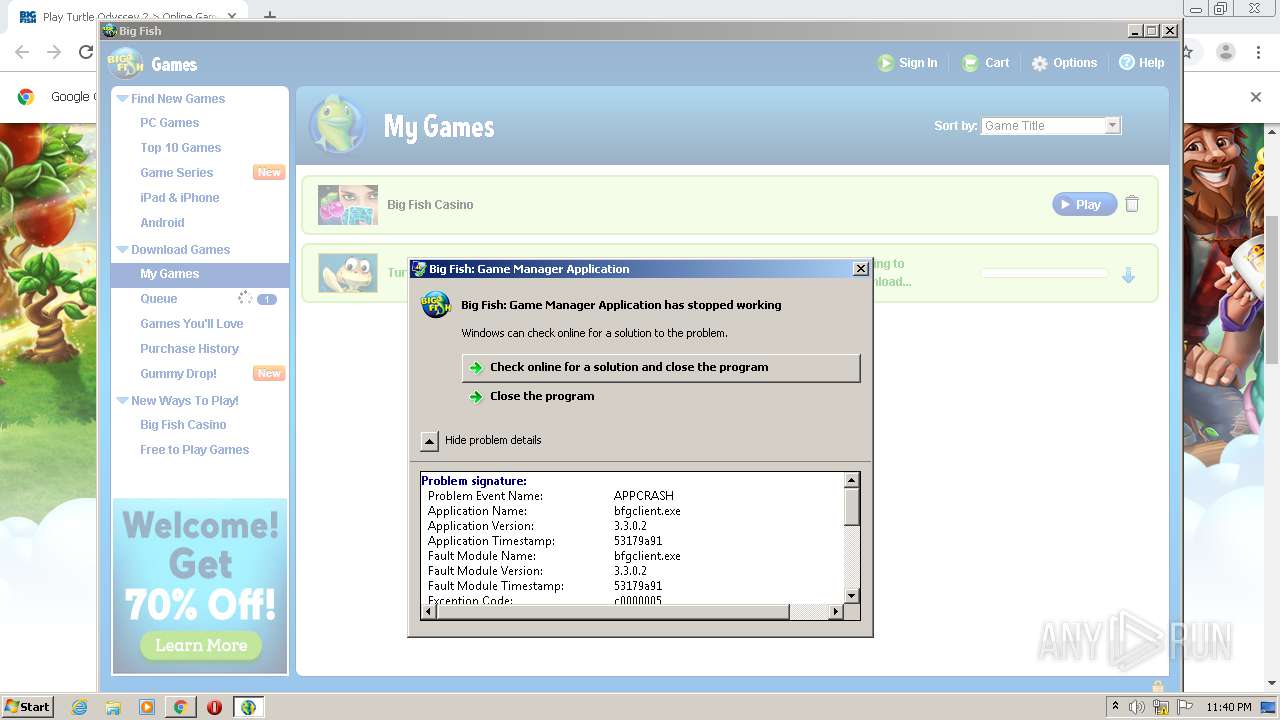
| 1456 | "C:\Program Files\bfgclient\bfgclient.exe" --type=renderer --no-sandbox --user-agent=BFGBrowser_Windows --lang --log-file="C:\BigFishCache/GameManager/log/cefLog.txt" --log-severity=disable --channel="572.0.962157814\518699400" /prefetch:3 | C:\Program Files\bfgclient\bfgclient.exe | — | bfgclient.exe | |||||||||||
User: admin Integrity Level: MEDIUM Description: Big Fish: Game Manager Application Exit code: 0 Version: 3.3.0.2 Modules
| |||||||||||||||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: 01000000 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (2204) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BrowserExitCodes |
| Operation: | write | Name: | 760-13236215924442750 |
Value: 259 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Update\ClientState\{8A69D345-D564-463c-AFF1-A69D9E530F96} |
| Operation: | write | Name: | dr |
Value: 1 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome |
| Operation: | write | Name: | UsageStatsInSample |
Value: 0 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BrowserExitCodes |
| Operation: | delete value | Name: | 3120-13213713943555664 |
Value: 0 | |||
| (PID) Process: | (760) chrome.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Google\Update\ClientStateMedium\{8A69D345-D564-463C-AFF1-A69D9E530F96} |
| Operation: | write | Name: | usagestats |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\BrowserMetrics\BrowserMetrics-5EE00F75-2F8.pma | — | |
MD5:— | SHA256:— | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\9e2bd5e9-955a-4985-b760-cd9fd6e80192.tmp | — | |
MD5:— | SHA256:— | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\data_reduction_proxy_leveldb\000028.dbtmp | — | |
MD5:— | SHA256:— | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Data\LevelDB\LOG.old | text | |
MD5:DA692BE42E4EF2668AE7499A7D5DA720 | SHA256:EB865CAF59002C092F5FDBE22D01935866BC1277108B29E897052CB2439630ED | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Platform Notifications\LOG.old | — | |
MD5:— | SHA256:— | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Site Characteristics Database\LOG.old~RF15cd1d.TMP | text | |
MD5:F69C20D5B552B8D973FB1CBA5FDD7D87 | SHA256:48799968D50E2D74E625A0AB18E93C6792AF20010334C6BB4E935C8D26F7026A | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\data_reduction_proxy_leveldb\LOG.old | text | |
MD5:33B05E8AC9C178C58ED3321F496588C0 | SHA256:2CDF6A09638A0B563EA2672D6926210771902E0A9203FE15D2857FC4EB954CDE | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Data\LevelDB\LOG.old~RF15cd1d.TMP | text | |
MD5:DA692BE42E4EF2668AE7499A7D5DA720 | SHA256:EB865CAF59002C092F5FDBE22D01935866BC1277108B29E897052CB2439630ED | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\shared_proto_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 760 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\shared_proto_db\LOG.old~RF15cf5f.TMP | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
4080 | chrome.exe | GET | 302 | 172.217.21.238:80 | http://redirector.gvt1.com/edgedl/chromewebstore/L2Nocm9tZV9leHRlbnNpb24vYmxvYnMvOTRmQUFXVHlhaGJaUTdMLWtCSkNJUl9ZQQ/1.0.0.5_nmmhkkegccagdldgiimedpiccmgmieda.crx | US | html | 520 b | whitelisted |
4080 | chrome.exe | GET | 200 | 173.194.182.167:80 | http://r2---sn-hpa7zns6.gvt1.com/edgedl/chromewebstore/L2Nocm9tZV9leHRlbnNpb24vYmxvYnMvOTRmQUFXVHlhaGJaUTdMLWtCSkNJUl9ZQQ/1.0.0.5_nmmhkkegccagdldgiimedpiccmgmieda.crx?cms_redirect=yes&mh=QJ&mip=185.128.27.133&mm=28&mn=sn-hpa7zns6&ms=nvh&mt=1591742235&mv=m&mvi=1&pl=24&shardbypass=yes | US | crx | 293 Kb | whitelisted |
4080 | chrome.exe | GET | 200 | 208.77.152.139:80 | http://downloads.bigfishgames.com/turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe?gameWID=F1365T1L1&downloadID=3075873673&siteID=1&langID=1&type=gminstaller | US | executable | 232 Kb | malicious |
4080 | chrome.exe | GET | 302 | 172.217.21.238:80 | http://redirector.gvt1.com/edgedl/chromewebstore/L2Nocm9tZV9leHRlbnNpb24vYmxvYnMvY2Y1QUFXUjZlVjI5UldyLVpDTFJFcEx6QQ/7719.805.0.2_pkedcjkdefgpdelpbcmbmeomcjbeemfm.crx | US | html | 525 b | whitelisted |
3036 | turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe | GET | 200 | 2.16.186.32:80 | http://cdn-games.bigfishsites.com/gm_32/gm_content_32/installThrottle.json?t=C:\Users\admin\AppData\Local\Temp\nswA0EB.tmp | unknown | text | 6 b | whitelisted |
2296 | turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe | GET | 200 | 2.16.186.32:80 | http://cdn-games.bigfishsites.com/gm_32/gm_installers/currentInstallers/Windows/bfginstaller32.exe | unknown | executable | 32.8 Mb | whitelisted |
4080 | chrome.exe | GET | 200 | 173.194.160.218:80 | http://r4---sn-hpa7zn7d.gvt1.com/edgedl/chromewebstore/L2Nocm9tZV9leHRlbnNpb24vYmxvYnMvY2Y1QUFXUjZlVjI5UldyLVpDTFJFcEx6QQ/7719.805.0.2_pkedcjkdefgpdelpbcmbmeomcjbeemfm.crx?cms_redirect=yes&mh=Nf&mip=185.128.27.133&mm=28&mn=sn-hpa7zn7d&ms=nvh&mt=1591742235&mv=m&mvi=3&pl=24&shardbypass=yes | US | crx | 823 Kb | whitelisted |
3204 | bfgclient.exe | GET | 200 | 2.16.186.16:80 | http://cdn-games.bigfishsites.com/gm_32/gm_content_32/LiveLoadScript/liveLoadScript.js?_=1591742423941 | unknown | text | 6.71 Kb | whitelisted |
3204 | bfgclient.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAVG%2Fhgj9%2BGUHaOfzhTEYXM%3D | US | der | 471 b | whitelisted |
2296 | turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe | GET | 200 | 208.77.152.139:80 | http://downloads.bigfishgames.com/tracking.php?track_msg=eyJJREVOVElGSUVSIjoiMzA3NTg3MzY3MyIsICJJREVOVElGSUVSX1RZUEUiOiJET1dOTE9BRElEIiwgIkNVUlJFTlRfU0lURUlEIjoiIiwgIkNVUlJFTlRfTEFOR1VBR0VJRCI6IiIsICJTVFVCX0xBTkdVQUdFSUQiOiIxIiwgIlNUVUJfU0lURUlEIjoiMSIsICJDT1VOVEVSIjoiMCIsIlVQR1JBREVTT1VSQ0UiOiJET1dOTE9BRCIsICJWRVJTSU9OX1RPIjoiMy4zLjAuMiIsICJWRVJTSU9OX0ZST00iOiIwLjAuMC4wIiwgIk9TTkFNRSI6IldJTl83IiwgIk9TVkVSU0lPTiI6IjYuMS43NjAxLjE3OTMyIiwgIklOU1RBTExBVElPTl9TVEFUVVMiOiJTVUNDRVNTIiwiRVJST1JfTEVWRUwiOiIwIn0= | US | text | 2 b | malicious |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4080 | chrome.exe | 172.217.16.173:443 | accounts.google.com | Google Inc. | US | whitelisted |
4080 | chrome.exe | 172.217.22.3:443 | clientservices.googleapis.com | Google Inc. | US | whitelisted |
4080 | chrome.exe | 2.16.186.33:443 | bigfishassets-a.akamaihd.net | Akamai International B.V. | — | whitelisted |
4080 | chrome.exe | 2.16.186.10:443 | bigfishthemes-a.akamaihd.net | Akamai International B.V. | — | whitelisted |
4080 | chrome.exe | 216.58.212.174:443 | www.google-analytics.com | Google Inc. | US | whitelisted |
4080 | chrome.exe | 2.16.186.35:443 | bigfishgames-a.akamaihd.net | Akamai International B.V. | — | whitelisted |
4080 | chrome.exe | 173.194.76.154:443 | stats.g.doubleclick.net | Google Inc. | US | whitelisted |
4080 | chrome.exe | 172.217.18.174:443 | clients1.google.com | Google Inc. | US | whitelisted |
4080 | chrome.exe | 152.199.23.241:443 | tags.tiqcdn.com | MCI Communications Services, Inc. d/b/a Verizon Business | US | suspicious |
4080 | chrome.exe | 2.18.232.23:443 | assets.adobedtm.com | Akamai International B.V. | — | whitelisted |
Domain | IP | Reputation |
|---|---|---|
clientservices.googleapis.com |
| whitelisted |
www.bigfishgames.com |
| malicious |
accounts.google.com |
| shared |
bigfishassets-a.akamaihd.net |
| whitelisted |
bigfishthemes-a.akamaihd.net |
| whitelisted |
www.google-analytics.com |
| whitelisted |
ssl.google-analytics.com |
| whitelisted |
bigfishgames-a.akamaihd.net |
| whitelisted |
clients1.google.com |
| whitelisted |
stats.g.doubleclick.net |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
4080 | chrome.exe | Potential Corporate Privacy Violation | ET POLICY PE EXE or DLL Windows file download HTTP |
4080 | chrome.exe | Misc activity | ET INFO EXE - Served Attached HTTP |
2296 | turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe | Misc activity | ADWARE [PTsecurity] PUA:Win32/Conduit |
2296 | turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe | Potential Corporate Privacy Violation | ET POLICY PE EXE or DLL Windows file download HTTP |
572 | bfgclient.exe | Potential Corporate Privacy Violation | ET POLICY PE EXE or DLL Windows file download HTTP |
Process | Message |
|---|---|
bfgclient.exe |
================================================================================
|
bfgclient.exe | PERF::06/09/2020 23:40:19.945::CLIENT_INIT::3.3.0.2
|
bfgclient.exe | INFO::06/09/2020 23:40:23.739::INFO_MESSAGE::Stub message received.
|
bfgclient.exe | INFO::06/09/2020 23:40:23.744::INFO_MESSAGE::l=1::s=1::z=C:\Users\admin\Downloads\turtleodyssey2_s1_l1_gF1365T1L1_d3075873673.exe
|
bfgclient.exe | PERF::06/09/2020 23:40:24.102::STARTUP_FROM_UI
|
bfgclient.exe | PERF::06/09/2020 23:40:24.153::URLS_SENT
|
bfgclient.exe | PERF::06/09/2020 23:40:24.268::OPTIONS_SENT
|
bfgclient.exe | PERF::06/09/2020 23:40:24.323::USER_DATA_SENT
|
bfgclient.exe | PERF::06/09/2020 23:40:24.481::GAME_UPDATE_REQUEST_BEGIN
|
bfgclient.exe | INFO::06/09/2020 23:40:24.532::INFO_MESSAGE::Stub message received.
|