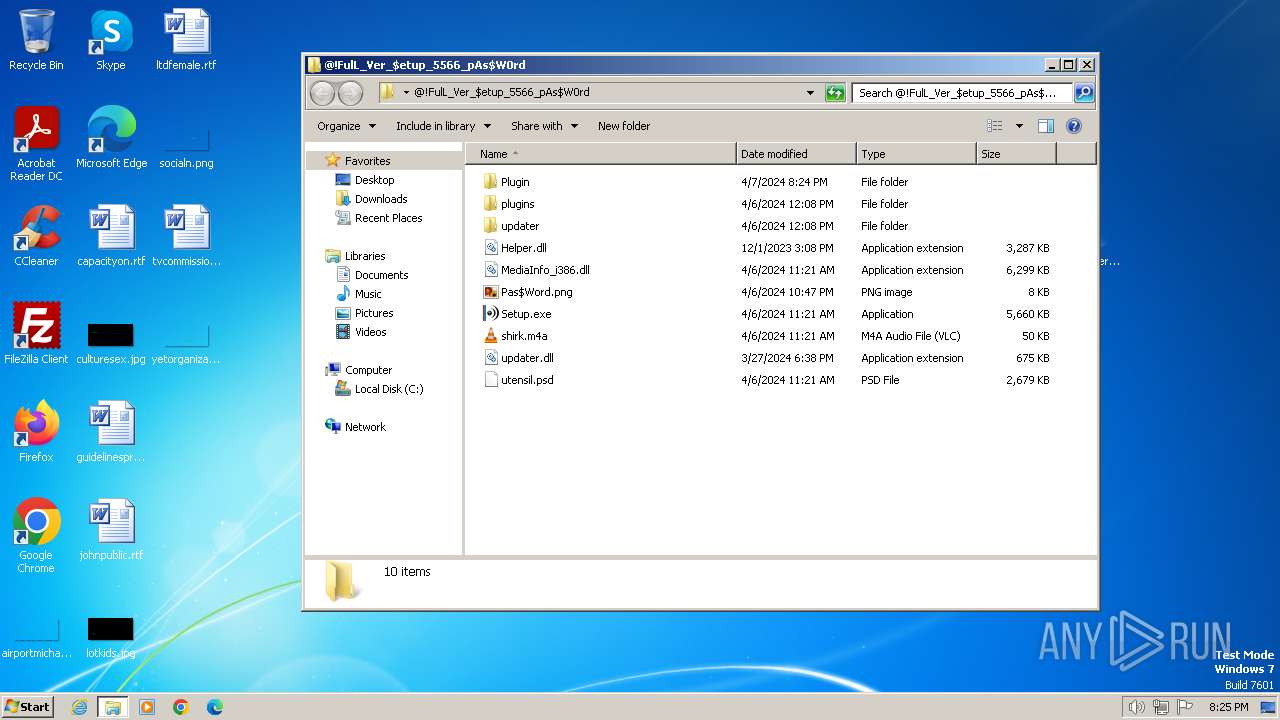
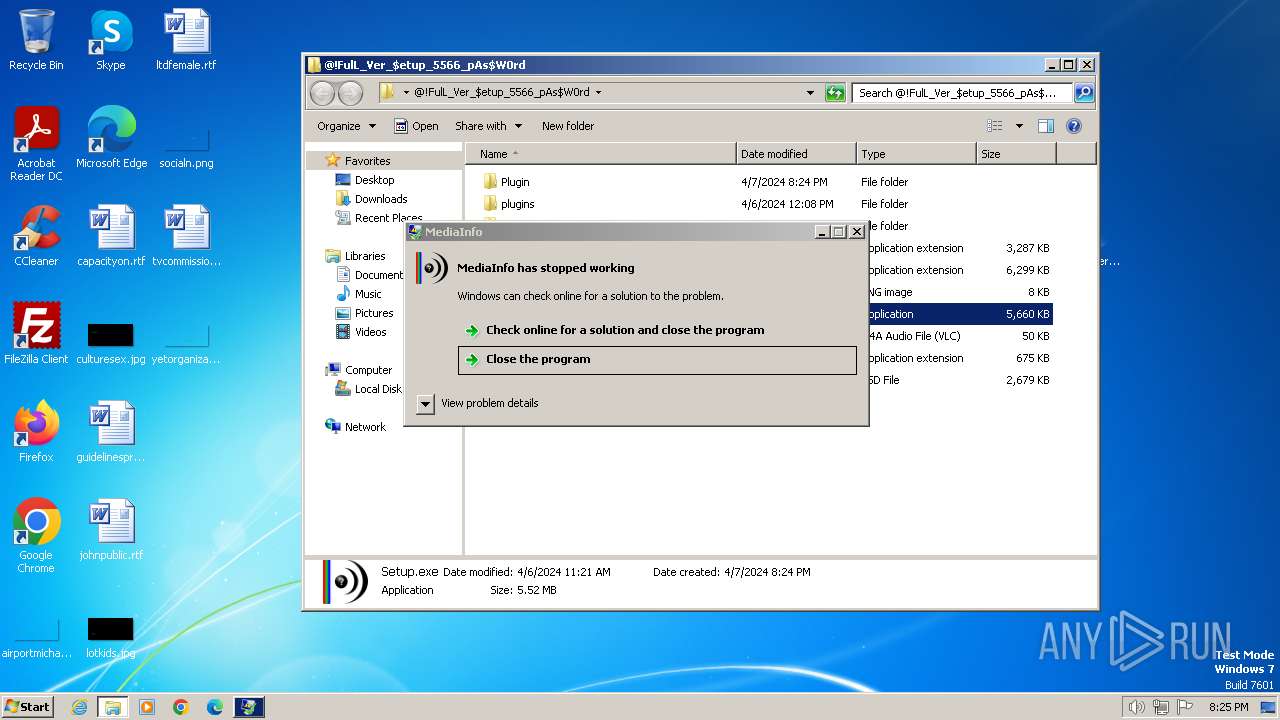
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
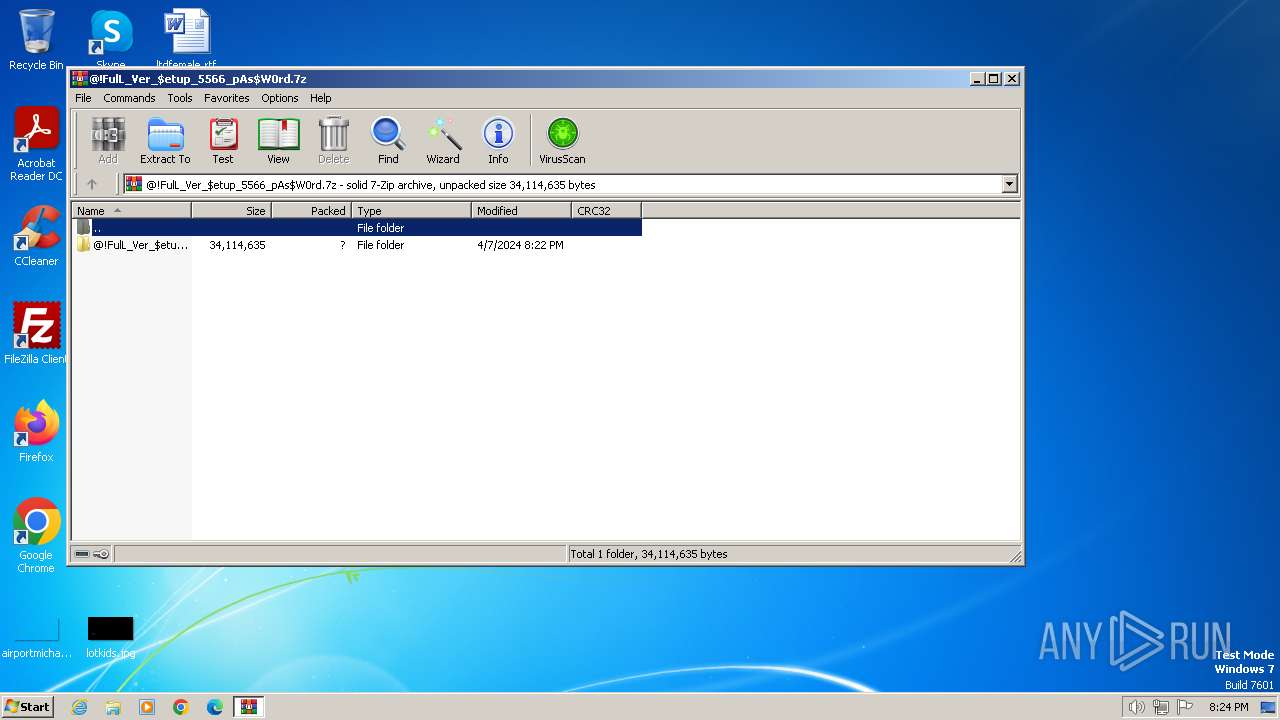
| File name: | @!FulL_Ver_$etup_5566_pAs$W0rd.7z |
| Full analysis: | https://app.any.run/tasks/ed2a98df-70f8-4aae-a393-43f560439979 |
| Verdict: | Malicious activity |
| Threats: | HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses. |
| Analysis date: | April 07, 2024, 19:24:24 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-7z-compressed |
| File info: | 7-zip archive data, version 0.4 |
| MD5: | 820E3E90C1158609FF259C8E4411BC90 |
| SHA1: | FD4002E63B305C33B788CB311570017A19DEA63C |
| SHA256: | A70576520A46CA740AAB3BA83AB919EBC94D1550EFD2FDB9A2DC9D5E12D9B62C |
| SSDEEP: | 98304:vUjaWTdCajOe3xw+hdB0a2HeqJr0DAlhhnb+sjs1UchJjk8vTs7ujEkKBFgJnM/M:g5PpftcR7vZmreqy+QOFIcuCWw |
| .7z | | | 7-Zip compressed archive (v0.4) (57.1) |
|---|---|---|
| .7z | | | 7-Zip compressed archive (gen) (42.8) |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
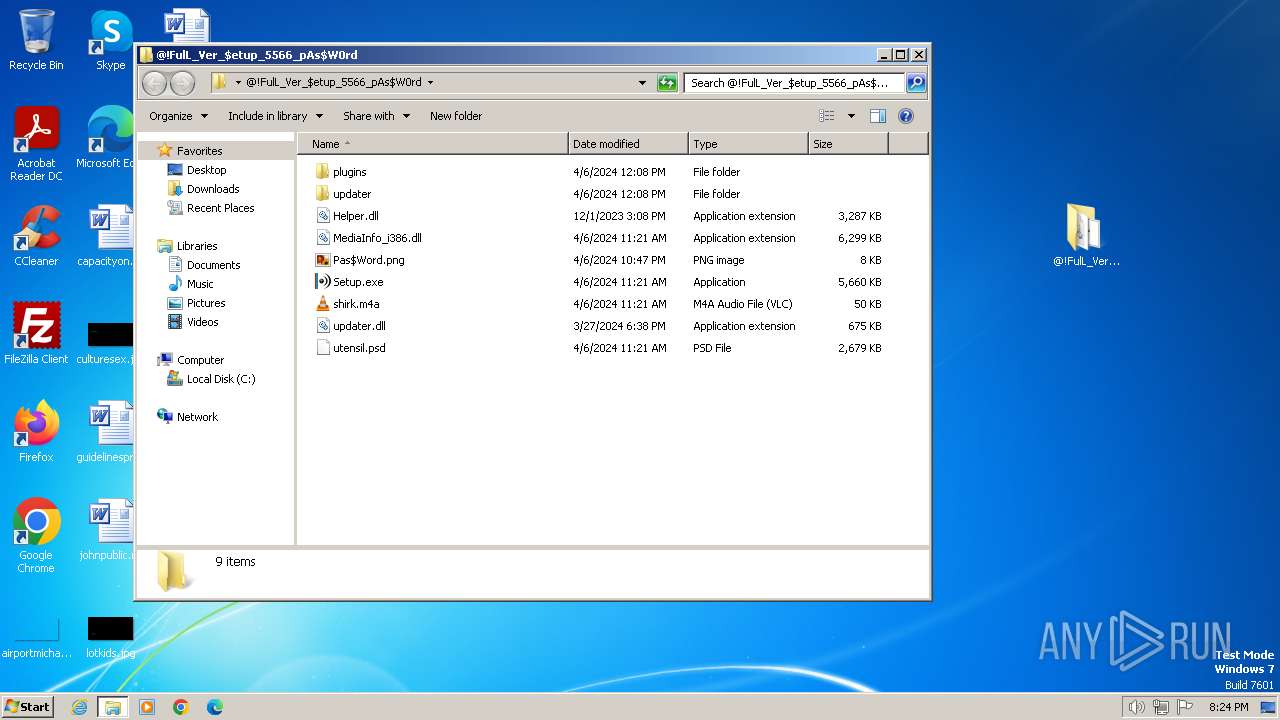
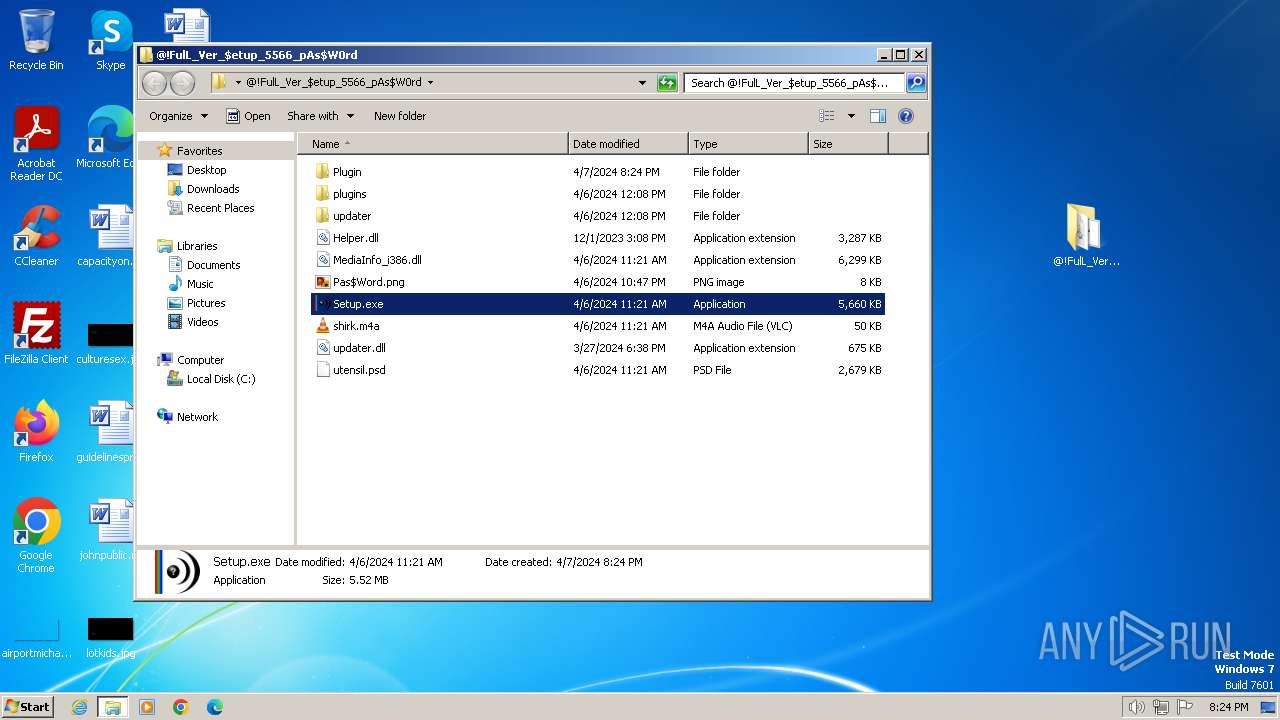
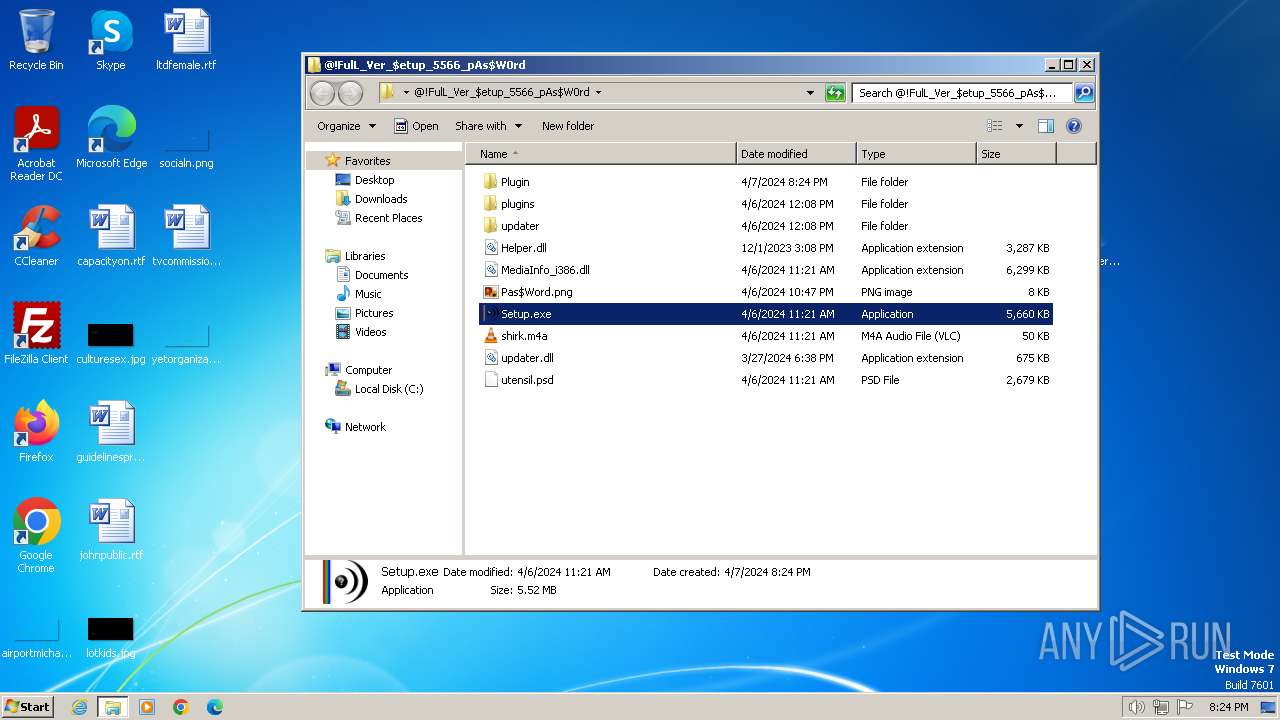
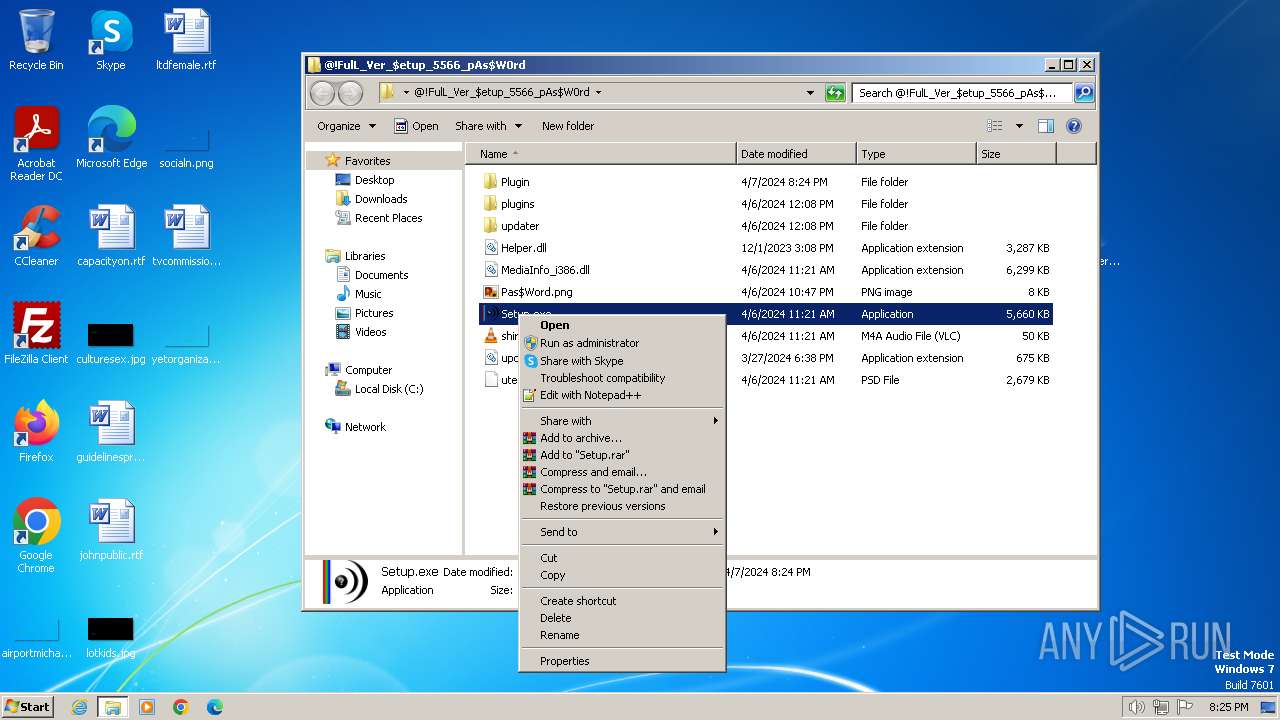
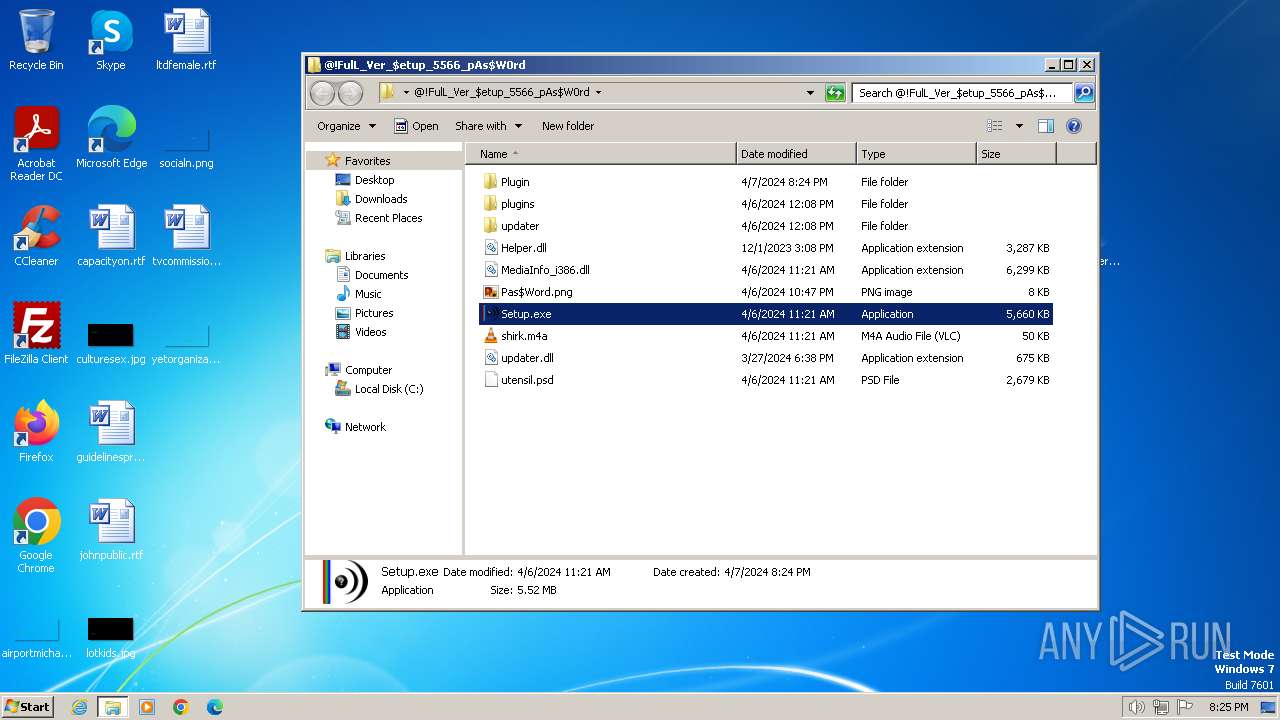
| 1336 | "C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe" | C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe | explorer.exe | ||||||||||||
User: admin Company: MediaArea.net Integrity Level: HIGH Description: MediaInfo Version: 24.03.0.0 Modules
| |||||||||||||||
| 1836 | "C:\Program Files\WinRAR\WinRAR.exe" "C:\Users\admin\AppData\Local\Temp\@!FulL_Ver_$etup_5566_pAs$W0rd.7z" | C:\Program Files\WinRAR\WinRAR.exe | — | explorer.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.91.0 Modules
| |||||||||||||||
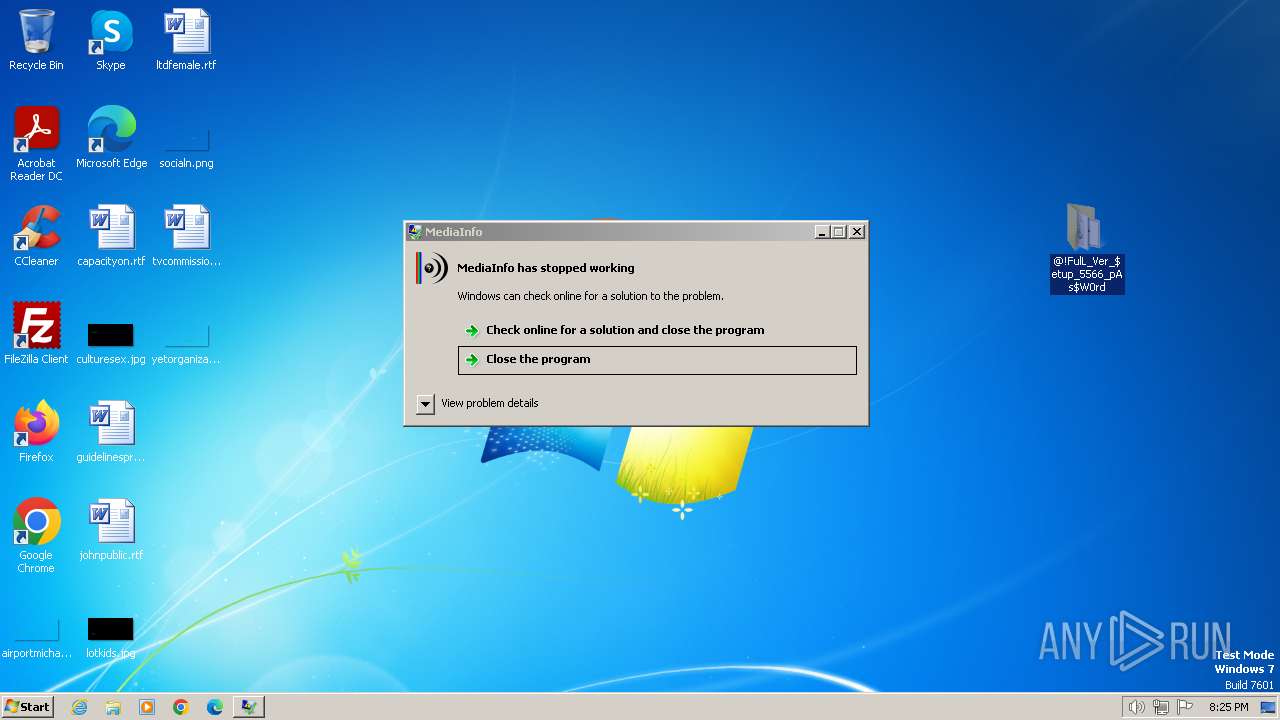
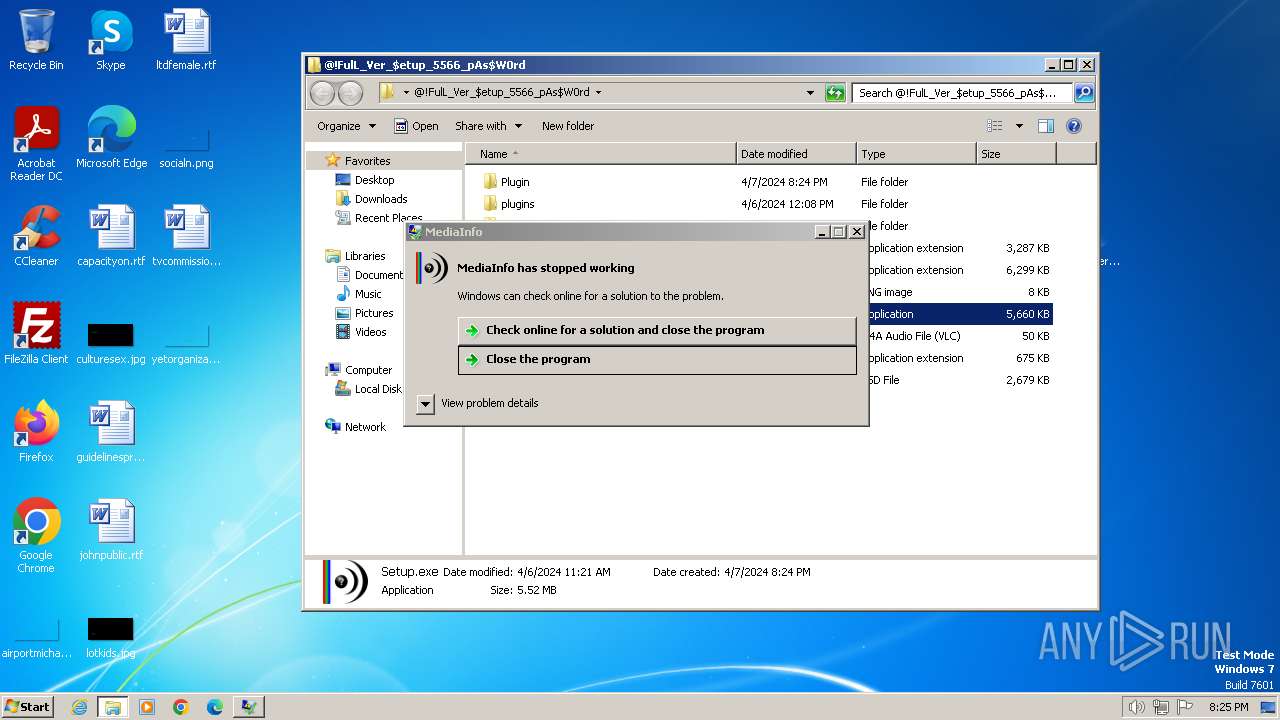
| 1976 | "C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe" | C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe | explorer.exe | ||||||||||||
User: admin Company: MediaArea.net Integrity Level: MEDIUM Description: MediaInfo Exit code: 3221225502 Version: 24.03.0.0 Modules
| |||||||||||||||
| 3488 | "C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe" | C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Setup.exe | explorer.exe | ||||||||||||
User: admin Company: MediaArea.net Integrity Level: MEDIUM Description: MediaInfo Exit code: 3221225502 Version: 24.03.0.0 Modules
| |||||||||||||||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\182\52C64B7E |
| Operation: | write | Name: | LanguageList |
Value: en-US | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\phacker.zip | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\Win7-KB3191566-x86.zip | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\curl-8.5.0_1-win32-mingw.zip | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\@!FulL_Ver_$etup_5566_pAs$W0rd.7z | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (1836) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\Pas$Word.png | image | |
MD5:C39B8CA4C54626D56A92ECEF26AF60E4 | SHA256:27C50281B1C0D57E1DD121DEF9B13CE8AF919F0672B505BAE8A1788BC6417041 | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\updater\nativeLang.xml | xml | |
MD5:E624E7D4BEA38DE2F1FC9C4E6D98AABD | SHA256:B02BF73815217FBE1FACC3690E2EBDD34B3A4170C9DBAEF699387854DBCB6F6E | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\updater\gup.xml | xml | |
MD5:ABDE55A0B1CB4A904E622C02F559DCD1 | SHA256:92717951AAE89E960B142CEF3D273F104051896A3D527A78CA4A88C22B5216A5 | |||
| 3488 | Setup.exe | C:\Users\admin\Desktop\@!FulL_Ver_$etup_5566_pAs$W0rd\Plugin\Tree\Example.csv | — | |
MD5:— | SHA256:— | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\utensil.psd | binary | |
MD5:66F4685D9859FAA5E5950BC639D79AE6 | SHA256:26301D3807B1B6C1C7E3FBA0E3A1548085F8C3ECA57362098A7595280614EBF2 | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\updater\GUP | executable | |
MD5:1884DD352C2B8DF7E7EE80573AF580AC | SHA256:F22A7438A2226321324A81926BB311C25377CE977A32C84064D29E932FA22598 | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\shirk.m4a | binary | |
MD5:F1D1448403A0D5FF0BD83E849633CDA6 | SHA256:65A8742EF84099B7B1B44D86B6B16B985CD070D0B1F722063B9B47A6909E63D9 | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\updater\README.md | text | |
MD5:BD0CD75D784913DED2152CD7A182853E | SHA256:0E7418F89CE1CAD3B24D37F2B599CDF0B9D2E9A2A401D00E2FB9579E900160C8 | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\MediaInfo_i386.dll | executable | |
MD5:FF47C873FE084F8CFC97ED0CB4645FF8 | SHA256:622E9F27884A00ECCF9F7E3D923887745E78BA962F54FCD150A3D3CE8C8A170A | |||
| 1836 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa1836.36798\@!FulL_Ver_$etup_5566_pAs$W0rd\plugins\Config\nppPluginList.dll | executable | |
MD5:B65FDDDD07B2CAC6FBE48B965A7F3F10 | SHA256:9FF8DBEB2D3CA17CD543621464F37B3D9B78B7D9194E83294E9D06624FABB7BF | |||
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 224.0.0.252:5355 | — | — | — | unknown |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |