ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | a5c1c0eb16016e22e2df4c09e91929d0f1aa4dc55c4e3d3f6d1b33918589eb5a.zip |
| Full analysis: | https://app.any.run/tasks/b196e527-3a54-4dd8-a90b-dd8c0a015f4f |
| Verdict: | Malicious activity |
| Threats: | A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools. |
| Analysis date: | August 01, 2025, 05:36:22 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v2.0 to extract, compression method=deflate |
| MD5: | 08C5F7DE76B6ADAA973ADE0FD97E9027 |
| SHA1: | A2DAE2B8A0C2B6EBB777D5C028617F0C0B30CD99 |
| SHA256: | A5C1C0EB16016E22E2DF4C09E91929D0F1AA4DC55C4E3D3F6D1B33918589EB5A |
| SSDEEP: | 12288:LgM7QCD80J2X2HYx+dqOm6wi4l/Zd1pYDG131lHMn:LgM7F4W2X+Yx776wtl/f1p331lsn |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | Deflated |
| ZipModifyDate: | 2025:07:31 20:59:02 |
| ZipCRC: | 0x3063530a |
| ZipCompressedSize: | 463256 |
| ZipUncompressedSize: | 550920 |
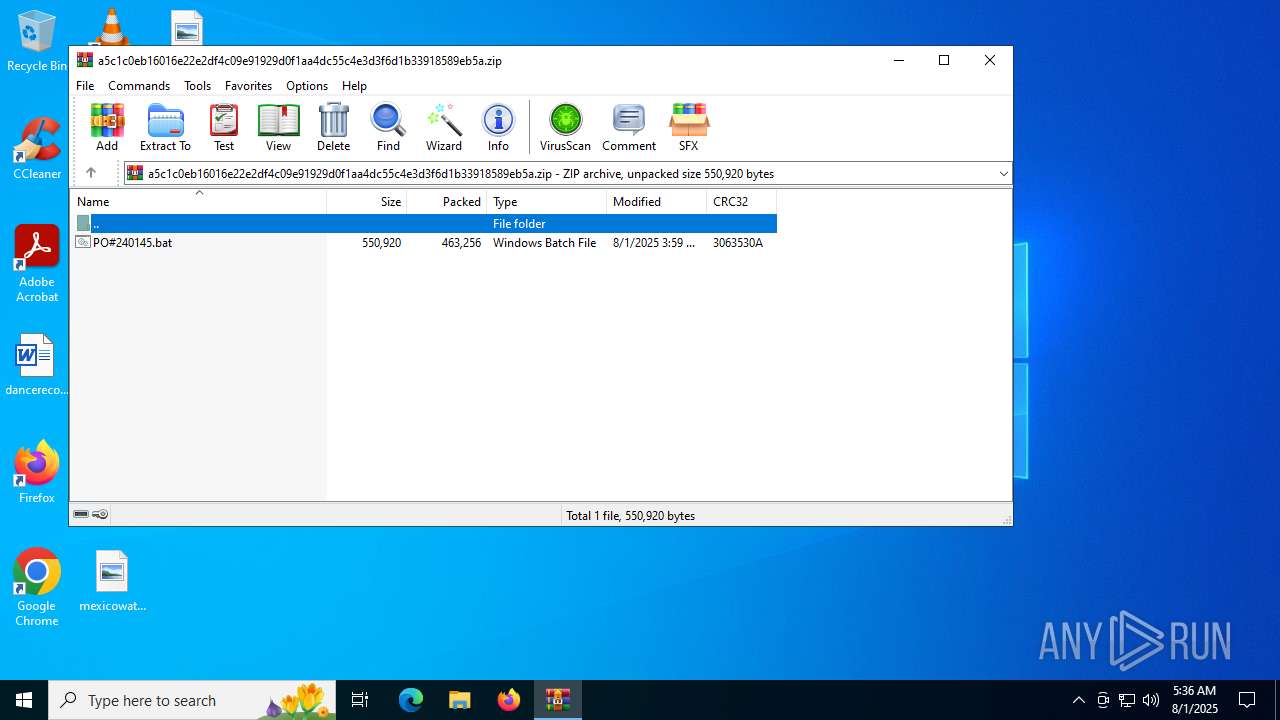
| ZipFileName: | PO#240145.bat |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 72 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 504 | "C:\Users\admin\Desktop\PO#240145.bat" | C:\Users\admin\Desktop\PO#240145.bat | explorer.exe | ||||||||||||
User: admin Company: 晶彩遊戲工作室 Integrity Level: MEDIUM Description: 三鍵反應遊戲 Exit code: 0 Version: 0.0.0.0 Modules
| |||||||||||||||
| 1156 | "C:\Users\admin\AppData\Roaming\FSEUWuGde.exe" | C:\Users\admin\AppData\Roaming\FSEUWuGde.exe | FSEUWuGde.exe | ||||||||||||
User: admin Company: 晶彩遊戲工作室 Integrity Level: MEDIUM Description: 三鍵反應遊戲 Version: 0.0.0.0 Modules
| |||||||||||||||
| 2200 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2384 | "C:\Users\admin\Desktop\PO#240145.bat" | C:\Users\admin\Desktop\PO#240145.bat | PO#240145.bat | ||||||||||||
User: admin Company: 晶彩遊戲工作室 Integrity Level: MEDIUM Description: 三鍵反應遊戲 Version: 0.0.0.0 Modules
| |||||||||||||||
| 3896 | "C:\Windows\System32\schtasks.exe" /Create /TN "Updates\FSEUWuGde" /XML "C:\Users\admin\AppData\Local\Temp\tmp749A.tmp" | C:\Windows\SysWOW64\schtasks.exe | — | FSEUWuGde.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Task Scheduler Configuration Tool Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
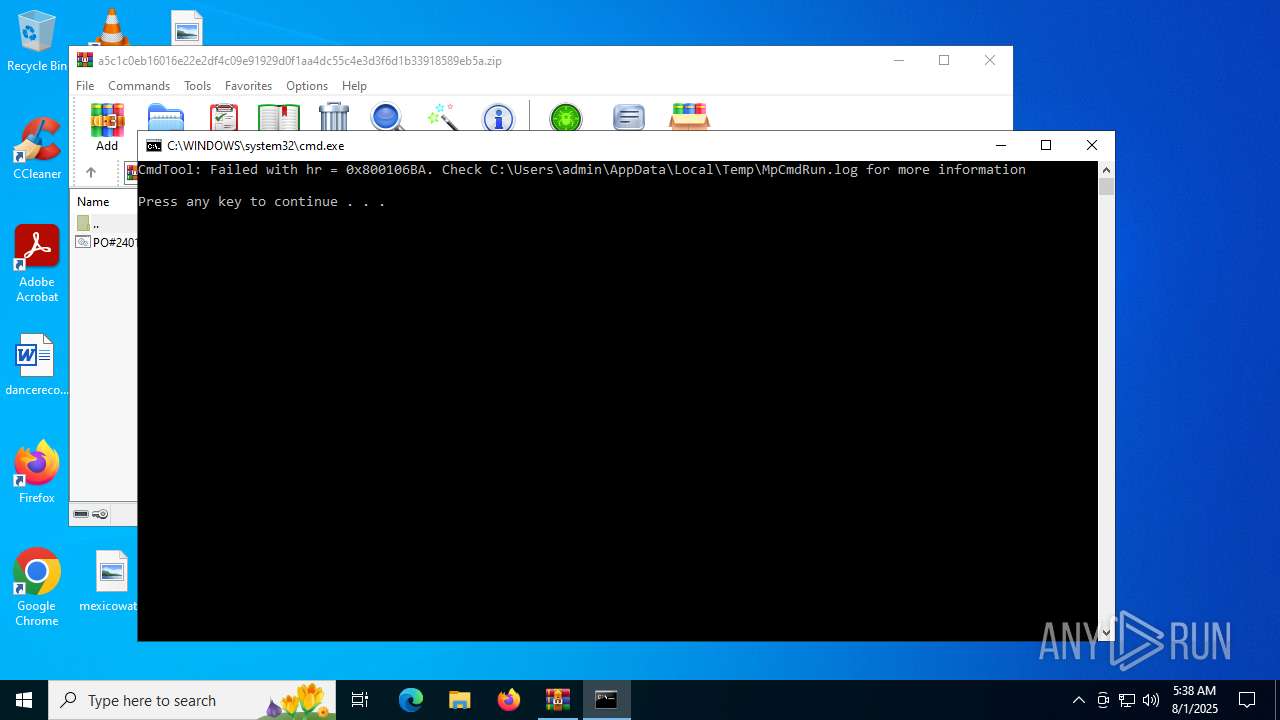
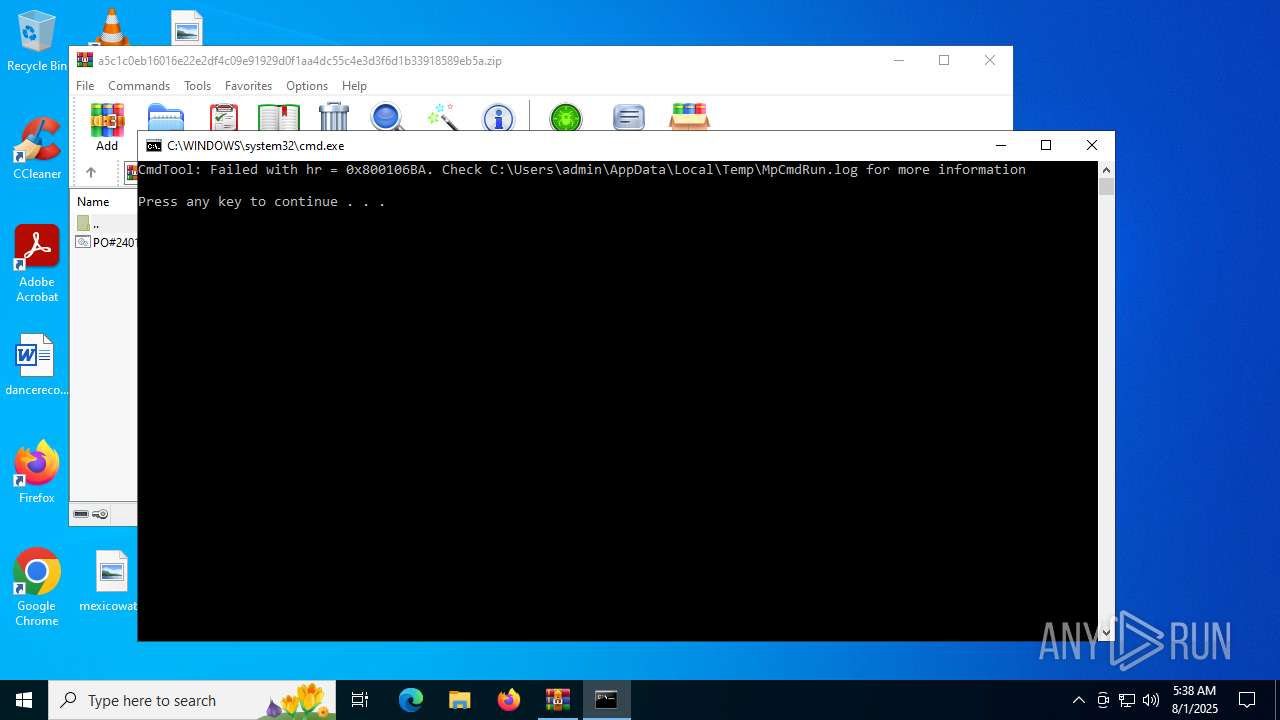
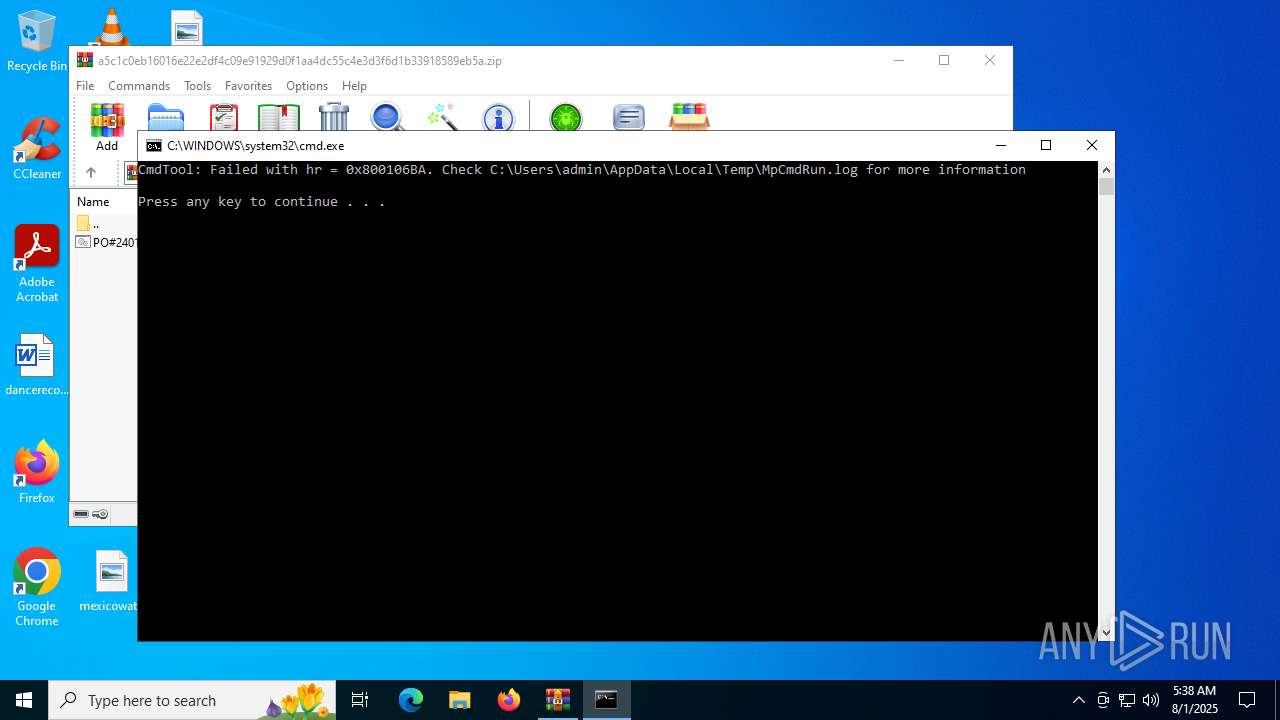
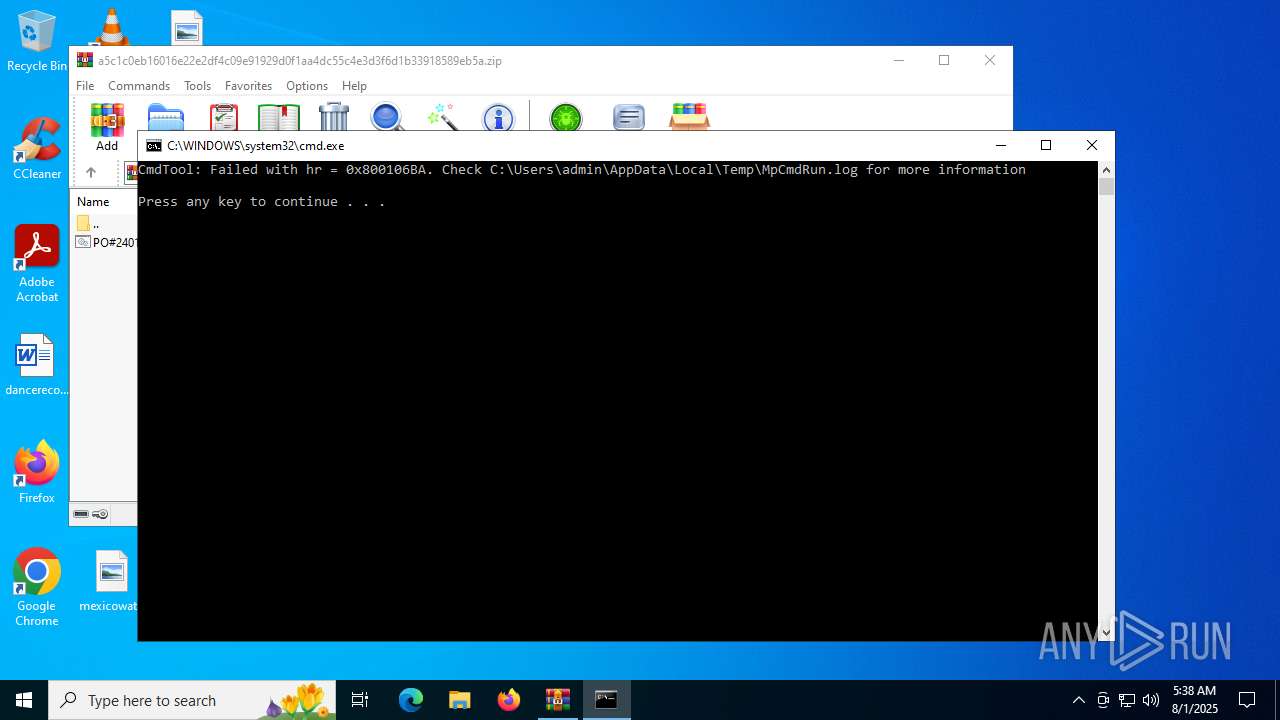
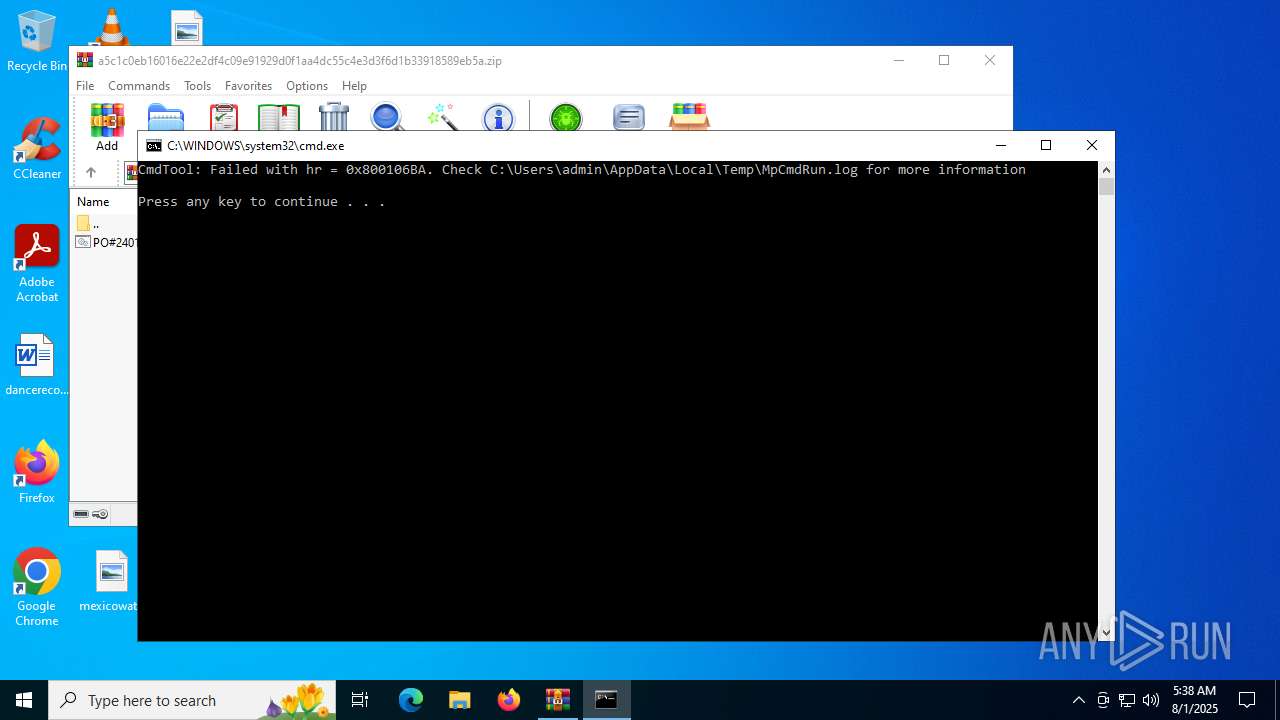
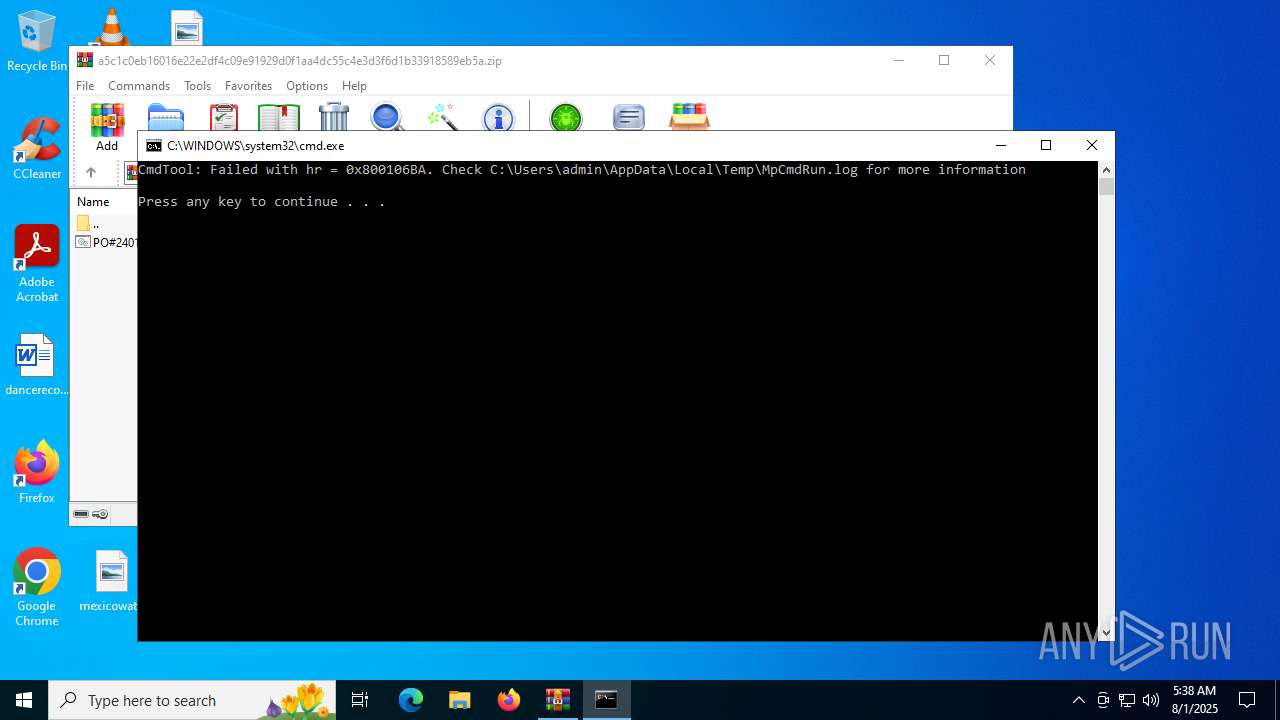
| 4120 | "C:\Program Files\Windows Defender\MpCmdRun.exe" -Scan -ScanType 3 -File "C:\Users\admin\AppData\Local\Temp\Rar$VR6492.49905" | C:\Program Files\Windows Defender\MpCmdRun.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Malware Protection Command Line Utility Exit code: 2 Version: 4.18.1909.6 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4948 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5468 | C:\WINDOWS\system32\cmd.exe /c ""C:\Users\admin\AppData\Local\Temp\Rar$VR6492.49905\Rar$Scan97877.bat" " | C:\Windows\System32\cmd.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6172 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | schtasks.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\preferences.zip | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\chromium_ext.zip | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\omni_23_10_2024_.zip | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\Desktop\a5c1c0eb16016e22e2df4c09e91929d0f1aa4dc55c4e3d3f6d1b33918589eb5a.zip | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (6492) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
| (PID) Process: | (2384) PO#240145.bat | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\PO#240145_RASAPI32 |
| Operation: | write | Name: | EnableFileTracing |
Value: 0 | |||
| (PID) Process: | (2384) PO#240145.bat | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\PO#240145_RASAPI32 |
| Operation: | write | Name: | EnableAutoFileTracing |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 504 | PO#240145.bat | C:\Users\admin\AppData\Local\Temp\tmp2B2D.tmp | xml | |
MD5:896313A9DE4B05FA75157B23A0DEF7B7 | SHA256:8F7F331BAE4EC6C27A50C2F0BAD67BD87213E4EB3C7AD96382B2840BE1F36FA9 | |||
| 4120 | MpCmdRun.exe | C:\Users\admin\AppData\Local\Temp\MpCmdRun.log | text | |
MD5:C971152AA48A3AC3E63FE9C550955011 | SHA256:3ED987727C66B677F8192ABCB22E80D98C5CE6366AFC5B258D435CFE25A20B0E | |||
| 504 | PO#240145.bat | C:\Users\admin\AppData\Roaming\FSEUWuGde.exe | executable | |
MD5:F11B7752D4D90ABCE909F3C580AEDD1C | SHA256:F6DC3F5E765A384C8317D418BE852E6B1909B89B2F90EA5483858FCA4CFFED4F | |||
| 6492 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$VR6492.49905\a5c1c0eb16016e22e2df4c09e91929d0f1aa4dc55c4e3d3f6d1b33918589eb5a.zip\PO#240145.bat | executable | |
MD5:F11B7752D4D90ABCE909F3C580AEDD1C | SHA256:F6DC3F5E765A384C8317D418BE852E6B1909B89B2F90EA5483858FCA4CFFED4F | |||
| 6748 | FSEUWuGde.exe | C:\Users\admin\AppData\Local\Temp\tmp749A.tmp | xml | |
MD5:896313A9DE4B05FA75157B23A0DEF7B7 | SHA256:8F7F331BAE4EC6C27A50C2F0BAD67BD87213E4EB3C7AD96382B2840BE1F36FA9 | |||
| 6492 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$VR6492.49905\Rar$Scan97877.bat | text | |
MD5:7E8310A7812A51BD6DA0FCE9E0822927 | SHA256:88A497CBF6800A9ABACF35BA7F63F2442EBDB8F7DBE711F8C39D9F8A6FA00C4C | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5944 | MoUsoCoreWorker.exe | GET | 200 | 23.216.77.28:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
5944 | MoUsoCoreWorker.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
4944 | RUXIMICS.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
2384 | PO#240145.bat | GET | 200 | 132.226.247.73:80 | http://checkip.dyndns.org/ | BR | html | 105 b | whitelisted |
— | — | GET | 200 | 104.21.80.1:443 | https://reallyfreegeoip.org/xml/109.26.61.227 | US | text | 352 b | malicious |
2384 | PO#240145.bat | GET | 200 | 132.226.247.73:80 | http://checkip.dyndns.org/ | BR | html | 105 b | whitelisted |
2384 | PO#240145.bat | GET | 200 | 132.226.247.73:80 | http://checkip.dyndns.org/ | BR | html | 105 b | whitelisted |
— | — | GET | 200 | 104.21.80.1:443 | https://reallyfreegeoip.org/xml/109.26.61.227 | US | — | — | unknown |
1156 | FSEUWuGde.exe | GET | 200 | 132.226.247.73:80 | http://checkip.dyndns.org/ | BR | html | 105 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1268 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4944 | RUXIMICS.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1268 | svchost.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
4944 | RUXIMICS.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
1268 | svchost.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
checkip.dyndns.org |
| whitelisted |
reallyfreegeoip.org |
| malicious |
cphost14.qhoster.net |
| malicious |
self.events.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2200 | svchost.exe | Device Retrieving External IP Address Detected | ET DYN_DNS External IP Lookup Domain in DNS Query (checkip .dyndns .org) |
2384 | PO#240145.bat | Device Retrieving External IP Address Detected | ET INFO External IP Lookup - checkip.dyndns.org |
2384 | PO#240145.bat | Device Retrieving External IP Address Detected | ET INFO 404/Snake/Matiex Keylogger Style External IP Check |
2200 | svchost.exe | Device Retrieving External IP Address Detected | INFO [ANY.RUN] External IP Address Lookup Domain (reallyfreegeoip .org) |
2384 | PO#240145.bat | Device Retrieving External IP Address Detected | ET INFO External IP Lookup - checkip.dyndns.org |
2384 | PO#240145.bat | Misc activity | ET INFO External IP Lookup Service Domain (reallyfreegeoip .org) in TLS SNI |
2200 | svchost.exe | Misc activity | ET INFO External IP Address Lookup Domain in DNS Lookup (reallyfreegeoip .org) |
2384 | PO#240145.bat | Device Retrieving External IP Address Detected | ET INFO External IP Lookup - checkip.dyndns.org |
1156 | FSEUWuGde.exe | Device Retrieving External IP Address Detected | ET INFO External IP Lookup - checkip.dyndns.org |
1156 | FSEUWuGde.exe | Device Retrieving External IP Address Detected | ET INFO 404/Snake/Matiex Keylogger Style External IP Check |