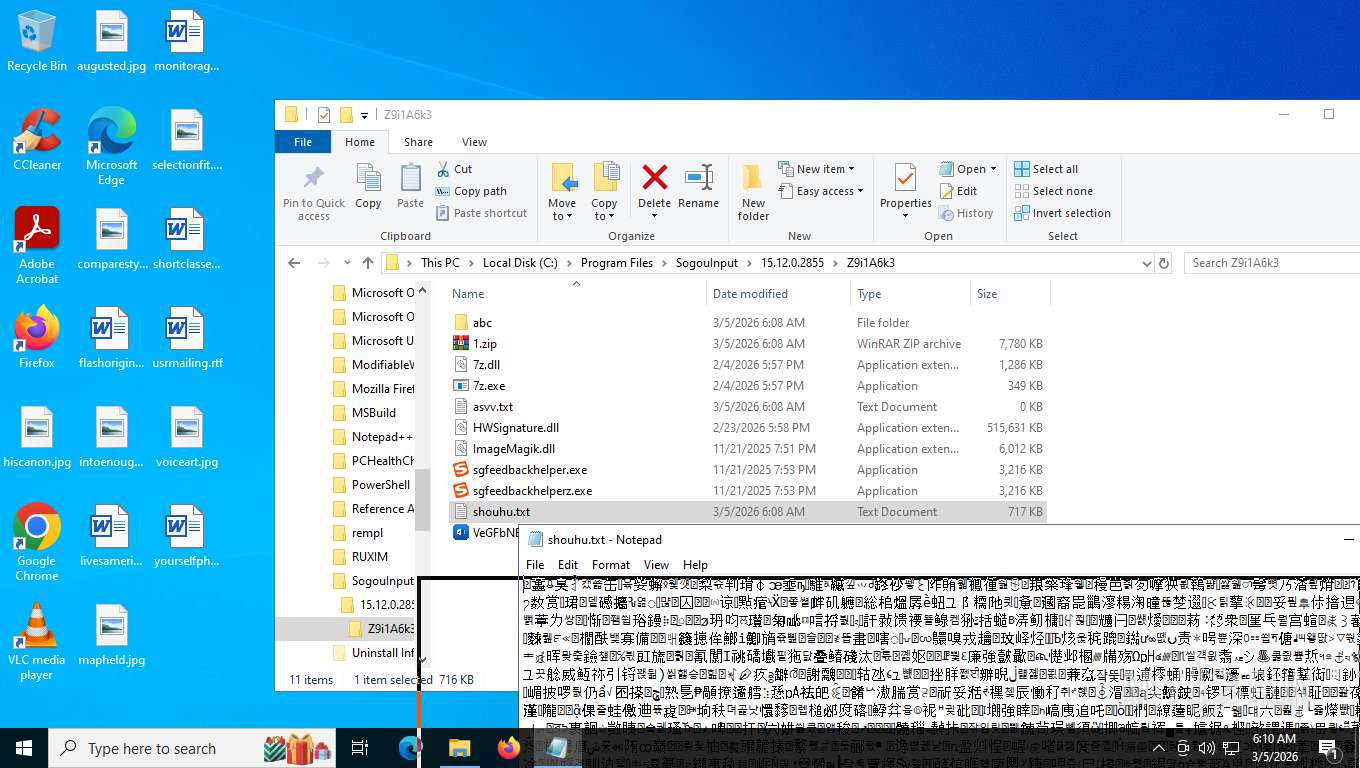
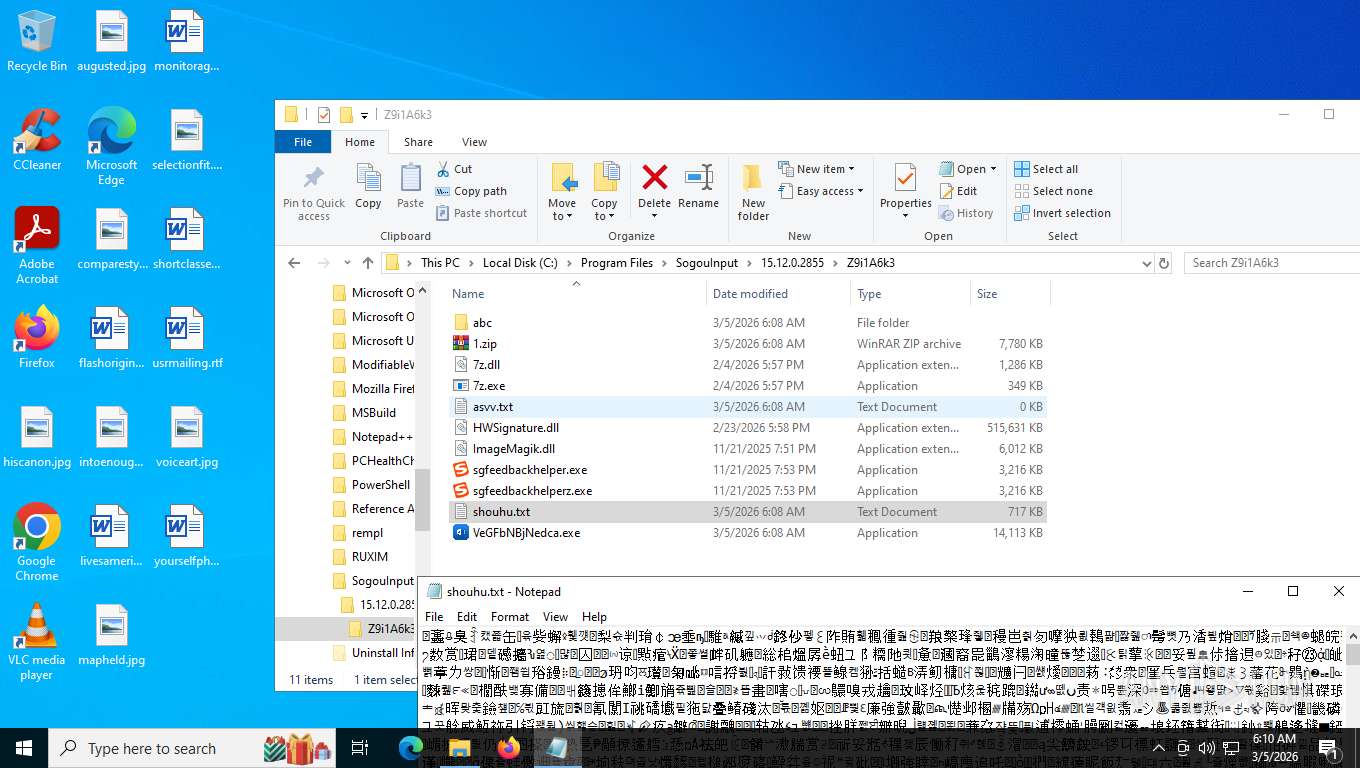
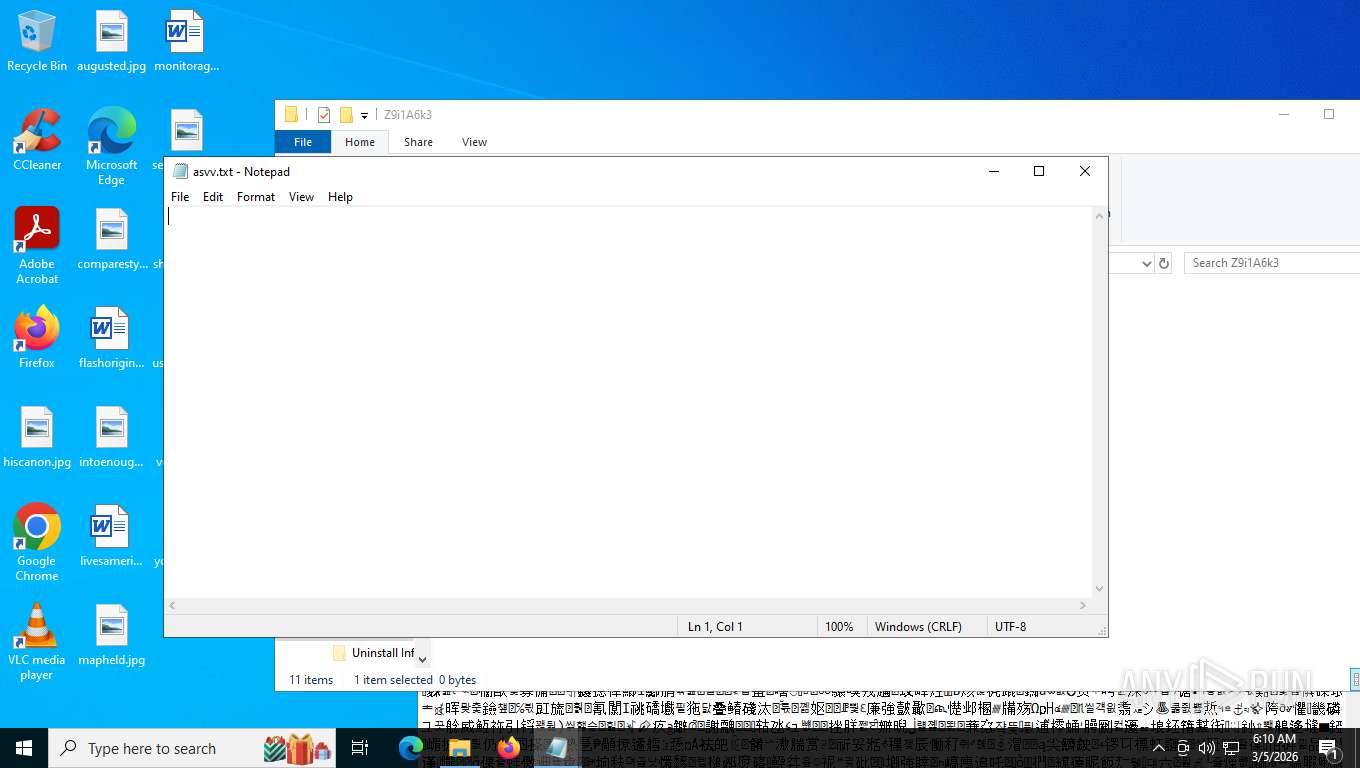
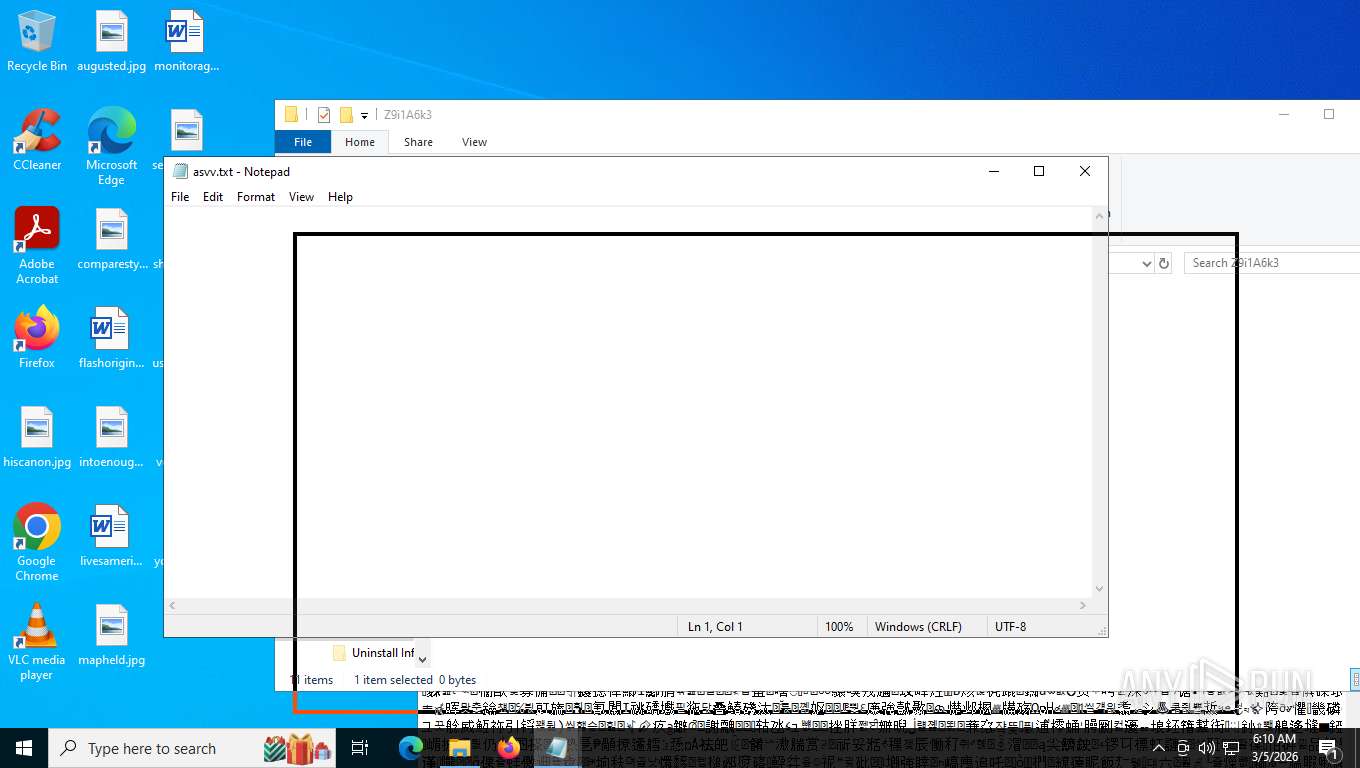
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
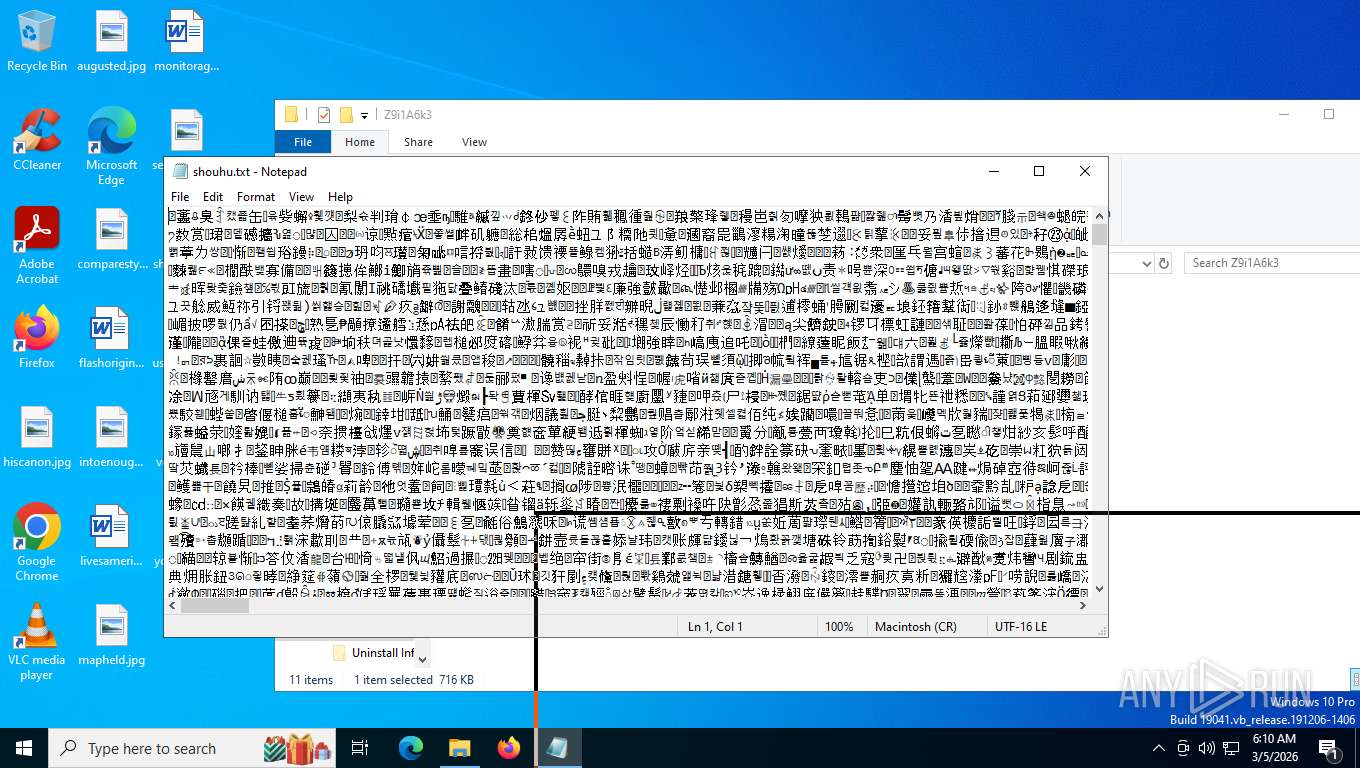
| File name: | 5eaf63eeeacf25c6ebb053737979b237 |
| Full analysis: | https://app.any.run/tasks/c130623c-573c-4e2a-89cc-60969c5e37bf |
| Verdict: | Malicious activity |
| Threats: | BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods. |
| Analysis date: | March 05, 2026, 11:08:37 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (GUI) x86-64, for MS Windows, 7 sections |
| MD5: | 5EAF63EEEACF25C6EBB053737979B237 |
| SHA1: | EECD2DF28634E27D807345D722246F1960704021 |
| SHA256: | 9D5E2993CB7369FE21013D30125626E597B94DA70228328E7253540041998374 |
| SSDEEP: | 98304:Ywz6EqL7smUyVYRqWa1h1j5qkbkAAsjgRvozAR80l7zdgtG1Rv8E67y6XQDm7egy:kLd79l6pkej7OtpbDrkmJe |
| .exe | | | Generic Win/DOS Executable (50) |
|---|---|---|
| .exe | | | DOS Executable Generic (49.9) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2026:02:27 13:26:59+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.43 |
| CodeSize: | 2239488 |
| InitializedDataSize: | 12243968 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x1ec920 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
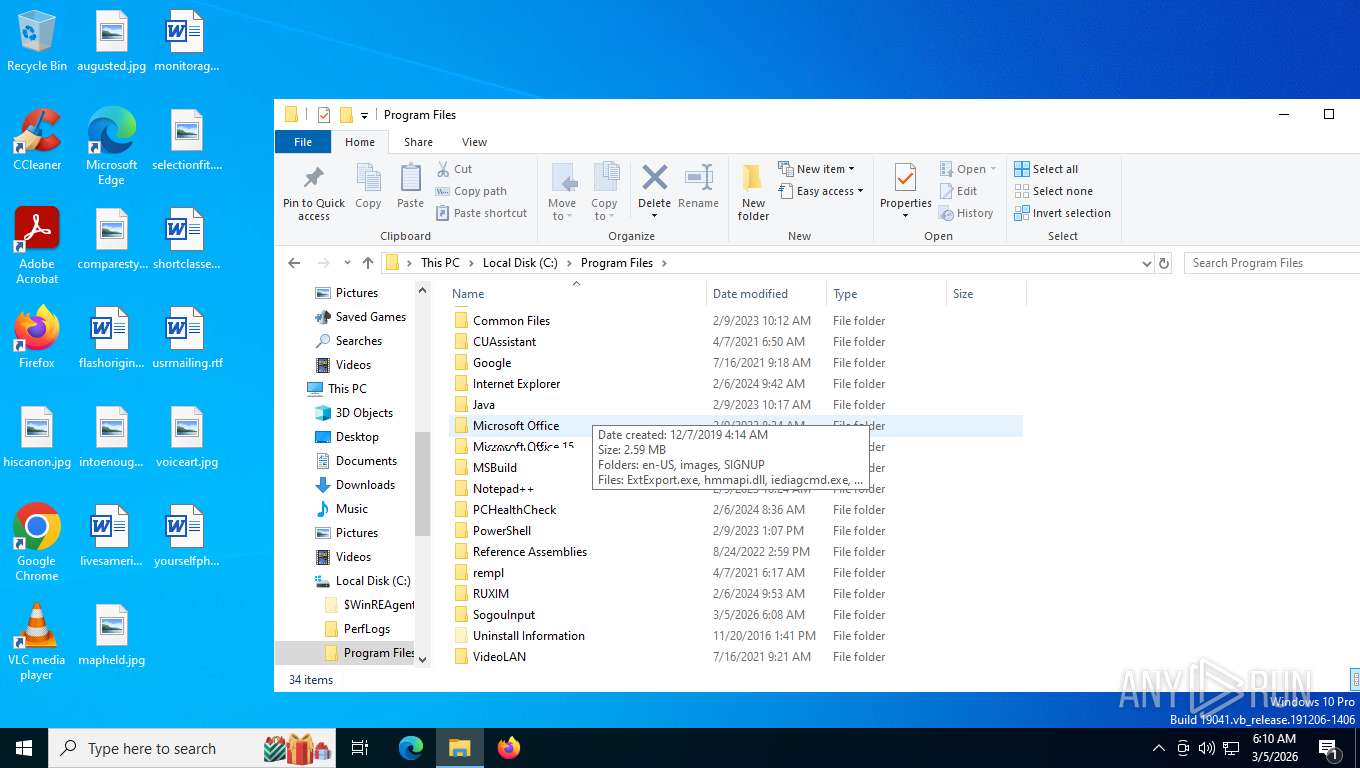
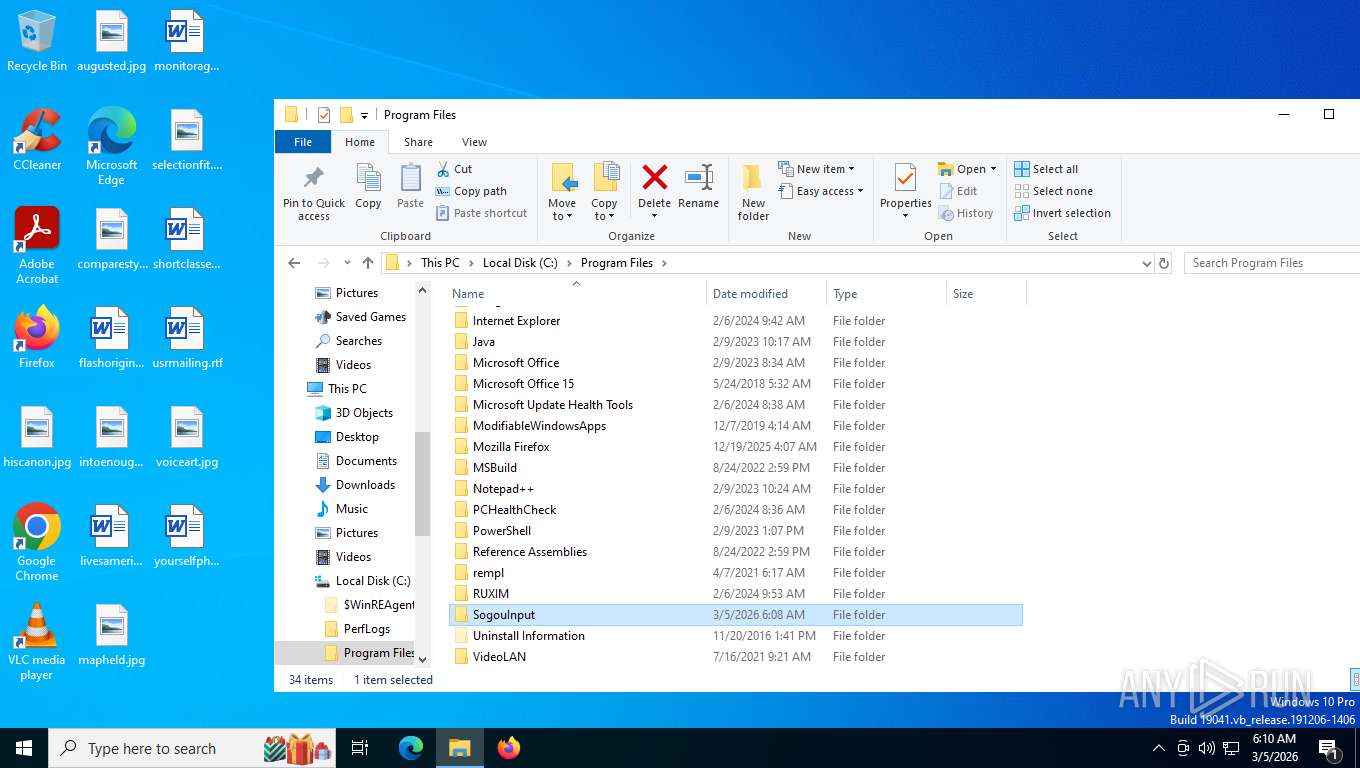
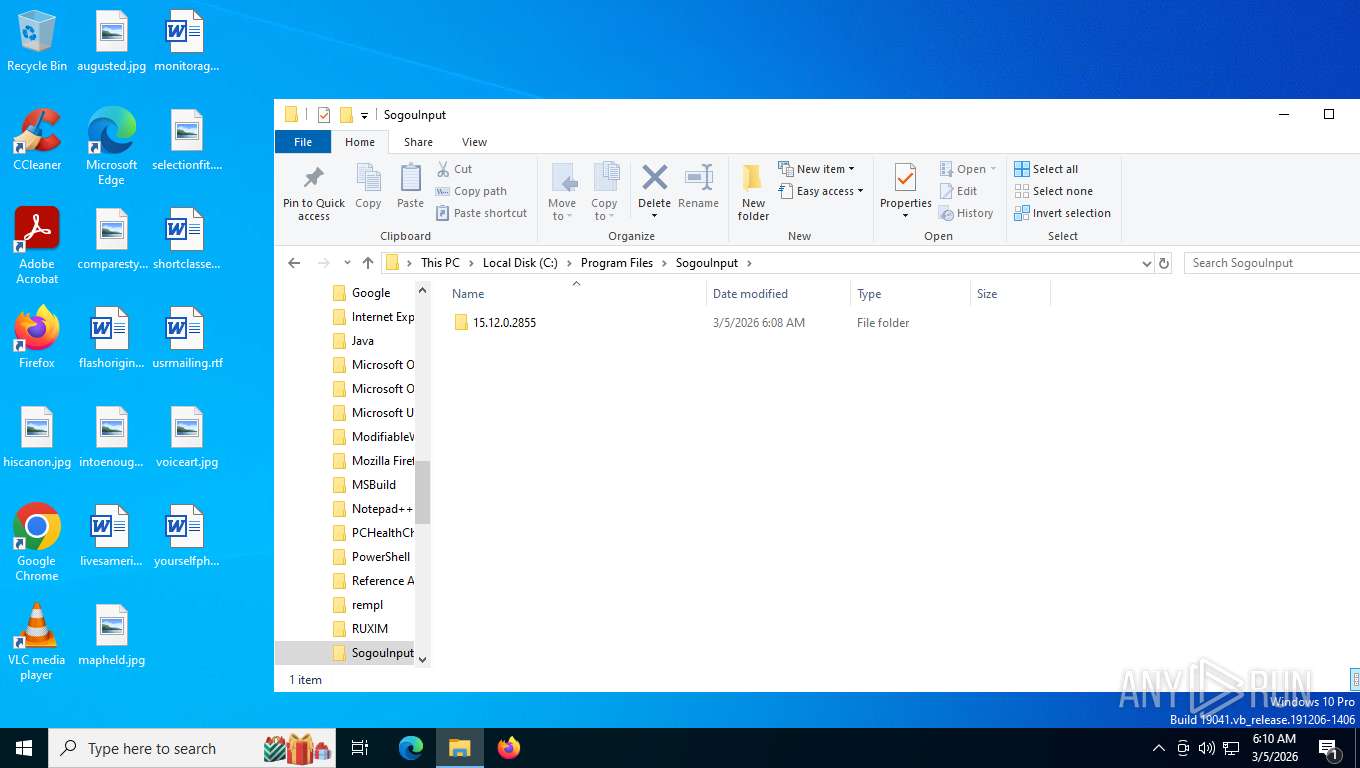
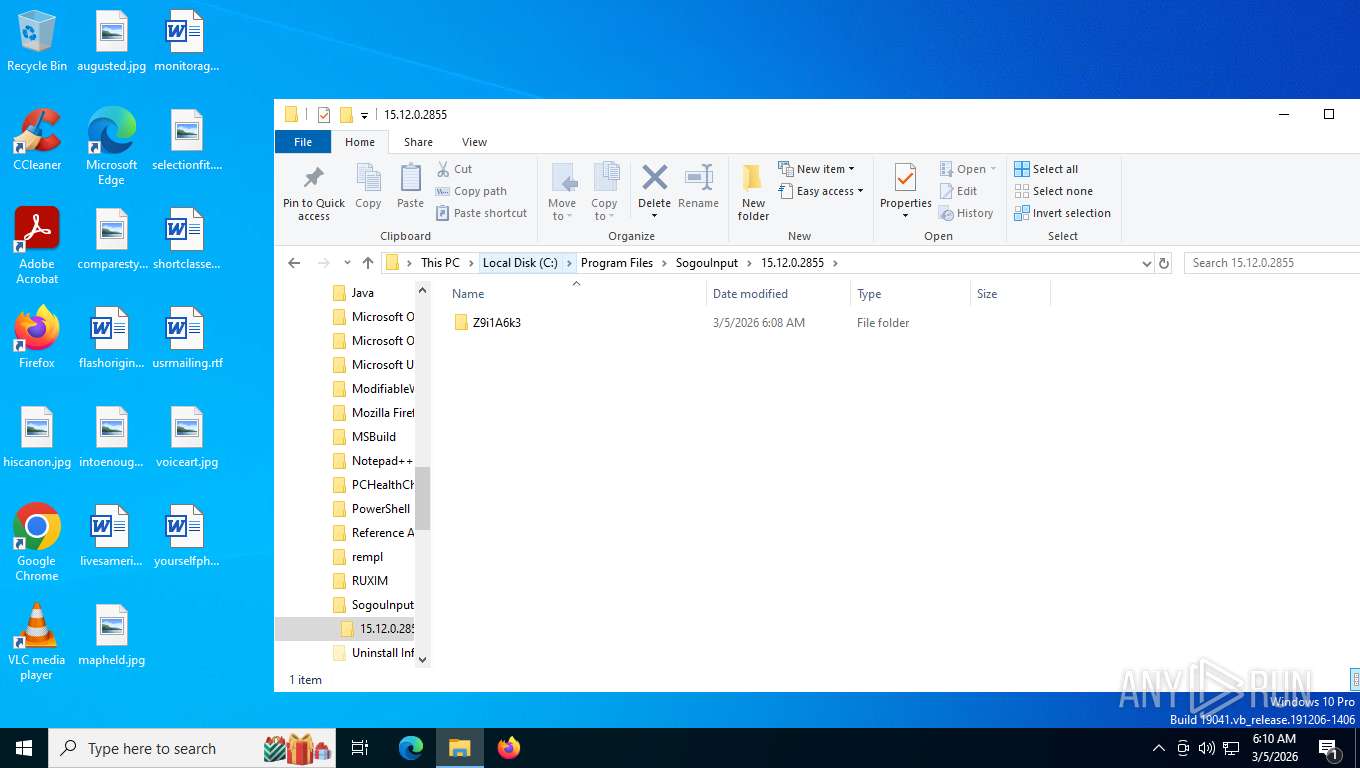
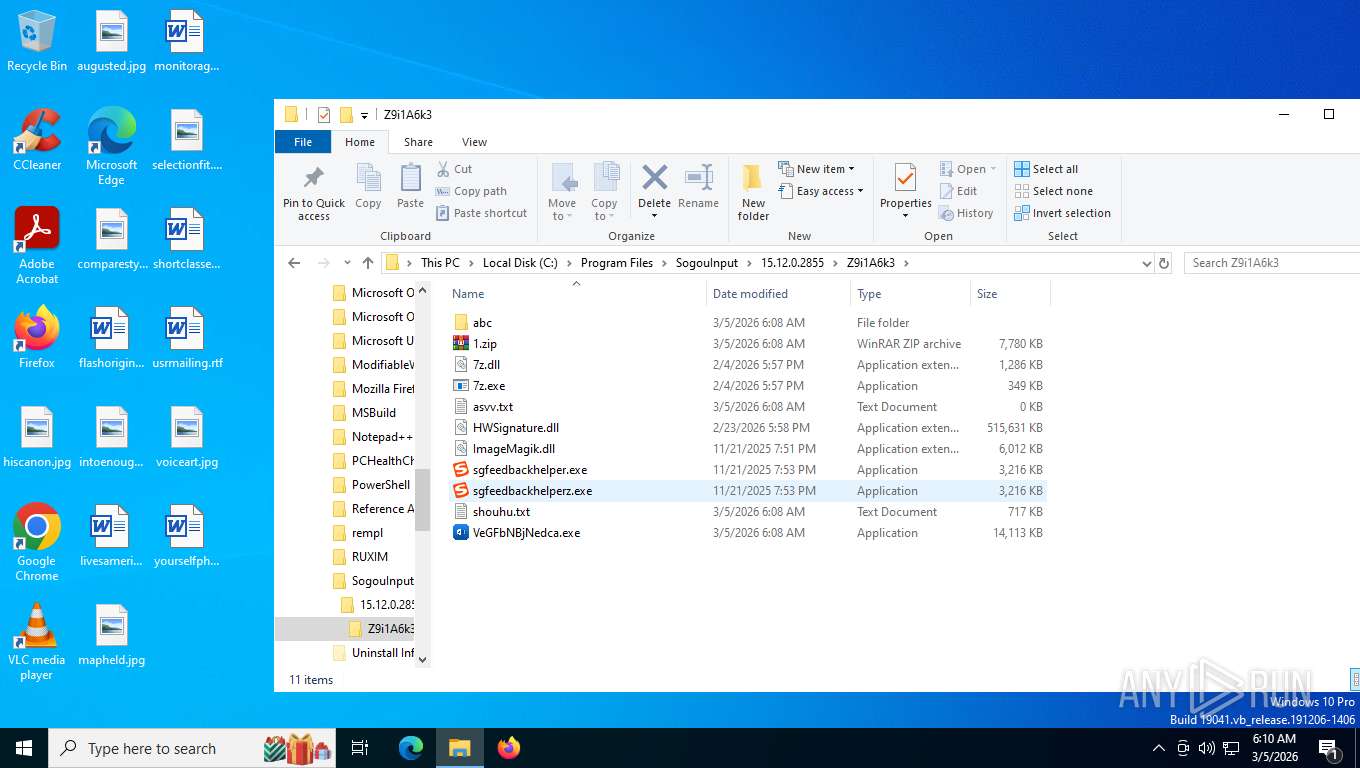
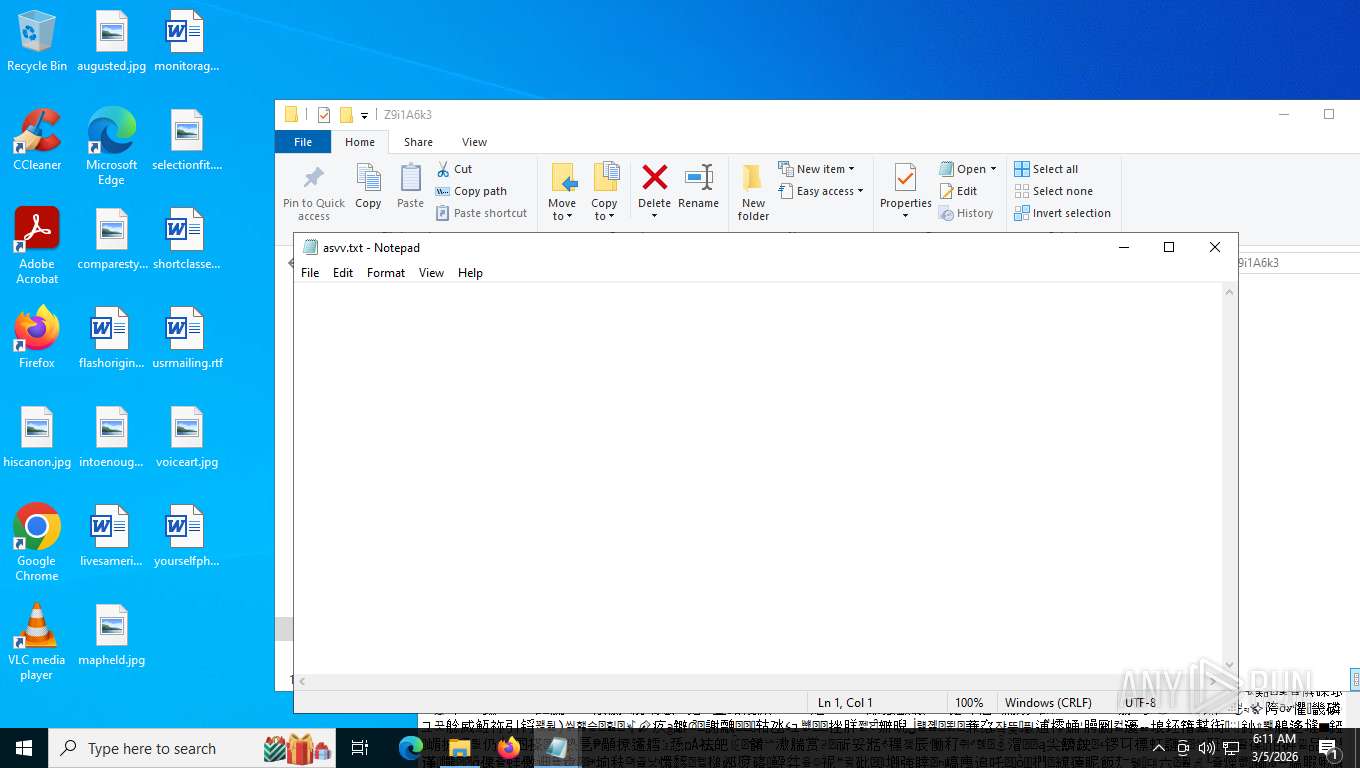
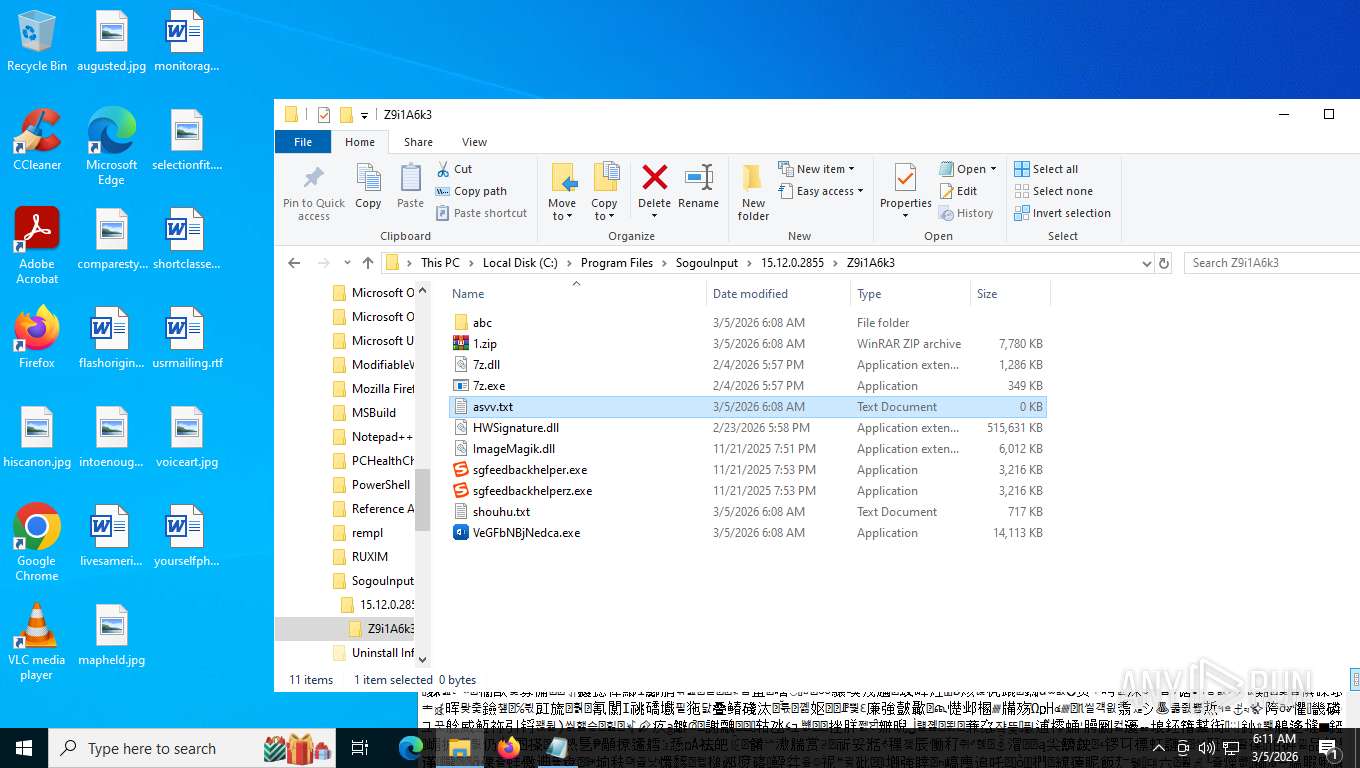
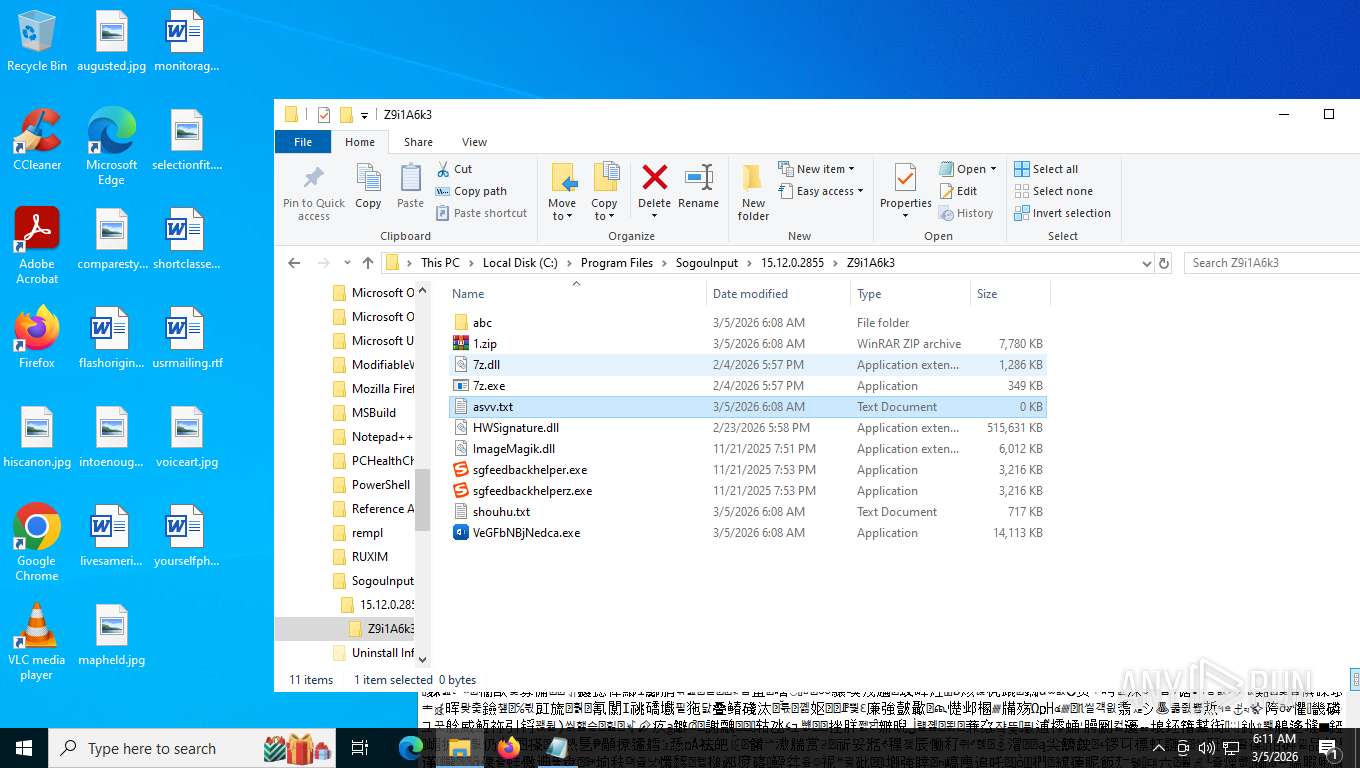
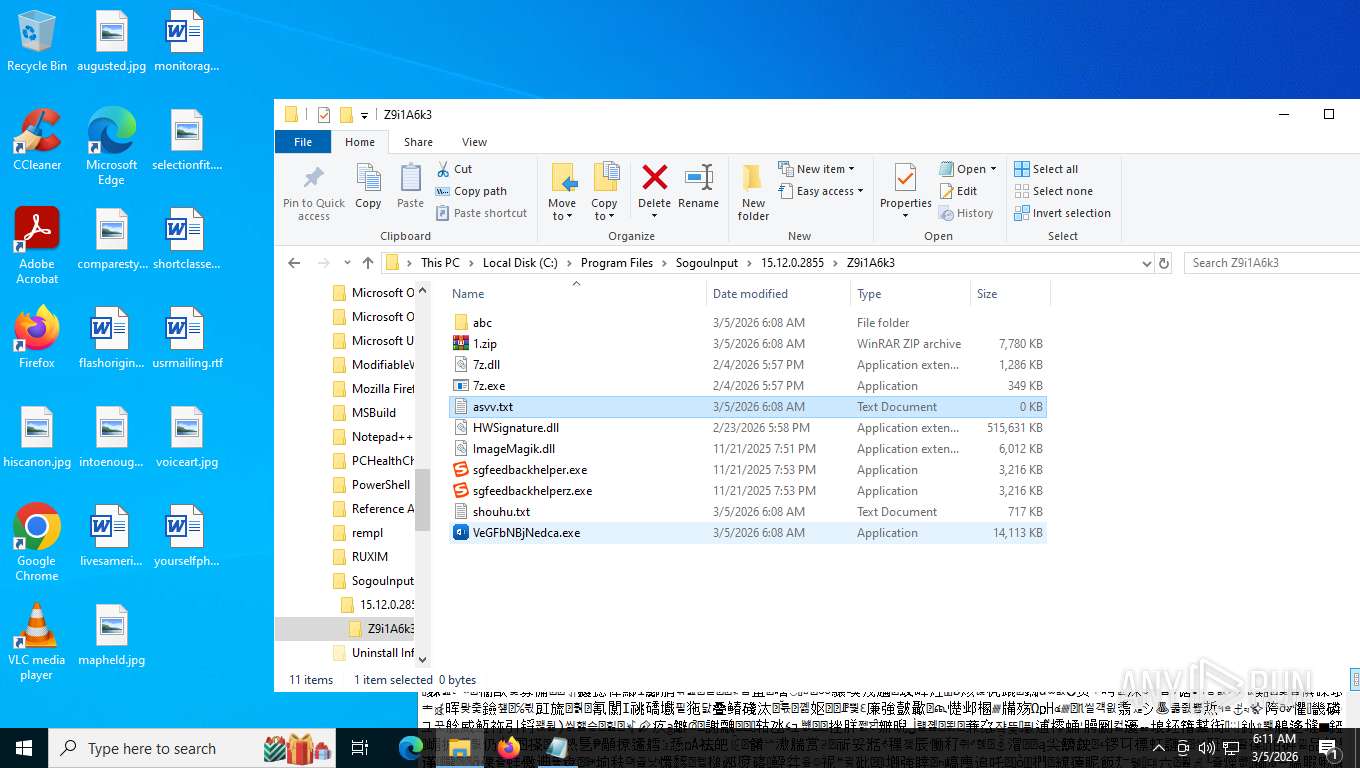
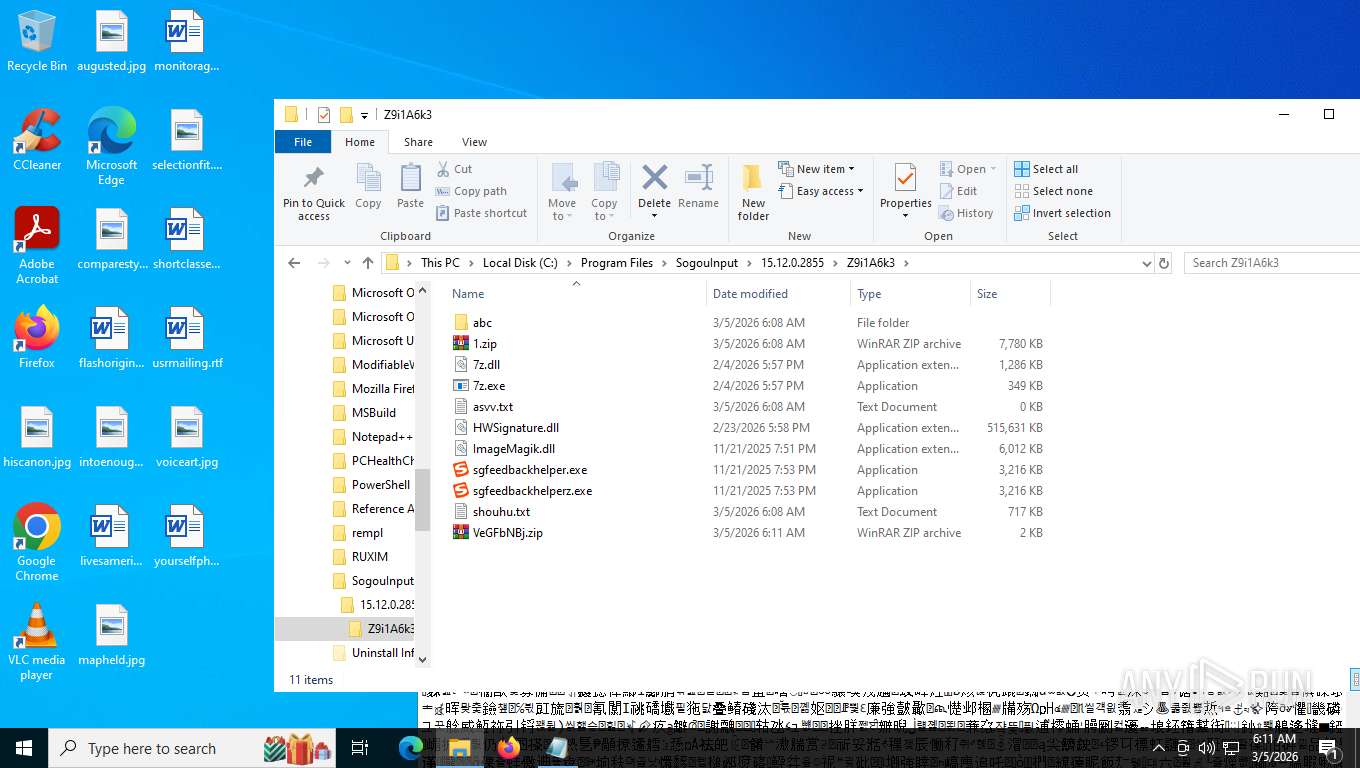
| 132 | "C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\sgfeedbackhelper.exe" | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\sgfeedbackhelper.exe | 5eaf63eeeacf25c6ebb053737979b237.exe | ||||||||||||
User: admin Company: Sogou.com Integrity Level: HIGH Description: 搜狗输入法 反馈帮助程序 Exit code: 0 Version: 15.11.0.2620 Modules
| |||||||||||||||
| 1136 | C:\WINDOWS\system32\cmd.exe "C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\ | C:\Windows\SysWOW64\cmd.exe | sgfeedbackhelperz.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 1073807364 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1932 | "C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\sgfeedbackhelperz.exe" Akfcde | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\sgfeedbackhelperz.exe | — | sgfeedbackhelper.exe | |||||||||||
User: admin Company: Sogou.com Integrity Level: HIGH Description: 搜狗输入法 反馈帮助程序 Exit code: 0 Version: 15.11.0.2620 Modules
| |||||||||||||||
| 2572 | "C:\Users\admin\AppData\Local\Temp\5eaf63eeeacf25c6ebb053737979b237.exe" | C:\Users\admin\AppData\Local\Temp\5eaf63eeeacf25c6ebb053737979b237.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 3636 | "C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\VeGFbNBjNedca.exe" | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\VeGFbNBjNedca.exe | VeGFbNBjNedca.exe | ||||||||||||
User: admin Integrity Level: HIGH Exit code: 1073807364 Modules
| |||||||||||||||
| 4304 | "C:\Program Files\RUXIM\PLUGscheduler.exe" | C:\Program Files\RUXIM\PLUGScheduler.exe | — | svchost.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Update LifeCycle Component Scheduler Exit code: 0 Version: 10.0.19041.3623 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4340 | "C:\Program Files (x86)\Google\GoogleUpdater\134.0.6985.0\updater.exe" --wake --system | C:\Program Files (x86)\Google\GoogleUpdater\134.0.6985.0\updater.exe | — | svchost.exe | |||||||||||
User: SYSTEM Company: Google LLC Integrity Level: SYSTEM Description: Google Updater Exit code: 0 Version: 134.0.6985.0 Modules
| |||||||||||||||
| 4468 | "C:\WINDOWS\SystemApps\Microsoft.Windows.Search_cw5n1h2txyewy\SearchApp.exe" -ServerName:CortanaUI.AppX8z9r6jm96hw4bsbneegw0kyxx296wr9t.mca | C:\Windows\SystemApps\Microsoft.Windows.Search_cw5n1h2txyewy\SearchApp.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Search application Exit code: 0 Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4540 | C:\WINDOWS\system32\cmd.exe "C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\ | C:\Windows\SysWOW64\cmd.exe | — | sgfeedbackhelperz.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4624 | "C:\WINDOWS\SystemApps\MicrosoftWindows.Client.CBS_cw5n1h2txyewy\TextInputHost.exe" -ServerName:InputApp.AppXjd5de1g66v206tj52m9d0dtpppx4cgpn.mca | C:\Windows\SystemApps\MicrosoftWindows.Client.CBS_cw5n1h2txyewy\TextInputHost.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Exit code: 0 Version: 123.26505.0.0 Modules
| |||||||||||||||
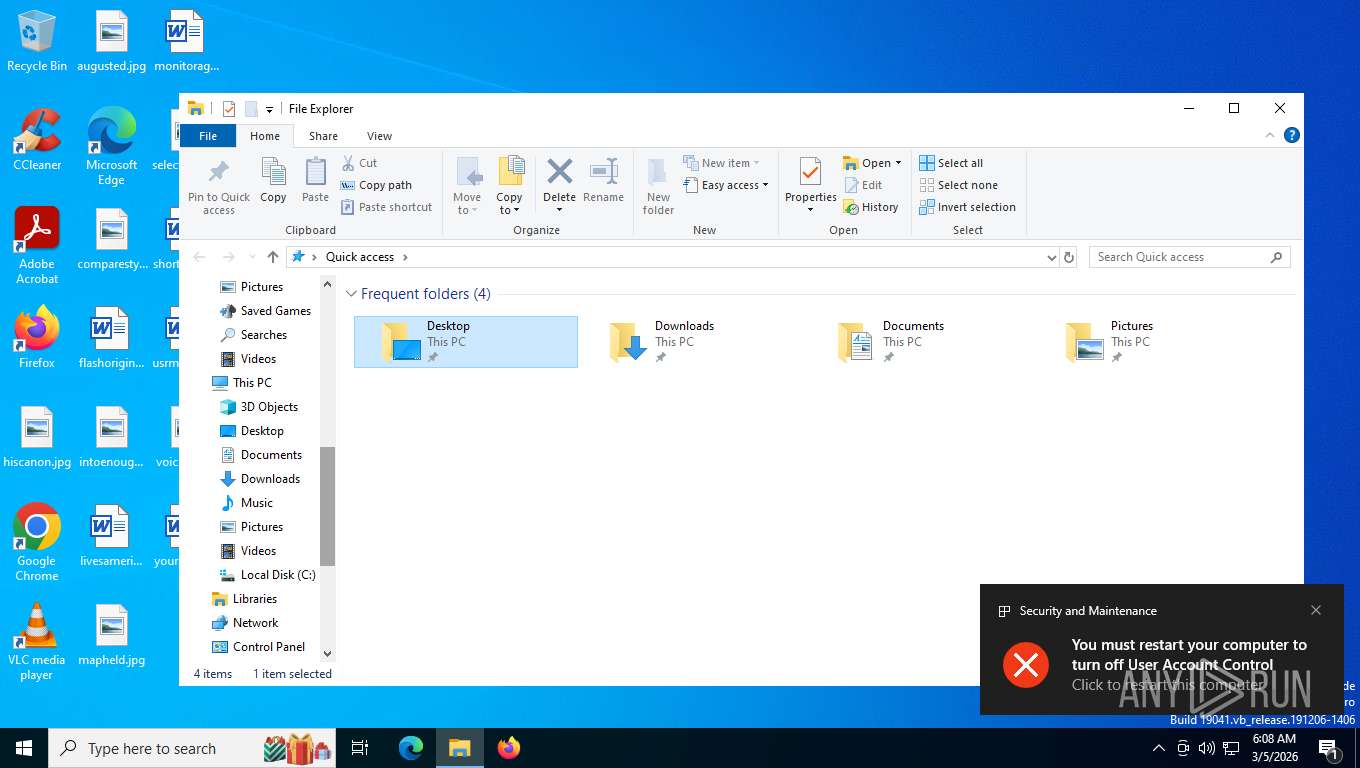
| (PID) Process: | (6640) 5eaf63eeeacf25c6ebb053737979b237.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System |
| Operation: | write | Name: | EnableLUA |
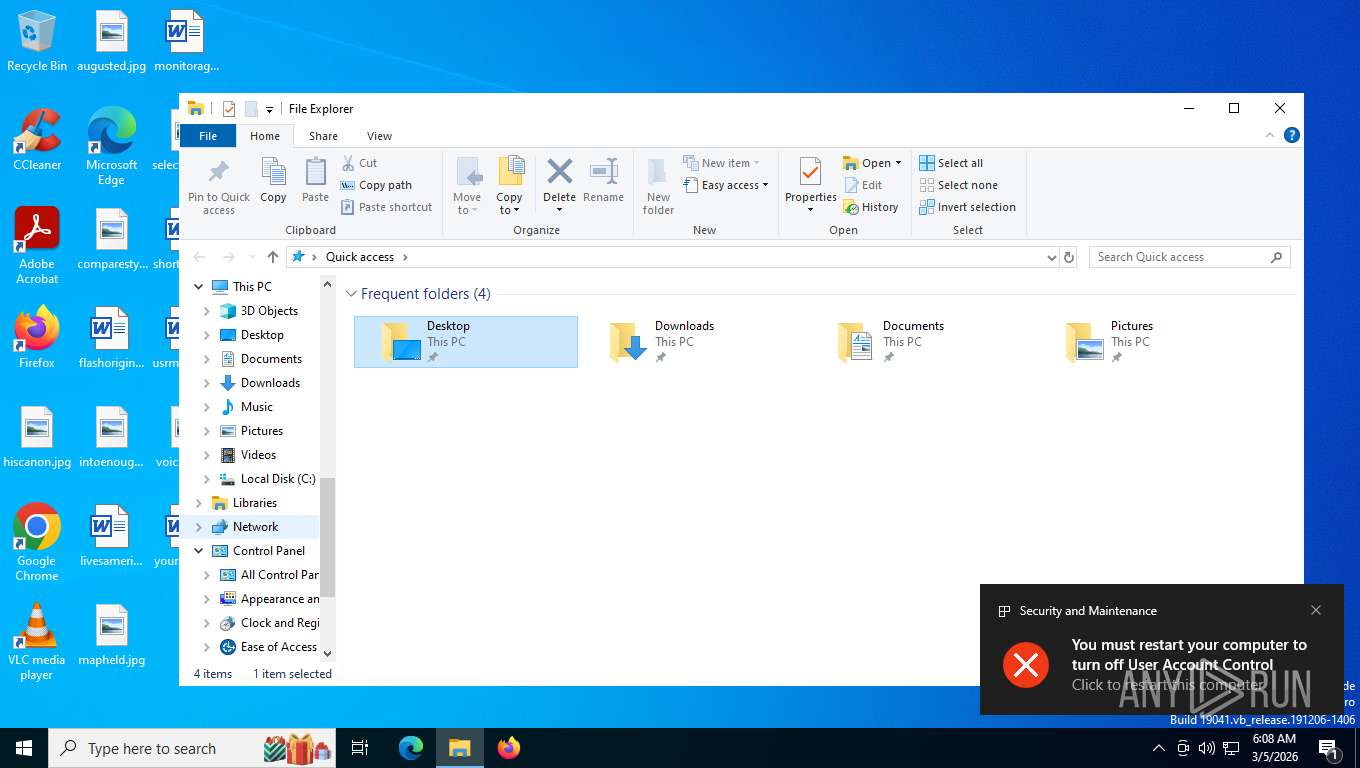
Value: 0 | |||
| (PID) Process: | (6640) 5eaf63eeeacf25c6ebb053737979b237.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender |
| Operation: | write | Name: | DisableAntiSpyware |
Value: 1 | |||
| (PID) Process: | (1932) sgfeedbackhelperz.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System |
| Operation: | write | Name: | EnableLUA |
Value: 0 | |||
| (PID) Process: | (1932) sgfeedbackhelperz.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender |
| Operation: | write | Name: | DisableAntiSpyware |
Value: 1 | |||
| (PID) Process: | (4696) notepad.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Notepad |
| Operation: | write | Name: | iWindowPosX |
Value: 286 | |||
| (PID) Process: | (4696) notepad.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Notepad |
| Operation: | write | Name: | iWindowPosY |
Value: 232 | |||
| (PID) Process: | (4696) notepad.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Notepad |
| Operation: | write | Name: | iWindowPosDX |
Value: 960 | |||
| (PID) Process: | (4696) notepad.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Notepad |
| Operation: | write | Name: | iWindowPosDY |
Value: 489 | |||
| (PID) Process: | (9084) TiWorker.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Component Based Servicing |
| Operation: | write | Name: | SessionIdHigh |
Value: 31239312 | |||
| (PID) Process: | (9084) TiWorker.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Component Based Servicing |
| Operation: | write | Name: | SessionIdLow |
Value: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
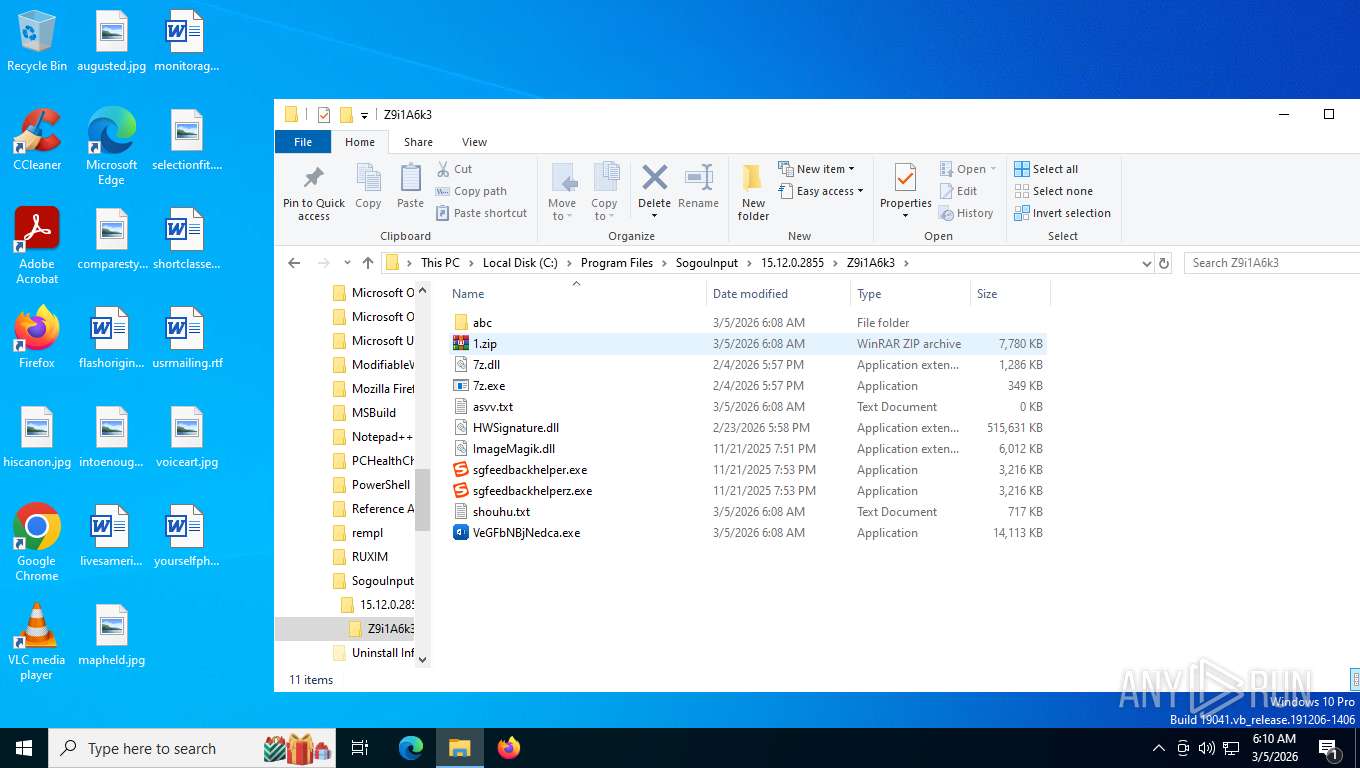
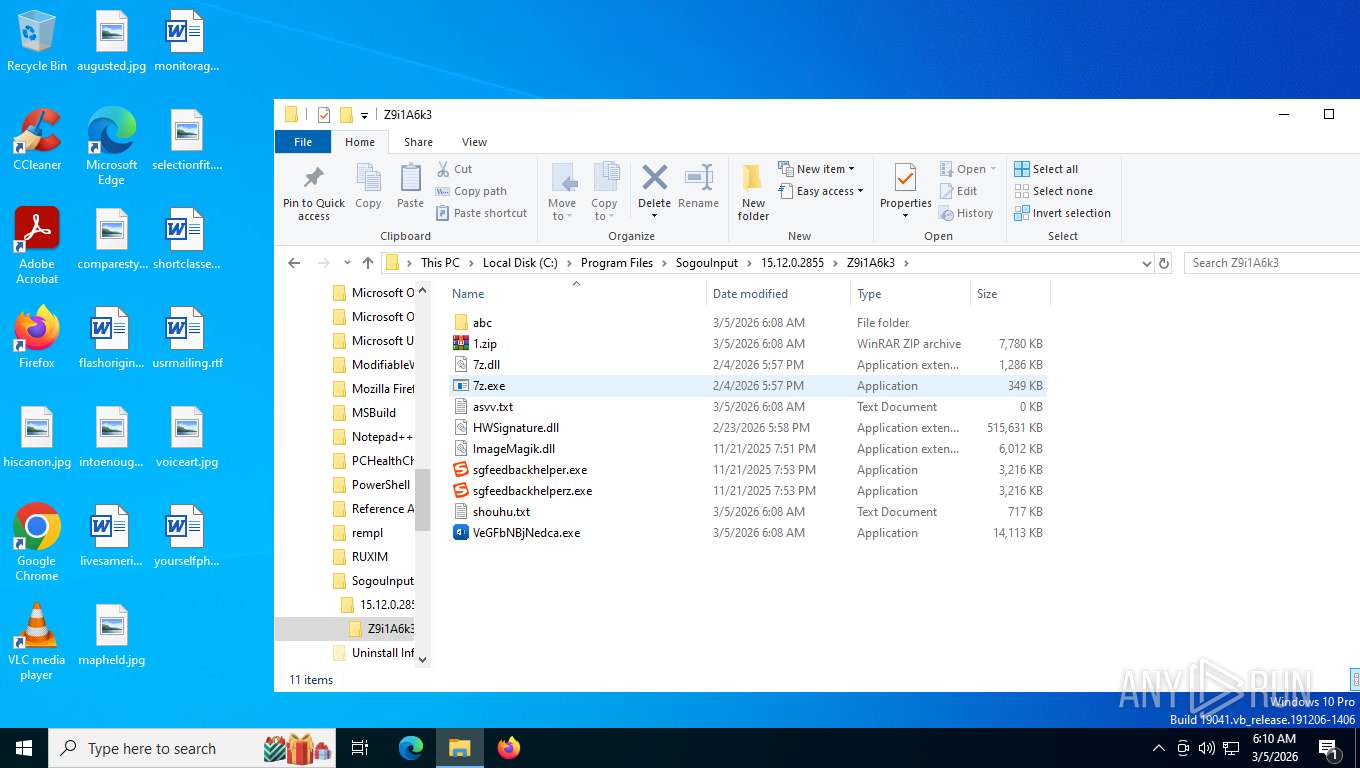
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\HWSignature.dll | — | |
MD5:— | SHA256:— | |||
| 9084 | TiWorker.exe | C:\Windows\Logs\CBS\CBS.log | — | |
MD5:— | SHA256:— | |||
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\VeGFbNBjNedca.exe | executable | |
MD5:5EAF63EEEACF25C6EBB053737979B237 | SHA256:9D5E2993CB7369FE21013D30125626E597B94DA70228328E7253540041998374 | |||
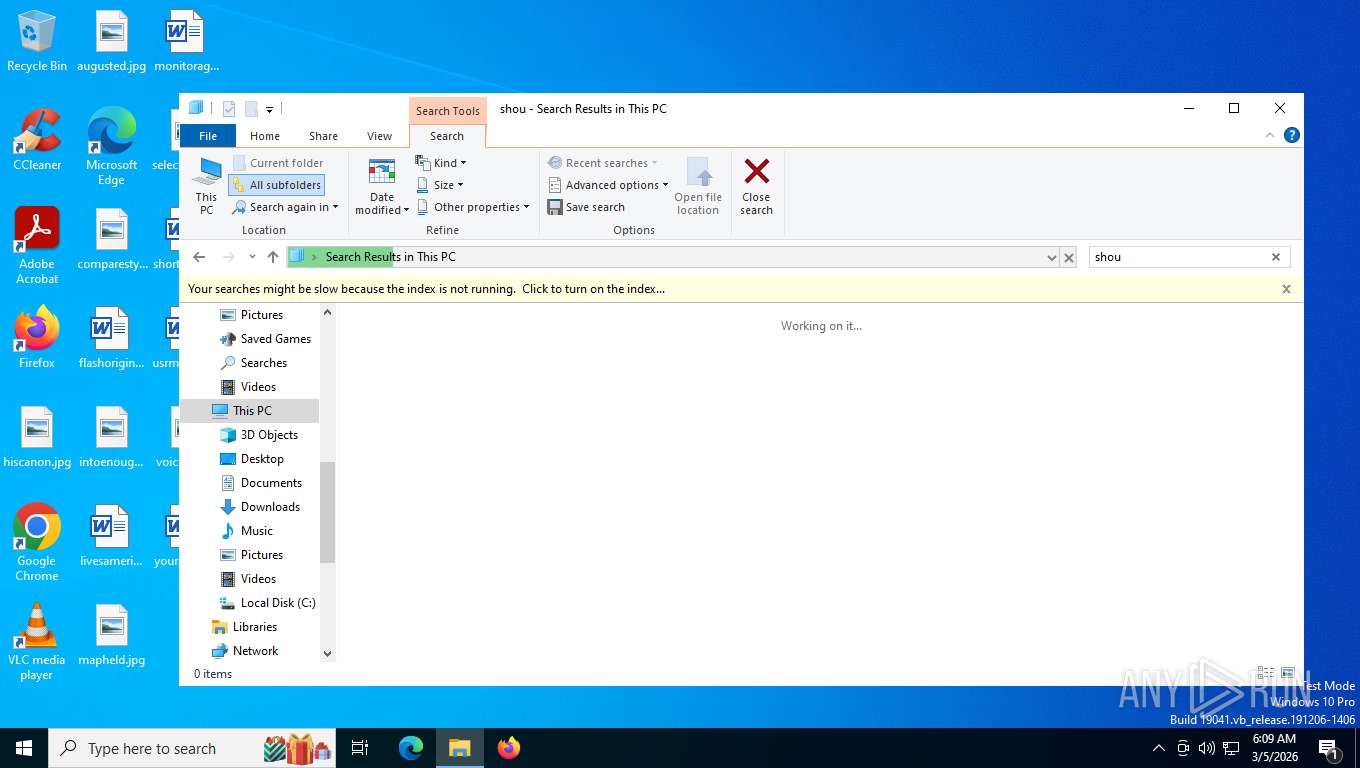
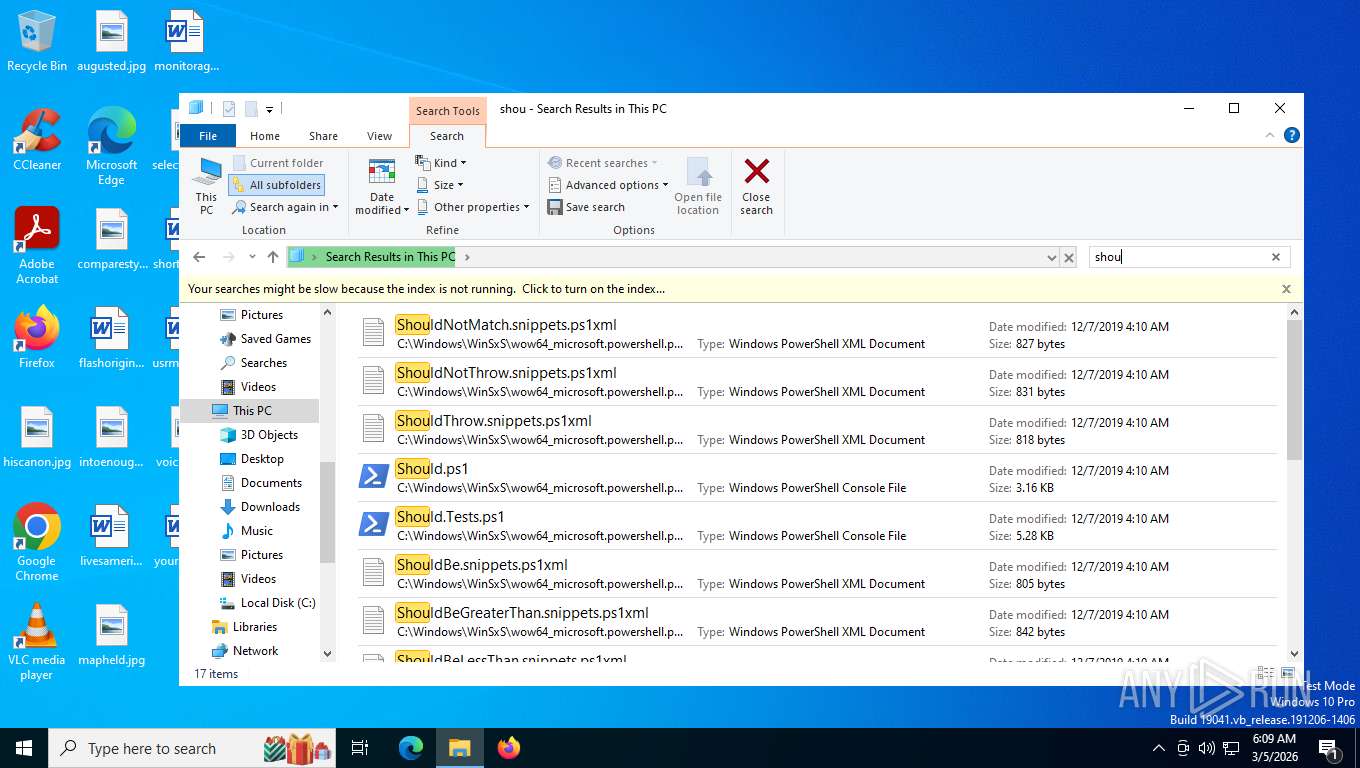
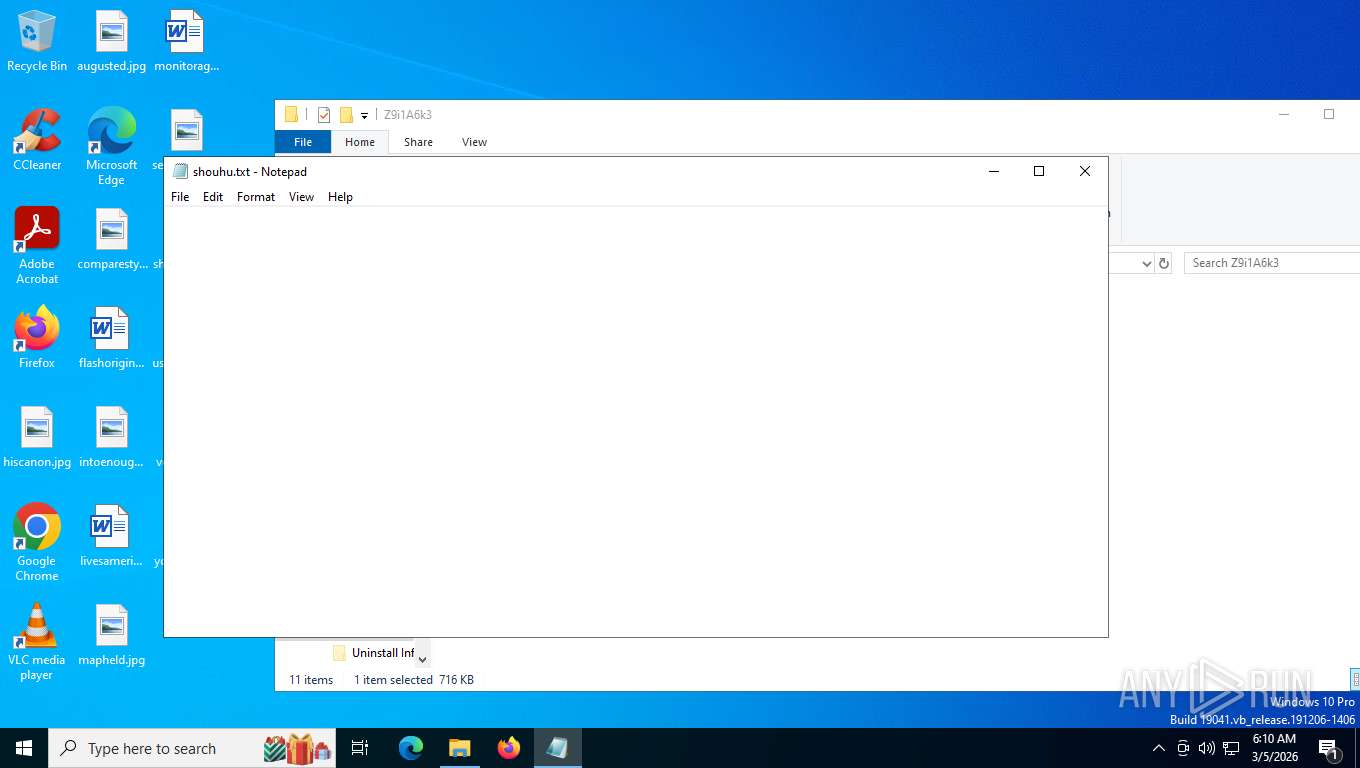
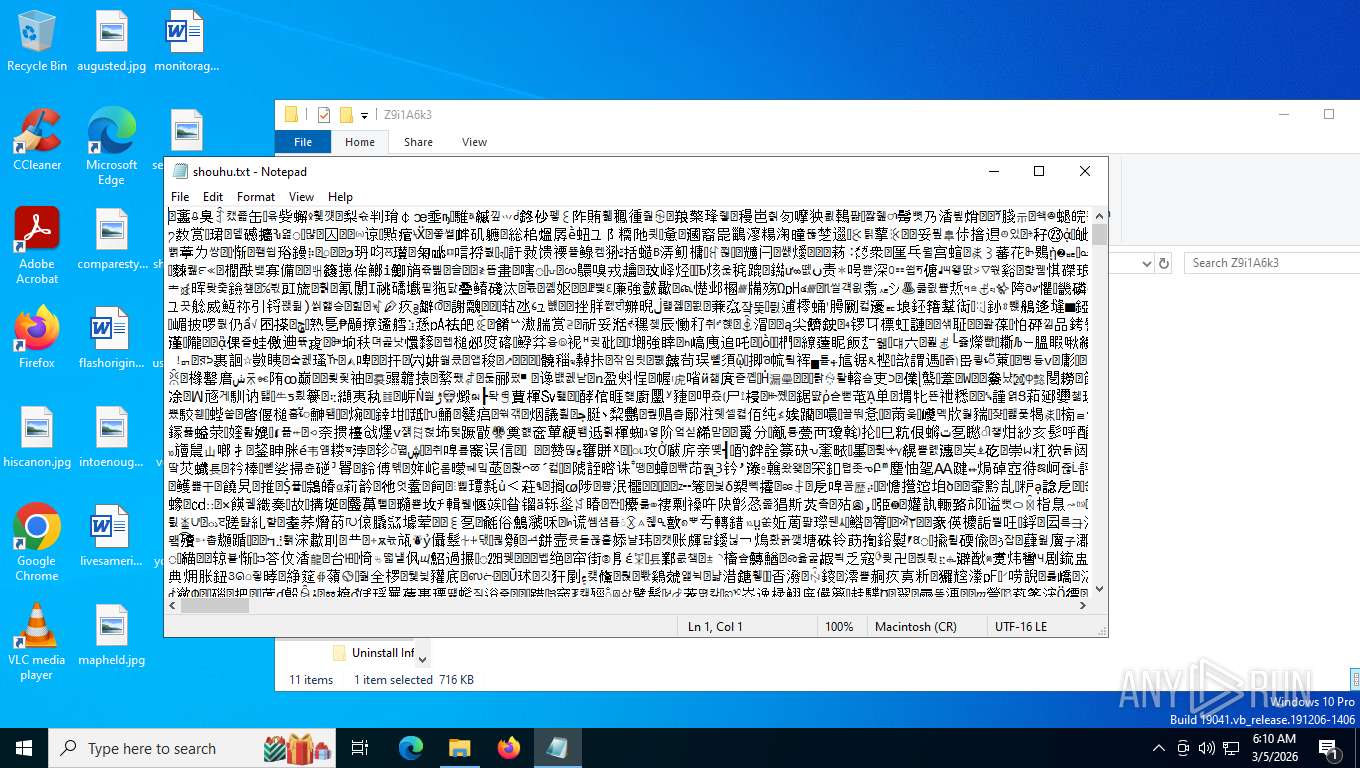
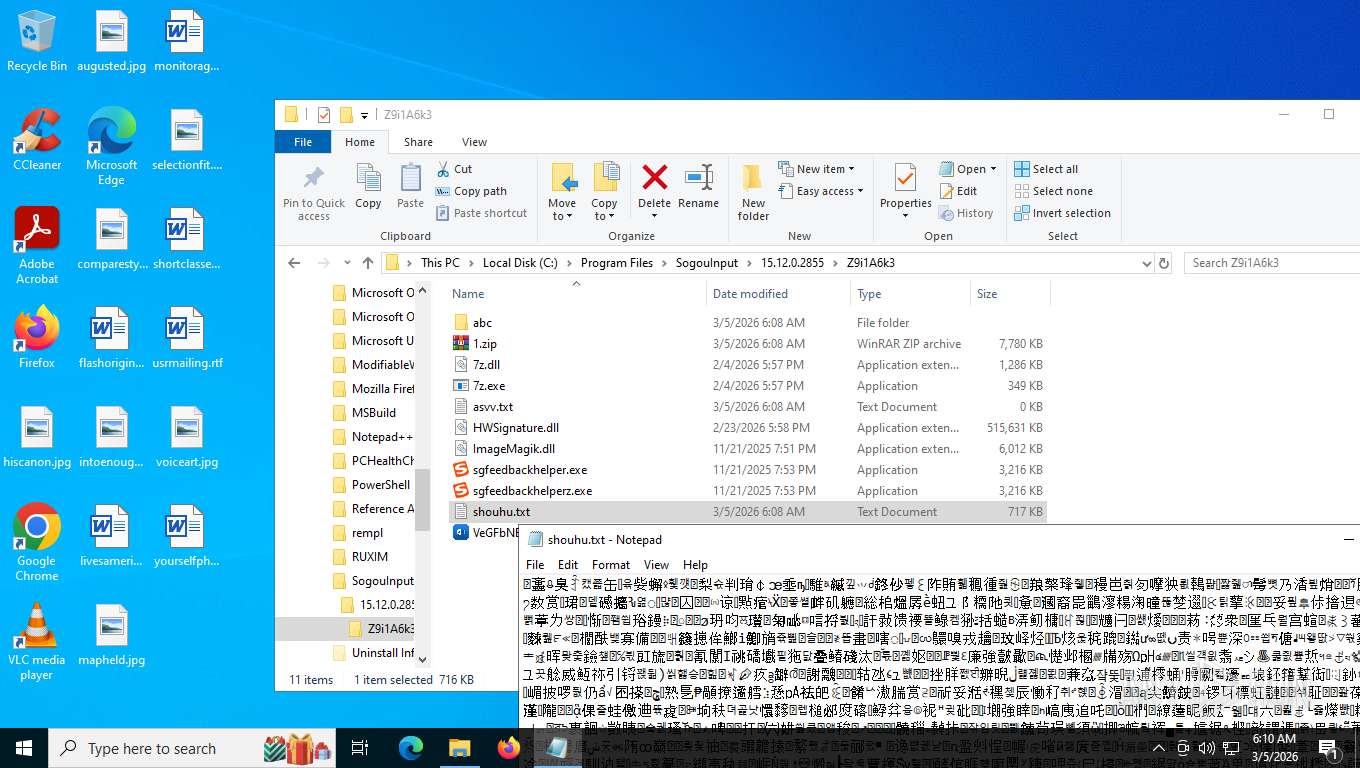
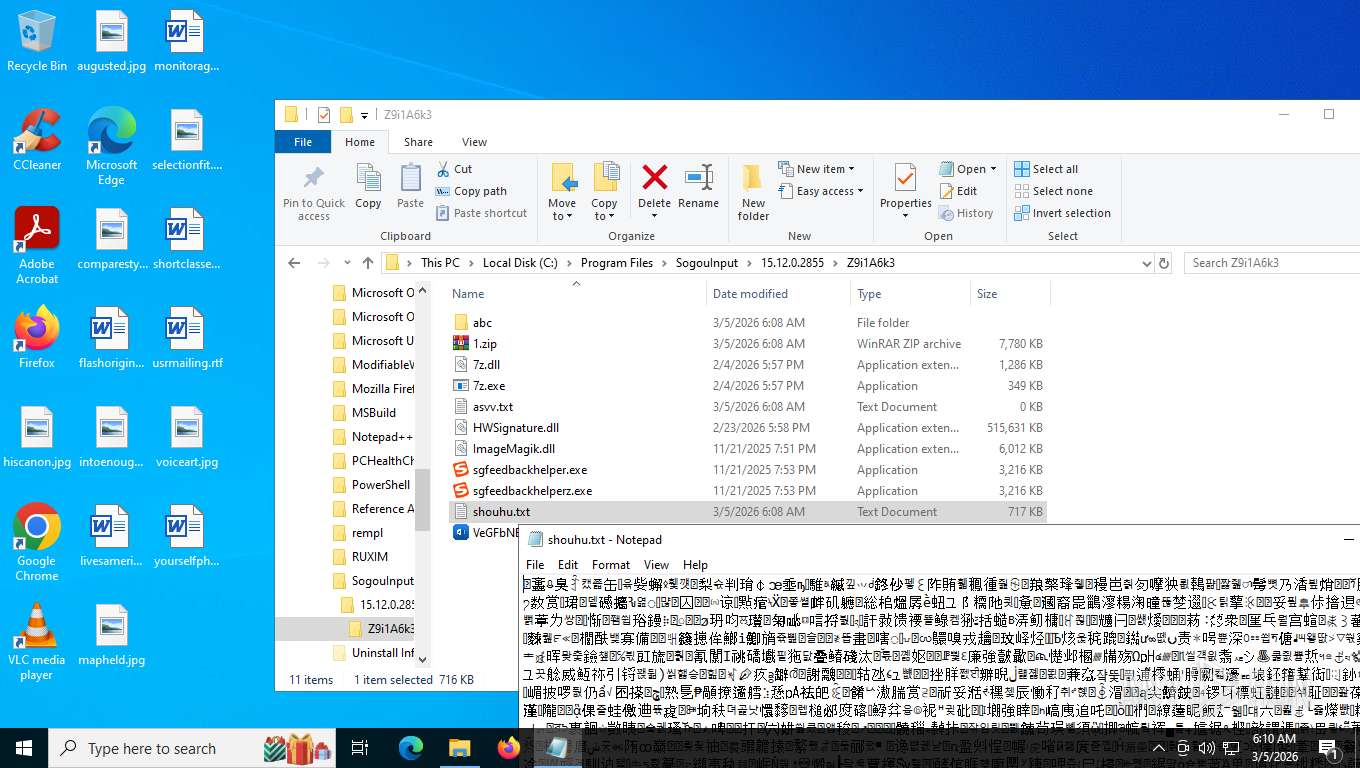
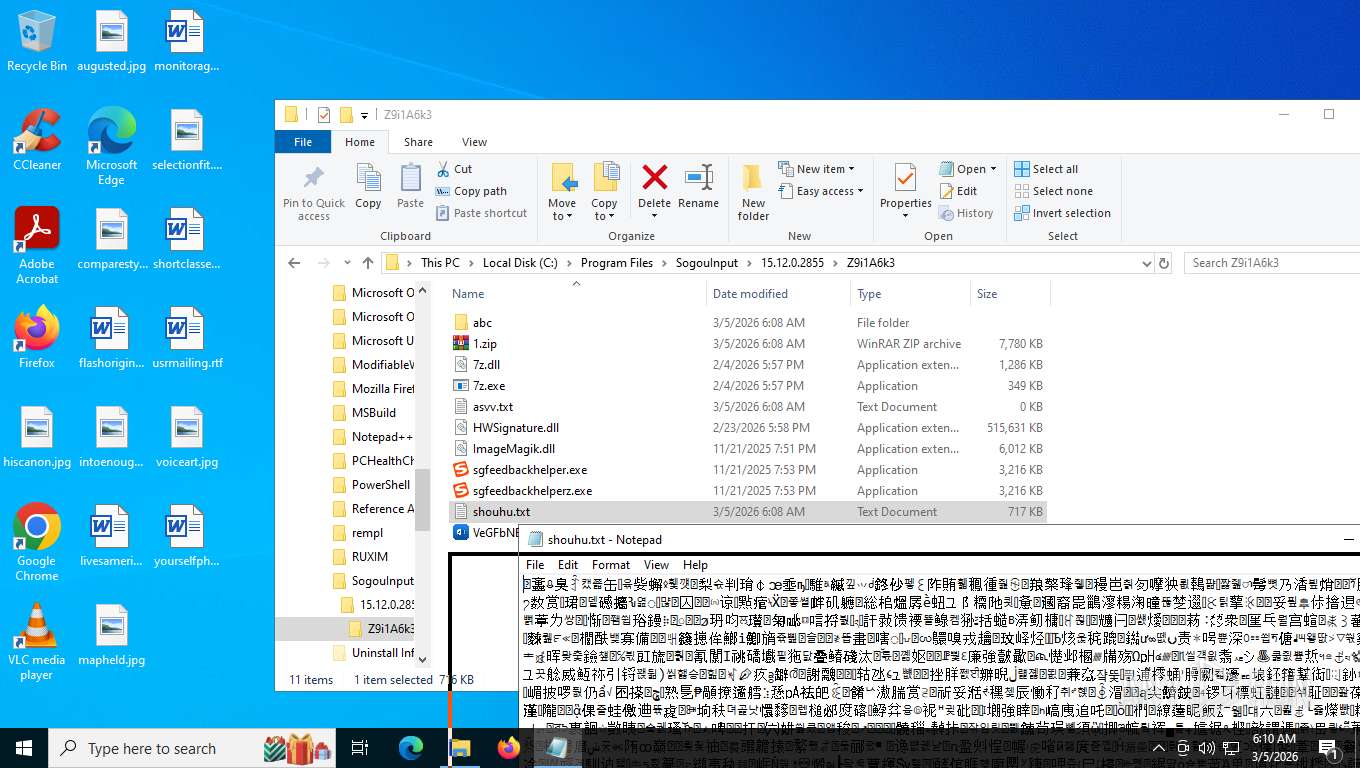
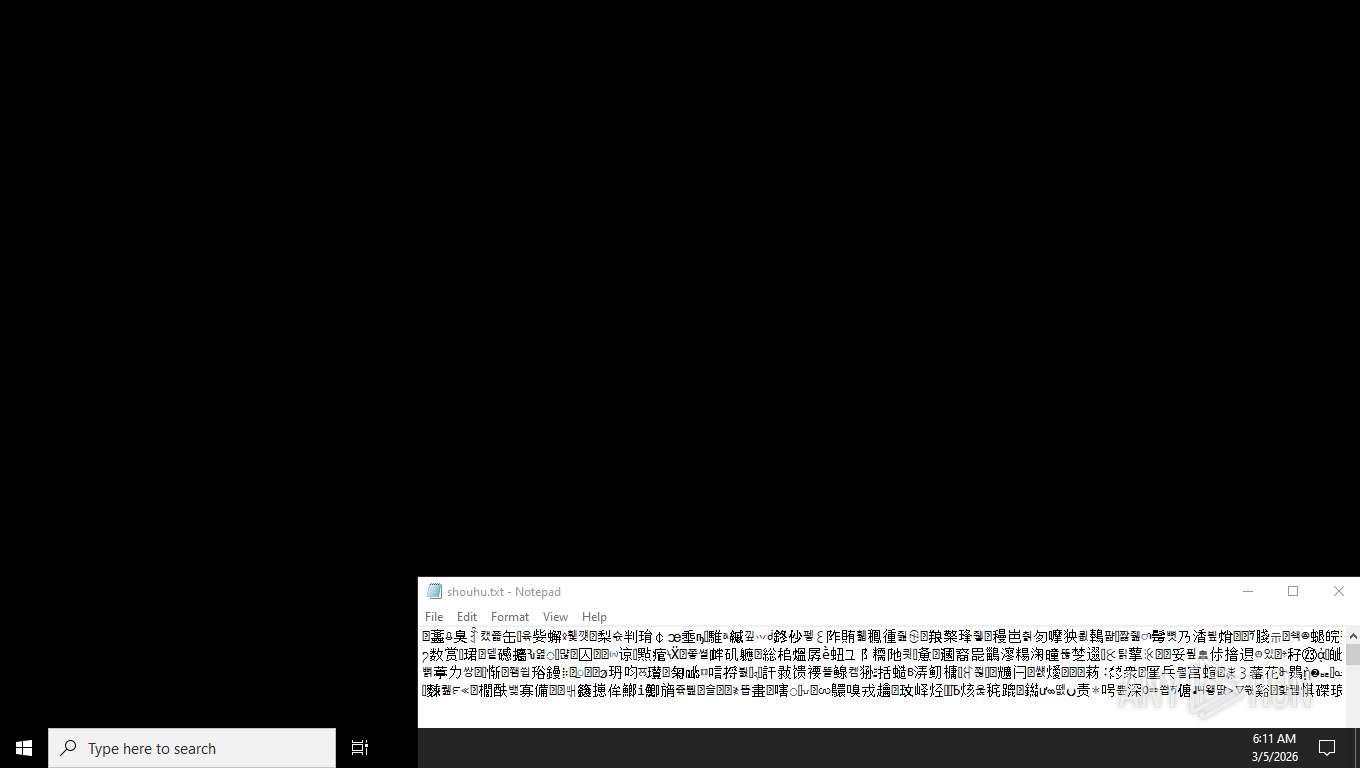
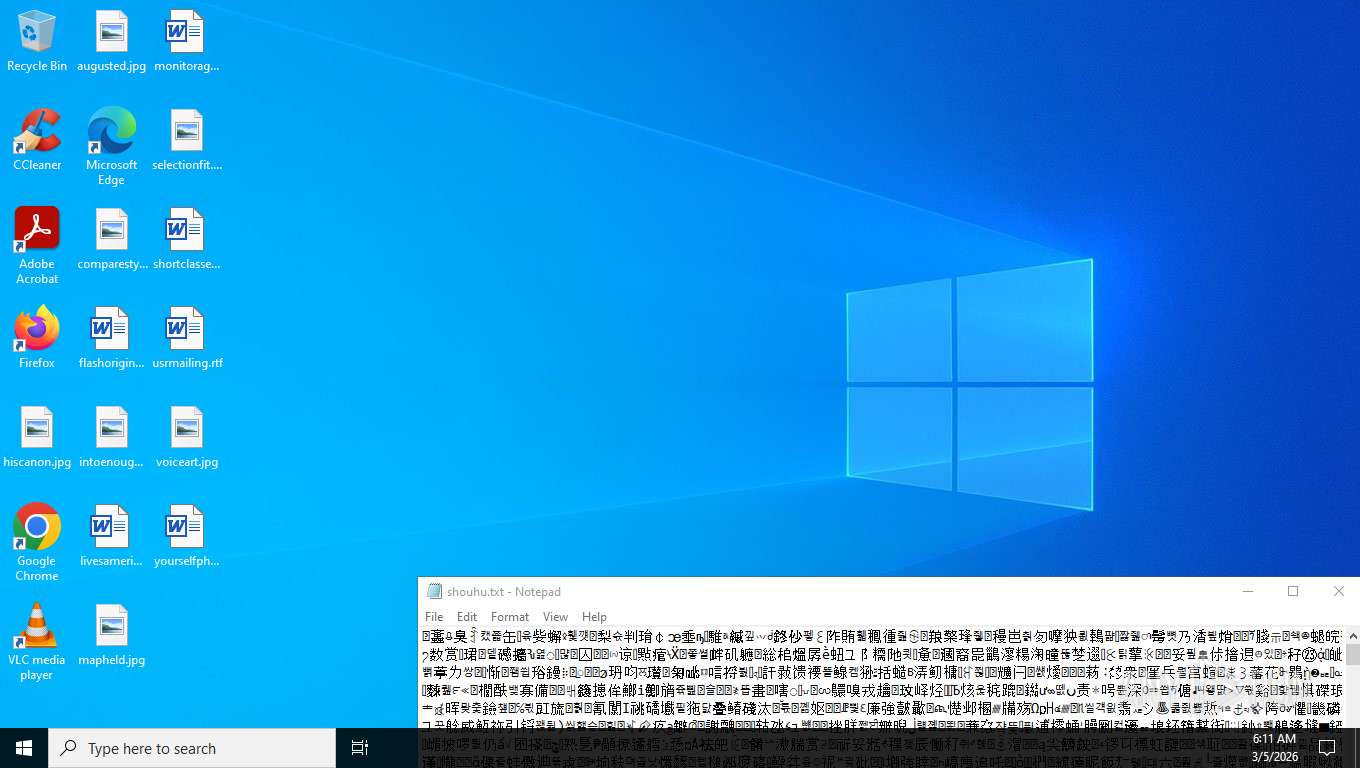
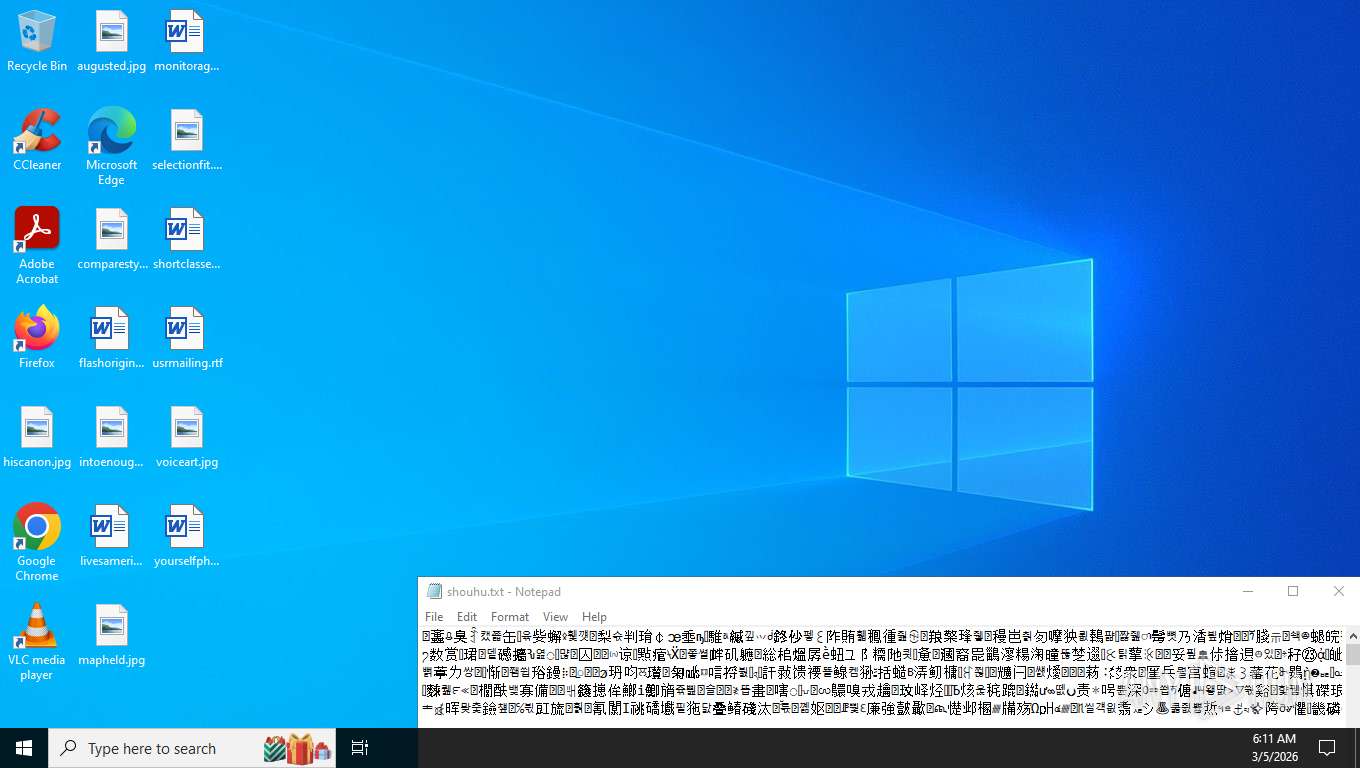
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\shouhu.txt | binary | |
MD5:0D90D16B62D4761CF83A88AD4C3BC41A | SHA256:2DA53835BA11C034E03D5A9F7DCAB80EDFABBE0D719C3DBCD97831F4358B6310 | |||
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\1.zip | compressed | |
MD5:8761B0E4FE304F6D2E54793C6F32E5AC | SHA256:C767FB075C38191F4FA7CC46AAC2369532EFA8E69B803FDF25B3673A7FC5E01A | |||
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\ImageMagik.dll | executable | |
MD5:CDFDF1939AA7A065AA9F3CD07A99ACDE | SHA256:B7934FD46C2FEF0EE93DCB33D03A9CEB7A560670F1666FA4EF0E66D04F7FB396 | |||
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Users\admin\AppData\Local\Temp\1772708926\....\TemporaryFile | executable | |
MD5:5EAF63EEEACF25C6EBB053737979B237 | SHA256:9D5E2993CB7369FE21013D30125626E597B94DA70228328E7253540041998374 | |||
| 6640 | 5eaf63eeeacf25c6ebb053737979b237.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\sgfeedbackhelper.exe | executable | |
MD5:BE9D0FD7235FD9C760ACABE2B26502FF | SHA256:B2230F1E1E4FE538EB3C513E6612D82453E708AC94373B155624A656620F1BBC | |||
| 132 | sgfeedbackhelper.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\Z9i1A6k3.lnk | binary | |
MD5:63ADA8215A678139B8CB0DBD263672F1 | SHA256:B201159B0CC5A17F900B1EB71732DFD6CC404B1A860522A094172A71EBD447A8 | |||
| 3636 | VeGFbNBjNedca.exe | C:\Program Files\SogouInput\15.12.0.2855\Z9i1A6k3\VeGFbNBj.zip | compressed | |
MD5:0108420081617FFC304CF051CB0F6EFD | SHA256:E2424A4972BC385E4A3F98E2238E4355BC58032161D327ED351AB5BB4273C1CE | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6768 | MoUsoCoreWorker.exe | GET | 304 | 40.127.240.158:443 | https://settings-win.data.microsoft.com/settings/v3.0/OneSettings/Client?OSVersionFull=10.0.19045.4046.amd64fre.vb_release.191206-1406&LocalDeviceID=s%3ABAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&AttrDataVer=186&OSUILocale=en-US&OSSkuId=48&App=WOSC&AppVer=&IsFlightingEnabled=0&TelemetryLevel=1&DeviceFamily=Windows.Desktop | US | — | — | whitelisted |
7236 | svchost.exe | GET | 304 | 51.124.78.146:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/UpdateHealthTools?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=s:BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&sampleId=s:95271487&appVer=10.0.19041.3626&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=SedimentPack&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | — | — | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
356 | svchost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAz1vQYrVgL0erhQLCPM8GY%3D | US | binary | 471 b | whitelisted |
356 | svchost.exe | POST | 200 | 20.190.160.65:443 | https://login.live.com/RST2.srf | US | xml | 1.24 Kb | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
356 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
7236 | svchost.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6696 | RUXIMICS.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6768 | MoUsoCoreWorker.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 2.16.204.149:443 | www.bing.com | AKAMAI-ASN1 | NL | whitelisted |
— | — | 172.211.123.248:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
356 | svchost.exe | 20.190.160.65:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
356 | svchost.exe | 184.30.131.245:80 | ocsp.digicert.com | AKAMAI-AS | US | whitelisted |
7236 | svchost.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
oneocsp.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
5512 | MoUsoCoreWorker.exe | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |