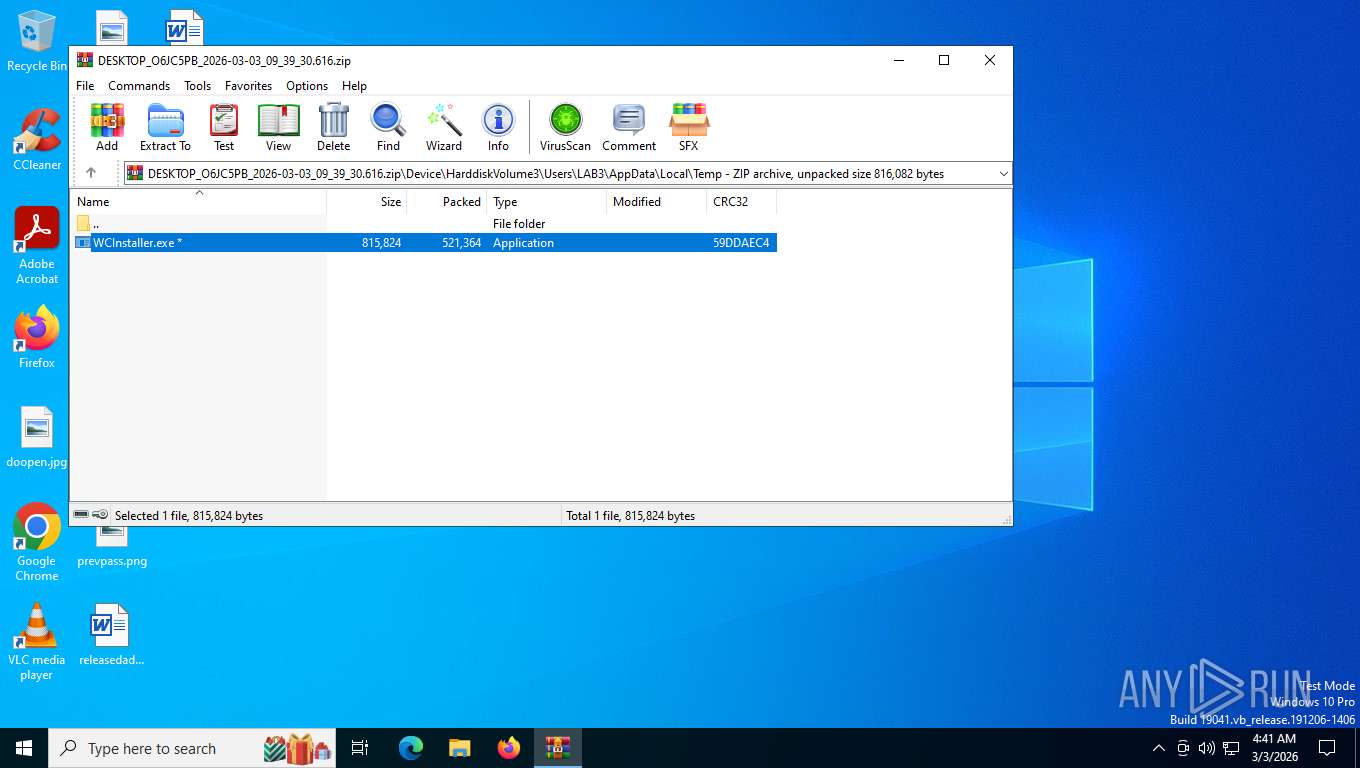
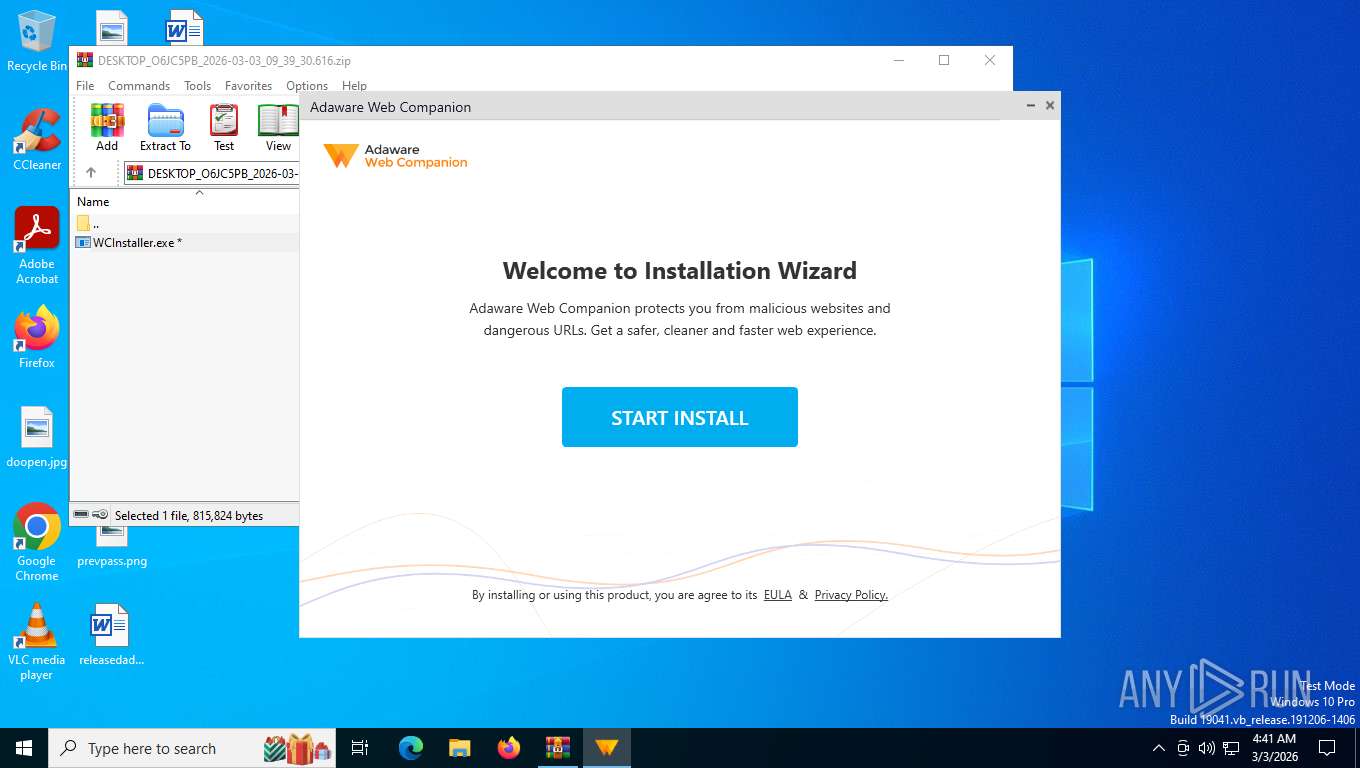
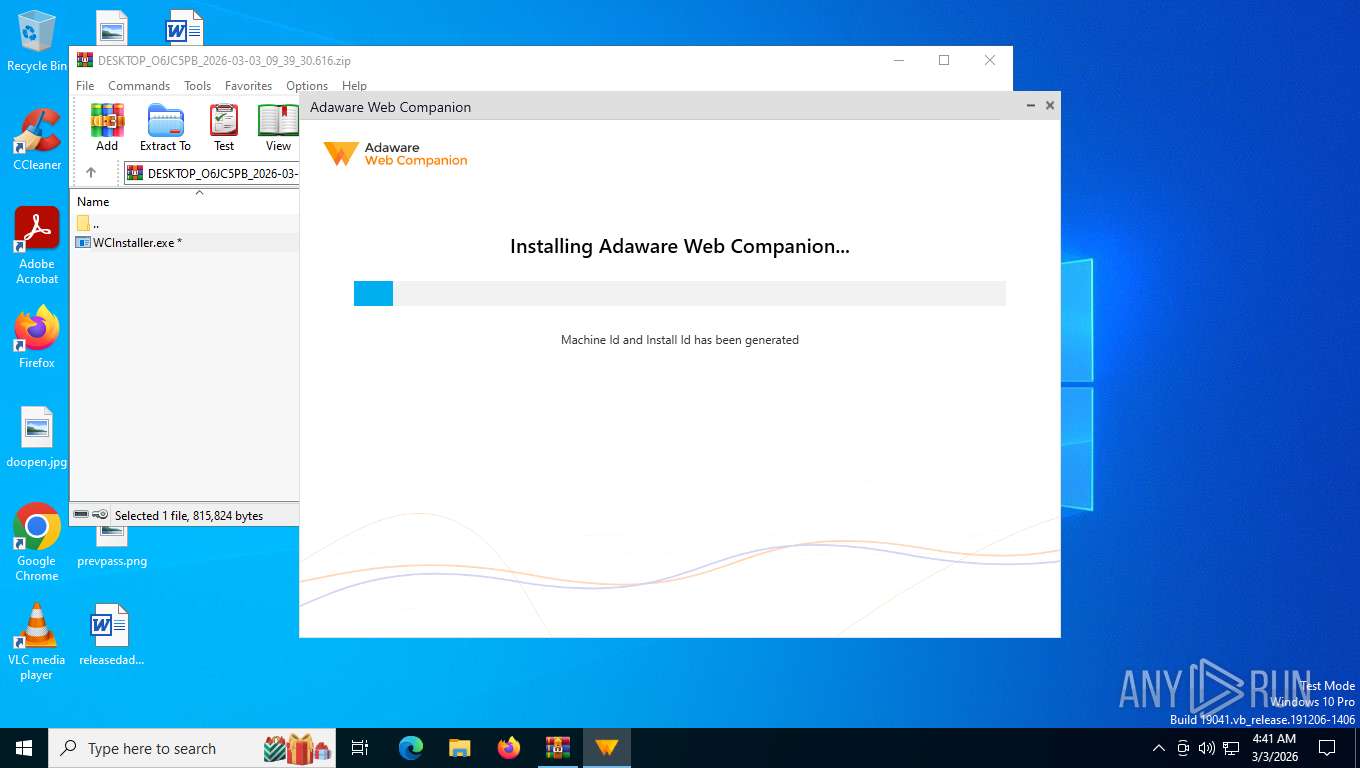
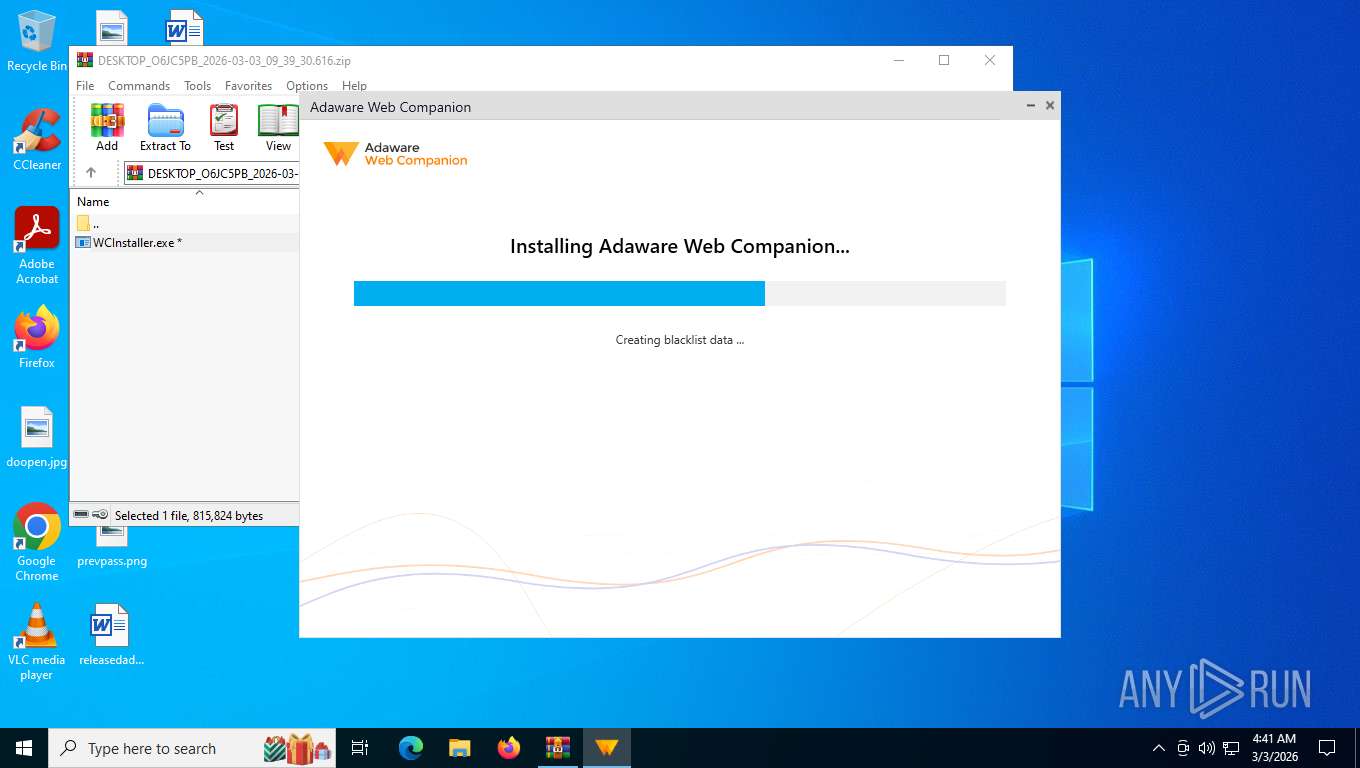
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
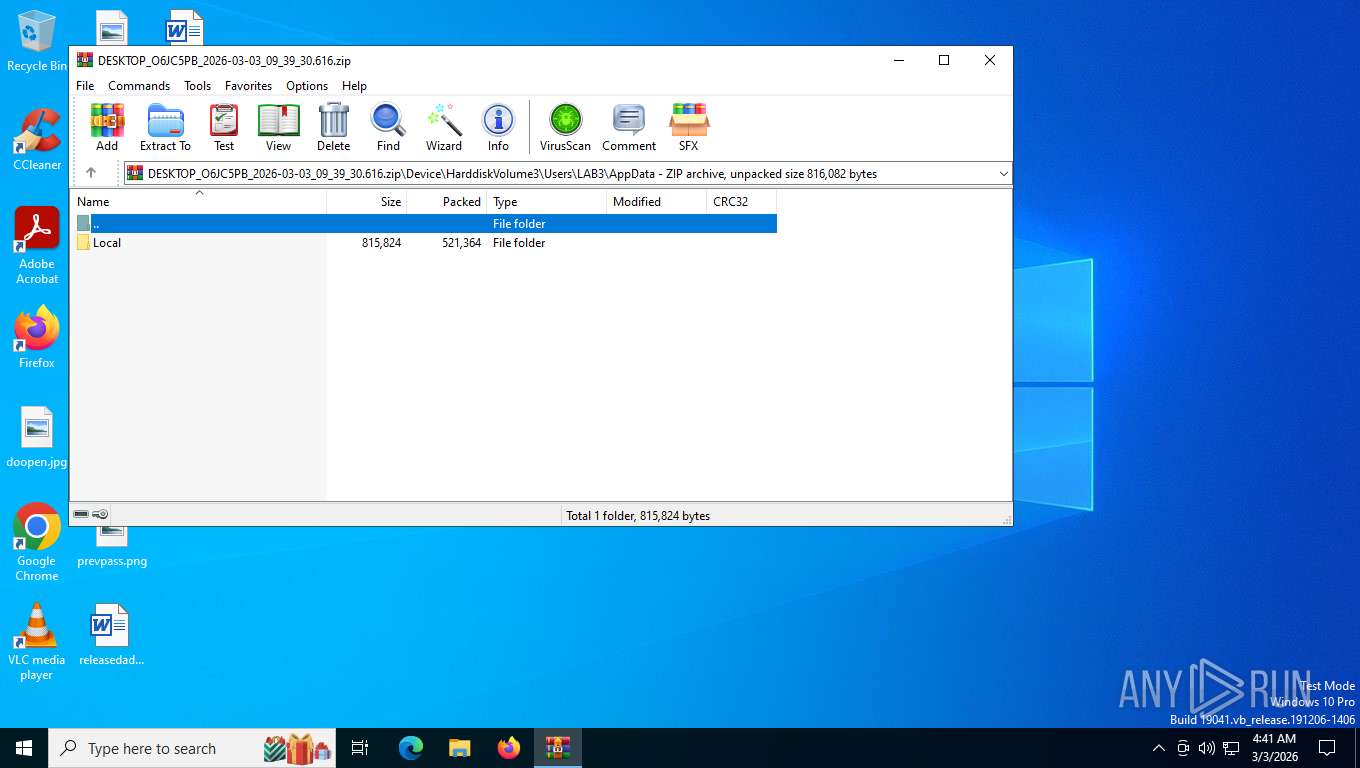
| File name: | DESKTOP_O6JC5PB_2026-03-03_09_39_30.616.zip |
| Full analysis: | https://app.any.run/tasks/4eef7615-cad9-4f6a-b8a8-dbfda78092f3 |
| Verdict: | Malicious activity |
| Threats: | Adware is a form of malware that targets users with unwanted advertisements, often disrupting their browsing experience. It typically infiltrates systems through software bundling, malicious websites, or deceptive downloads. Once installed, it may track user activity, collect sensitive data, and display intrusive ads, including pop-ups or banners. Some advanced adware variants can bypass security measures and establish persistence on devices, making removal challenging. Additionally, adware can create vulnerabilities that other malware can exploit, posing a significant risk to user privacy and system security. |
| Analysis date: | March 03, 2026, 09:40:56 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v4.5 to extract, compression method=deflate |
| MD5: | A75AB2A57CEA363F94C16D2C60B004F7 |
| SHA1: | F9FF9E2A2FB851A8B6BD4D4F6A0A097088EA978A |
| SHA256: | 94A71593A5F8D601AE8F5F645A9C2D4D859E82AA8B8229084FF9185E0A867094 |
| SSDEEP: | 24576:Hzg7um0jKWaO5KMx20tjY71Z0eNsZuCotn+fy25+ersTumNAU1jue:Hzg7um0jKWaO5KMx20tjY71Z0eNsZuCg |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | 0x0801 |
| ZipCompression: | Deflated |
| ZipModifyDate: | 1980:00:00 00:00:00 |
| ZipCRC: | 0x59ddaec4 |
| ZipCompressedSize: | 521364 |
| ZipUncompressedSize: | 815824 |
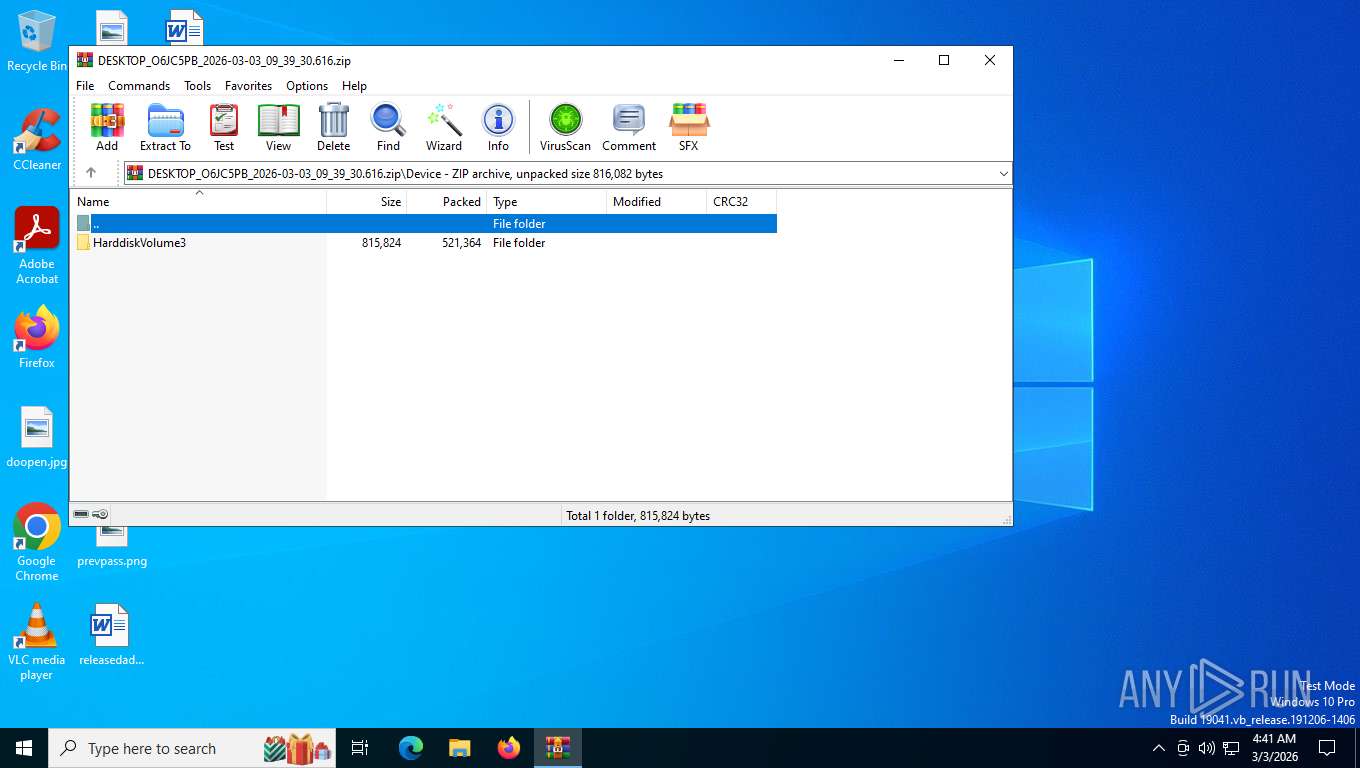
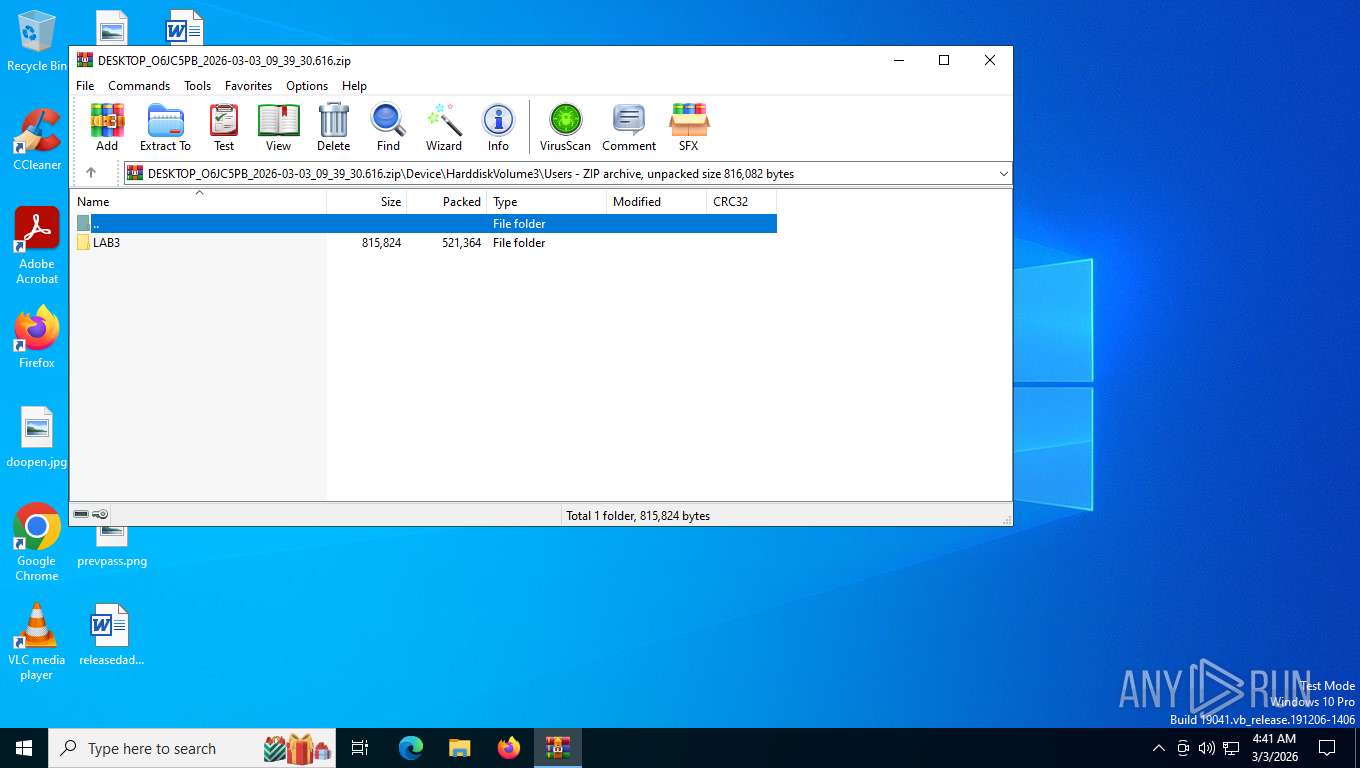
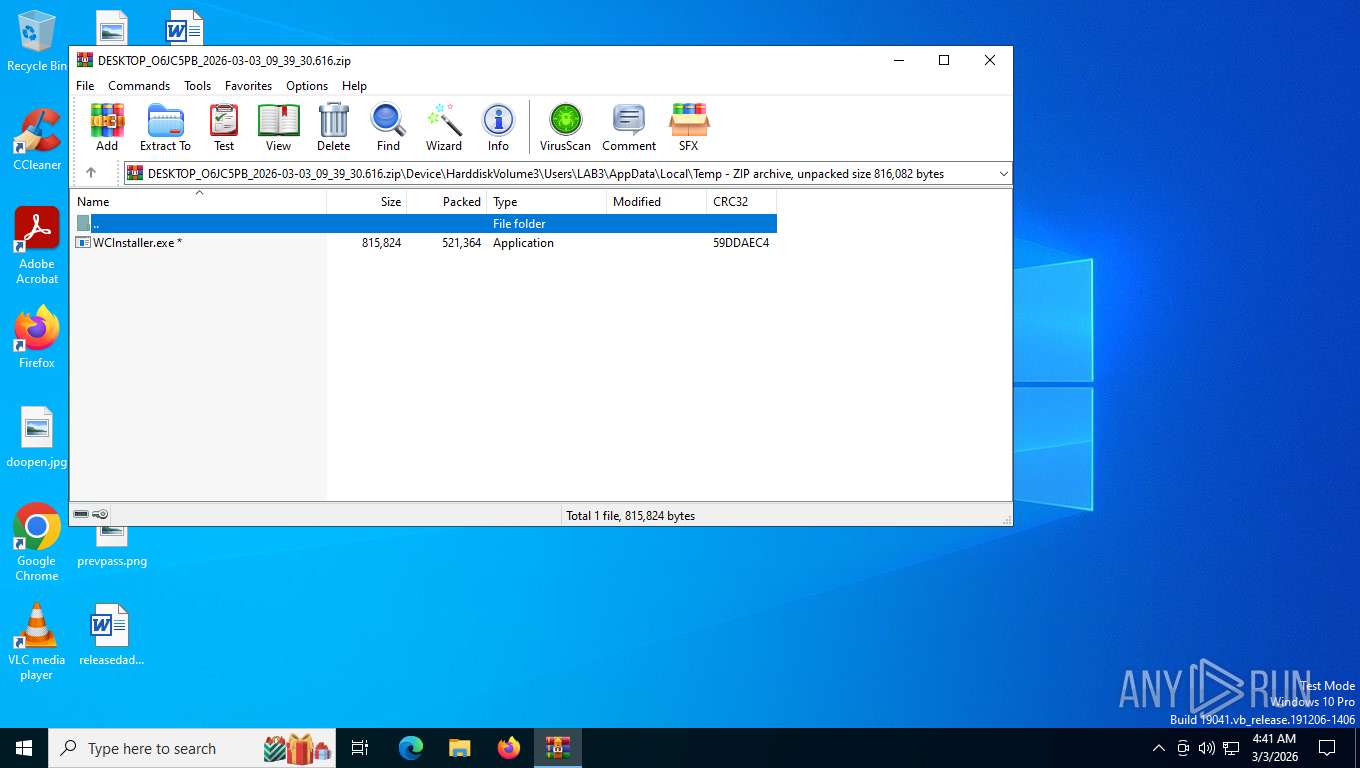
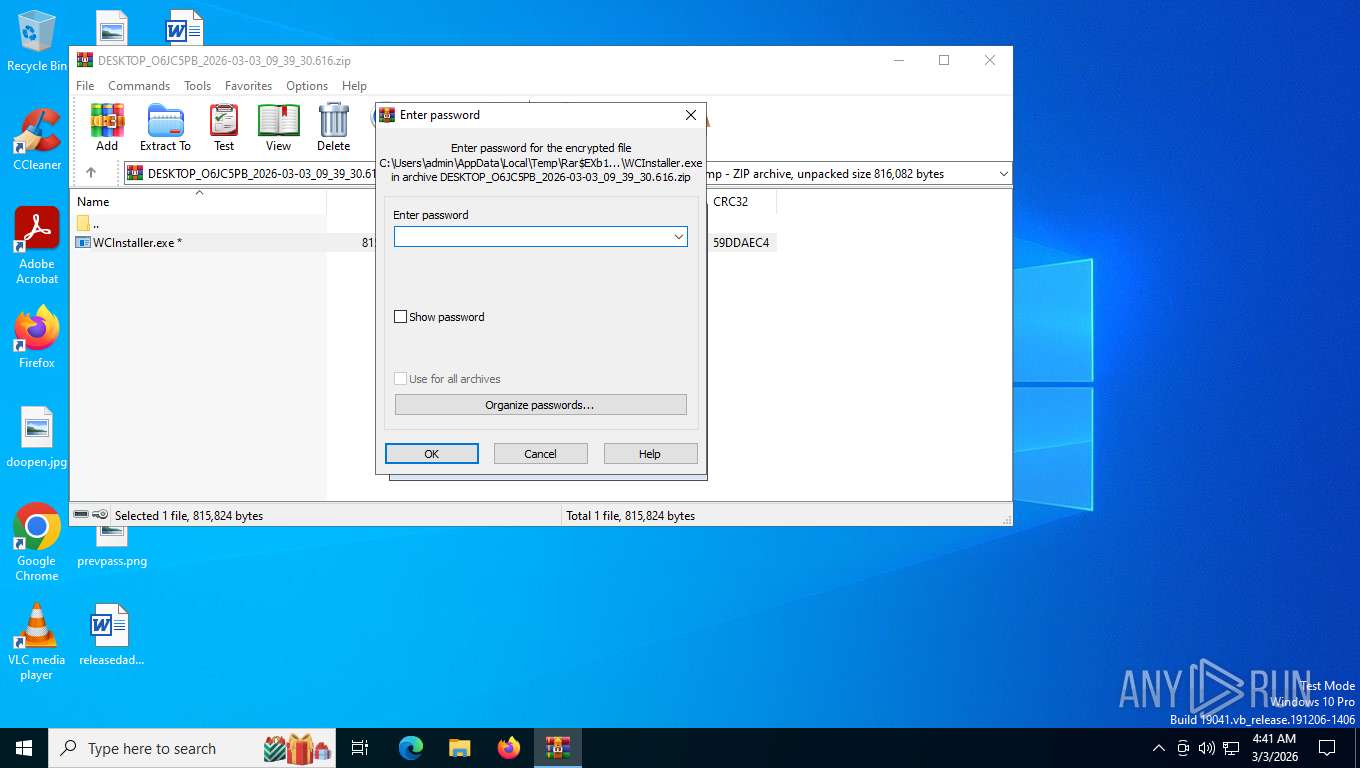
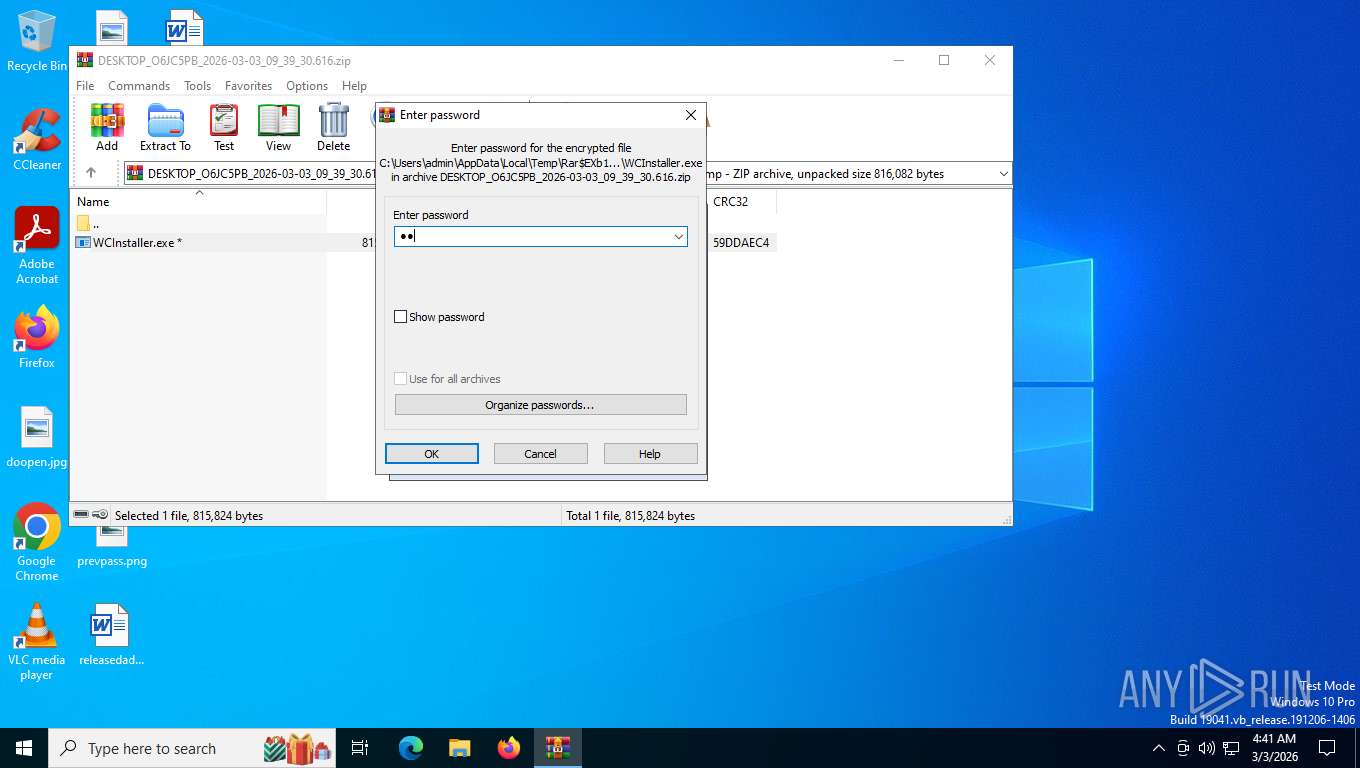
| ZipFileName: | Device/HarddiskVolume3/Users/LAB3/AppData/Local/Temp/WCInstaller.exe |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1084 | "sc.exe" Create "DCIService" binPath= "C:\Program Files (x86)\Lavasoft\Web Companion\Service\x64\DCIService.exe" DisplayName= "DCIService" start= auto | C:\Windows\SysWOW64\sc.exe | — | WCInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1760 | C:\WINDOWS\system32\net1 start bddci | C:\Windows\System32\net1.exe | — | net.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
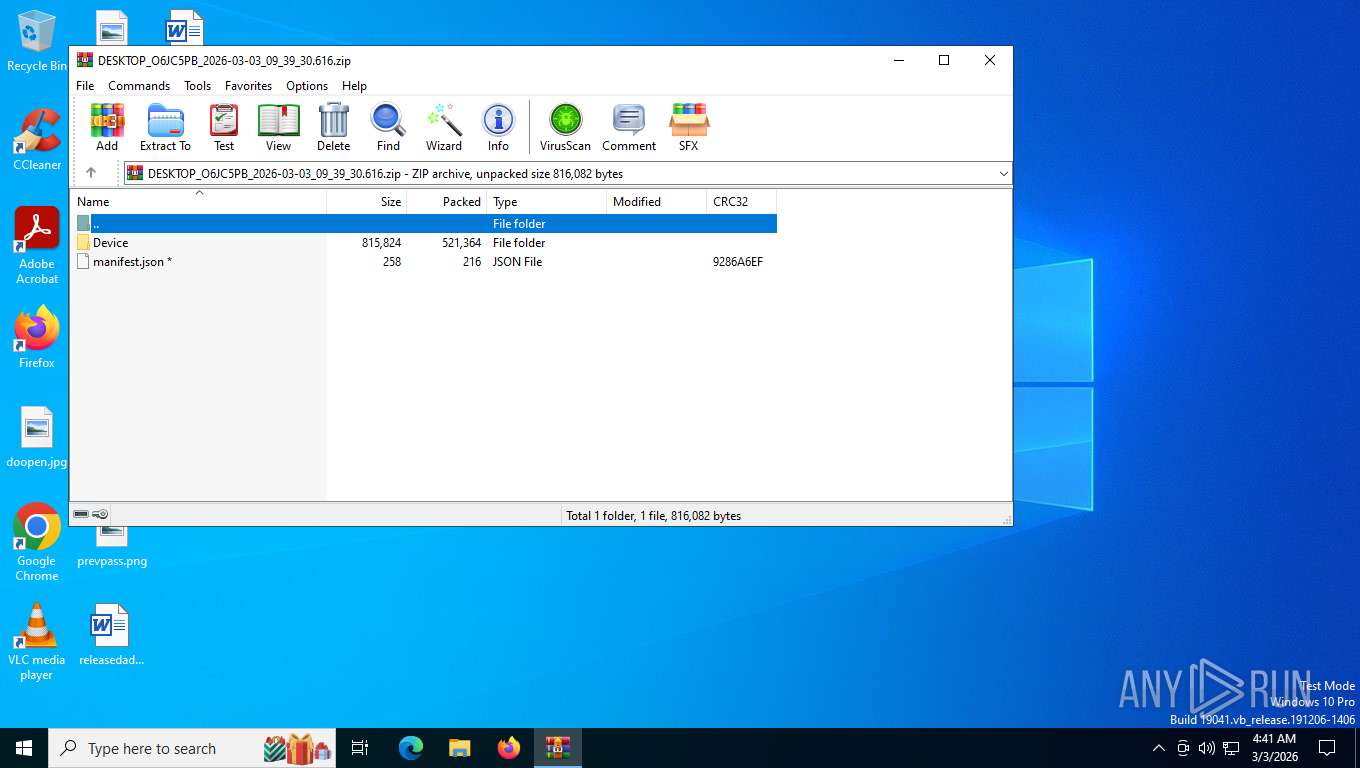
| 1840 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\DESKTOP_O6JC5PB_2026-03-03_09_39_30.616.zip | C:\Program Files\WinRAR\WinRAR.exe | explorer.exe | ||||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Version: 5.91.0 Modules
| |||||||||||||||
| 2496 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | sc.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3020 | "sc.exe" description "CompanionService" "Ad-Aware Web Companion Internet security service" | C:\Windows\SysWOW64\sc.exe | — | WCInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3192 | "sc.exe" Create "CompanionService" binPath= "C:\Program Files (x86)\Lavasoft\Web Companion\Application\CompanionService.WinService.exe" DisplayName= "Companion Service" start= auto | C:\Windows\SysWOW64\sc.exe | — | WCInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4644 | "C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe" --install --geo= | C:\Program Files (x86)\Lavasoft\Web Companion\Application\WebCompanion.exe | WCInstaller.exe | ||||||||||||
User: admin Company: Lavasoft Integrity Level: HIGH Description: Web Companion Version: 14.2.5.13567 Modules
| |||||||||||||||
| 4700 | "C:\Users\admin\AppData\Local\Temp\Rar$EXb1840.1018\Device\HarddiskVolume3\Users\LAB3\AppData\Local\Temp\WCInstaller.exe" | C:\Users\admin\AppData\Local\Temp\Rar$EXb1840.1018\Device\HarddiskVolume3\Users\LAB3\AppData\Local\Temp\WCInstaller.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Lavasoft Integrity Level: MEDIUM Description: Web Companion Exit code: 3221226540 Version: 14.2.5.13567 Modules
| |||||||||||||||
| 4804 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | sc.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5152 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\chromium_ext.zip | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\omni_23_10_2024_.zip | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Downloads\chromium_build 1.zip | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\DESKTOP_O6JC5PB_2026-03-03_09_39_30.616.zip | |||
| (PID) Process: | (1840) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface |
| Operation: | write | Name: | ShowPassword |
Value: 0 | |||
| (PID) Process: | (8324) WCInstaller.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\WCInstaller_RASAPI32 |
| Operation: | write | Name: | EnableFileTracing |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\BCUSDK.dll | executable | |
MD5:0B1063C14E21A8B3A07E7D3A4B6C6205 | SHA256:33AD8242E6FC6B7C71B1B0972DDB972019257933914A7A3110039F95B85E9CCE | |||
| 1840 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$EXb1840.1018\Device\HarddiskVolume3\Users\LAB3\AppData\Local\Temp\WCInstaller.exe | executable | |
MD5:478DEA3E7A6F9D2ECC31419E4D5261F2 | SHA256:A34551F564CF7D1B649080203EE32B95E6BA5D7C50E2B2481977FC53D8018117 | |||
| 8324 | WCInstaller.exe | C:\Users\admin\AppData\Local\Temp\WC\App.config | xml | |
MD5:4488D78B4AE19275BE35177D9E818BBA | SHA256:B238E109CEA93140470DE6412D5AFEB8663D1AB1785E7D234AB827291629053C | |||
| 1840 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$EXb1840.1018\manifest.json | text | |
MD5:AA54B6D33405829C187DA6C70F7E784B | SHA256:1CD8E0503C953BD3D95AF01948417E6063F5B7DF56529BF812CC6C05193E2325 | |||
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\CompanionService.Wcf.dll.config | xml | |
MD5:FE23C4EB3329EF255BE914714ADBF35D | SHA256:C6DC041A92C38FEFA20299ED91E1B1FC4CA8AB83F07C336B149820D160F2EE05 | |||
| 8324 | WCInstaller.exe | C:\ProgramData\Lavasoft\Web Companion\Options\Statistics.txt | text | |
MD5:083D3049B42702C4D3721C77AAC07527 | SHA256:78BE6EB878392710078286DD83B2D30FA949FE4A37E3303E61B42B5B7162128D | |||
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\BCUEngineS.dll | executable | |
MD5:DB11C7E28A2E8A680873232C710504D8 | SHA256:68AFDEB99C717BAB1C91E6EFC9DAAA6294B1A8C21FCAE0DDE6D564EB57C617AC | |||
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\CompanionService.Wcf.dll | executable | |
MD5:20FC2A8AA591C6CFCBBEE42B1326BC7F | SHA256:588B93A6AAA0BB38321B02889B11D188B56922B5C5081B30BDFBD134544518B7 | |||
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\CompanionService.WinService.exe | executable | |
MD5:9B4797365F0F7257FC83FD0C6D1BAF3E | SHA256:031C4F9753F41C8D25AD76B0DF01E6834BA2CEB795E5E0228D4D79305571D210 | |||
| 8324 | WCInstaller.exe | C:\Program Files (x86)\Lavasoft\Web Companion\Application\CompanionService.WinService.exe.config | xml | |
MD5:B3D25C3859D007758FE56B3CB988577F | SHA256:85E6DB0CDA658F5C1382FFC97BF2FBB9BB796434B0E1205A250D7F407582A26F | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
8324 | WCInstaller.exe | GET | 204 | 104.16.148.130:443 | https://partner-tracking.lavasoft.com/api/tracking/wc?downloadedDate=2026-03-03T09%3A41%3A16.9360363Z | US | — | — | unknown |
6768 | MoUsoCoreWorker.exe | GET | 304 | 4.231.128.59:443 | https://settings-win.data.microsoft.com/settings/v3.0/OneSettings/Client?OSVersionFull=10.0.19045.4046.amd64fre.vb_release.191206-1406&LocalDeviceID=s%3ABAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&AttrDataVer=186&OSUILocale=en-US&OSSkuId=48&App=WOSC&AppVer=&IsFlightingEnabled=0&TelemetryLevel=1&DeviceFamily=Windows.Desktop | US | — | — | whitelisted |
7564 | svchost.exe | GET | 304 | 4.231.128.59:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/UpdateHealthTools?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=s:BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&sampleId=s:95271487&appVer=10.0.19041.3626&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=SedimentPack&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | — | — | whitelisted |
8324 | WCInstaller.exe | POST | 200 | 104.16.148.130:443 | https://featureflags.lavasoft.com/api/feature/WC | US | text | 981 b | unknown |
8324 | WCInstaller.exe | POST | 200 | 104.18.26.149:443 | https://flwadw.com/v1/event-stat?Type=Start&ProductID=wc&EventVersion=1 | US | text | 29 b | unknown |
5568 | SearchApp.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAjTxtAB8my1oj8MfWpz%2F7Y%3D | US | binary | 314 b | whitelisted |
5568 | SearchApp.exe | GET | 200 | 204.79.197.203:80 | http://oneocsp.microsoft.com/ocsp/MFQwUjBQME4wTDAJBgUrDgMCGgUABBQ3L3%2F%2Fa6ADK8NraY2GXzVaYrHG4AQUb6t%2B2v%2BXQ3LsO2d33oJhNYhHQoUCEzMAAAAGb6JMMcOVb6sAAAAAAAY%3D | US | binary | 959 b | whitelisted |
356 | svchost.exe | POST | 200 | 20.190.159.0:443 | https://login.live.com/RST2.srf | US | — | 11.1 Kb | whitelisted |
356 | svchost.exe | POST | 200 | 20.190.159.0:443 | https://login.live.com/RST2.srf | US | — | 10.3 Kb | whitelisted |
356 | svchost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
7564 | svchost.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
7208 | RUXIMICS.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6768 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5568 | SearchApp.exe | 2.16.241.218:443 | www.bing.com | AKAMAI-ASN1 | NL | whitelisted |
5568 | SearchApp.exe | 184.30.131.245:80 | ocsp.digicert.com | AKAMAI-AS | US | whitelisted |
5568 | SearchApp.exe | 204.79.197.203:80 | oneocsp.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3412 | svchost.exe | 172.211.123.250:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
356 | svchost.exe | 20.190.159.0:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
oneocsp.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
login.live.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
7564 | svchost.exe | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
8324 | WCInstaller.exe | Possibly Unwanted Program Detected | ADWARE [ANY.RUN] Adaware Web Companion |
Process | Message |
|---|---|
WebCompanion.exe | Native library pre-loader is trying to load native SQLite library "C:\Program Files (x86)\Lavasoft\Web Companion\Application\x86\SQLite.Interop.dll"...
|
WebCompanion.exe | WebCompanion.exe Error: 0 : |
WebCompanion.exe | System.IO.FileNotFoundException: Could not find file 'C:\ProgramData\Lavasoft\Web Companion\Options\EventSafeguard.txt'.
File name: 'C:\ProgramData\Lavasoft\Web Companion\Options\EventSafeguard.txt'
at System.IO.__Error.WinIOError(Int32 errorCode, String maybeFullPath)
at System.IO.File.InternalMove(String sourceFileName, String destFileName, Boolean checkHost)
at System.IO.File.Move(String sourceFileName, String destFileName)
at Lavasoft.Events.EventSafeguard.RenameSafeguardFile()
|