ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
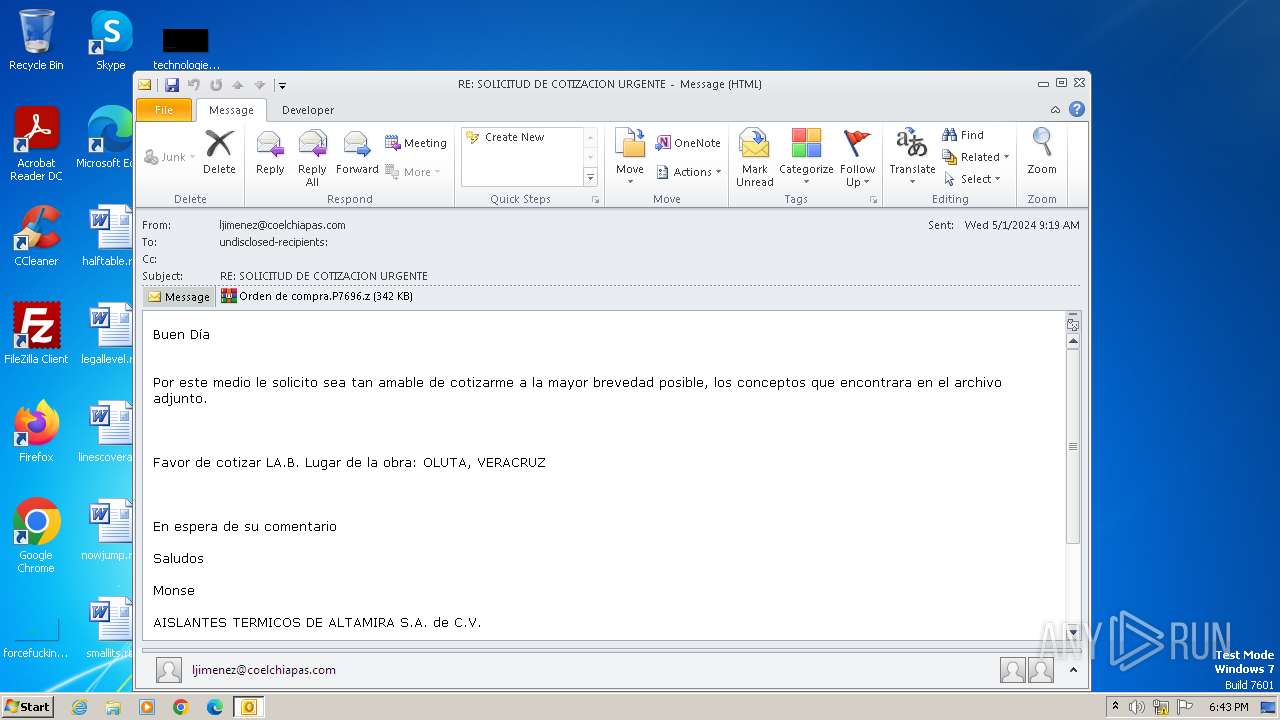
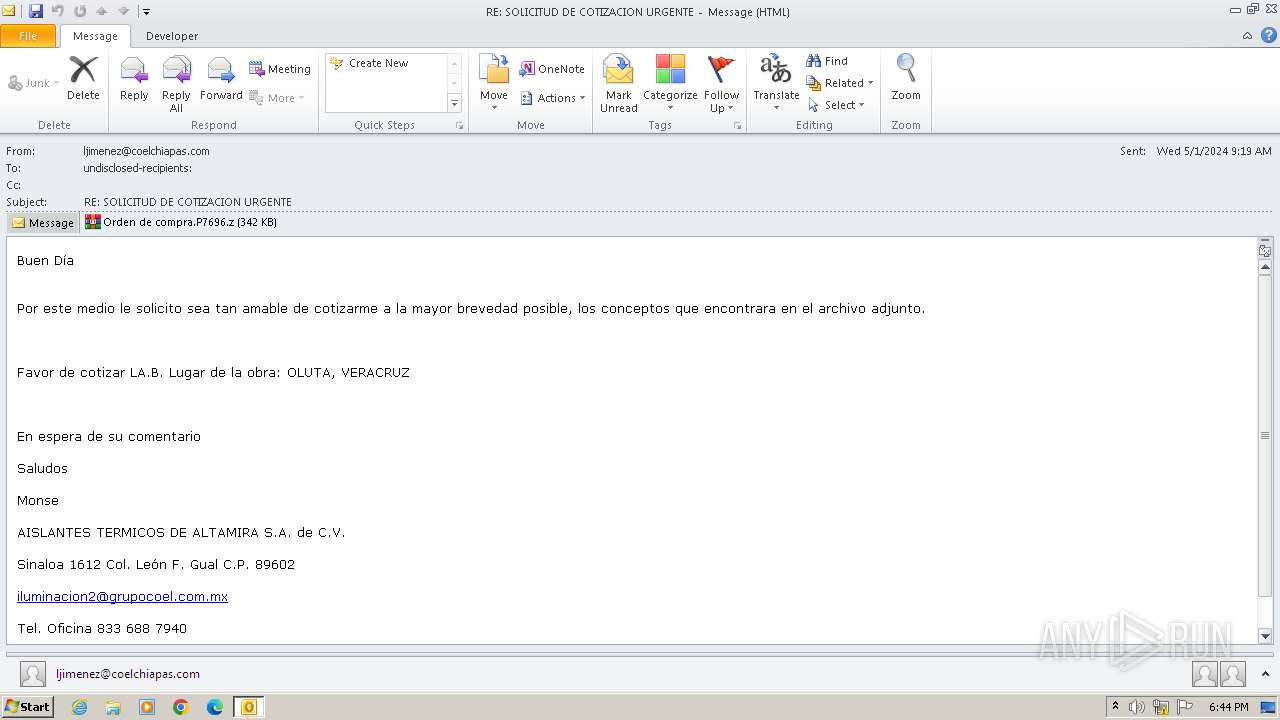
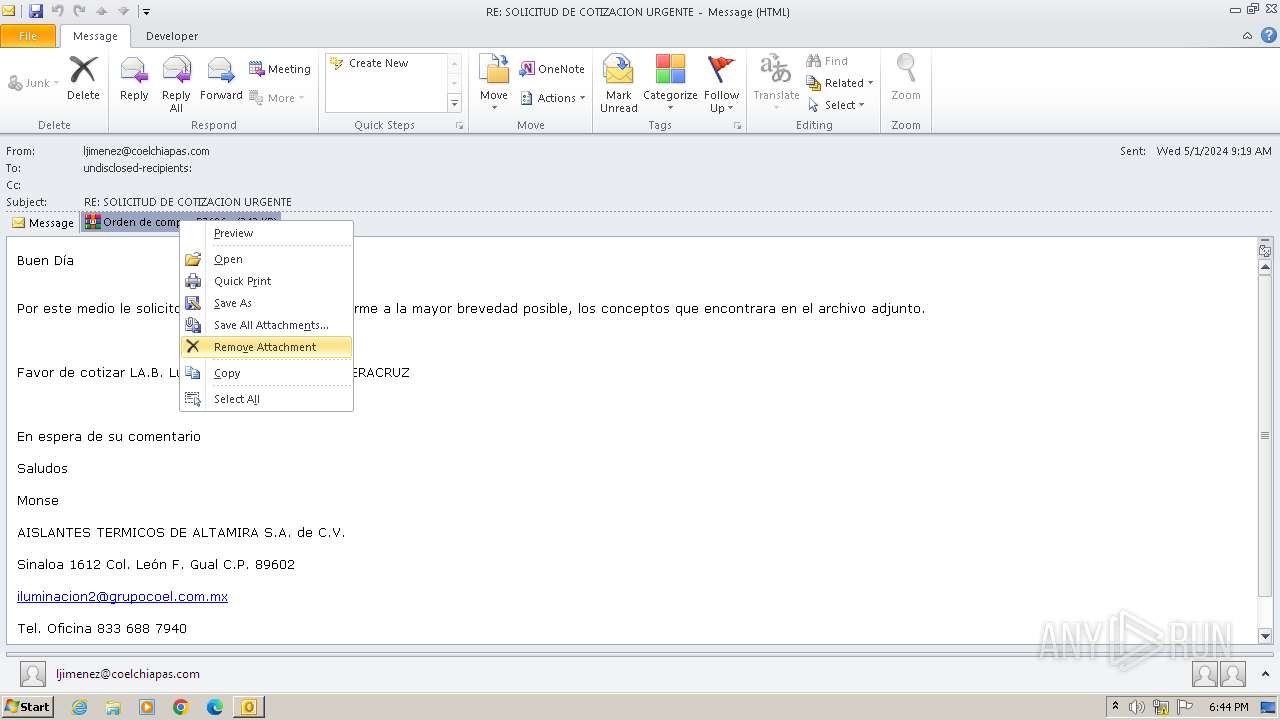
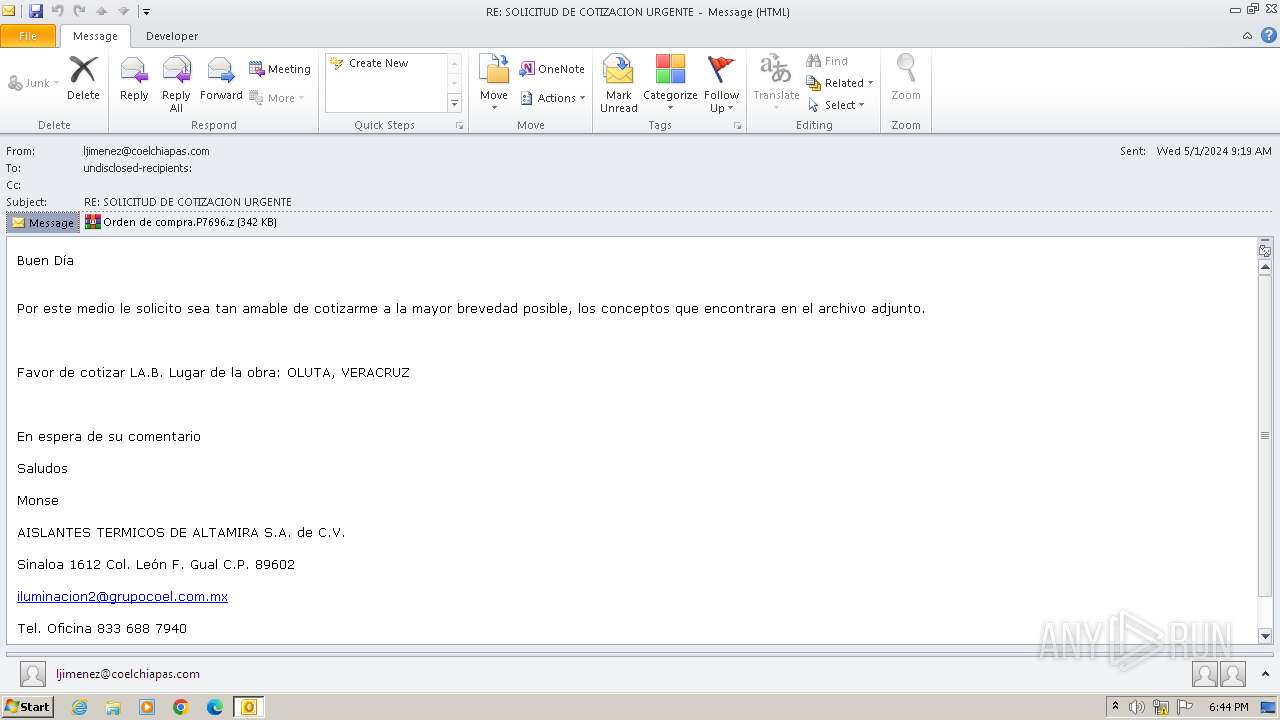
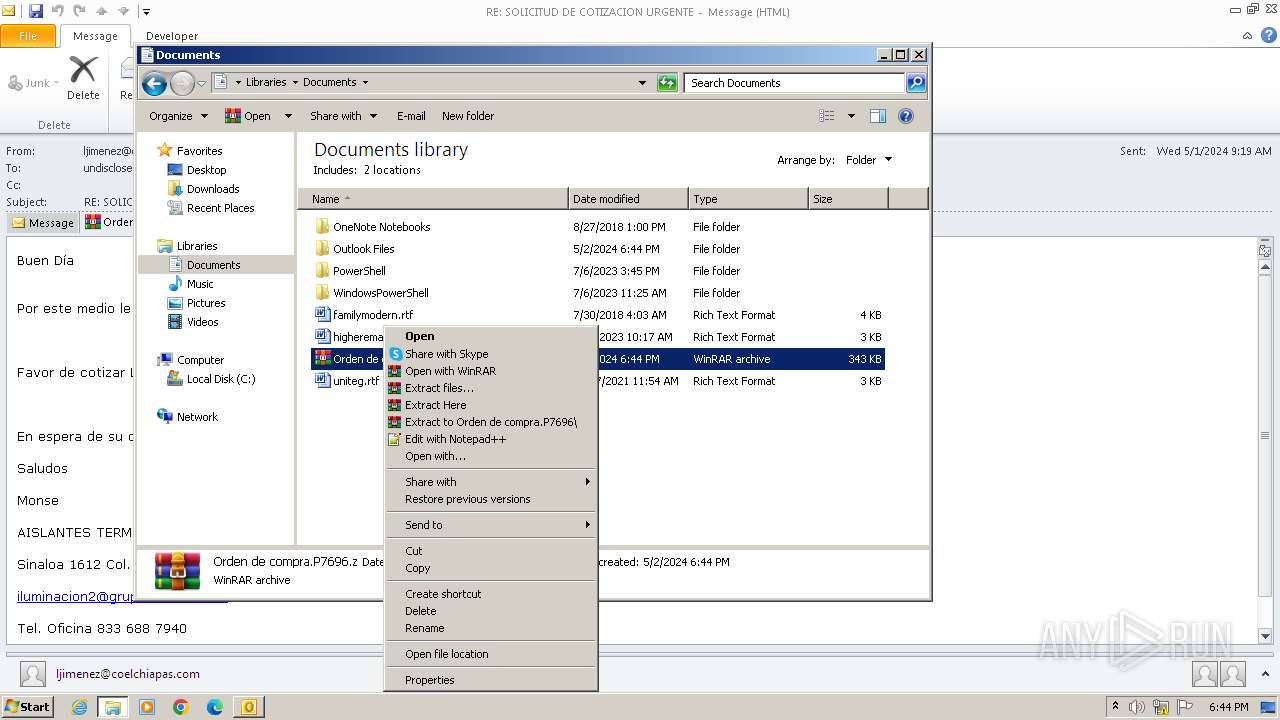
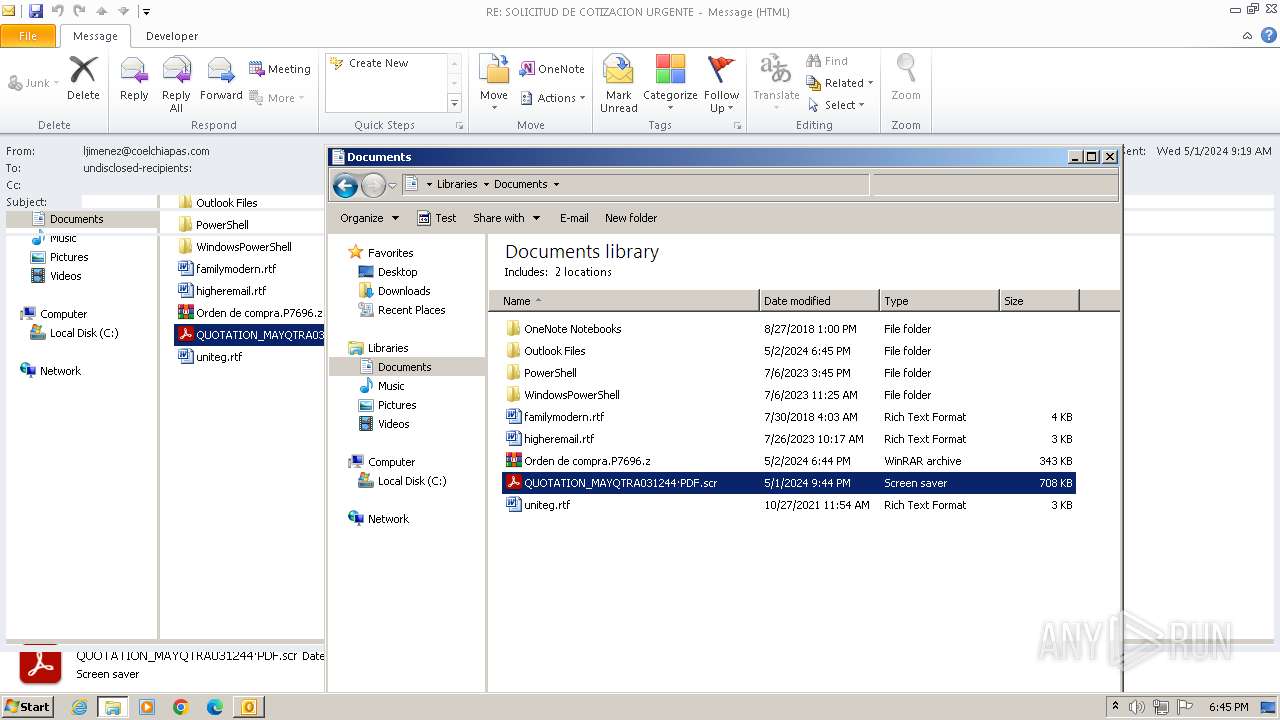
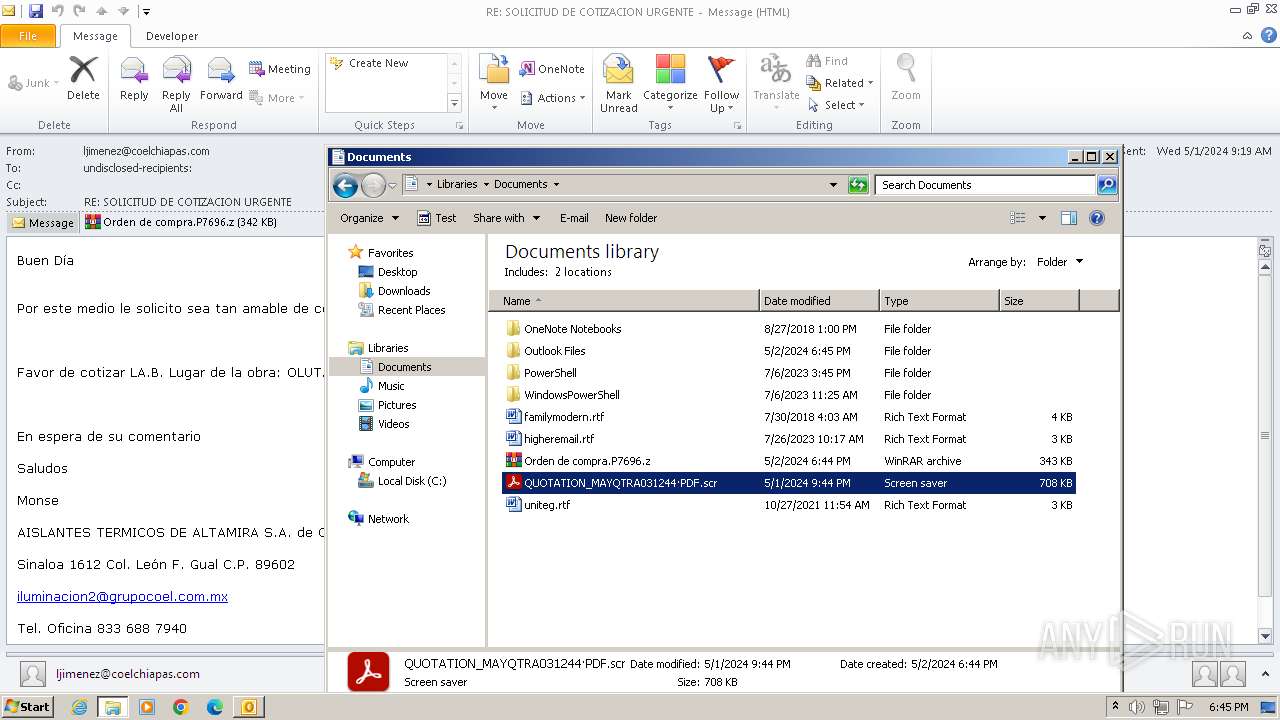
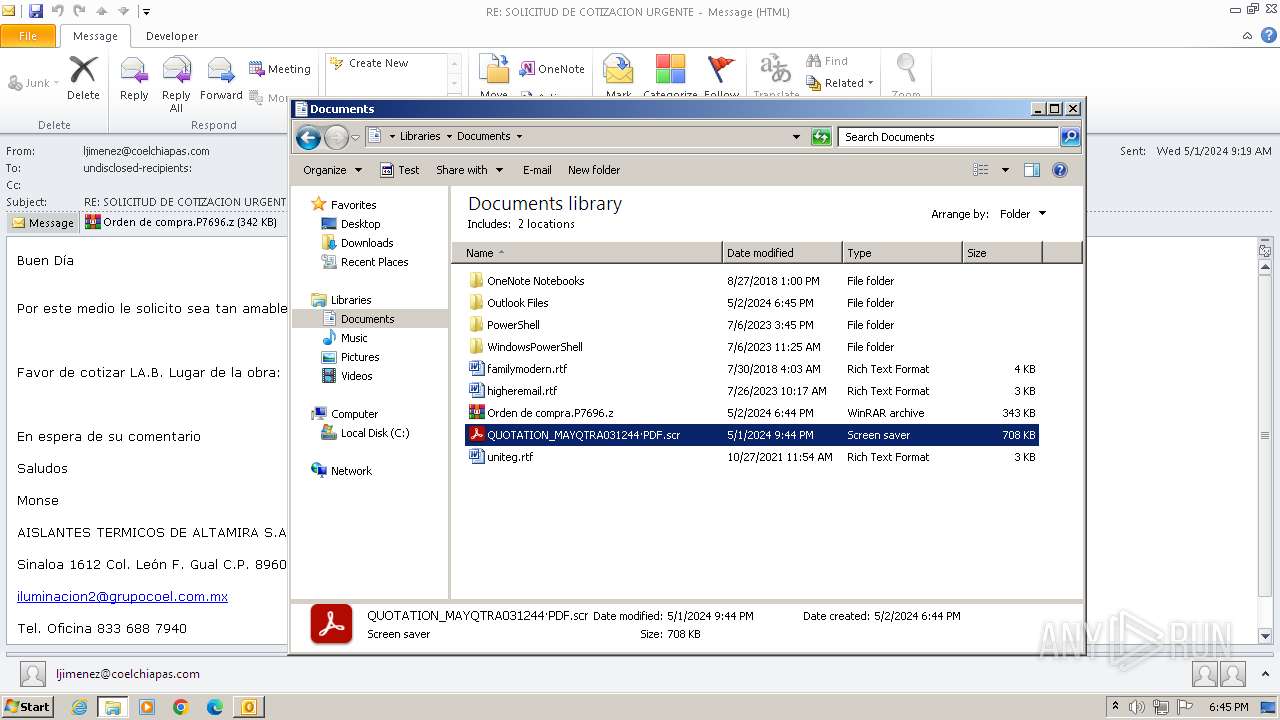
| File name: | RE_ SOLICITUD DE COTIZACION URGENTE.eml |
| Full analysis: | https://app.any.run/tasks/19d9f7b1-b0e5-4d33-bf33-f6375a136a74 |
| Verdict: | Malicious activity |
| Threats: | Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold. |
| Analysis date: | May 02, 2024, 17:43:46 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | message/rfc822 |
| File info: | SMTP mail, Unicode text, UTF-8 text, with CRLF line terminators |
| MD5: | 67A30F812E6DFAA9C4FBC01214FB5E7A |
| SHA1: | BE64250492C9861149DD375B23994FA215A31389 |
| SHA256: | 621662A893C222BB8E2B8D1A776E0516369DC8574756A98C1BF3D58F0C463226 |
| SSDEEP: | 12288:C4hU6oGo9n5mVvMw4AUydFQxn3OazaiDpJ5pg:C4mnOMkUpx35Jlpg |
| .eml | | | E-Mail message (Var. 1) (100) |
|---|
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
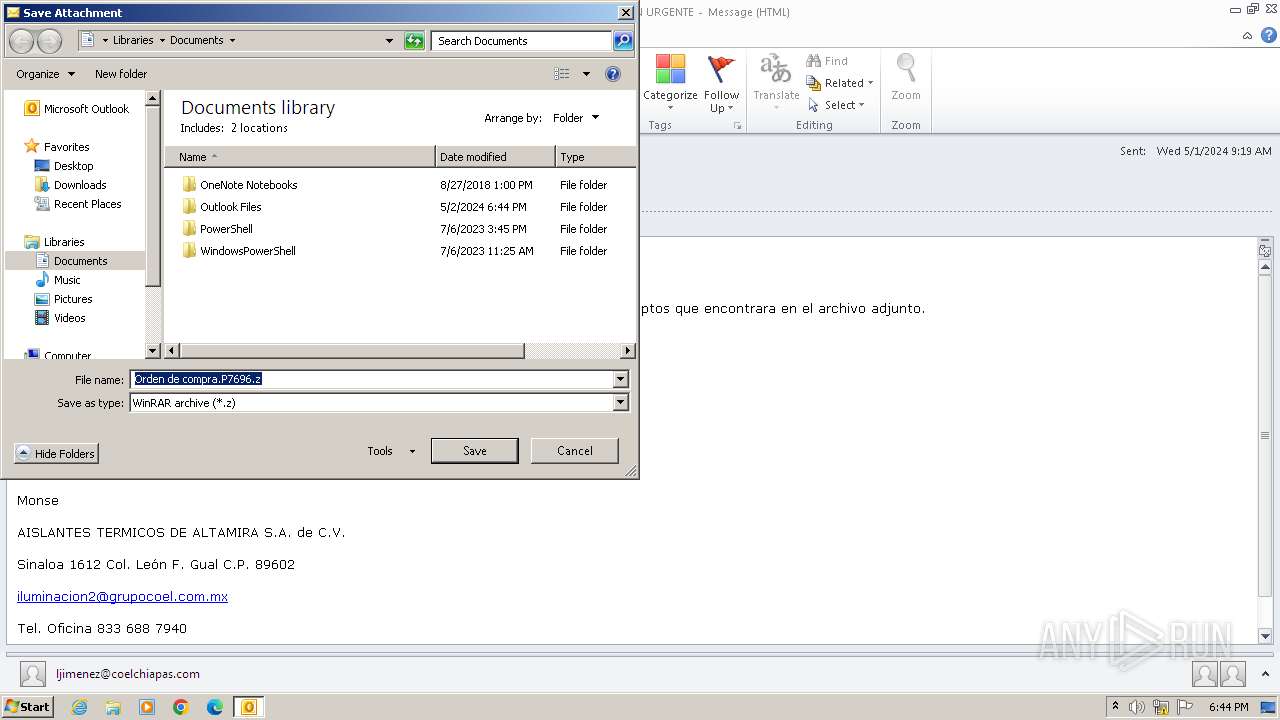
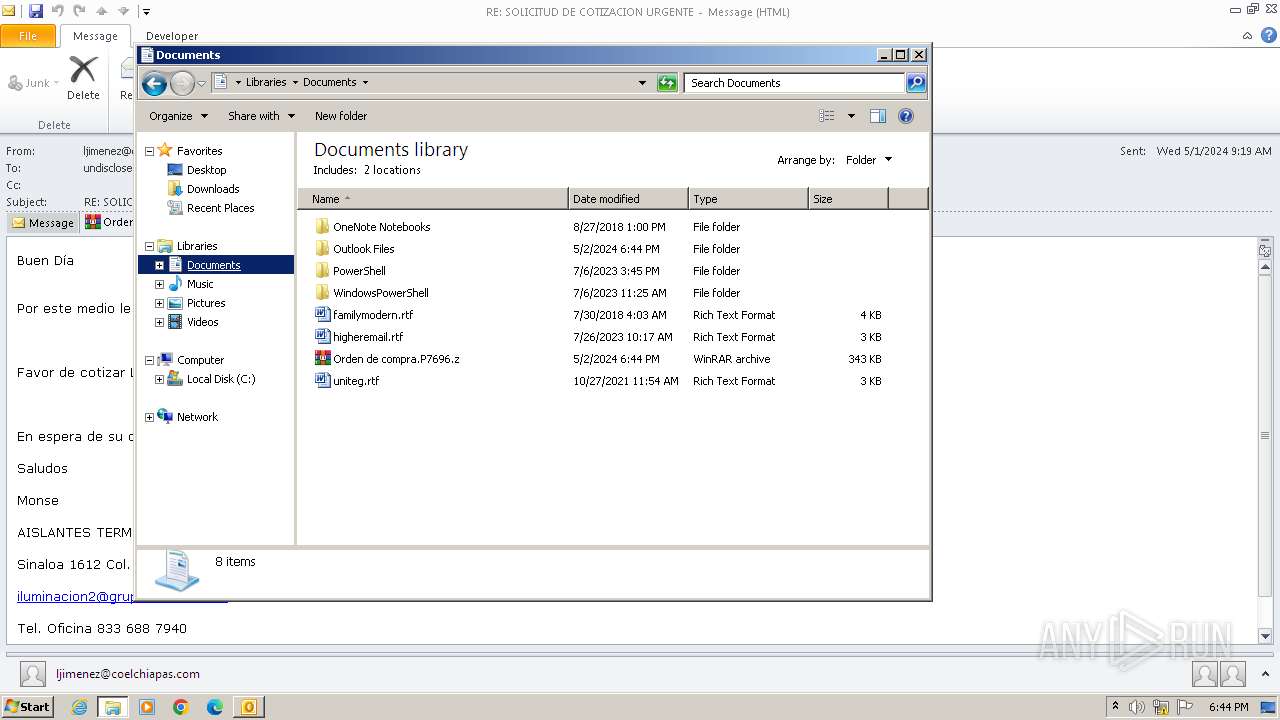
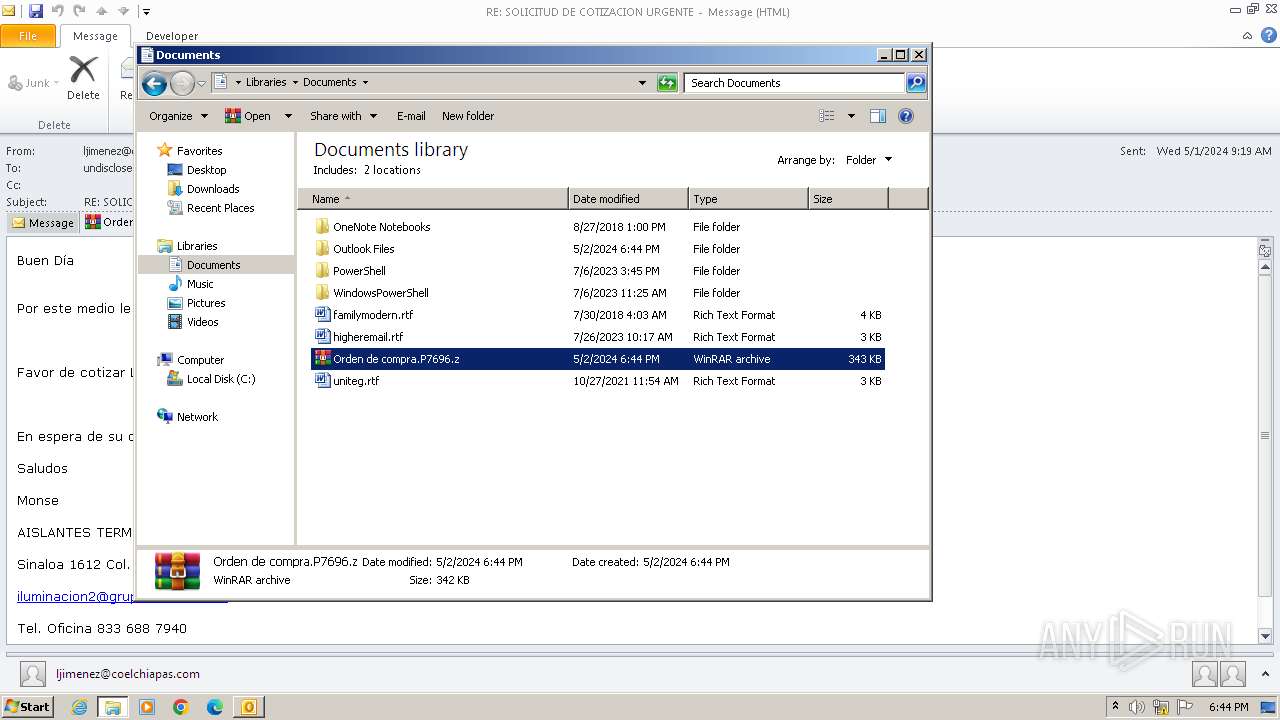
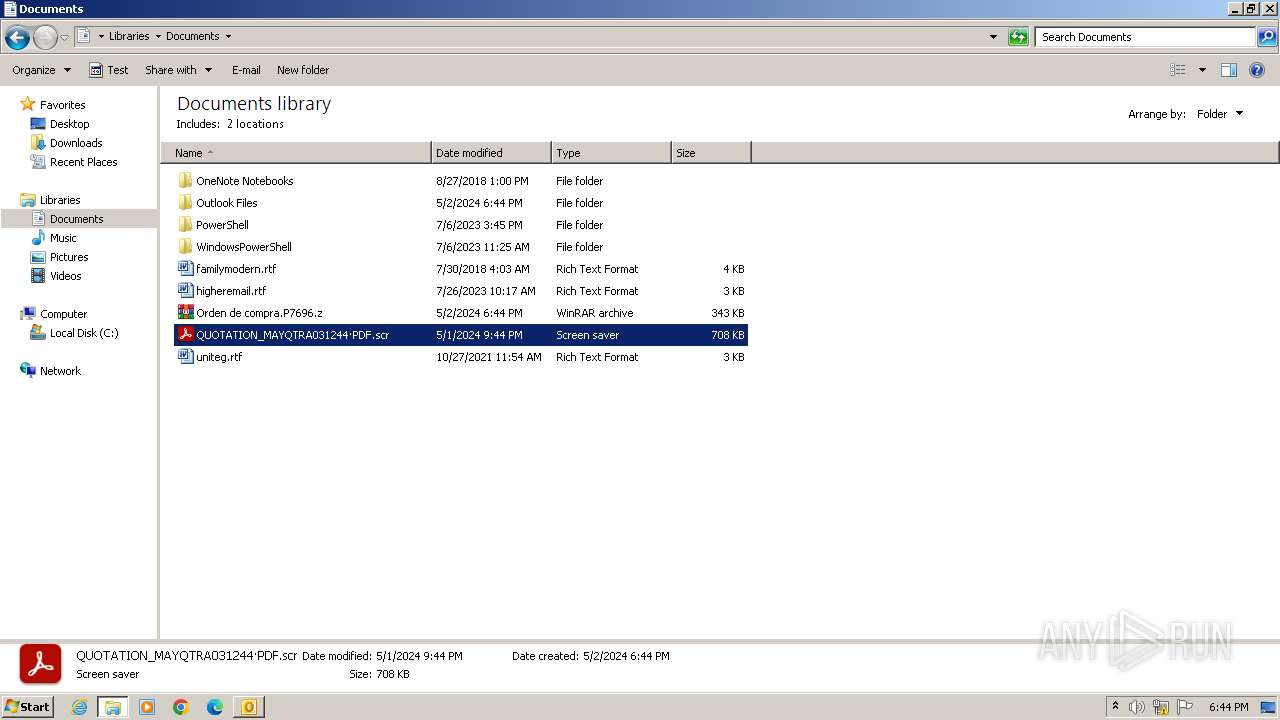
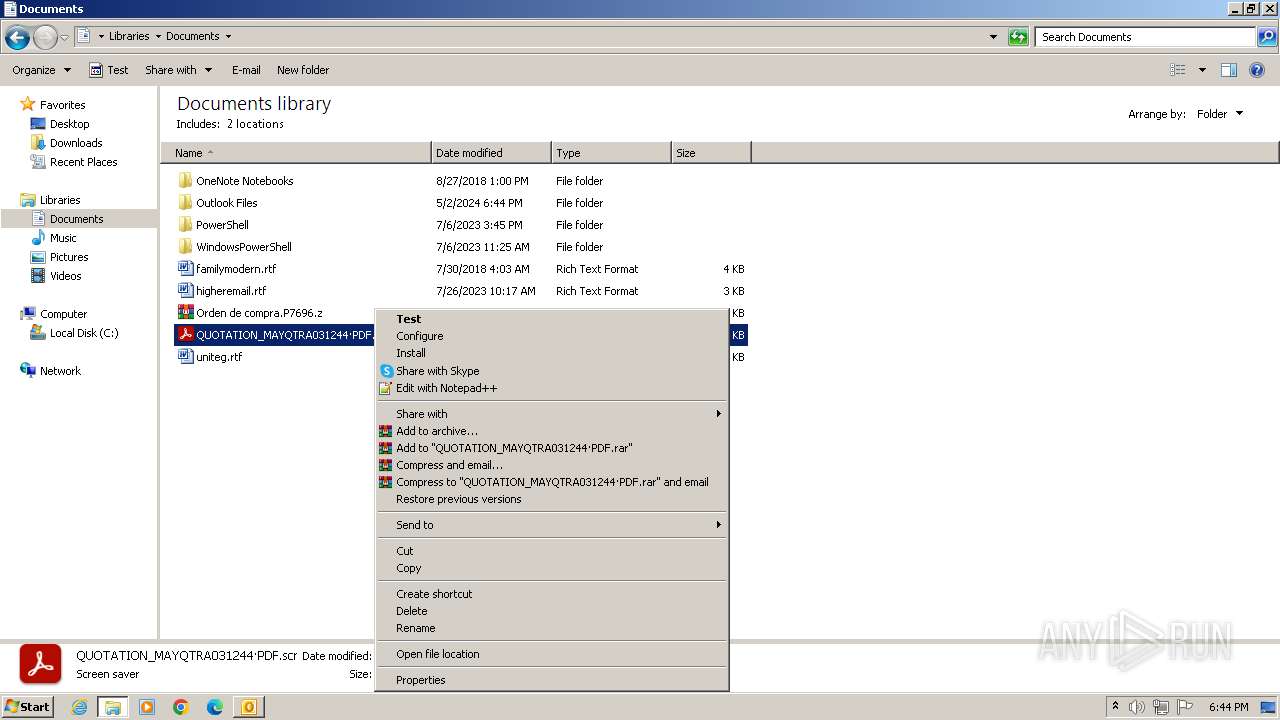
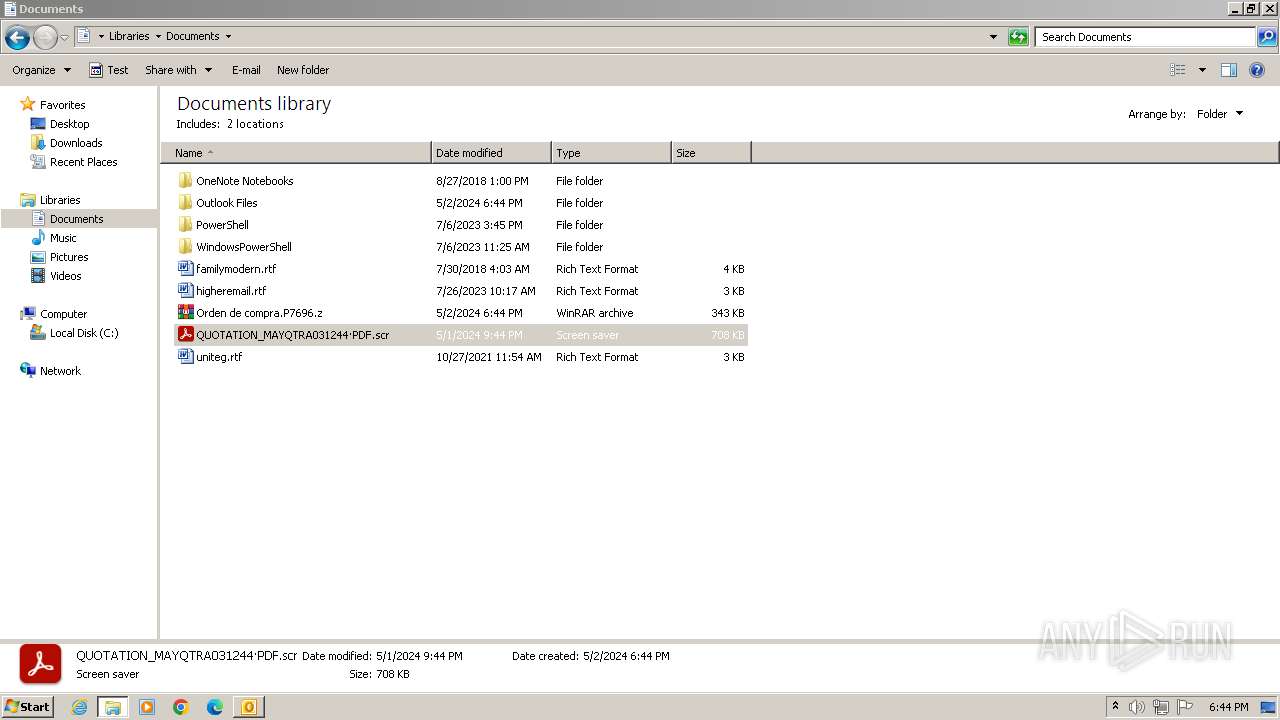
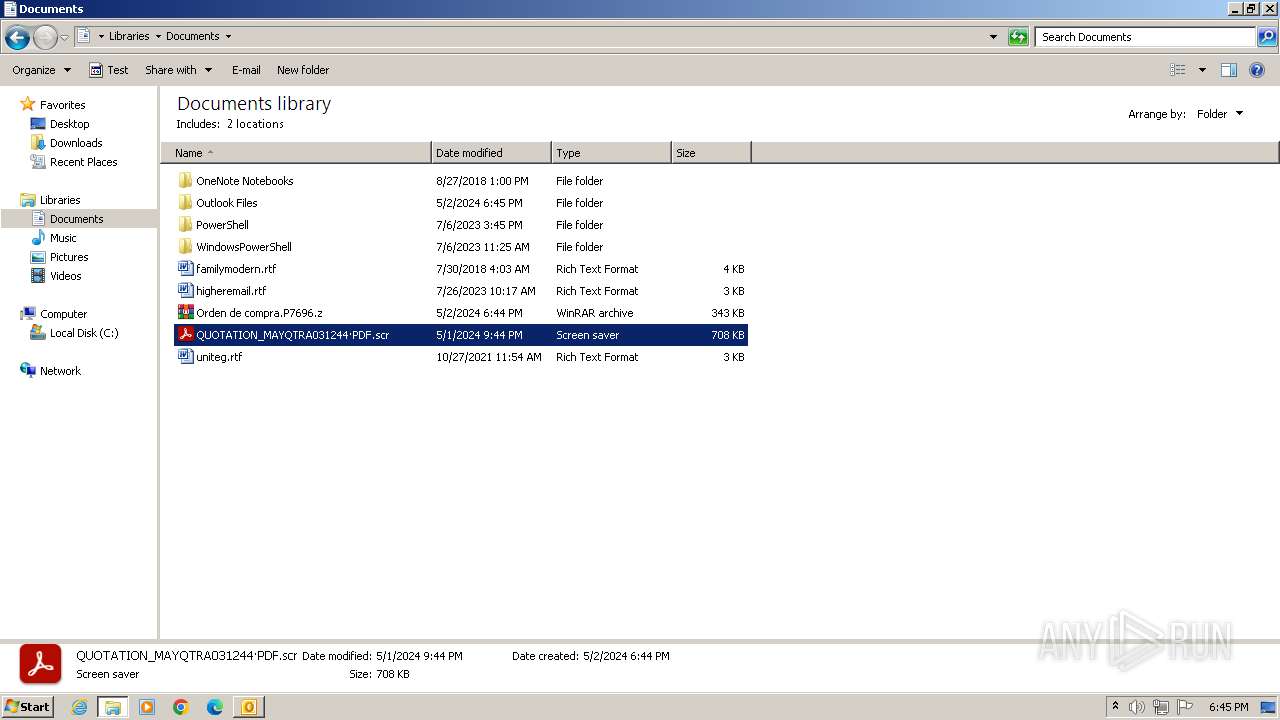
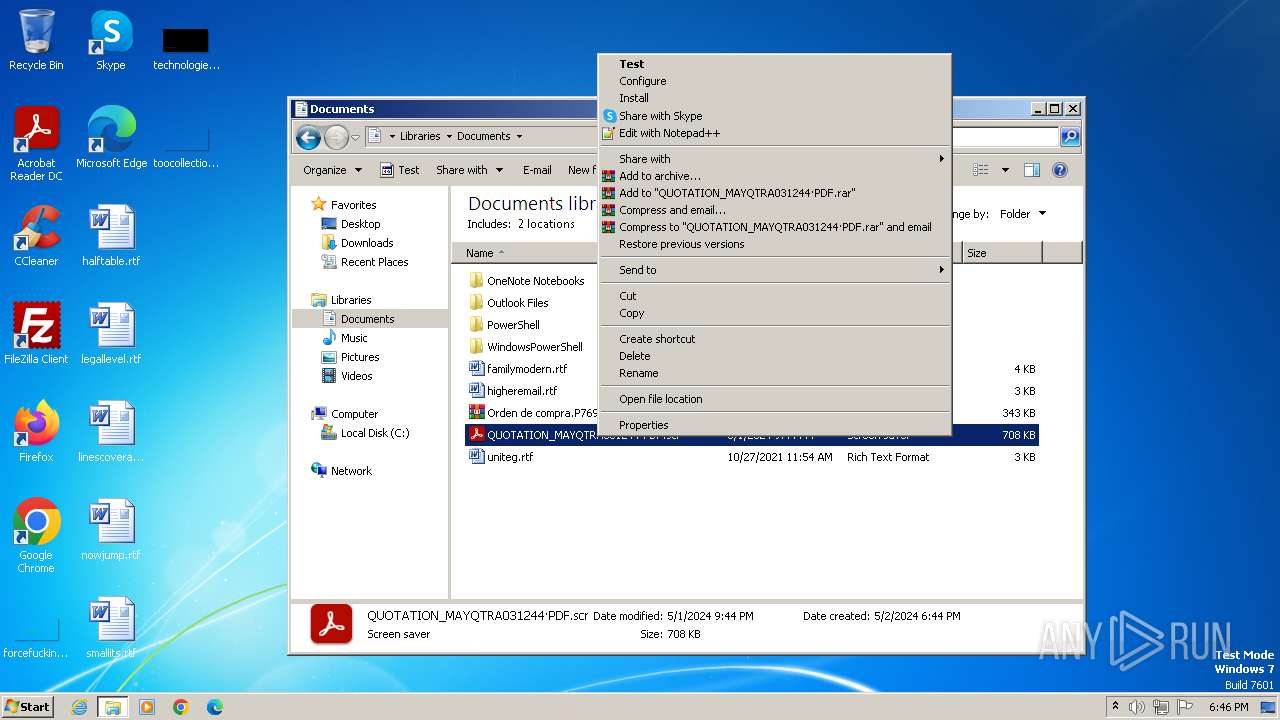
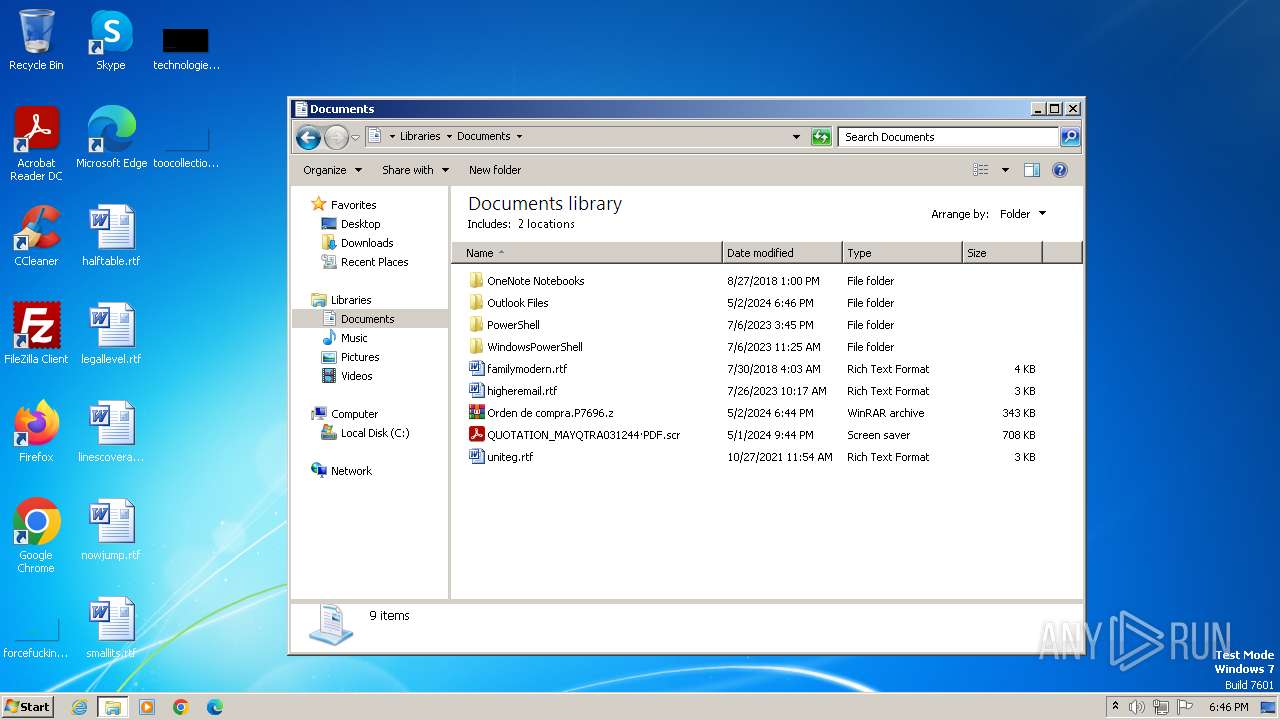
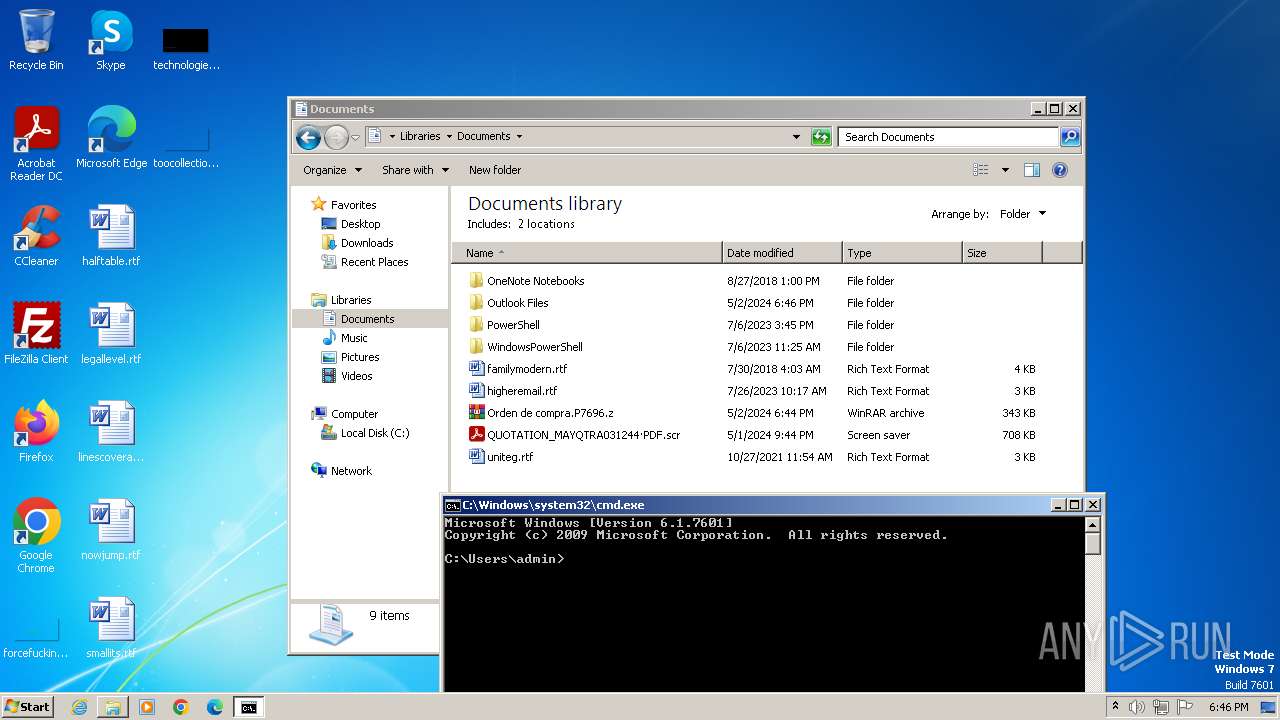
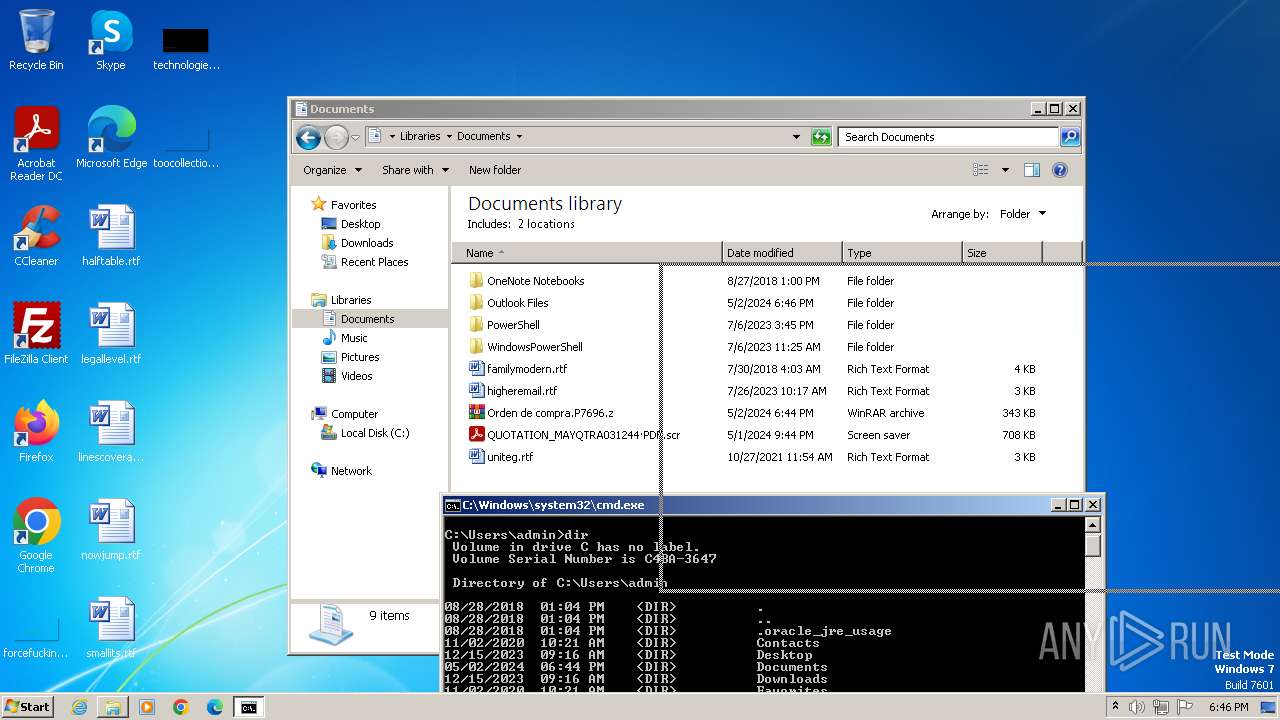
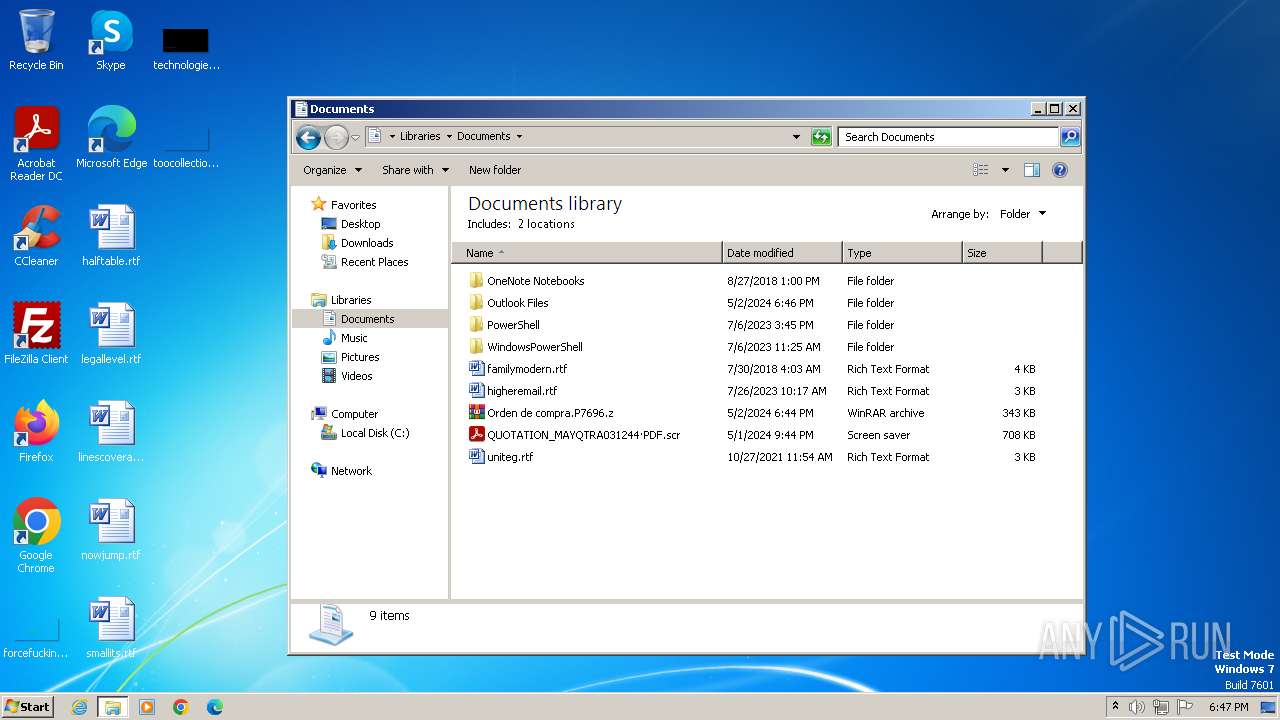
| 1072 | "C:\Program Files\WinRAR\WinRAR.exe" x -iext -ow -ver -- "C:\Users\admin\Documents\Orden de compra.P7696.z" C:\Users\admin\Documents\ | C:\Program Files\WinRAR\WinRAR.exe | explorer.exe | ||||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.91.0 Modules
| |||||||||||||||
| 1616 | "C:\Windows\explorer.exe" | C:\Windows\explorer.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
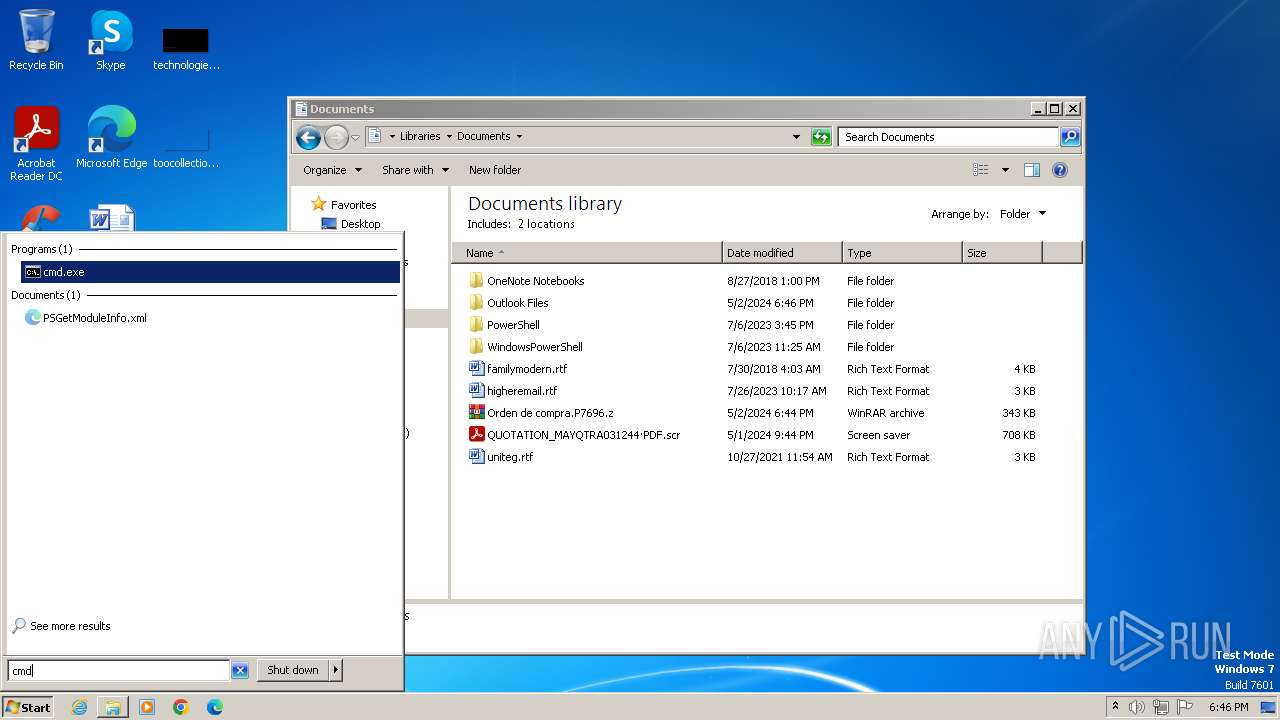
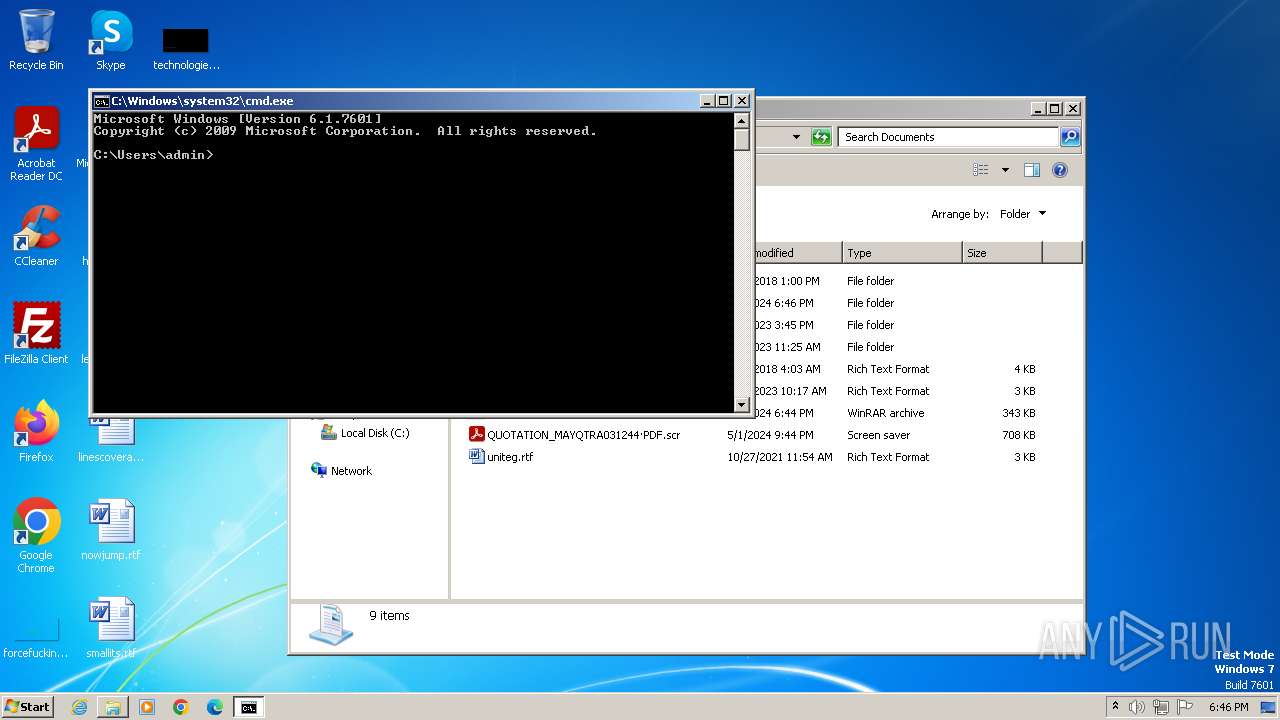
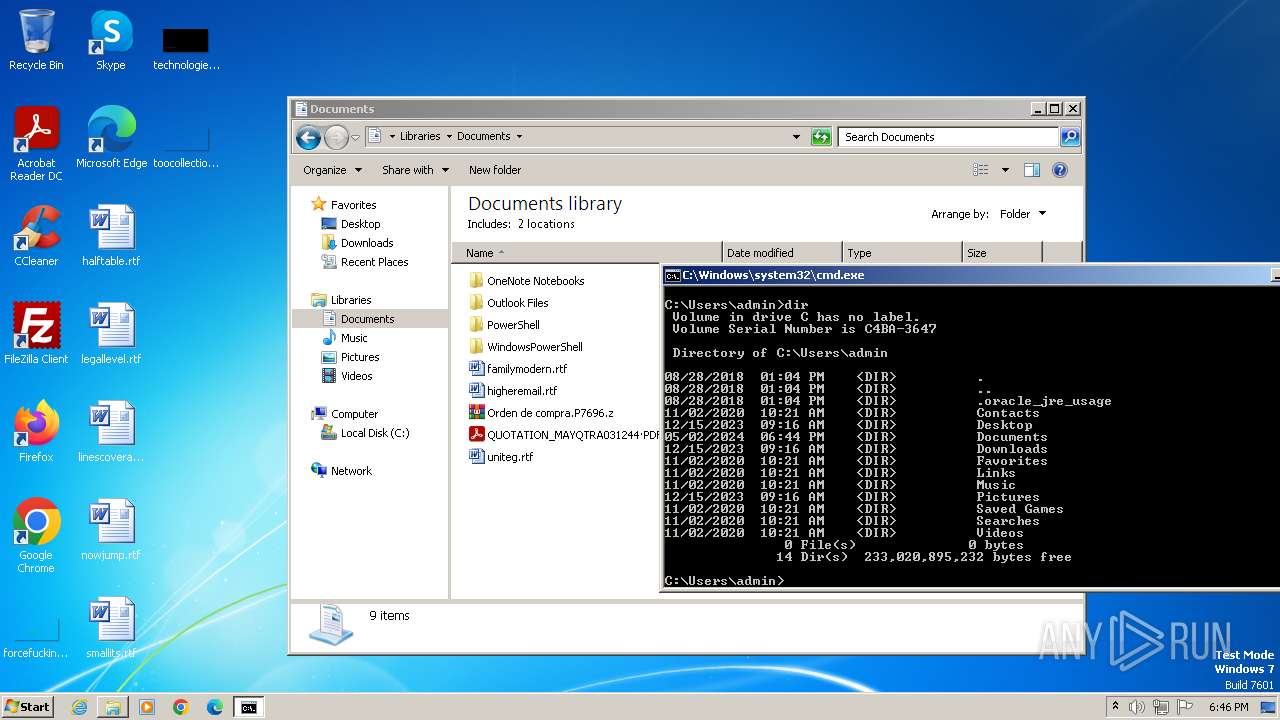
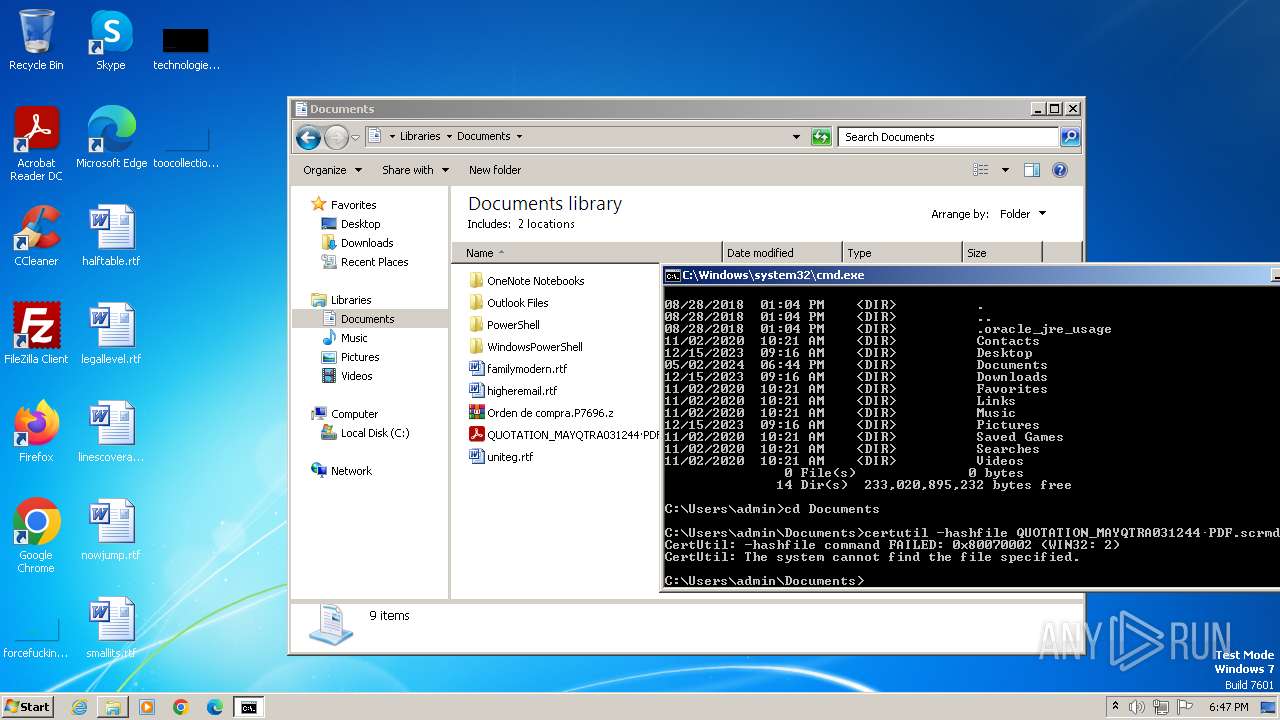
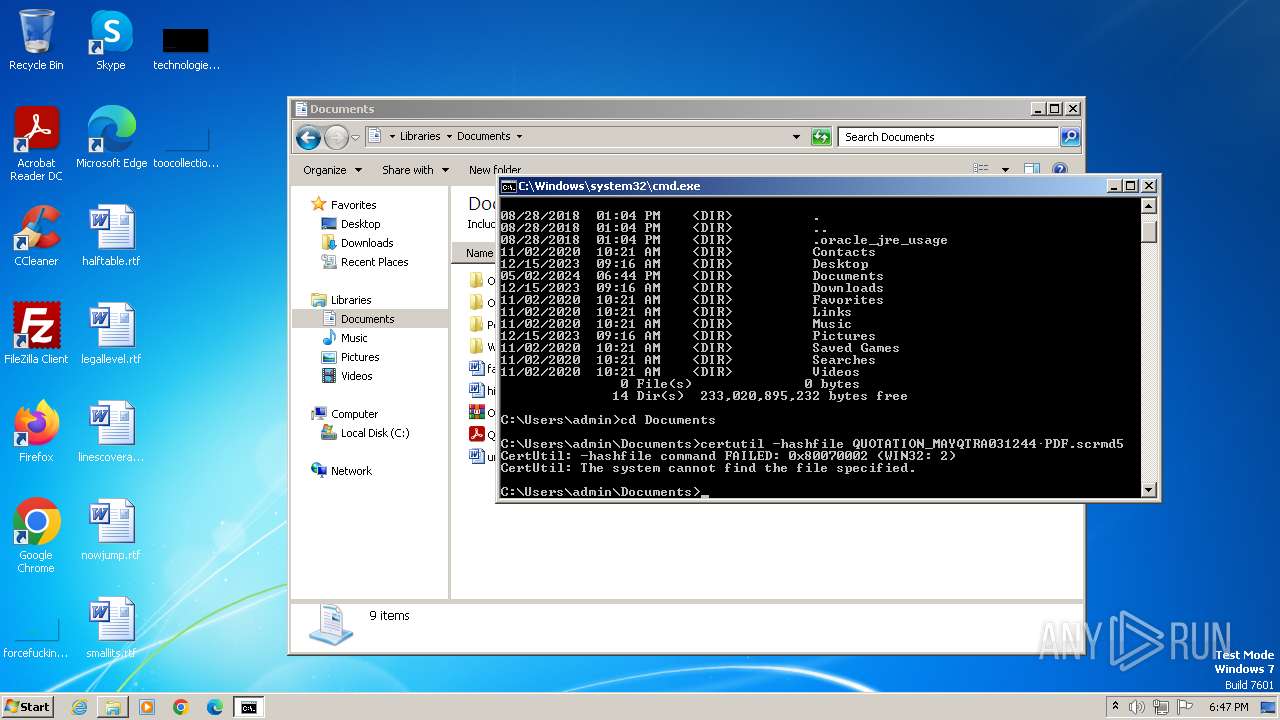
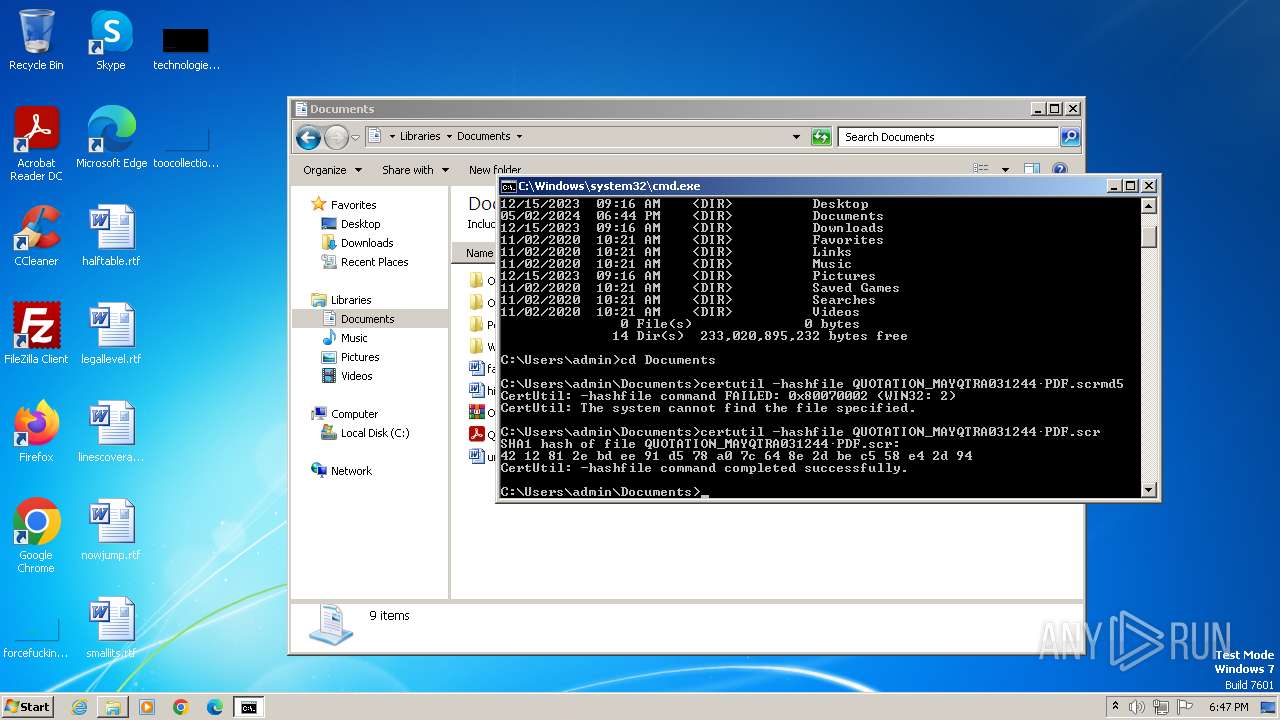
| 2288 | certutil -hashfile QUOTATION_MAYQTRA031244·PDF.scr | C:\Windows\System32\certutil.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: CertUtil.exe Exit code: 0 Version: 6.1.7601.18151 (win7sp1_gdr.130512-1533) Modules
| |||||||||||||||
| 2300 | "C:\Windows\Microsoft.NET\Framework\v4.0.30319\RegAsm.exe" | C:\Windows\Microsoft.NET\Framework\v4.0.30319\RegAsm.exe | QUOTATION_MAYQTRA031244·PDF.scr | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft .NET Assembly Registration Utility Exit code: 4294967295 Version: 4.8.3761.0 built by: NET48REL1 Modules
| |||||||||||||||
| 2384 | "C:\Windows\Microsoft.NET\Framework\v4.0.30319\RegAsm.exe" | C:\Windows\Microsoft.NET\Framework\v4.0.30319\RegAsm.exe | QUOTATION_MAYQTRA031244·PDF.scr | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft .NET Assembly Registration Utility Exit code: 4294967295 Version: 4.8.3761.0 built by: NET48REL1 Modules
AgentTesla(PID) Process(2384) RegAsm.exe Protocolsmtp Hostgator3220.hostgator.com Port587 Usernamedworld@qlststv.com PasswordDasco..!@@hT!3V | |||||||||||||||
| 2544 | "C:\Program Files\Windows Media Player\wmpnscfg.exe" | C:\Program Files\Windows Media Player\wmpnscfg.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Media Player Network Sharing Service Configuration Application Exit code: 0 Version: 12.0.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
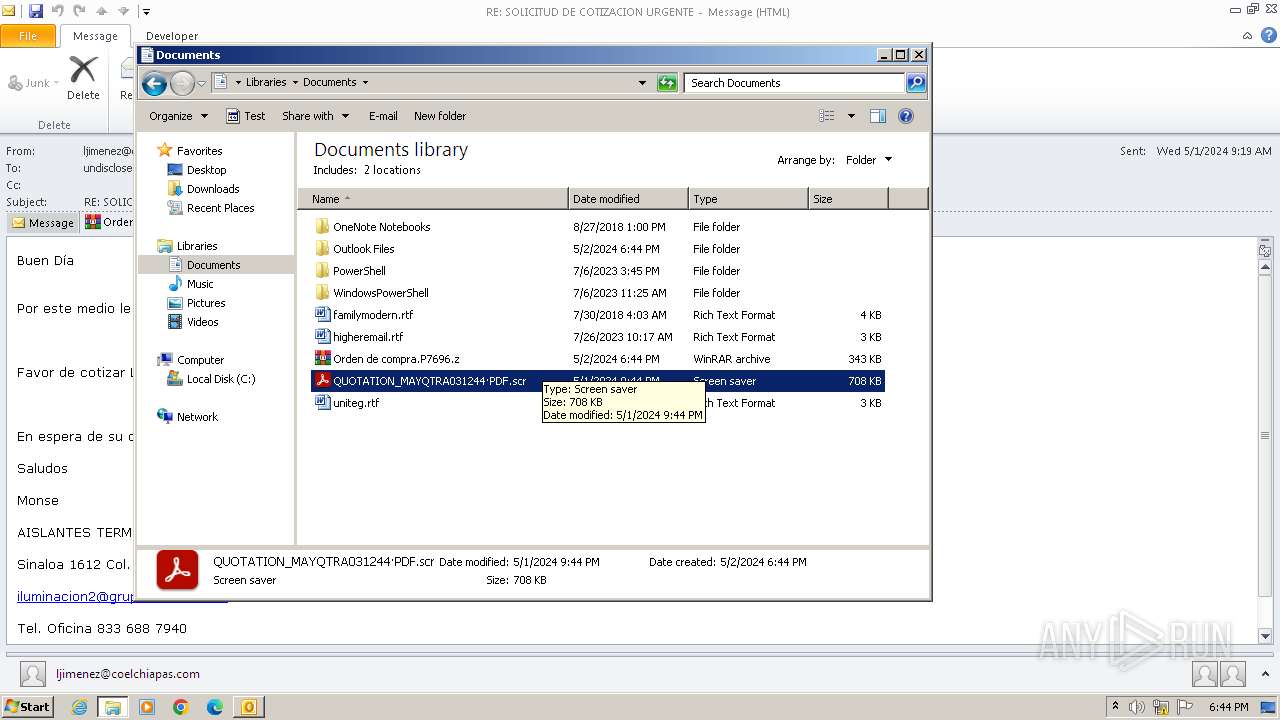
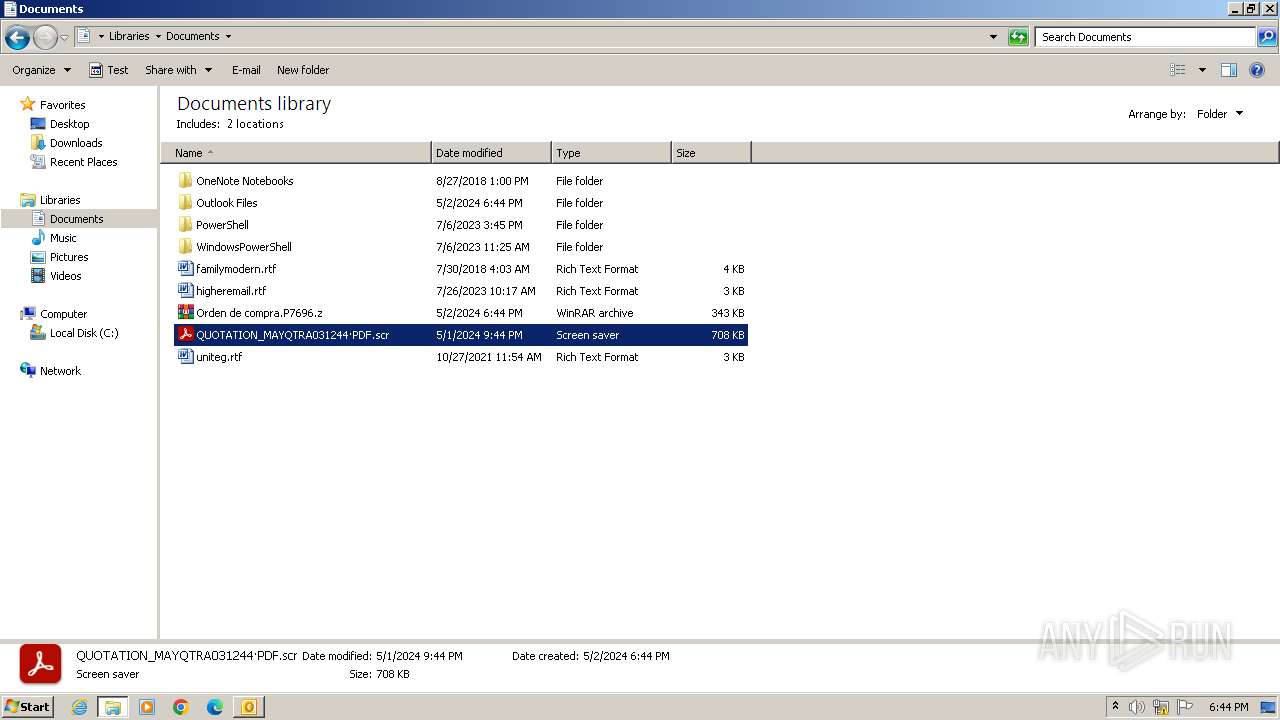
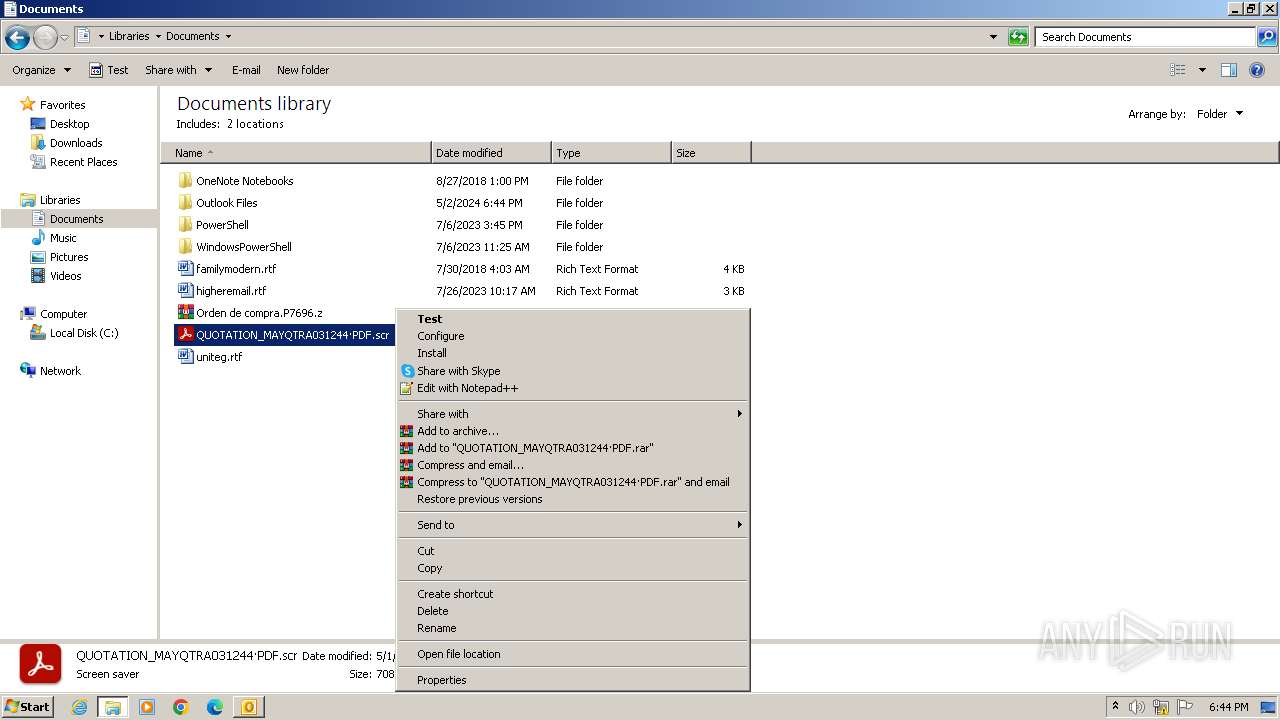
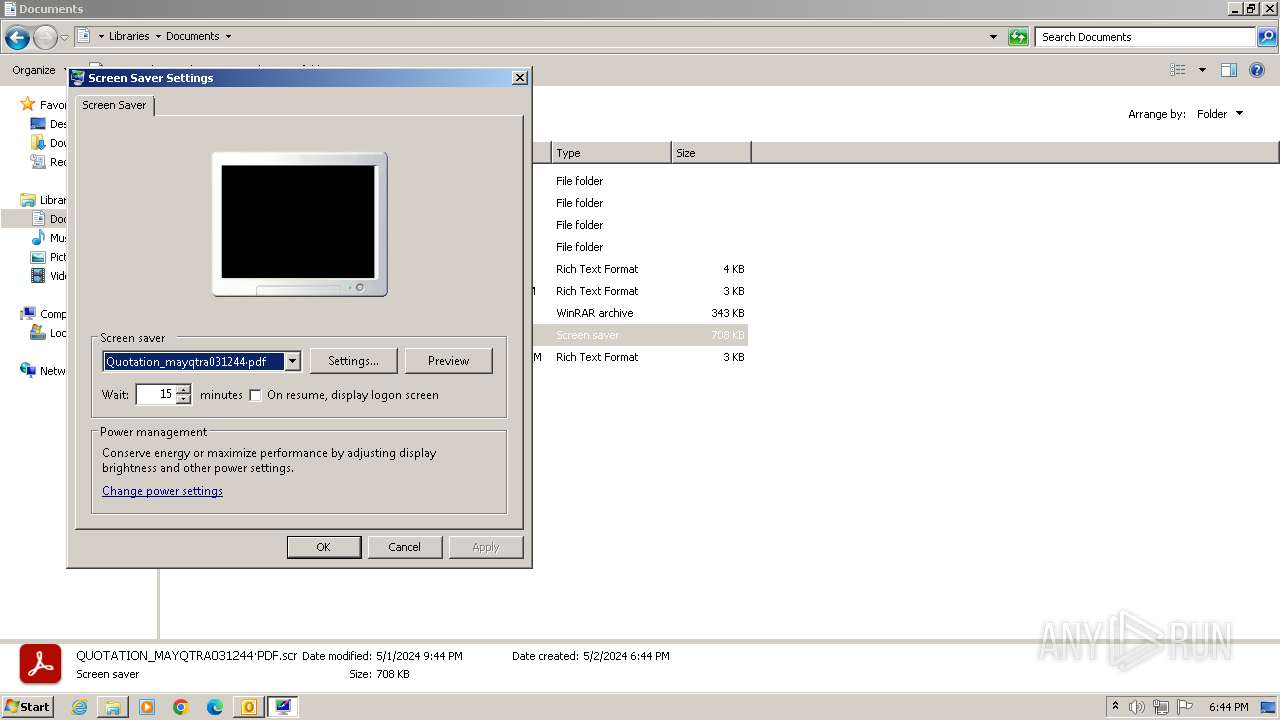
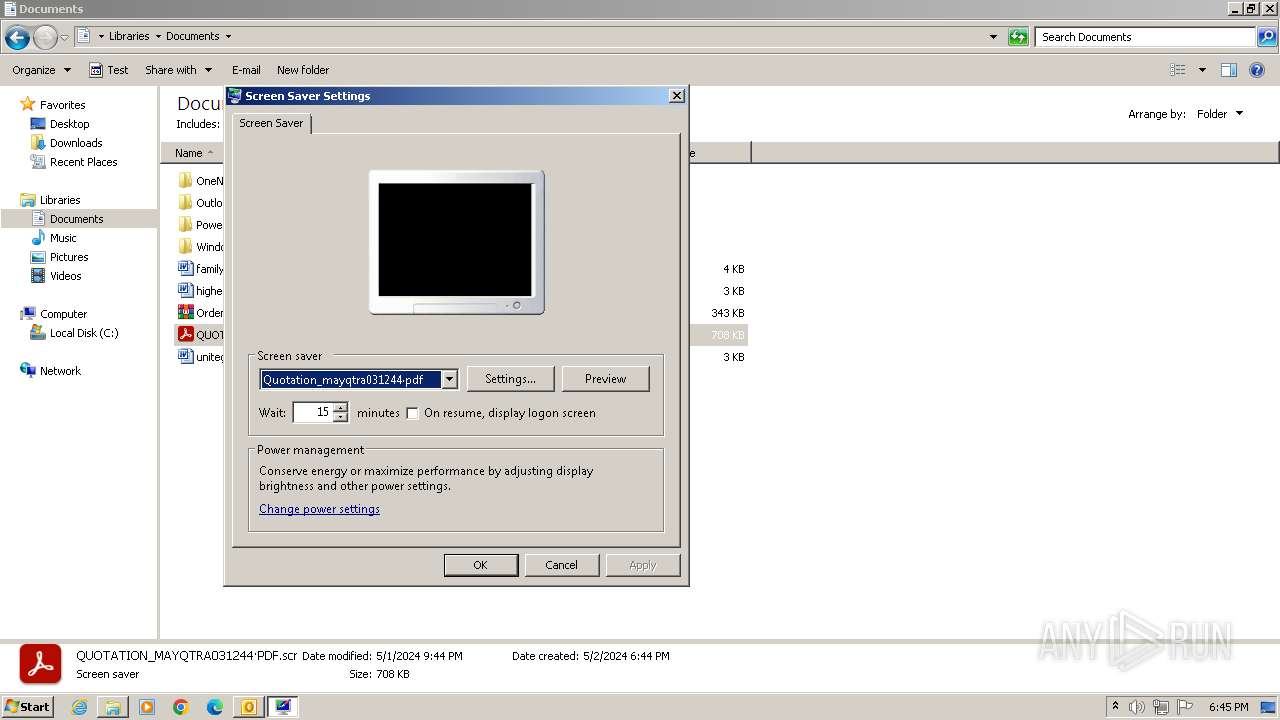
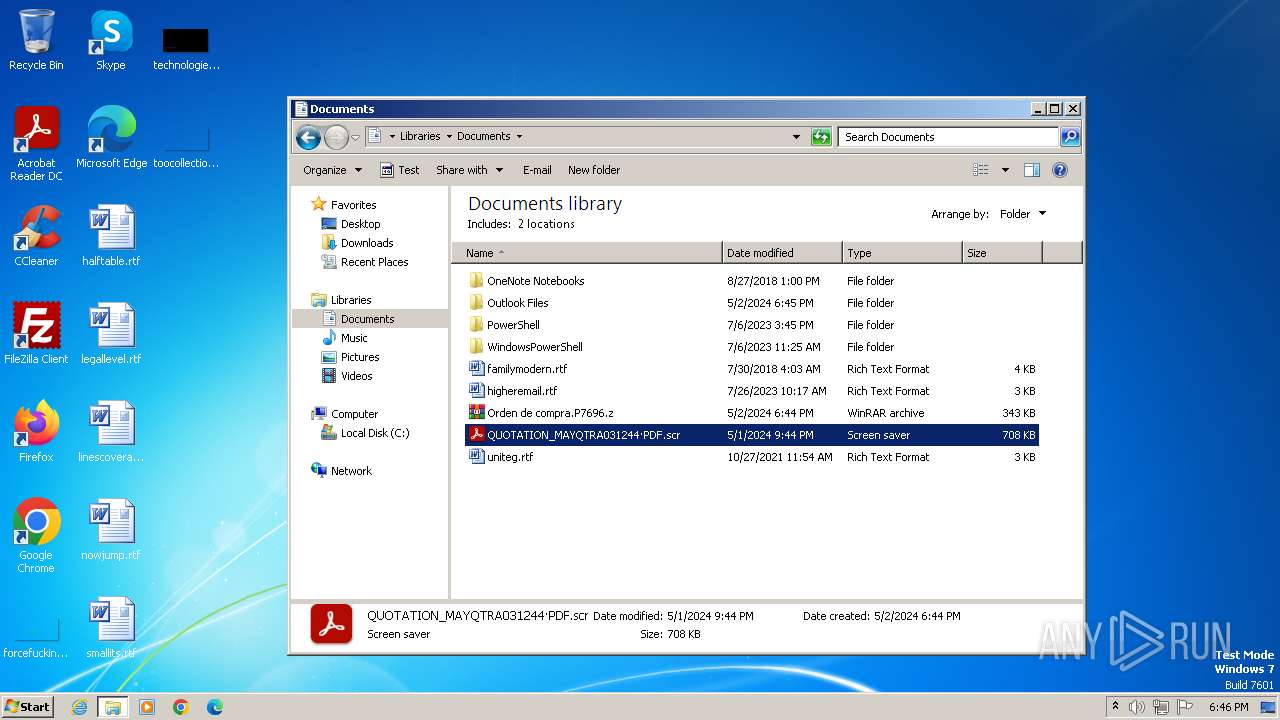
| 2556 | "C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr" /S | C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr | — | explorer.exe | |||||||||||
User: admin Company: command-line Integrity Level: MEDIUM Description: ESET Exit code: 0 Version: 0.0.0.0 Modules
| |||||||||||||||
| 2600 | "Powershell.exe" 'C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr' 'C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ESET.exe' | C:\Windows\System32\WindowsPowerShell\v1.0\Powershell.exe | — | QUOTATION_MAYQTRA031244·PDF.scr | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 1 Version: 10.0.14409.1005 (rs1_srvoob.161208-1155) Modules
| |||||||||||||||
| 2616 | "Powershell.exe" 'C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr' 'C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ESET.exe' | C:\Windows\System32\WindowsPowerShell\v1.0\Powershell.exe | — | QUOTATION_MAYQTRA031244·PDF.scr | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 1 Version: 10.0.14409.1005 (rs1_srvoob.161208-1155) Modules
| |||||||||||||||
| 2692 | "C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr" /S | C:\Users\admin\Documents\QUOTATION_MAYQTRA031244·PDF.scr | — | explorer.exe | |||||||||||
User: admin Company: command-line Integrity Level: MEDIUM Description: ESET Exit code: 0 Version: 0.0.0.0 Modules
| |||||||||||||||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1033 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1041 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1046 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1036 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1031 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1040 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1049 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 3082 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1042 |
Value: Off | |||
| (PID) Process: | (3972) OUTLOOK.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1055 |
Value: Off | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Temp\CVR2906.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\Documents\Outlook Files\Outlook Data File - NoMail.pst | — | |
MD5:— | SHA256:— | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Microsoft\Outlook\mapisvc.inf | text | |
MD5:F3B25701FE362EC84616A93A45CE9998 | SHA256:B3D510EF04275CA8E698E5B3CBB0ECE3949EF9252F0CDC839E9EE347409A2209 | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Roaming\Microsoft\Templates\~WRD0000.tmp | — | |
MD5:— | SHA256:— | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Temp\tmp2BA7.tmp | binary | |
MD5:4E5FD95E767F2AB1883CC524570657DF | SHA256:1D89B3C337672D86321E6667ED4D688E3A3904712C7C5DD21ED44655C5BF3B82 | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Roaming\Microsoft\Templates\~$rmalEmail.dotm | binary | |
MD5:A05630F037C05D973CA846D39DCD63B5 | SHA256:BD8D2C9838535E337048066E543BD932F526E9C571942B21FE744E397DD7A7C2 | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\{25BD4A9C-A9F2-4998-A59A-5B677739BB7E}\{1C306CB1-771E-4B4B-A902-86E897877F5B}.png | image | |
MD5:4C61C12EDBC453D7AE184976E95258E1 | SHA256:296526F9A716C1AA91BA5D6F69F0EB92FDF79C2CB2CFCF0CEB22B7CCBC27035F | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.Outlook\DQRKK8ER\Orden de compra P7696.z | lzh | |
MD5:1EB7788A33AEE6D74F476DC1D11E7E65 | SHA256:F4D4E891C6AEDB87609BAC8028C8F545F2440C54A2D747B96499A508CC191027 | |||
| 3972 | OUTLOOK.EXE | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.Outlook\DQRKK8ER\Orden de compra P7696.z:Zone.Identifier | text | |
MD5:FBCCF14D504B7B2DBCB5A5BDA75BD93B | SHA256:EACD09517CE90D34BA562171D15AC40D302F0E691B439F91BE1B6406E25F5913 | |||
| 2792 | rundll32.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Themes\Custom.theme | text | |
MD5:C1FCF55A48CAF02CBC0FEC89C8B44C9D | SHA256:1497F2B7237A7DAEF8DF4568F8BFEF1B7B8FEBE4082A797725C410DF1CE3B961 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3008 | RegAsm.exe | GET | — | 208.95.112.1:80 | http://ip-api.com/line/?fields=hosting | US | — | — | unknown |
3276 | RegAsm.exe | GET | 200 | 208.95.112.1:80 | http://ip-api.com/line/?fields=hosting | US | text | 6 b | unknown |
2384 | RegAsm.exe | GET | 200 | 208.95.112.1:80 | http://ip-api.com/line/?fields=hosting | US | text | 6 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | unknown |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
3972 | OUTLOOK.EXE | 64.4.26.155:80 | config.messenger.msn.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
1088 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |
2300 | RegAsm.exe | 208.95.112.1:80 | ip-api.com | TUT-AS | US | unknown |
2384 | RegAsm.exe | 208.95.112.1:80 | ip-api.com | TUT-AS | US | unknown |
2384 | RegAsm.exe | 198.57.247.184:587 | gator3220.hostgator.com | UNIFIEDLAYER-AS-1 | US | unknown |
3008 | RegAsm.exe | 208.95.112.1:80 | ip-api.com | TUT-AS | US | unknown |
3276 | RegAsm.exe | 208.95.112.1:80 | ip-api.com | TUT-AS | US | unknown |
Domain | IP | Reputation |
|---|---|---|
config.messenger.msn.com |
| whitelisted |
ip-api.com |
| shared |
gator3220.hostgator.com |
| malicious |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Potential Corporate Privacy Violation | AV POLICY Internal Host Retrieving External IP Address (ip-api. com) |
— | — | Device Retrieving External IP Address Detected | POLICY [ANY.RUN] External Hosting Lookup by ip-api |
— | — | Device Retrieving External IP Address Detected | ET POLICY External IP Lookup ip-api.com |
— | — | Potential Corporate Privacy Violation | AV POLICY Internal Host Retrieving External IP Address (ip-api. com) |
— | — | Device Retrieving External IP Address Detected | POLICY [ANY.RUN] External Hosting Lookup by ip-api |
— | — | Device Retrieving External IP Address Detected | ET POLICY External IP Lookup ip-api.com |
— | — | Potential Corporate Privacy Violation | AV POLICY Internal Host Retrieving External IP Address (ip-api. com) |
— | — | Device Retrieving External IP Address Detected | POLICY [ANY.RUN] External Hosting Lookup by ip-api |
— | — | Device Retrieving External IP Address Detected | ET POLICY External IP Lookup ip-api.com |
— | — | Misc activity | INFO [ANY.RUN] SMTP email client opens transfer with server (EHLO) |