ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
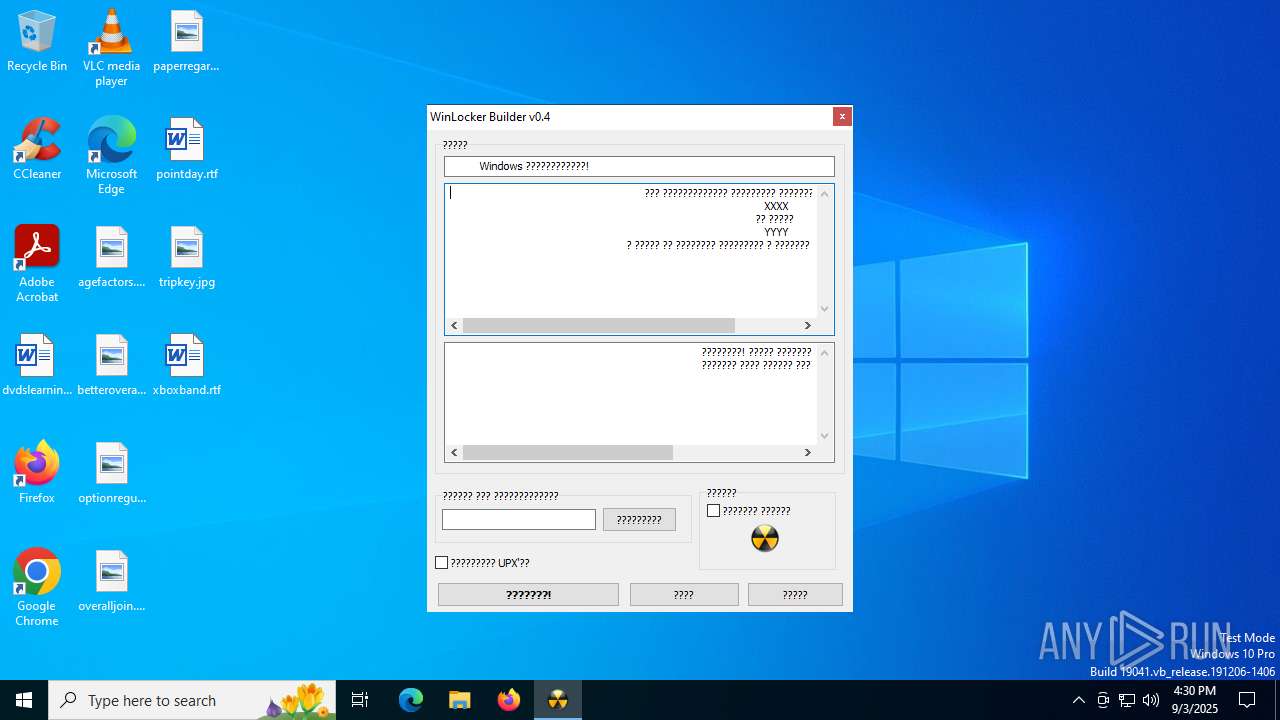
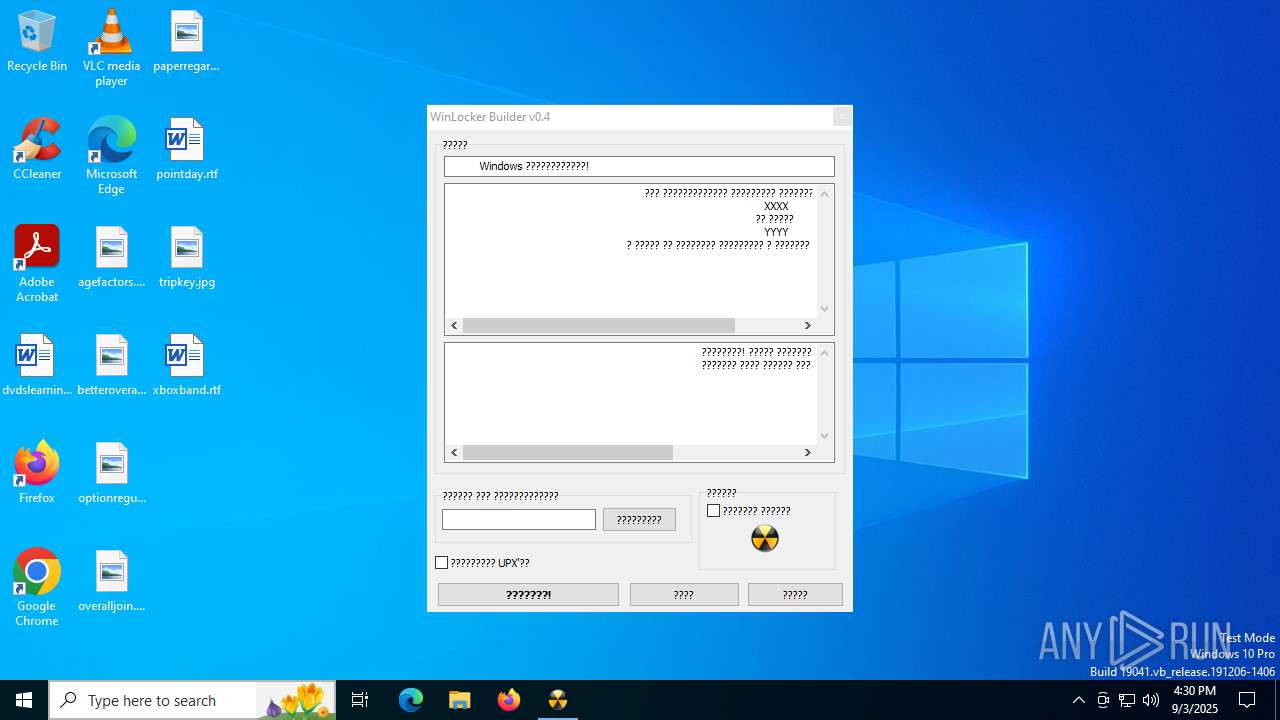
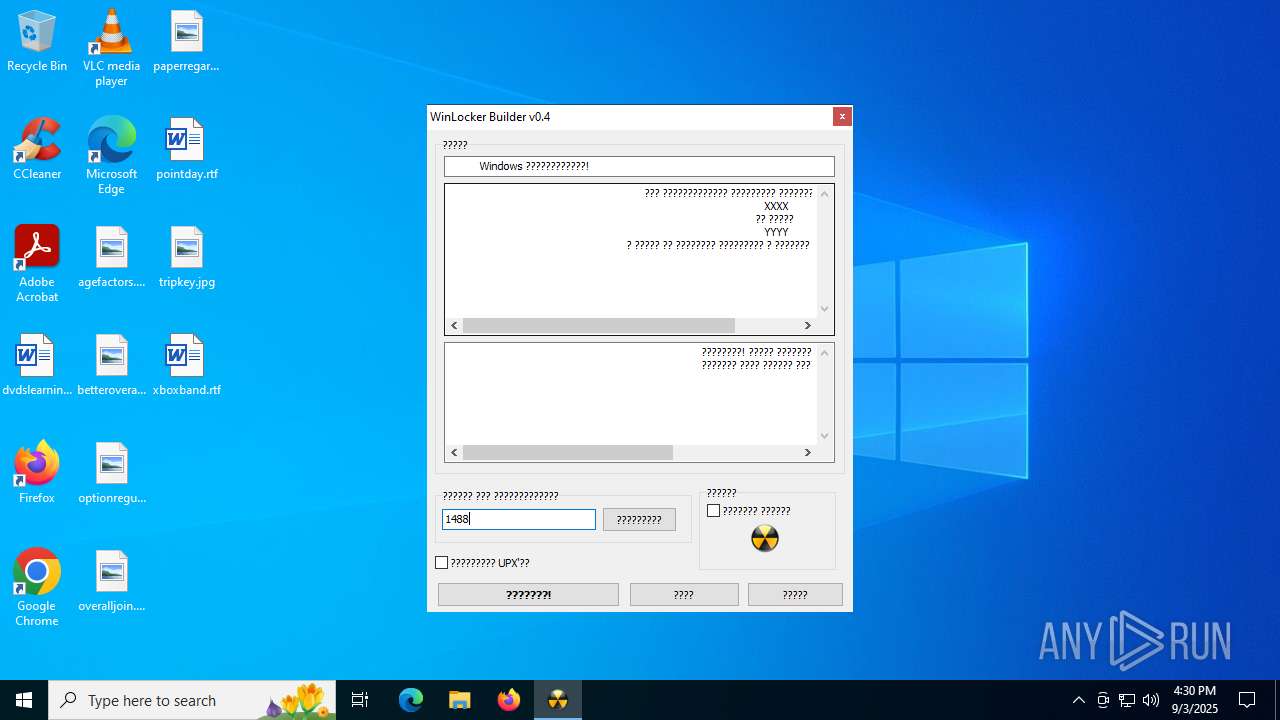
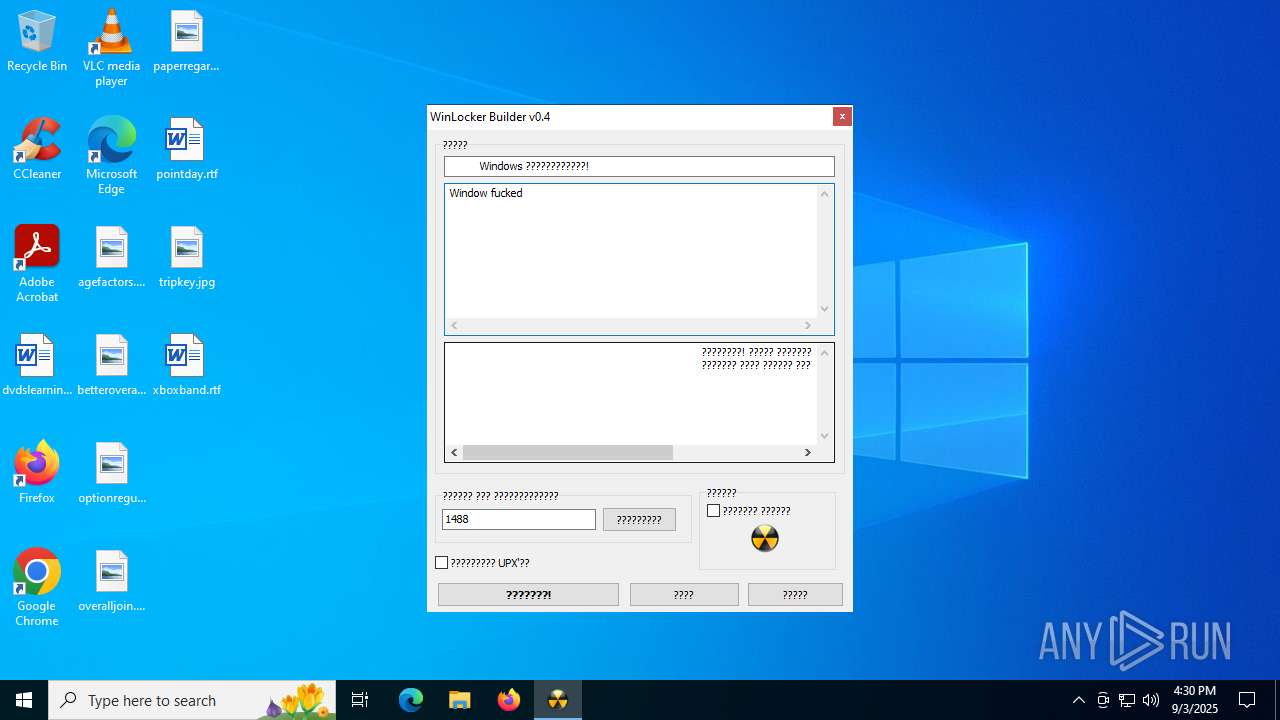
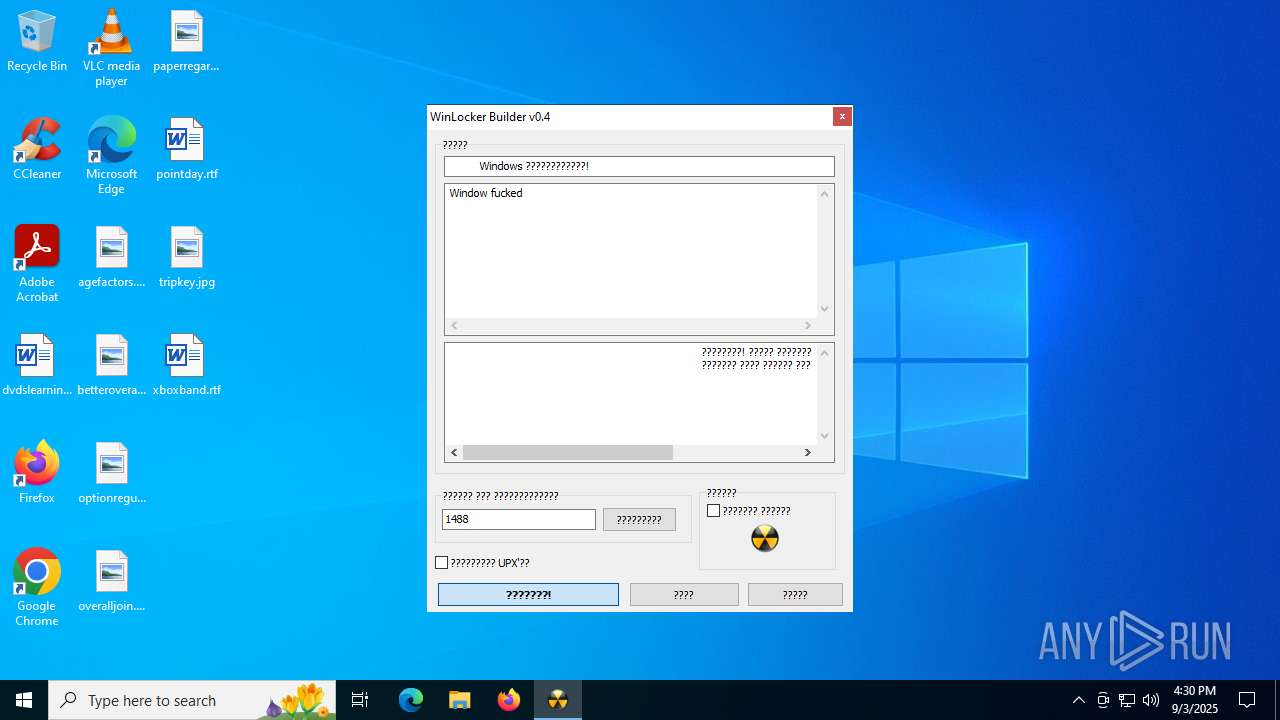
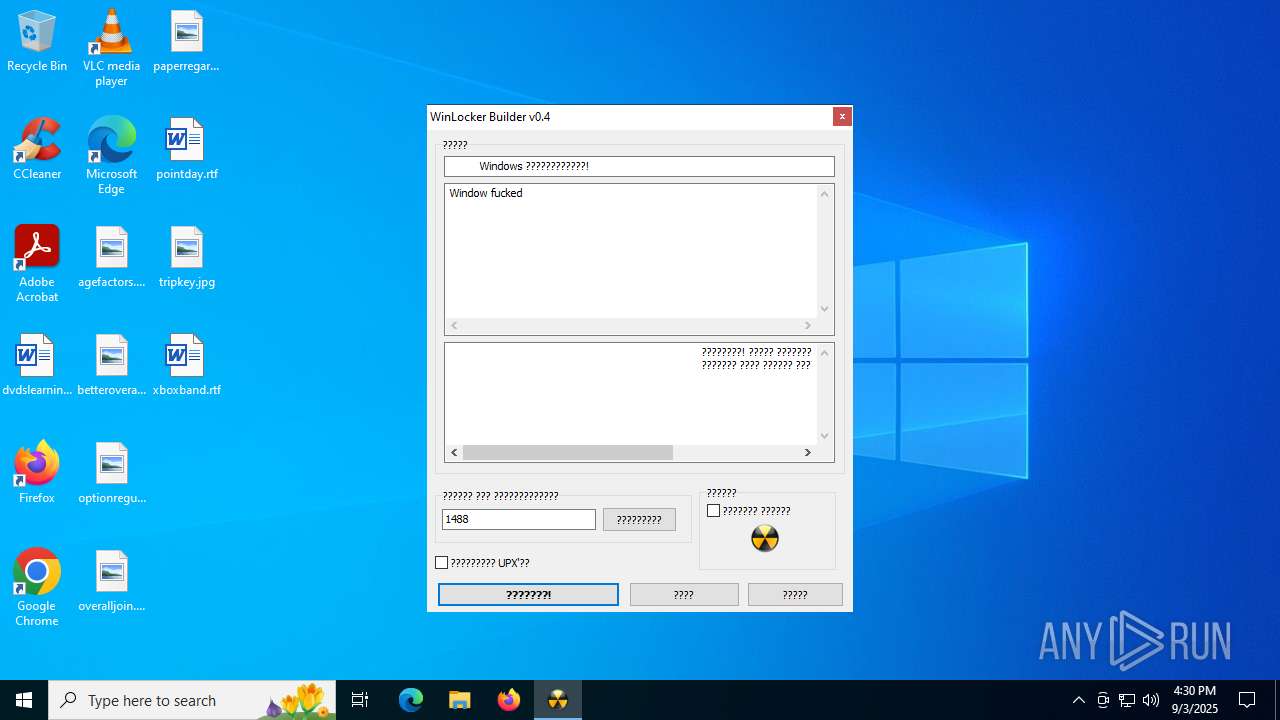
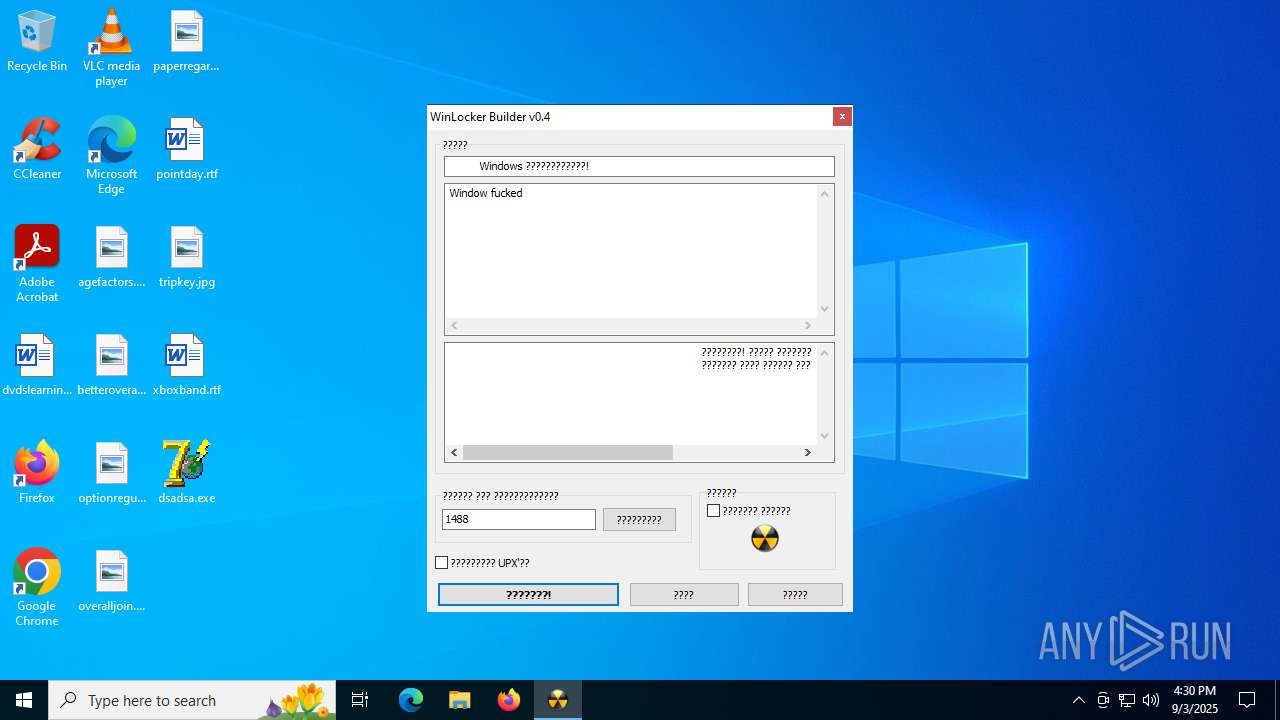
| File name: | WinLocker_Builder_0.4.exe |
| Full analysis: | https://app.any.run/tasks/015ed812-e549-497b-871e-40cd3a109a79 |
| Verdict: | Malicious activity |
| Threats: | DBatLoader is a loader malware used for distributing payloads of different types, including WarzoneRAT and Formbook. It is employed in multi-stage attacks that usually start with a phishing email carrying a malicious attachment. |
| Analysis date: | September 03, 2025, 16:30:00 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 10 sections |
| MD5: | 81DD862410AF80C9D2717AF912778332 |
| SHA1: | 8F1DF476F58441DB5973CCFDC211C8680808FFE1 |
| SHA256: | 60E76EDA46185D1D2E9463D15E31D4C87EB03535D368CC3471C55992BC99AD5F |
| SSDEEP: | 12288:0L/xX5KVeOnuH/u1Wig295xsmVXf6AaQLmEc+pdmWSwIHUOS6VpW:0bxpUz13g27raQmEcomWSHHUDv |
| .exe | | | ASPack compressed Win32 Executable (generic) (92.6) |
|---|---|---|
| .exe | | | Win32 Executable (generic) (3.1) |
| .exe | | | Win16/32 Executable Delphi generic (1.4) |
| .exe | | | Generic Win/DOS Executable (1.3) |
| .exe | | | DOS Executable Generic (1.3) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 1999:01:31 11:45:16+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, Bytes reversed lo, 32-bit, Bytes reversed hi |
| PEType: | PE32 |
| LinkerVersion: | 2.25 |
| CodeSize: | 354816 |
| InitializedDataSize: | 851968 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x12e001 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 0.4.0.0 |
| ProductVersionNumber: | 0.4.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Russian |
| CharacterSet: | Windows, Cyrillic |
| CompanyName: | VAN32 |
| FileDescription: | WinLocker Builder |
| FileVersion: | 0.4.0.0 |
| InternalName: | WinLocker Builder |
| LegalCopyright: | - |
| LegalTrademarks: | - |
| OriginalFileName: | WinLocker Builder.exe |
| ProductName: | WinLocker Builder |
| ProductVersion: | 0.4.0.0 |
| Comments: | - |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
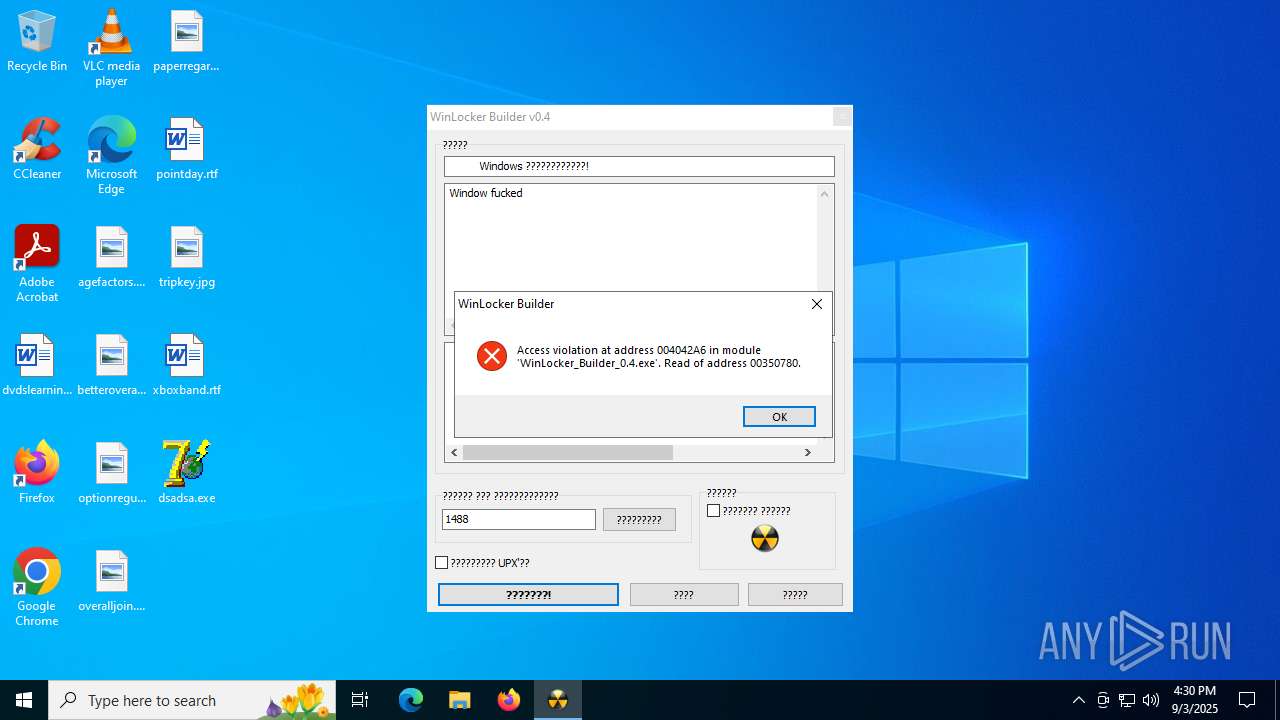
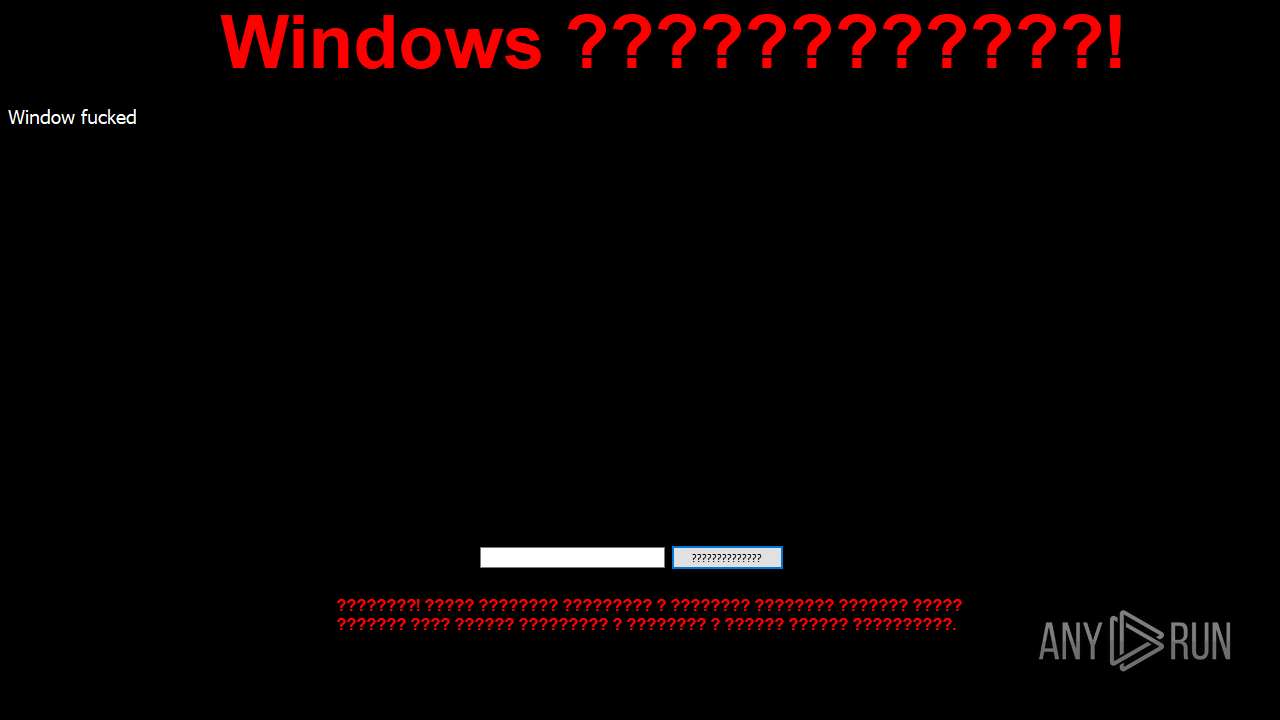
| 4084 | "C:\Users\admin\Desktop\dsadsa.exe" | C:\Users\admin\Desktop\dsadsa.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Modules
| |||||||||||||||
| 4444 | "C:\Users\admin\AppData\Local\Temp\WinLocker_Builder_0.4.exe" | C:\Users\admin\AppData\Local\Temp\WinLocker_Builder_0.4.exe | explorer.exe | ||||||||||||
User: admin Company: VAN32 Integrity Level: MEDIUM Description: WinLocker Builder Version: 0.4.0.0 Modules
| |||||||||||||||
| 6840 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\Software\Microsoft\Windows\Shell\BagMRU |
| Operation: | write | Name: | NodeSlots |
Value: 02020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202020202 | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\Software\Microsoft\Windows\Shell\BagMRU |
| Operation: | write | Name: | MRUListEx |
Value: 040000000000000003000000110000000E000000100000000F0000000C0000000D0000000B000000050000000A000000090000000800000001000000070000000600000002000000FFFFFFFF | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\Software\Microsoft\Windows\Shell\BagMRU\4 |
| Operation: | write | Name: | MRUListEx |
Value: 040000000000000003000000050000000200000001000000FFFFFFFF | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\Software\Microsoft\Windows\Shell\Bags\119\Shell |
| Operation: | write | Name: | SniffedFolderType |
Value: Documents | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer |
| Operation: | write | Name: | GlobalAssocChangedCounter |
Value: 121 | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\LastVisitedPidlMRULegacy |
| Operation: | write | Name: | 0 |
Value: 570069006E004C006F0063006B00650072005F004200750069006C006400650072005F0030002E0034002E00650078006500000014001F50E04FD020EA3A6910A2D808002B30309D14002E80922B16D365937A46956B92703ACA08AF0000 | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\LastVisitedPidlMRULegacy |
| Operation: | write | Name: | MRUListEx |
Value: 00000000FFFFFFFF | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\OpenSavePidlMRU\exe |
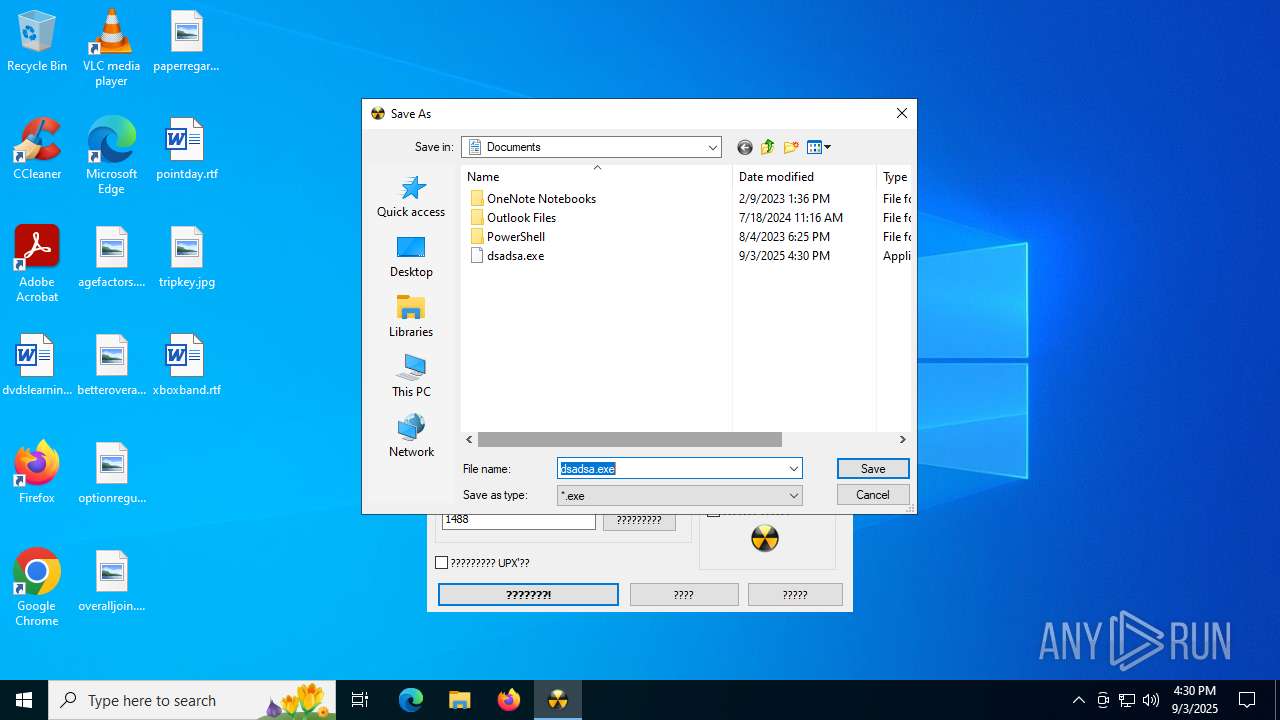
| Operation: | write | Name: | 2 |
Value: 14001F50E04FD020EA3A6910A2D808002B30309D14002E80922B16D365937A46956B92703ACA08AF60003200000000000000000080006473616473612E6578650000460009000400EFBE00000000000000002E00000000000000000000000000000000000000000000000000000000006400730061006400730061002E0065007800650000001A000000 | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\OpenSavePidlMRU\exe |
| Operation: | write | Name: | MRUListEx |
Value: 020000000100000000000000FFFFFFFF | |||
| (PID) Process: | (4444) WinLocker_Builder_0.4.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\ComDlg32\OpenSavePidlMRU\* |
| Operation: | write | Name: | 9 |
Value: 14001F50E04FD020EA3A6910A2D808002B30309D14002E80922B16D365937A46956B92703ACA08AF60003200000000000000000080006473616473612E6578650000460009000400EFBE00000000000000002E00000000000000000000000000000000000000000000000000000000006400730061006400730061002E0065007800650000001A000000 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
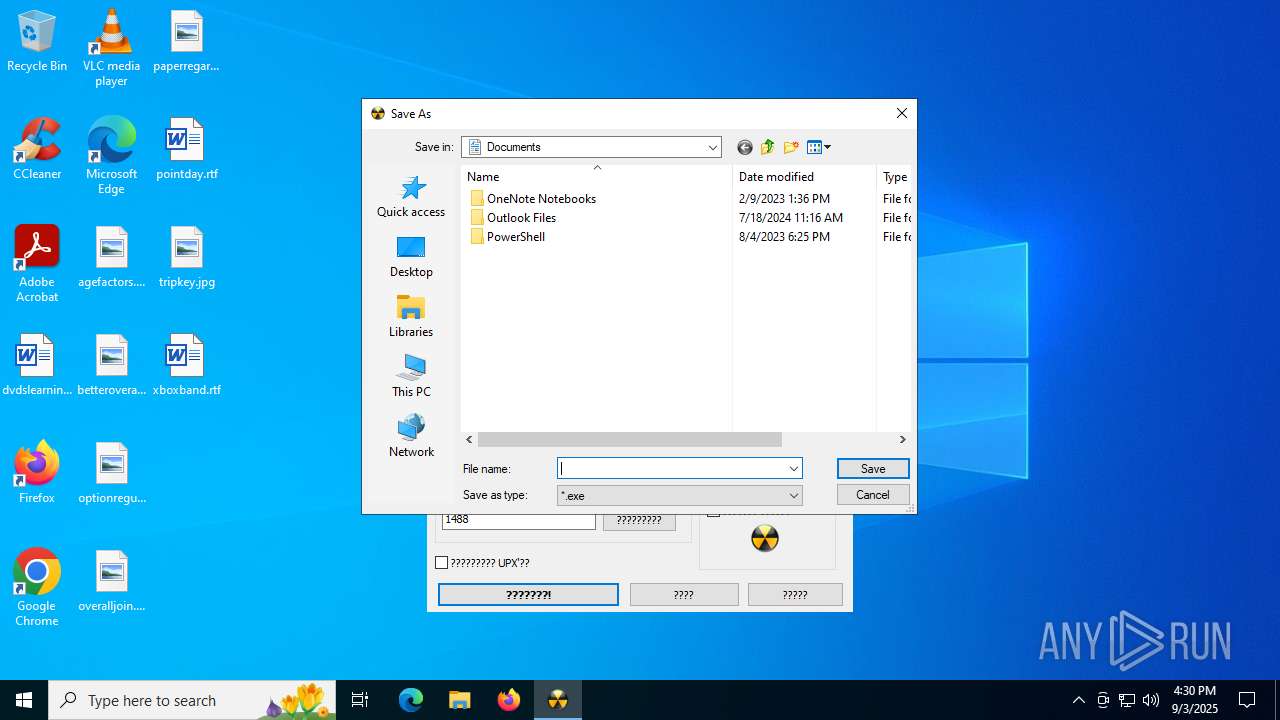
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Documents\RCX479E.tmp | executable | |
MD5:7335FC512377E72533C3D6C182C7F109 | SHA256:79B94A3E044F115FD41E2AF3B885726054D82568E7871E92D34404FEB1D7CF54 | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Documents\dsadsa.exe | executable | |
MD5:97EB6F7EC0586FE37B82DBE2F522DA35 | SHA256:F738AFBD4C316267D35E2F4D7B818139A55D8EF6B636C3BF736F1672CB4C8EA1 | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Desktop\dsadsa.exe | executable | |
MD5:97EB6F7EC0586FE37B82DBE2F522DA35 | SHA256:F738AFBD4C316267D35E2F4D7B818139A55D8EF6B636C3BF736F1672CB4C8EA1 | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Documents\RCX47CE.tmp | executable | |
MD5:07E02F5600758F7E3D97D9FE5341FEEE | SHA256:EFC8685D0B4C2E827A97F392F2281562D8F19776644BCE3D94E915291C11018E | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Documents\RCX47DE.tmp | executable | |
MD5:3CD54CA0B5923F3FB801027BBB4E8680 | SHA256:40F6FEA44D8B9BFBA036193AF9F28B34F58608639F44E8E7D886D41ED6408FDC | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Desktop\RCX6D5B.tmp | executable | |
MD5:07E02F5600758F7E3D97D9FE5341FEEE | SHA256:EFC8685D0B4C2E827A97F392F2281562D8F19776644BCE3D94E915291C11018E | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Desktop\RCX6D6C.tmp | executable | |
MD5:3CD54CA0B5923F3FB801027BBB4E8680 | SHA256:40F6FEA44D8B9BFBA036193AF9F28B34F58608639F44E8E7D886D41ED6408FDC | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Documents\RCX47EF.tmp | executable | |
MD5:8D6503D01C6685381F54D71384E7EF48 | SHA256:F2D6094C5E33E228DE2D4ED6A41ABE92B5BA57CE181B8EB8C4BE626BC77B62CA | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Desktop\RCX6D4B.tmp | executable | |
MD5:7335FC512377E72533C3D6C182C7F109 | SHA256:79B94A3E044F115FD41E2AF3B885726054D82568E7871E92D34404FEB1D7CF54 | |||
| 4444 | WinLocker_Builder_0.4.exe | C:\Users\admin\Desktop\RCX6D6D.tmp | executable | |
MD5:8D6503D01C6685381F54D71384E7EF48 | SHA256:F2D6094C5E33E228DE2D4ED6A41ABE92B5BA57CE181B8EB8C4BE626BC77B62CA | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5248 | SIHClient.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | DE | binary | 419 b | whitelisted |
5248 | SIHClient.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Update%20Secure%20Server%20CA%202.1.crl | DE | binary | 407 b | whitelisted |
2528 | svchost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
1268 | svchost.exe | GET | 200 | 2.16.164.66:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
5328 | SearchApp.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
1268 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4836 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5328 | SearchApp.exe | 2.16.241.207:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
5328 | SearchApp.exe | 184.30.131.245:80 | ocsp.digicert.com | AKAMAI-AS | US | whitelisted |
2528 | svchost.exe | 20.190.159.64:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
2528 | svchost.exe | 184.30.131.245:80 | ocsp.digicert.com | AKAMAI-AS | US | whitelisted |
1268 | svchost.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
login.live.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |