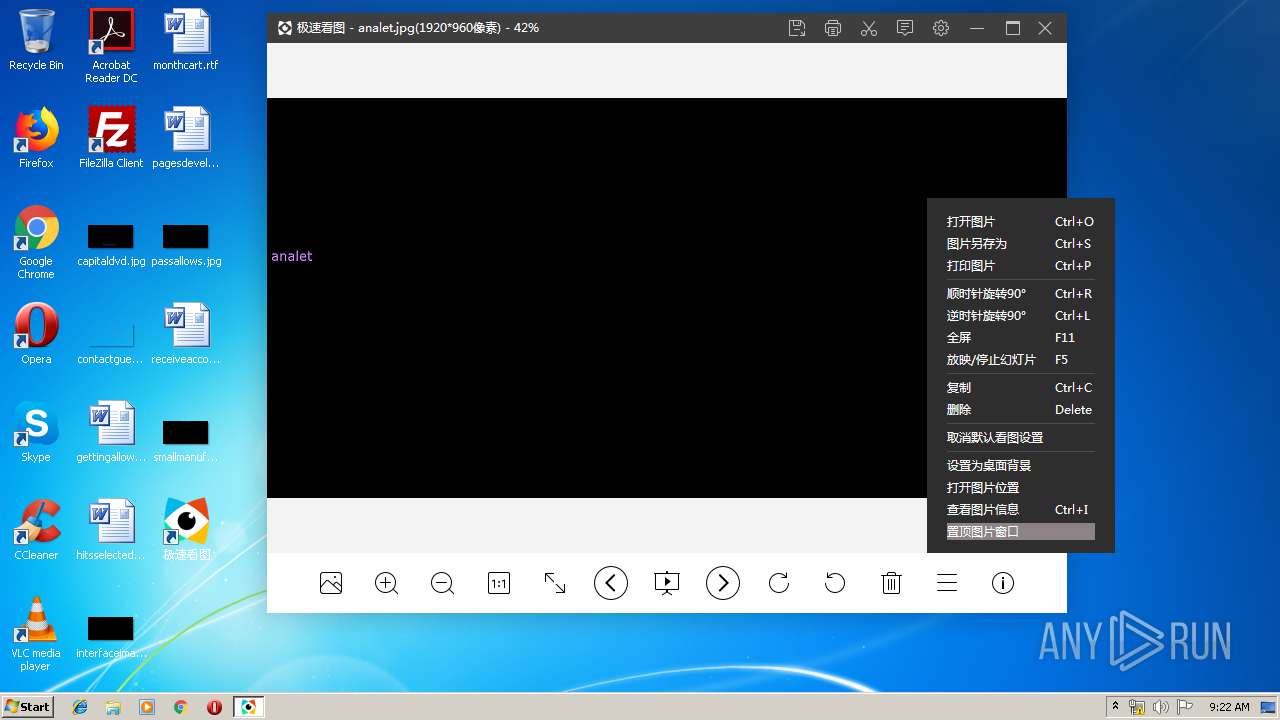
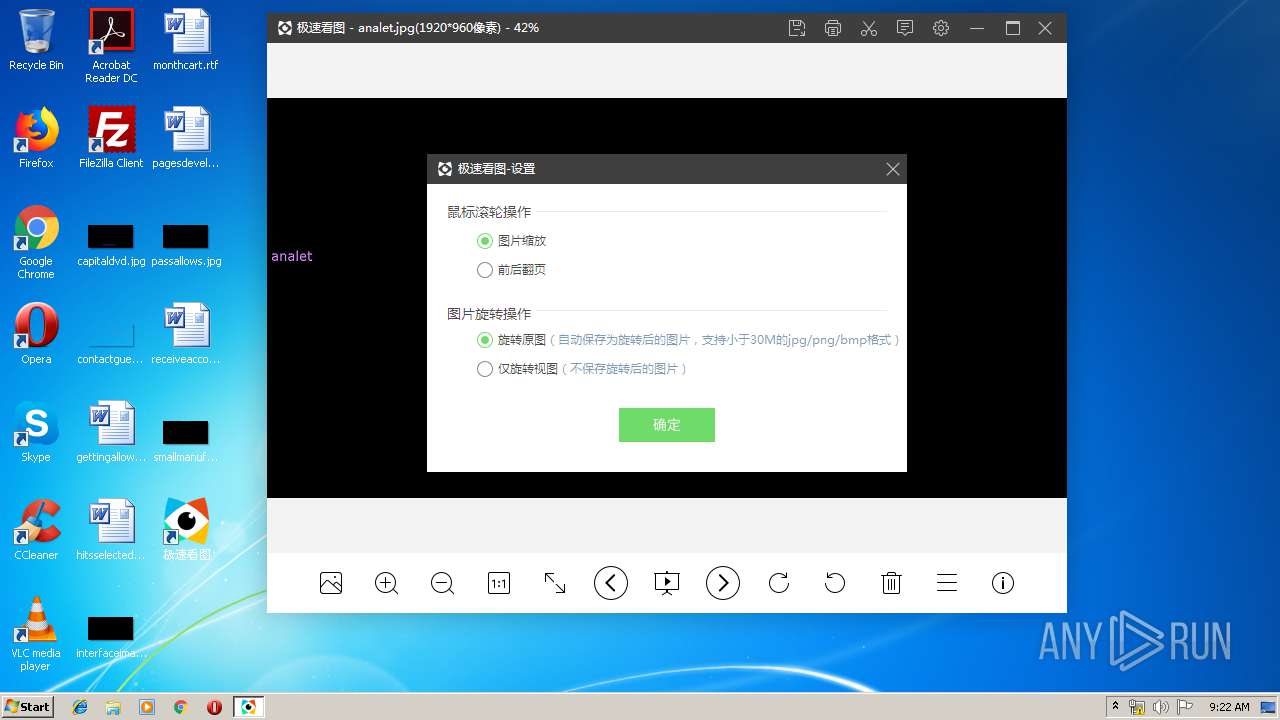
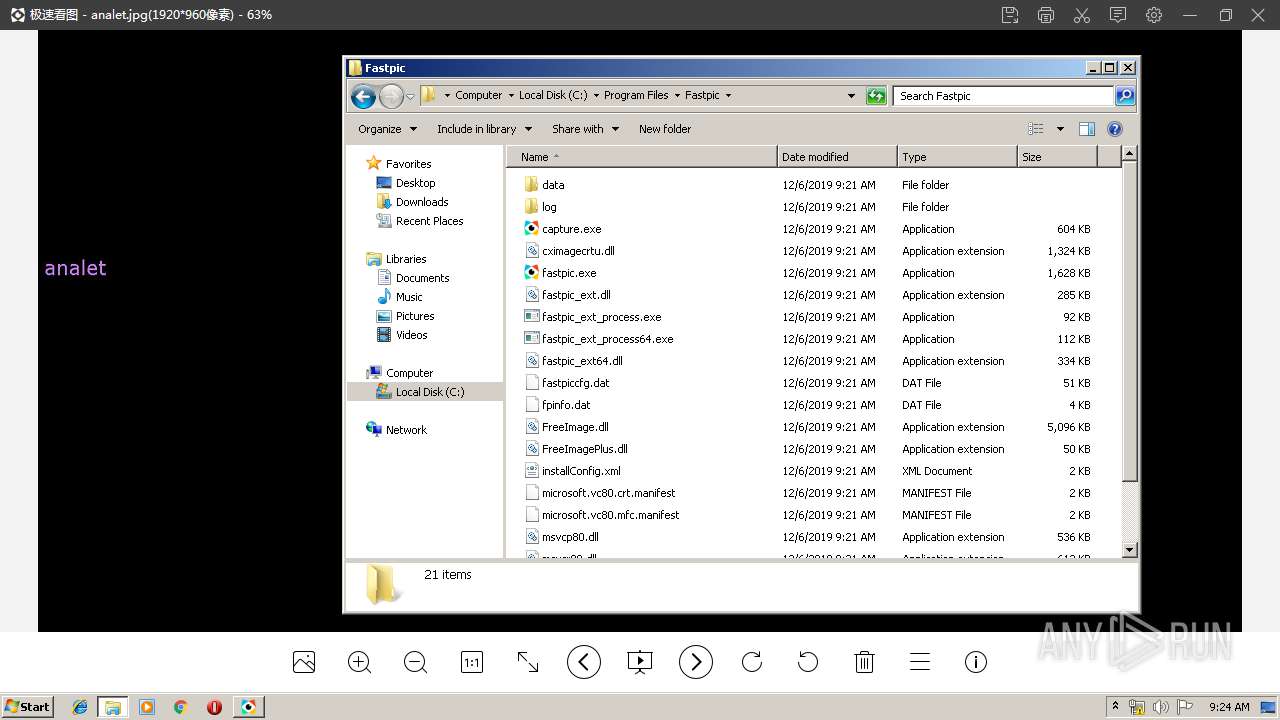
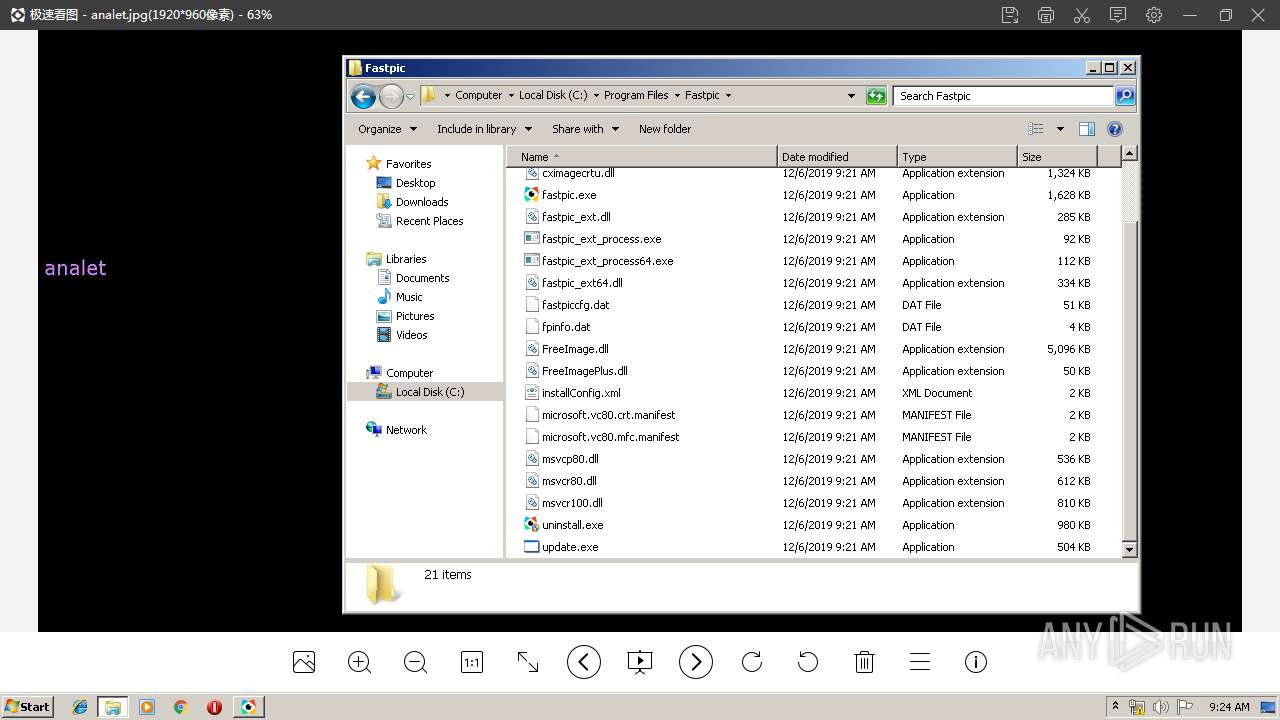
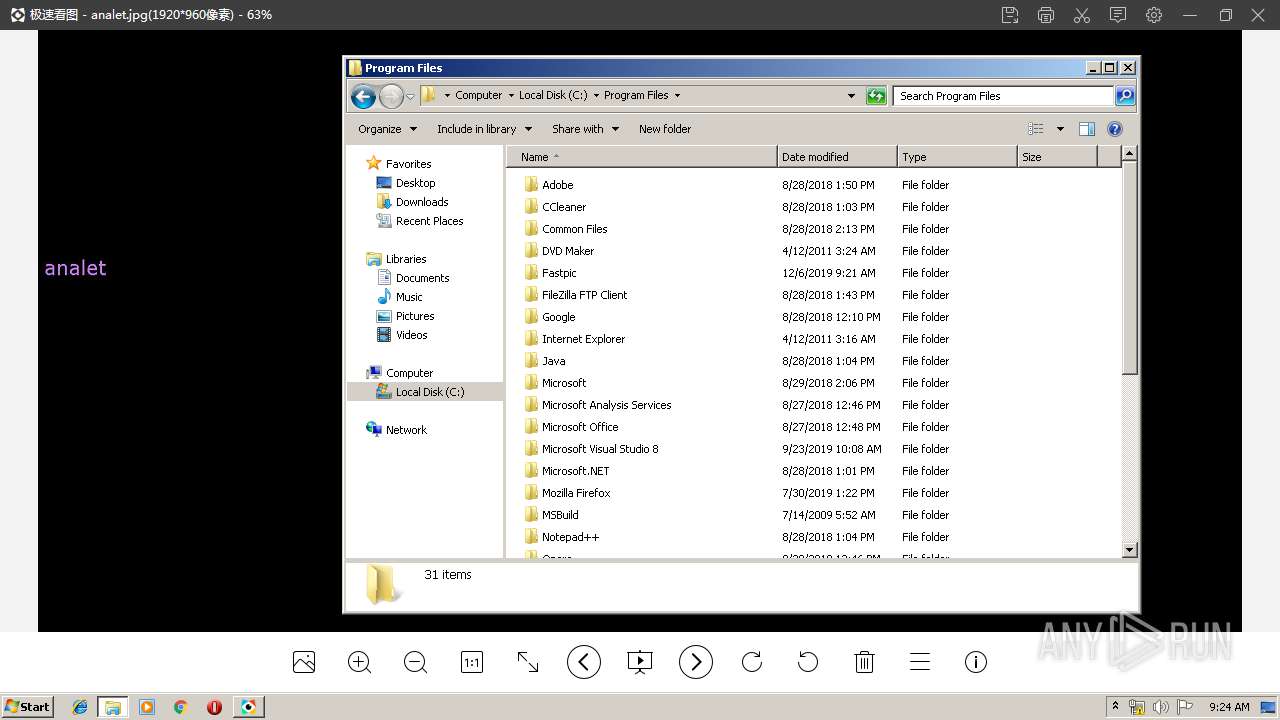
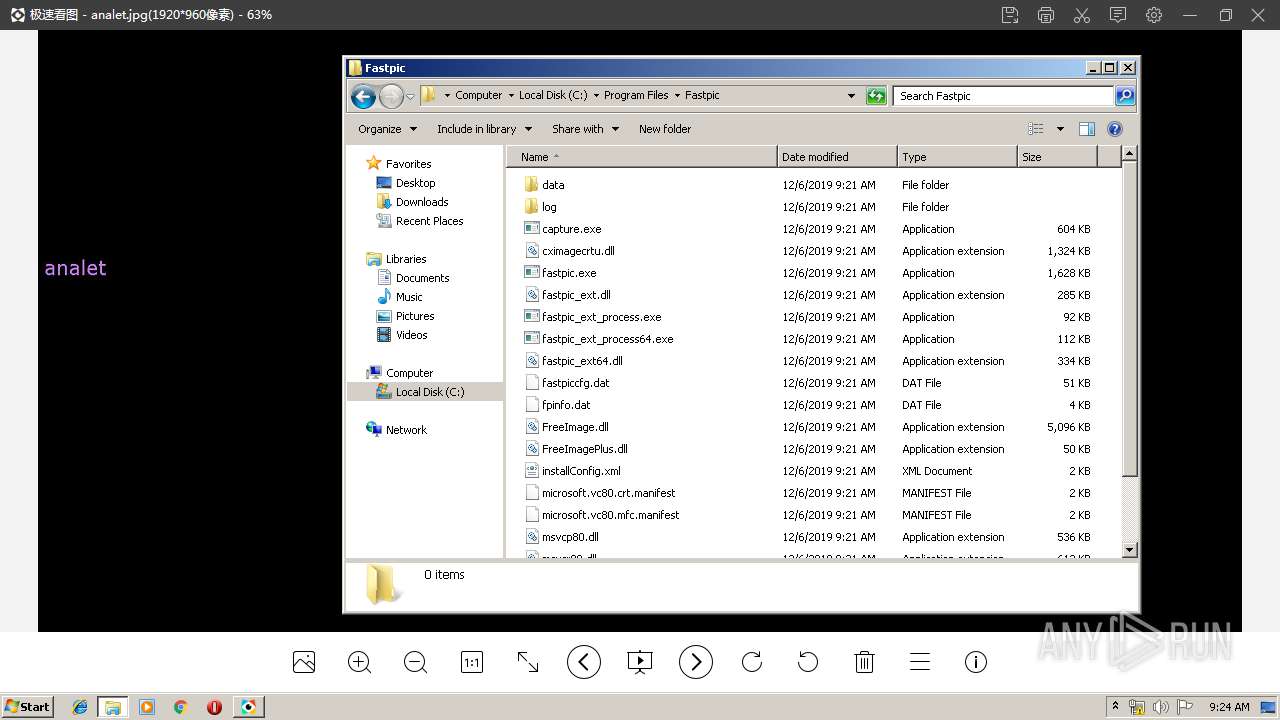
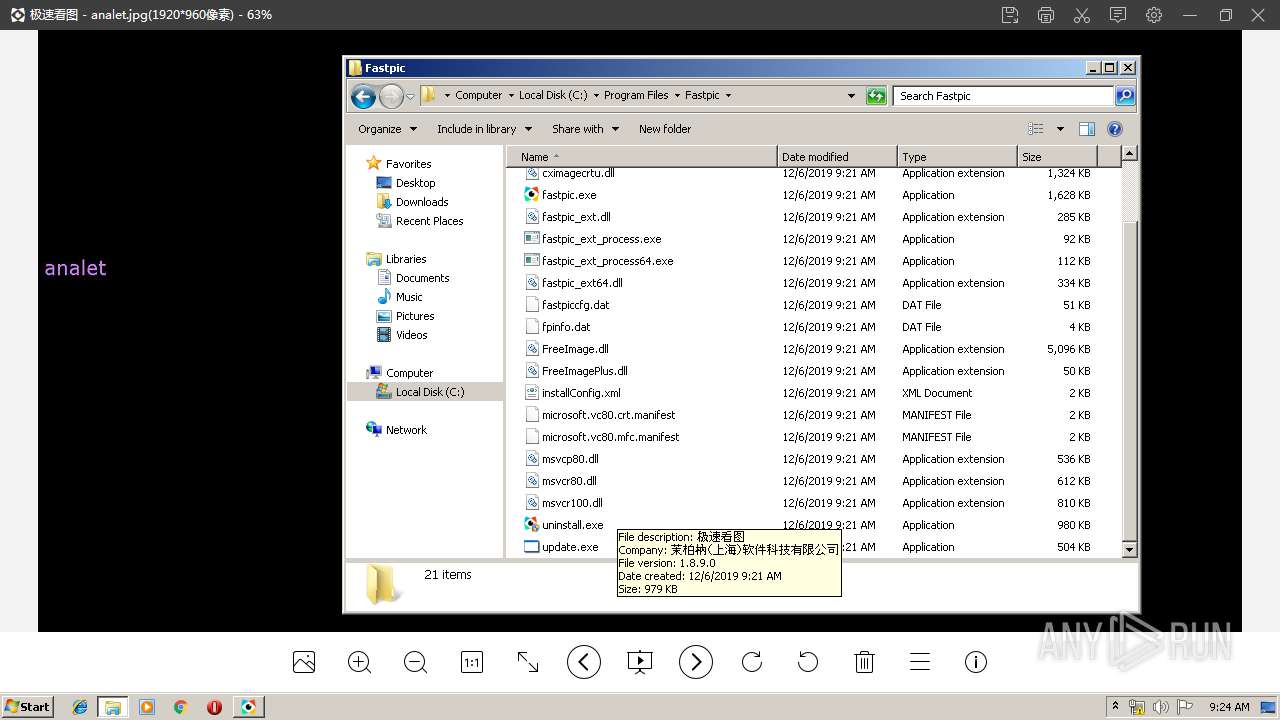
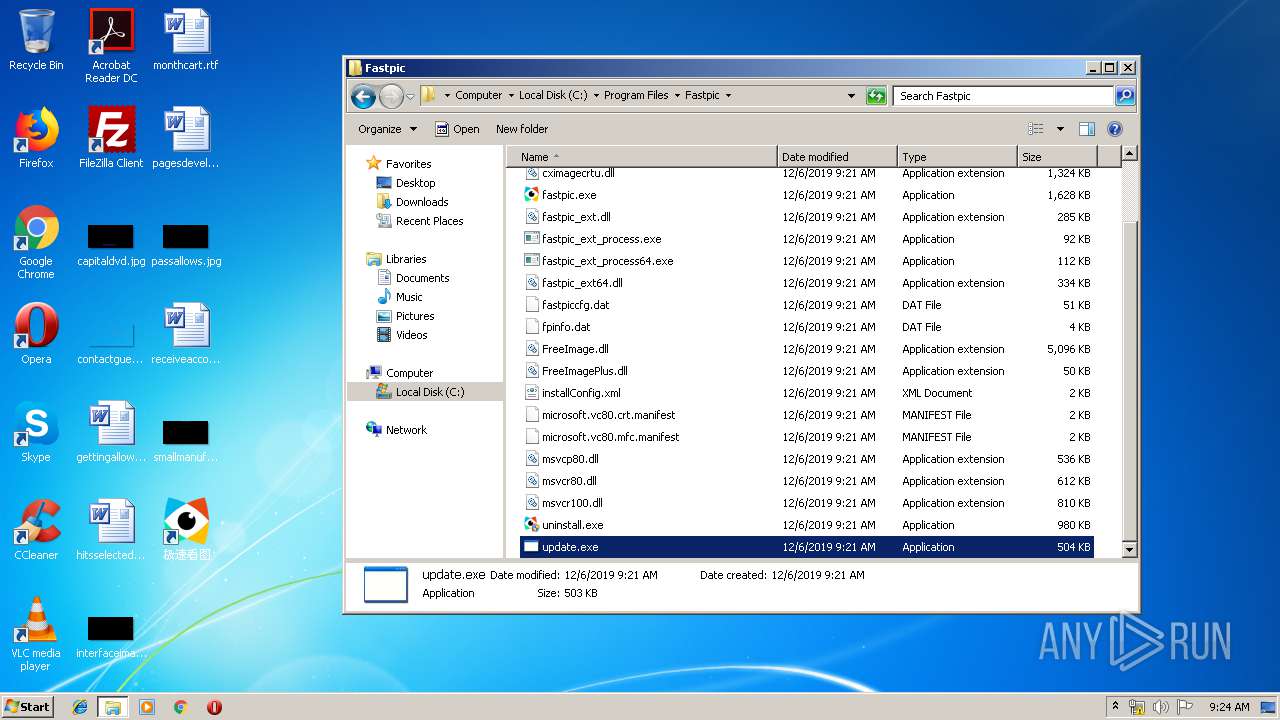
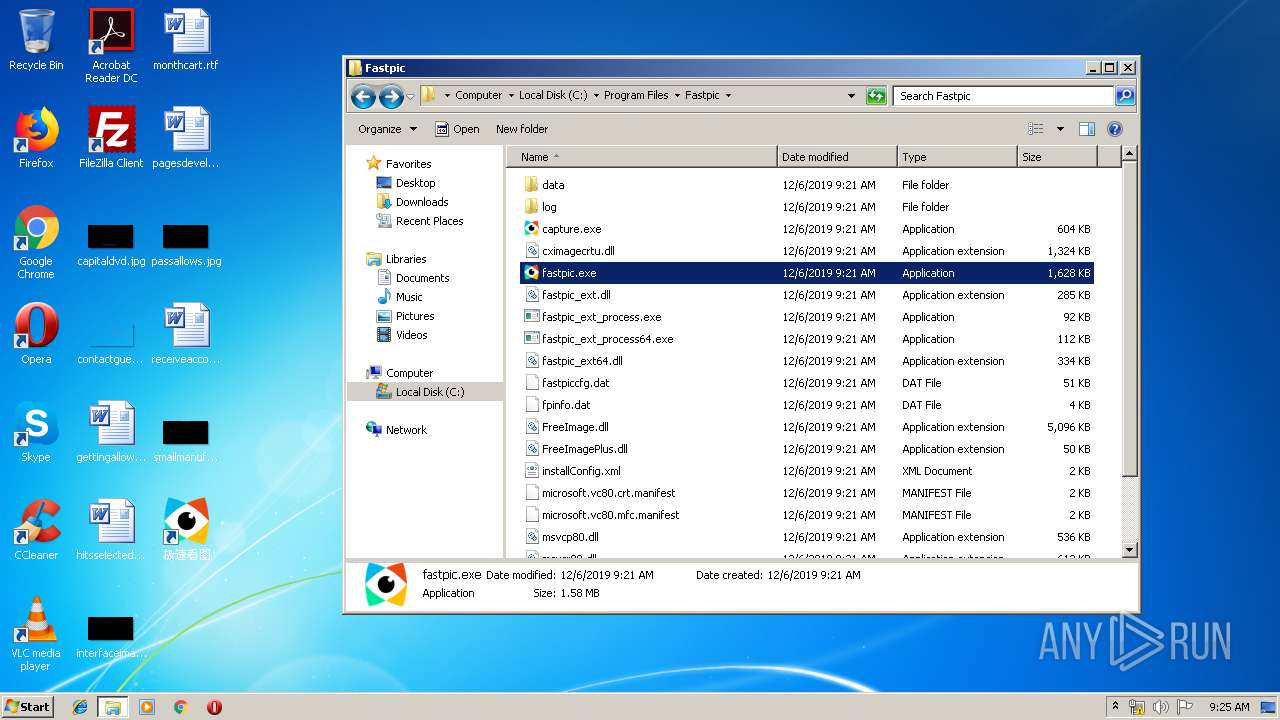
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
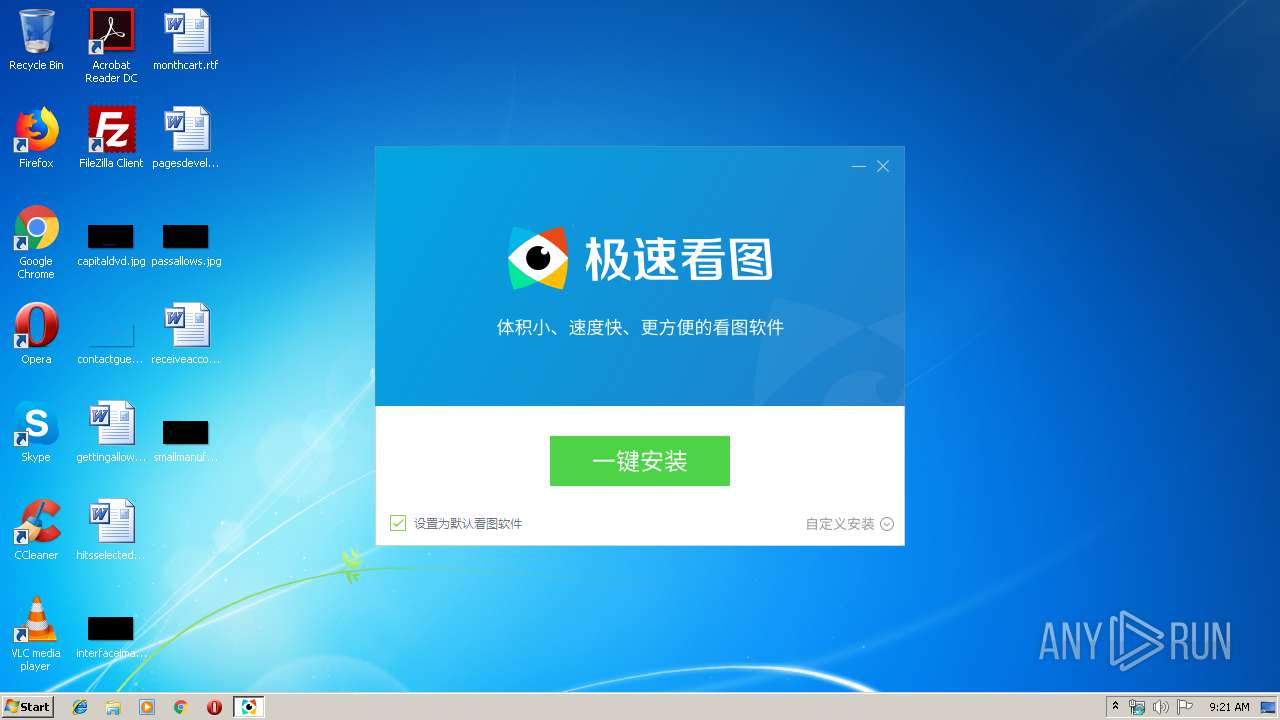
| File name: | Fastpic_Setup_18_2_1.exe |
| Full analysis: | https://app.any.run/tasks/b6cd09df-200d-48ef-ad51-c00fd42e7da5 |
| Verdict: | Malicious activity |
| Threats: | Adware is a form of malware that targets users with unwanted advertisements, often disrupting their browsing experience. It typically infiltrates systems through software bundling, malicious websites, or deceptive downloads. Once installed, it may track user activity, collect sensitive data, and display intrusive ads, including pop-ups or banners. Some advanced adware variants can bypass security measures and establish persistence on devices, making removal challenging. Additionally, adware can create vulnerabilities that other malware can exploit, posing a significant risk to user privacy and system security. |
| Analysis date: | December 06, 2019, 09:21:06 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows |
| MD5: | 076333999AE44D0C5EE0DD7EE3AC717B |
| SHA1: | B46ABA16FFACB5B8D41C01099C49A9CC52081934 |
| SHA256: | 4AB9E11F76FAE7D927F1F2161AE94DDFB3CBD0650496B231238A8C13C0B70E28 |
| SSDEEP: | 98304:dkGJ/luAOyiLI9TV7Abp6ooh8BmOHfHxU5HlaFv+v6ggWwaBWNxUNUCTLoyiCUu:dZ/luAOyiLI95At6ooDCK5HdyXW3BNTd |
| .exe | | | Win32 Executable MS Visual C++ (generic) (42.2) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (37.3) |
| .dll | | | Win32 Dynamic Link Library (generic) (8.8) |
| .exe | | | Win32 Executable (generic) (6) |
| .exe | | | Generic Win/DOS Executable (2.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 1970:01:10 08:00:16+01:00 |
| PEType: | PE32 |
| LinkerVersion: | 8 |
| CodeSize: | 622592 |
| InitializedDataSize: | 176128 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x691de |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 2018.1.31.1106 |
| ProductVersionNumber: | 1.1.9.1 |
| FileFlagsMask: | 0x0017 |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Chinese (Simplified) |
| CharacterSet: | Unicode |
| CompanyName: | 茉柏枘(上海)软件科技有限公司 |
| FileDescription: | 极速看图安装程序 |
| FileVersion: | 1, 1, 9, 1 |
| InternalName: | fastpic安装 |
| LegalCopyright: | 茉柏枘(上海)软件科技有限公司 |
| OriginalFileName: | fastpic_Installer.exe |
| ProductName: | 极速看图安装程序 |
| ProductVersion: | 1.1.9.1 |
| Architecture: | IMAGE_FILE_MACHINE_I386 |
|---|---|
| Subsystem: | IMAGE_SUBSYSTEM_WINDOWS_GUI |
| Compilation Date: | 10-Jan-1970 07:00:16 |
| Detected languages: |
|
| Debug artifacts: |
|
| CompanyName: | 茉柏枘(上海)软件科技有限公司 |
| FileDescription: | 极速看图安装程序 |
| FileVersion: | 1, 1, 9, 1 |
| InternalName: | fastpic安装 |
| LegalCopyright: | 茉柏枘(上海)软件科技有限公司 |
| OriginalFilename: | fastpic_Installer.exe |
| ProductName: | 极速看图安装程序 |
| ProductVersion: | 1.1.9.1 |
| Magic number: | MZ |
|---|---|
| Bytes on last page of file: | 0x0090 |
| Pages in file: | 0x0003 |
| Relocations: | 0x0000 |
| Size of header: | 0x0004 |
| Min extra paragraphs: | 0x0000 |
| Max extra paragraphs: | 0xFFFF |
| Initial SS value: | 0x0000 |
| Initial SP value: | 0x00B8 |
| Checksum: | 0x0000 |
| Initial IP value: | 0x0000 |
| Initial CS value: | 0x0000 |
| Overlay number: | 0x0000 |
| OEM identifier: | 0x0000 |
| OEM information: | 0x0000 |
| Address of NE header: | 0x00000108 |
| Signature: | PE |
|---|---|
| Machine: | IMAGE_FILE_MACHINE_I386 |
| Number of sections: | 4 |
| Time date stamp: | 10-Jan-1970 07:00:16 |
| Pointer to Symbol Table: | 0x00000000 |
| Number of symbols: | 0 |
| Size of Optional Header: | 0x00E0 |
| Characteristics: |
|
Name | Virtual Address | Virtual Size | Raw Size | Charateristics | Entropy |
|---|---|---|---|---|---|
.text | 0x00001000 | 0x00097193 | 0x00098000 | IMAGE_SCN_CNT_CODE, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ | 6.65704 |
.rdata | 0x00099000 | 0x0001FC2D | 0x00020000 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 4.98937 |
.data | 0x000B9000 | 0x00008C80 | 0x00005000 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 4.3624 |
.rsrc | 0x000C2000 | 0x00005D9C | 0x00006000 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 4.00104 |
Title | Entropy | Size | Codepage | Language | Type |
|---|---|---|---|---|---|
1 | 5.253 | 1054 | Latin 1 / Western European | English - United States | RT_MANIFEST |
2 | 3.85676 | 2920 | Latin 1 / Western European | Chinese - PRC | RT_ICON |
3 | 3.67216 | 5160 | Latin 1 / Western European | Chinese - PRC | RT_ICON |
4 | 3.31804 | 11560 | Latin 1 / Western European | Chinese - PRC | RT_ICON |
200 | 2.66751 | 62 | Latin 1 / Western European | Chinese - PRC | RT_GROUP_ICON |
ADVAPI32.dll |
COMCTL32.dll |
GDI32.dll |
KERNEL32.dll |
MSIMG32.dll |
OLEAUT32.dll |
SHELL32.dll |
SHLWAPI.dll |
USER32.dll |
VERSION.dll |
Title | Ordinal | Address |
|---|---|---|
??0?$_CallBack@VKSimpleDirectInfoc@@@?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@QAE@ABU012@@Z | 1 | 0x000590B2 |
??0?$_CallBack@VKSimpleDirectInfoc@@@?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@QAE@XZ | 2 | 0x000590BD |
??0?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@QAE@XZ | 3 | 0x000596AC |
??0?$kxThreadBase@VLocker@kbase@@@kbase@@QAE@XZ | 4 | 0x00059ADE |
??0ReportHelper@business_publish@@AAE@XZ | 5 | 0x0005E1F0 |
??1?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@UAE@XZ | 6 | 0x000596ED |
??1?$kxThreadBase@VLocker@kbase@@@kbase@@UAE@XZ | 7 | 0x00059B1A |
??1ReportHelper@business_publish@@UAE@XZ | 8 | 0x000590CB |
??4?$_CallBack@VKSimpleDirectInfoc@@@?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@QAEAAU012@ABU012@@Z | 9 | 0x000590C6 |
??_7?$_CallBack@VKSimpleDirectInfoc@@@?$kxQueueThreadRun@VKSimpleDirectInfoc@@$03VLocker@kbase@@@kbase@@6B@ | 10 | 0x000A6D18 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
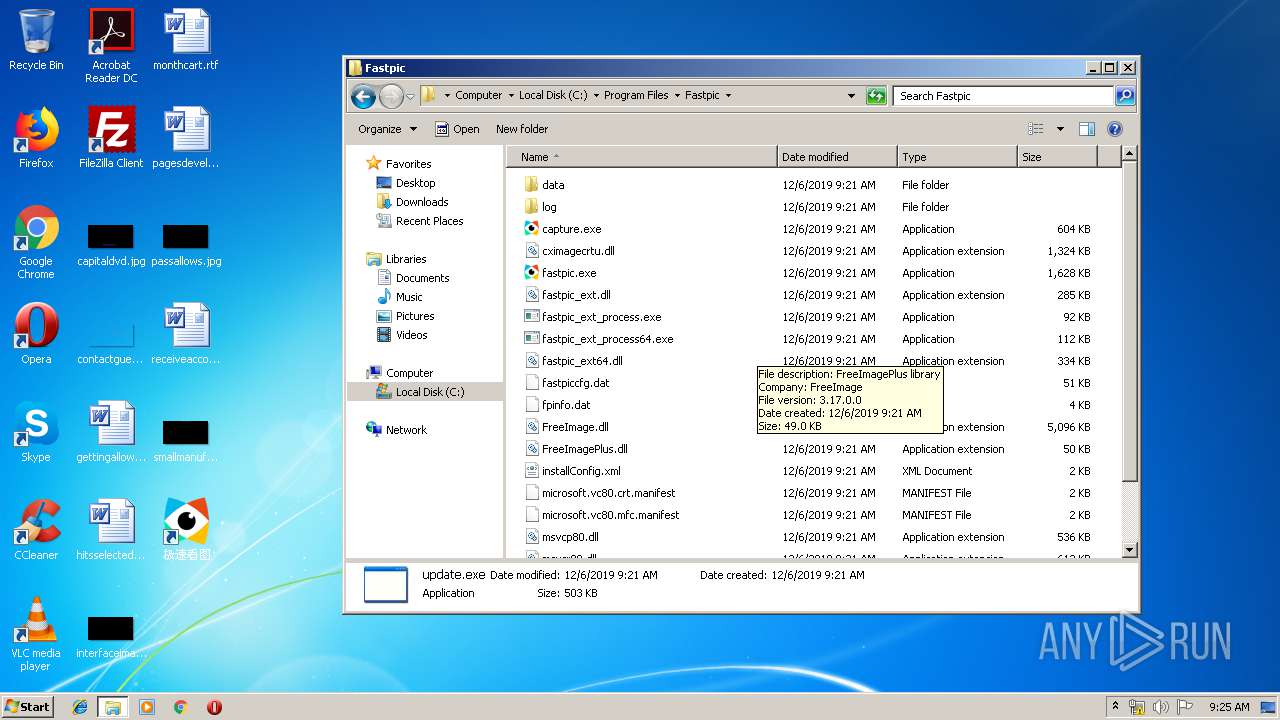
| 184 | "C:\Program Files\Fastpic\update.exe" | C:\Program Files\Fastpic\update.exe | — | explorer.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: MEDIUM Description: 极速看图 Exit code: 0 Version: 1.1.9.1 Modules
| |||||||||||||||
| 352 | C:\Windows\Explorer.EXE | C:\Windows\explorer.exe | — | — | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 388 | "C:\Users\admin\Downloads\Fastpic_Setup_18_2_1.exe" | C:\Users\admin\Downloads\Fastpic_Setup_18_2_1.exe | explorer.exe | ||||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: HIGH Description: 极速看图安装程序 Exit code: 0 Version: 1, 1, 9, 1 Modules
| |||||||||||||||
| 864 | C:\Windows\system32\svchost.exe -k netsvcs | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1428 | "C:\Program Files\Fastpic\fastpic_ext_process.exe" /ext:1 | C:\Program Files\Fastpic\fastpic_ext_process.exe | — | Fastpic_Setup_18_2_1.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: HIGH Description: 极速看图右键辅助 Exit code: 0 Version: 1.1.8.8 Modules
| |||||||||||||||
| 1484 | "C:\Program Files\Fastpic\update.exe" | C:\Program Files\Fastpic\update.exe | — | explorer.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: MEDIUM Description: 极速看图 Exit code: 0 Version: 1.1.9.1 Modules
| |||||||||||||||
| 2236 | "C:\Program Files\Fastpic\fastpic.exe" /setdefault:1 | C:\Program Files\Fastpic\fastpic.exe | — | Fastpic_Setup_18_2_1.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: HIGH Description: 极速看图 Exit code: 0 Version: 1.1.9.1 Modules
| |||||||||||||||
| 2400 | "C:\Program Files\Fastpic\fastpic.exe" | C:\Program Files\Fastpic\fastpic.exe | Fastpic_Setup_18_2_1.exe | ||||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: HIGH Description: 极速看图 Exit code: 0 Version: 1.1.9.1 Modules
| |||||||||||||||
| 2700 | "C:\Users\admin\Downloads\Fastpic_Setup_18_2_1.exe" | C:\Users\admin\Downloads\Fastpic_Setup_18_2_1.exe | — | explorer.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: MEDIUM Description: 极速看图安装程序 Exit code: 3221226540 Version: 1, 1, 9, 1 Modules
| |||||||||||||||
| 3060 | "C:\Program Files\Fastpic\capture.exe" | C:\Program Files\Fastpic\capture.exe | — | explorer.exe | |||||||||||
User: admin Company: 茉柏枘(上海)软件科技有限公司 Integrity Level: MEDIUM Description: 极速看图 Exit code: 4294967295 Version: 1.1.8.8 Modules
| |||||||||||||||
| (PID) Process: | (352) explorer.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\12B\52C64B7E |
| Operation: | write | Name: | LanguageList |
Value: en-US | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{30DB6ADA-05D2-41ac-B949-54208D1270E1}\Implemented Categories\{91D4A3D4-0265-4126-B734-2180E7627227} |
| Operation: | write | Name: | uuid |
Value: 0df7c42f288d03df3edcffc3f1447b1c | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_CURRENT_USER\Software\fastpic |
| Operation: | write | Name: | tid1 |
Value: 1 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_CURRENT_USER\Software\fastpic |
| Operation: | write | Name: | tid2 |
Value: 1 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_CURRENT_USER\Software\fastpic |
| Operation: | write | Name: | id |
Value: 168 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_CURRENT_USER\Software\fastpic |
| Operation: | write | Name: | installtime |
Value: 1575624104 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Fastpic |
| Operation: | write | Name: | DisplayIcon |
Value: C:\Program Files\Fastpic\fastpic.exe | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Fastpic |
| Operation: | write | Name: | DisplayVersion |
Value: 1.1.9.2 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Fastpic |
| Operation: | write | Name: | DisplayName |
Value: 极速看图 | |||
| (PID) Process: | (388) Fastpic_Setup_18_2_1.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Fastpic |
| Operation: | write | Name: | UninstallString |
Value: C:\Program Files\Fastpic\uninstall.exe | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\60.png | image | |
MD5:4A8BC327EEC2196F058CF65ADC1F893A | SHA256:1B0FAF30E33EFA4553BD0A6DC28600F18438D87EF66C0D108AF5F3ADE01D77C6 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\3.png | image | |
MD5:07B93E4303598ED7BC8020B10109C86C | SHA256:D33D7D08642EC5A861E649525AF7C776E076864305A451C8CD943C26D8C602D2 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\40.png | image | |
MD5:07B93E4303598ED7BC8020B10109C86C | SHA256:D33D7D08642EC5A861E649525AF7C776E076864305A451C8CD943C26D8C602D2 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\43.png | image | |
MD5:7D4067AA48FDAE41E8E5BDAEBDC794E5 | SHA256:367E5A7440950541C12ED3ED97FF756DE1EACFB26ED2609A2E1687EF9B76895C | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\41.png | image | |
MD5:3B66693AC372F82E08E7479ADA10CB1A | SHA256:F7E7F80949D2FC8C4DE448E6055BD5122BE5E169E05742257C3902FEBE207FDA | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\42.png | image | |
MD5:0DB7BB30F406E5E06F22EDEE39F24921 | SHA256:742EF1C61F0B7BF68ED2170E3CF977532A3A6BEC8C6618A9AA386B736D546CC9 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\55.png | image | |
MD5:50DC3853BE6A852BA137EE3D899EEC93 | SHA256:3949CC54BFABD08E10F8879D35B9929C627B96543FFF19E6AB3E344C23106BE9 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\44.png | image | |
MD5:B2F56ABCA310694A208AC9C4BA308388 | SHA256:67486B148D86DECD78C51E3A8BF426AD64D476F38CB4C2AD757D1FF73D7CFFF1 | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\57.png | image | |
MD5:E0FAD7346EABDA4D66A77A3A276D9FBA | SHA256:85EAF9ABF52681B9AFDBD2CD45CB4107D4C80A221DC7DB0E3081AEA7439600ED | |||
| 388 | Fastpic_Setup_18_2_1.exe | C:\Users\admin\AppData\Local\Temp\~39b792\res\58.png | image | |
MD5:F2599FE7571B78C88CBD64D8FD6A57DE | SHA256:A31BCFE3AD61855ED821BC1A69A715CDBB6E4A29D158450F8716DA749150F8AB | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3936 | update.exe | GET | 200 | 123.6.2.61:80 | http://upd.52pcfree.com/3/update/update_config.dat?time=1575624110 | CN | binary | 598 b | malicious |
388 | Fastpic_Setup_18_2_1.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
3936 | update.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
2400 | fastpic.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
2400 | fastpic.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
2400 | fastpic.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
2400 | fastpic.exe | POST | 200 | 139.199.214.236:80 | http://info.52pcfree.com/c/ | CN | binary | 43 b | suspicious |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
388 | Fastpic_Setup_18_2_1.exe | 139.199.214.236:80 | info.52pcfree.com | Shenzhen Tencent Computer Systems Company Limited | CN | malicious |
2400 | fastpic.exe | 139.199.214.236:80 | info.52pcfree.com | Shenzhen Tencent Computer Systems Company Limited | CN | malicious |
3936 | update.exe | 139.199.214.236:80 | info.52pcfree.com | Shenzhen Tencent Computer Systems Company Limited | CN | malicious |
3936 | update.exe | 123.6.2.61:80 | upd.52pcfree.com | CHINA UNICOM China169 Backbone | CN | malicious |
3544 | fastpic.exe | 139.199.214.236:80 | info.52pcfree.com | Shenzhen Tencent Computer Systems Company Limited | CN | malicious |
Domain | IP | Reputation |
|---|---|---|
info.52pcfree.com |
| suspicious |
upd.52pcfree.com |
| malicious |
PID | Process | Class | Message |
|---|---|---|---|
388 | Fastpic_Setup_18_2_1.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
388 | Fastpic_Setup_18_2_1.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
2400 | fastpic.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
2400 | fastpic.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
3936 | update.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
3936 | update.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
3936 | update.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
3936 | update.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
2400 | fastpic.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |
2400 | fastpic.exe | Misc activity | ADWARE [PTsecurity] PUP.Win32/KingSoft.E |