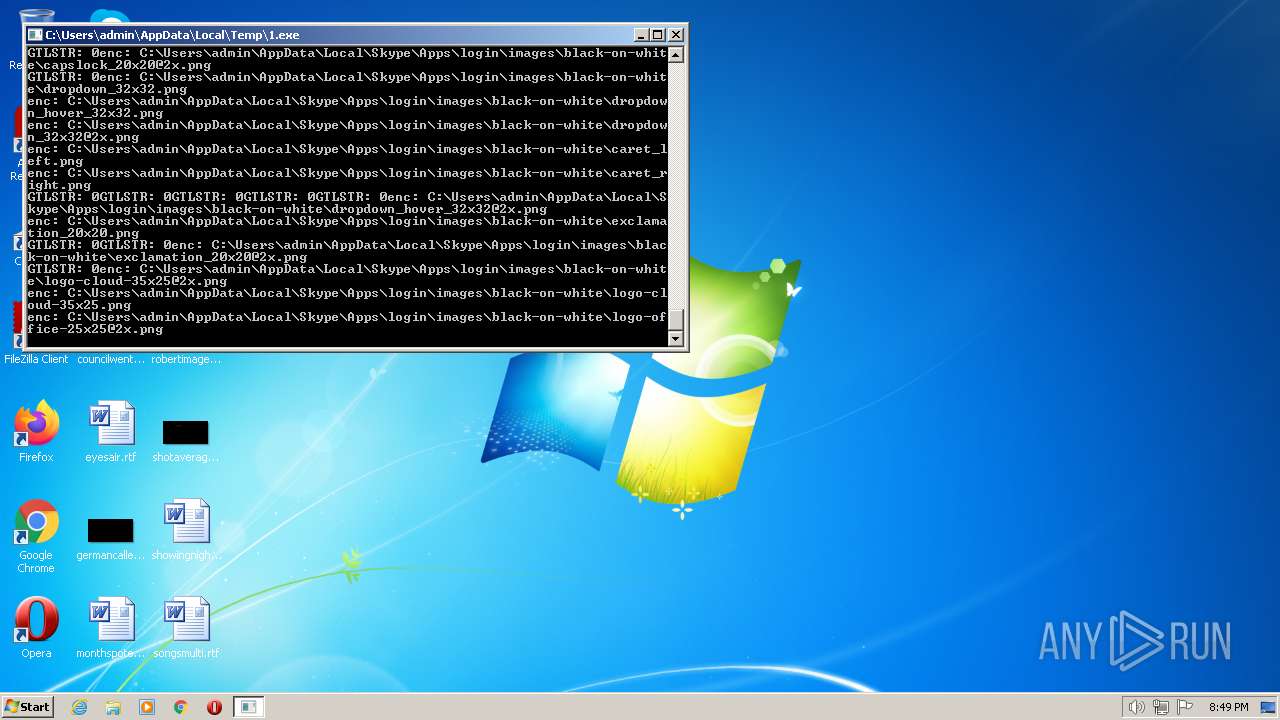
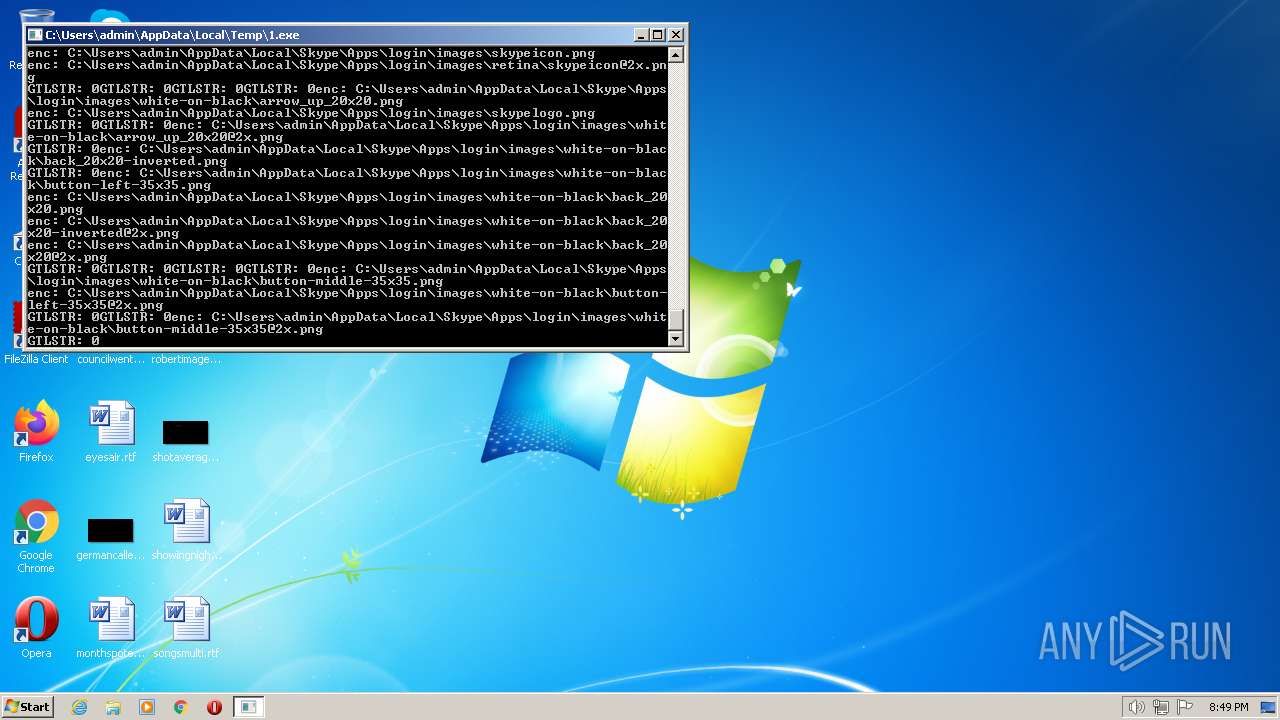
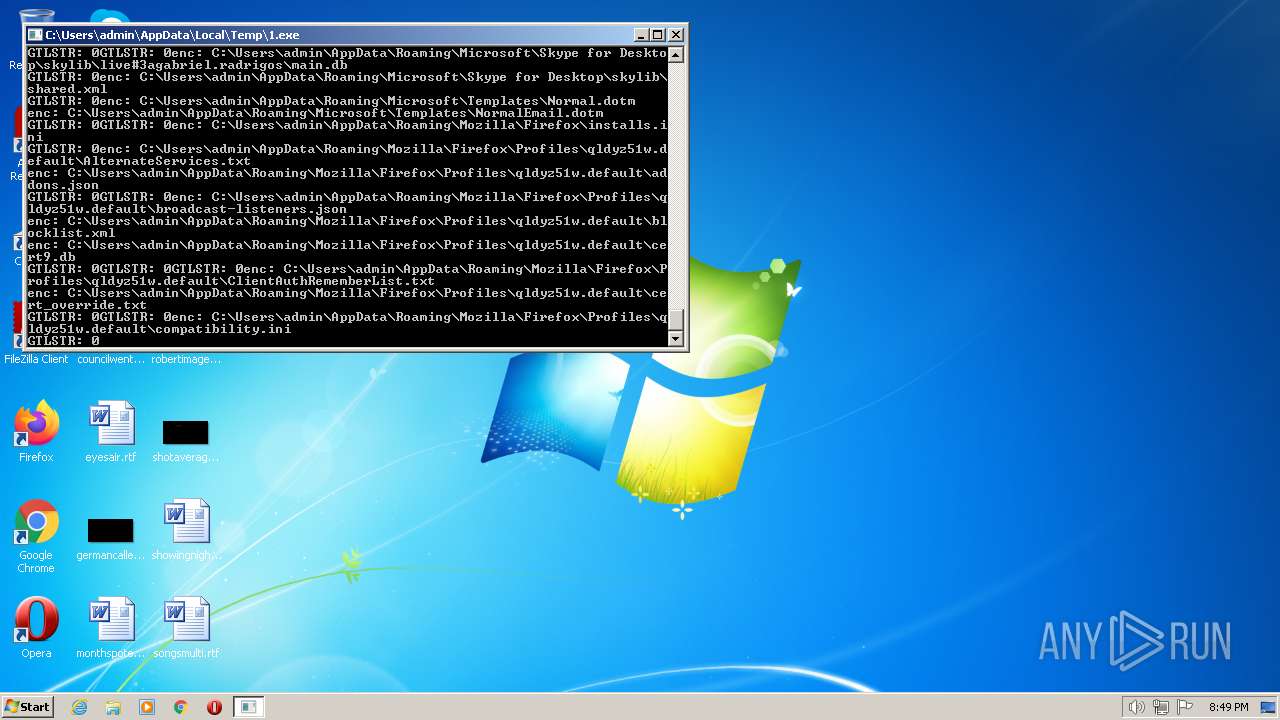
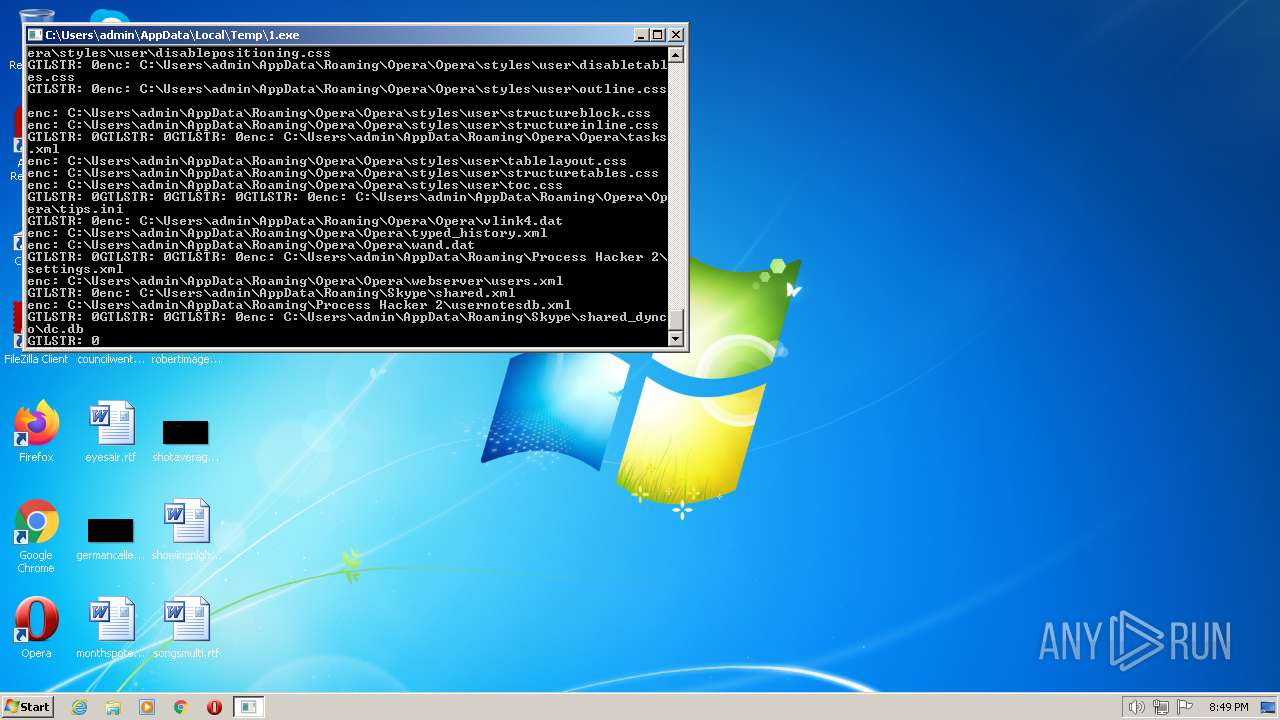
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | 1.exe |
| Full analysis: | https://app.any.run/tasks/6fef0597-65ad-4ec1-a84c-6eee6177429f |
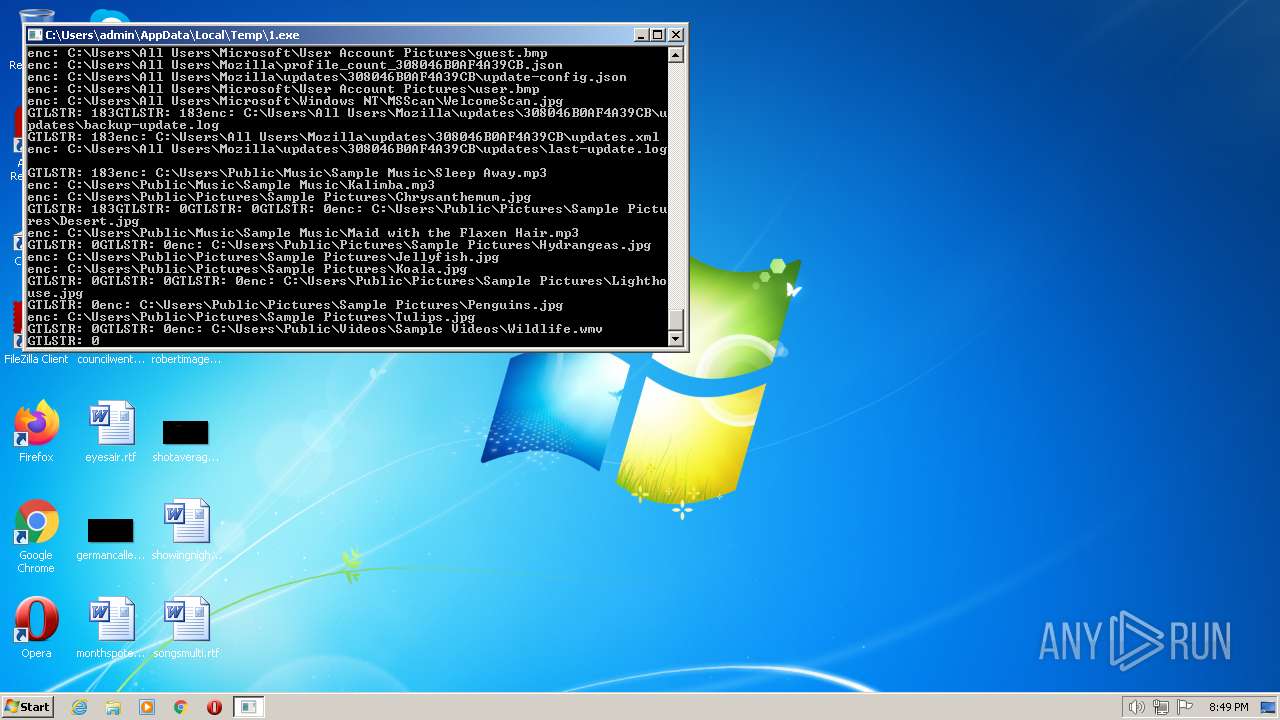
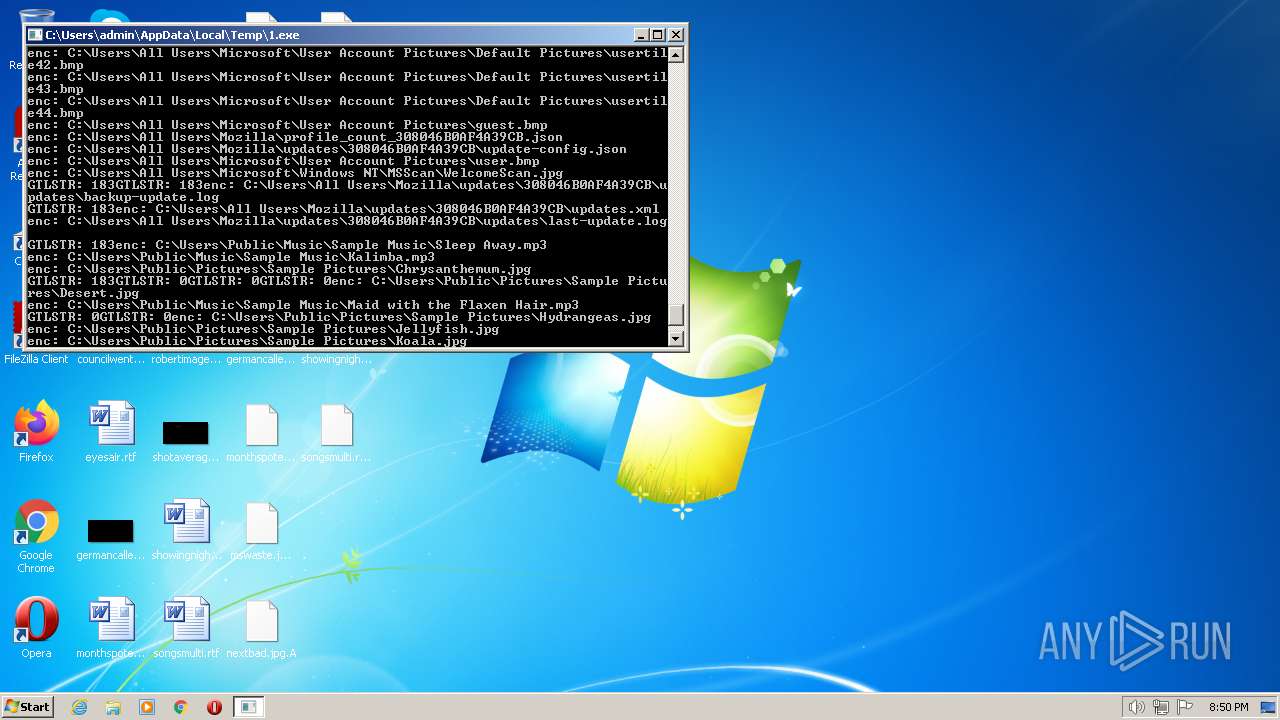
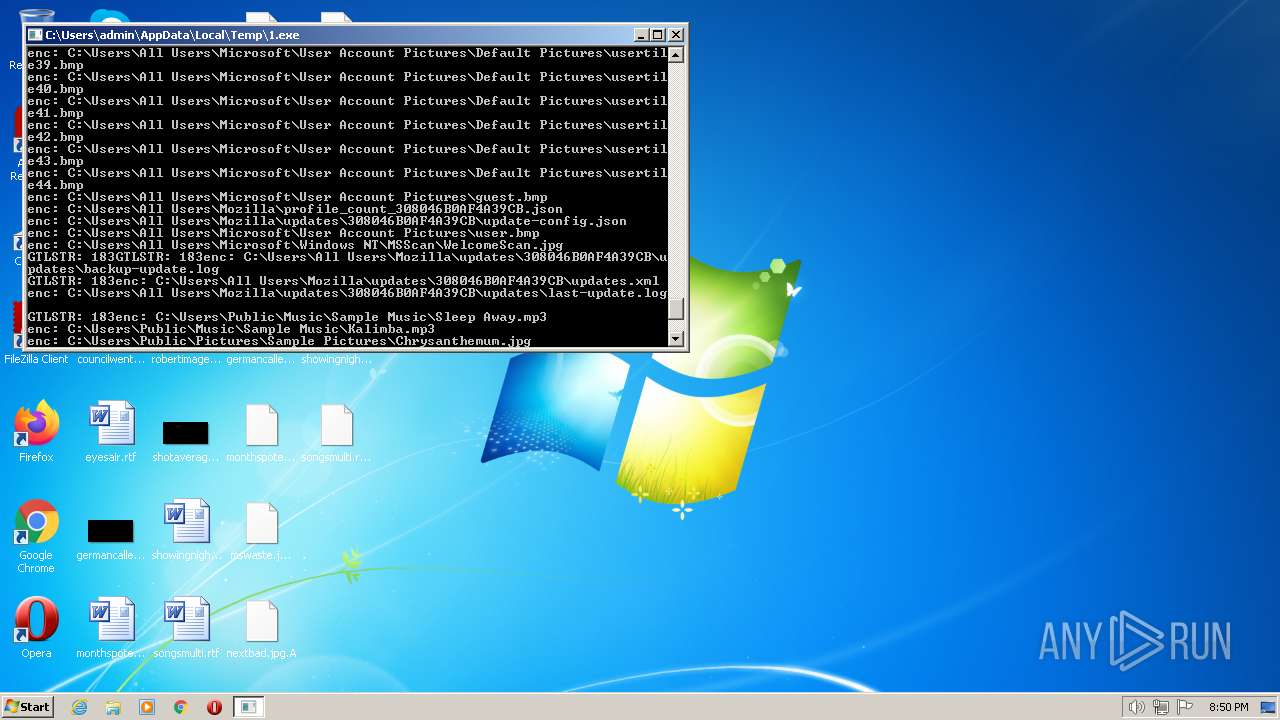
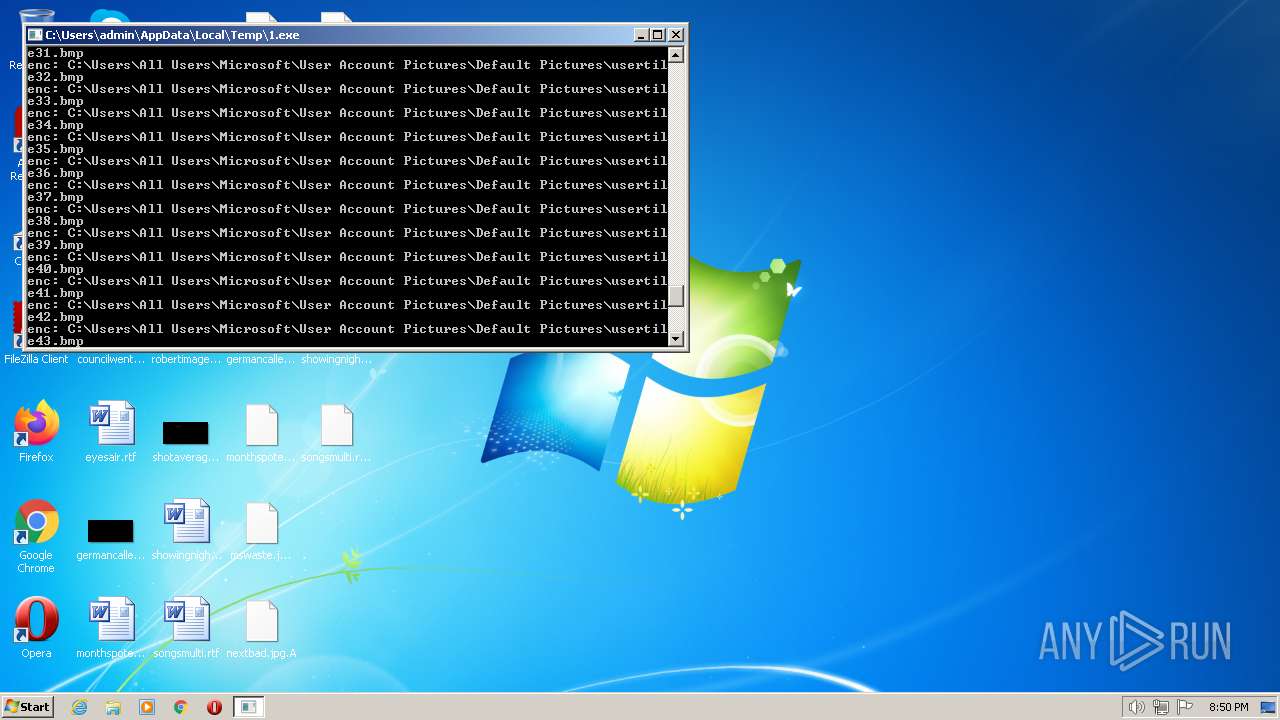
| Verdict: | Malicious activity |
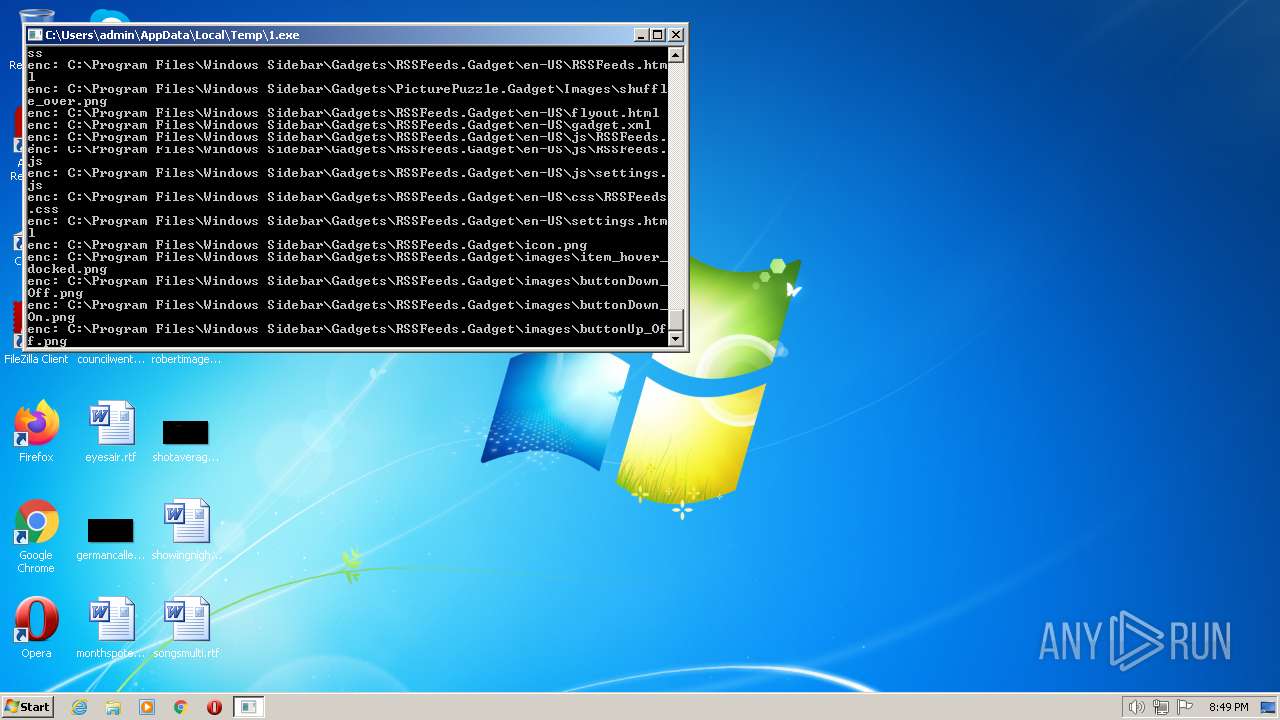
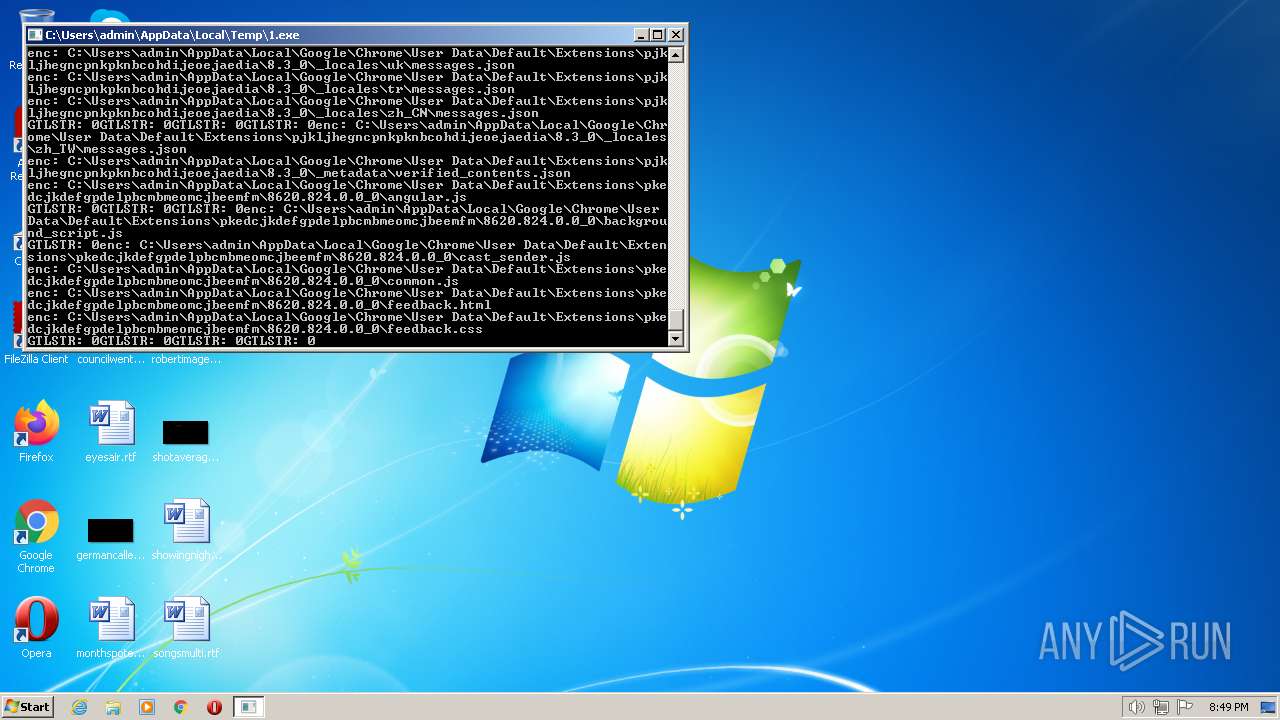
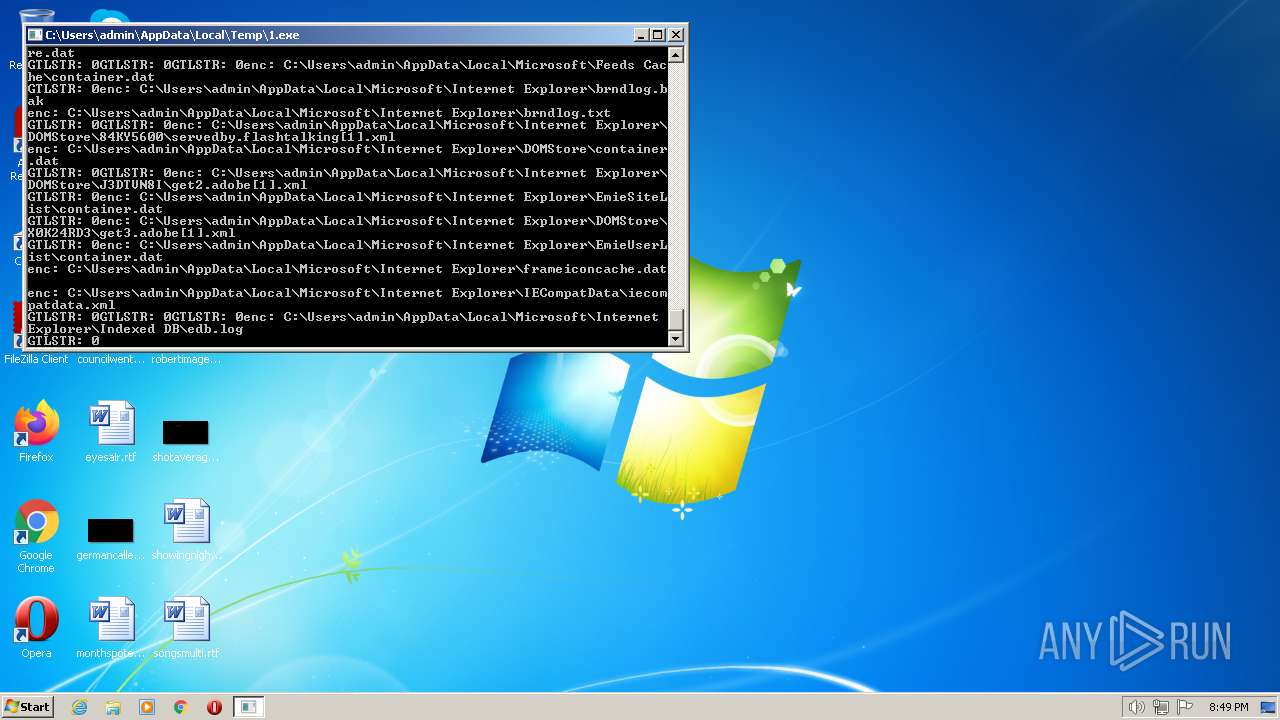
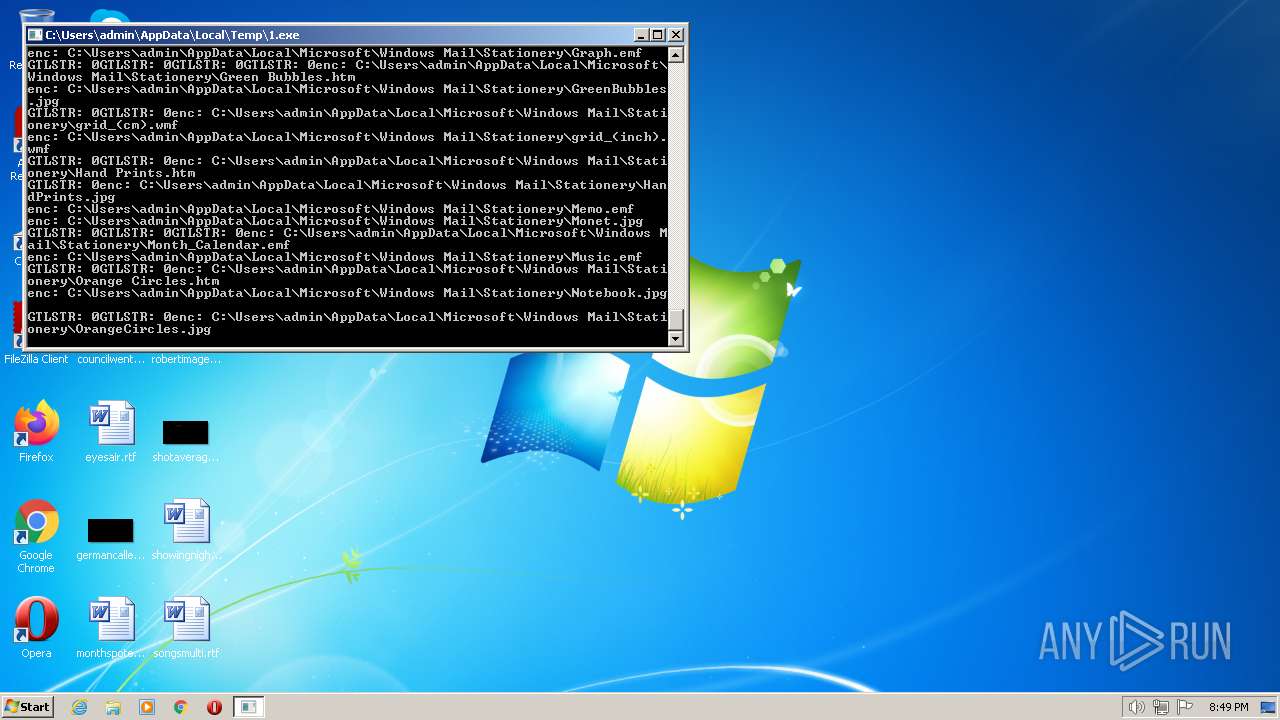
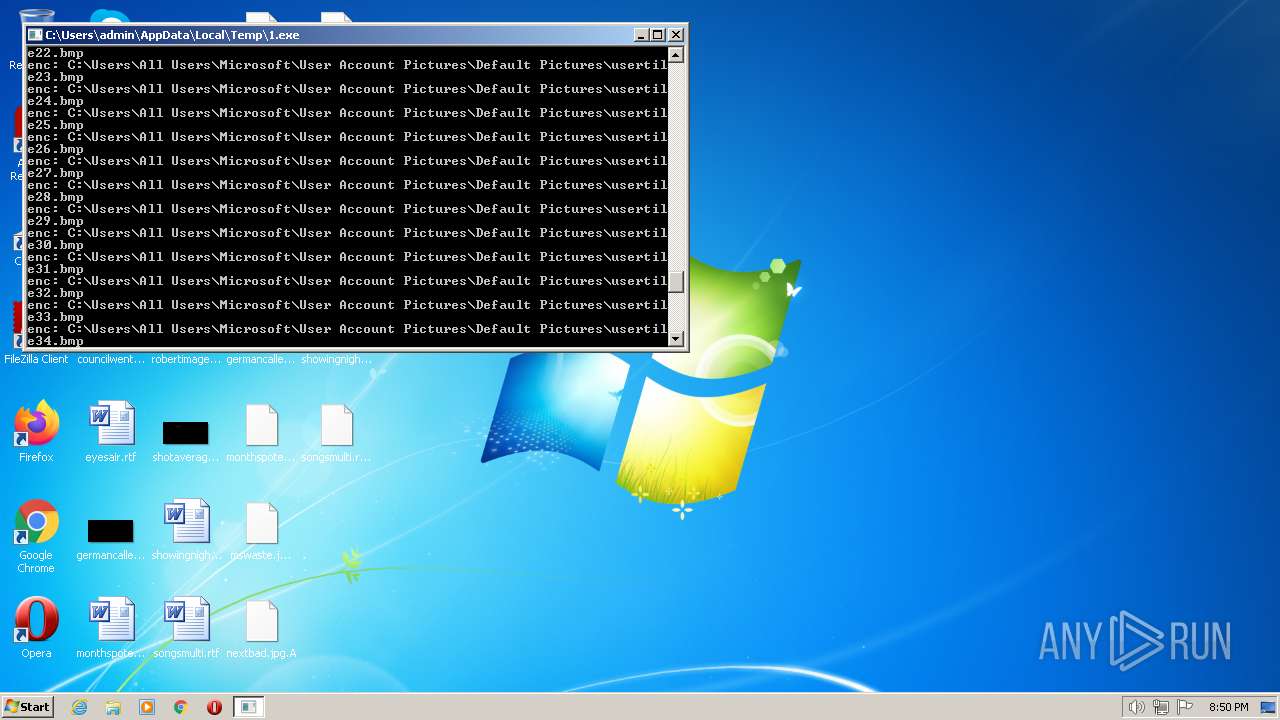
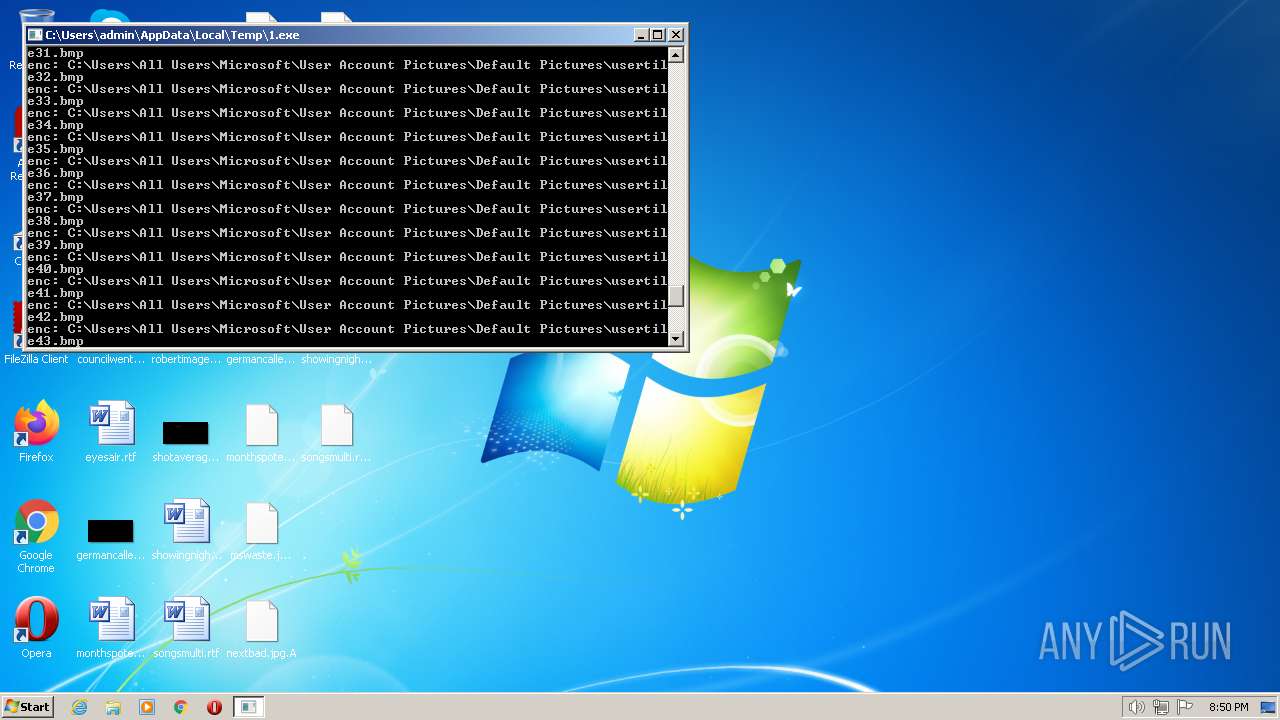
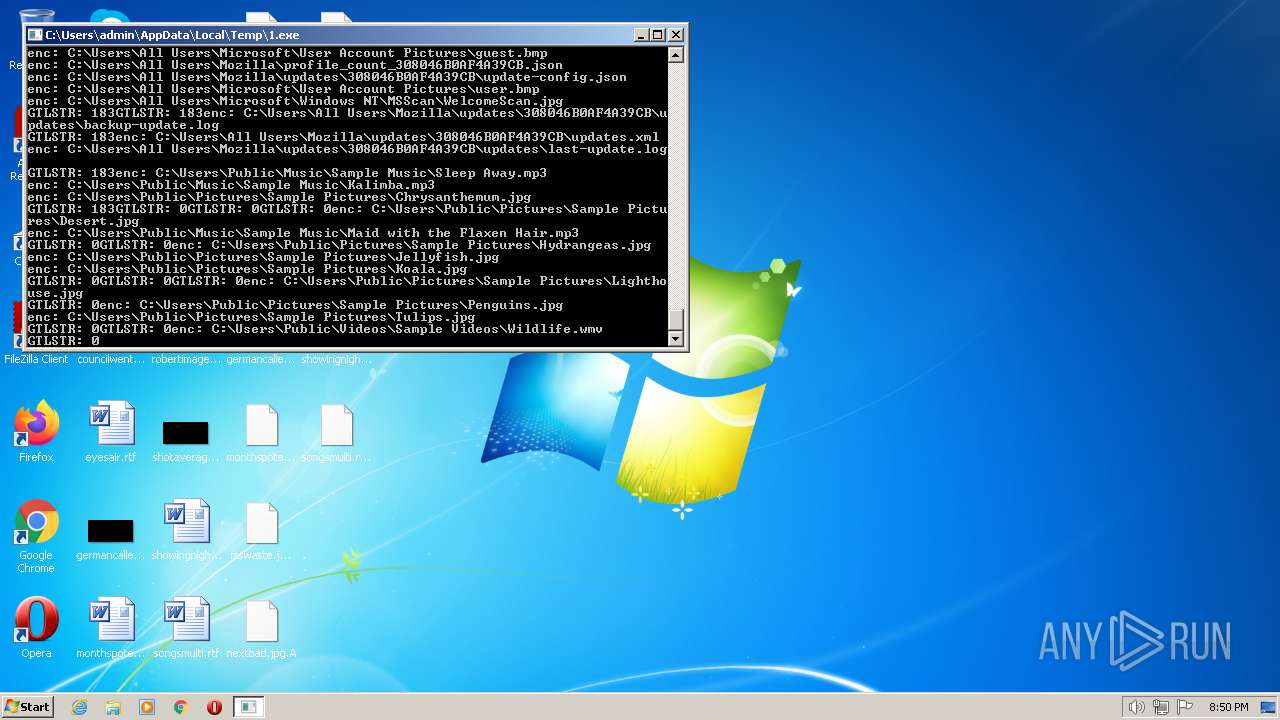
| Threats: | Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying. |
| Analysis date: | February 18, 2023, 20:49:36 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (console) Intel 80386, for MS Windows, UPX compressed |
| MD5: | E925C39FF36886405DA1BAC4CCB24739 |
| SHA1: | 5184FA06ED53FA10C1997838C9139646AB7F567A |
| SHA256: | 3C3525CD365CA7A0DA6782B3DC2FFABBF7D454426EFCD5074287A436443BADE3 |
| SSDEEP: | 192:kGtkUjI7vNjb+QcIW/qwDeiGUpQzSgba2AJX5dw8XgUPntJY+OGlDwVs:kG8jb+cW/qwDeihOzSgbabX5dw8QUPnl |
| .exe | | | Win64 Executable (generic) (39.5) |
|---|---|---|
| .exe | | | UPX compressed Win32 Executable (38.7) |
| .dll | | | Win32 Dynamic Link Library (generic) (9.4) |
| .exe | | | Win32 Executable (generic) (6.4) |
| .exe | | | Generic Win/DOS Executable (2.8) |
| Subsystem: | Windows command line |
|---|---|
| SubsystemVersion: | 6 |
| ImageVersion: | - |
| OSVersion: | 6 |
| EntryPoint: | 0xb360 |
| UninitializedDataSize: | 32768 |
| InitializedDataSize: | 4096 |
| CodeSize: | 12288 |
| LinkerVersion: | 11 |
| PEType: | PE32 |
| ImageFileCharacteristics: | Executable, 32-bit |
| TimeStamp: | 2023:02:18 16:26:25+00:00 |
| MachineType: | Intel 386 or later, and compatibles |
| Architecture: | IMAGE_FILE_MACHINE_I386 |
|---|---|
| Subsystem: | IMAGE_SUBSYSTEM_WINDOWS_CUI |
| Compilation Date: | 18-Feb-2023 16:26:25 |
| Detected languages: |
|
| Magic number: | MZ |
|---|---|
| Bytes on last page of file: | 0x0090 |
| Pages in file: | 0x0003 |
| Relocations: | 0x0000 |
| Size of header: | 0x0004 |
| Min extra paragraphs: | 0x0000 |
| Max extra paragraphs: | 0xFFFF |
| Initial SS value: | 0x0000 |
| Initial SP value: | 0x00B8 |
| Checksum: | 0x0000 |
| Initial IP value: | 0x0000 |
| Initial CS value: | 0x0000 |
| Overlay number: | 0x0000 |
| OEM identifier: | 0x0000 |
| OEM information: | 0x0000 |
| Address of NE header: | 0x000000F8 |
| Signature: | PE |
|---|---|
| Machine: | IMAGE_FILE_MACHINE_I386 |
| Number of sections: | 3 |
| Time date stamp: | 18-Feb-2023 16:26:25 |
| Pointer to Symbol Table: | 0x00000000 |
| Number of symbols: | 0 |
| Size of Optional Header: | 0x00E0 |
| Characteristics: |
|
Name | Virtual Address | Virtual Size | Raw Size | Charateristics | Entropy |
|---|---|---|---|---|---|
UPX0 | 0x00001000 | 0x00008000 | 0x00000000 | IMAGE_SCN_CNT_UNINITIALIZED_DATA, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 0 |
UPX1 | 0x00009000 | 0x00003000 | 0x00002600 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 7.74033 |
.rsrc | 0x0000C000 | 0x00001000 | 0x00000400 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 4.13471 |
Title | Entropy | Size | Codepage | Language | Type |
|---|---|---|---|---|---|
1 | 4.91161 | 381 | UNKNOWN | English - United States | RT_MANIFEST |
ADVAPI32.dll |
KERNEL32.DLL |
MSVCP110.dll |
MSVCR110.dll |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 3452 | "C:\Users\admin\AppData\Local\Temp\1.exe" | C:\Users\admin\AppData\Local\Temp\1.exe | Explorer.EXE | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0407-0000-0000000FF1CE}-C\AccessMUI.xml.A | binary | |
MD5:865311C01CF347F672FC02C1303B7505 | SHA256:3DA0887CC7C5C15760F8F57F32BD3940D9BDD6CE8074CB8E1A0284A3A77CB666 | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-040C-0000-0000000FF1CE}-C\AccessMUI.xml.A | binary | |
MD5:309EB363114188075A21AA9A77D35A93 | SHA256:3A254DFDB8458DE54F0CA460B8B2EDEE70D4DE92BA0B8372C5CB858E0F5C416E | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0407-0000-0000000FF1CE}-C\Setup.xml.A | binary | |
MD5:D7C5CFBC235431BDFF92CEBDAA010B81 | SHA256:20B1A6E3CF3092B5B5C81756ED2B7926D486025C85EF1B8301EA0D7F71DF2613 | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-040C-0000-0000000FF1CE}-C\branding.xml.A | binary | |
MD5:DE81E82495628F55A5423E8455ED113B | SHA256:9DCA14F37D9E1CC8F2CBA019C200CB315F319EF65570B6F725A75261E7F6E277 | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-040C-0000-0000000FF1CE}-C\Setup.xml.A | binary | |
MD5:724ACCEFBDB4C5FAB06FEB34173FF248 | SHA256:6451130E090DE7675E6466C1ABCCE81C0ABFF88E8A4915DE8D476D5A0CE6E04B | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0411-0000-0000000FF1CE}-C\Setup.xml.A | binary | |
MD5:13BBF8484FE00FA006E1A30C442CB73F | SHA256:3BF1BE6735793B106DA623B4D74F7D992AF7F124E4F2BAD1701F35B70B7F0583 | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0410-0000-0000000FF1CE}-C\Setup.xml.A | binary | |
MD5:8CE95C6497880D7E0871379BA50C7679 | SHA256:5C47796E449F60E5D1632E6B2A7880024BE87FC27463FE6825DB73EAF9B3CFA9 | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0411-0000-0000000FF1CE}-C\branding.xml.A | binary | |
MD5:F525D0EC927B4244F380FFBF37017675 | SHA256:94AAC9C1F4321B58798477FF9AD5075C0C1EC4ACCD77CD07C56E21214C4C428C | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0416-0000-0000000FF1CE}-C\AccessMUI.xml.A | binary | |
MD5:1467476C4F03CDB4AD71E3BBF46766CC | SHA256:862F95A3E307E585A7D034897C69AB533D21435FB6727011B50F6C6B86D33B4F | |||
| 3452 | 1.exe | C:\MSOCache\All Users\{90140000-0015-0416-0000-0000000FF1CE}-C\branding.xml.A | binary | |
MD5:C59343C45545A13DB0AB9F130A9DFF19 | SHA256:9989E5C4393EB6D5115184750B80CE884226CF266153E2564BD9C8D4D6602C3E | |||