ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
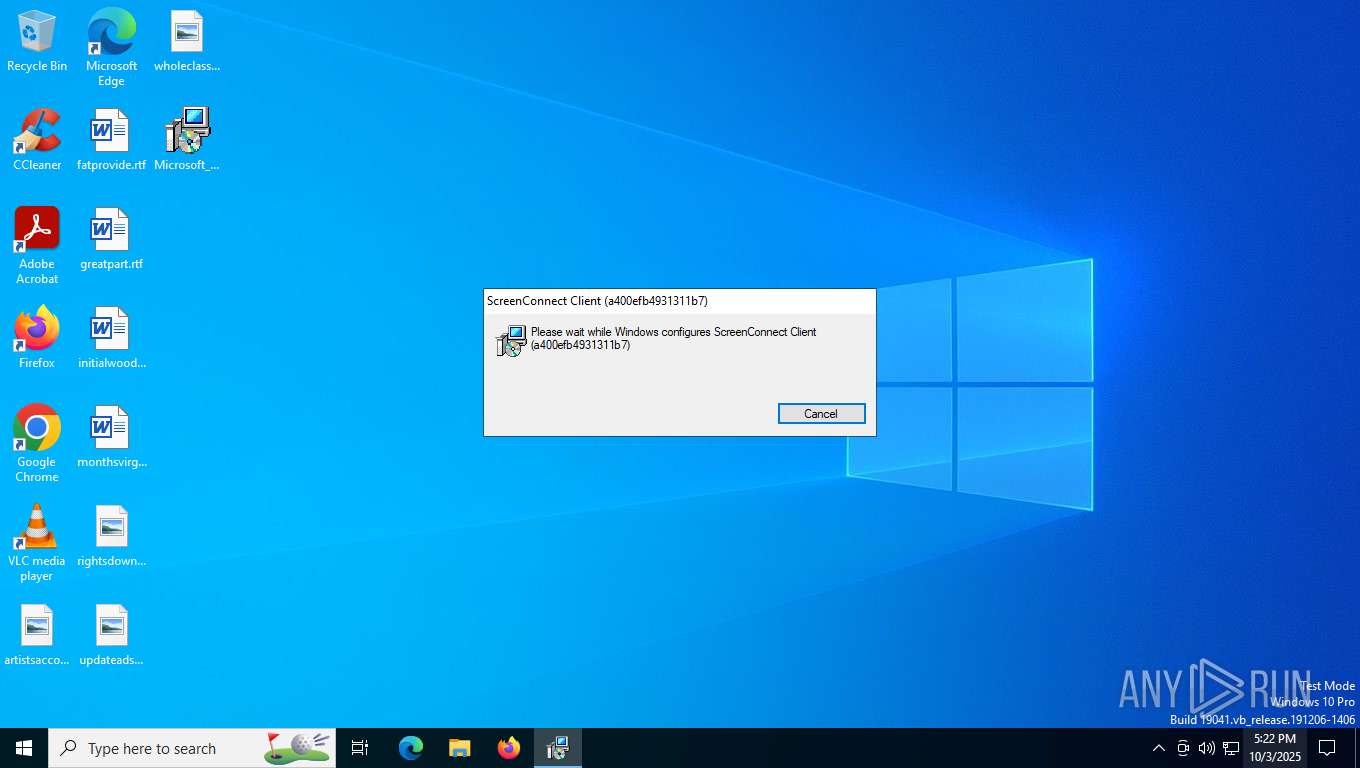
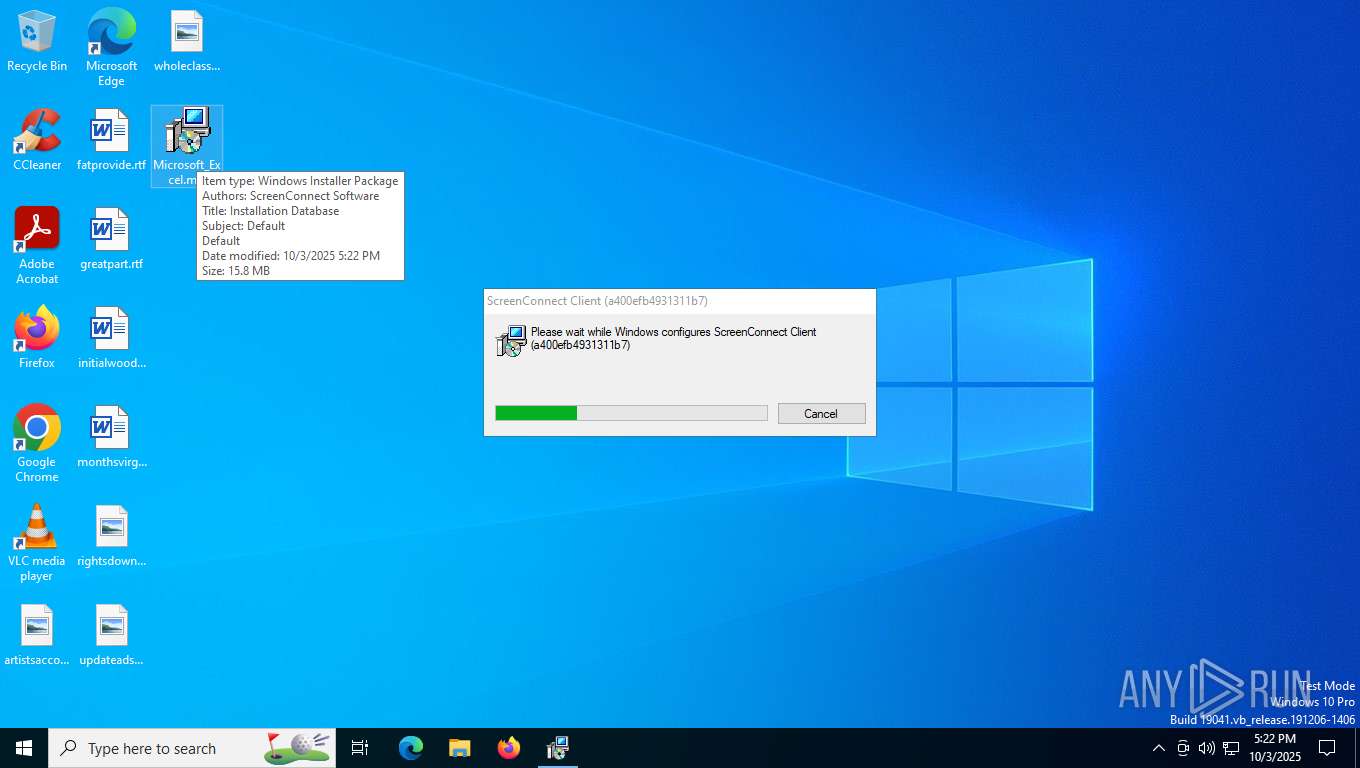
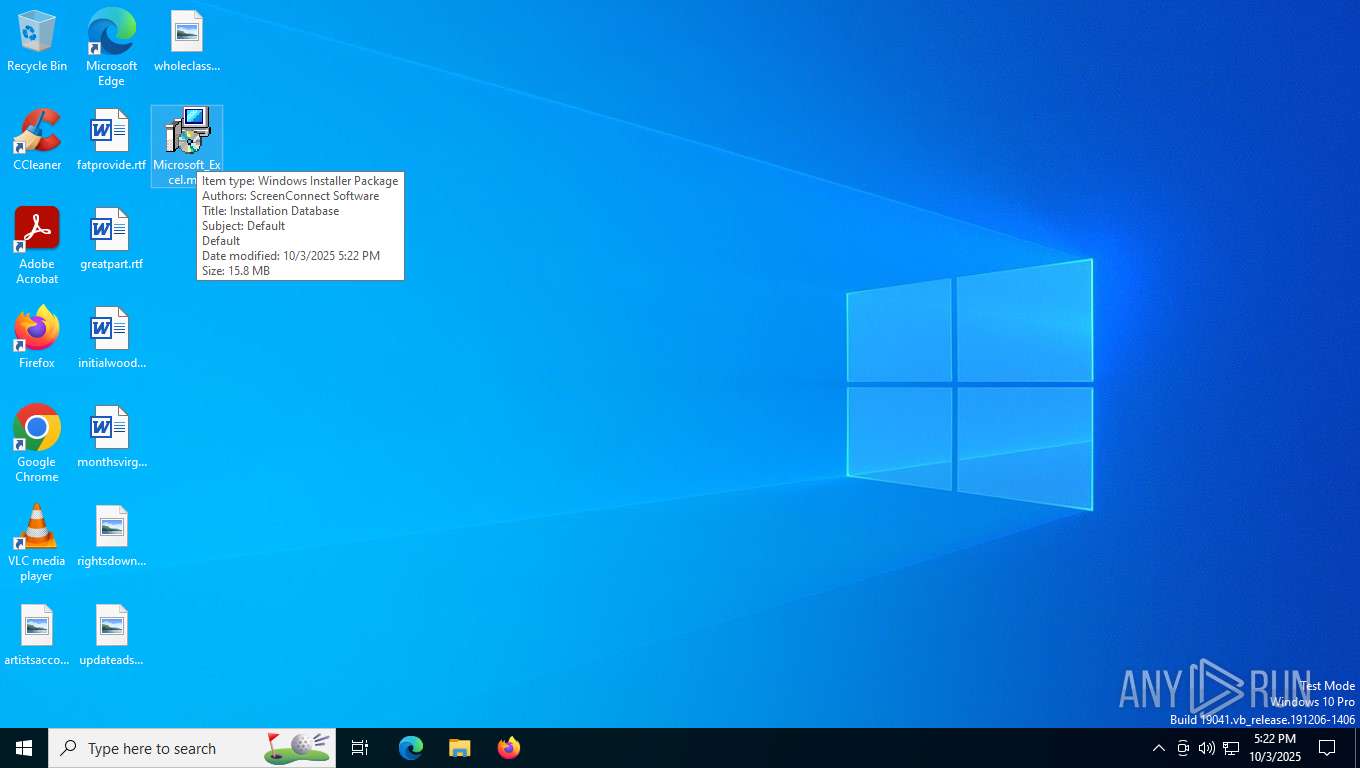
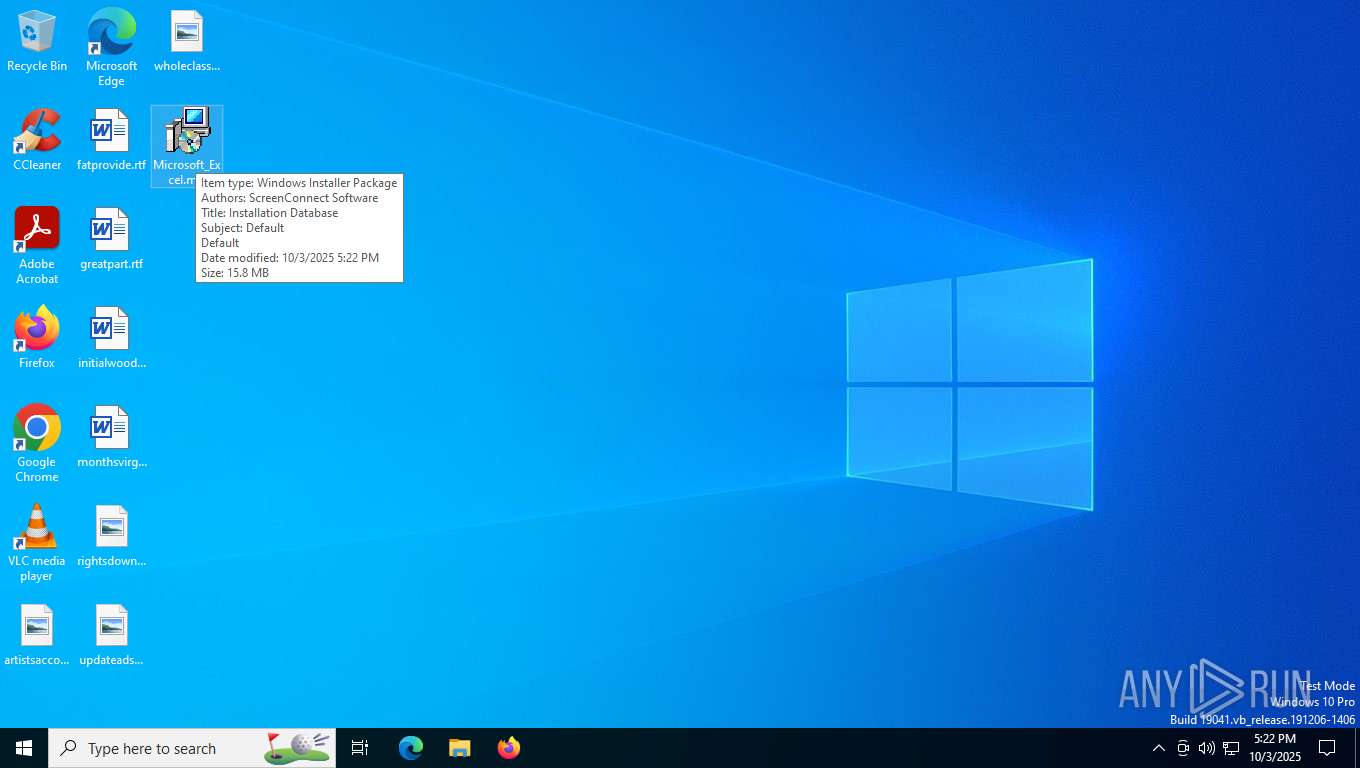
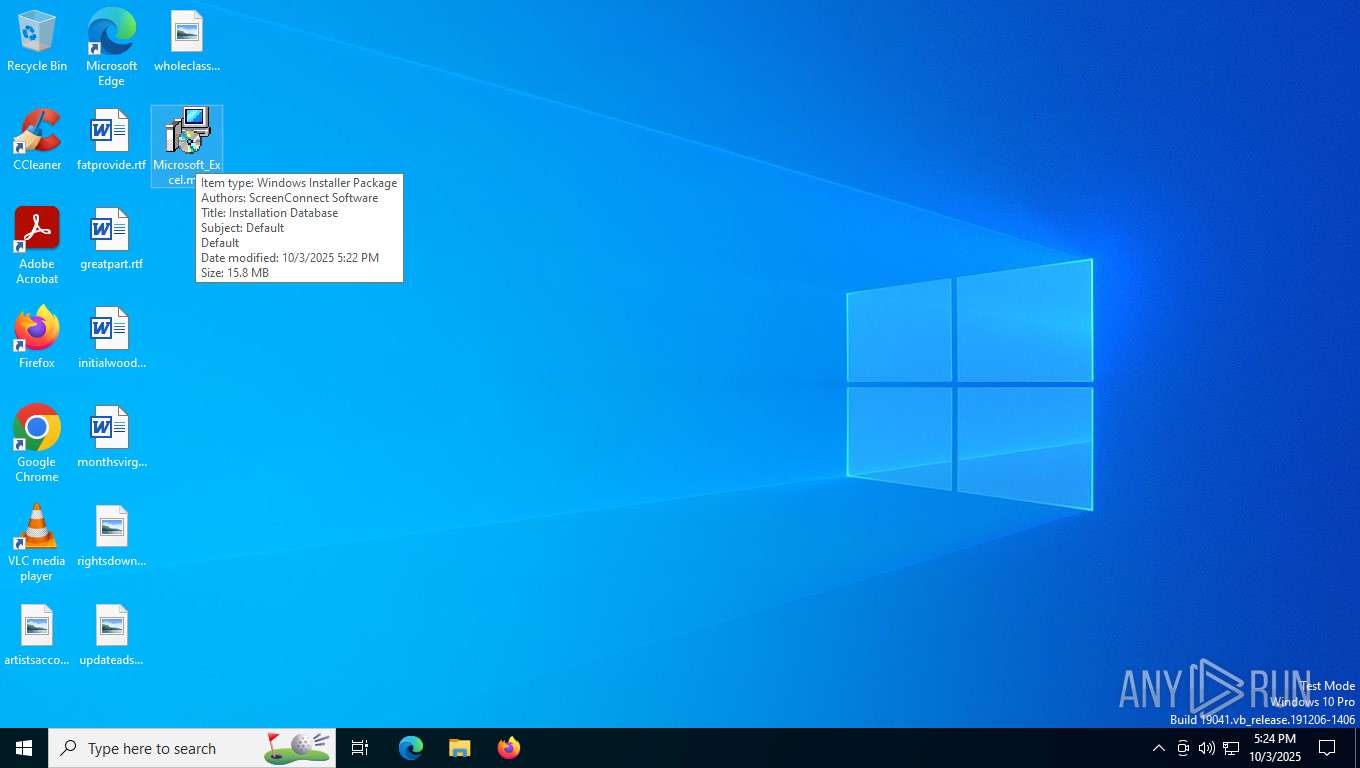
| File name: | Microsoft_Excel.msi |
| Full analysis: | https://app.any.run/tasks/0a4ba380-1cb2-444c-a8a4-5d04dfe751b5 |
| Verdict: | Malicious activity |
| Threats: | Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links. |
| Analysis date: | October 03, 2025, 17:21:59 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-msi |
| File info: | Composite Document File V2 Document, Little Endian, Os: Windows, Version 6.2, MSI Installer, Code page: 1252, Title: Installation Database, Subject: Default, Author: ScreenConnect Software, Keywords: Default, Comments: Default, Template: Intel;1033, Revision Number: {63F222AA-0C09-8B28-5ABB-E7221BC1F823}, Create Time/Date: Wed Dec 18 21:40:44 2024, Last Saved Time/Date: Wed Dec 18 21:40:44 2024, Number of Pages: 200, Number of Words: 2, Name of Creating Application: Windows Installer XML Toolset (3.11.0.1701), Security: 2 |
| MD5: | 11DD50D77AE2C24C8331D15F6ABE97D6 |
| SHA1: | D5B2B79DF6158F66DAEDF570E5762A2359296FD1 |
| SHA256: | 1FD040C91B03F71D5A120F3C6B696DA441D8424BA6F874991F5E7F1B014BEB65 |
| SSDEEP: | 196608:mlpHh8xBXNw0lpHhKlpHh9lpHh1lpHh3lpHhKklpHhKYylpHhKY:WB8xcIBaBVBtBLBlB6B |
| .msi | | | Microsoft Windows Installer (98.5) |
|---|---|---|
| .msi | | | Microsoft Installer (100) |
| CodePage: | Windows Latin 1 (Western European) |
|---|---|
| Title: | Installation Database |
| Subject: | Default |
| Author: | ScreenConnect Software |
| Keywords: | Default |
| Comments: | Default |
| Template: | Intel;1033 |
| RevisionNumber: | {63F222AA-0C09-8B28-5ABB-E7221BC1F823} |
| CreateDate: | 2024:12:18 21:40:44 |
| ModifyDate: | 2024:12:18 21:40:44 |
| Pages: | 200 |
| Words: | 2 |
| Software: | Windows Installer XML Toolset (3.11.0.1701) |
| Security: | Read-only recommended |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 688 | rundll32.exe "C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp",zzzzInvokeManagedCustomActionOutOfProc SfxCA_1518671 1 ScreenConnect.InstallerActions!ScreenConnect.ClientInstallerActions.FixupServiceArguments | C:\Windows\SysWOW64\rundll32.exe | msiexec.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1288 | "C:\Program Files (x86)\ScreenConnect Client (a400efb4931311b7)\ScreenConnect.WindowsClient.exe" "RunRole" "a399e2ce-4607-47dc-ba47-3f75768c2ace" "User" | C:\Program Files (x86)\ScreenConnect Client (a400efb4931311b7)\ScreenConnect.WindowsClient.exe | ScreenConnect.ClientService.exe | ||||||||||||
User: admin Company: ScreenConnect Software Integrity Level: MEDIUM Description: ScreenConnect Client Version: 24.4.4.9118 Modules
| |||||||||||||||
| 2152 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2672 | C:\WINDOWS\system32\msiexec.exe /V | C:\Windows\System32\msiexec.exe | services.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows® installer Version: 5.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2884 | C:\Windows\syswow64\MsiExec.exe -Embedding FB53C11B4BADD451EB888B30118E91C6 C | C:\Windows\SysWOW64\msiexec.exe | — | msiexec.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows® installer Exit code: 0 Version: 5.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4016 | C:\Windows\syswow64\MsiExec.exe -Embedding 0E54273A579E7F7C21BEB632F5238382 | C:\Windows\SysWOW64\msiexec.exe | — | msiexec.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows® installer Exit code: 0 Version: 5.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4620 | C:\Windows\syswow64\MsiExec.exe -Embedding 1EBE367069D7ECC4D51B48CD00E6AD42 E Global\MSI0000 | C:\Windows\SysWOW64\msiexec.exe | — | msiexec.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows® installer Exit code: 0 Version: 5.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5040 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | SrTasks.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5292 | C:\WINDOWS\system32\srtasks.exe ExecuteScopeRestorePoint /WaitForRestorePoint:14 | C:\Windows\System32\SrTasks.exe | — | msiexec.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Microsoft® Windows System Protection background tasks. Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppGetSnapshots (Leave) |
Value: 48000000000000000DFD8D438A34DC01700A000018060000D20700000100000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppEnumGroups (Enter) |
Value: 48000000000000000DFD8D438A34DC01700A000018060000D10700000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppEnumGroups (Leave) |
Value: 48000000000000000DFD8D438A34DC01700A000018060000D10700000100000000000000010000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppCreate (Enter) |
Value: 4800000000000000285F90438A34DC01700A000018060000D00700000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\VssapiPublisher |
| Operation: | write | Name: | IDENTIFY (Enter) |
Value: 48000000000000006A2395438A34DC01700A00004C1C0000E8030000010000000000000000000000A168DACC74440842A7FD785B88EB24E700000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SystemRestore |
| Operation: | write | Name: | SrCreateRp (Enter) |
Value: 4800000000000000153889438A34DC01700A000018060000D50700000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppGetSnapshots (Enter) |
Value: 48000000000000006B9A8B438A34DC01700A000018060000D20700000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SPP |
| Operation: | write | Name: | LastIndex |
Value: 14 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\SPP |
| Operation: | write | Name: | SppGatherWriterMetadata (Enter) |
Value: 48000000000000001AC192438A34DC01700A000018060000D30700000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2672) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\VSS\Diag\VssapiPublisher |
| Operation: | write | Name: | IDENTIFY (Leave) |
Value: 4800000000000000669145448A34DC01700A00004C1C0000E8030000000000000000000000000000A168DACC74440842A7FD785B88EB24E700000000000000000000000000000000 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2672 | msiexec.exe | C:\System Volume Information\SPP\metadata-2 | — | |
MD5:— | SHA256:— | |||
| 2672 | msiexec.exe | C:\Windows\Installer\175479.msi | — | |
MD5:— | SHA256:— | |||
| 6364 | msiexec.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\FE17BEC2A573BC9AE36869D0274FFA19_6DA81F04C5F9EAD2CD0268808FCE61E1 | binary | |
MD5:61D90F82A2F0EDC98BF60883A590A982 | SHA256:C1FA44B85833E428B10CA18485E42C34C1DBC516CB999865CF8BEC1271B97D54 | |||
| 688 | rundll32.exe | C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp-\Microsoft.Deployment.Compression.dll | executable | |
MD5:4717BCC62EB45D12FFBED3A35BA20E25 | SHA256:E04DE7988A2A39931831977FA22D2A4C39CF3F70211B77B618CAE9243170F1A7 | |||
| 6364 | msiexec.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\FE17BEC2A573BC9AE36869D0274FFA19_6DA81F04C5F9EAD2CD0268808FCE61E1 | binary | |
MD5:8DCD590E6F13B65687329322140E6E5E | SHA256:856AD0747D959C839C64498FBDE10AF255A9398423FEEF0A32319FE80D244282 | |||
| 6364 | msiexec.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\248DDD9FCF61002E219645695E3FFC98_EB6660ADA54D907AB1364F711C276089 | binary | |
MD5:4C48B49E381F68B63BE1F6AE2444DA94 | SHA256:9796D3A383E66AD609FFE36395E4FAEDEA4D0FE74BA2F78BE619D43054FE8838 | |||
| 6364 | msiexec.exe | C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp | executable | |
MD5:4ABAD4FD1A22BC922B457C28D1E40F1A | SHA256:DB51E4B70F27D0BF28789EA3345BF693035916461D22661C26F149C5BC8891ED | |||
| 688 | rundll32.exe | C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp-\Microsoft.Deployment.WindowsInstaller.dll | executable | |
MD5:5EF88919012E4A3D8A1E2955DC8C8D81 | SHA256:3E54286E348EBD3D70EAED8174CCA500455C3E098CDD1FCCB167BC43D93DB29D | |||
| 688 | rundll32.exe | C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp-\ScreenConnect.Core.dll | executable | |
MD5:665A8C1E8BA78F0953BC87F0521905CC | SHA256:3D016BEF20B3D2425939BFE32BEA6F8C08649399D8BE5A83EB461BC0E0C914EB | |||
| 688 | rundll32.exe | C:\Users\admin\AppData\Local\Temp\MSI2BE2.tmp-\ScreenConnect.InstallerActions.dll | executable | |
MD5:7572B9AE2ECF5946645863A828678B5A | SHA256:BE89FE3C59FD927B3B45FEBD183FDDC1D990994D4B64D689EB04A40D8964F493 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | GET | 200 | 104.84.152.9:443 | https://www.bing.com/DSB/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=US&setlang=en-us&clientDateTime=10%2F3%2F2025%2C%205%3A24%3A03%20PM | NL | binary | 59.6 Kb | unknown |
— | — | POST | 200 | 20.190.160.22:443 | https://login.live.com/RST2.srf | US | xml | 11.2 Kb | unknown |
— | — | POST | 200 | 20.190.160.22:443 | https://login.live.com/RST2.srf | US | xml | 11.1 Kb | unknown |
— | — | POST | 200 | 20.190.160.22:443 | https://login.live.com/RST2.srf | US | xml | 11.3 Kb | unknown |
— | — | POST | 200 | 20.190.160.5:443 | https://login.live.com/RST2.srf | US | xml | 11.3 Kb | unknown |
— | — | POST | 200 | 20.190.160.2:443 | https://login.live.com/RST2.srf | US | — | 11.3 Kb | unknown |
— | — | POST | 200 | 40.126.32.133:443 | https://login.live.com/RST2.srf | US | xml | 11.0 Kb | unknown |
— | — | GET | 200 | 95.101.142.225:443 | https://www.bing.com/th?id=ODSWG.31bcf3d1-4df8-4c6a-9b3a-447ced8d6c39&pid=dsb | unknown | — | — | unknown |
— | — | GET | 200 | 95.101.142.232:443 | https://www.bing.com/client/config?cc=US&setlang=en-US | unknown | binary | 2.15 Kb | unknown |
— | — | GET | 200 | 20.199.58.43:443 | https://arc.msn.com/v3/Delivery/Placement?pubid=da63df93-3dbc-42ae-a505-b34988683ac7&pid=280815&adm=2&w=1&h=1&wpx=1&hpx=1&fmt=json&cltp=app&dim=le&rafb=0&nct=1&pm=1&cfmt=text,image,poly&sft=jpeg,png,gif&topt=1&poptin=0&localid=w:AC7699B0-48EA-FD22-C8DC-06A02098A0F0&ctry=US&time=20251003T172403Z&lc=en-US&pl=en-US&idtp=mid&uid=9115d6d1-9f4e-4053-9297-2a8c833b3912&aid=00000000-0000-0000-0000-000000000000&ua=WindowsShellClient%2F9.0.40929.0%20%28Windows%29&asid=a111f54dbc234be7824dfff7da355f6b&ctmode=MultiSession&arch=x64&betaedgever=0.0.0.0&canedgever=0.0.0.0&cdm=1&cdmver=10.0.19041.3636&currsel=137271744000000000&devedgever=0.0.0.0&devfam=Windows.Desktop&devform=Unknown&devosver=10.0.19045.4046&disphorzres=1360&dispsize=16.3&dispvertres=768&fosver=16299&isu=0&lo=4245683&metered=false&nettype=ethernet&npid=sc-280815&oemName=DELL&oemid=DELL&ossku=Professional&prevosver=15063&smBiosDm=DELL&stabedgever=133.0.3065.92&tl=2&tsu=1636213&waasBldFlt=1&waasCfgExp=1&waasCfgSet=1&waasRetail=1&waasRing=&svoffered=2 | US | binary | 3.20 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
6364 | msiexec.exe | 65.9.95.93:80 | ocsps.ssl.com | AMAZON-02 | US | whitelisted |
5904 | ScreenConnect.ClientService.exe | 194.102.105.26:8880 | listen.onyxaquarius.top | — | RO | unknown |
6340 | slui.exe | 4.154.209.85:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
2152 | slui.exe | 4.154.209.85:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5224 | SearchApp.exe | 2.16.241.218:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
5276 | svchost.exe | 40.126.32.76:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
ocsps.ssl.com |
| whitelisted |
listen.onyxaquarius.top |
| unknown |
activation-v2.sls.microsoft.com |
| whitelisted |
dns.msftncsi.com |
| whitelisted |
www.bing.com |
| whitelisted |
login.live.com |
| whitelisted |
arc.msn.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2428 | svchost.exe | A Network Trojan was detected | MALWARE [ANY.RUN] Suspected Domain Associated with Malware Distribution (onyxaquarius .top) |
2428 | svchost.exe | Potentially Bad Traffic | ET DNS Query to a *.top domain - Likely Hostile |