ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
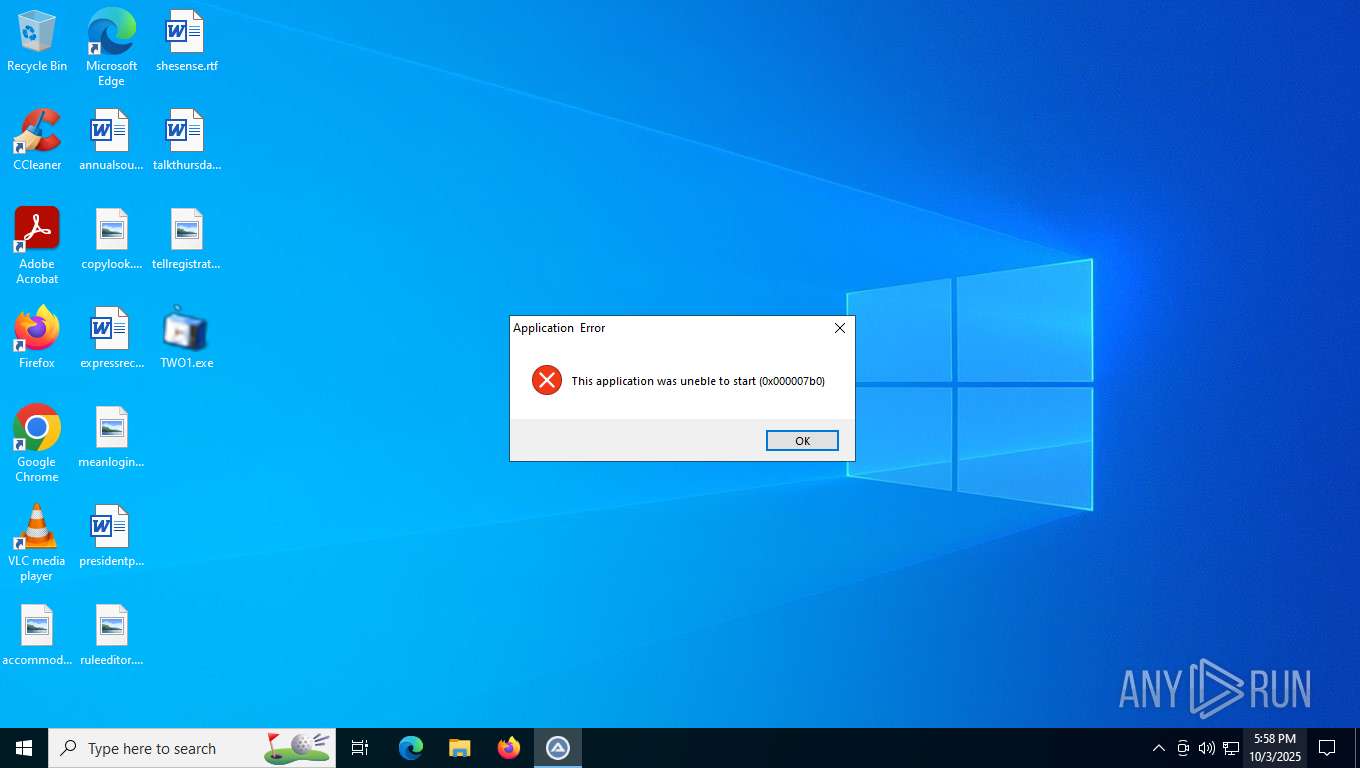
| File name: | TWO1.exe |
| Full analysis: | https://app.any.run/tasks/0f82eed5-fbbf-4858-8b5f-45f10bba6e9a |
| Verdict: | Malicious activity |
| Threats: | Lumma is an information stealer, developed using the C programming language. It is offered for sale as a malware-as-a-service, with several plans available. It usually targets cryptocurrency wallets, login credentials, and other sensitive information on a compromised system. The malicious software regularly gets updates that improve and expand its functionality, making it a serious stealer threat. |
| Analysis date: | October 03, 2025, 17:57:54 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 6 sections |
| MD5: | E85FF3C8B17DB2E64CA3F8B9435524C7 |
| SHA1: | 557662626B8487DB282C18ECDF0796B6AB24F0E9 |
| SHA256: | 1285169ABAE30BA3D353644ED90DED5D7FE5EA119A027E8EEE1AEB8511C13F06 |
| SSDEEP: | 98304:F7Lc7jeWqkliwEH2cHJiwDmJNFfVe94+ViXj7kwwbwnb3V1tbBYdDSWDZz:kx2N |
| .exe | | | Win32 Executable MS Visual C++ (generic) (42.2) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (37.3) |
| .dll | | | Win32 Dynamic Link Library (generic) (8.8) |
| .exe | | | Win32 Executable (generic) (6) |
| .exe | | | Generic Win/DOS Executable (2.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2013:07:21 23:53:50+00:00 |
| ImageFileCharacteristics: | Executable, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 10 |
| CodeSize: | 26624 |
| InitializedDataSize: | 435200 |
| UninitializedDataSize: | 16896 |
| EntryPoint: | 0x352e |
| OSVersion: | 5.1 |
| ImageVersion: | 6 |
| SubsystemVersion: | 5.1 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2504 | cmd | C:\Windows\SysWOW64\cmd.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3420 | C:\Users\admin\AppData\Local\Temp\33824\Colorado.scr | C:\Users\admin\AppData\Local\Temp\33824\Colorado.scr | explorer.exe | ||||||||||||
User: admin Company: AutoIt Team Integrity Level: MEDIUM Description: AutoIt v3 Script (Beta) Exit code: 0 Version: 3, 3, 17, 0 Modules
| |||||||||||||||
| 4928 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6752 | findstr "bdservicehost ekrn AvastUI SophosHealth AVGUI nsWscSvc" | C:\Windows\SysWOW64\findstr.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Find String (QGREP) Utility Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6916 | cmd.exe /c cmd < Enrollment.mpg | C:\Windows\SysWOW64\cmd.exe | — | TWO1.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7208 | tasklist | C:\Windows\SysWOW64\tasklist.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Lists the current running tasks Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7240 | findstr /V "Parking" Galleries | C:\Windows\SysWOW64\findstr.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Find String (QGREP) Utility Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7240 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7784 | "C:\Users\admin\Desktop\TWO1.exe" | C:\Users\admin\Desktop\TWO1.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| (PID) Process: | (3420) Colorado.scr | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
| (PID) Process: | (3420) Colorado.scr | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (3420) Colorado.scr | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 7784 | TWO1.exe | C:\Users\admin\AppData\Local\Temp\Autumn.mpg | binary | |
MD5:3D63C8E5E89AF68F381B1BF9EAD204C4 | SHA256:70AA751A70950D4183BBF5643C238BD4C3164EFD8BF87A017CBE5C980AD605E3 | |||
| 8032 | extrac32.exe | C:\Users\admin\AppData\Local\Temp\Wedding | binary | |
MD5:878E3AD9B9008400C460E748F780704E | SHA256:FF384A83F5AAC313FB1CD470599A820FA2FA1B2C519479FF06F645F8CA7C5486 | |||
| 8032 | extrac32.exe | C:\Users\admin\AppData\Local\Temp\Brake | binary | |
MD5:06163459E95A4DCAD5C032E3BEC4164C | SHA256:C6E8FCFBED67009957DA1741102FD01D8E7779724182F42EDB794EEA5BB773F7 | |||
| 8032 | extrac32.exe | C:\Users\admin\AppData\Local\Temp\Access | binary | |
MD5:F3087C5BA5E4DCFAD5BA18E966D813B2 | SHA256:6F477CB285693000D506AE2DBC4F65FDC4D05F05B19D4DB674B88C02E72C7DA1 | |||
| 7784 | TWO1.exe | C:\Users\admin\AppData\Local\Temp\Morris.mpg | binary | |
MD5:C4921CCBCC47FFF43F82483C9F383DC3 | SHA256:28C85B43CEEC7772AAE200415FAE818FDB82D9F8EBAD84967EC0A71629AAED52 | |||
| 7784 | TWO1.exe | C:\Users\admin\AppData\Local\Temp\Sides.mpg | binary | |
MD5:E38B8E6B1E3B23BAF26A1CF87471DA07 | SHA256:646CF75565A204A7E06904985DD04496AC0A1AF2ADAFC2CBFD238A8CC041BBCF | |||
| 7784 | TWO1.exe | C:\Users\admin\AppData\Local\Temp\Drop.mpg | binary | |
MD5:12FA0AE572EBAA4D7D308843415842BE | SHA256:635BB9C3E7AF806A7C6F2A35B6259CCF85790C8833E16C433A59E6170CDA96AF | |||
| 7784 | TWO1.exe | C:\Users\admin\AppData\Local\Temp\nsq1F22.tmp\nsExec.dll | executable | |
MD5:08E9796CA20C5FC5076E3AC05FB5709A | SHA256:8165C7AEF7DE3D3E0549776535BEDC380AD9BE7BB85E60AD6436F71528D092AF | |||
| 8032 | extrac32.exe | C:\Users\admin\AppData\Local\Temp\Doe | binary | |
MD5:D797B28D19A8E5ACCBB7589D99ECE691 | SHA256:A4BBEA31839EE463FADD7D47700693D50F88AAE1ACB4C5BB6FF4430D9782726C | |||
| 8032 | extrac32.exe | C:\Users\admin\AppData\Local\Temp\Innovative | binary | |
MD5:C7FC0FBAD8504BCA216A5C21C9F296E0 | SHA256:F02DF5BBAB3309F3402B8CC95970AB05686EA9379C17659DC3C0414C7BBA77B4 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | GET | 200 | 149.154.167.99:443 | https://telegram.me/rif0lm | GB | html | 12.0 Kb | unknown |
— | — | GET | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | — | — | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 62 b | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 5.69 Kb | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 5 b | unknown |
— | — | POST | 500 | 4.154.209.85:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | unknown |
— | — | POST | 500 | 4.154.209.85:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 2.13 Kb | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 11.3 Kb | unknown |
— | — | POST | 200 | 49.13.36.184:443 | https://pp.jullianacalhau.com.br/ | DE | text | 108 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
6016 | MoUsoCoreWorker.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
992 | RUXIMICS.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
— | — | 23.192.36.142:443 | www.bing.com | AKAMAI-AS | US | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5948 | svchost.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
2172 | slui.exe | 4.154.185.43:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
7240 | slui.exe | 4.154.185.43:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3420 | Colorado.scr | 149.154.167.99:443 | telegram.me | Telegram Messenger Inc | GB | whitelisted |
3420 | Colorado.scr | 49.13.36.184:443 | pp.jullianacalhau.com.br | Hetzner Online GmbH | DE | unknown |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
SBrSBcCQFZkXMd.SBrSBcCQFZkXMd |
| unknown |
activation-v2.sls.microsoft.com |
| whitelisted |
telegram.me |
| whitelisted |
pp.jullianacalhau.com.br |
| malicious |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
2428 | svchost.exe | A Network Trojan was detected | MALWARE [ANY.RUN] Win32/Lumma DNS Activity observed |
— | — | A Network Trojan was detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M1 |
— | — | A Network Trojan was detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M1 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Active C2 Responding with plugins Config M1 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Active C2 Responding with plugins Config M1 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M2 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M2 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M2 |
— | — | Malware Command and Control Activity Detected | ET MALWARE Win32/Stealc/Vidar Stealer Style Headers In HTTP POST M2 |