700K+
analysts worldwide contribute samples to ANY.RUN’s database
Intelligence comes from millions of sandbox investigations into live malware and phishing threats.
*Based on ANY.RUN’s internal research: nearly 30% of unique malicious IOCs identified in the analyzed sandbox sessions were already known to ANY.RUN and available in TI Feeds.
Get a head start on emerging threats with timely, trusted intelligence from real‑world malware investigations.

ANY.RUN extracts and enriches IOCs from real investigations conducted by a global community, giving your team evidence to trust and act on.

Receive continuously updated IOCs from new malware and phishing investigations to identify emerging threats earlier.

TI Feeds data is relevant to threats SOC teams encounter in daily operation, enabling earlier identification and faster prioritization of malicious activity.
Indicator overlap magnifies the problem with false positives
Outdated intel leaves security gaps, letting new malware slip past defenses
Zero alert context leads to hours wasted on investigations
Too many alerts flood your team with false alarms
Lack of automation slows down triage & response, increasing workload
Unstructured data forces manual work and slows response
99% unique indicators from malware configs not found elsewhere
Real-time updates pull fresh IOCs from the latest malware & phishing attacks
Threat reports linked to indicators fuel quick, informed actions
High-fidelity filtering ensures zero noise, so your team can trust the alerts they get
Plug-and-play connectors and API/SDK provide fast IOC ingestion
STIX/TAXII support ensures seamless ingestion into your tools
Our real-time feeds provide actionable cyber threat data with near-zero false positives. Perfect for SIEM integration and threat hunting.
From basic enrichment to full operational intelligence, choose the plan that fits your team's workflows.
Access the original sandbox analysis behind each IOC to verify malicious activity and understand the full attack context.
Malware behavior: Graph of actions (e.g., file drops, registry changes).
Network activity: Map of C2 connections.
Videos & screenshots: Visual proof of malicious activity.
MITRE ATT&CK TTPs: List of tactics used.
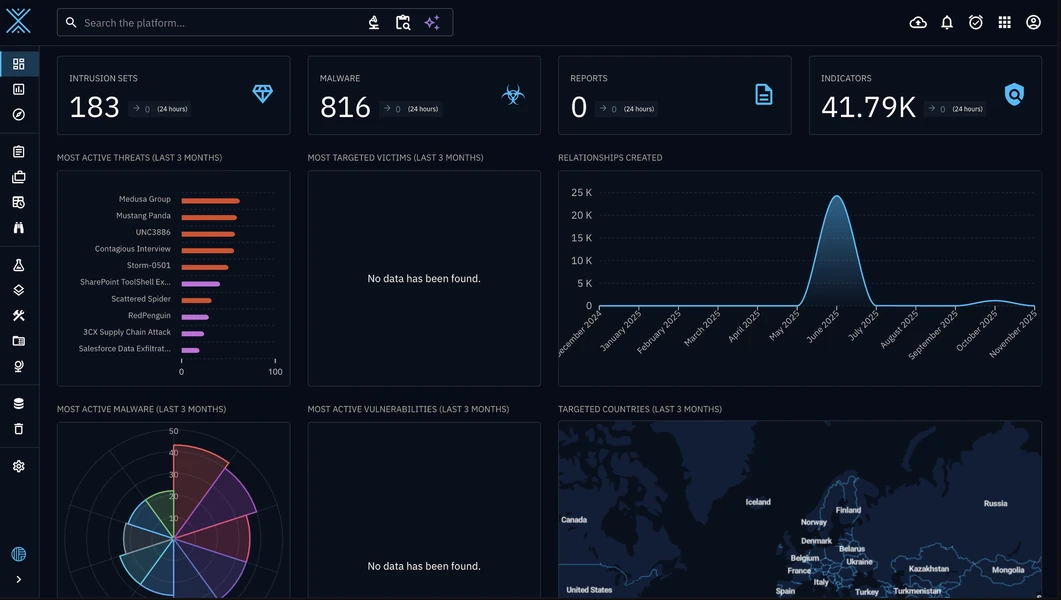
Watch a SOC analyst review a TI Feeds sandbox report in OpenCTI.
Speed up mitigation with clear insights for quick action.
Improve threat visibility with a view of its behavior on a live system.
Enable junior staff to handle incidents on their own.
Discover the role quality threat data plays in maintaining fast MTTD & MTTR, lowering false positives, and reducing dwell time.
Uncover how threat intelligence helps security teams accelerate incident response, beat alert fatigue, and improve overall performance.
See which costly expenses can be minimized or removed completely with timely updates to your detection systems using fresh IOCs.
Equip your security team with full access to the latest threat data that can: