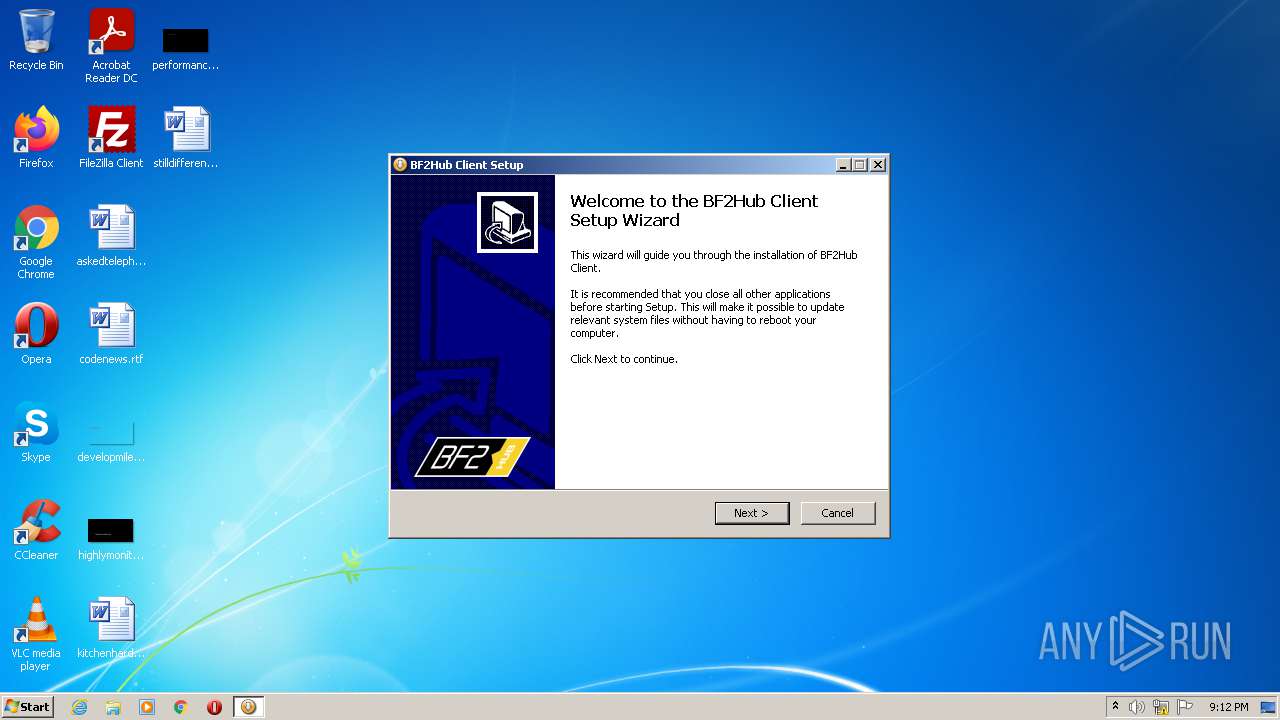
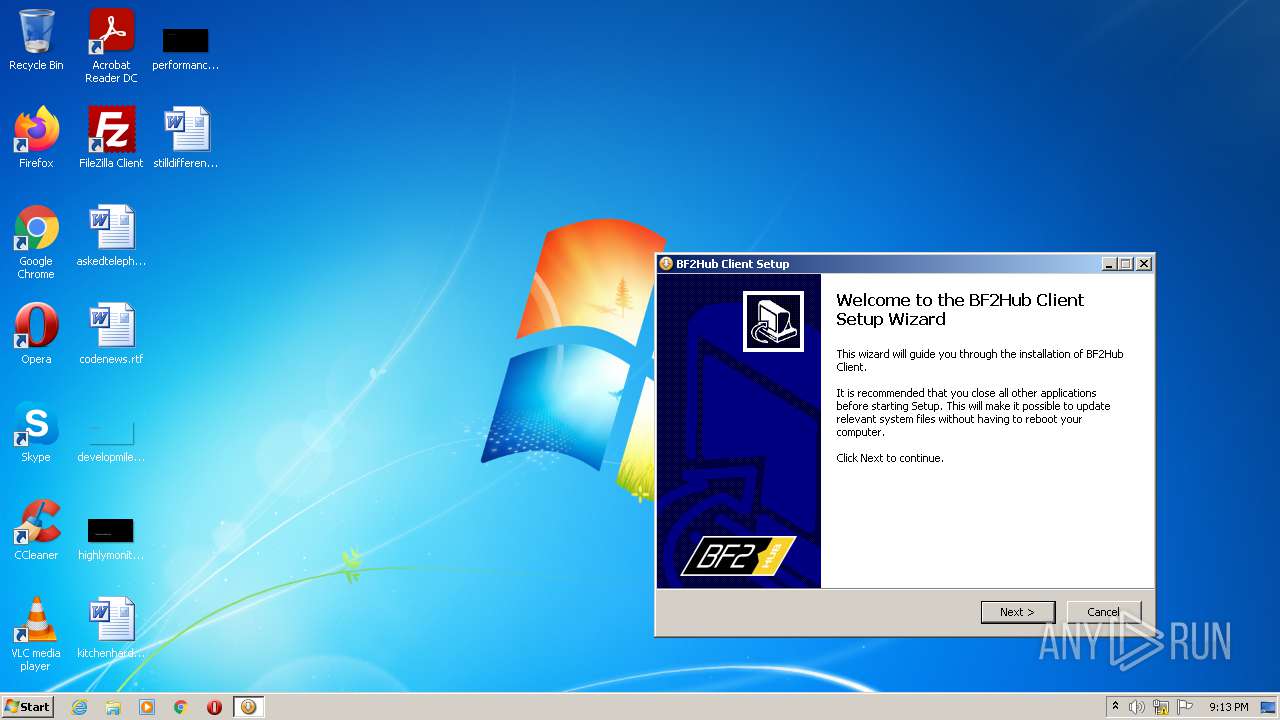
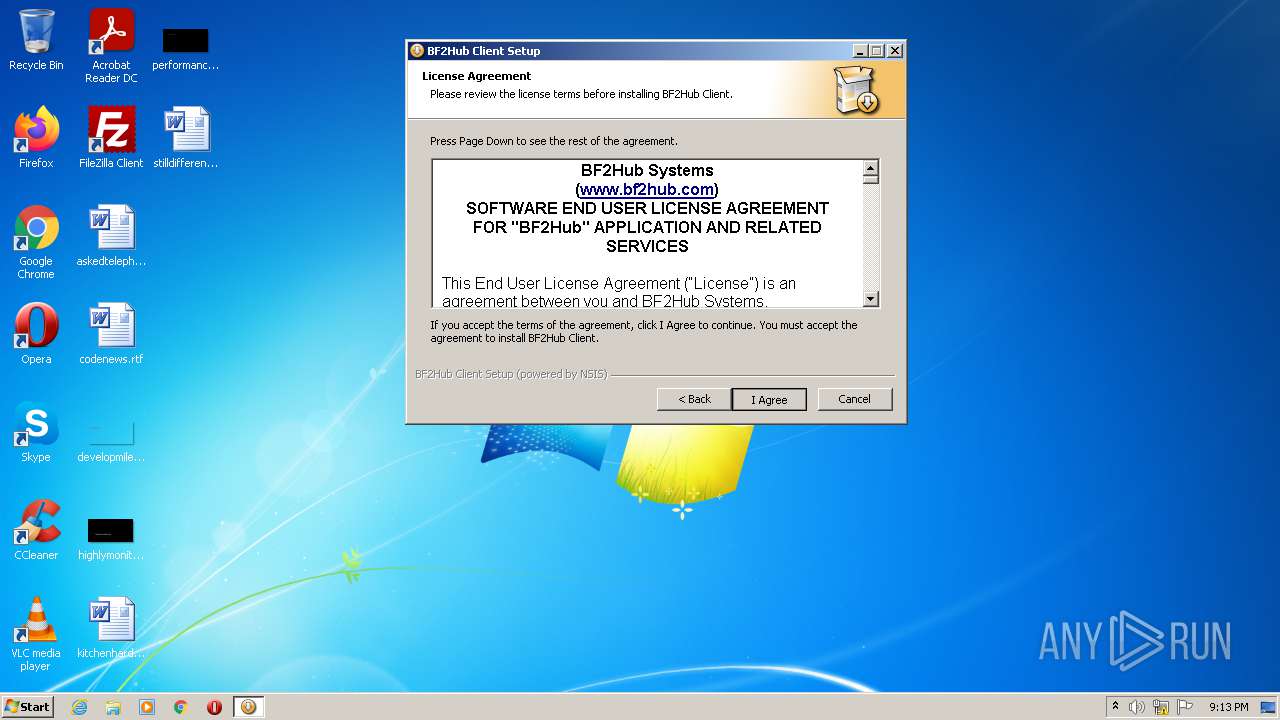
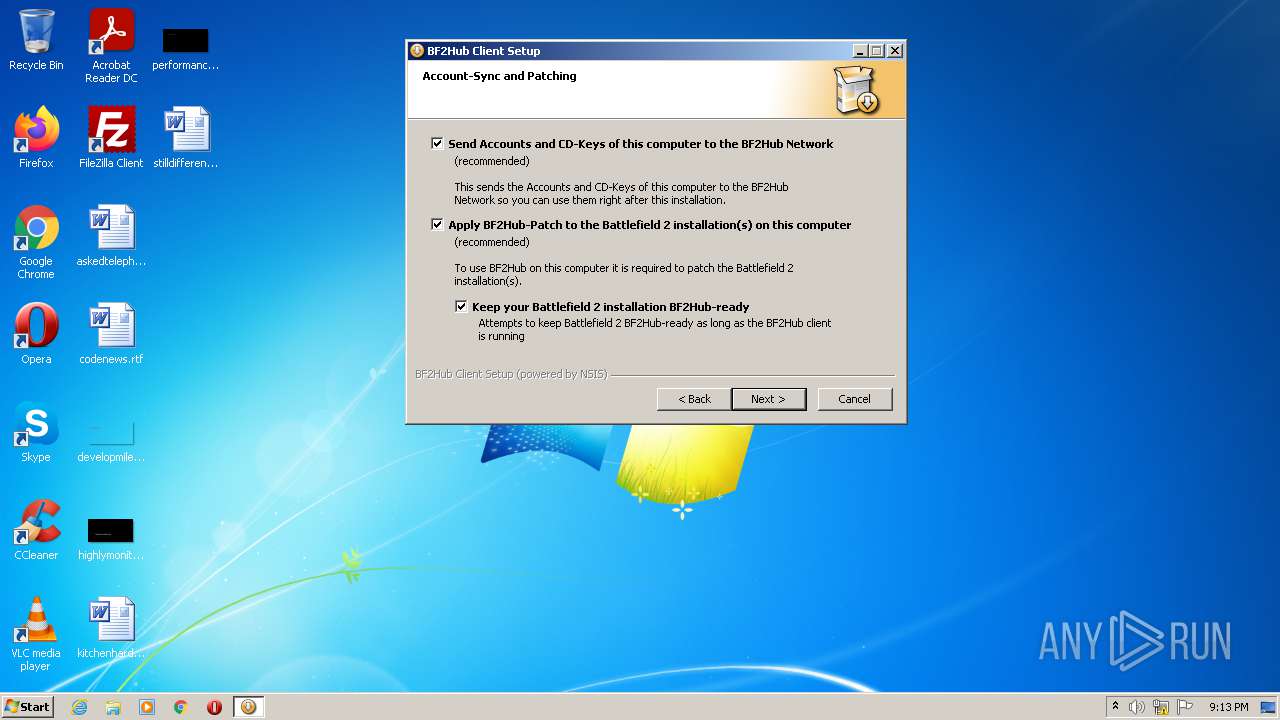
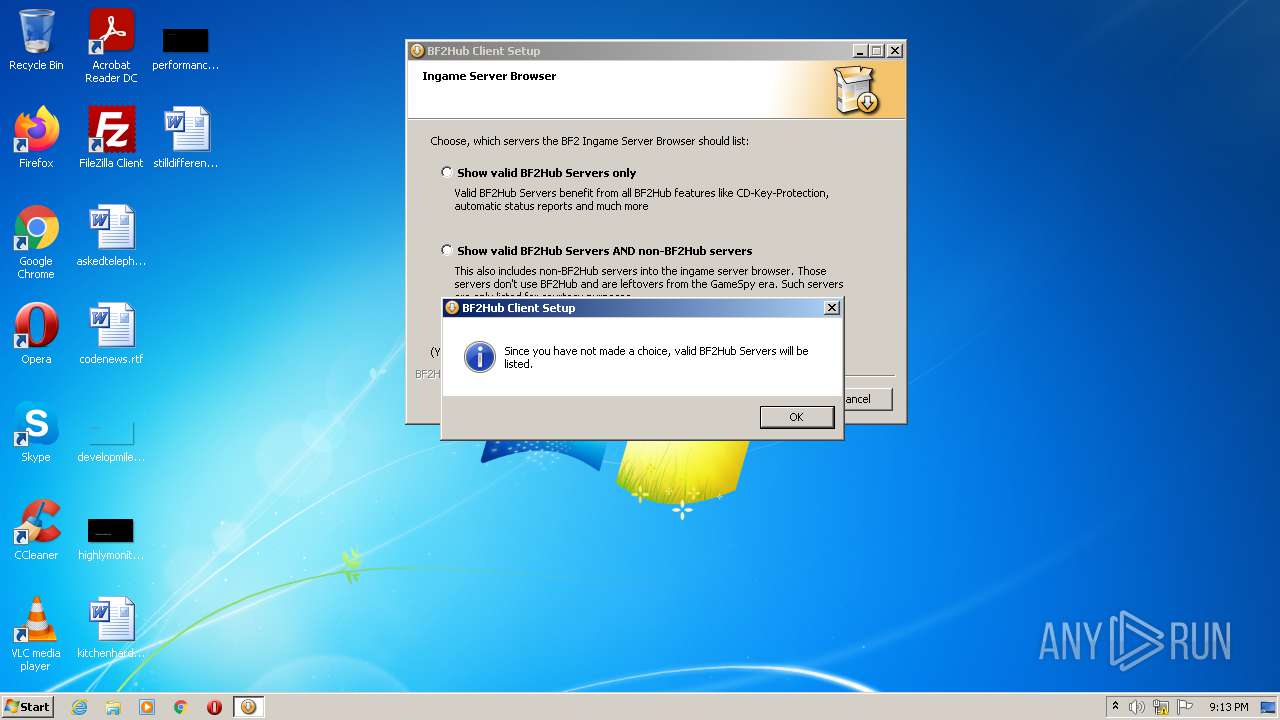
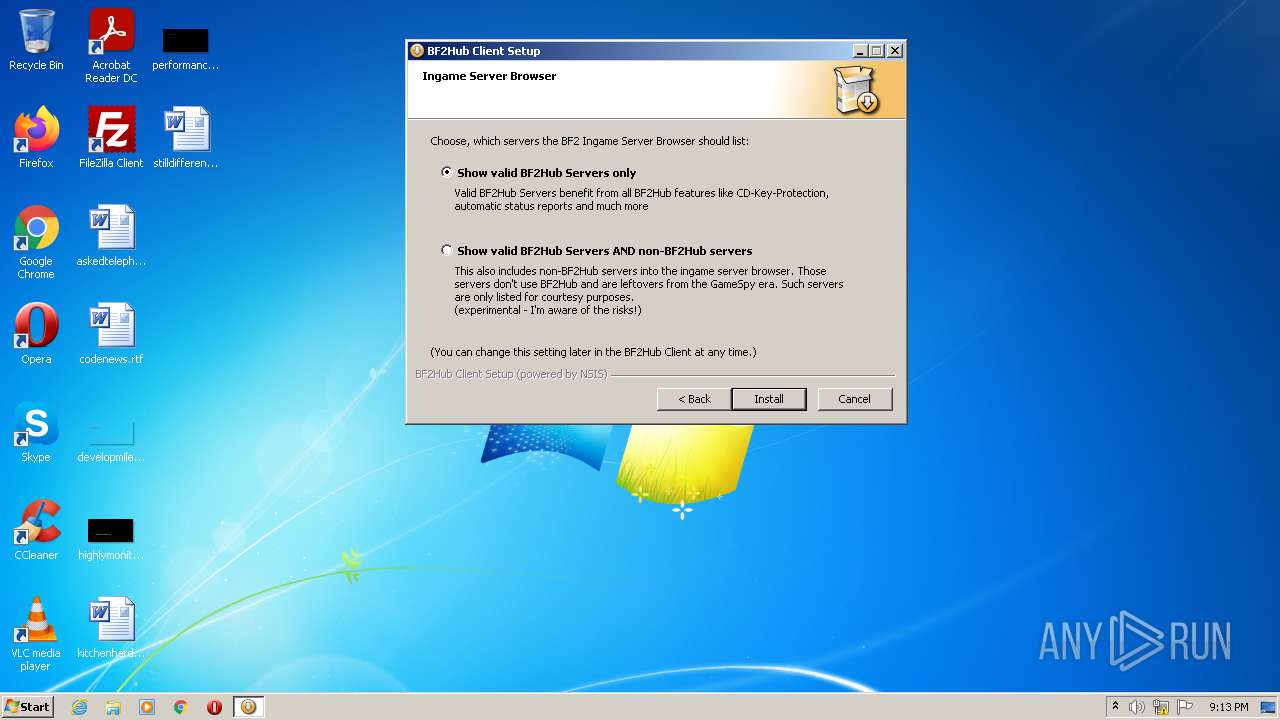
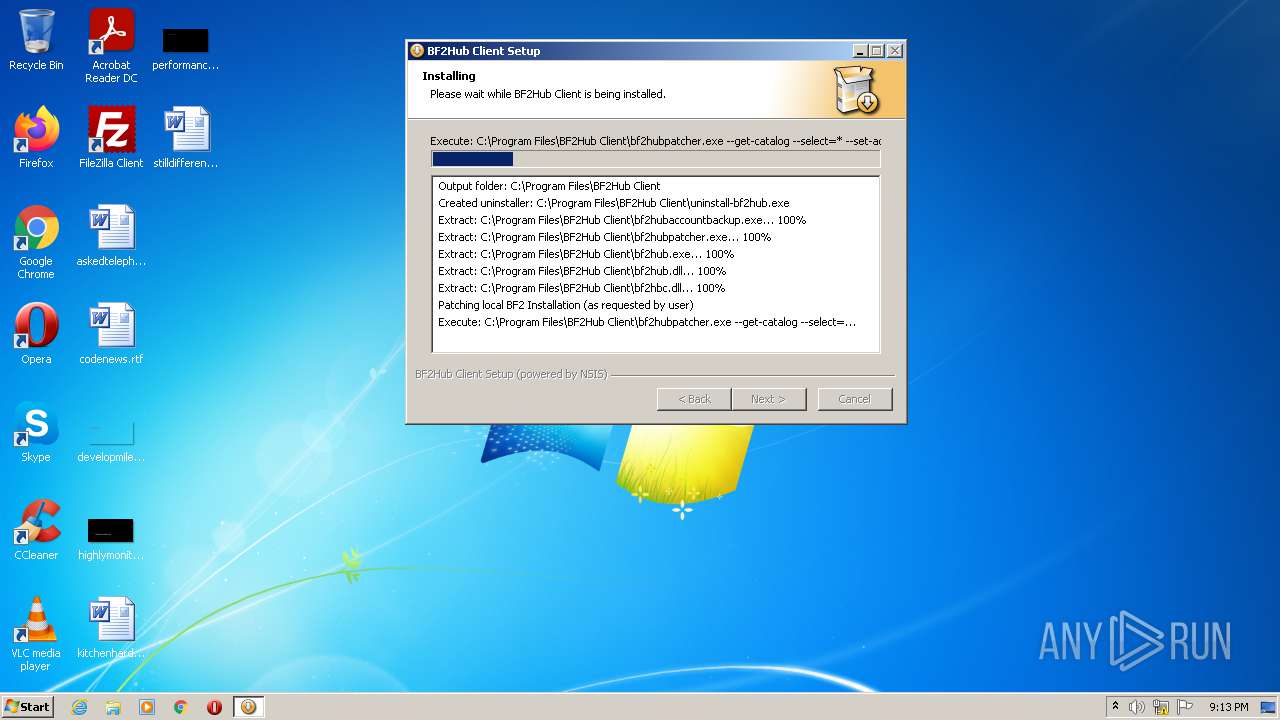
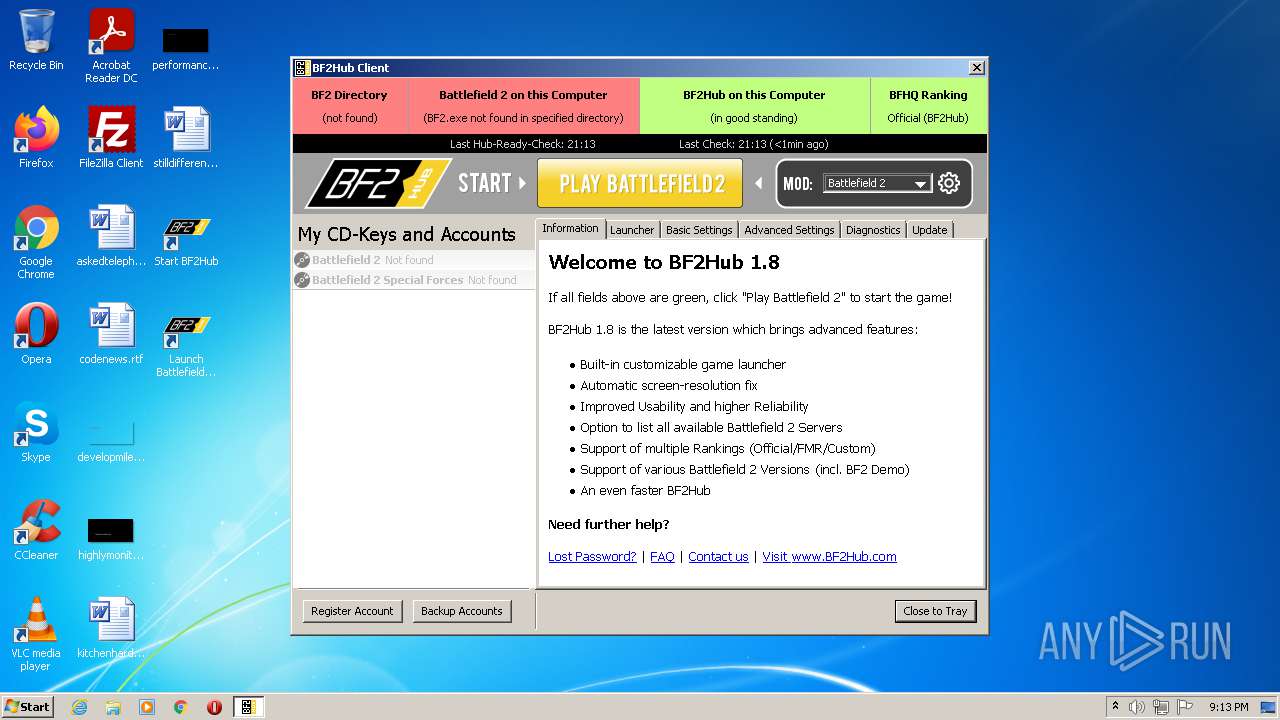
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | bf2hub-client-setup.exe |
| Full analysis: | https://app.any.run/tasks/497f6938-8f98-4b8d-8f61-42e95520ca82 |
| Verdict: | Malicious activity |
| Analysis date: | October 14, 2021, 20:12:46 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archive |
| MD5: | 0025F279B51B9CC083160B60DBD0FE7B |
| SHA1: | 91BB4F5FCC0481F57D72231CCC7D5E8FB676401D |
| SHA256: | F8B924FC4F4E72D9849BA73B37F9B228C189C21F3BD98142E9B094054C00D7C9 |
| SSDEEP: | 49152:PeX65pp628idAIR7yomlzQU/v/jxwE8FZj3UpFWvP3joY3F5:mN28dIR794ztPj2E8bgFWvPz3F5 |
| .exe | | | NSIS - Nullsoft Scriptable Install System (94.8) |
|---|---|---|
| .exe | | | Win32 Executable MS Visual C++ (generic) (3.4) |
| .dll | | | Win32 Dynamic Link Library (generic) (0.7) |
| .exe | | | Win32 Executable (generic) (0.5) |
| .exe | | | Generic Win/DOS Executable (0.2) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2009:06:06 23:41:48+02:00 |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 23040 |
| InitializedDataSize: | 119808 |
| UninitializedDataSize: | 1024 |
| EntryPoint: | 0x30cb |
| OSVersion: | 4 |
| ImageVersion: | 6.1 |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| Architecture: | IMAGE_FILE_MACHINE_I386 |
|---|---|
| Subsystem: | IMAGE_SUBSYSTEM_WINDOWS_GUI |
| Compilation Date: | 06-Jun-2009 21:41:48 |
| Detected languages: |
|
| Magic number: | MZ |
|---|---|
| Bytes on last page of file: | 0x0090 |
| Pages in file: | 0x0003 |
| Relocations: | 0x0000 |
| Size of header: | 0x0004 |
| Min extra paragraphs: | 0x0000 |
| Max extra paragraphs: | 0xFFFF |
| Initial SS value: | 0x0000 |
| Initial SP value: | 0x00B8 |
| Checksum: | 0x0000 |
| Initial IP value: | 0x0000 |
| Initial CS value: | 0x0000 |
| Overlay number: | 0x0000 |
| OEM identifier: | 0x0000 |
| OEM information: | 0x0000 |
| Address of NE header: | 0x000000D8 |
| Signature: | PE |
|---|---|
| Machine: | IMAGE_FILE_MACHINE_I386 |
| Number of sections: | 5 |
| Time date stamp: | 06-Jun-2009 21:41:48 |
| Pointer to Symbol Table: | 0x00000000 |
| Number of symbols: | 0 |
| Size of Optional Header: | 0x00E0 |
| Characteristics: |
|
Name | Virtual Address | Virtual Size | Raw Size | Charateristics | Entropy |
|---|---|---|---|---|---|
.text | 0x00001000 | 0x000058D2 | 0x00005A00 | IMAGE_SCN_CNT_CODE, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ | 6.4331 |
.rdata | 0x00007000 | 0x00001190 | 0x00001200 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 5.17976 |
.data | 0x00009000 | 0x0001AF78 | 0x00000400 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 4.6178 |
.ndata | 0x00024000 | 0x00016000 | 0x00000000 | IMAGE_SCN_CNT_UNINITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 0 |
.rsrc | 0x0003A000 | 0x00006F30 | 0x00007000 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 5.75293 |
Title | Entropy | Size | Codepage | Language | Type |
|---|---|---|---|---|---|
1 | 5.21446 | 958 | UNKNOWN | English - United States | RT_MANIFEST |
2 | 5.61959 | 4264 | UNKNOWN | English - United States | RT_ICON |
3 | 4.84061 | 3752 | UNKNOWN | English - United States | RT_ICON |
4 | 6.16608 | 2216 | UNKNOWN | English - United States | RT_ICON |
5 | 3.91942 | 1640 | UNKNOWN | English - United States | RT_ICON |
6 | 5.42186 | 1384 | UNKNOWN | English - United States | RT_ICON |
7 | 5.58096 | 1128 | UNKNOWN | English - United States | RT_ICON |
8 | 3.74963 | 744 | UNKNOWN | English - United States | RT_ICON |
9 | 3.01957 | 296 | UNKNOWN | English - United States | RT_ICON |
102 | 2.60055 | 168 | UNKNOWN | English - United States | RT_DIALOG |
ADVAPI32.dll |
COMCTL32.dll |
GDI32.dll |
KERNEL32.dll |
SHELL32.dll |
USER32.dll |
VERSION.dll |
ole32.dll |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
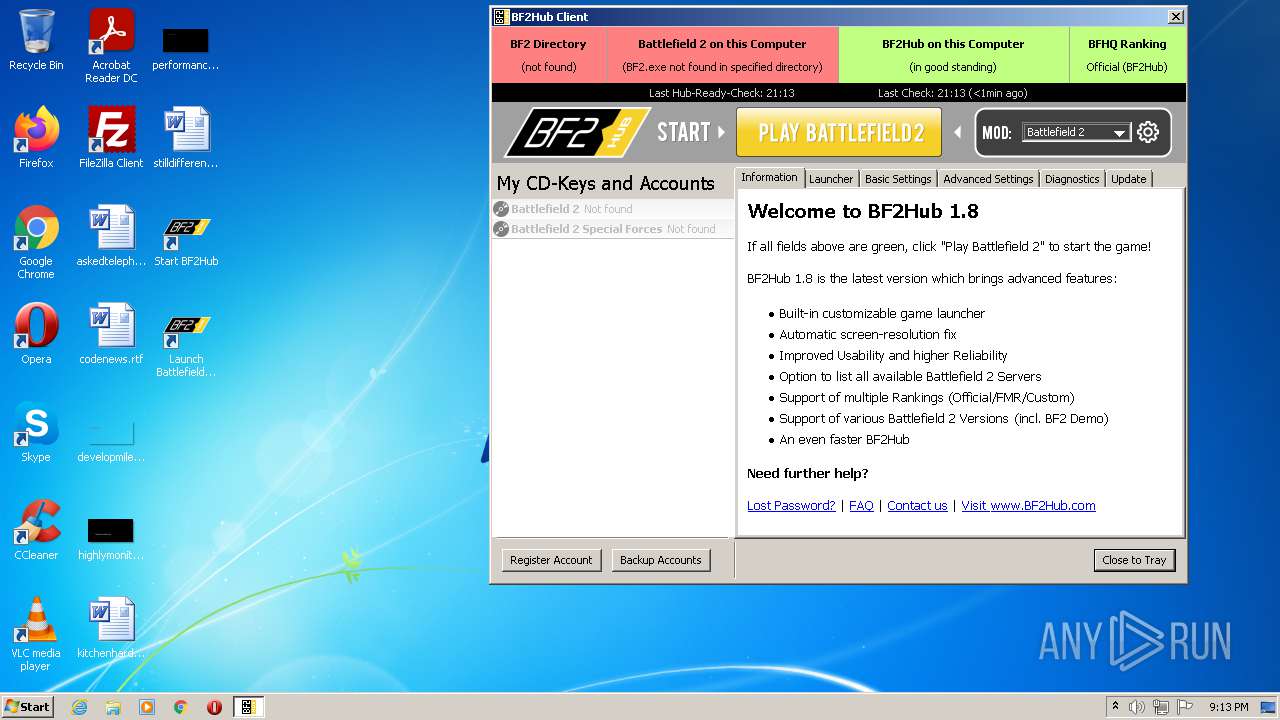
| 2072 | "C:\Program Files\BF2Hub Client\bf2hubpatcher.exe" --get-catalog --select=* --set-acl --patch | C:\Program Files\BF2Hub Client\bf2hubpatcher.exe | bf2hub-client-setup.exe | ||||||||||||
User: admin Company: BF2Hub Systems Integrity Level: HIGH Description: BF2Hub Patcher Exit code: 0 Version: 1.8.0.43 Modules
| |||||||||||||||
| 2172 | "C:\Program Files\BF2Hub Client\bf2hubaccountbackup.exe" --send | C:\Program Files\BF2Hub Client\bf2hubaccountbackup.exe | — | bf2hub-client-setup.exe | |||||||||||
User: admin Company: BF2Hub Systems Integrity Level: HIGH Description: BF2Hub Account Backup Exit code: 1 Version: 1.8.0.55 Modules
| |||||||||||||||
| 2740 | "C:\Users\admin\AppData\Local\Temp\bf2hub-client-setup.exe" | C:\Users\admin\AppData\Local\Temp\bf2hub-client-setup.exe | Explorer.EXE | ||||||||||||
User: admin Integrity Level: HIGH Exit code: 0 Modules
| |||||||||||||||
| 3444 | "C:\Users\admin\AppData\Local\Temp\bf2hub-client-setup.exe" | C:\Users\admin\AppData\Local\Temp\bf2hub-client-setup.exe | — | Explorer.EXE | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 3221226540 Modules
| |||||||||||||||
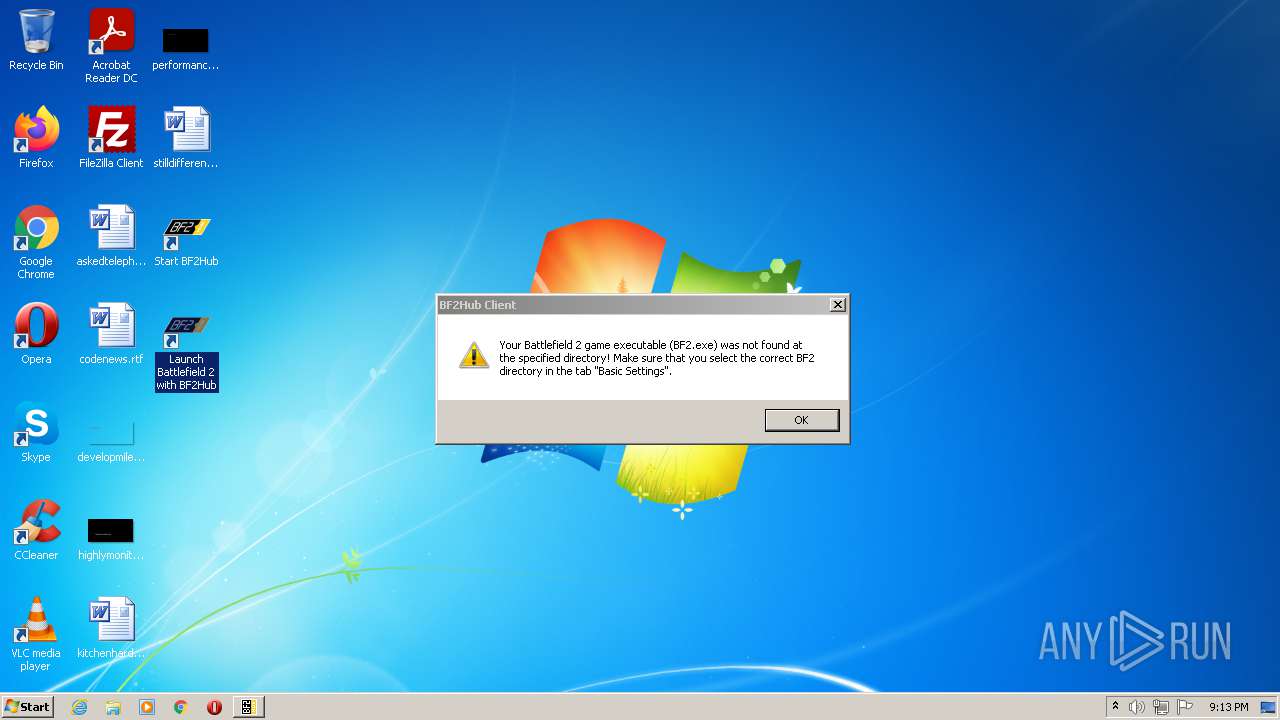
| 3472 | "C:\Program Files\BF2Hub Client\bf2hub.exe" --launch=bf2 | C:\Program Files\BF2Hub Client\bf2hub.exe | — | Explorer.EXE | |||||||||||
User: admin Company: BF2Hub Systems Integrity Level: MEDIUM Description: BF2Hub Client Exit code: 0 Version: 1.8.0.55 Modules
| |||||||||||||||
| 3688 | "C:\Program Files\BF2Hub Client\bf2hub.exe" 328014 | C:\Program Files\BF2Hub Client\bf2hub.exe | Explorer.EXE | ||||||||||||
User: admin Company: BF2Hub Systems Integrity Level: MEDIUM Description: BF2Hub Client Exit code: 0 Version: 1.8.0.55 Modules
| |||||||||||||||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | hrpApplyOnStartup |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_CURRENT_USER\Software\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | hrpApplyOnStartup |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | hrpInterval |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_CURRENT_USER\Software\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | hrpInterval |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | serverBrowserMode |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_CURRENT_USER\Software\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | serverBrowserMode |
Value: 1 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\BF2Hub Systems\BF2Hub Client |
| Operation: | write | Name: | client_opmode |
Value: 2 | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run |
| Operation: | write | Name: | BF2Hub Client |
Value: C:\Program Files\BF2Hub Client\bf2hub.exe | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\bf2hub |
| Operation: | write | Name: | DisplayName |
Value: BF2Hub Client | |||
| (PID) Process: | (2740) bf2hub-client-setup.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\bf2hub |
| Operation: | write | Name: | UninstallString |
Value: C:\Program Files\BF2Hub Client\uninstall-bf2hub.exe | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2740 | bf2hub-client-setup.exe | C:\ProgramData\Microsoft\Windows\Start Menu\Programs\BF2Hub Client\BF2Hub Client.lnk | lnk | |
MD5:9D947191BD28EBBDA1A6B473242E8363 | SHA256:7D9CBF7A102CD9BBFBC8CAB1E522C4A97FC09593BA4FA38473FCADE15CC97082 | |||
| 2740 | bf2hub-client-setup.exe | C:\Users\admin\AppData\Local\Temp\nsi4DC7.tmp\nsProcess.dll | executable | |
MD5:05450FACE243B3A7472407B999B03A72 | SHA256:95FE9D92512FF2318CC2520311EF9145B2CEE01209AB0E1B6E45C7CE1D4D0E89 | |||
| 2740 | bf2hub-client-setup.exe | C:\Program Files\BF2Hub Client\uninstall-bf2hub.exe | executable | |
MD5:51CBA2F32E2C1813BD1BD707B25DB284 | SHA256:47F46D87B568E0D2116DBCF84E106F3038F8F9765E1B825625763BA983F9978F | |||
| 2740 | bf2hub-client-setup.exe | C:\Users\admin\AppData\Local\Temp\nsi4DC7.tmp\modern-header.bmp | image | |
MD5:852B07C25E75B8A5356931C91C834EFC | SHA256:BD146E39AF28CEC251D63DA453CB8F04B74904A643F4C3DAB52EF2B5BCB4BB3A | |||
| 2740 | bf2hub-client-setup.exe | C:\Program Files\BF2Hub Client\bf2hub.exe | executable | |
MD5:EB8FAA78641C2064E3DDDEE4A5A5CAEA | SHA256:E8841A4B215A4295ACA508C8856EAB0F9B68EB950252C9CB55C96220B1483D0C | |||
| 2740 | bf2hub-client-setup.exe | C:\Program Files\BF2Hub Client\bf2hub.dll | executable | |
MD5:A6D781EB0E2D0EE05254A295496B8CC3 | SHA256:FCA71944FA86359532711F052CA88901430B48D466FD902A74F5BEF81F1D5CC0 | |||
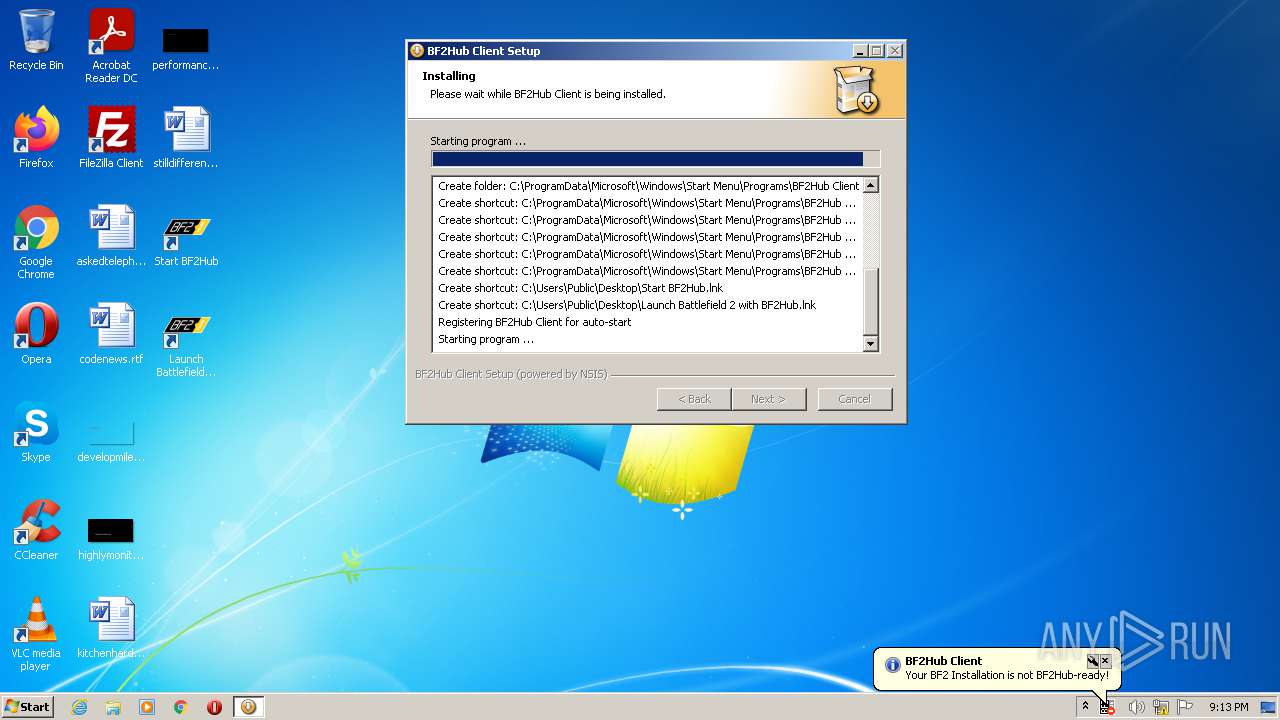
| 2740 | bf2hub-client-setup.exe | C:\Users\Public\Desktop\Launch Battlefield 2 with BF2Hub.lnk | lnk | |
MD5:A42B378C313DEE795BC49A4DD1716B9D | SHA256:CF53F74B487A2E5D8F50A509315EAE1656649C0D4581058E416FC87E495684C0 | |||
| 2740 | bf2hub-client-setup.exe | C:\ProgramData\Microsoft\Windows\Start Menu\Programs\BF2Hub Client\Uninstall BF2Hub Client.lnk | lnk | |
MD5:463CF319B641D72E265961D7AB192809 | SHA256:DBF7A3BF625173C31A444F42D9482E85B765442C608F620AE0221308FC363FB2 | |||
| 2740 | bf2hub-client-setup.exe | C:\Users\Public\Desktop\Start BF2Hub.lnk | lnk | |
MD5:7C14496F144024B0977BB1C566CD3CA6 | SHA256:CE166499AA9D5FDEE9668C951DF88E362660D3BE98E95B068D1D7F50E3AD2823 | |||
| 2740 | bf2hub-client-setup.exe | C:\Users\admin\AppData\Local\Temp\nsi4DC7.tmp\modern-wizard.bmp | image | |
MD5:41115D9A620A39B034FEFFFC3CB09E4B | SHA256:372B4C739C62B27FFD868A2470631F09314F0D8C9BABF49D24BE8DA0E2B36B60 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3688 | bf2hub.exe | POST | 200 | 92.204.50.8:80 | http://update.bf2hub.com/api/update-check-r4.php | DE | html | 1.07 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 51.124.78.146:443 | — | Microsoft Corporation | GB | whitelisted |
3688 | bf2hub.exe | 92.204.50.8:80 | accountcheck.bf2hub.com | QSC AG | DE | unknown |
Domain | IP | Reputation |
|---|---|---|
patches.bf2hub.com |
| unknown |
accountcheck.bf2hub.com |
| unknown |
update.bf2hub.com |
| unknown |
Process | Message |
|---|---|
bf2hub-client-setup.exe | ExecShellAsUser: DLL_PROCESS_ATTACH |
bf2hub-client-setup.exe | ExecShellAsUser: got desktop |
bf2hub-client-setup.exe | ExecShellAsUser: elevated process detected |
bf2hub-client-setup.exe | ExecShellAsUser: NSPIM_UNLOAD wait... |
bf2hub-client-setup.exe | ExecShellAsUser: thread finished |
bf2hub-client-setup.exe | ExecShellAsUser: NSPIM_UNLOAD |
bf2hub-client-setup.exe | ExecShellAsUser: DLL_PROCESS_DETACH |