ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
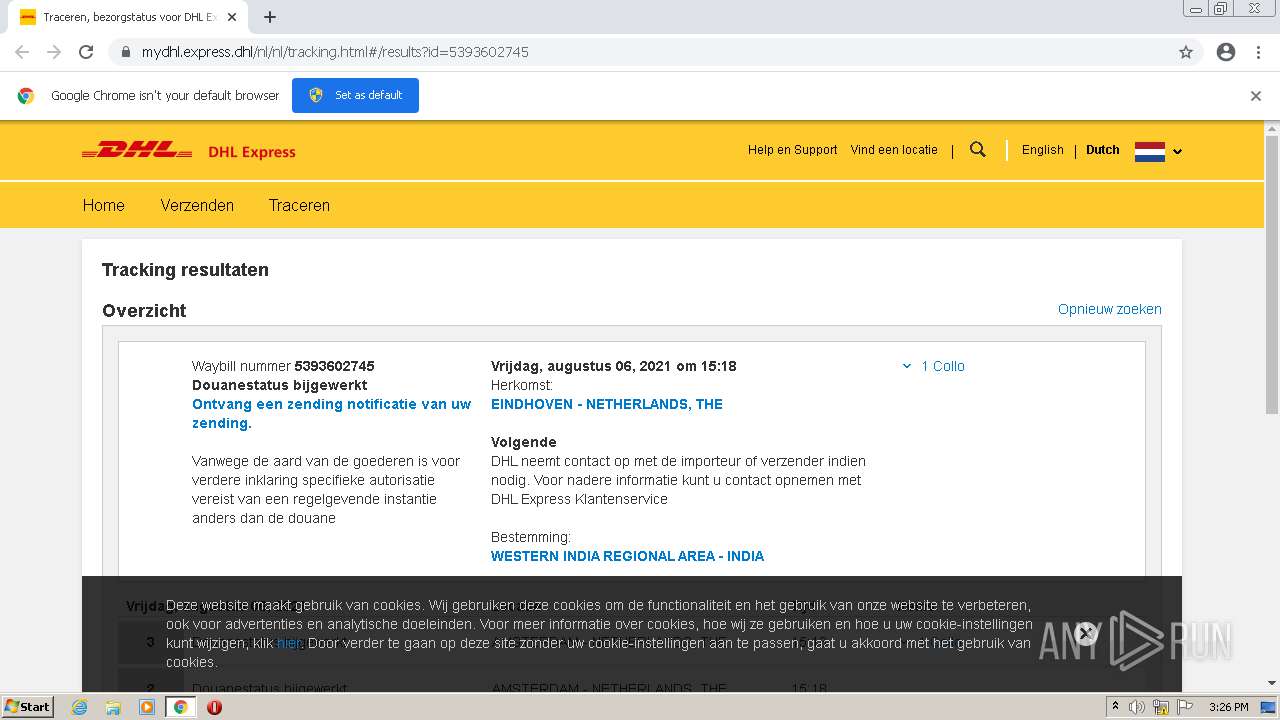
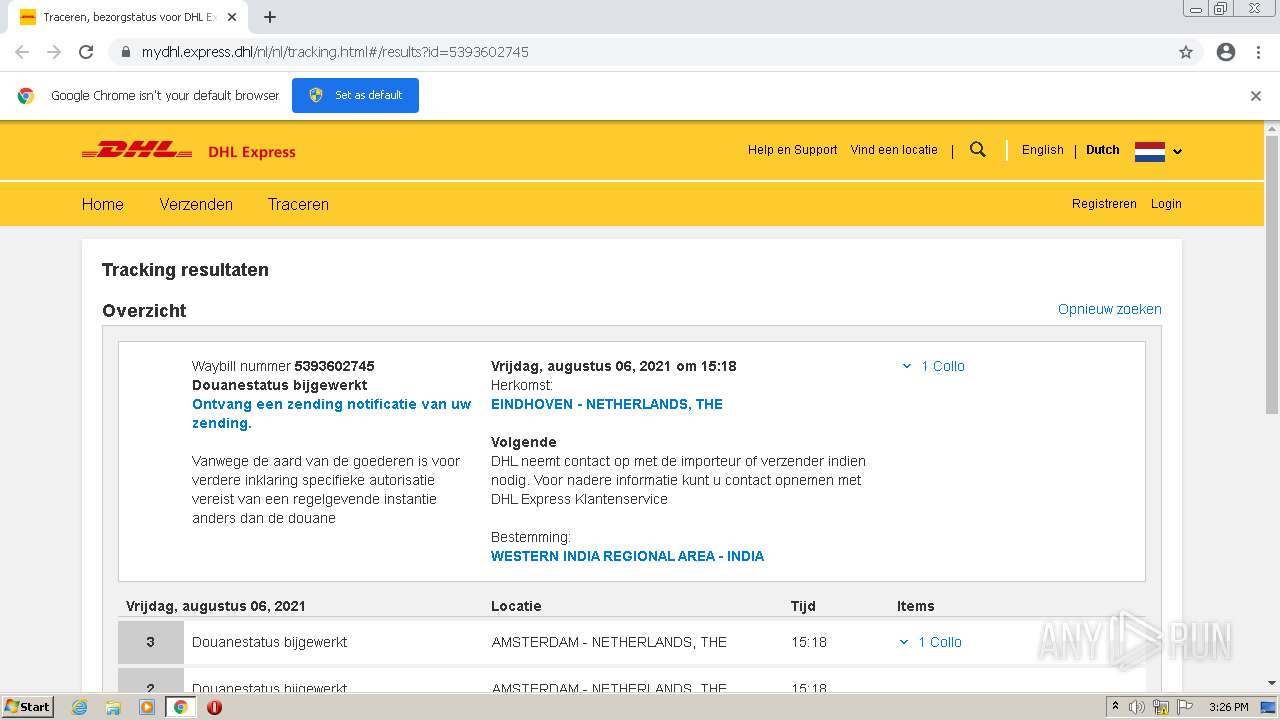
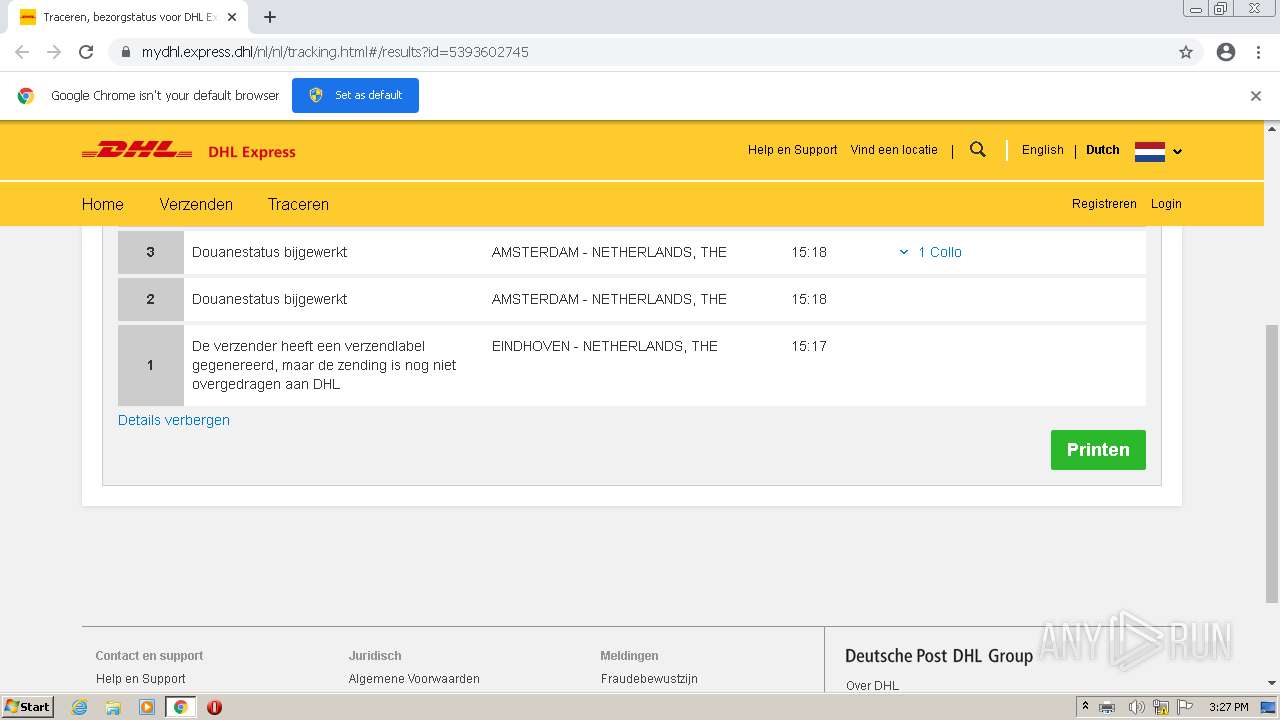
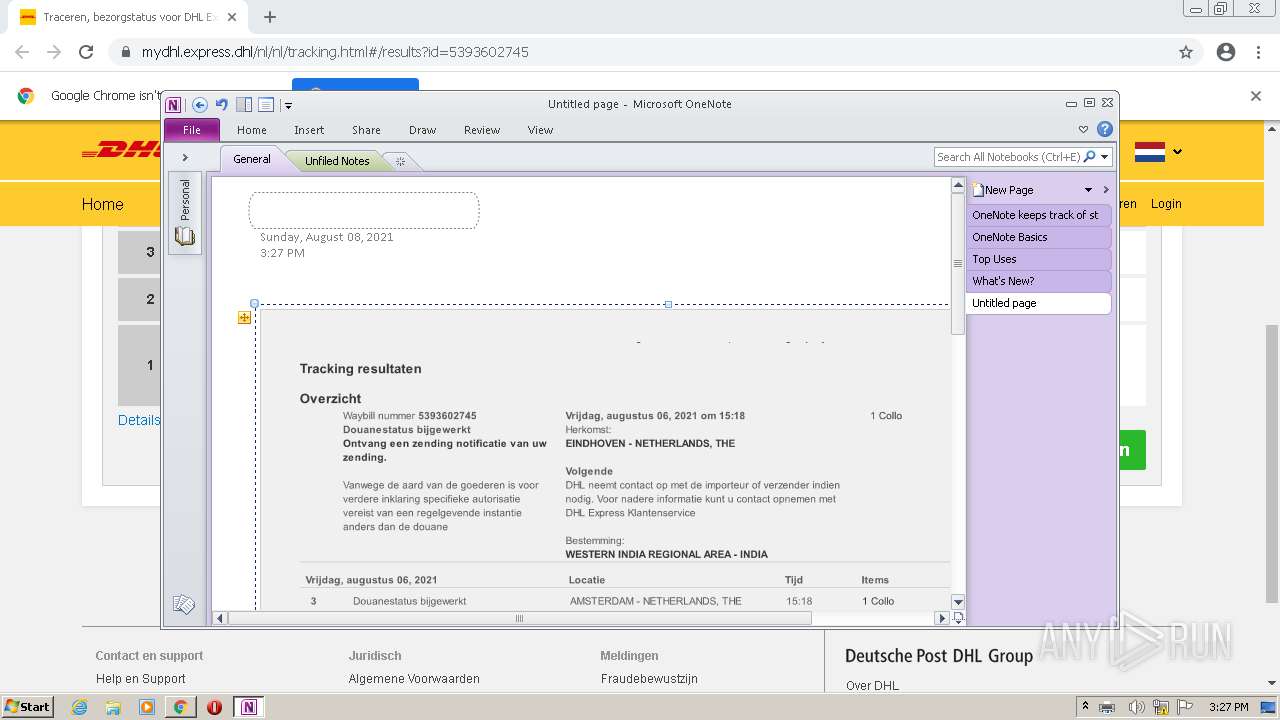
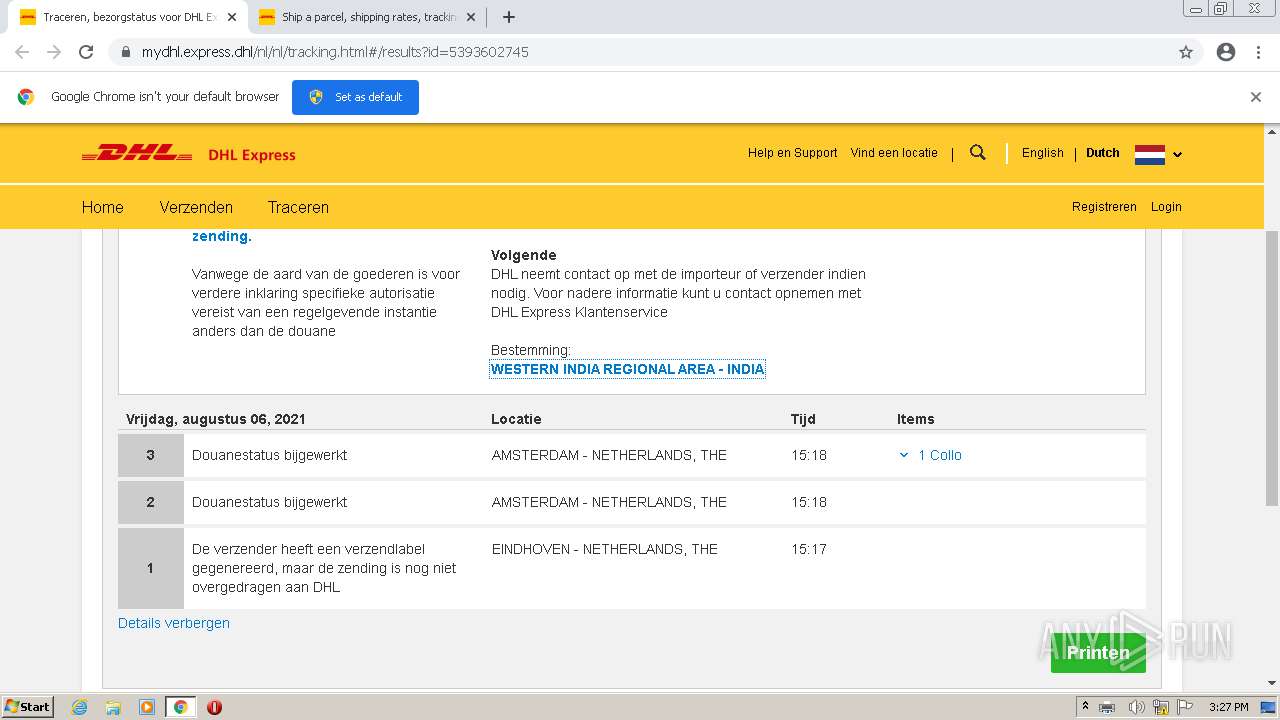
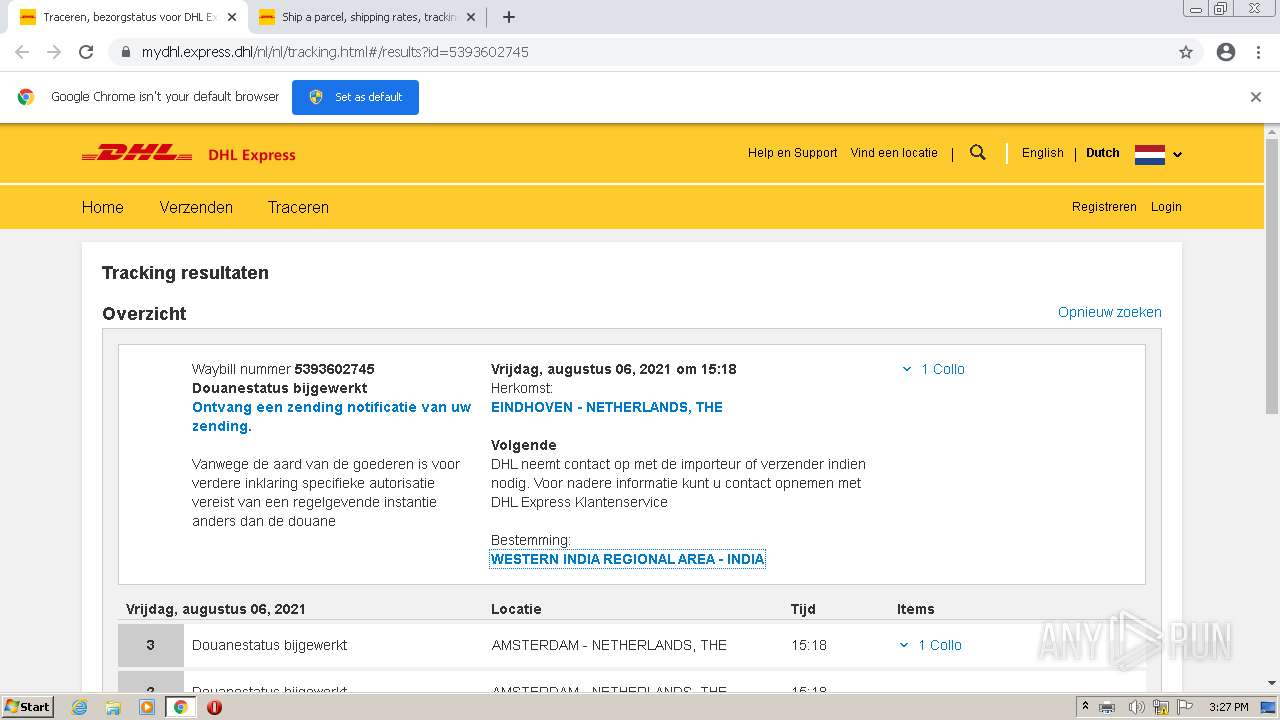
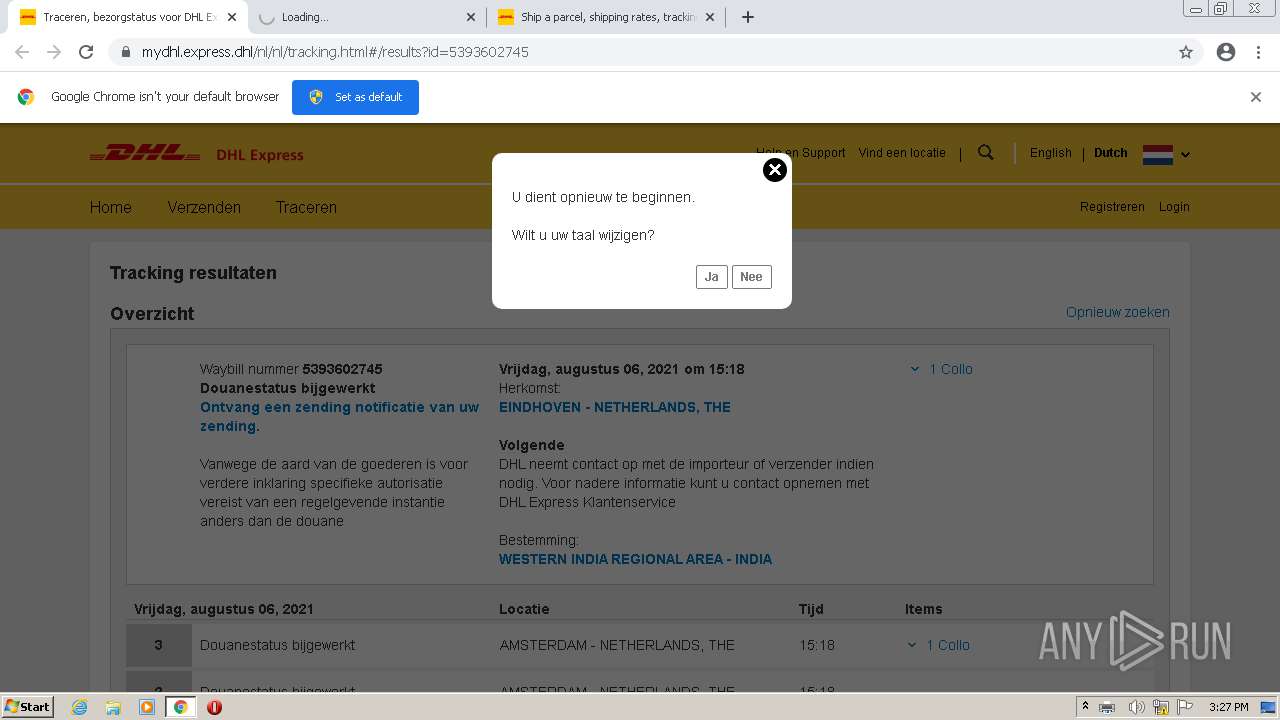
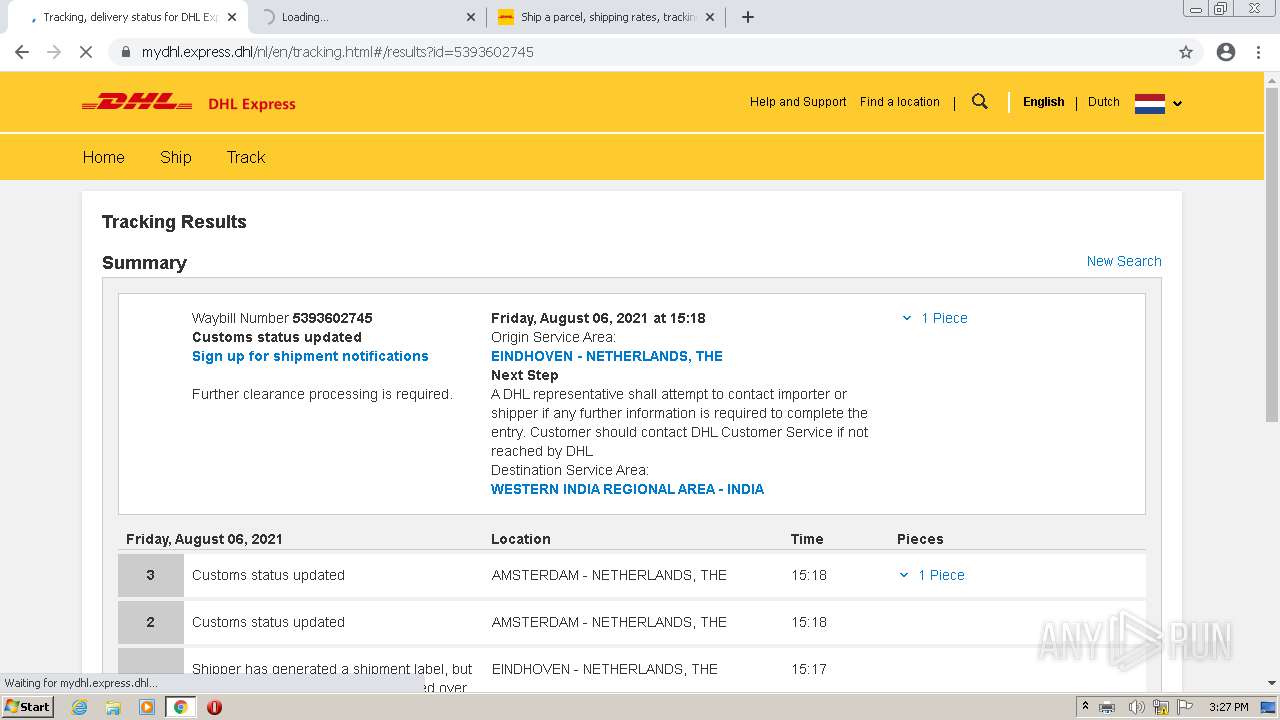
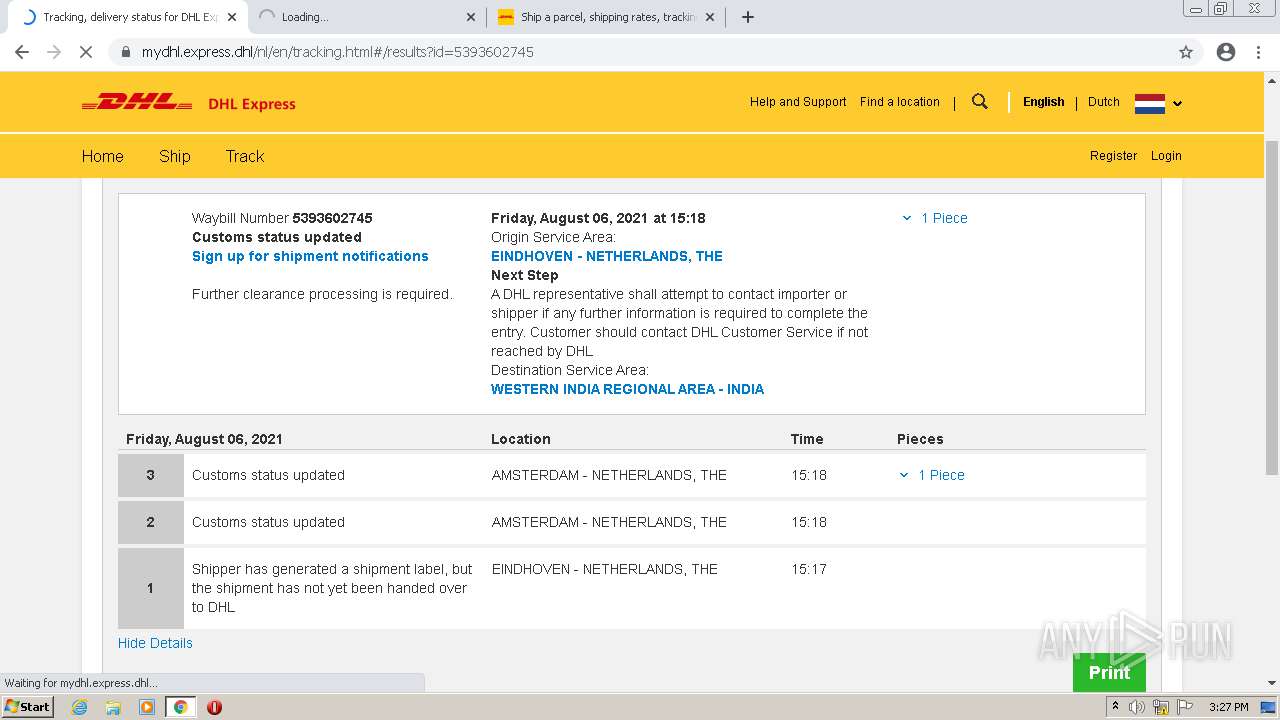
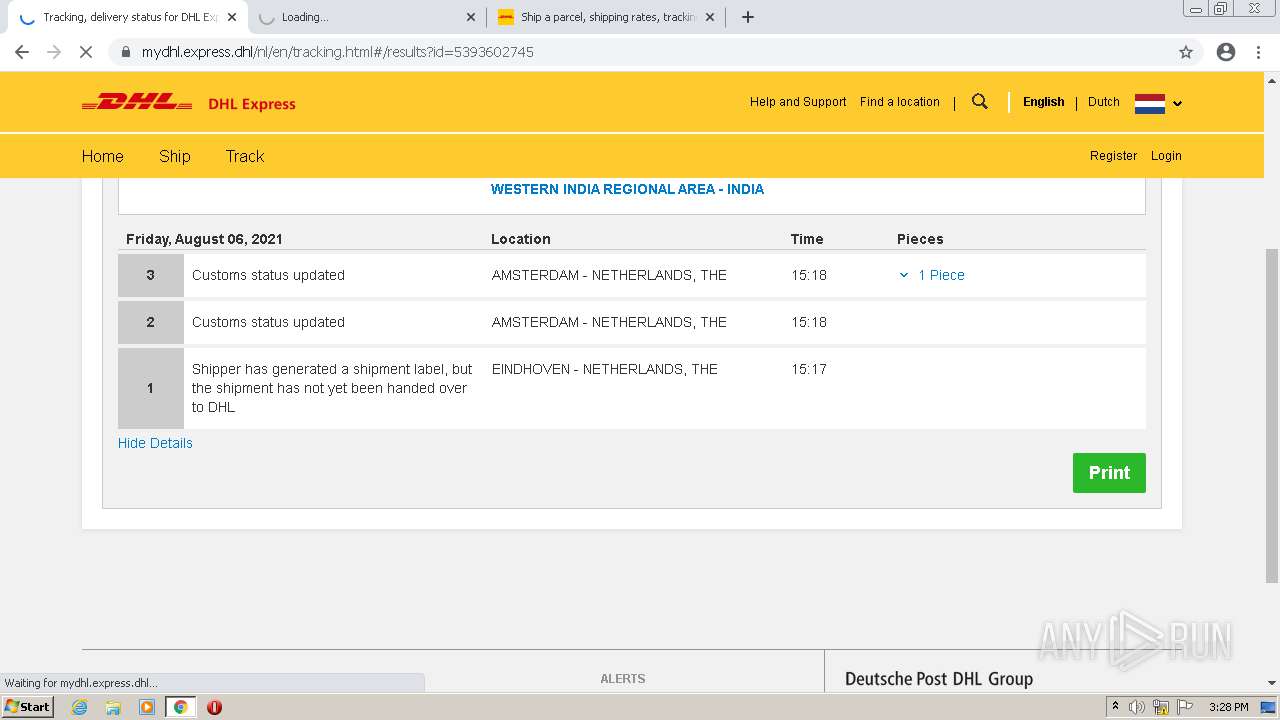
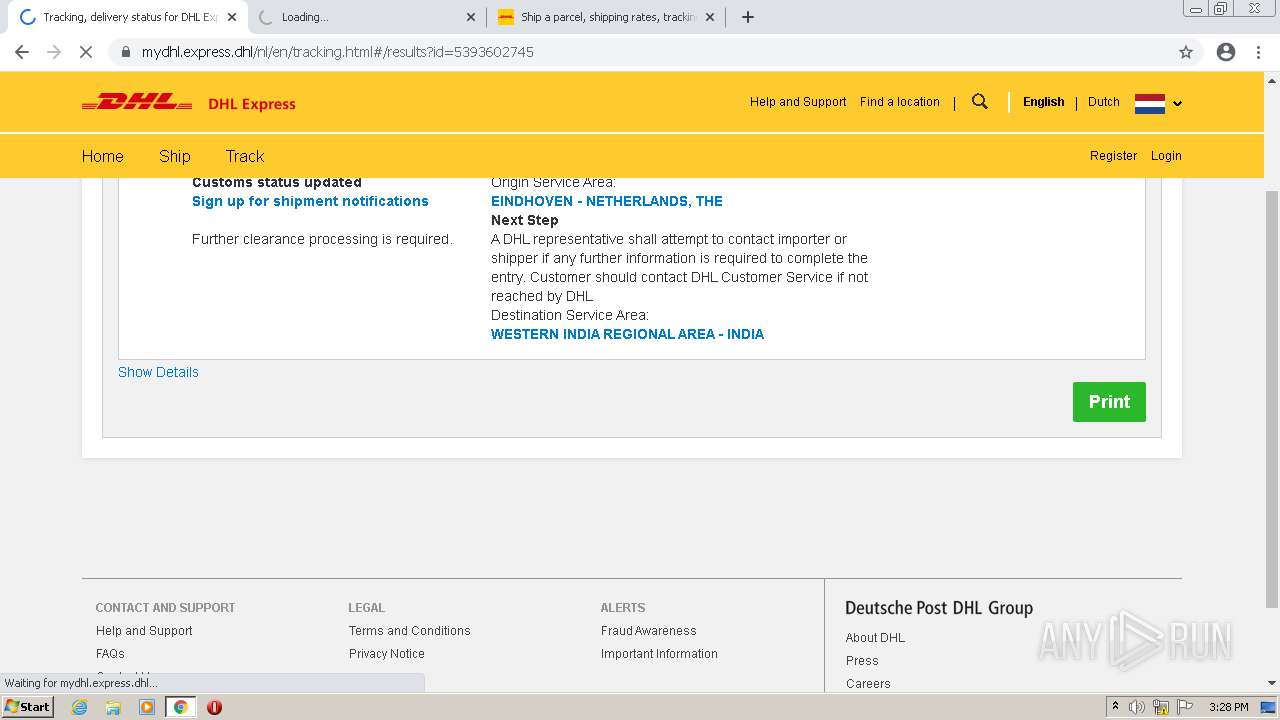
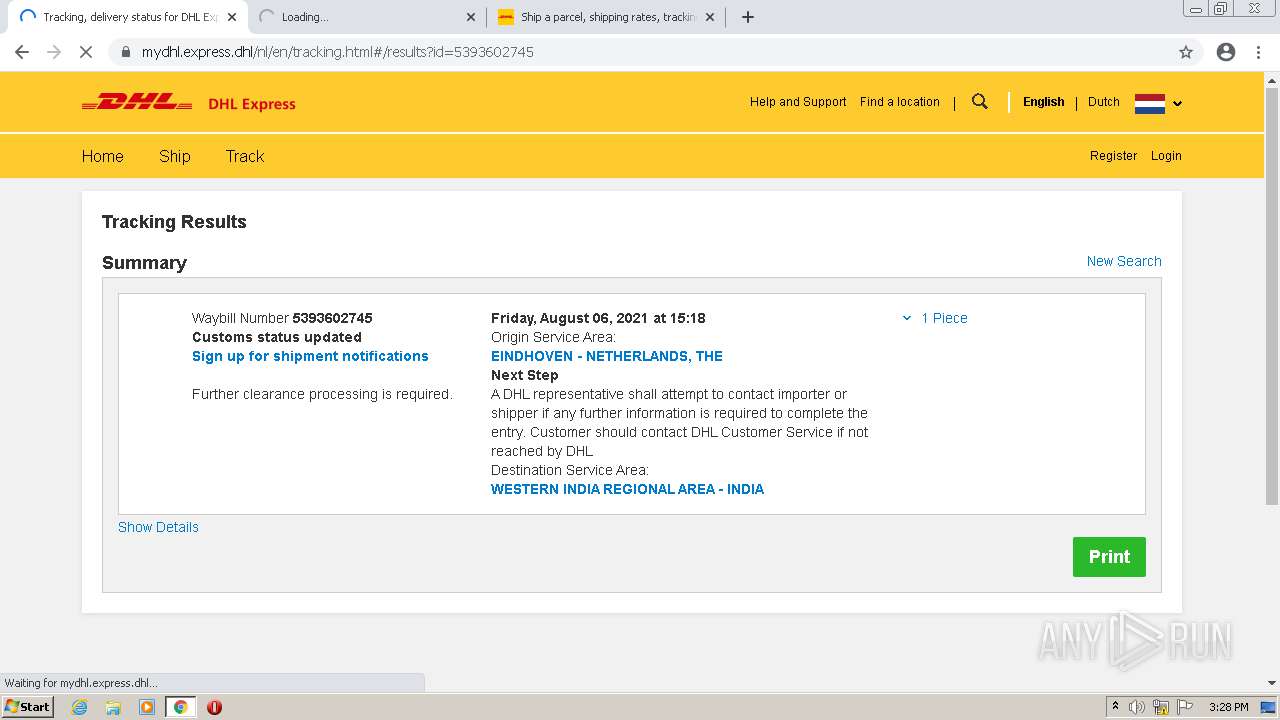
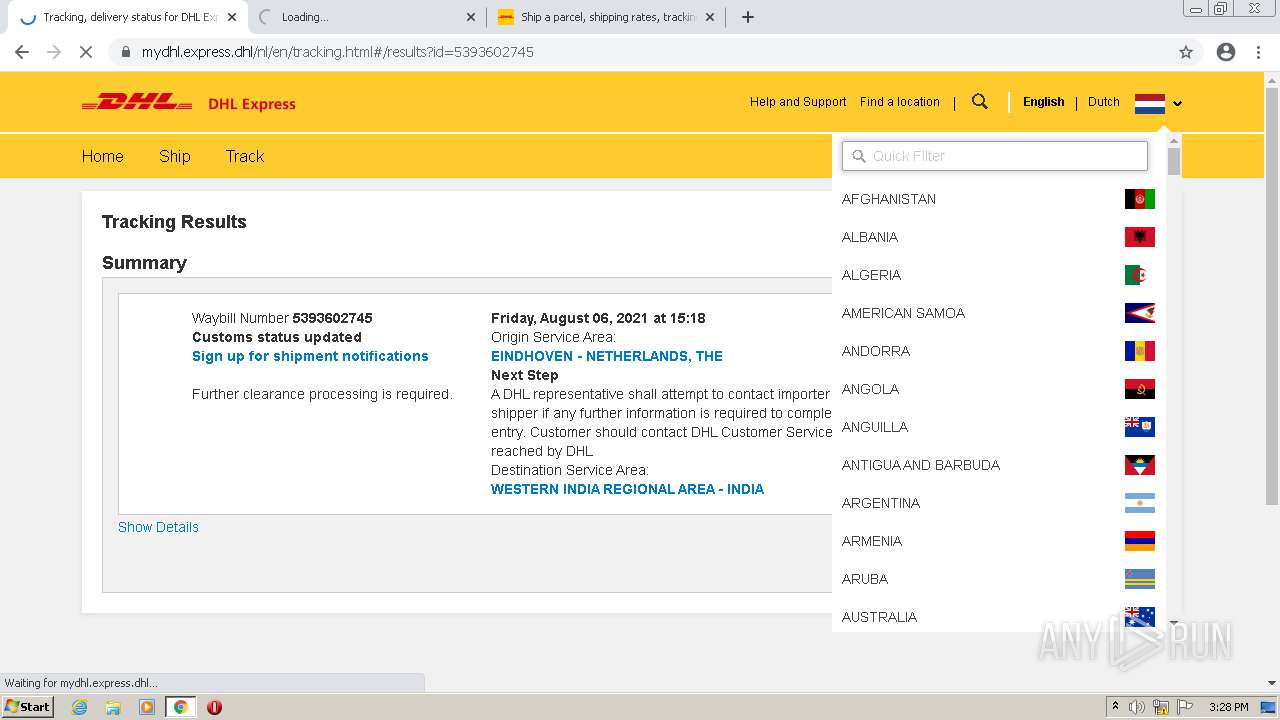
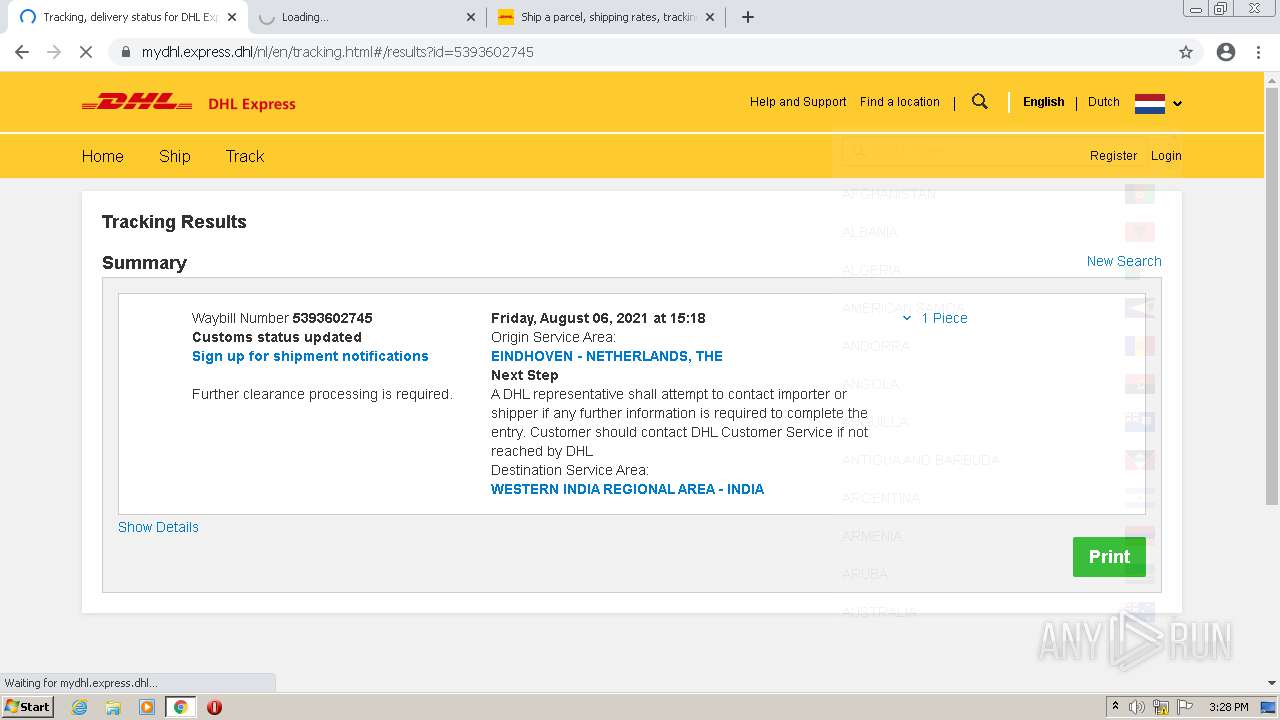
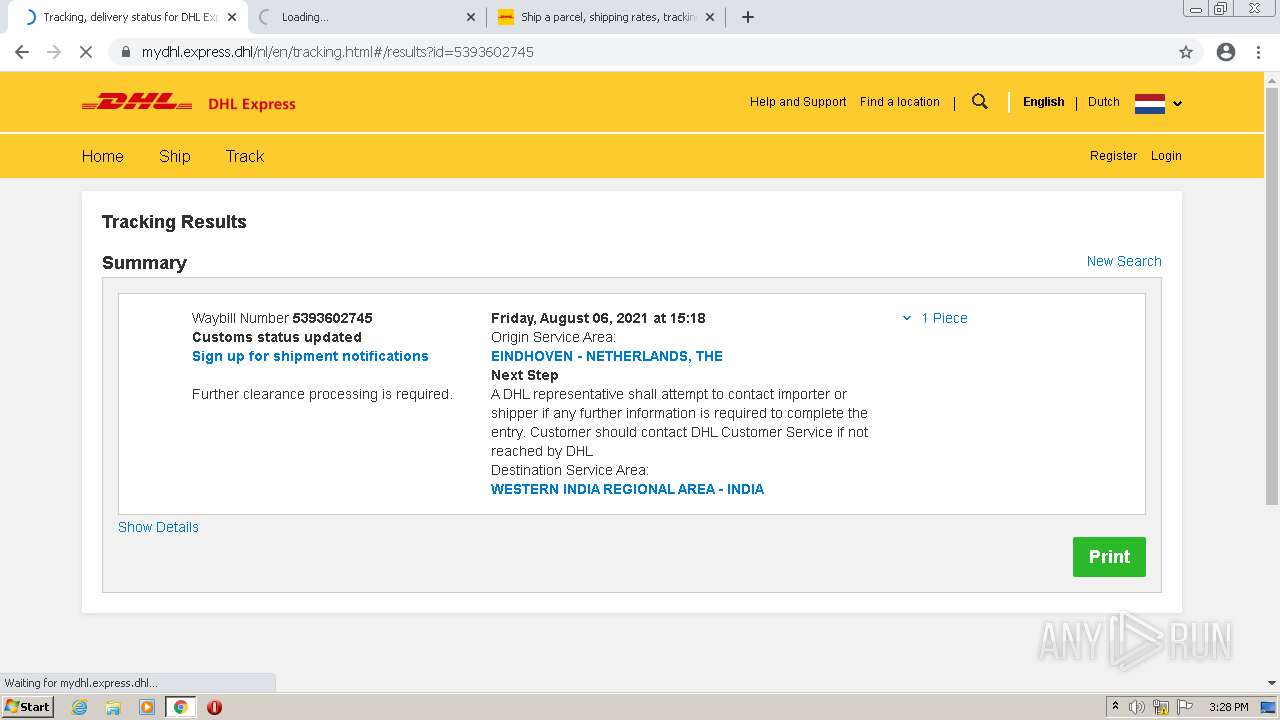
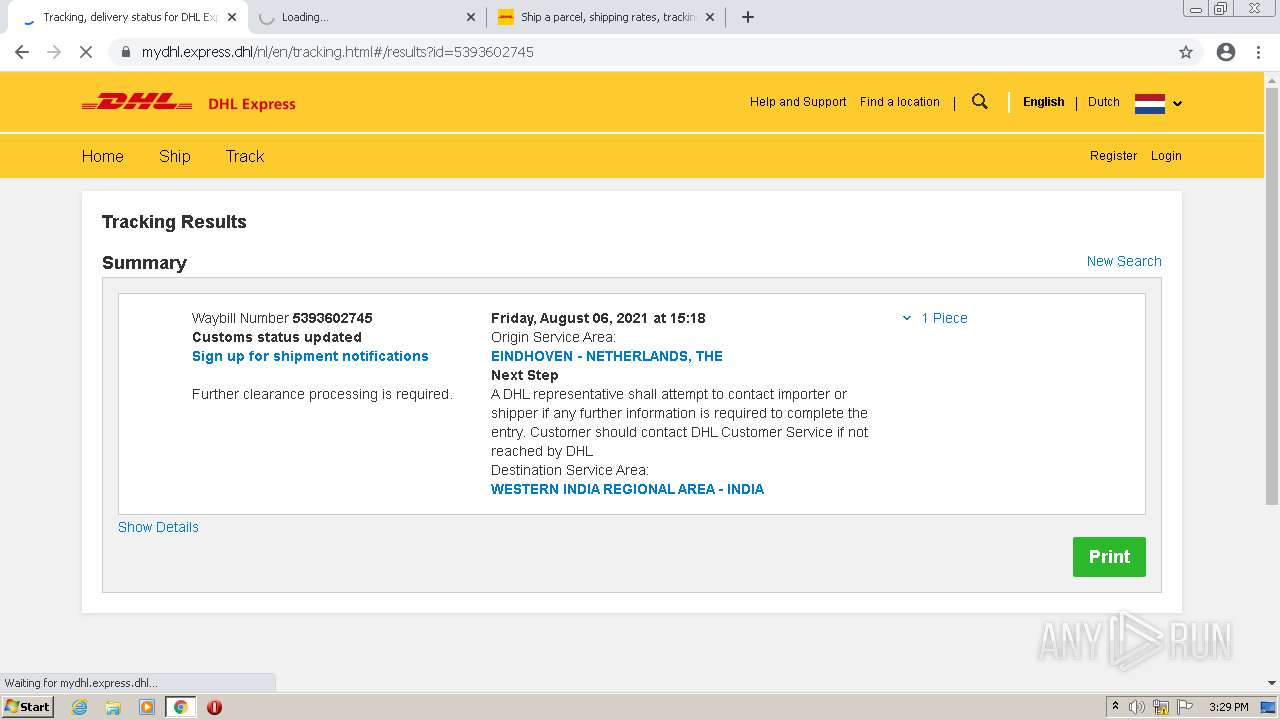
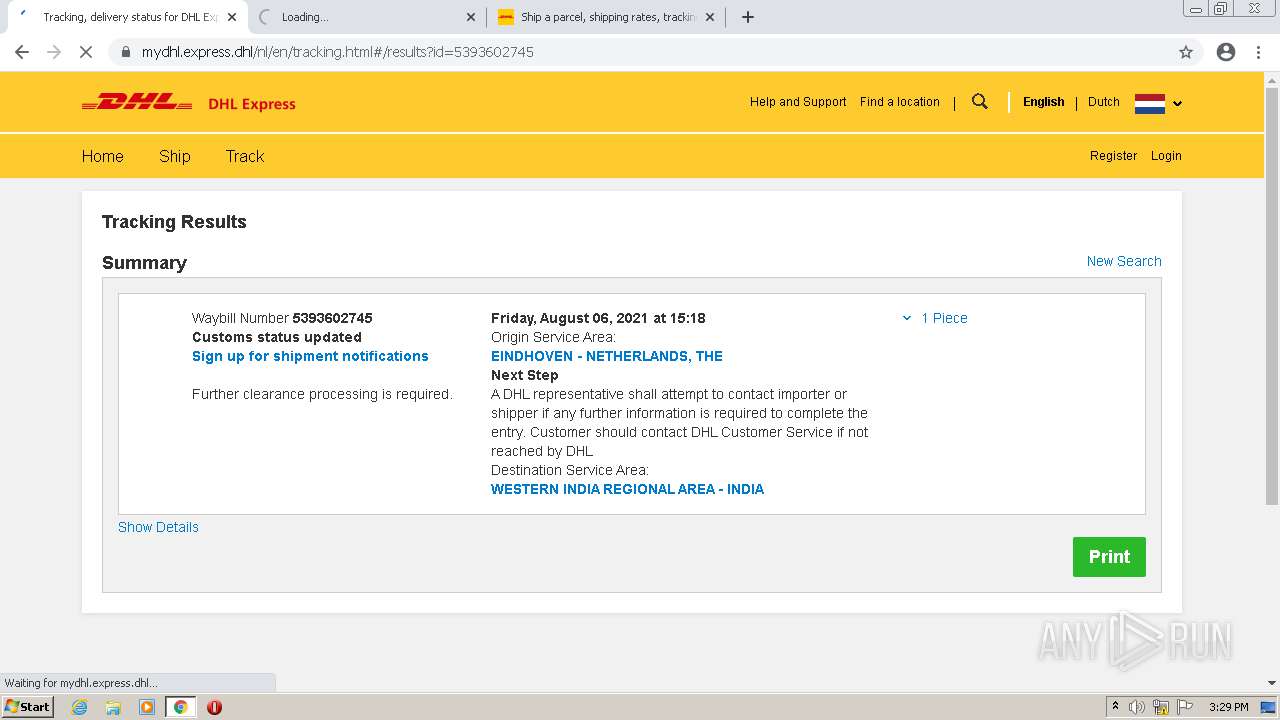
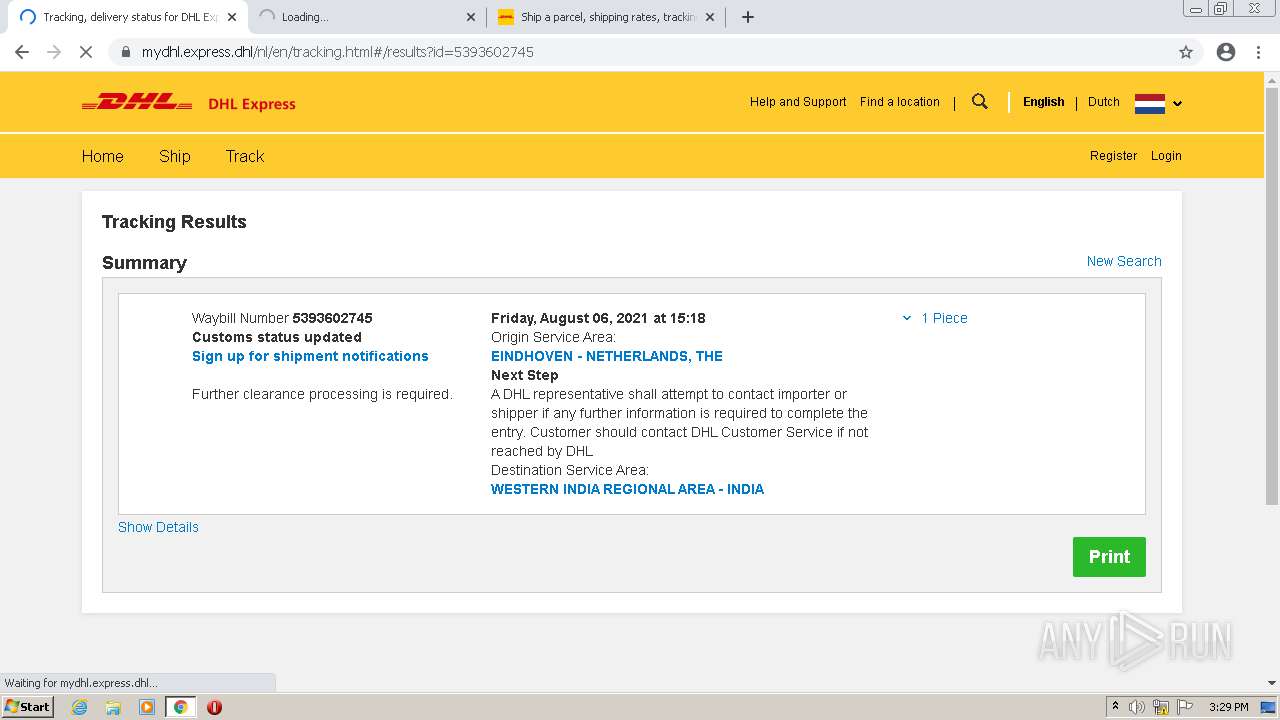
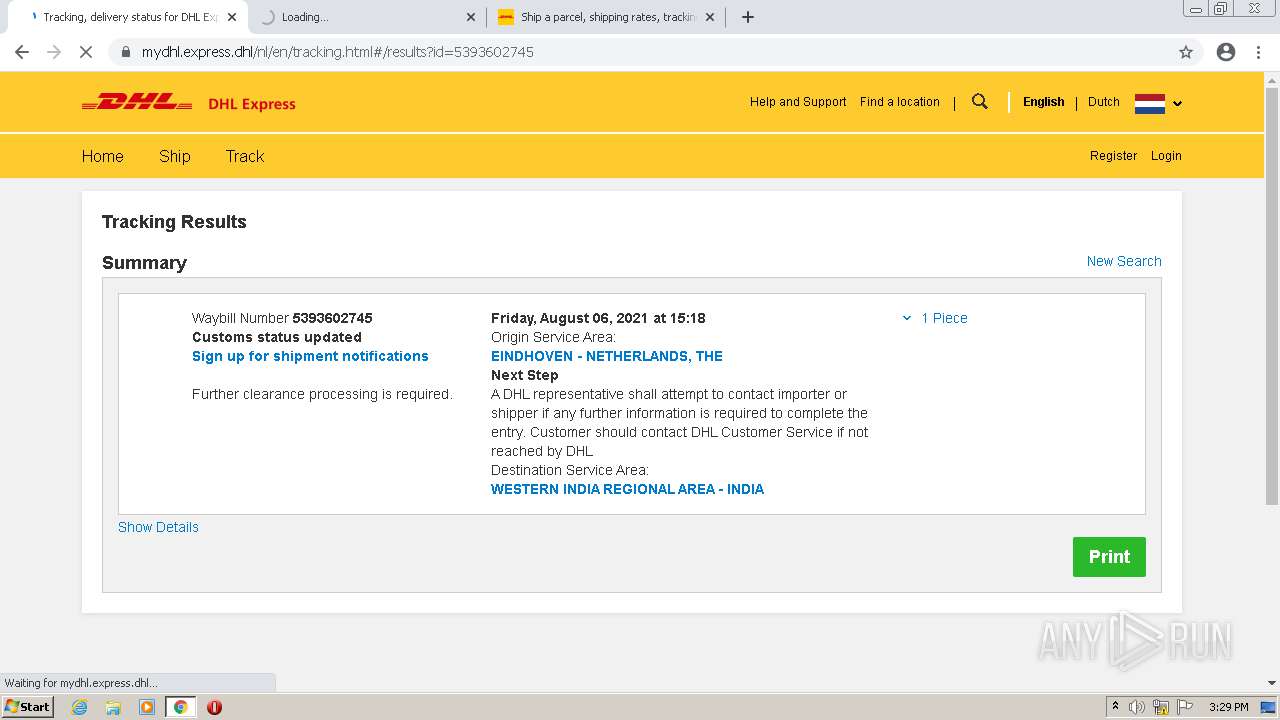
| URL: | https://mydhl.express.dhl/nl/nl/tracking.html#/results?id=5393602745 |
| Full analysis: | https://app.any.run/tasks/d1954fb8-0aaa-442e-98b3-6e9edd14699f |
| Verdict: | Malicious activity |
| Analysis date: | August 08, 2021, 14:26:35 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MD5: | 1867BCADFDB4DD746D2230B537F7C4AA |
| SHA1: | 4FDAFCAECD13572101252C09E401621A41241B17 |
| SHA256: | F68B27A5A56D890C5379929911A020F611D4F1F36D00163C103E275136FB7A33 |
| SSDEEP: | 3:N8FYDMNPPZHuIM8+HBYzZXiQn:2FCUPxHuIM8+Hq1n |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 296 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --disable-gpu-compositing --lang=en-US --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=10 --no-v8-untrusted-code-mitigations --mojo-platform-channel-handle=3656 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 504 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=utility --mojo-platform-channel-handle=1812 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 1308 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=printing.mojom.PrintingService --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=pdf_conversion --mojo-platform-channel-handle=3208 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2036 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=printing.mojom.PrintCompositor --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=print_compositor --mojo-platform-channel-handle=3200 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2060 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=utility --mojo-platform-channel-handle=2184 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2124 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=utility --mojo-platform-channel-handle=2160 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2628 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=chrome.mojom.UtilWin --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=none --mojo-platform-channel-handle=2792 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2672 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=ppapi --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --ppapi-flash-args --lang=en-US --device-scale-factor=1 --ppapi-antialiased-text-enabled=0 --ppapi-subpixel-rendering-setting=0 --mojo-platform-channel-handle=3364 /prefetch:3 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2848 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=gpu-process --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --gpu-preferences=MAAAAAAAAADgACAwAAAAAAAAAAAAAAAAAABgAAAAAAAQAAAAAAAAAAAAAAAAAAAAKAAAAAQAAAAgAAAAAAAAACgAAAAAAAAAMAAAAAAAAAA4AAAAAAAAABAAAAAAAAAAAAAAAAUAAAAQAAAAAAAAAAAAAAAGAAAAEAAAAAAAAAABAAAABQAAABAAAAAAAAAAAQAAAAYAAAA= --mojo-platform-channel-handle=1048 /prefetch:2 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| 2908 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --field-trial-handle=1060,14332550778998010207,5360752865066377236,131072 --enable-features=PasswordImport --lang=en-US --service-sandbox-type=network --mojo-platform-channel-handle=1252 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | chrome.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 86.0.4240.198 Modules
| |||||||||||||||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: 01000000 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Update\ClientState\{8A69D345-D564-463c-AFF1-A69D9E530F96} |
| Operation: | write | Name: | dr |
Value: 1 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Chrome |
| Operation: | write | Name: | UsageStatsInSample |
Value: 0 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Google\Update\ClientStateMedium\{8A69D345-D564-463C-AFF1-A69D9E530F96} |
| Operation: | write | Name: | usagestats |
Value: 0 | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Update\ClientState\{8A69D345-D564-463c-AFF1-A69D9E530F96} |
| Operation: | write | Name: | metricsid |
Value: | |||
| (PID) Process: | (3236) chrome.exe | Key: | HKEY_CURRENT_USER\Software\Google\Update\ClientState\{8A69D345-D564-463c-AFF1-A69D9E530F96} |
| Operation: | write | Name: | metricsid_installdate |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\BrowserMetrics\BrowserMetrics-610FE9AC-CA4.pma | — | |
MD5:— | SHA256:— | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\7213d4a7-6430-4c6a-8c23-8ab4ab2b7045.tmp | text | |
MD5:A54D39E8D0231375C46F085CAD35B9A1 | SHA256:95205F1F079E6C5DECB96E4C36432198199D4147499FC7B37B2766502B628FE9 | |||
| 3992 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\CrashpadMetrics.pma | binary | |
MD5:03C4F648043A88675A920425D824E1B3 | SHA256:F91DBB7C64B4582F529C968C480D2DCE1C8727390482F31E4355A27BB3D9B450 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Data\LevelDB\LOG.old~RF10bf89.TMP | text | |
MD5:64AD8ED3E666540337BA541C549F72F7 | SHA256:BECBDB08B5B37D203A85F2E974407334053BB1D2270F0B3C9A4DB963896F2206 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Data\LevelDB\LOG.old | text | |
MD5:5BD3C311F2136A7A88D3E197E55CF902 | SHA256:FA331915E1797E59979A3E4BCC2BD0D3DEAA039B94D4DB992BE251FD02A224B9 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Local Storage\leveldb\LOG.old | text | |
MD5:7721CDA9F5B73CE8A135471EB53B4E0E | SHA256:DD730C576766A46FFC84E682123248ECE1FF1887EC0ACAB22A5CE93A450F4500 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Extension State\LOG.old~RF10c6ad.TMP | text | |
MD5:D097F8EB2230B3F32C41C5D75790508C | SHA256:ADDF87D20CD455CFB4AACB6B76719629C0277A4CF70B496343047BB73ABBAEF5 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\df7d8518-29cd-42f8-8704-0da9ba252125.tmp | binary | |
MD5:5058F1AF8388633F609CADB75A75DC9D | SHA256:CDB4EE2AEA69CC6A83331BBE96DC2CAA9A299D21329EFB0336FC02A82E1839A8 | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Extension Settings\pkedcjkdefgpdelpbcmbmeomcjbeemfm\LOG.old | text | |
MD5:5202CA4D6AF0C37DAEC0D528CC7F2986 | SHA256:8F5B8FF94B14C36EA0CBE8FA0A4D165A632B45F834BBB7239E1A6CF6685F256C | |||
| 3236 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Site Characteristics Database\LOG.old~RF10bf79.TMP | text | |
MD5:936EB7280DA791E6DD28EF3A9B46D39C | SHA256:CBAF2AFD831B32F6D1C12337EE5D2F090D6AE1F4DCB40B08BEF49BF52AD9721F | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2908 | chrome.exe | GET | 301 | 184.24.11.104:80 | http://www.dhl.co.in/en/country_profile.html | US | — | — | suspicious |
896 | svchost.exe | GET | 206 | 173.194.137.74:80 | http://r5---sn-aigzrn76.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw?cms_redirect=yes&mh=-b&mip=85.203.34.115&mm=28&mn=sn-aigzrn76&ms=nvh&mt=1628432658&mv=m&mvi=5&pl=24&rmhost=r2---sn-aigzrn76.gvt1.com&shardbypass=yes&smhost=r2---sn-aigzrn7e.gvt1.com | US | binary | 43.1 Kb | whitelisted |
896 | svchost.exe | HEAD | 403 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw | US | — | — | whitelisted |
896 | svchost.exe | GET | 206 | 173.194.137.74:80 | http://r5---sn-aigzrn76.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw?cms_redirect=yes&mh=-b&mip=85.203.34.115&mm=28&mn=sn-aigzrn76&ms=nvh&mt=1628432658&mv=m&mvi=5&pl=24&rmhost=r2---sn-aigzrn76.gvt1.com&shardbypass=yes&smhost=r2---sn-aigzrn7e.gvt1.com | US | binary | 9.40 Kb | whitelisted |
896 | svchost.exe | GET | 302 | 172.217.23.110:80 | http://redirector.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw | US | html | 549 b | whitelisted |
2908 | chrome.exe | GET | 204 | 172.217.16.131:80 | http://www.gstatic.com/generate_204 | US | — | — | whitelisted |
896 | svchost.exe | GET | 302 | 172.217.23.110:80 | http://redirector.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw | US | html | 549 b | whitelisted |
896 | svchost.exe | HEAD | 200 | 173.194.137.74:80 | http://r5---sn-aigzrn76.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw?cms_redirect=yes&mh=-b&mip=85.203.34.115&mm=28&mn=sn-aigzrn76&ms=nvh&mt=1628432418&mv=m&mvi=5&pl=24&rmhost=r2---sn-aigzrn76.gvt1.com&shardbypass=yes&smhost=r2---sn-aigzrn7e.gvt1.com | US | — | — | whitelisted |
896 | svchost.exe | GET | 302 | 172.217.23.110:80 | http://redirector.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw | US | html | 549 b | whitelisted |
896 | svchost.exe | GET | 302 | 172.217.23.110:80 | http://redirector.gvt1.com/edgedl/release2/chrome_component/AJD927i74k1lBFPyofryMko_1.3.36.91/bMPY3gg4TVlmGEtJqGkFyw | US | html | 549 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
2908 | chrome.exe | 104.109.79.23:443 | mydhl.express.dhl | Akamai International B.V. | NL | whitelisted |
2908 | chrome.exe | 34.240.91.113:443 | dpm.demdex.net | Amazon.com, Inc. | IE | suspicious |
2908 | chrome.exe | 142.250.185.206:443 | clients2.google.com | Google Inc. | US | whitelisted |
2908 | chrome.exe | 2.18.232.23:443 | assets.adobedtm.com | Akamai International B.V. | — | whitelisted |
2908 | chrome.exe | 34.102.188.203:443 | vawidget-eu.express.dhl | — | US | unknown |
2908 | chrome.exe | 20.190.160.129:443 | login.microsoftonline.com | Microsoft Corporation | US | suspicious |
2908 | chrome.exe | 172.217.18.99:443 | ssl.gstatic.com | Google Inc. | US | whitelisted |
2908 | chrome.exe | 54.154.124.189:443 | dpm.demdex.net | Amazon.com, Inc. | IE | unknown |
2908 | chrome.exe | 34.248.191.66:443 | cm.everesttech.net | Amazon.com, Inc. | IE | suspicious |
2908 | chrome.exe | 40.68.95.2:443 | mytime.dpdhl.com | Microsoft Corporation | NL | unknown |
Domain | IP | Reputation |
|---|---|---|
accounts.google.com |
| shared |
mydhl.express.dhl |
| whitelisted |
clients2.google.com |
| whitelisted |
assets.adobedtm.com |
| whitelisted |
dpm.demdex.net |
| whitelisted |
s.go-mpulse.net |
| whitelisted |
vawidget-eu.express.dhl |
| unknown |
dpcomdhl.demdex.net |
| whitelisted |
cm.everesttech.net |
| whitelisted |
c.go-mpulse.net |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2908 | chrome.exe | Generic Protocol Command Decode | SURICATA HTTP unable to match response to request |