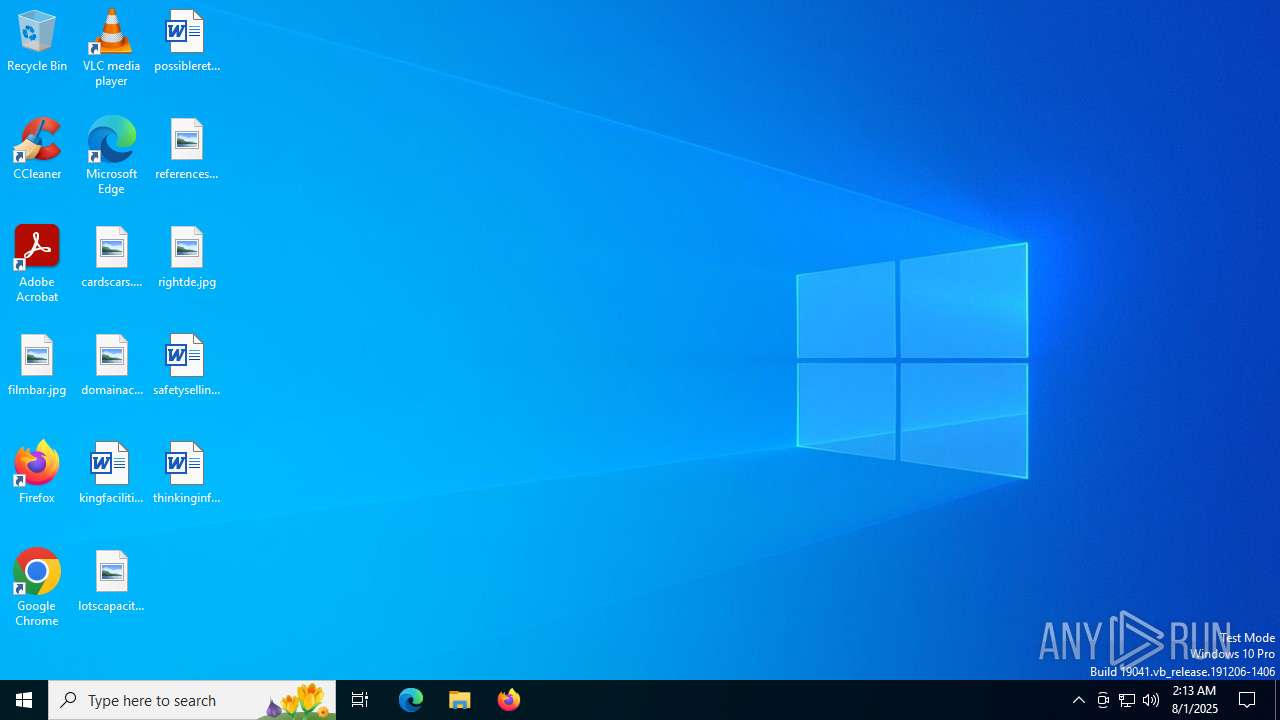
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
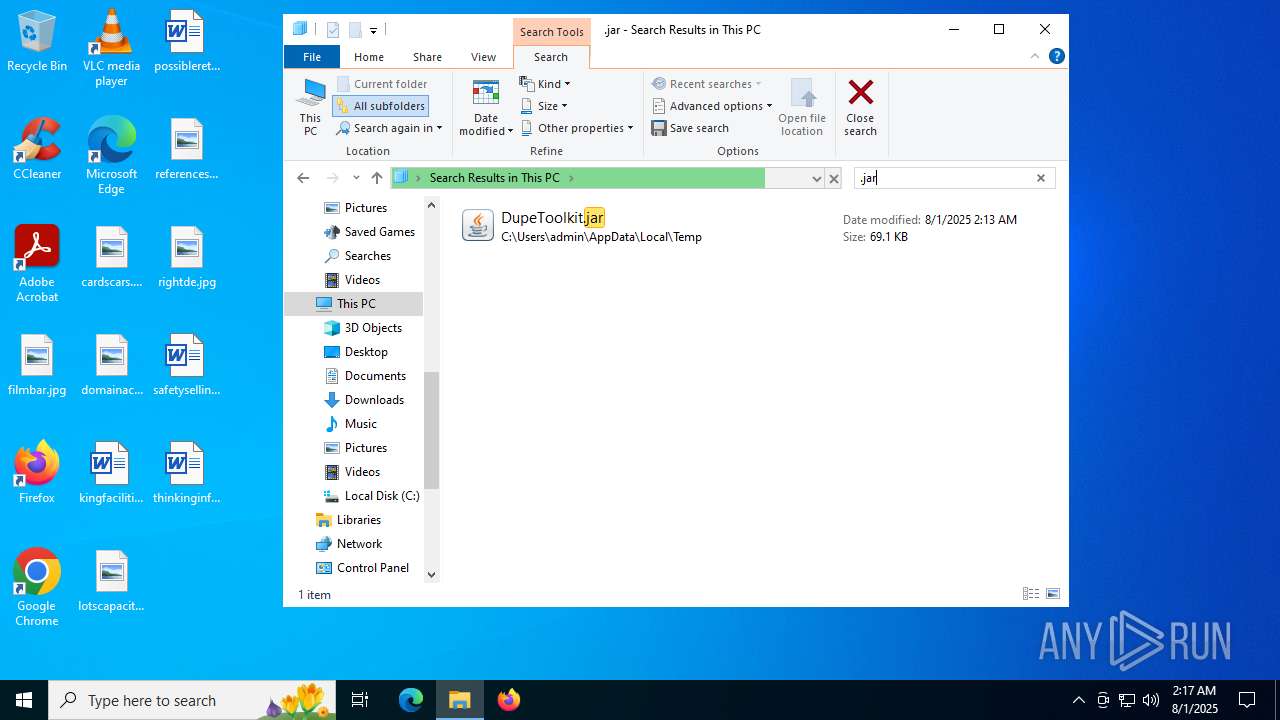
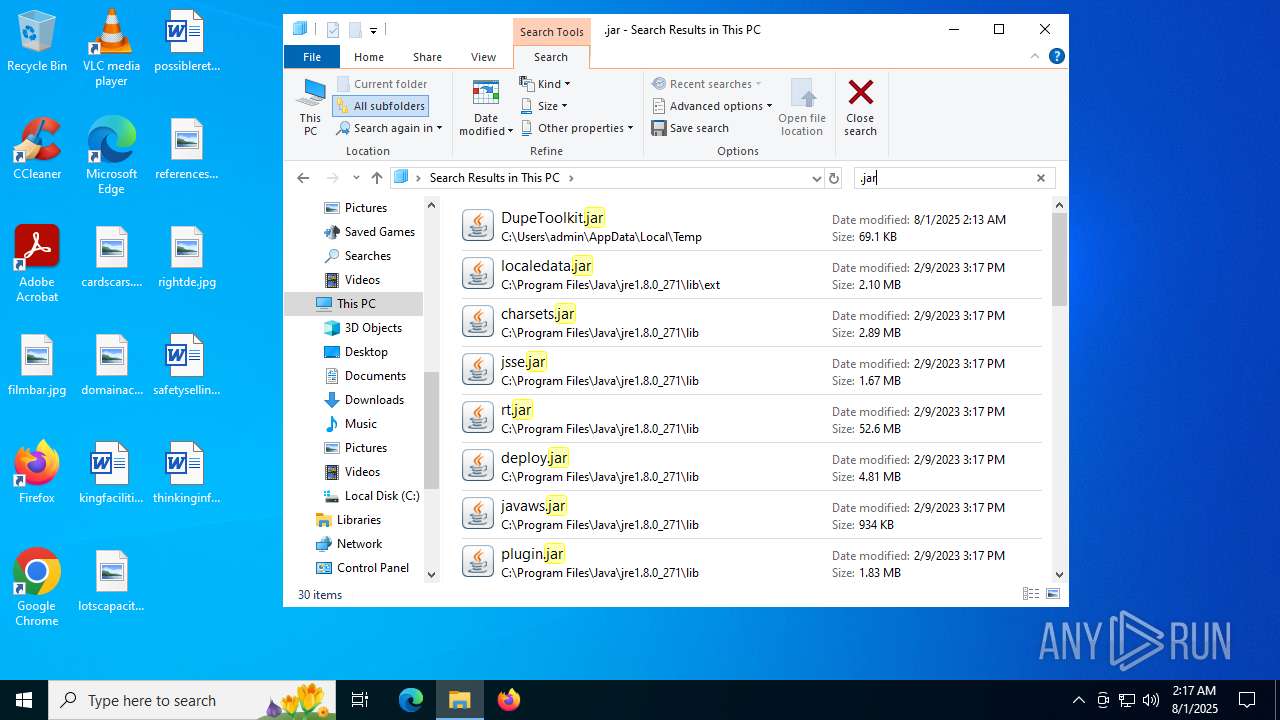
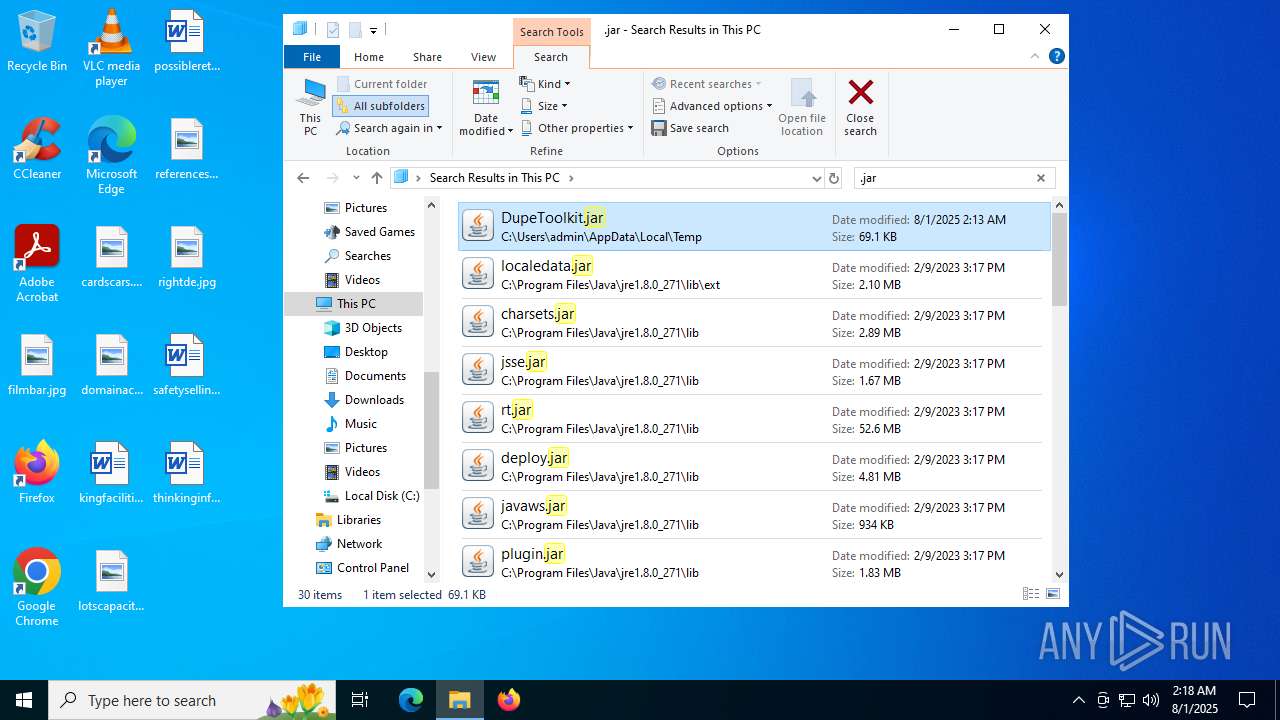
| File name: | DupeToolkit.jar |
| Full analysis: | https://app.any.run/tasks/65eae0a2-05dd-496c-84cf-ab5ba42f80f5 |
| Verdict: | Malicious activity |
| Analysis date: | August 01, 2025, 02:13:07 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v1.0 to extract, compression method=store |
| MD5: | EE31E658AB9026A155B2023063315002 |
| SHA1: | B8C1DB6C7C30A9C93ED9C3D654EAF702011E20D6 |
| SHA256: | E57B45B9F3631FD9F6F9451D8AA436B1C7B56B75F8928F2A974C32E84C481A6B |
| SSDEEP: | 1536:k7/sySaNn0uP474r32jkGvmARWDk/iQICnfeg2:i0yd2uP4USjkrAcDLQICfeg2 |
| .jar | | | Java Archive (78.3) |
|---|---|---|
| .zip | | | ZIP compressed archive (21.6) |
| ZipRequiredVersion: | 10 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | None |
| ZipModifyDate: | 1980:01:01 00:00:00 |
| ZipCRC: | 0x00000000 |
| ZipCompressedSize: | - |
| ZipUncompressedSize: | - |
| ZipFileName: | assets/ |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 472 | "C:\Users\admin\AppData\Local\Microsoft\OneDrive\21.220.1024.0005\FileCoAuth.exe" -Embedding | C:\Users\admin\AppData\Local\Microsoft\OneDrive\21.220.1024.0005\FileCoAuth.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft OneDriveFile Co-Authoring Executable Exit code: 0 Version: 21.220.1024.0005 Modules
| |||||||||||||||
| 620 | C:\Users\admin\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe /update /restart /updateSource:ODU /peruser /childprocess | C:\Users\admin\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe | OneDriveSetup.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft OneDrive (32 bit) Setup Exit code: 0 Version: 21.220.1024.0005 Modules
| |||||||||||||||
| 2120 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | icacls.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2140 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2716 | C:\WINDOWS\system32\icacls.exe C:\ProgramData\Oracle\Java\.oracle_jre_usage /grant "everyone":(OI)(CI)M | C:\Windows\System32\icacls.exe | — | javaw.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3028 | /updateInstalled /background | C:\Users\admin\AppData\Local\Microsoft\OneDrive\OneDrive.exe | — | OneDriveSetup.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft OneDrive Exit code: 2147943660 Version: 21.220.1024.0005 Modules
| |||||||||||||||
| 3108 | C:\WINDOWS\System32\rundll32.exe C:\WINDOWS\System32\shell32.dll,SHCreateLocalServerRunDll {9aa46009-3ce0-458a-a354-715610a075e6} -Embedding | C:\Windows\System32\rundll32.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3392 | "C:\Users\admin\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe" /update /restart /updateSource:ODU | C:\Users\admin\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe | — | OneDrive.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft OneDrive (32 bit) Setup Exit code: 0 Version: 21.220.1024.0005 Modules
| |||||||||||||||
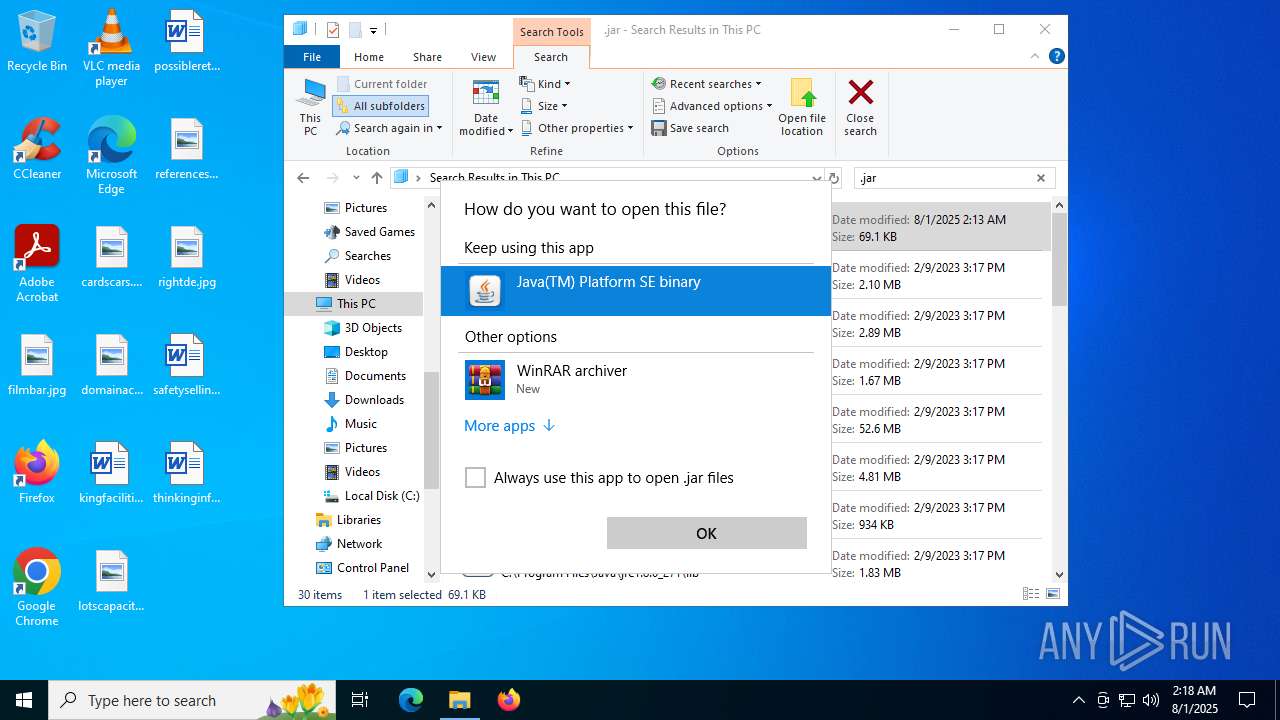
| 3788 | "C:\Program Files\Java\jre1.8.0_271\bin\javaw.exe" -jar C:\Users\admin\AppData\Local\Temp\DupeToolkit.jar | C:\Program Files\Java\jre1.8.0_271\bin\javaw.exe | — | explorer.exe | |||||||||||
User: admin Company: Oracle Corporation Integrity Level: MEDIUM Description: Java(TM) Platform SE binary Exit code: 1 Version: 8.0.2710.9 Modules
| |||||||||||||||
| 3880 | C:\WINDOWS\system32\SearchIndexer.exe /Embedding | C:\Windows\System32\SearchIndexer.exe | — | services.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Microsoft Windows Search Indexer Version: 7.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\WOW6432Node\Interface\{466F31F7-9892-477E-B189-FA5C59DE3603}\TypeLib |
| Operation: | write | Name: | Version |
Value: 1.0 | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\Interface\{869BDA08-7ACF-42B8-91AE-4D8D597C0B33}\TypeLib |
| Operation: | write | Name: | Version |
Value: 1.0 | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\WOW6432Node\Interface\{869BDA08-7ACF-42B8-91AE-4D8D597C0B33}\TypeLib |
| Operation: | write | Name: | Version |
Value: 1.0 | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\Interface\{679EC955-75AA-4FB2-A7ED-8C0152ECF409}\TypeLib |
| Operation: | write | Name: | Version |
Value: 1.0 | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\WOW6432Node\Interface\{679EC955-75AA-4FB2-A7ED-8C0152ECF409}\TypeLib |
| Operation: | write | Name: | Version |
Value: 1.0 | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\WOW6432Node\CLSID\{4410DC33-BC7C-496B-AA84-4AEA3EEE75F7}\InProcServer32 |
| Operation: | write | Name: | ThreadingModel |
Value: Both | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\CLSID\{4410DC33-BC7C-496B-AA84-4AEA3EEE75F7}\InProcServer32 |
| Operation: | write | Name: | ThreadingModel |
Value: Both | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\odopen\DefaultIcon |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\odopen\shell\open\command |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (6312) OneDrive.exe | Key: | HKEY_CLASSES_ROOT\odopen\shell\open |
| Operation: | delete key | Name: | (default) |
Value: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 5988 | svchost.exe | C:\Users\admin\AppData\Local\Temp\BIT54A9.tmp | — | |
MD5:— | SHA256:— | |||
| 5988 | svchost.exe | C:\Users\admin\AppData\Local\Temp\wct548A.tmp | — | |
MD5:— | SHA256:— | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\Local\Microsoft\OneDrive\Update\OneDriveSetup.exe | — | |
MD5:— | SHA256:— | |||
| 620 | OneDriveSetup.exe | C:\Users\admin\AppData\Local\Temp\tmp61F7.tmp | — | |
MD5:— | SHA256:— | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\Local\Microsoft\OneDrive\logs\Personal\TraceArchive.0304.0013-36.etl | abr | |
MD5:97596EEBD1886A7637AEC1F4739959FC | SHA256:43A342C94BDA9B236D3D1F45711C0B2FB9FA179CF7E0C9252E6DB0EE1930811F | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\Local\Microsoft\OneDrive\logs\Personal\SyncEngine-2025-08-01.0214.6312.1.aodl | binary | |
MD5:28DCA2FF4B34B5A52A2E59DF202A6ED3 | SHA256:33BACCB7296F1ED1F995FC77A23049F261CF391AC0388F9E8DD161F8C17B7F94 | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\E2C6CBAF0AF08CF203BA74BF0D0AB6D5_6372E0472AFF76BB926C97818BC773B9 | der | |
MD5:FA762B161F45FF06C65404A6A36252D6 | SHA256:0099EDFE2F9DA7770FF749D177DB9D7C982F7C4A95FFC3D749FDC87AB5EE7451 | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\26C212D9399727259664BDFCA073966E_F9F7D6A7ECE73106D2A8C63168CDA10D | der | |
MD5:002C663D88921A24B042603B69E711CC | SHA256:C6259D0D302E40FFB5B4E7D91101110B8966988A057F5E7D53928D829DEB53E1 | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\Local\Microsoft\OneDrive\logs\Personal\DeviceFailureDatagram\DeviceHealthSummaryConfiguration.ini | text | |
MD5:4F099B97B37E41A1FAA0FE9D6BF0B45F | SHA256:4C7C28C65ECDB44E38162D37899FFD03490C25A263B637D232F493ED8C13A3D8 | |||
| 6312 | OneDrive.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\INetCache\IE\KCV3KQBA\update100[1].xml | xml | |
MD5:53244E542DDF6D280A2B03E28F0646B7 | SHA256:36A6BD38A8A6F5A75B73CAFFAE5AE66DFABCAEFD83DA65B493FA881EA8A64E7D | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2528 | svchost.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.216.77.42:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
6312 | OneDrive.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEA77flR%2B3w%2FxBpruV2lte6A%3D | US | binary | 471 b | whitelisted |
1868 | backgroundTaskHost.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEApDqVCbATUviZV57HIIulA%3D | US | binary | 471 b | whitelisted |
6312 | OneDrive.exe | GET | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
1036 | SIHClient.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | NL | binary | 420 b | whitelisted |
1036 | SIHClient.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Update%20Secure%20Server%20CA%202.1.crl | NL | binary | 408 b | whitelisted |
2940 | svchost.exe | GET | 200 | 23.3.109.48:80 | http://x1.c.lencr.org/ | DE | binary | 734 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1268 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6292 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1268 | svchost.exe | 23.216.77.42:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1268 | svchost.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
1268 | svchost.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
5944 | MoUsoCoreWorker.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
2528 | svchost.exe | 20.190.160.131:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |