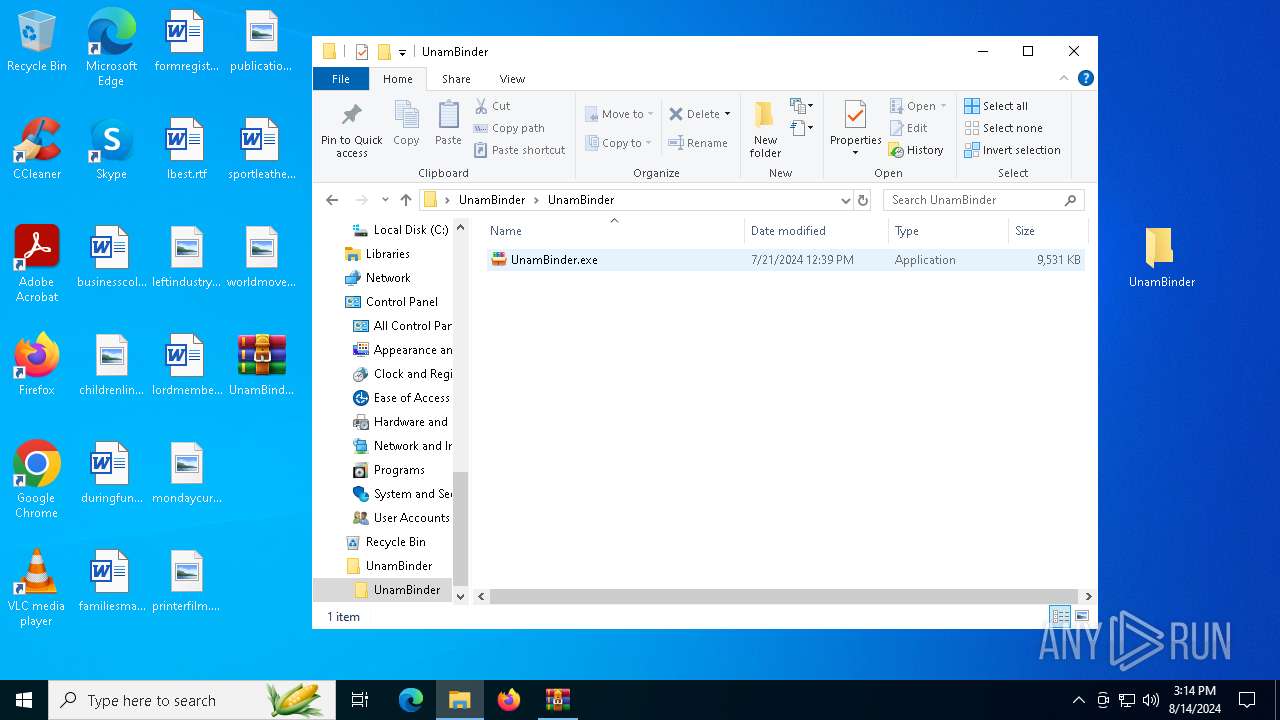
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
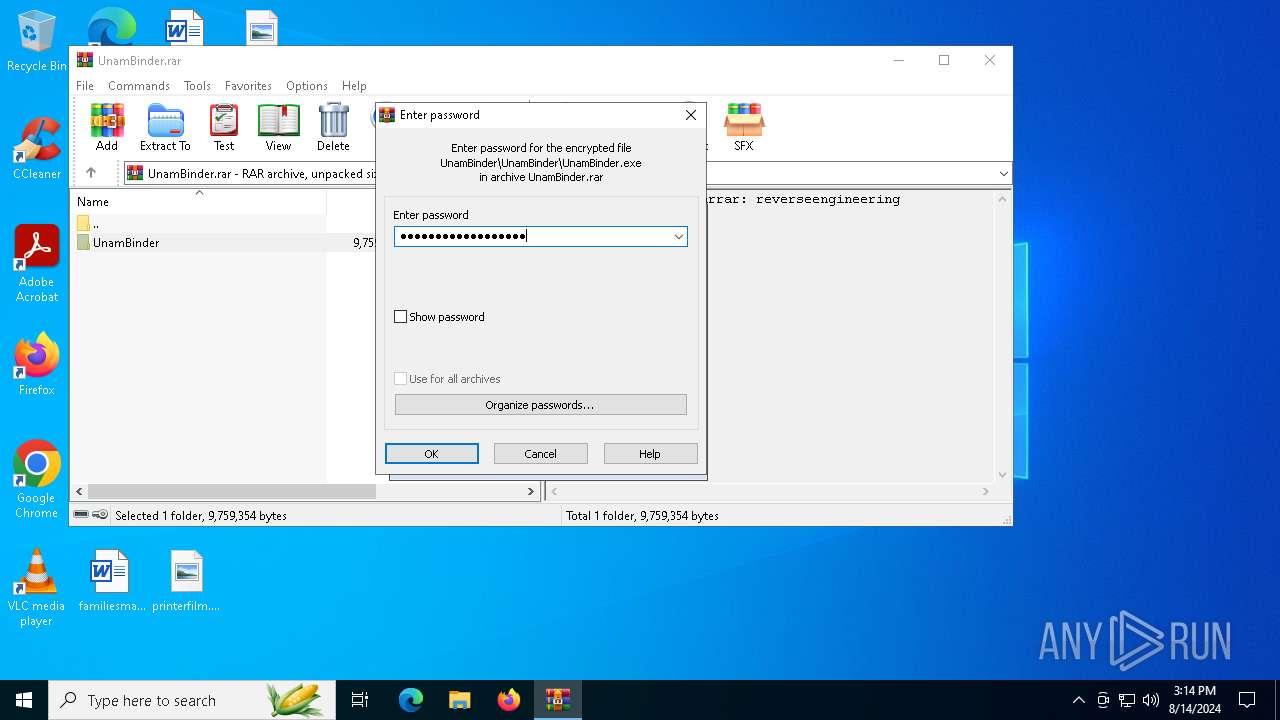
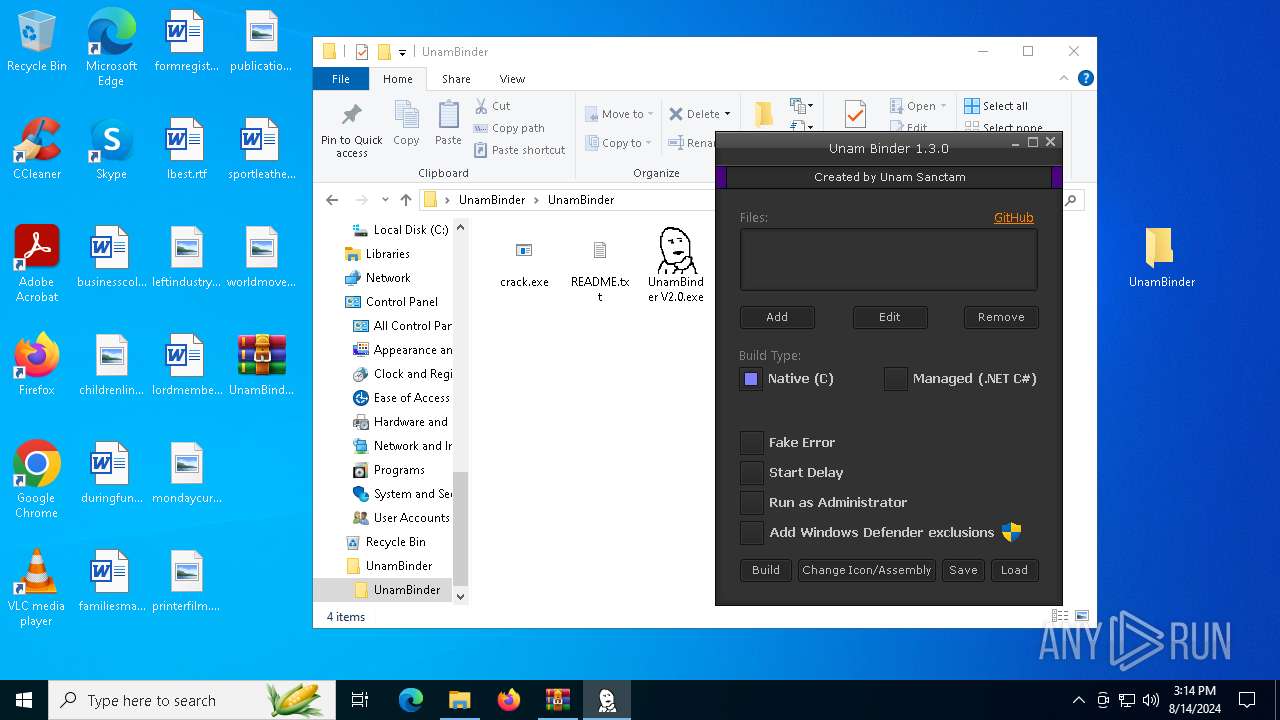
| File name: | UnamBinder.rar |
| Full analysis: | https://app.any.run/tasks/48d052a0-9e32-4b90-9c0f-30f2c891e13e |
| Verdict: | Malicious activity |
| Threats: | XWorm is a remote access trojan (RAT) sold as a malware-as-a-service. It possesses an extensive hacking toolset and is capable of gathering private information and files from the infected computer, hijacking MetaMask and Telegram accounts, and tracking user activity. XWorm is typically delivered to victims' computers through multi-stage attacks that start with phishing emails. |
| Analysis date: | August 14, 2024, 15:13:36 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-rar |
| File info: | RAR archive data, v5 |
| MD5: | AAB24D1586850A4D148EAFEDD2FA7A27 |
| SHA1: | BDC8D522BA4ABBDBDB63F45B6EBD98DD300013B8 |
| SHA256: | DBF2CB7DA5398A29CAF5D636A76C716801D6562646EDC694B2C9F2AE6289642C |
| SSDEEP: | 98304:ZiBqT/u99DKmqxHPorRRVTshbmk+ou7M4PiKovQfNI+IcyiGlHZlZqnkTspgYrCD:q4827GqLZM1e2fRlDYV |
| .rar | | | RAR compressed archive (v5.0) (61.5) |
|---|---|---|
| .rar | | | RAR compressed archive (gen) (38.4) |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 2256 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2424 | "C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy Bypass Add-MpPreference -ExclusionPath 'C:\Users\admin\AppData\Local\Temp\Windows Driver Fondation.exe' | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | UnamBinder V2.0.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows PowerShell Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2480 | "C:\Windows\System32\schtasks.exe" /create /f /sc minute /mo 1 /tn "Windows Driver Fondation" /tr "C:\Users\admin\AppData\Local\Temp\Windows Driver Fondation" | C:\Windows\System32\schtasks.exe | — | crack.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Task Scheduler Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3176 | C:\WINDOWS\System32\rundll32.exe C:\WINDOWS\System32\shell32.dll,SHCreateLocalServerRunDll {9aa46009-3ce0-458a-a354-715610a075e6} -Embedding | C:\Windows\System32\rundll32.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4576 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | schtasks.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5152 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
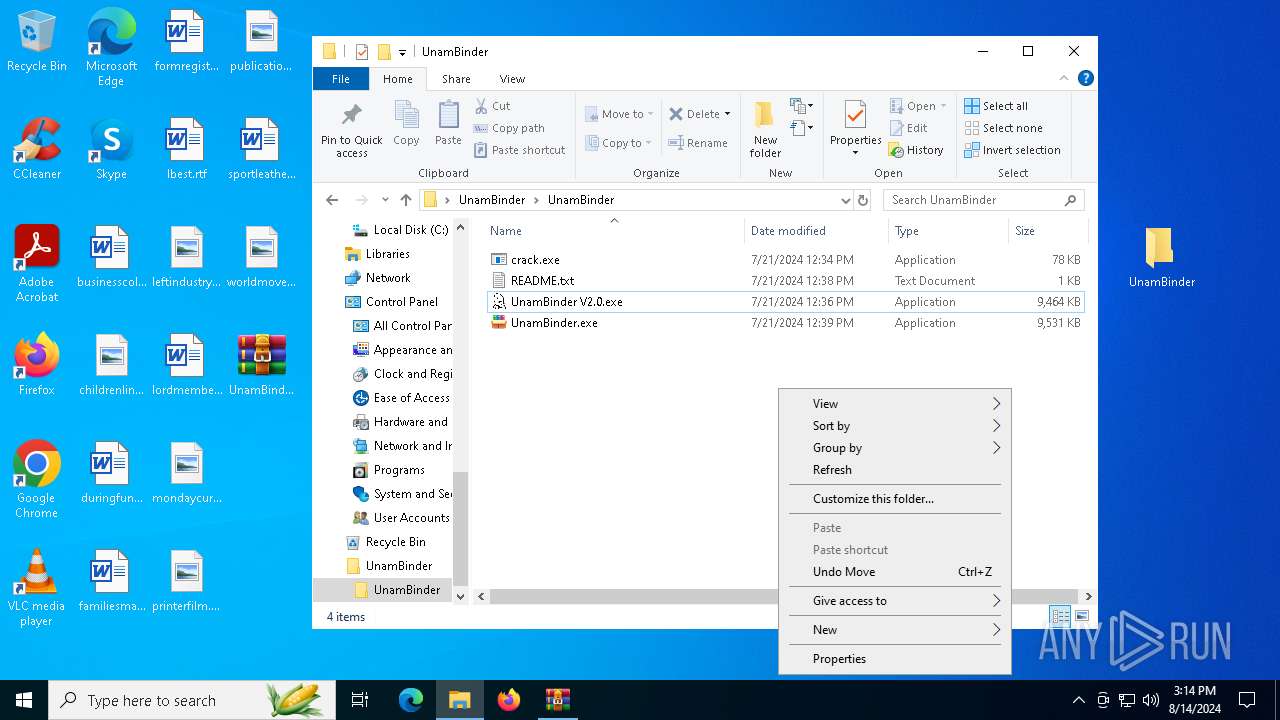
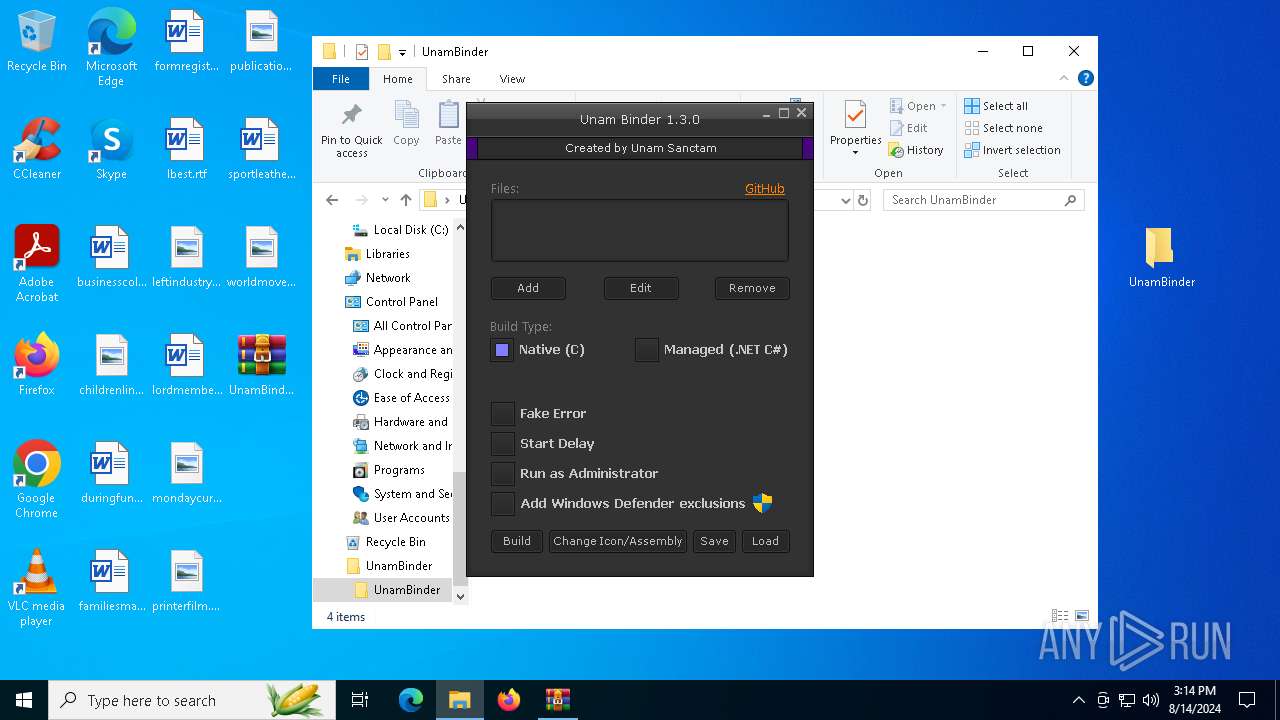
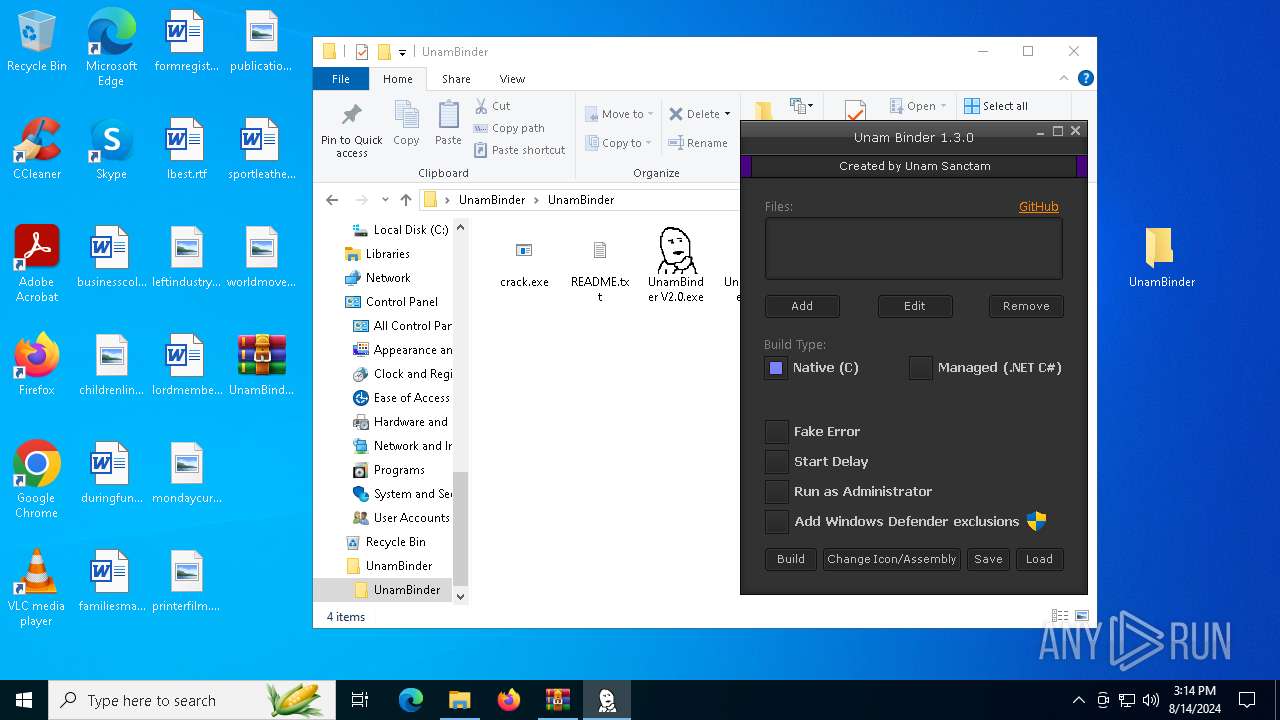
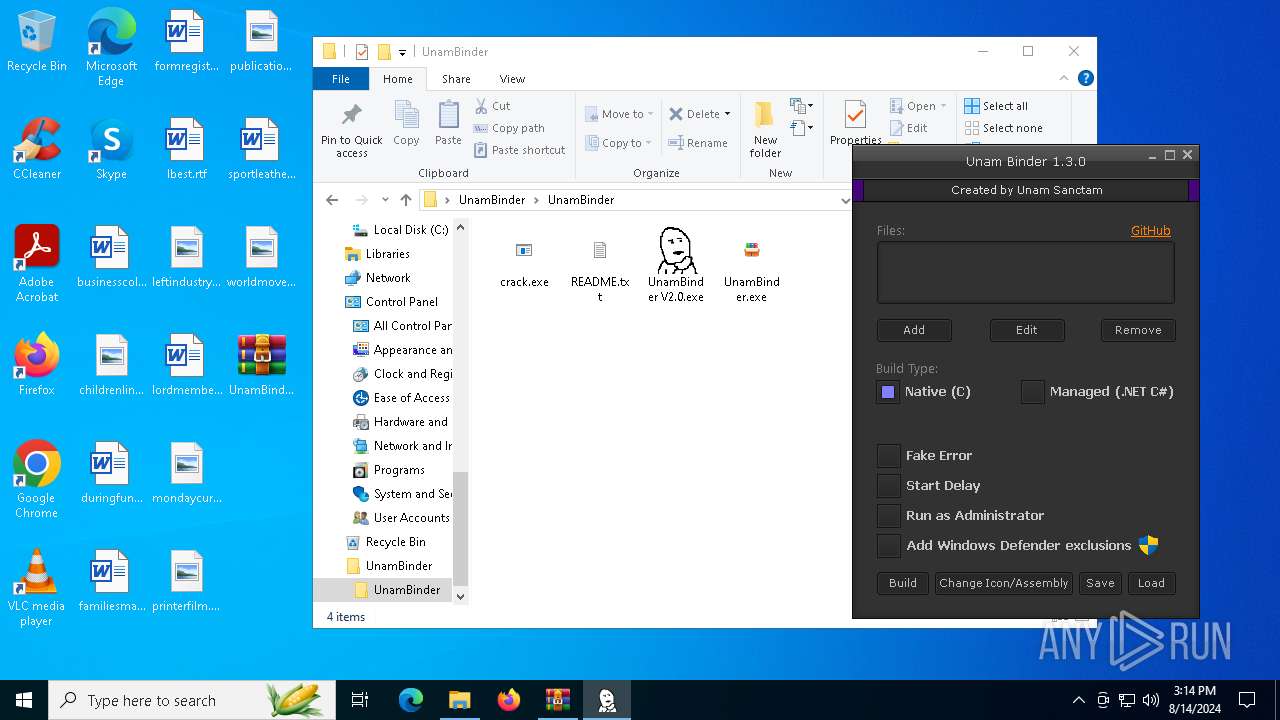
| 6196 | "C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder V2.0.exe" | C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder V2.0.exe | UnamBinder V2.0.exe | ||||||||||||
User: admin Integrity Level: HIGH Description: UnamBinder Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| 6252 | "C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder.exe" | C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
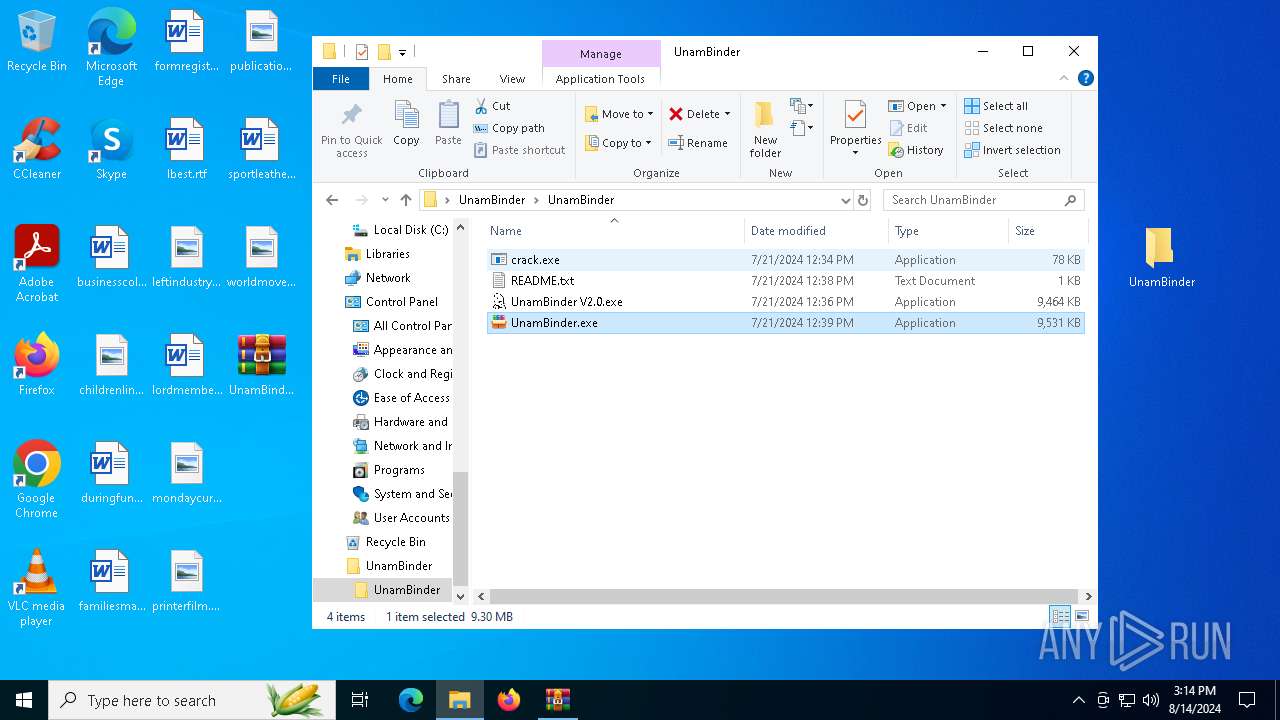
| 6272 | "C:\Users\admin\Desktop\UnamBinder\UnamBinder\crack.exe" | C:\Users\admin\Desktop\UnamBinder\UnamBinder\crack.exe | UnamBinder.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Visual C++ 2008 Redistributable Setup Version: 9.0.30729.5677 Modules
XWorm(PID) Process(6272) crack.exe C2jajaovh.duckdns.org:1605 Keys AES<123456789> Options Splitter<Xwormmm> Sleep time3 USB drop nameXWorm V5.0 MutexULGFpUS9mj98magF | |||||||||||||||
| 6352 | "C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder V2.0.exe" | C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder V2.0.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Description: UnamBinder Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\GoogleChromeEnterpriseBundle64.zip | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\Desktop\UnamBinder.rar | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
| (PID) Process: | (6452) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface |
| Operation: | write | Name: | ShowPassword |
Value: 0 | |||
| (PID) Process: | (6252) UnamBinder.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | ProxyBypass |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 6272 | crack.exe | C:\Users\admin\AppData\Local\Temp\Windows Driver Fondation | executable | |
MD5:6BBA70ECF767C84AFF30E2F51E3F74EC | SHA256:010B8DB19EAD1BA157738C6DA0D1E5AE38F611AAC56DE325E872E1DC61229CF2 | |||
| 2424 | powershell.exe | C:\Users\admin\AppData\Local\Temp\__PSScriptPolicyTest_0ku3muyu.2fk.ps1 | text | |
MD5:D17FE0A3F47BE24A6453E9EF58C94641 | SHA256:96AD1146EB96877EAB5942AE0736B82D8B5E2039A80D3D6932665C1A4C87DCF7 | |||
| 6252 | UnamBinder.exe | C:\Users\admin\Desktop\UnamBinder\UnamBinder\crack.exe | executable | |
MD5:6BBA70ECF767C84AFF30E2F51E3F74EC | SHA256:010B8DB19EAD1BA157738C6DA0D1E5AE38F611AAC56DE325E872E1DC61229CF2 | |||
| 6452 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRb6452.26304\UnamBinder\UnamBinder\UnamBinder.exe | executable | |
MD5:E28B353CDD171BEBC92BFBA22DF84E55 | SHA256:9540580E625097FAC1E7F290EF3672D37E30DC27CA5349A2F525BA2DA4980531 | |||
| 6252 | UnamBinder.exe | C:\Users\admin\Desktop\UnamBinder\UnamBinder\README.txt | text | |
MD5:E5C9AA021D1B344F9EE1575DC90F834B | SHA256:888837FD33A8BCB6E5E15F2017B66B69C3041A6C1718E8DA527DF05544B47922 | |||
| 6272 | crack.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\Windows Driver Fondation.lnk | lnk | |
MD5:3D42676F9AA3D37F2143CE6E7CBCA063 | SHA256:2E0BD5B988DECCCFABE0739FFA8BFDAC8C53086612477FB6BF4678AF0358DF4B | |||
| 6252 | UnamBinder.exe | C:\Users\admin\Desktop\UnamBinder\UnamBinder\UnamBinder V2.0.exe | executable | |
MD5:A6886FBA3A6A16A2F59412DCDBD2AE1C | SHA256:A9D75135B88E4506DE39D75EFB6756B0334E450CF0091E4A9272DA05C4778159 | |||
| 2424 | powershell.exe | C:\Users\admin\AppData\Local\Temp\__PSScriptPolicyTest_e5k1bu0n.5qj.psm1 | text | |
MD5:D17FE0A3F47BE24A6453E9EF58C94641 | SHA256:96AD1146EB96877EAB5942AE0736B82D8B5E2039A80D3D6932665C1A4C87DCF7 | |||
| 6196 | UnamBinder V2.0.exe | C:\Users\admin\AppData\Local\Temp\Windows Driver Fondation.exe | executable | |
MD5:6BBA70ECF767C84AFF30E2F51E3F74EC | SHA256:010B8DB19EAD1BA157738C6DA0D1E5AE38F611AAC56DE325E872E1DC61229CF2 | |||
| 2424 | powershell.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\PowerShell\StartupProfileData-NonInteractive | binary | |
MD5:449BA96A3A1C2379331844F085CF42AB | SHA256:AE40B0EA3C56B9CF1C5E1C1E3B01E49A8E75EF8F106F779409474C6F94D1EFCD | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6808 | backgroundTaskHost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
2608 | svchost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
5336 | SearchApp.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
2608 | svchost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
6860 | backgroundTaskHost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
5028 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
3888 | svchost.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
1164 | RUXIMICS.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
2120 | MoUsoCoreWorker.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5028 | svchost.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
5336 | SearchApp.exe | 2.23.209.156:443 | www.bing.com | Akamai International B.V. | GB | unknown |
5336 | SearchApp.exe | 192.229.221.95:80 | ocsp.digicert.com | EDGECAST | US | whitelisted |
2608 | svchost.exe | 40.126.32.133:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | unknown |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
login.live.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
th.bing.com |
| whitelisted |
fd.api.iris.microsoft.com |
| whitelisted |
arc.msn.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2256 | svchost.exe | Misc activity | ET INFO DYNAMIC_DNS Query to *.duckdns. Domain |
2256 | svchost.exe | Potentially Bad Traffic | ET INFO DYNAMIC_DNS Query to a *.duckdns .org Domain |
2256 | svchost.exe | Potentially Bad Traffic | ET INFO DYNAMIC_DNS Query to a *.duckdns .org Domain |
2256 | svchost.exe | Misc activity | ET INFO DYNAMIC_DNS Query to *.duckdns. Domain |
2256 | svchost.exe | Potentially Bad Traffic | ET INFO DYNAMIC_DNS Query to a *.duckdns .org Domain |
2256 | svchost.exe | Misc activity | ET INFO DYNAMIC_DNS Query to *.duckdns. Domain |