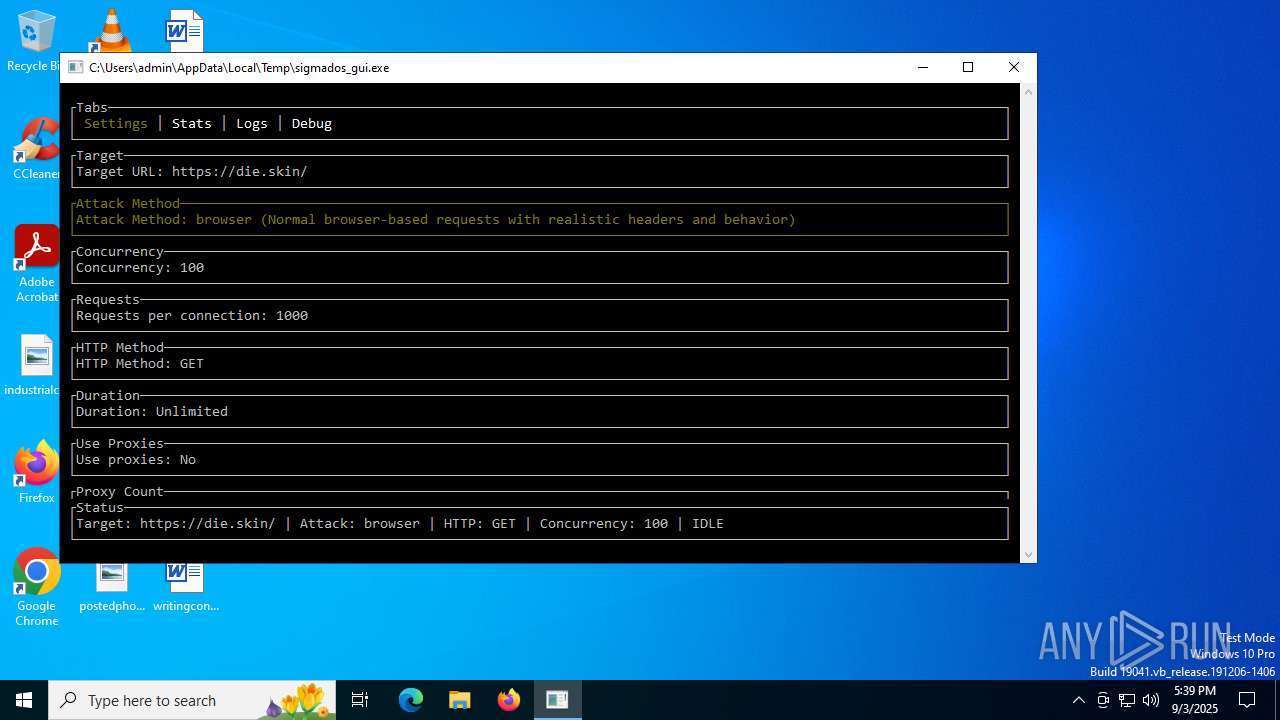
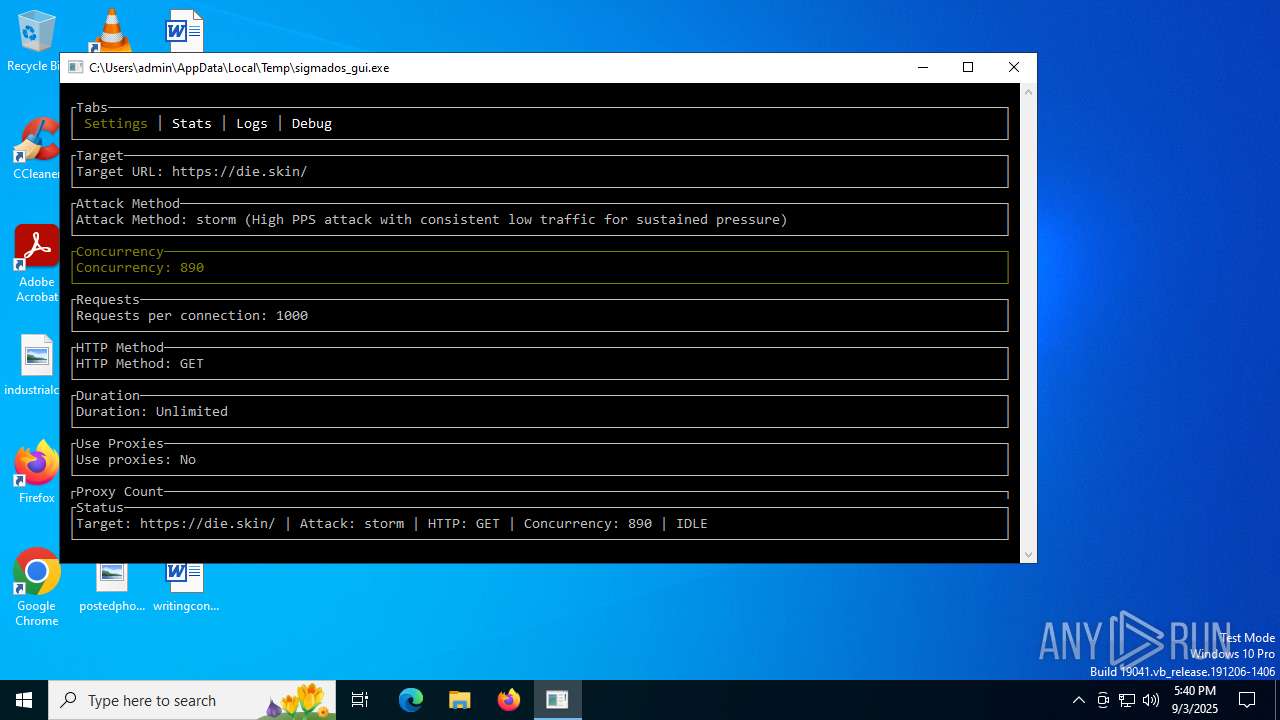
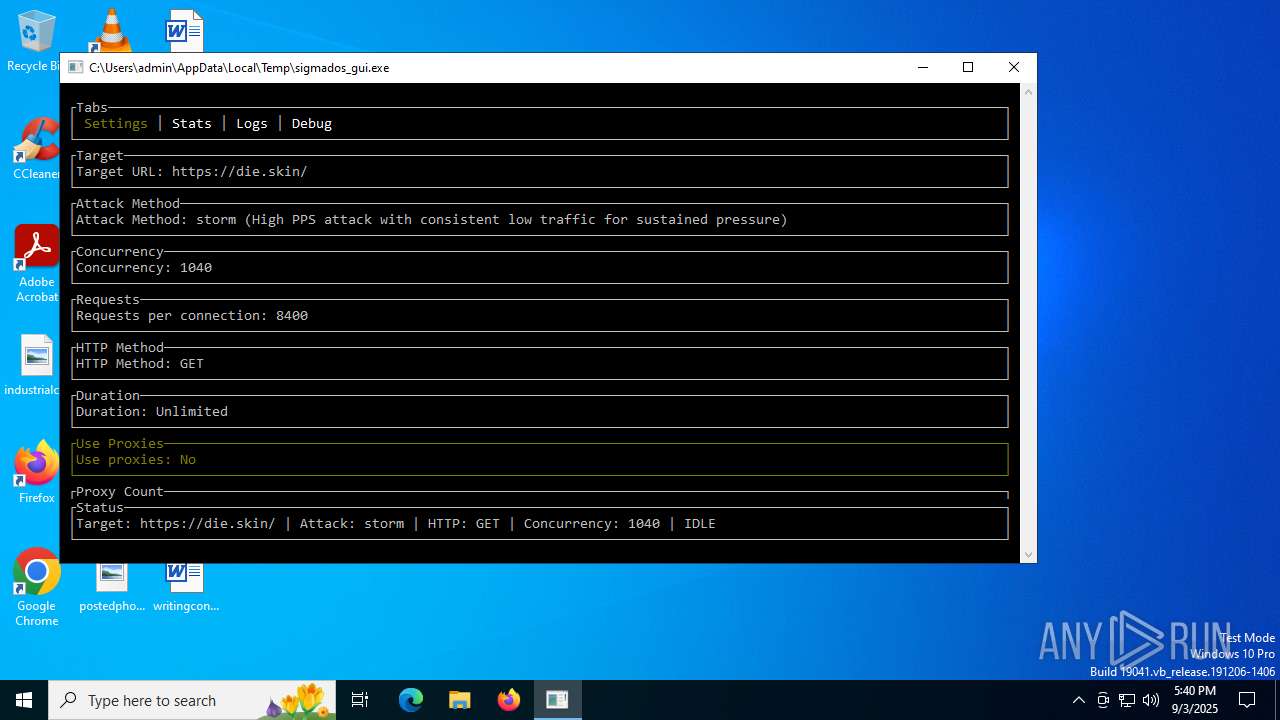
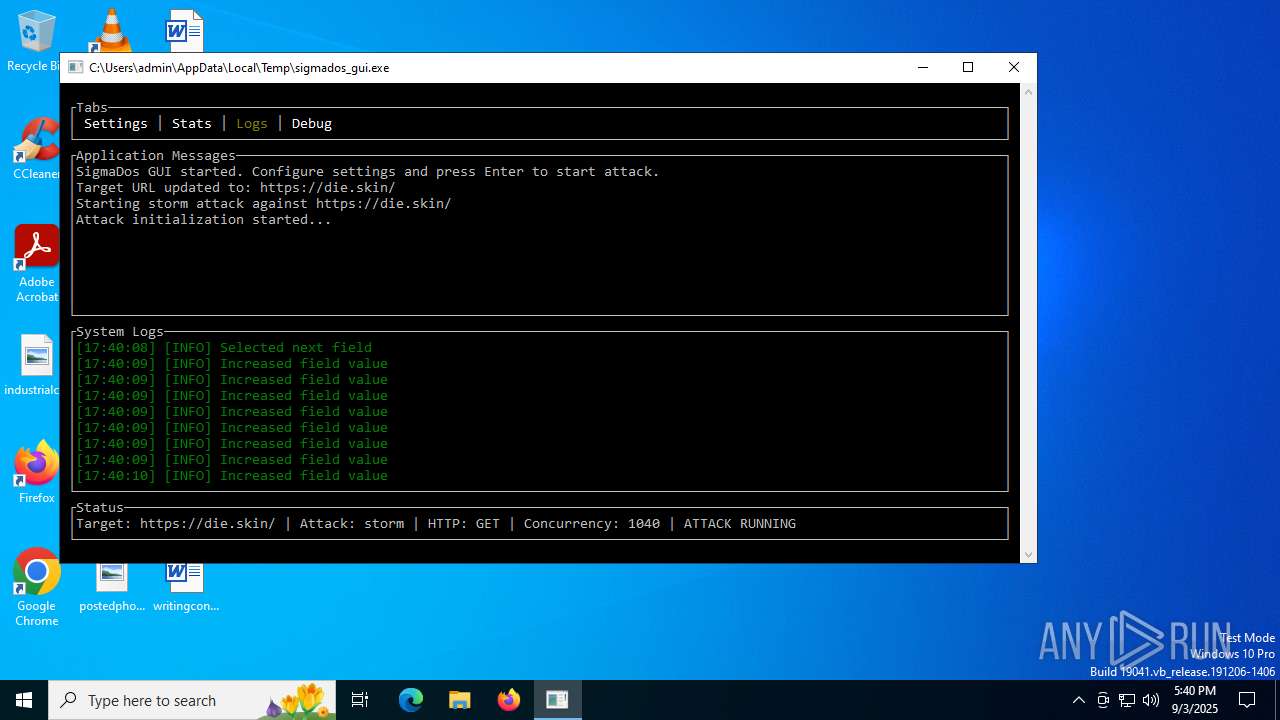
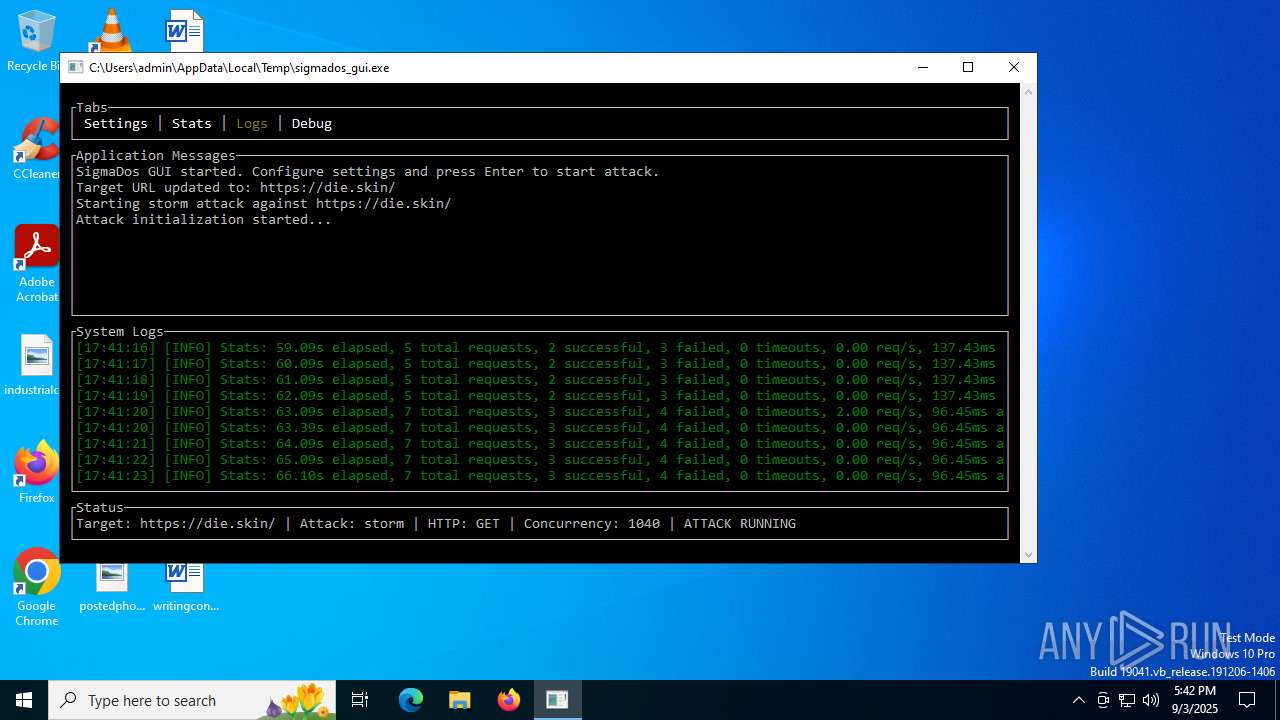
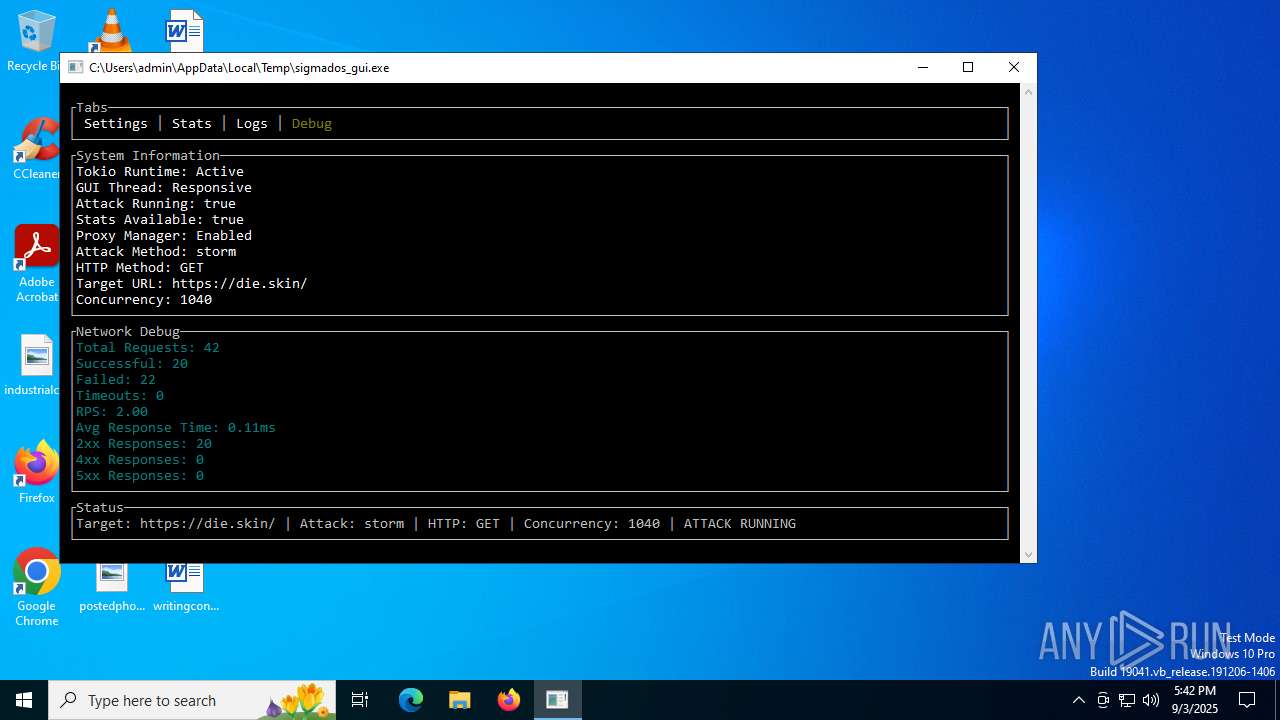
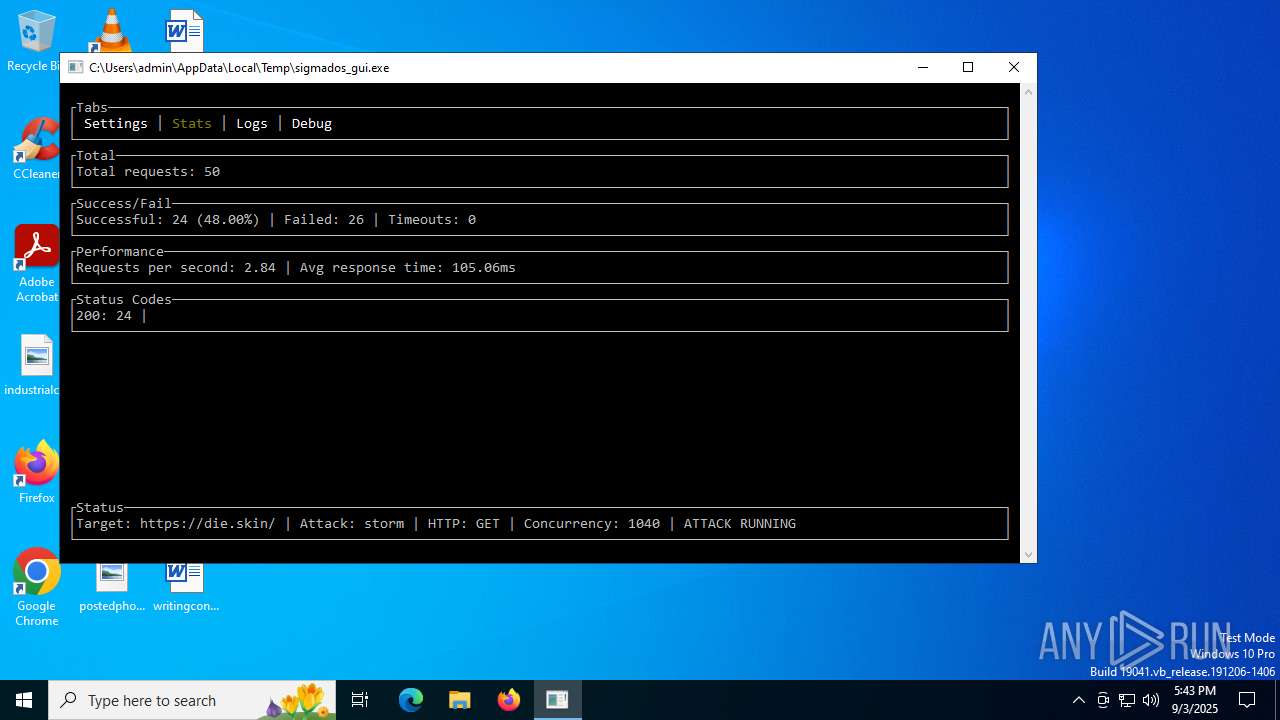
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
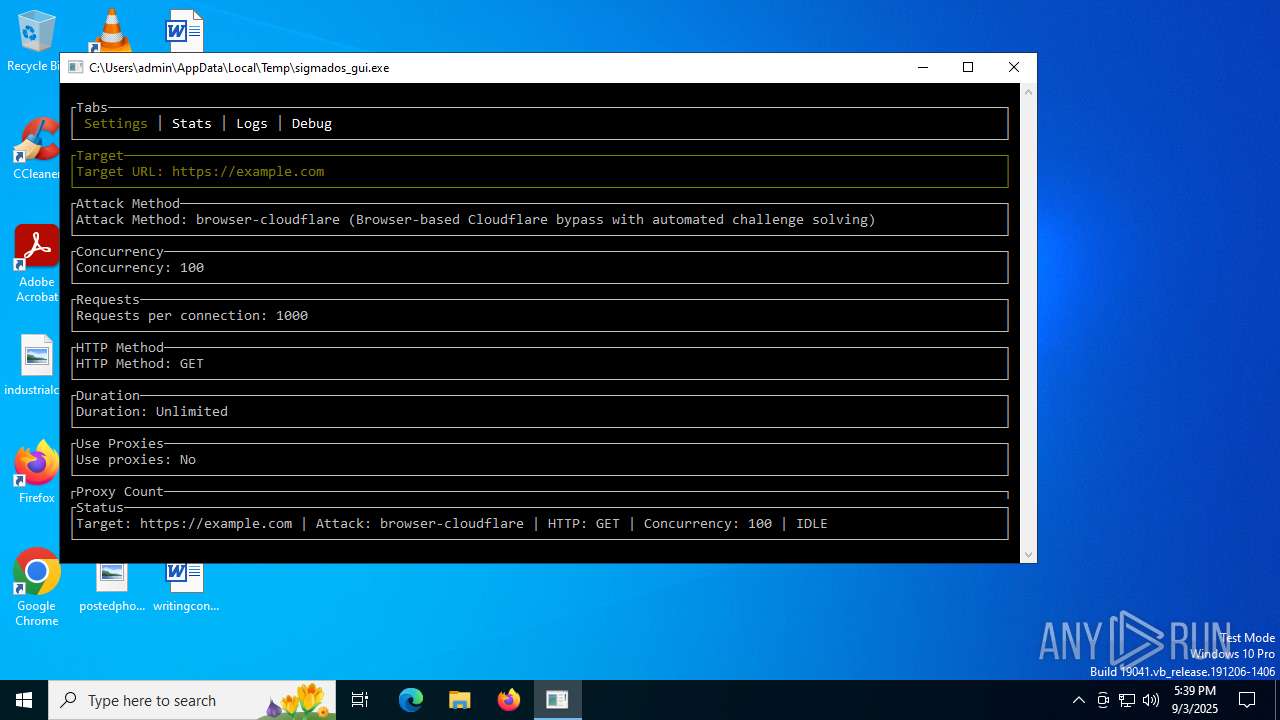
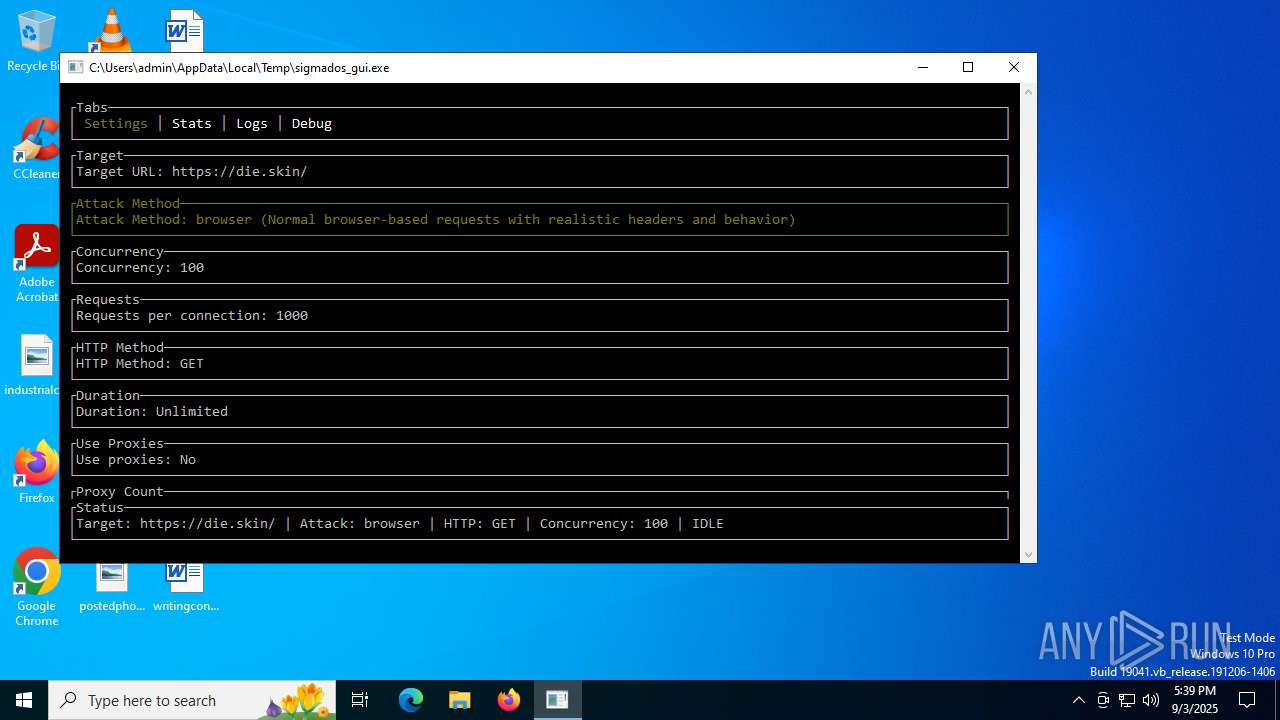
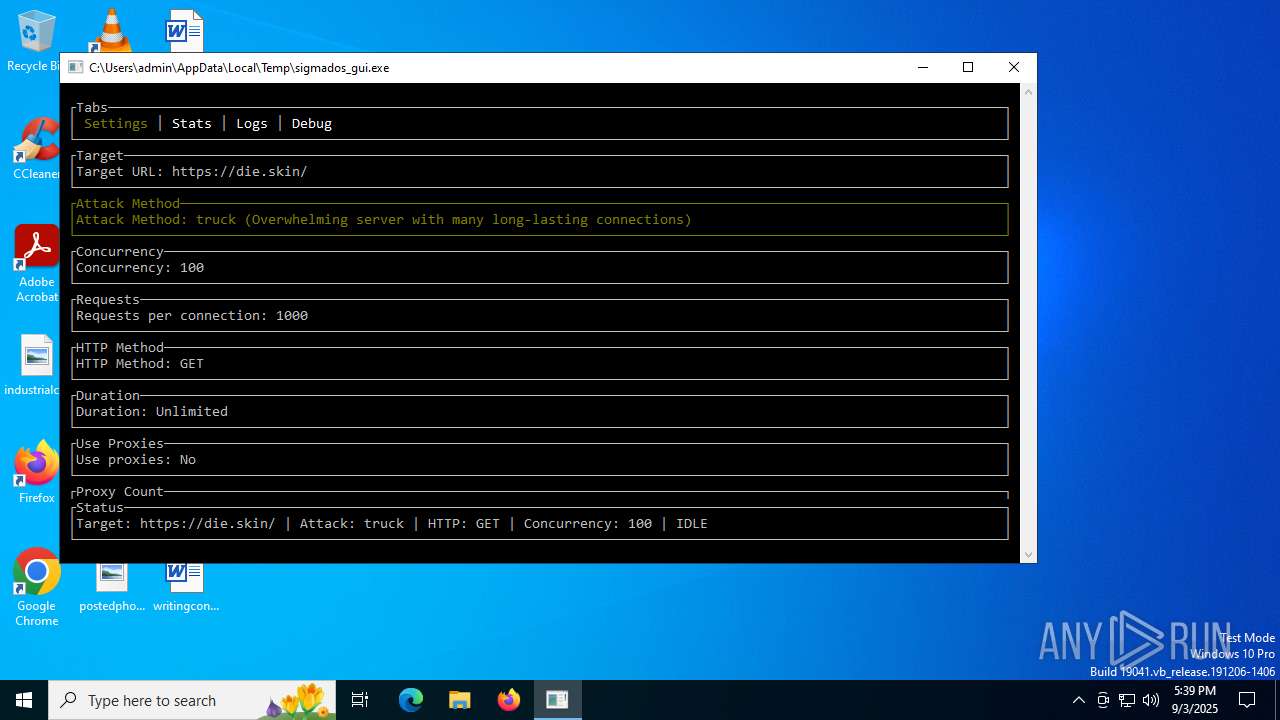
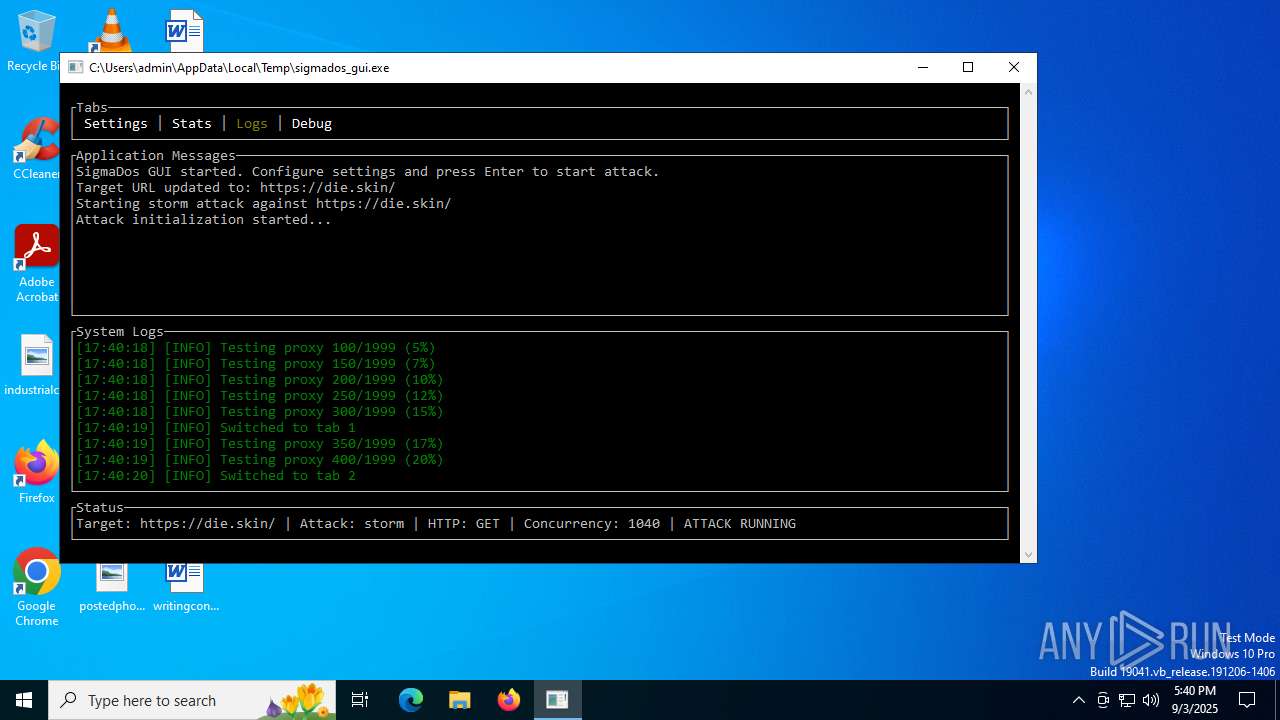
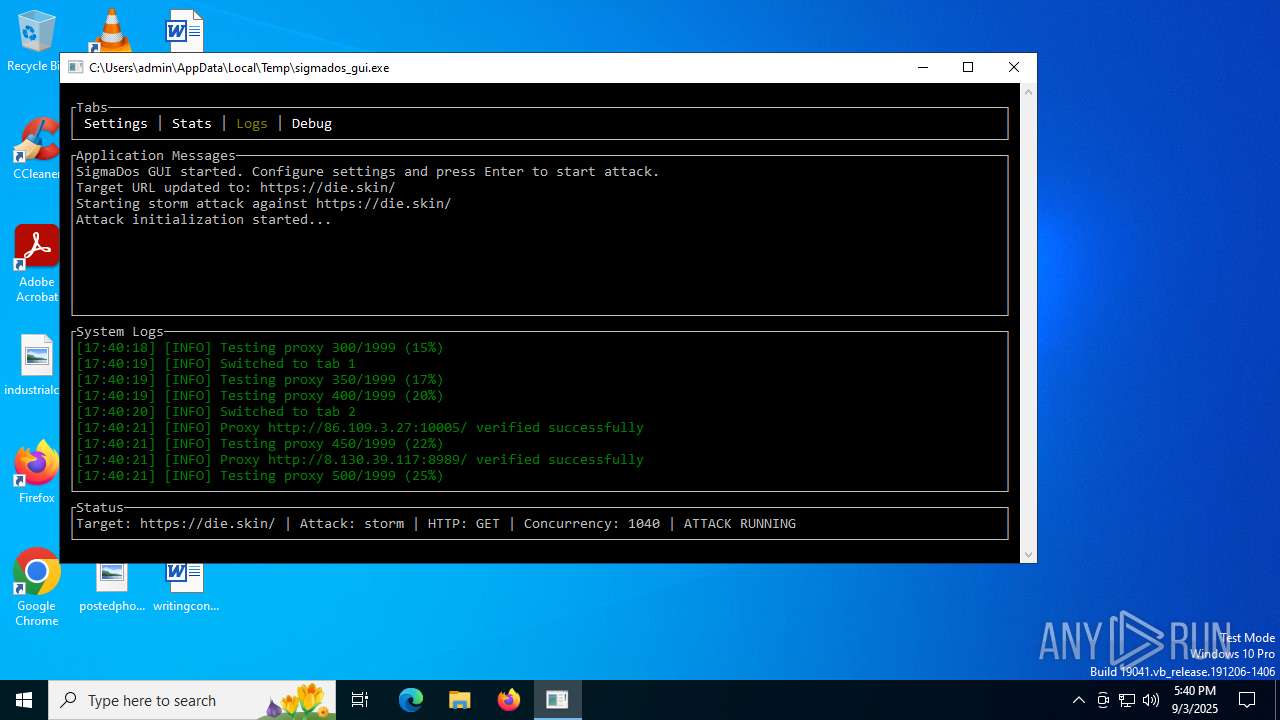
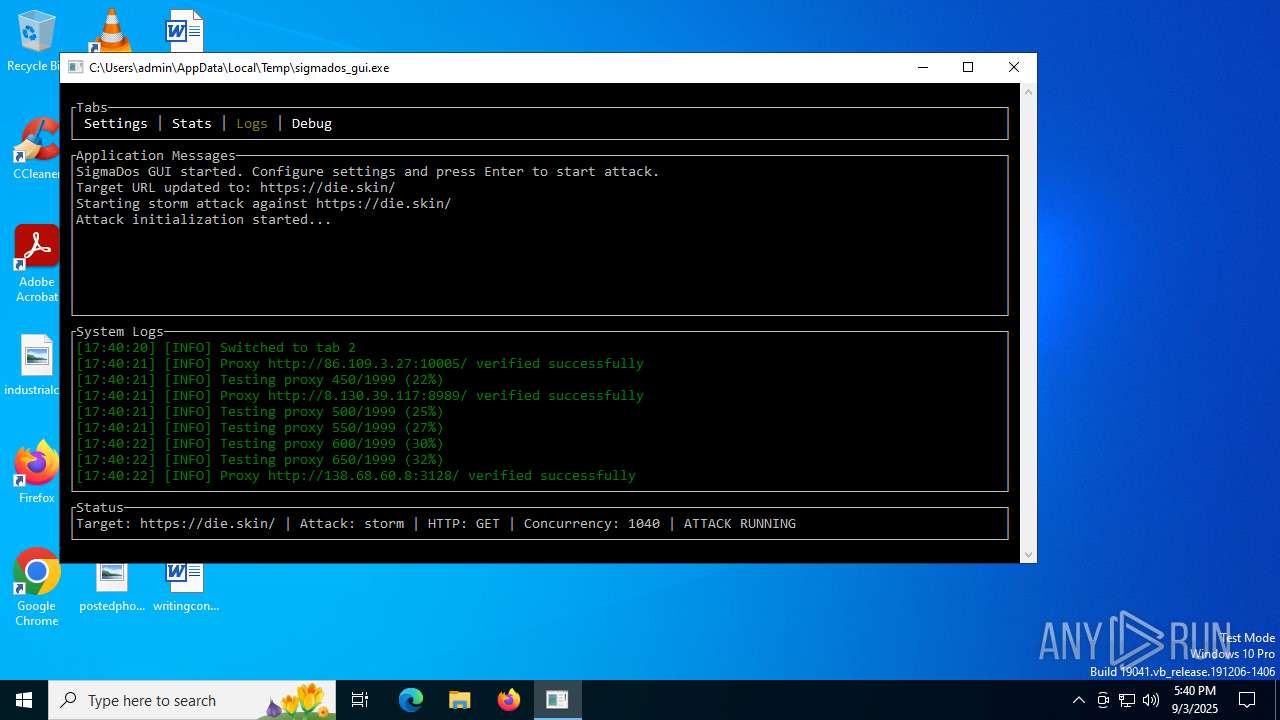
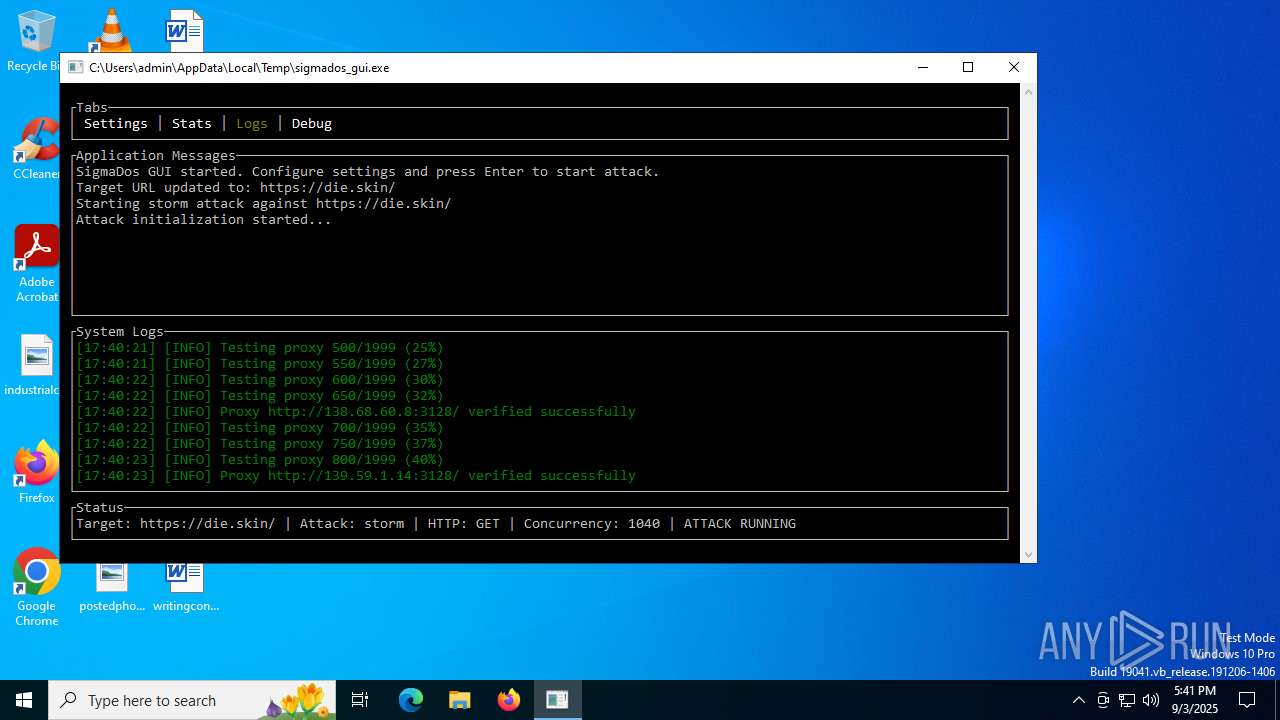
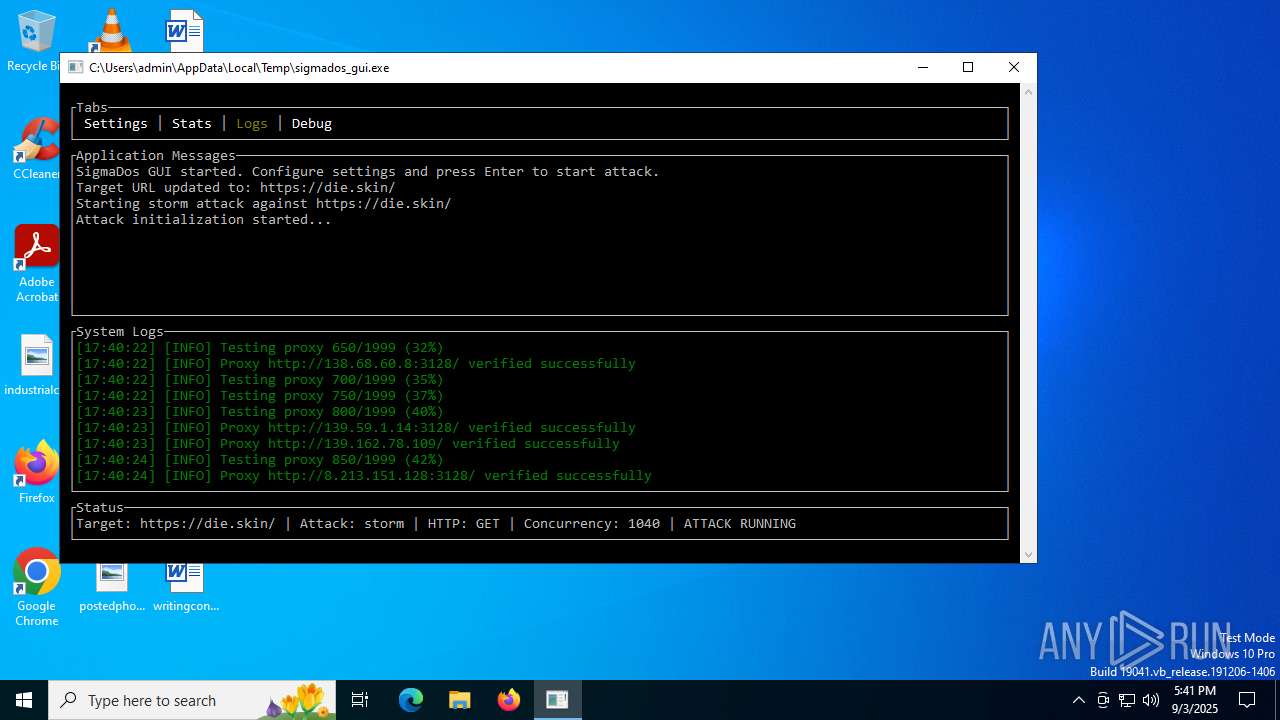
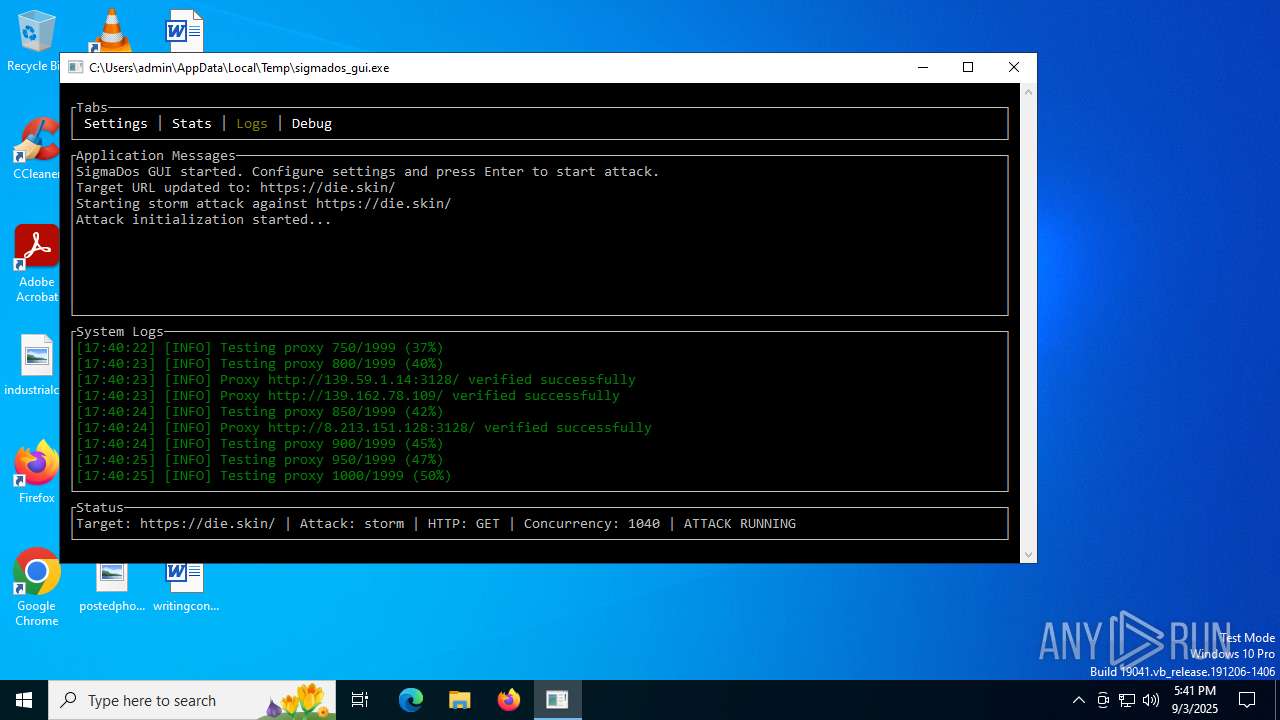
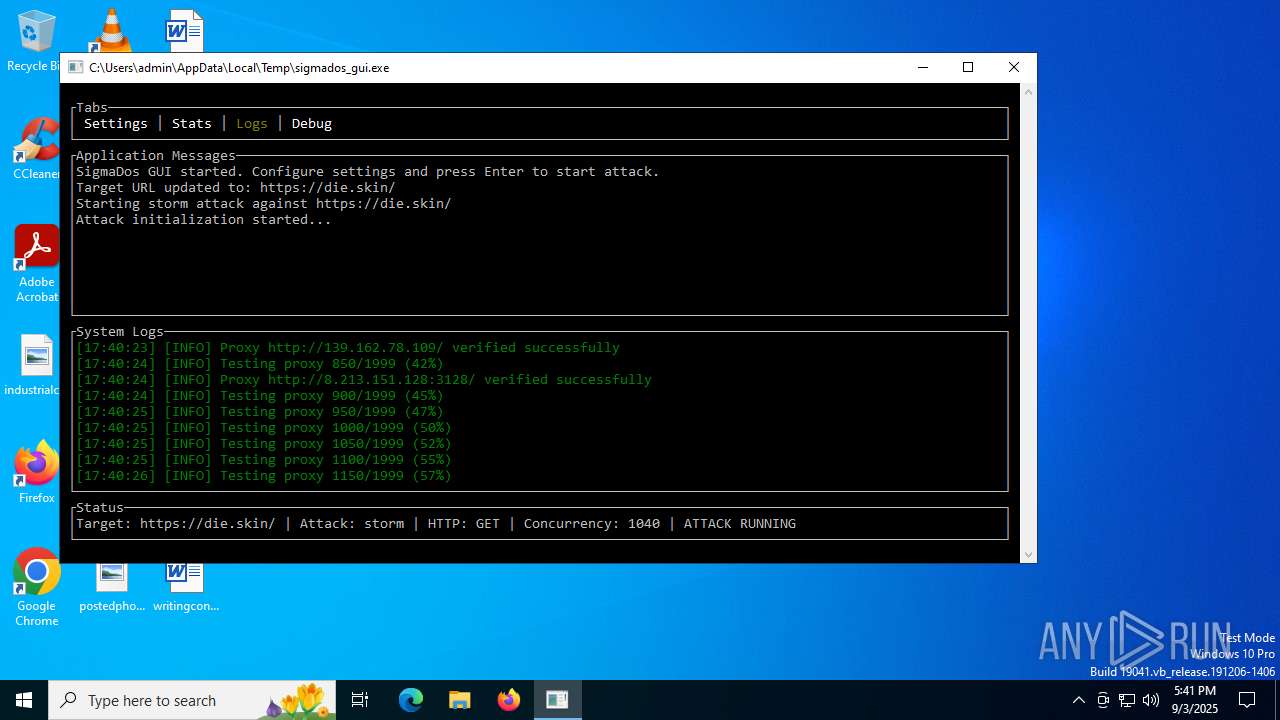
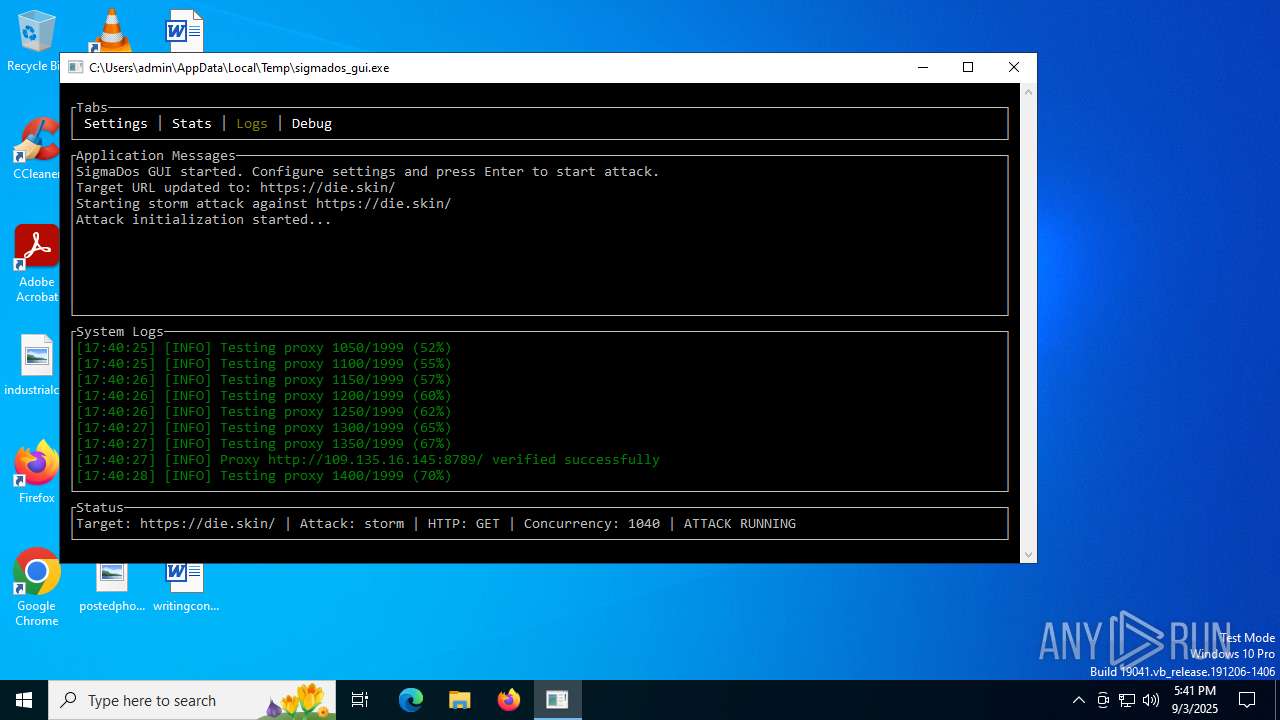
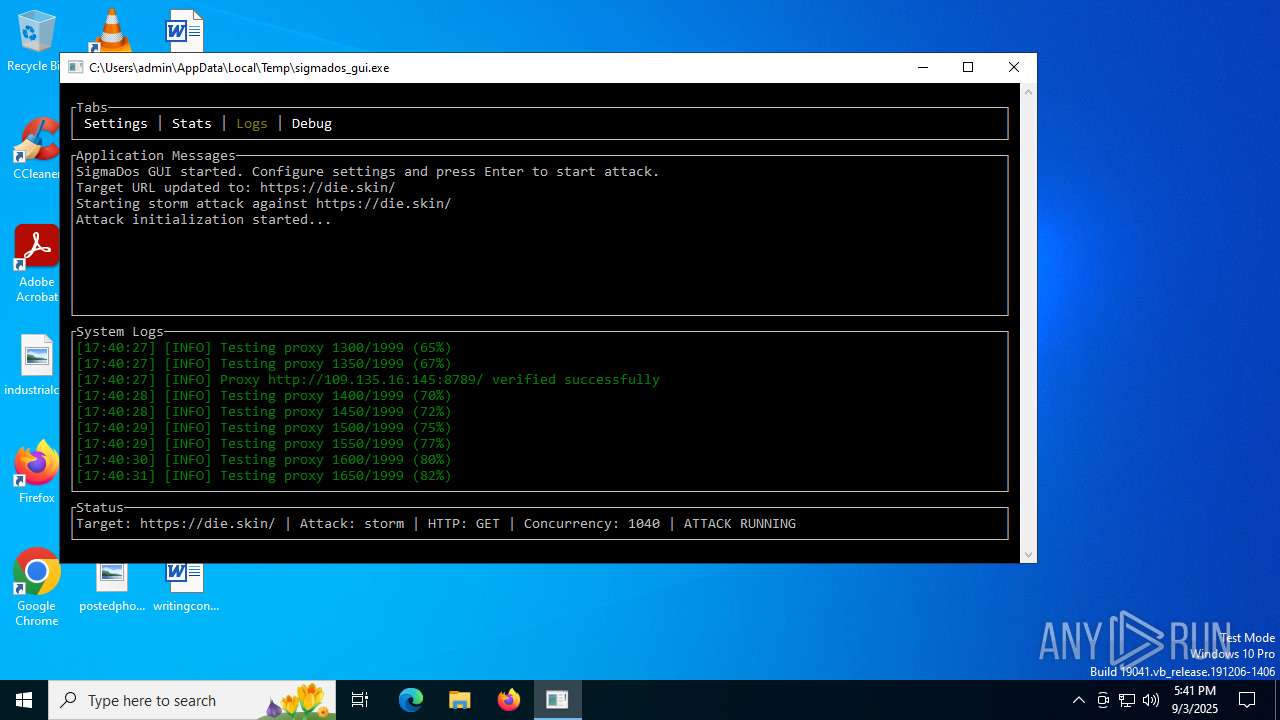
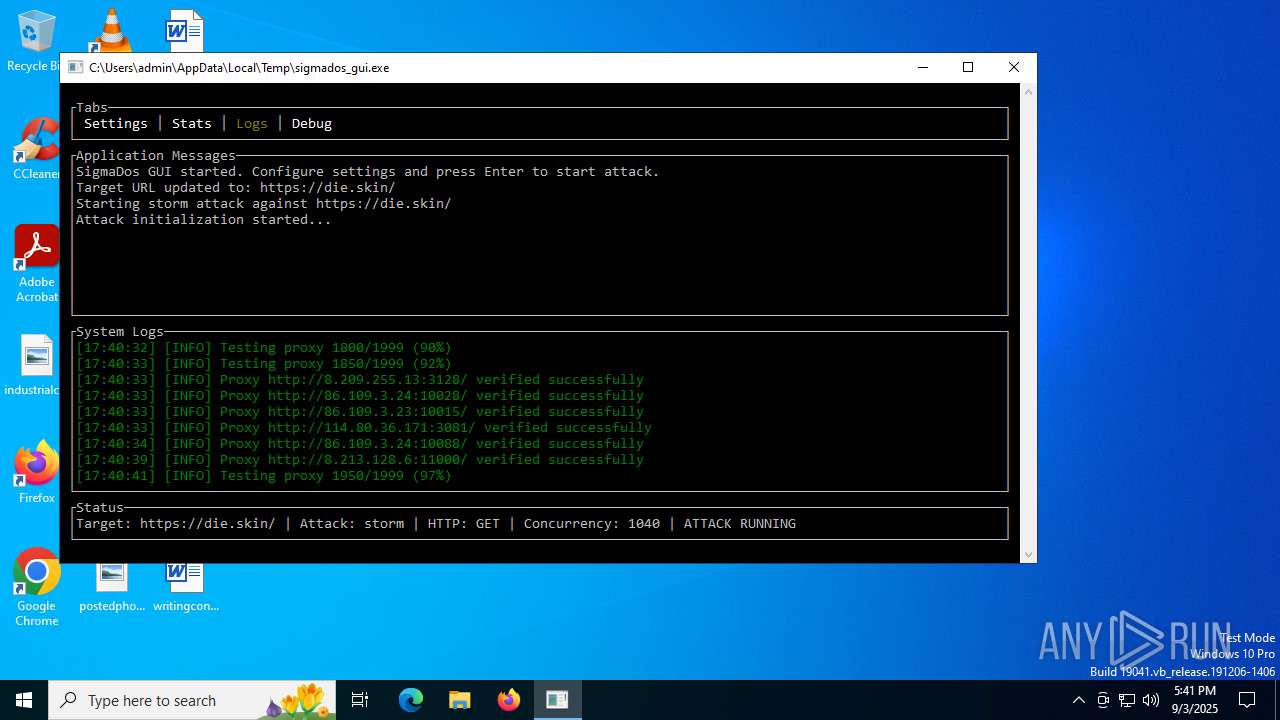
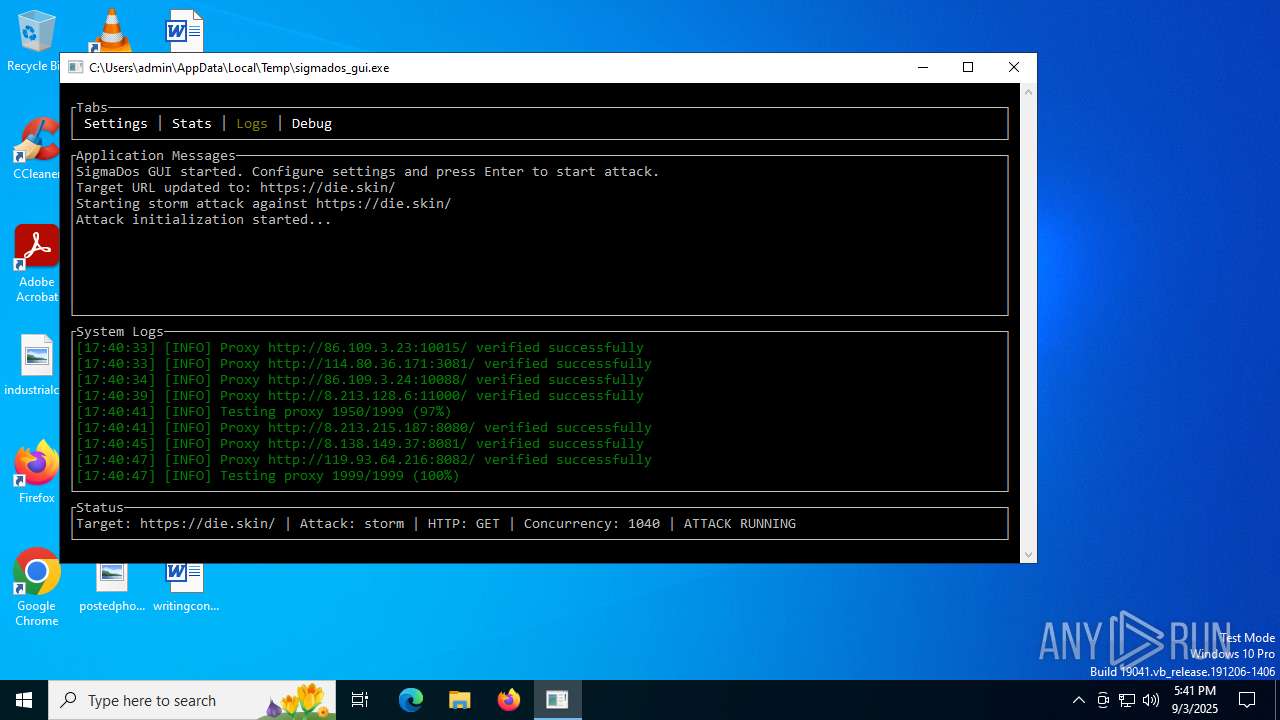
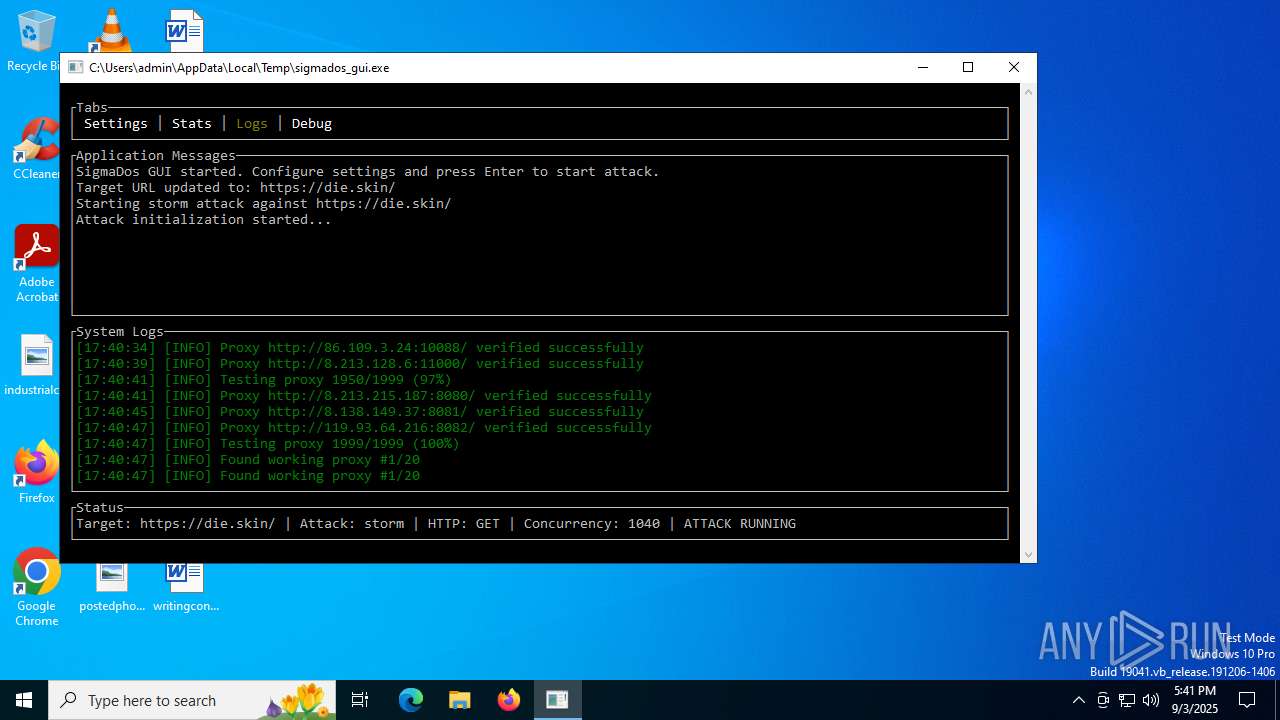
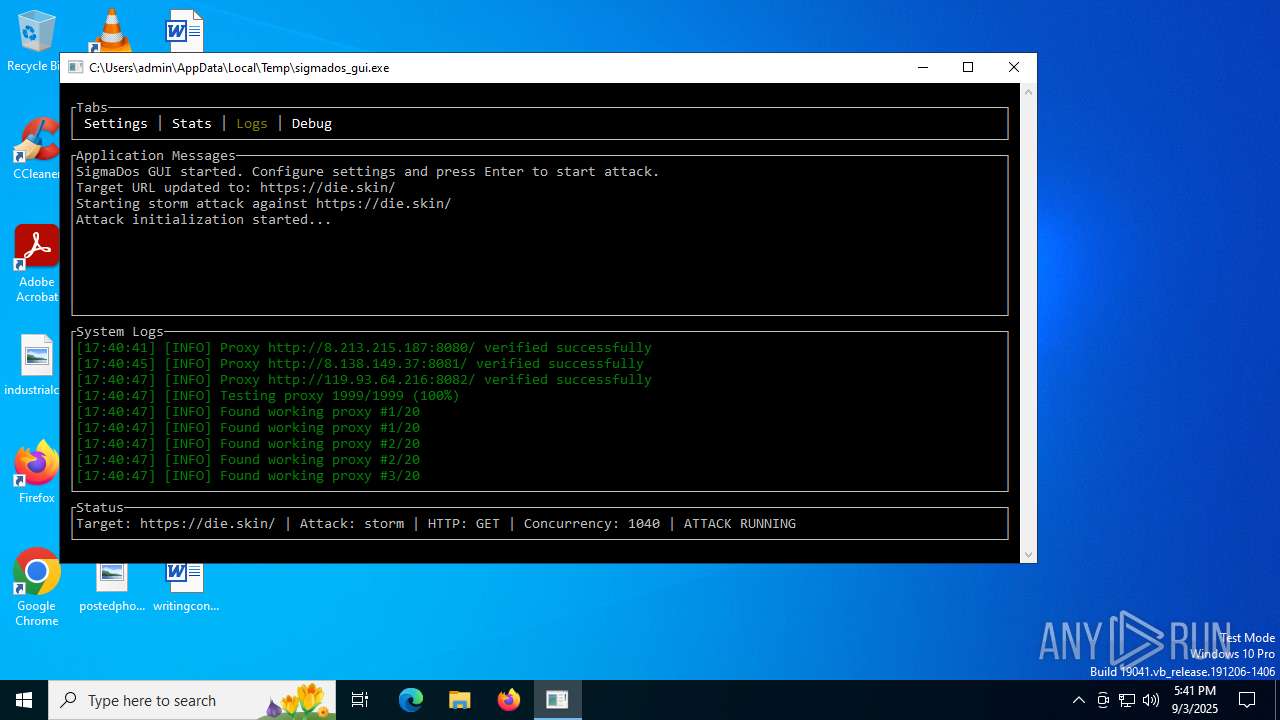
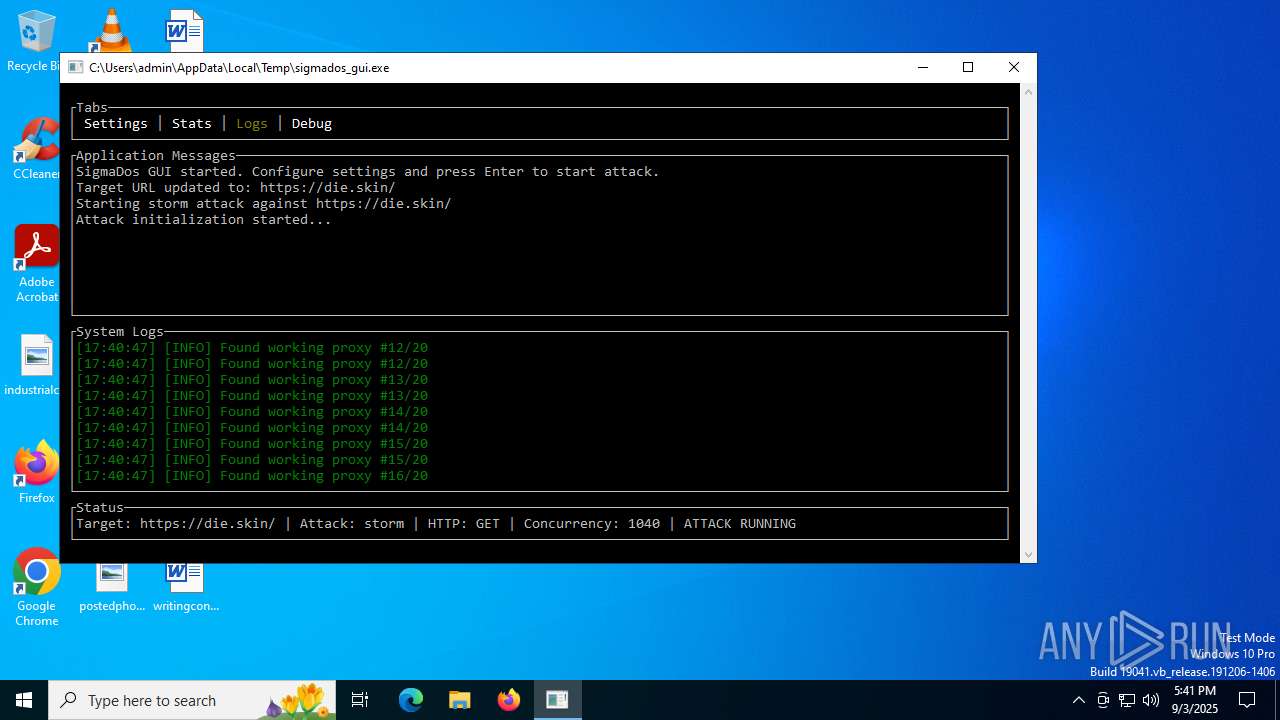
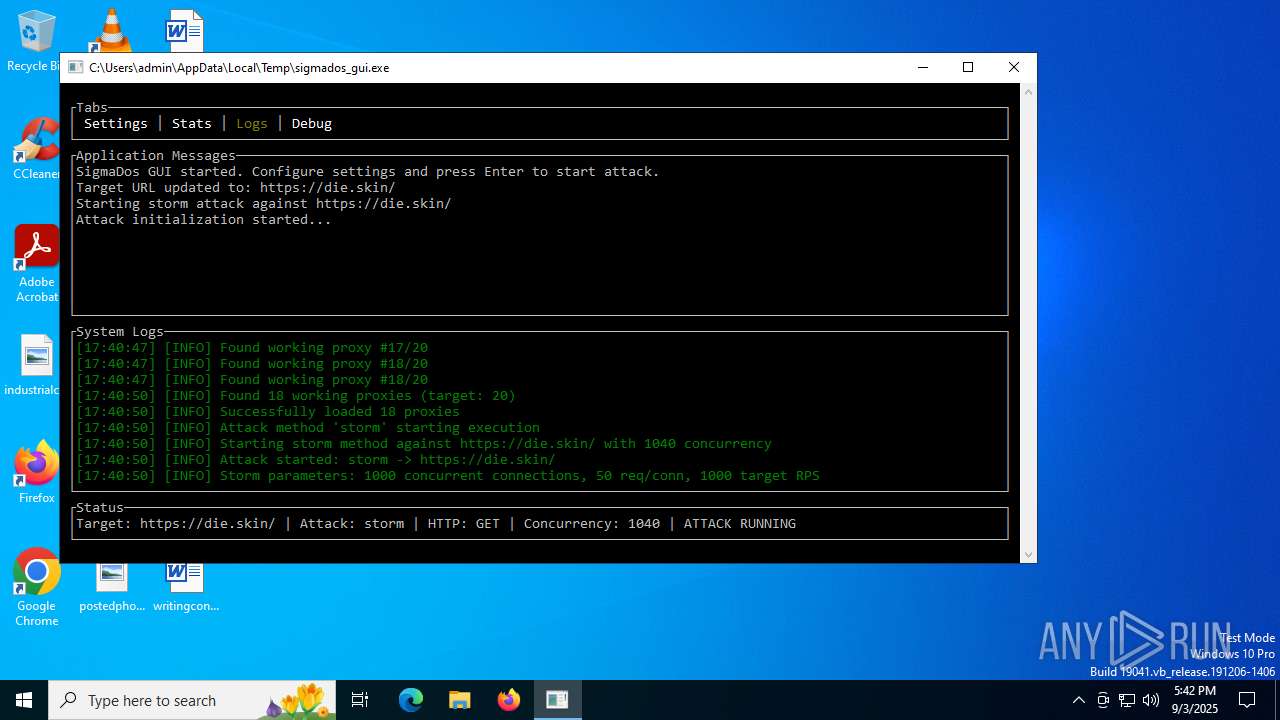
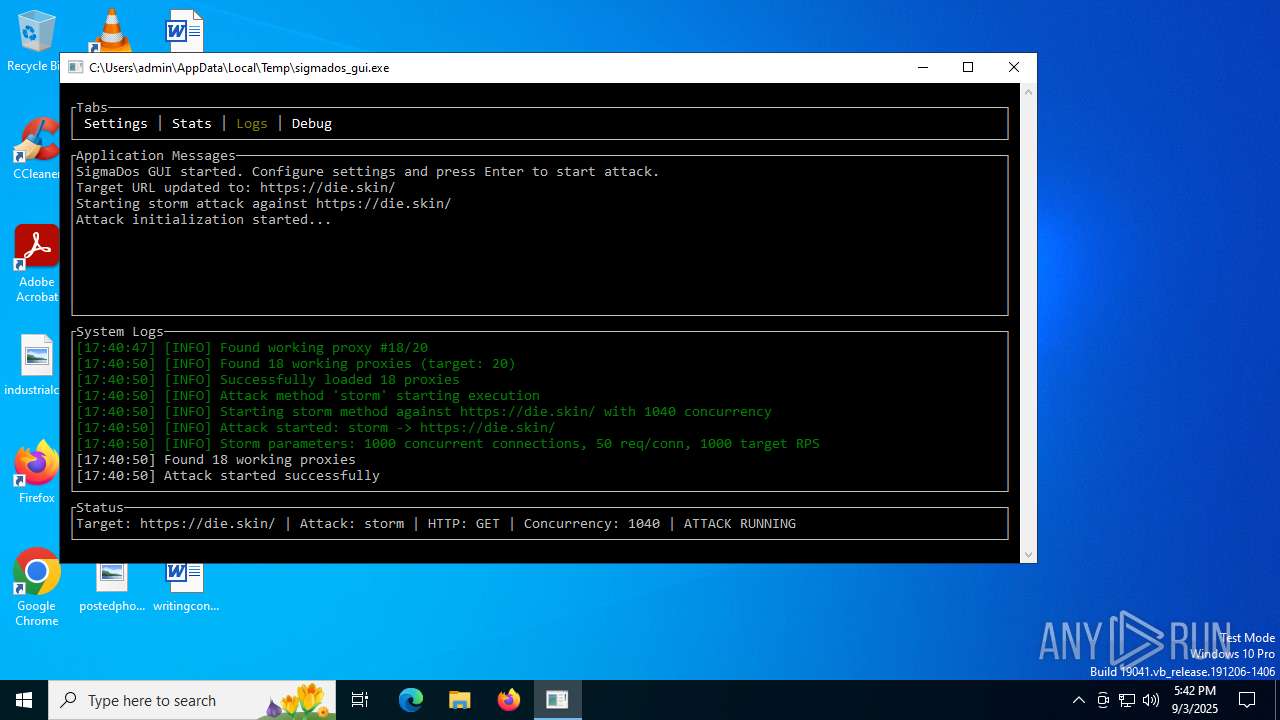
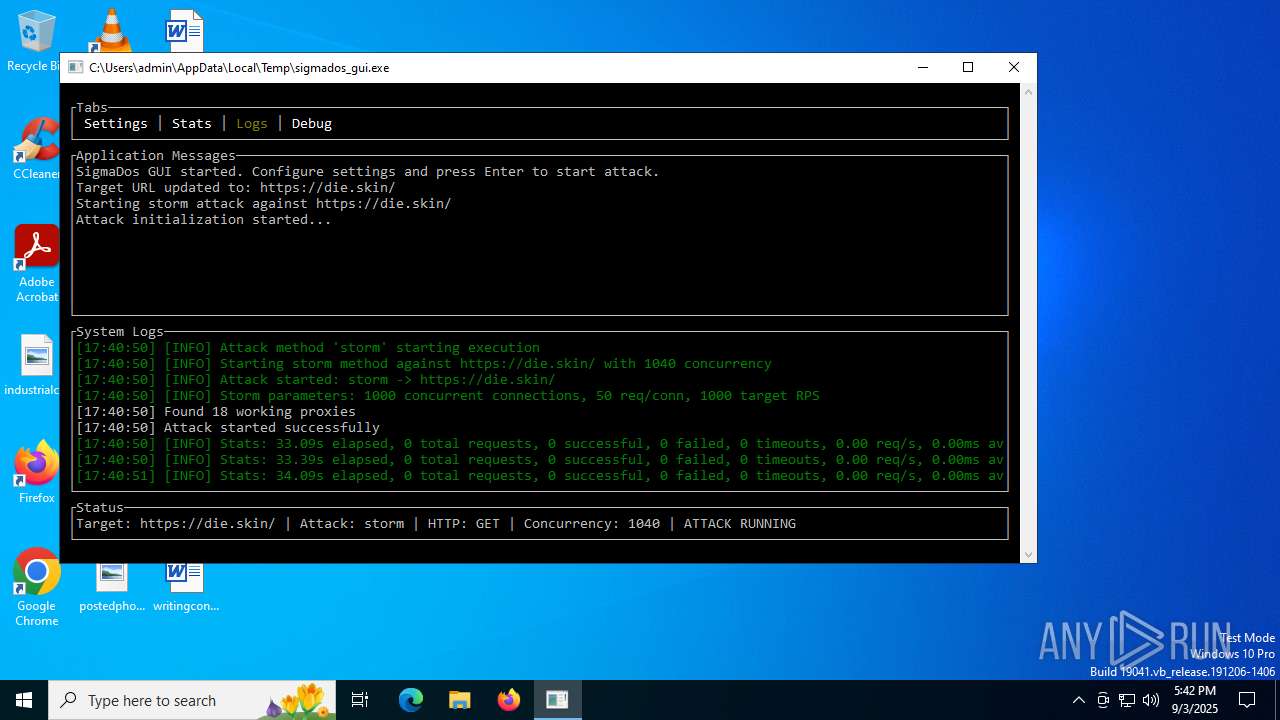
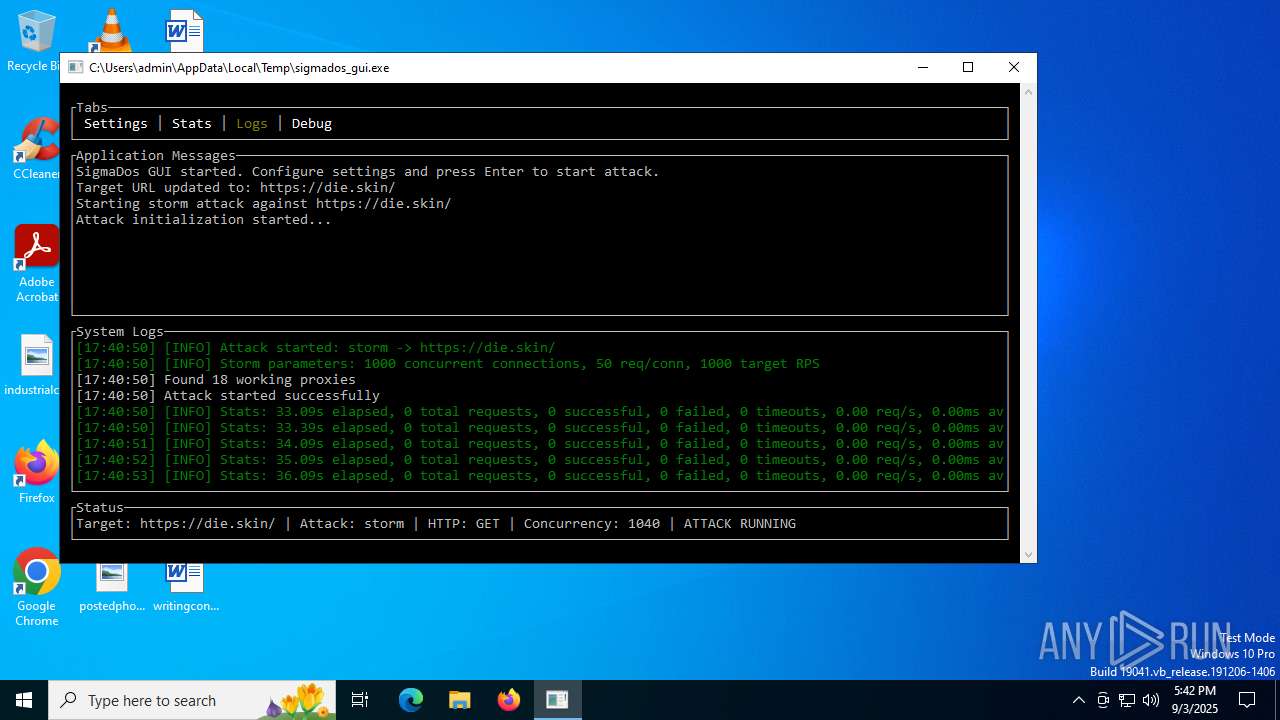
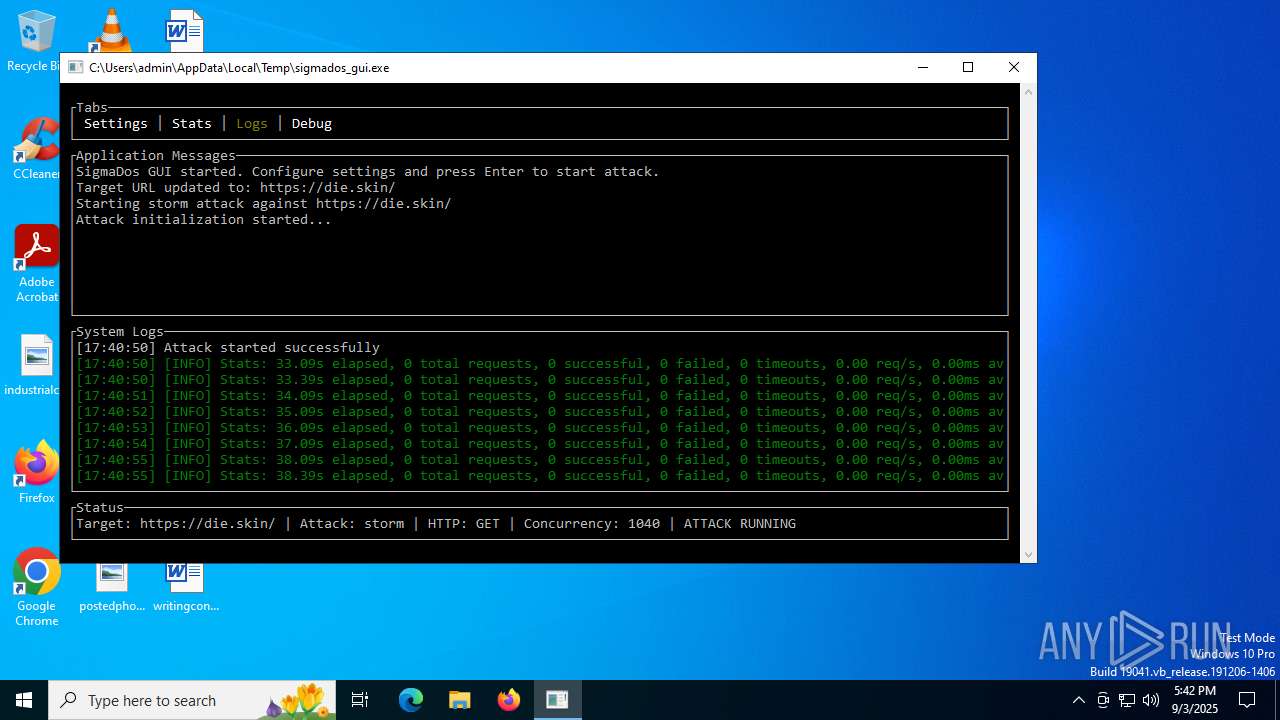
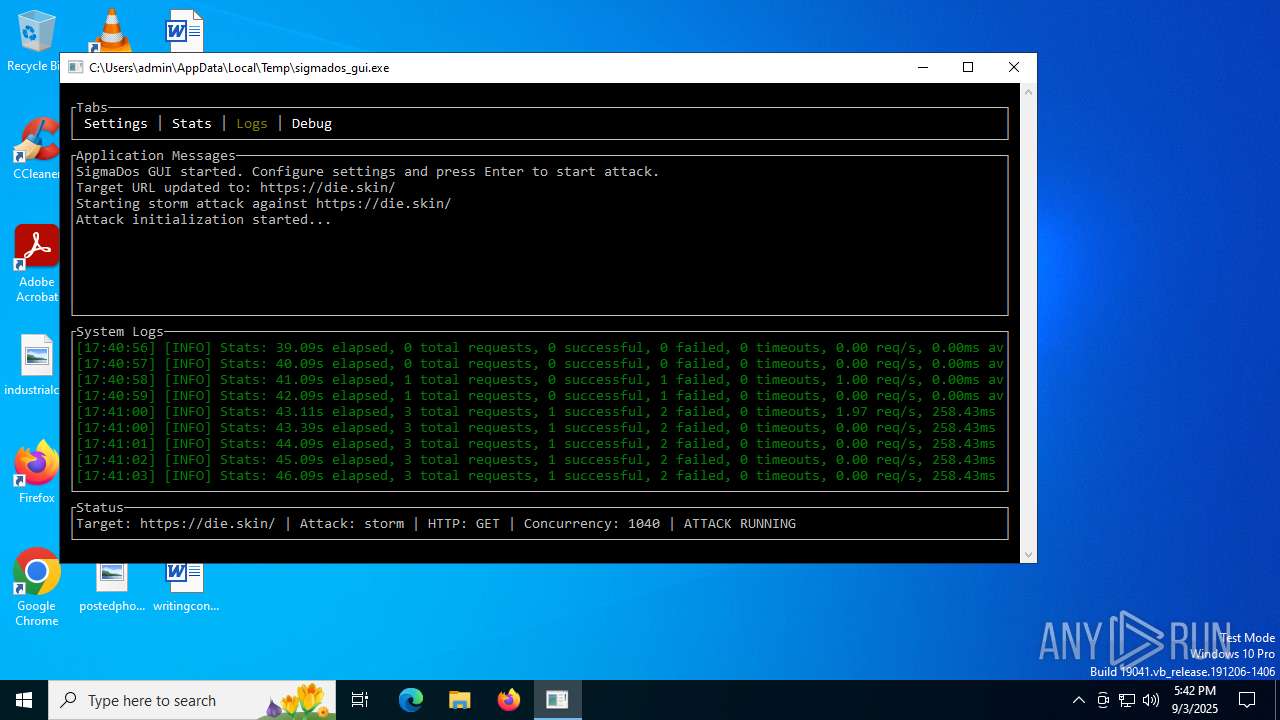
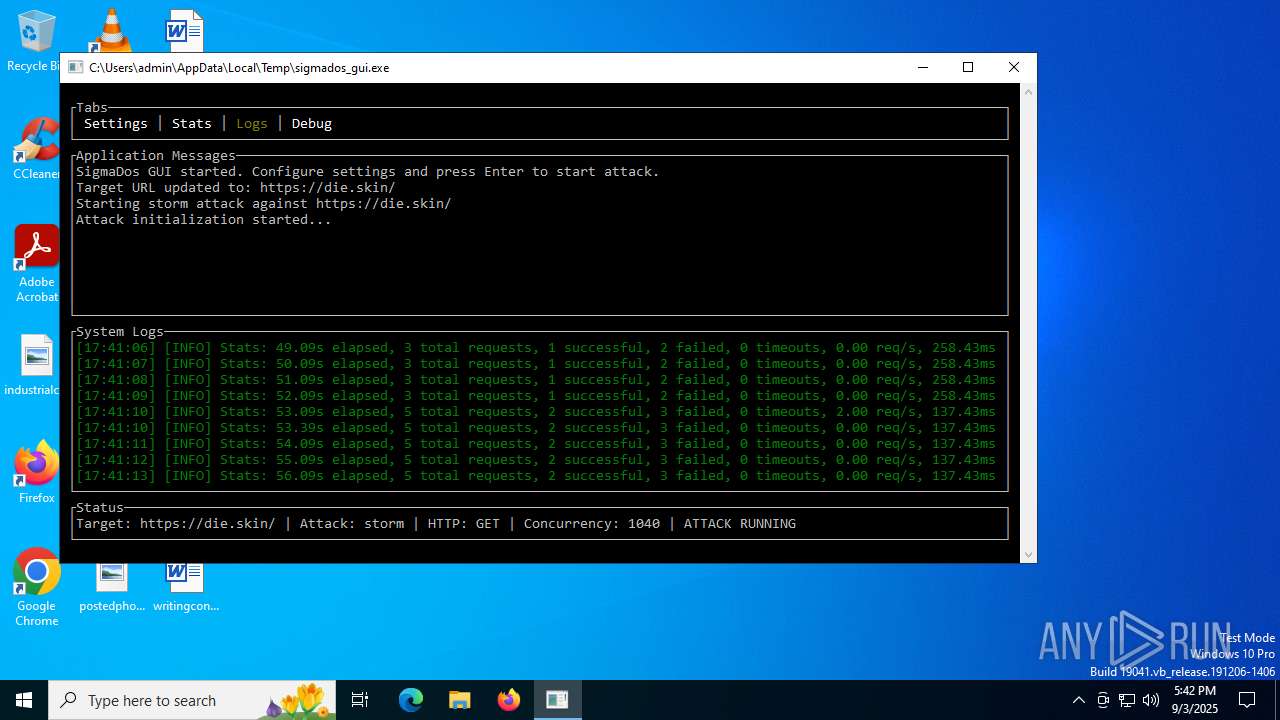
| File name: | sigmados_gui.exe |
| Full analysis: | https://app.any.run/tasks/71ed9cd4-b8d5-410c-a963-9a9fead690b8 |
| Verdict: | Malicious activity |
| Analysis date: | September 03, 2025, 17:39:10 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (console) x86-64, for MS Windows, 5 sections |
| MD5: | 82A88D4C68E609EA9DE50D6179DDB6FF |
| SHA1: | 5A876813D3E45F00E97158506A16462BC63F307E |
| SHA256: | DAC583013A661B2A371609BB75DA8640C01DC32DC0BDB3F42756998B8FBD819F |
| SSDEEP: | 98304:n1rVKYQ2cQDPBjgdmKVLLqSHGKkdfLO6HUFFxkRNYwRyTTgR8V6eieOu4lgulBvF:JJcAbRyTTgY6WiTcXjT3Y2h+ijt |
| .exe | | | Win64 Executable (generic) (87.3) |
|---|---|---|
| .exe | | | Generic Win/DOS Executable (6.3) |
| .exe | | | DOS Executable Generic (6.3) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2025:09:03 17:16:49+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.44 |
| CodeSize: | 10499072 |
| InitializedDataSize: | 4668416 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x9e4a74 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows command line |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1056 | "C:\Users\admin\AppData\Local\Temp\sigmados_gui.exe" | C:\Users\admin\AppData\Local\Temp\sigmados_gui.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Modules
| |||||||||||||||
| 2200 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3888 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4724 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | sigmados_gui.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6524 | SIHClient.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Update%20Secure%20Server%20CA%202.1.crl | NL | binary | 407 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 814 b | whitelisted |
1268 | svchost.exe | GET | 200 | 23.216.77.28:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 216.205.52.172:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 141.101.120.148:80 | http://www.google.com:80 | unknown | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 216.205.52.115:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 102.177.176.84:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 108.162.192.95:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 108.162.193.188:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
1056 | sigmados_gui.exe | CONNECT | 400 | 216.205.52.212:80 | http://www.google.com:80 | US | html | 155 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
5944 | MoUsoCoreWorker.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5504 | RUXIMICS.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
1268 | svchost.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
3644 | svchost.exe | 40.126.31.128:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
3644 | svchost.exe | 2.17.190.73:80 | ocsp.digicert.com | AKAMAI-AS | DE | whitelisted |
1268 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1268 | svchost.exe | 23.216.77.28:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1268 | svchost.exe | 23.35.229.160:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
1056 | sigmados_gui.exe | Potentially Bad Traffic | ET INFO HTTP traffic on port 443 (CONNECT) |