ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | Luczystrap.exe |
| Full analysis: | https://app.any.run/tasks/31a35a9f-c70a-42bf-a180-2a2733f15f77 |
| Verdict: | Malicious activity |
| Analysis date: | November 08, 2025, 21:57:57 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (GUI) x86-64, for MS Windows, 10 sections |
| MD5: | 3C9C66D70BD0E4F260BAA74EC9108EEA |
| SHA1: | C4EA77FD838EA882716515AAE5548999CB2252FA |
| SHA256: | D71C31057677BC392F680C6303DCFDA9FA8F366240284DAC6D5A14F7CC352424 |
| SSDEEP: | 393216:3U4FNAGOicBQlKd7L9NvtiNFoL0Fn1jioDTfVL8pAU9TZyaerkBrsuLAZBWF2:3vNAti0nNvtfqjLDTmTEdQBrJkQ2 |
| .exe | | | Generic Win/DOS Executable (50) |
|---|---|---|
| .exe | | | DOS Executable Generic (49.9) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2025:09:25 19:23:21+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.44 |
| CodeSize: | 6348288 |
| InitializedDataSize: | 3501568 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x5c30d0 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 1.4.9.0 |
| ProductVersionNumber: | 1.4.9.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Neutral |
| CharacterSet: | Unicode |
| CompanyName: | Luczystrap |
| FileDescription: | Luczystrap |
| FileVersion: | 1.4.9 |
| InternalName: | Luczystrap.dll |
| LegalCopyright: | |
| OriginalFileName: | Luczystrap.dll |
| ProductName: | Luczystrap |
| ProductVersion: | 1.4.9 |
| AssemblyVersion: | 1.4.9.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 6992 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
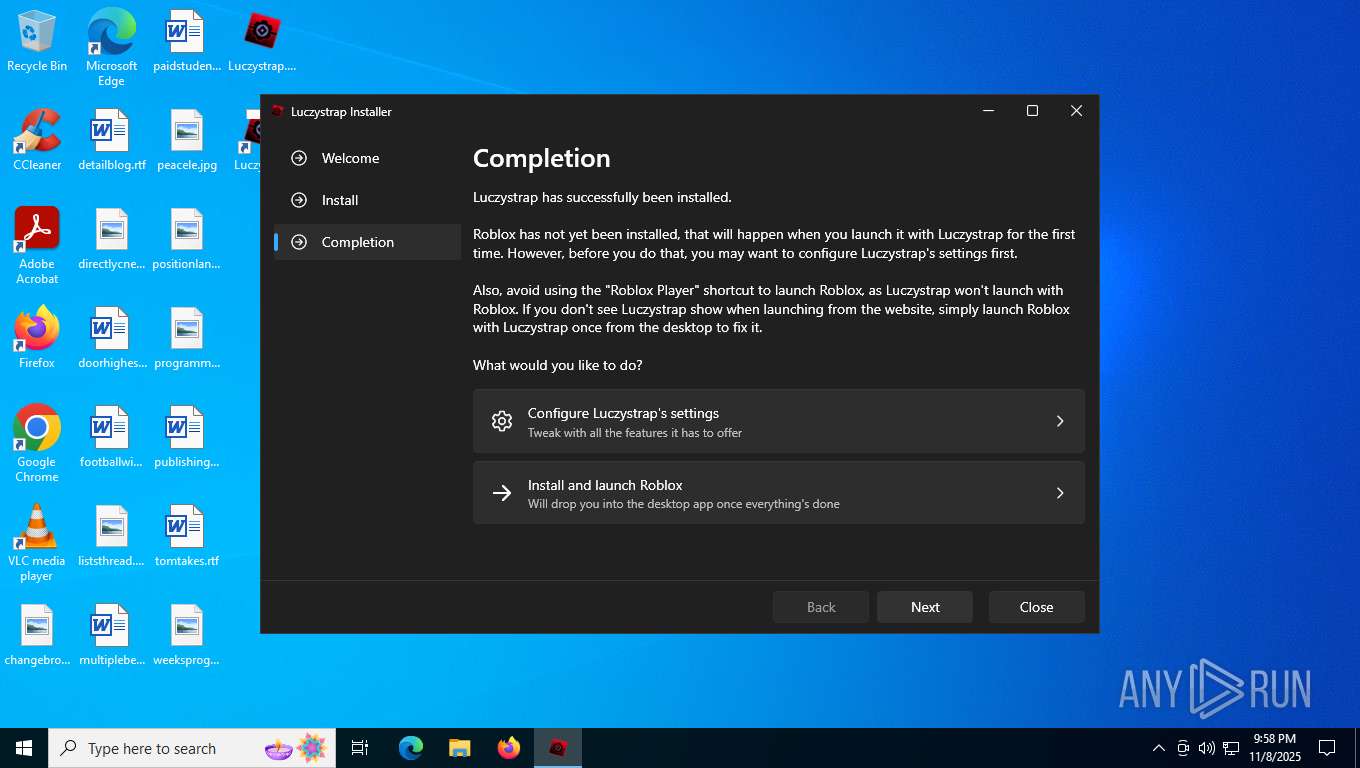
| 7888 | "C:\Users\admin\Desktop\Luczystrap.exe" | C:\Users\admin\Desktop\Luczystrap.exe | explorer.exe | ||||||||||||
User: admin Company: Luczystrap Integrity Level: MEDIUM Description: Luczystrap Version: 1.4.9 Modules
ims-api(PID) Process(7888) Luczystrap.exe Discord-Webhook-Tokens (1)1435648454318887056/q5OwTDzKE-uqT6iP0KzzJr0Y4kiyXvB0KpjJljbNYLVfMoXkYQv7wr_gFNyriq4yh7A5 Discord-Info-Links 1435648454318887056/q5OwTDzKE-uqT6iP0KzzJr0Y4kiyXvB0KpjJljbNYLVfMoXkYQv7wr_gFNyriq4yh7A5 Get Webhook Infohttps://discord.com/api/webhooks/1435648454318887056/q5OwTDzKE-uqT6iP0KzzJr0Y4kiyXvB0KpjJljbNYLVfMoXkYQv7wr_gFNyriq4yh7A5 | |||||||||||||||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | DisplayIcon |
Value: C:\Users\admin\AppData\Local\Luczystrap\Luczystrap.exe,0 | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | DisplayName |
Value: Luczystrap | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | DisplayVersion |
Value: 1.4.9.0 | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | InstallDate |
Value: 20251108 | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | InstallLocation |
Value: C:\Users\admin\AppData\Local\Luczystrap | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | ModifyPath |
Value: "C:\Users\admin\AppData\Local\Luczystrap\Luczystrap.exe" -menu | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | QuietUninstallString |
Value: "C:\Users\admin\AppData\Local\Luczystrap\Luczystrap.exe" -uninstall -quiet | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | UninstallString |
Value: "C:\Users\admin\AppData\Local\Luczystrap\Luczystrap.exe" -uninstall | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | NoModify |
Value: 0 | |||
| (PID) Process: | (7888) Luczystrap.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Luczystrap |
| Operation: | write | Name: | NoRepair |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\License - Fluent System Icons.txt | text | |
MD5:F225F140316A29CBE720CBC0CD7C258D | SHA256:9BE360C19BF5502C7927A6CA365A7504B620B408CDF6E3E2413FA63A325BD381 | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\hr\Luczystrap.resources.dll | executable | |
MD5:9C4EF666AC498BDE110A78A4287938BA | SHA256:C51B58D2D2846B1F2FF7A23B3BCA1CE1059B50286E71C11D576F83C6DEDB846E | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\License - Fira Code.txt | text | |
MD5:9D87BF1D936FF3FE5F930AAB8D550A04 | SHA256:0AAEE97F09D5416EB763F36280F7BCCD37776585F768BC35740CF7DDA961A5EA | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\Luczystrap.dll | binary | |
MD5:FFA85A8DD9A59903FD551E091F53551C | SHA256:70F111F0A6D0E4869C4BFC55D68227F6637B312EB4B4830C672AA436BF676BCB | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\Luczystrap.runtimeconfig.json | binary | |
MD5:394D97D8E1185DB1D1E5672511ED5774 | SHA256:EAEFCEC287B085437AD735F2A7715E2097676BE3333A480DB6C77B2866B836F2 | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\en-US\Luczystrap.resources.dll | executable | |
MD5:F5F64393FB46990C389ECA21271E25E9 | SHA256:2A48BDA66539CD5E4CC52C3BA0287665BC5EA1DA4291D204EC9531458C2CFCB8 | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\cs\Luczystrap.resources.dll | executable | |
MD5:A6AC596E9B113195CA091FDD3FBF7613 | SHA256:E8450BFDE8EAC7DFC2AA67566FE23E0F797C93D68B4516AEA646AB5FB03FBC87 | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\fa\Luczystrap.resources.dll | executable | |
MD5:F1F5A284739D98086705BCA569FF3C40 | SHA256:0917FE74D0507F9BE5C1C507688259C1AE55C2125FB73018D2648E3445E4EDEA | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\hu\Luczystrap.resources.dll | executable | |
MD5:76D00E35E4796C615D2762D75B3DA8AA | SHA256:E1E1B32B4F8E1C02F986611F622CCABB42E6972750278125FDC258036EFFDBB0 | |||
| 7888 | Luczystrap.exe | C:\Users\admin\AppData\Local\Temp\.net\Luczystrap\1ed0\da\Luczystrap.resources.dll | executable | |
MD5:180AB835AD5FDA239B26602941D9A799 | SHA256:D39D7131BBB8D1A90B38907B5BE8E761184EE8AC787B3001BA3667674BFA846A | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5596 | MoUsoCoreWorker.exe | GET | 200 | 2.16.168.114:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | RU | binary | 825 b | whitelisted |
— | — | GET | 200 | 18.66.192.61:443 | https://setup.rbxcdn.com/version | US | text | 24 b | unknown |
— | — | GET | 200 | 18.66.192.61:443 | https://setup.rbxcdn.com/version-f6dd34ecac7b4642-rbxPkgManifest.txt | US | — | — | unknown |
— | — | GET | — | 18.66.192.123:443 | https://setup.rbxcdn.com/version-f6dd34ecac7b4642-RobloxApp.zip | US | — | — | unknown |
— | — | POST | 500 | 4.154.185.43:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | unknown |
6416 | svchost.exe | GET | 200 | 2.16.168.114:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | RU | binary | 825 b | whitelisted |
— | — | GET | 200 | 23.201.250.50:443 | https://clientsettingscdn.roblox.com/v2/client-version/WindowsPlayer | NL | binary | 119 b | unknown |
— | — | POST | 204 | 2.16.204.153:443 | https://www.bing.com/web/xlsc.aspx?t=5&dl=1&wsbc=1 | unknown | — | — | unknown |
— | — | POST | — | 4.154.185.43:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | — | — | unknown |
— | — | GET | 200 | 2.16.168.114:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | RU | binary | 825 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
7088 | SearchApp.exe | 2.16.204.142:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
— | — | 192.168.100.255:138 | — | — | — | whitelisted |
6416 | svchost.exe | 2.16.168.114:80 | crl.microsoft.com | Akamai International B.V. | RU | whitelisted |
5596 | MoUsoCoreWorker.exe | 2.16.168.114:80 | crl.microsoft.com | Akamai International B.V. | RU | whitelisted |
— | — | 2.16.168.114:80 | crl.microsoft.com | Akamai International B.V. | RU | whitelisted |
7888 | Luczystrap.exe | 54.192.35.27:443 | setup.rbxcdn.com | AMAZON-02 | US | whitelisted |
7888 | Luczystrap.exe | 140.82.121.6:443 | api.github.com | GITHUB | US | whitelisted |
7888 | Luczystrap.exe | 23.201.250.50:443 | clientsettingscdn.roblox.com | AKAMAI-AS | CH | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
setup.rbxcdn.com |
| whitelisted |
api.github.com |
| whitelisted |
clientsettingscdn.roblox.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |